How To Use Ghidra For Malware Analysis - Establishing Context on ...
How To Use Ghidra For Malware Analysis - Identifying, Decoding and ...
Ghidra for malware analysis: how to actually use it without losing your ...
⛏ A detailed guide on how to use Ghidra to Reverse Engineer Malware ...
How to use Ghidra for malware analysis, reverse-engineering | TechTarget
Ghidra UI Updates for Malware Analysis and Introduction to python3 ...
AgentTesla Malware Analysis - How To Resolve API Hashes With ...
How to Deconstruct and Reverse Engineer Malware Using Ghidra ...
How to Use Ghidra to Analyse Shellcode and Extract Cobalt Strike ...
How to Use Ghidra to Reverse Engineer Malware | Varonis
A Guide to Ghidra Scripting Development for Malware Researchers ...
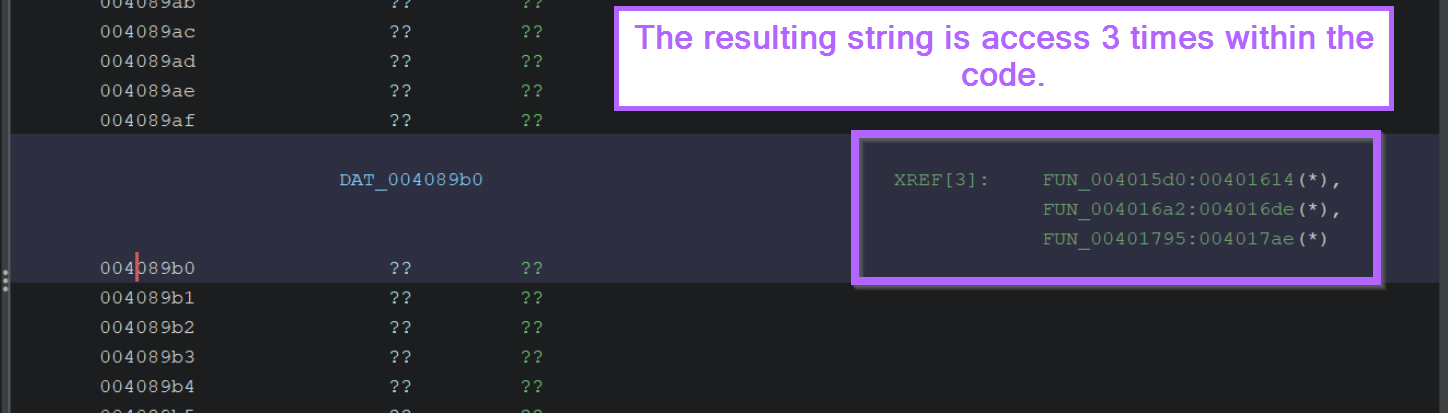
Ghidra For Malware Analysis - Pivoting from String Cross References
CS6038 2020: Week 13 Lec. 2 - Static Android Malware Analysis in Ghidra ...
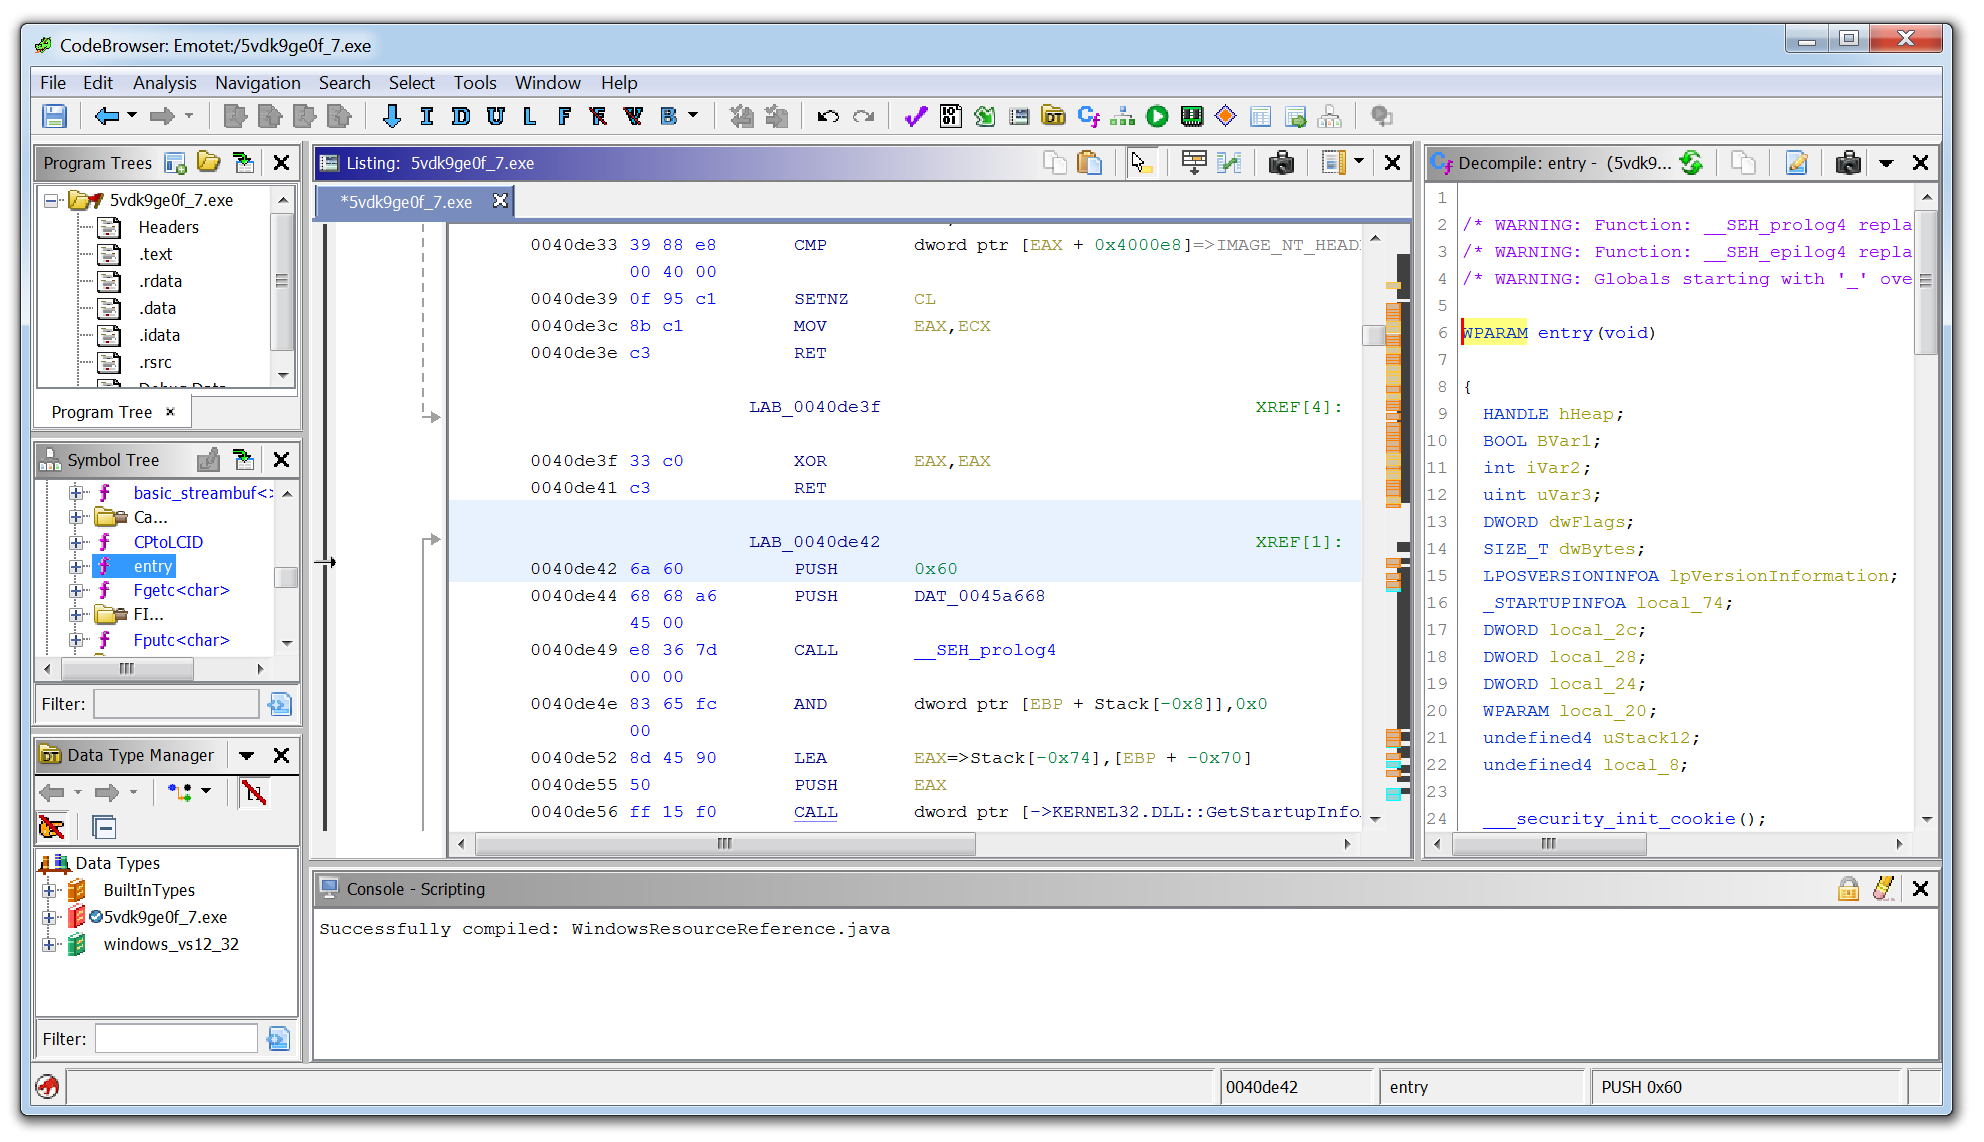
Malware Analysis at Scale ~ Defeating EMOTET by Ghidra ~ - TT Security ...
Android Malware Analysis Part3 - Ghidra and Malware Reverse Engineering ...
How to use Ghidra to Reverse Engineer Mobile Application | by K O M A L ...
GHIDRA Tutorial — Learn How to Use Reverse Engineering Tool - YouTube
Understanding and Improving The Ghidra UI for Malware Analysis
Getting Started With Ghidra For Malware Analysis : r/ReverseEngineering
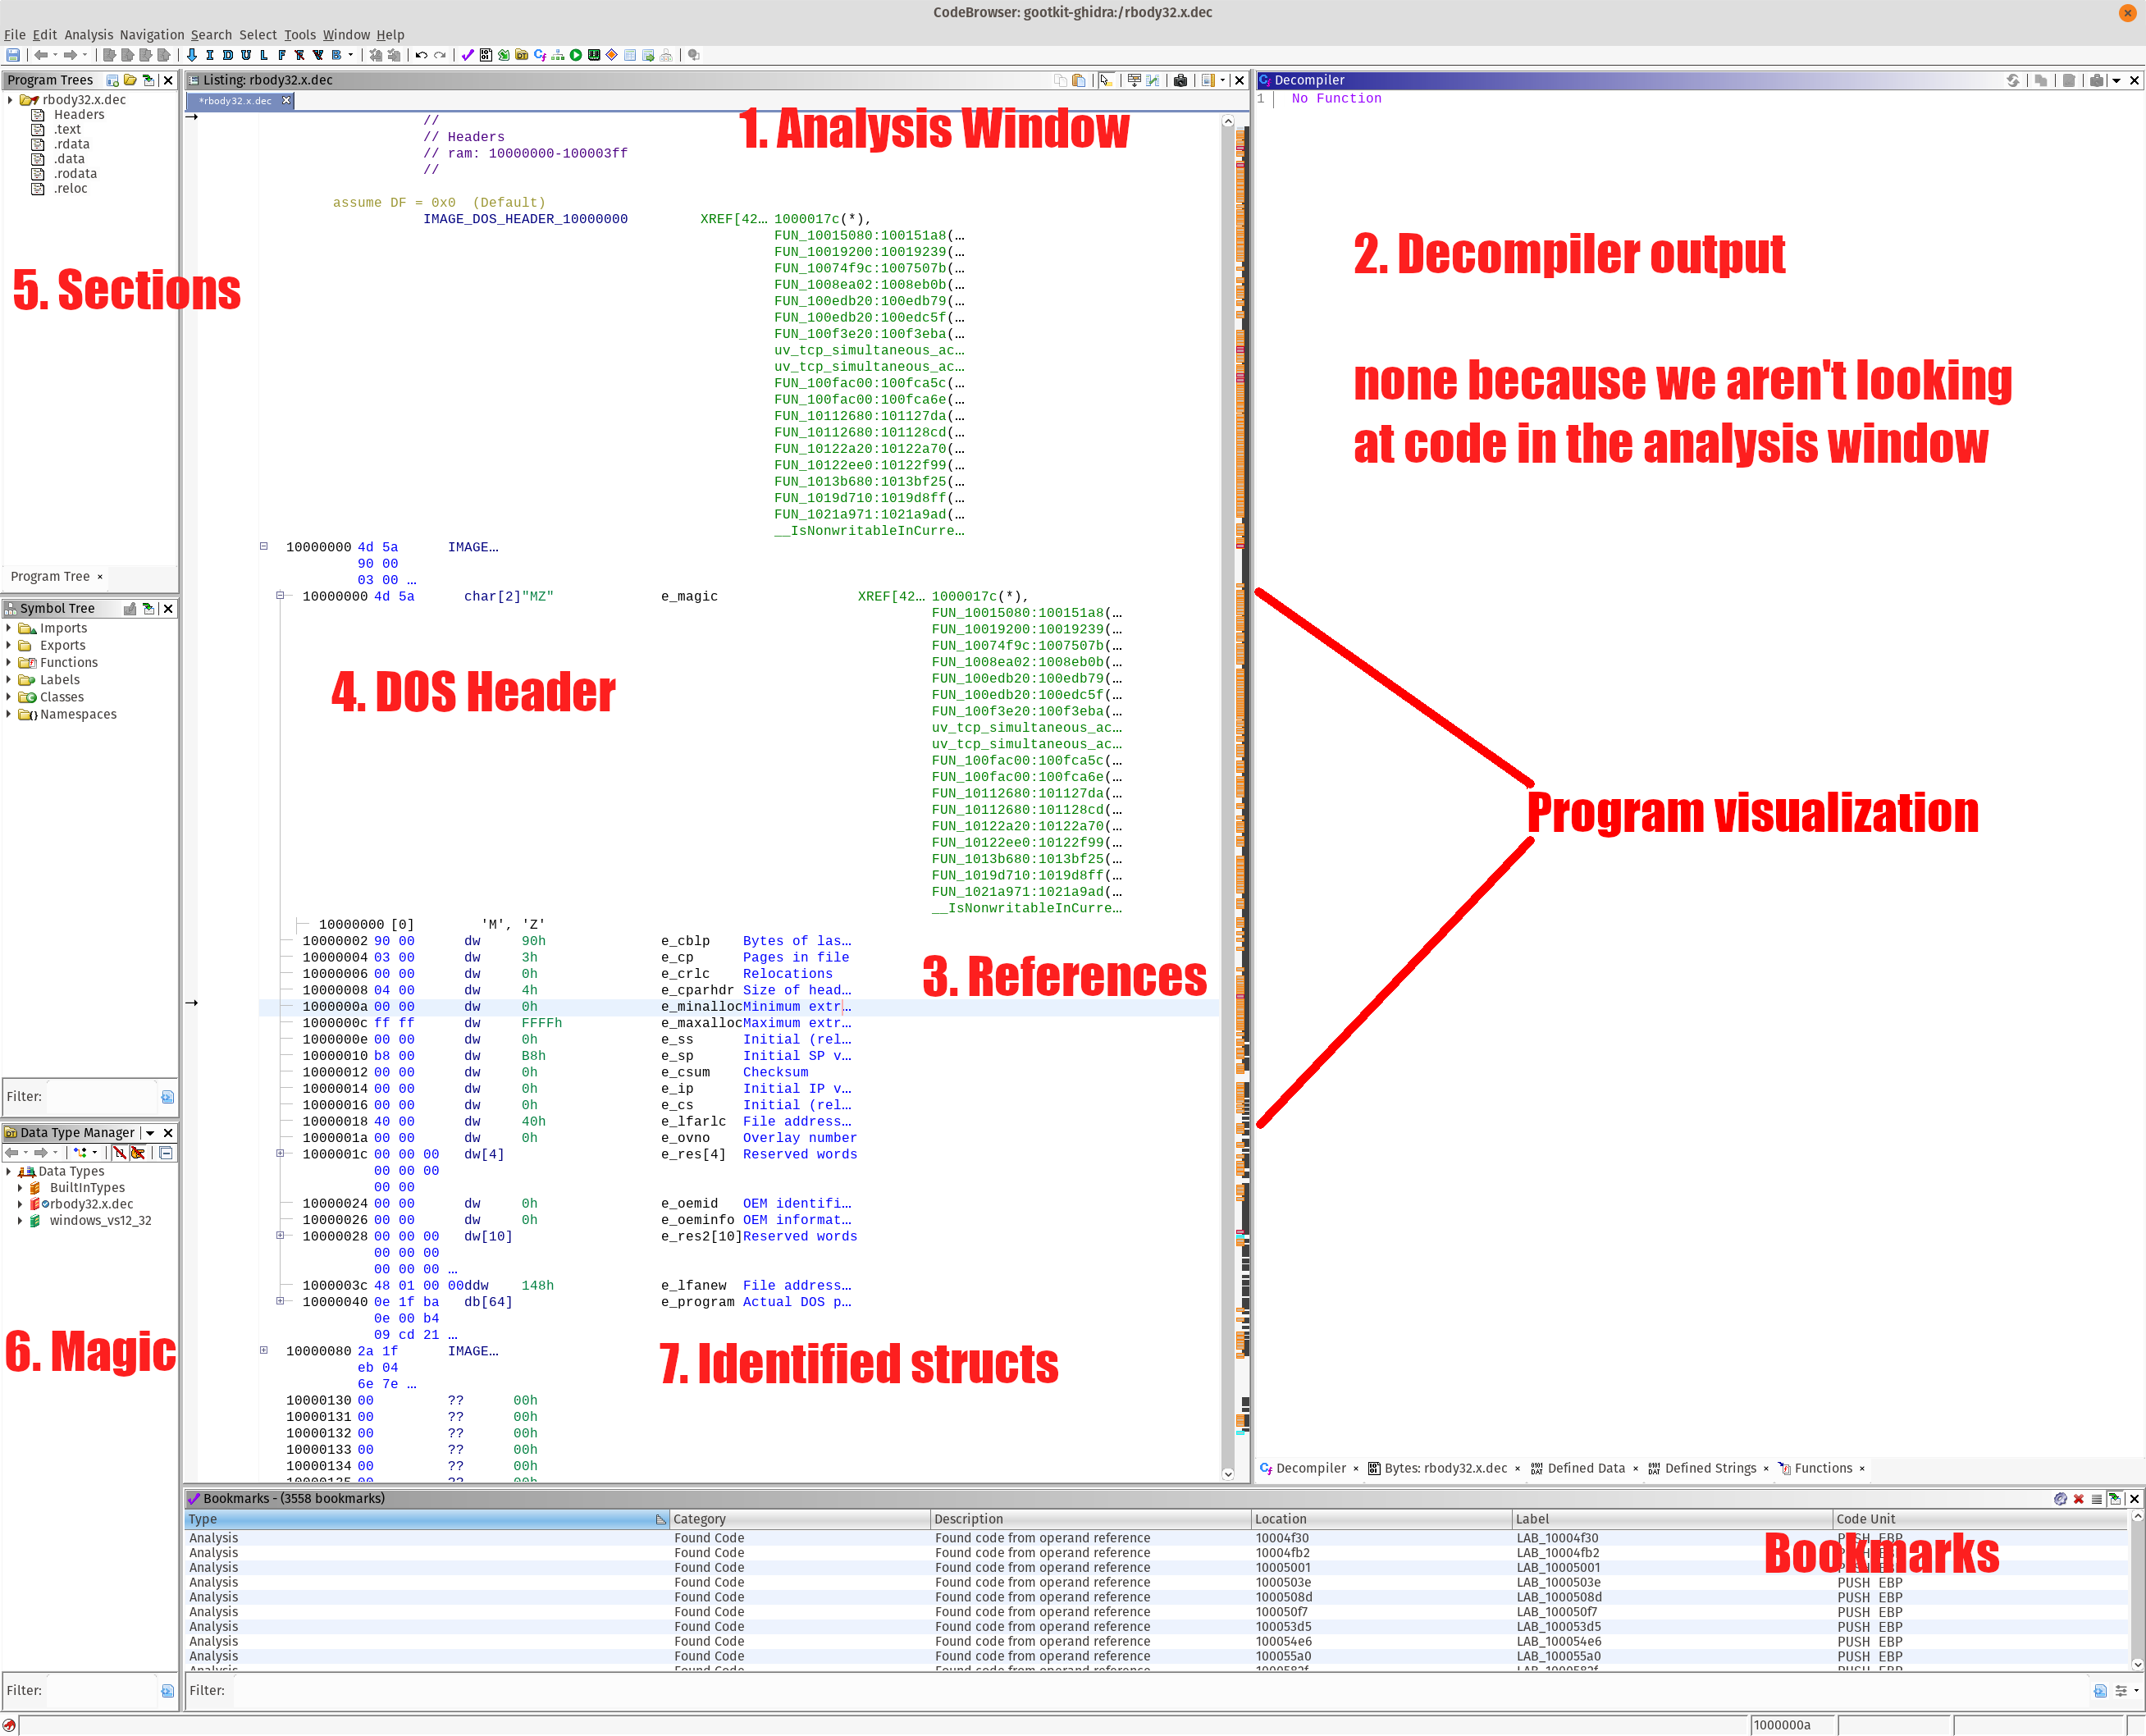
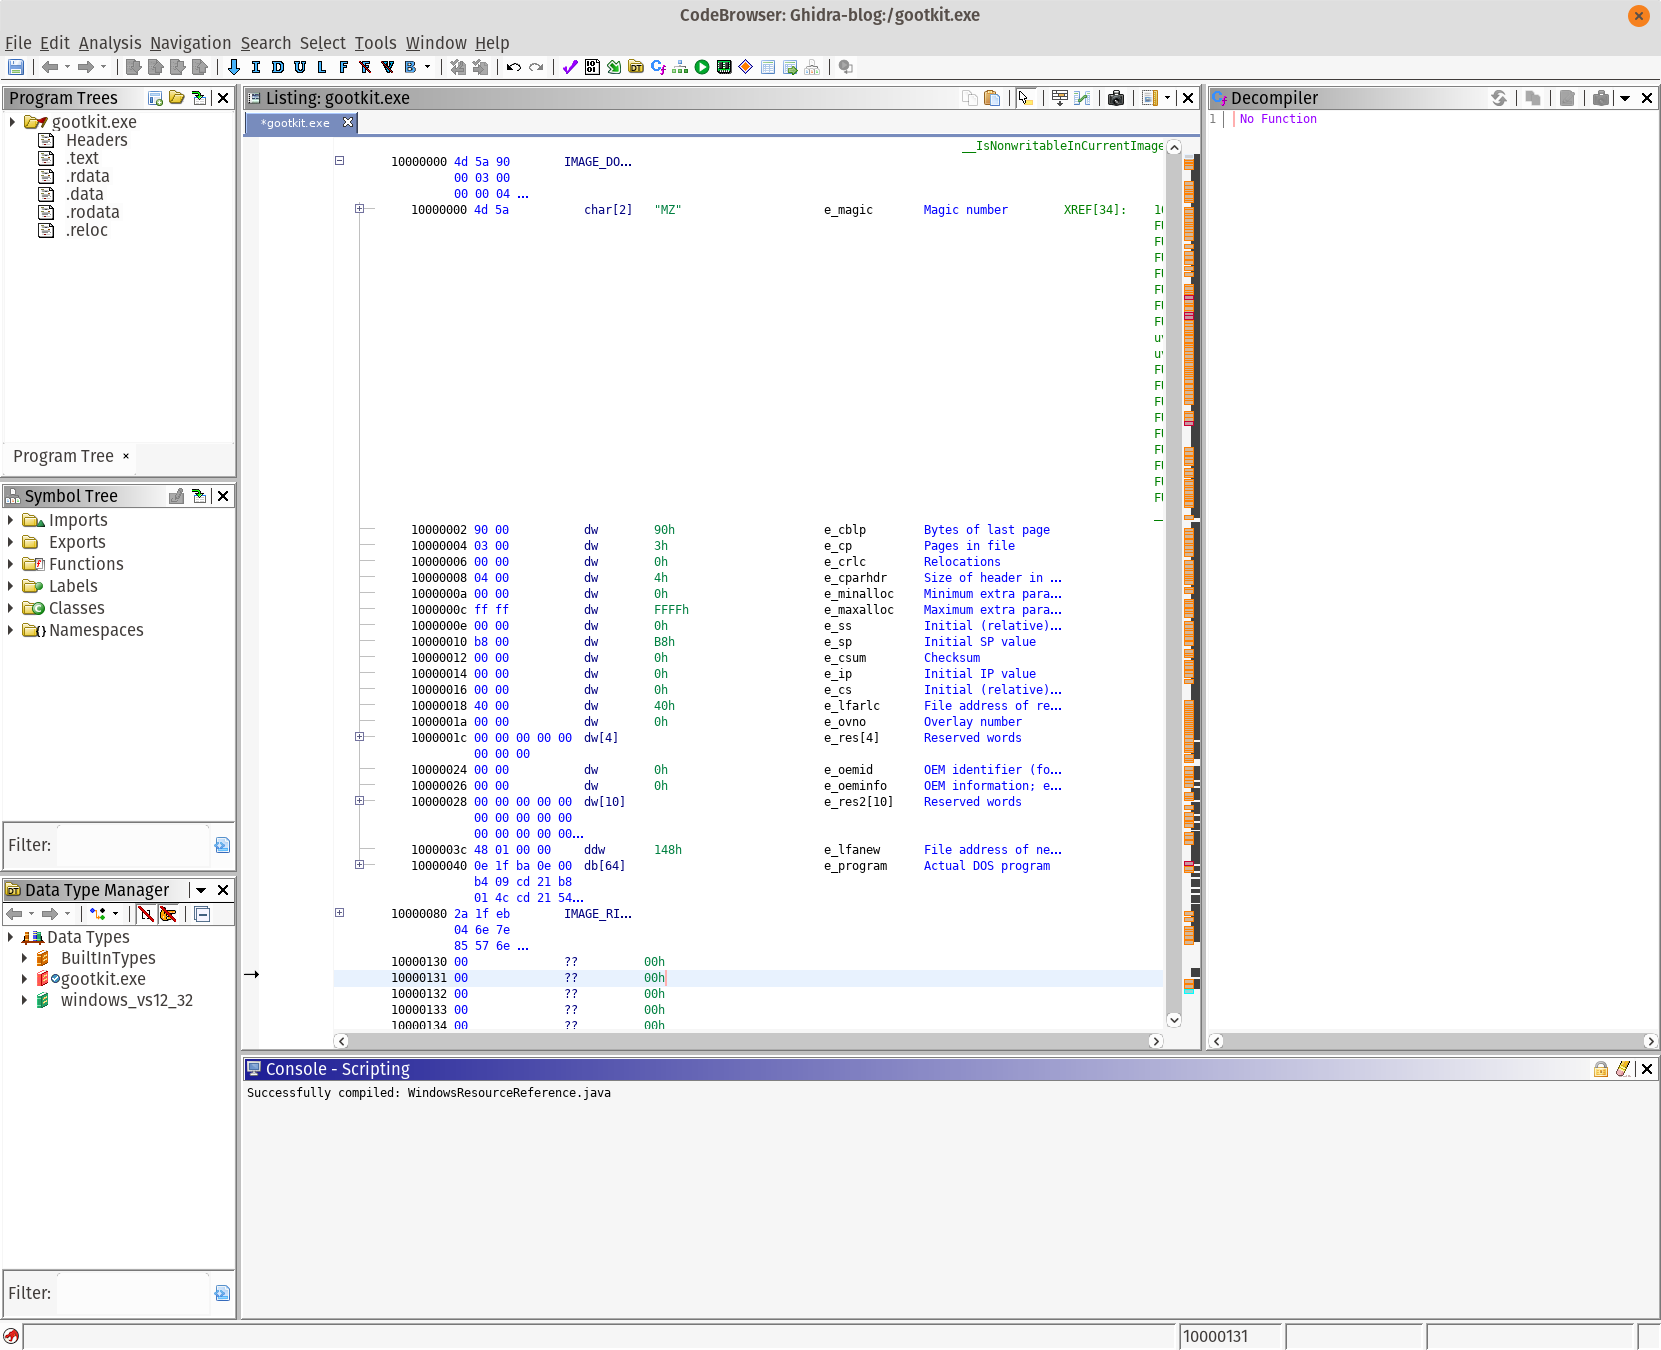
Reverse Engineering Gootkit with Ghidra Part I – Open Malware - Danny ...
Malware Analysis Lab Basics - Part 2 - Installing Ghidra - YouTube
Starting Real Malware Analysis with Ghidra | Reverse Engineering - YouTube
ANALYSIS MALWARE WITH GHIDRA - YouTube
Malware Analysis With Ghidra - Stuxnet Analysis - YouTube
Malware Analysis with Ghidra | TryHackMe Advanced static analysis - YouTube
Exploring Malware Analysis with Ghidra - YouTube
GitHub - ceeddulin-web/malware-analysis: Malware Analysis Lab – Static ...
Ghidra for Ethical Hackers: A Practical Guide to Master Reverse ...
Analysis Techniques For Beginners Getting Started With Ghidra | Embee ...
Create YARA rules with GHIDRA | MALWARE Analysis of Havoc Demon ...
Ghidra Tutorial - Using Entropy To Locate a Cobalt Strike Decryption ...
Tracking Malware Behaviour in Ghidra : From Named Pipes to Process ...
Malware Analysis Guides - Embee Research
Malware Analysis with Ghidra | TryHackMe Advanced Static Analysis
HTB Challenge: Simple Encryptor Part 1 · Malware Analysis: Or How I ...
Ghidra Basics - Manual Shellcode Analysis and C2 Extraction : r/blueteamsec
Ghidra Firmware Analysis Guide | PDF | String (Computer Science ...
Practical Malware Analysis - Chapter 21 Lab Write-up : Jai Minton
Deobfuscating the Latest GuLoader: Automating Analysis with Ghidra ...
The Top 20 Malware Analysis Tools for 2026
Amazon.com: Ghidra for Security Professionals: Advanced Reverse ...
Importance of Symbols in Malware Analysis and Ghidra Setup | Course Hero
How to Analyze Ransomware with ANY.RUN & Ghidra
Ghidra Nation State Level Reverse Engineering Tools – Open Malware ...
13 Best Malware Analysis Tools Of 2026 - RankRed
Exploring Ghidra: An Essential Guide for Malware Analysis | Course Hero
Online Course: Reverse Engineering Malware with Ghidra from Pluralsight ...
Beginner Ghidra Guide - Manual Shellcode Decryption
11 Best Malware Analysis Tools and Their Features
Reverse Engineering AgentTesla Malware with Ghidra: A Step-by-Step ...
Advanced Malware Analysis with Ghidra: Tools, Techniques & | Course Hero
Firmware Reversing and Analysis Tools - Thyrasec
Analysis of RedXOR Malware – RIT Computing Security Blog
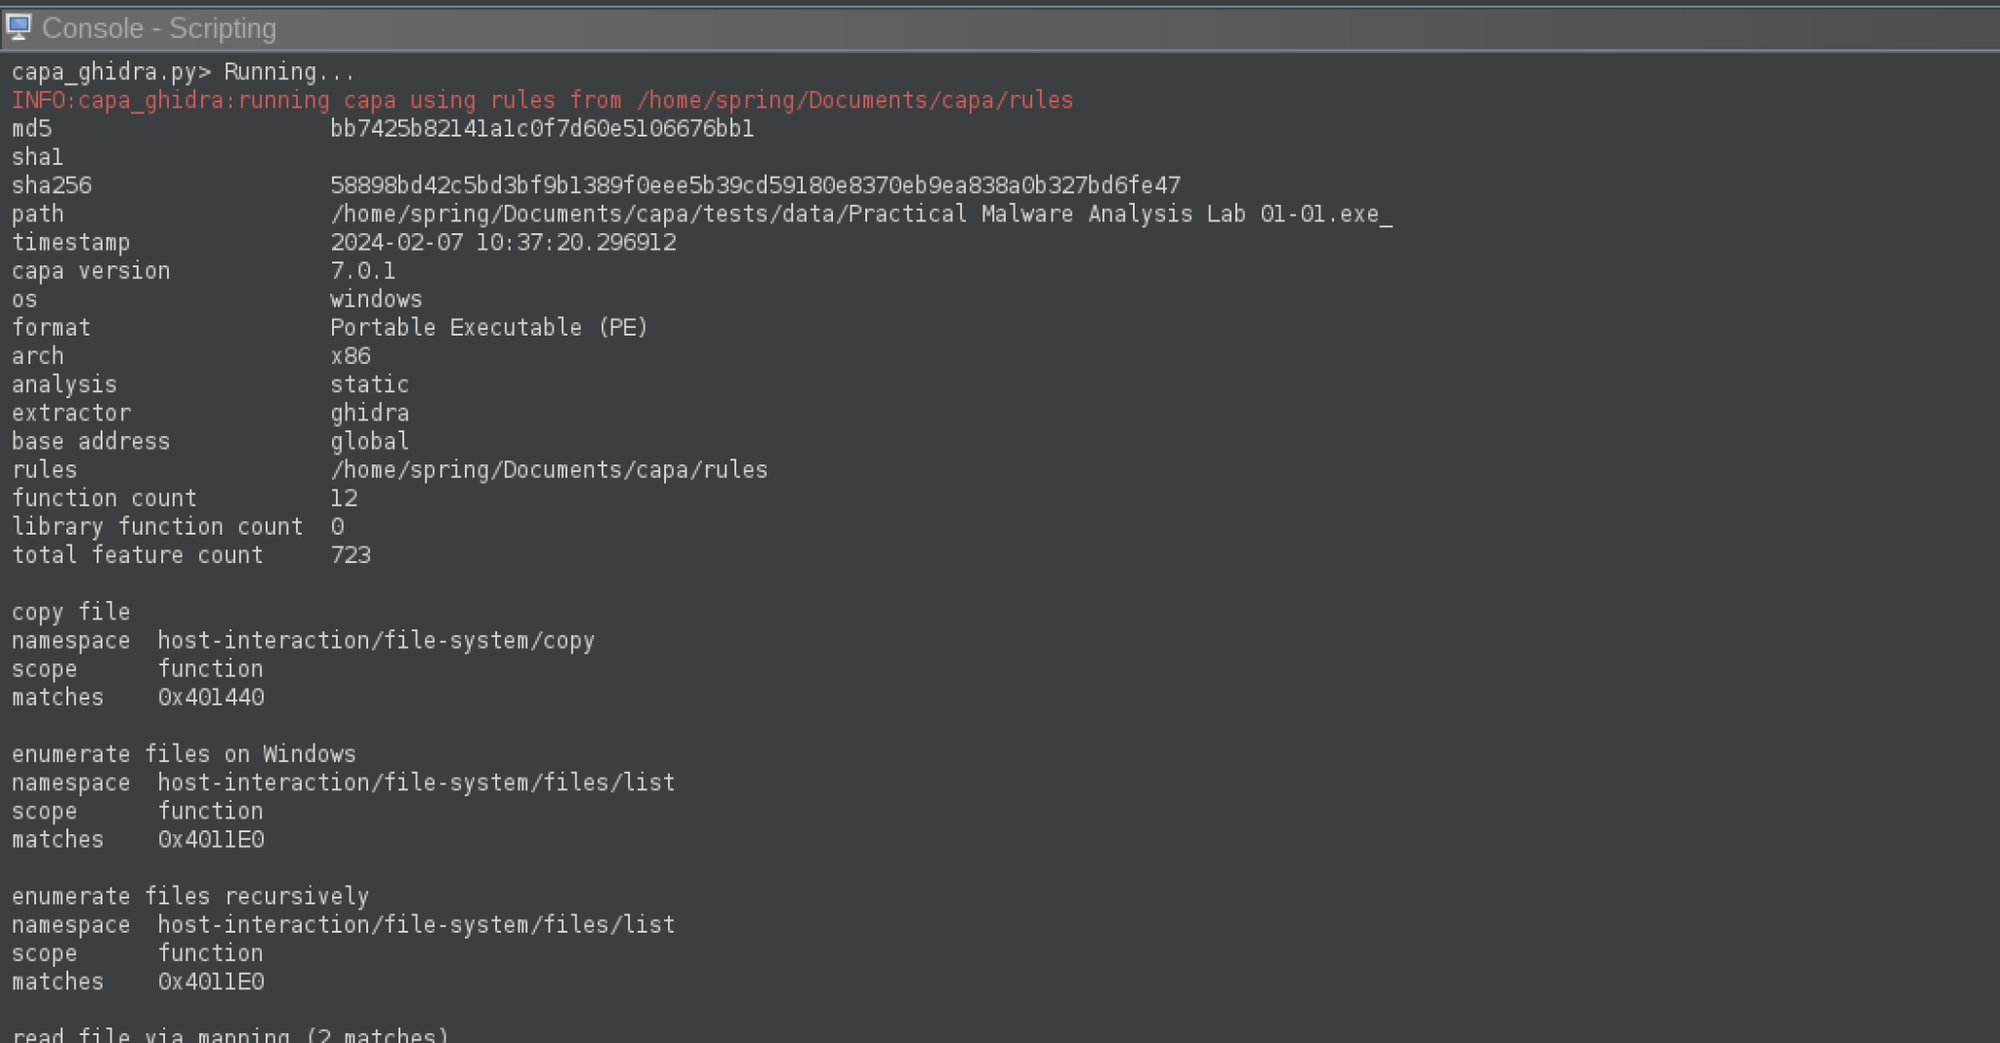
Riding Dragons: capa Harnesses Ghidra | Google Cloud Blog
CS6038/CS5138 Malware Analysis, UC by ckane
Getting Started with Ghidra: Hands-On with the Powerful Reverse ...
#cyberdefense #cyberattacks #cybersecurity #cybersecuritytips # ...
Defeating Windows API Hashing in Malware with Hashdb-Ghidra | aj-tap
GREM Journey: Navigating SANS FOR610 and the Certification Experience ...
Unmasking TeslaCrypt: A Deep Dive into Ransomware Analysis and Prevention
Reverse Engineering with Ghidra
What is Ghidra and Why is it Important?
#cybersecurity #webinar #ghidra #malwareanalysis | Elephant Scale
#malware #detection #yara #ghidra #re | Matthew Brennan