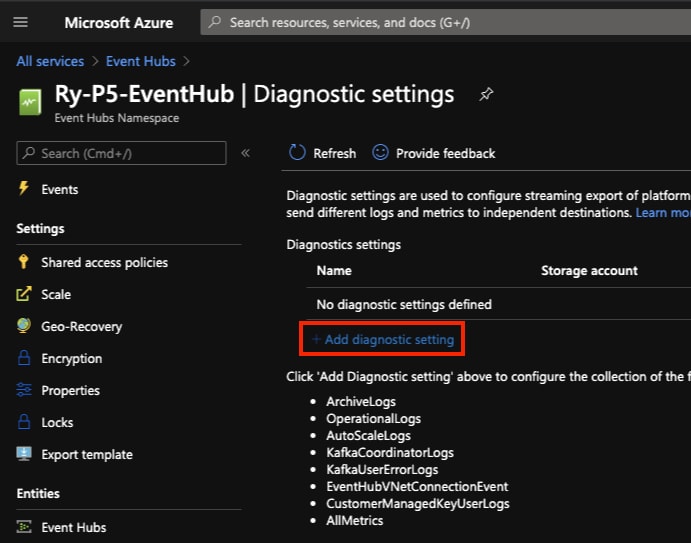
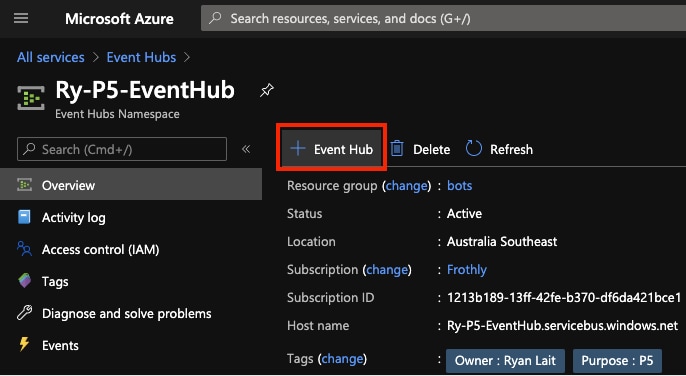
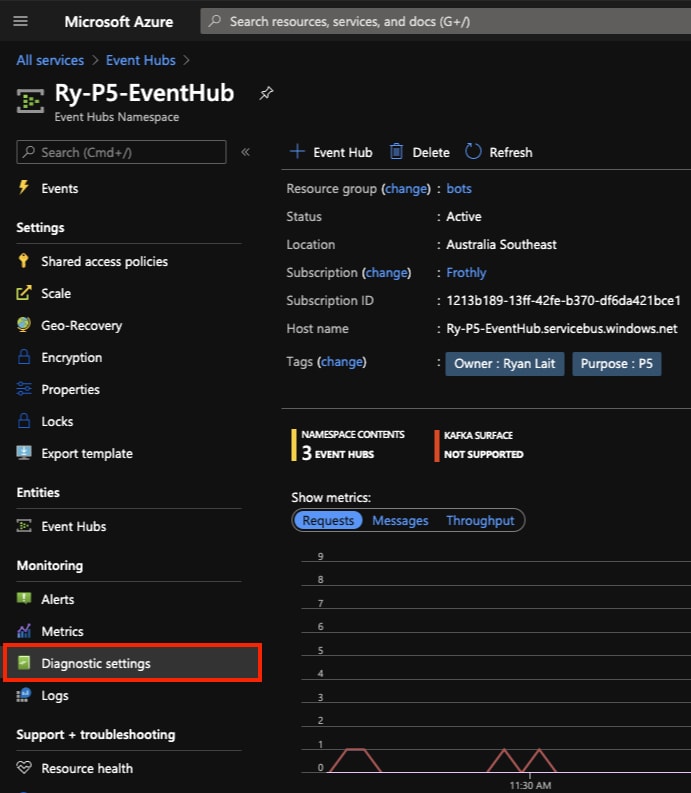
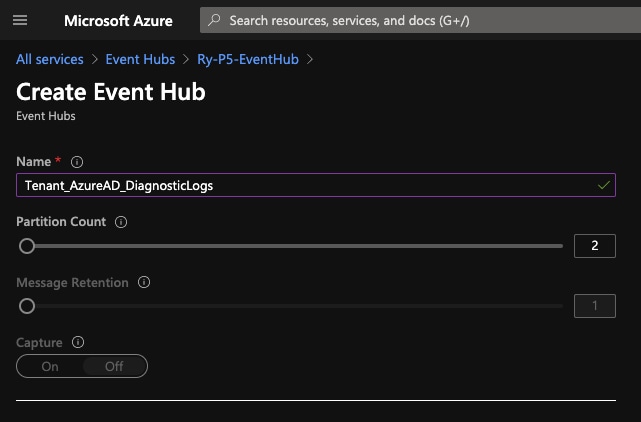
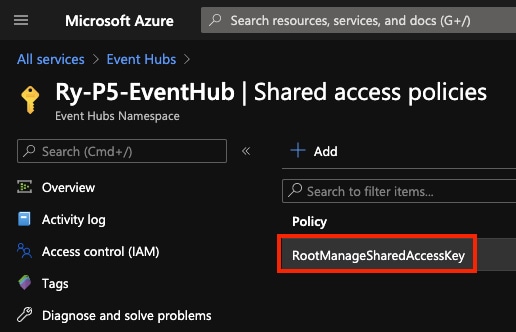
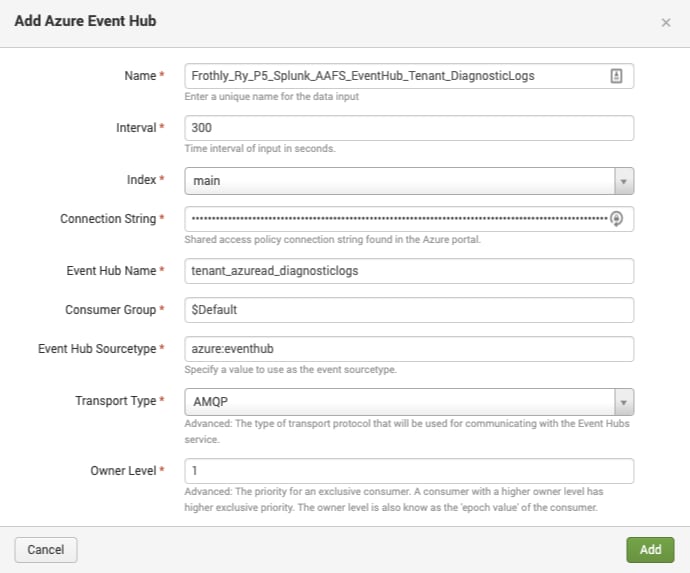
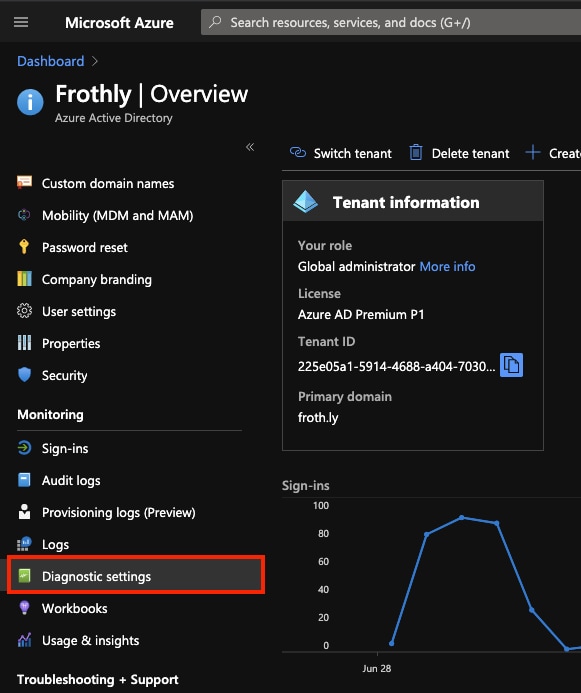
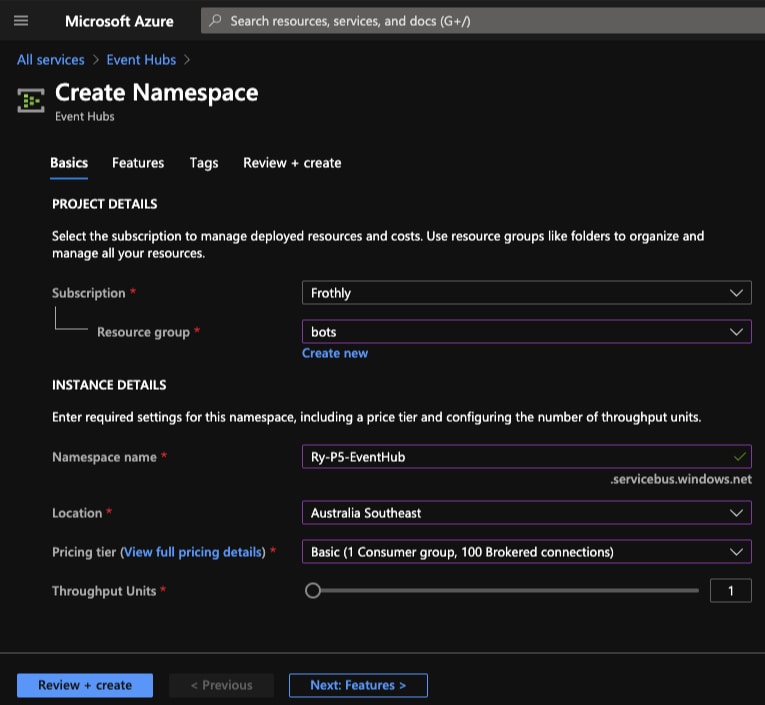
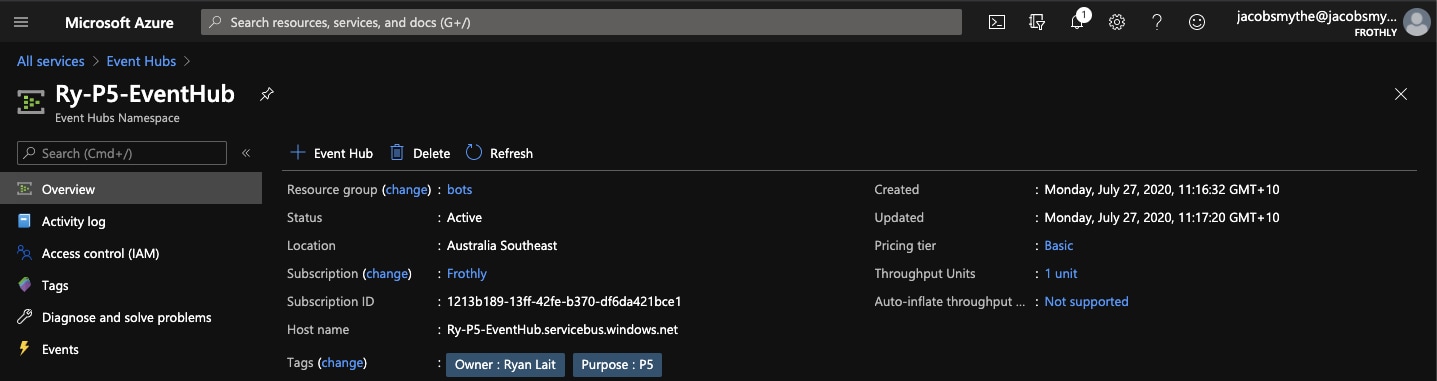
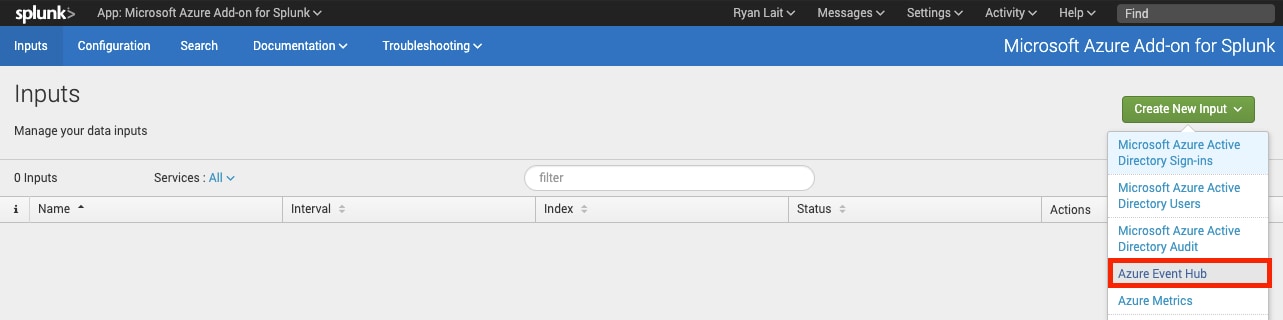
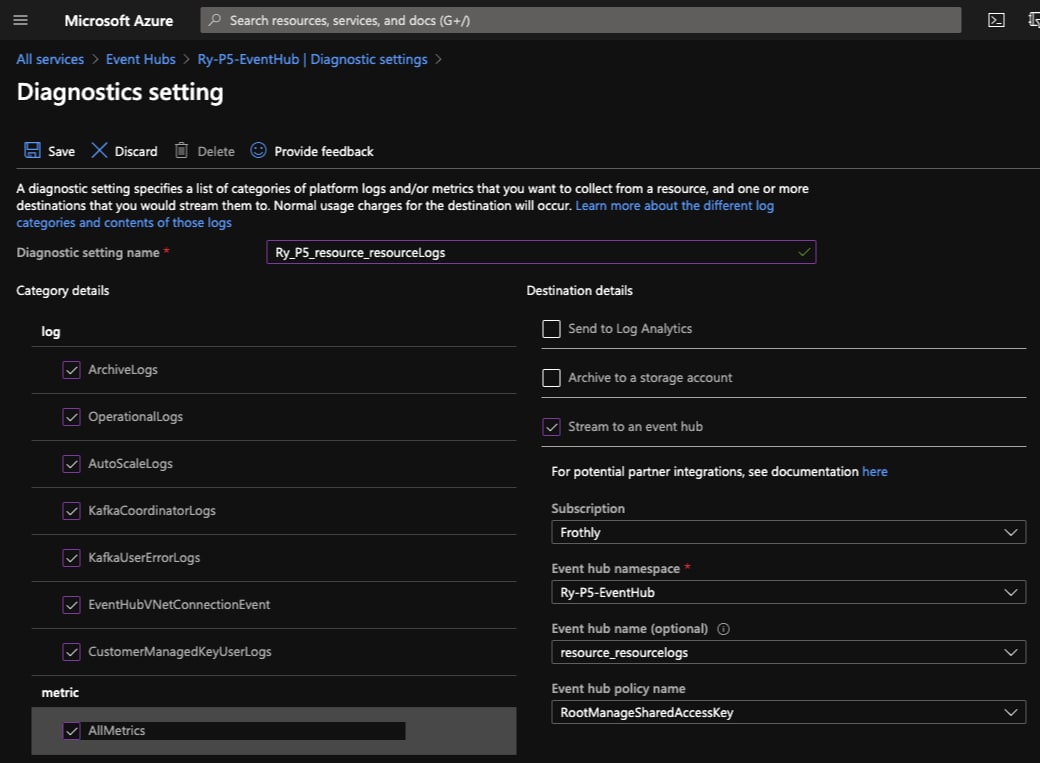
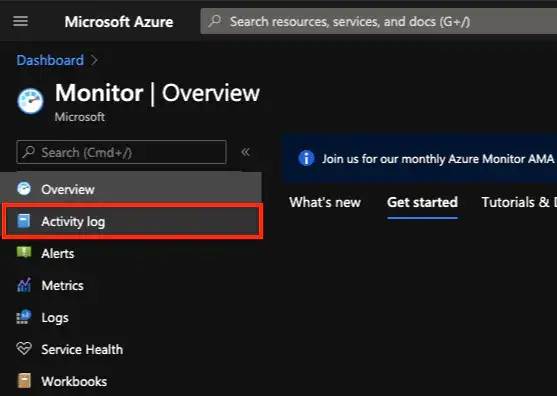
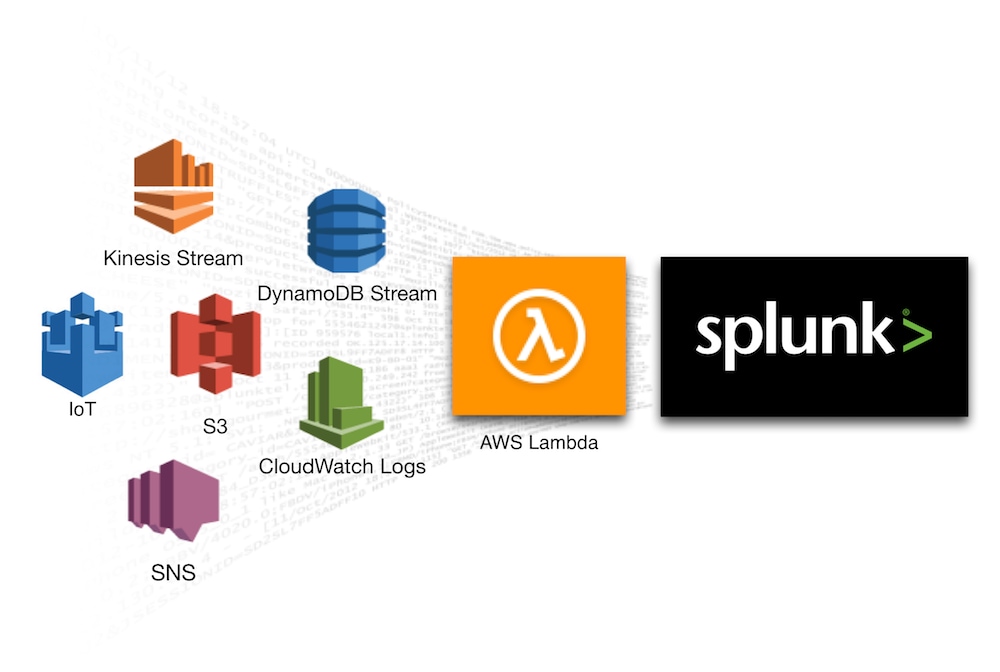
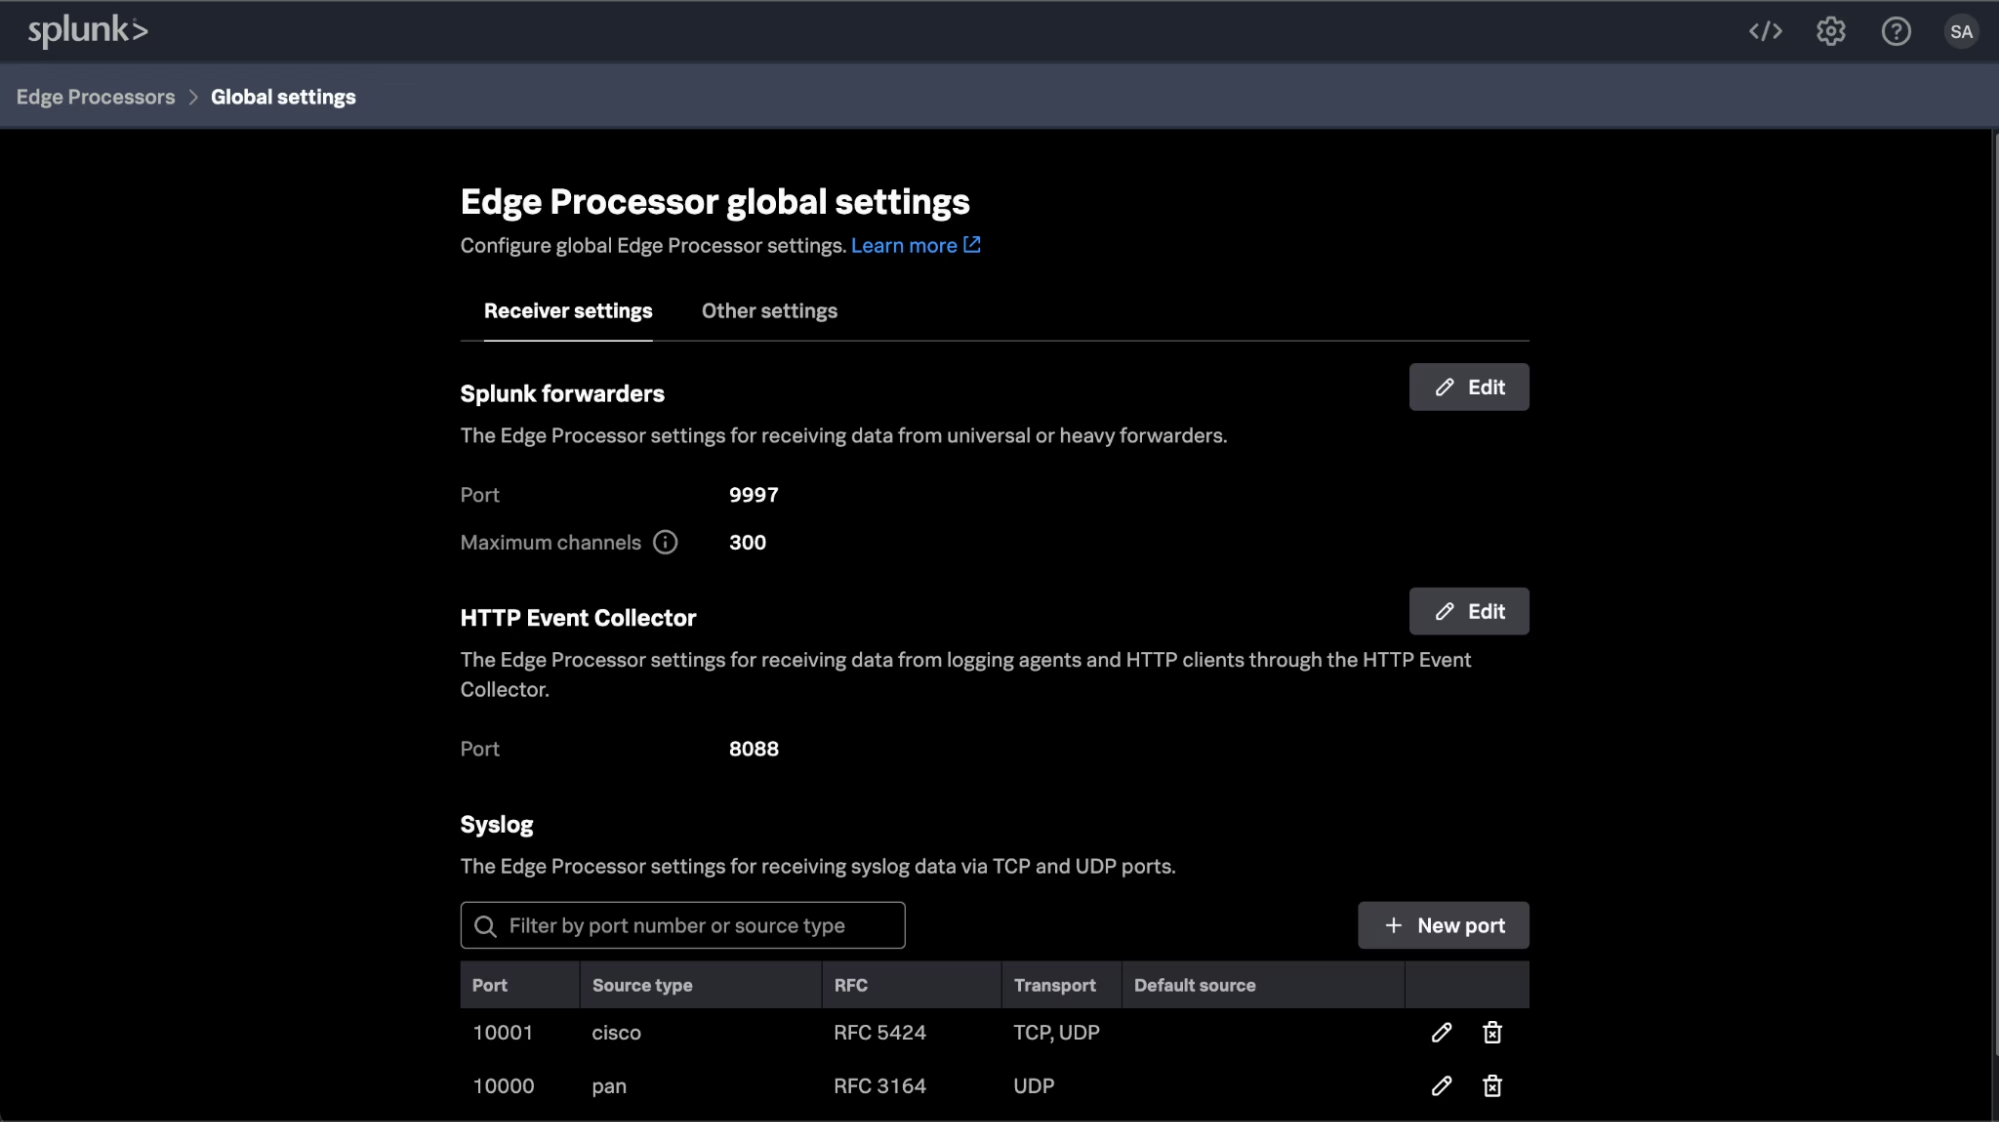
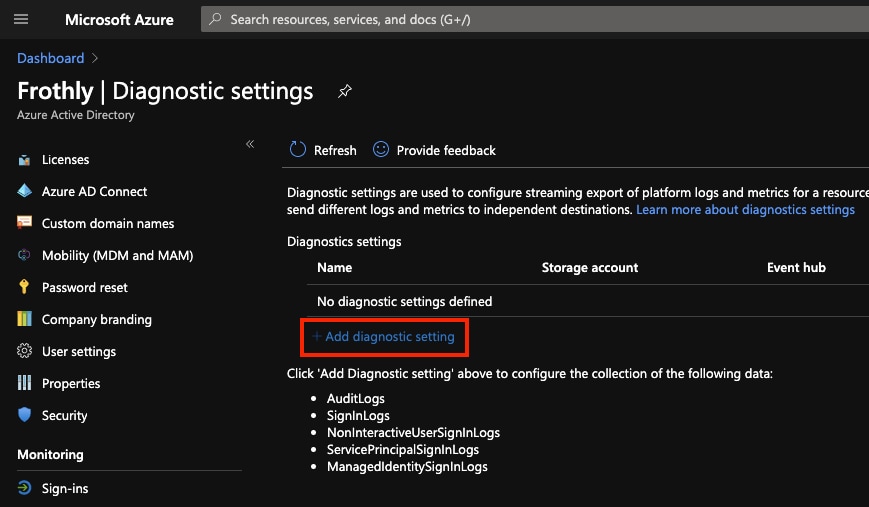
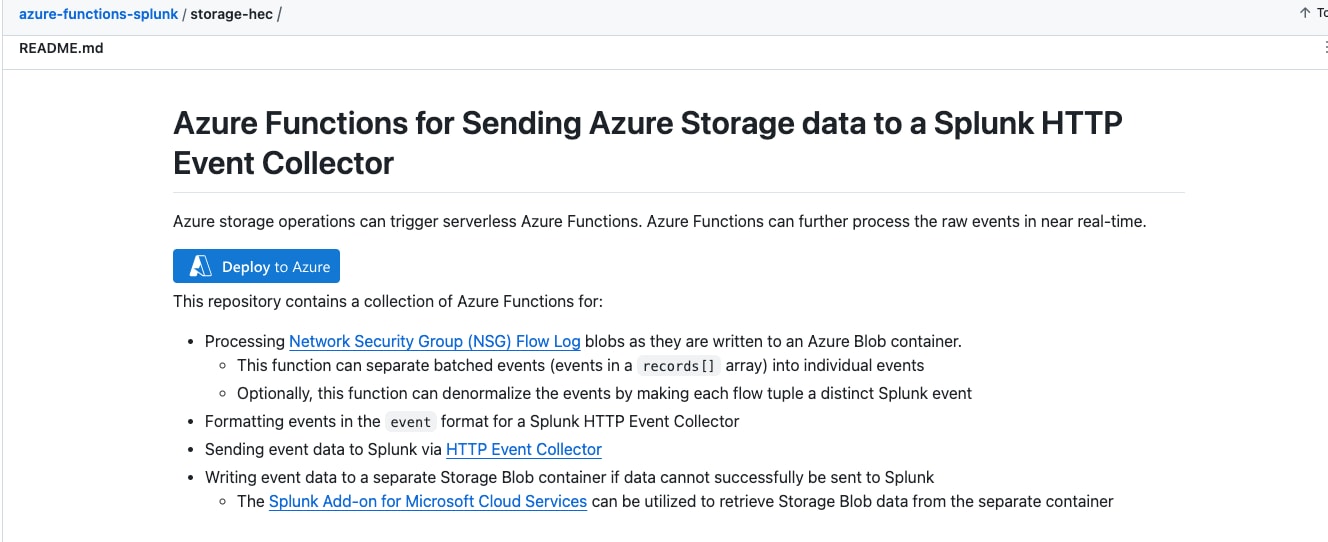
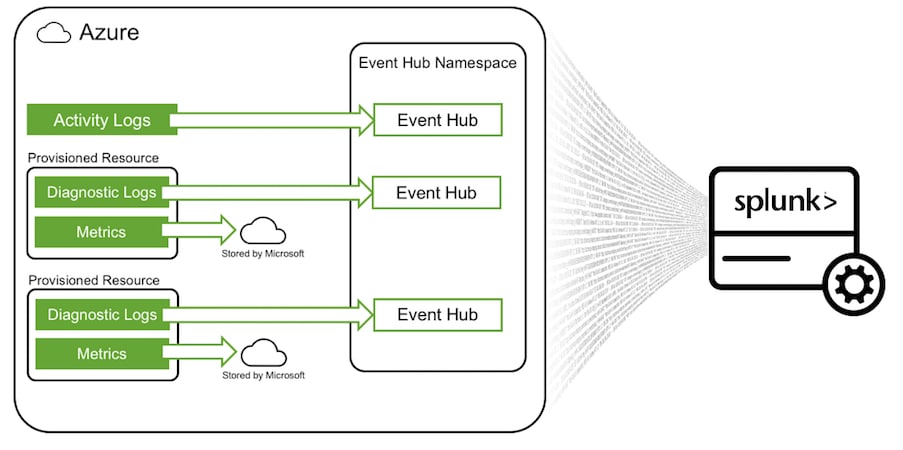
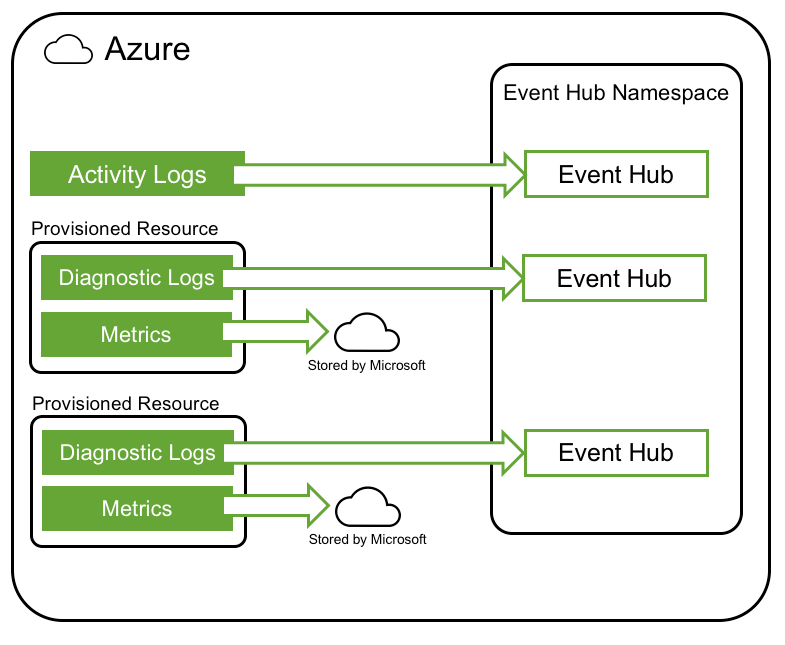
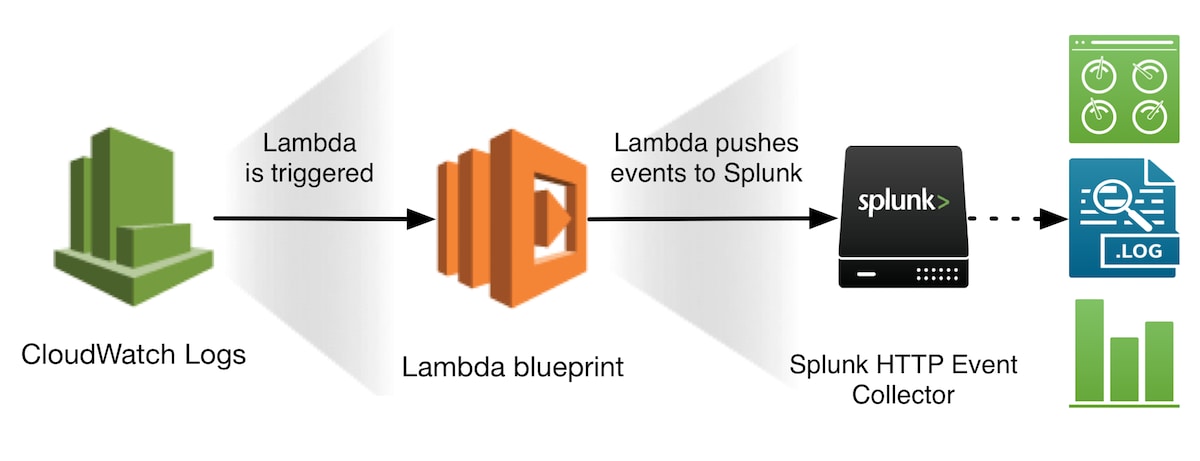
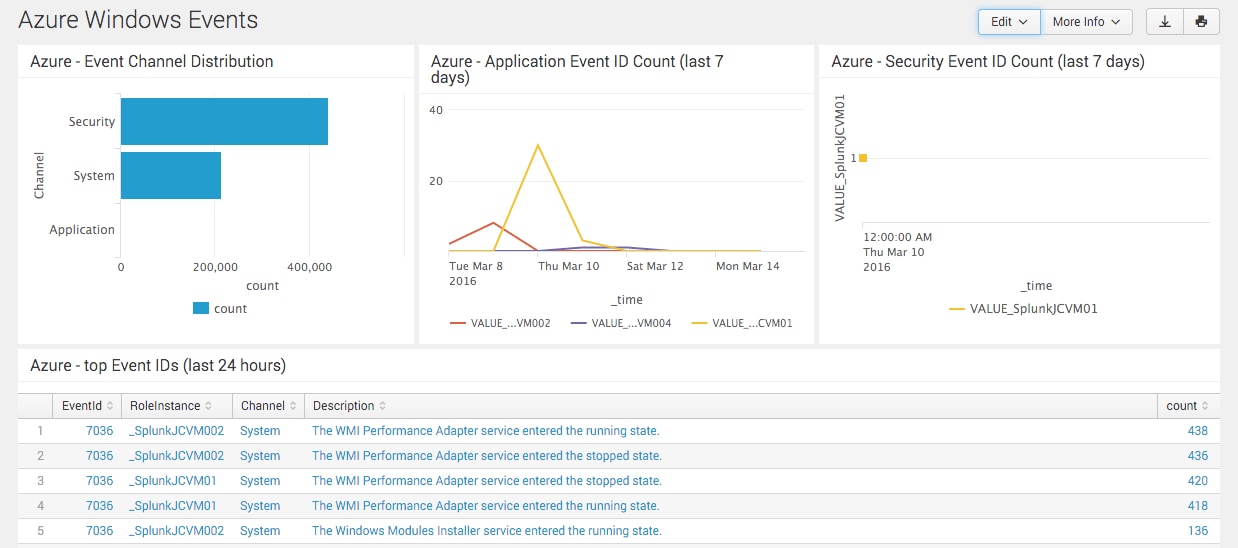
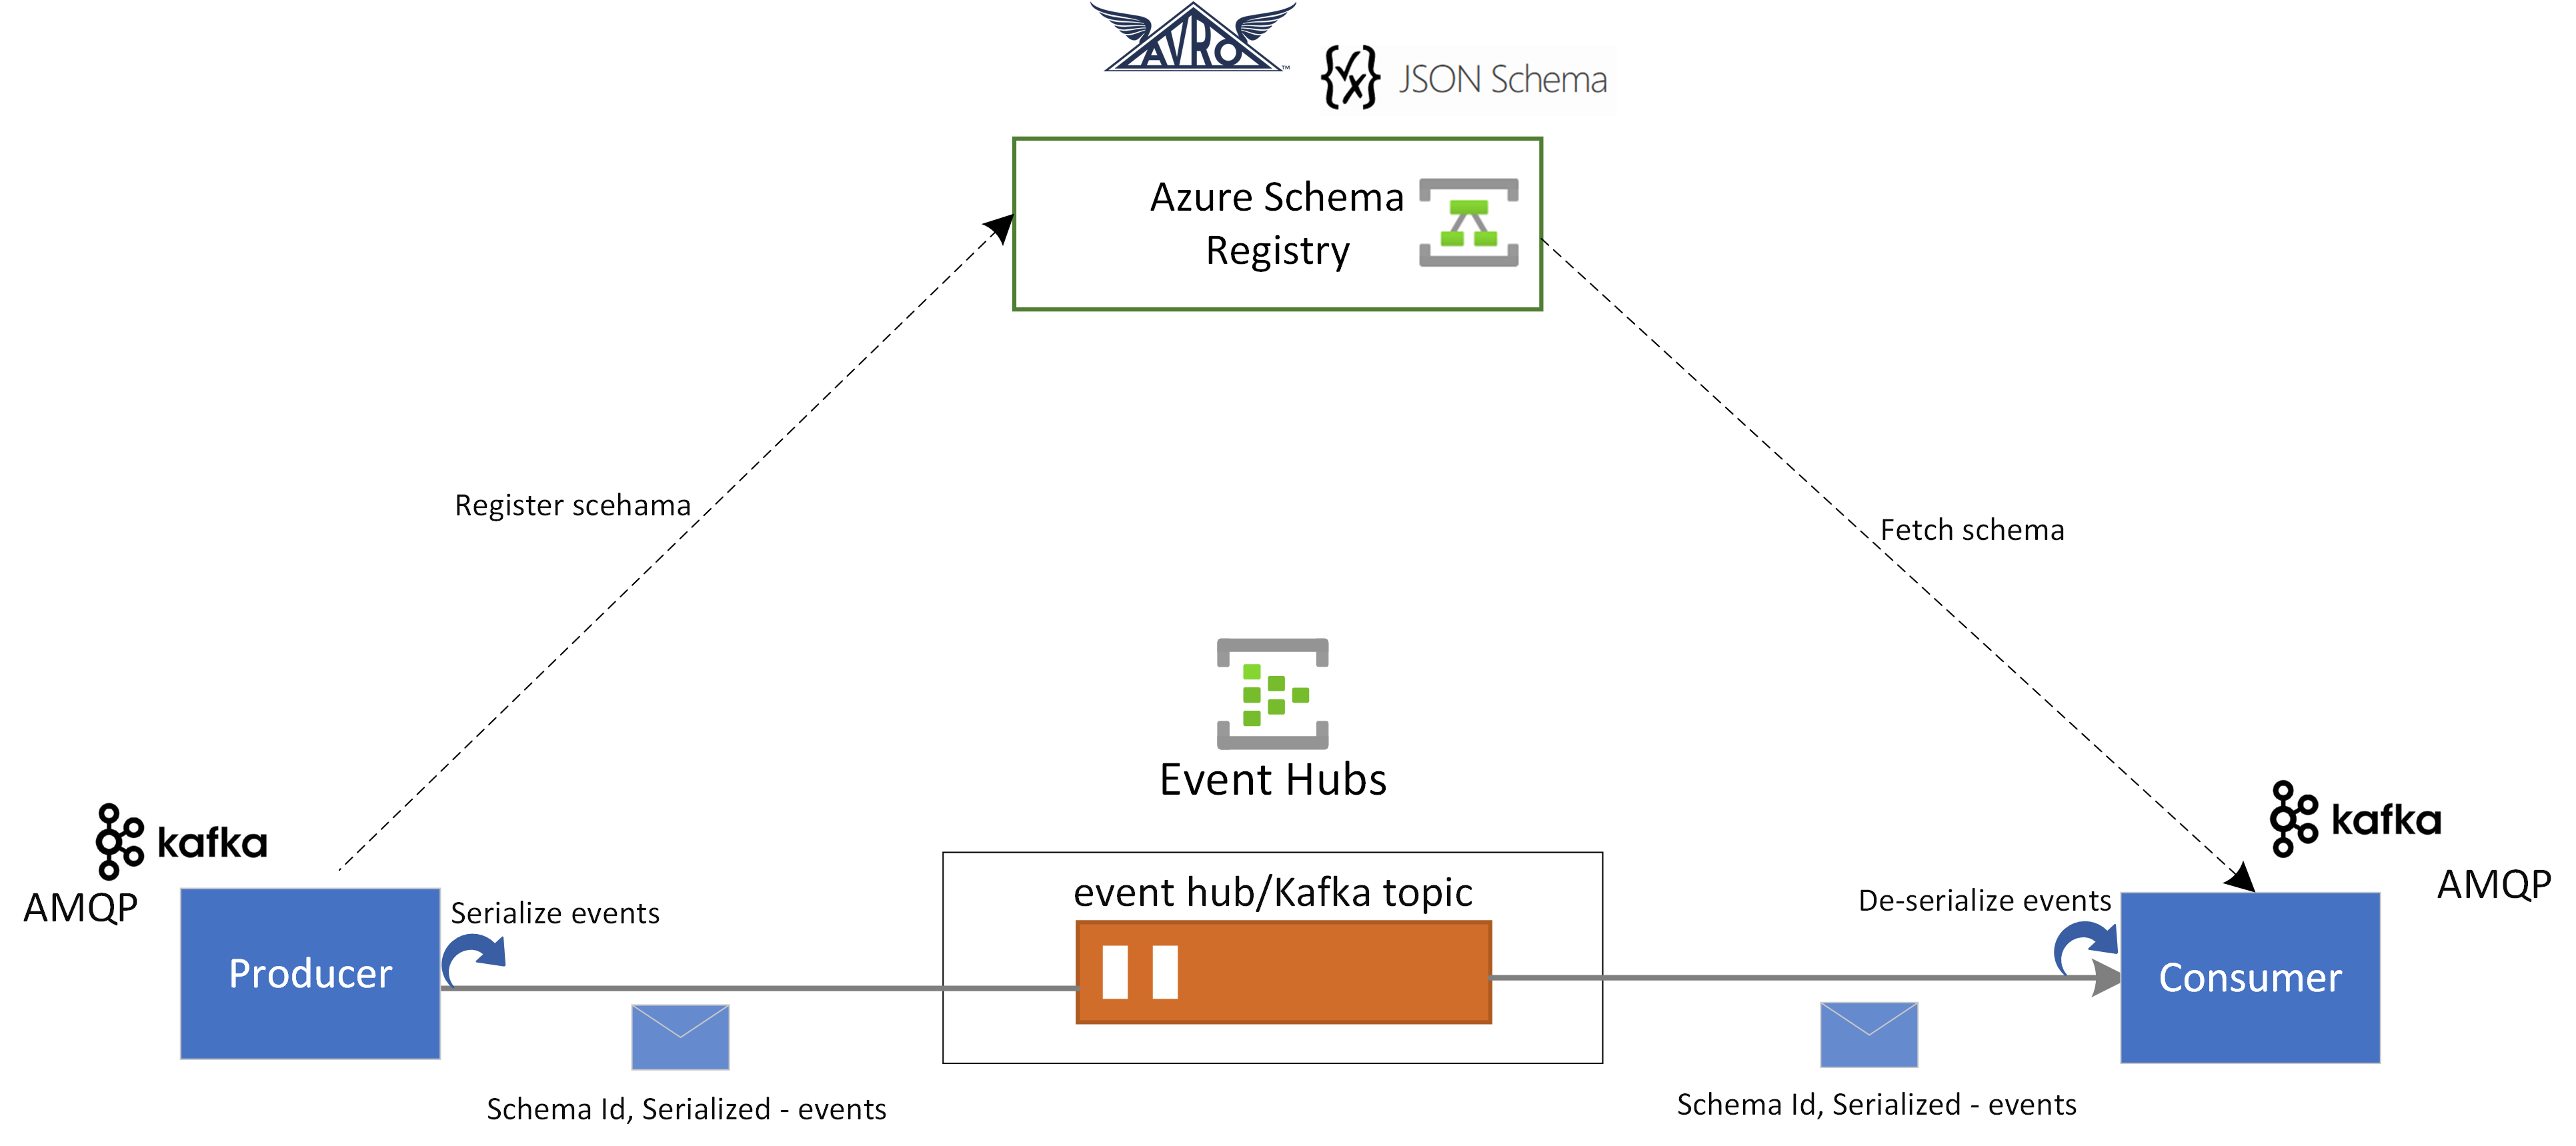
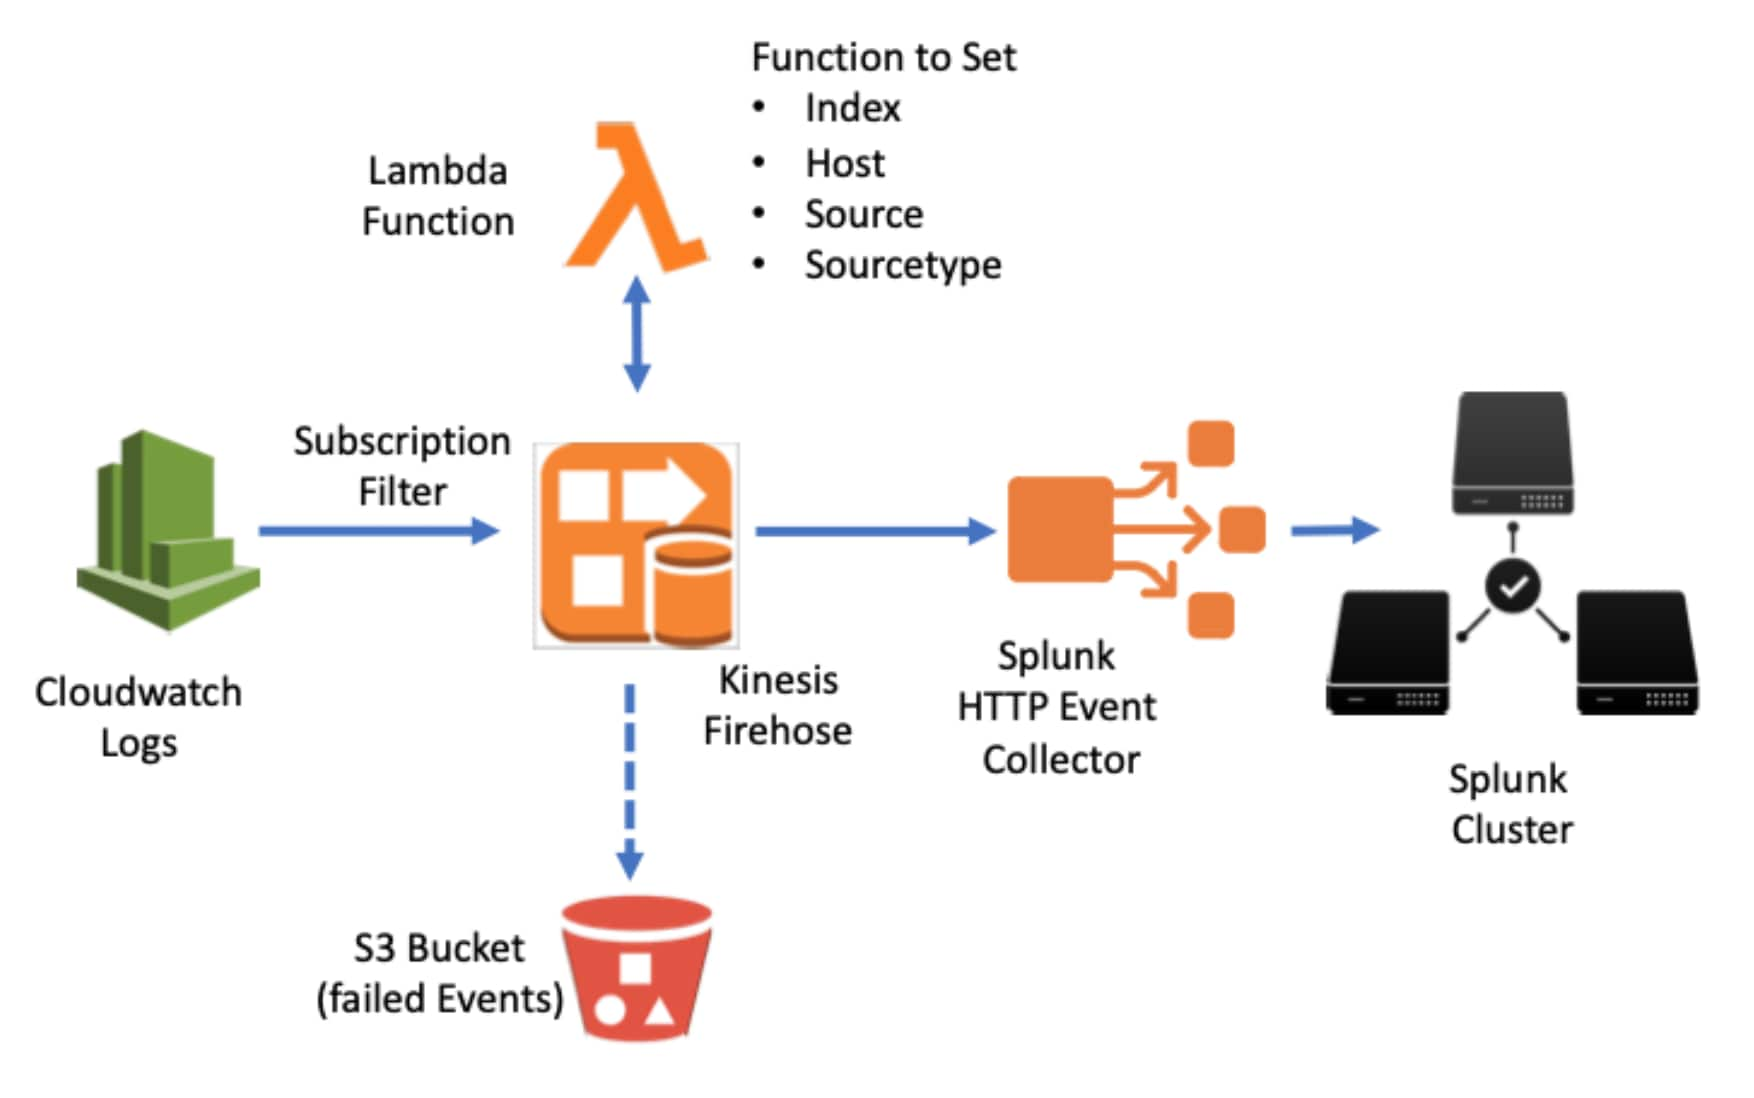
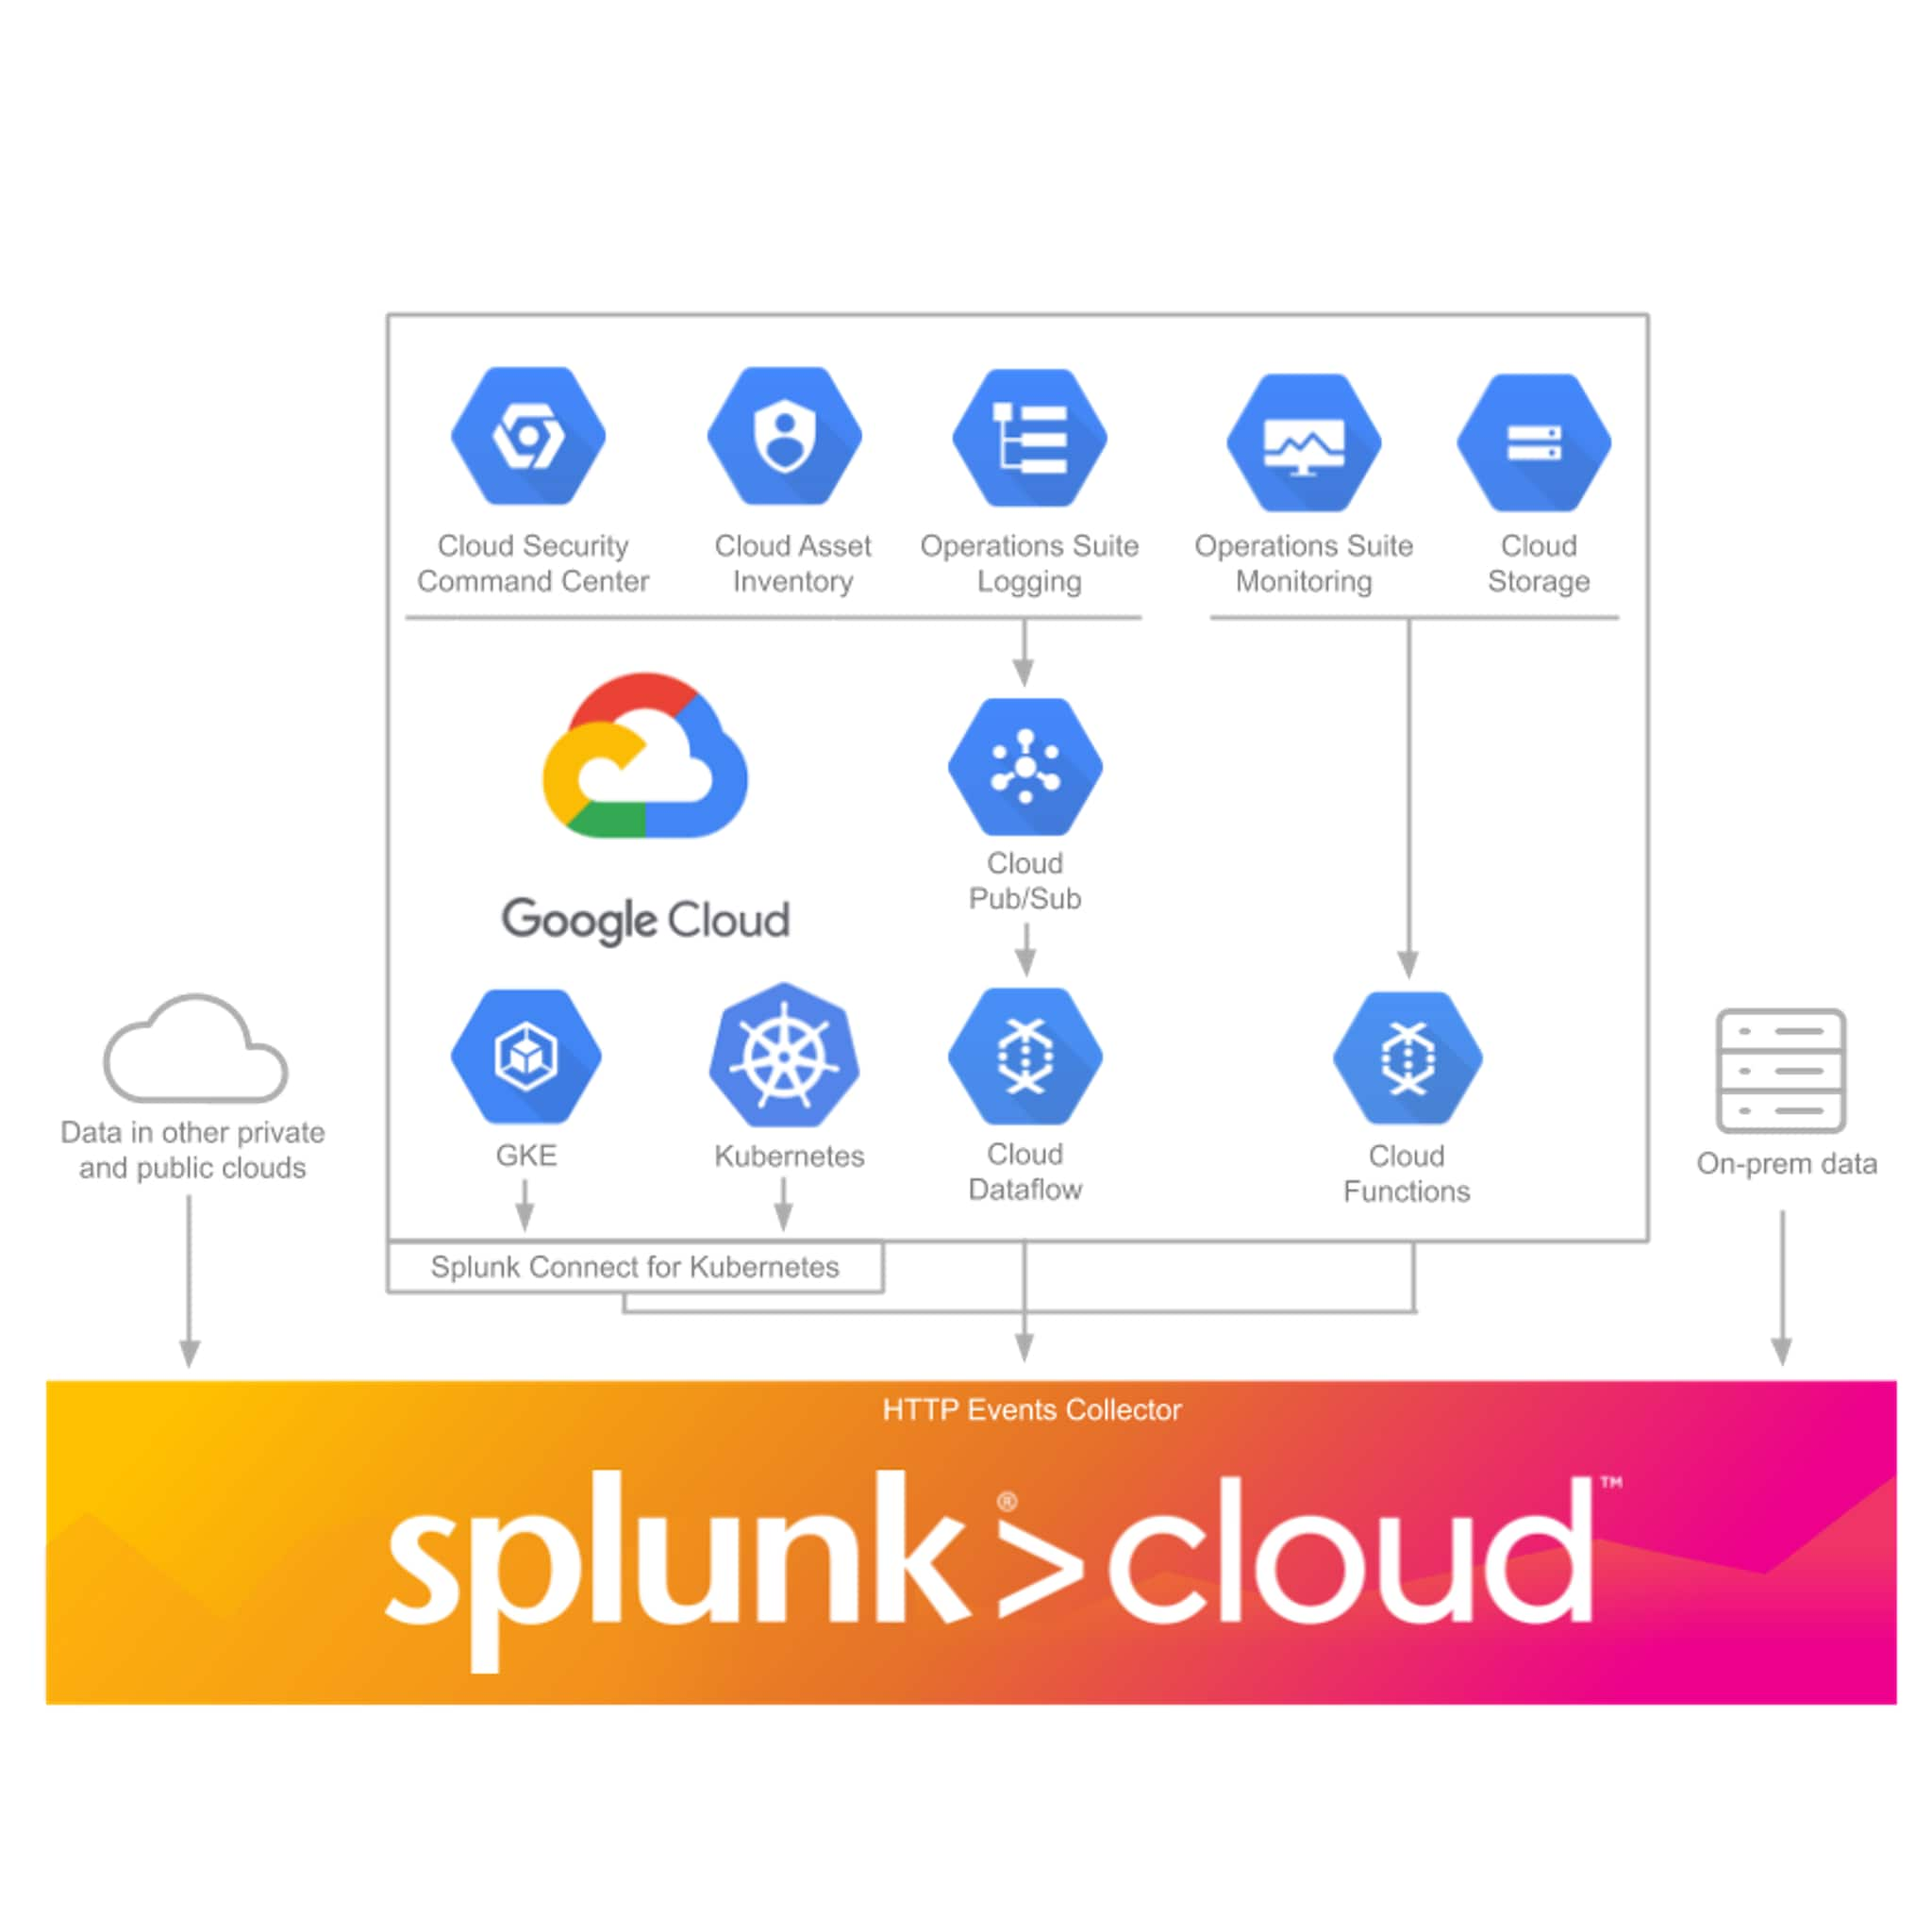
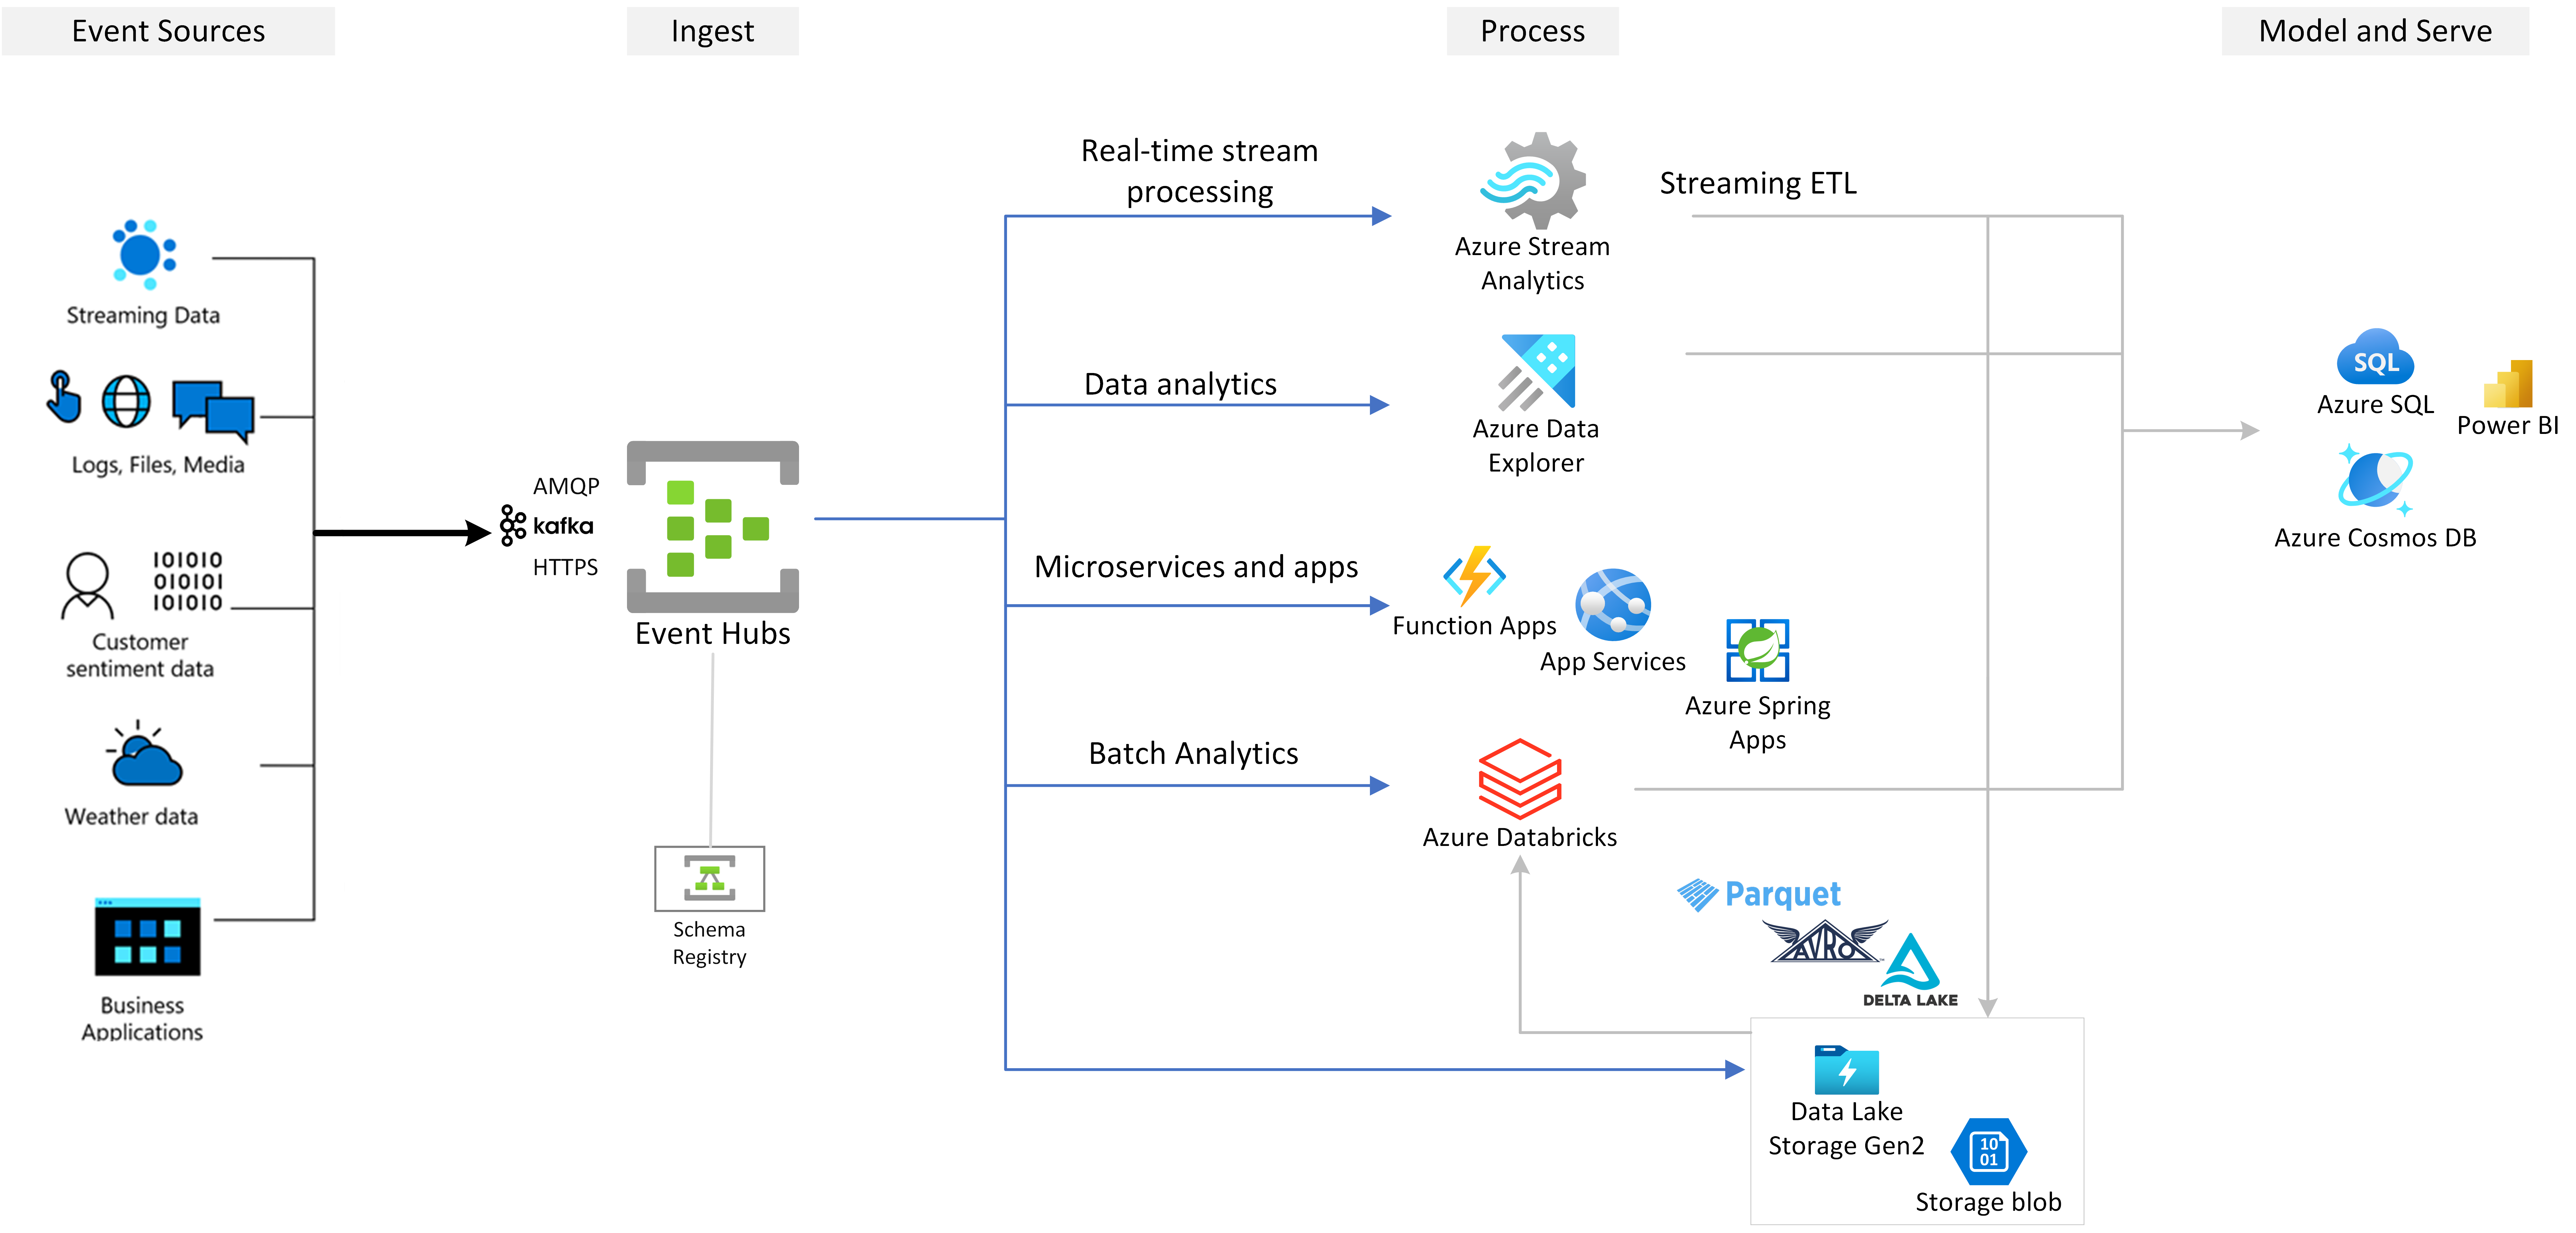
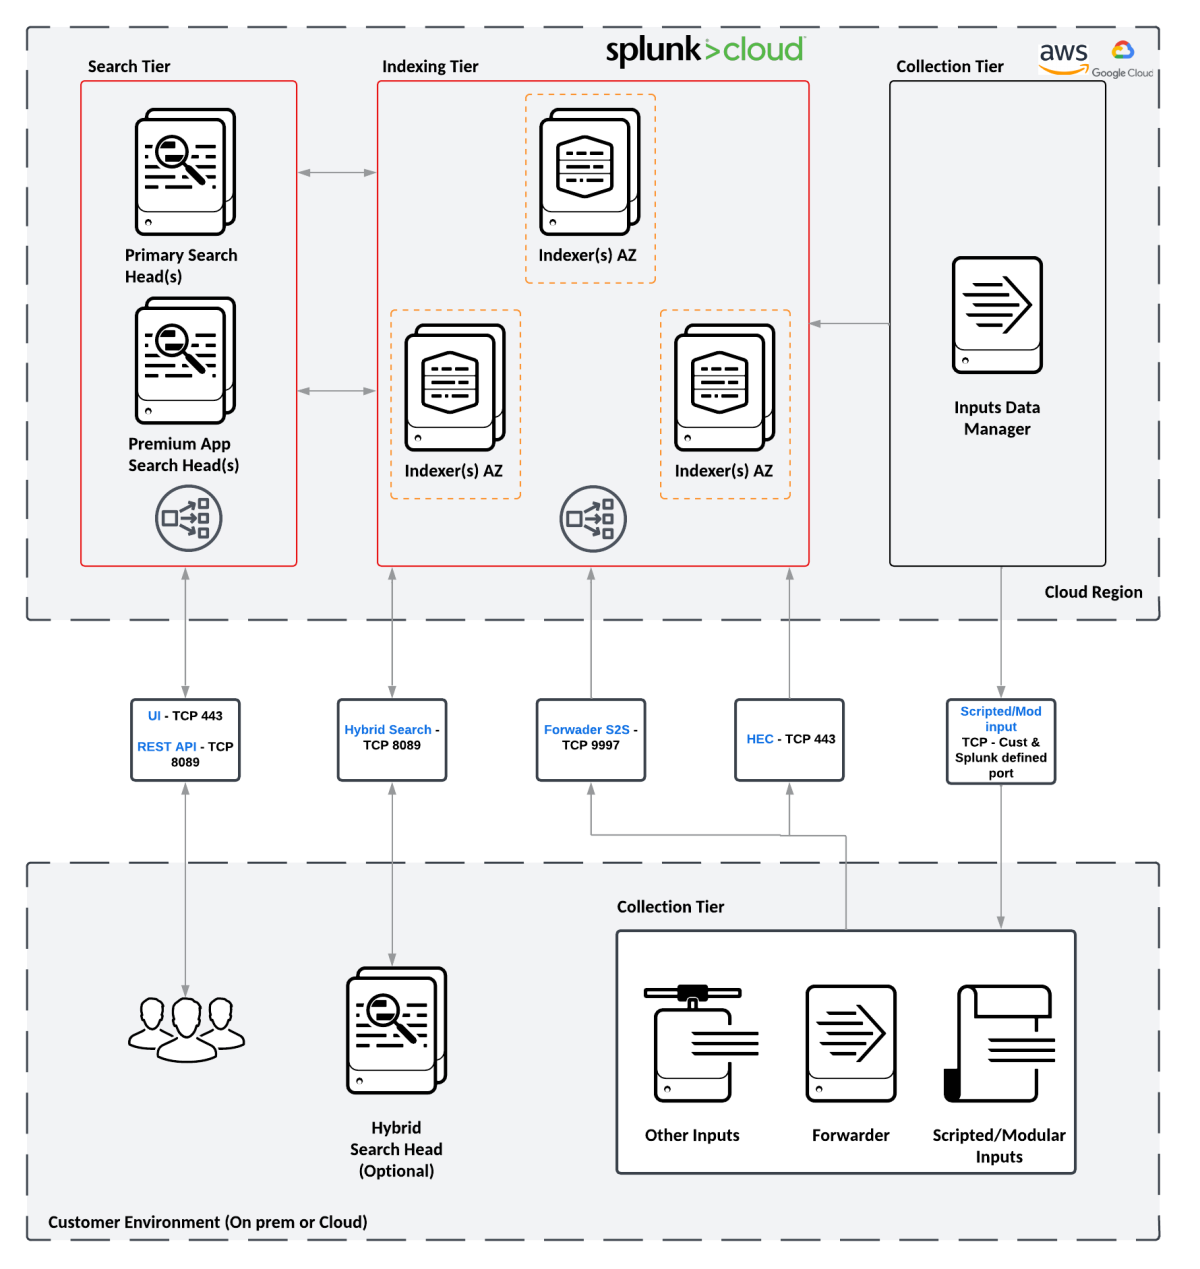
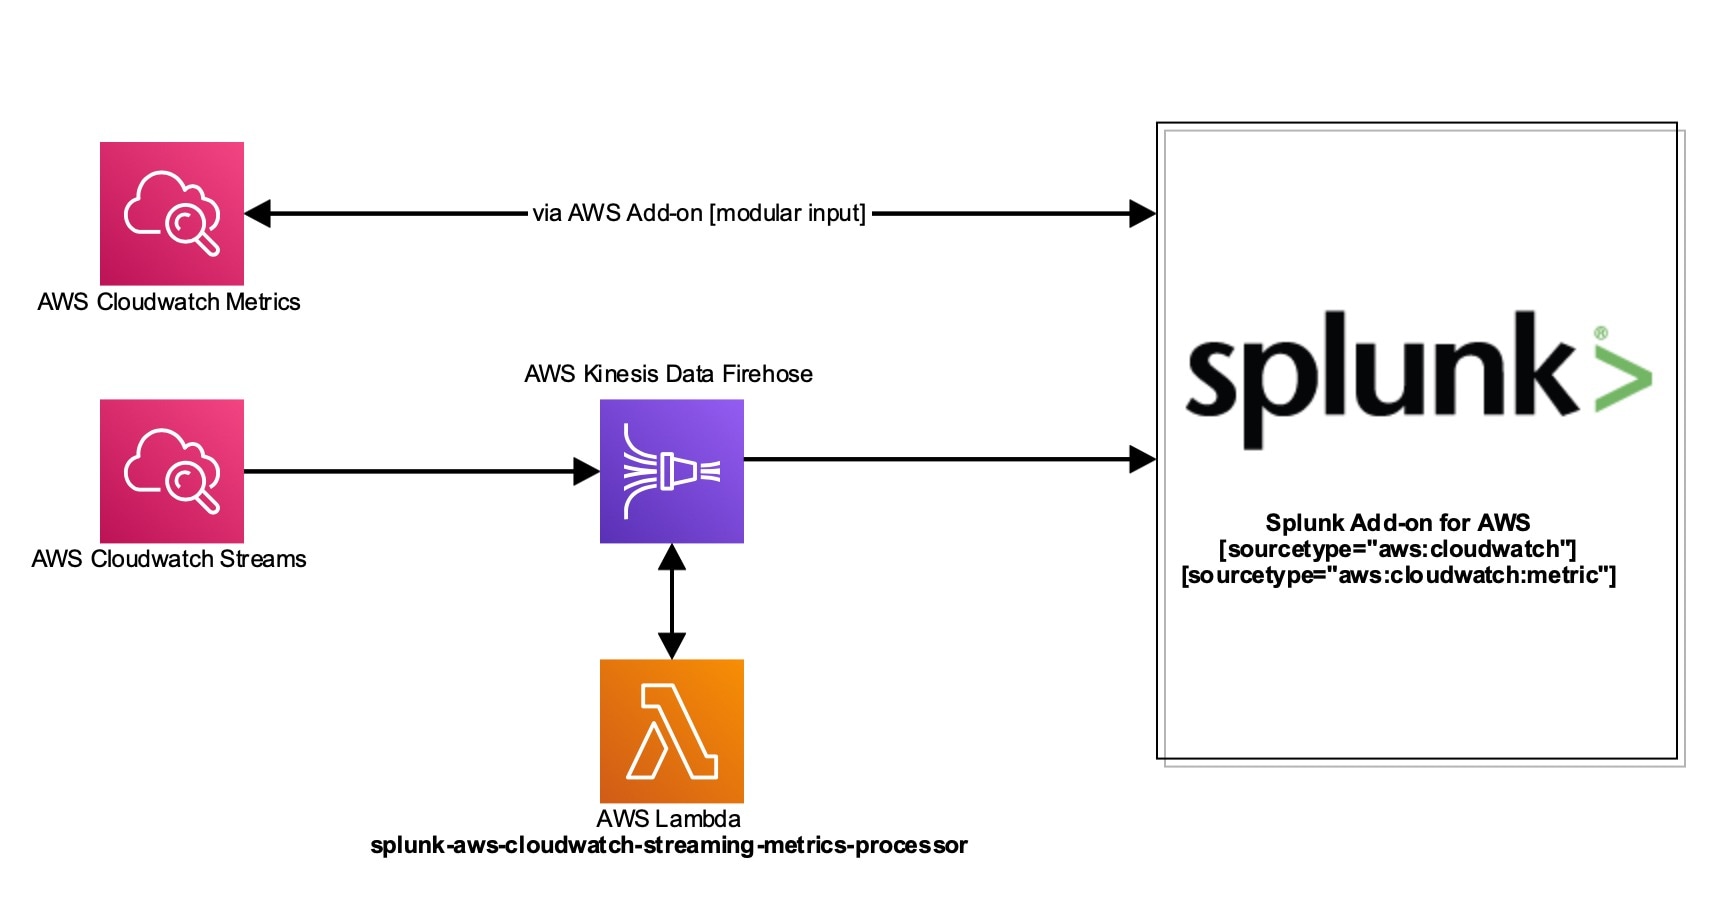
Splunking Azure: Event Hubs | Splunk
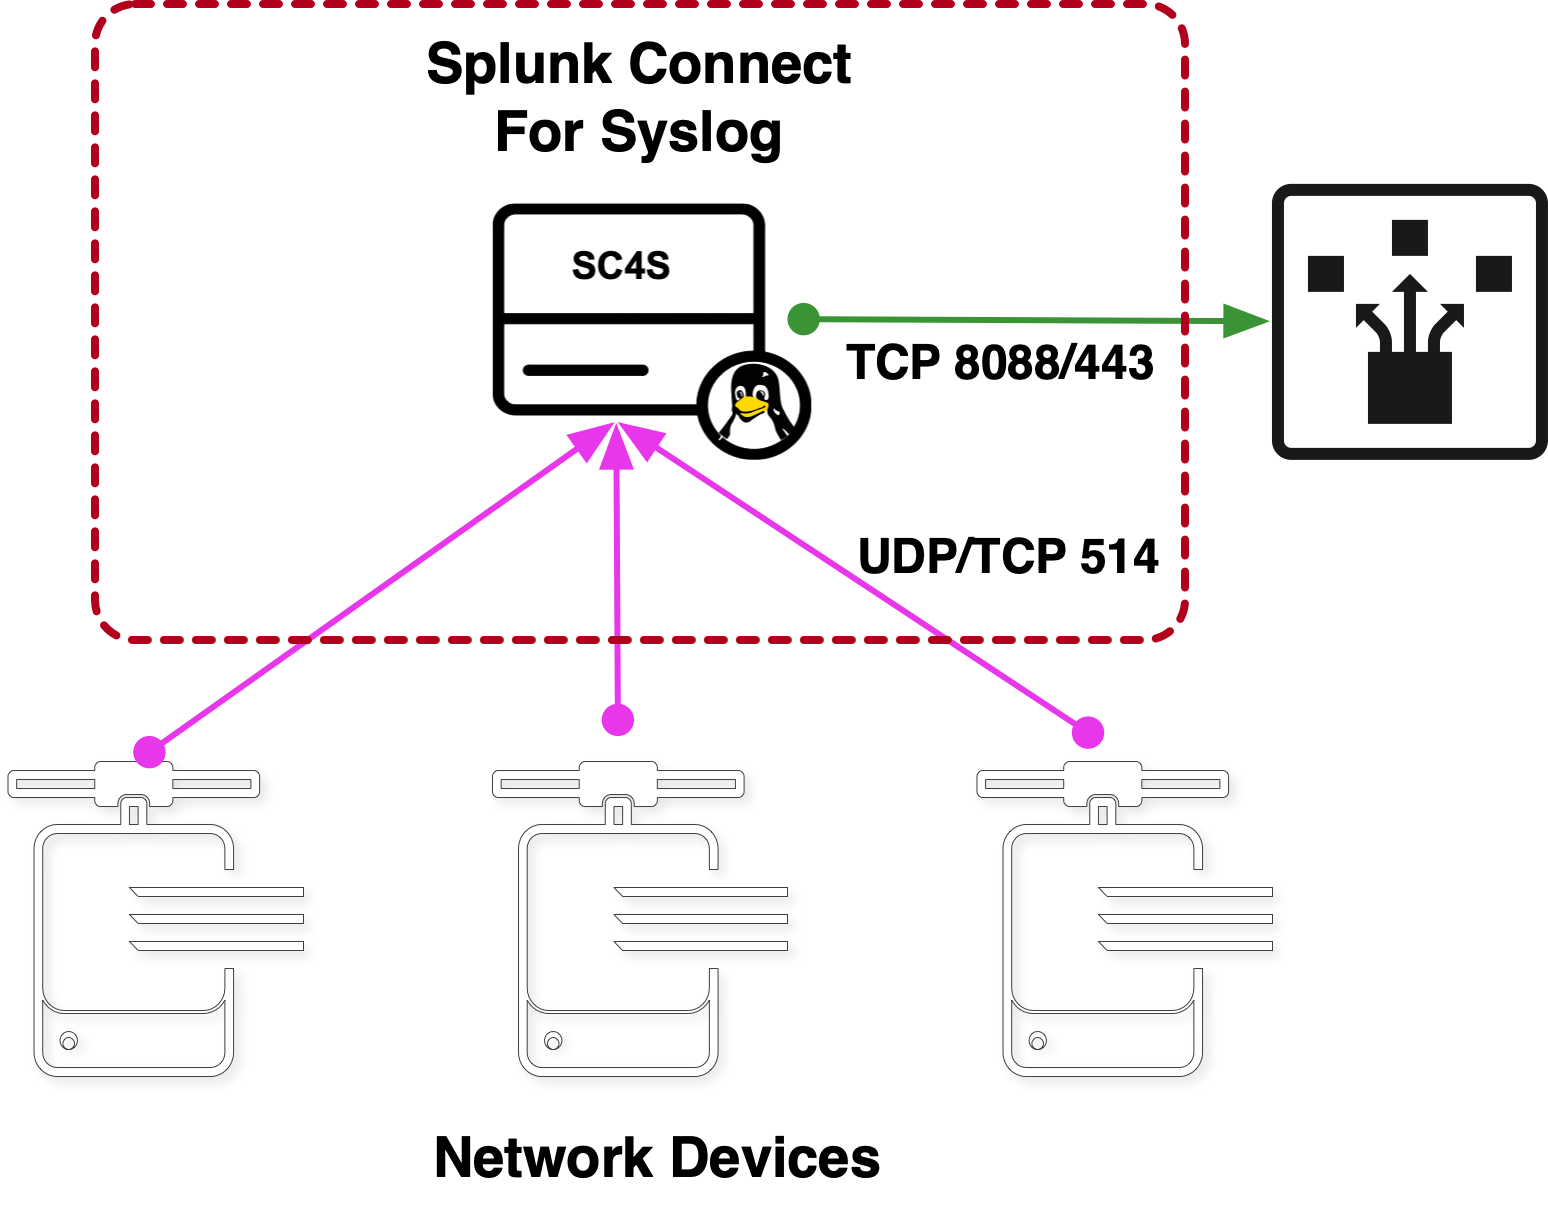
Splunk Connect Konfiguration , Splunking Azure: Event Hubs – WACX
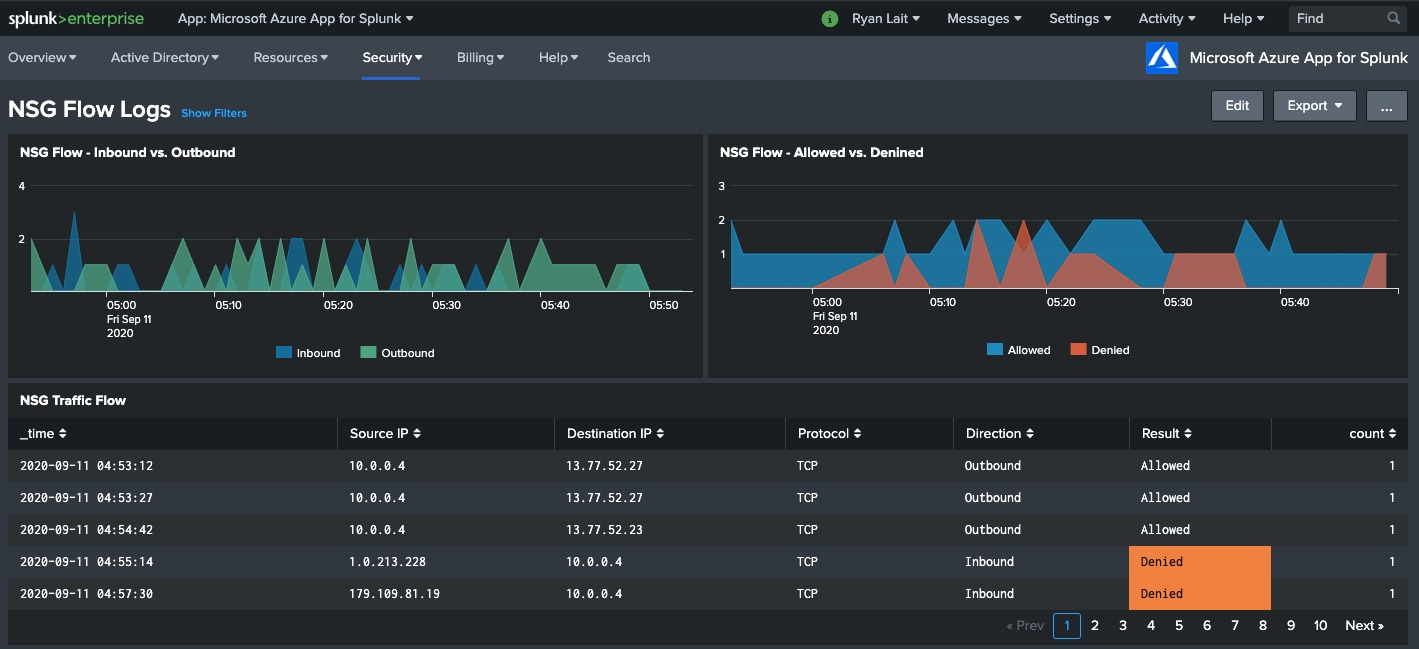
Splunking Azure: NSG Flow Logs | Splunk
Splunking Webhooks with the HTTP Event Collector | Splunk
Splunking Microsoft Azure Monitor Data – Part 2 – Splunk Setup | Splunk
Splunking Microsoft Azure Monitor Data – Part 1 – Azure Setup | Splunk
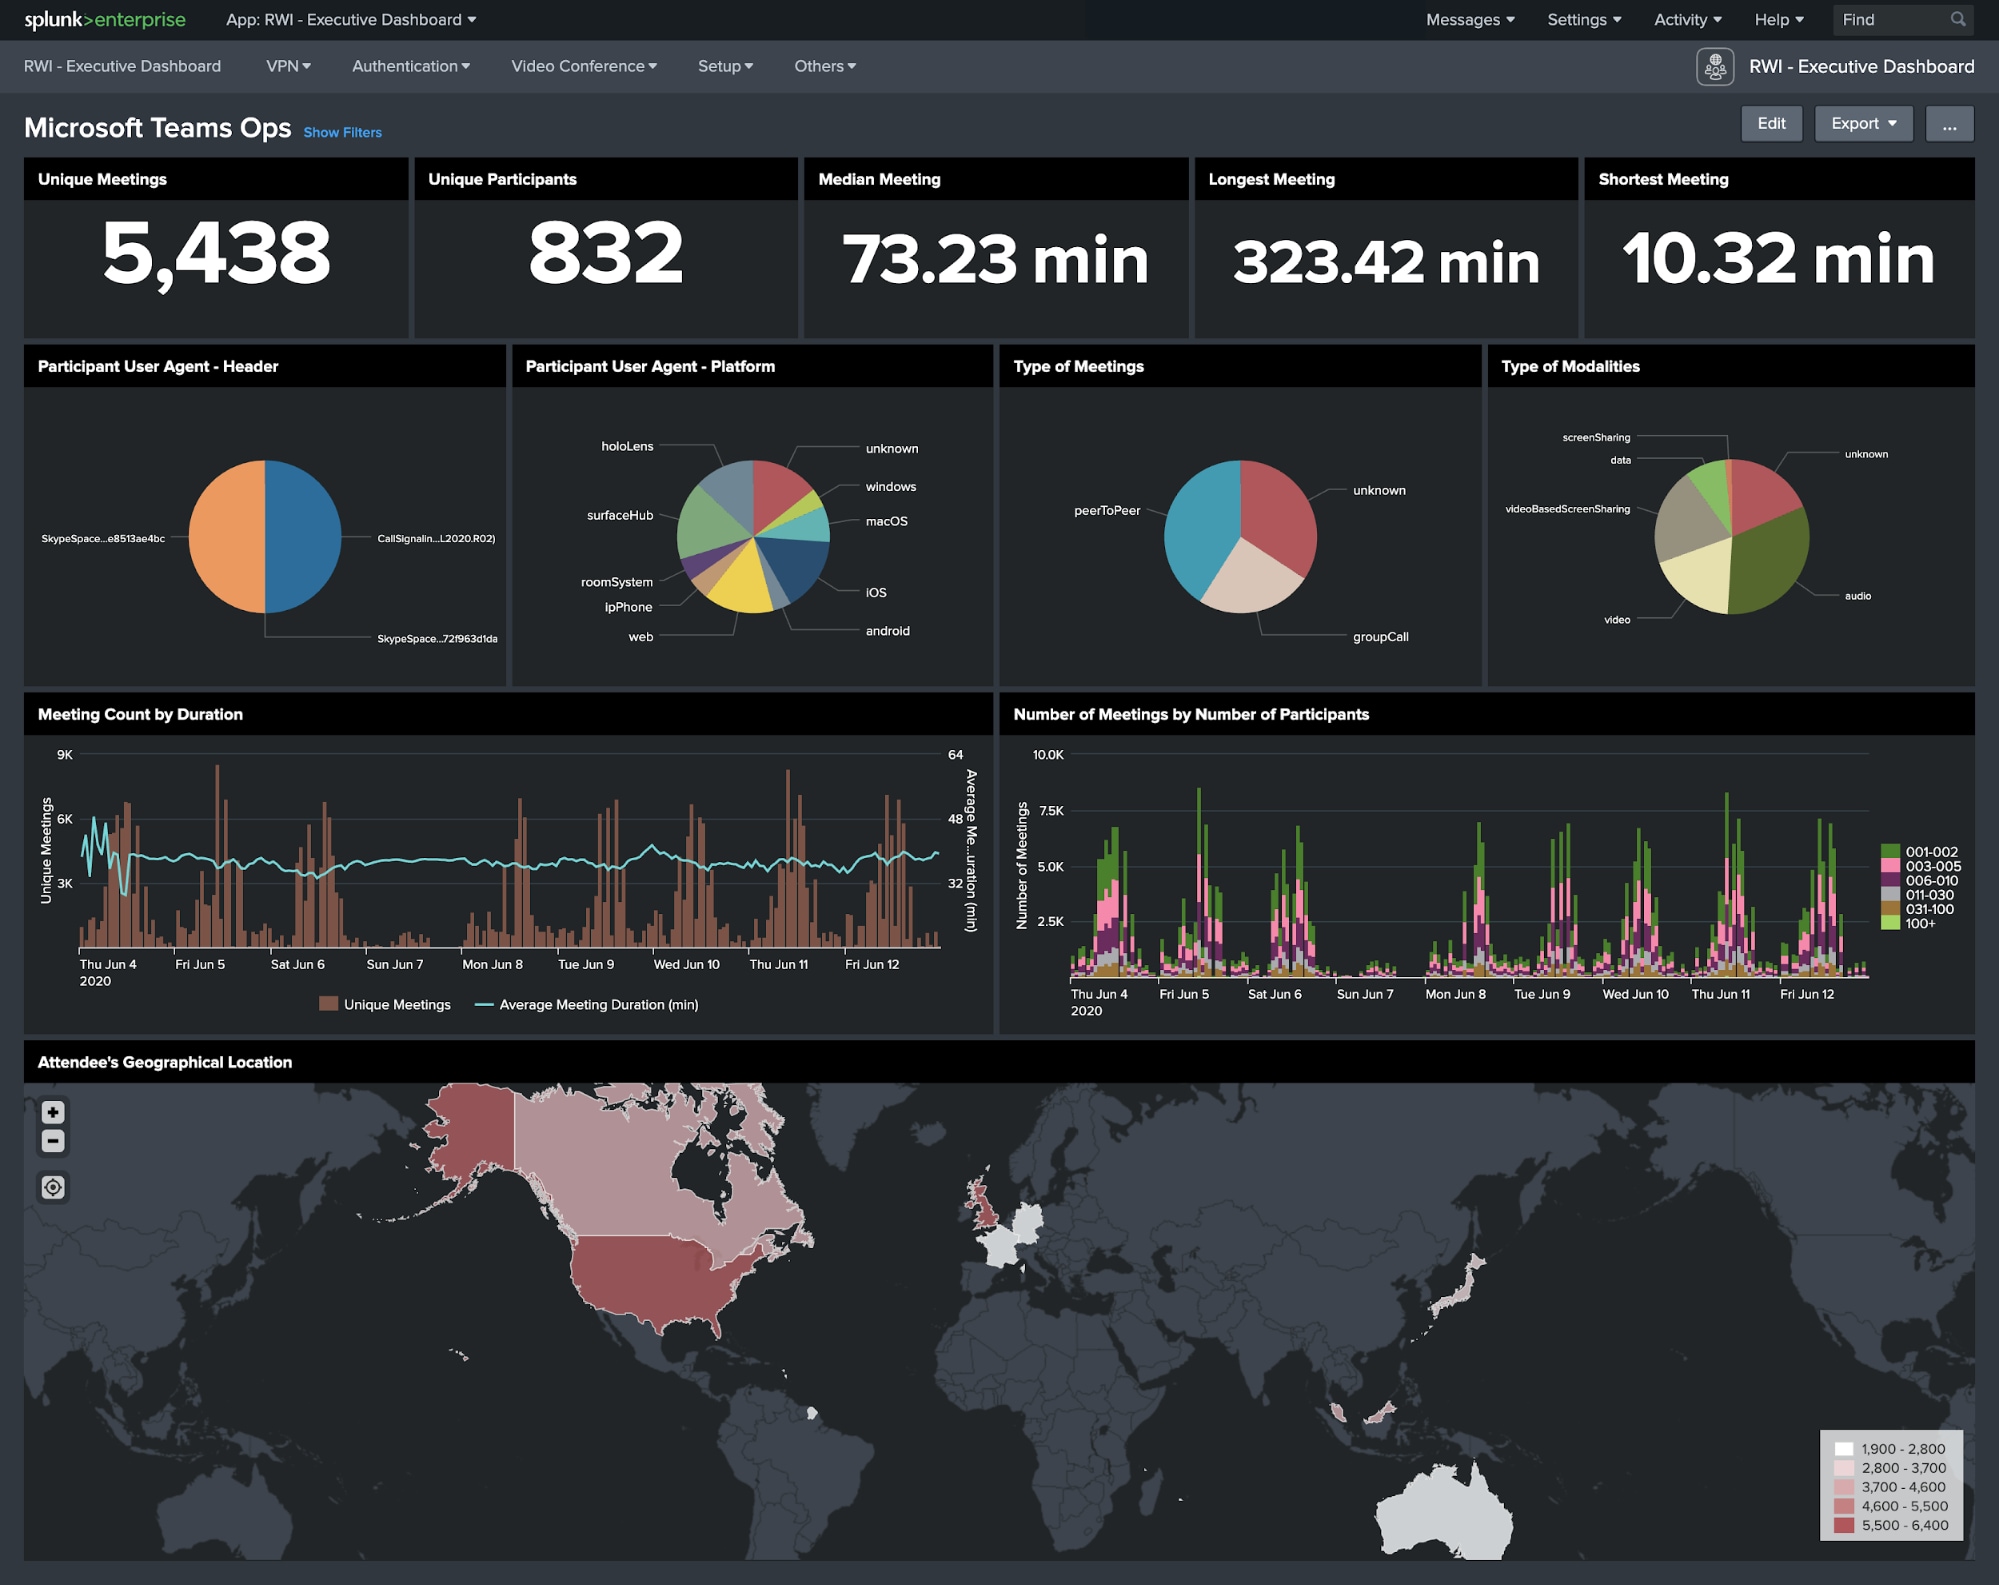
Splunking Microsoft Teams Data | Splunk
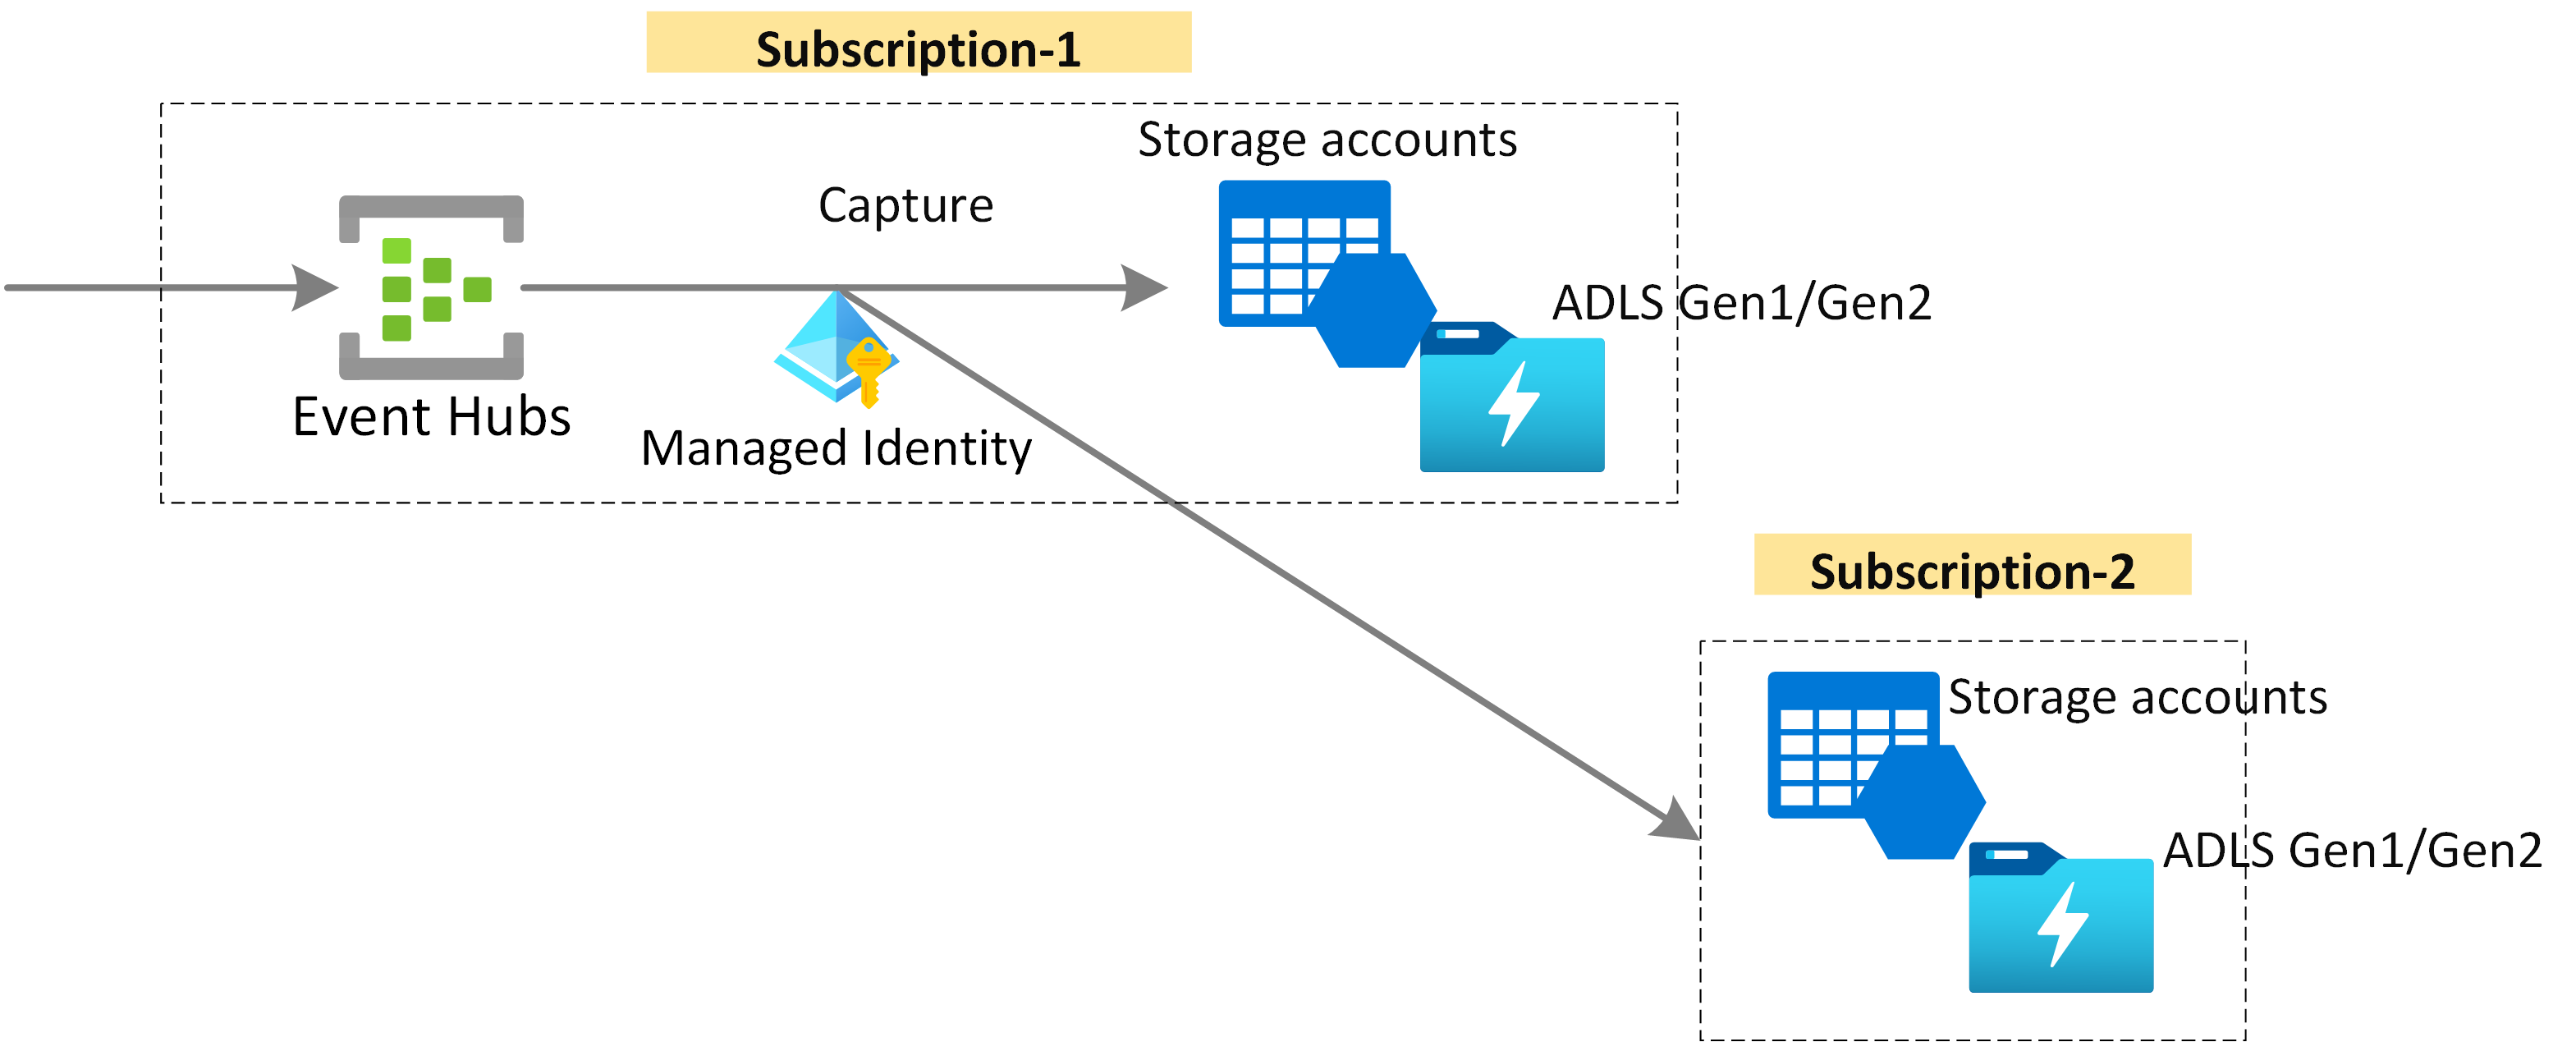
Use managed Identities to capture events - Azure Event Hubs | Microsoft ...
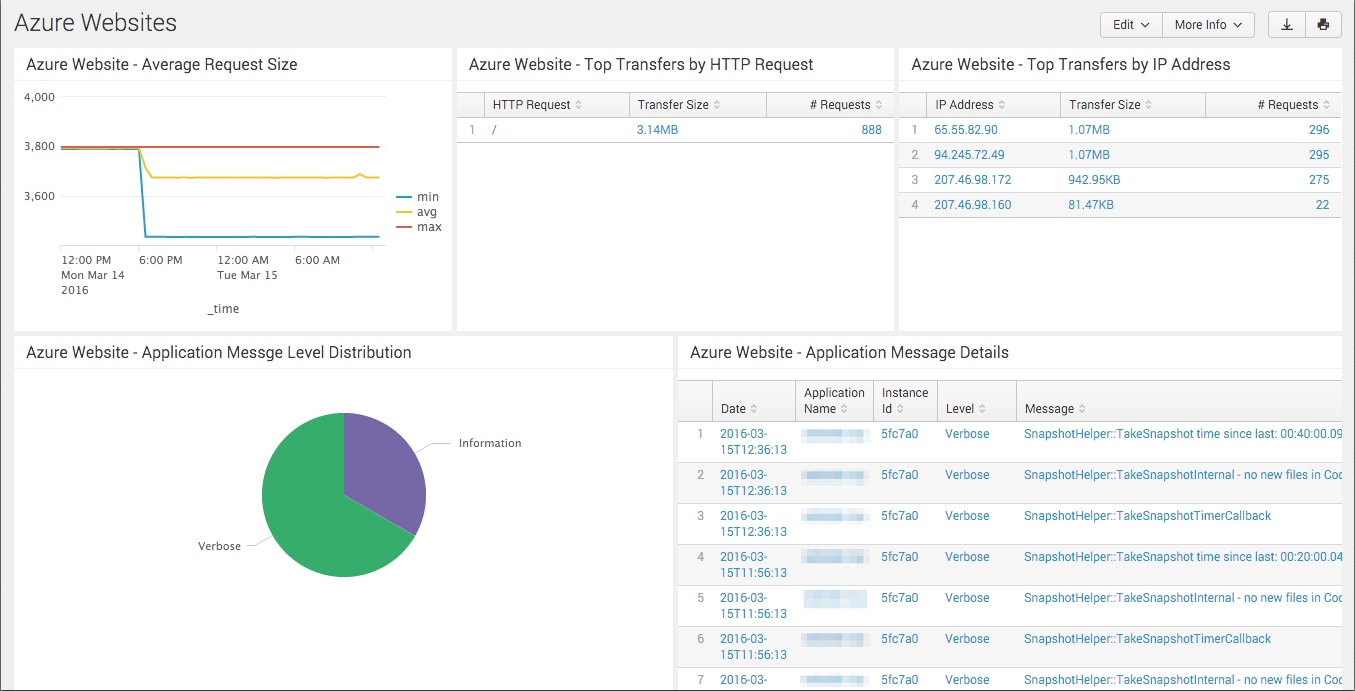
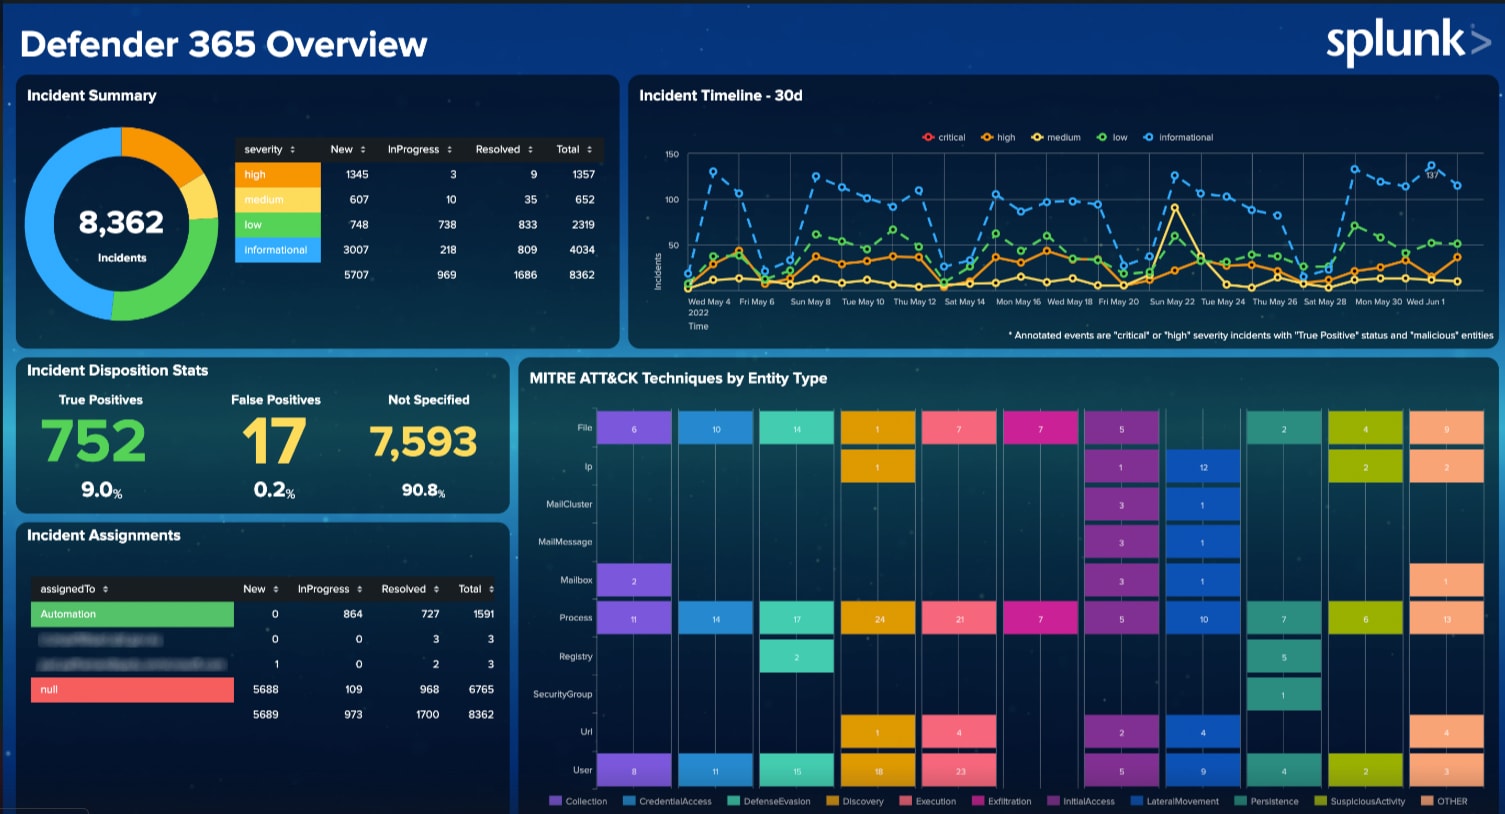
Splunking Microsoft Azure Data | Splunk
Splunking Microsoft Cloud Data: Part 1 | Splunk
New Splunk Tools for .NET Developers | Splunk
Splunk in 60 Minutes | Splunk Tutorial For Beginners | Splunk Training ...
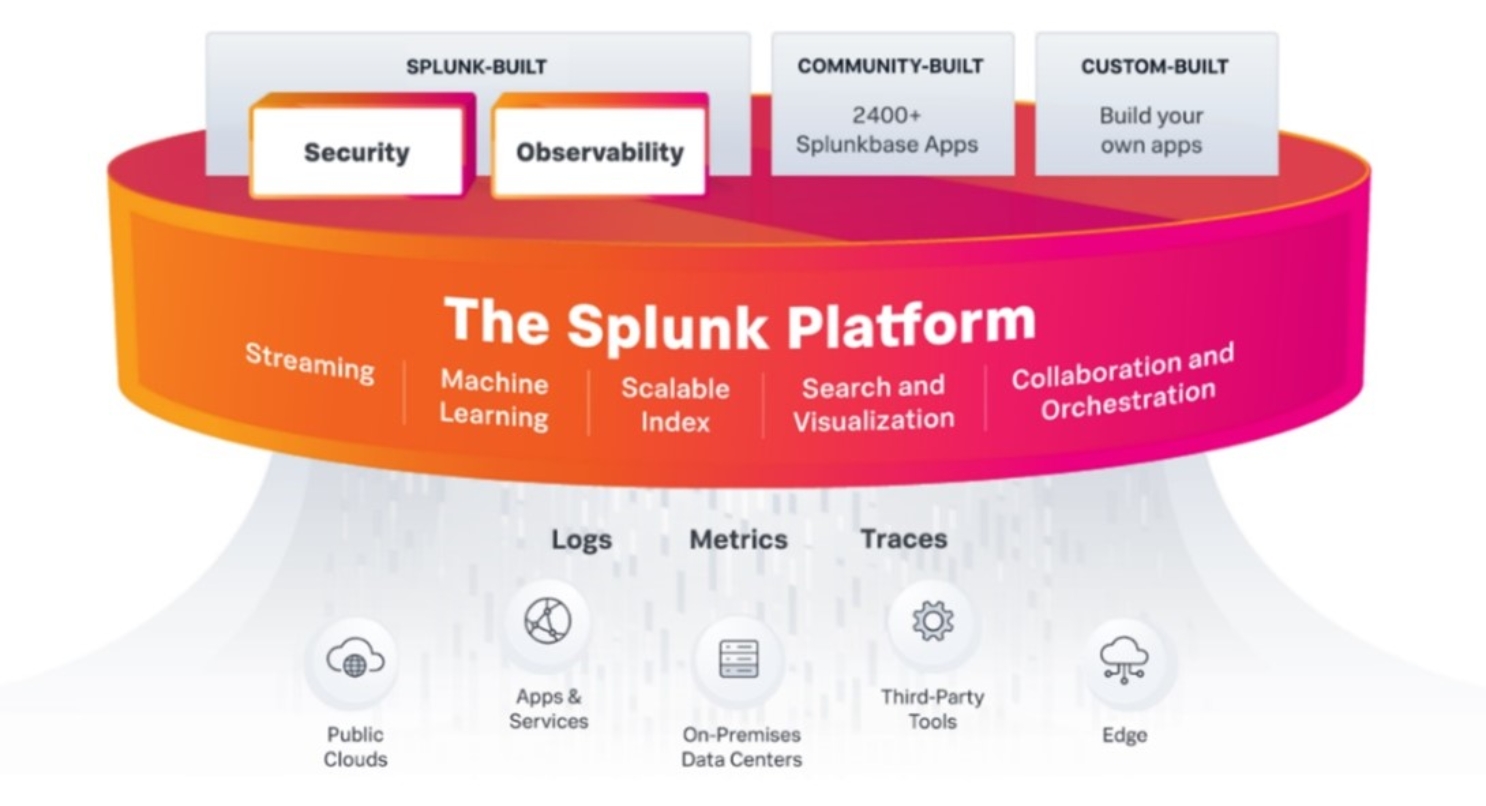
Splunk 제품 | Splunk
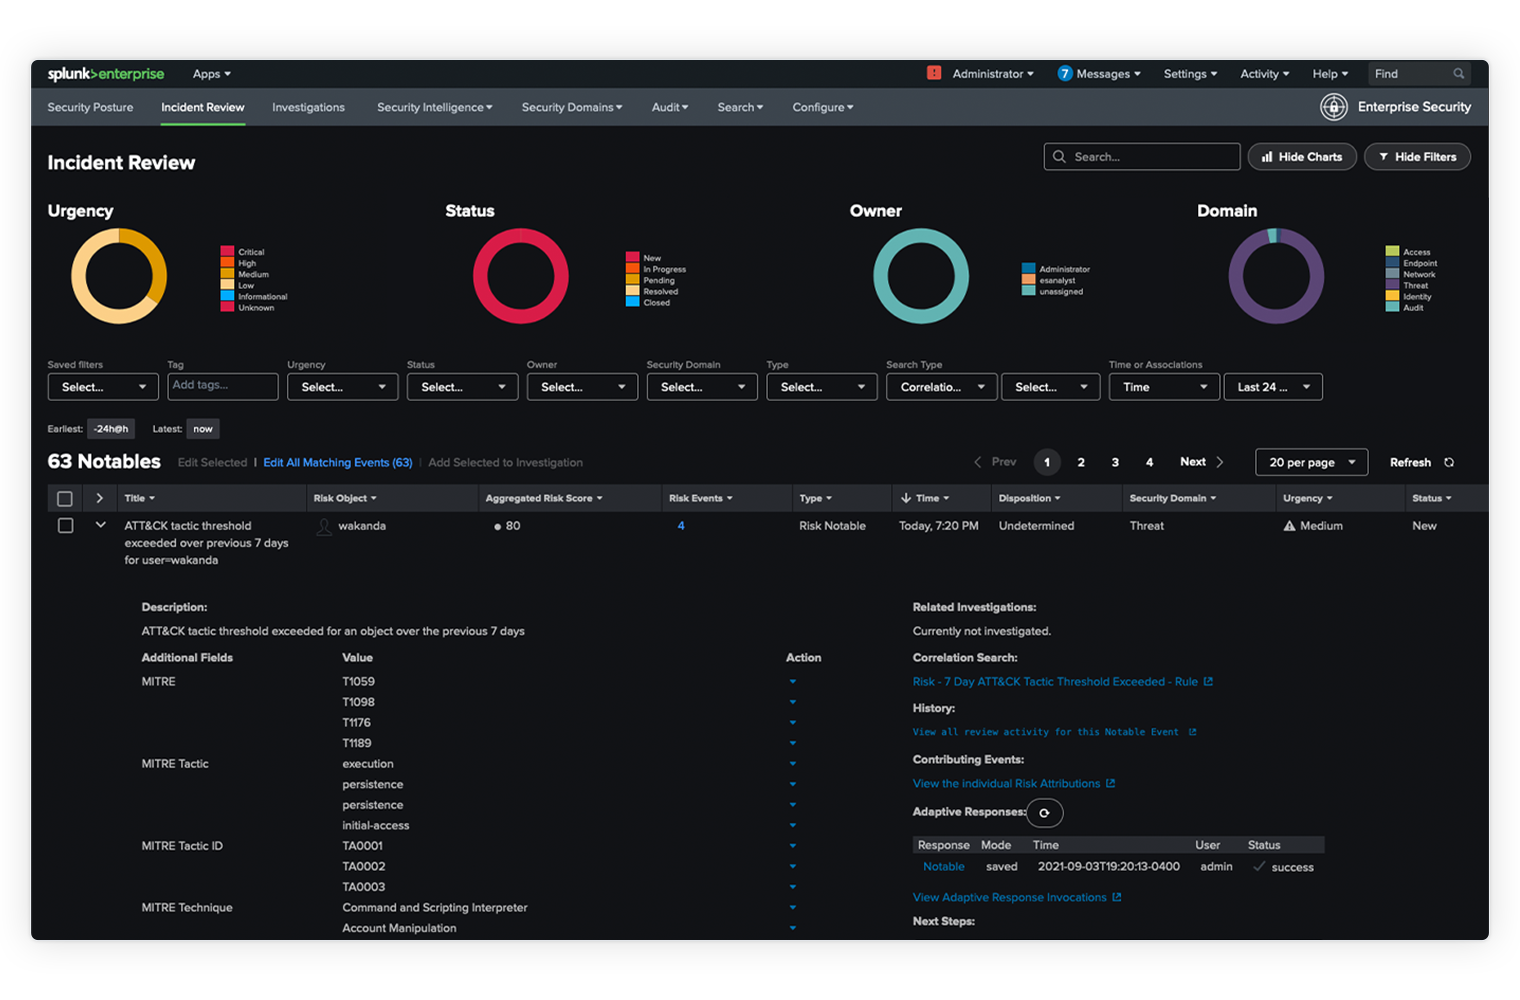
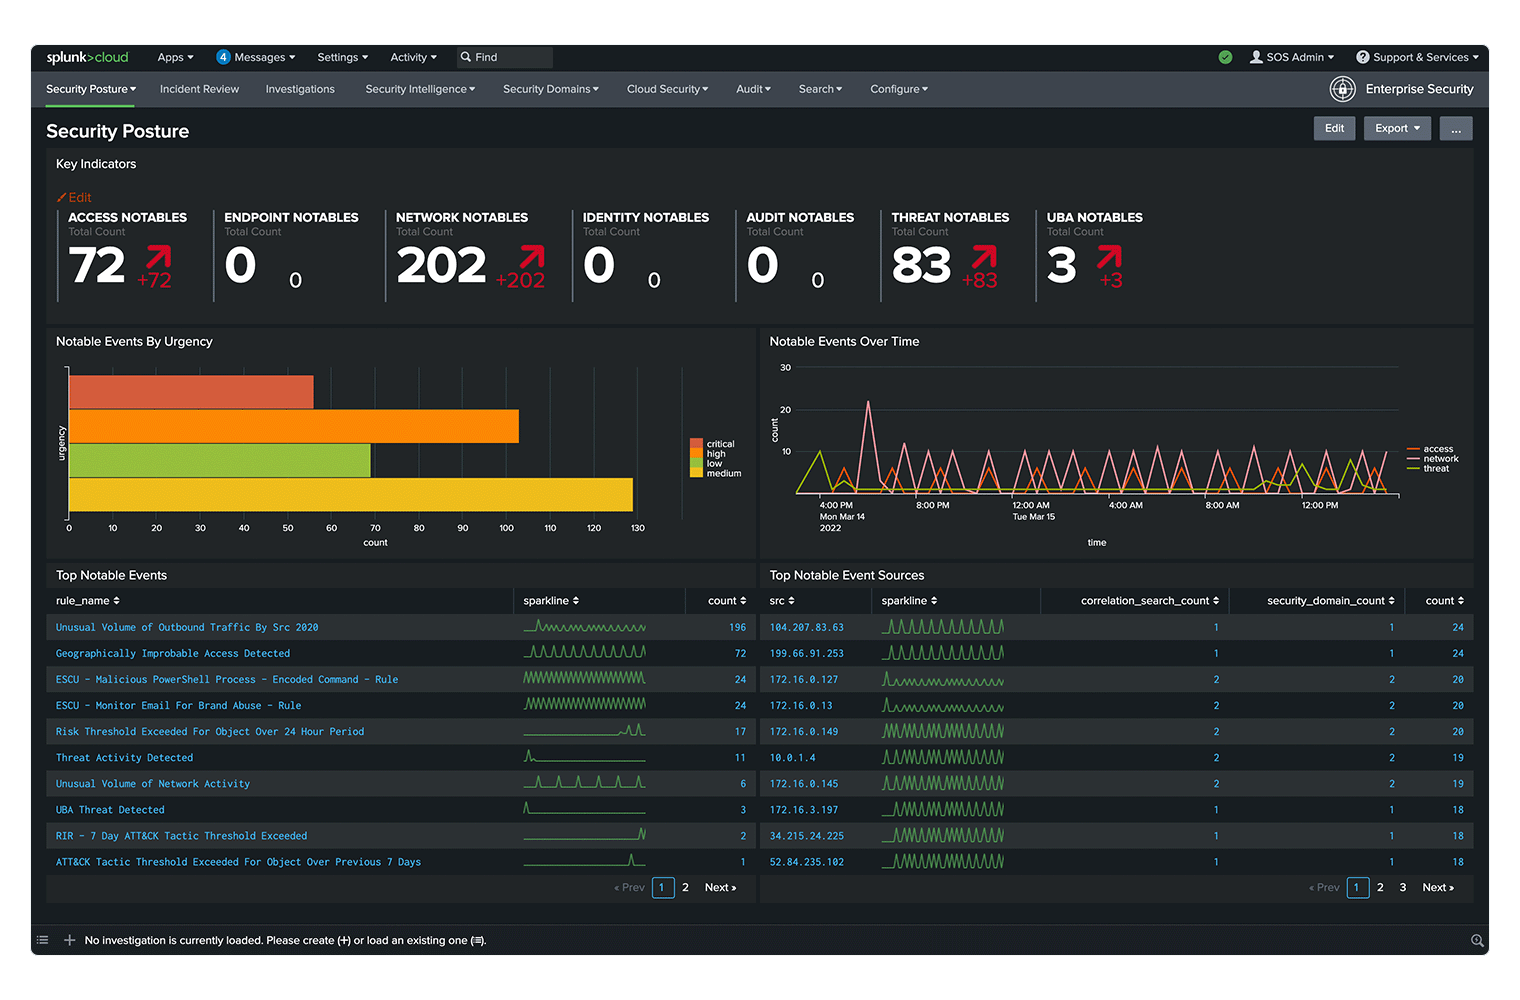
What Is A Notable Event In Splunk
Security Software & Solutions | Splunk
SPLのコマンドタイプを学ぶ~効率的なサーチの実行順序とその調査方法~ | Splunk
Event Hubs Multiple Consumers at Jacob Lutz blog
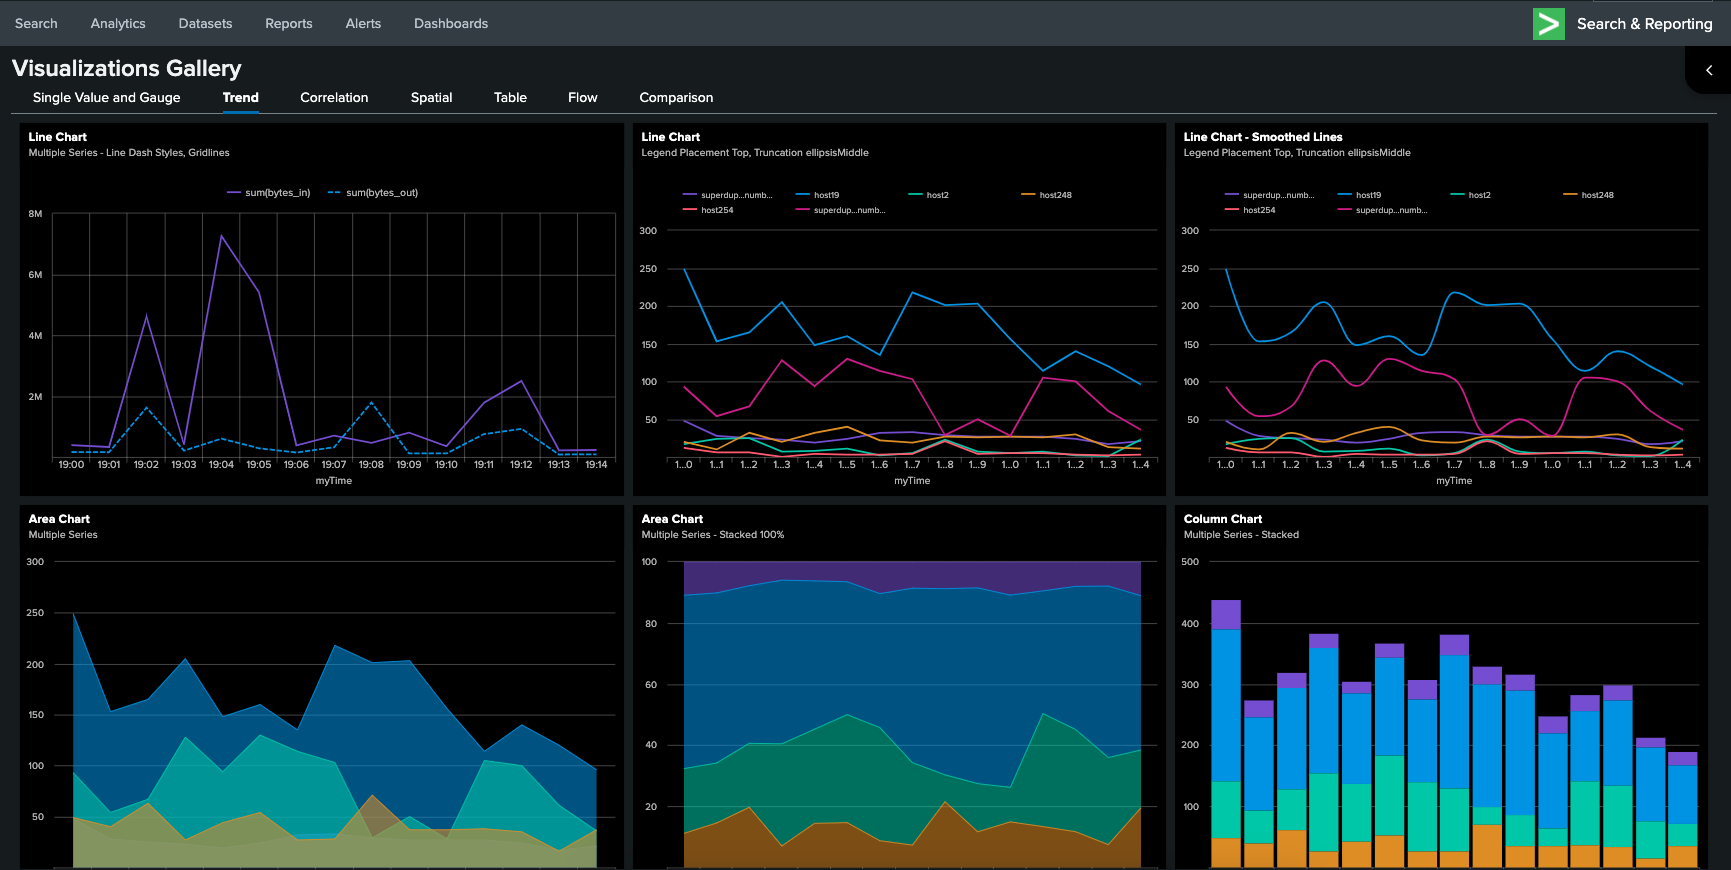
Dashboard Studio: Tabbed Dashboards | Splunk
脆弱性、脅威、リスクの基本 | Splunk
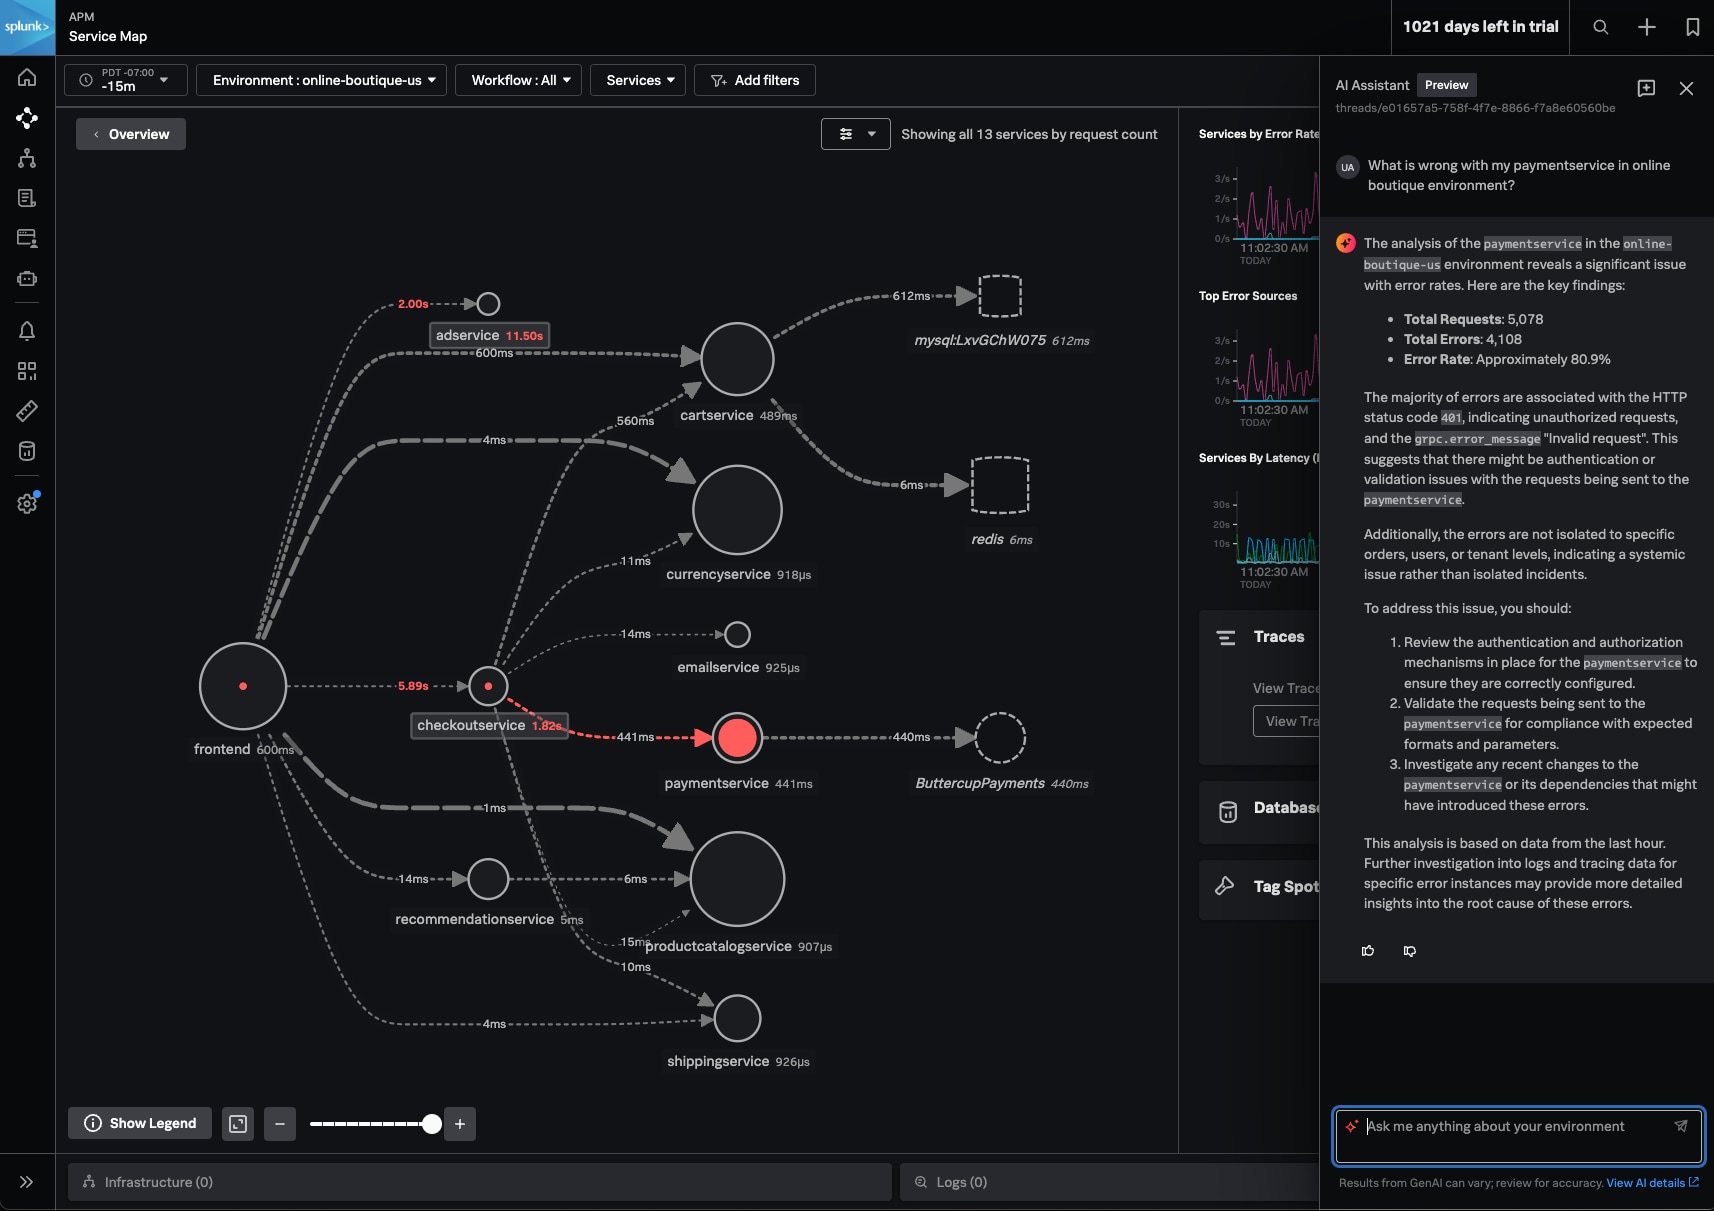
OpenTelemetry、自動インストルメンテーション、Splunk Observability Cloudの活用促進 | Splunk
データプラットフォームとは? | Splunk
Hunting M365 Invaders: Dissecting Email Collection Techniques | Splunk
An easy way to generate sample data | Splunk
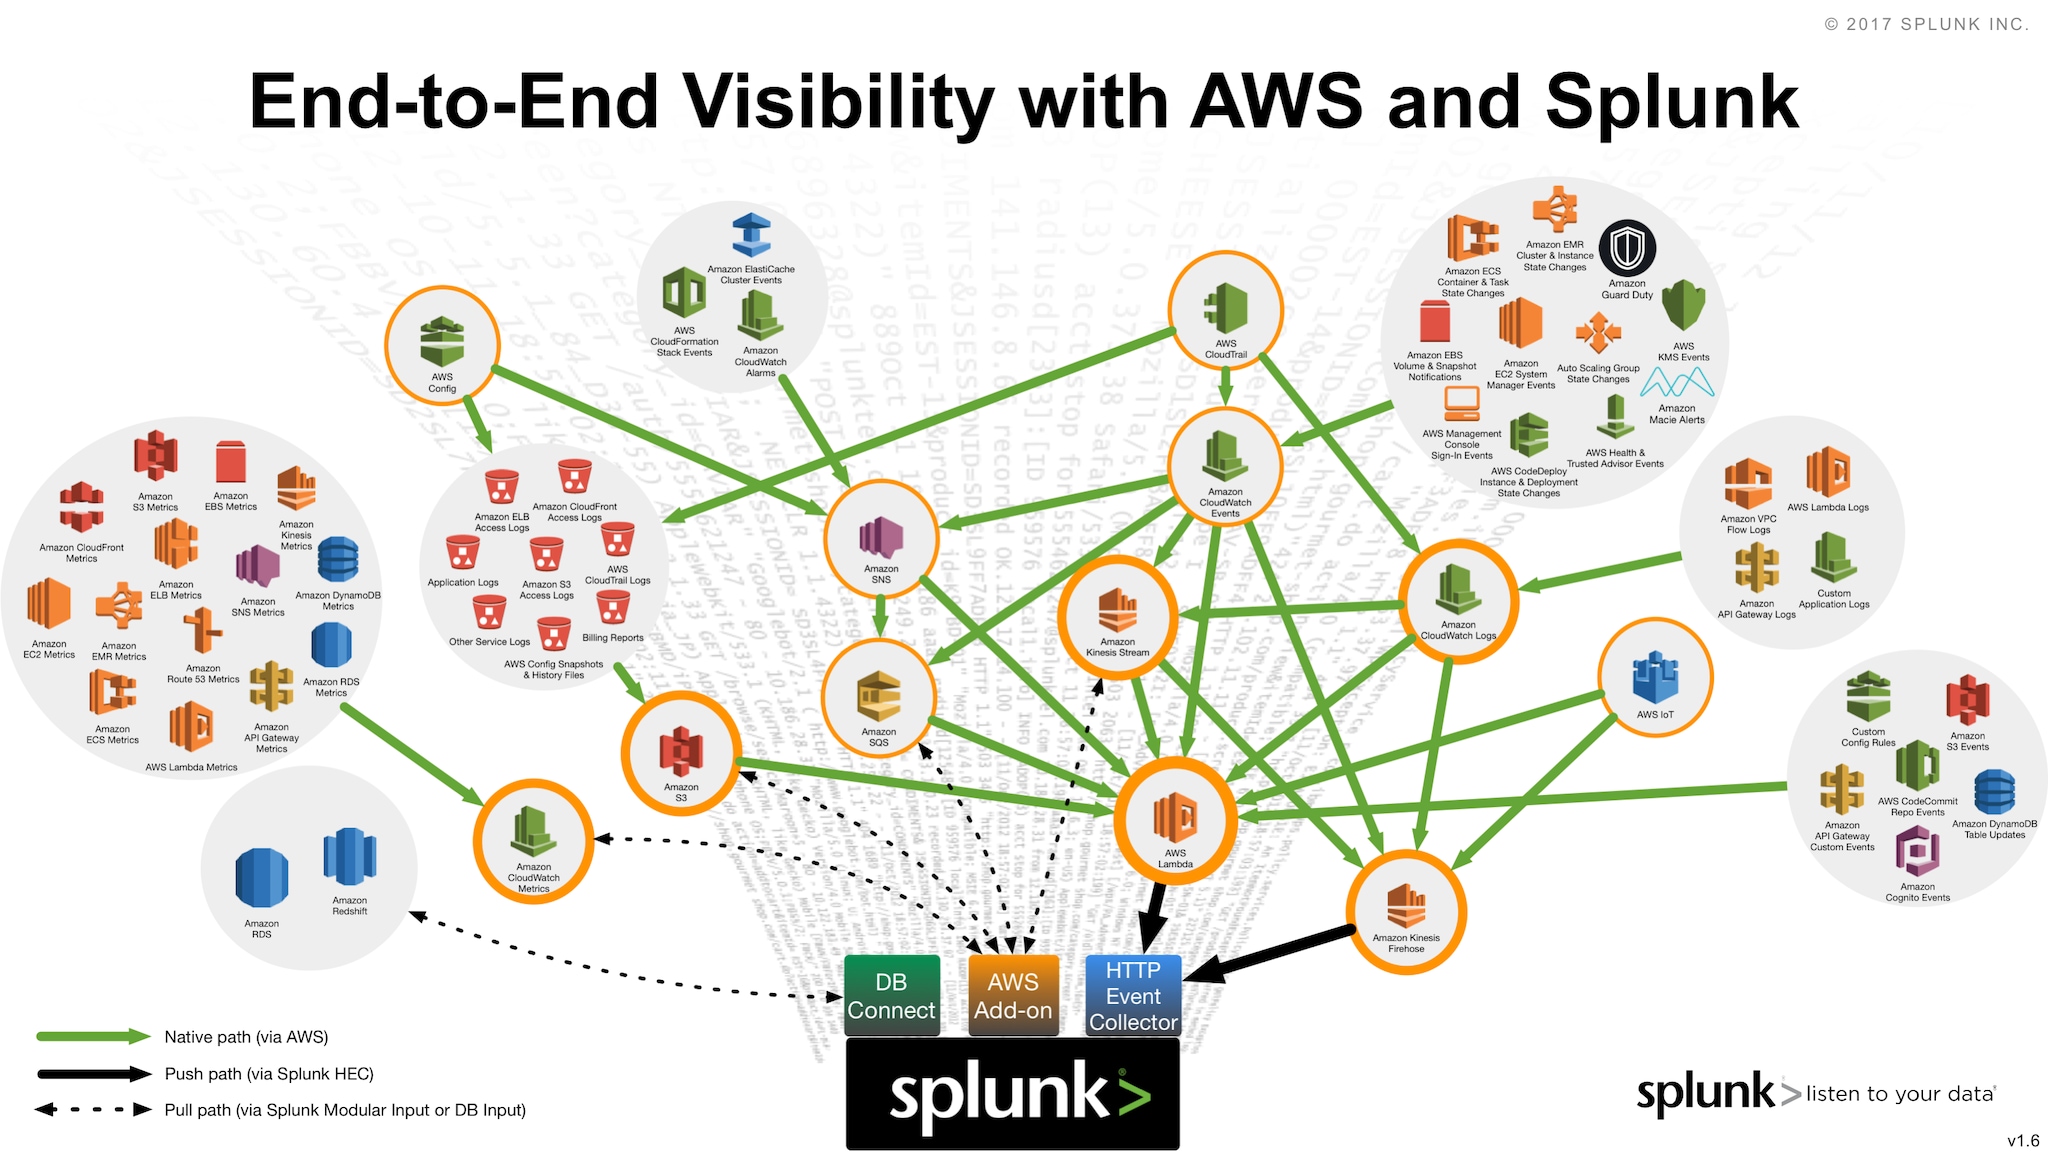
Splunking NetFlow with Splunk Stream - Part 1: Getting NetFlow data ...
Splunk Observability Cloud | Splunk
Setting Up the New Microsoft Teams Add-on for Splunk | Splunk
Splunk integration - Vulnerability intelligence for SIEM | Tenable®
Splunk Blogs | Splunk
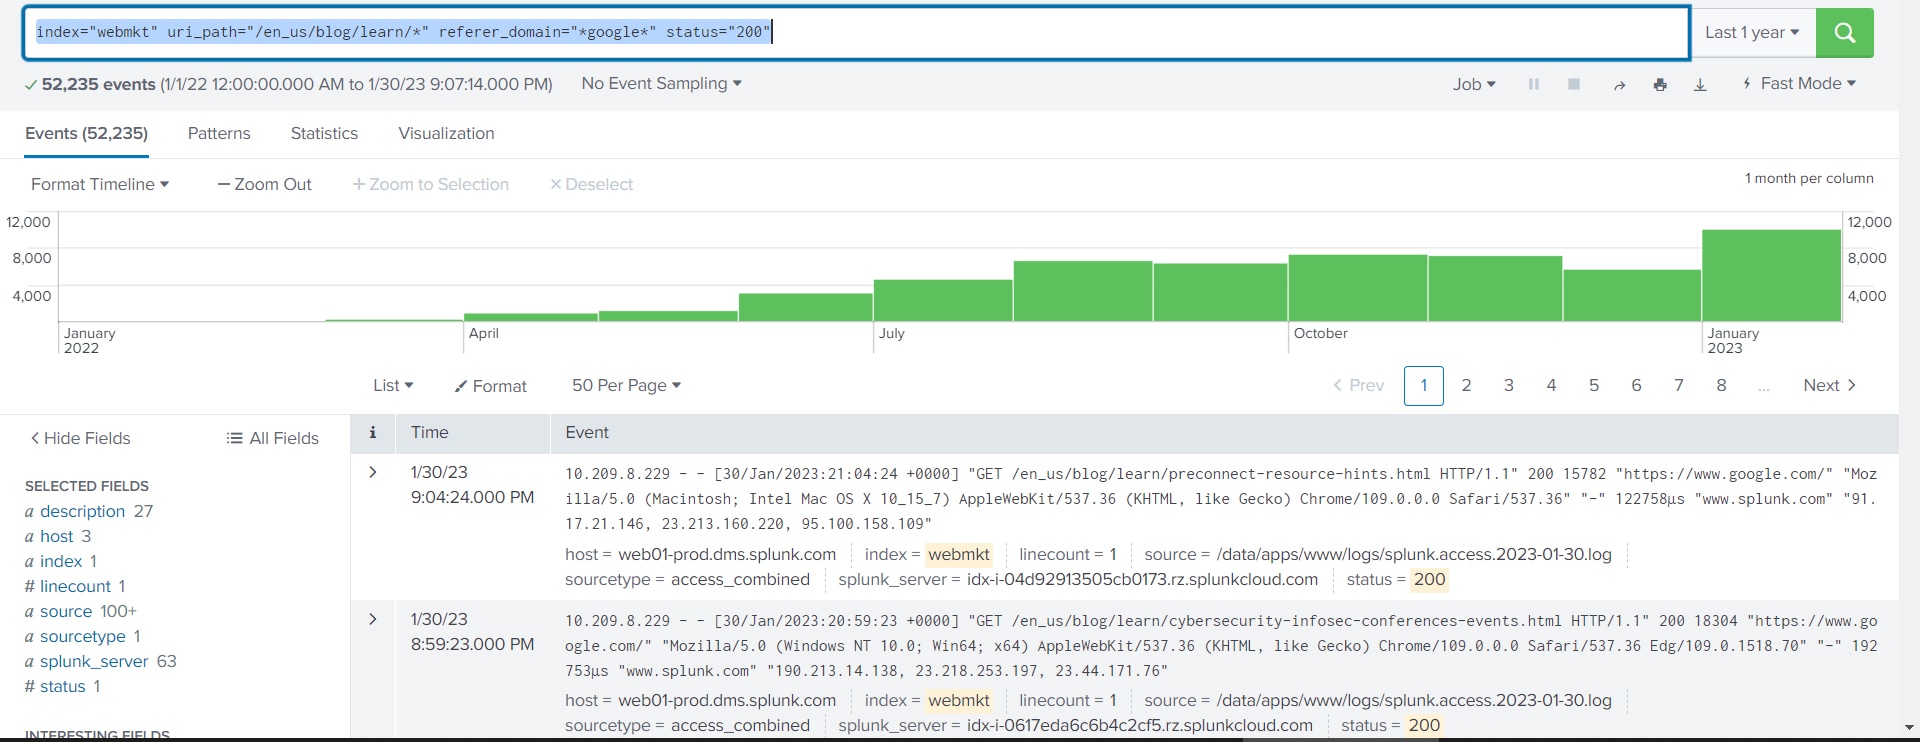
Splunk Search Interface. Splunk has its own Query language… | by Anvesh ...
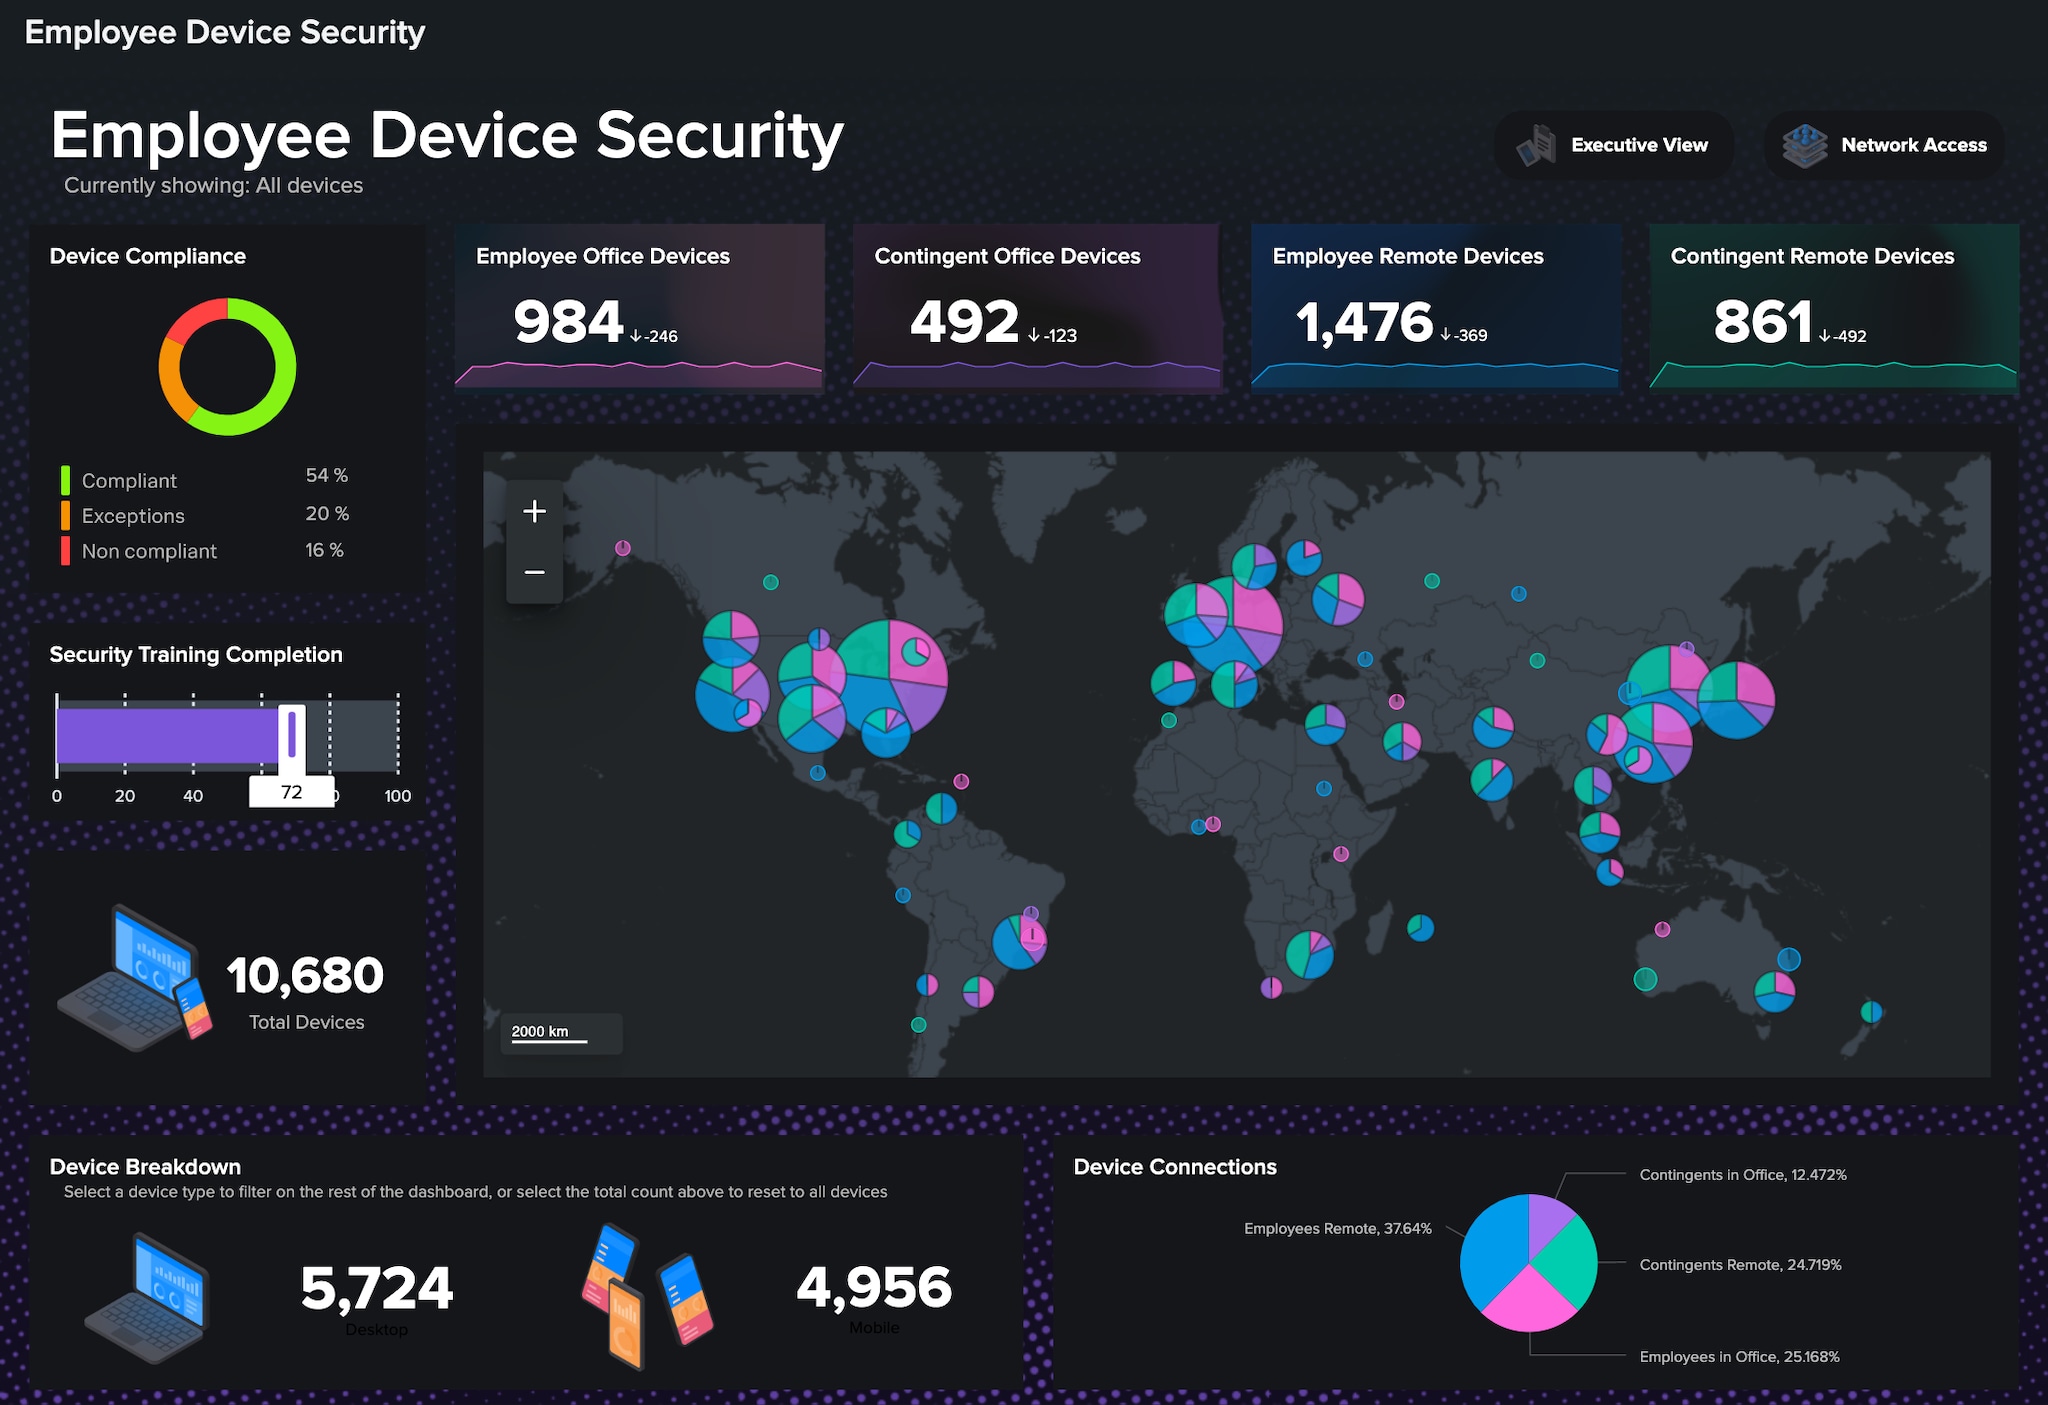
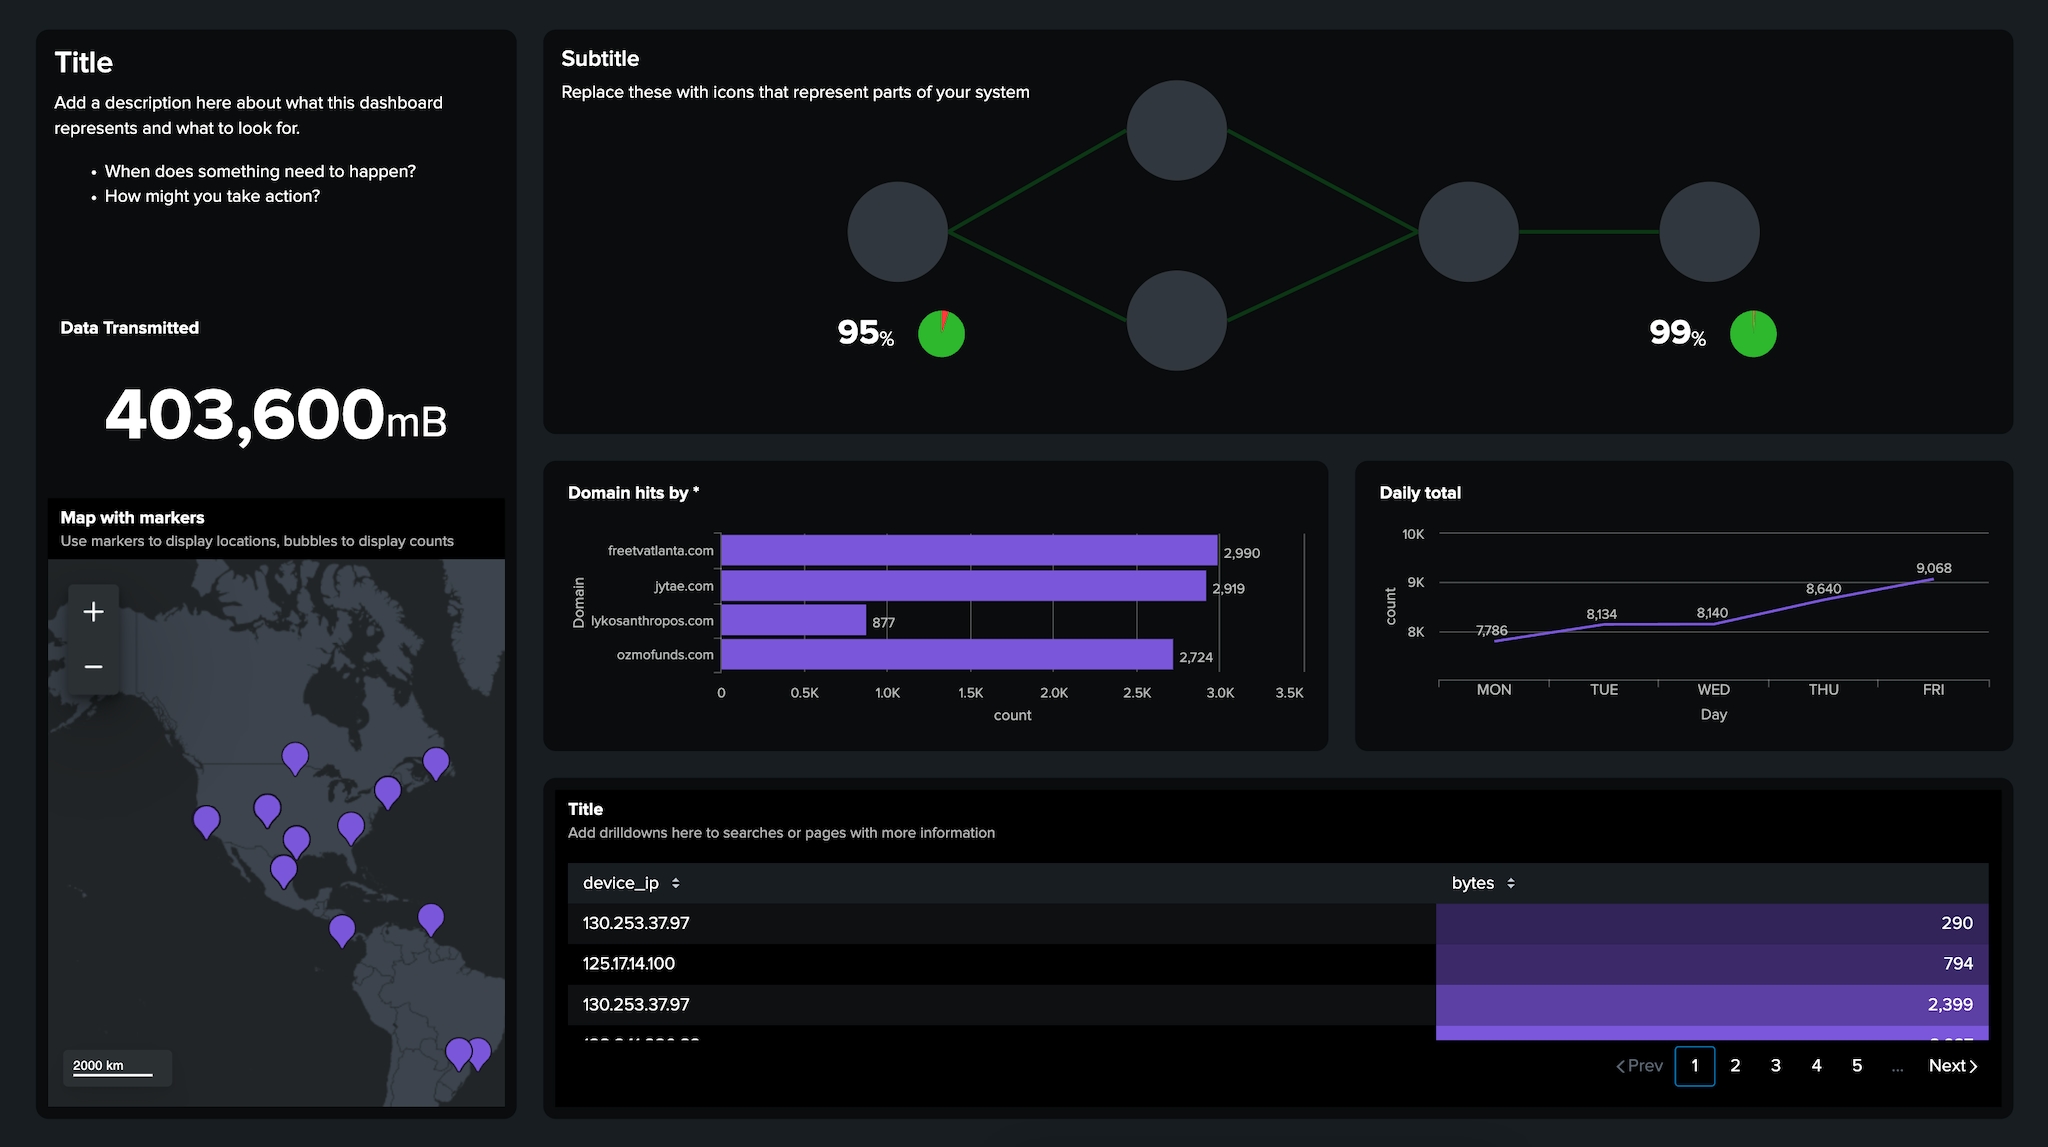
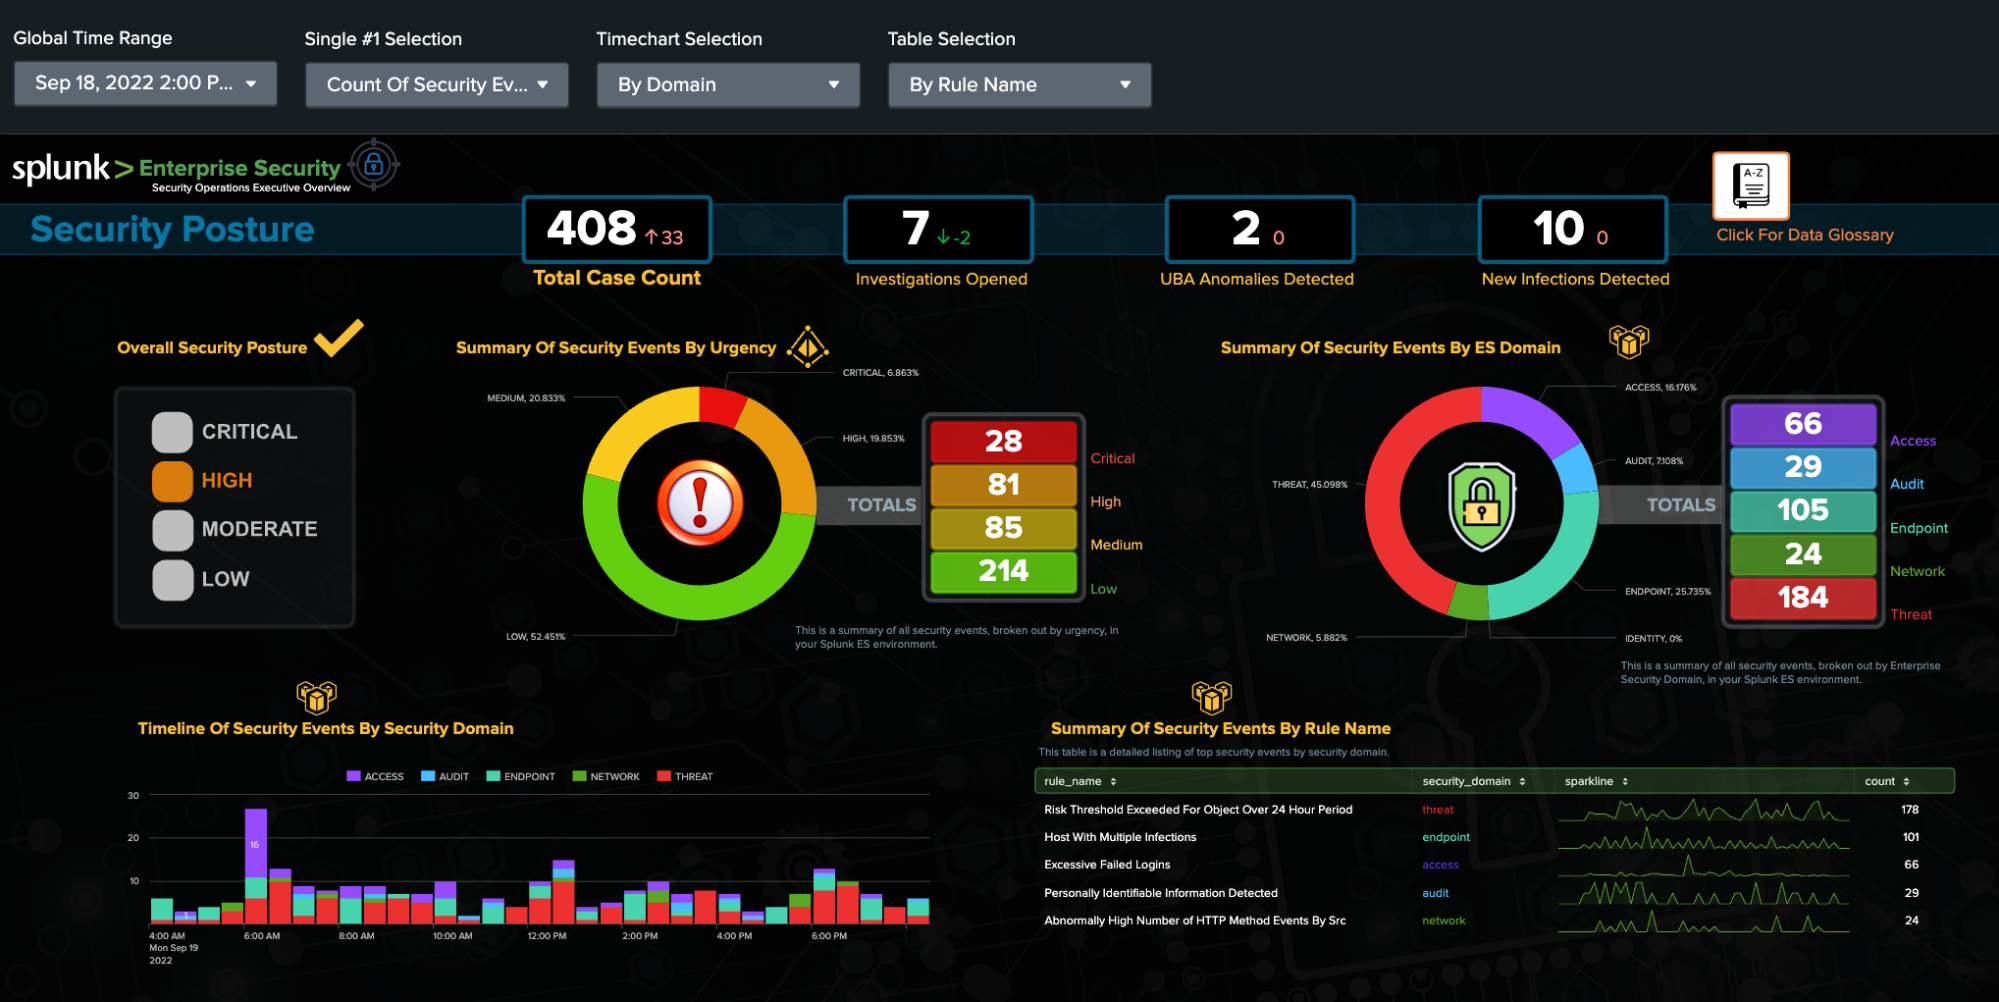
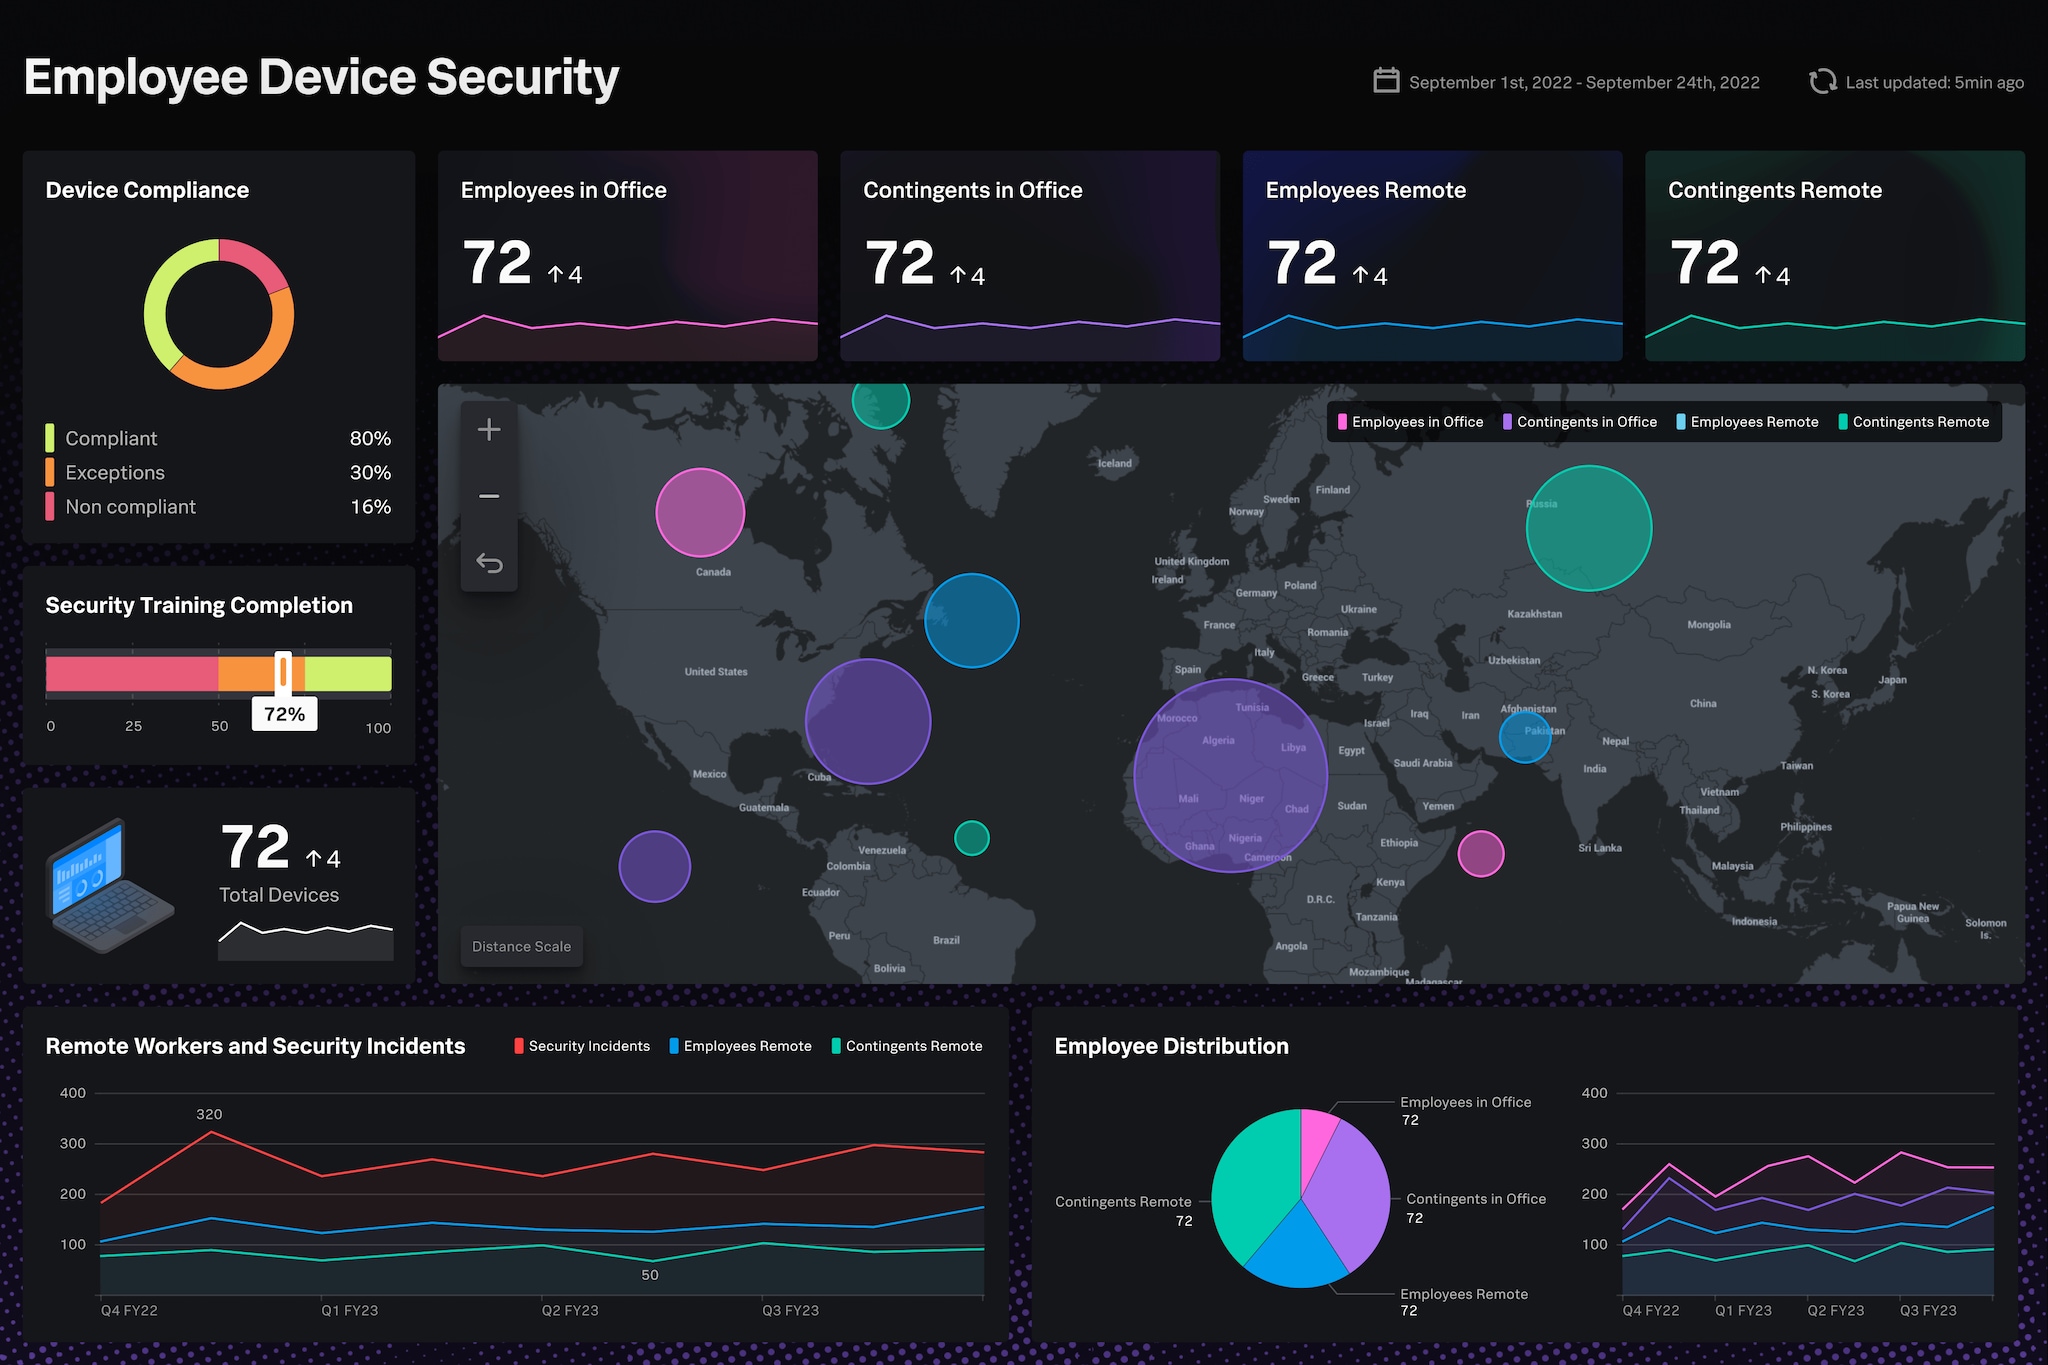
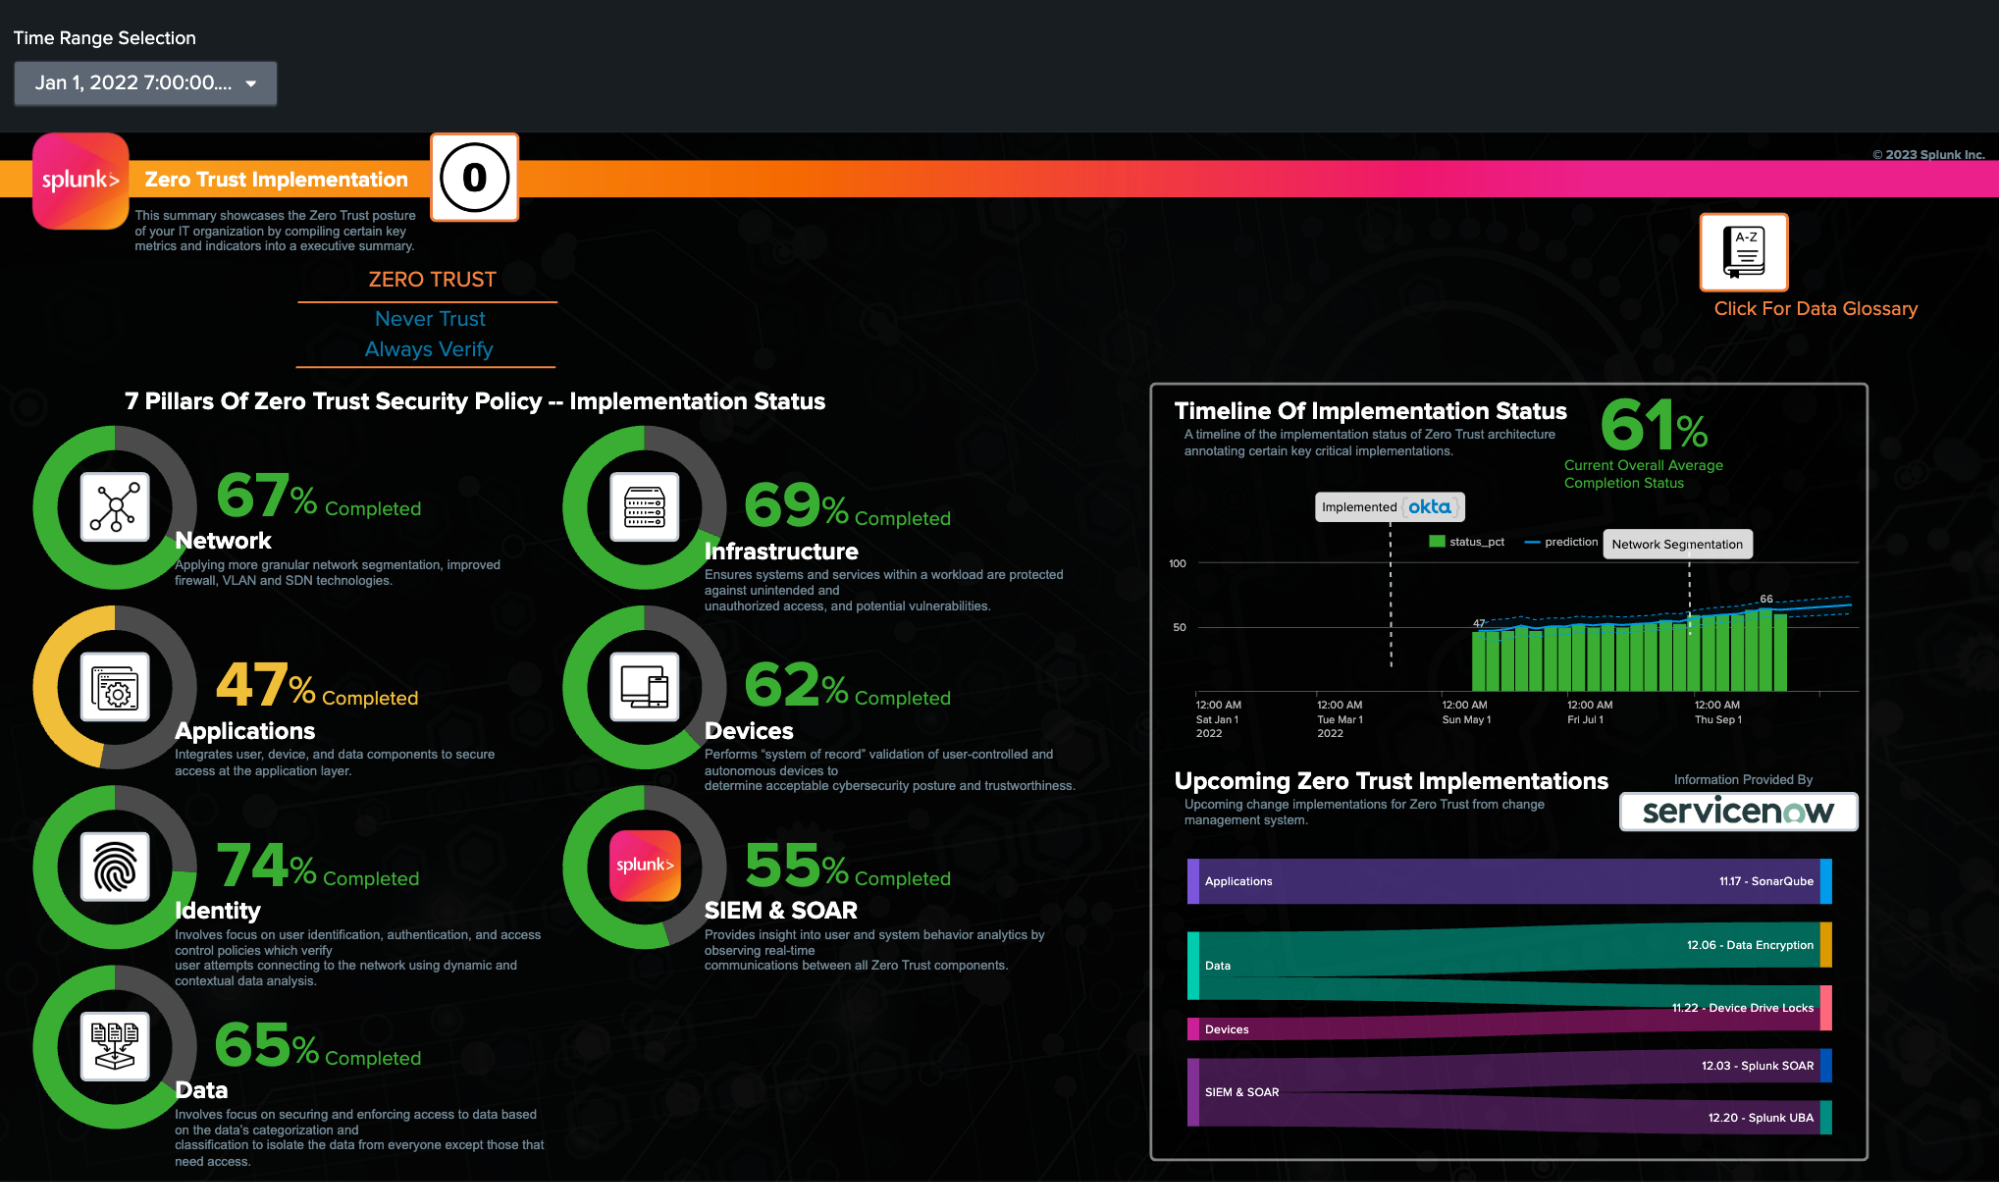
Leveraging Splunk Dashboards for Executive Visibility | Splunk
IT Operations Analytics: An Introduction | Splunk
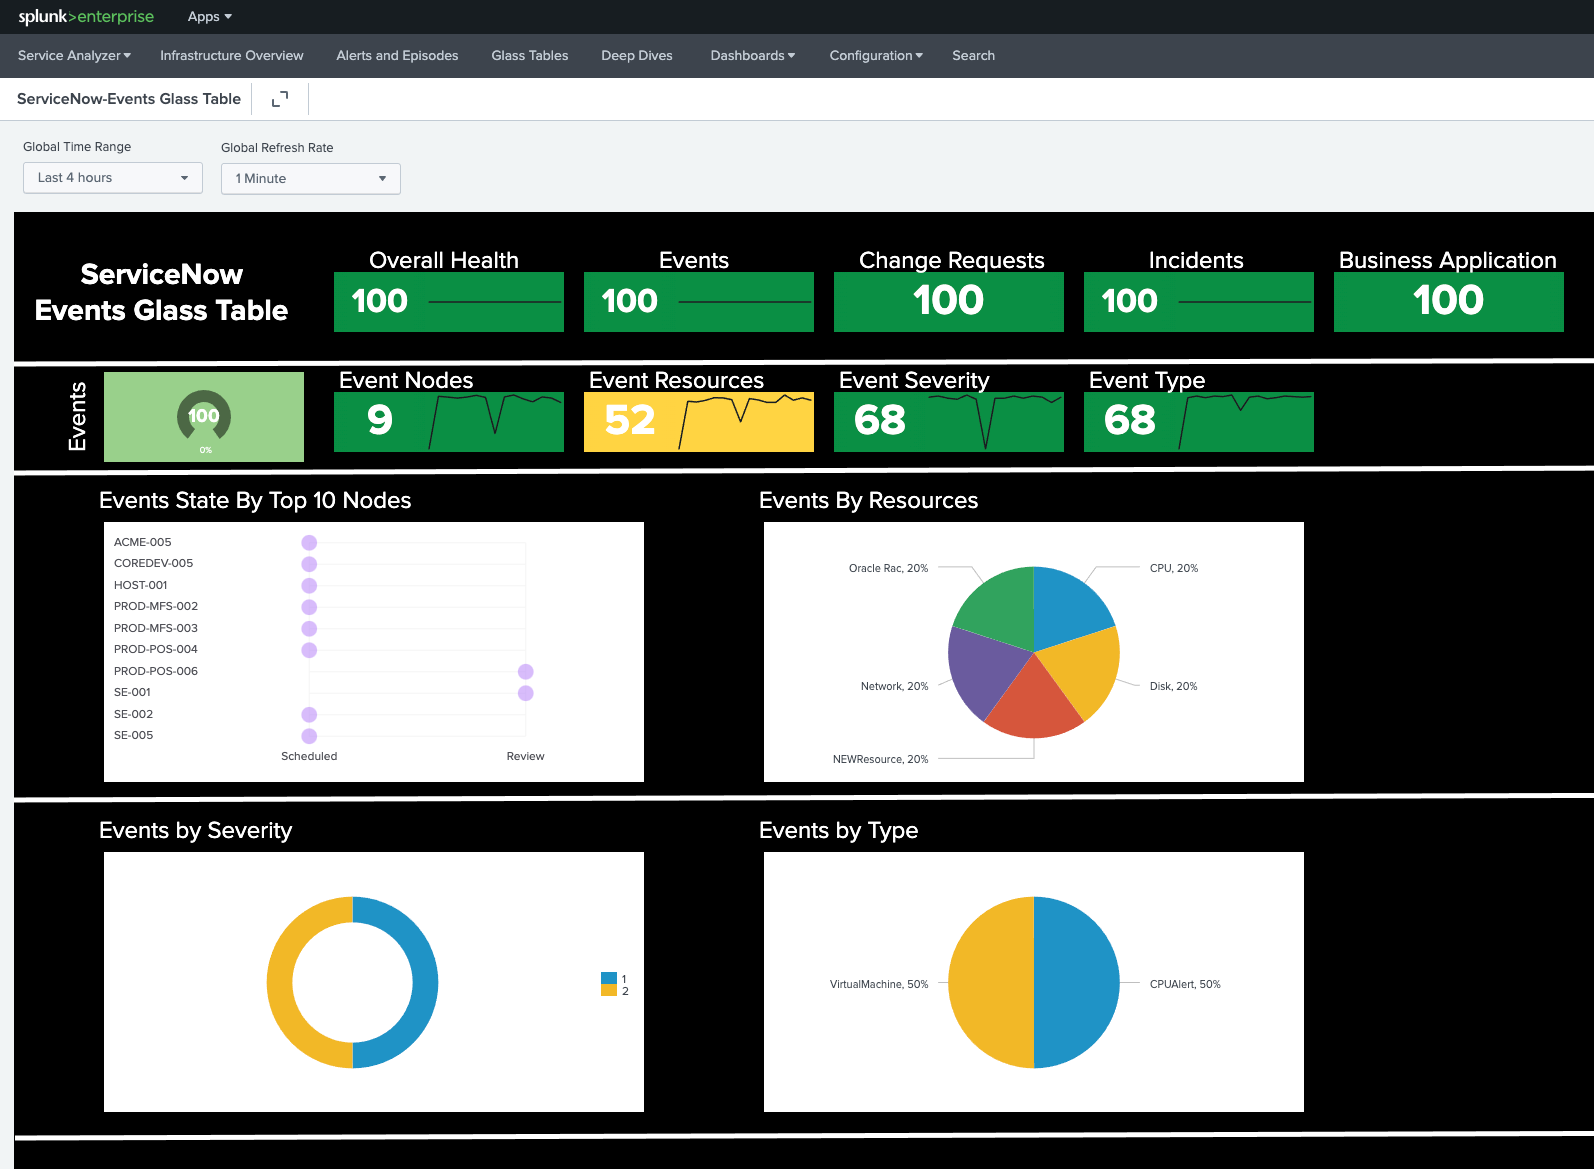
ServiceNow Is Available in Splunk Enterprise! | Splunk
Dashboard Studio:タブ形式のダッシュボード | Splunk
Sourcetypes Gone Wild | Splunk
Splunk Log Practices | Splunk logging best practices – WTRDQ
Partners | Splunk
Security Monitoring | Splunk
SplunkShow Enterprise Security Sandbox | Splunk
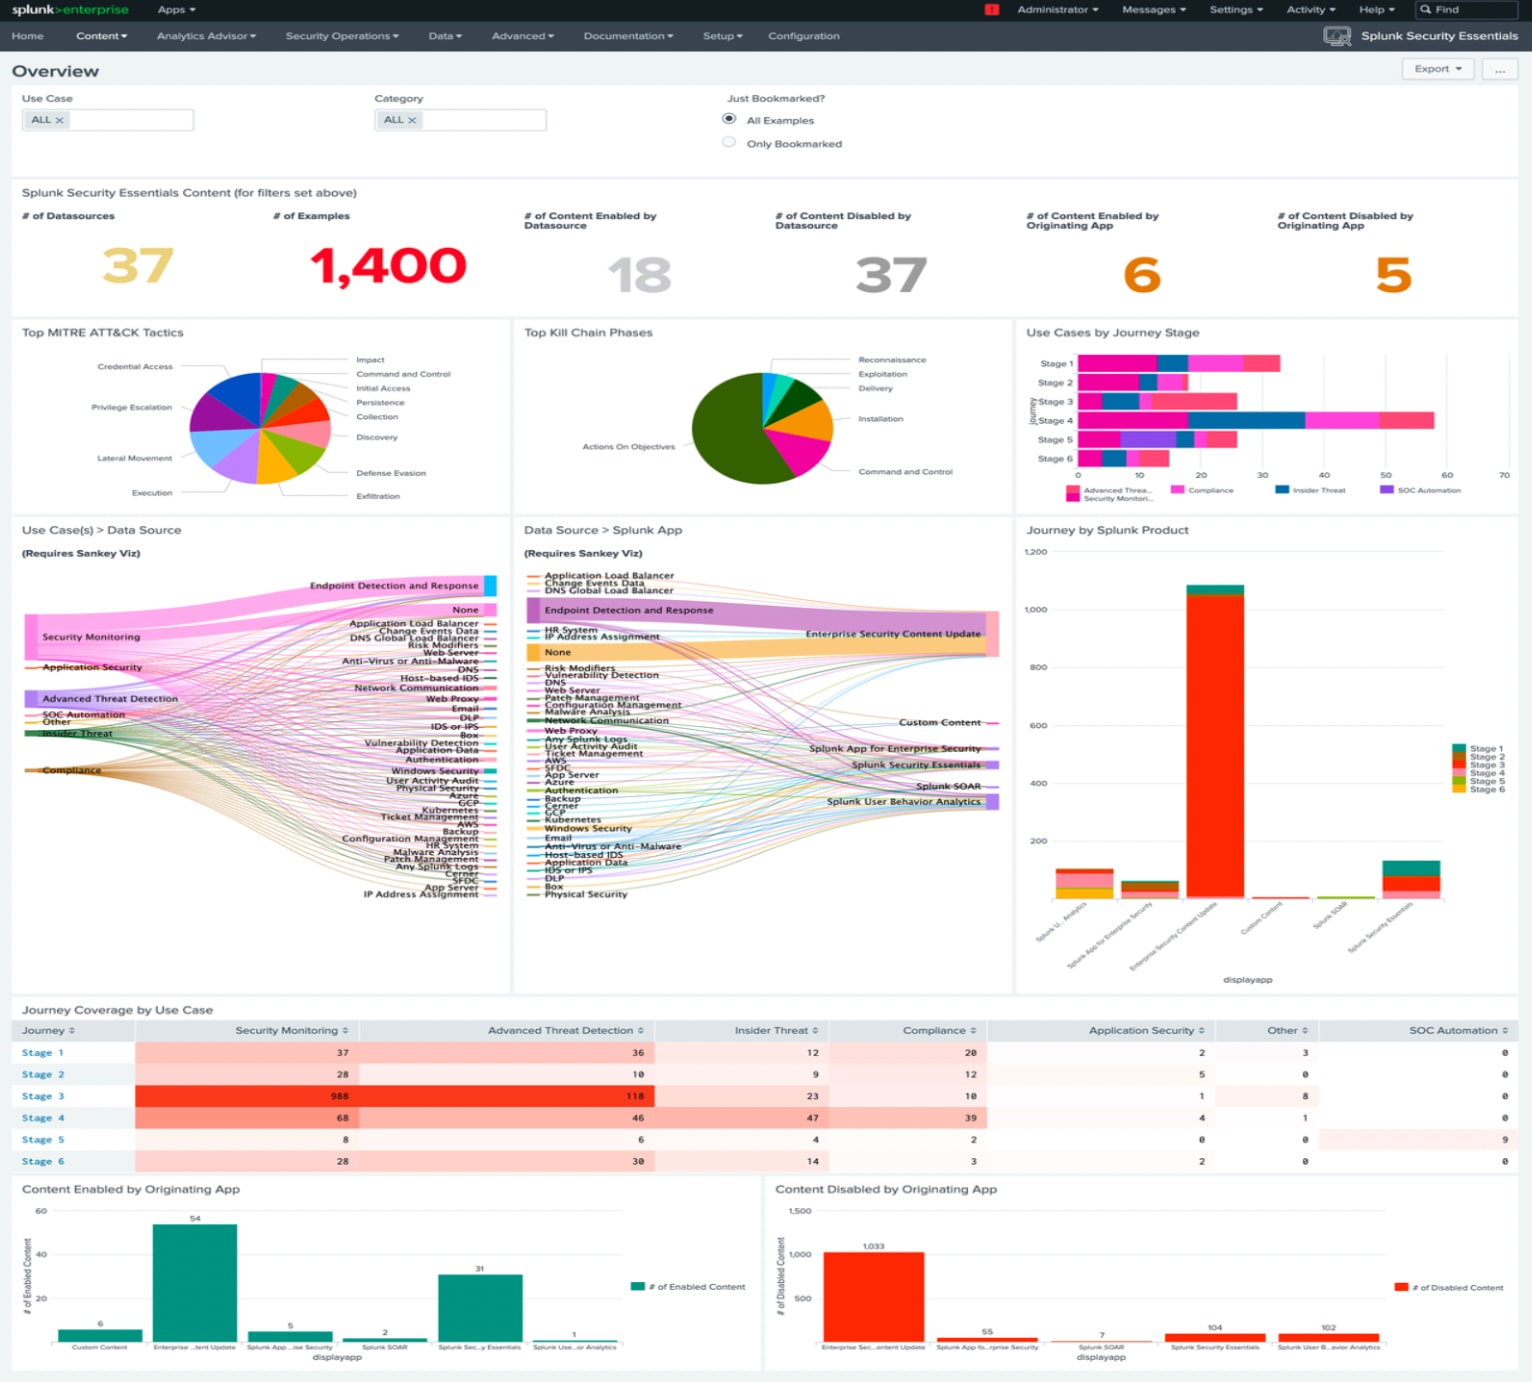
Do More with Splunk Security Essentials 3.7.0 | Splunk
Dashboard Studio: Sweating the Small Stuff | Splunk
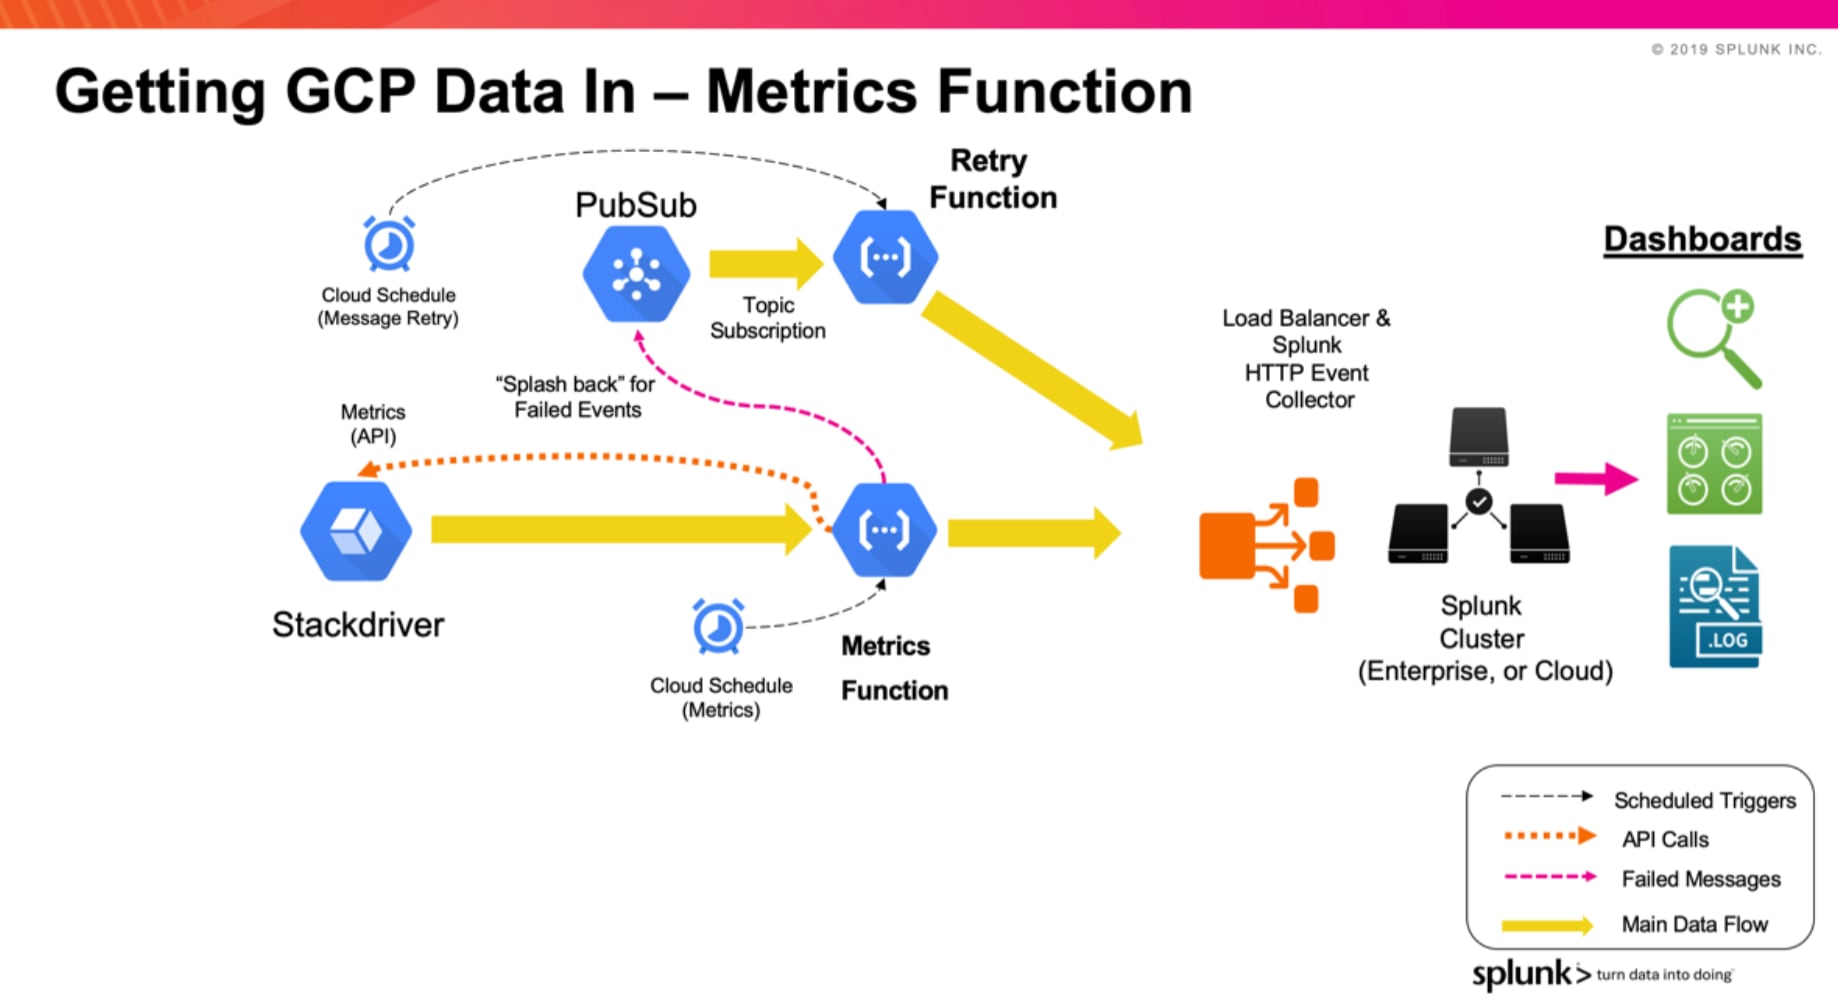
Getting Microsoft Azure data into the Splunk platform - Splunk ...
Splunking Your *.conf Files: How to Track Configuration Changes Like a ...
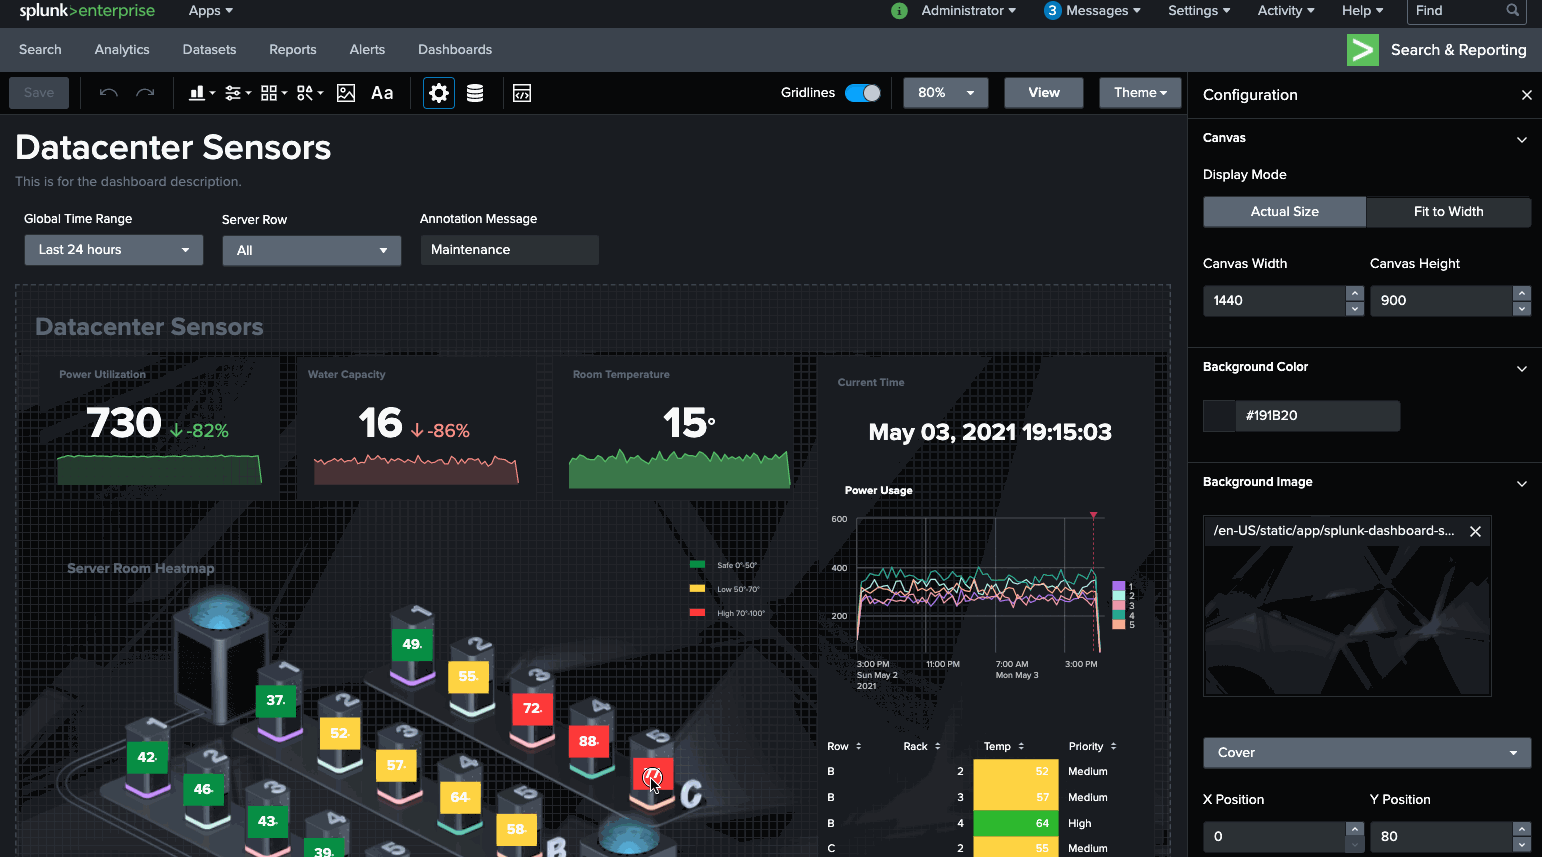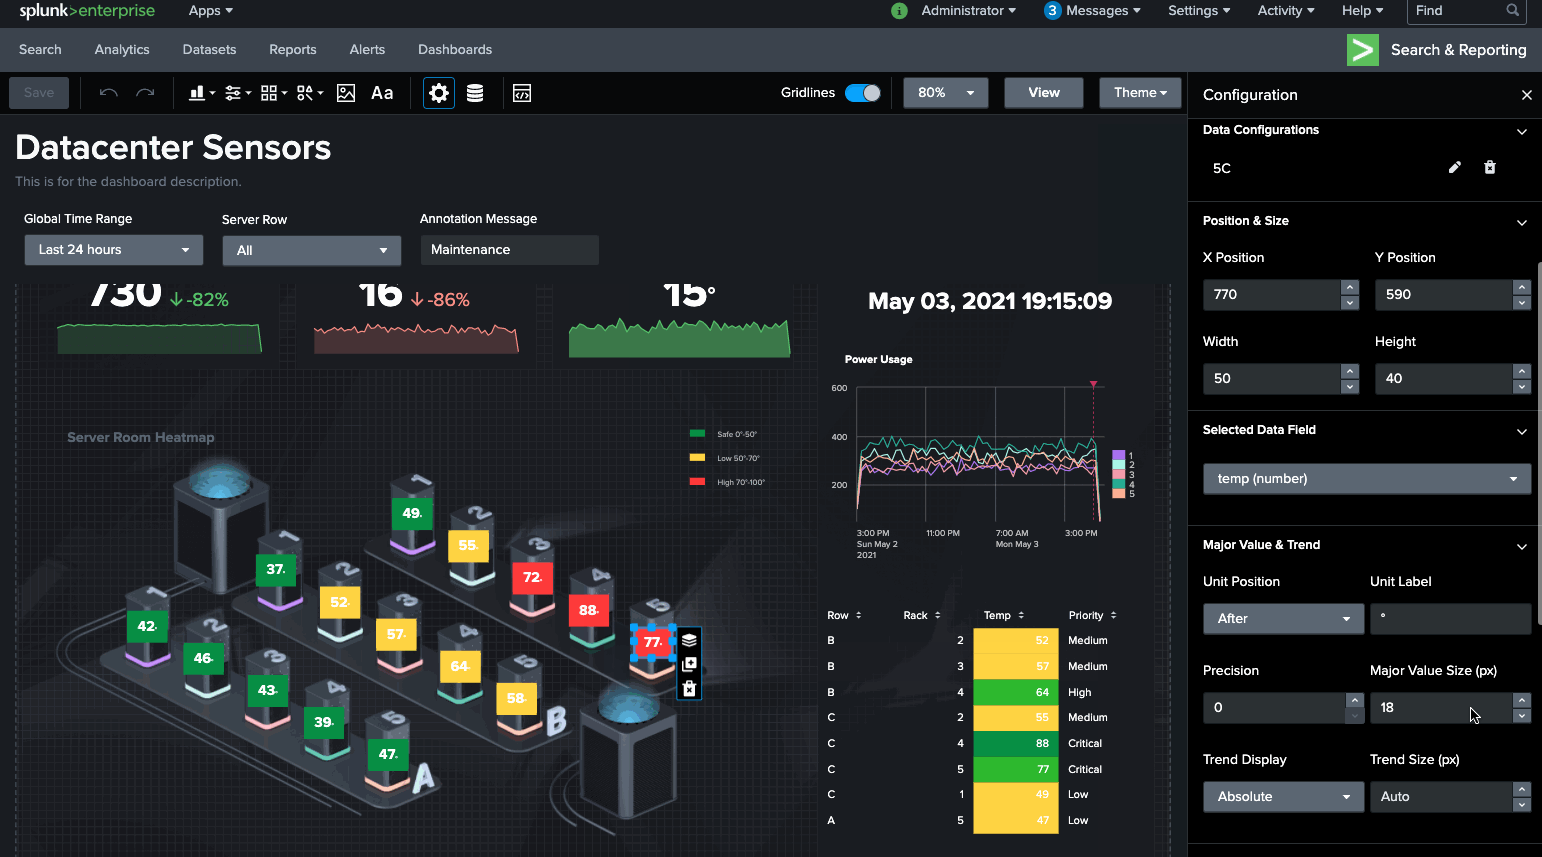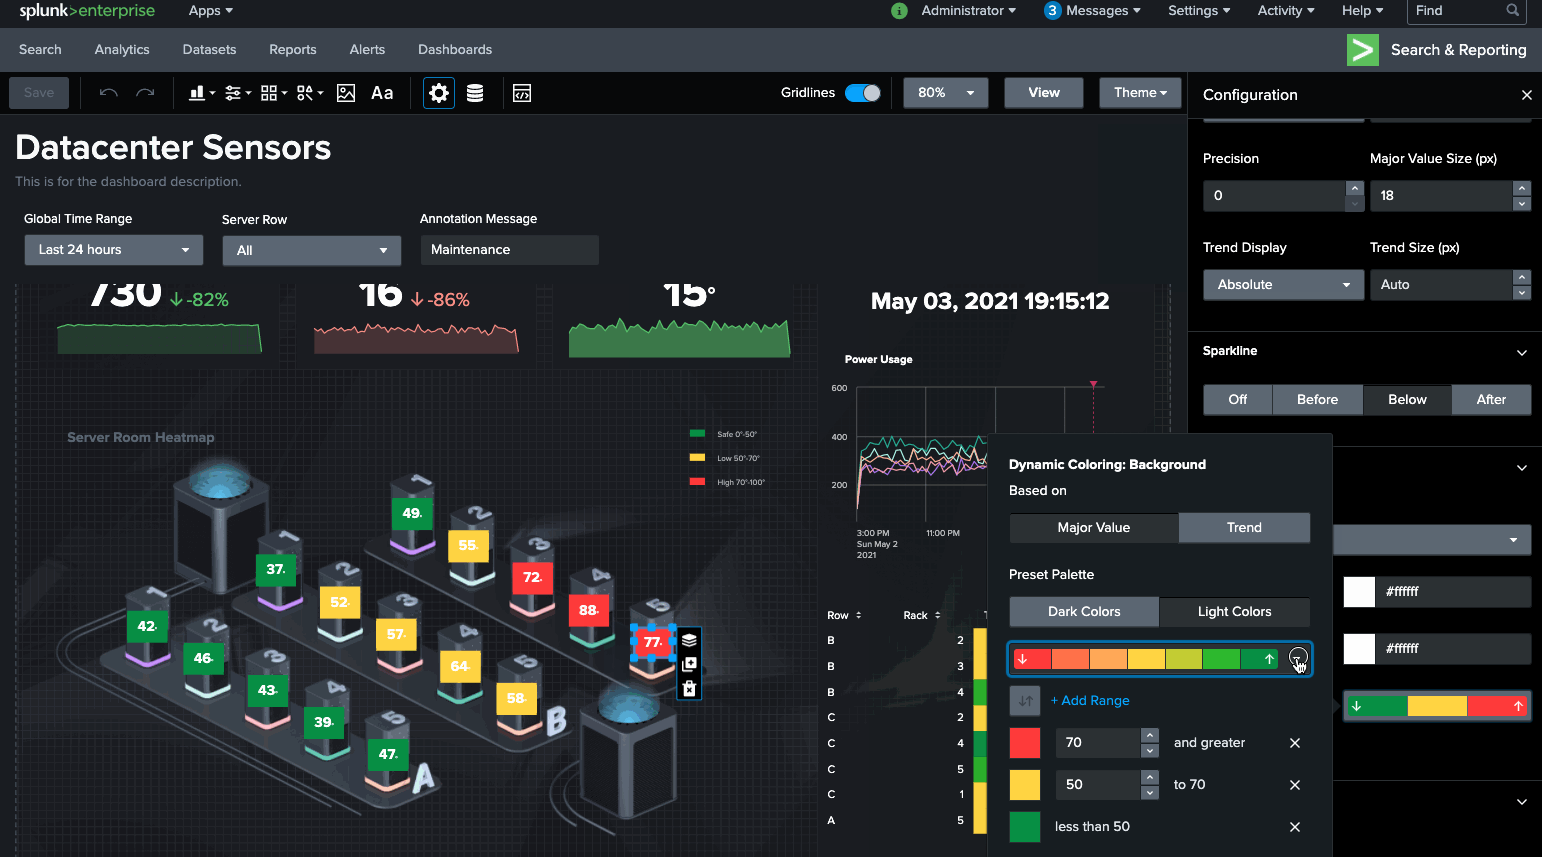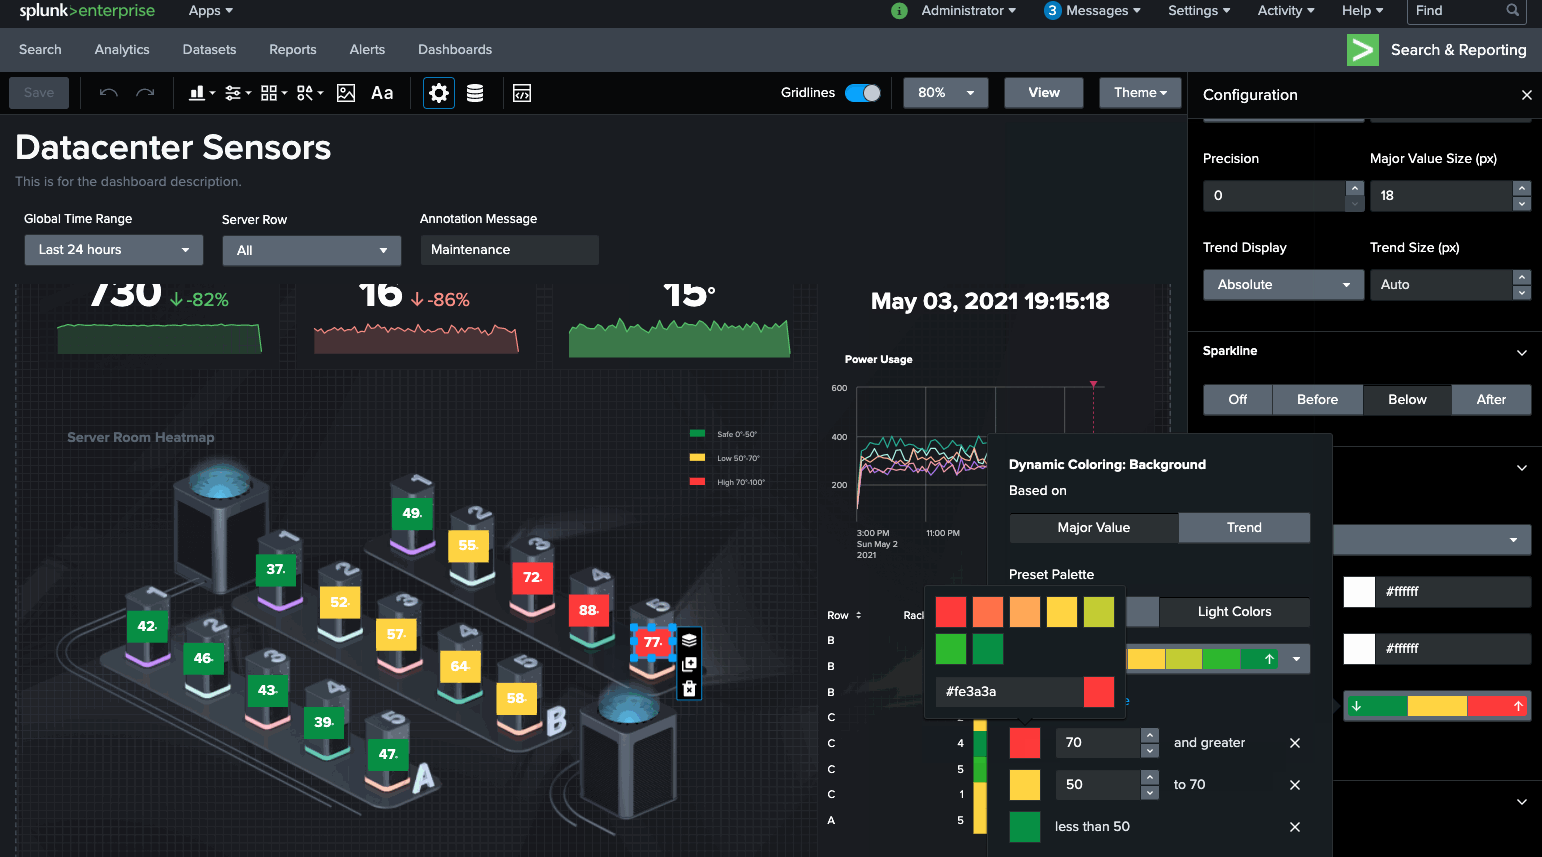
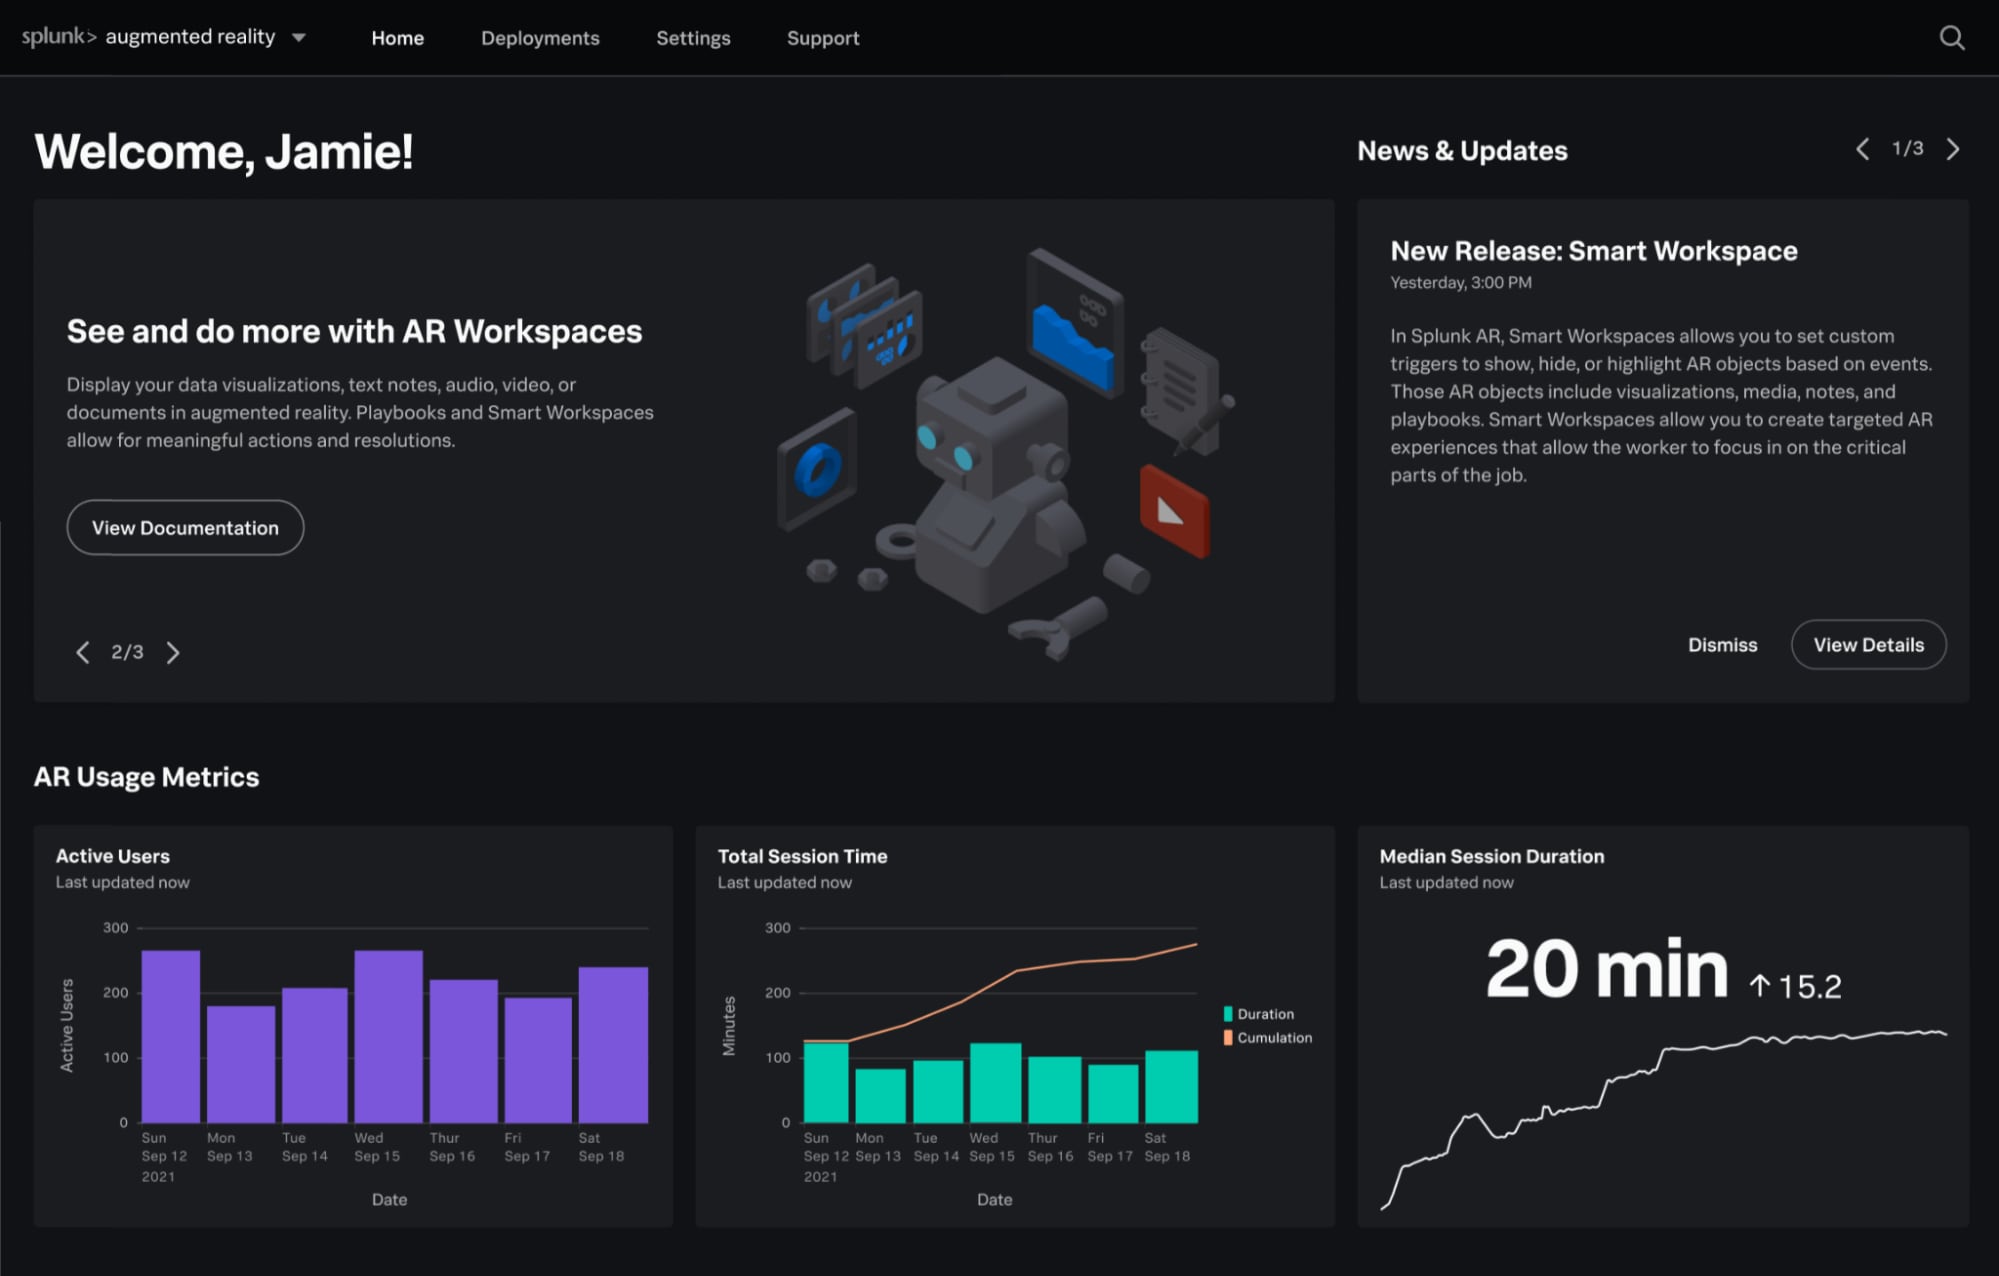
Splunk Brings Augmented Reality Into The Server Room – NEMXDG
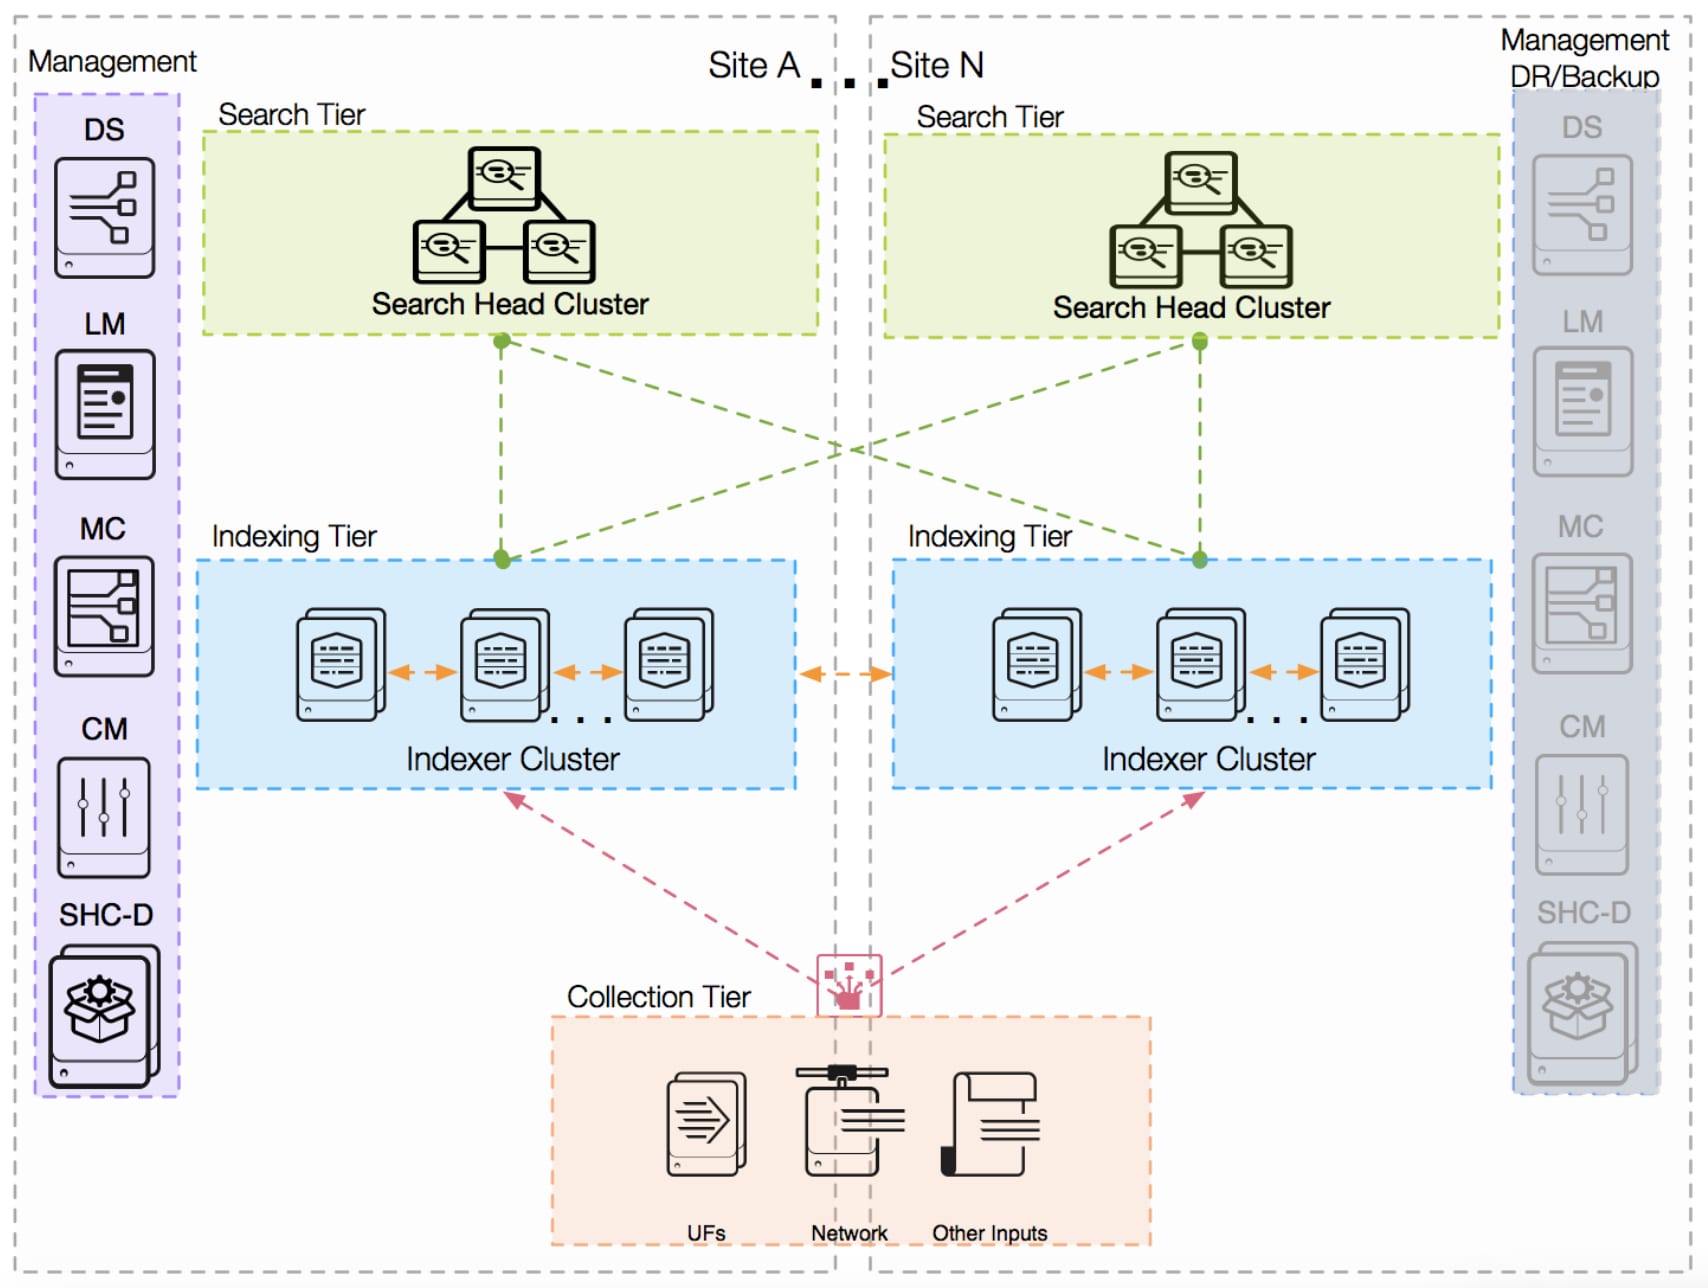
Splunk Cluster Pushing _ Deploy a heavy forwarder – LYIFAM
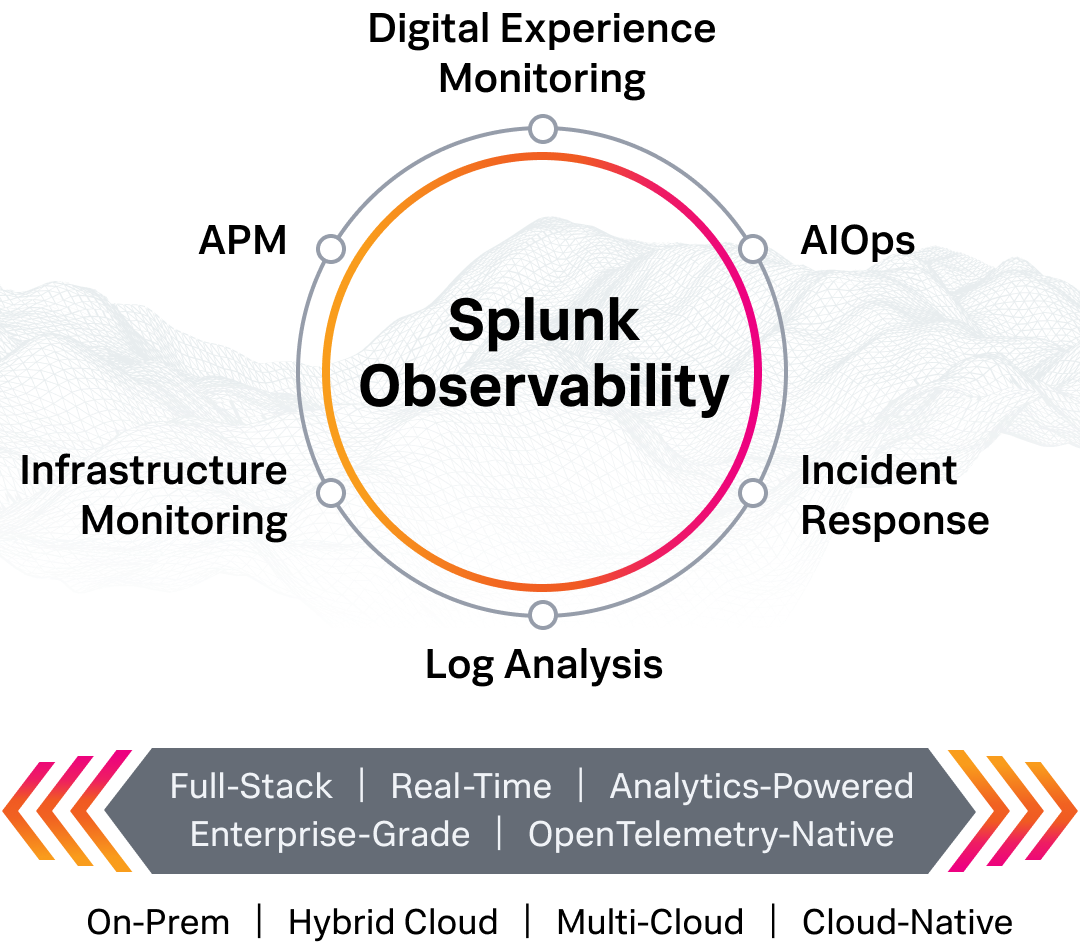
Introducing The Splunk Observability Suite – VKFUU
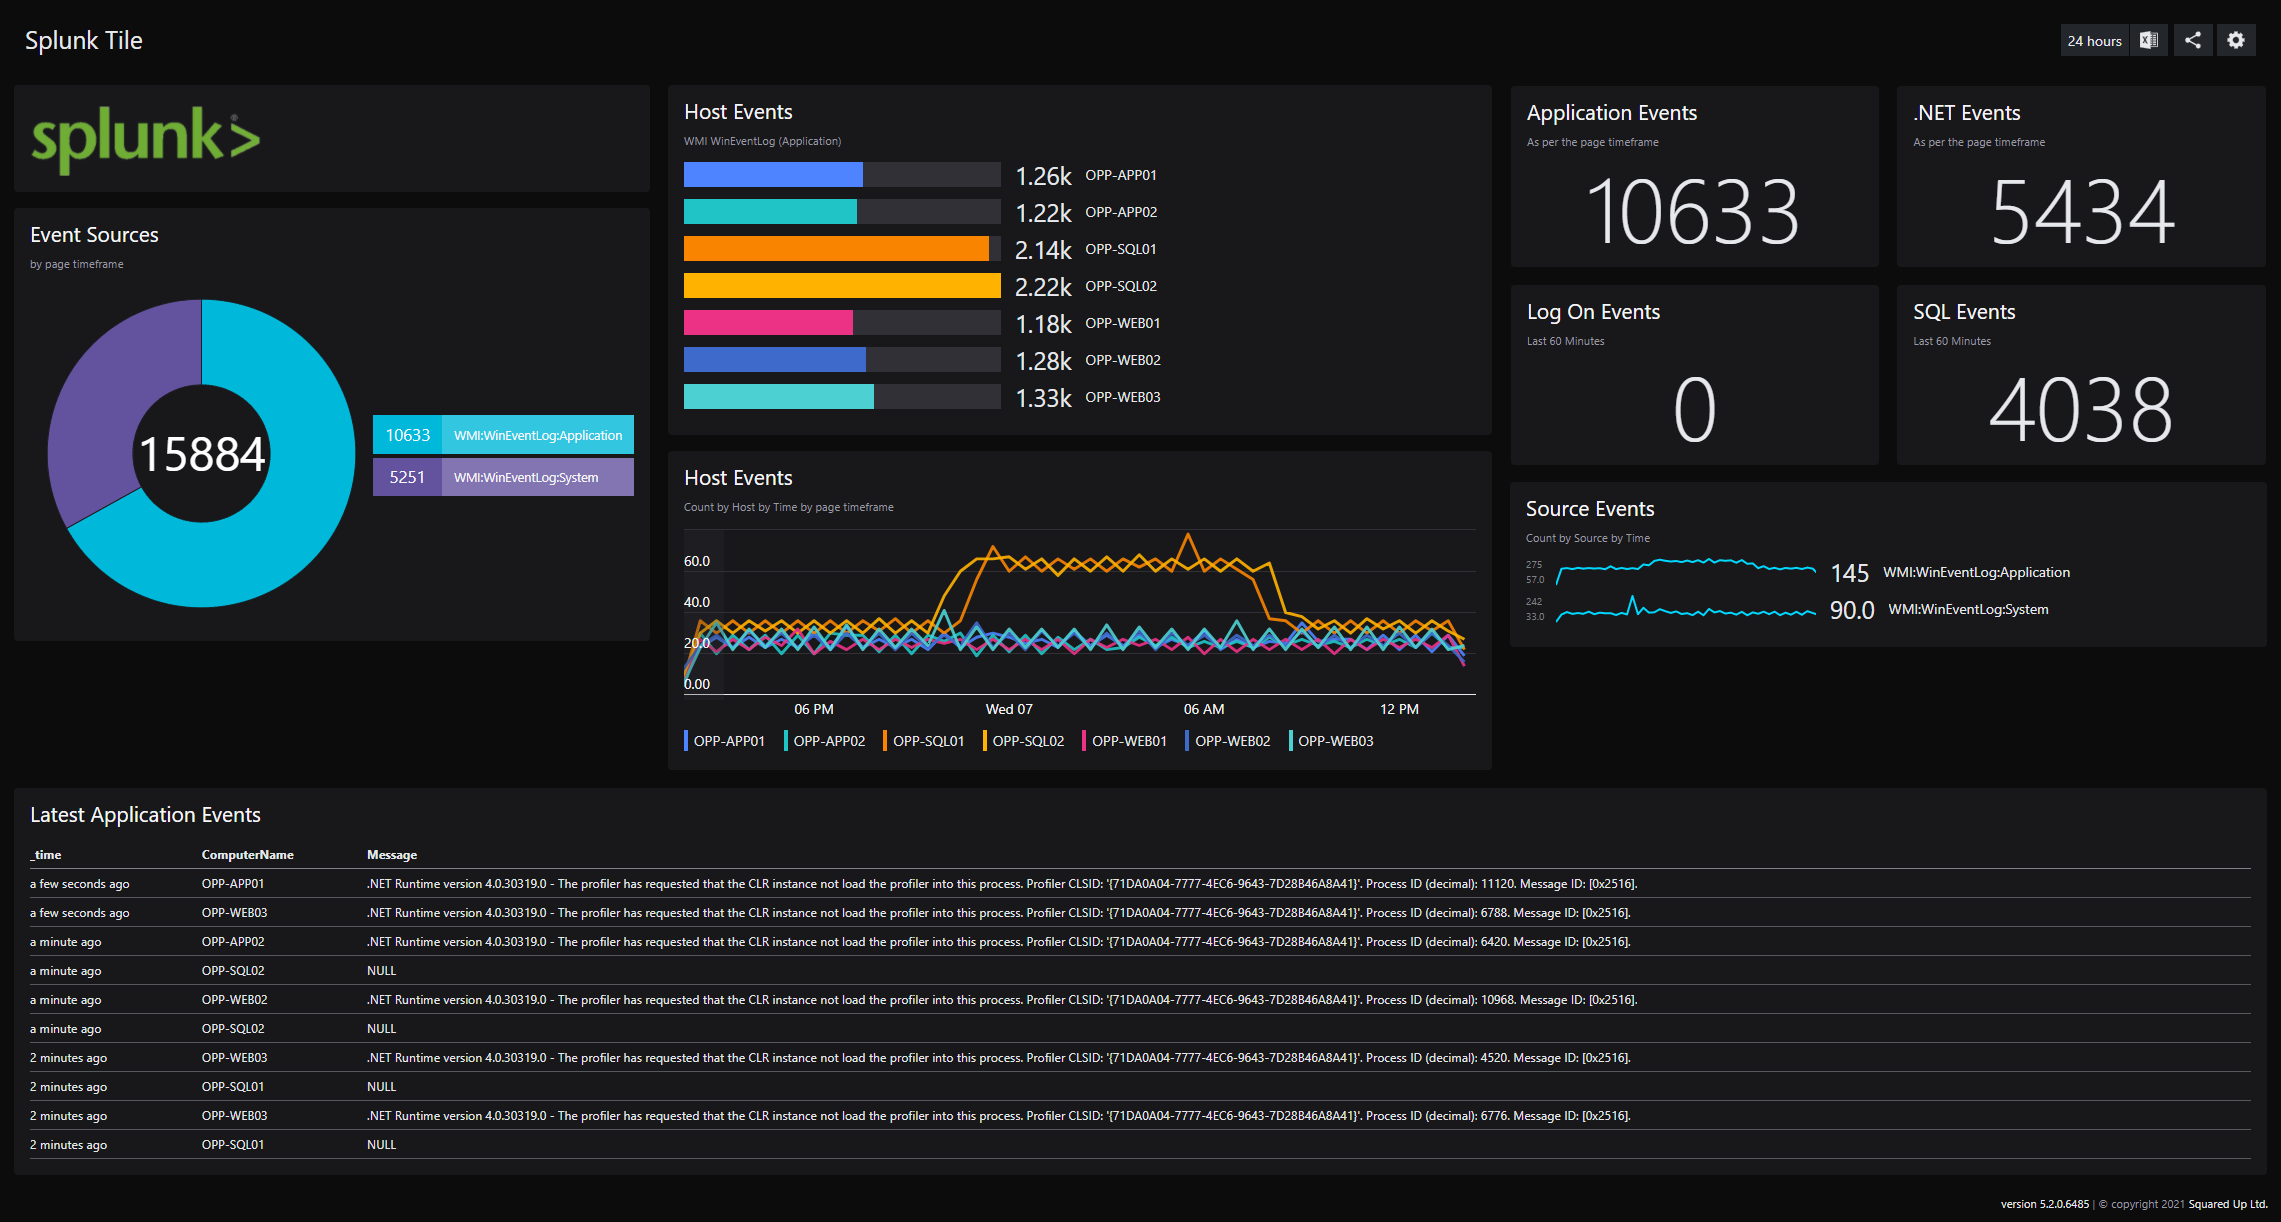
Visualize any Splunk data - SquaredUp
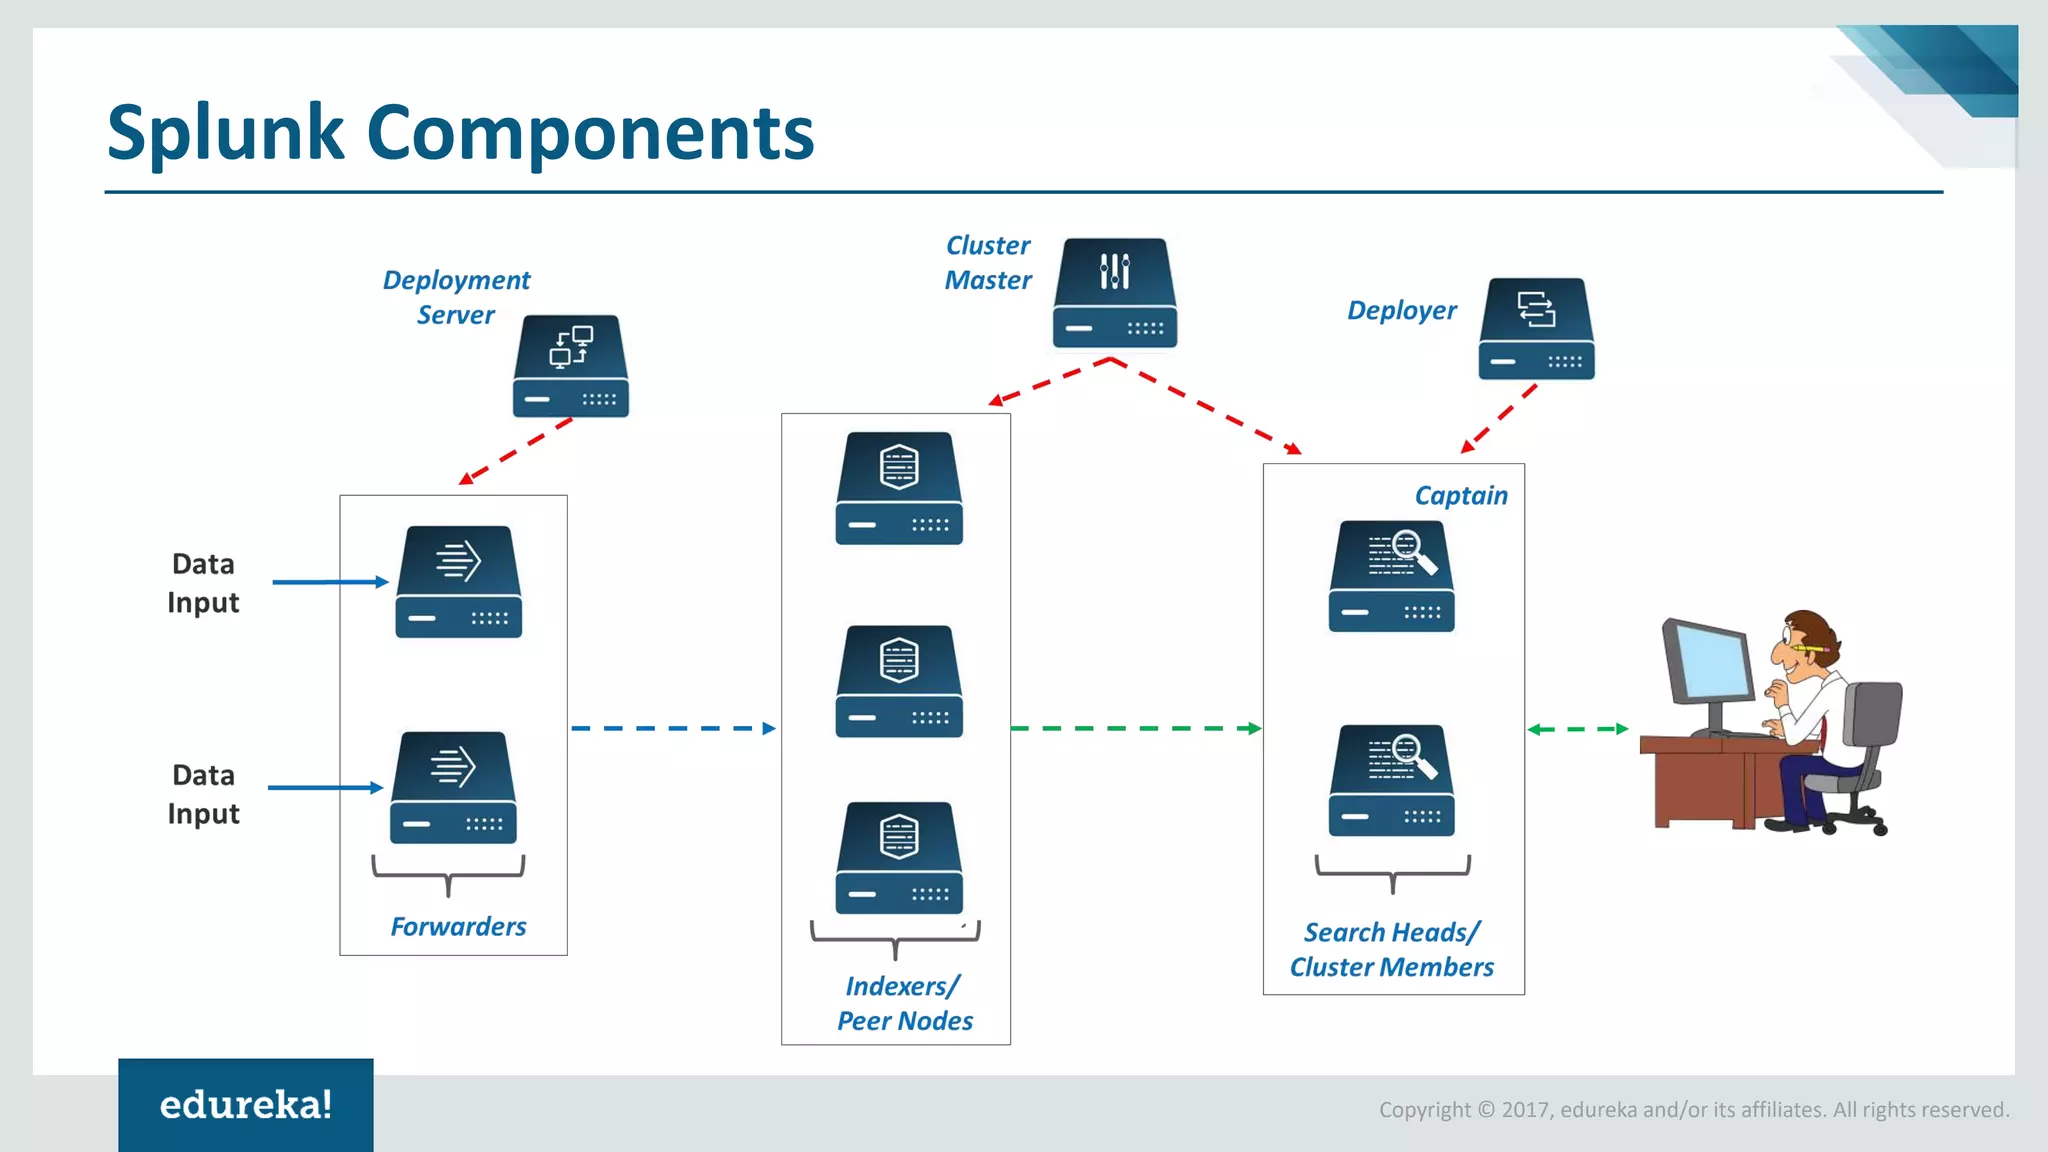
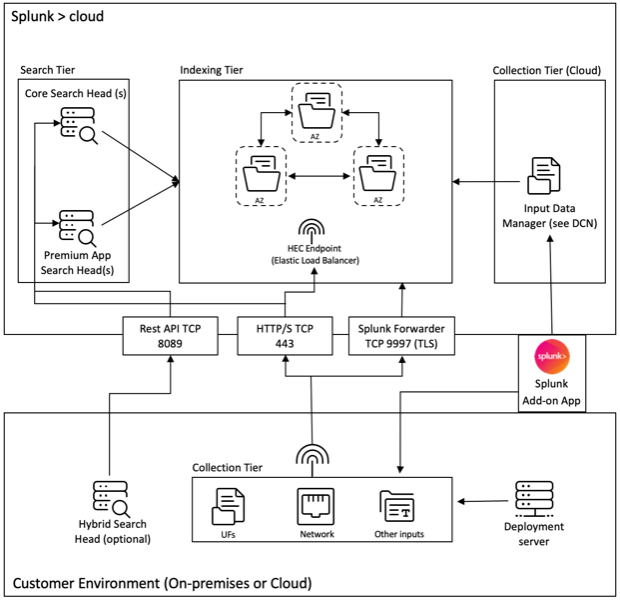
Splunk architecture with Citrix Analytics add-on application
Azure Event Hub Schema Registry – RYJIWN
Digital Guardian Splunk at James Mansell blog
Splunk Log Processing at Alana Mcgovern blog
Splunk in 2026
splunk ローリングリスタート – c# ローリングリスタート – WIUX
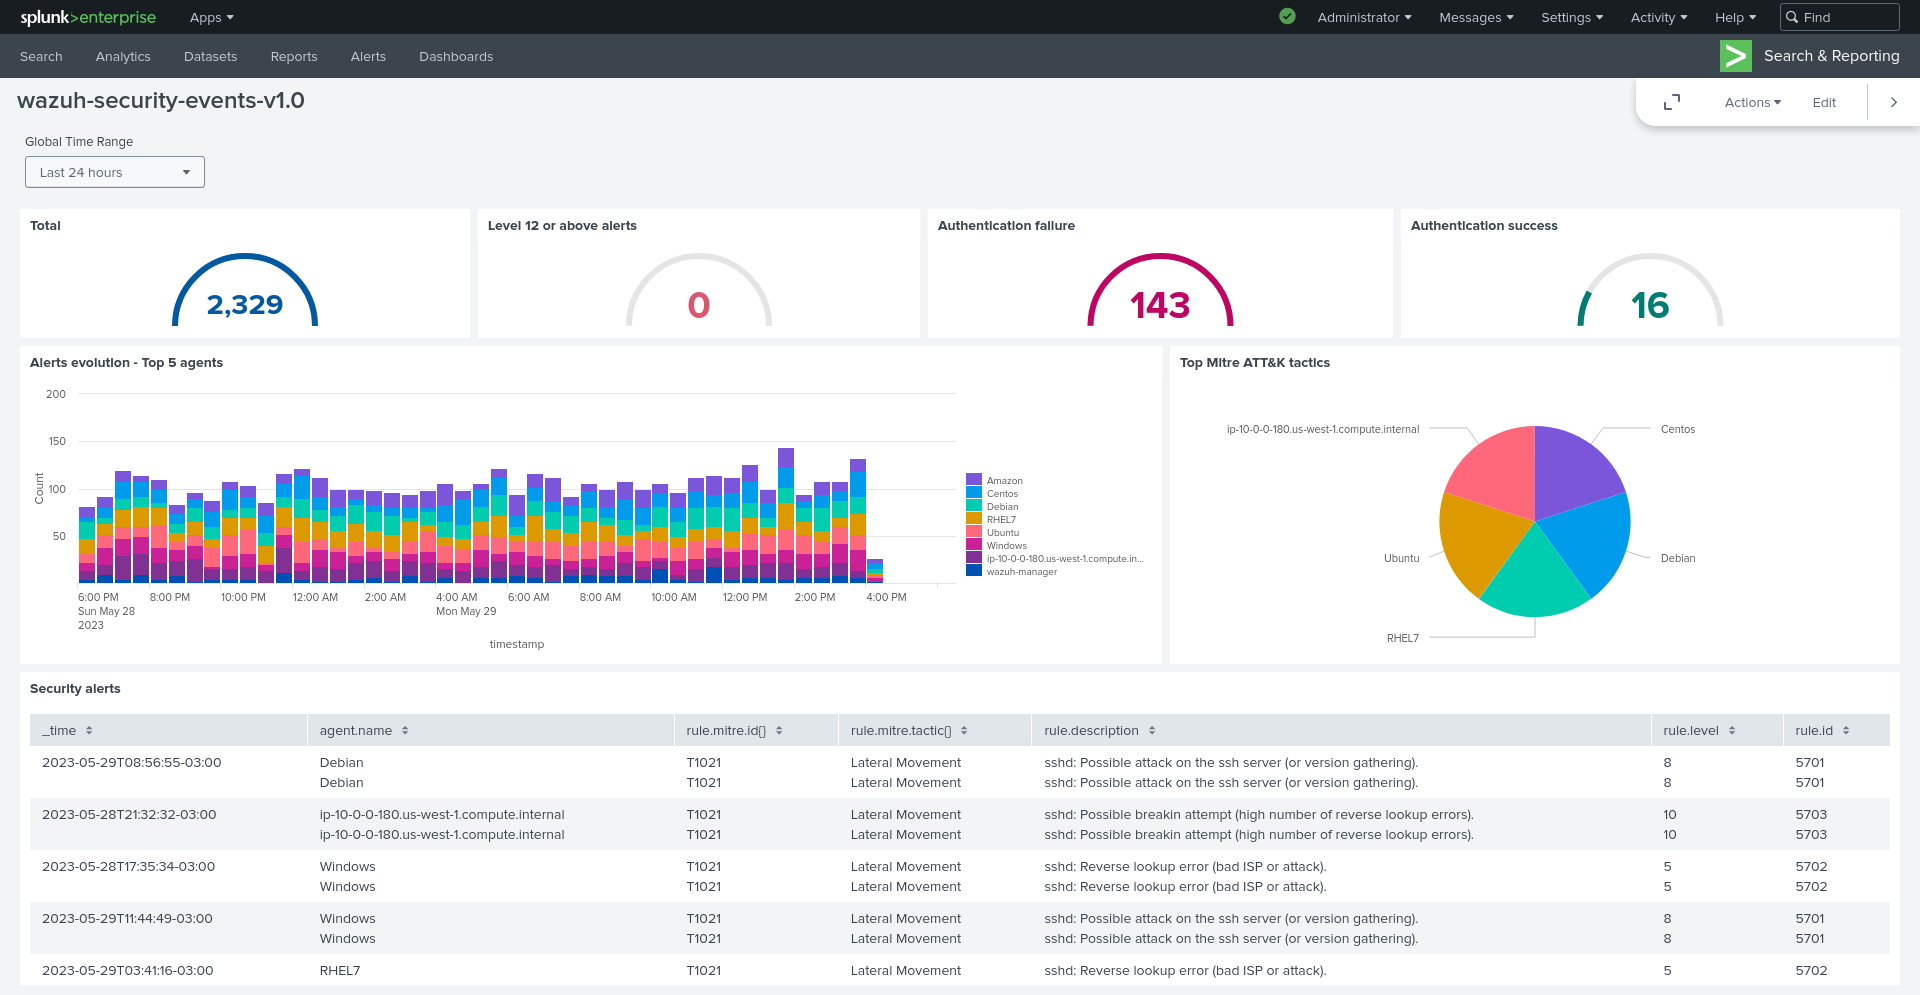
Splunk integration · Wazuh documentation
Istio / Comprehensive Network Security at Splunk
Splunk Cloud Platform Experiences - Splunk Documentation
Cyber Vision Splunk Add-on
Splunk UI and the Dashboard Framework: More Visual Control Than Ever ...
Splunk アカウント – Splunk 仕組み : Splunk Enterprise無料ダウンロード – TOKTVT
Event Hub Partitions Explained at Andy Sage blog
Kostenlose Splunk Soar-Testversion – CBPG
What Are Splunk Logs at William Gutirrez blog
Case Study: Splunk Log Aggregation
What Are Splunk Apps at Alan Koester blog
Easily Improve Agent Saturation with the Splunk Ad... - Splunk Community
Range Function Splunk at Ebony Dunlop blog
Article On Matatag Lesson Logstash Vs Splunk Siem Dashboards
Splunk Dashboard Templates
How Splunk SOAR is Helping Organizations Achieve a More Resilient ...
Splunk - STelligence
Private Locations — Splunk Observability Cloud Documentation – NRFGY
Types Of Dashboards In Splunk - Design Talk
Introducing The Splunk Observability Suite – TUIK
Splunk Network Monitoring Dashboard – SFKAD
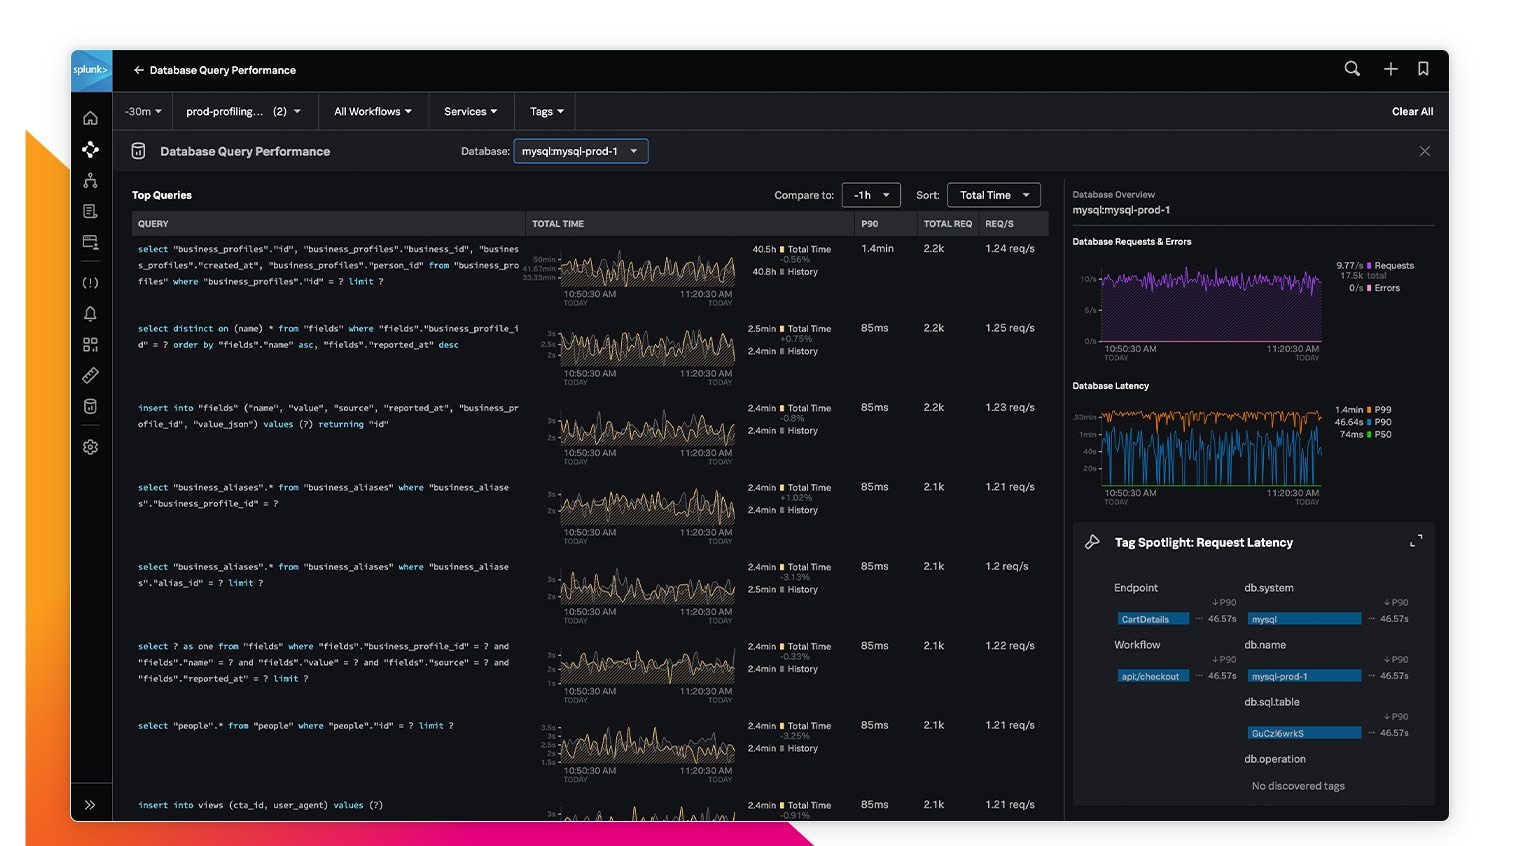
Splunk Database Monitoring - Splunk Community
Aws Dashboards And Reports Splunk at Rachel Shortland blog
TryHackMe | Splunk: Basics – Igor_sec's Blog
Bucket In Splunk Query at Raymond Workman blog
Based on this image's title: “Splunking Azure: Event Hubs | Splunk”