Showing 119 of 119on this page. Filters & sort apply to loaded results; URL updates for sharing.119 of 119 on this page
Windows Security Log Event ID 4656 - A handle to an object was requested
Event ID 4656 - Repeated Security Event log - PlugPlayManager
Windows event ID 4656 - A handle to an object was requested | Windows ...
windows - Event 4656 on file server for files and folders not opened ...
DA Form 4656 - Scheduling Worksheet | Free Online Forms
TCVN - 4656 - 1 - 2009 | PDF
DA FORM 4656 Fillable - Army Pubs 4656 PDF | DA Forms 2024
DA FORM 4656 – Scheduling Worksheet | Army Pubs DA Form
リモート Shutdown アクセスが拒否されました
Check Who accessed a Shared Folder and Made File Changes
How to Track Who Changed a File or a Folder in Windows | ManageEngine ...
Quick Development Tips: How to monitor a folder and trigger an action ...
4656(S, F) A handle to an object was requested. - Windows 10 ...
Event ID 4656: A Handle to an Object was Requested [Fix]
Audit user access to a file - Software & Applications - Spiceworks ...
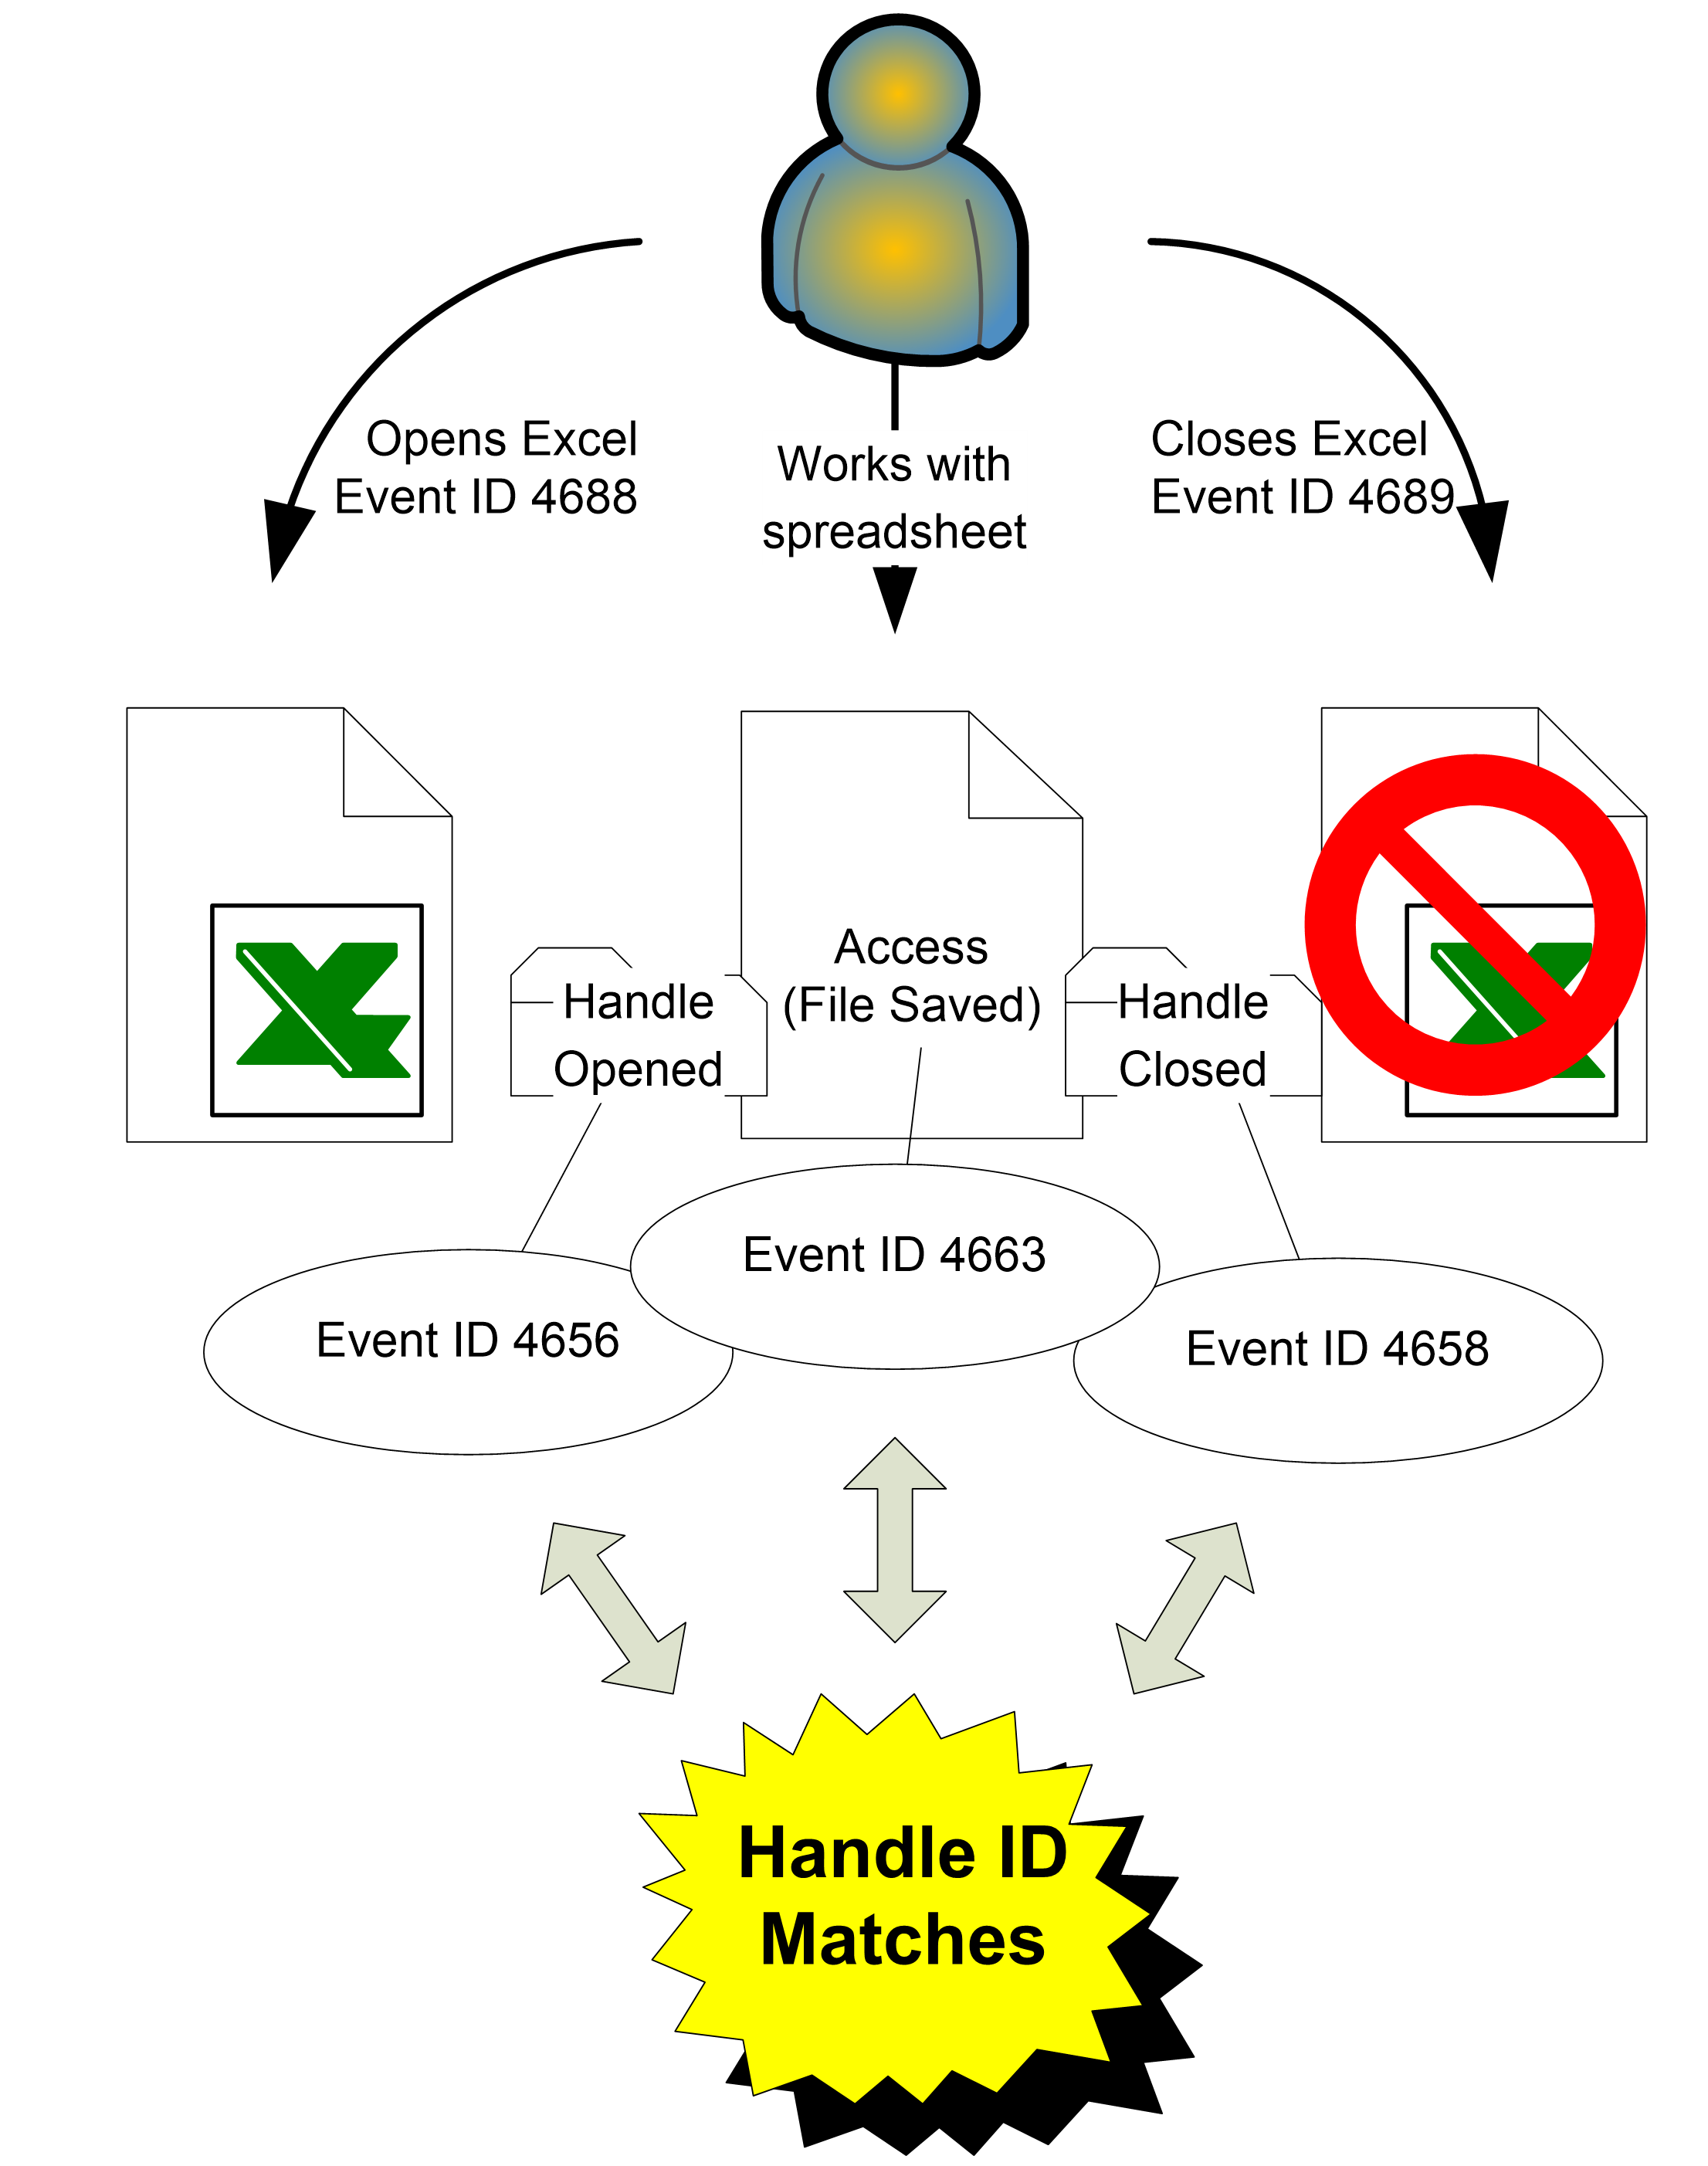
Chapter 7 Object Access Events
Is the Equivalent of a Field in a File System
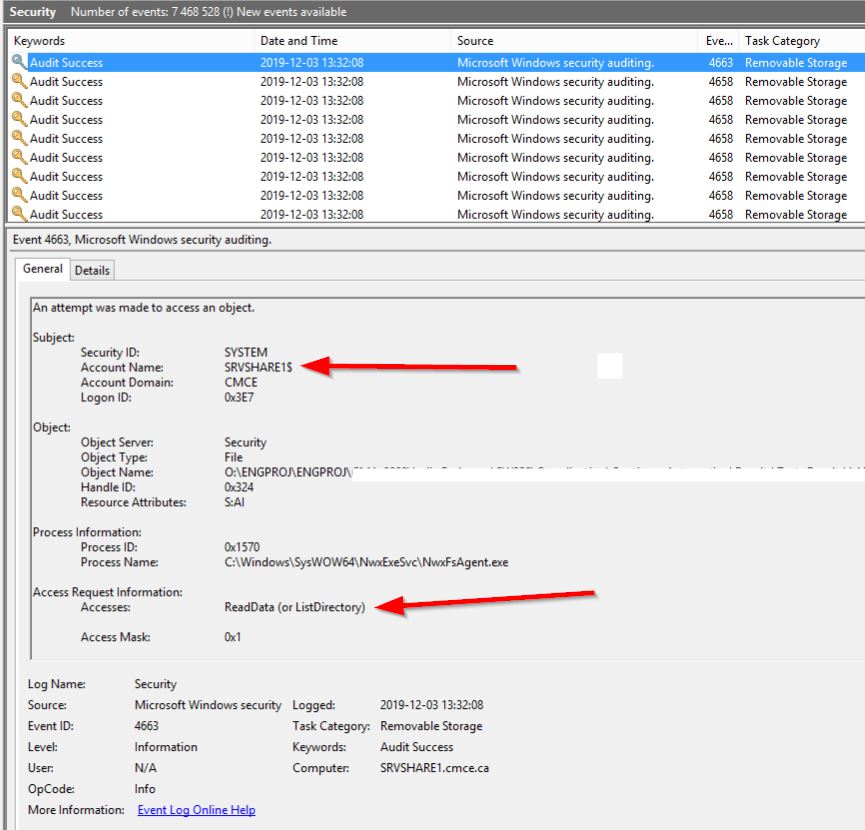
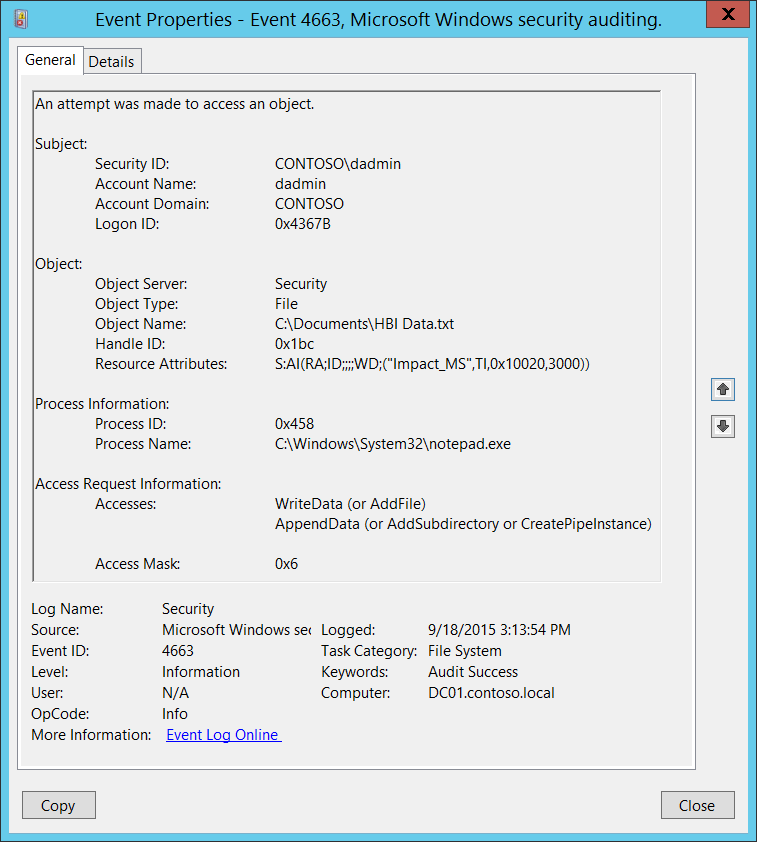
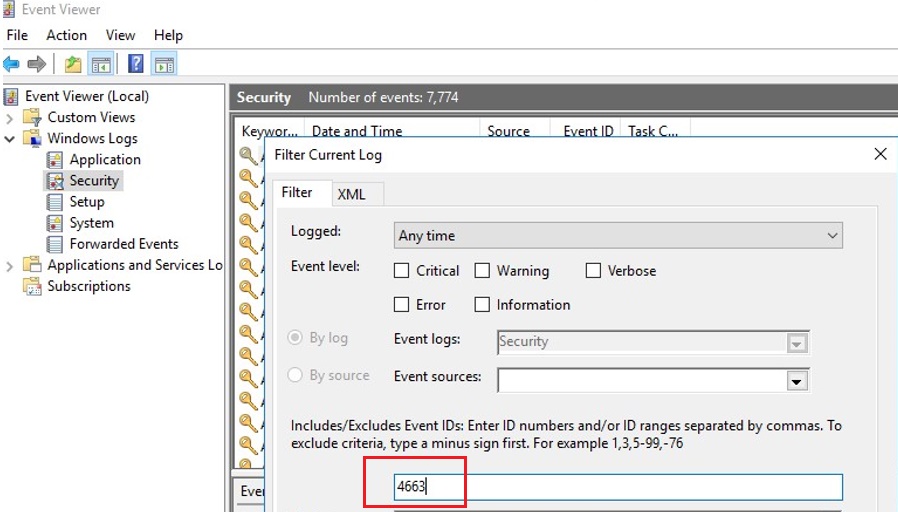
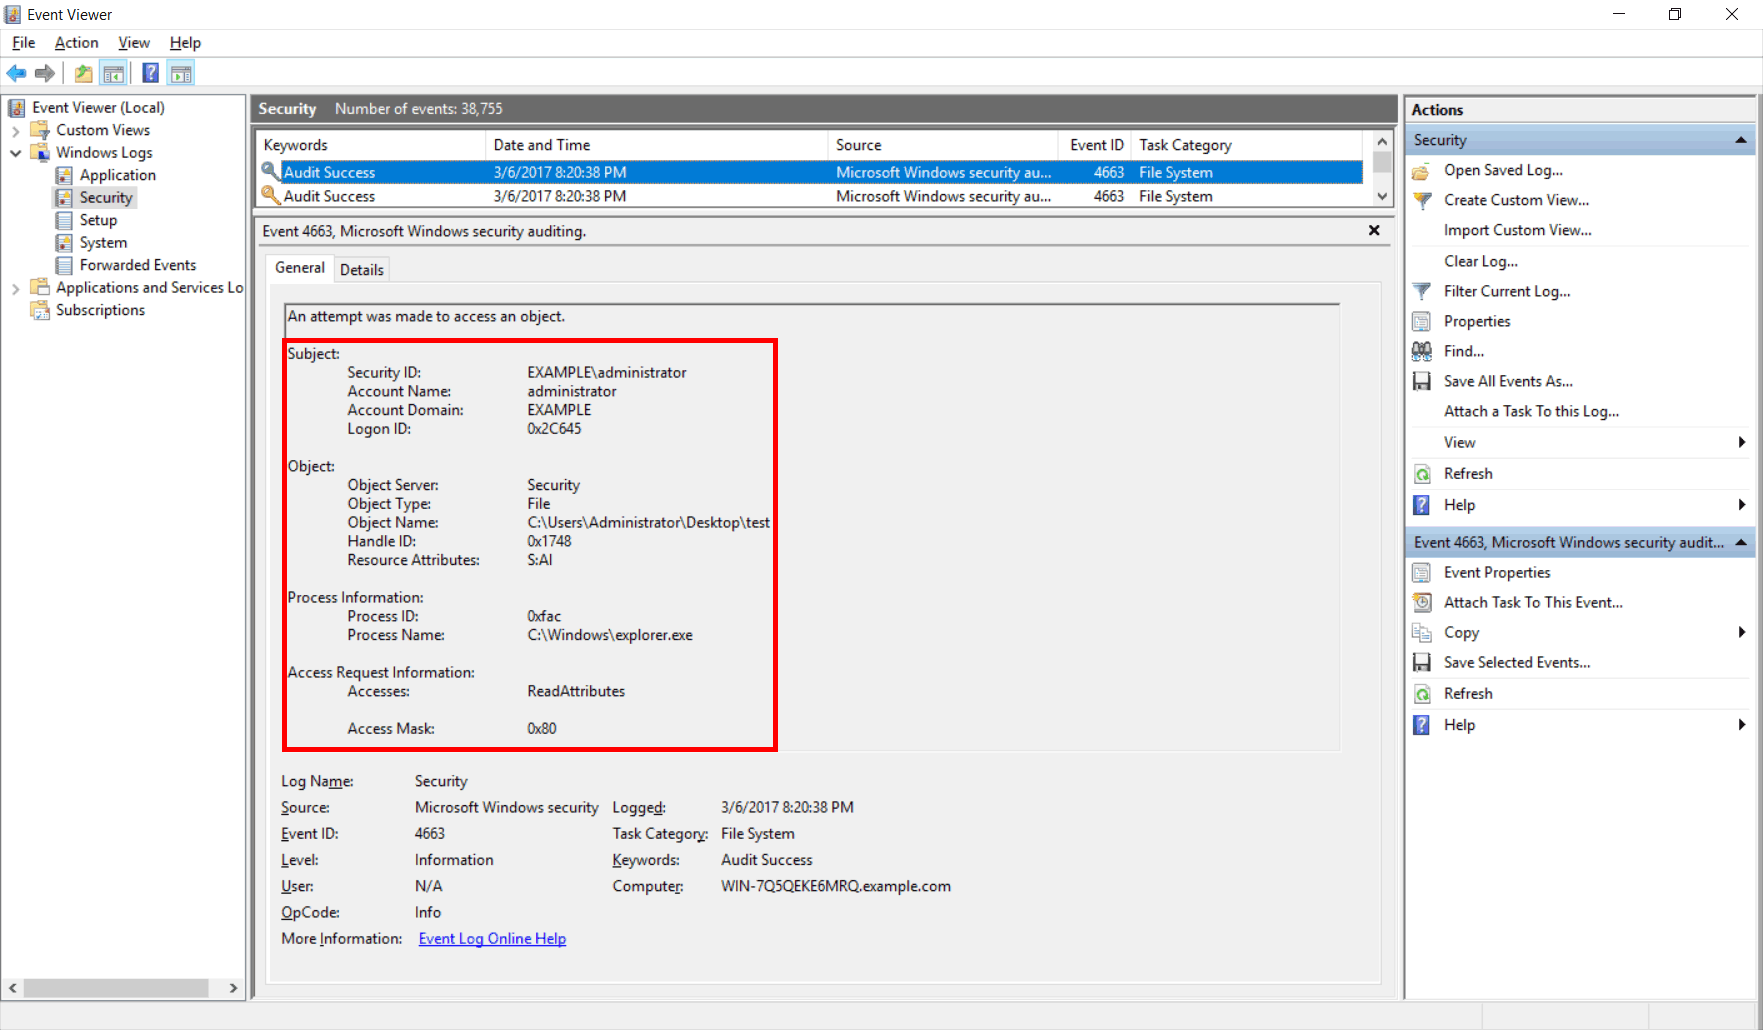
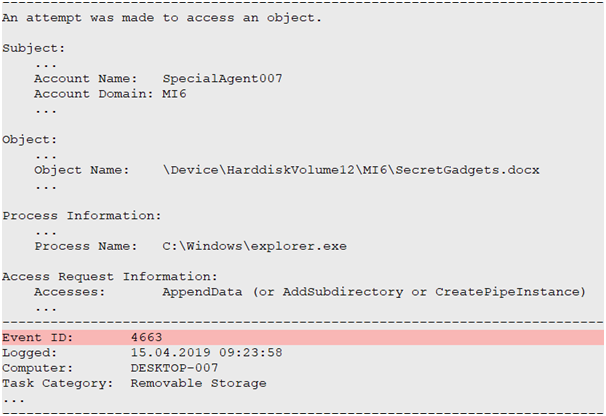
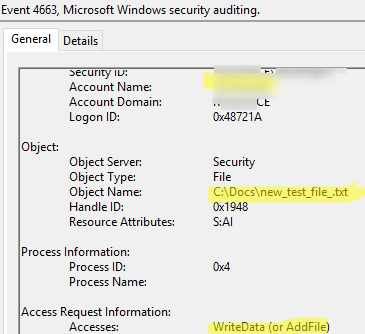
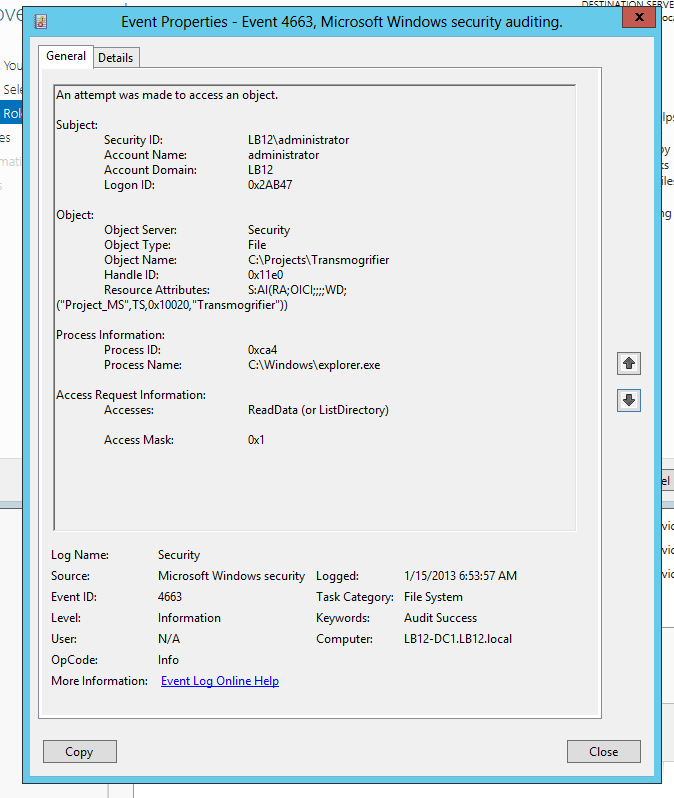
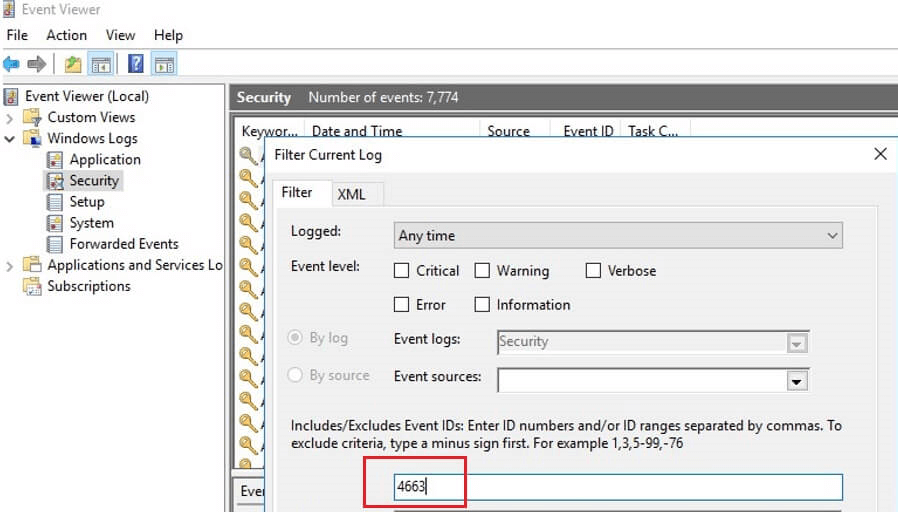
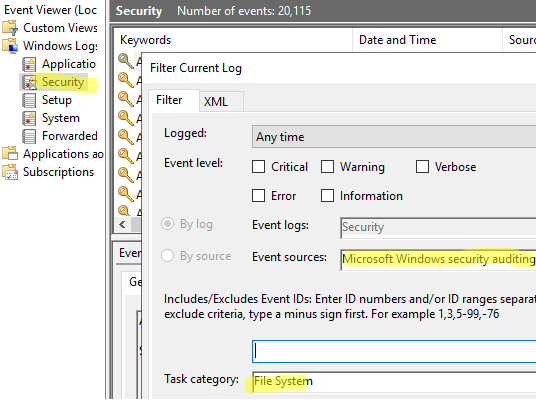
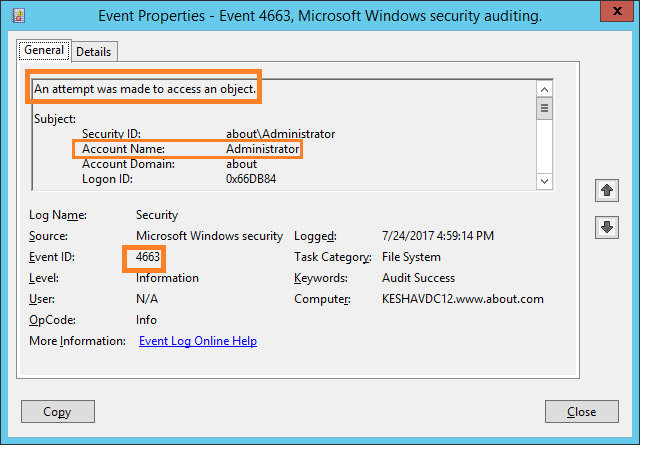
Fix: Event ID 4663, An Attempt Was Made to Access An Object
Solved: Too much event id 4663 generated for file access audit on a ...
Windows Security Fundamentals: Hands-On Lab - GeeksforGeeks
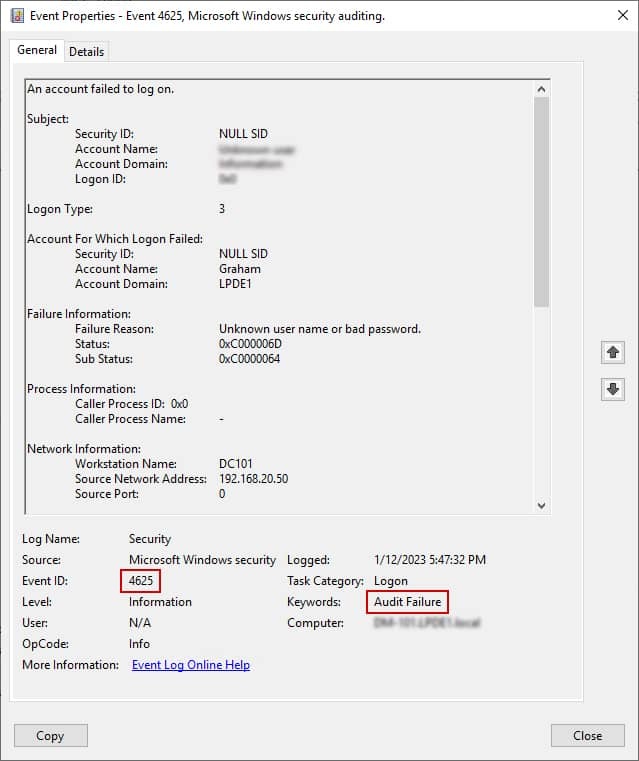
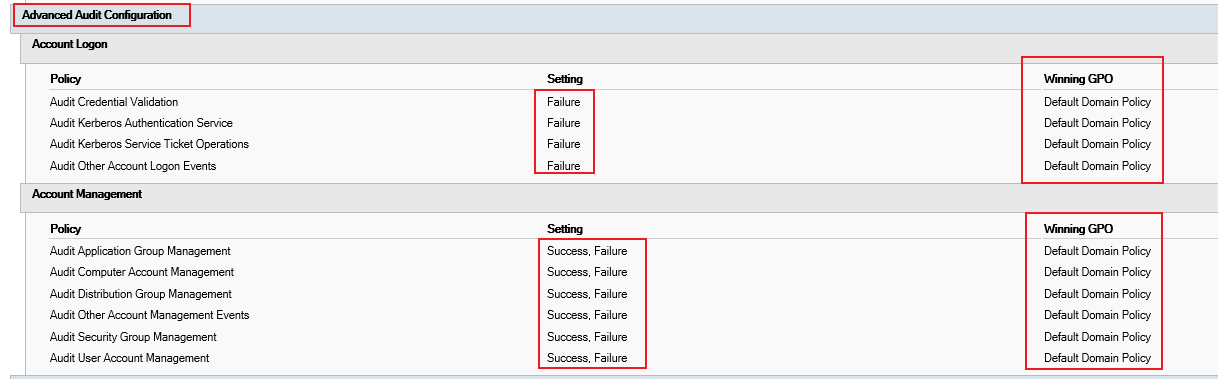
Audit Failed Logon Events or Attempts in Active Directory
What 0xc000006a - User Logon Misspelled or Bad Password
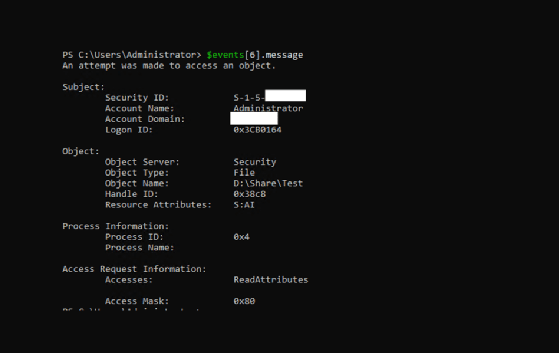
Generate a Windows file server audit via PowerShell | TechTarget
Eventos 4659, 4660 y 4663: Auditoría de Acceso a Objetos en Windows ...
Audit changes in the Windows registry – 4sysops
PPT - Chapter 14: Other Audit Events PowerPoint Presentation, free ...
Security Auditing Enhancements in Windows Server 2012 – 4sysops
security - Sources (protocols) for Audit Failures (Event ID 4625) in ...
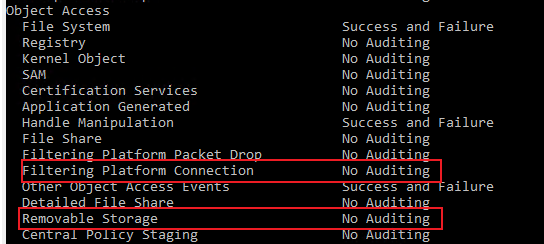
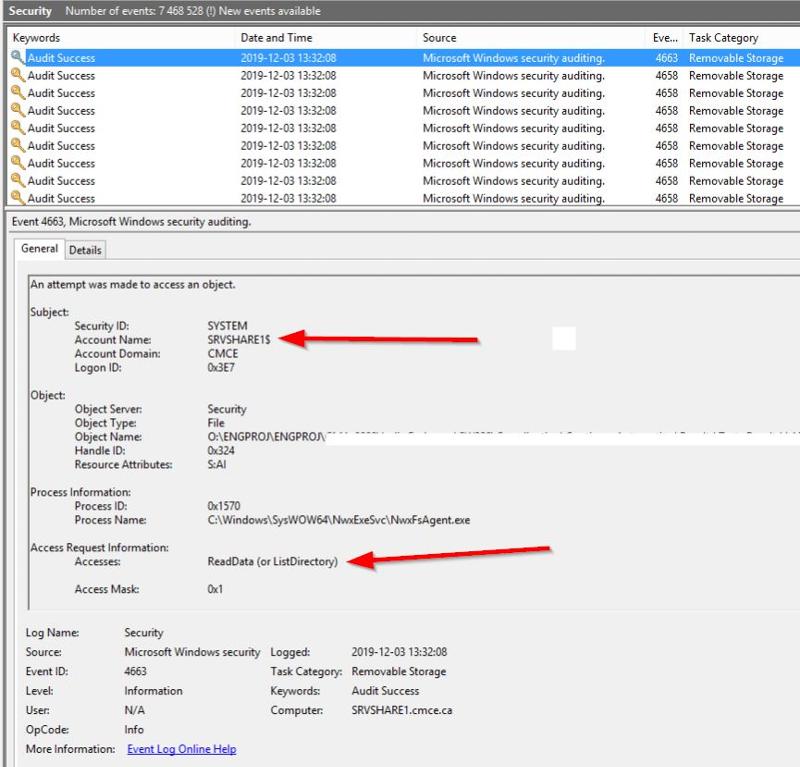
Security Event Logs Filling With Removable Storage (4658 & 4663) and ...
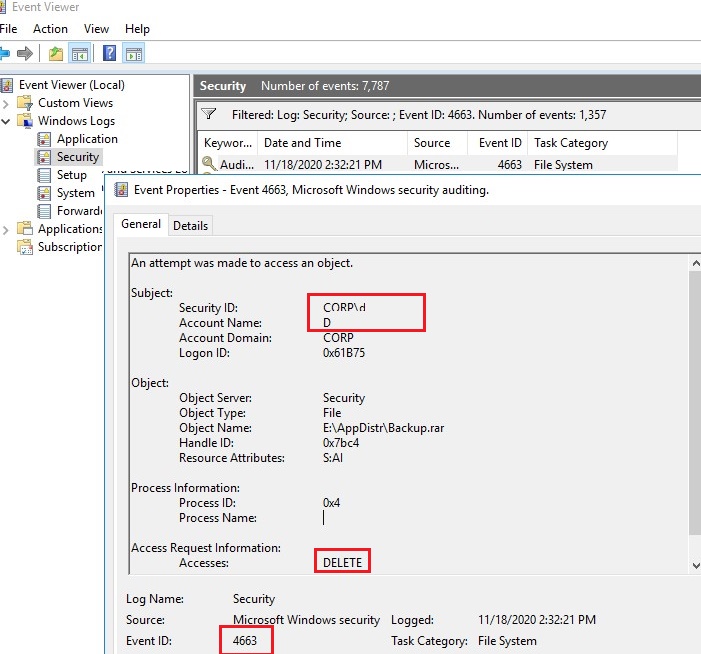
How to Detect Who Deleted a File on Windows Server with Audit Policy ...
SecuritySynapse: Monitoring USB Storage Activity with Splunk – Part II ...
How To Detect File Changes in Windows Server | Blumira
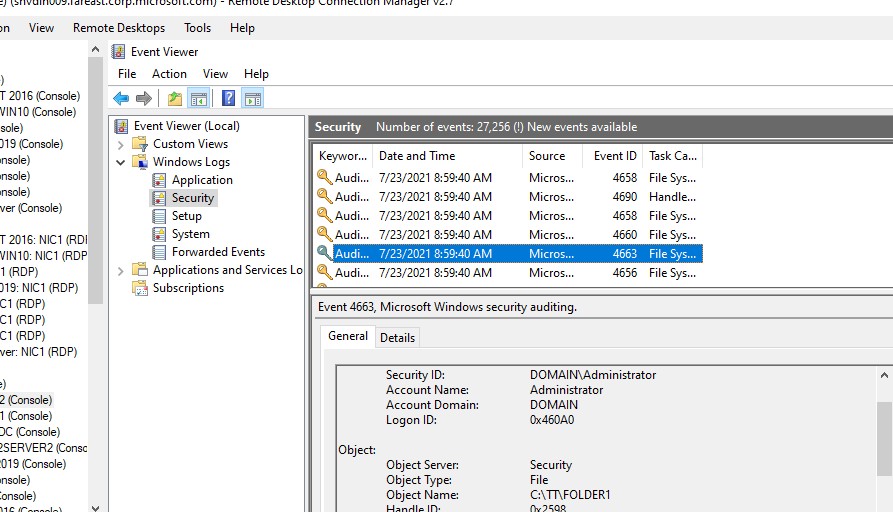
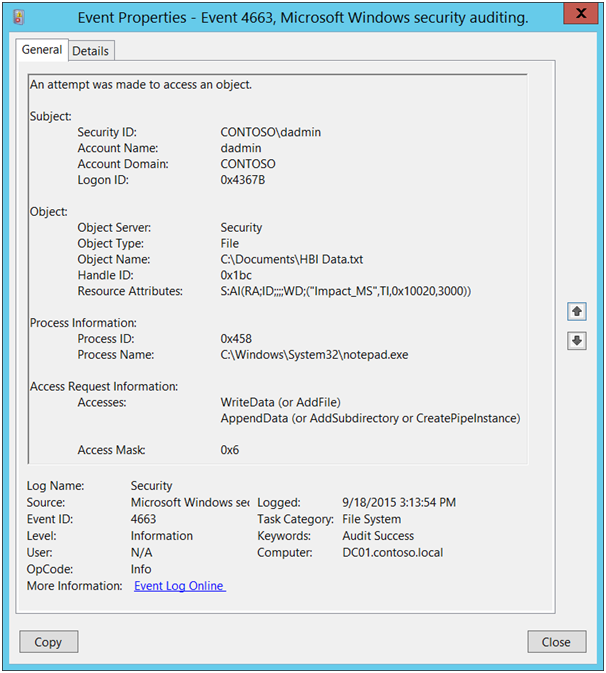
4663(S) An attempt was made to access an object. - Windows 10 ...
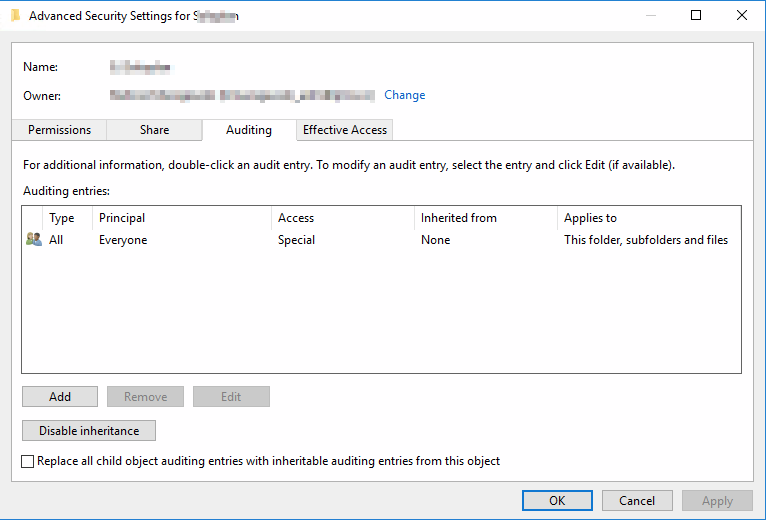
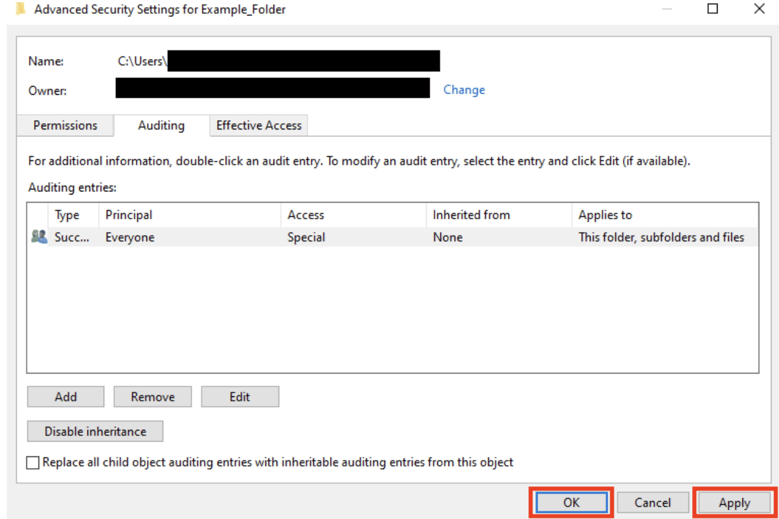
How to configure file and folder access auditing in Windows
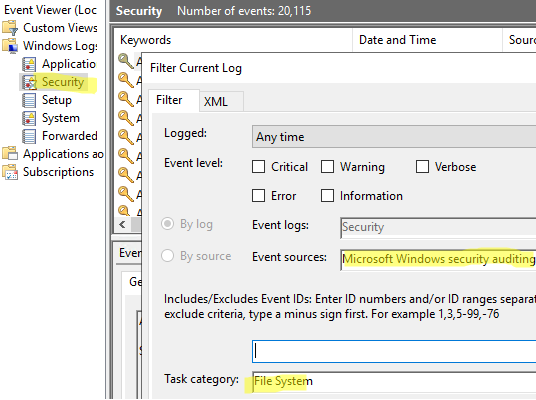
Configure File and Folder Access Auditing on Windows (GPO) | Windows OS Hub
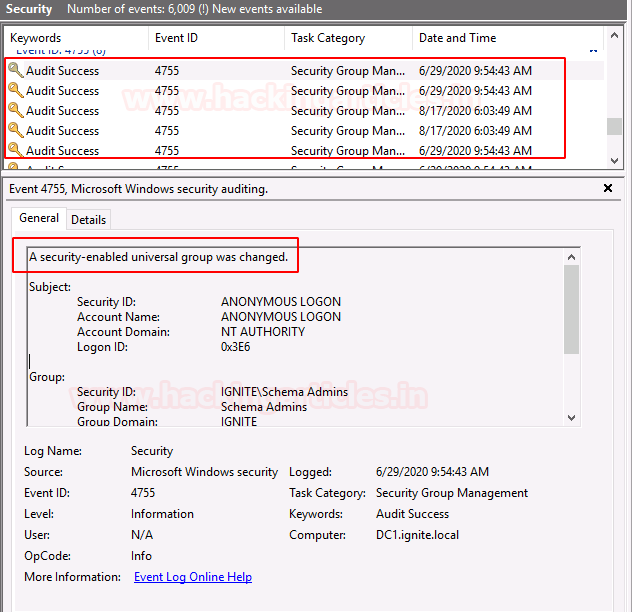
Incident Response: Windows Account Management Event (Part 2) - Hacking ...
4658(S) The handle to an object was closed. - Windows 10 | Microsoft Learn
Windows Attack and Defense - Credentials in Object Properties - Academy ...
Windows Security Log Event ID 4663 - An attempt was made to access an ...
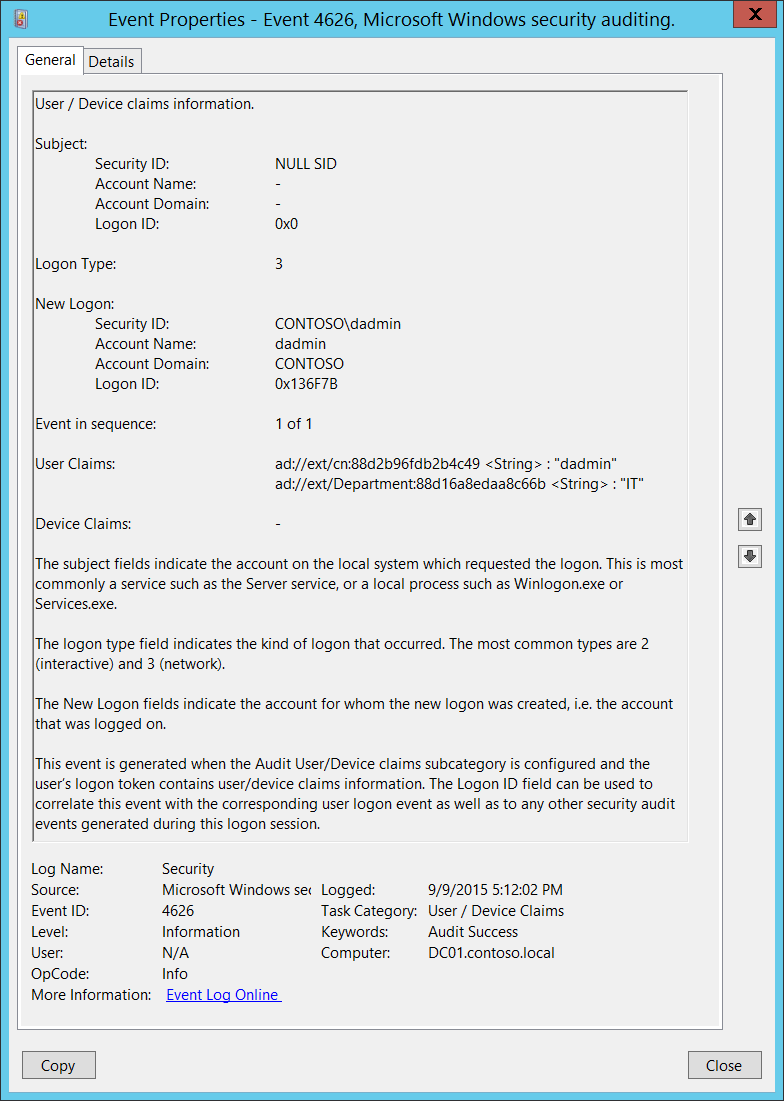
4626(S) User/Device claims information. - Windows 10 | Microsoft Learn
Auditing object deletions - Microsoft Q&A
Auditing files on Windows Server
Configure File Access Auditing in Windows Server 2016 - RootUsers
Tons of 4625 and 4634 events - Microsoft Q&A
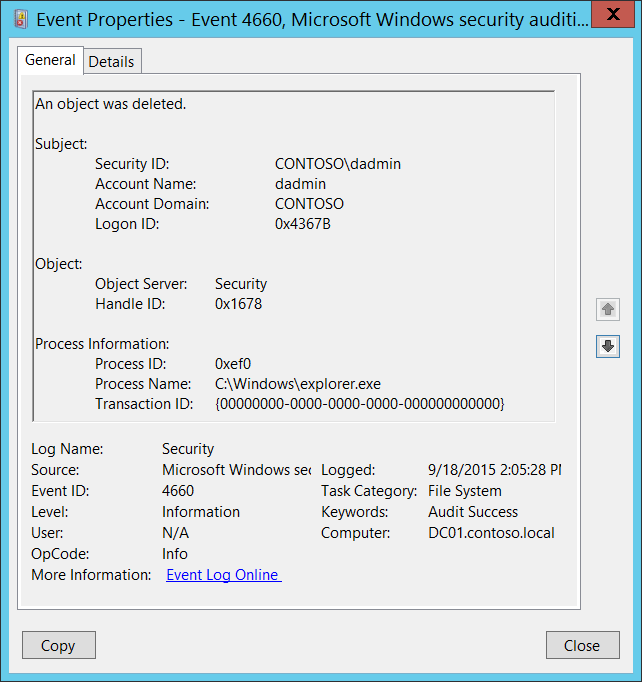
4660(S) An object was deleted. - Windows 10 | Microsoft Learn
How to Audit Permission Changes on File Servers
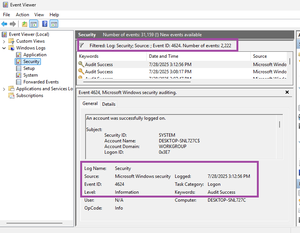
How to Check Active Directory Audit Logs in Event Viewer
Windows Event Logs & Finding Evil Course | HTB Academy
windows - I am continuously getting Audit Failure on the computer. Does ...
Event ID 4663 -Occurrence , Log fields Explanation & Use cases ...
Something Wrong with 4625 AuditLog - Microsoft Q&A
Auditing AD administrators with Windows 2008 R2's Event Viewer | TechTarget
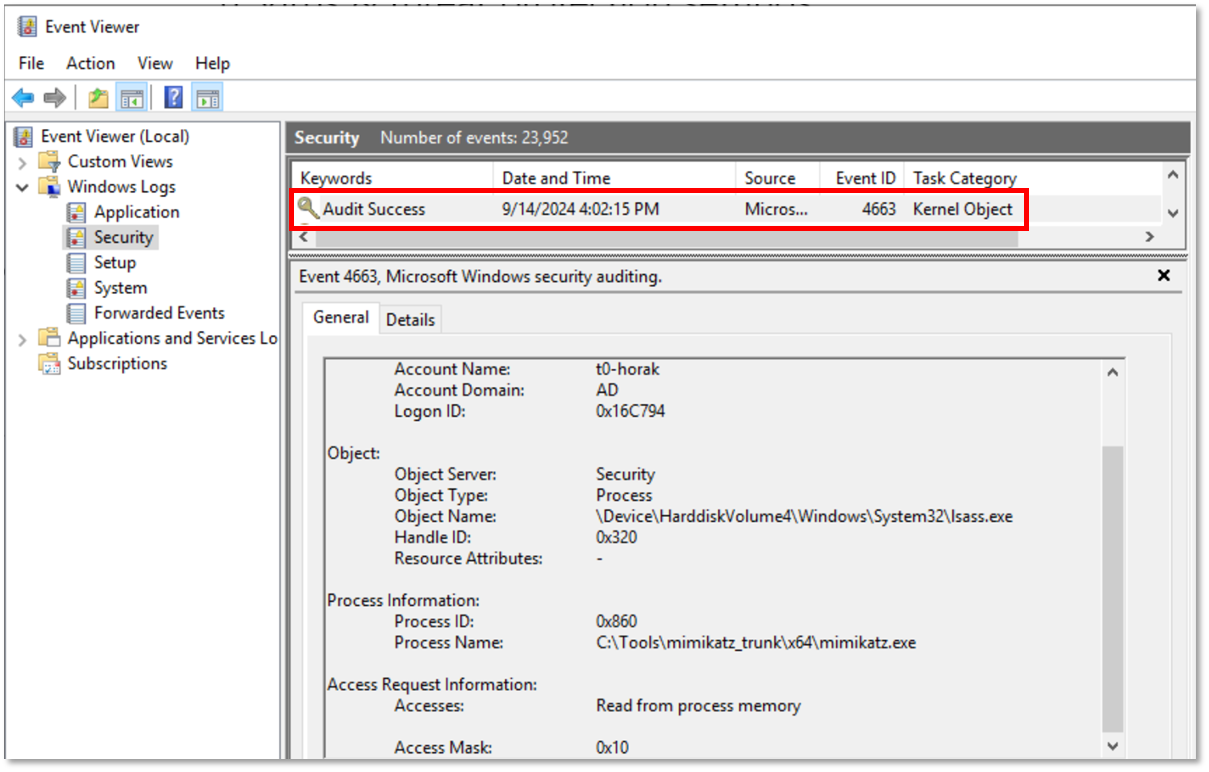
Protecting Cached Credentials with Advanced Auditing
How to use Security Auditing to track which Computer has accessed a ...
How to Detect Who Modified Permissions to an Organizational Unit ...
4776(S, F) The computer attempted to validate the credentials for an ...
How to Track File Access, Modify and Delete Actions in Windows Folder
How to audit process tracking | ManageEngine ADAudit Plus
SAM-4656 - Temperatura Corporal Fiebre - SRProSecure
Deceptive-Auditing: An Active Directory Honeypots Tool - Black Hills ...
Unlocking Active Directory User Accounts | Windows OS Hub
Windows Event Log Analysis - Incident Response Guide
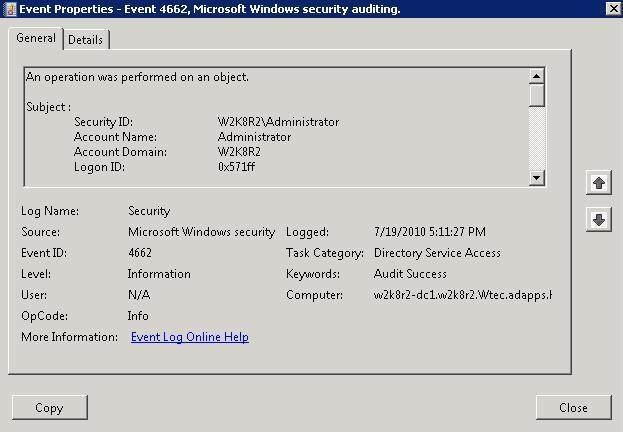
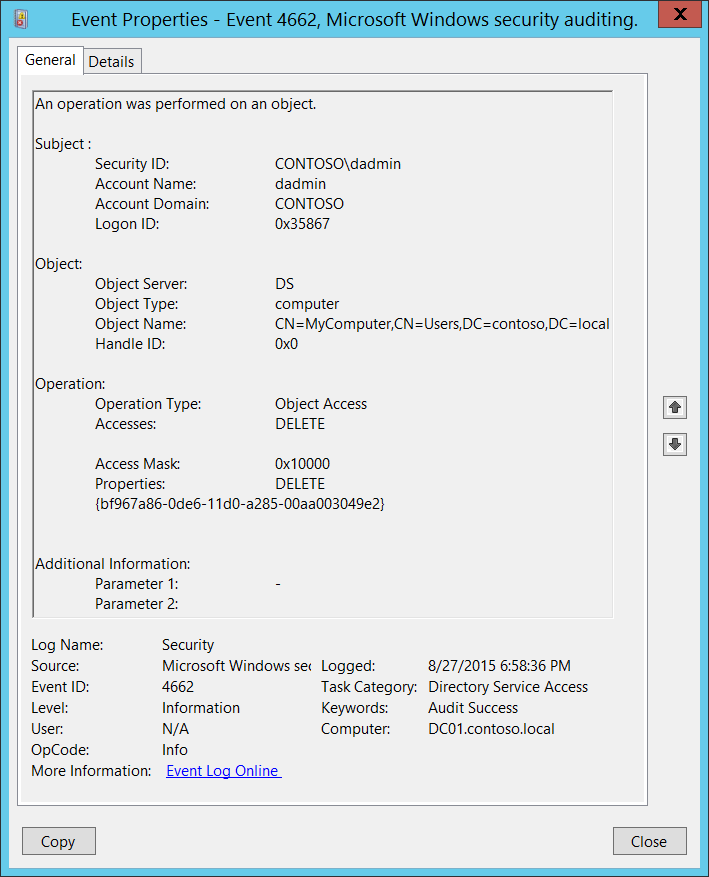
4662(S, F) An operation was performed on an object. - Windows 10 ...
4661(S, F) A handle to an object was requested. - Windows 10 ...
4674(S, F) An operation was attempted on a privileged object. - Windows ...
Problems with folder auditing - Microsoft Q&A
Blog
How to Detect Who Deleted a File on Windows Server with Audit Policy?
4690(S) An attempt was made to duplicate a handle to an object ...
How to Audit File or Folder Deletion in Windows Server?
4906(S) The CrashOnAuditFail value has changed. - Windows 10 ...
How to Audit Failed Access Attempts to a Shared Folder | ADAudit Plus