Showing 120 of 120on this page. Filters & sort apply to loaded results; URL updates for sharing.120 of 120 on this page
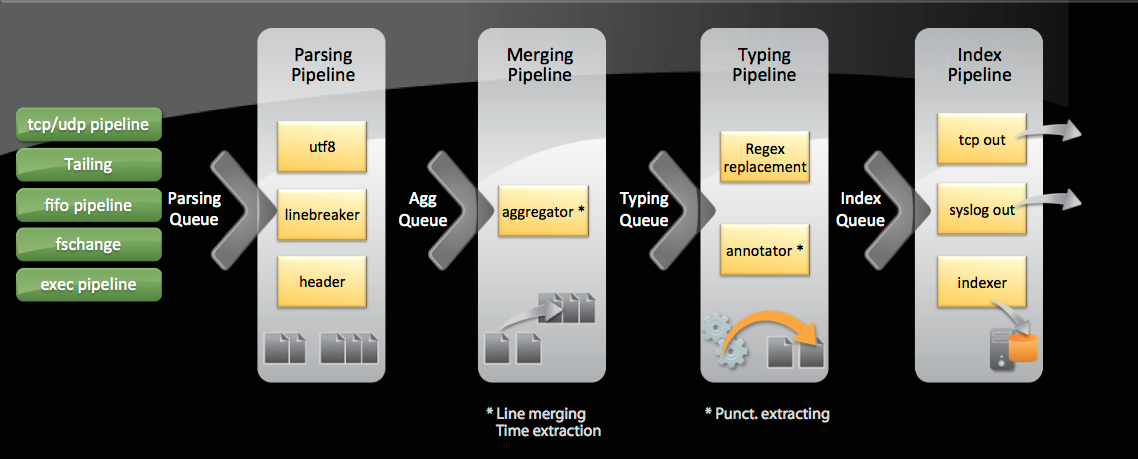
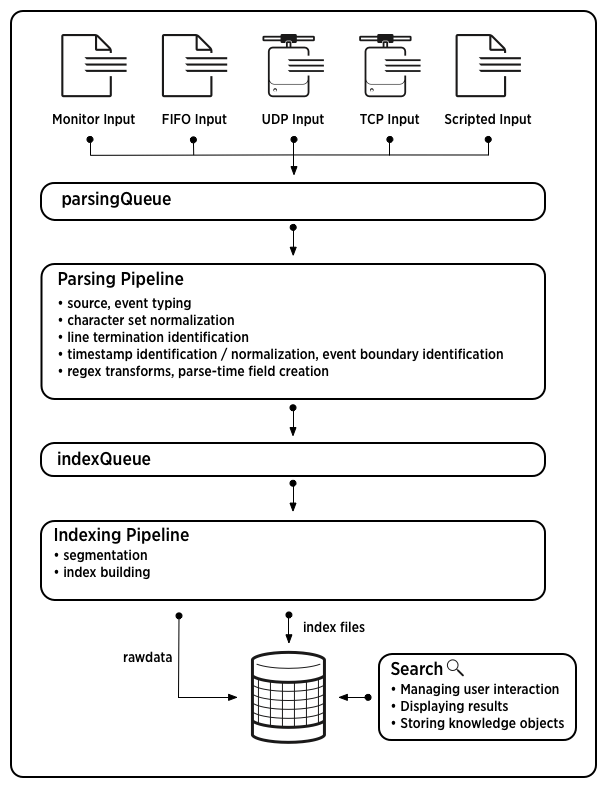
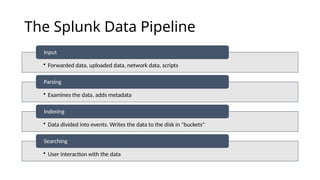
Splunk Data Input Pipeline and Processors | Function1
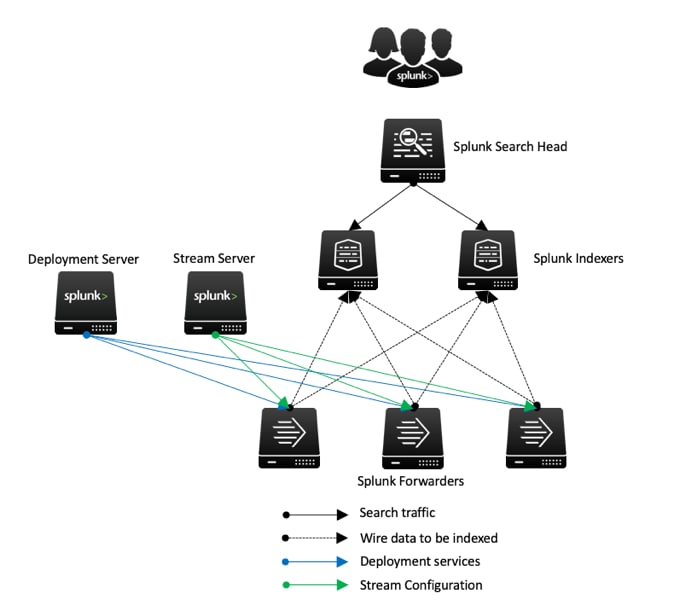
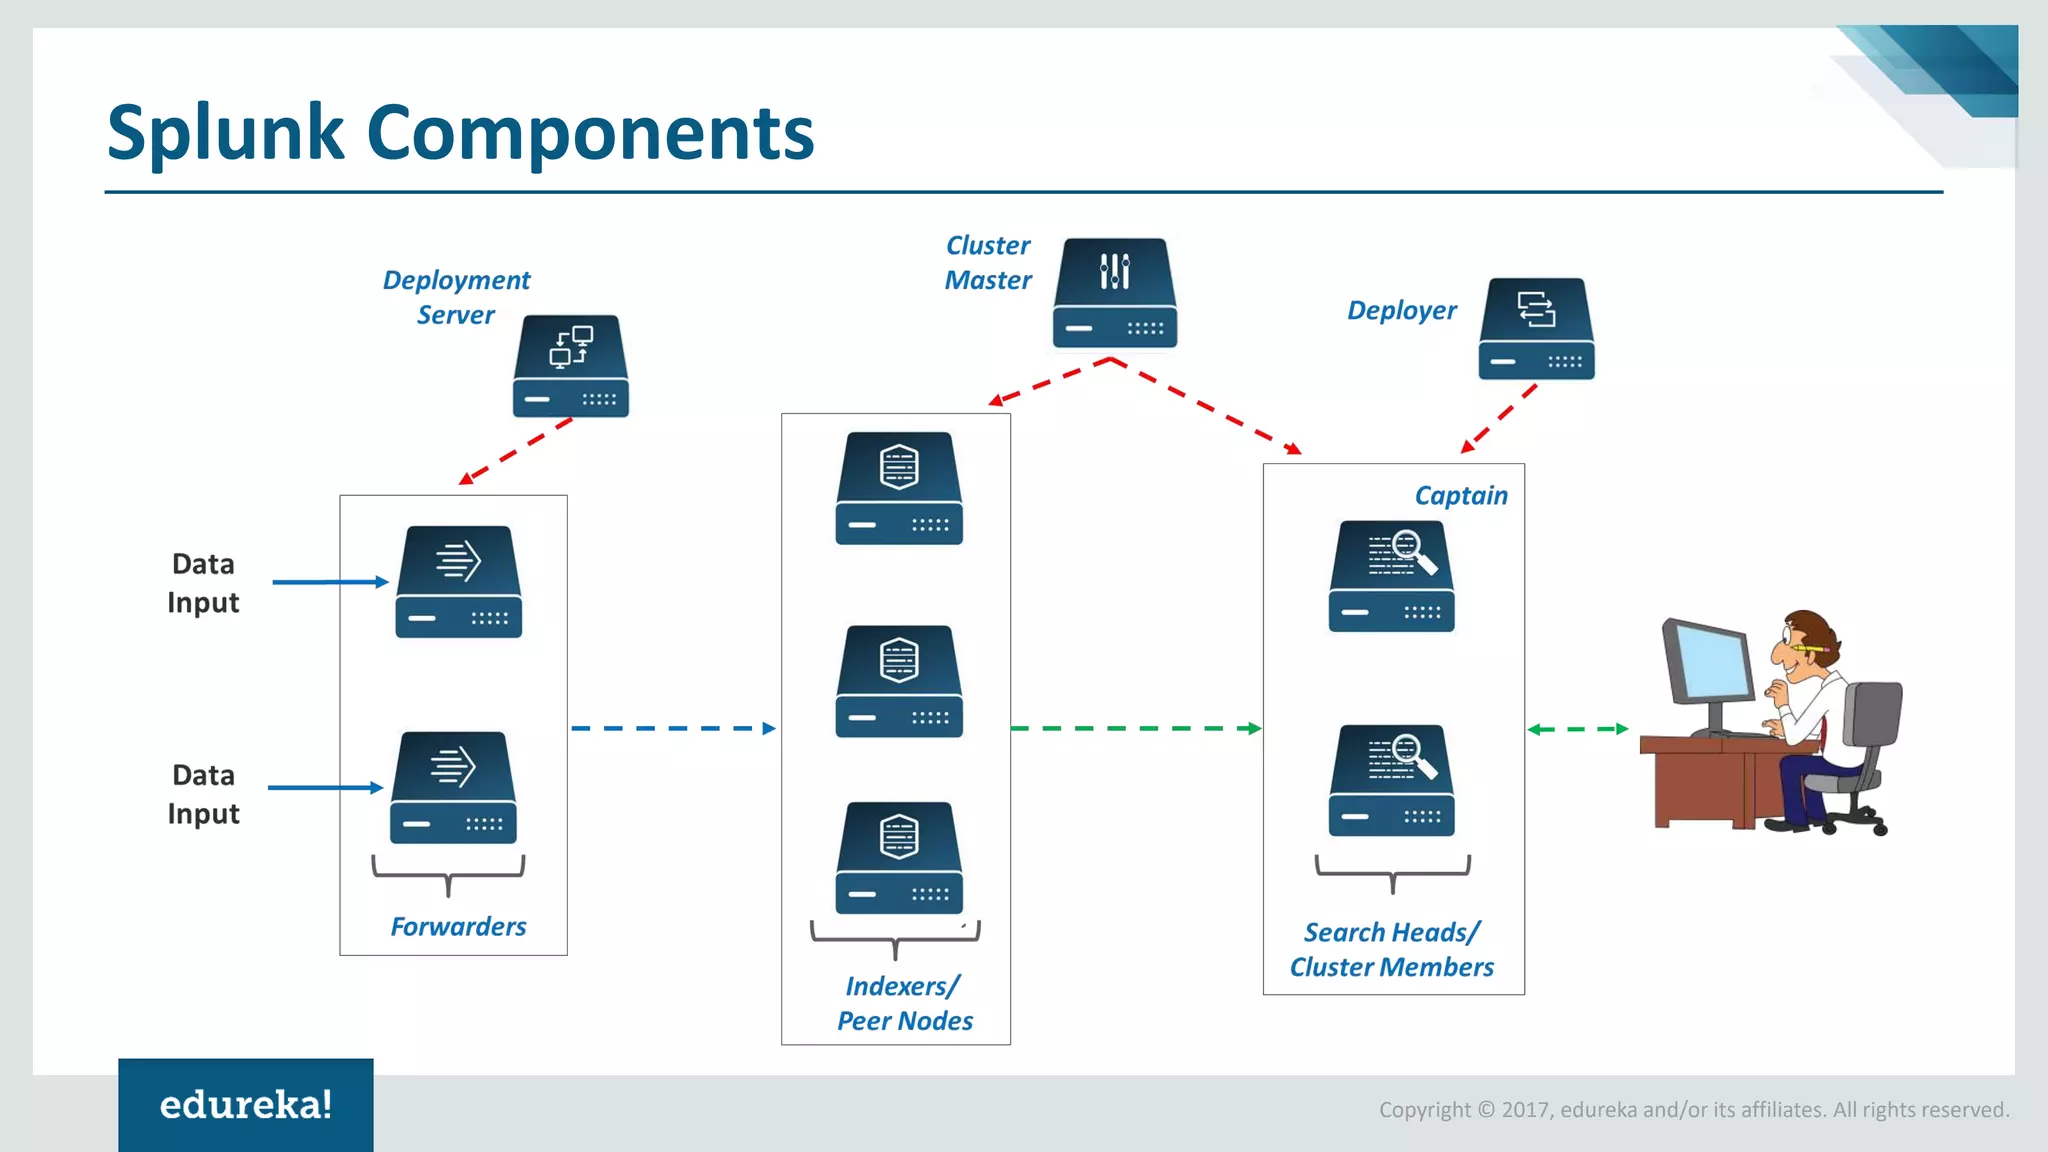
Splunk Data Flow: From Forwarder Input to Search Head Results ...
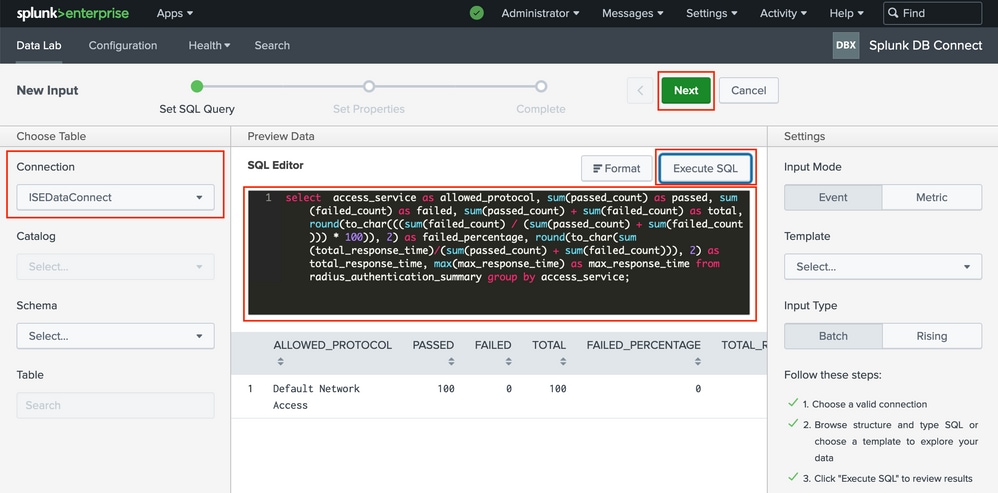
Configure ISE 3.2 Data Connect Integration with Splunk - Cisco
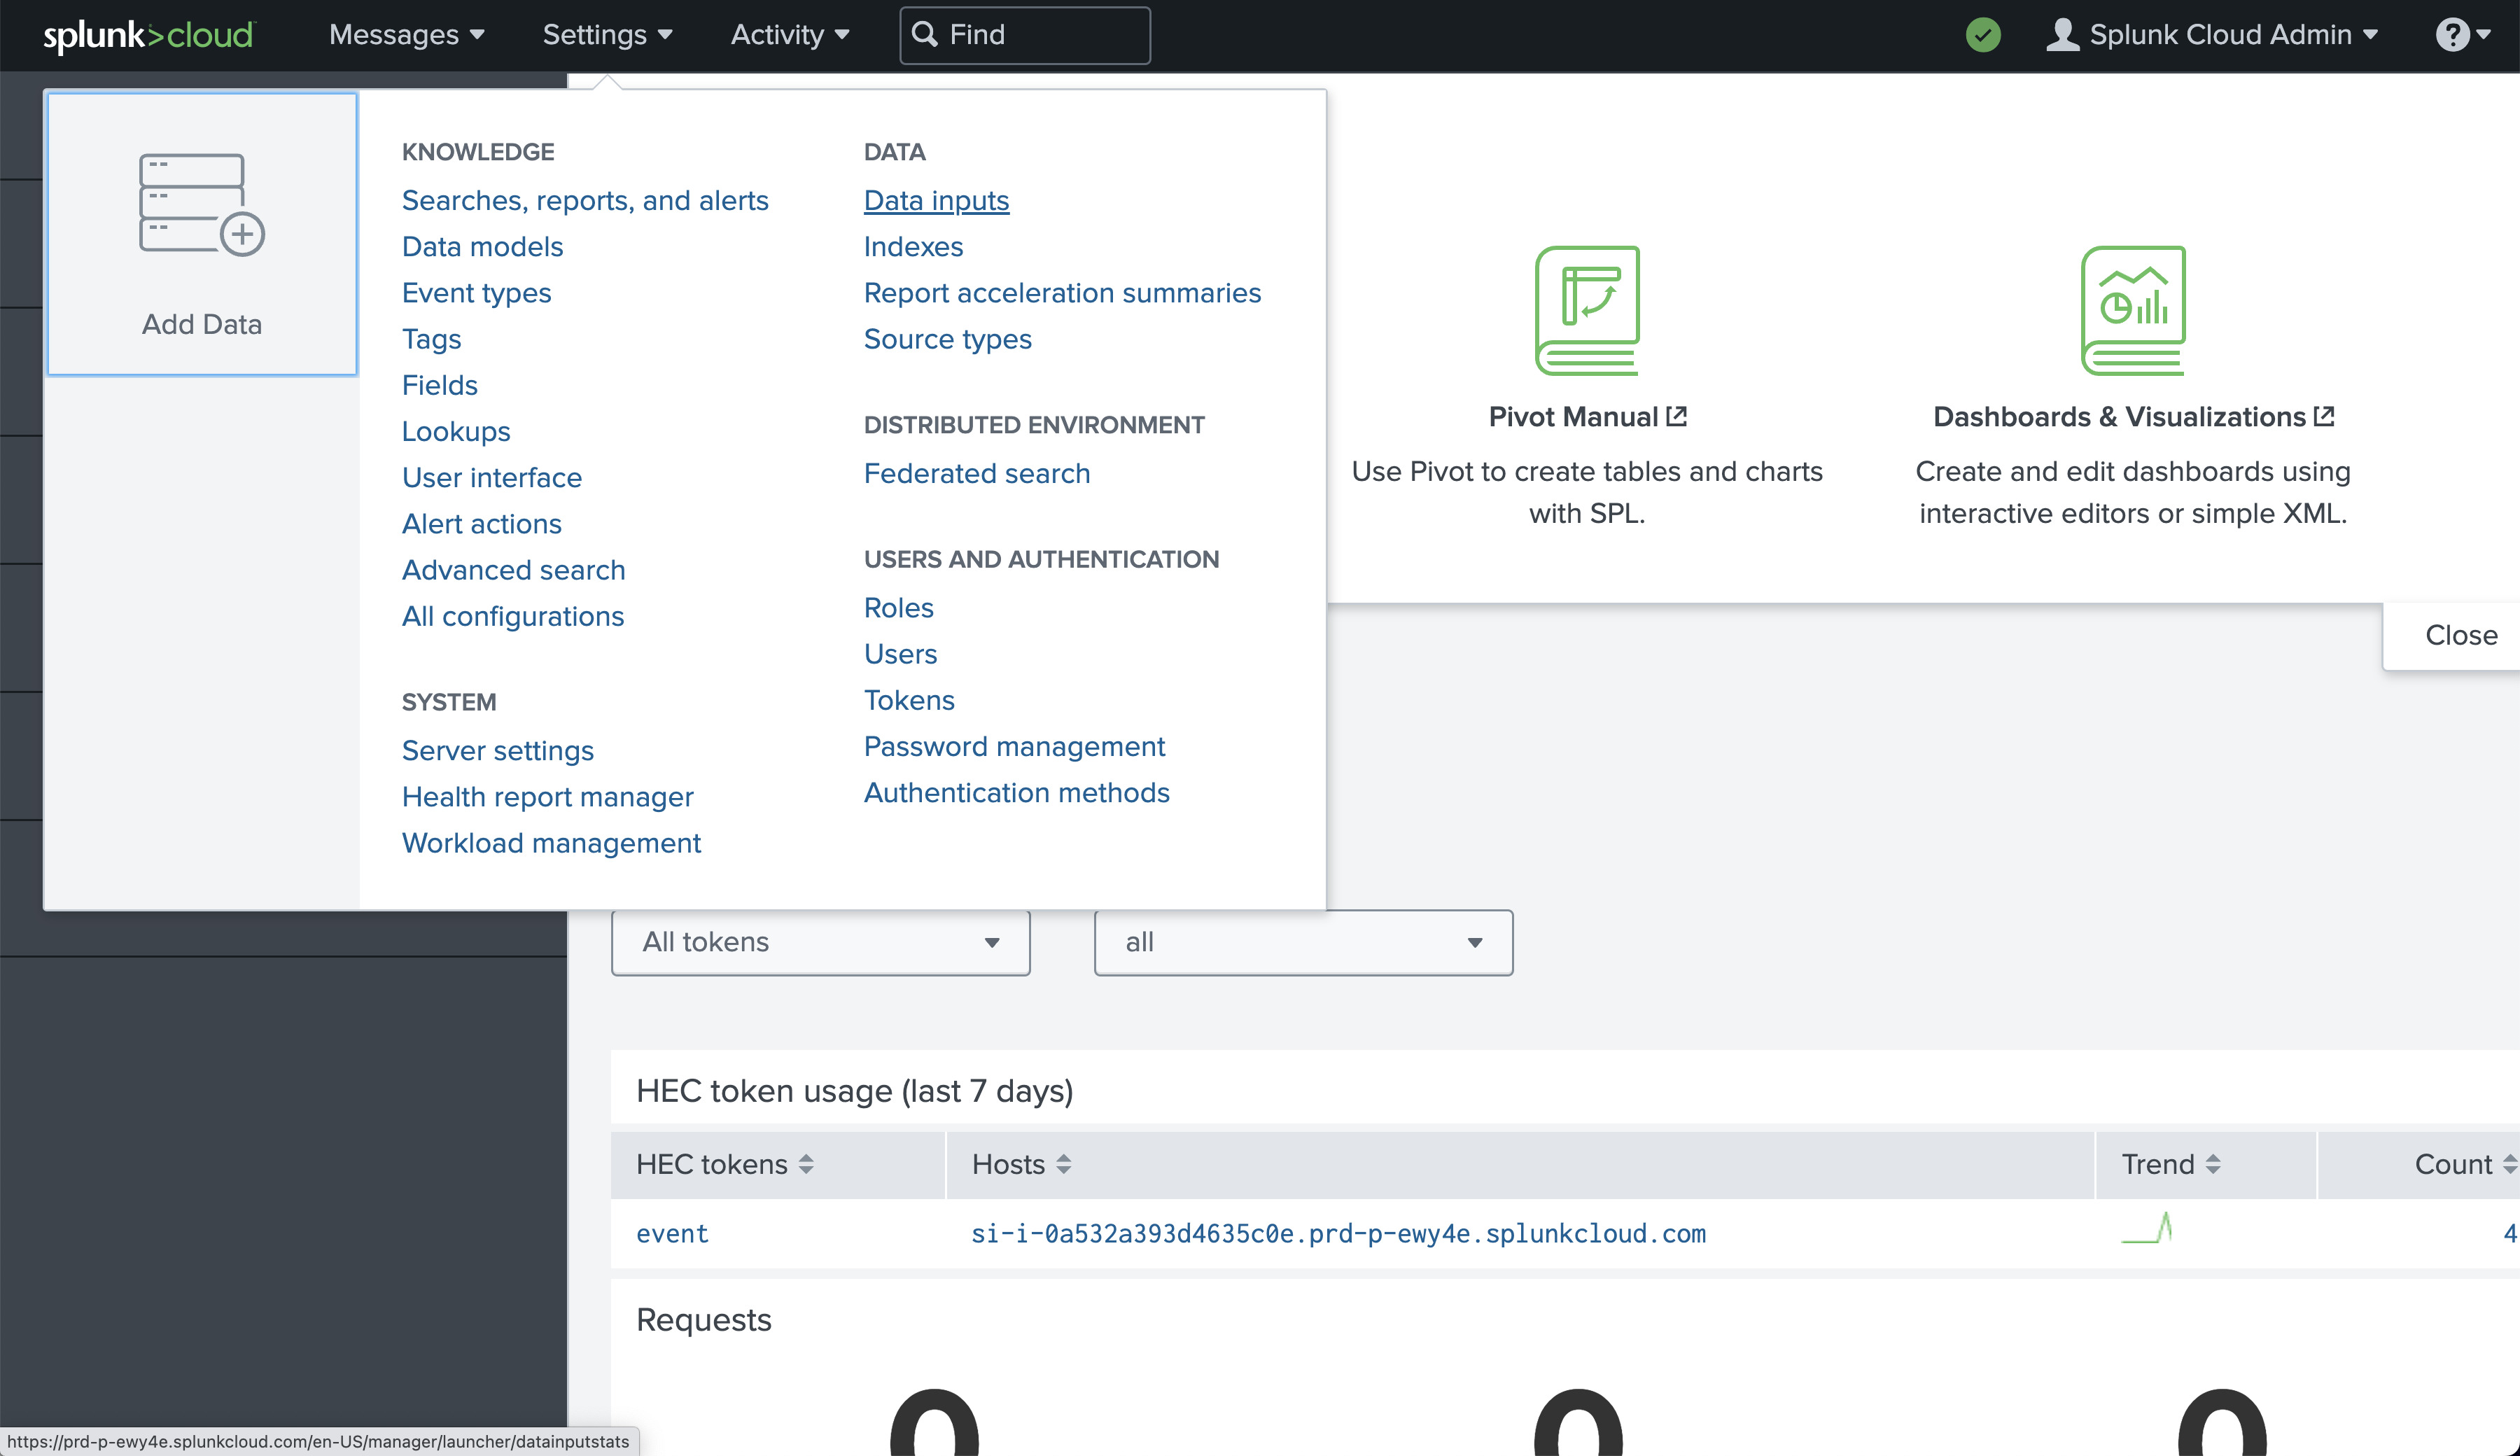
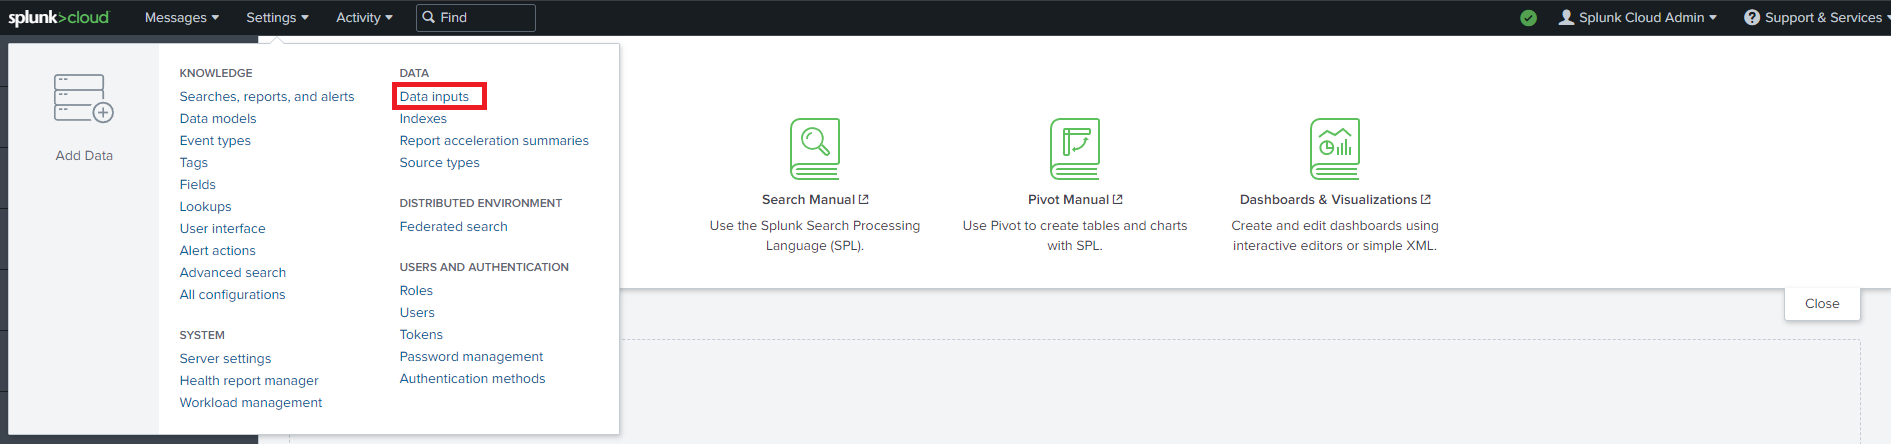
Introducing Inputs Data Manager on Splunk Cloud | Splunk
API Data Input | Splunkbase
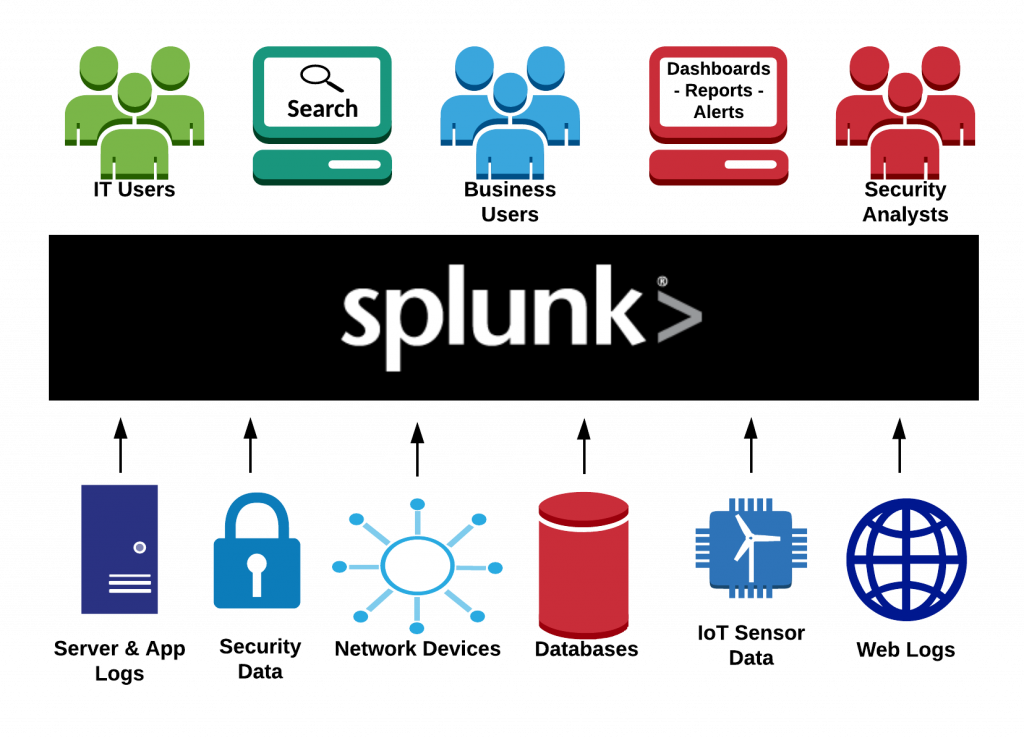
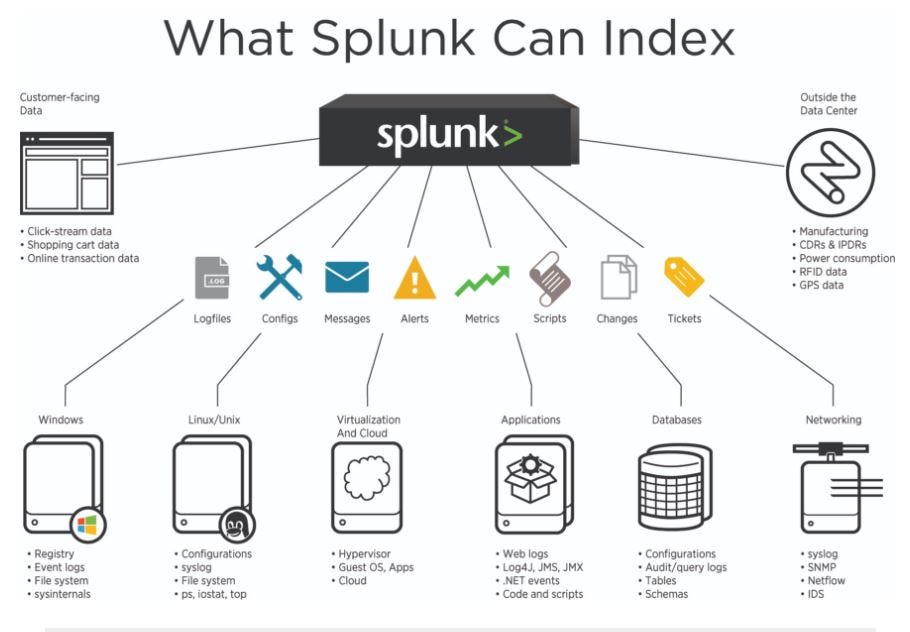
Splunk Data Ingestion - Tpoint Tech
Upload the tutorial data - Splunk Documentation
Splunk Data Ingestion Methods: Made Easy 101 - Learn | Hevo
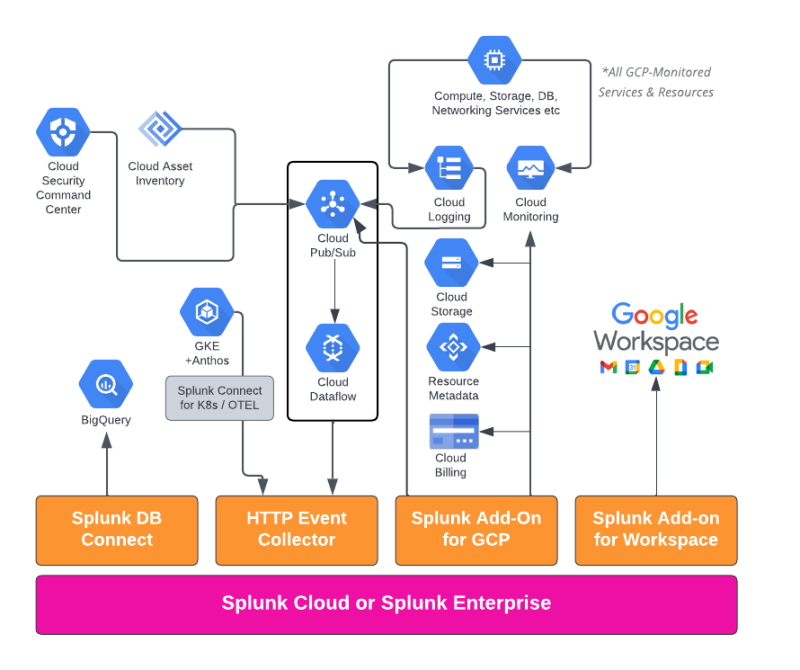
Getting Google Cloud Platform data into the Splunk platform - Splunk ...
Migrating AWS inputs to Data Manager - Splunk Lantern
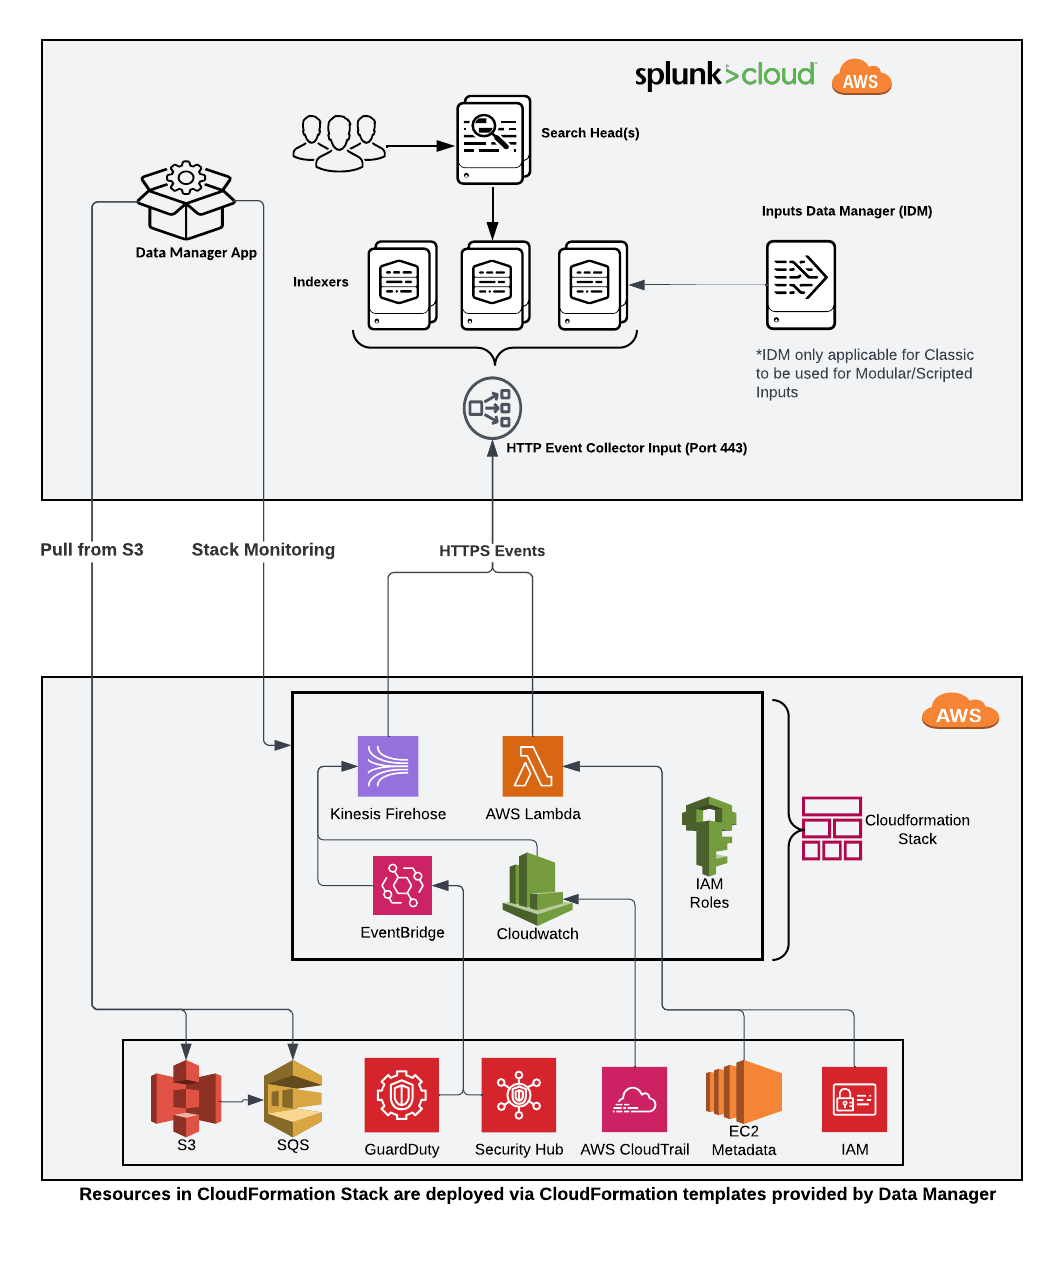
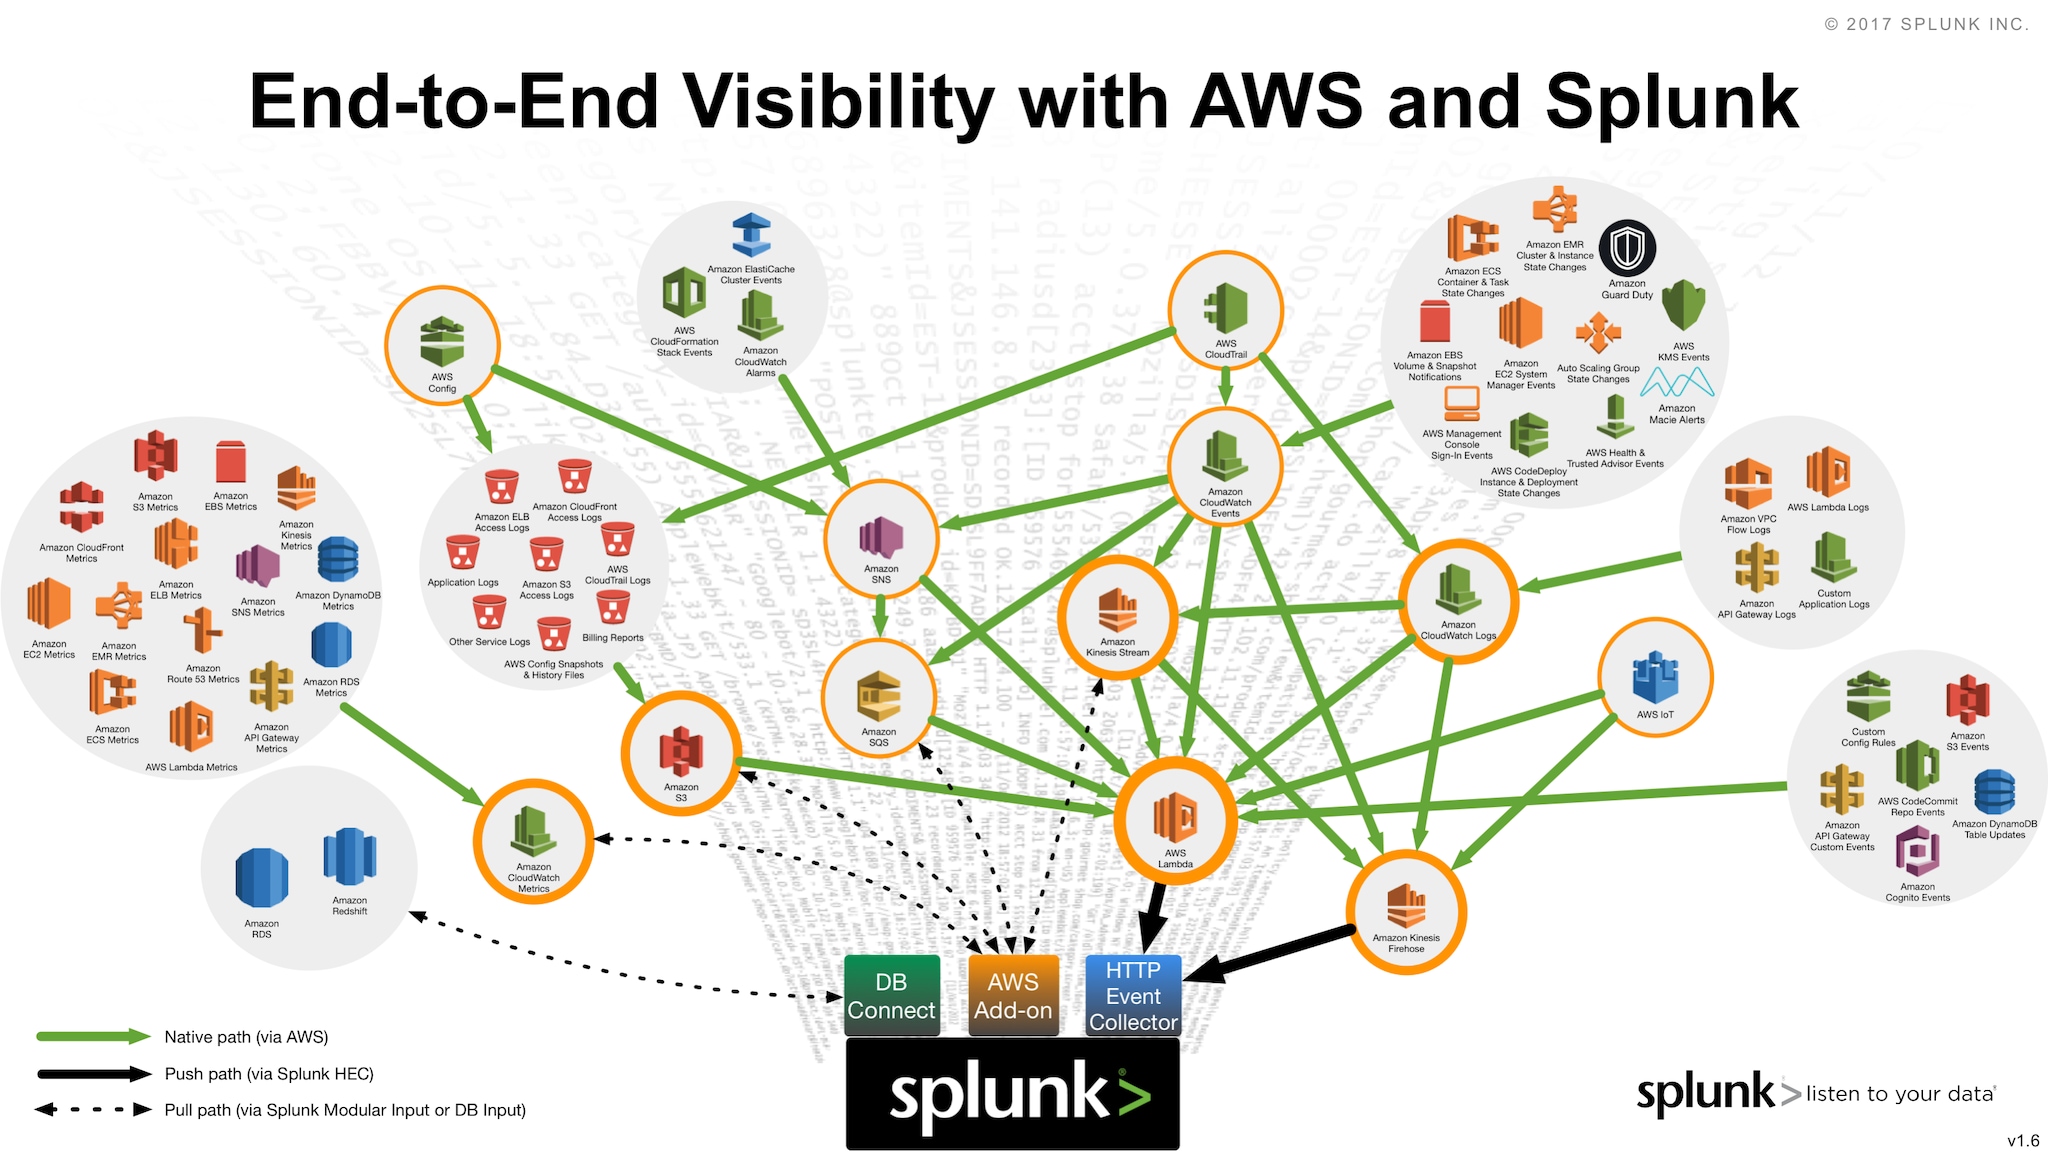
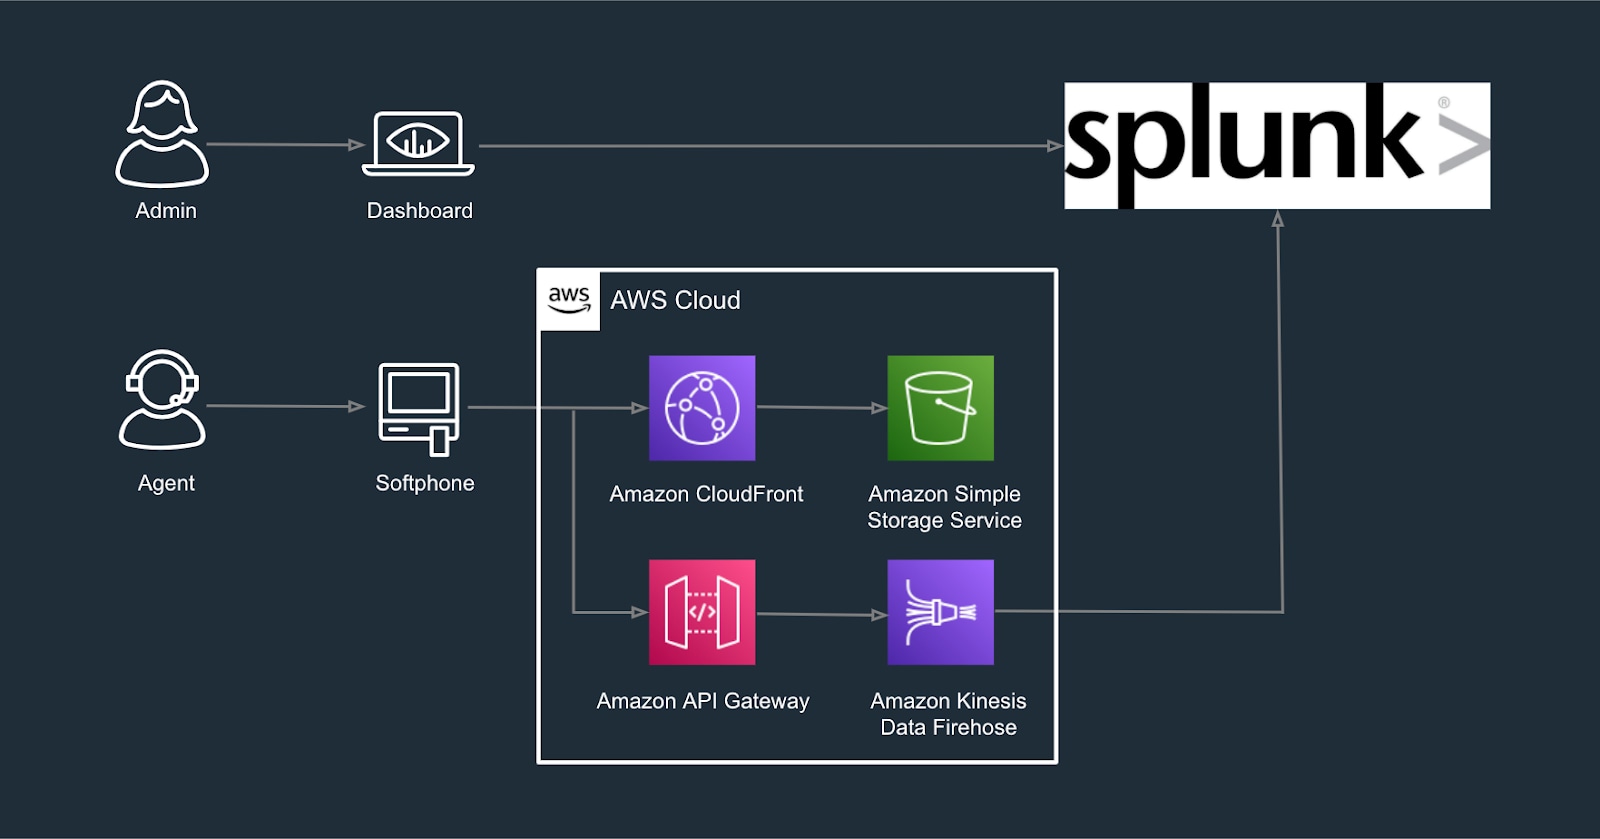
Getting AWS data into the Splunk platform - Splunk Documentation
An easy way to generate sample data | Splunk
BugSnag docs › Product › Integrations › Data forwarding › Splunk
Chapter 8: Getting Data In | Splunk 9.x Enterprise Certified Admin Guide
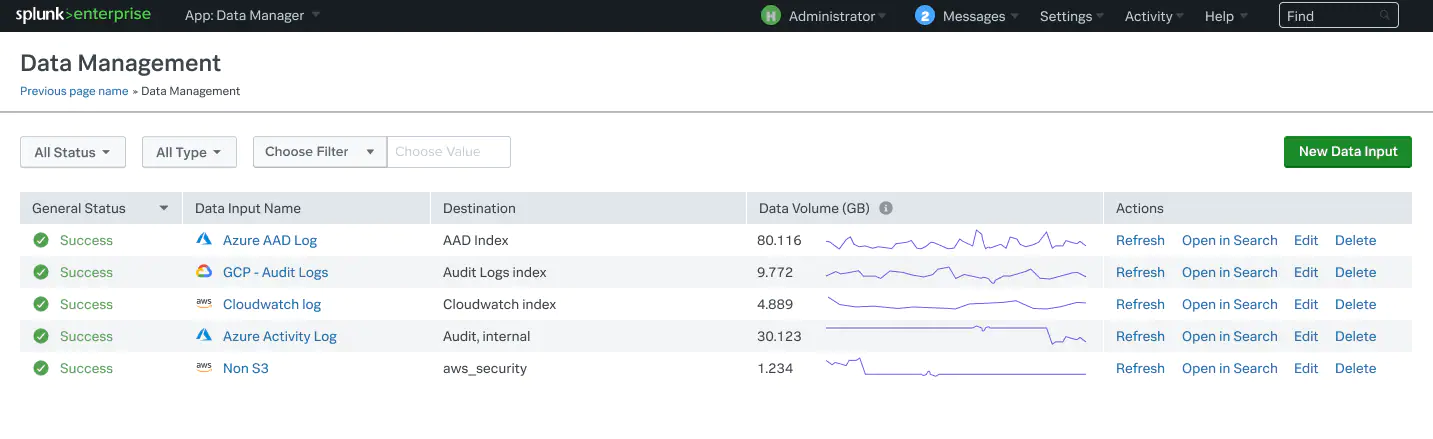
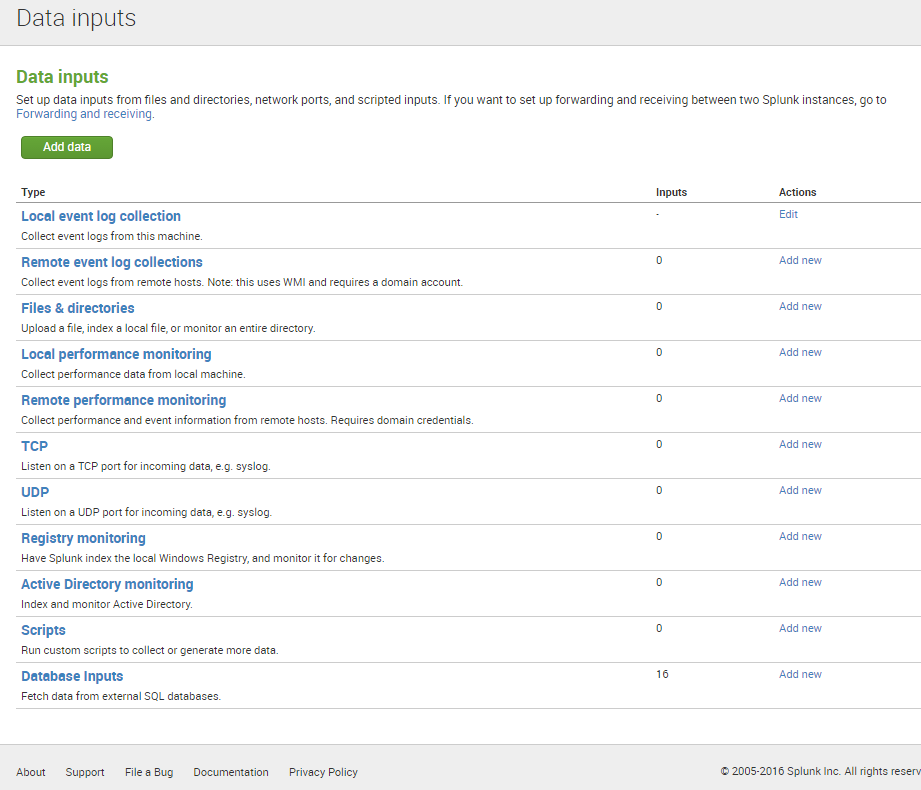
Splunk Data Integration - Getting Data Into Splunk
Configuration parameters and the data pipeline - Splunk Documentation
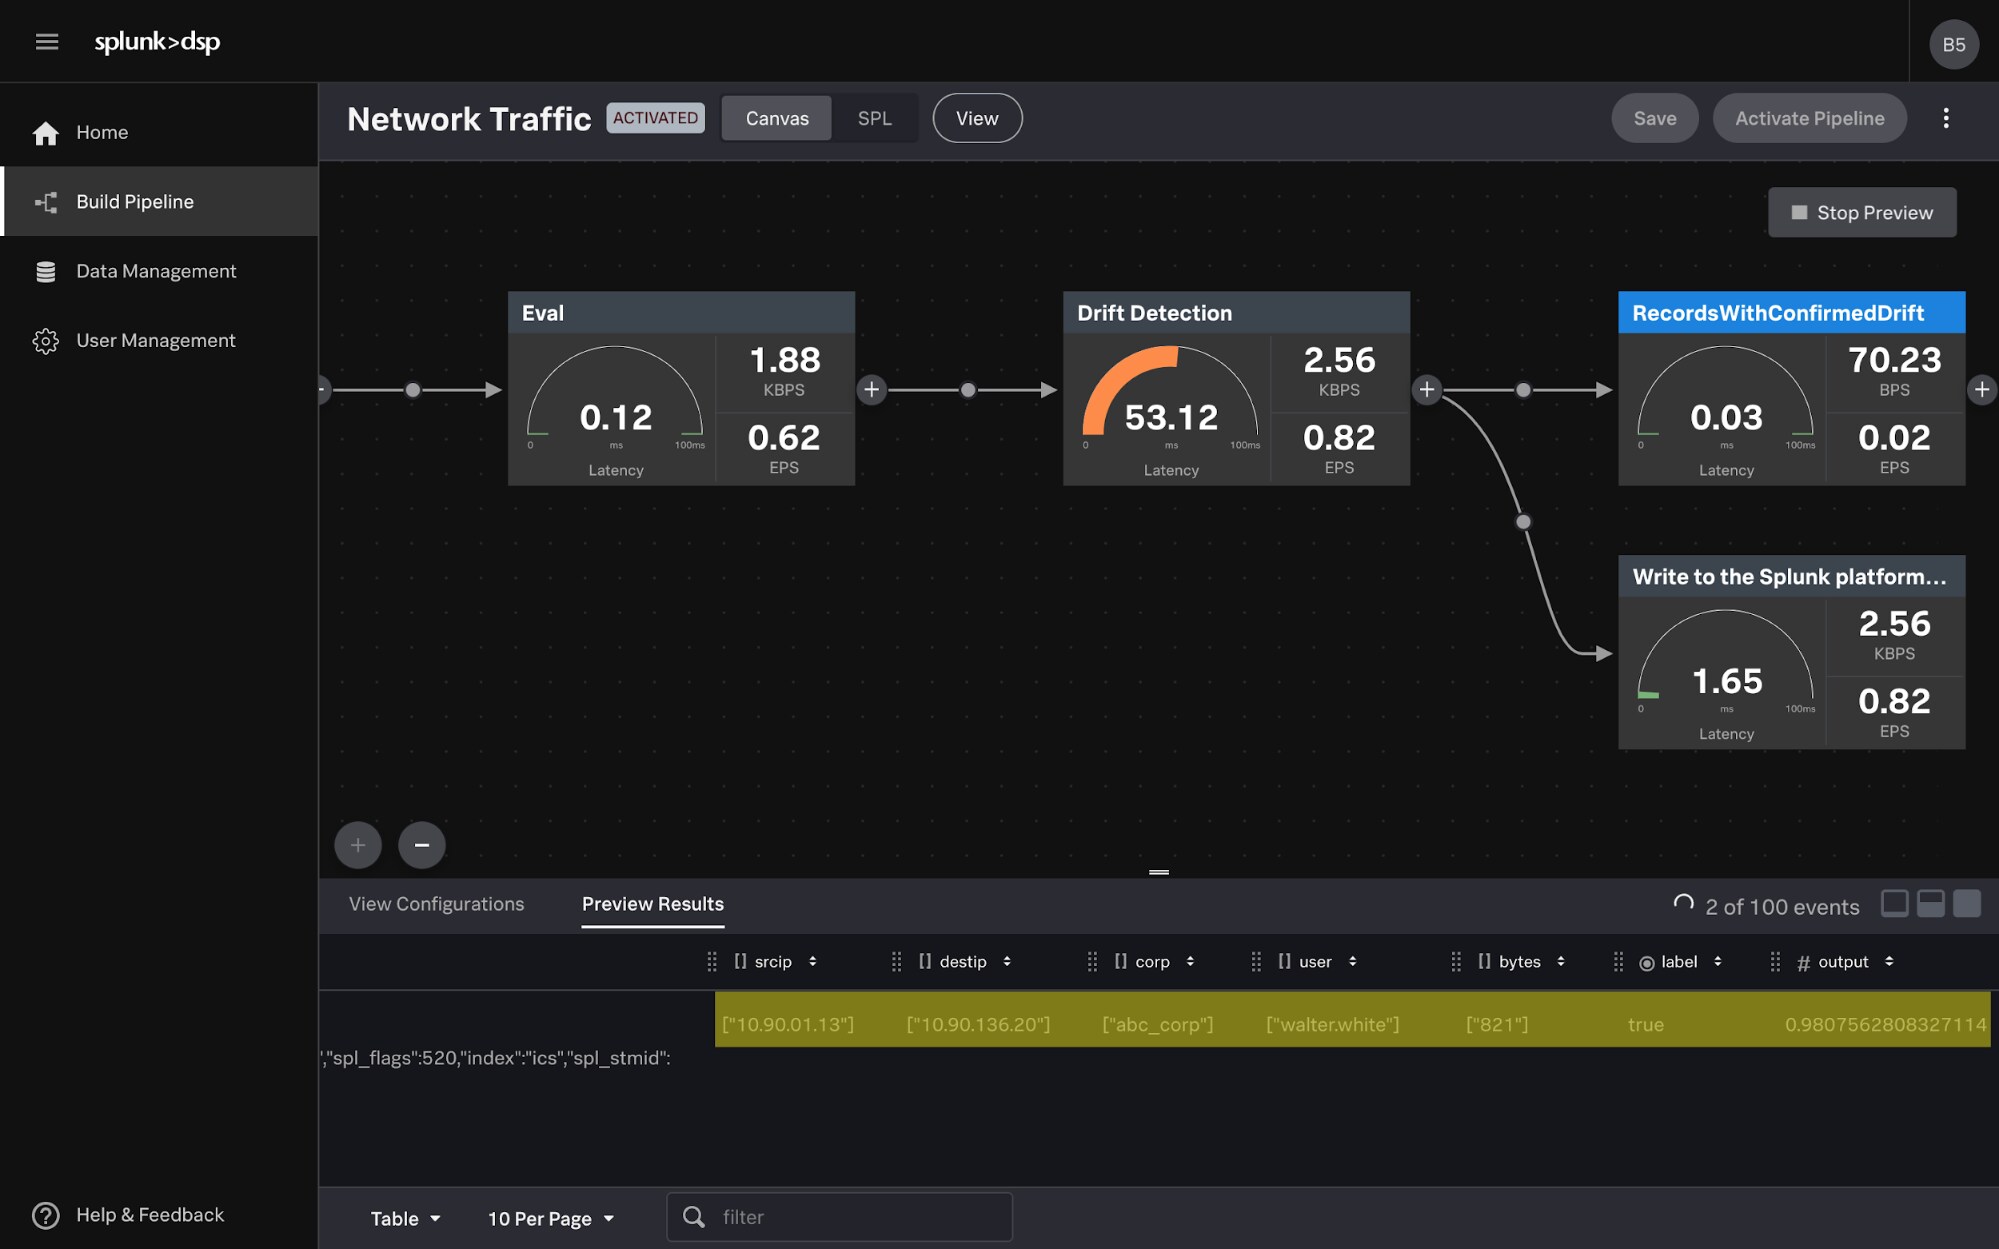
Getting started with Splunk Data Management Pipeline Builders - Splunk ...
How to collect events and metrics data from Splunk Enterprise | BMC ...
Splunk Intro, Data Ingestion. Let’s Learn Splunk from ground ZERO. | by ...
How to Simulate Data Flow and Pulling Logs From AWS to Splunk | Splunk
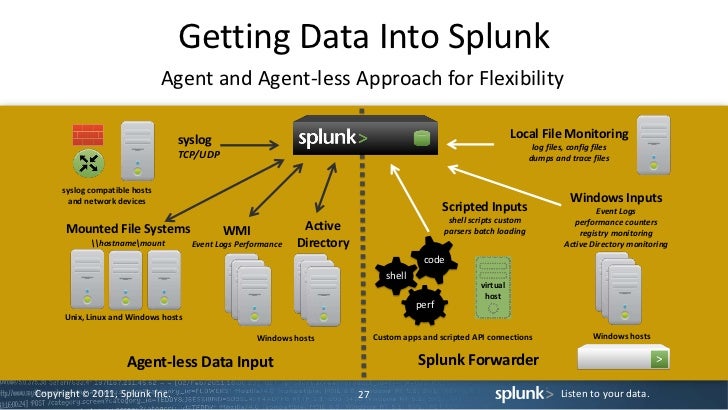
Getting Data Into Splunk Agent
Getting data from your REST APIs into Splunk | Splunk
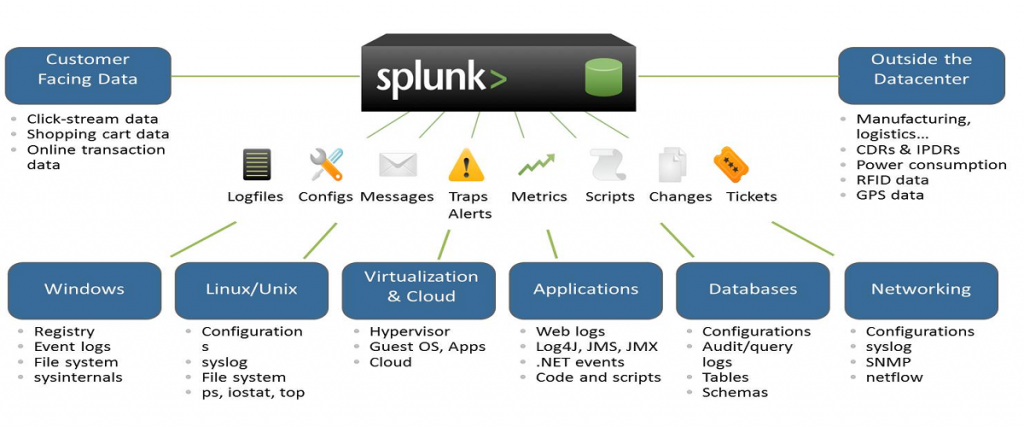
Splunk's Input Methods and Data Feeds
How to preserve all configured data inputs when up... - Splunk Community
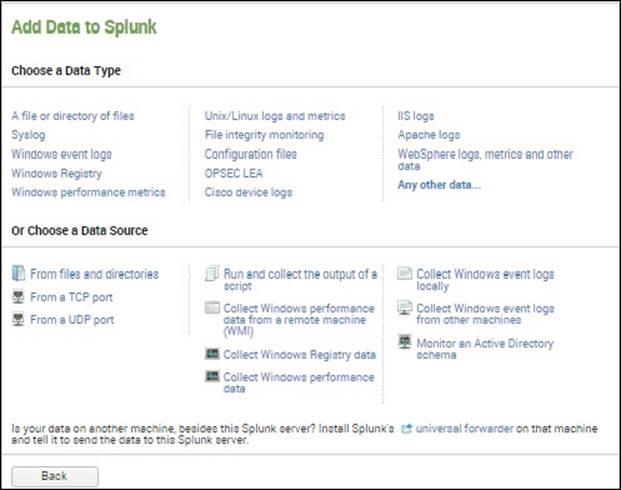
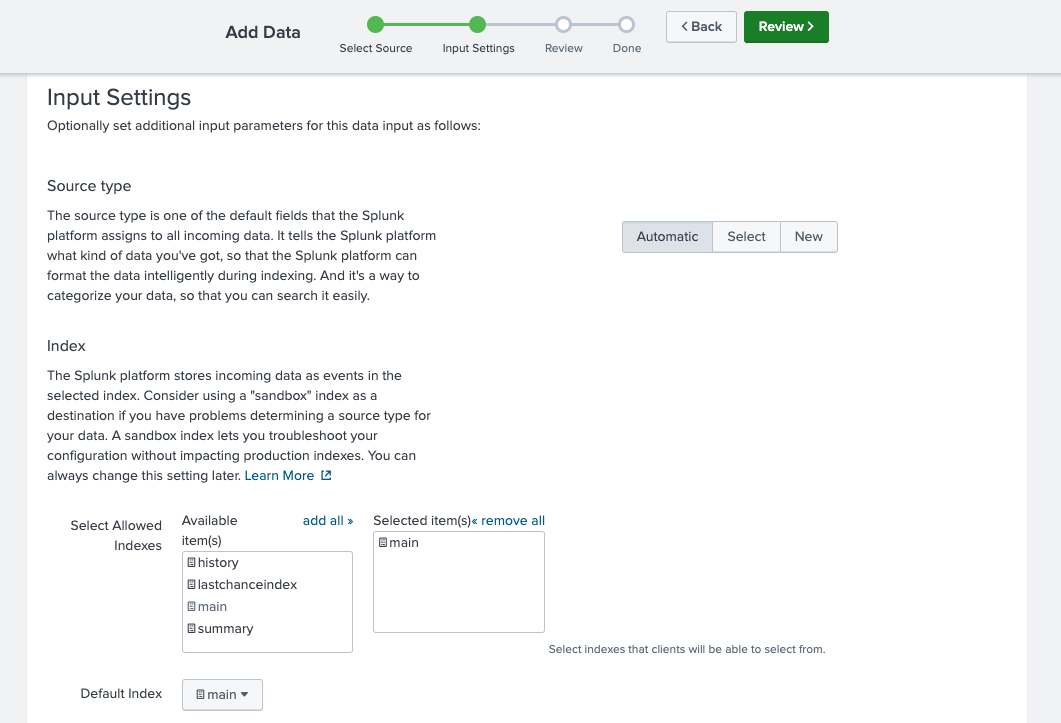
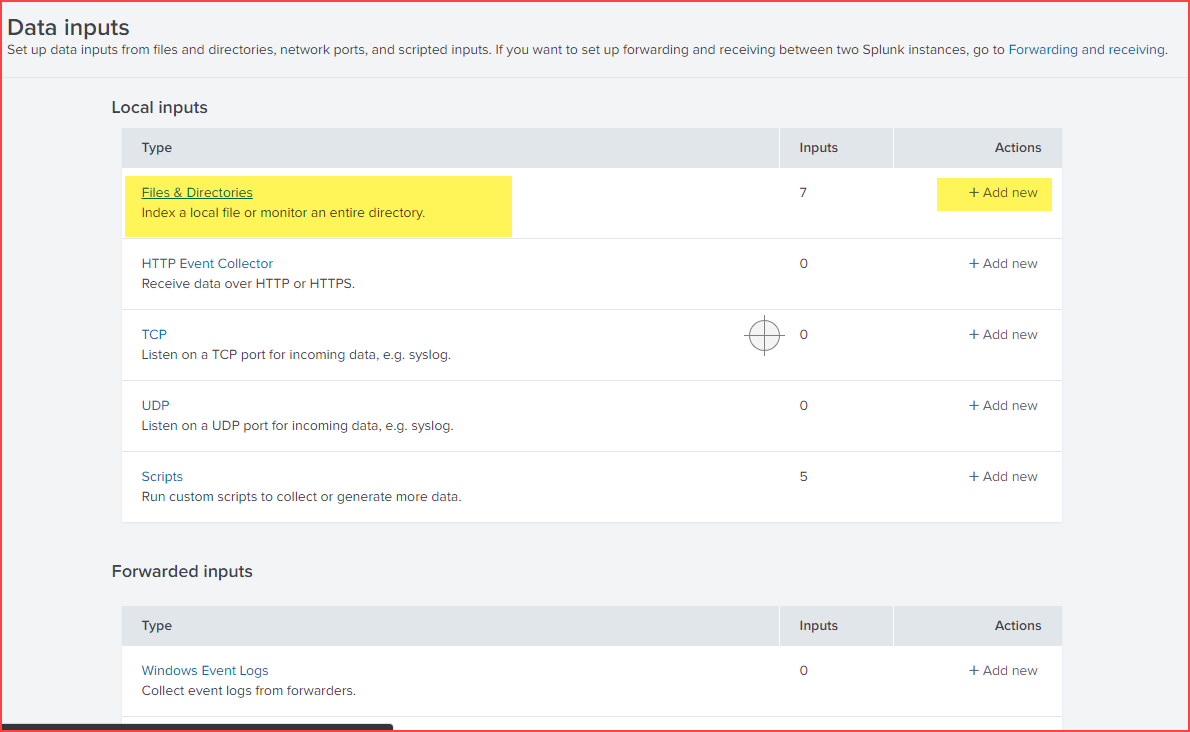
How to Onboard Data into Splunk via the Web Interface - Hurricane Labs
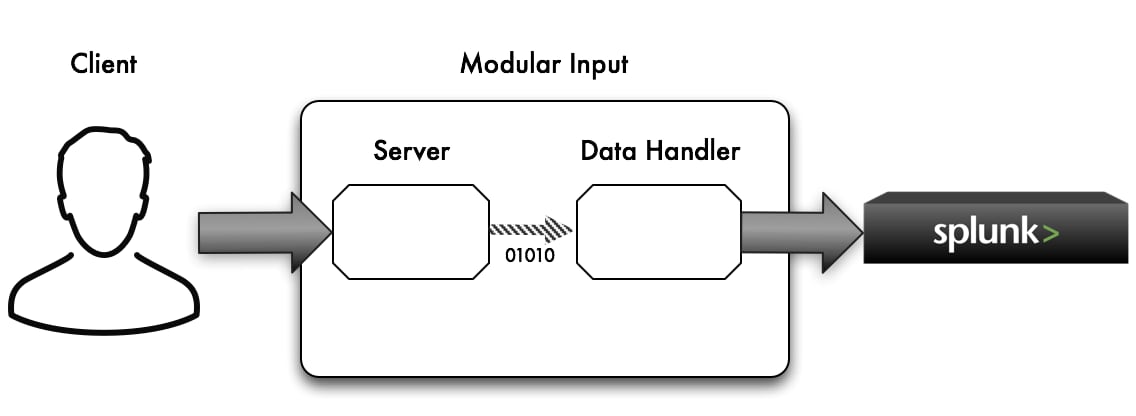
Splunk Modular Inputs / JMS Messaging Module Input | PPTX
Solved: After upgrading to Splunk 6.4.0, why is my Data in... - Splunk ...
What Is Splunk Cooked Data at Cynthia Ridgeway blog
Getting Data into Splunk | PPTX
Getting data into Splunk
Dynamic Data: Data Retention Options in Splunk Cloud Platform | Splunk
Splunk Data Ingestion | Ingest Actions: Data Access When, Where and How ...
Getting Data into Splunk | PPT
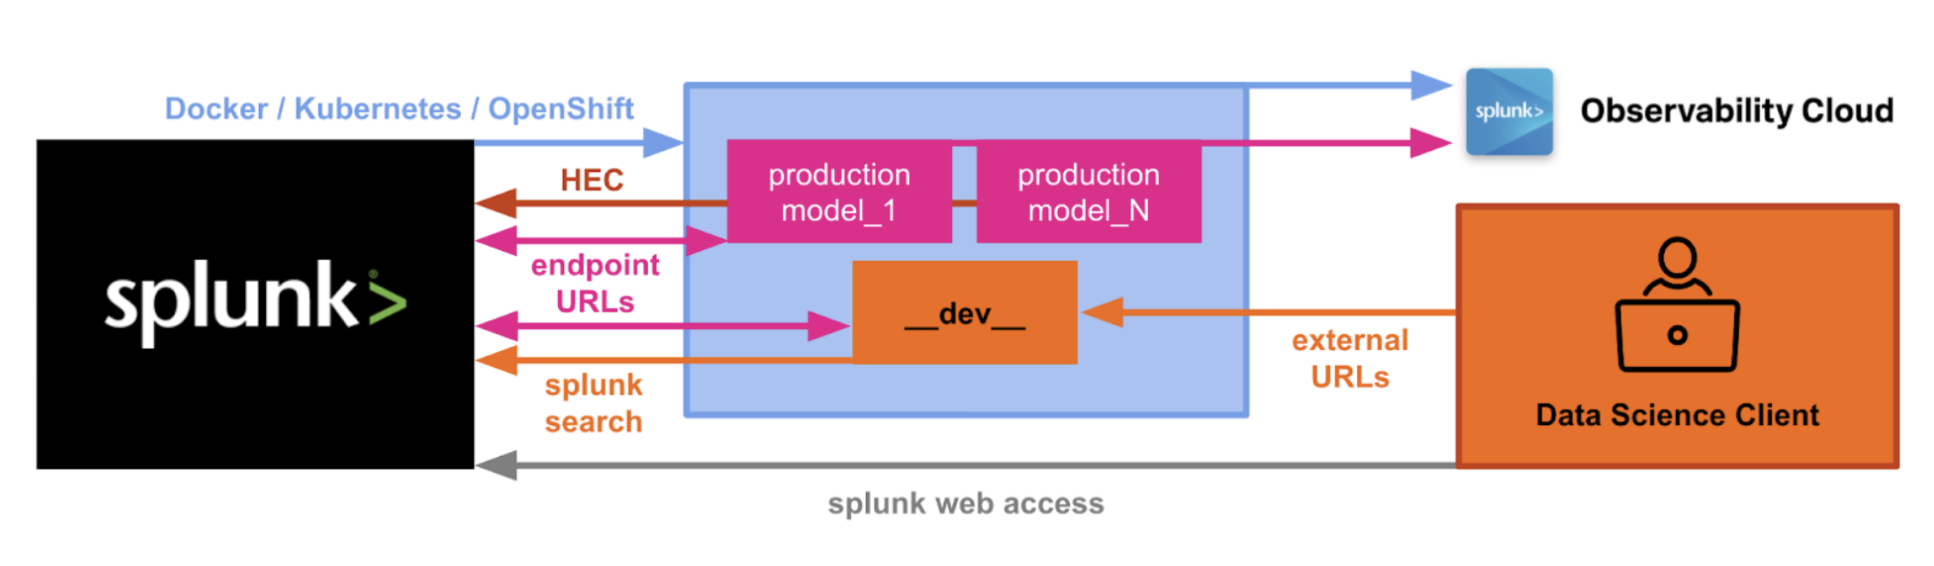
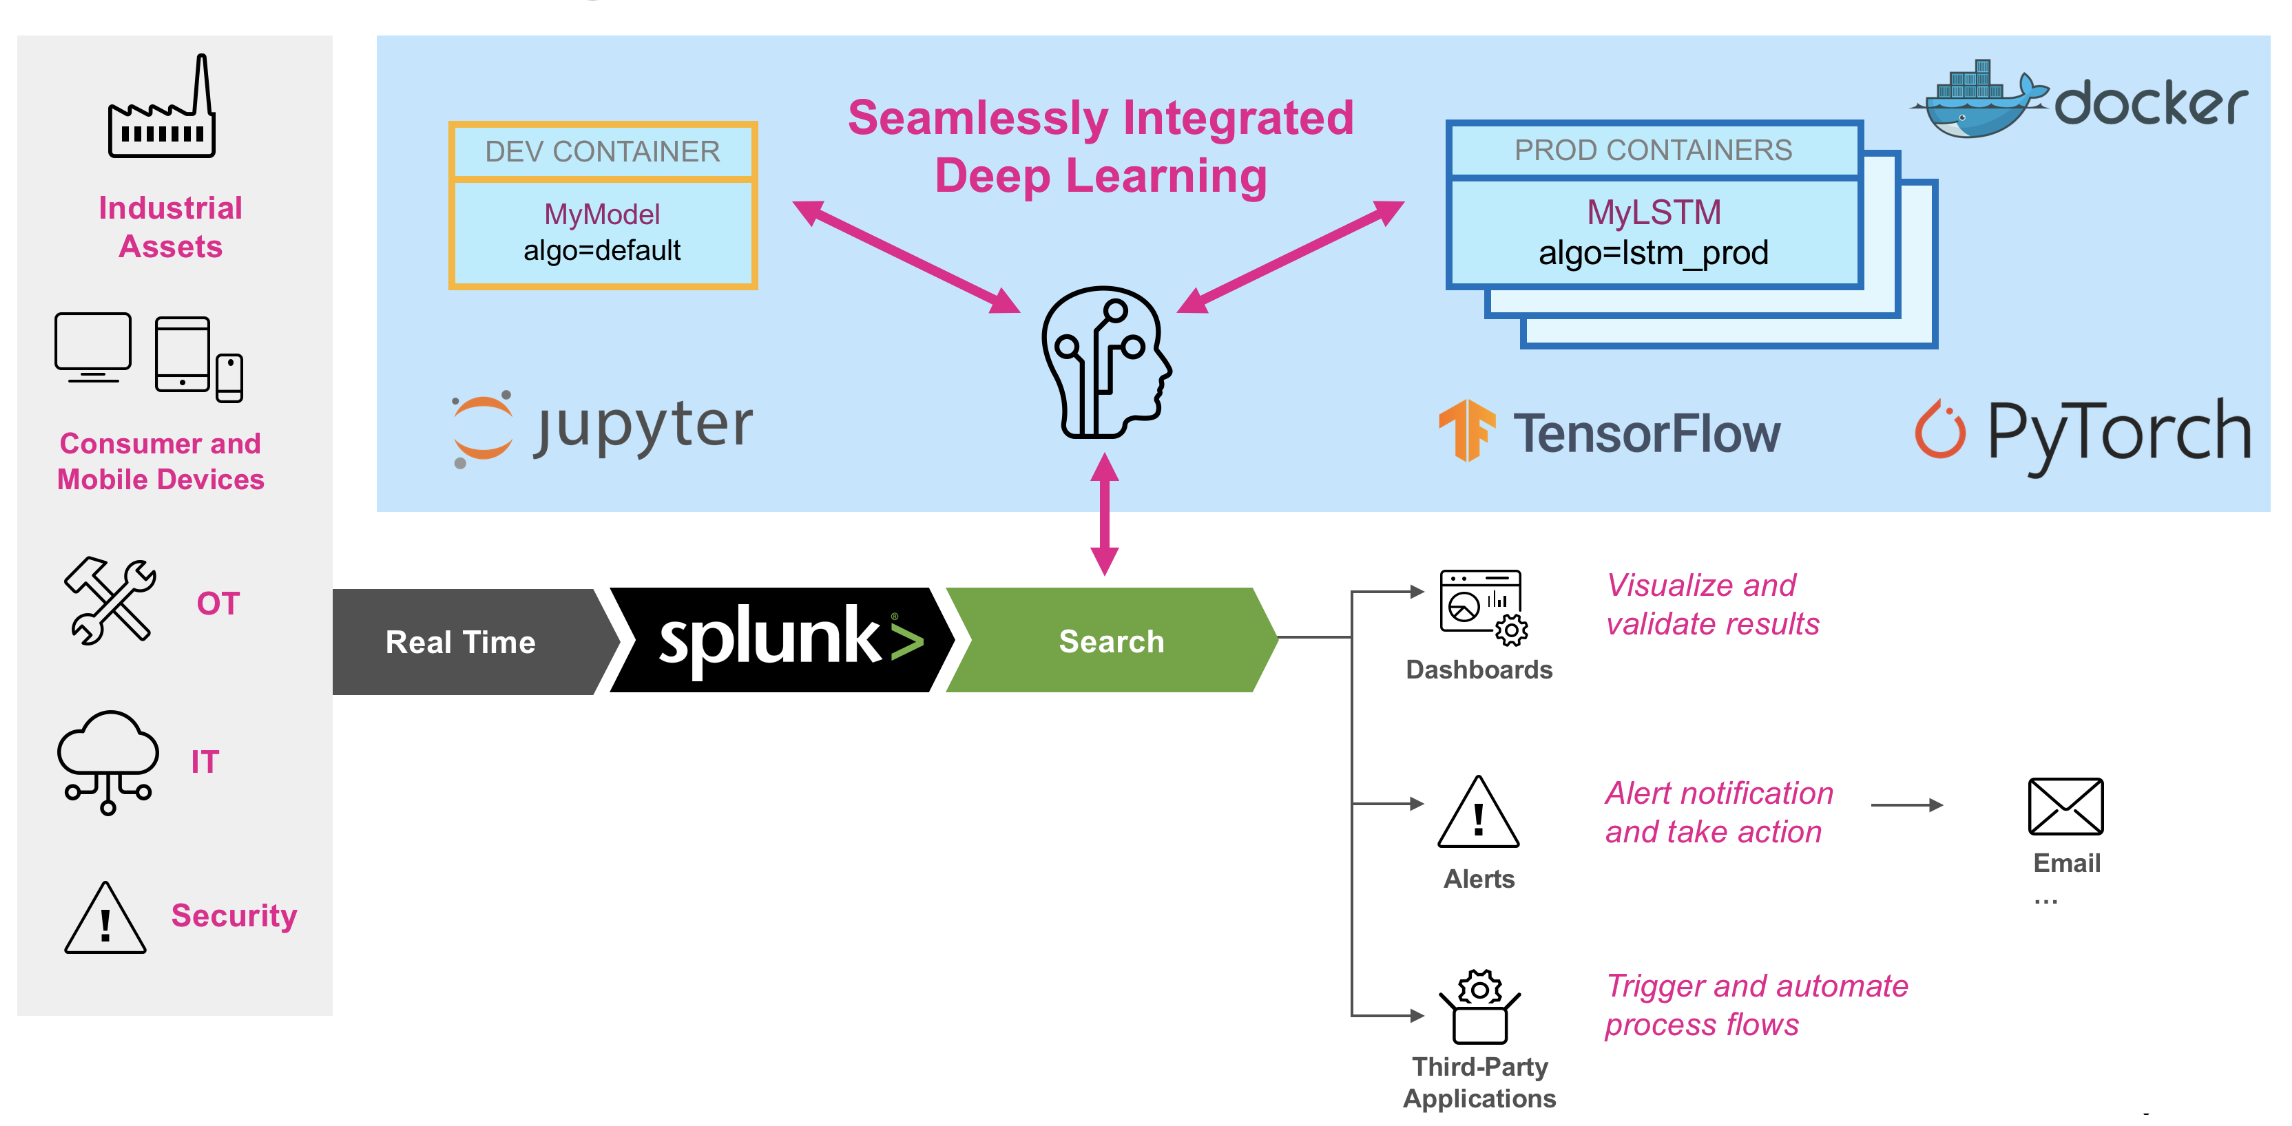
Splunk App for Data Science and Deep Learning architecture - Splunk ...
Getting Microsoft Azure data into the Splunk platform - Splunk ...
Visualize any Splunk data - SquaredUp
Modular inputs basic example - Splunk Documentation
What Is Splunk Database at Dean Metoyer blog
Splunk Integration
Logging to Splunk | Nametag Developer Documentation
How to Install Splunk Log Analyzer on CentOS 7
Splunk
Integrate with Splunk
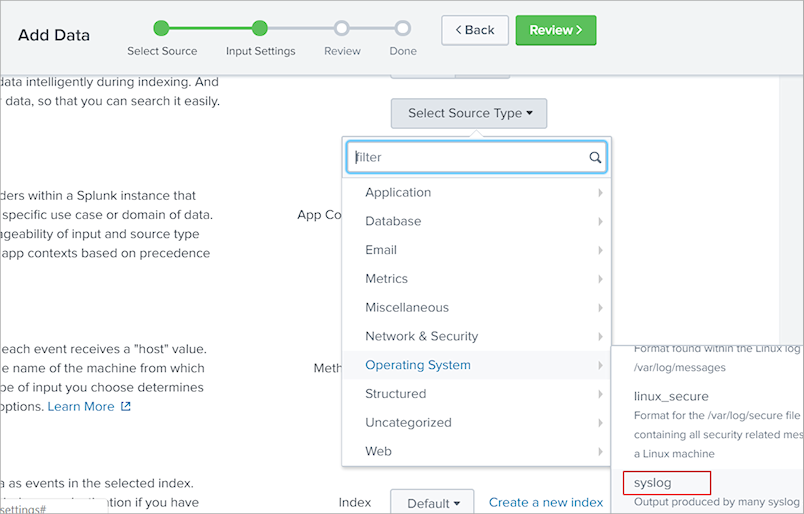
Usando o Splunk como Syslog Server - Brainwork
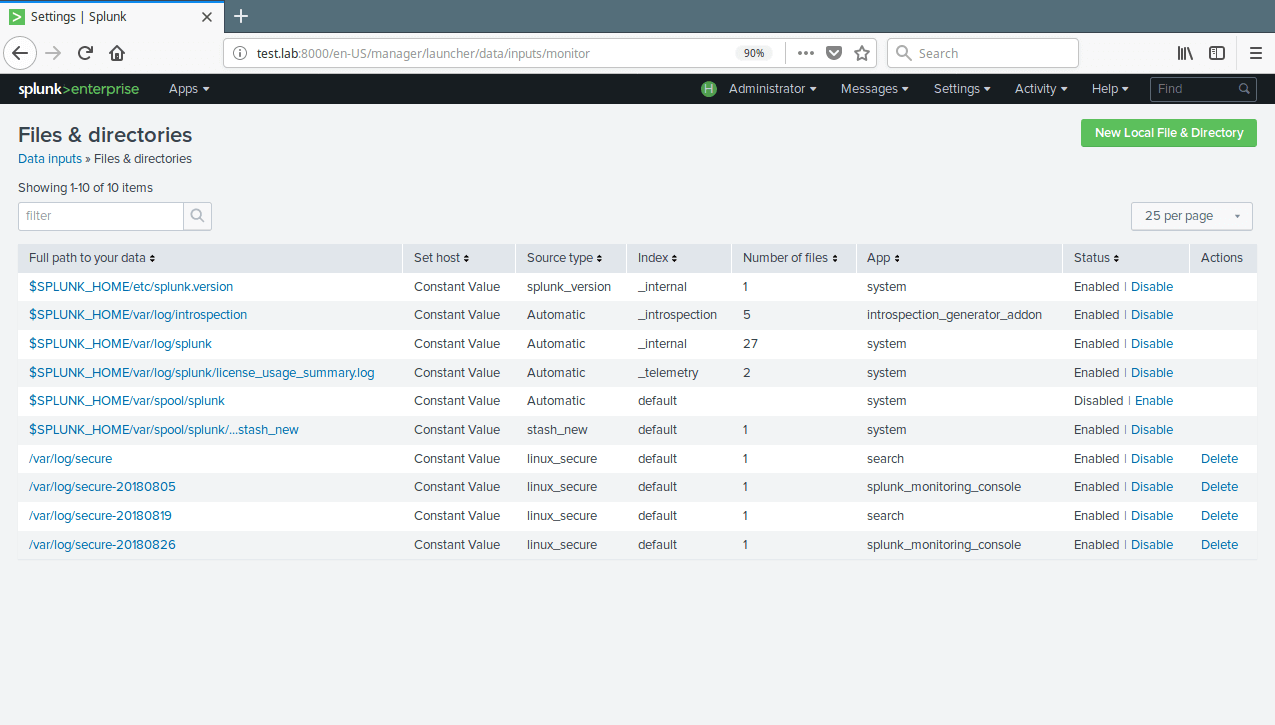
The Beginners Guide to Splunk Monitors - Kinney Group
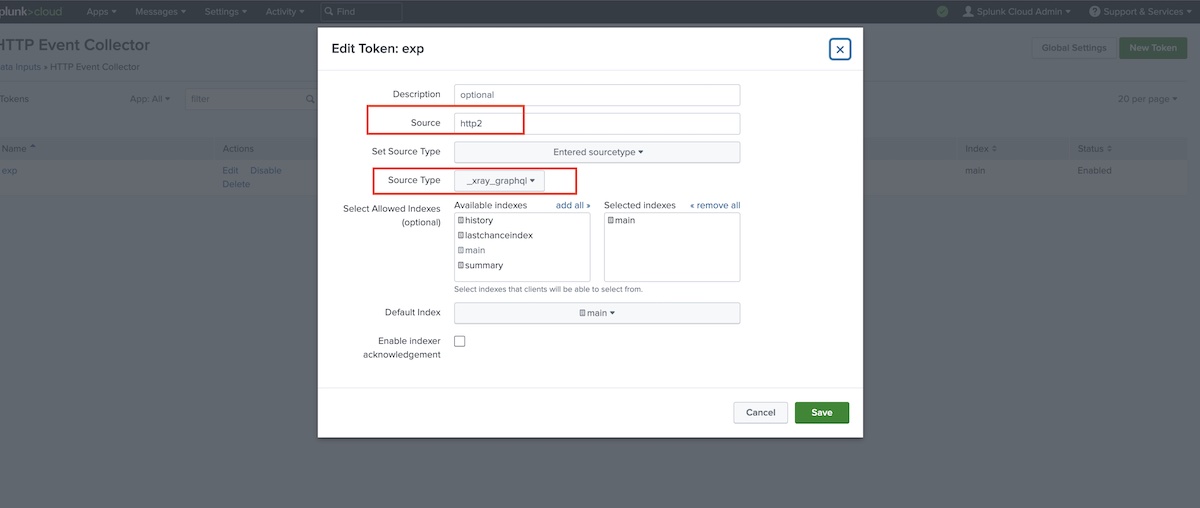
Sending Logs to Splunk Enterprise and Splunk Cloud
Configuring the Splunk System
Monitoring files activity with Splunk – Resilio Active Everywhere
Configure inputs in Splunk Infrastructure Monitoring Add-on - Splunk ...
Monitoring files activity with Splunk - Resilio Help Center
Splunk Integration | Analytics Plus
Splunk integration
Dynamic Data:Splunk Cloud Platformのデータ保持オプション | Splunk
Configuring Access Splunk application
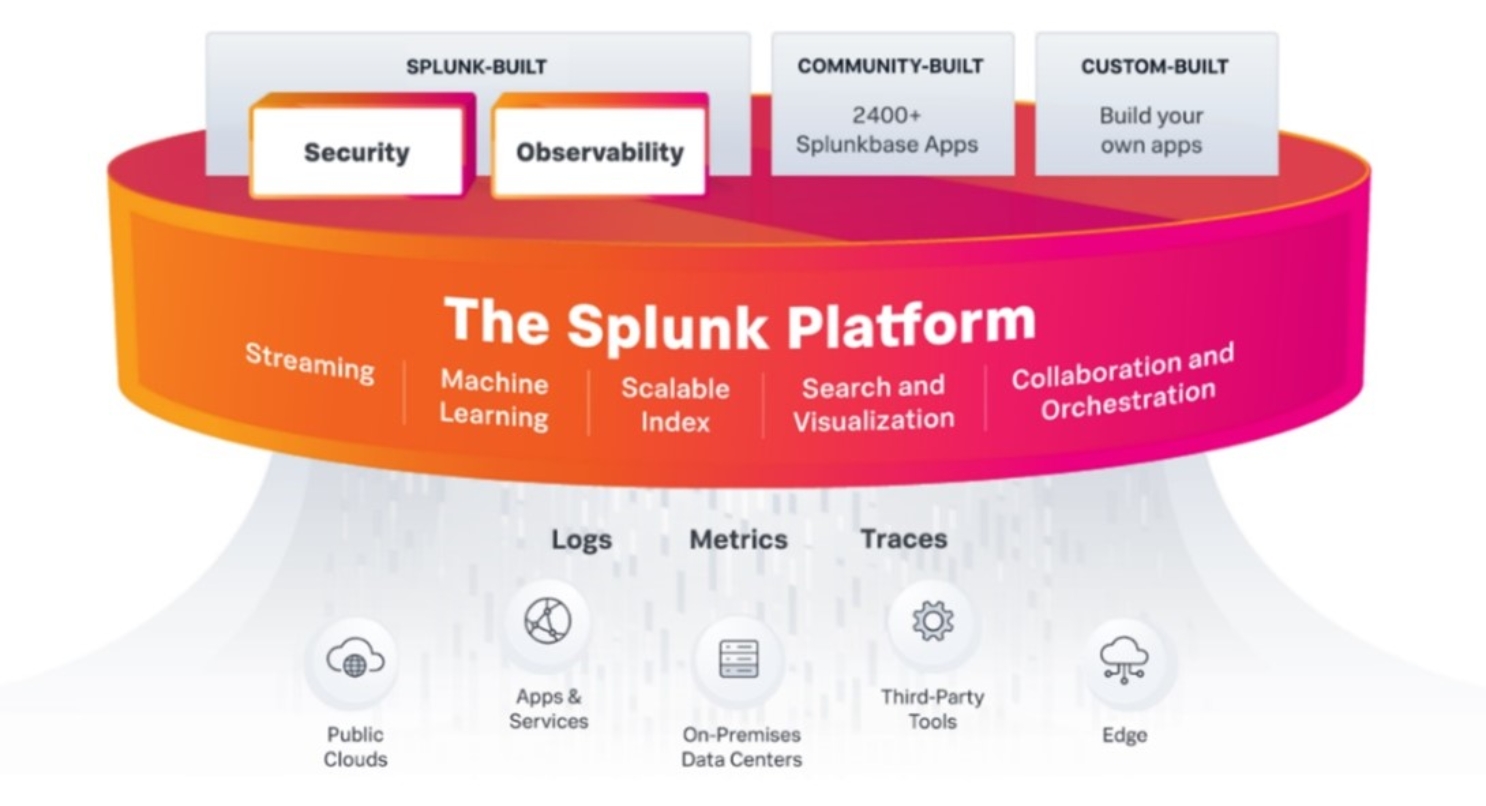
Splunk Enterprise: Product Features | Splunk
Send alerts to Splunk | Atlassian Support
Install Latest Splunk 7.2.0 on Ubuntu 18.04 LTS at Google Cloud ...
Data Manipulation in Splunk: PART I – NetwerkLABS
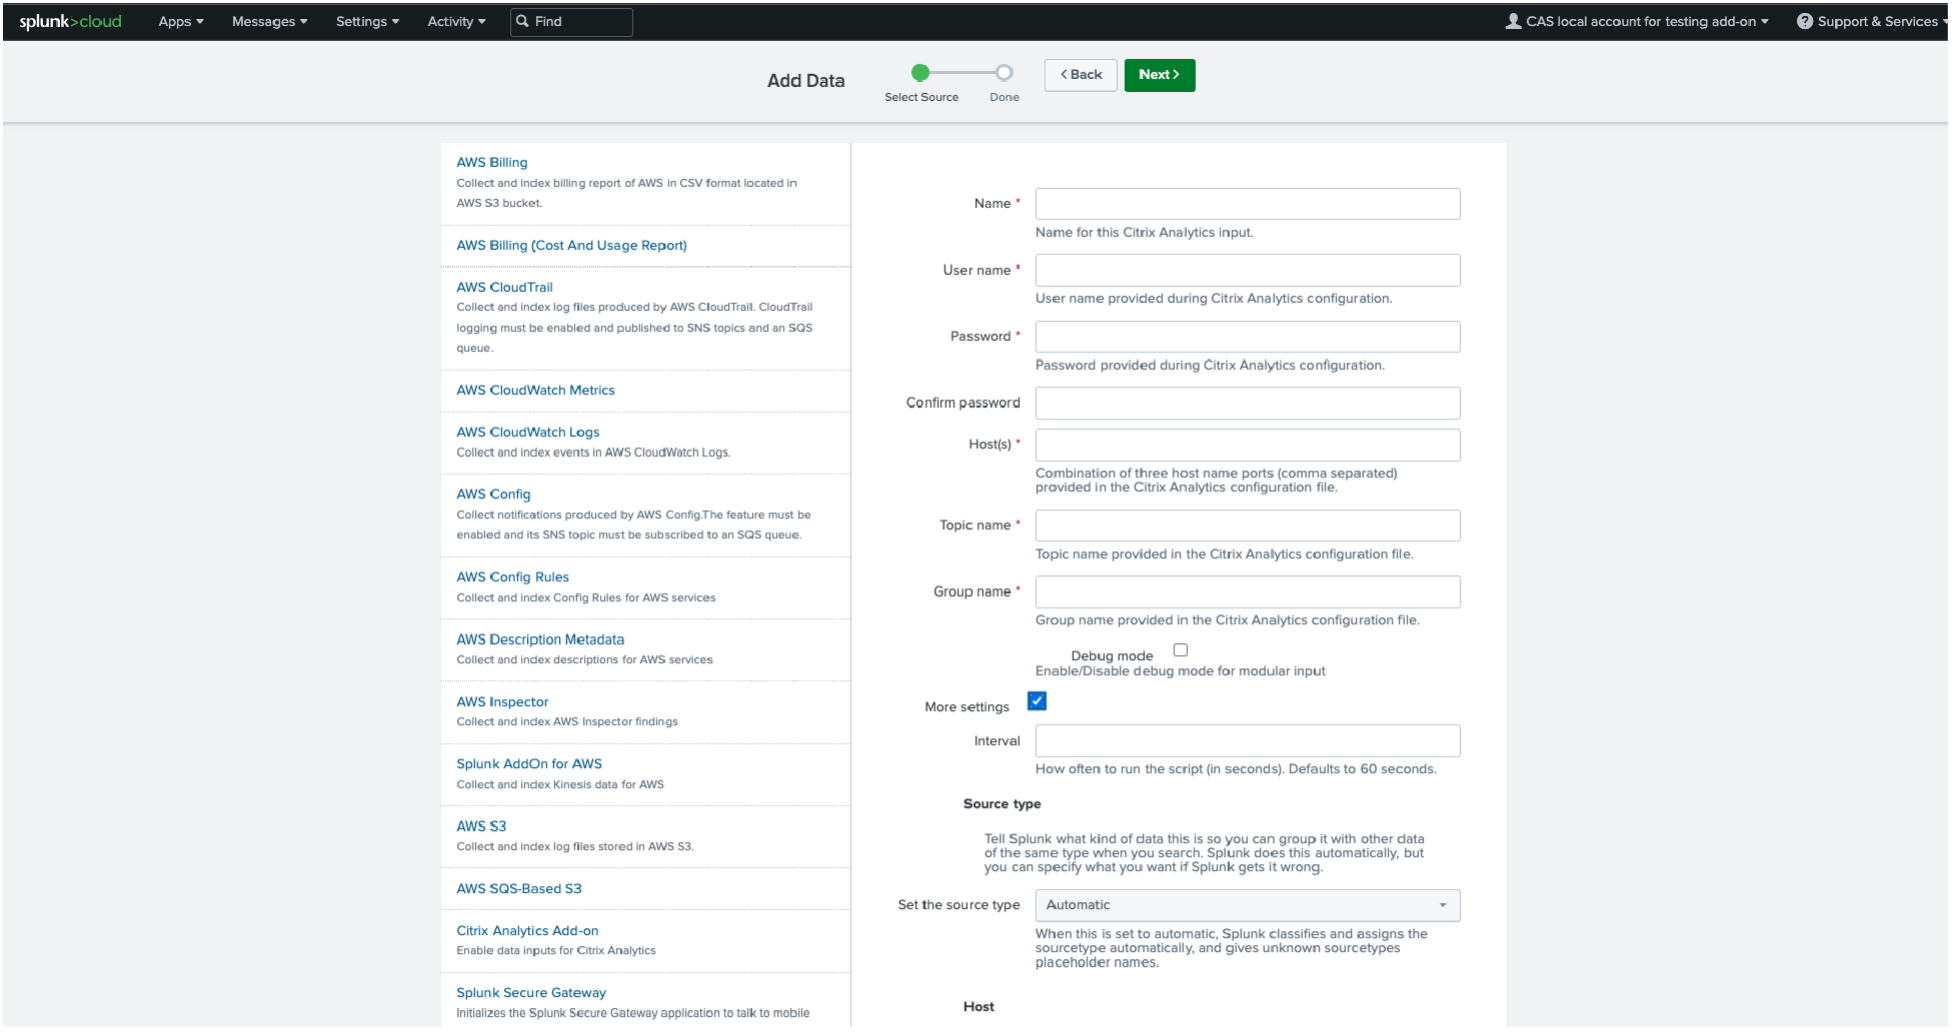
Splunk integration | Citrix Analytics for Security™
Install Latest Splunk 7.2.0 into Ubuntu and CentOS - NetSec
Introduction to Splunk | Splunk 7.x Quick Start Guide
Integrate Splunk with Ansible Automation Controller: Logging ...
Integrating with Splunk: You Gotta Think Outside the Box | Splunk
Splunk in 60 Minutes | Splunk Tutorial For Beginners | Splunk Training ...
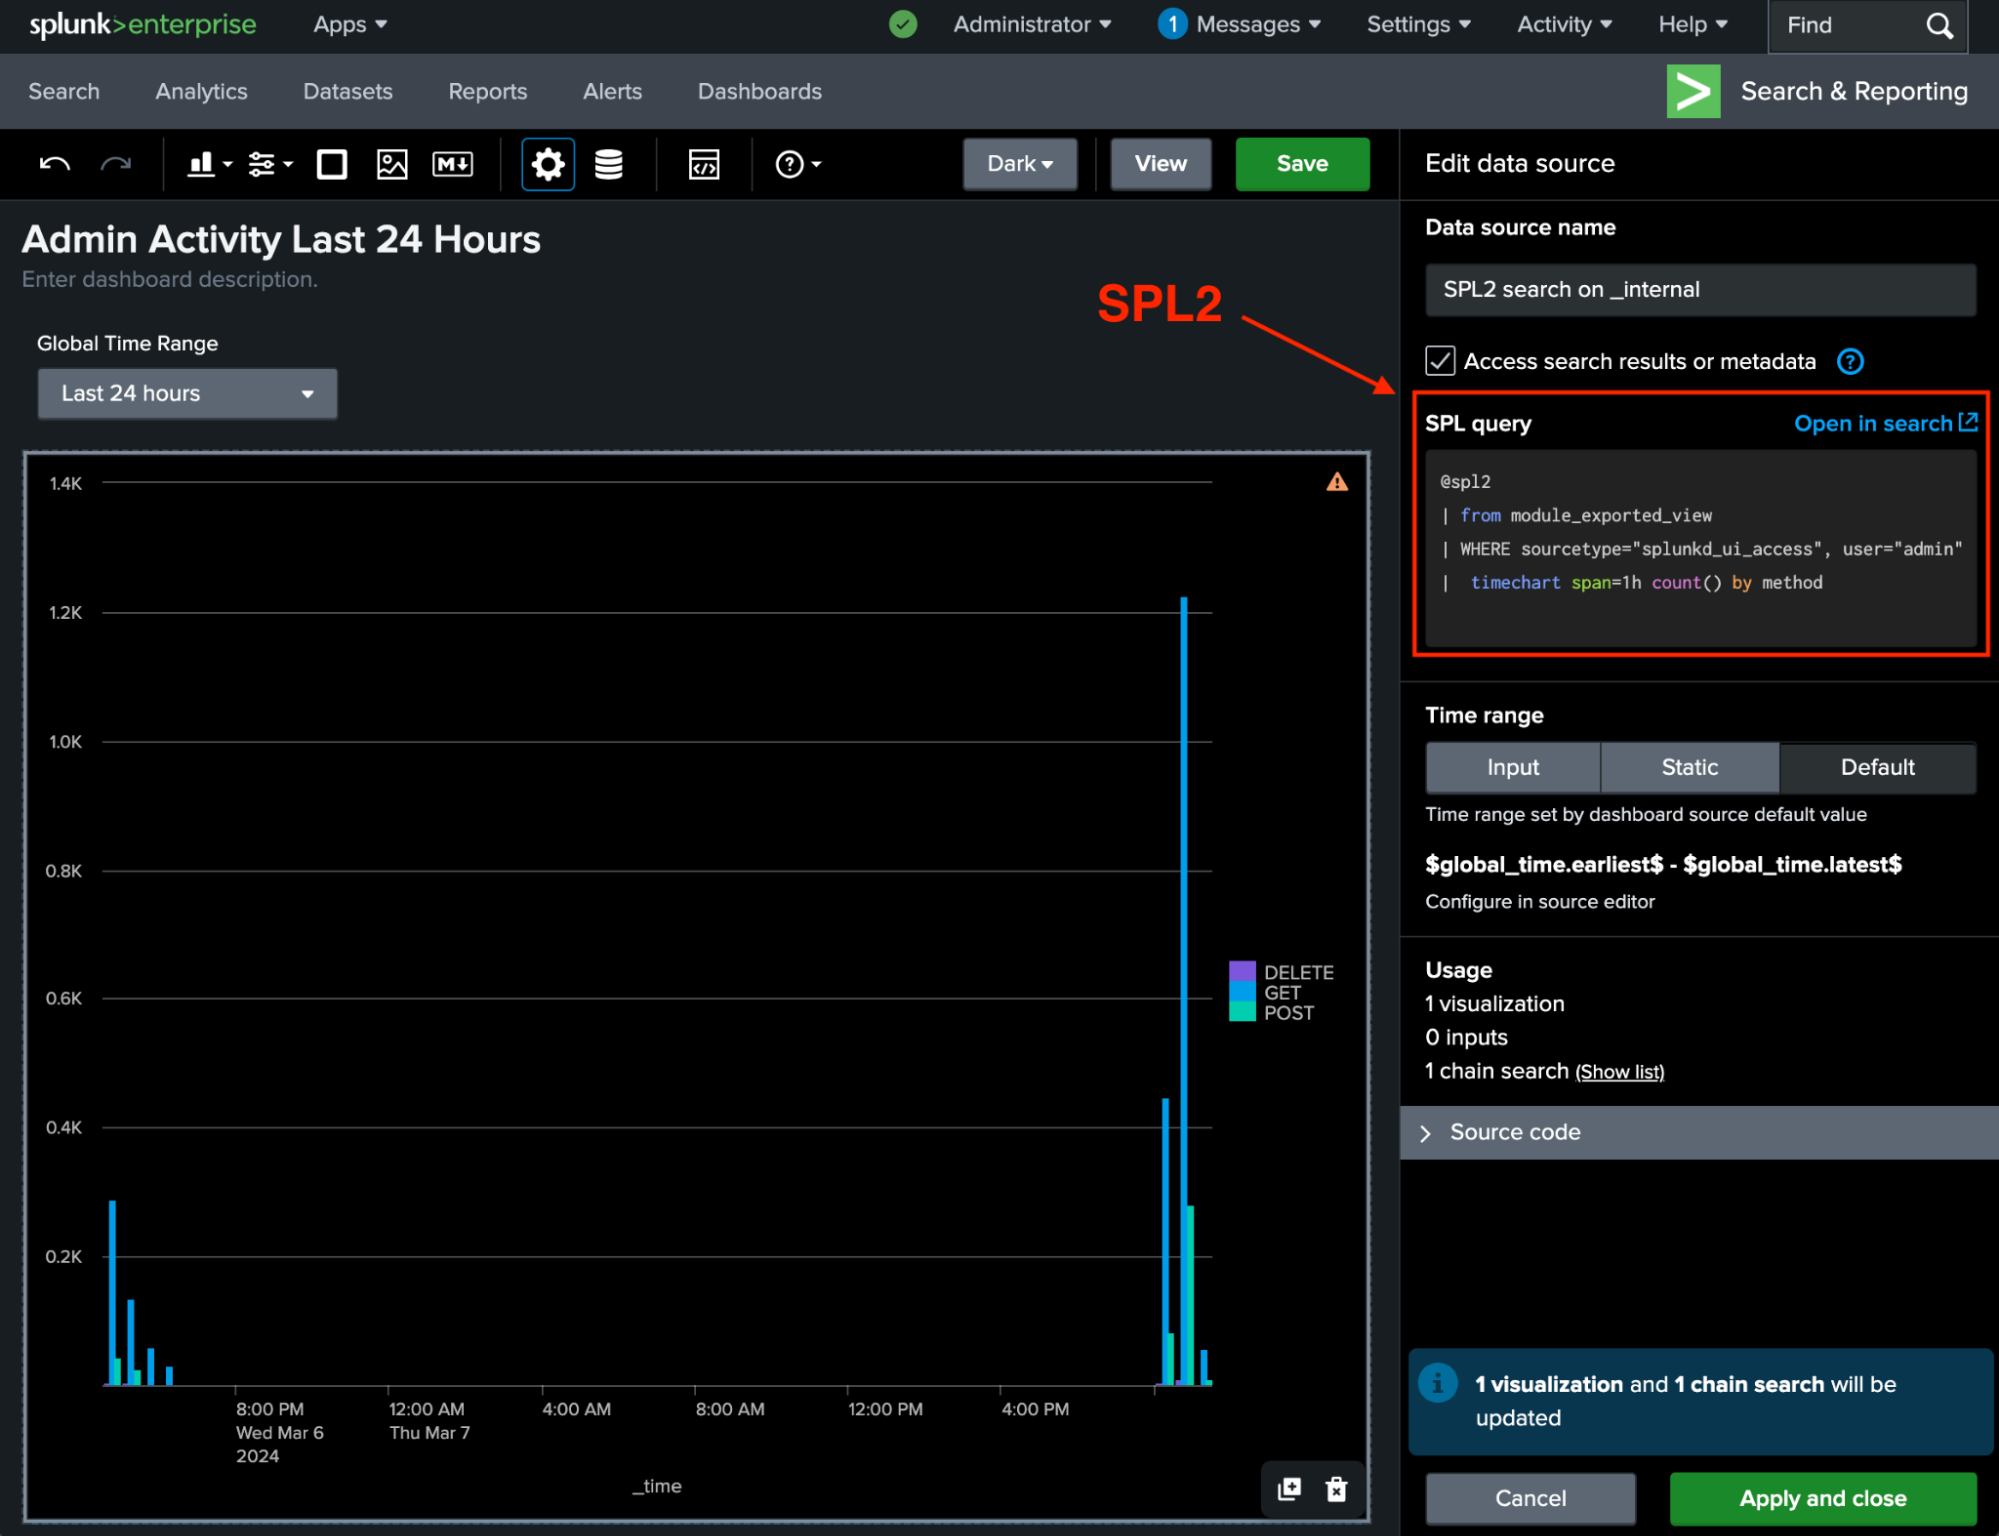
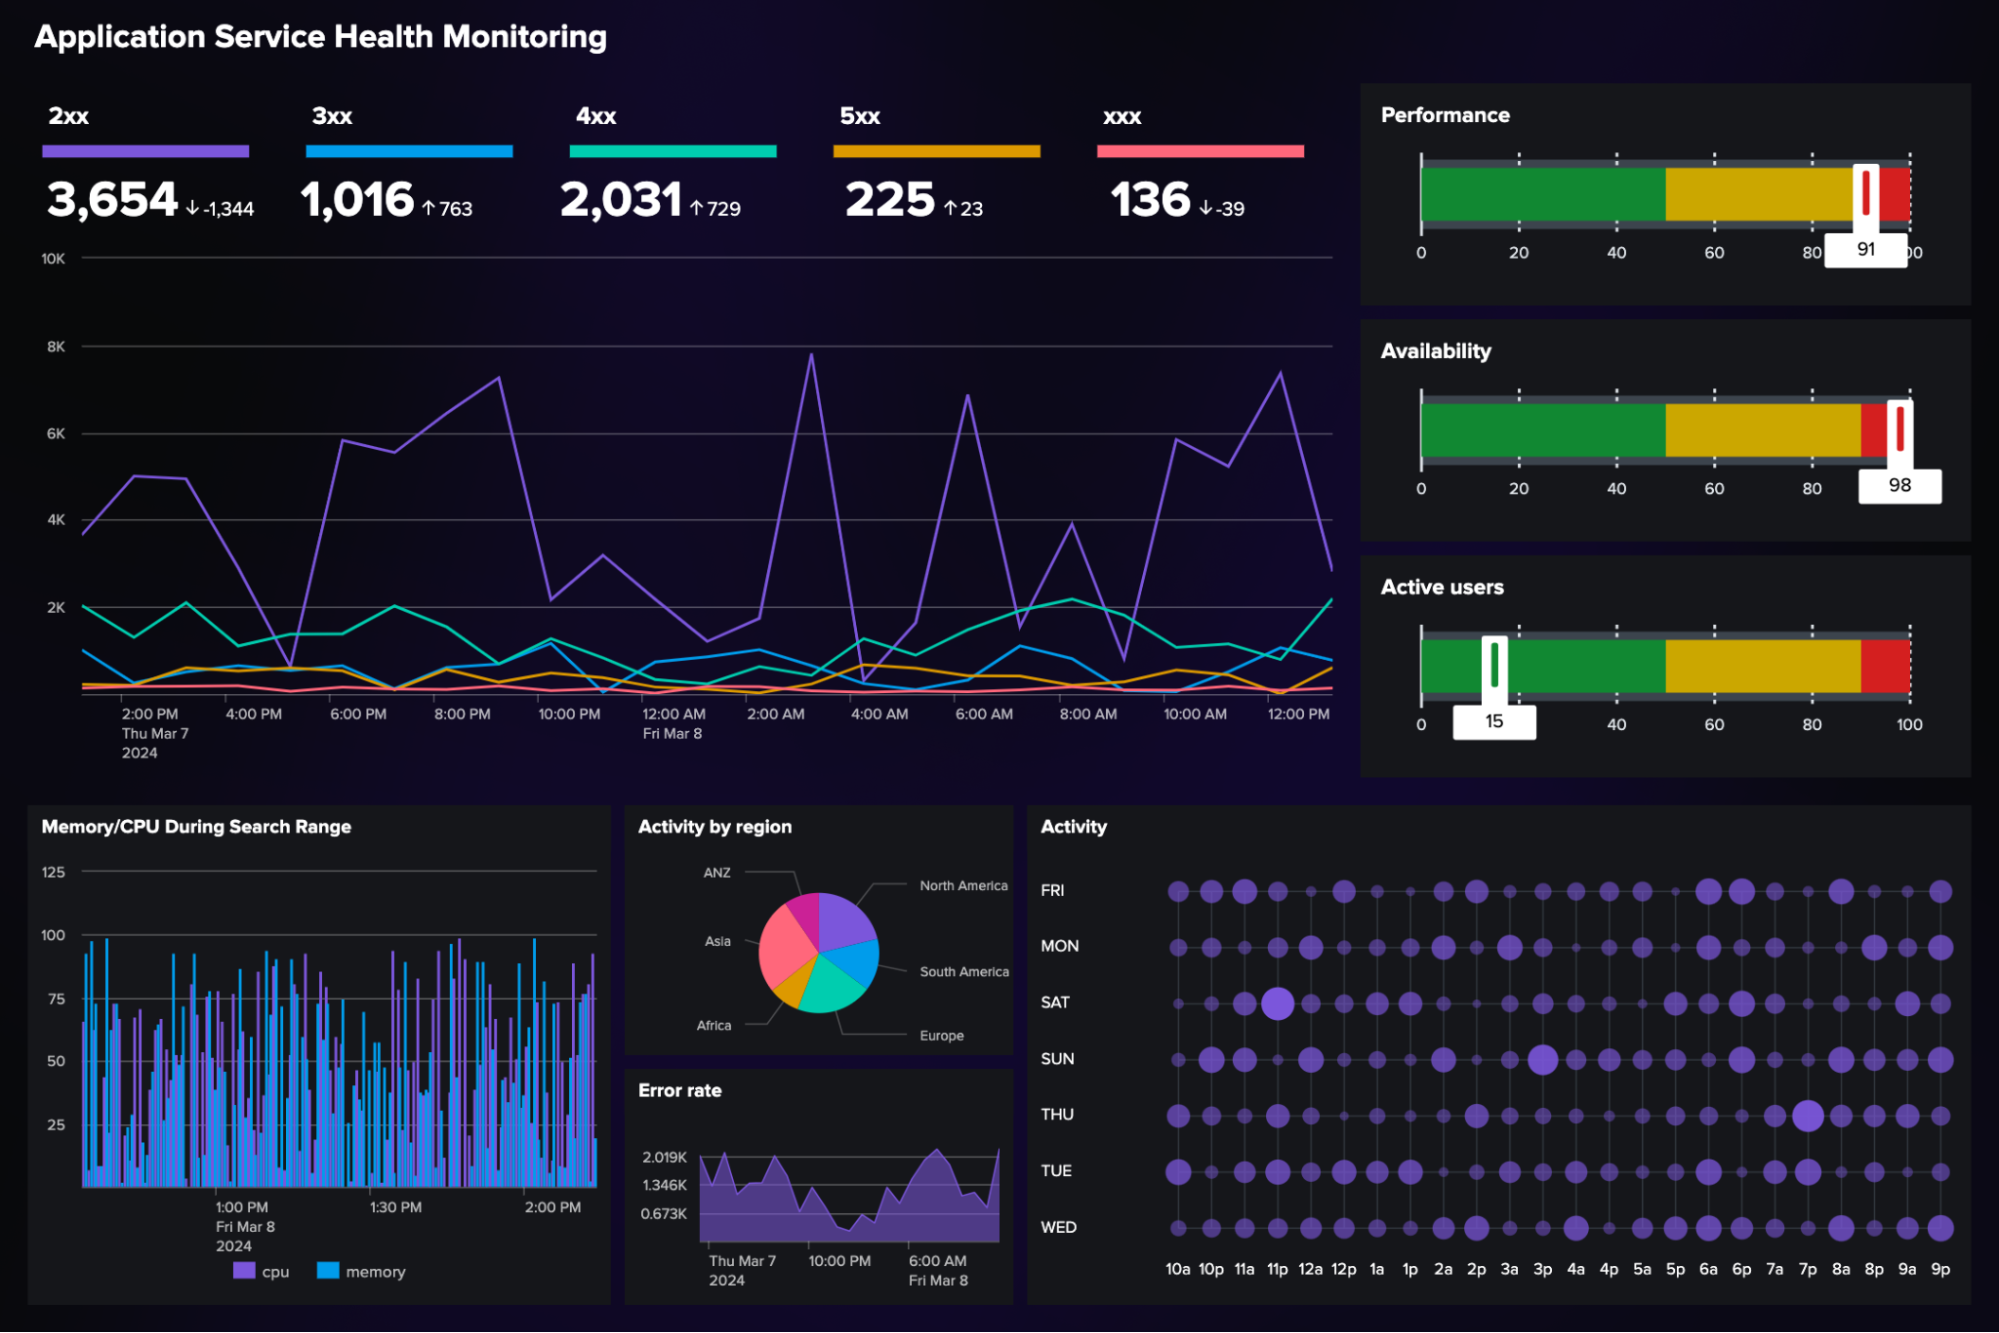
Dashboards Beta v0.8: Examples Hub | Splunk
Splunk inputs.conf examples - feryweather
Solutions - Cisco SD-WAN Splunk Integration User Guide - Cisco
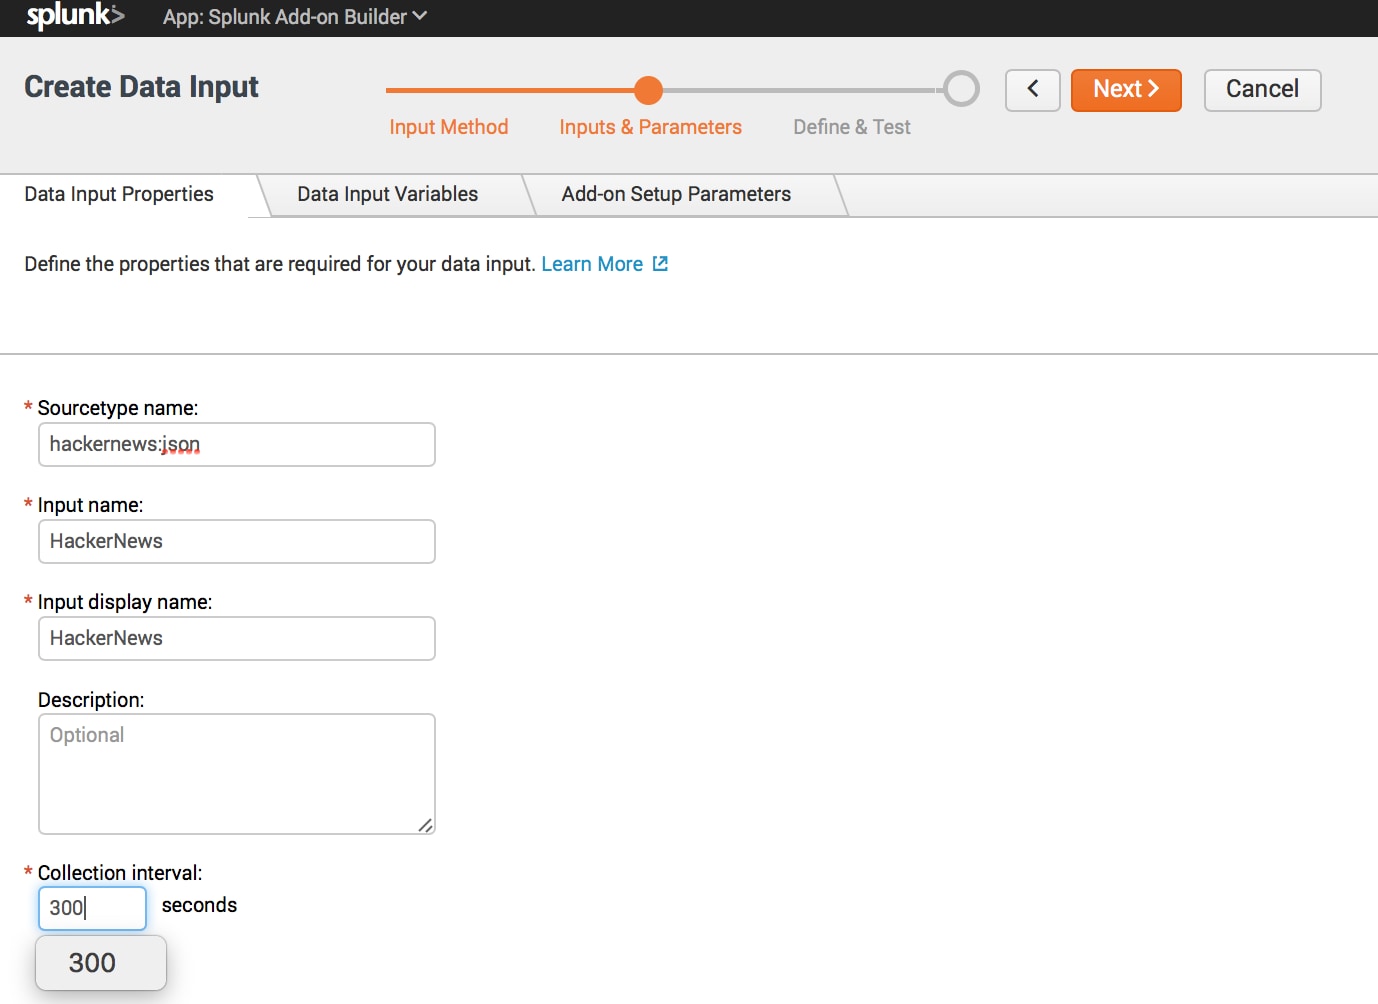
Easily Create Mod Inputs Using Splunk Add-on Builder 2.0 – Part IV | Splunk
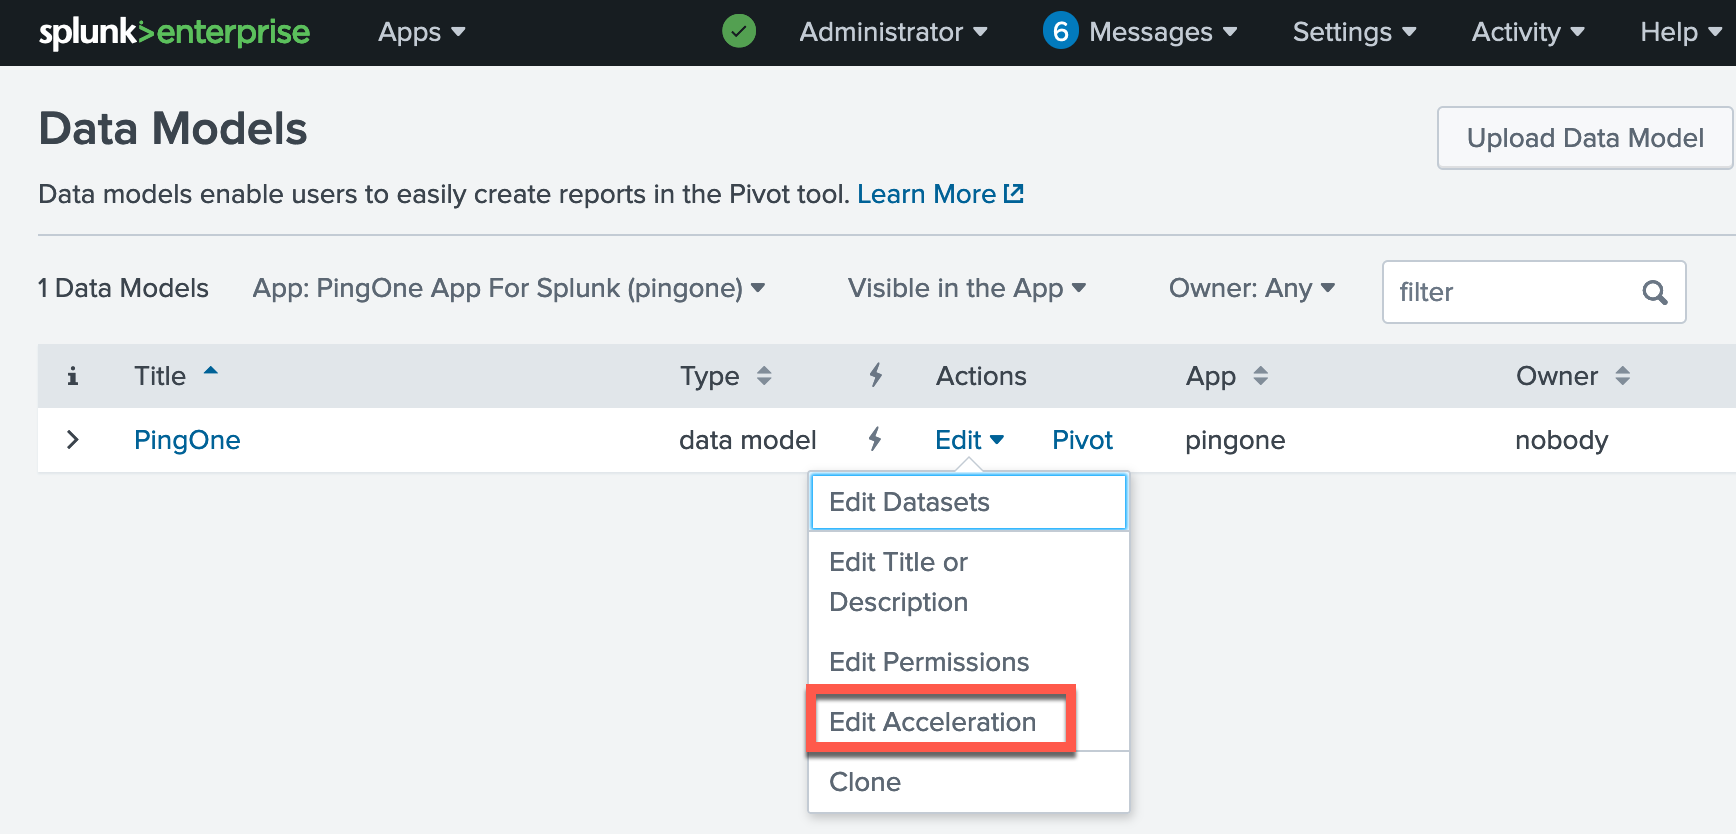
Monitoring activity with Splunk | PingOne
Splunk Log File Example _ How the Splunk platform handles log file ...
Splunk Universal Forwarder 远程数据采集 | Splunk
CREATING A SPLUNK CLOUD CONNECTION | ThingParkX
Splunk 数据采集详解与使用示例 | Splunk 教程
Dashboards Beta v0.9: All Things Inputs | Splunk
Splunk Where Example at Tawana Tibbs blog
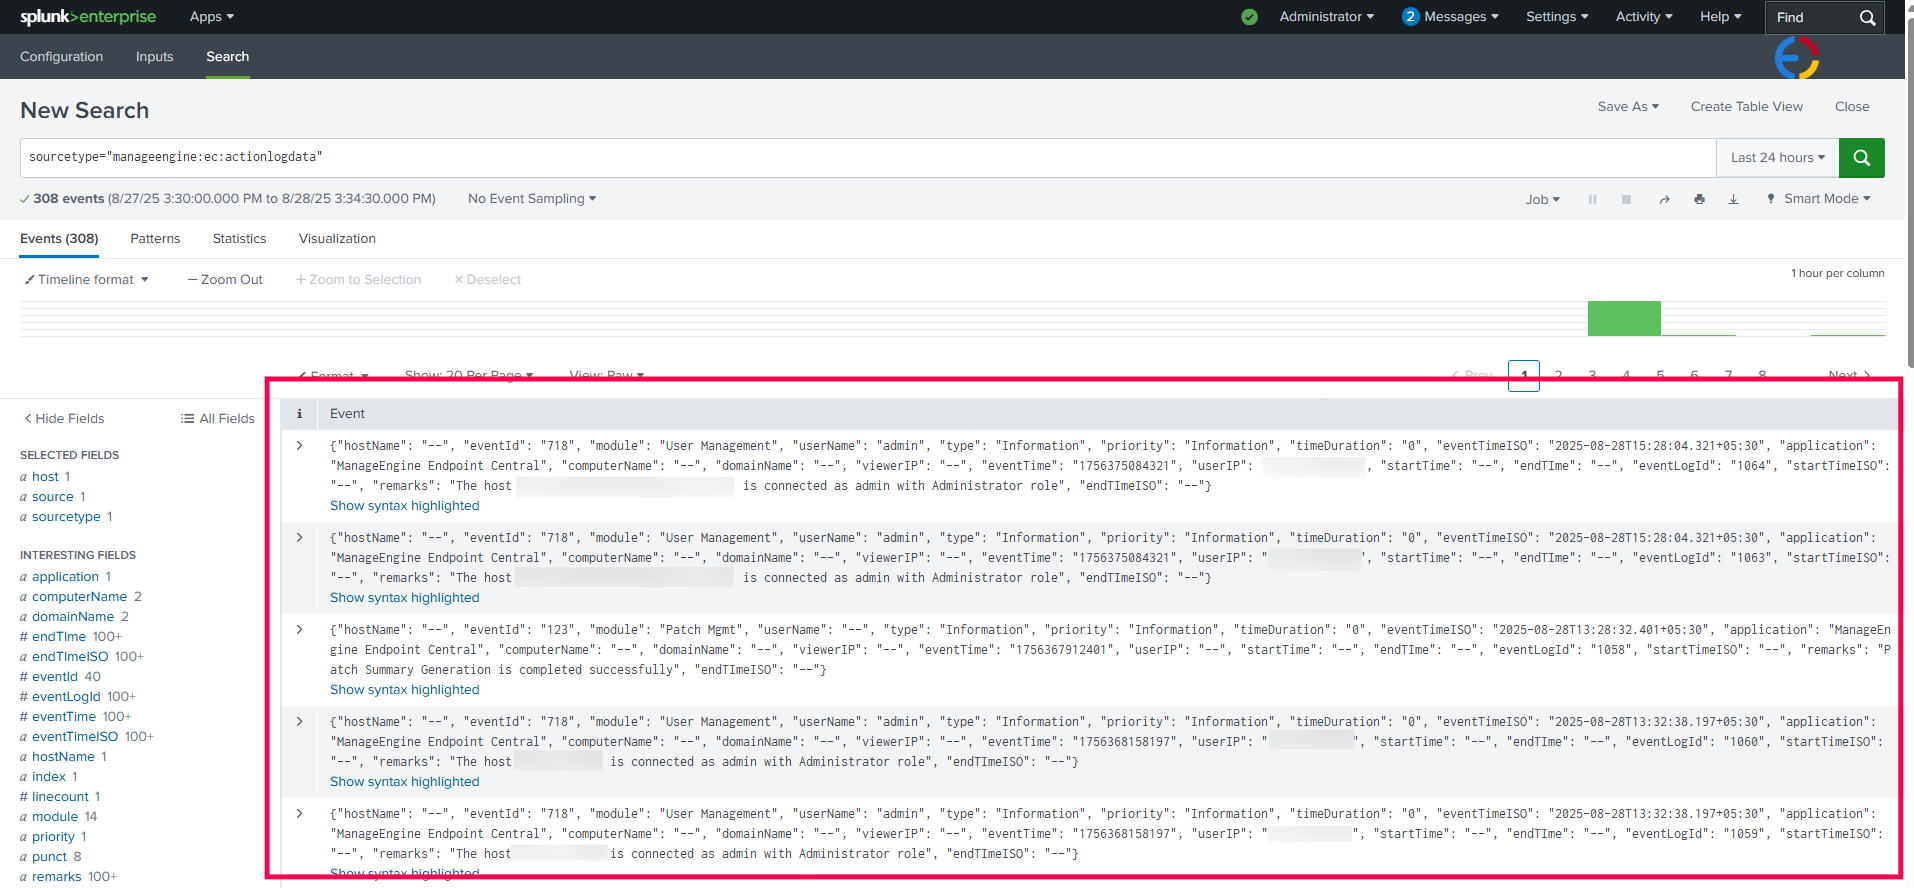
Splunk Integration | ManageEngine Endpoint Central
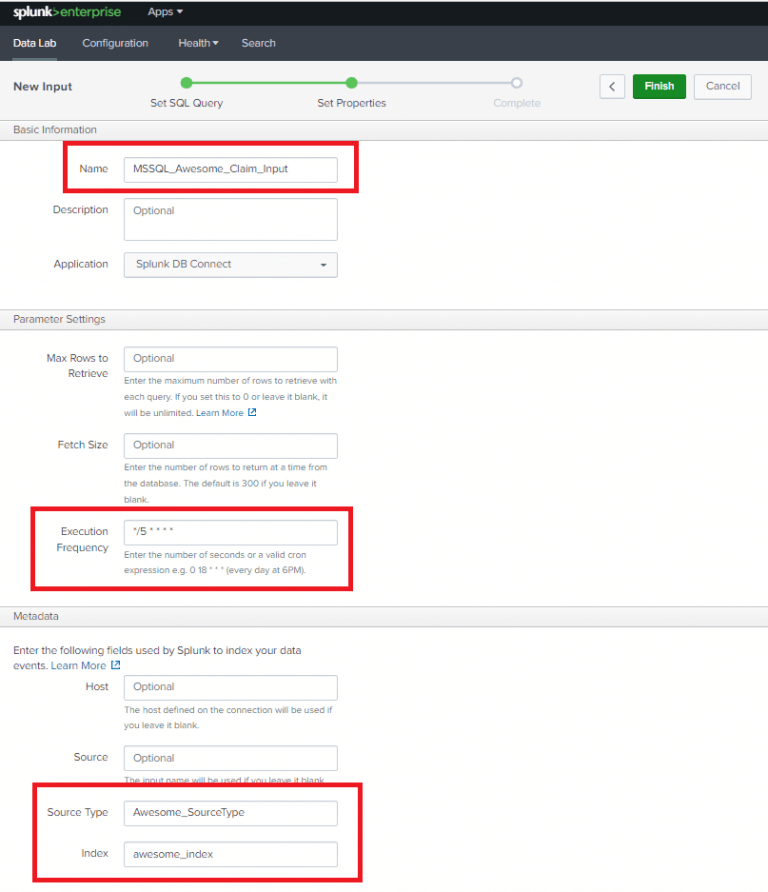
Business Analytics using Splunk and Database
Deplying the Splunk - Deploying Splunk.pptx
How to Send your RADIUS Logs to Splunk | Keytos Docs
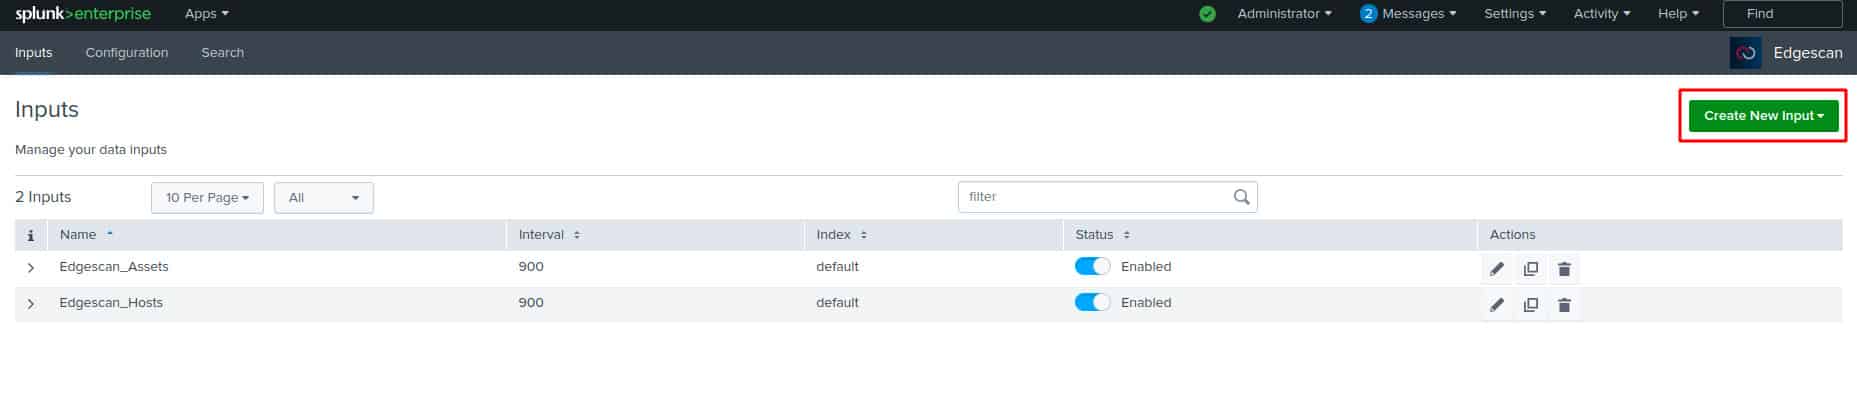
Splunk | Edgescan
Splunk Integration Guide
Exporting test runs to Splunk | Sergio Freire
Splunk Dashboards Tutorial at Frank Warner blog
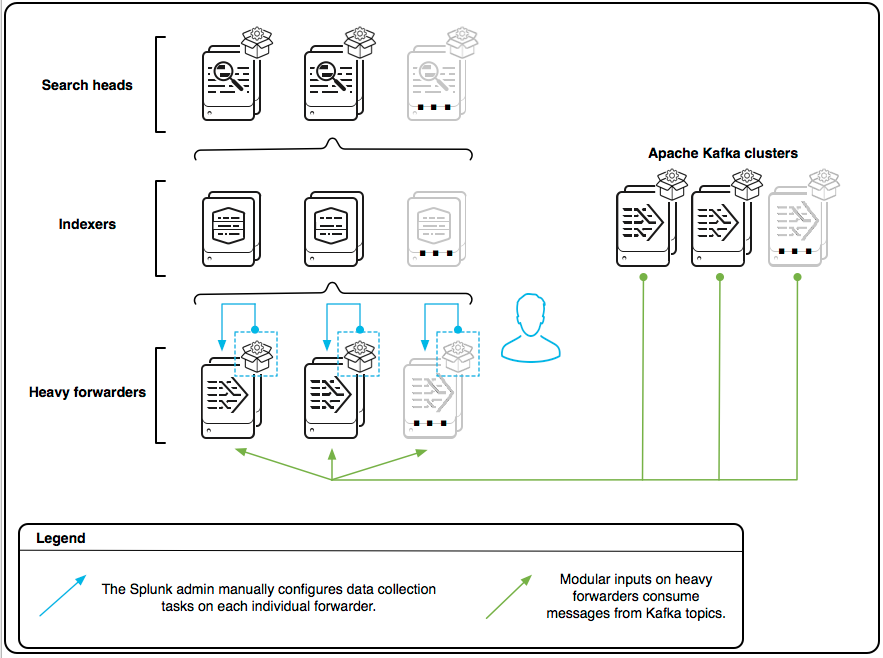
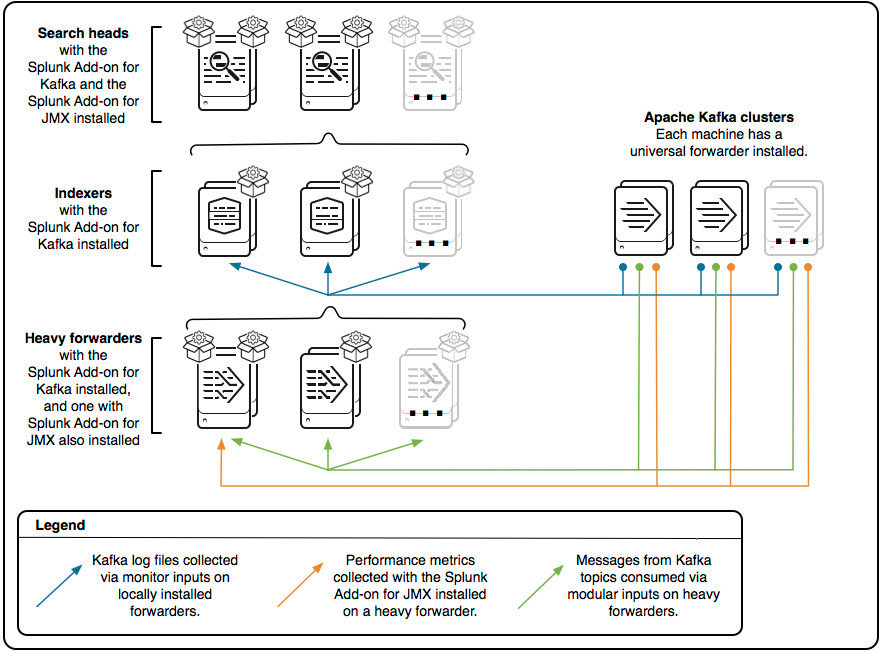
Inputs for the Splunk Add-on for Kafka - Splunk Documentation
Solved: Splunk Addon data-inputs duplicate events - Splunk Community
Splunk | PPTX
ICYMI: Splunk Events Integration now available - New Releases - Sensu ...
Dashboard Studio: Show (Or Hide) The Latest Features in Splunk Cloud ...
Splunk Architecture Guide – Splunk Architectures – YTXPJ
Medium
TryHackMe | Splunk: Basics – Igor_sec's Blog
Splunking with Sysmon -Global Information Security Society of Pakistan
Splunk_Data_Inputs - Mist
Starting with Splunk: A Comprehensive Guide for Beginners
ИБ по частям: Splunk. TCP Input's