Showing 120 of 120on this page. Filters & sort apply to loaded results; URL updates for sharing.120 of 120 on this page
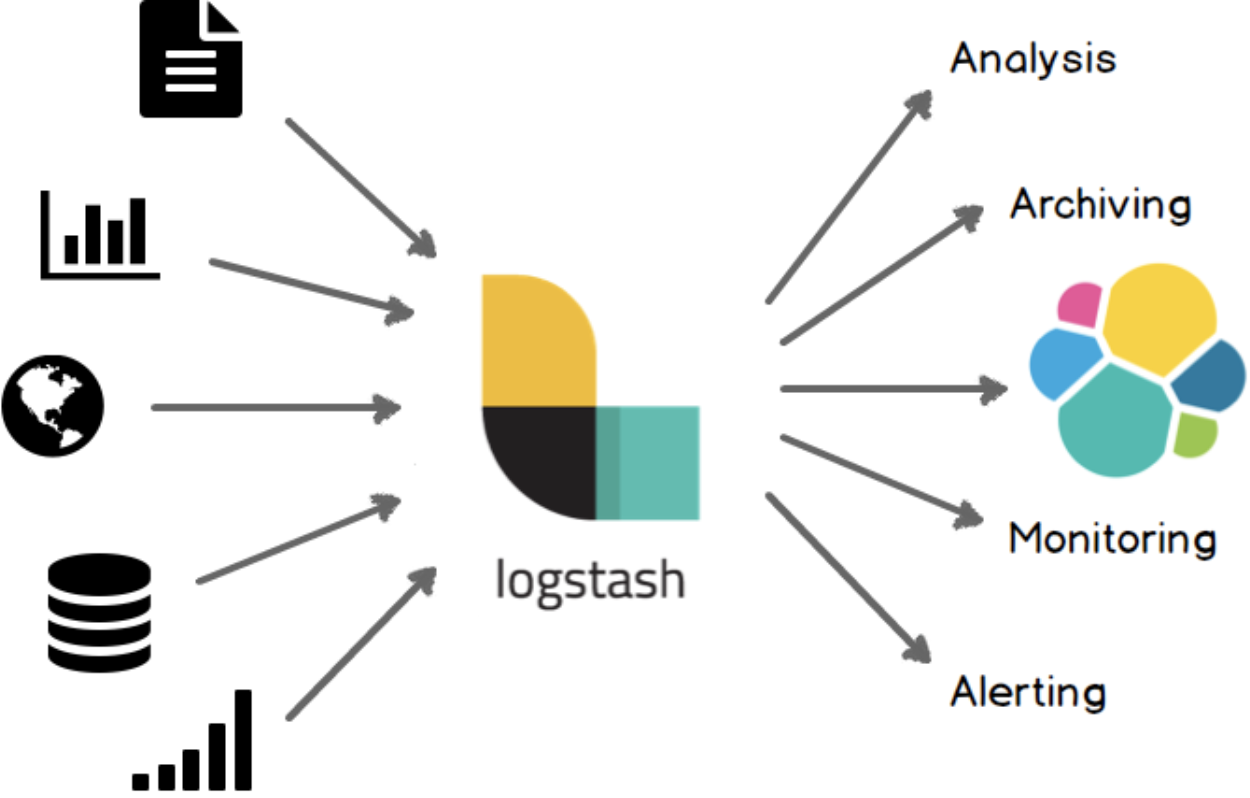
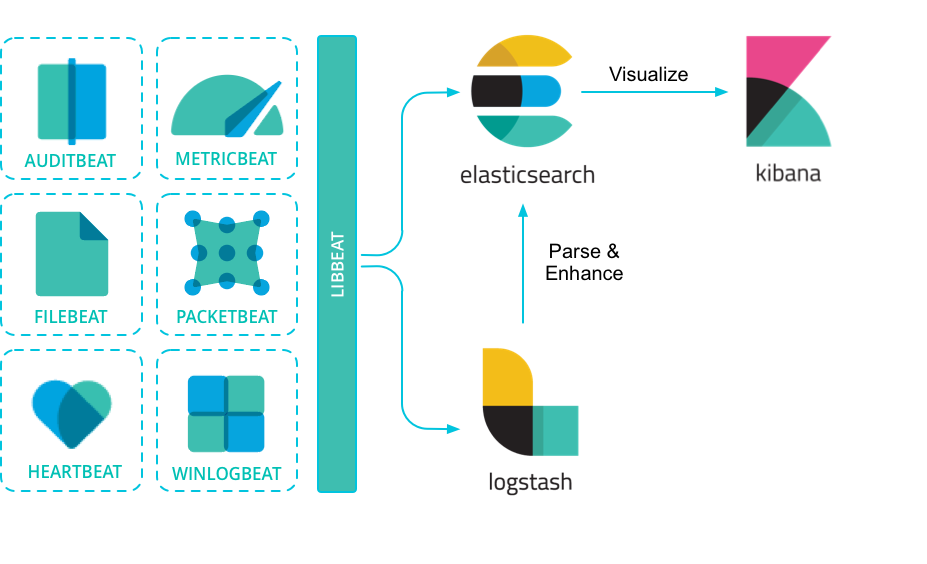
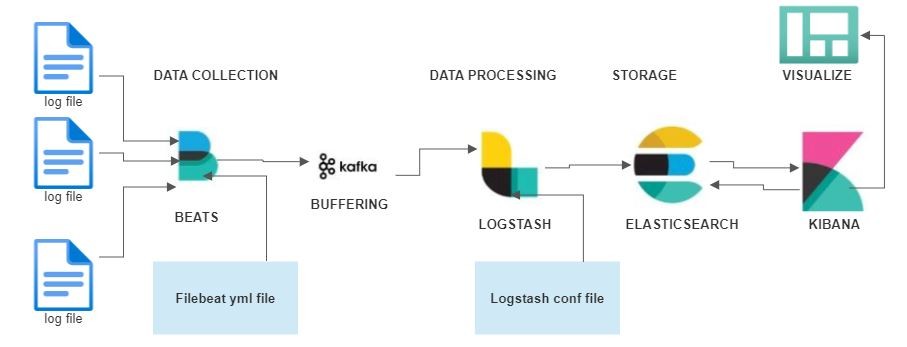
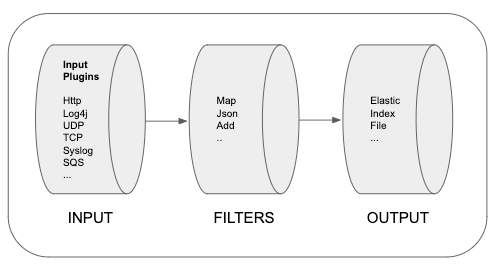
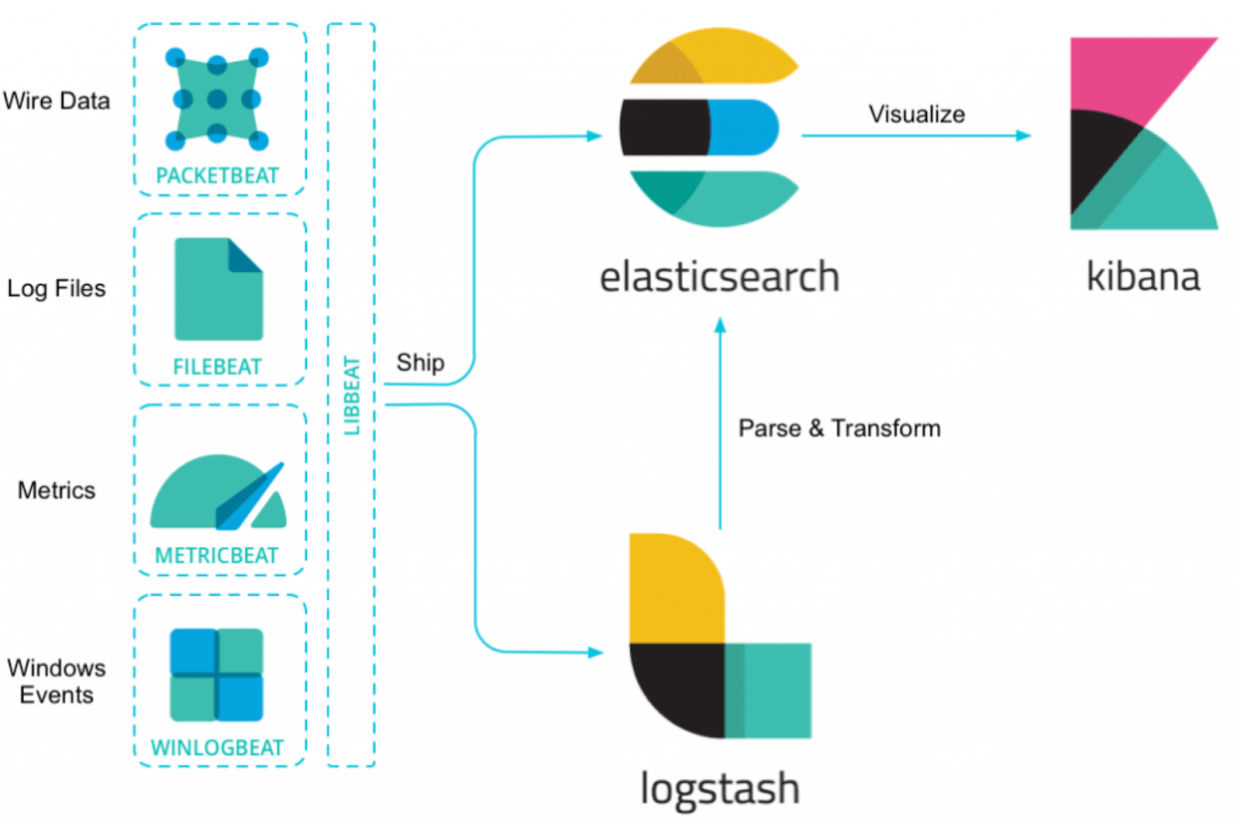
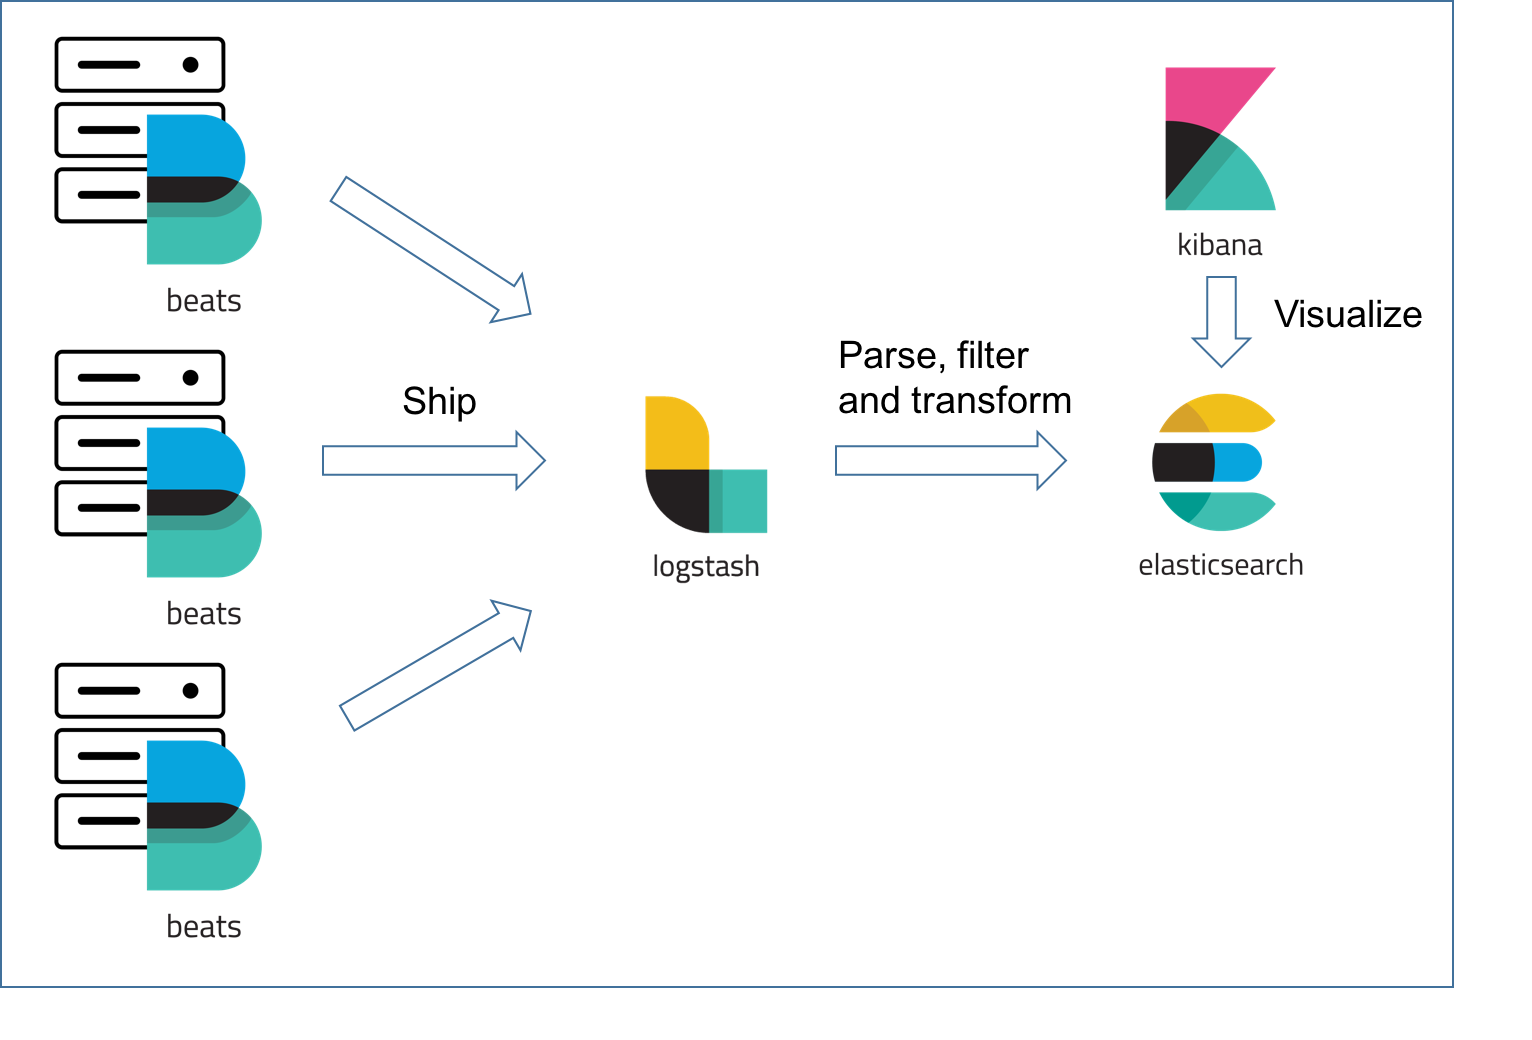
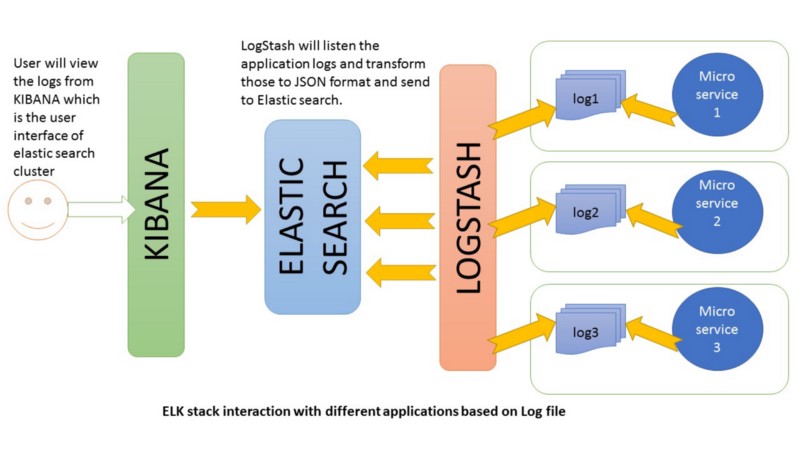
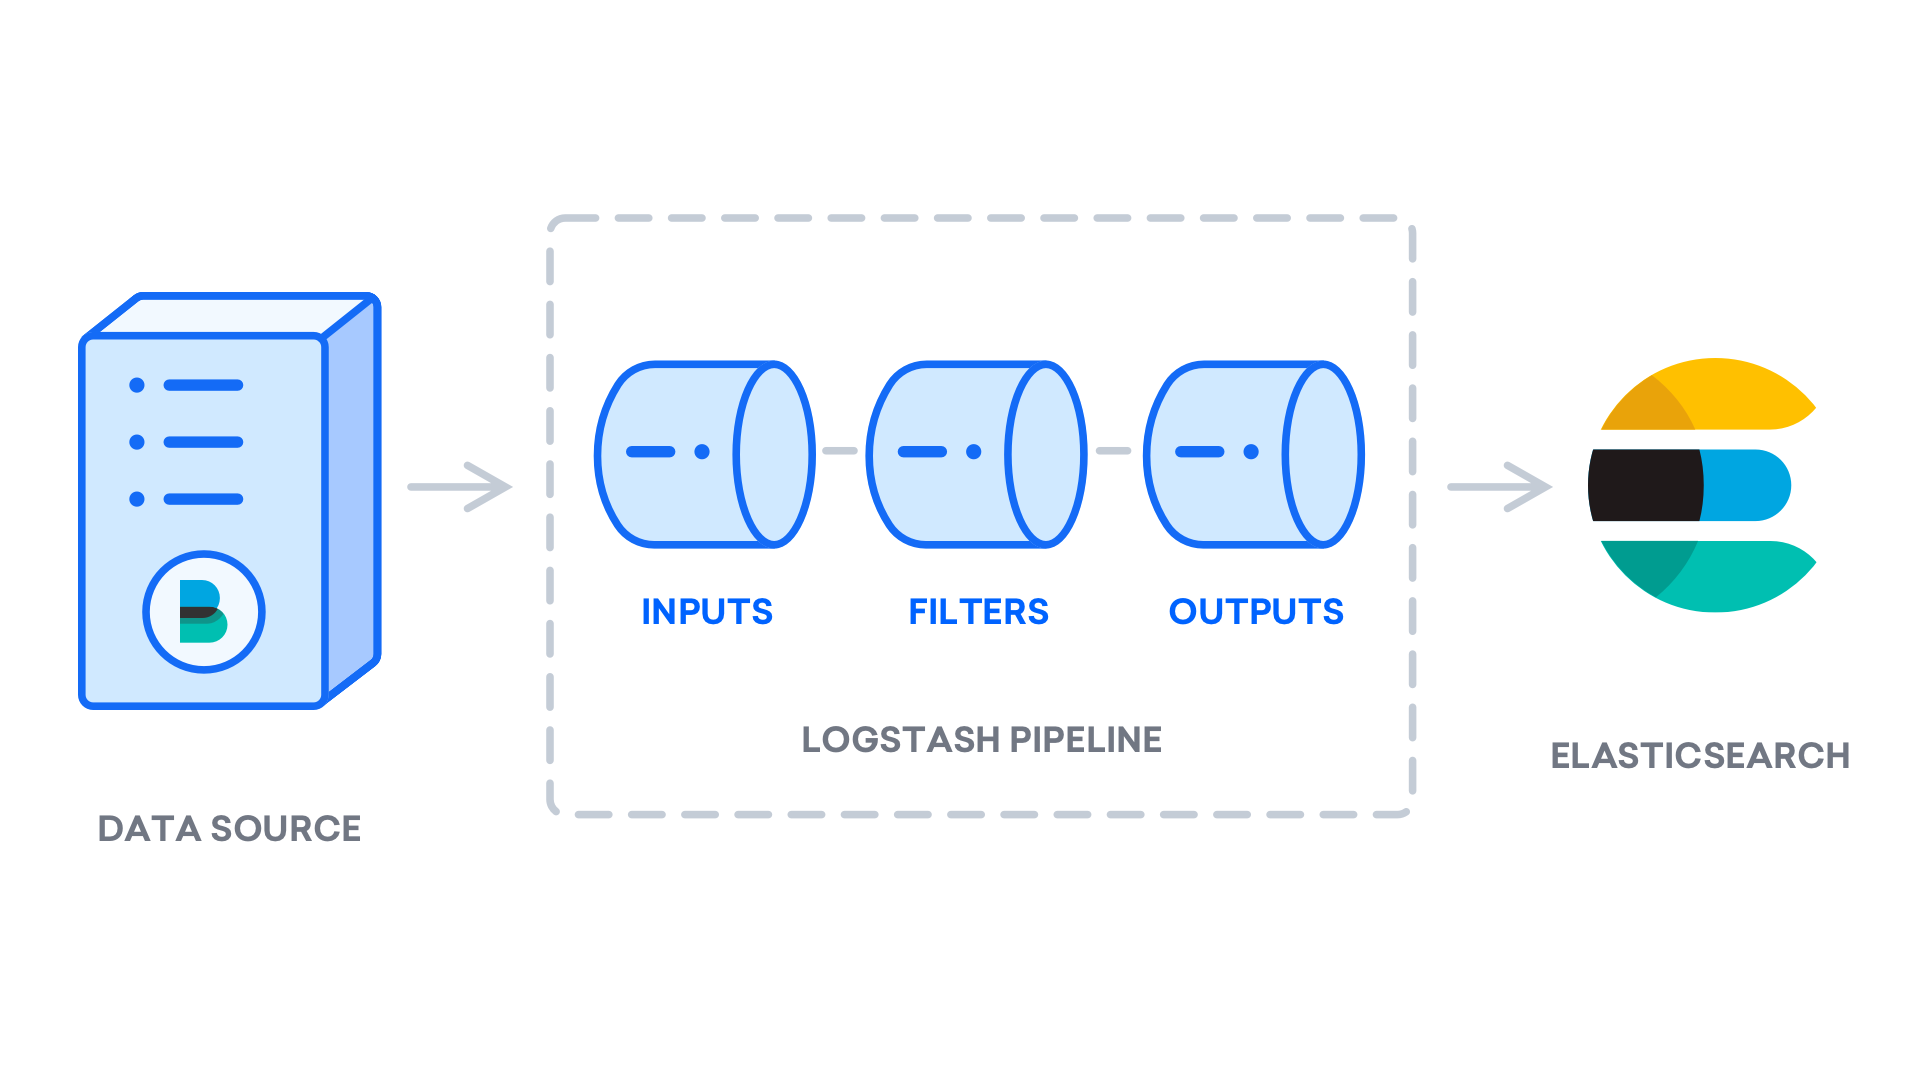
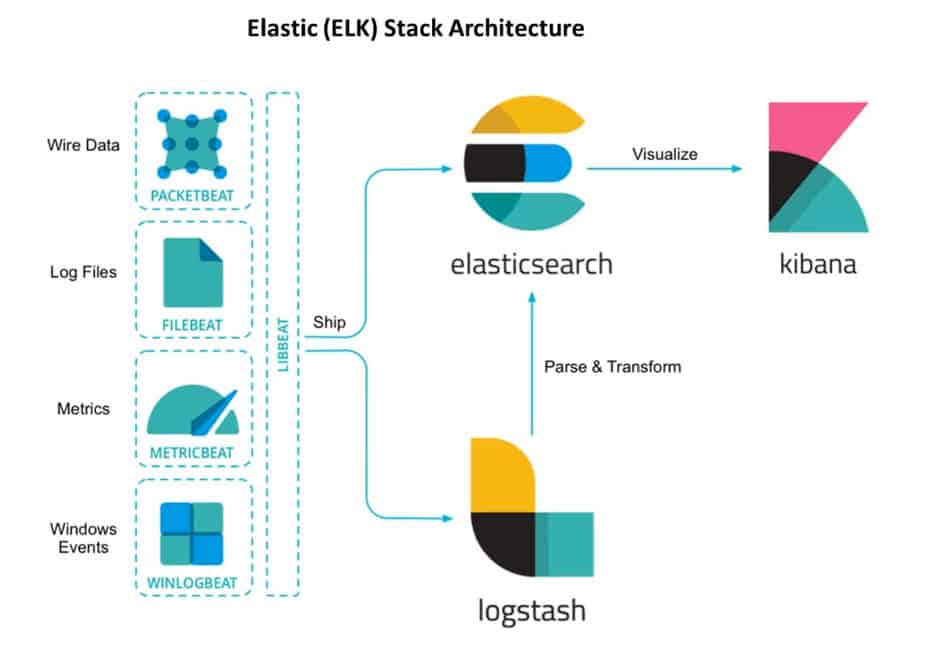
Workflow of the Elastic Stack log ingestion and processing. | Download ...
Start your log collection and analysis with Elastic | Elastic
Unlocking security data sources with the Elastic Stack | Elastic Blog
How to extract all log sources in ELK? - Elasticsearch - Discuss the ...
Yazılım Çorbası: Elastic Stack - Log Management
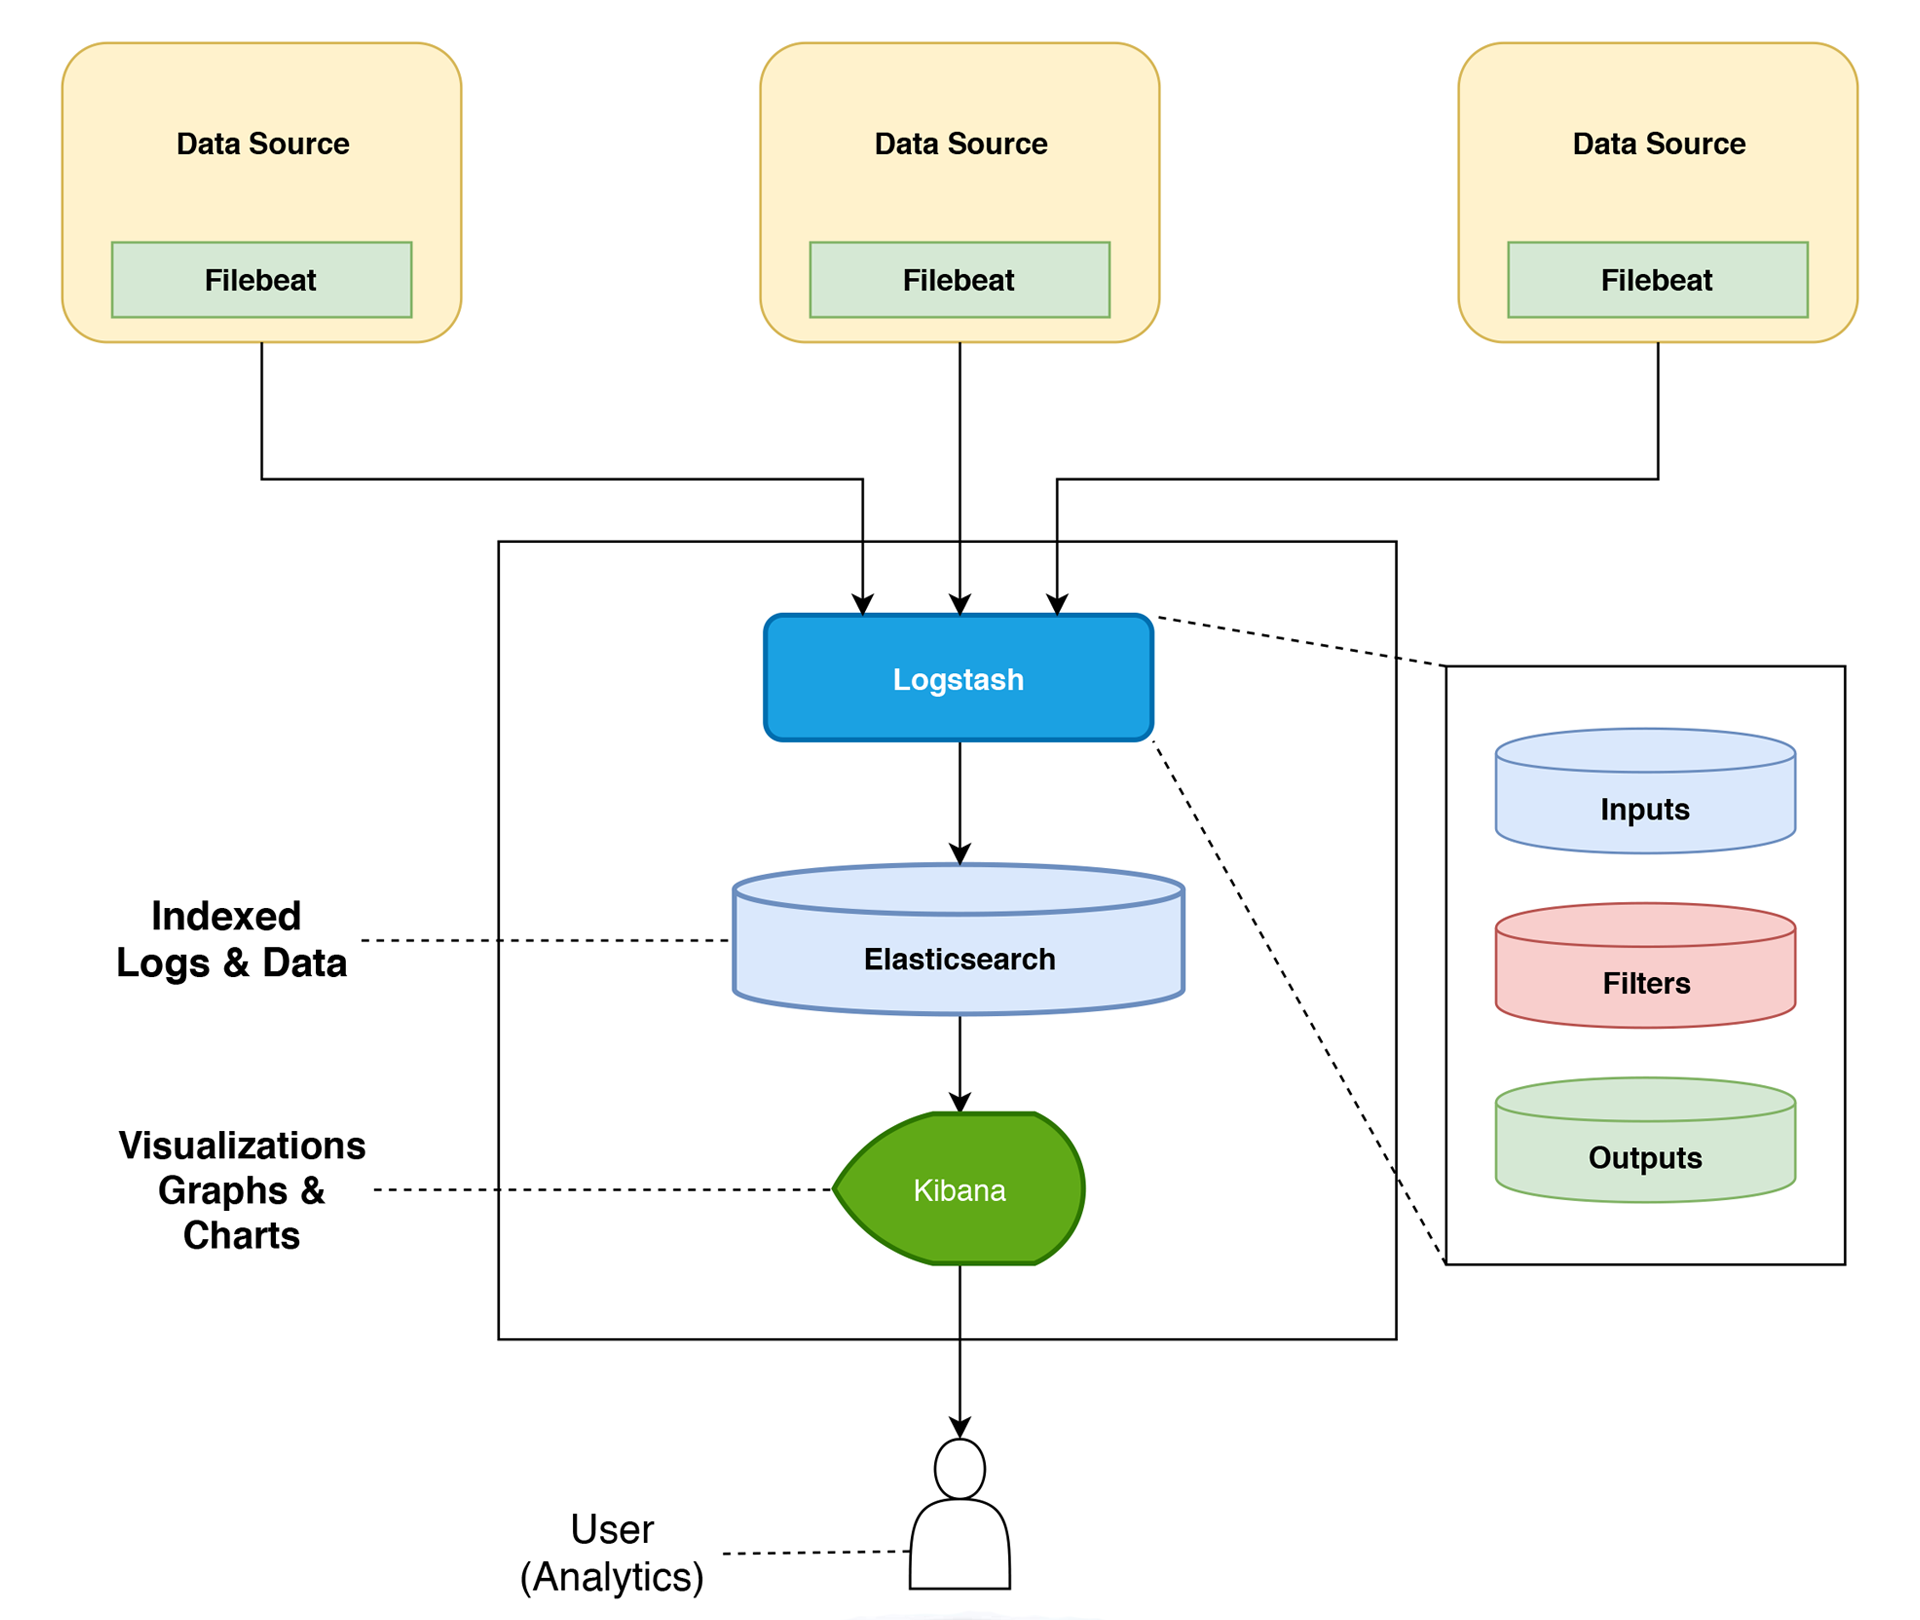
| Three log servers sending their logfiles to the Elastic Stack Server ...
Log analytics | Elastic
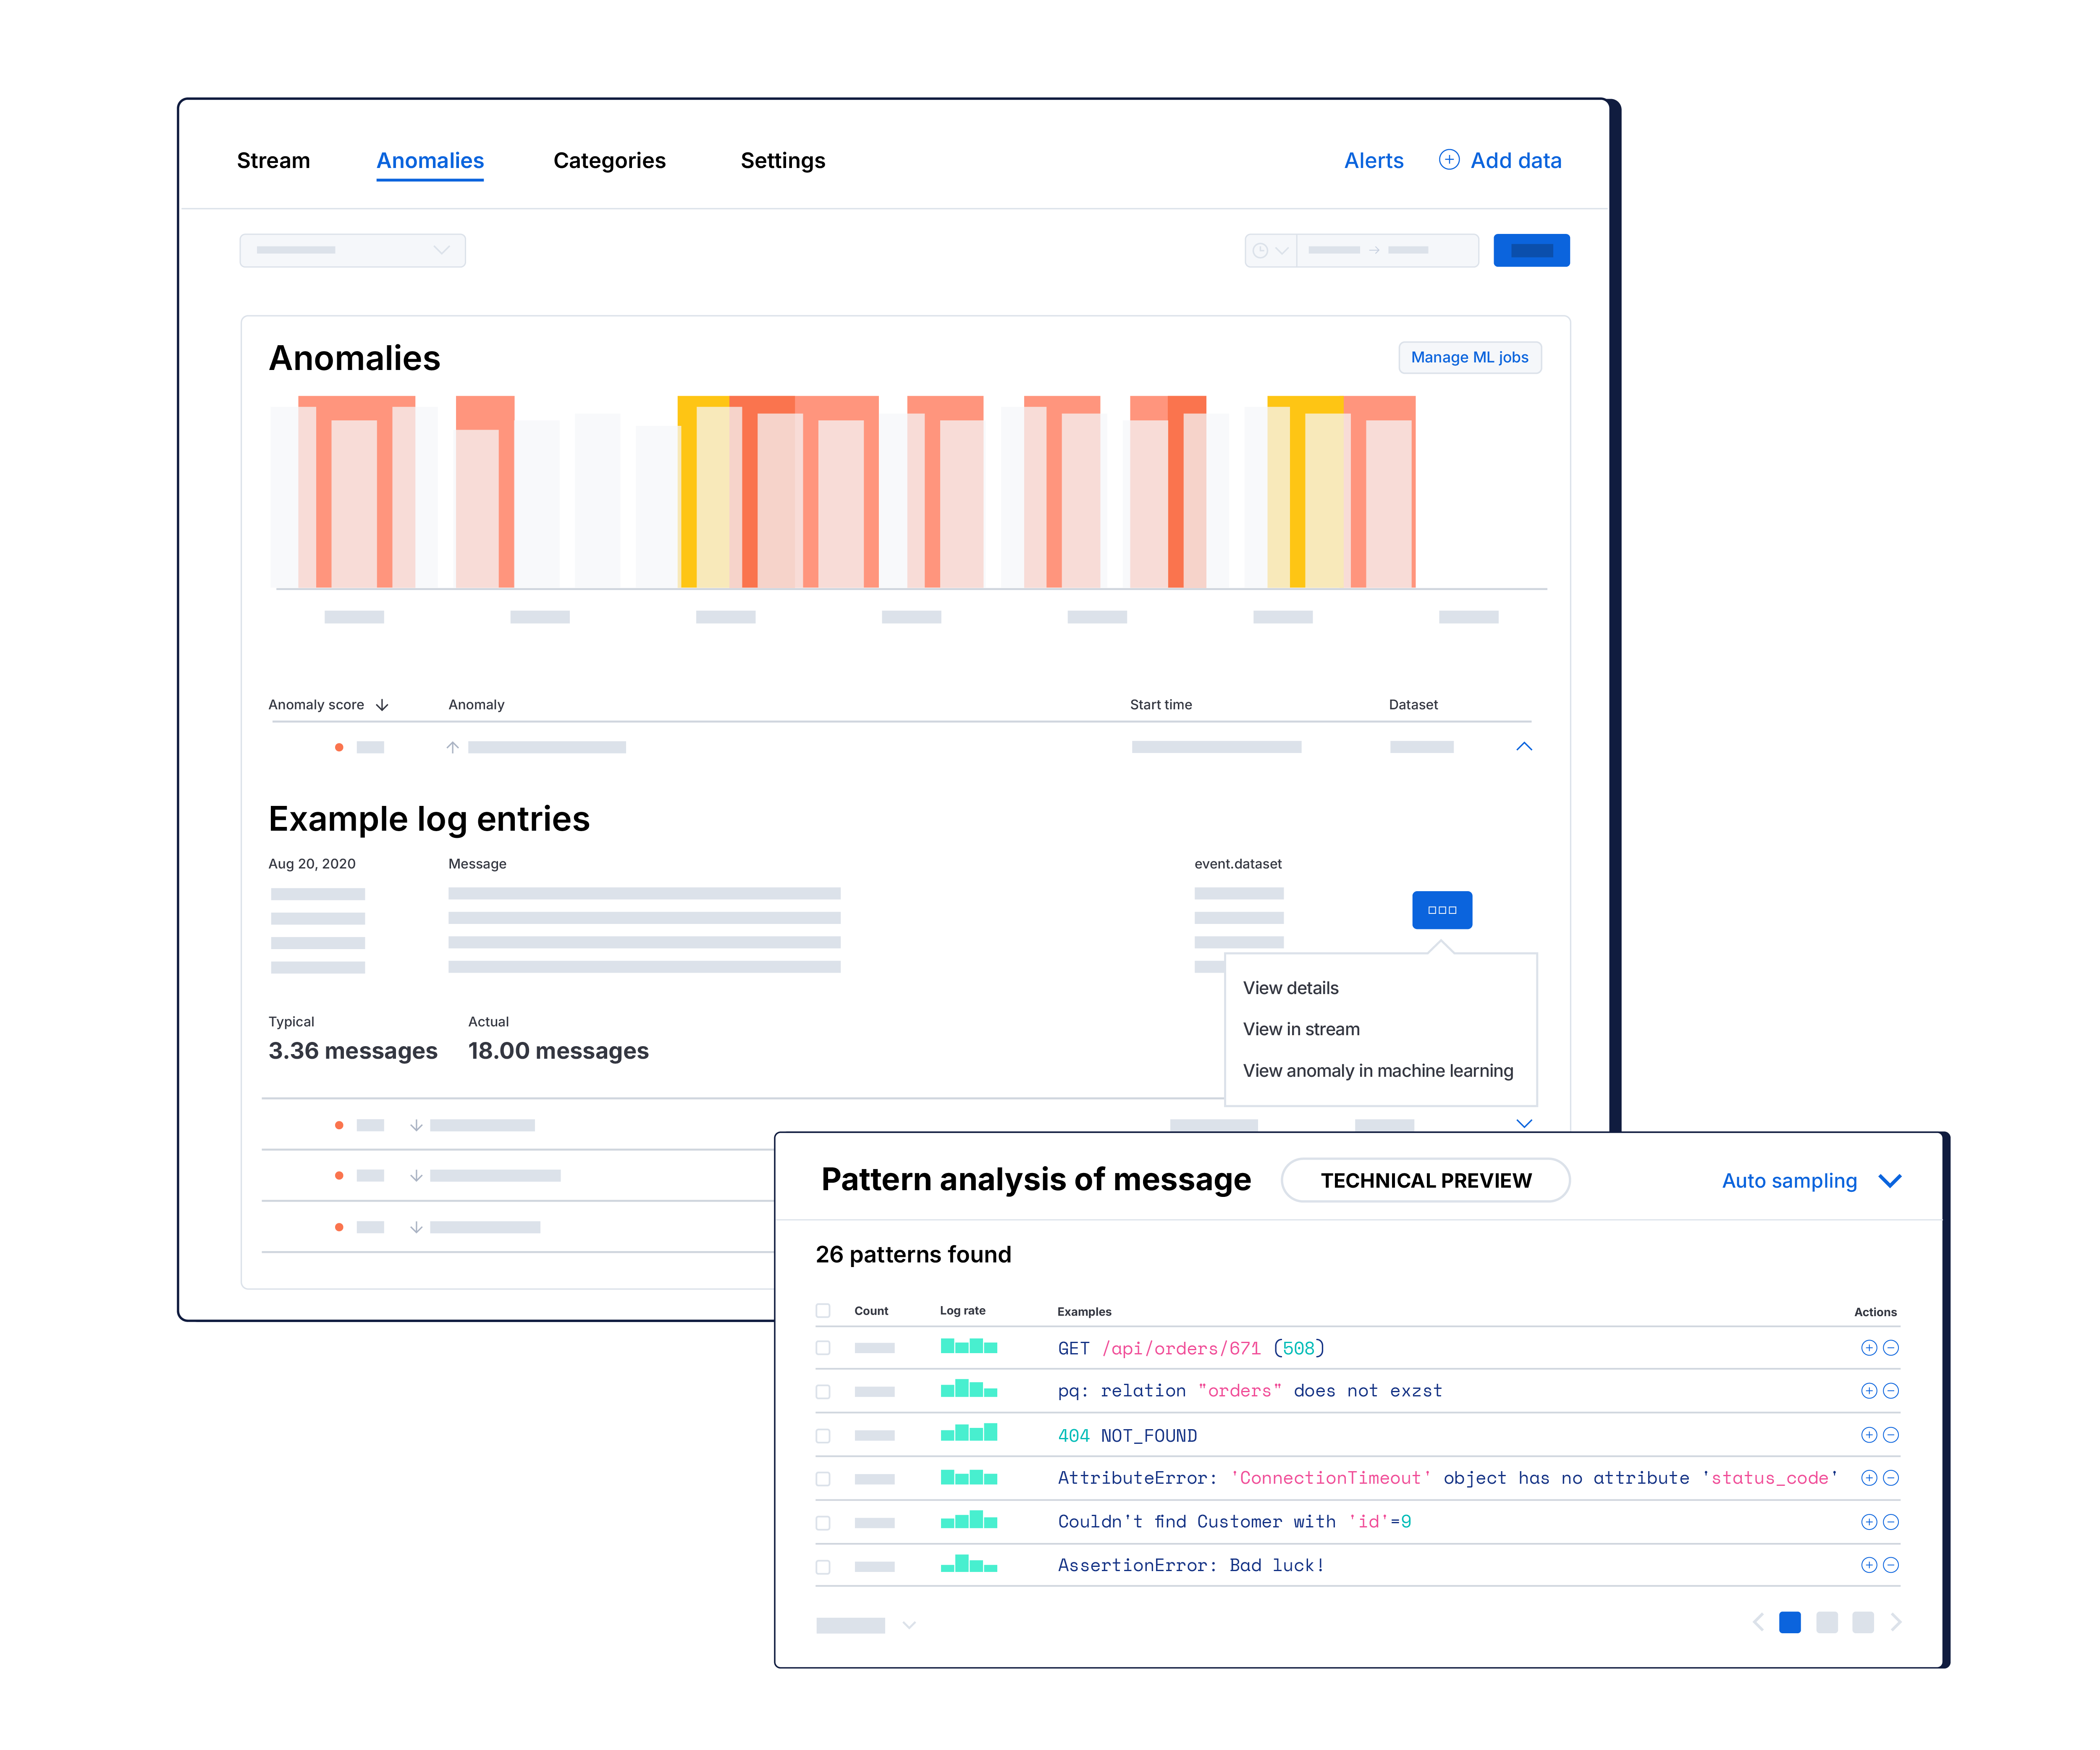
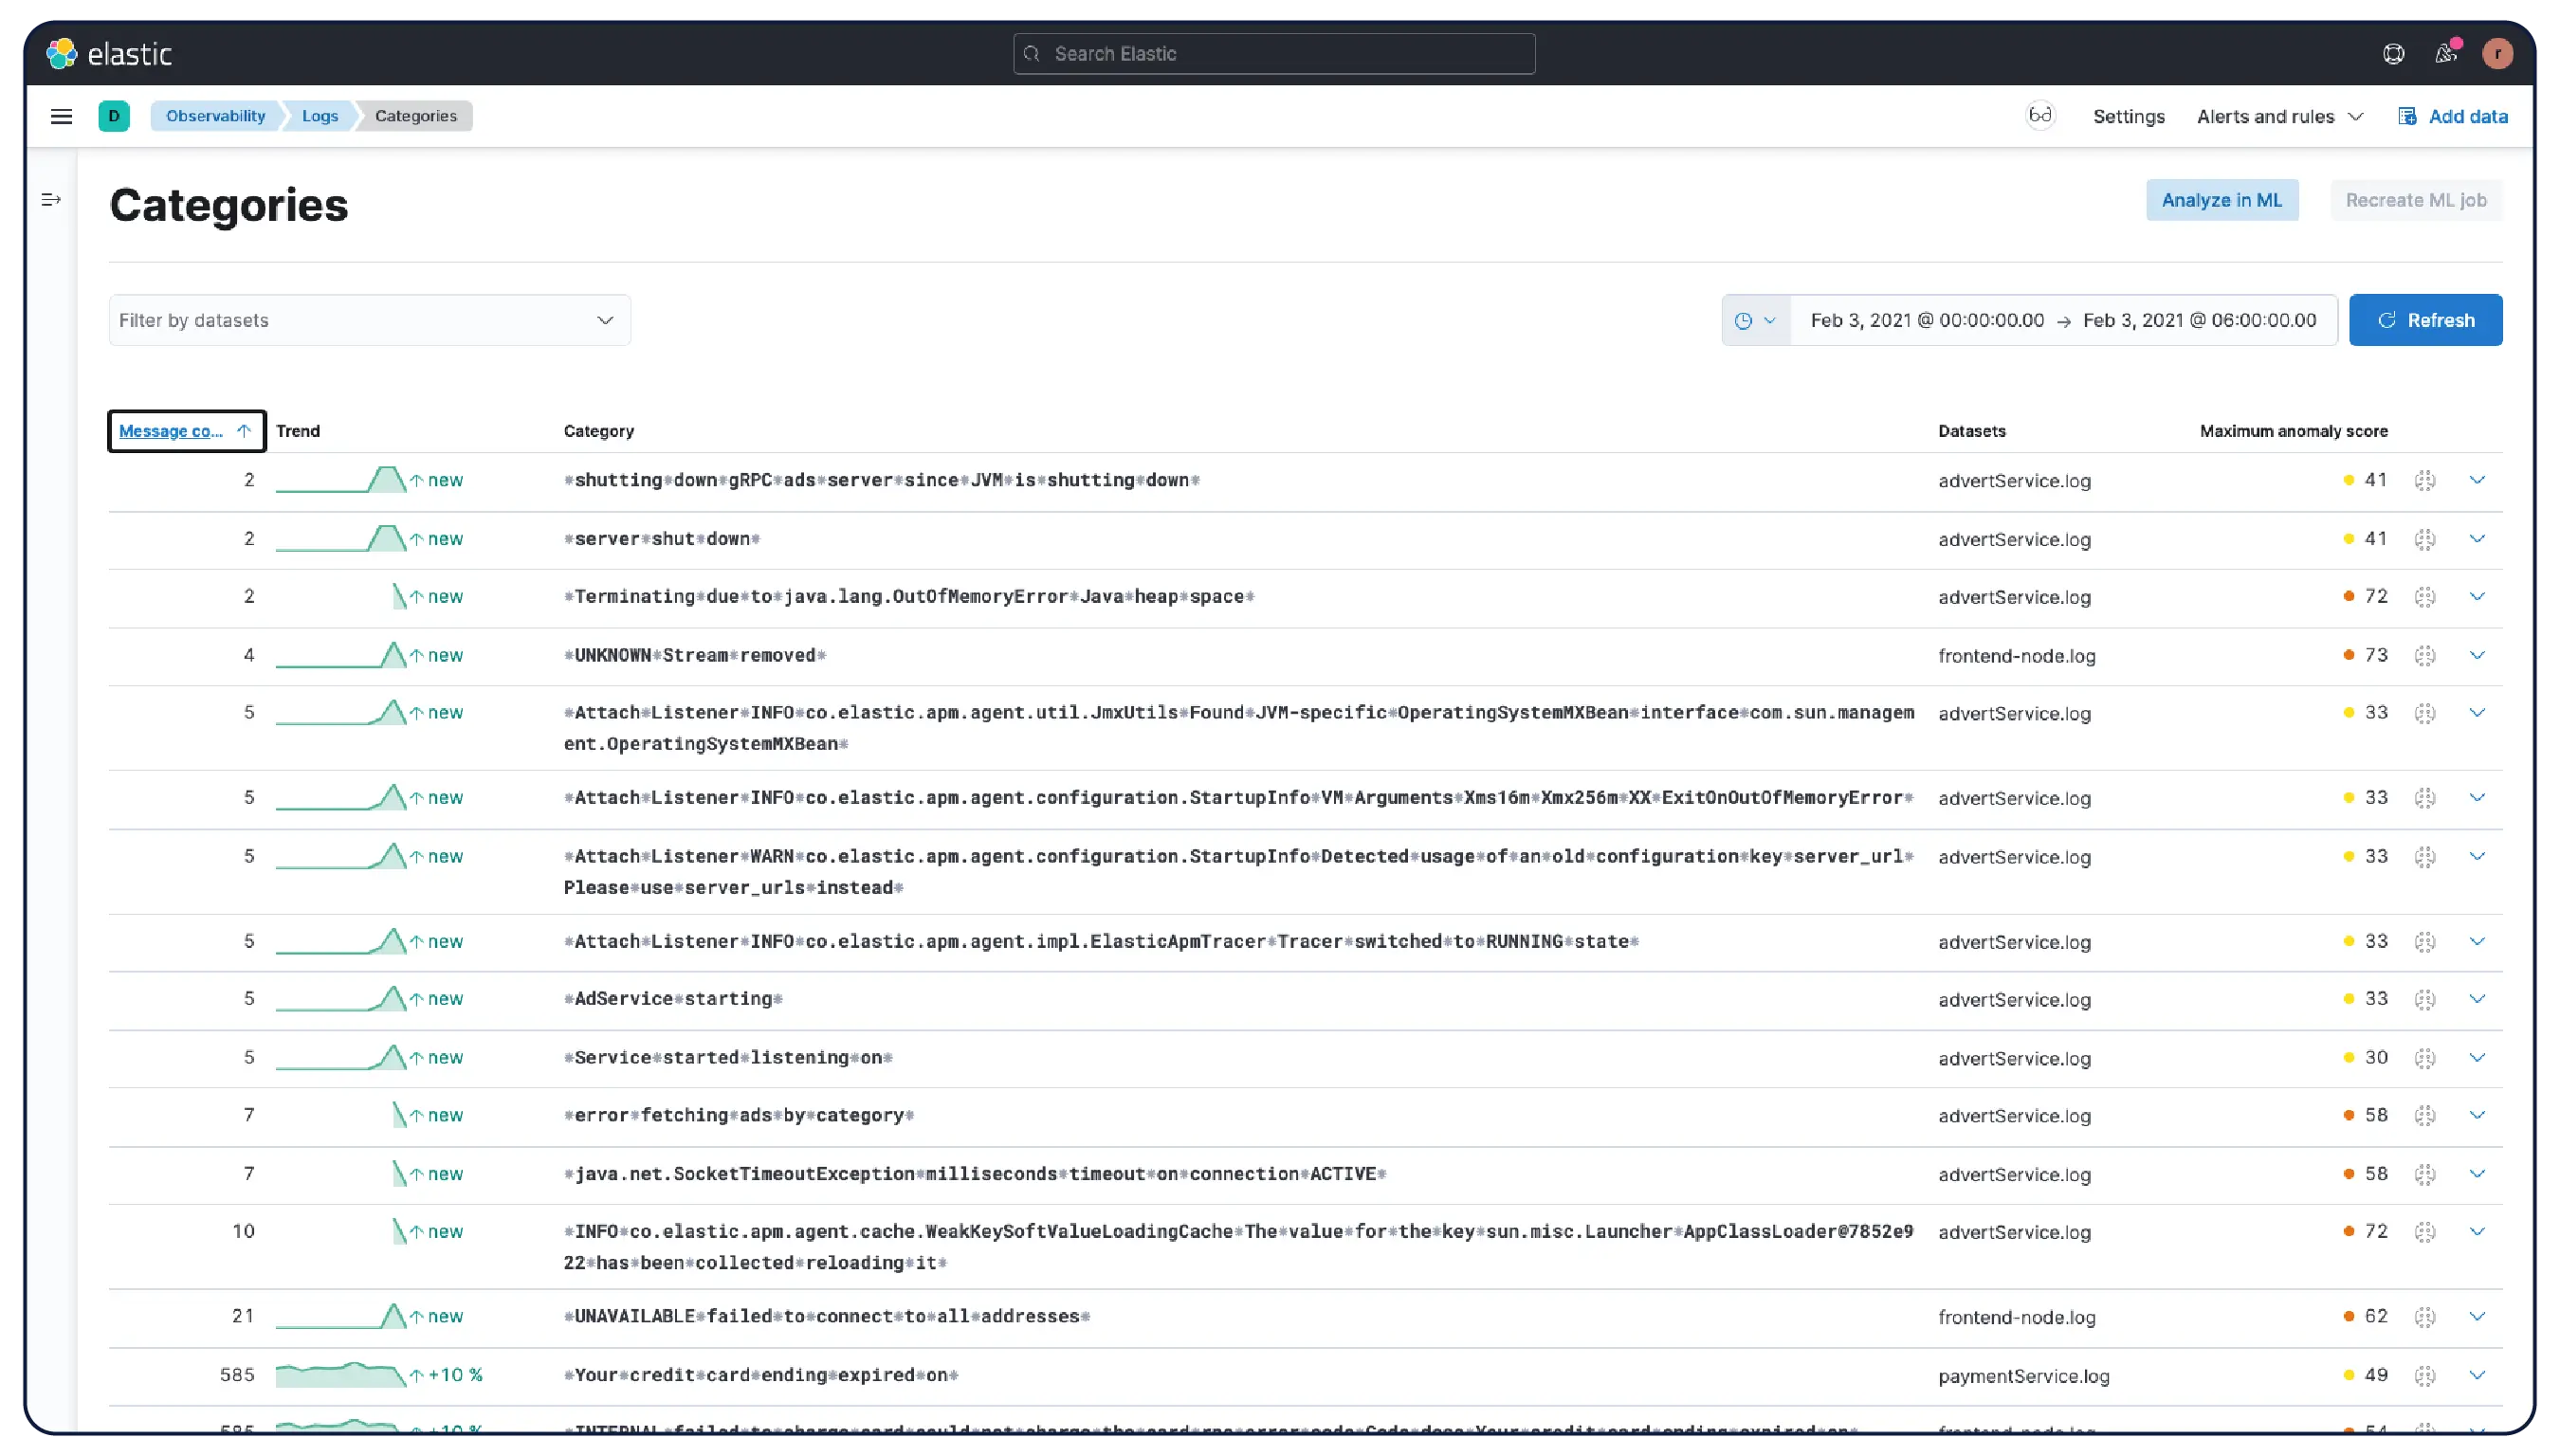
Elastic Logs 7.6 released with log categorization and more | Elastic Blog
Observability Overview - Logs not shown as log source - Elastic ...
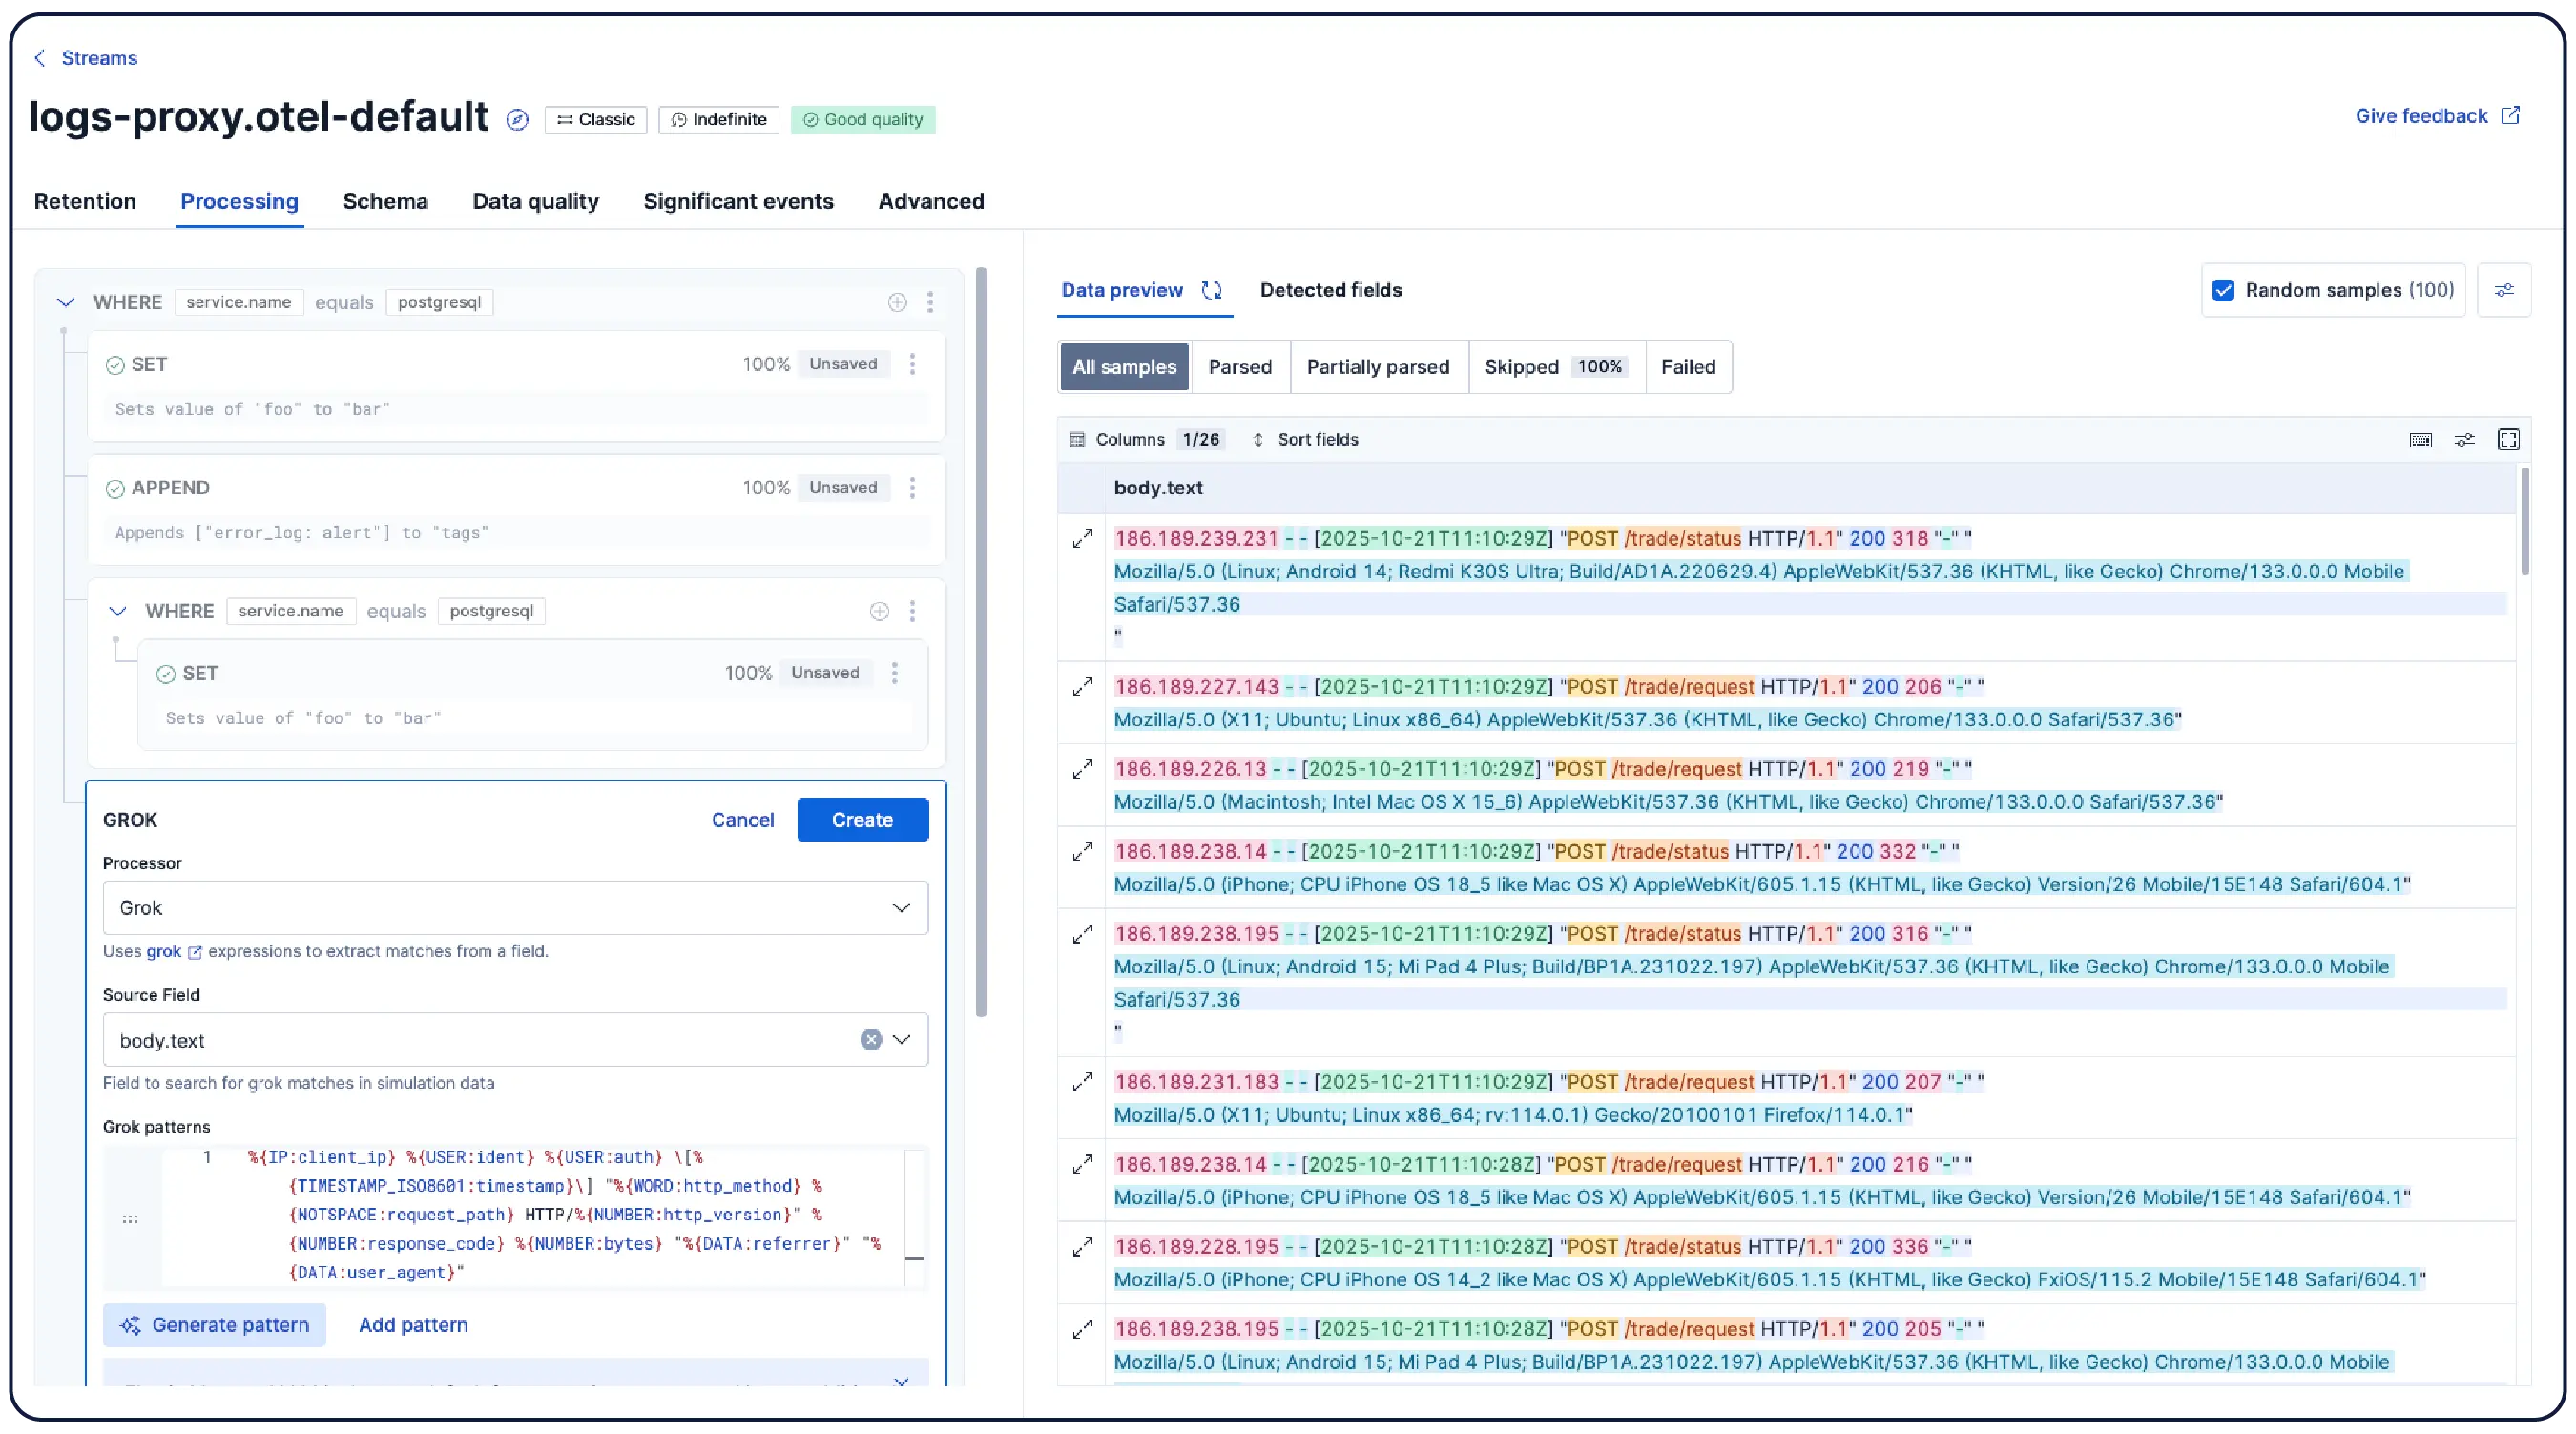
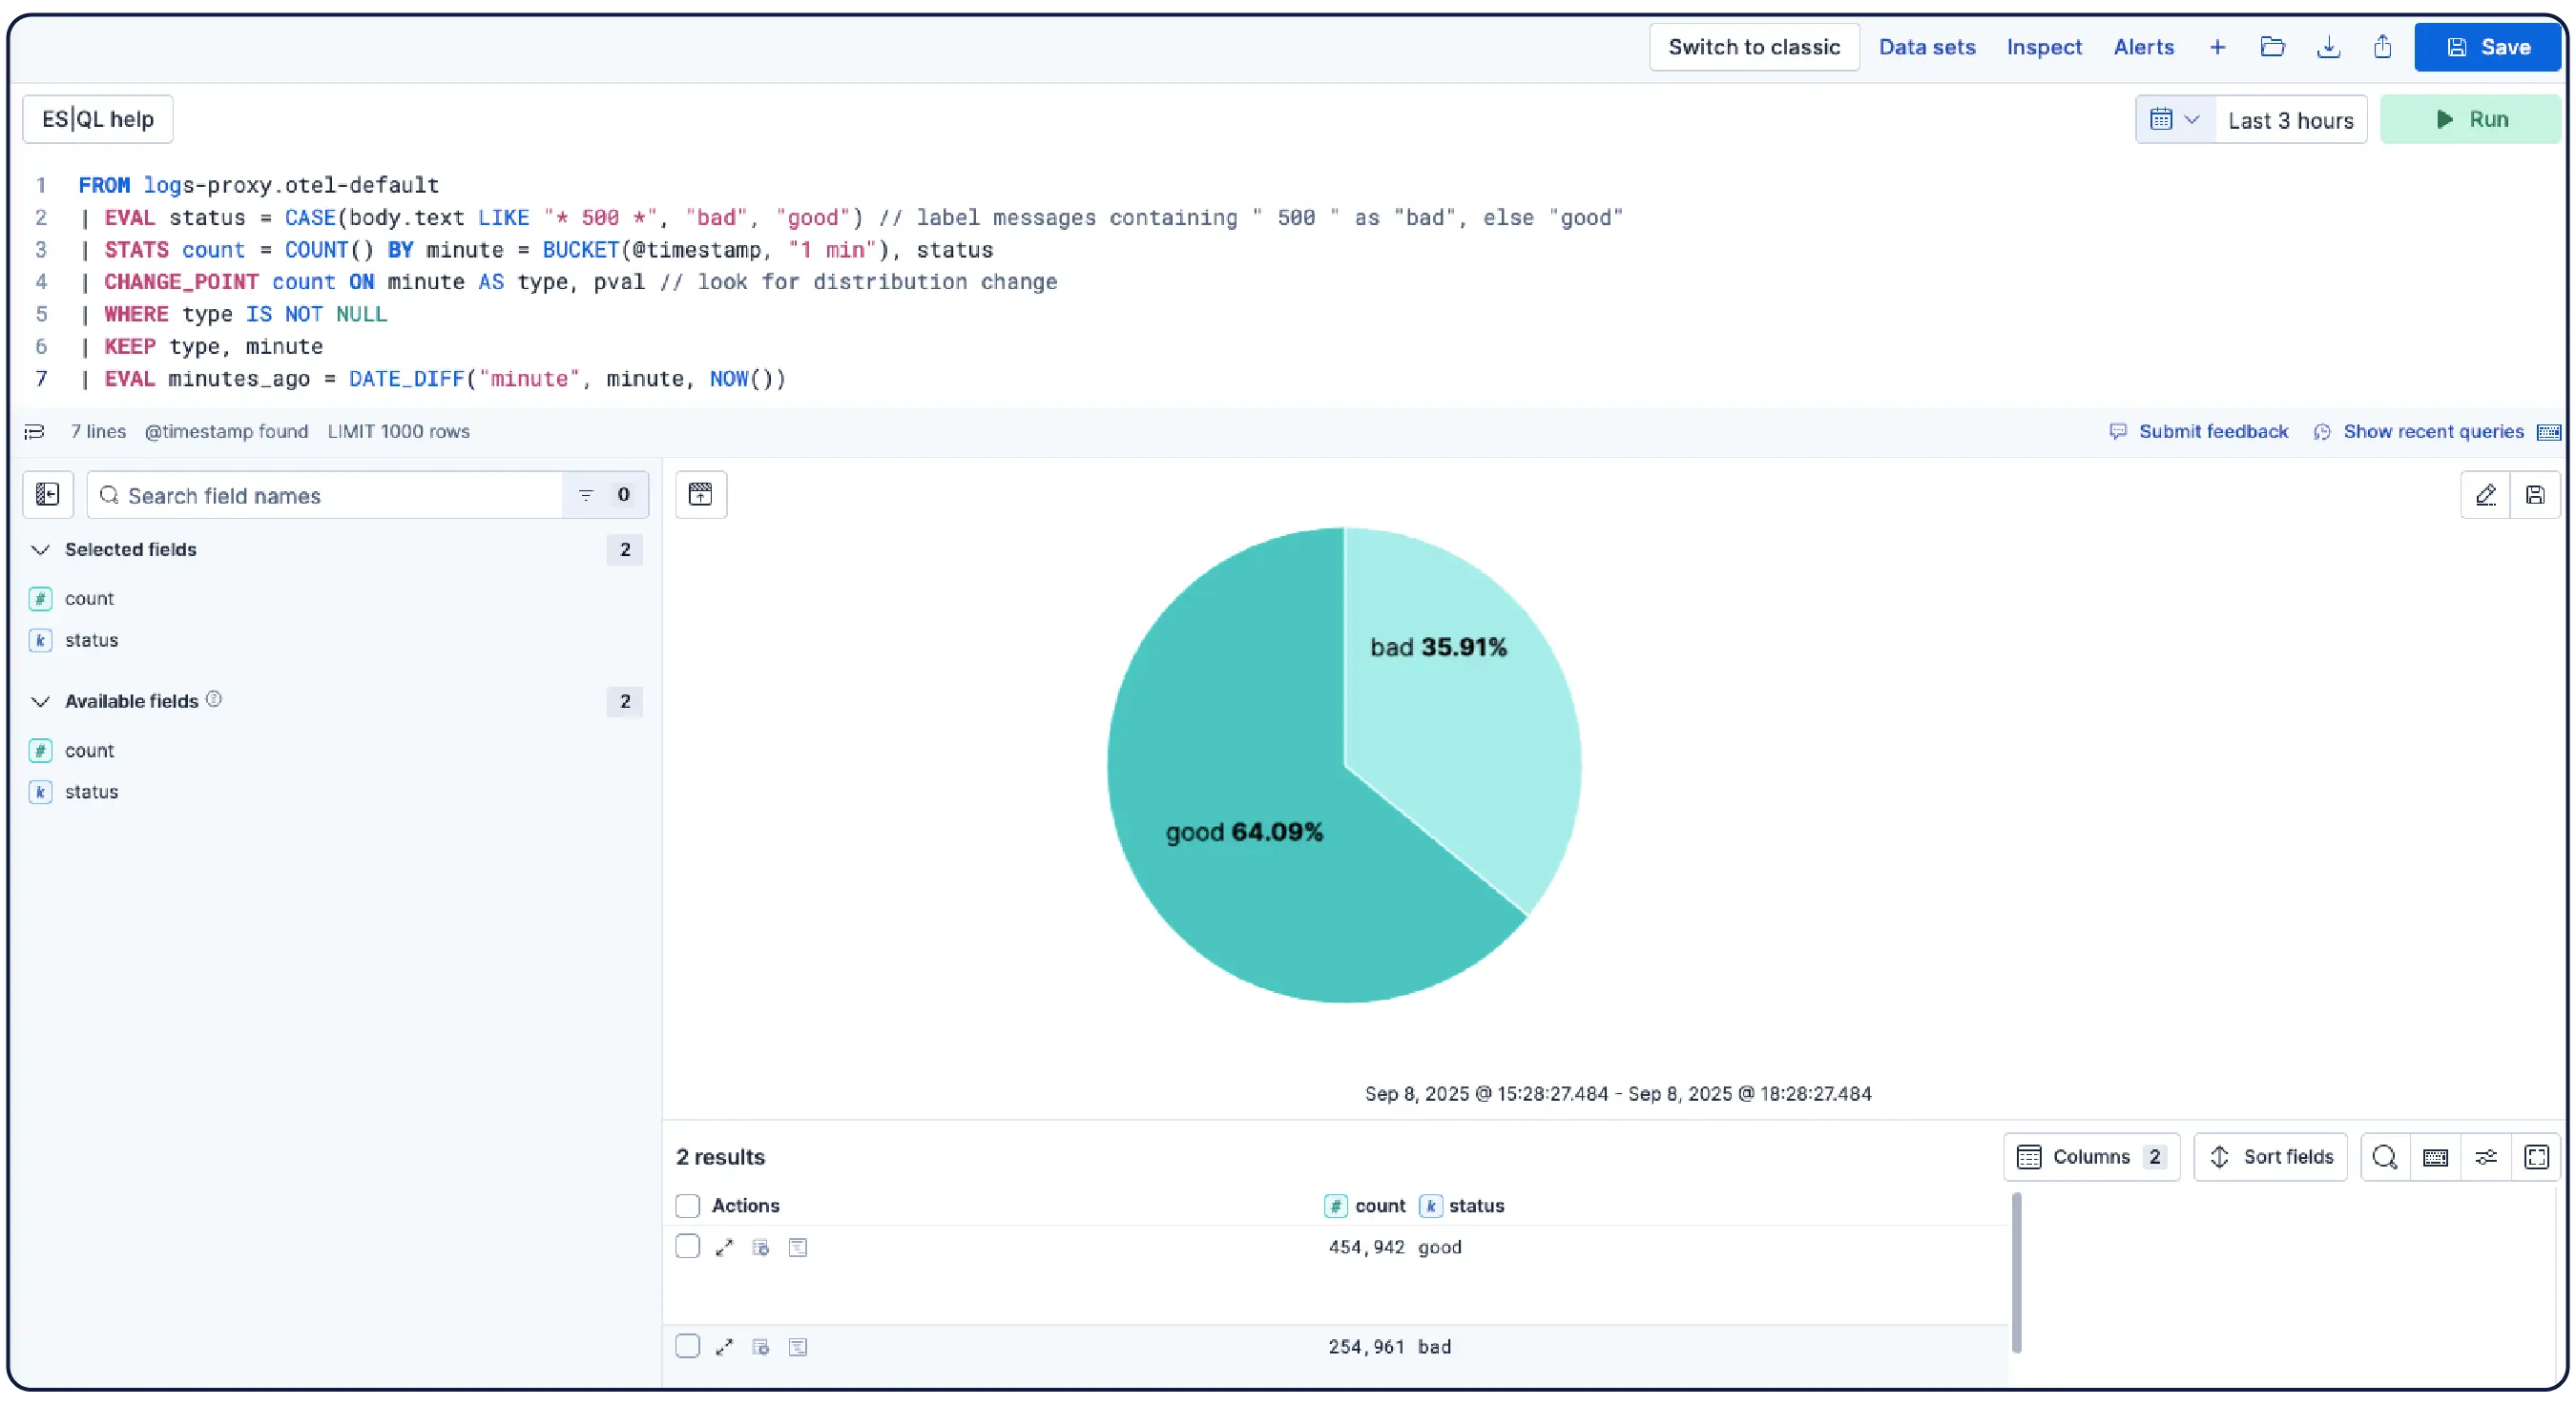
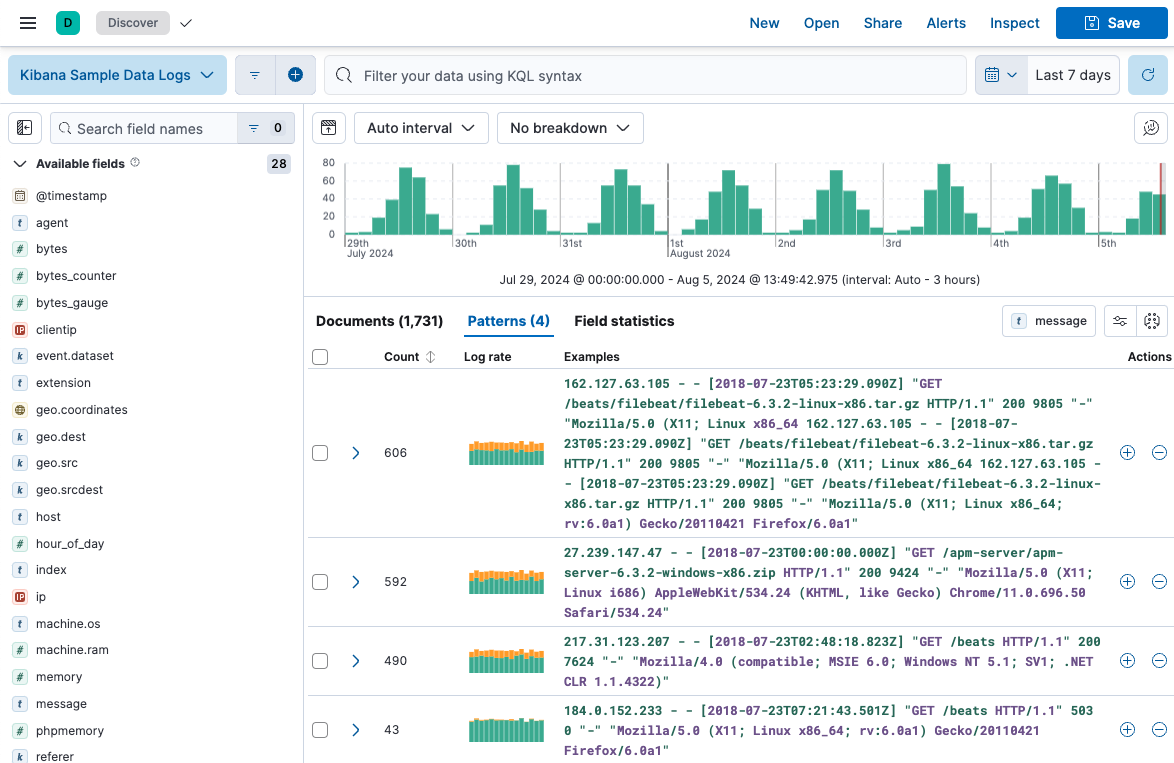
Run a pattern analysis on your log data | Elastic Docs
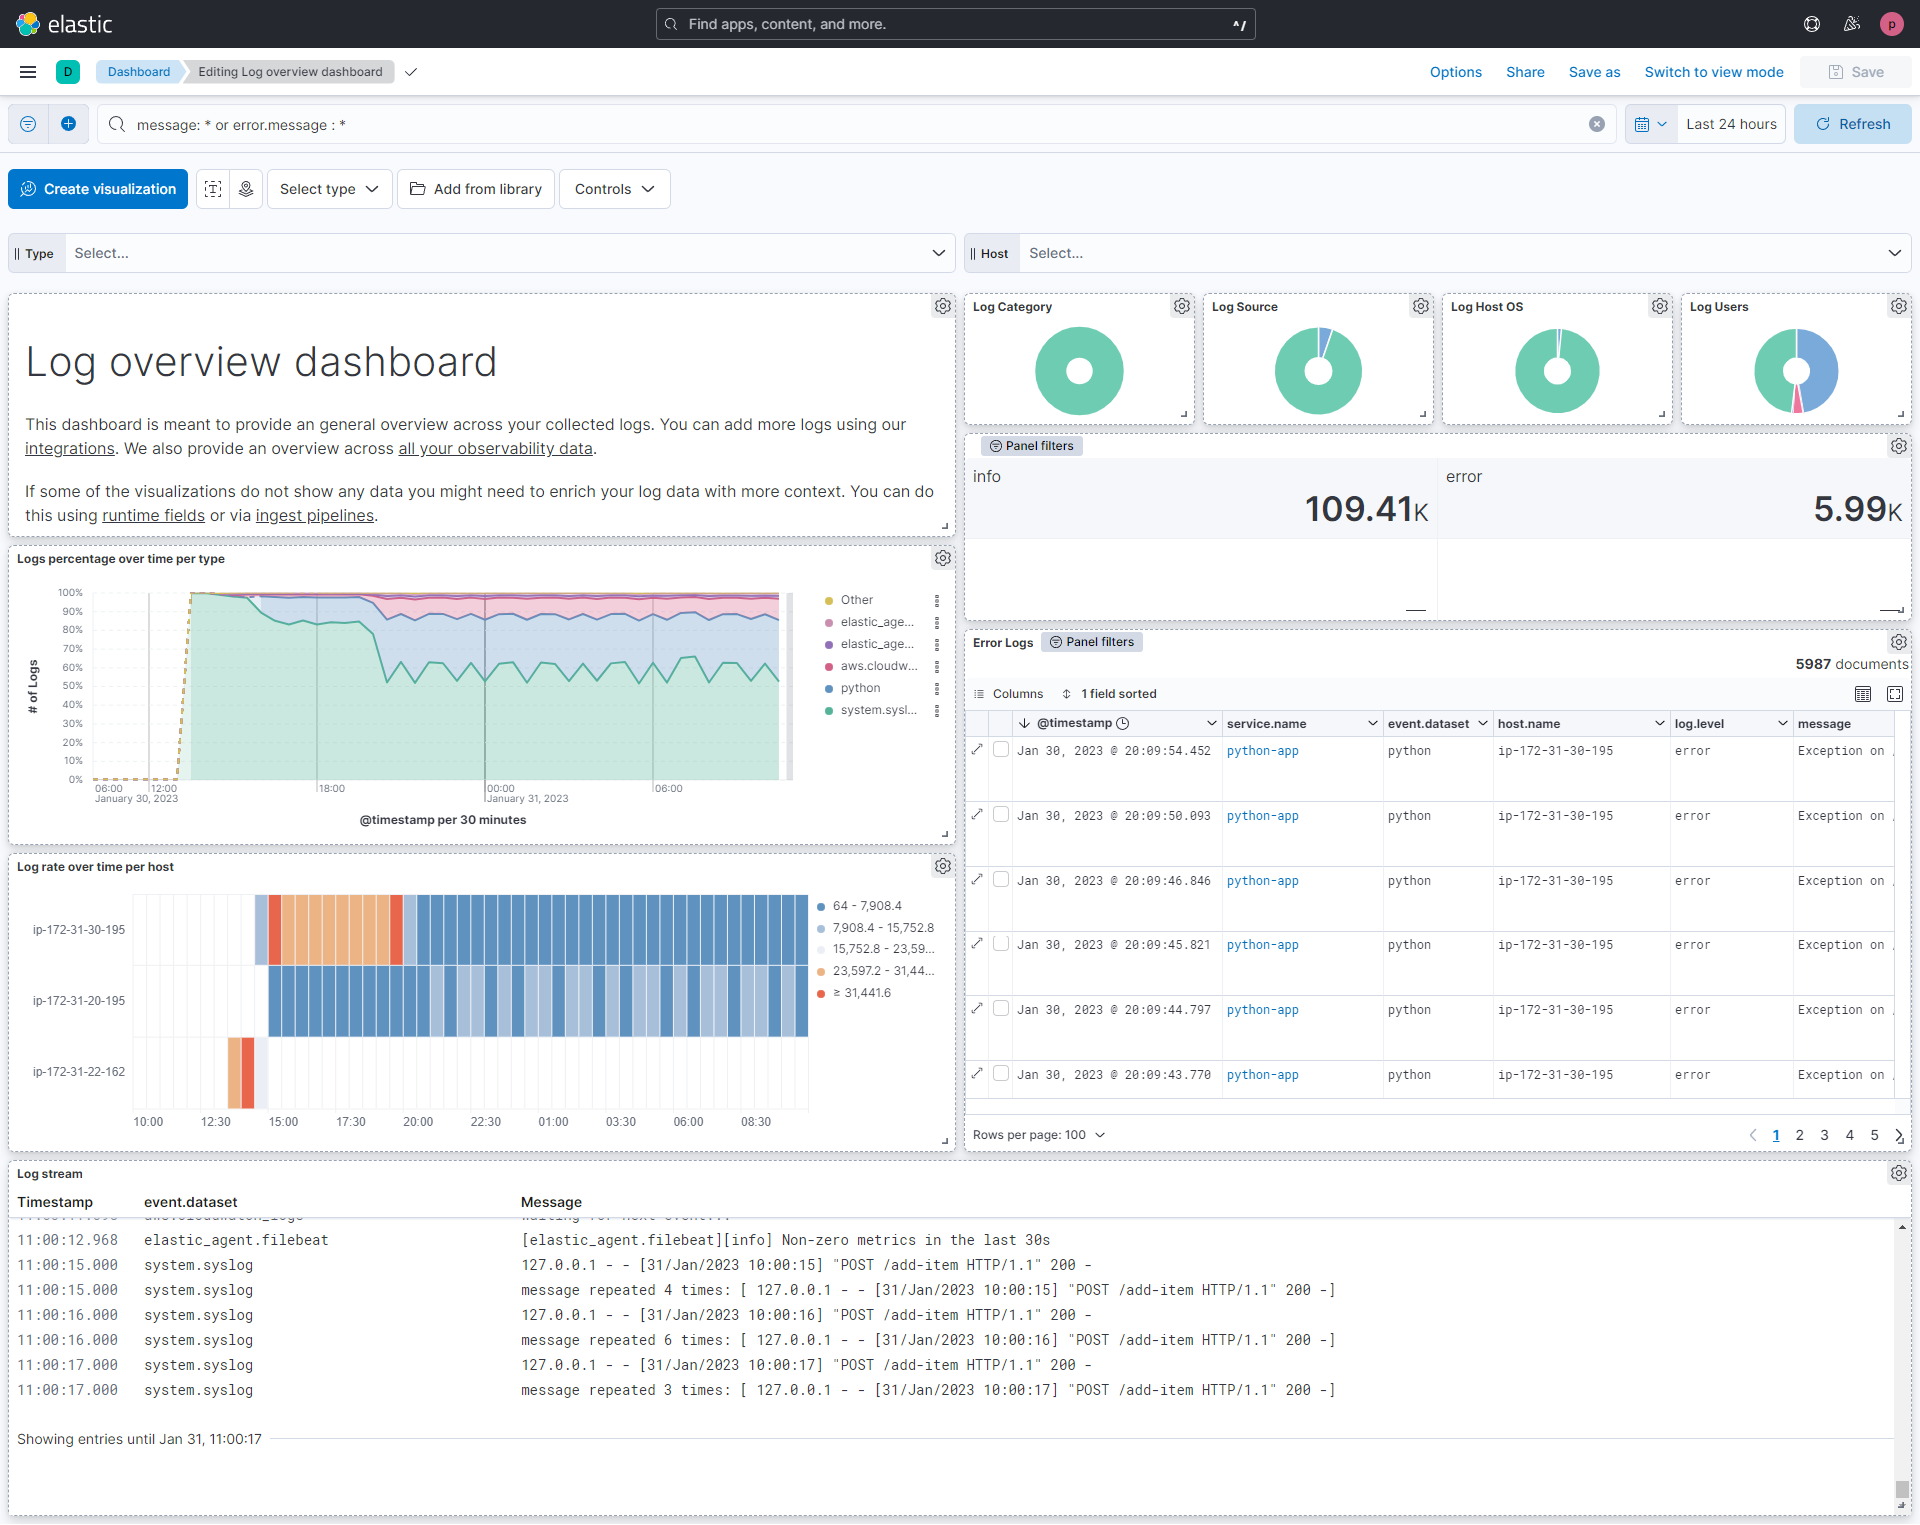
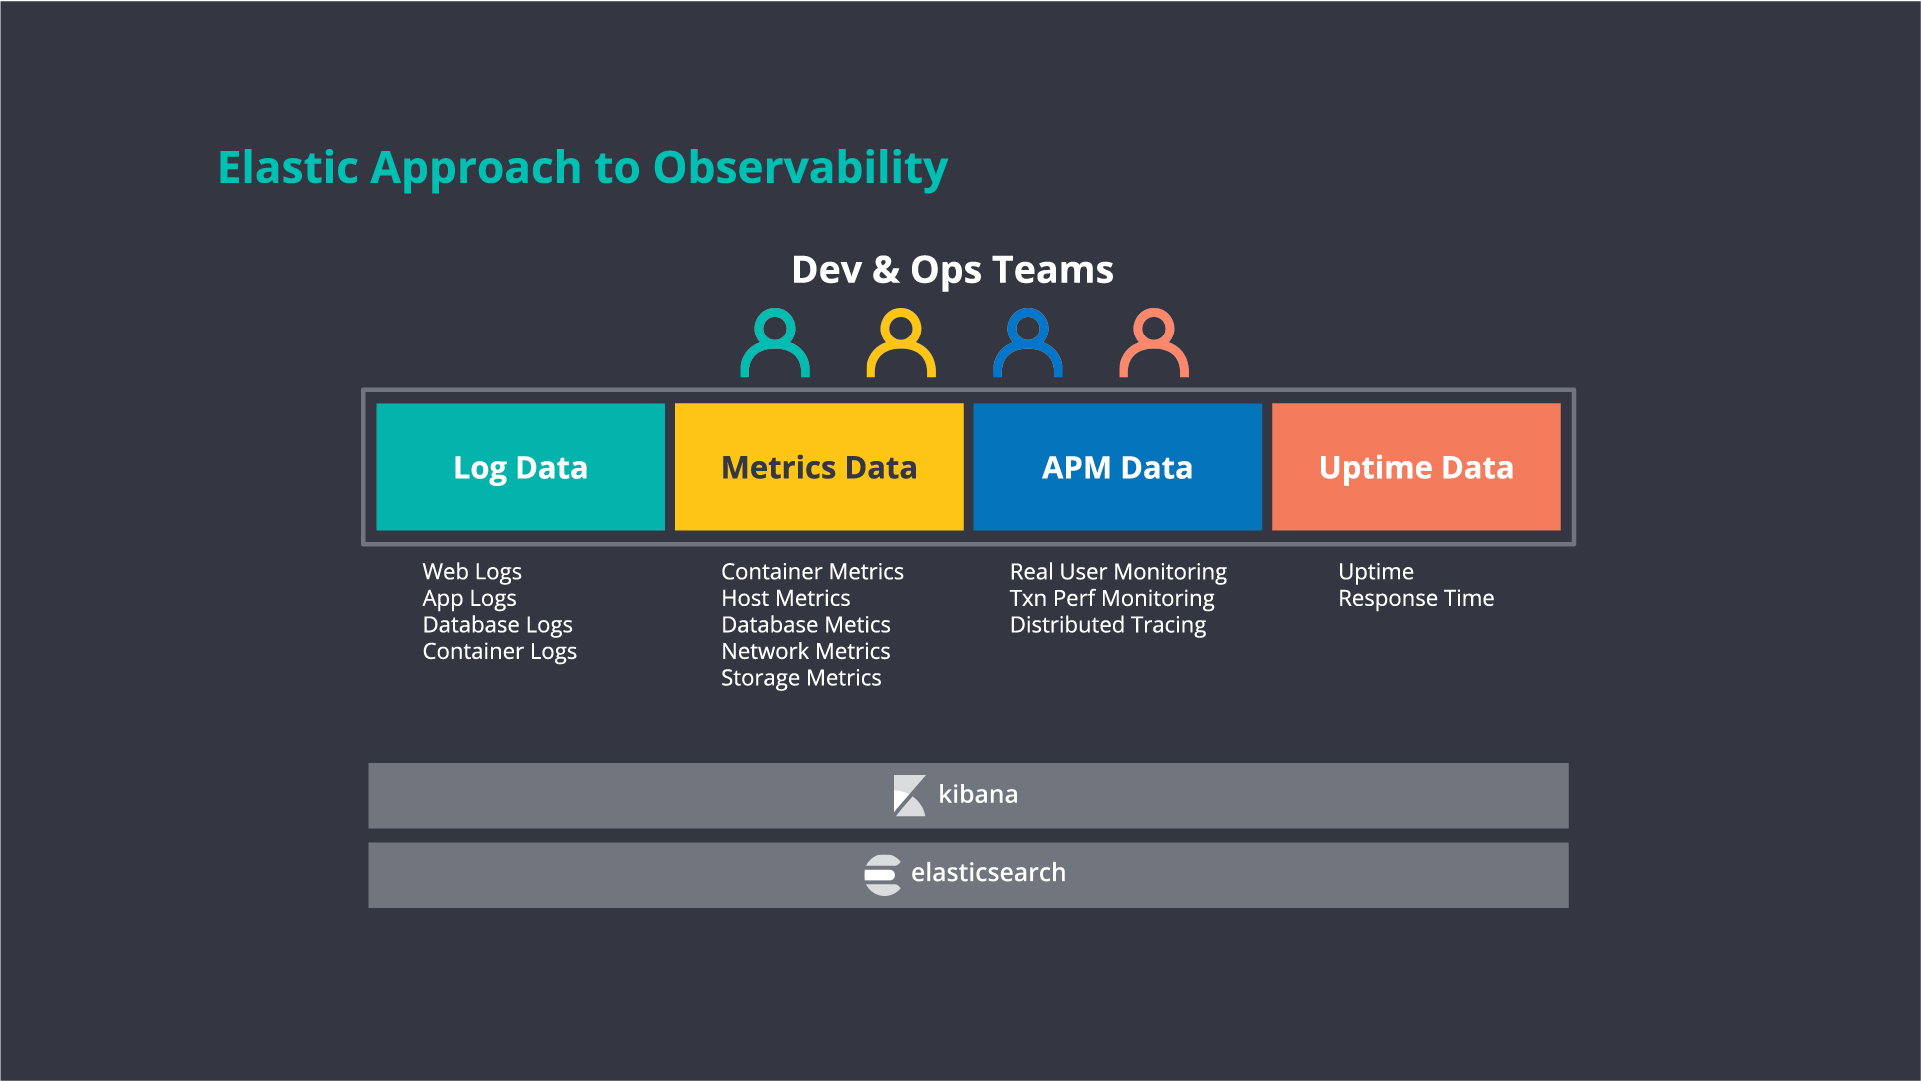
Log Monitoring with Elastic Observability | Elastic
Elastic Log Monitoring _ Enable logging and monitoring – VXLW
Upper figure is a well log view of elastic logs generated from RPM (red ...
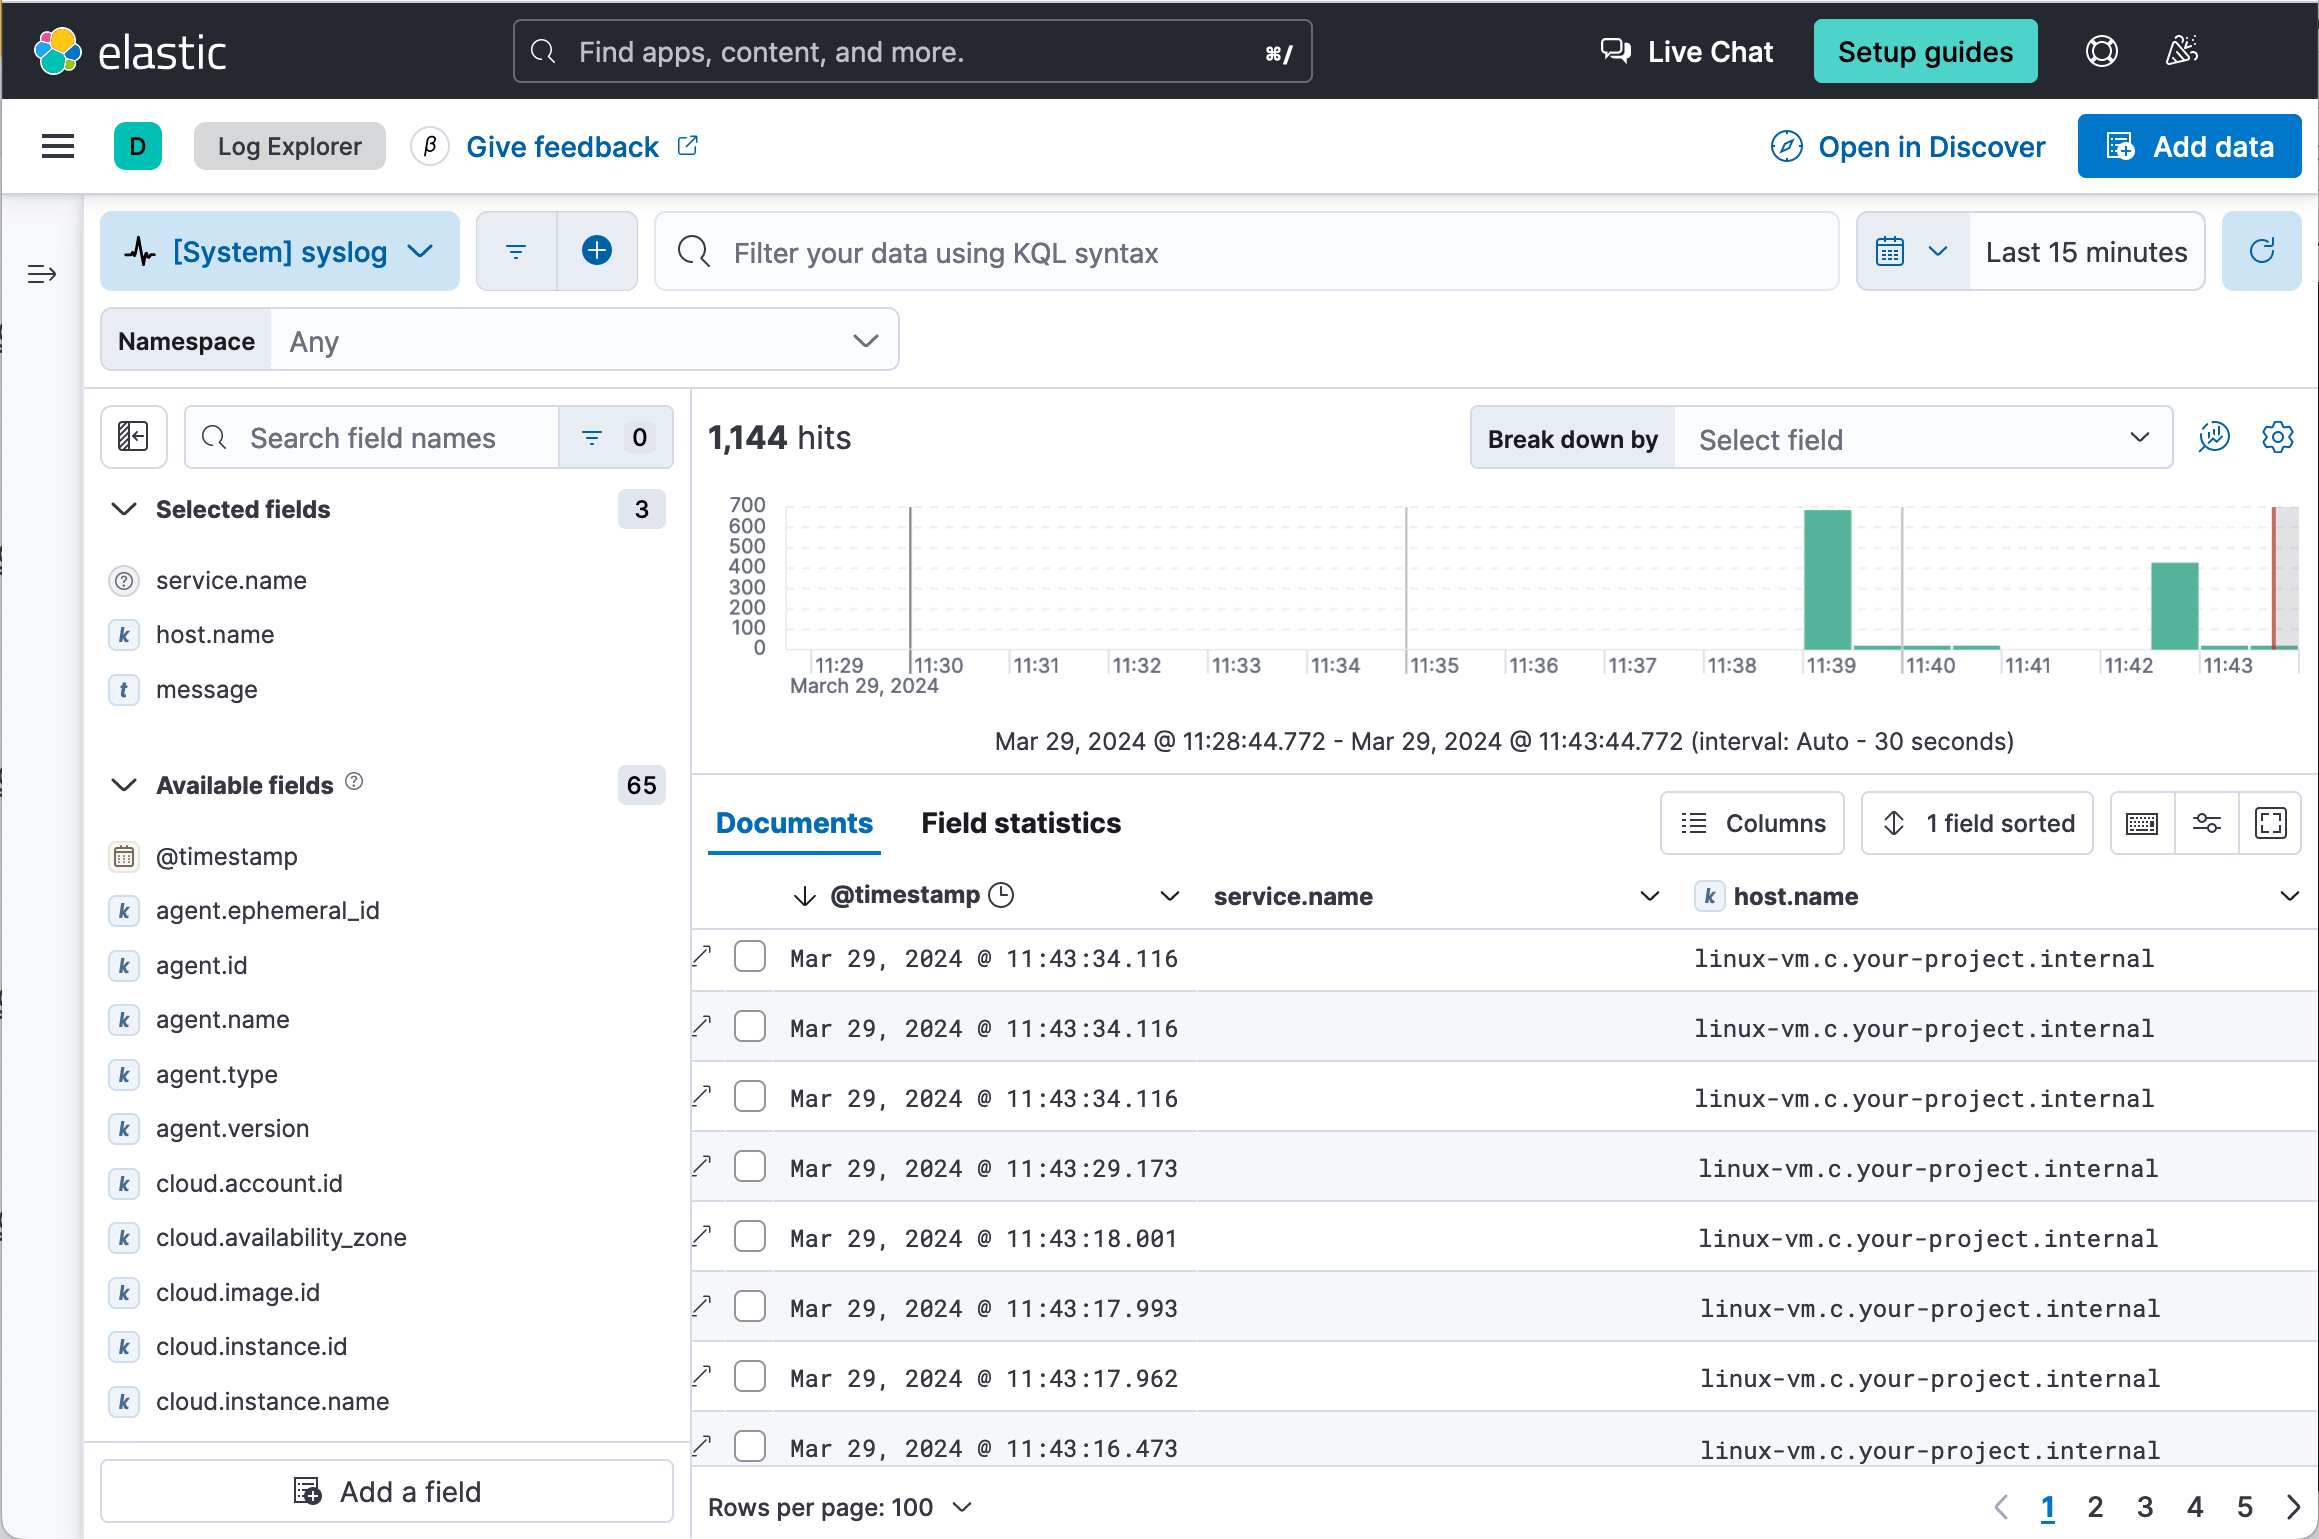
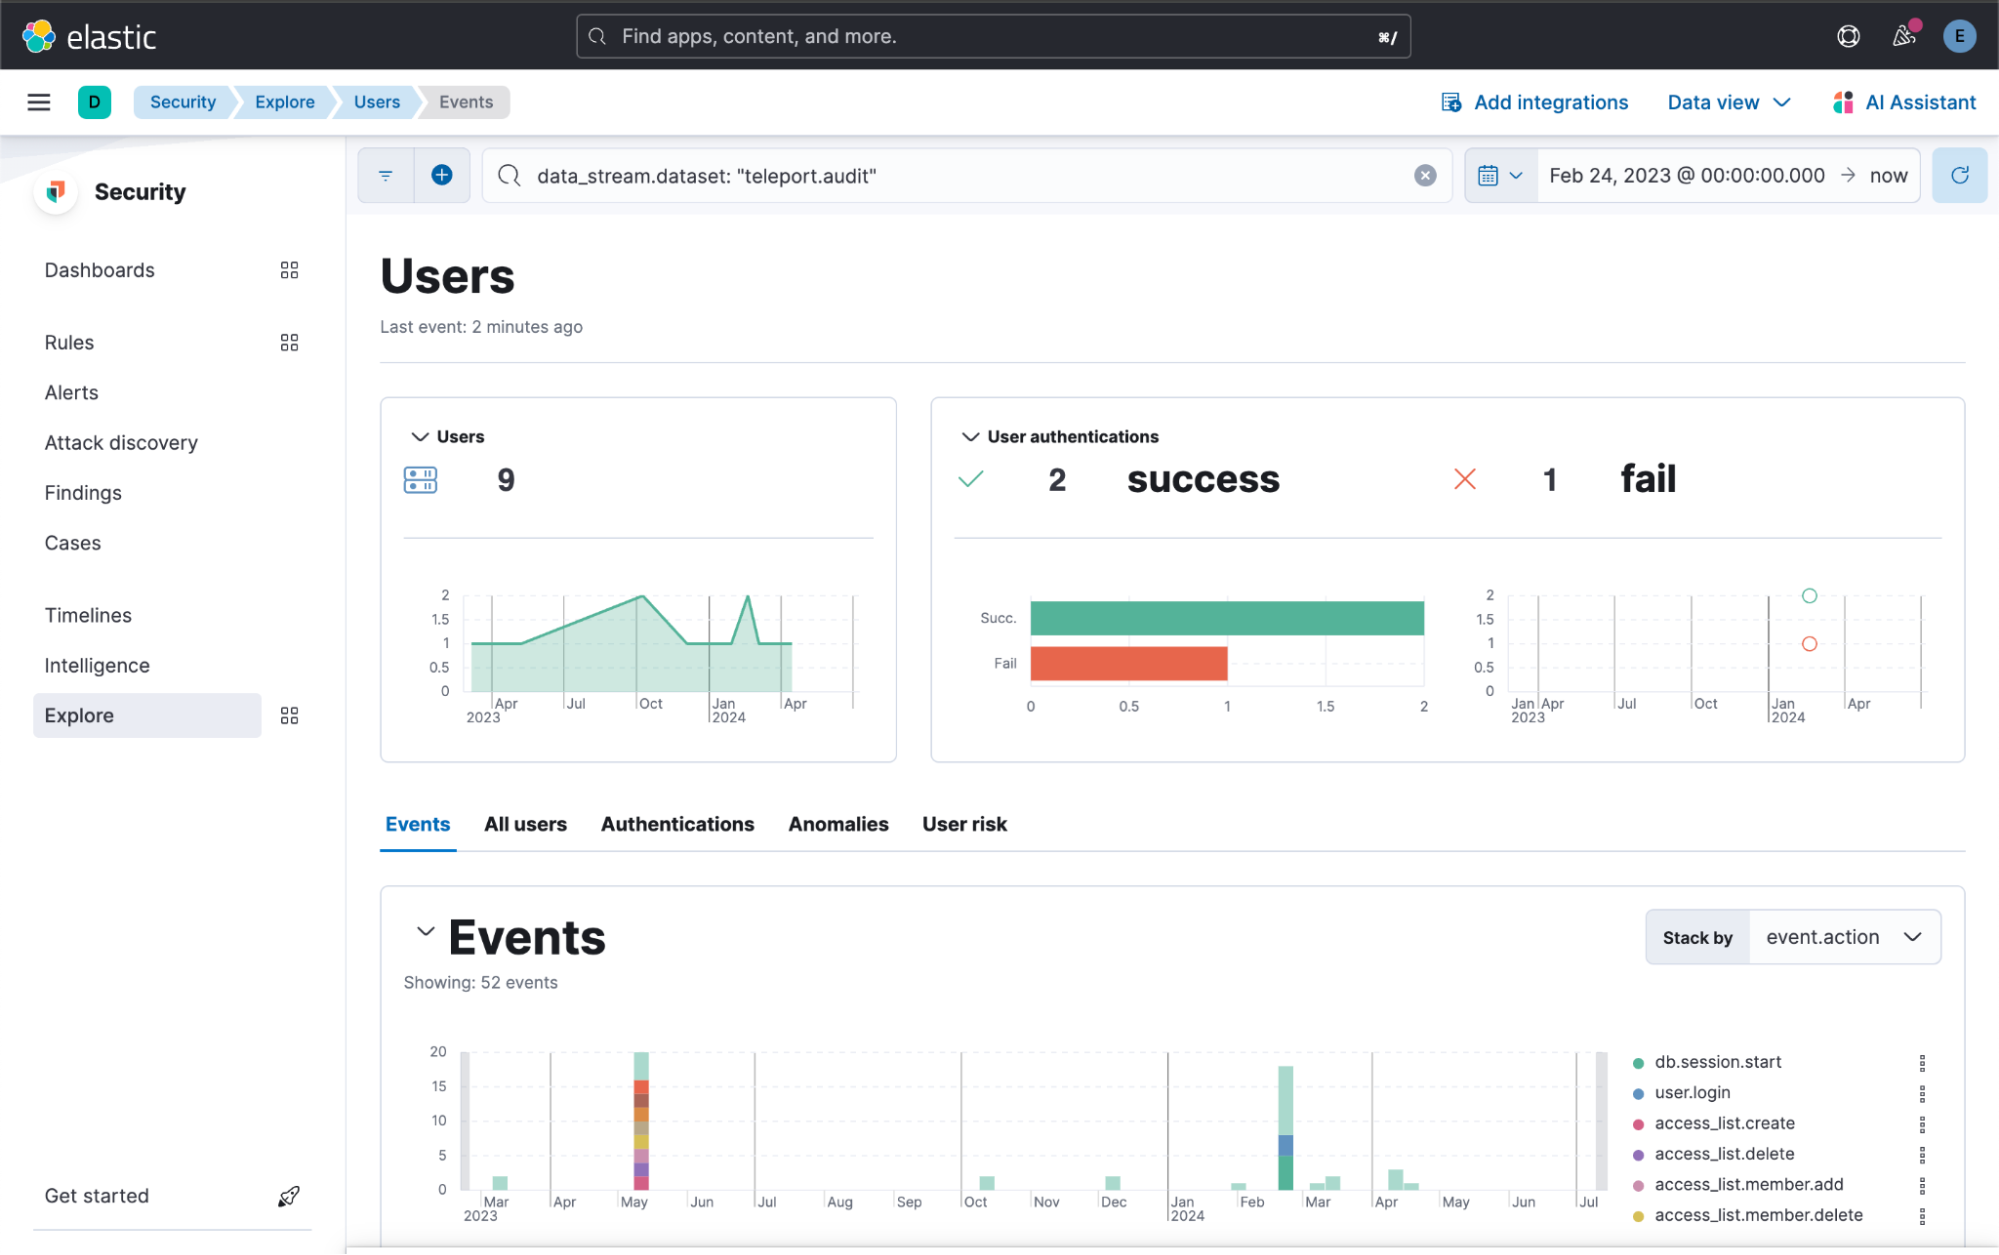
Elastic Log Monitoring Demo: Interactive log management and monitoring ...
Slow Query Logging for Elasticsearch and Elastic Cloud
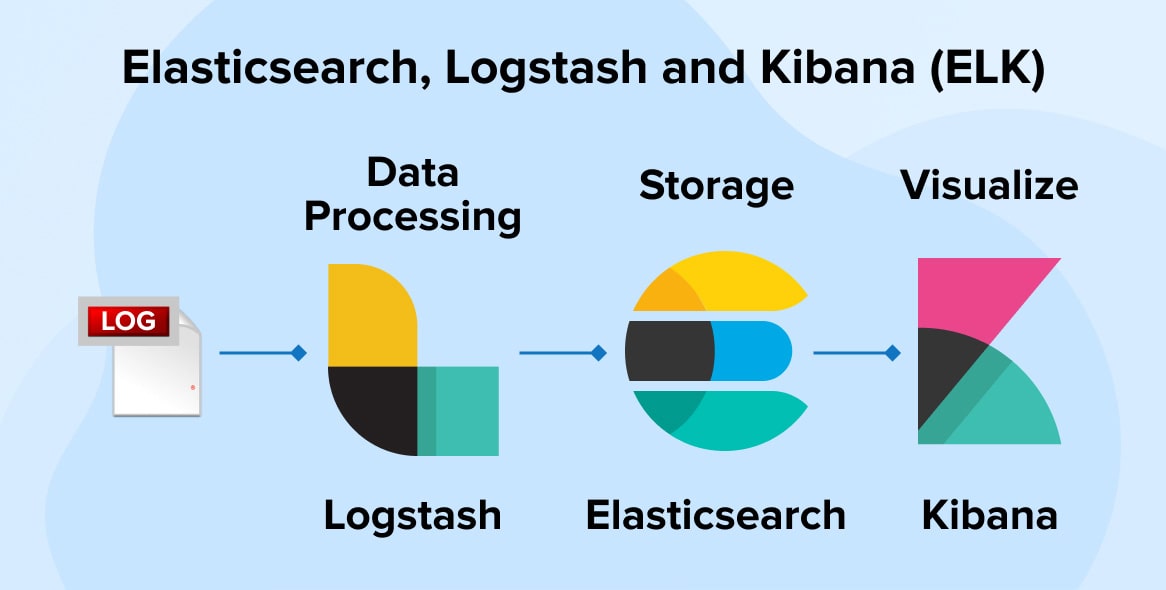
ELK Introduction — Log Consolidation with ELK Stack 1.2 documentation
Log Management - Servizio gestito QUICOLLECT e QUIELM
Logging With the Elastic Stack
Elastic Agent to Logstash for routing to multiple Elasticsearch ...
How to Externalize Logs to Elastic Stack | MuleSoft Blog
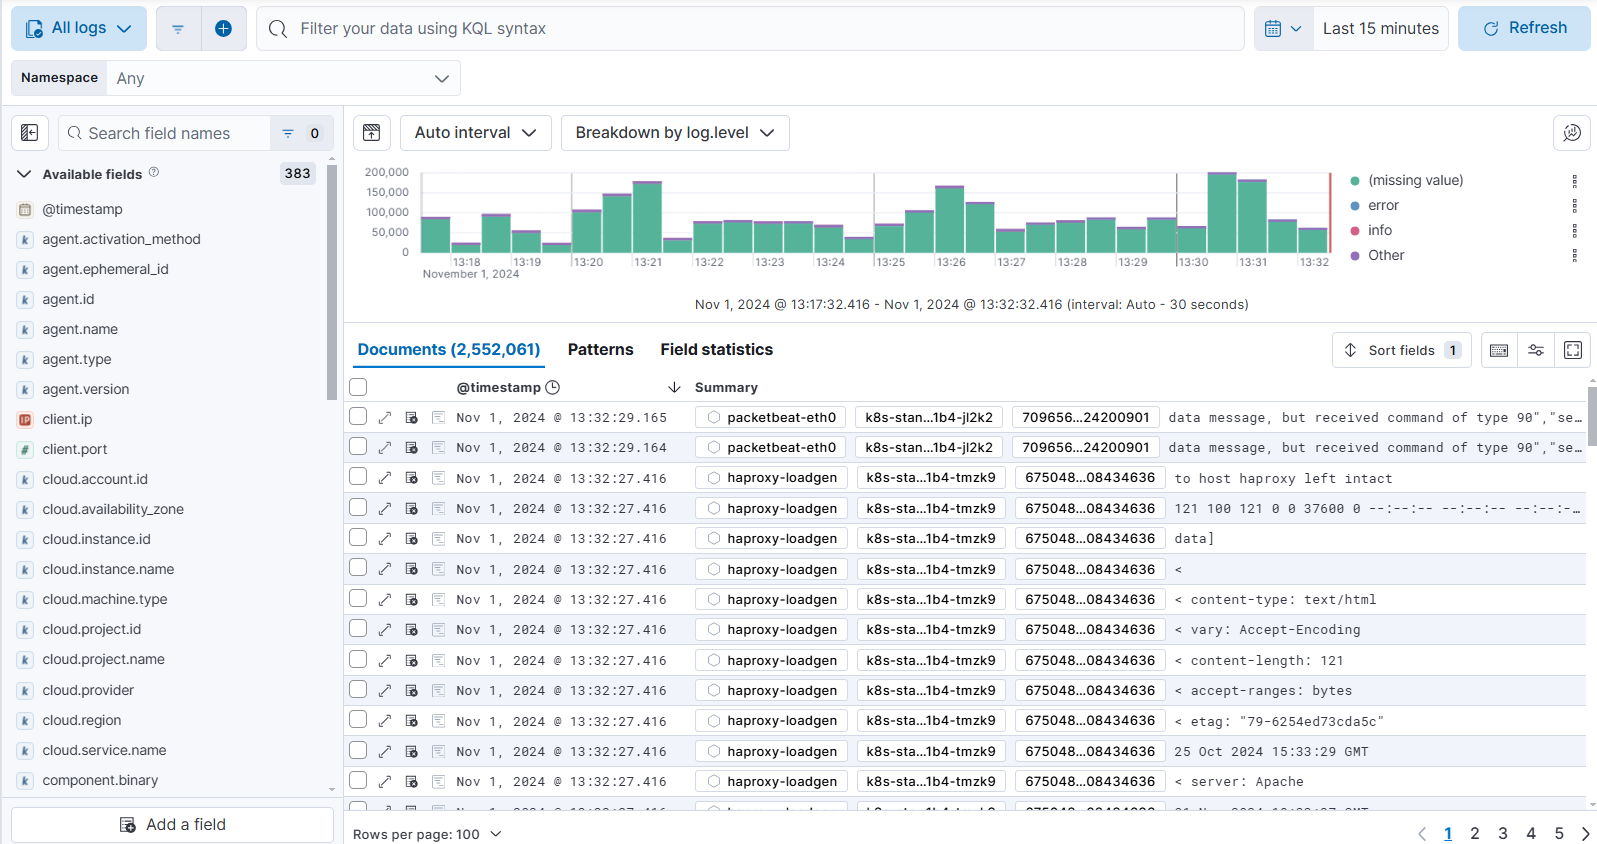
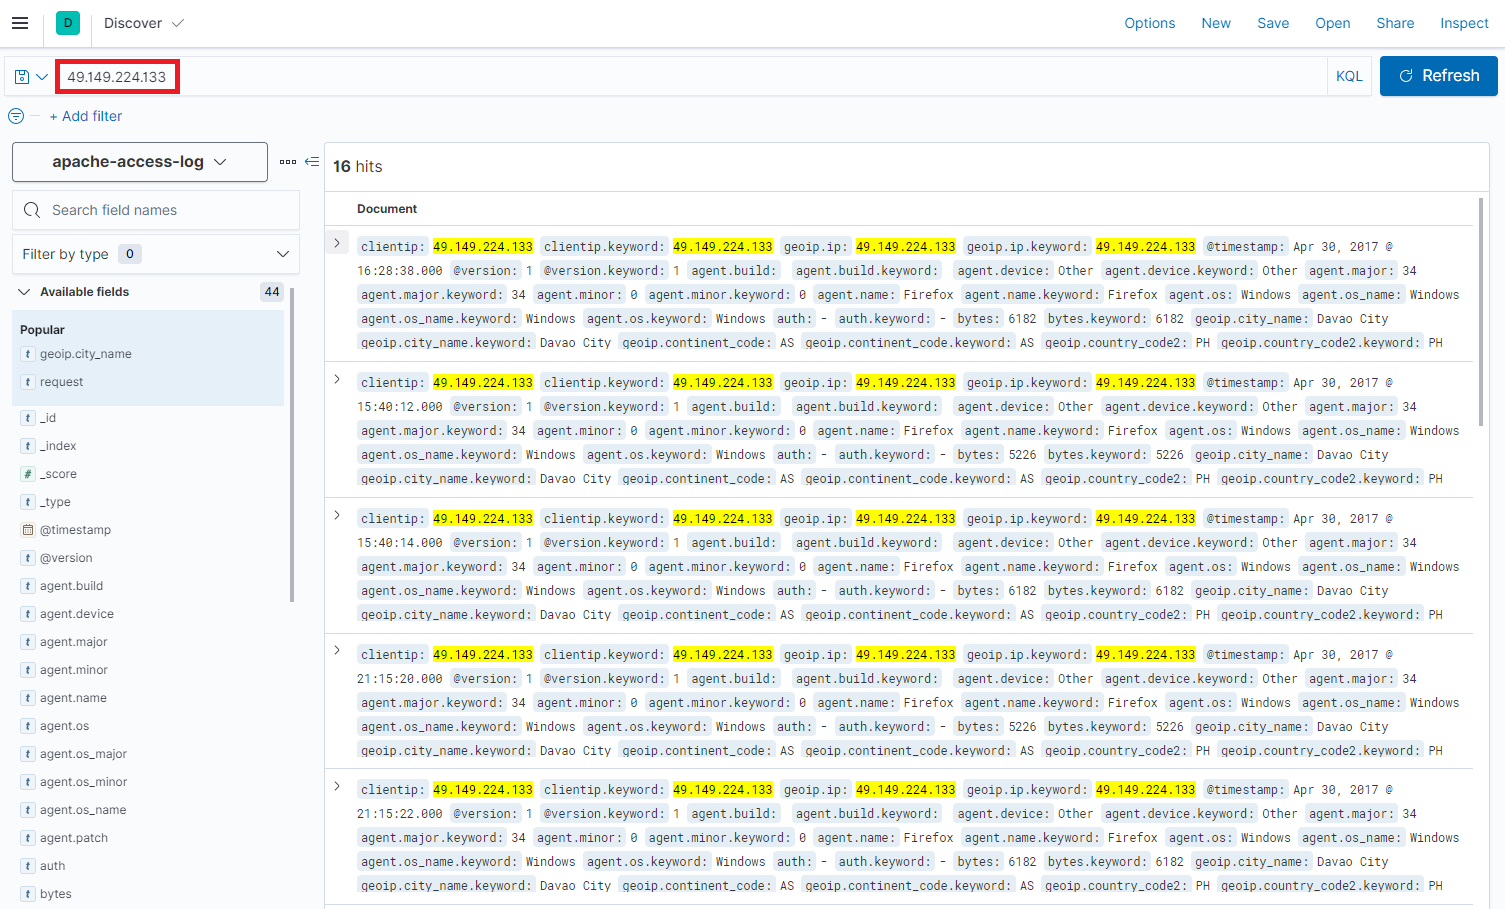
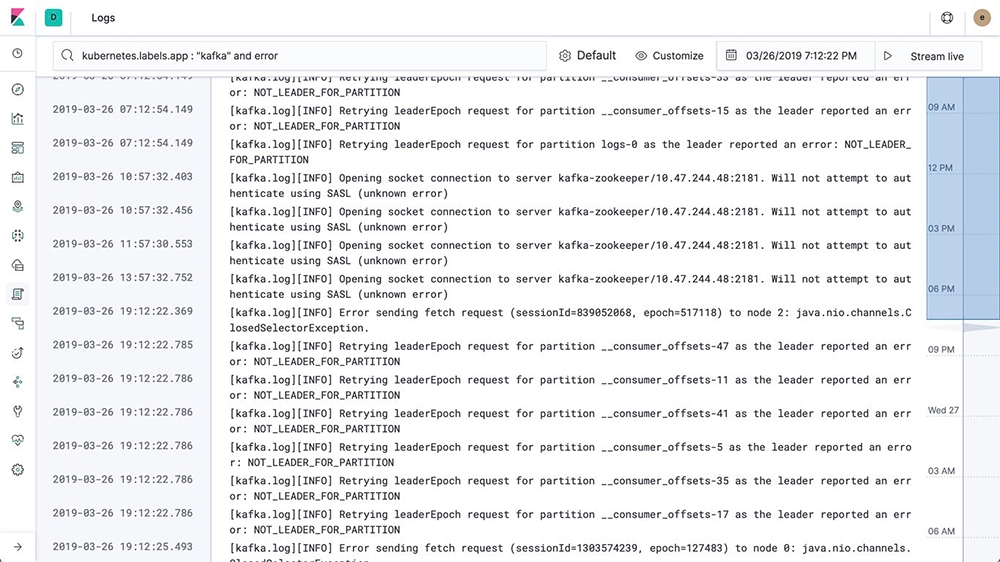
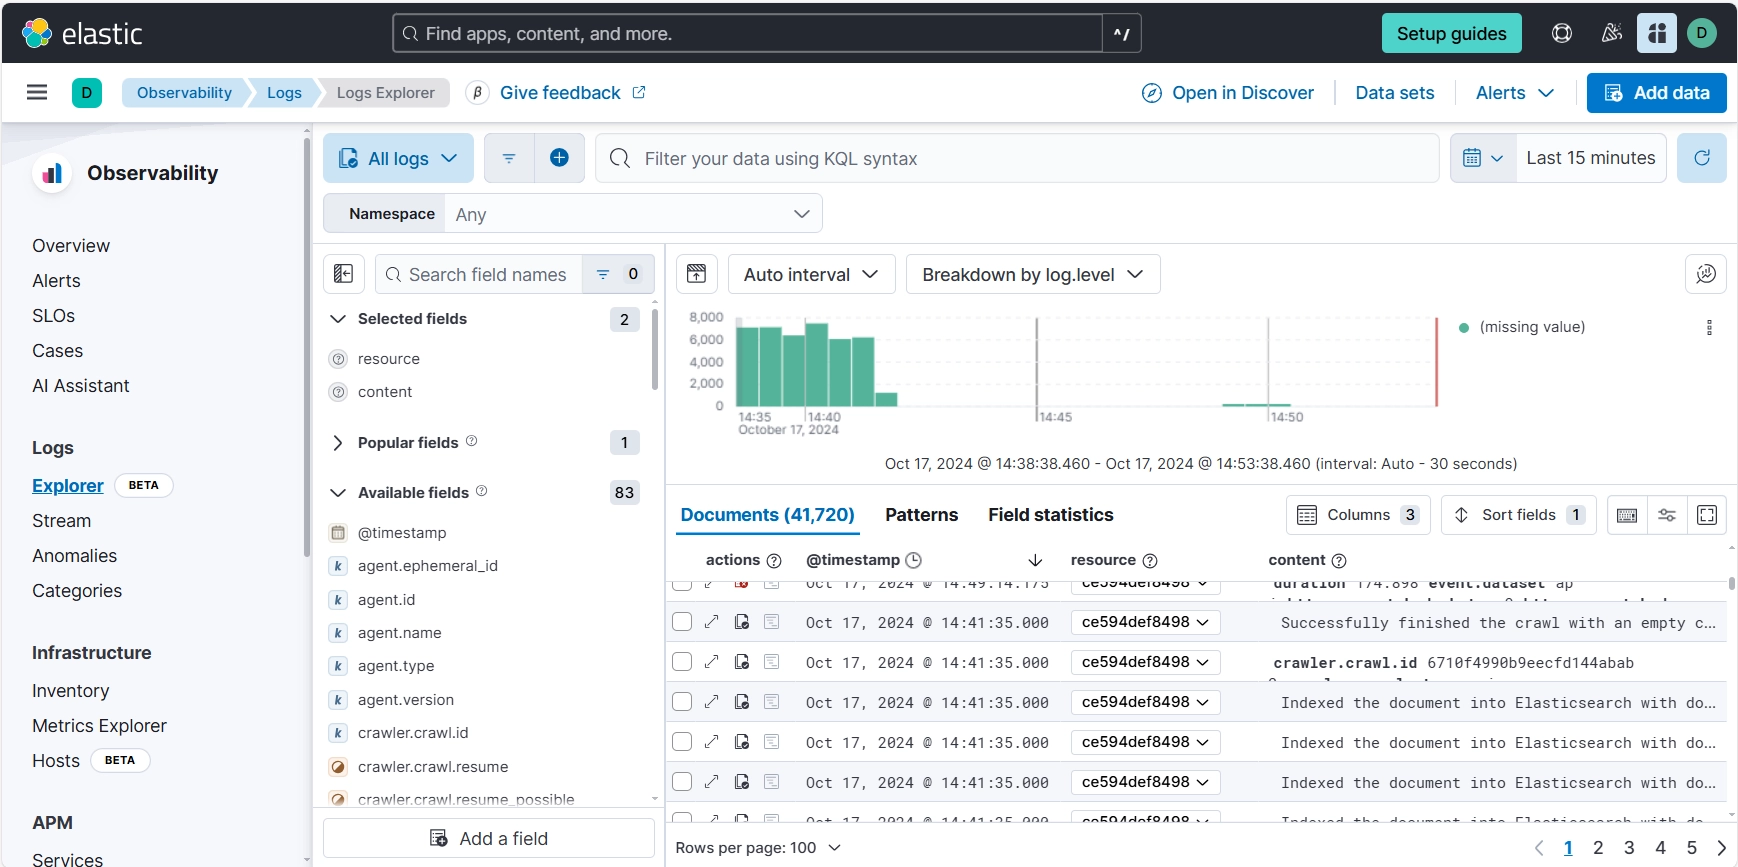
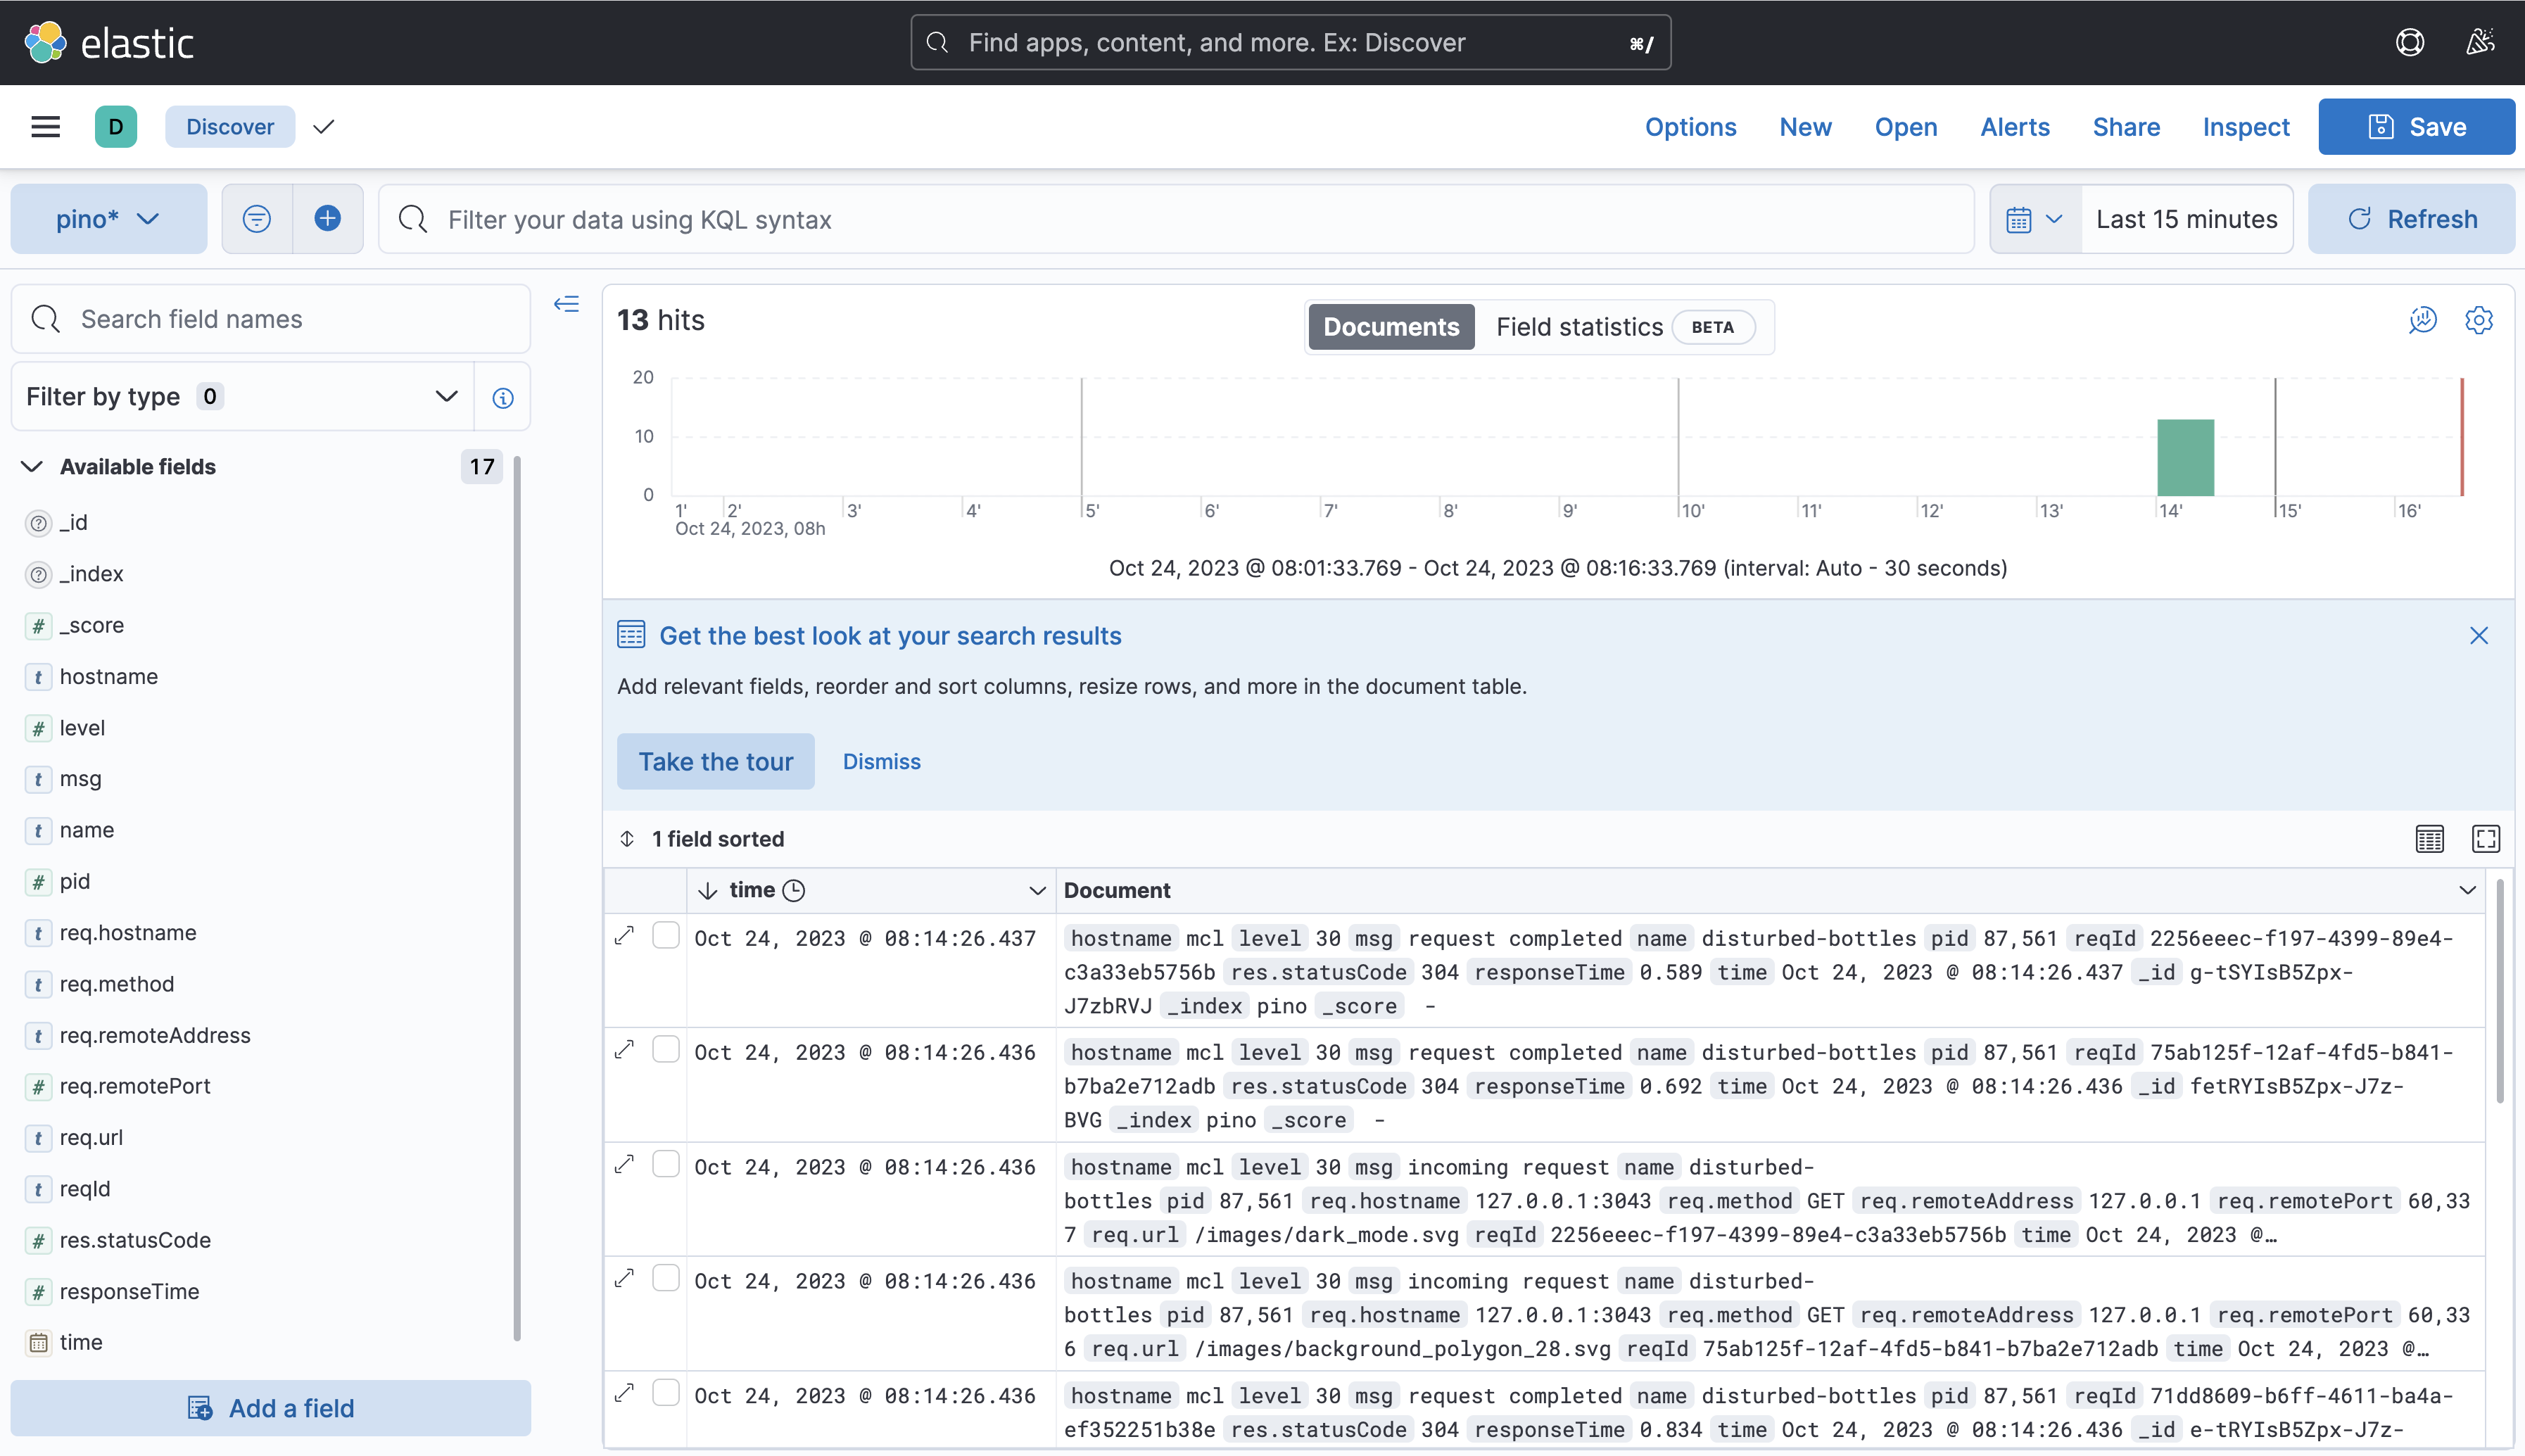
Explore logs in Discover | Elastic Docs
Using Logstash To Analyse Iis Log Files With Kibana – KUYE
Running a Multi-Node Elastic Search Cluster Locally with Docker Compose ...
Elevate Your Logs: Mastering Centralised Logging with Elastic Stack ...
ELK stack - Log Analysis and Monitoring
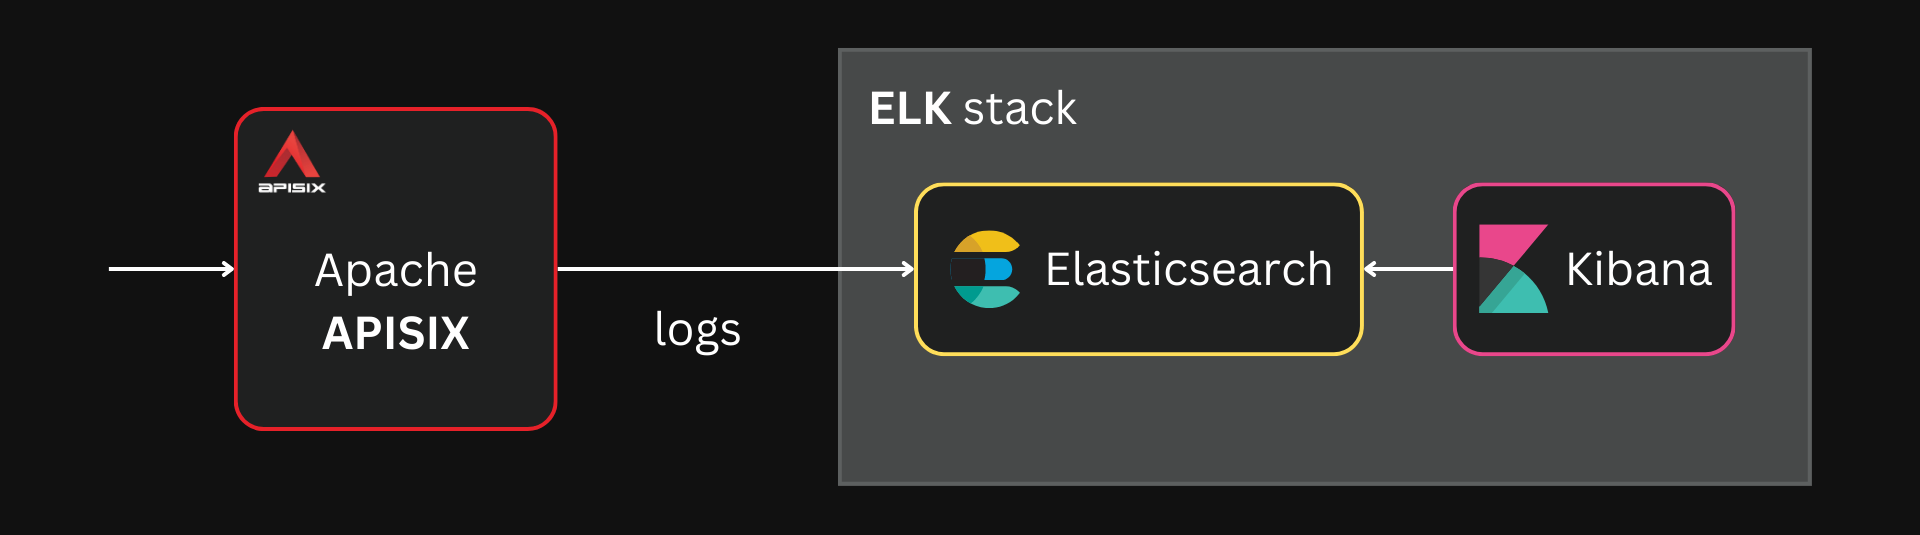
Combing through APISIX Logs with the Elastic (ELK) Stack | Navendu ...
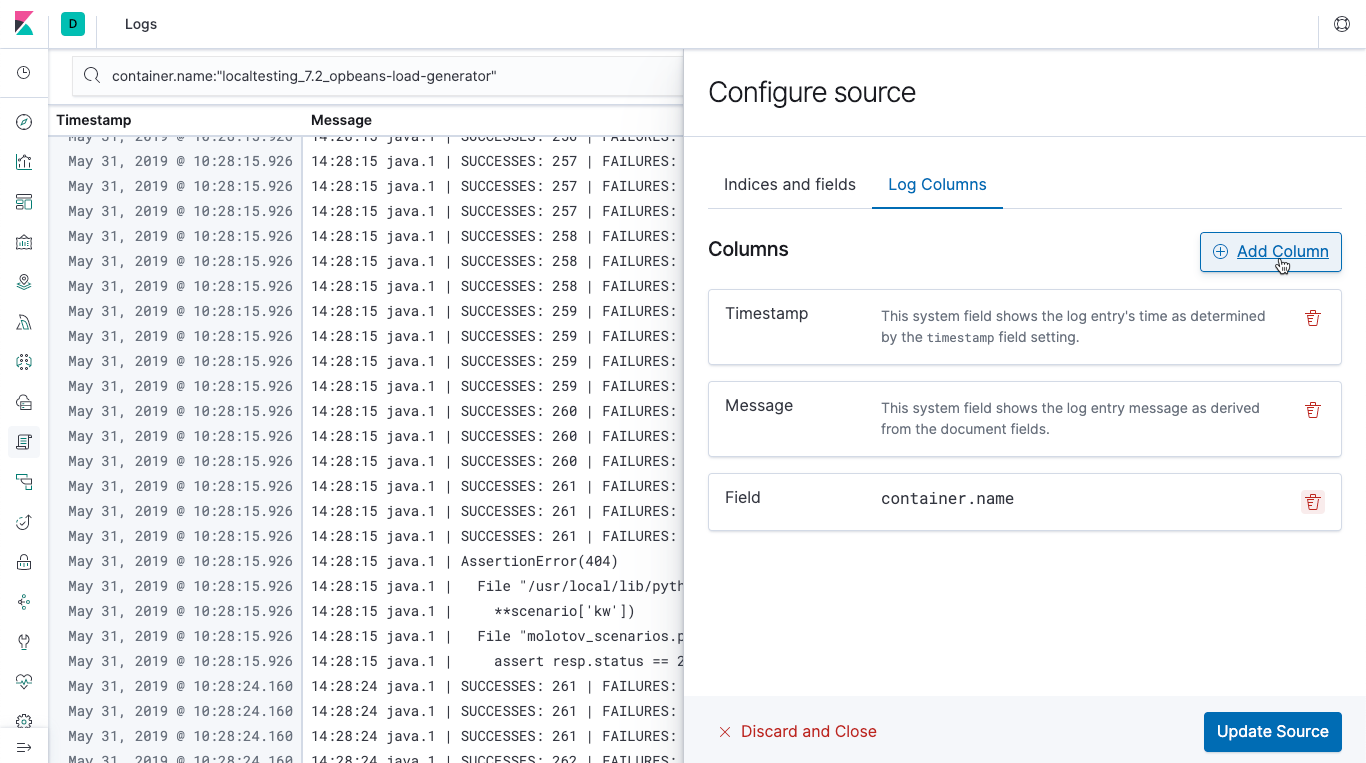
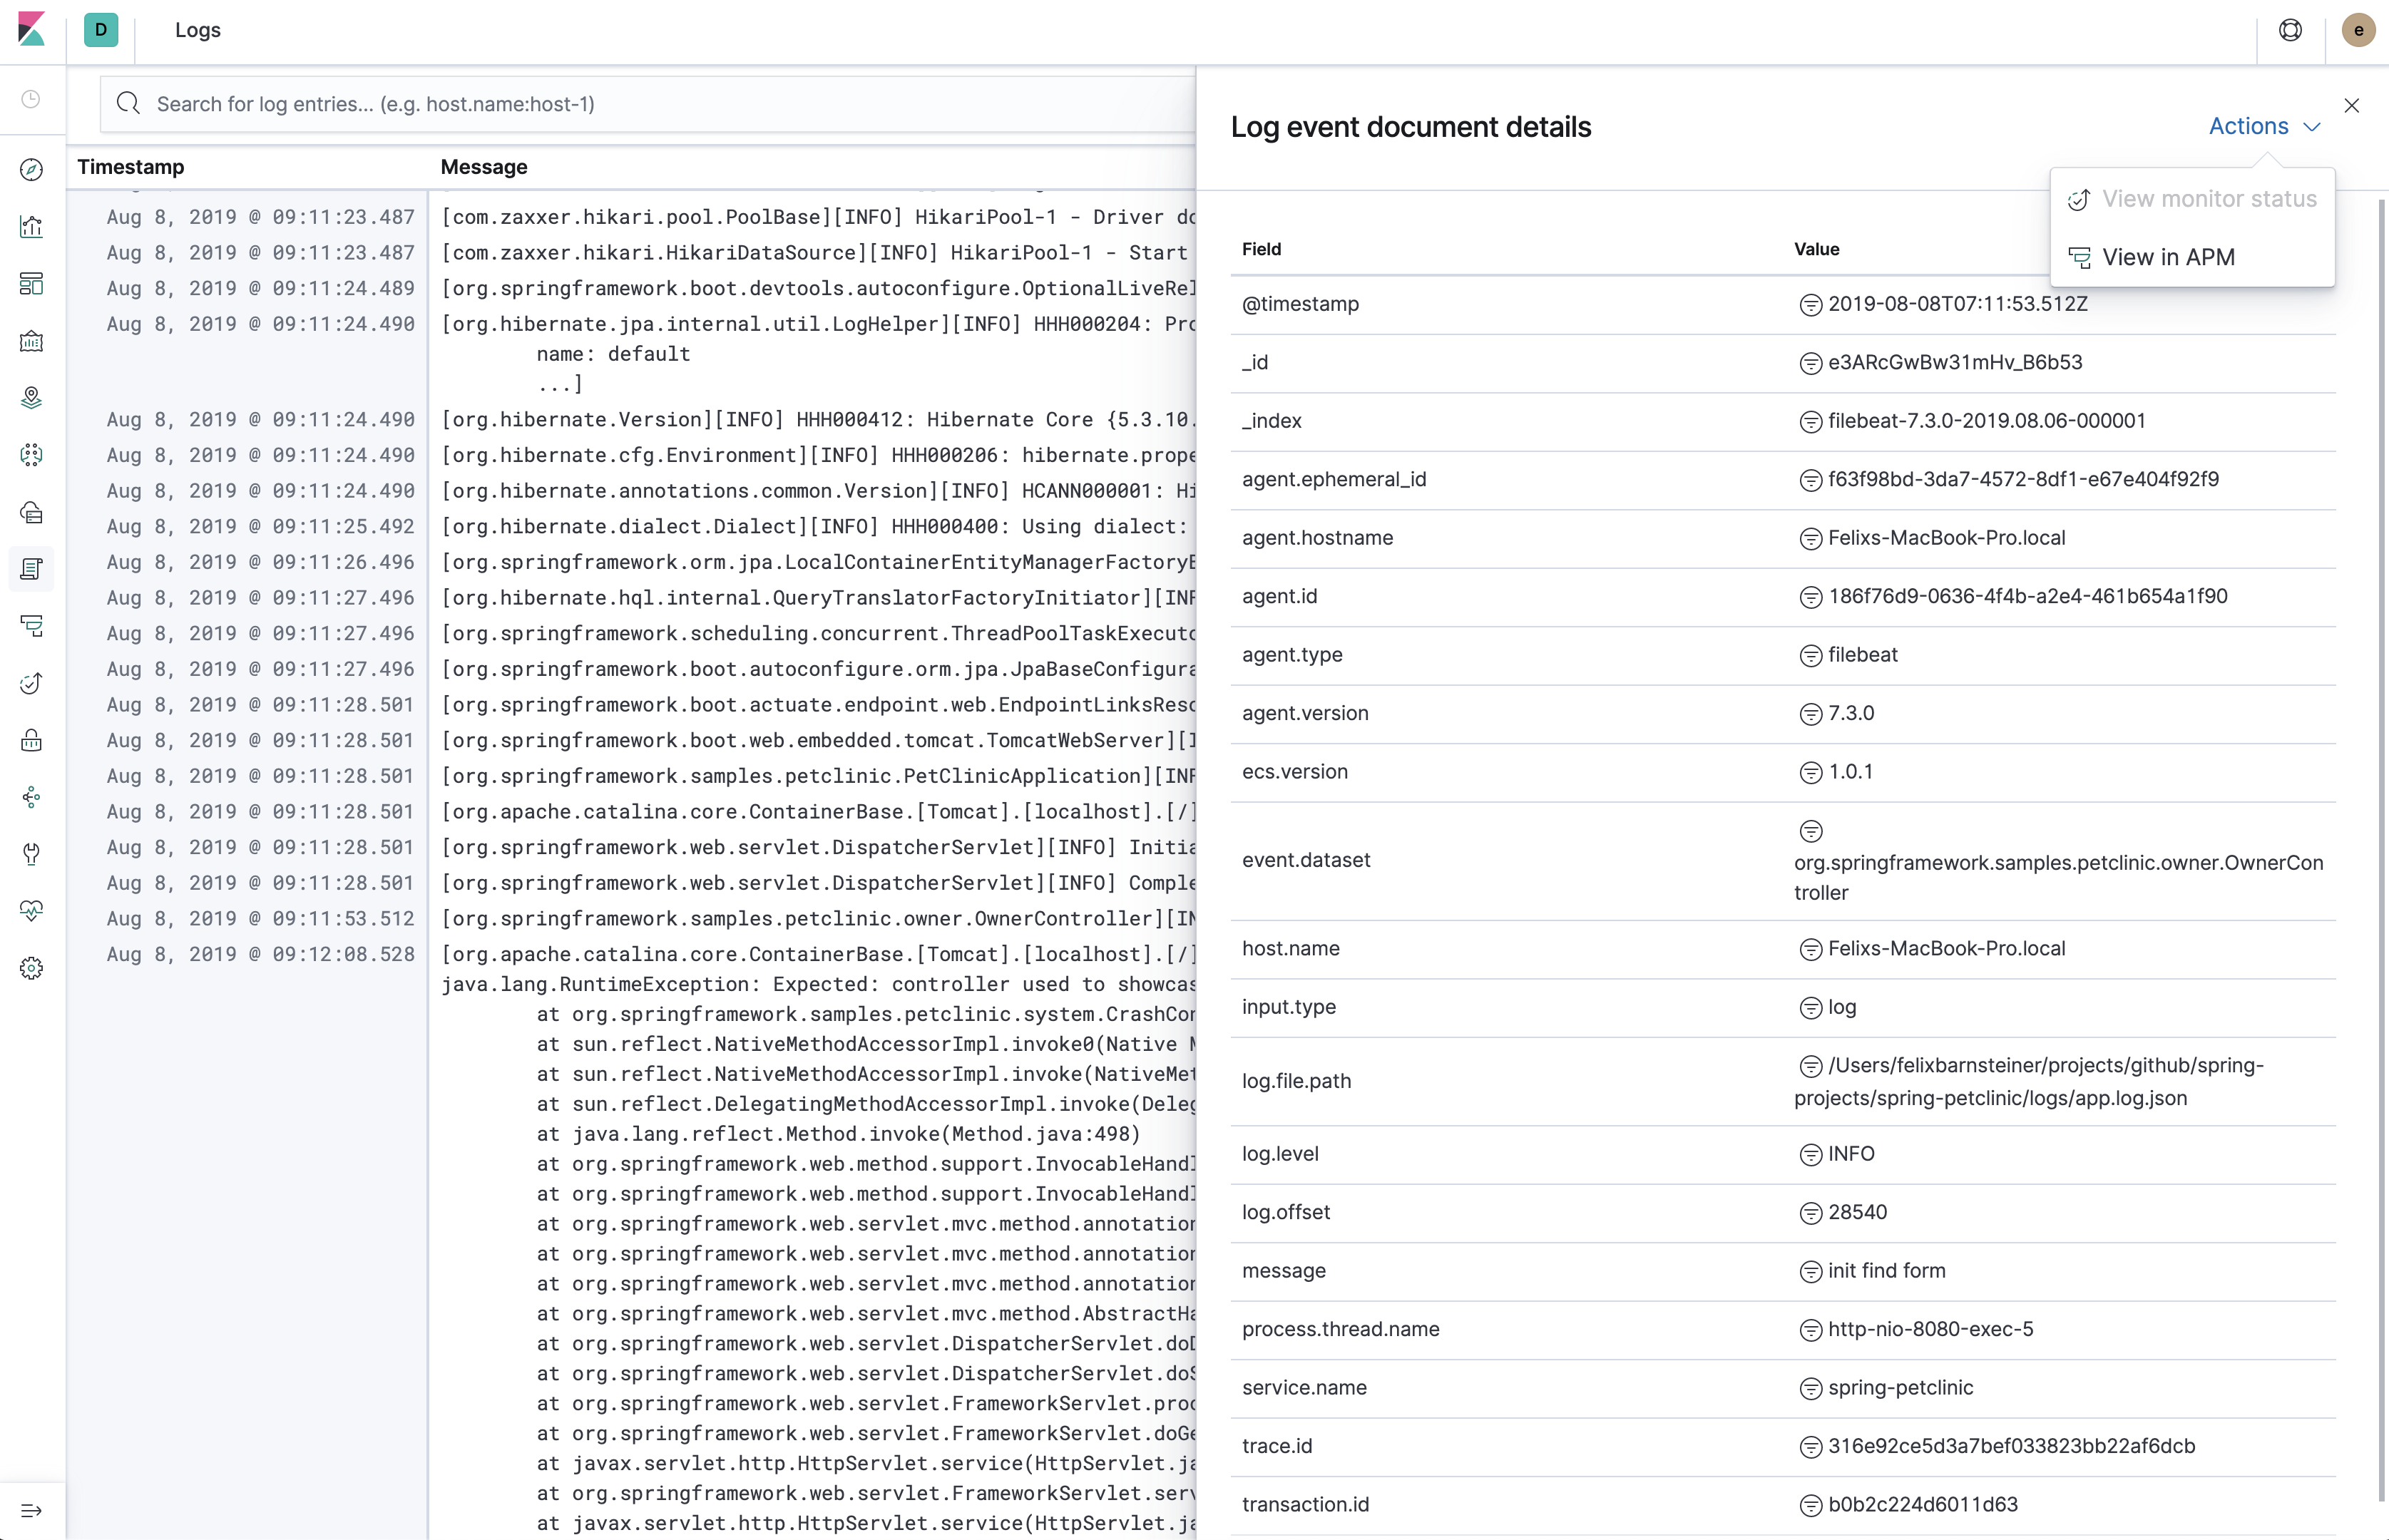
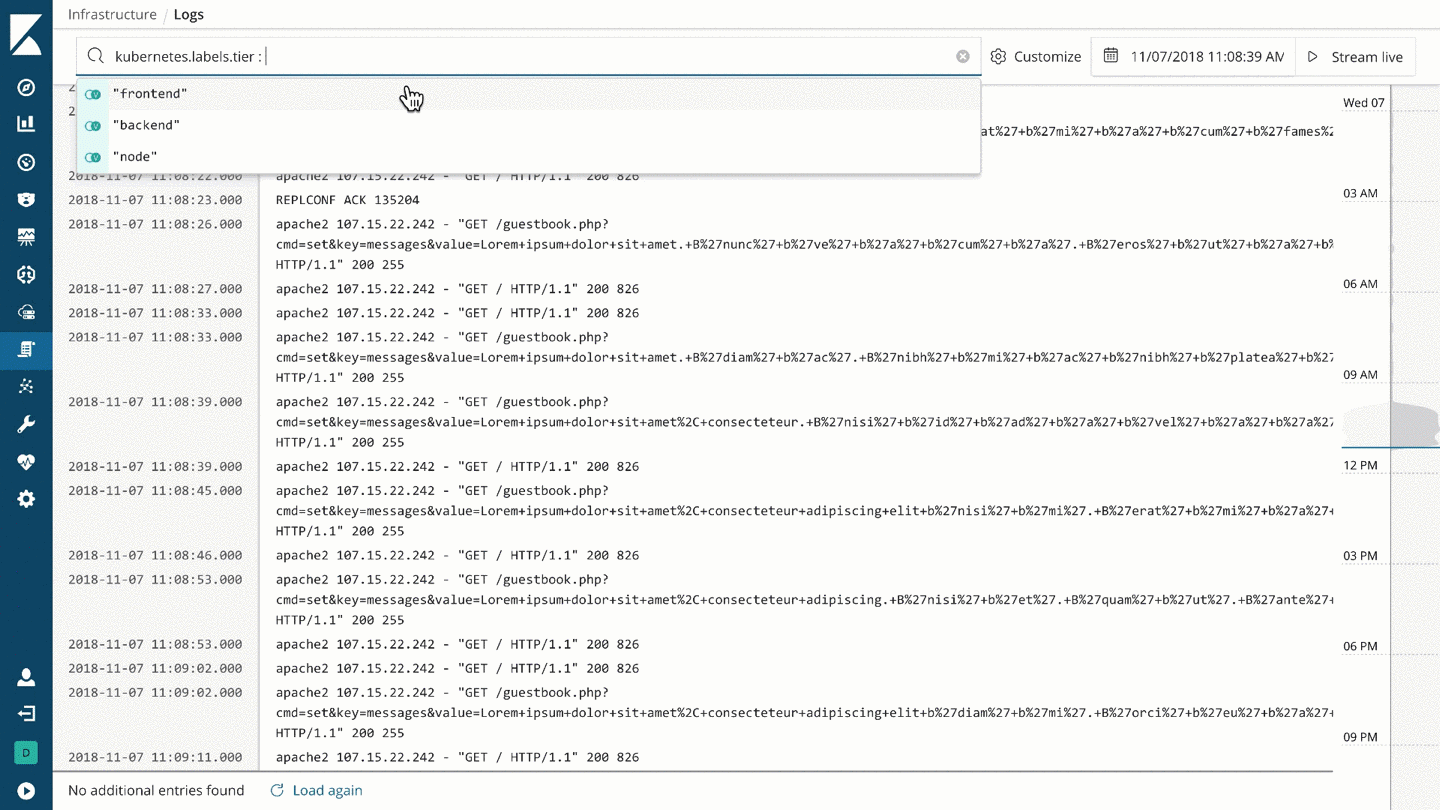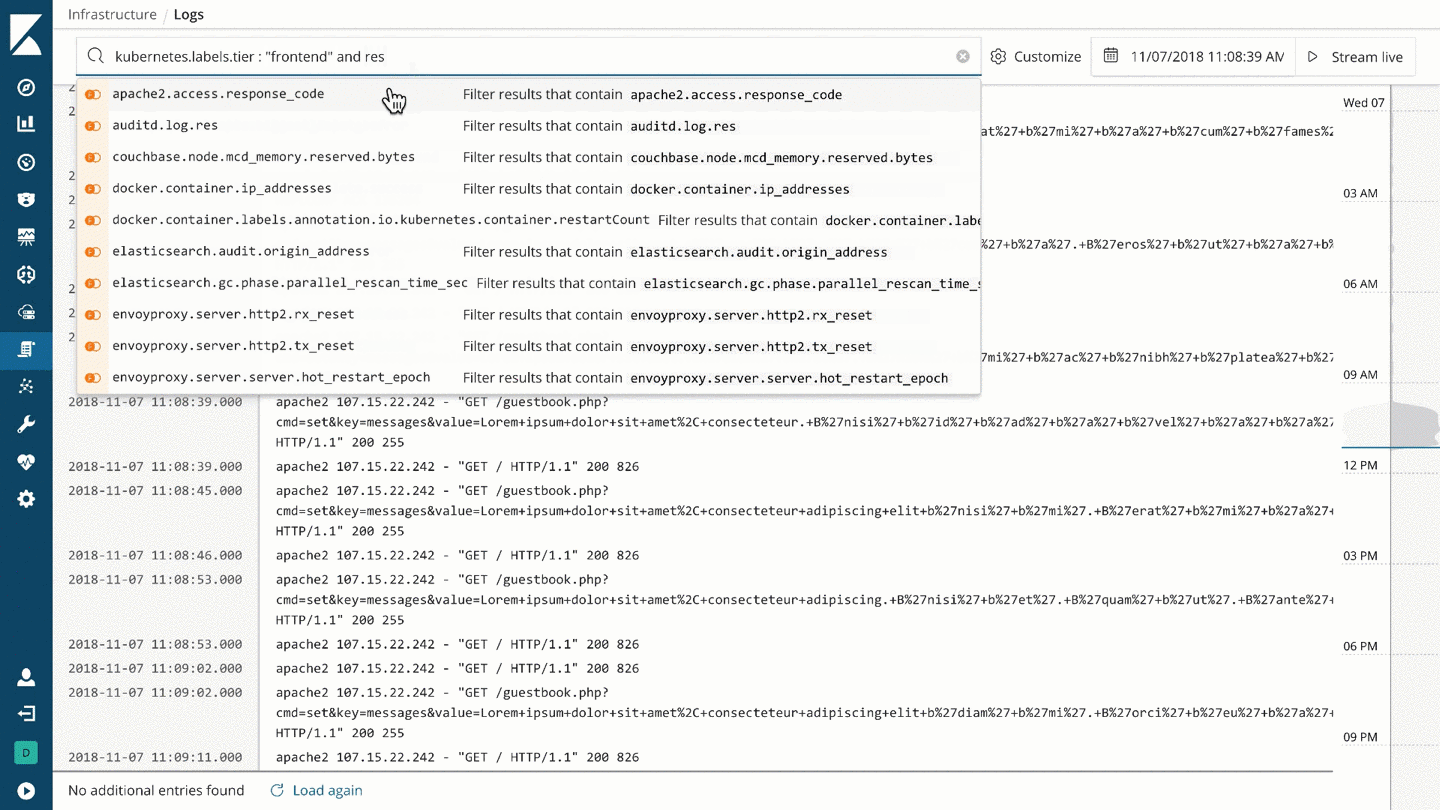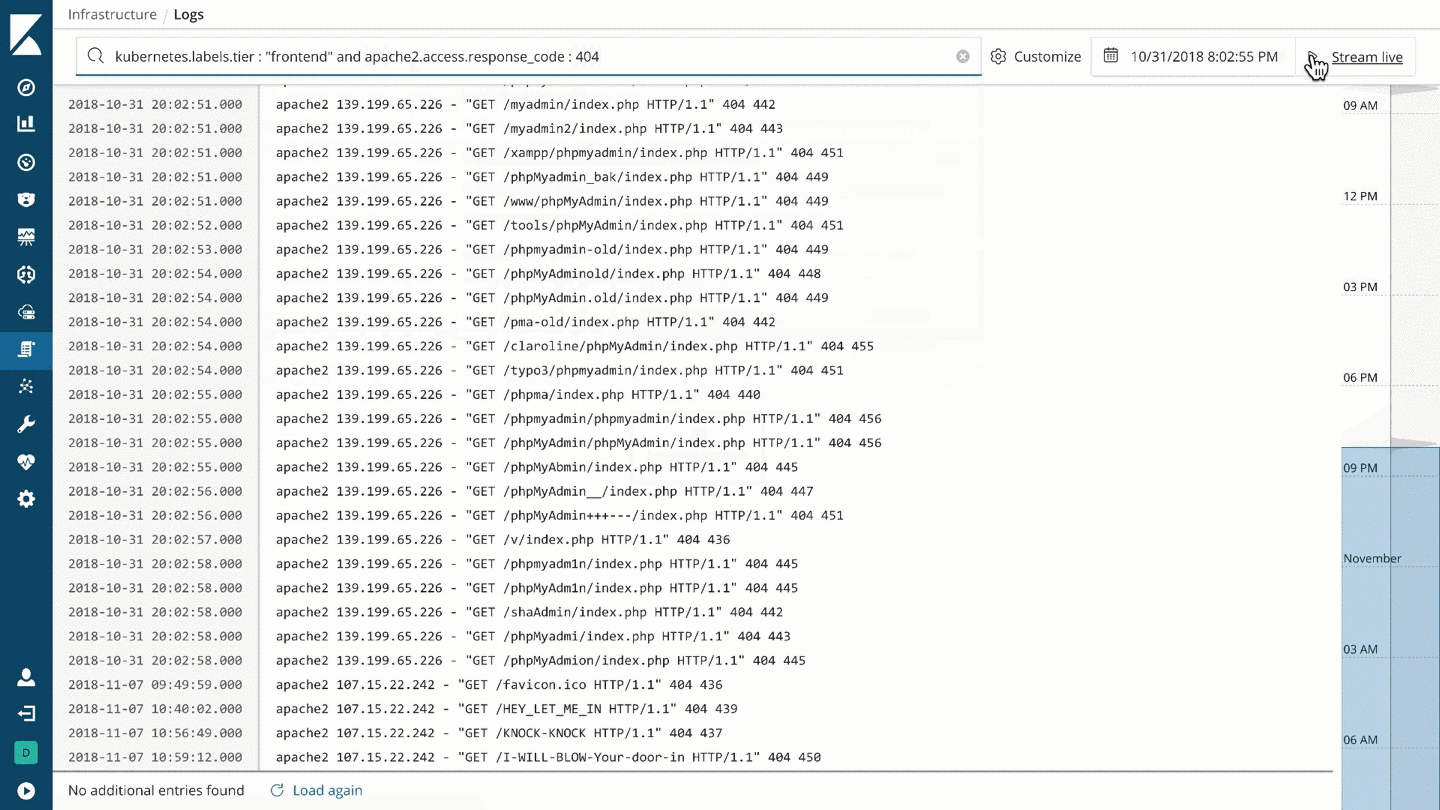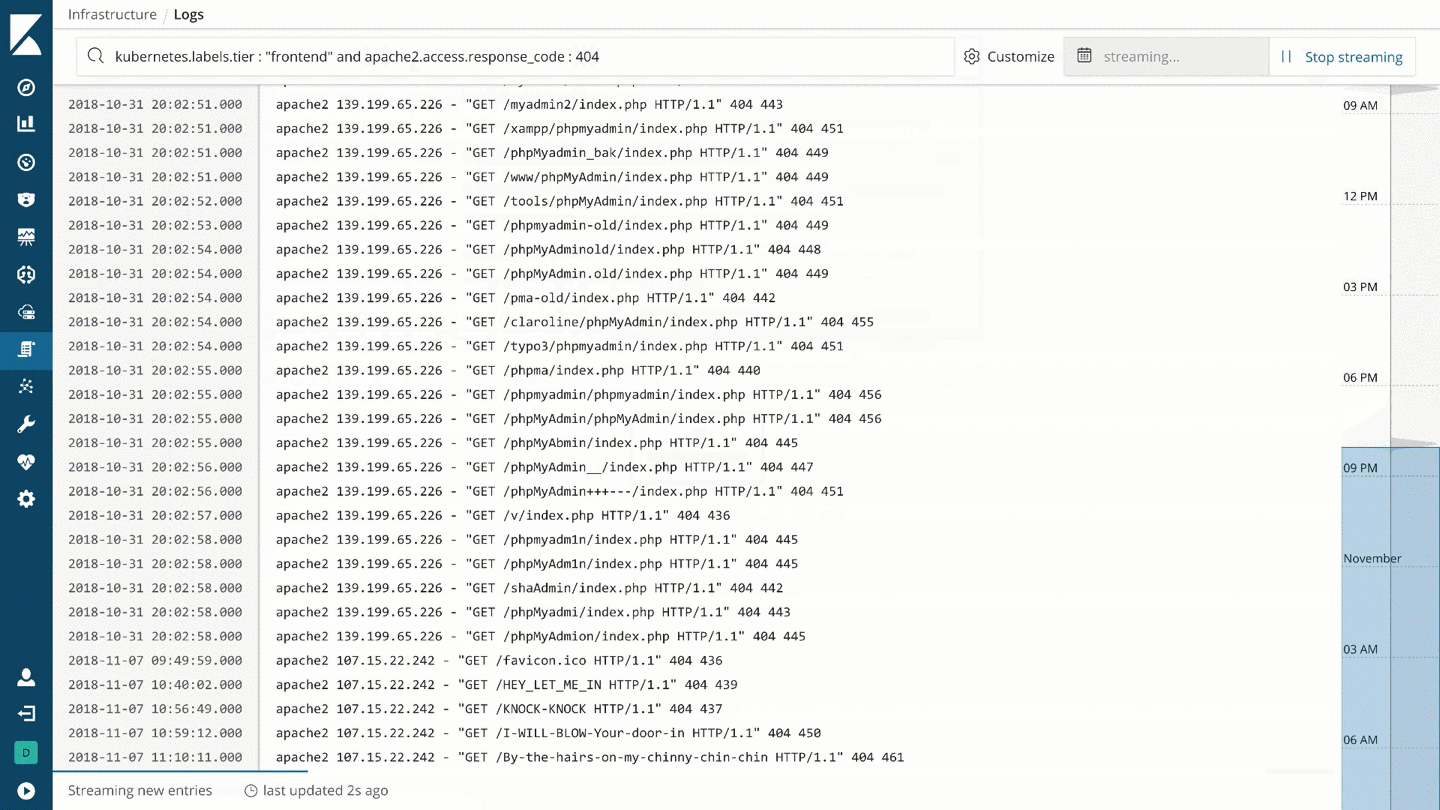
Elastic Logs 7.2.0 adds customizable views and improved Kubernetes ...
什么是日志分析? | Elastic
GitHub - 1ArMeH1/laravel-filebeat-elk: Laravel Log Management using ...
로그 파일 종합 안내서 | Elastic
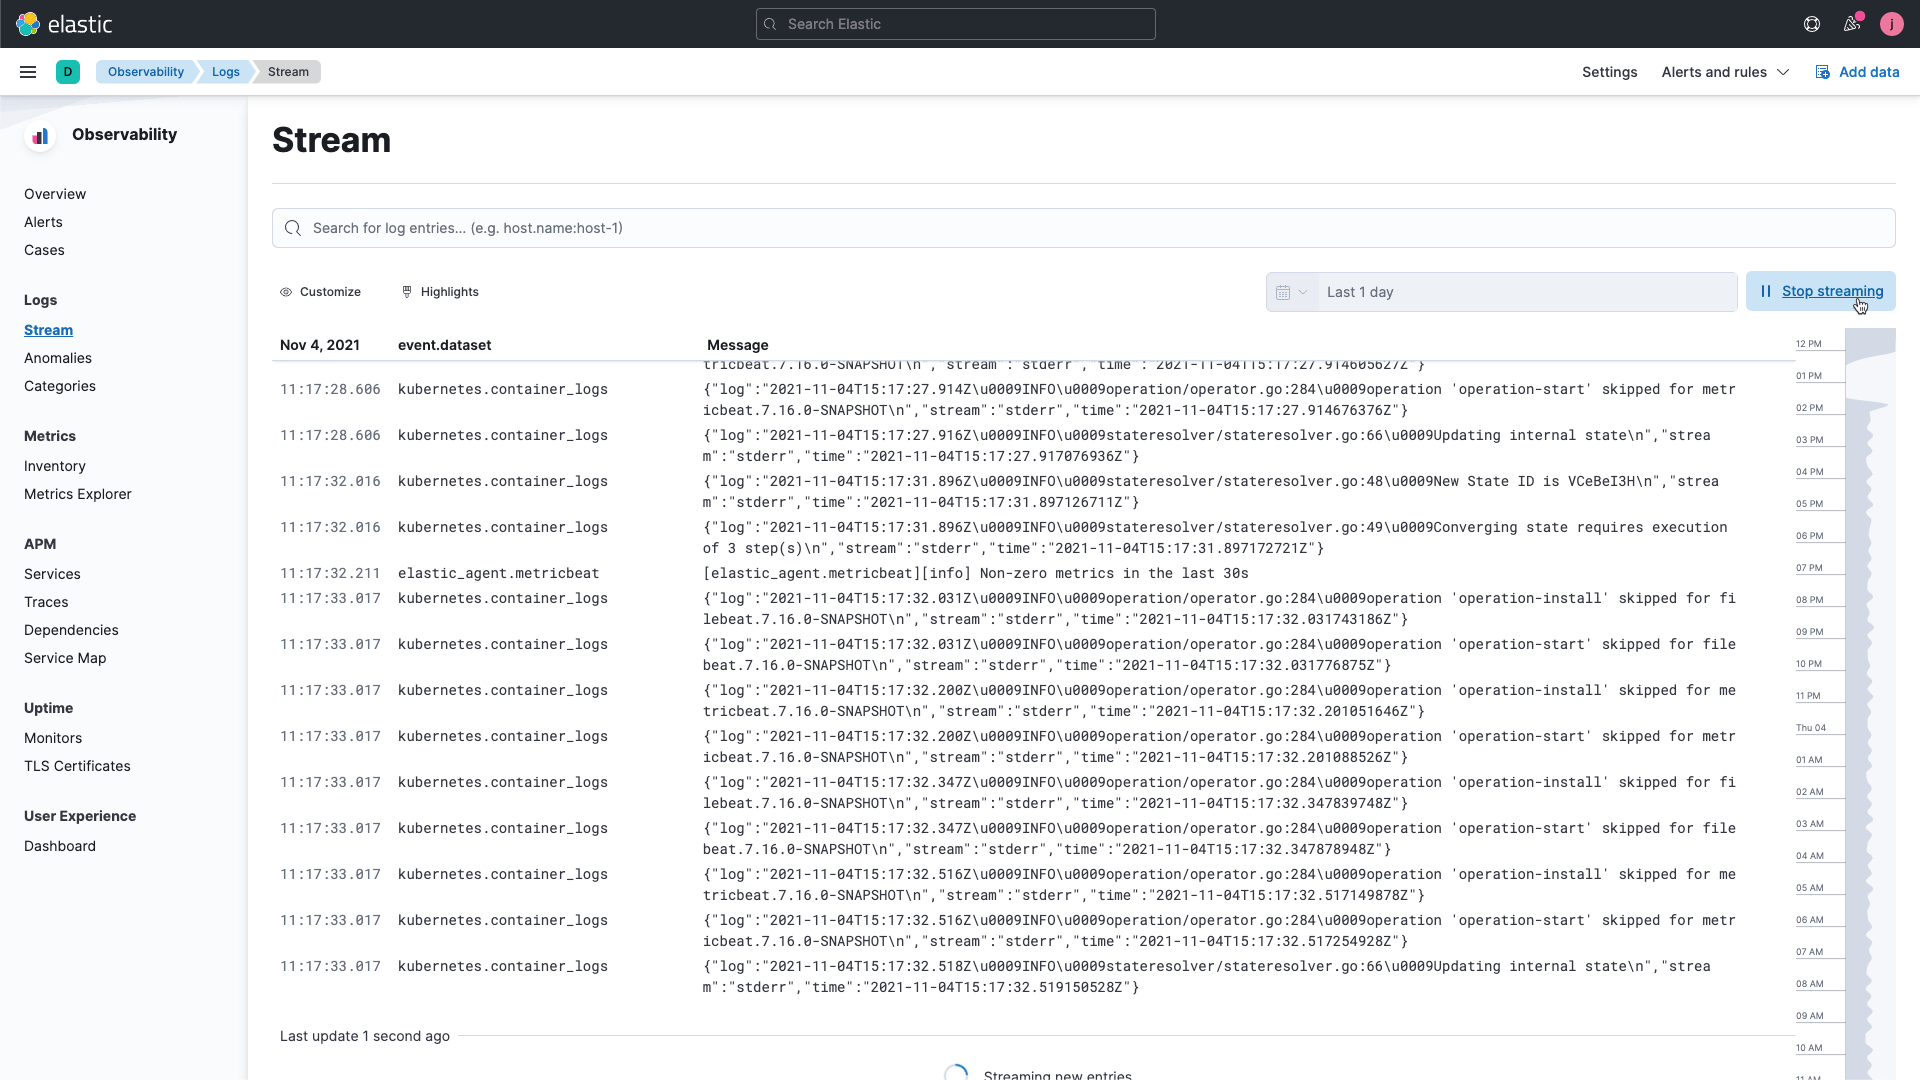
Logs Stream | Elastic Observability [8.19] | Elastic
Left ? Measured and modelled elastic logs for Well A. Rock physics ...
Microsoft and Elastic Partner to Offer Elastic Stack on Azure
Some computed elastic logs. | Download Scientific Diagram
Introduction | ECS Logging Reference | Elastic
Log Analyzer and Log Analysis Tools for 2026 | Uptrace
ELK Elasticsearch Logstash and Kibana Stack for Log Management | PPT
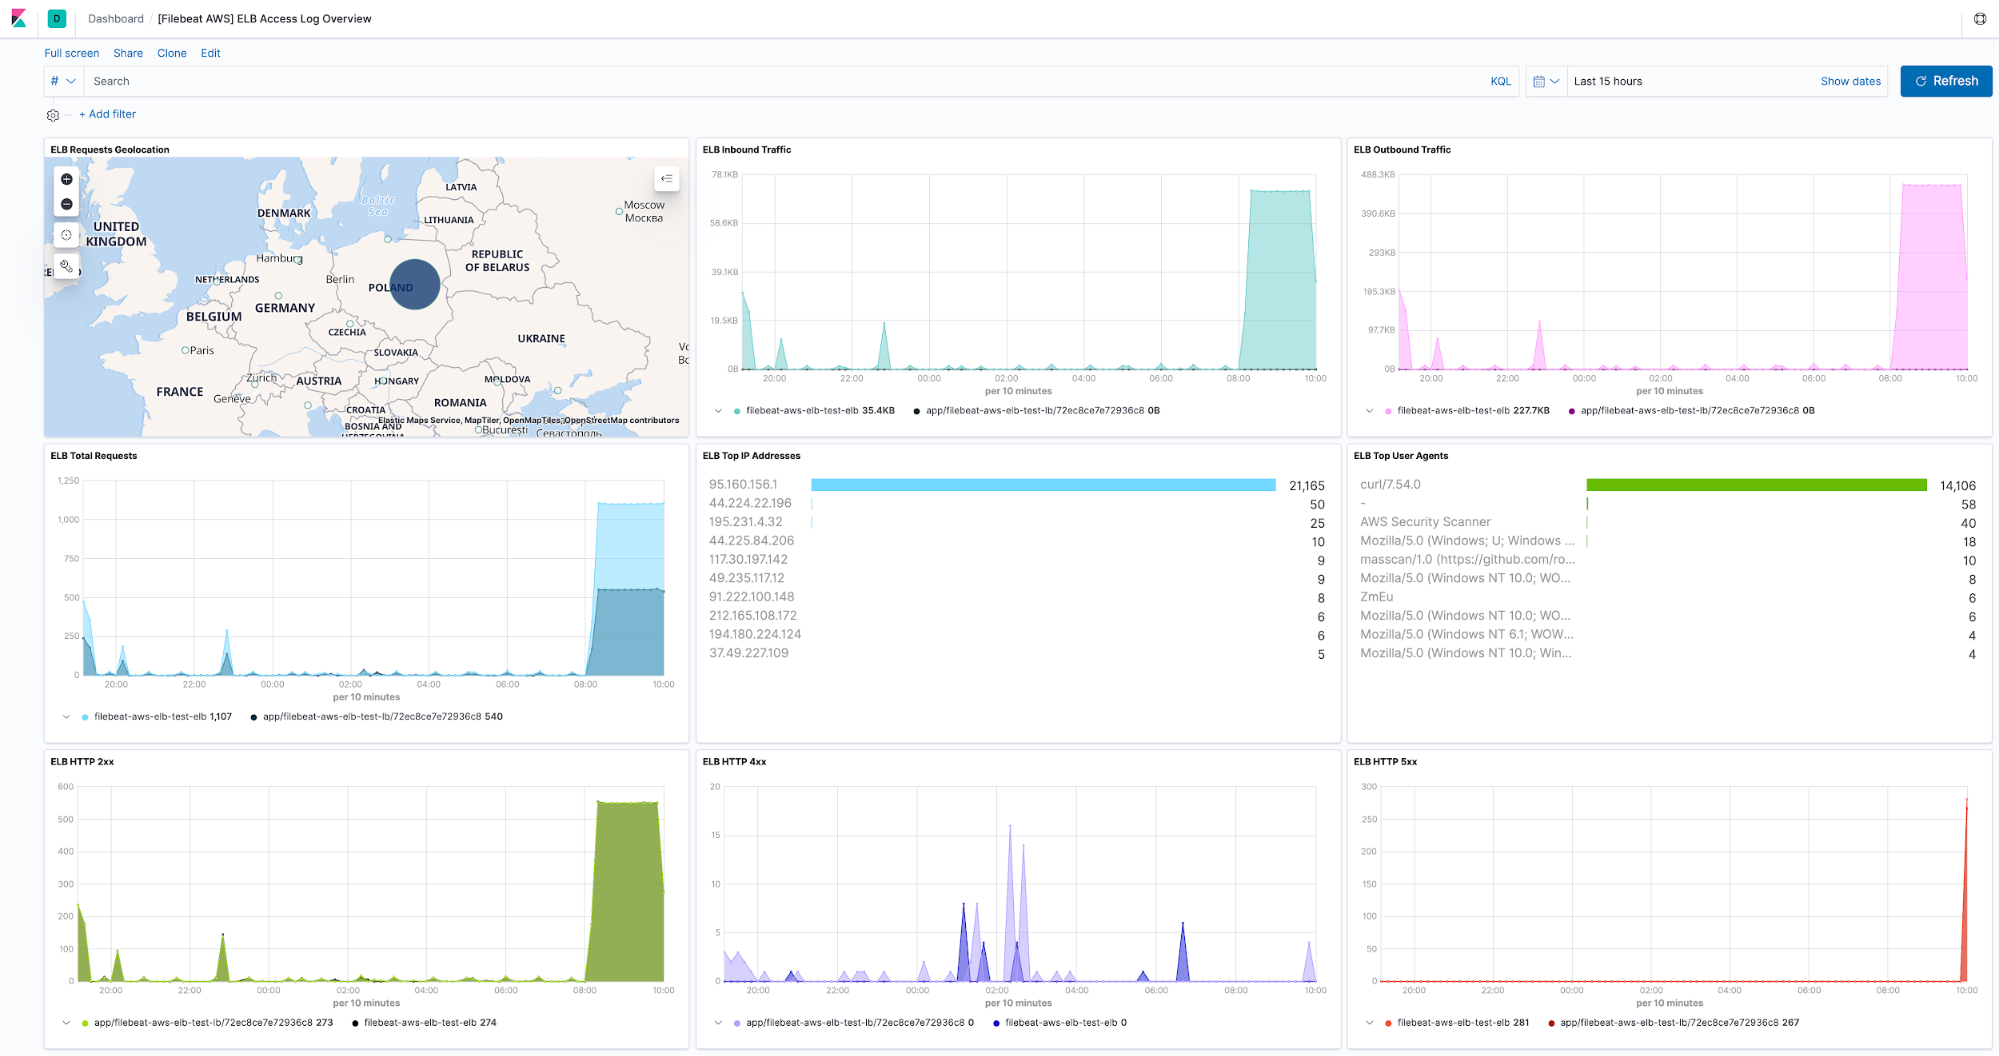
Debugging Kibana Dashboards | Elastic Blog
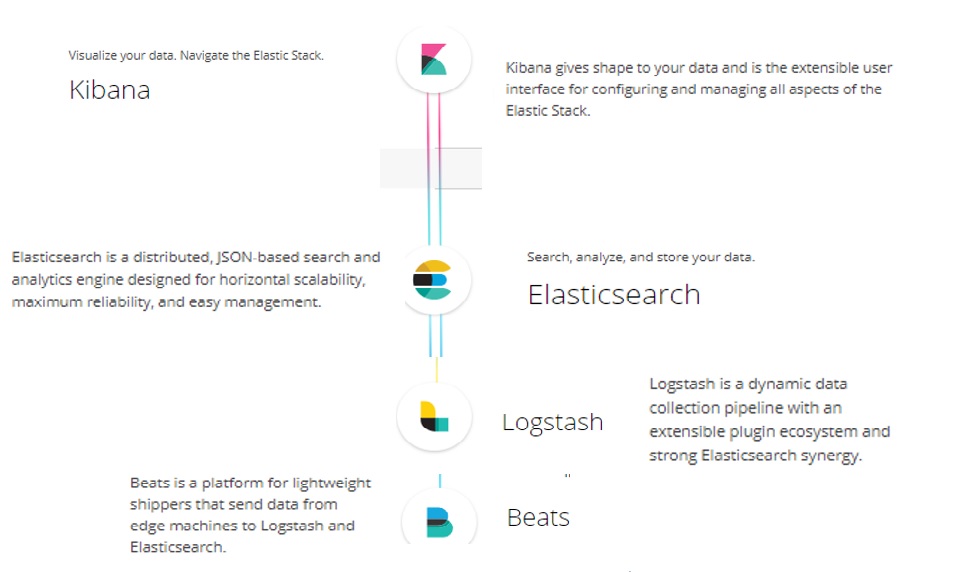
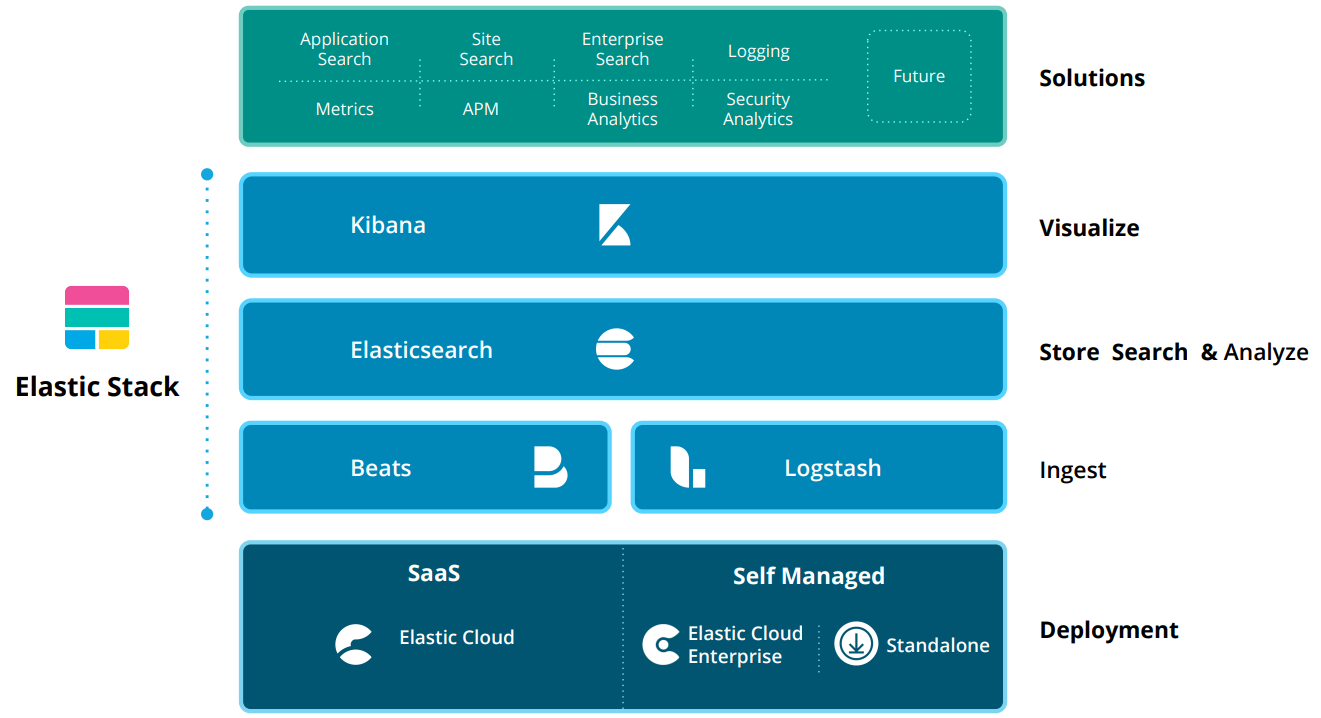
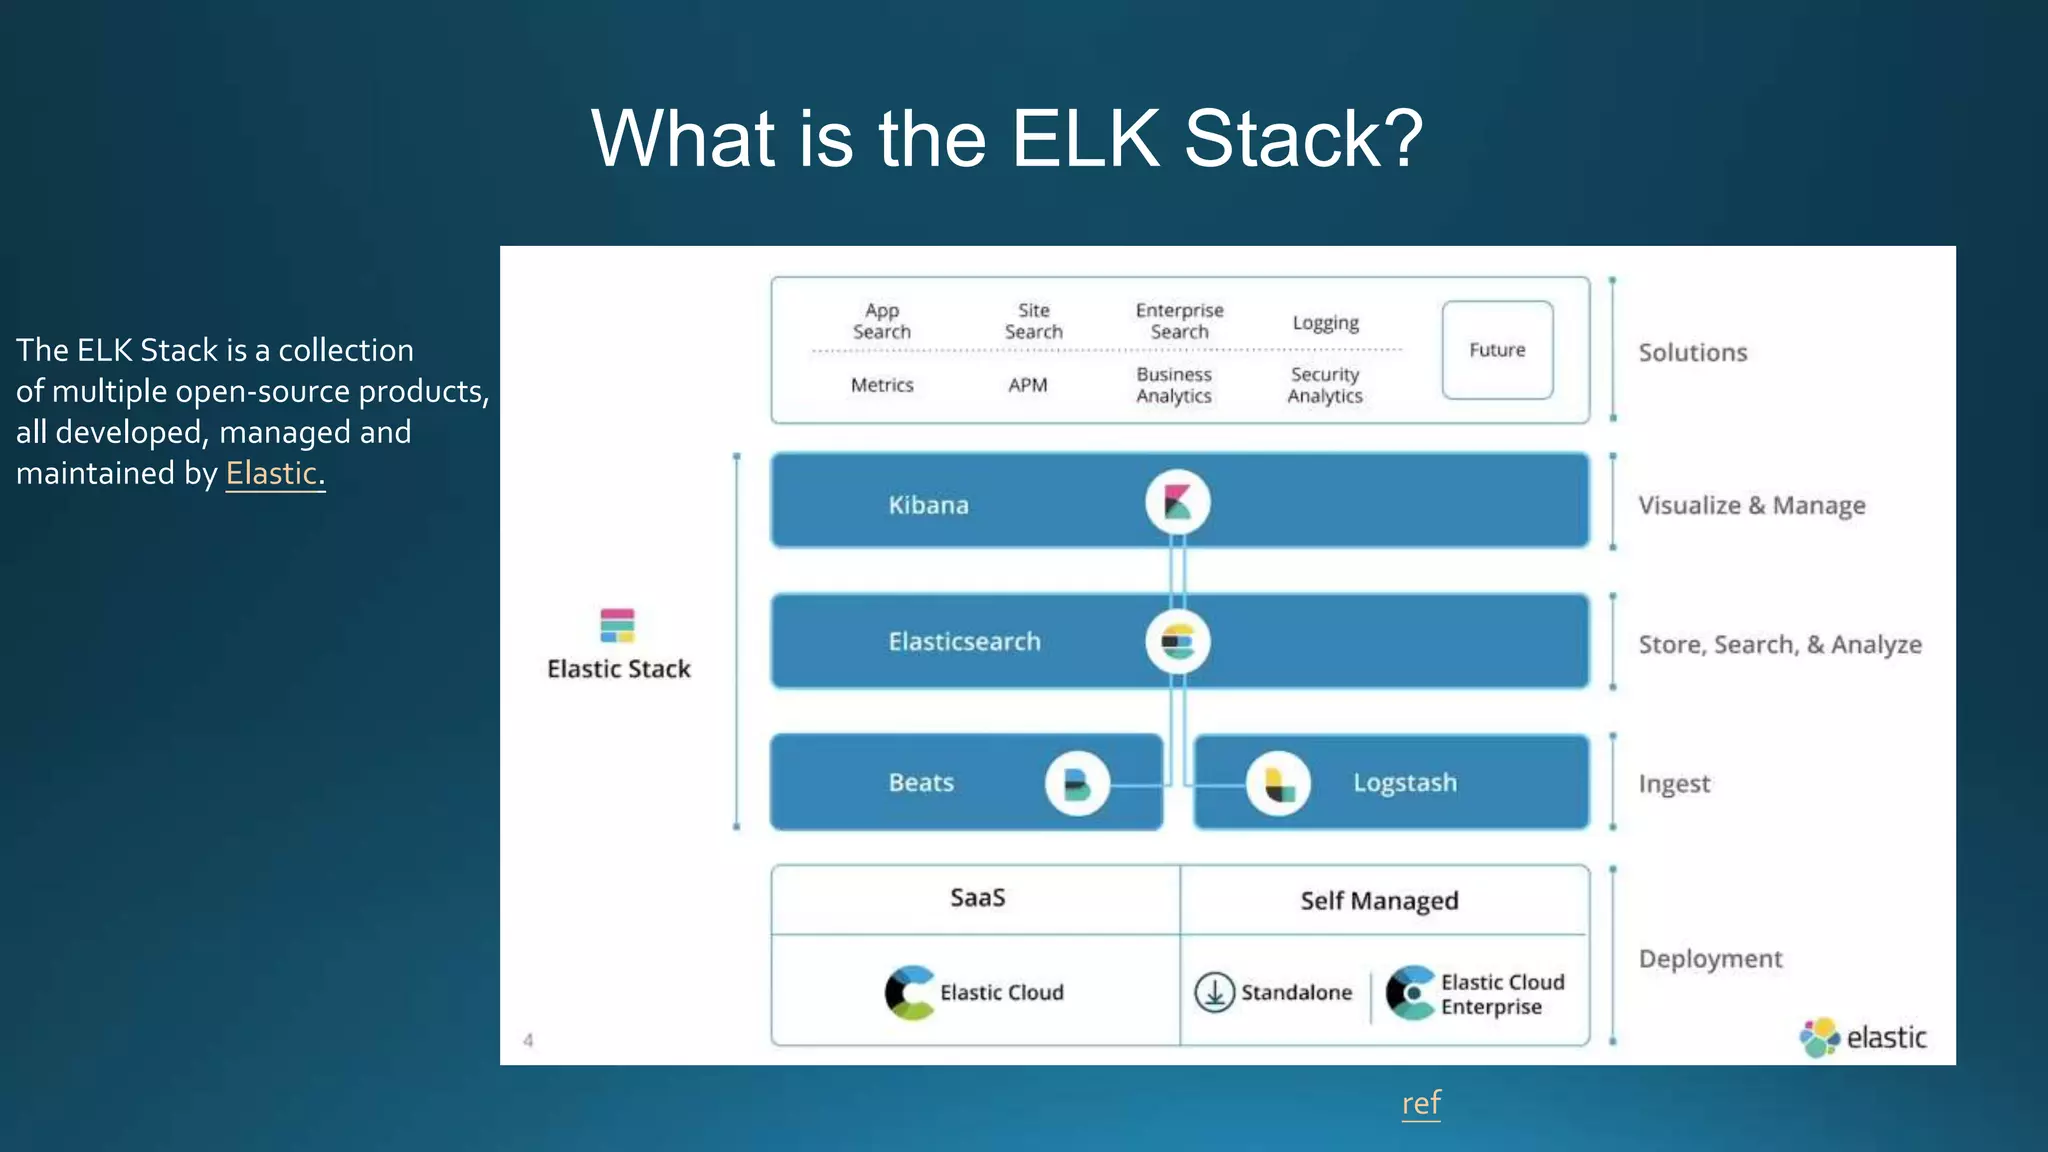
Elastic Stack Introduction | PPTX
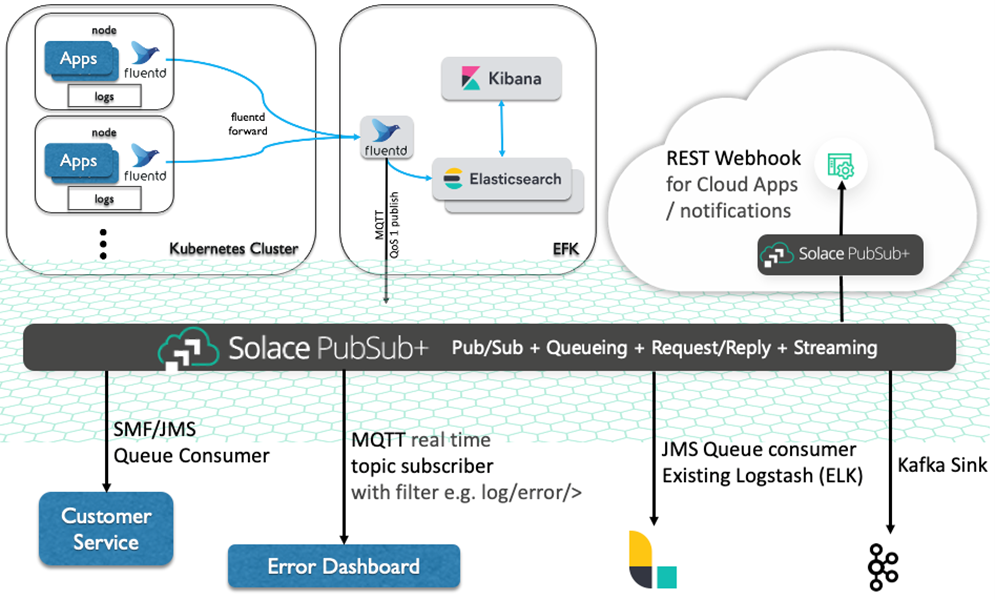
Event-Driven Logging with Elastic Stack - DEV Community
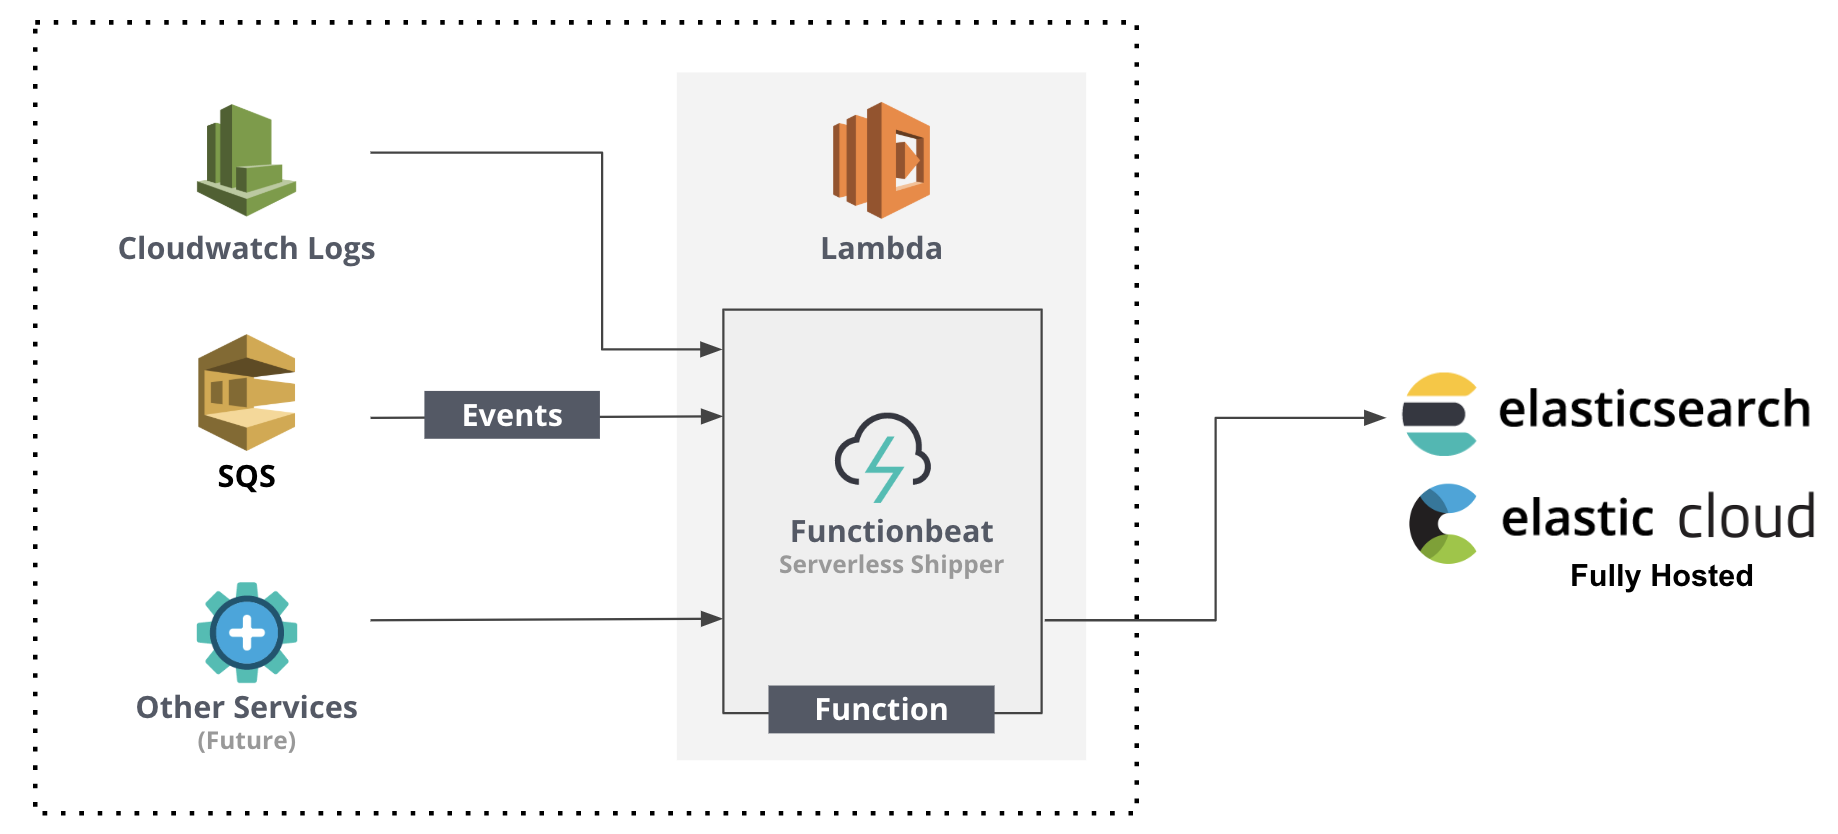
Functionbeat: Ingest Serverless Cloud Data to Elasticsearch | Elastic Blog
Elastic Logs GA Released | Elastic Blog
Elastic 5分钟教程:使用Logs应用搜索你的日志-腾讯云开发者社区-腾讯云
Analyze and compare hosts | Elastic Observability [8.19] | Elastic
How Does Elastic Stack Work at Leonard Hazzard blog
2. Introduction To The Elastic Stack | Exploit. Learn. Secure.
Elasticsearch Log Level , Logging settings in Kibana – SDQVM
Analyze Logs with Elastic Cloud from Azure Spring Apps | Microsoft Learn
Event-Driven Logging with Elastic Stack | Solace
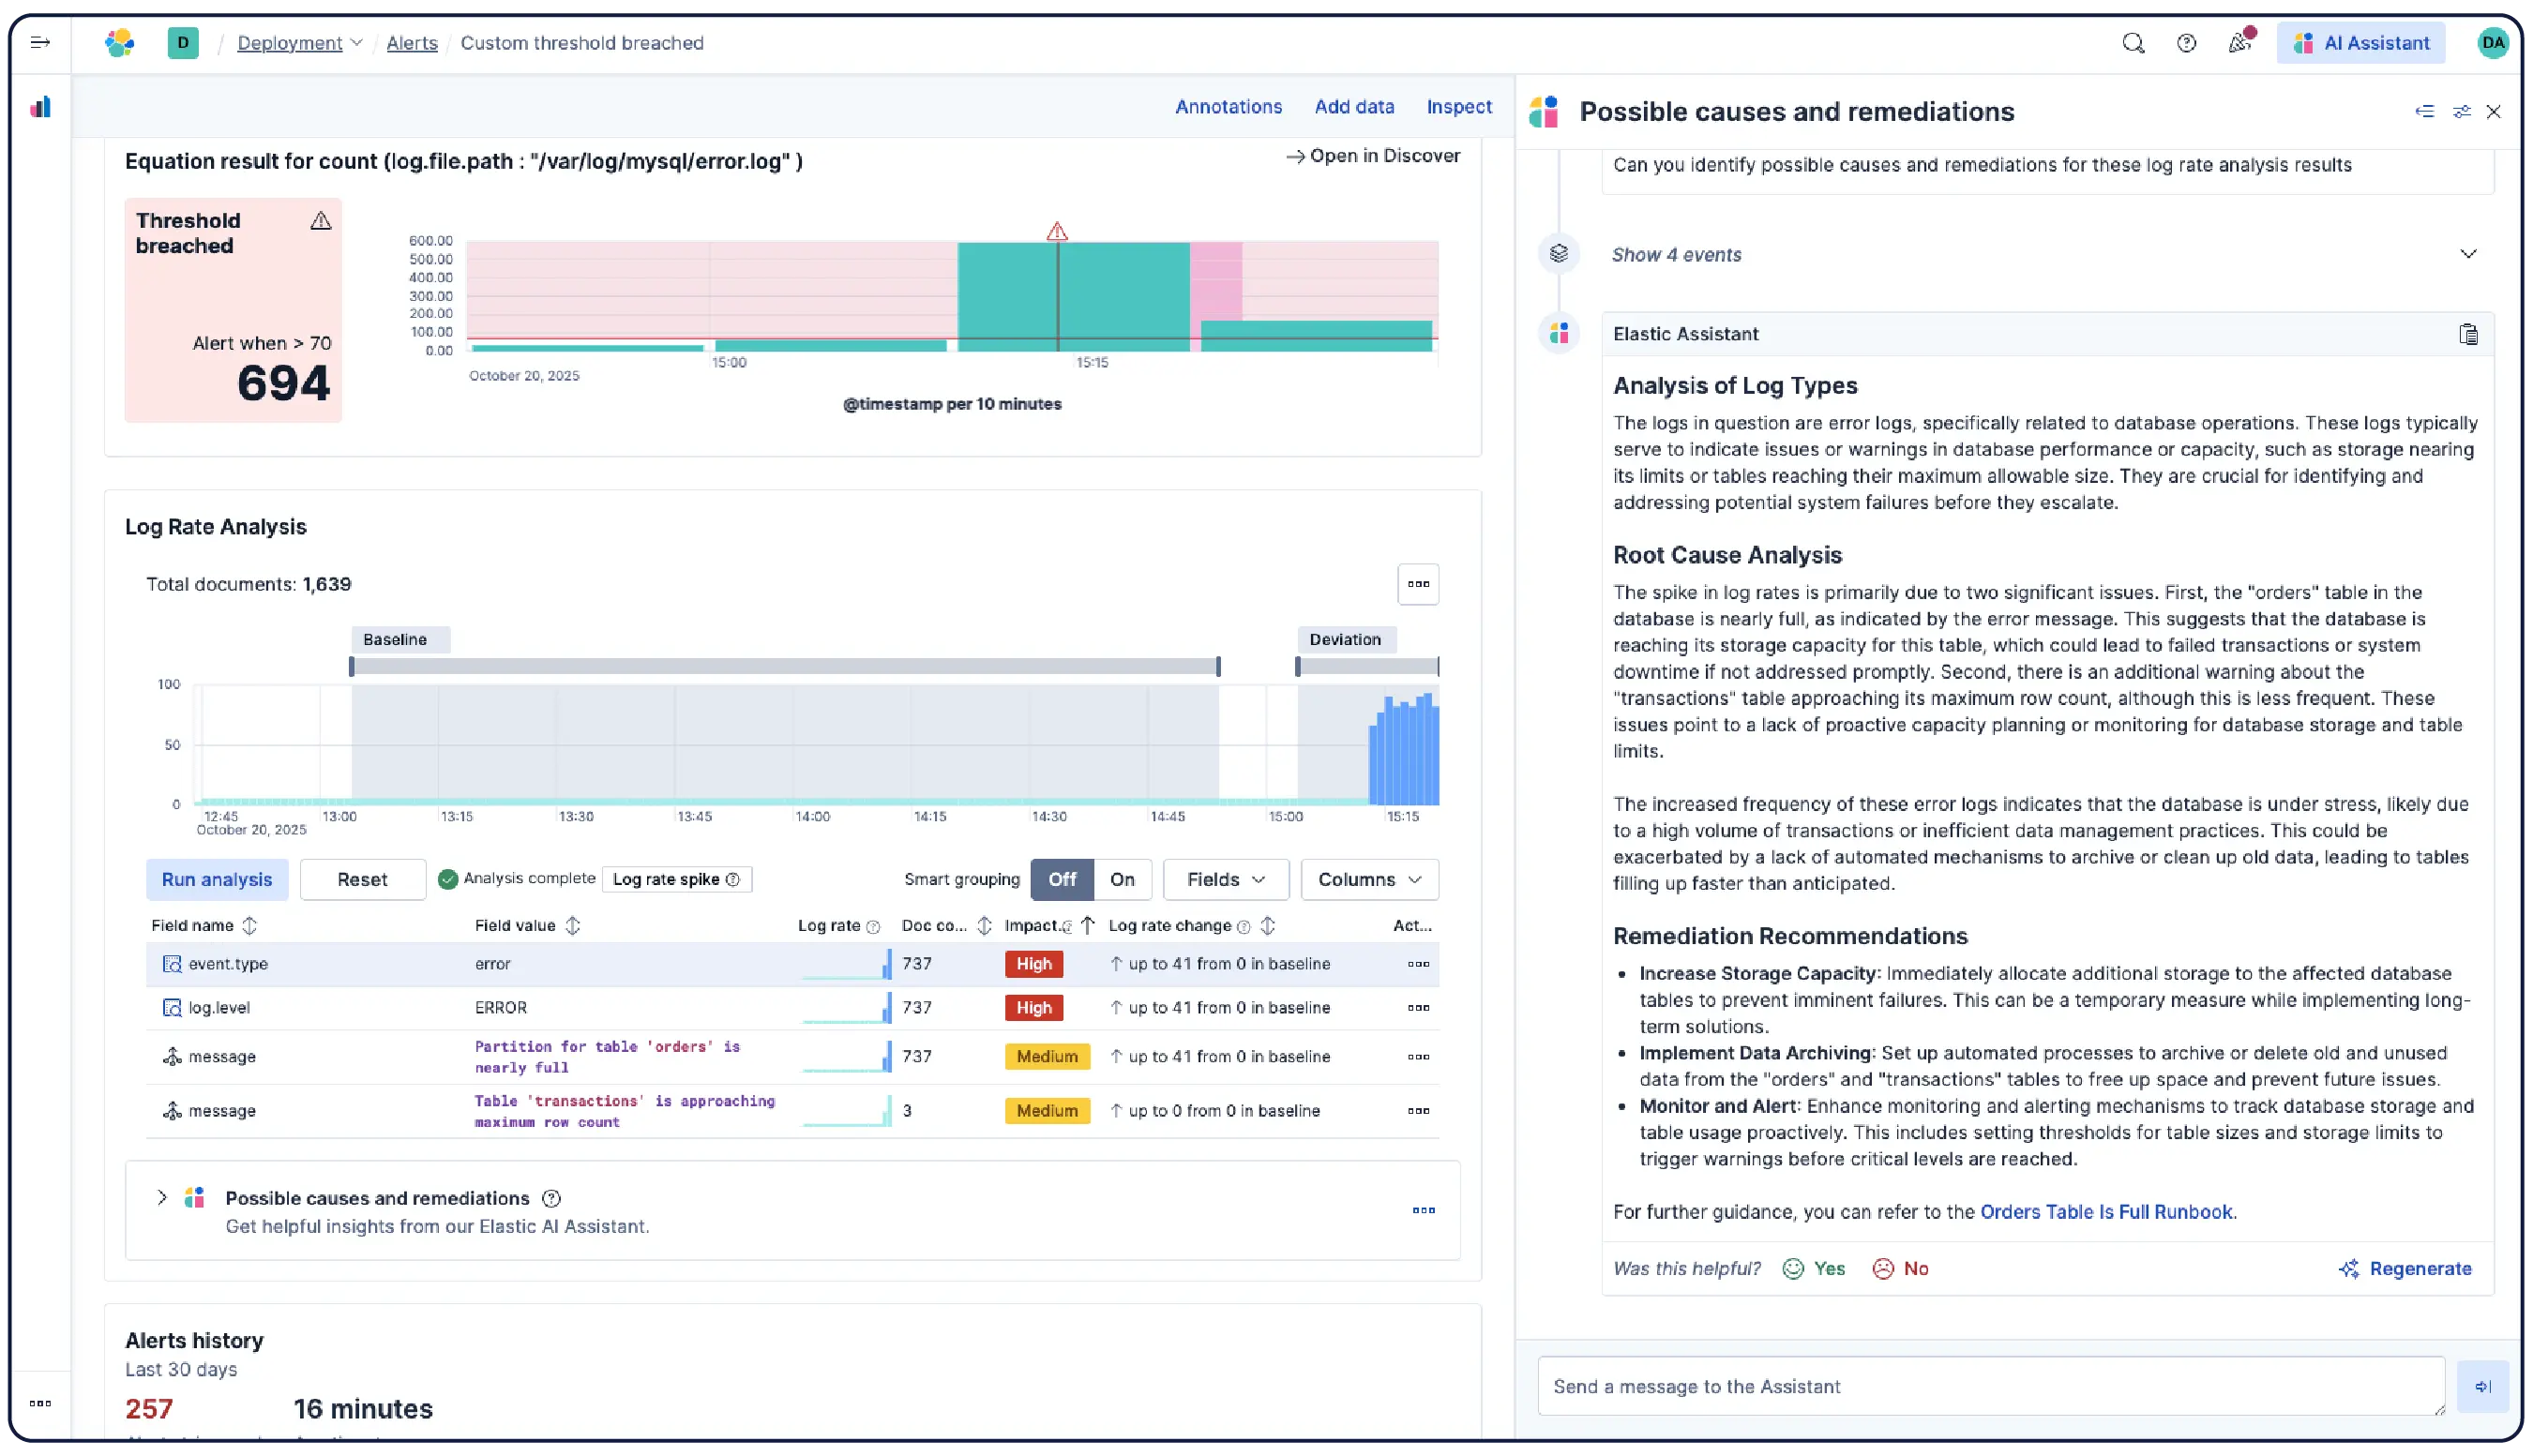
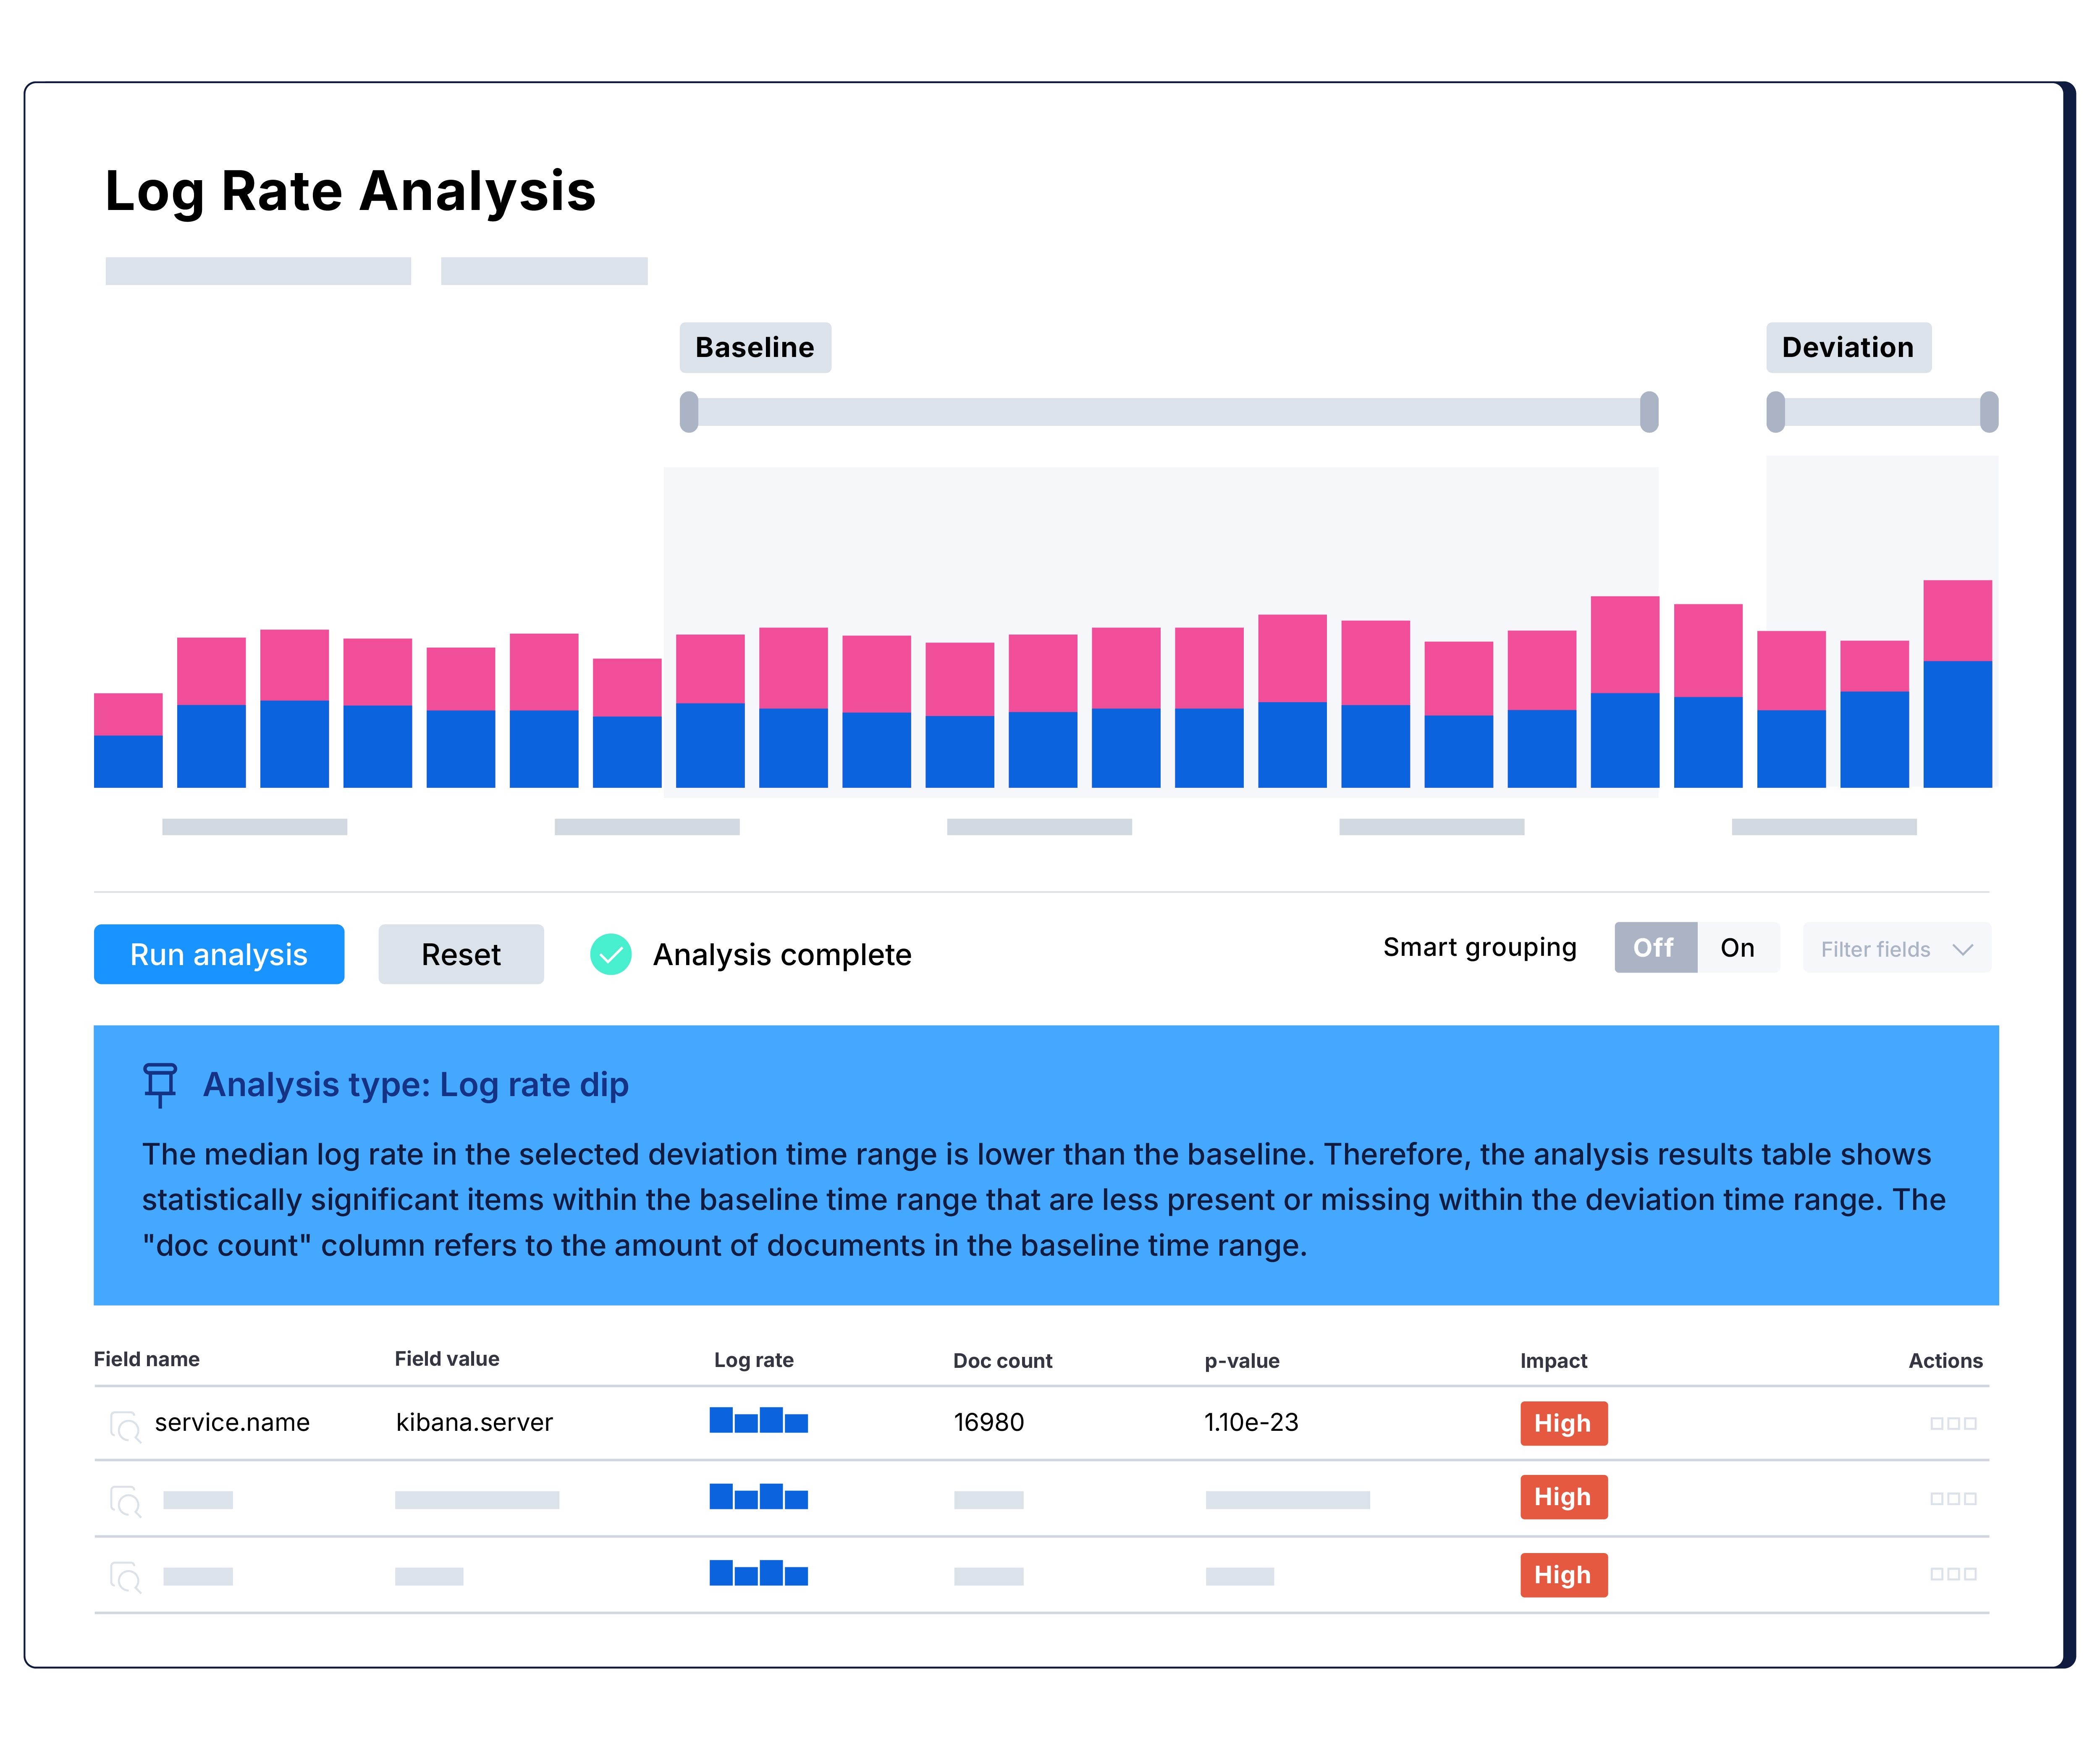
Root cause analysis with logs: Elastic Observability's AIOps Labs ...
Crossplots of measured elastic logs (left) and rock physics modelled ...
Getting started with free and open Elastic Observability | Elastic Blog
Monitoreo de Google Cloud con el Elastic Stack y Google Operations ...
What is ELK Stack and why is it so popular for log management? The ELK ...
Observability:为 Logstash 输出配置 SSL/TLS - Elastic Agent_logstash output ...
Top 10 Log Monitoring & Management Tools in 2026
Making the most of your unstructured log data through enterprise log ...
Logging With the Elastic Stack - DZone Big Data
a Elastic logs, raw logs and petrophysical interpretation logs. b ...
Elastic Common Schema .NET library and integrations released for ...
Elastic Kibana User Guide _ Kibana Guide – DGAM
elastic stack - How to gather logs to Elasticsearch - Stack Overflow
Elastic Stack: (ELK) Elasticsearch, Kibana & Logstash | Elastic
GitHub - linuxacademy/content-elastic-log-samples: Myles Elastic Stack ...
Log source "unknown" in Observability Overview - Logs - Discuss the ...
Filebeat vs. Logstash — The Evolution of a Log Shipper
Elastic instance displaying threat logs. | Download Scientific Diagram
Elastic accelerates SIEM data onboarding with Automatic Import powered ...
ELKonomics: ELK (Elastic Stack) Log Management Costs | Infographic | Loggly
Elasticsearch Log Format | How to log all executed elasticsearch ...
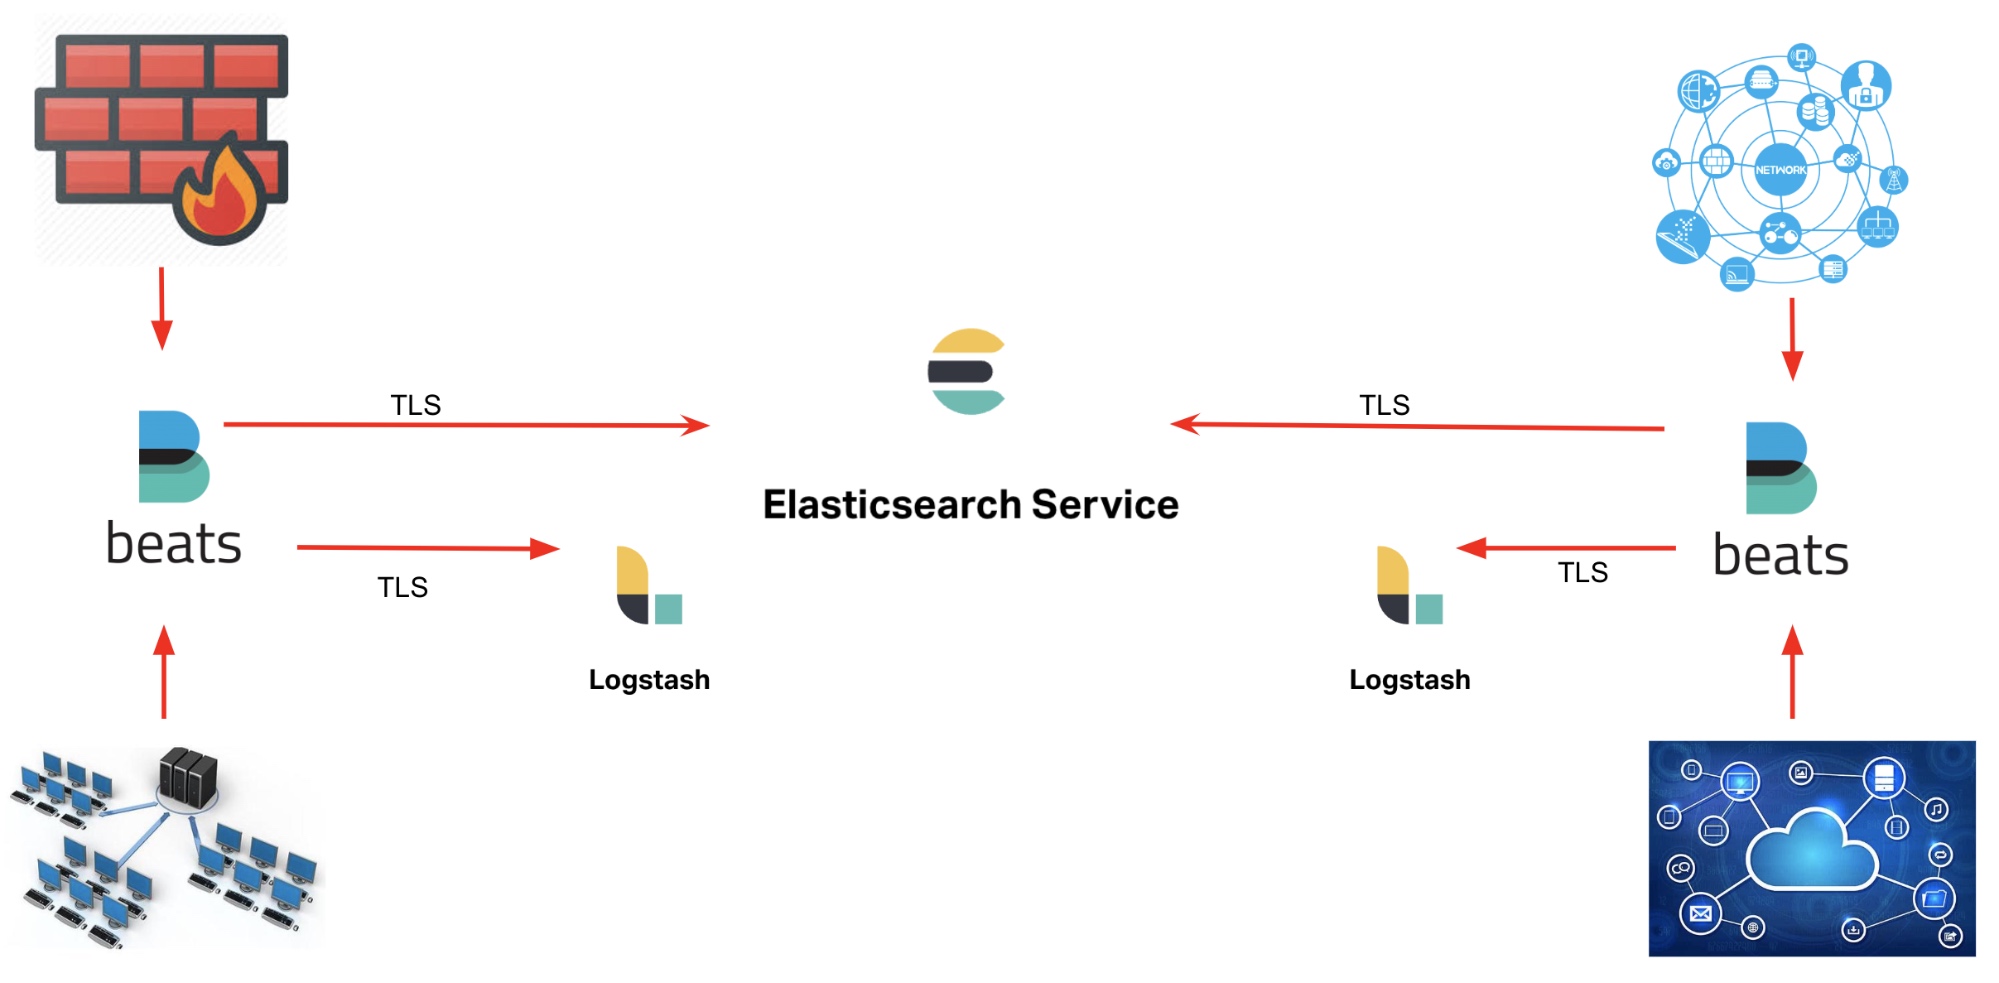
Ingest data from Beats with Logstash as a proxy | Elastic Docs
ELK Stack- Elasticsearch, Logstash and Kibana | LKDR Tech Blog
How to use Elasticsearch, Logstash and Kibana to visualise logs in ...
How To Install Elasticsearch, Logstash, and Kibana (Elastic Stack) on ...
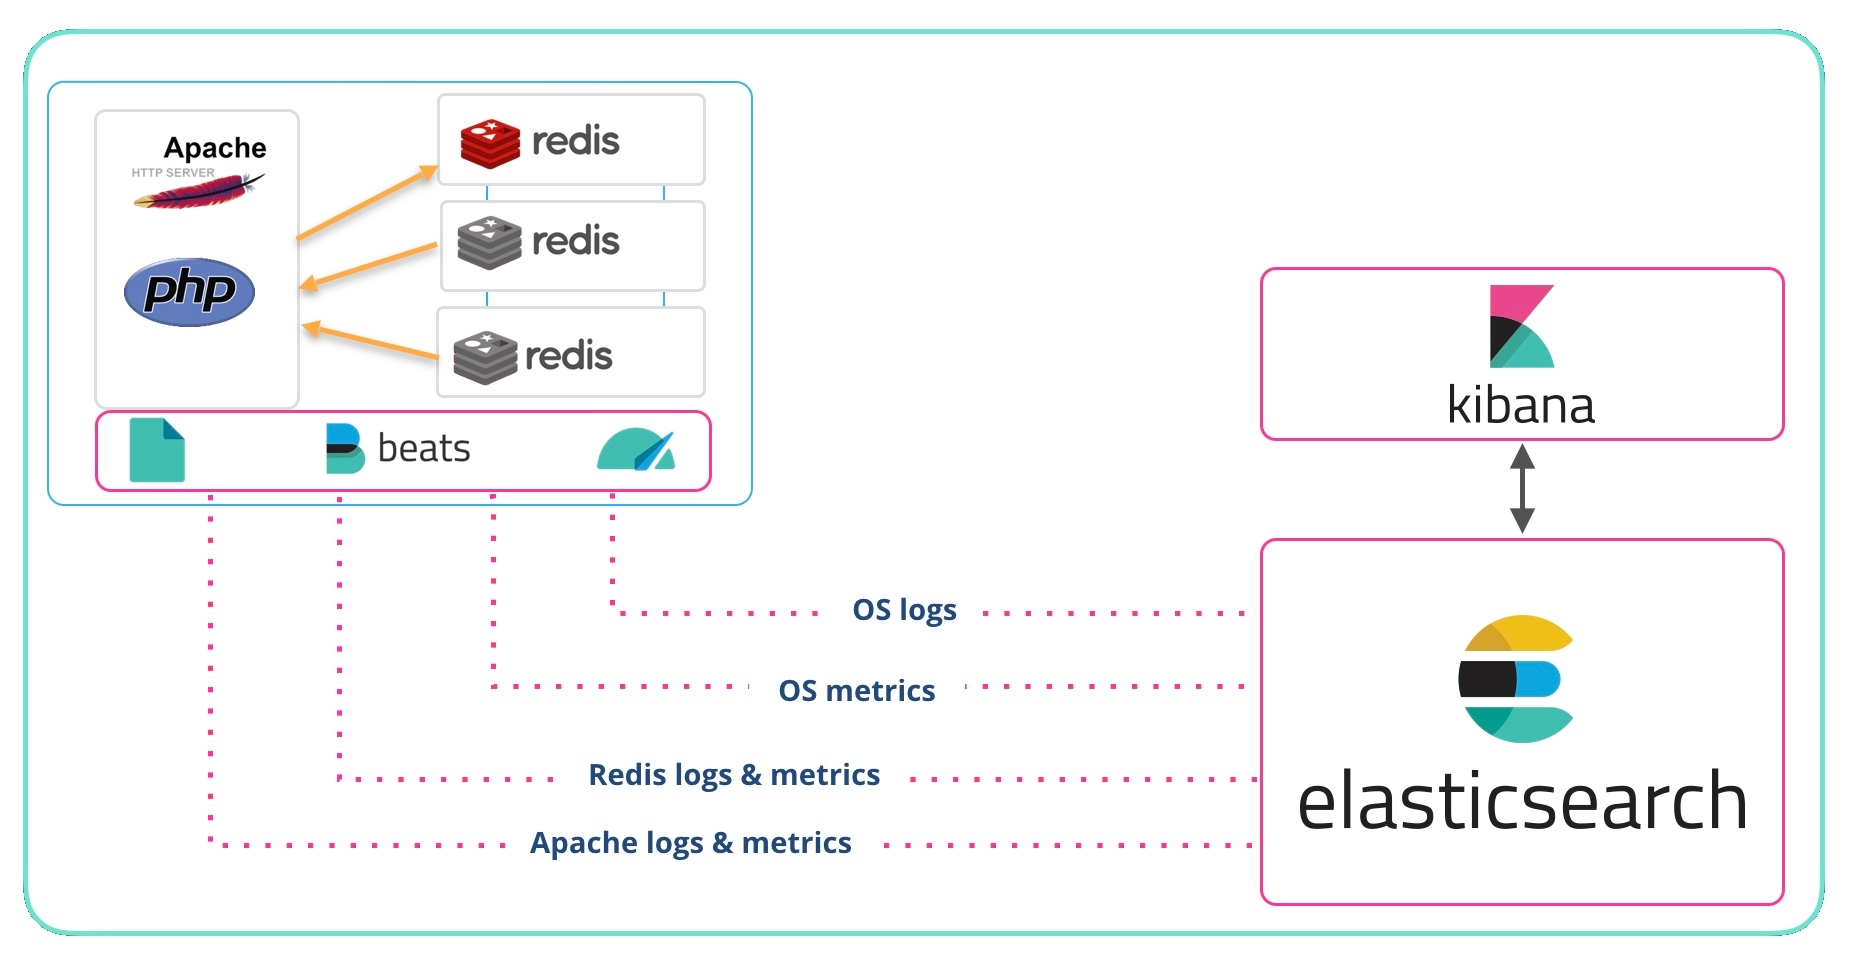
Get logs and metrics from your systems with Beats System modules ...
What is the ELK Stack | ELK | Elasticsearch | Logstash | Kibana - YouTube
What Is ELK Stack? | Elasticsearch, Logstash, & Kibana | NinjaOne
Elasticsearch Data Activity History: Control Your Data
The Complete Guide to the ELK Stack - Logz.io
Elasticsearch Stack Elk , Découvrez la stack ELK – TBMV
Alibaba Cloud Elasticsearch: What's New and Latest Features - Alibaba ...
Logging to ElasticSearch (or any other destination) | Platformatic Open ...
Centralized log-management-with-elastic-stack | PPTX
Elasticsearch Server with parsed logs | Download Scientific Diagram
The ELK Stack ( Elasticsearch, Logstash, and Kibana ) Using Filebeat ...
Elasticsearch - Sematext Documentation
Elasticsearch for Java Developers: Elasticsearch Ecosystem - Java Code ...
GitHub - it-system-software/elastic-logs: Demo project for elasticsearch
GitHub - team-data-science/Elasticsearch-Log-Analysis: Elasticsearch ...
11 mejores herramientas de gestión de logs para 2026
Elastische logboeken integreren met Azure Monitor - Microsoft Azure ...
Traces and Logs Processing | elastic/apm-data | DeepWiki
Medium
ElasticLog – Talend Custom Components – Talend Skill
Elasticsearch Get All Documents – JCGDPK
LoggingELK Reference