Showing 120 of 120on this page. Filters & sort apply to loaded results; URL updates for sharing.120 of 120 on this page
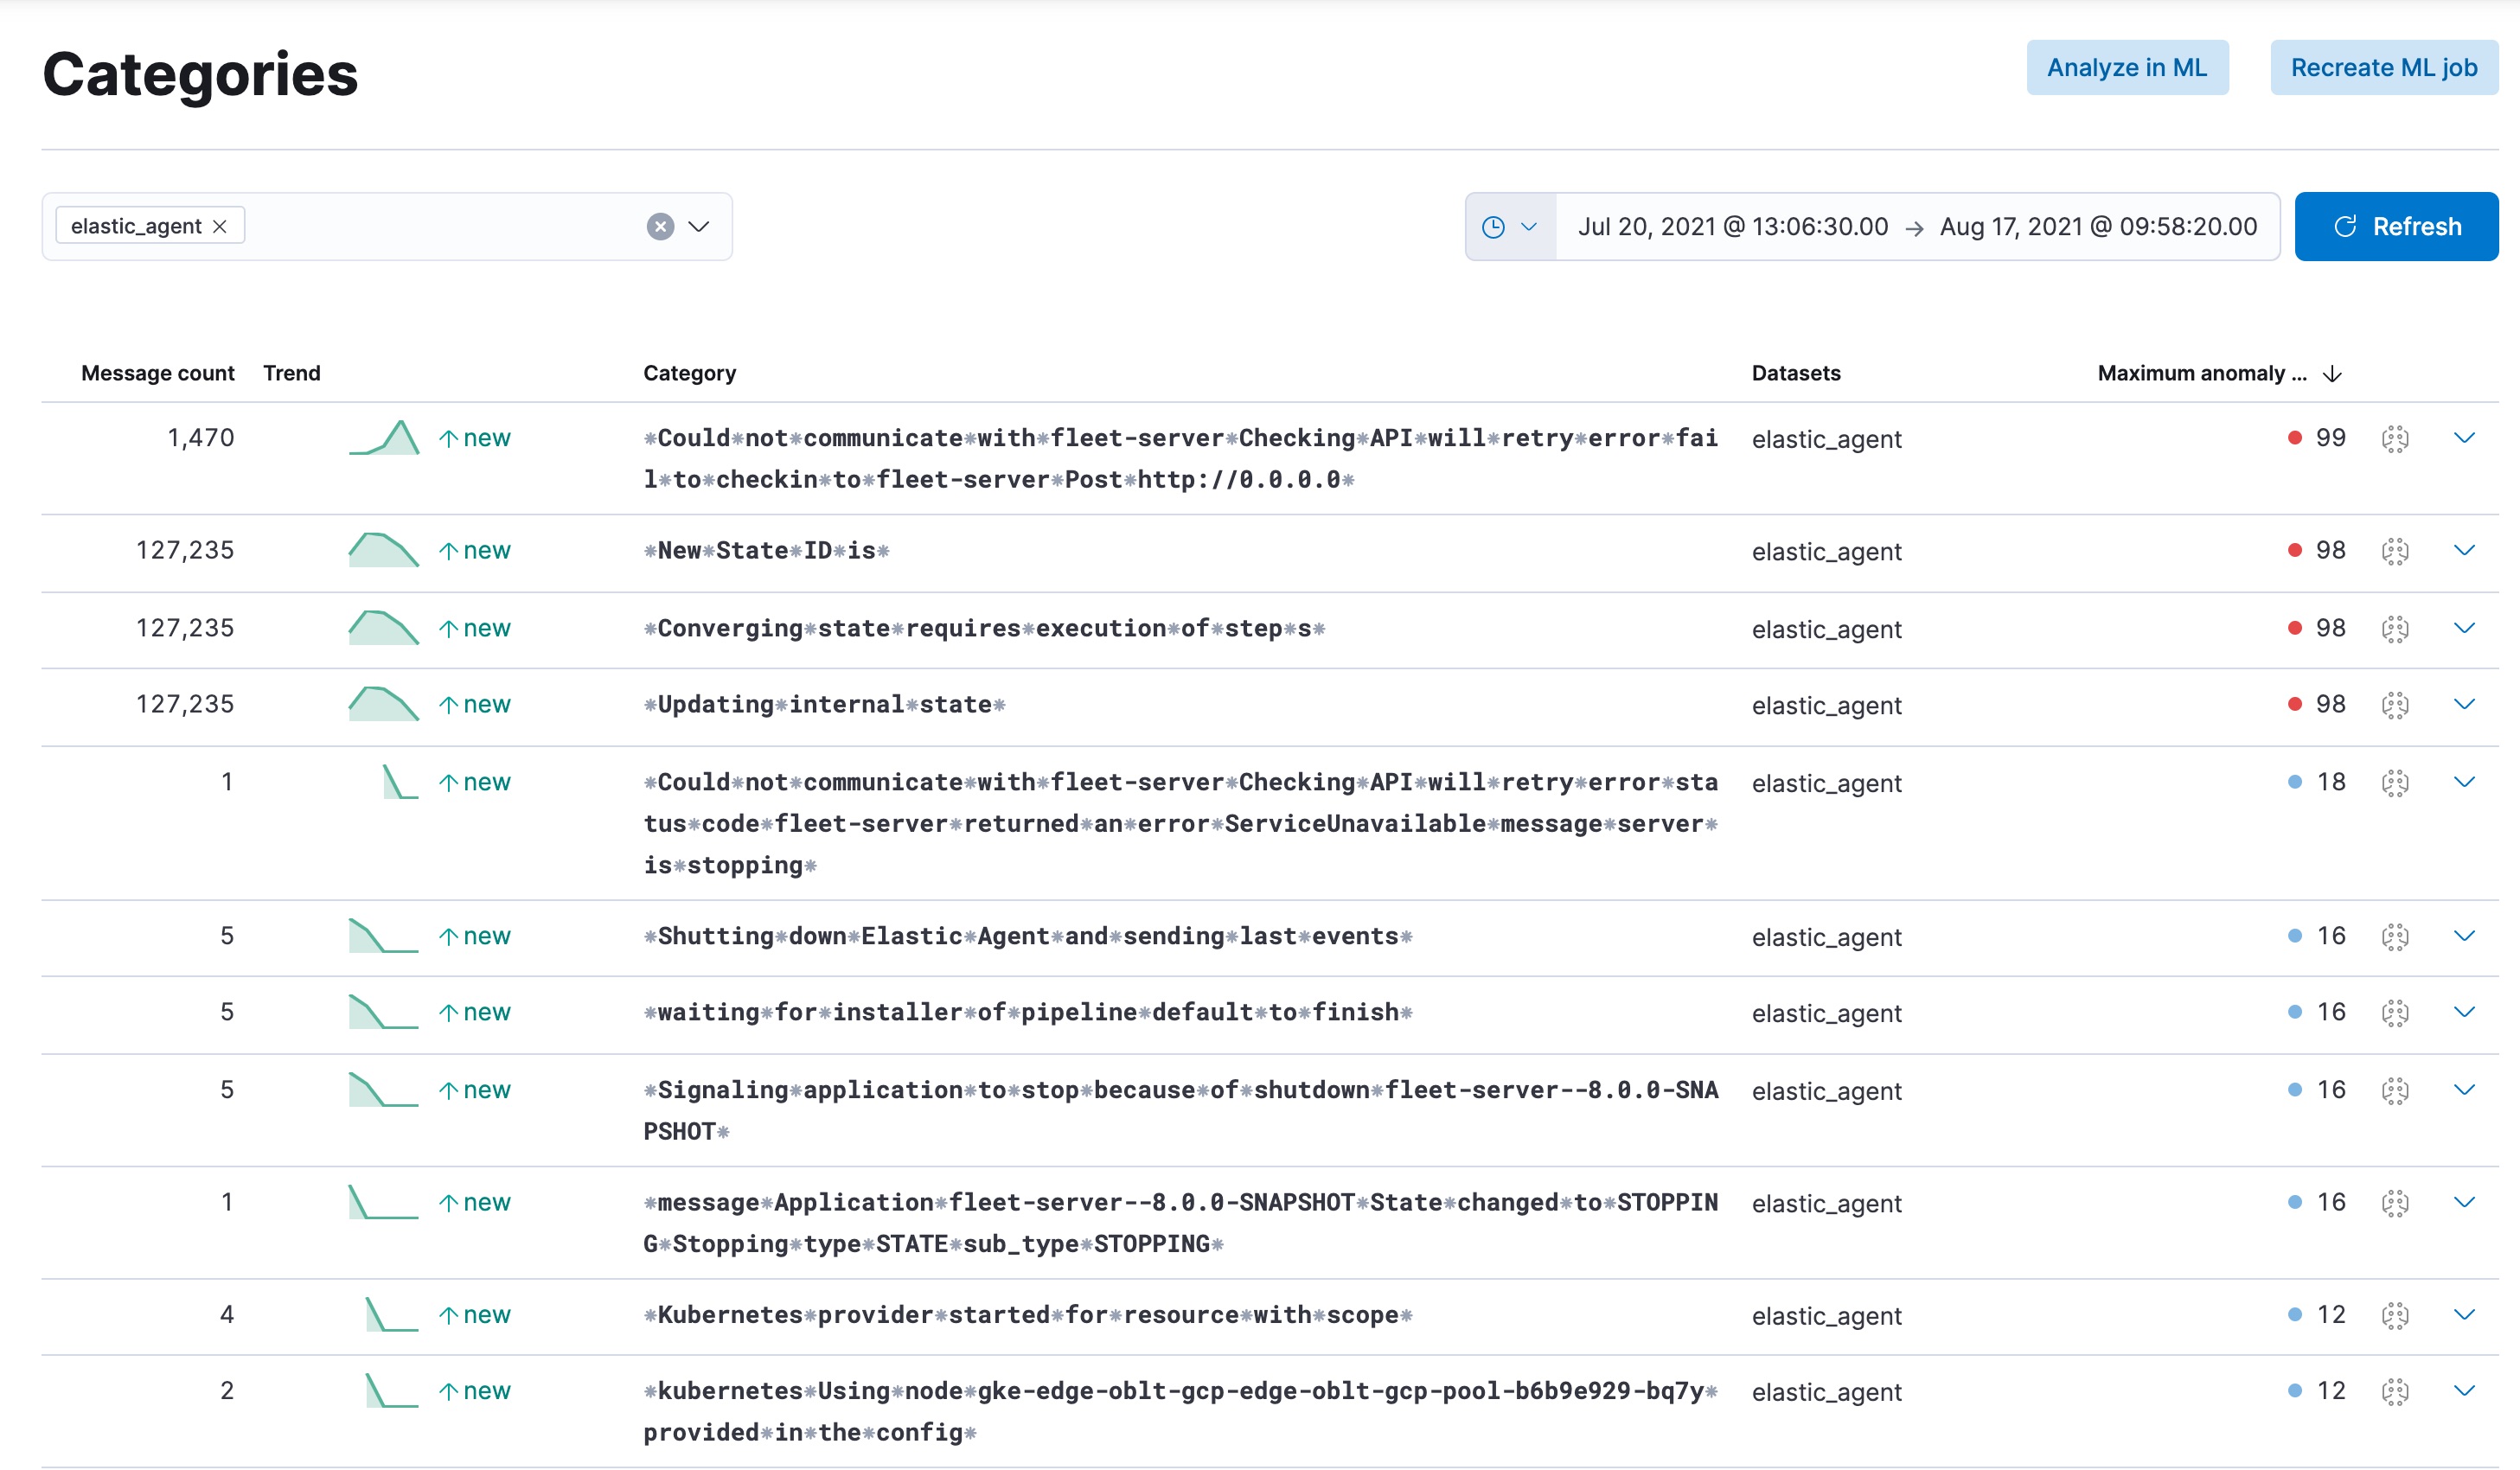
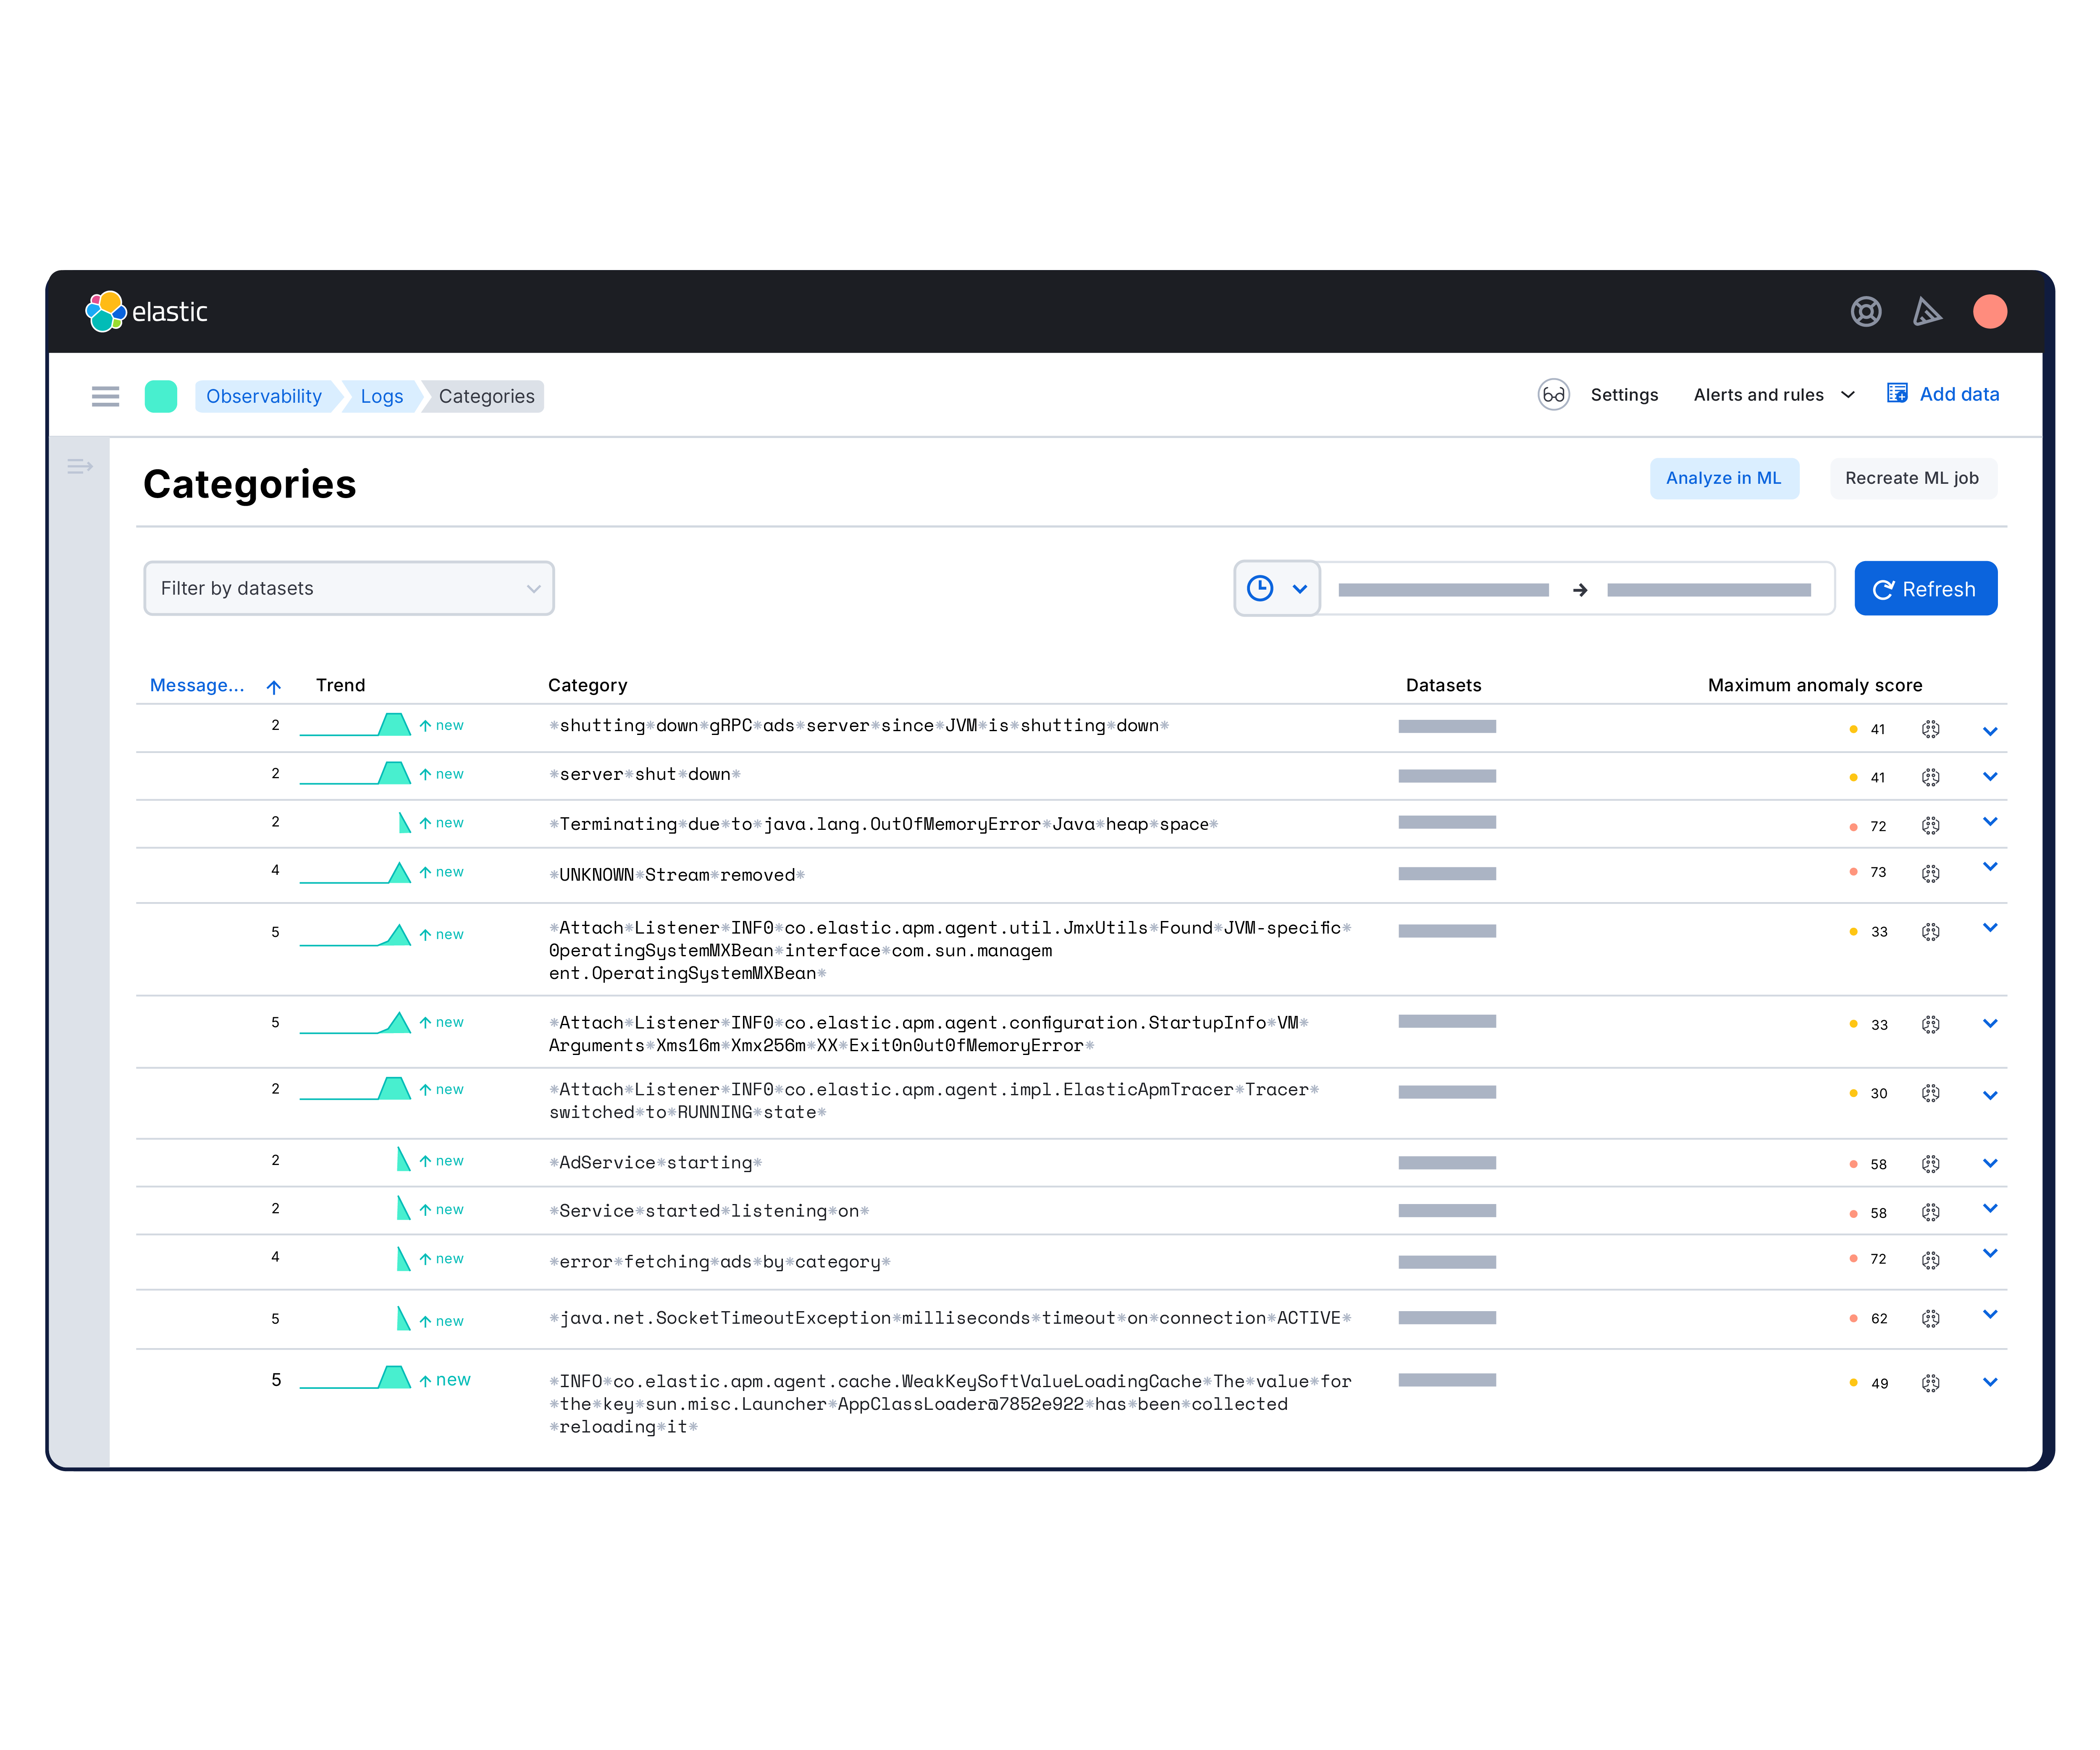
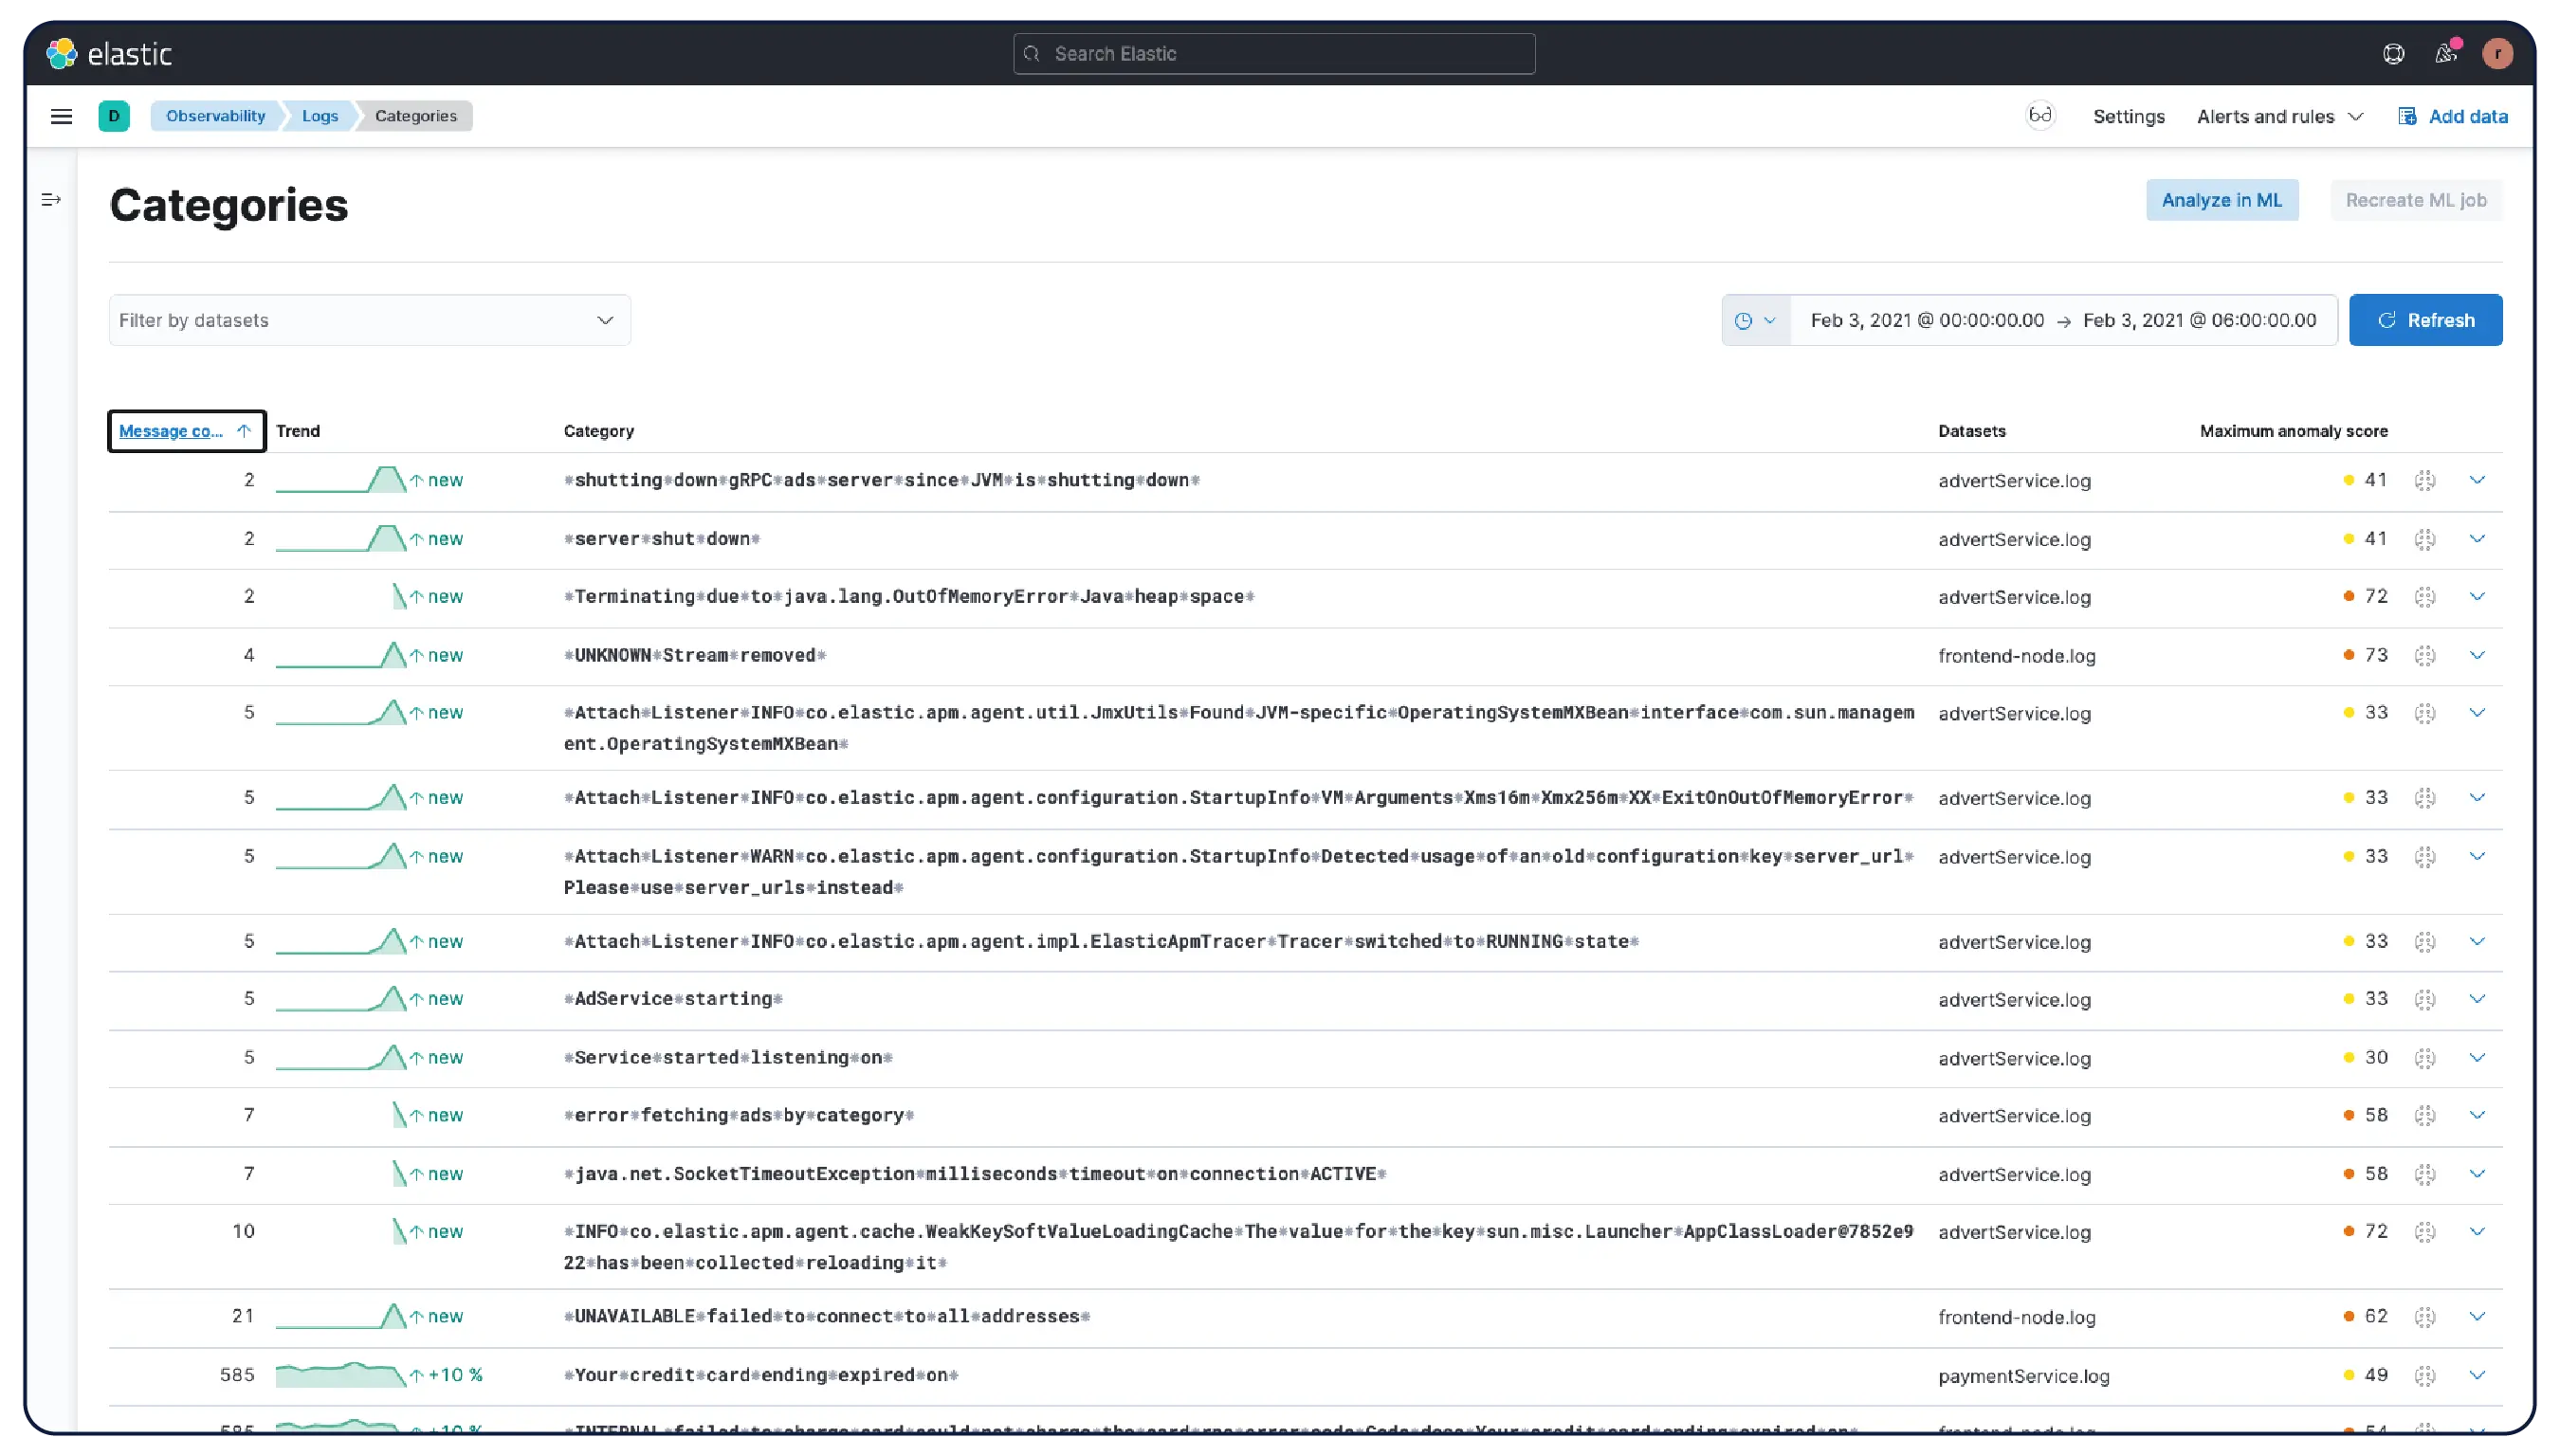
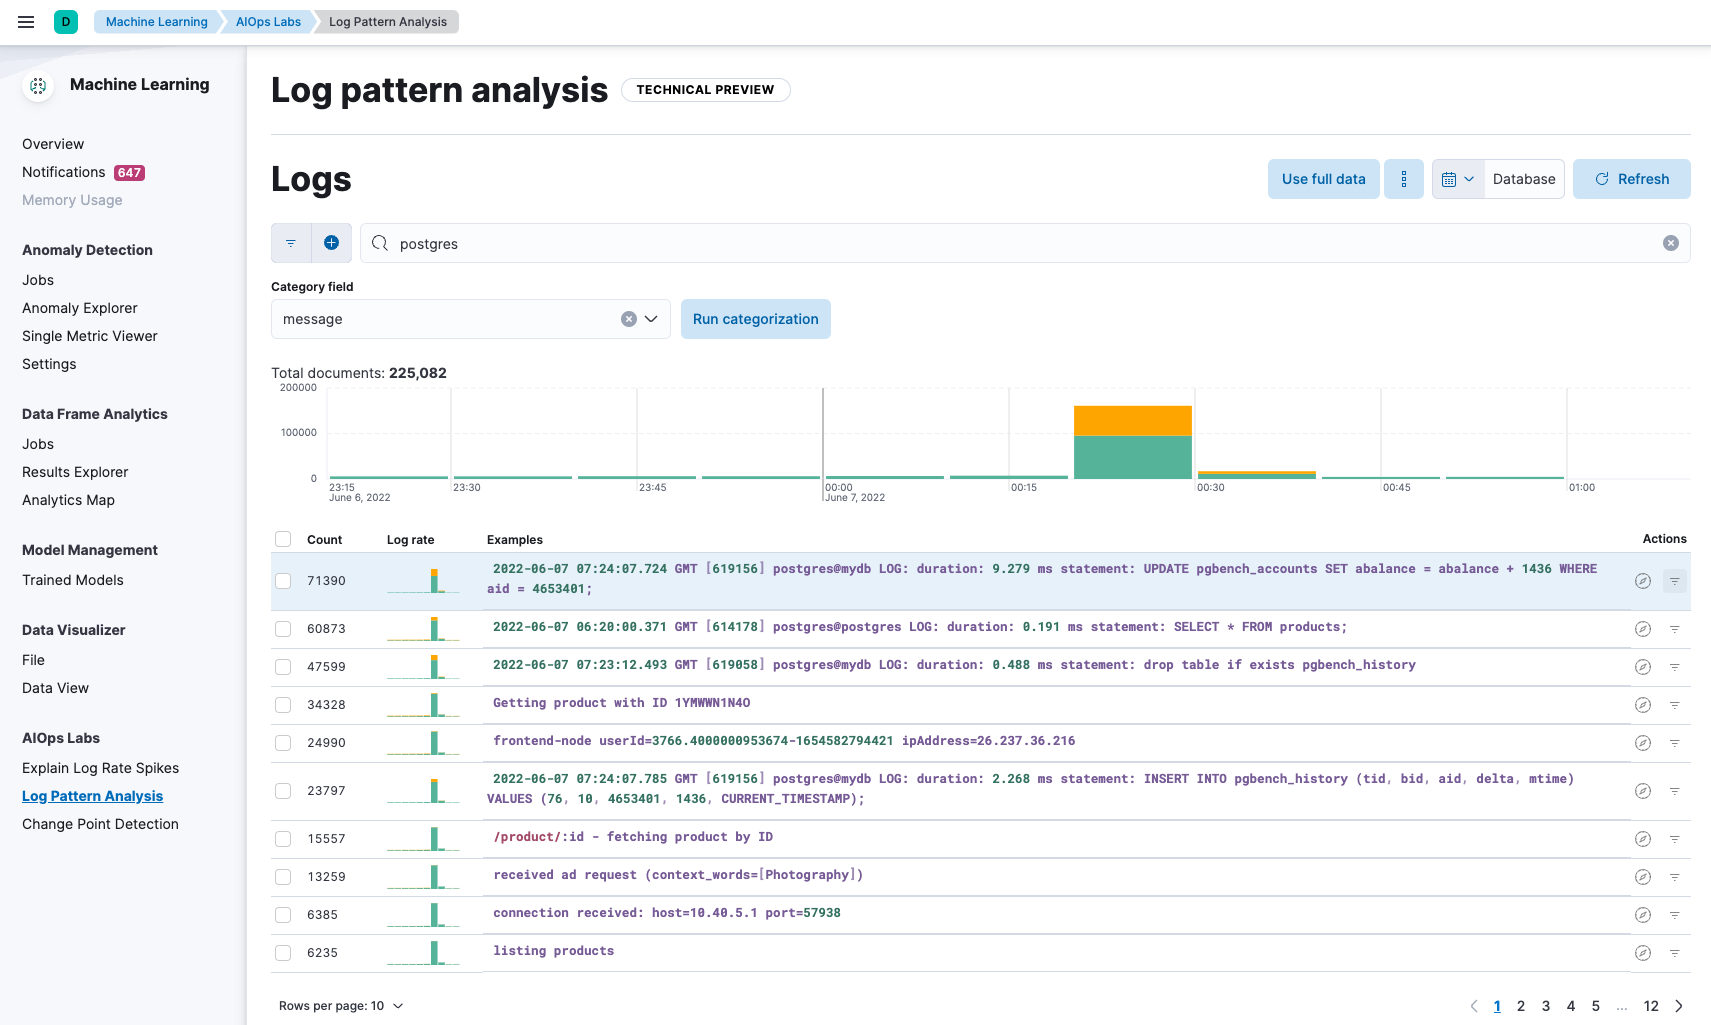
Categorize log entries | Elastic Docs
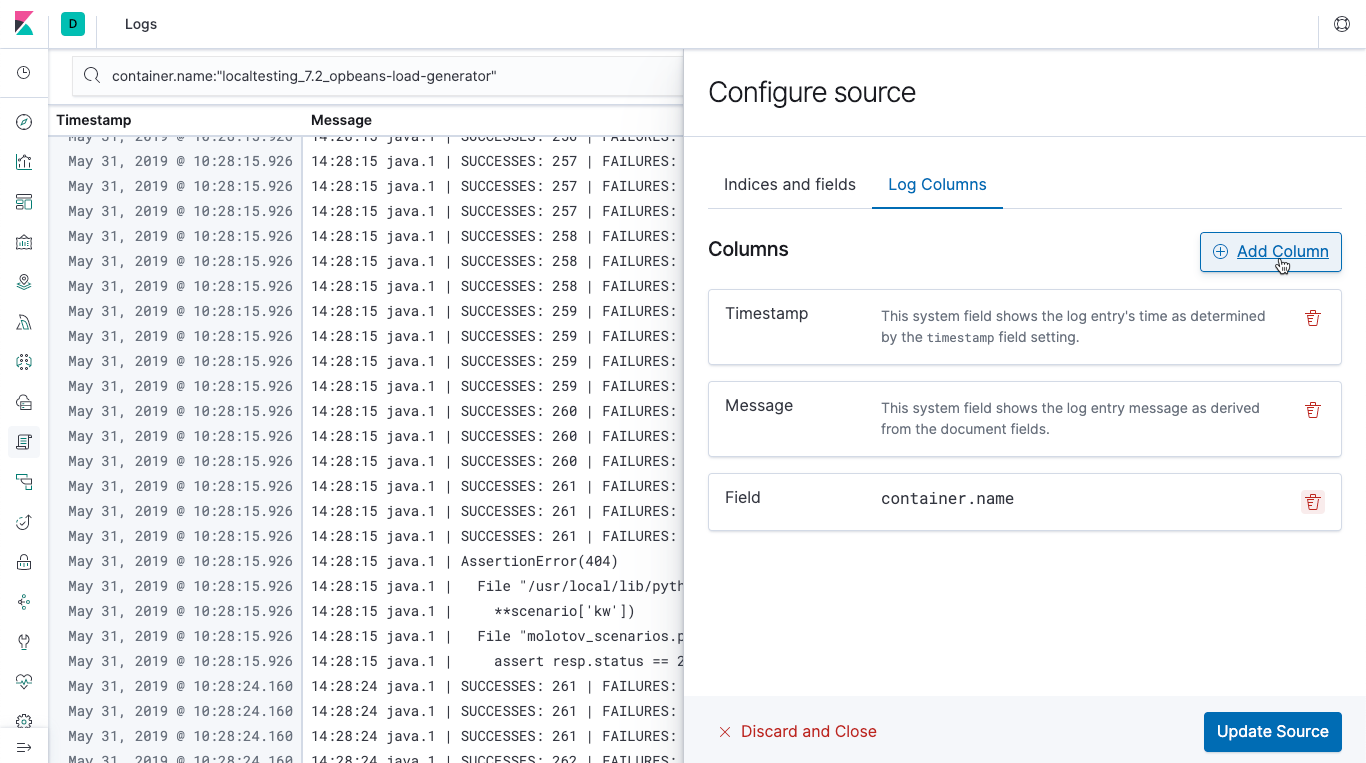
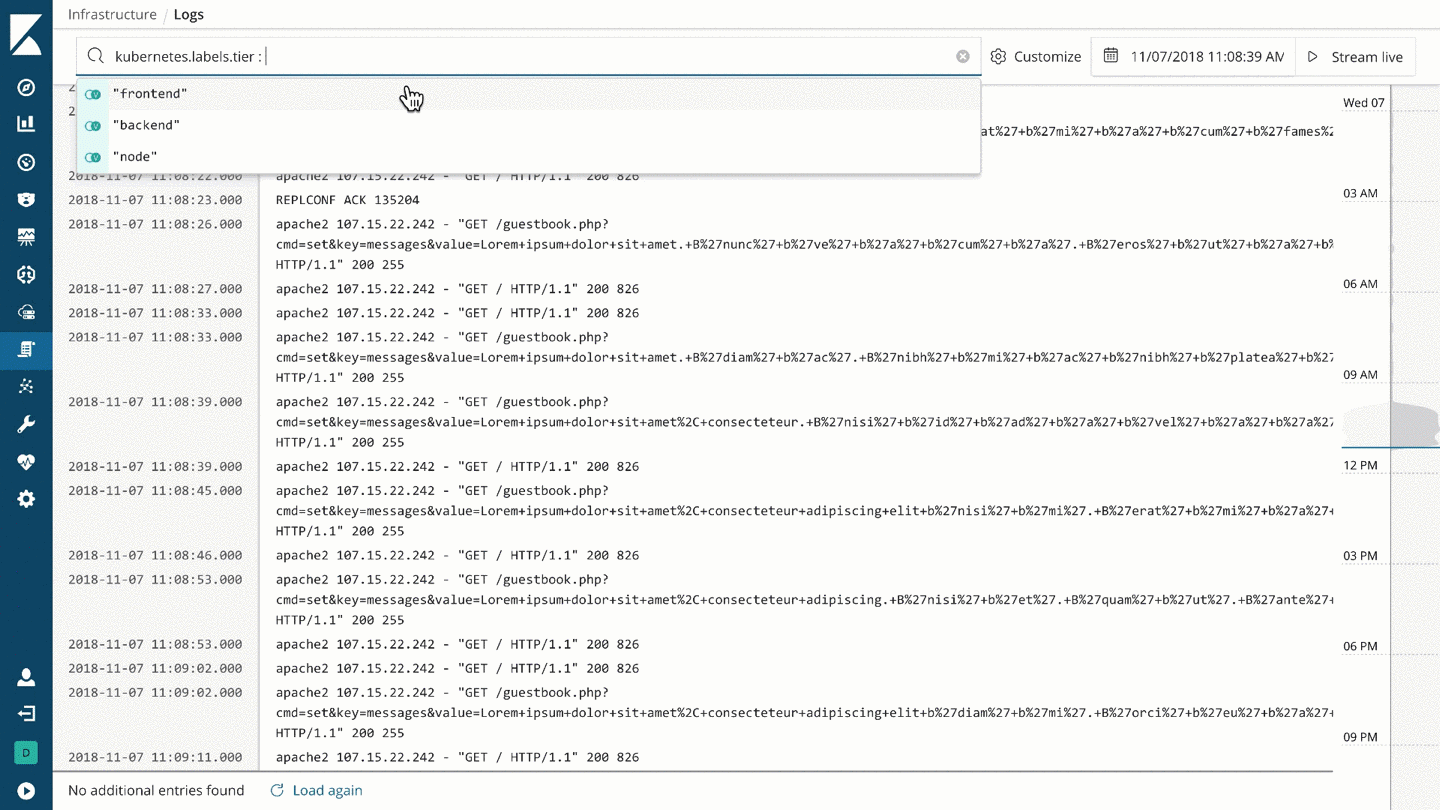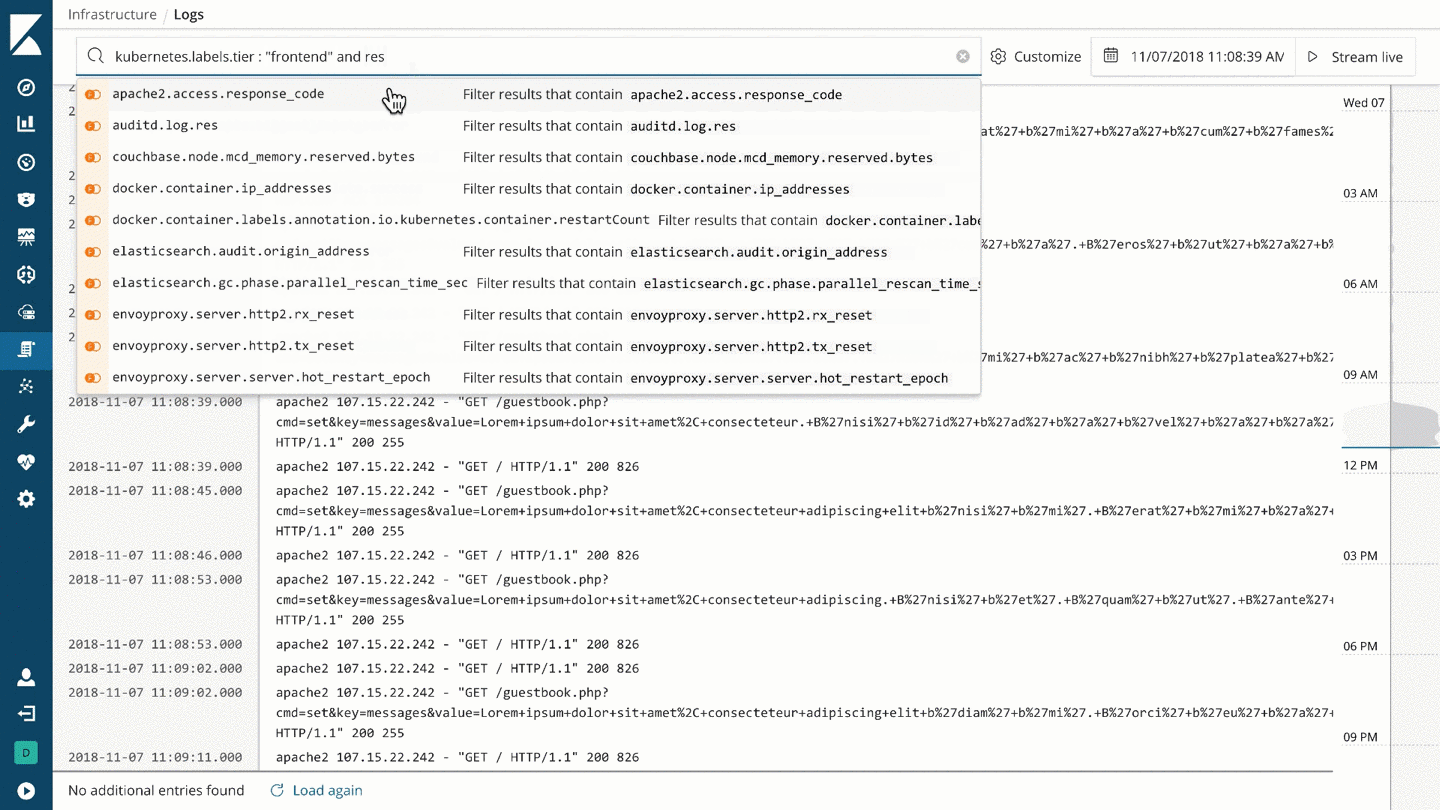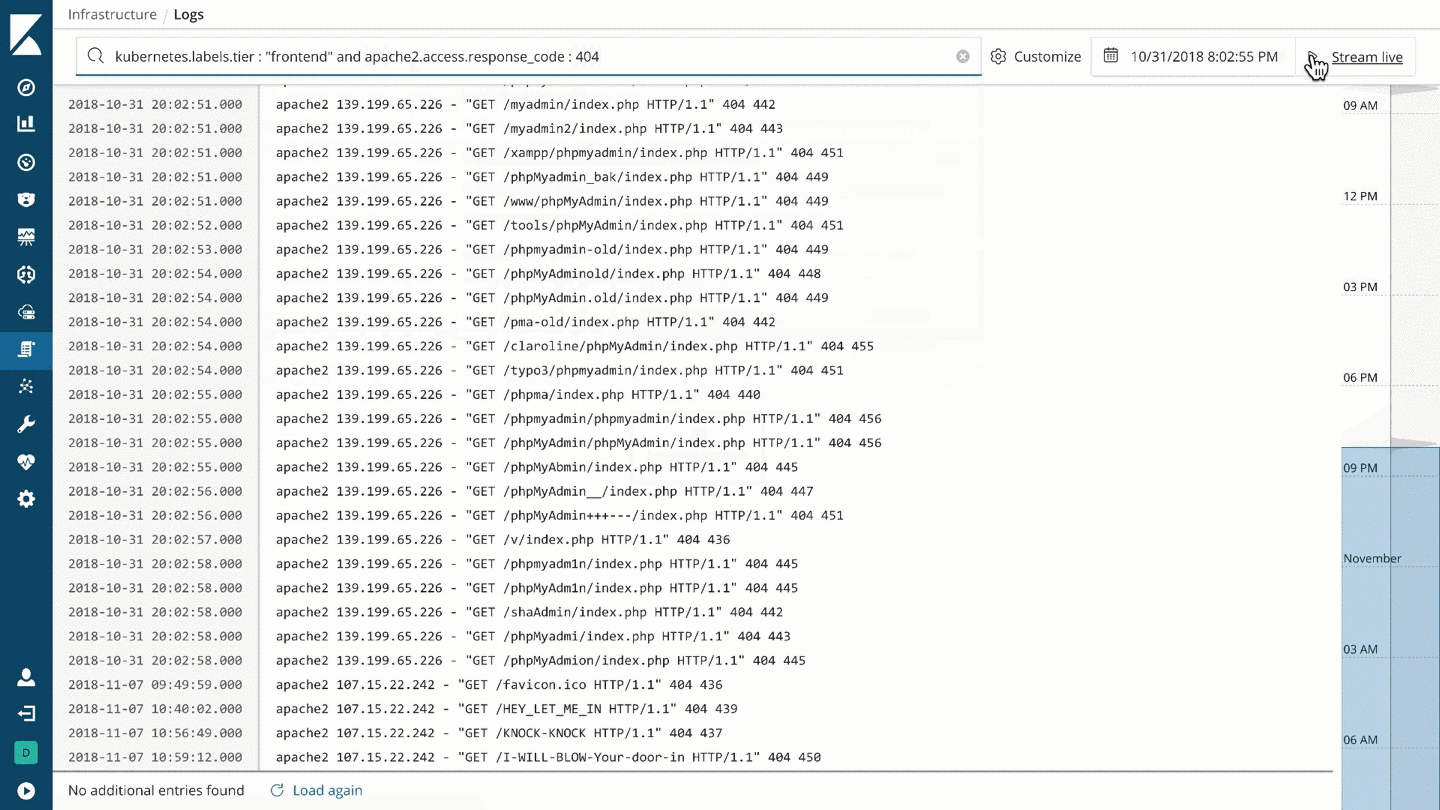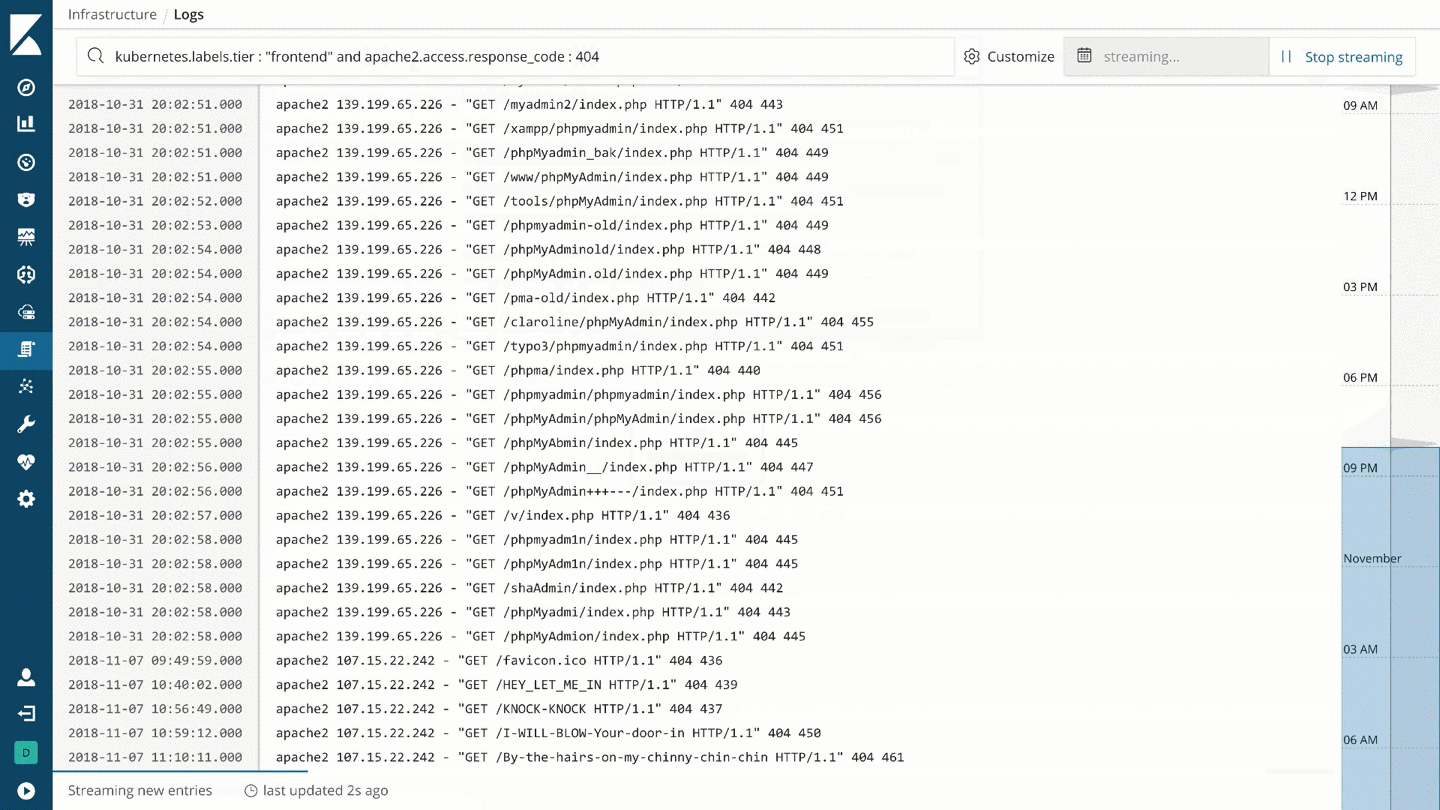
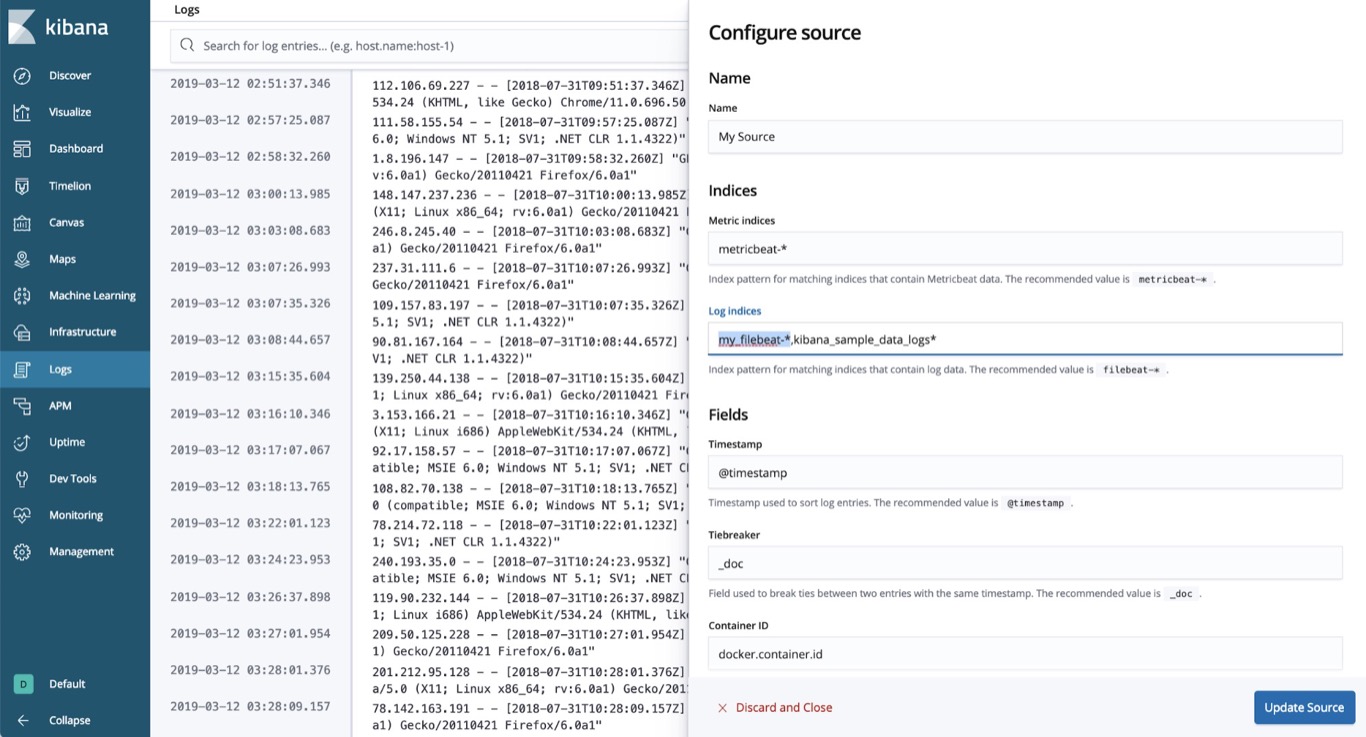
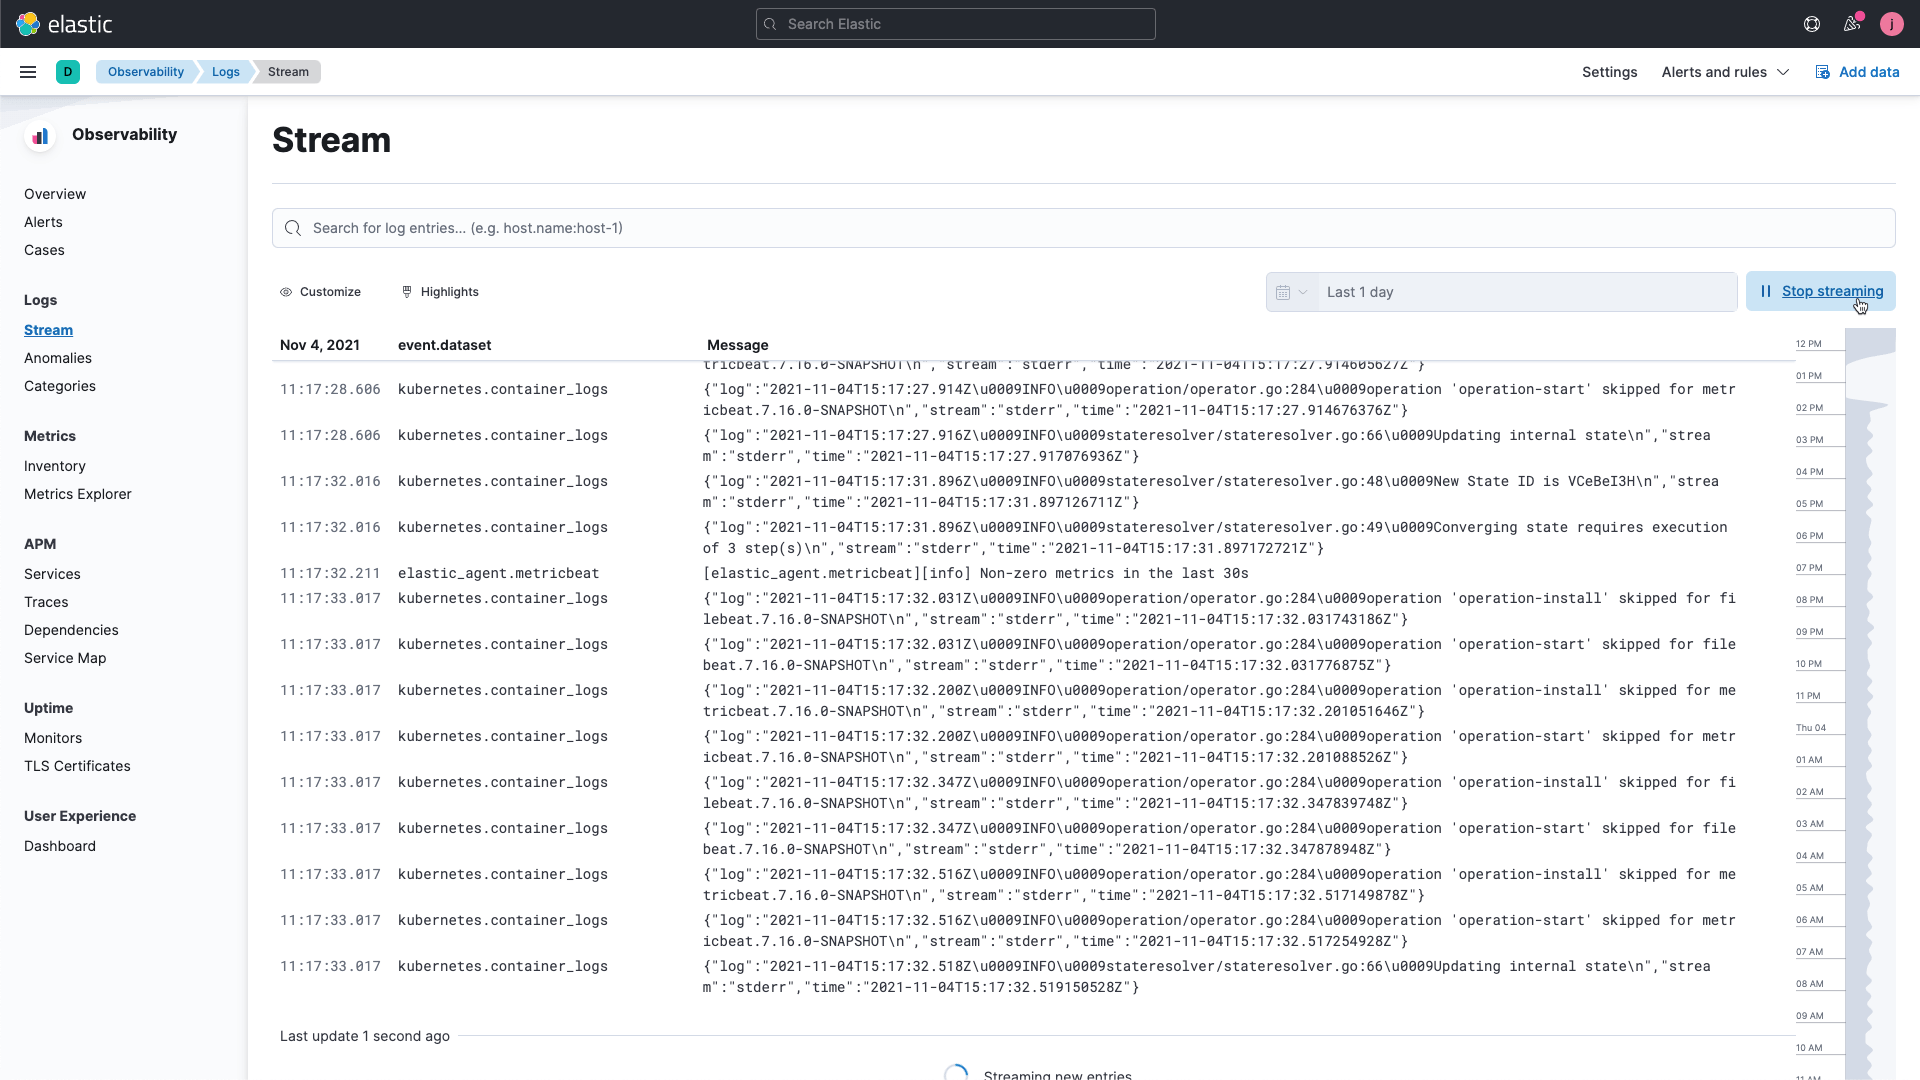
Elastic Logs 7.2.0 adds customizable views and improved Kubernetes ...
Software Log Management: Elastic tra i Visionary di Gartner
Log analytics | Elastic
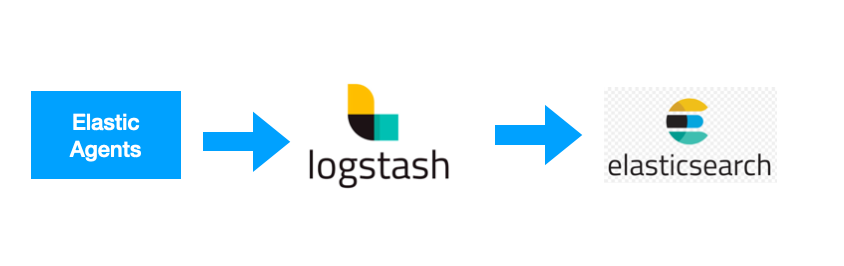
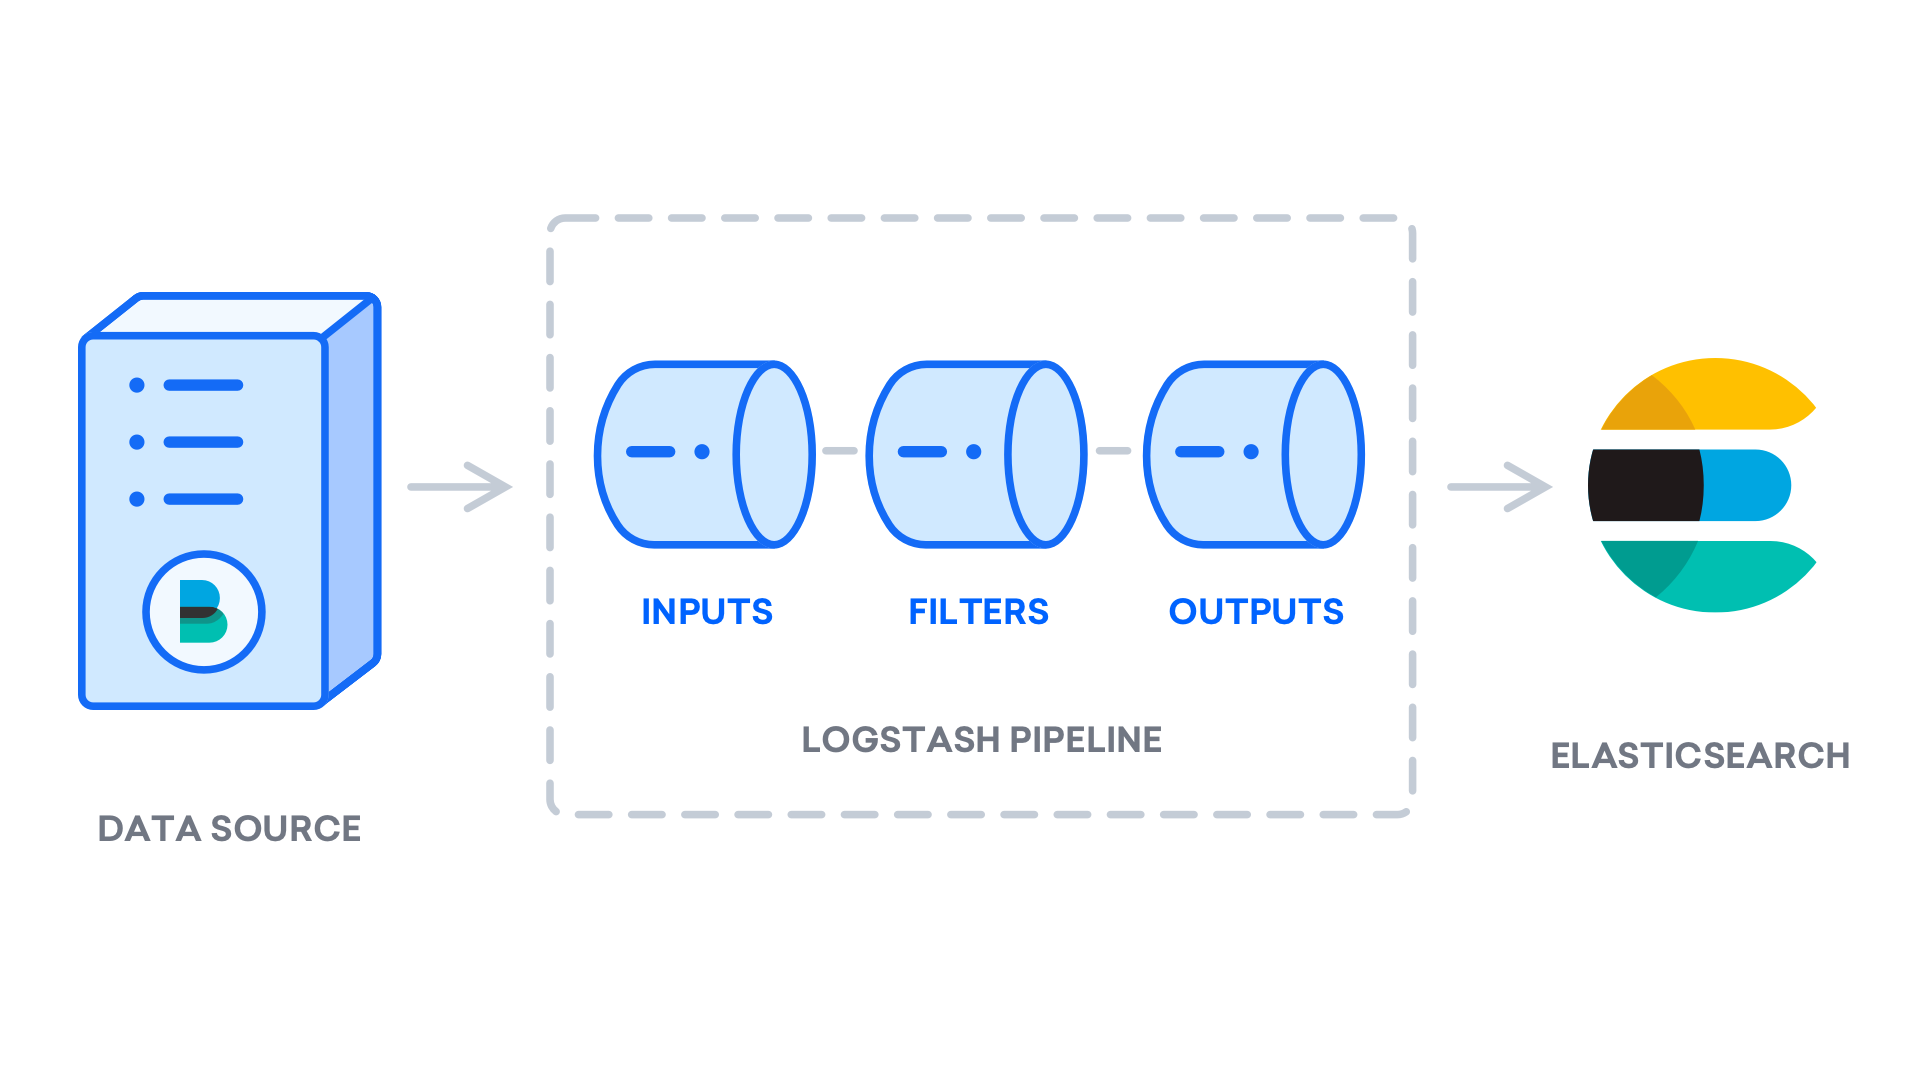
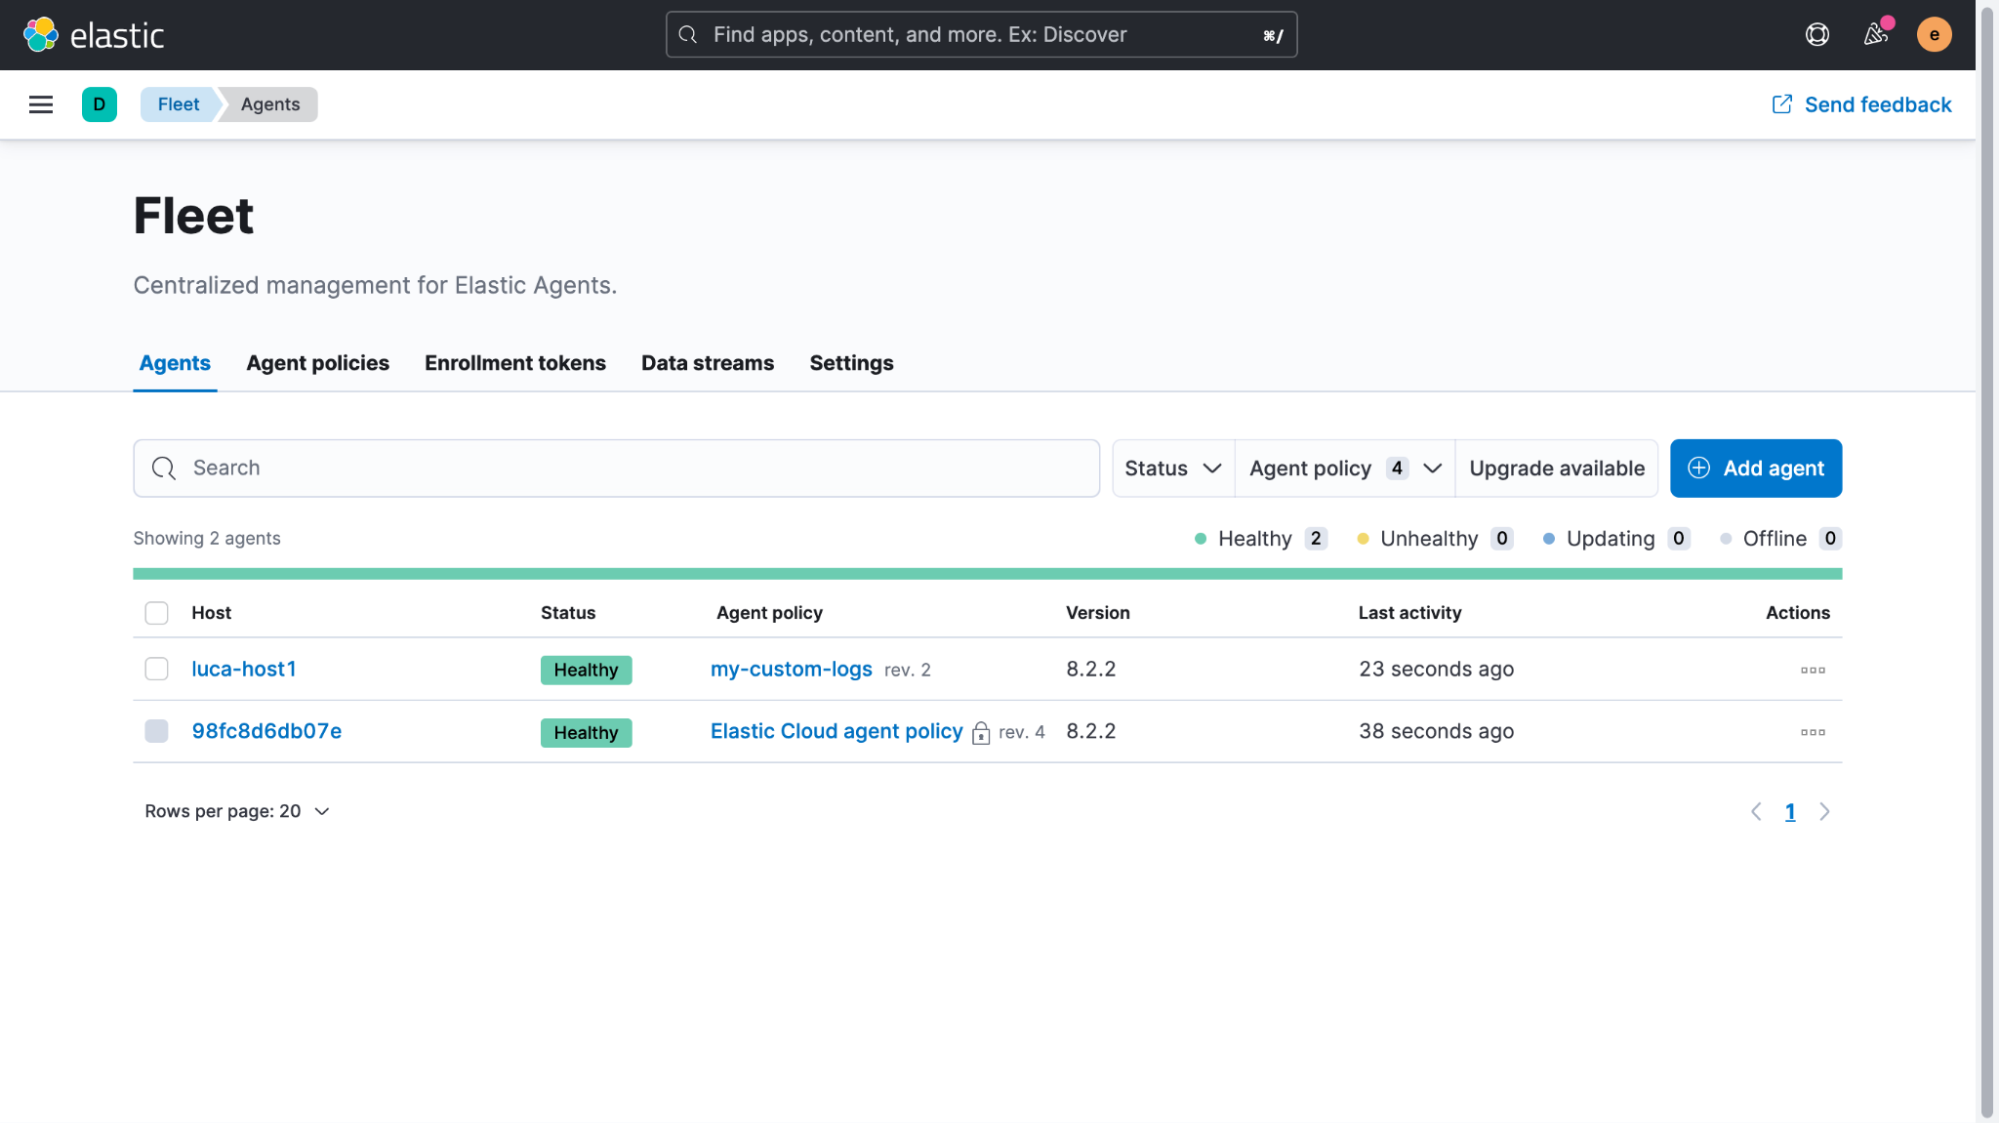
Elastic Agent to Logstash to Elasticsearch: Logstash as a proxy ...
Elastic Agent to Logstash for routing to multiple Elasticsearch ...
Yazılım Çorbası: Elastic Stack - Log Management
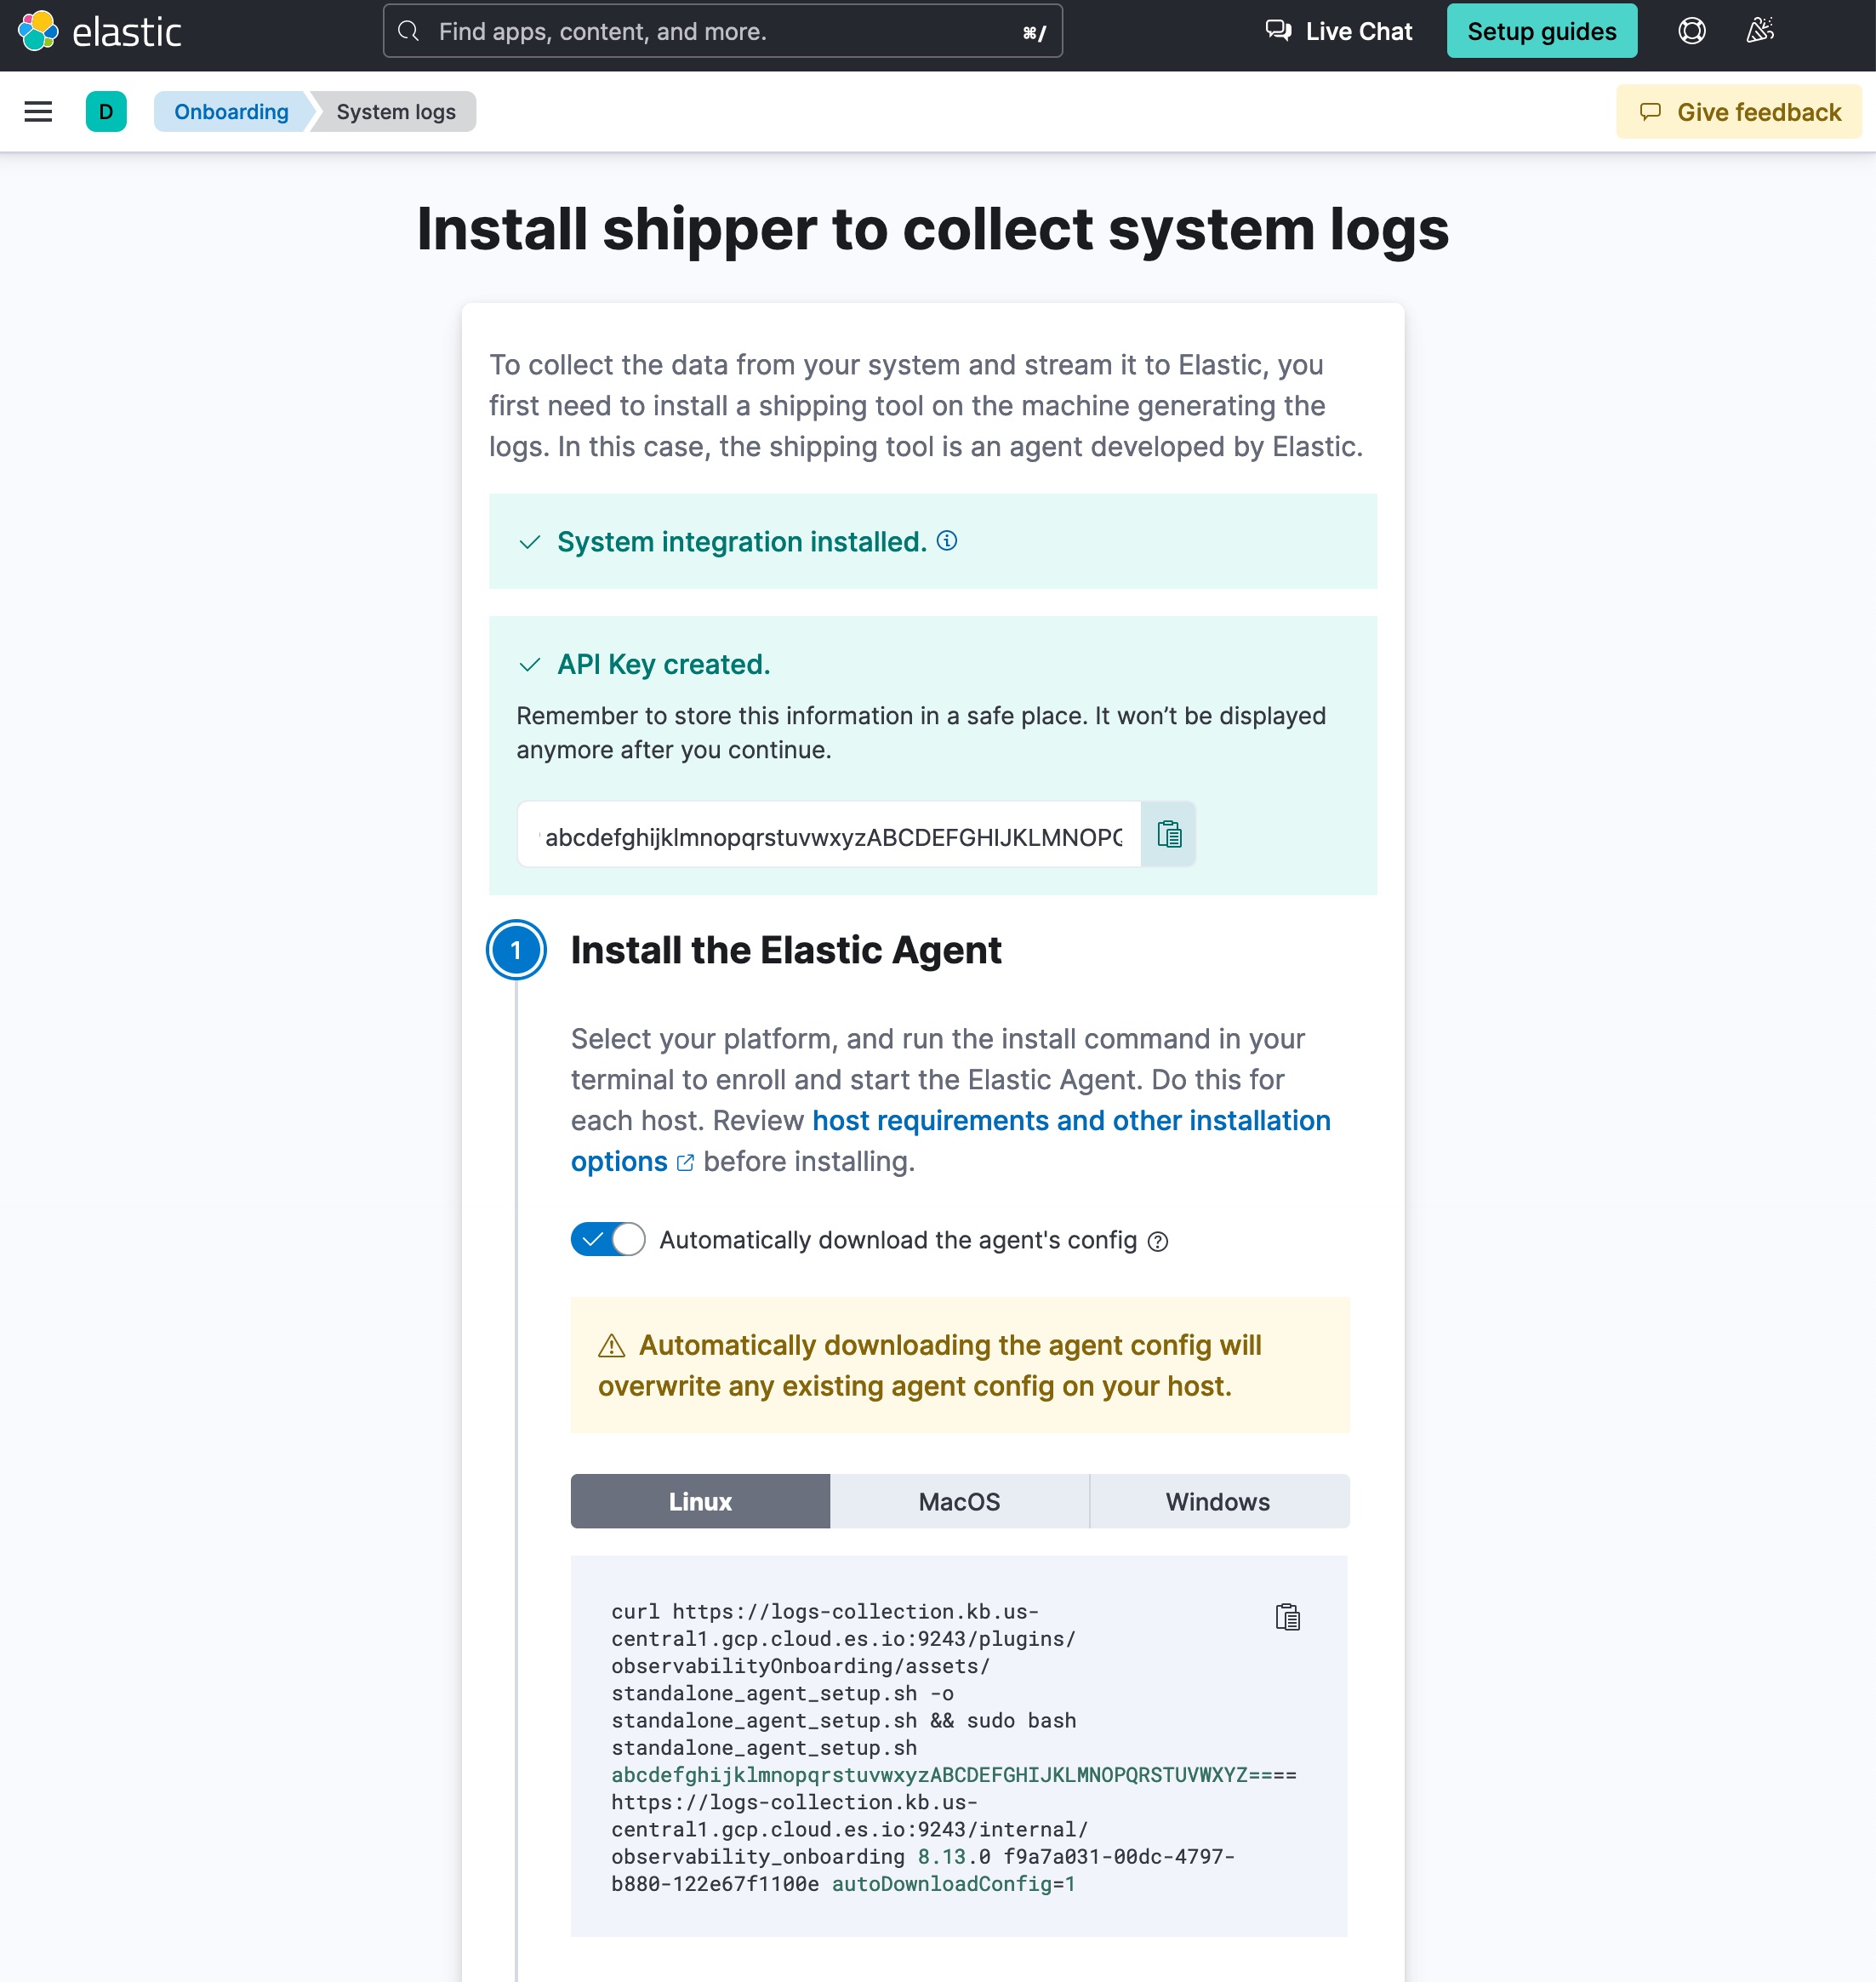
Start your log collection and analysis with Elastic | Elastic
Elastic Log Monitoring Demo: Interactive log management and monitoring ...
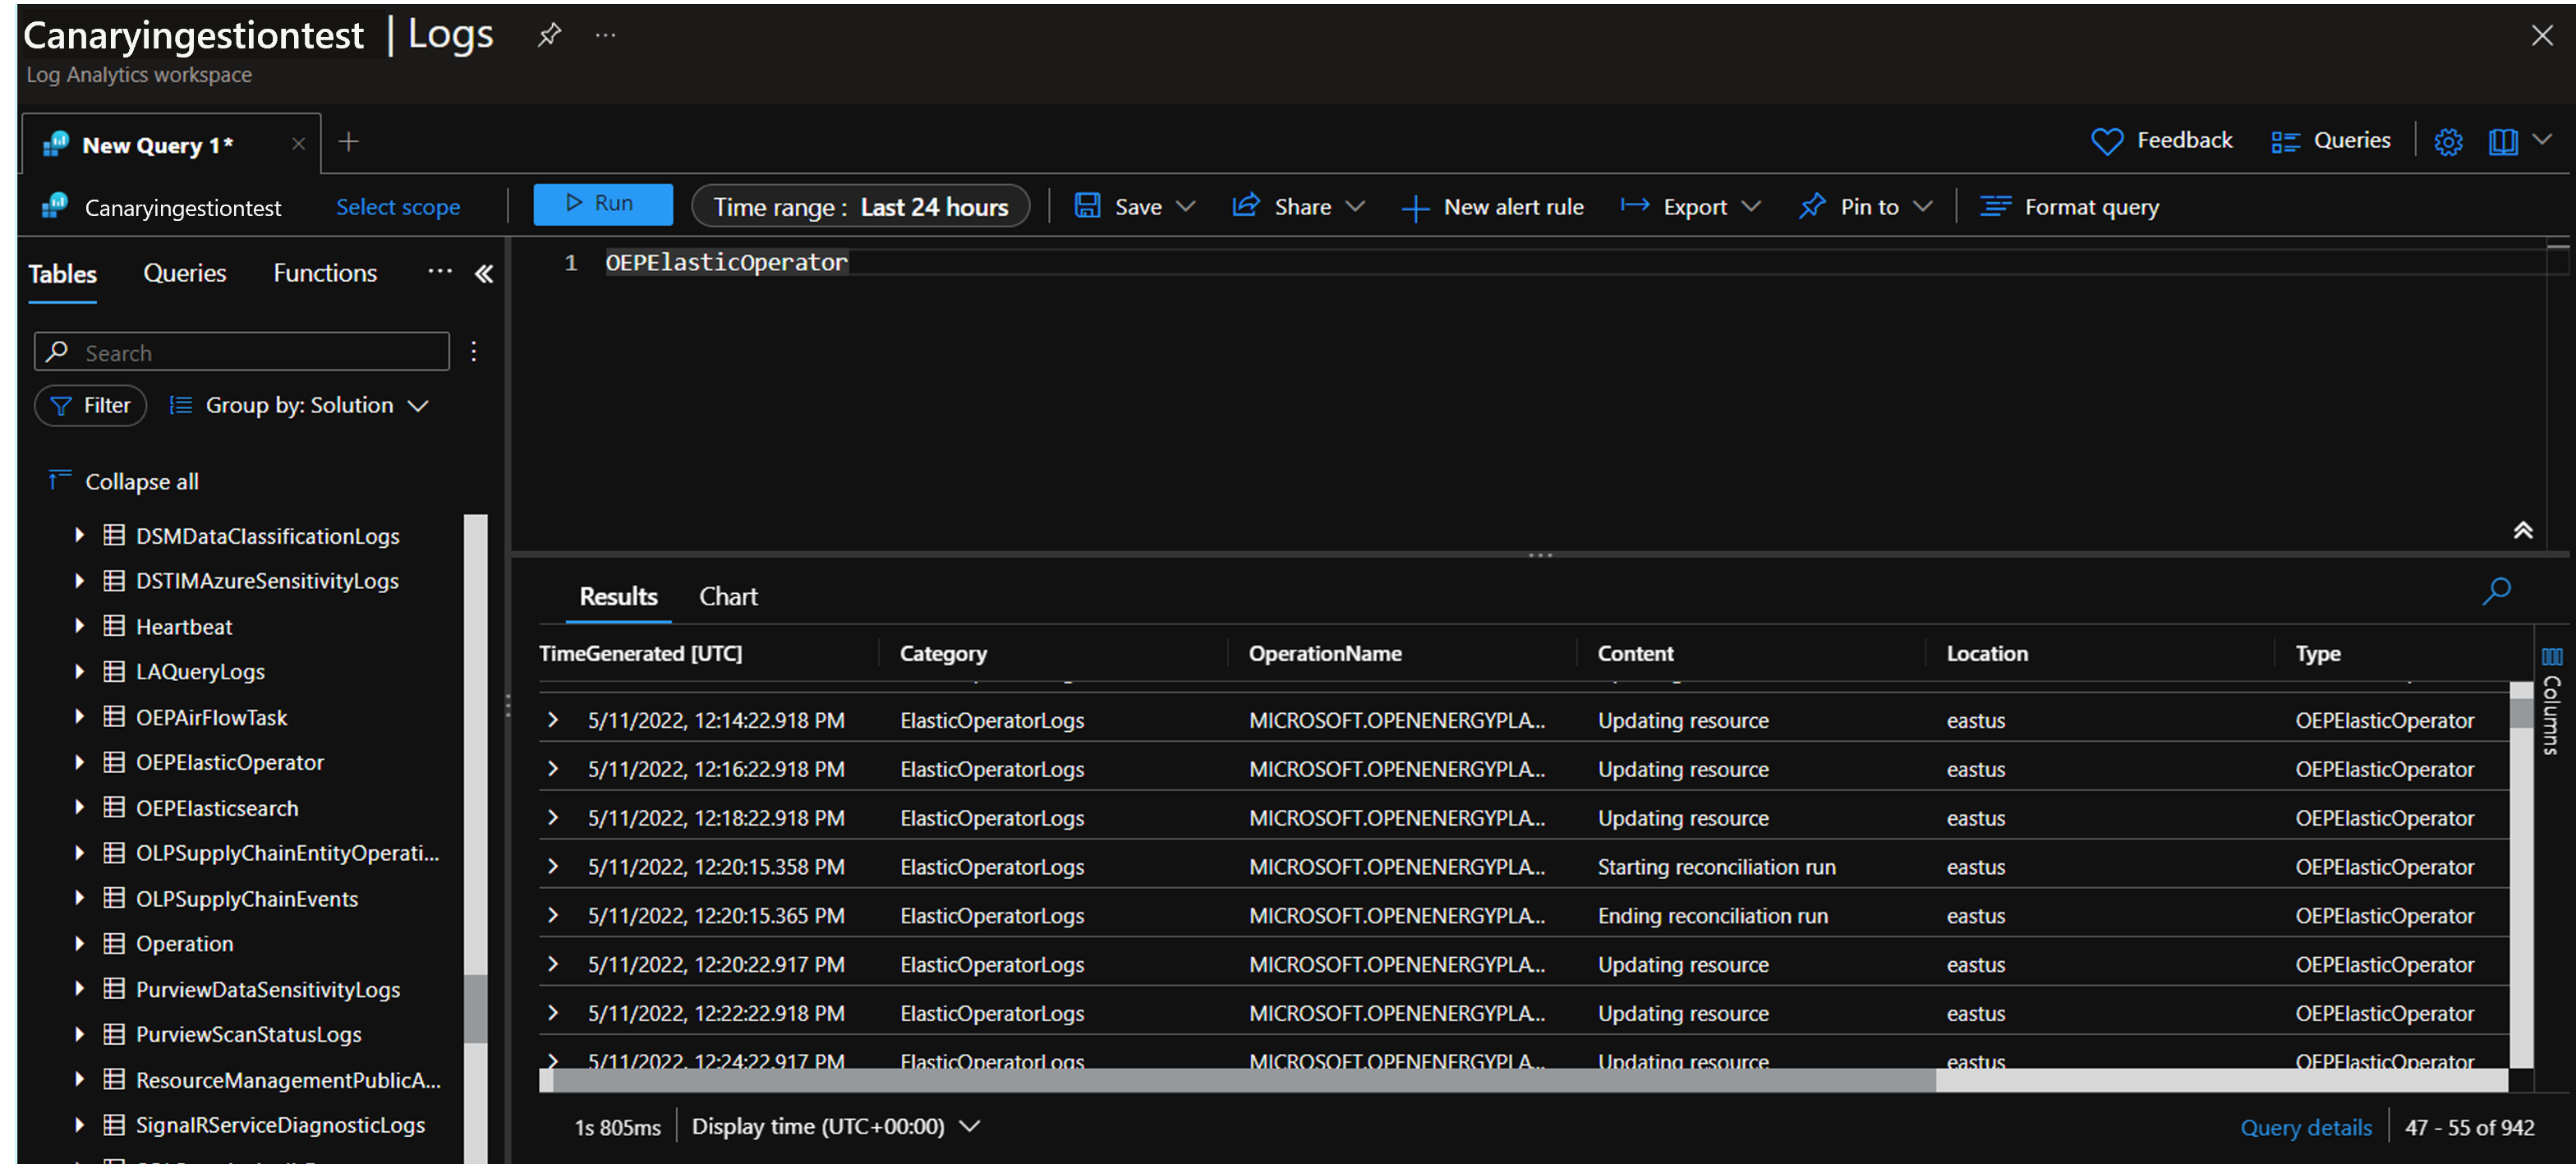
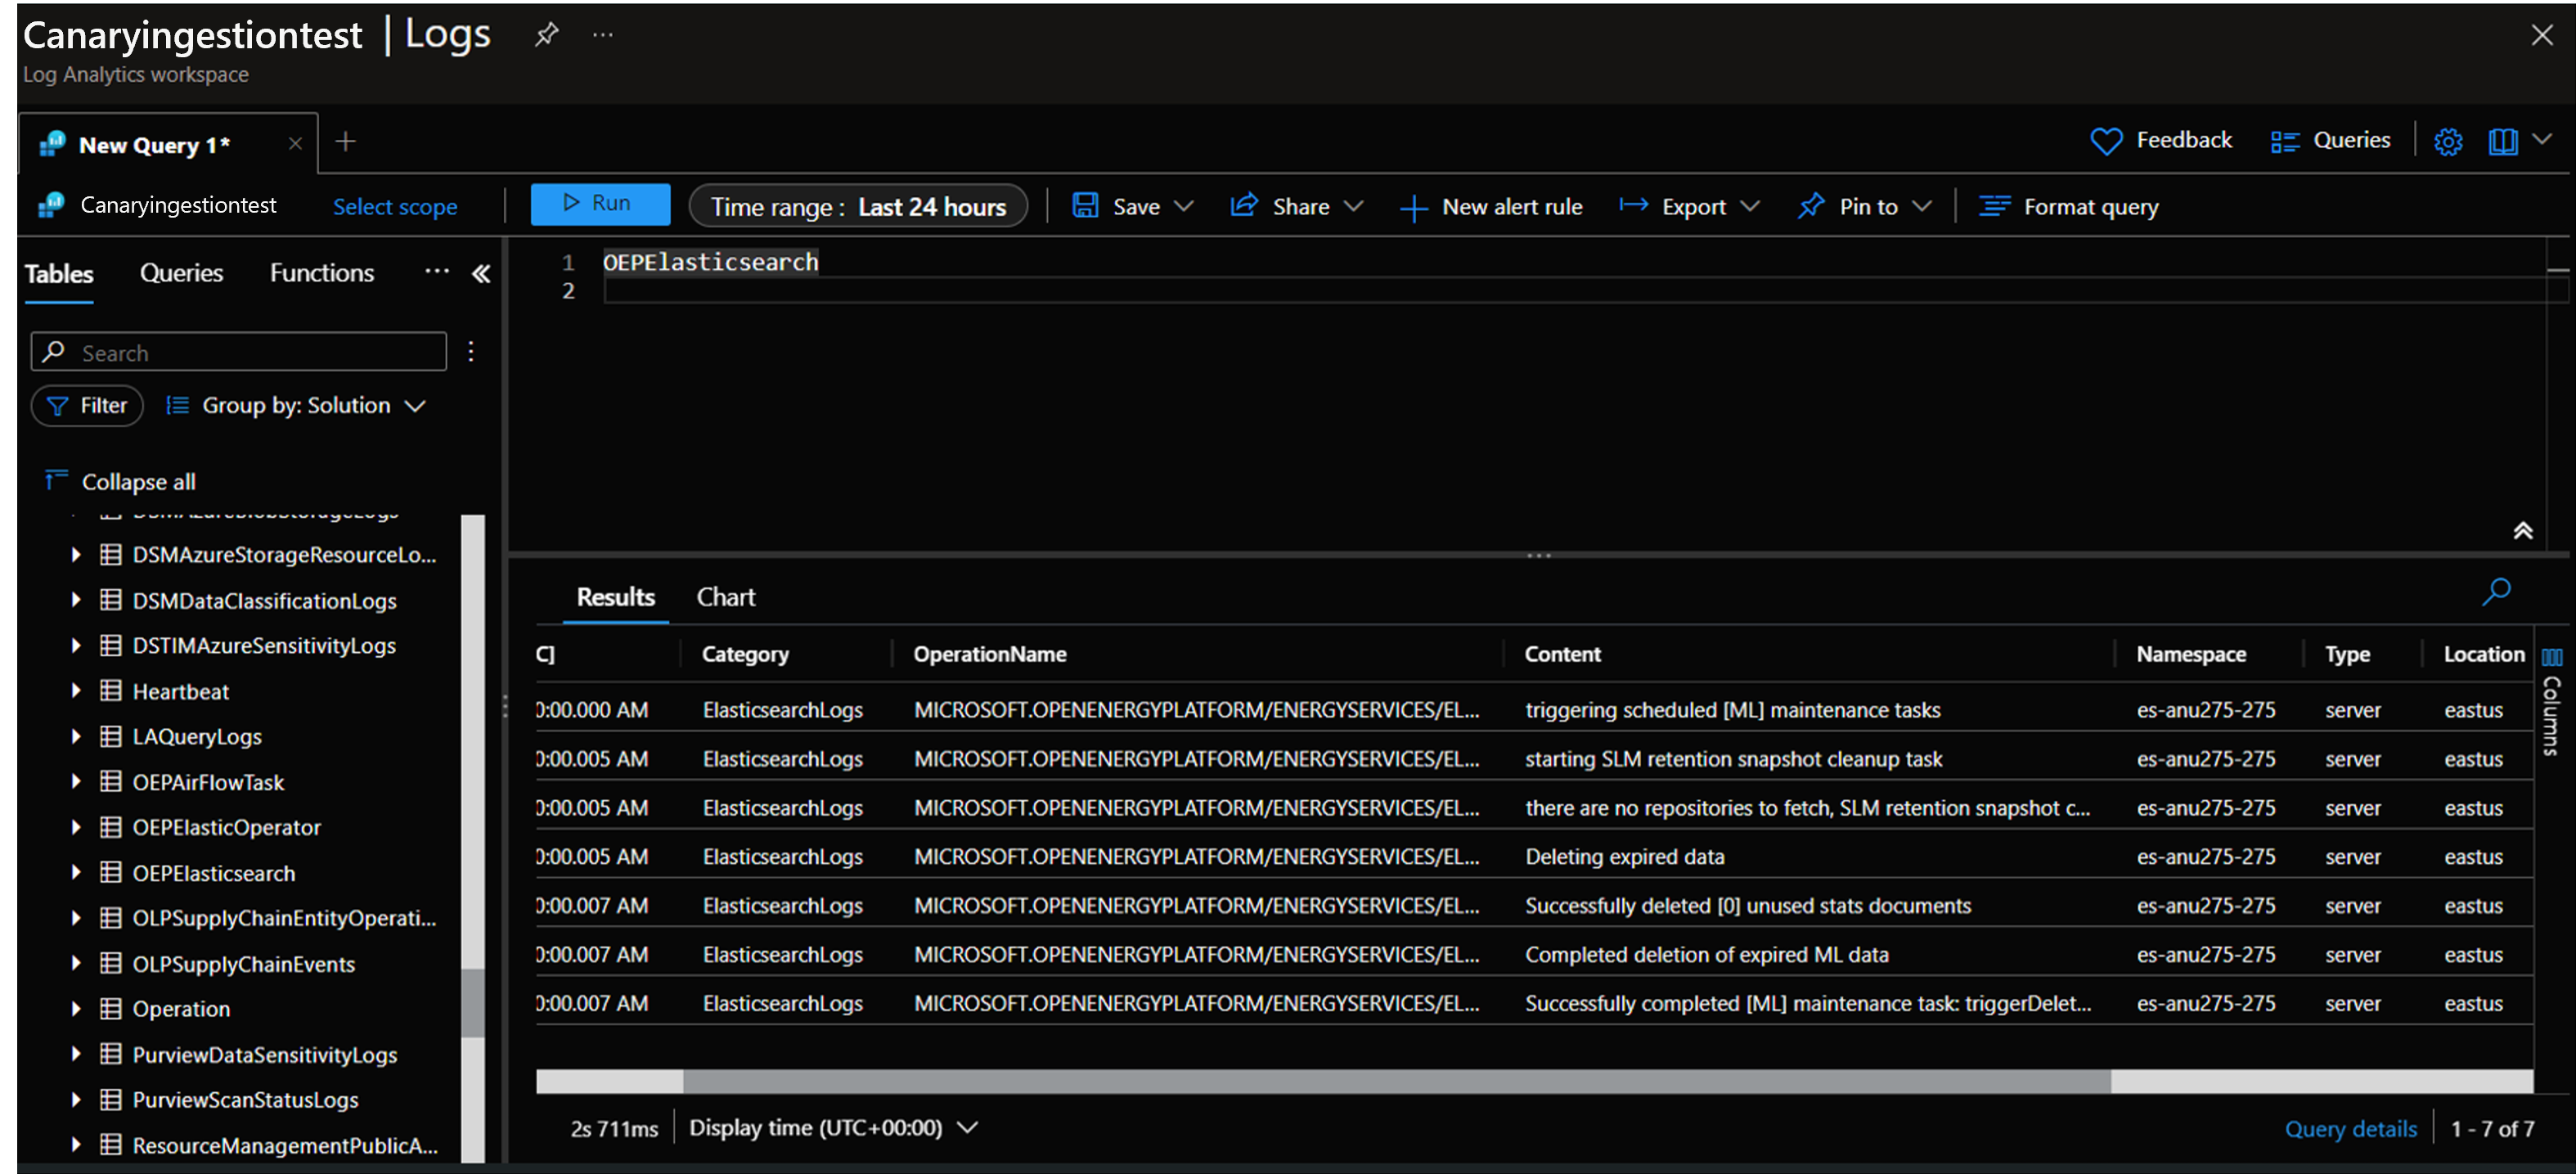
Integrate elastic logs with Azure Monitor - Microsoft Azure Data ...
What is Log Analytics? | Elastic
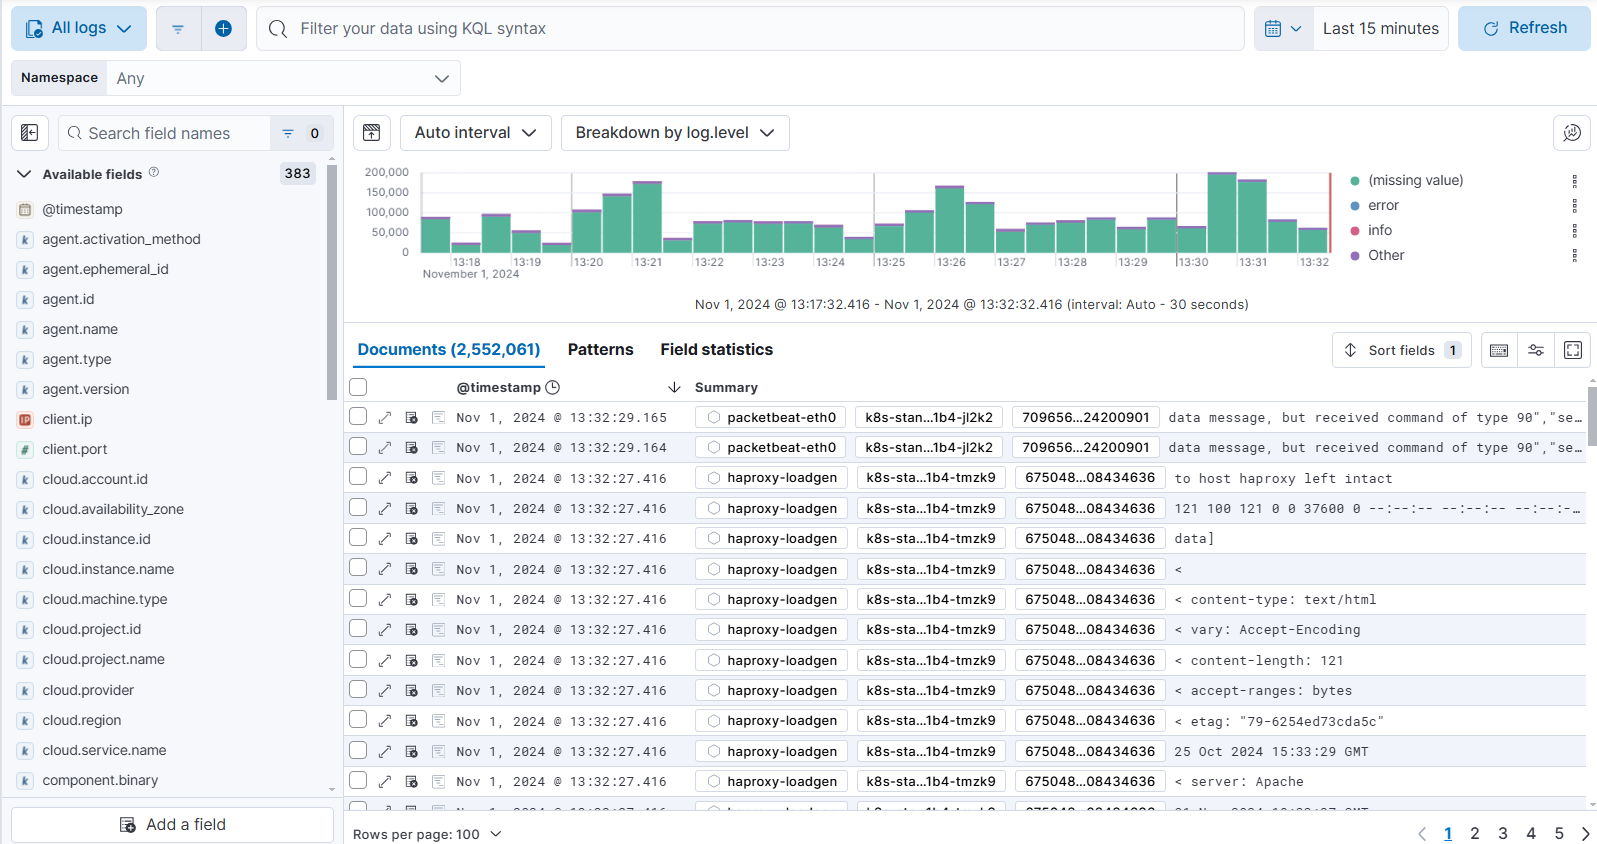
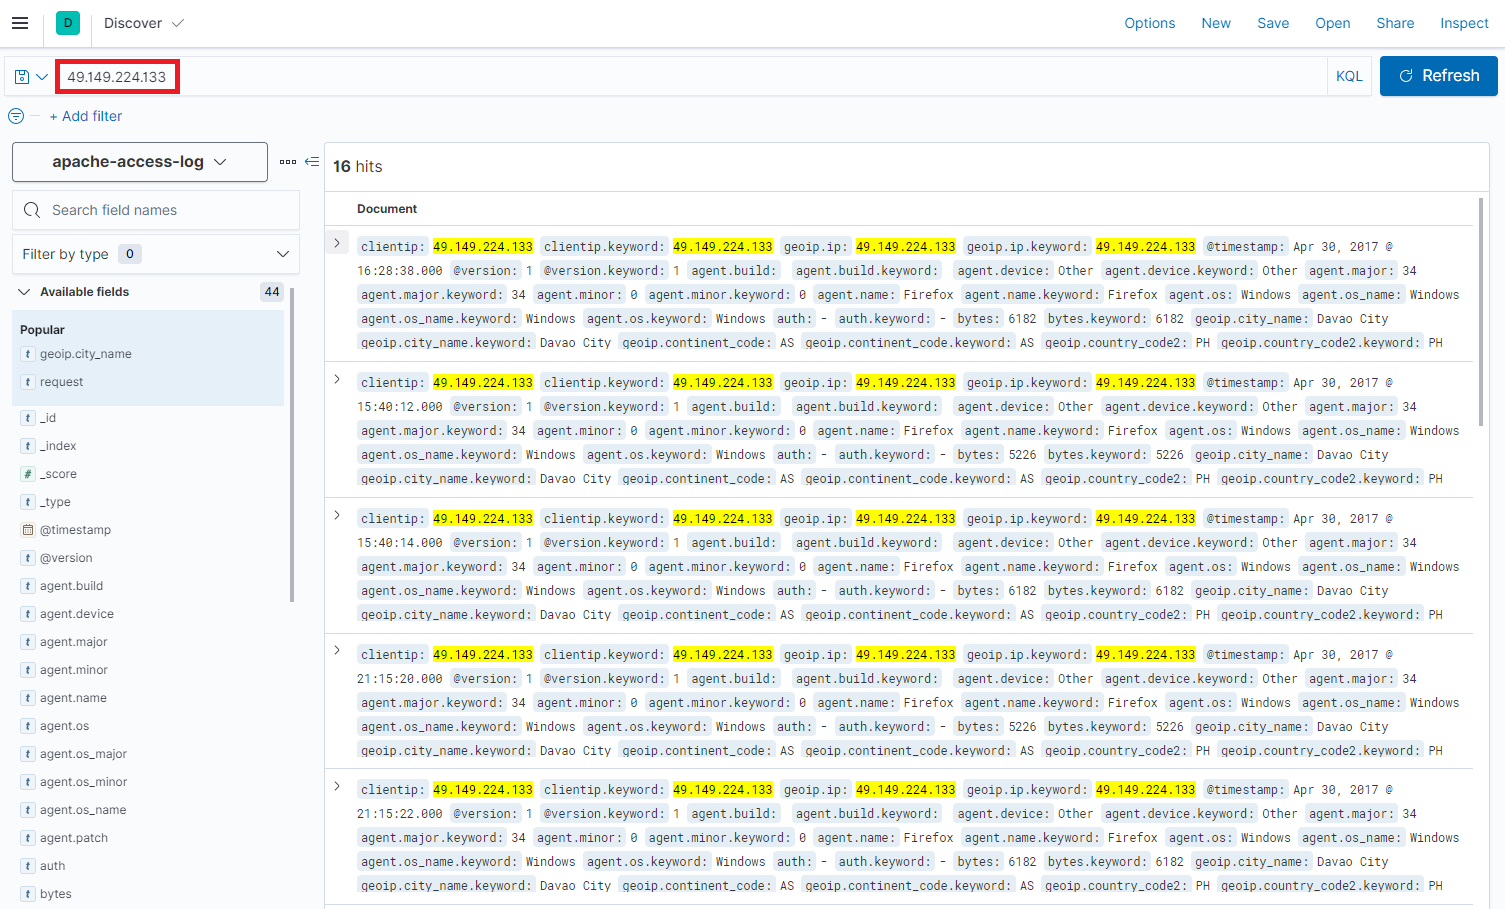
Explore logs in Discover | Elastic Docs
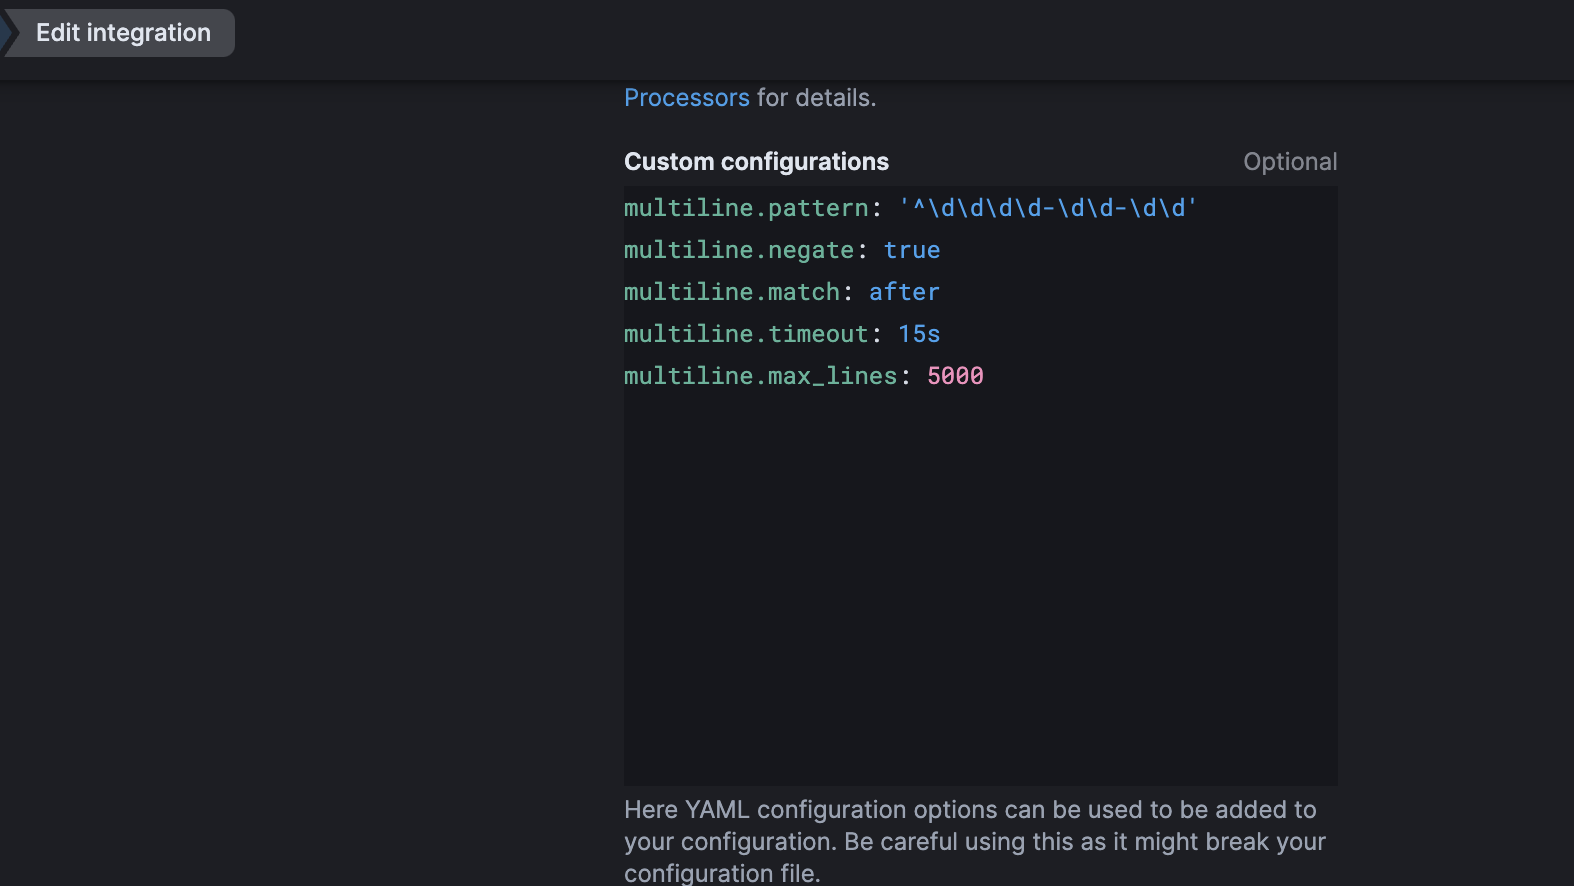
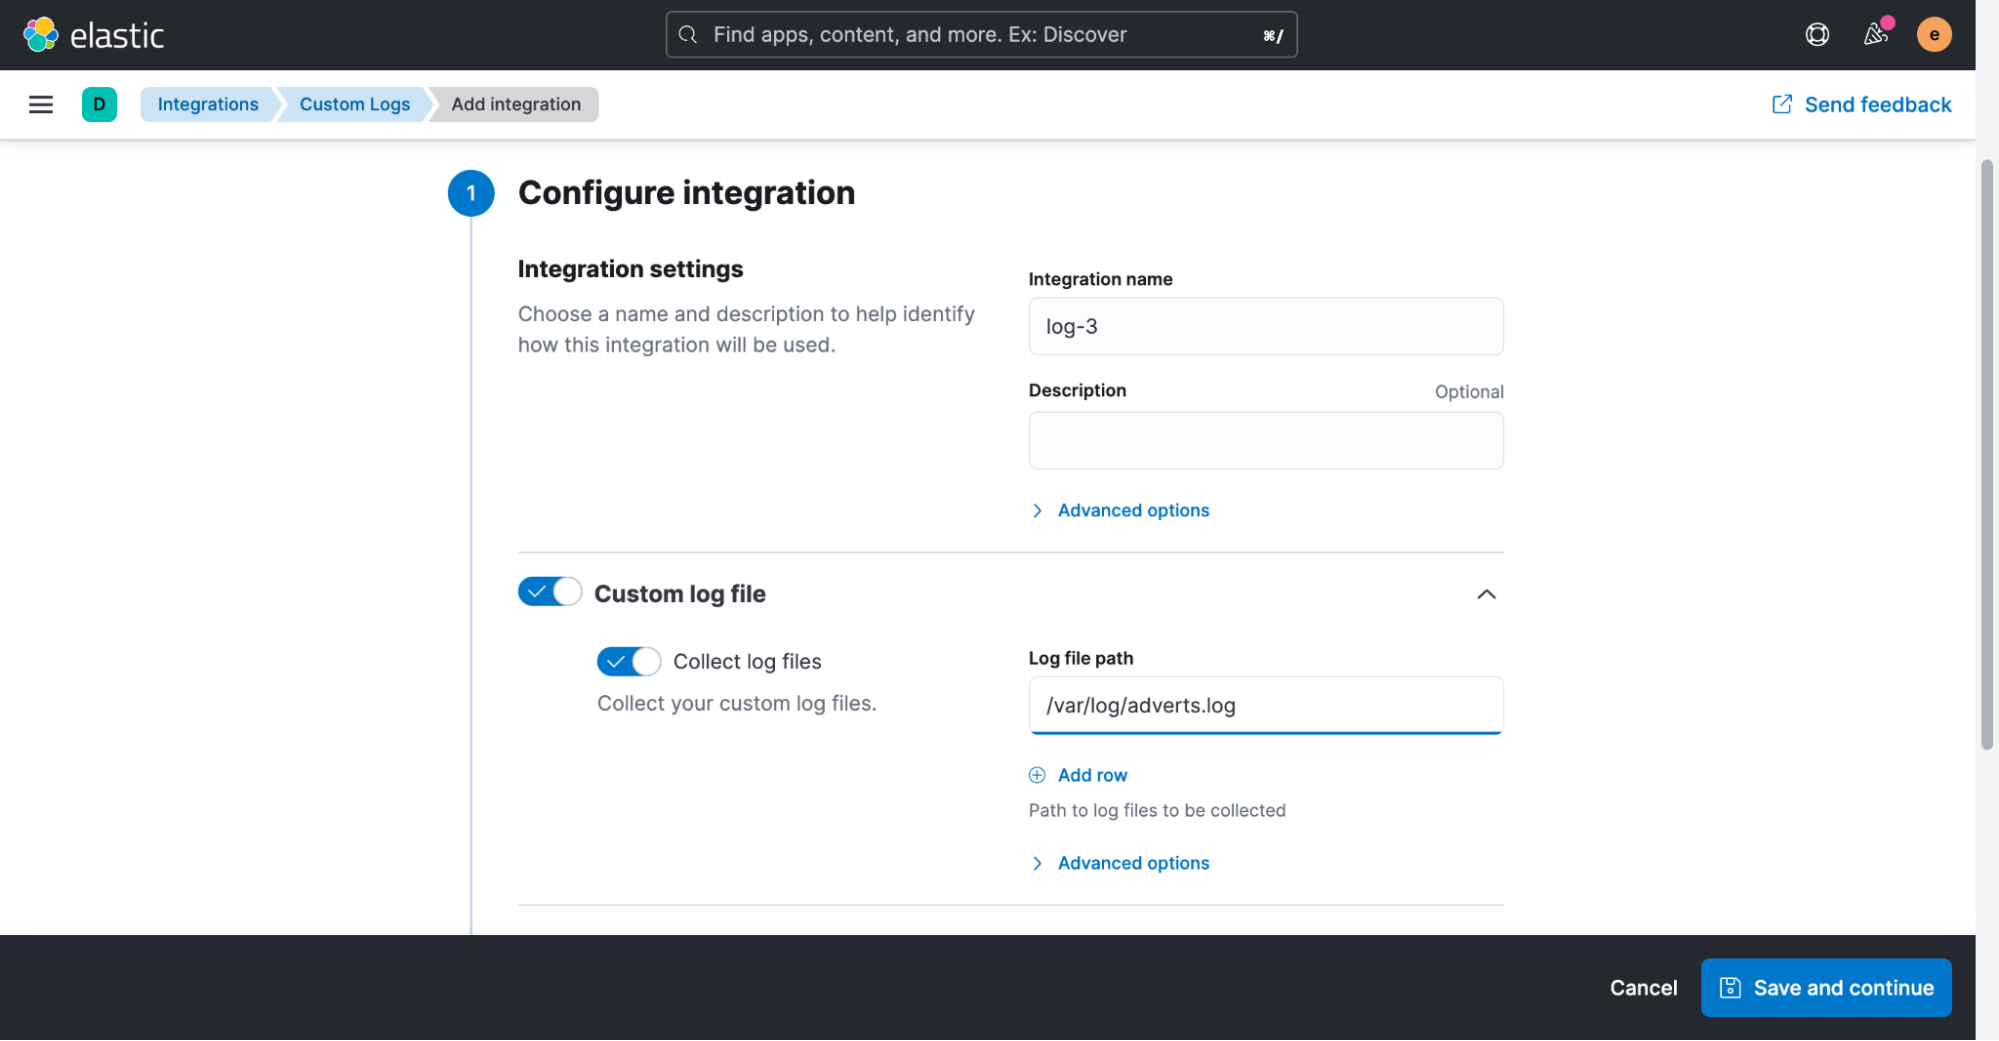
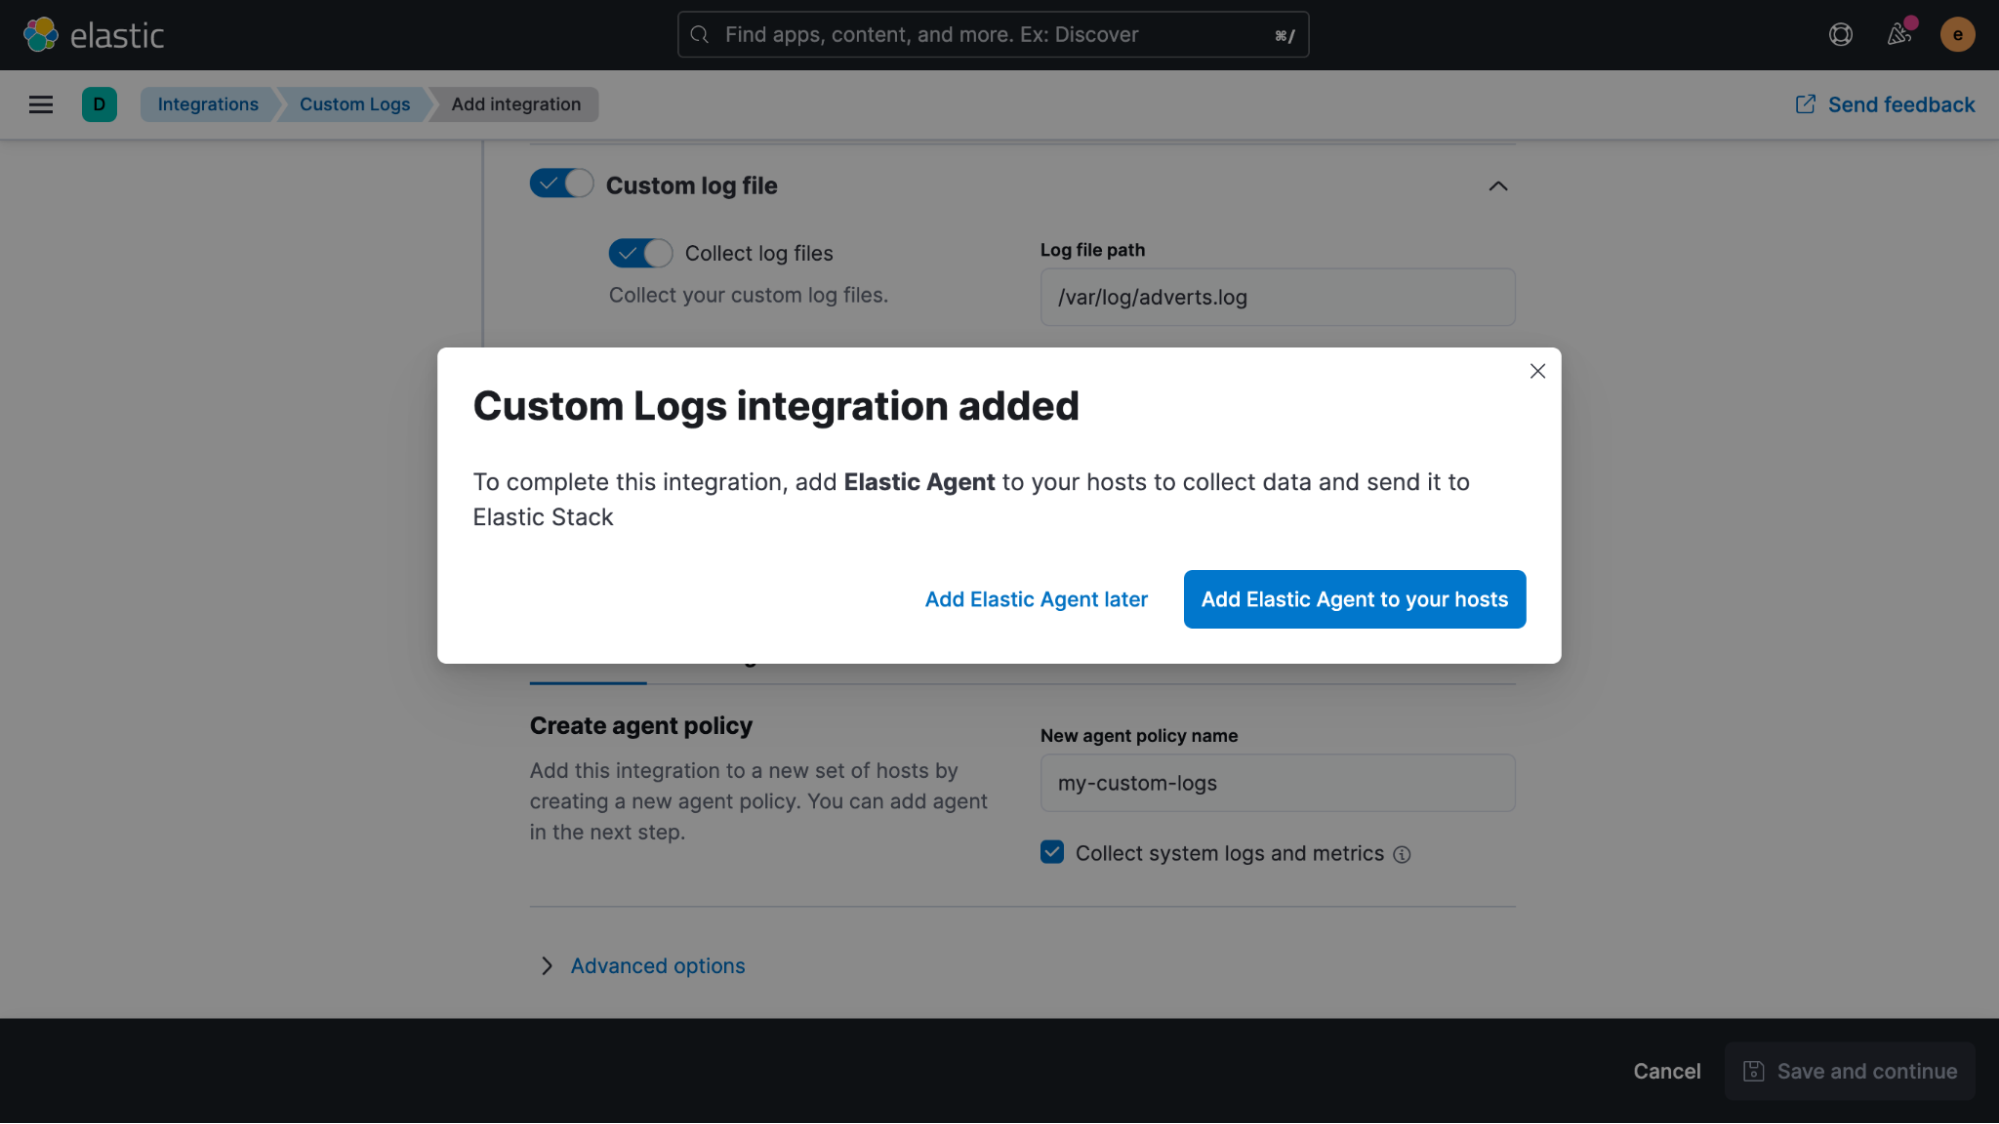
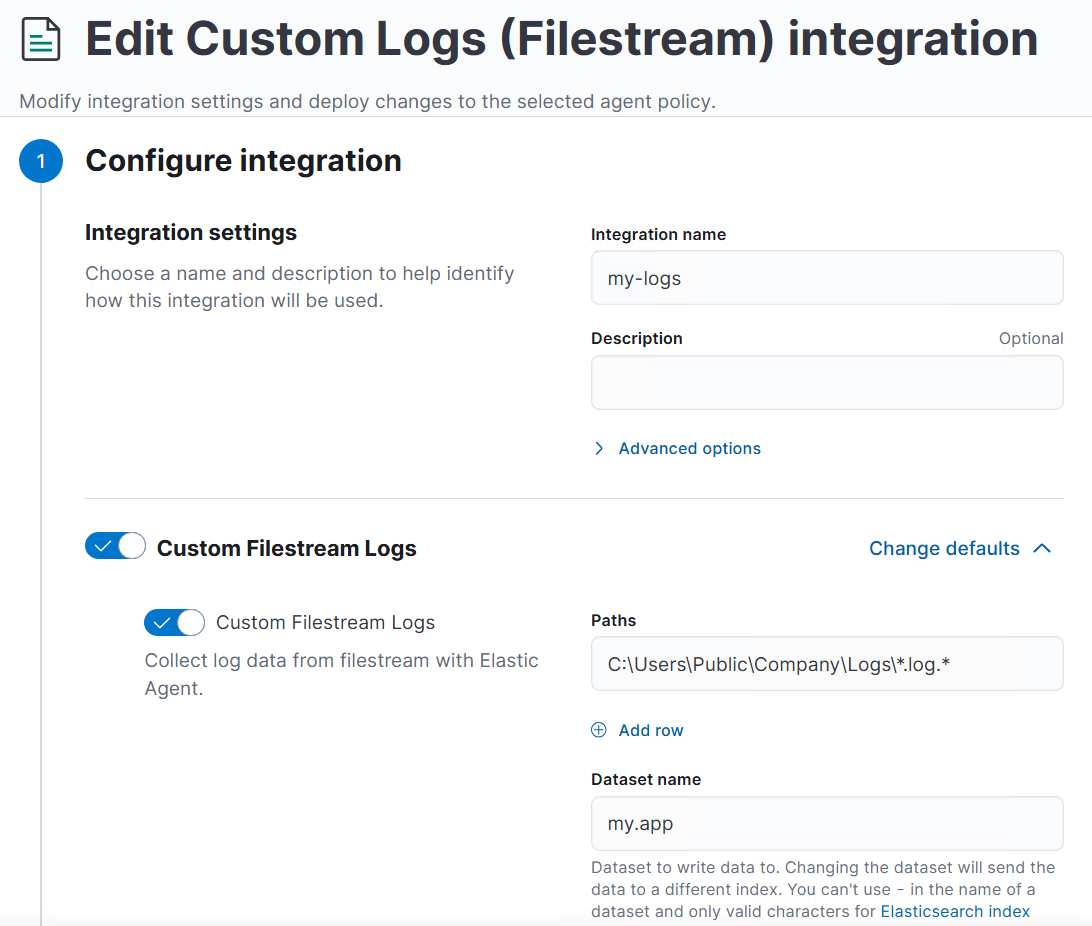
Elastic Agent with custom log integration - Elastic Agent - Discuss the ...
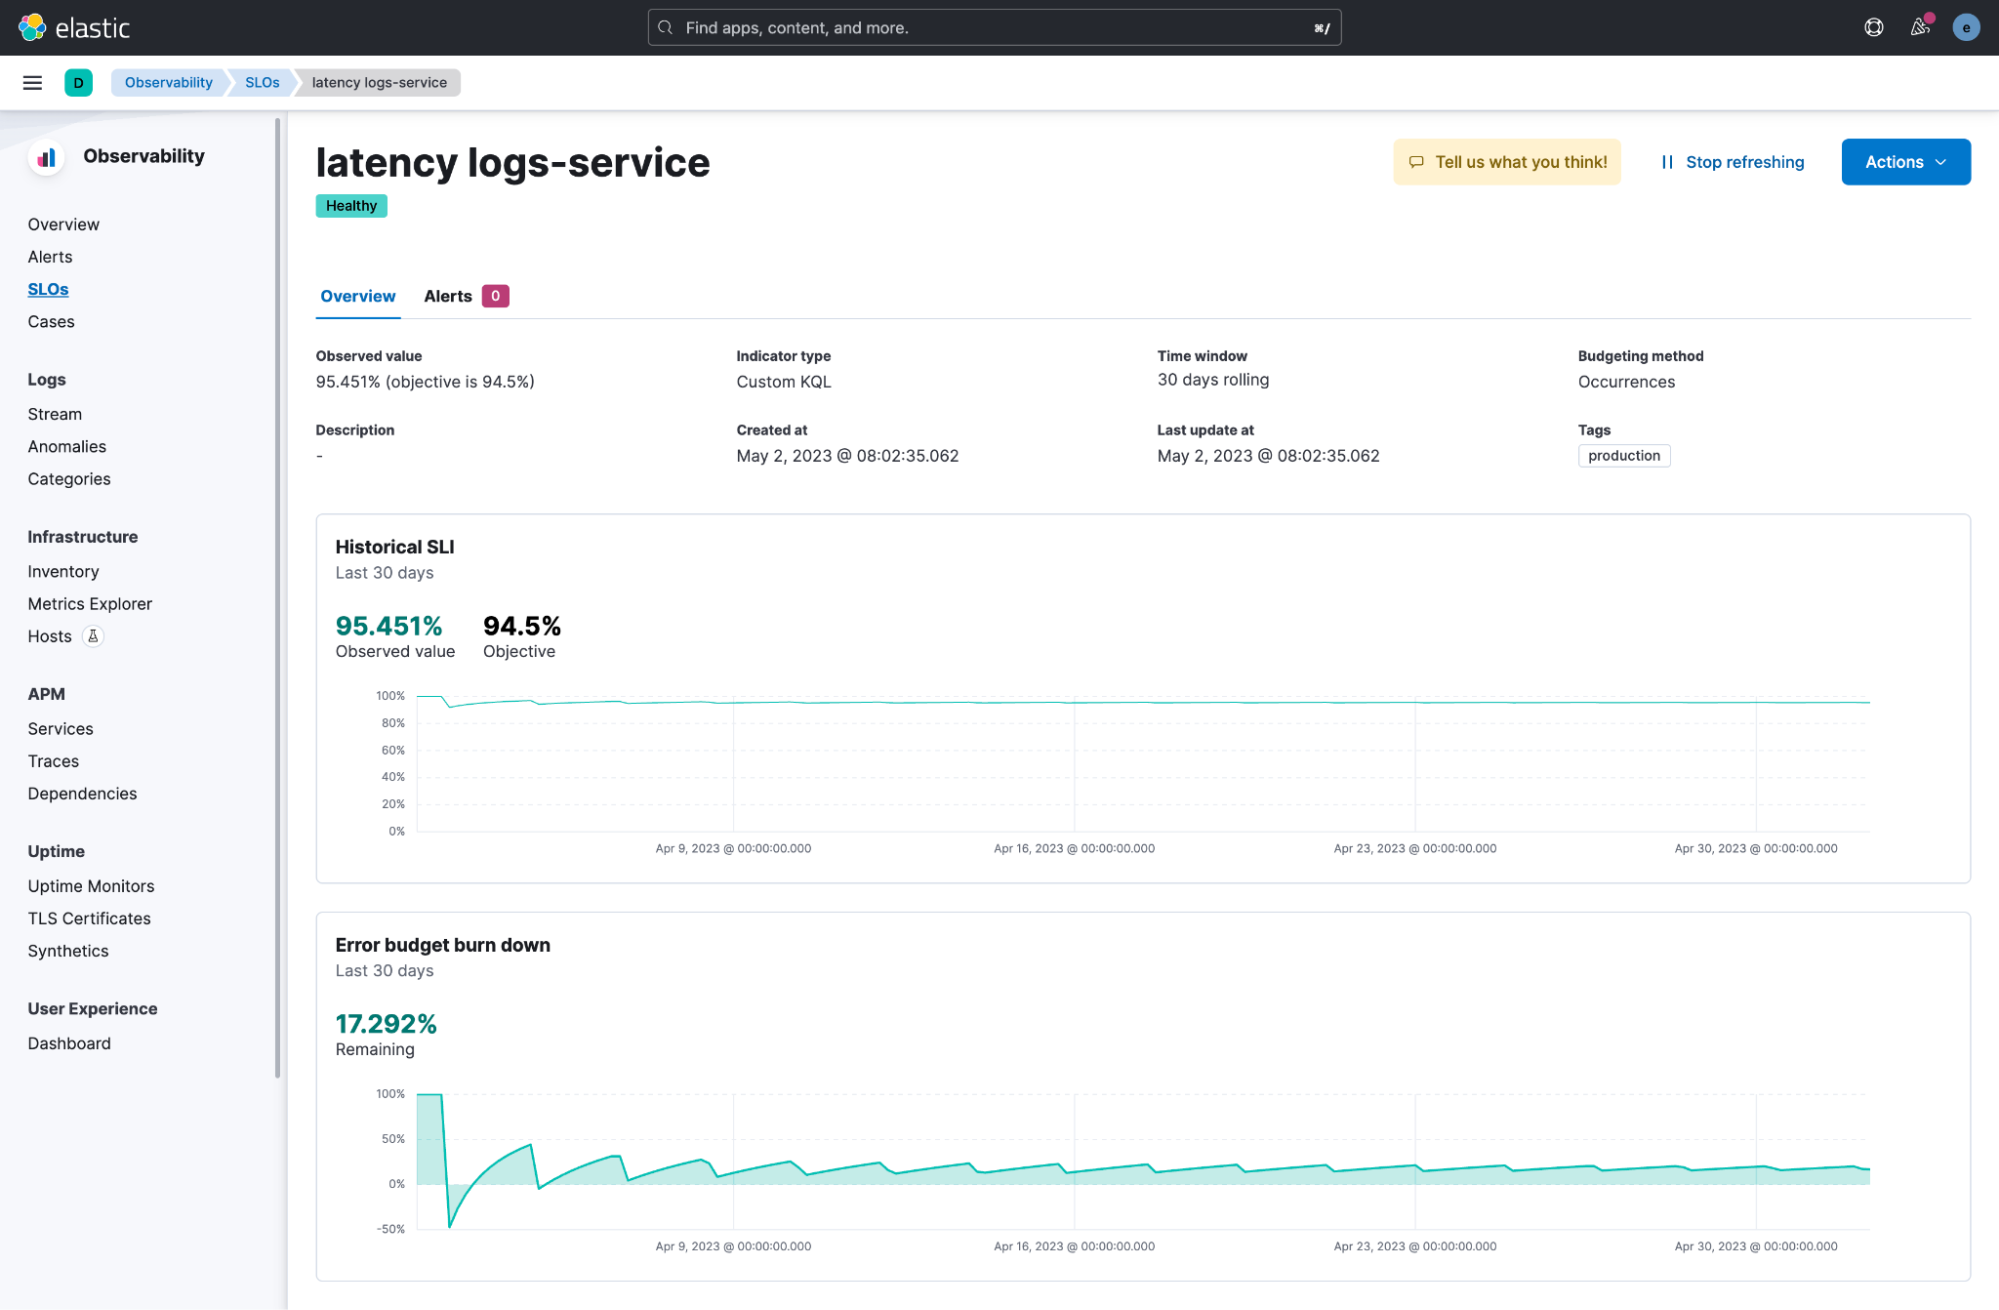
Elastic Observability 8.8: Efficient operations with GitOps-based ...
Elastic 5分钟教程:使用Logs应用搜索你的日志-腾讯云开发者社区-腾讯云
Log Forwarding Capabilities - Logstash - Discuss the Elastic Stack
Elastic 101 log enrichment | PPTX
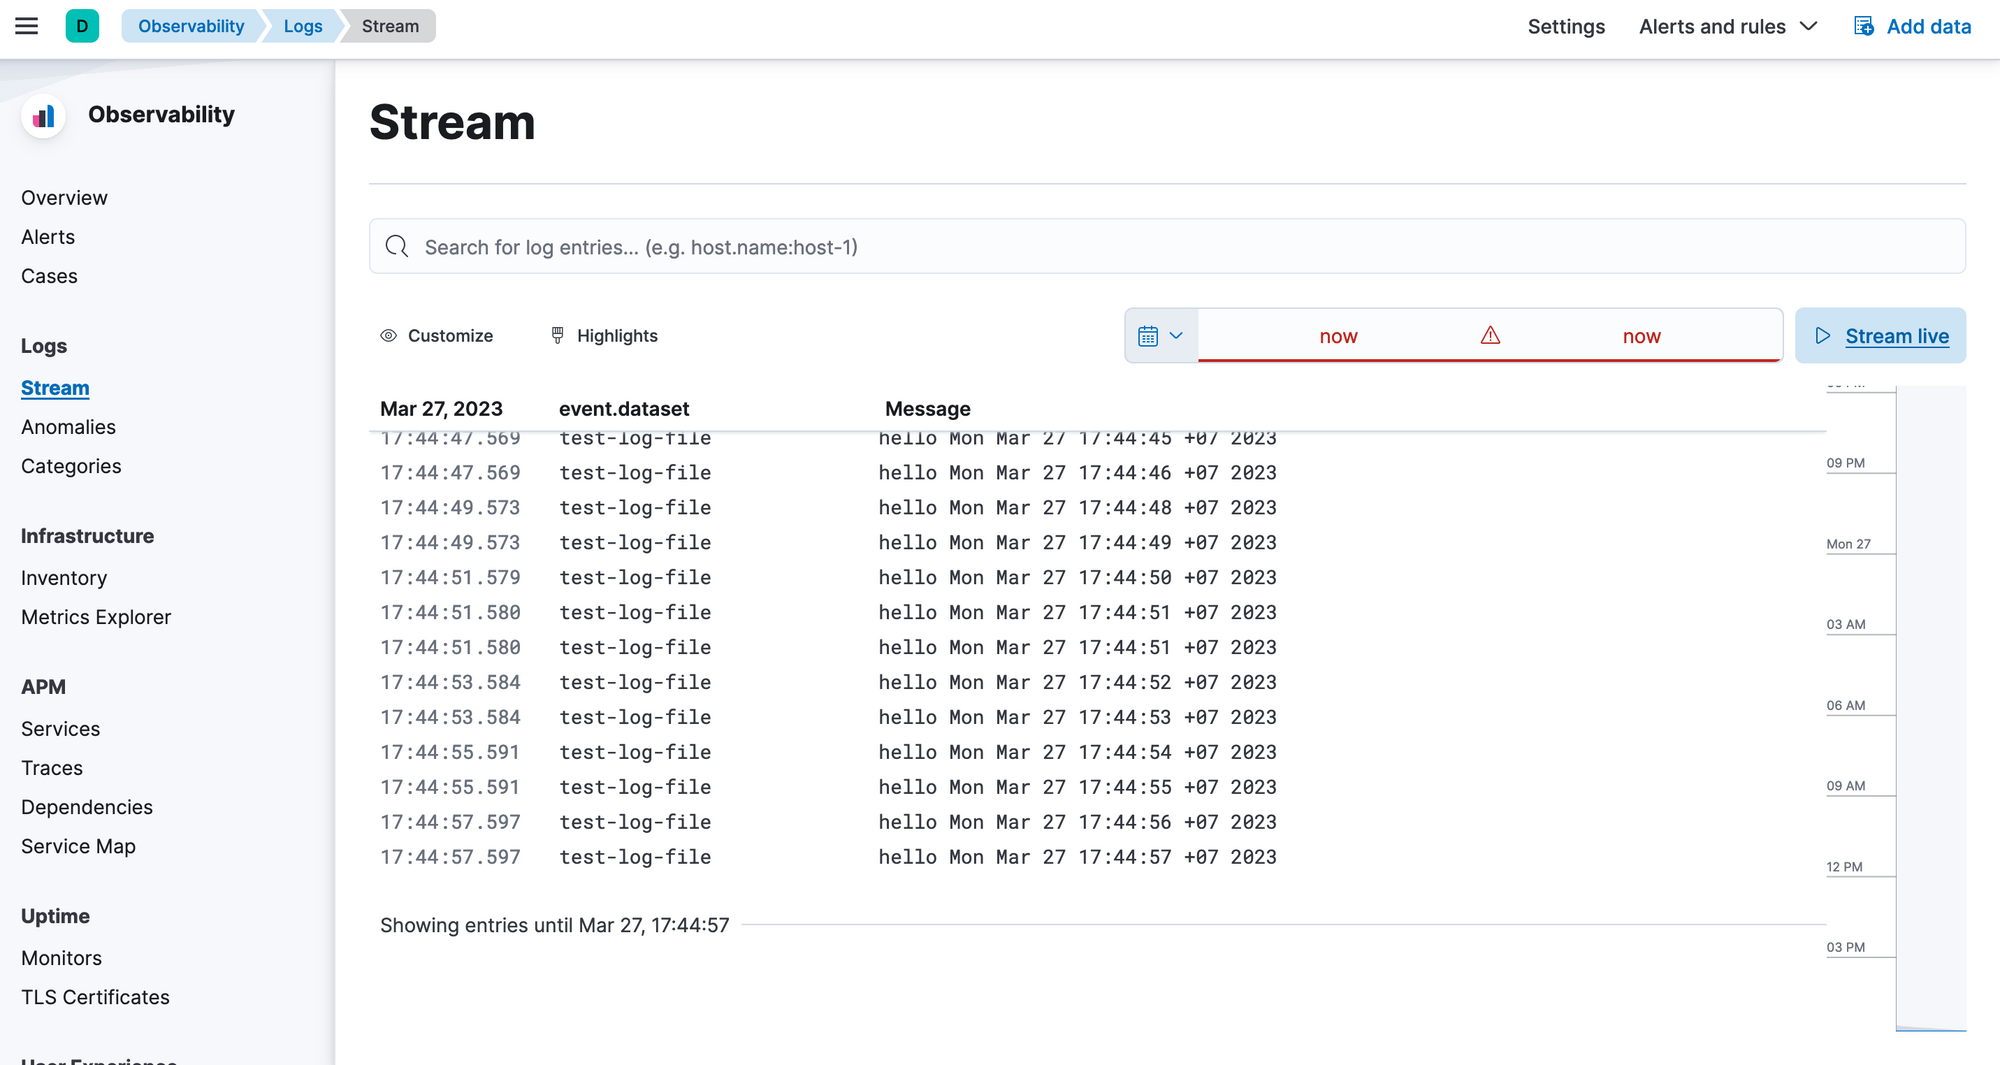
Stream log from file to Elastic Search
(Color online) (a) Log range-square corrected elastic returns, (b ...
Elastic Endpoint Integration - Large amount of Log data ingested ...
Unleash the full power of your log data | Elastic Videos
Visualizing Apache Logs With Elastic Stack on Debian 10 | Linode Docs
Session 1: Logging Into Elastic & Managing Agents and Policies Walk Through
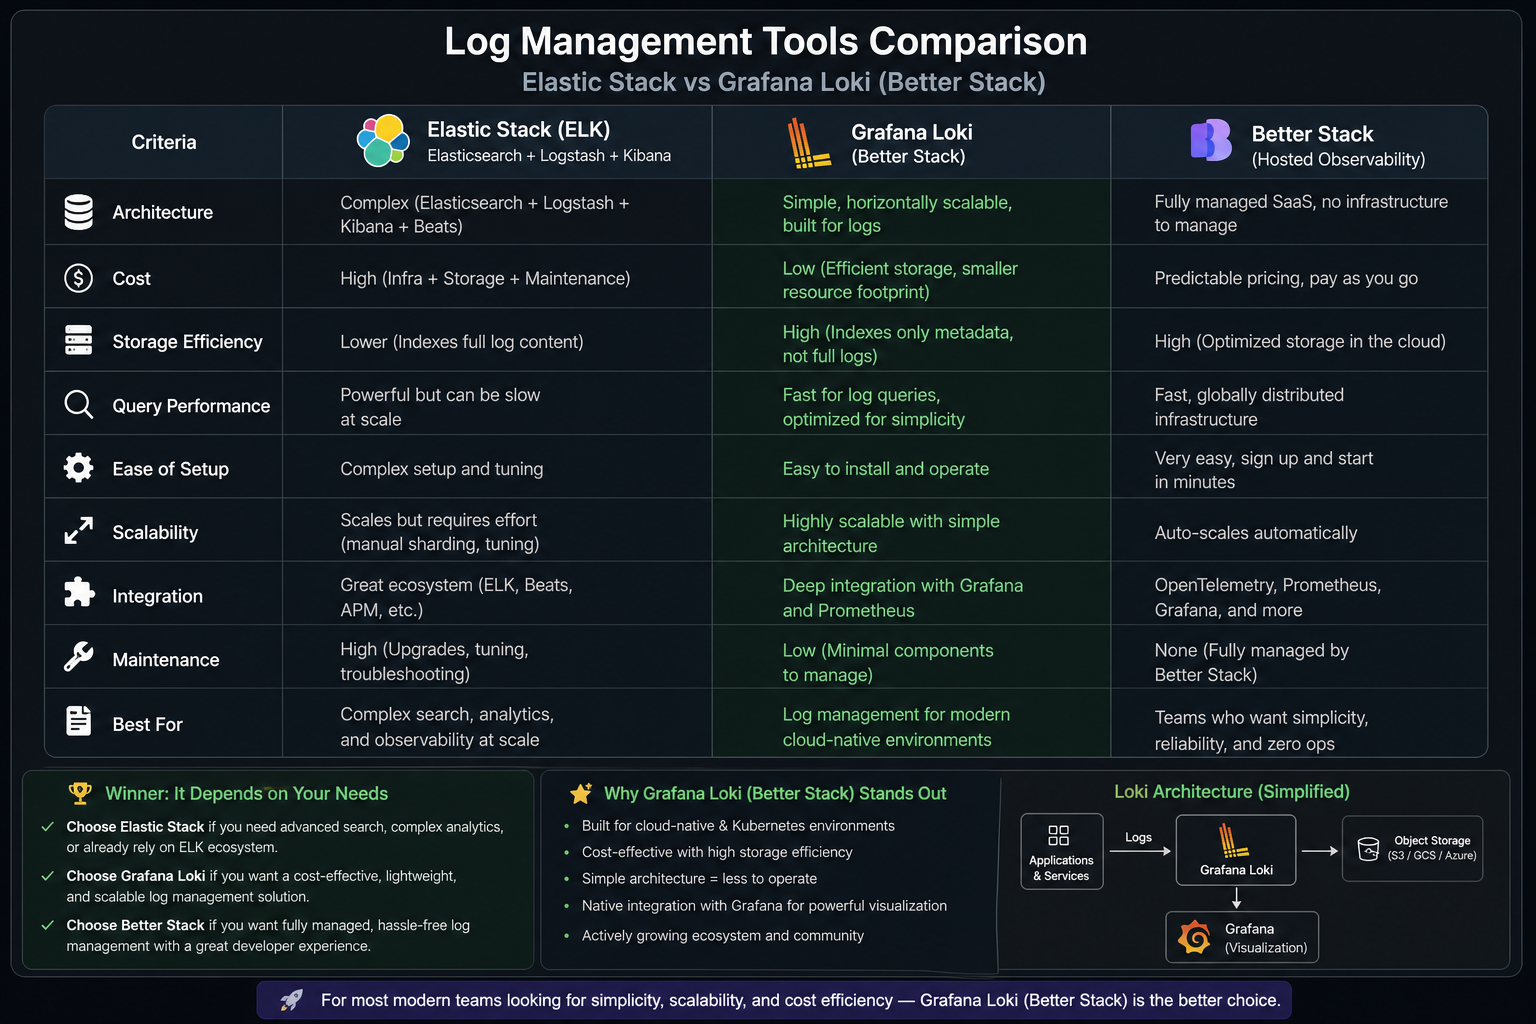
Splunk Alternatives for Log Management: Elastic vs Better Stack vs ...
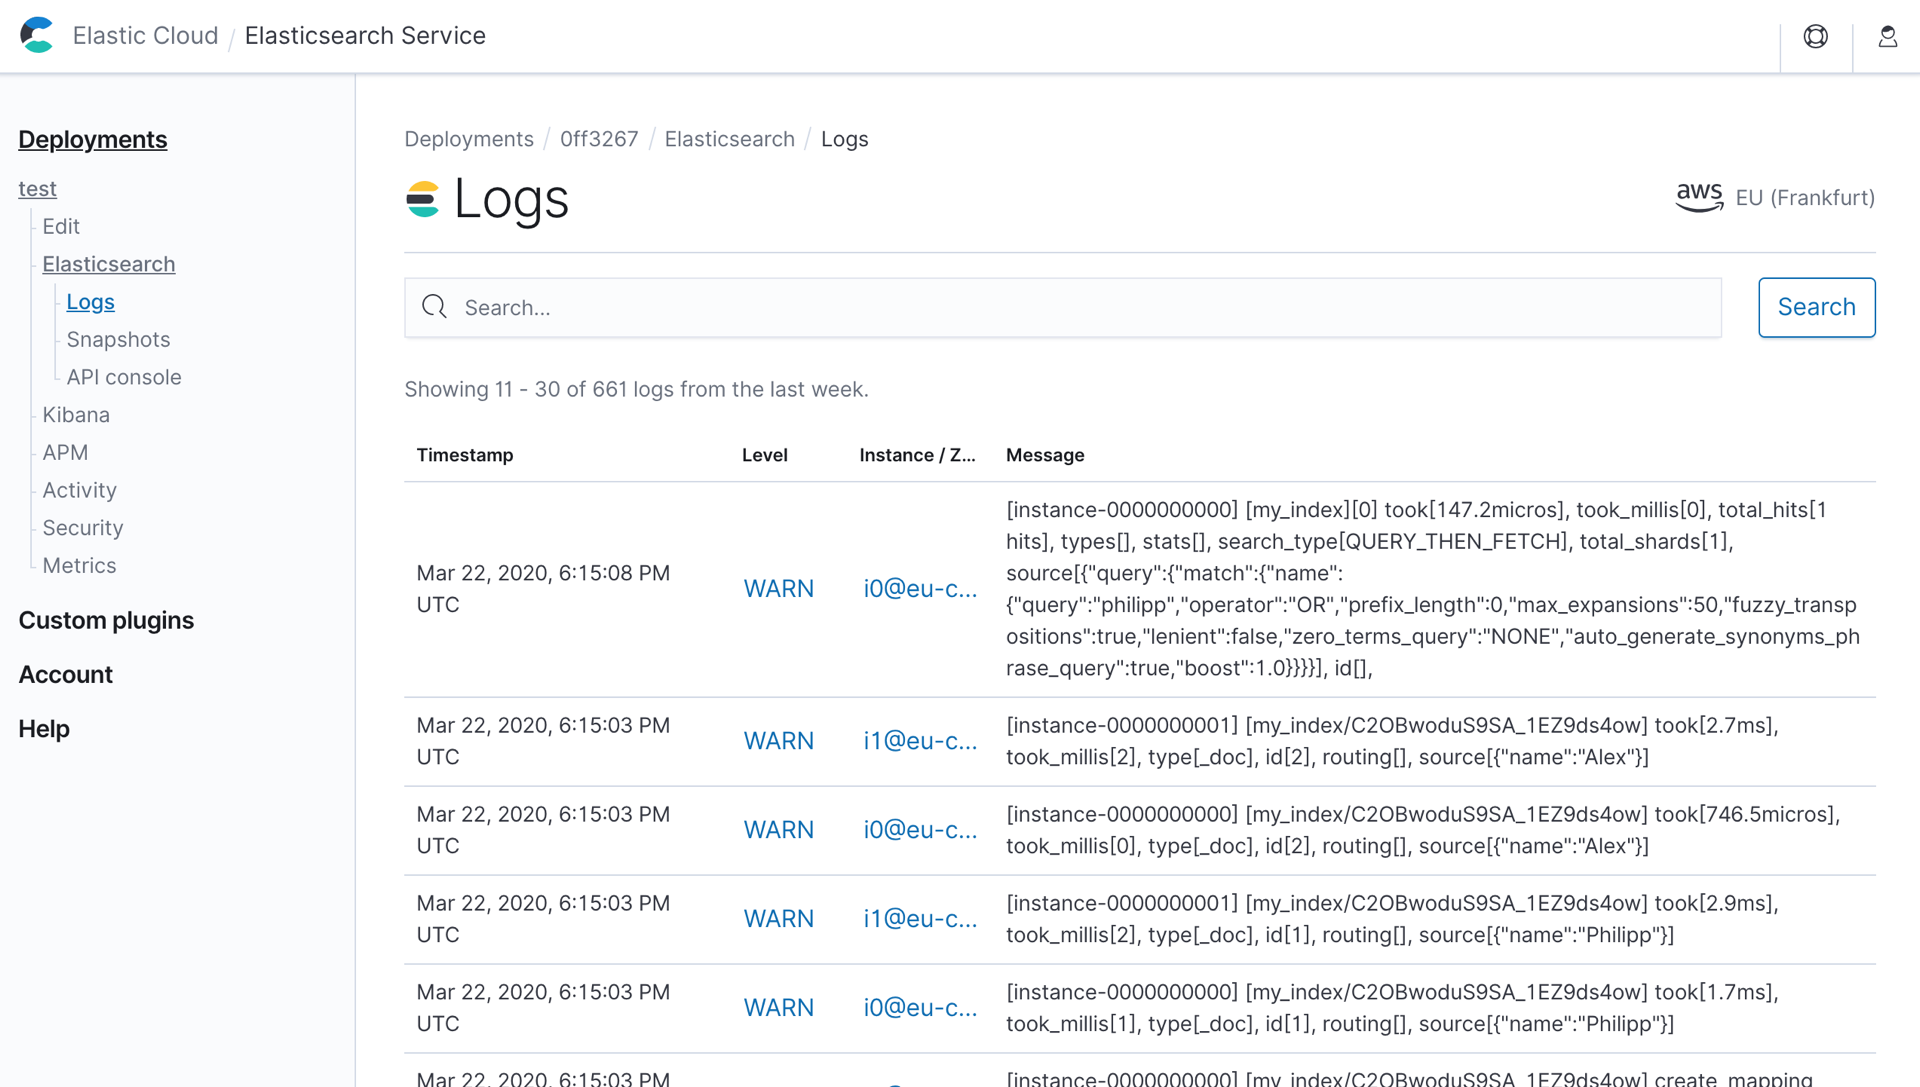
Slow Query Logging for Elasticsearch and Elastic Cloud
Custom Log integration multiple pipelines - Elastic Agent - Discuss the ...
SIEM and Log Retention in a Single Elastic Stack
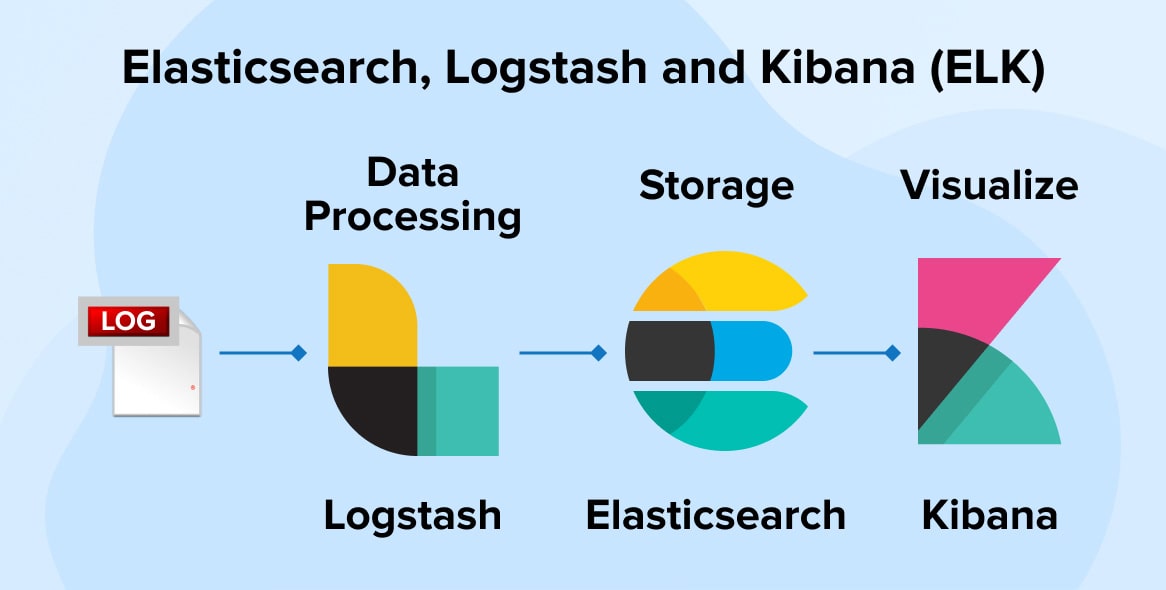
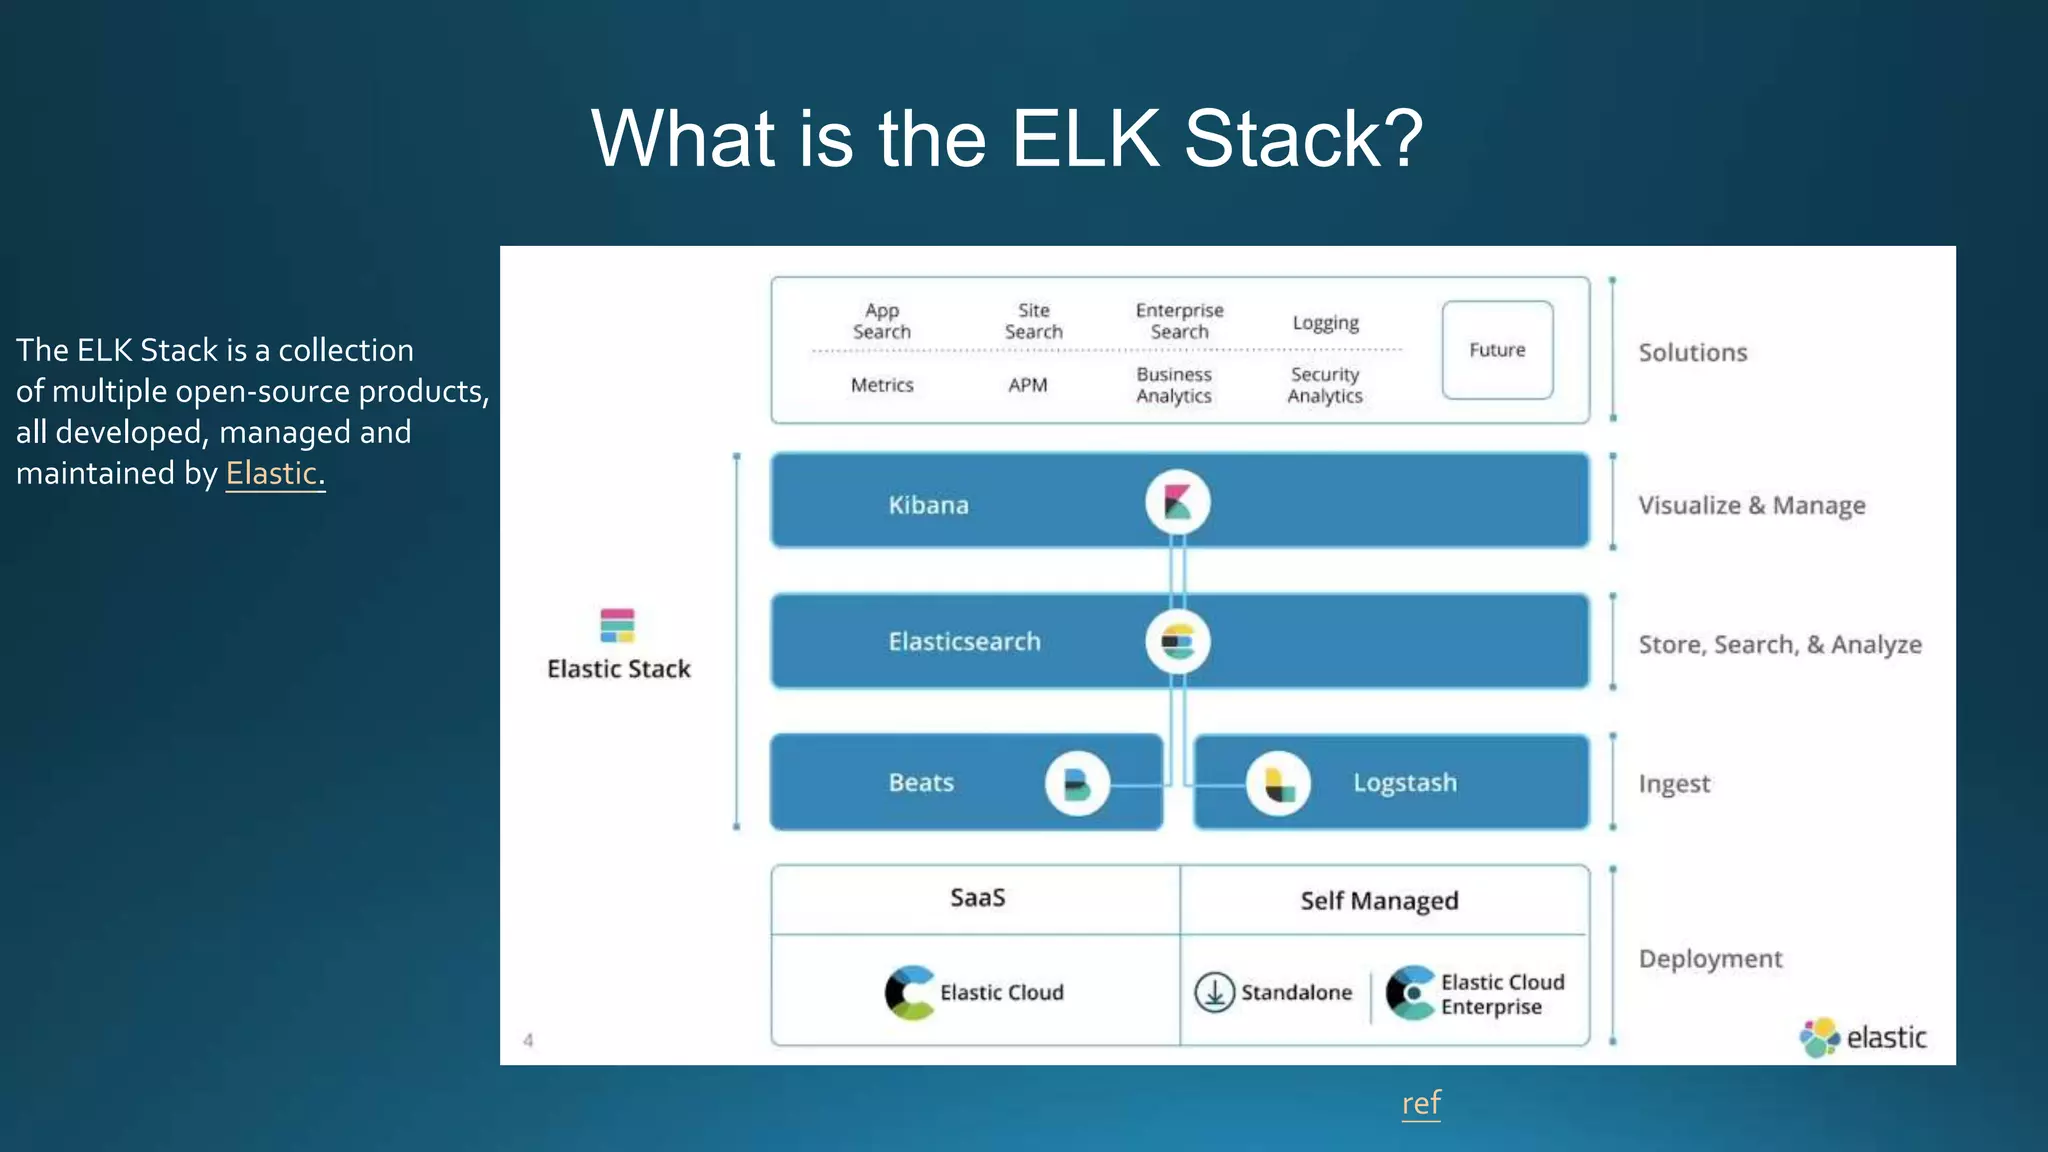
Difference Between Elastic Stack And Elasticsearch at Albert ...
Elastic Streams uses agentic AI to simplify log parsing and accelerate ...
Observability:如何把 Elastic Agent 采集的数据输入到 Logstash 并最终写入到 Elasticsearch ...
Elastic Log Alerting | OpenFunction
Elastic - ELK, Logstash & Kibana | PPTX
Comparison of log and ultrasonic-based elastic moduli and stress ...
Elastic Logs GA Released | Elastic Blog
AWS Elastic Beanstalk – Logging to Logentries & InsightOps from Python
Elastic stack Presentation | PPT
Using Elasticsearch for Log Search and Analysis | Elastic Videos
How do I use Elastic Agent to send log data to Logstash? - Elastic ...
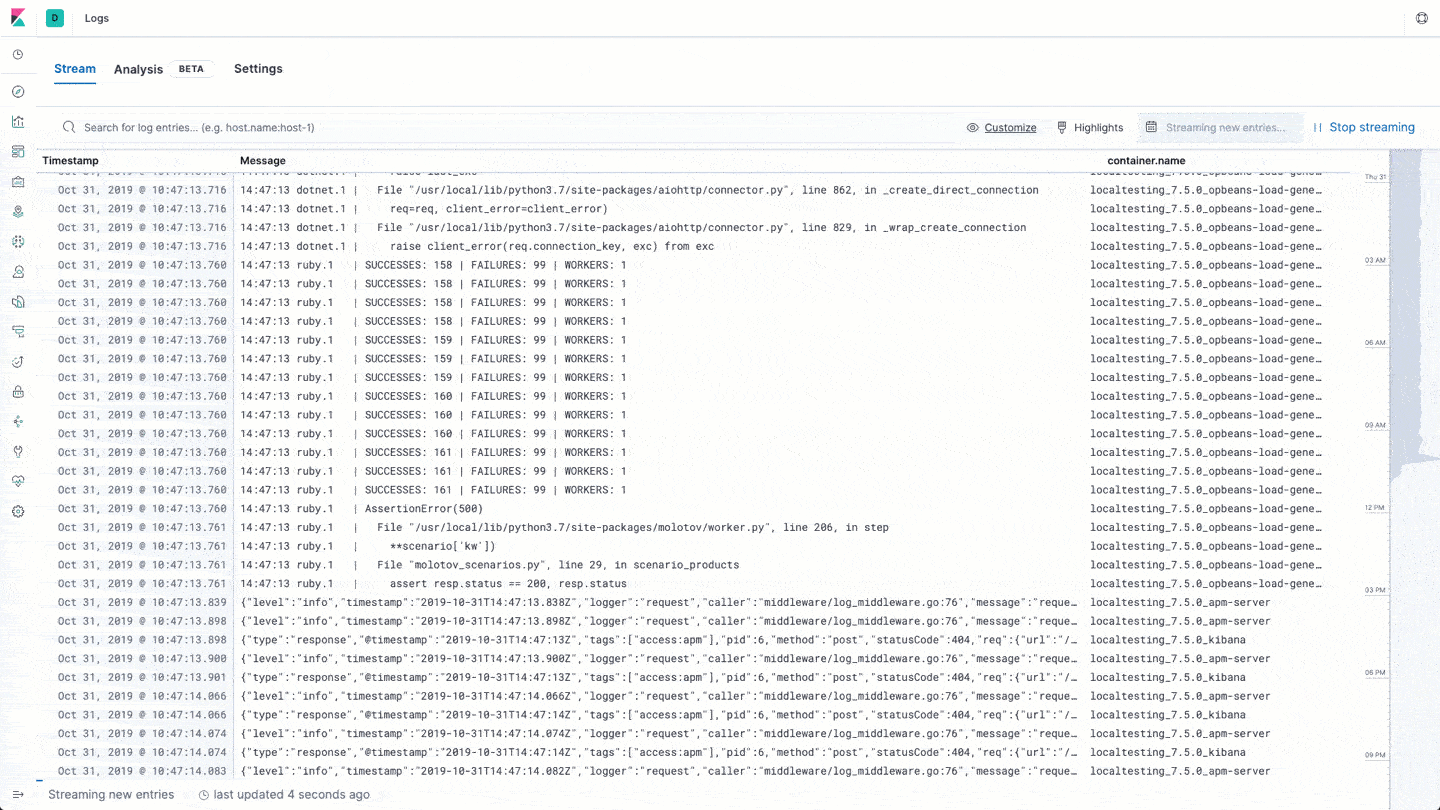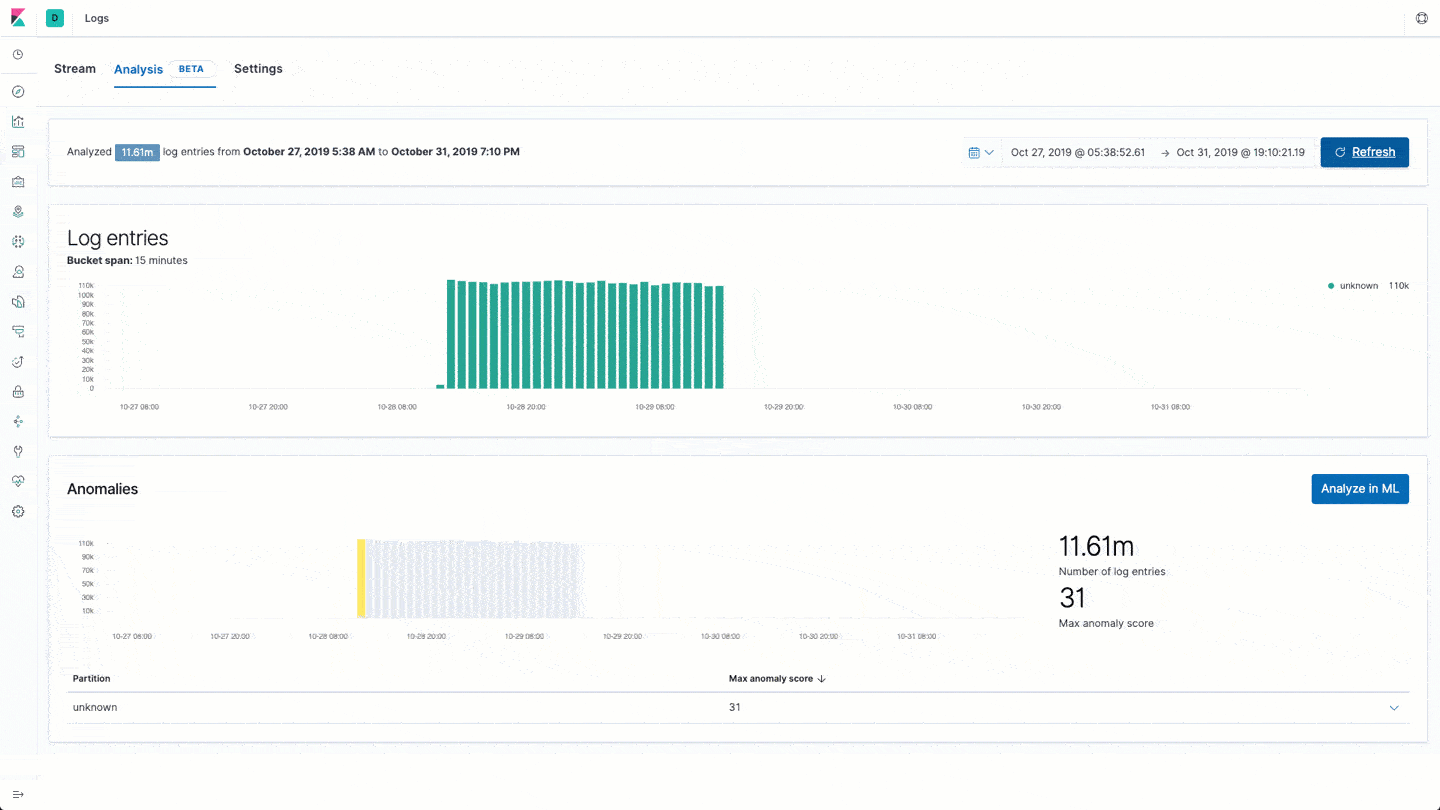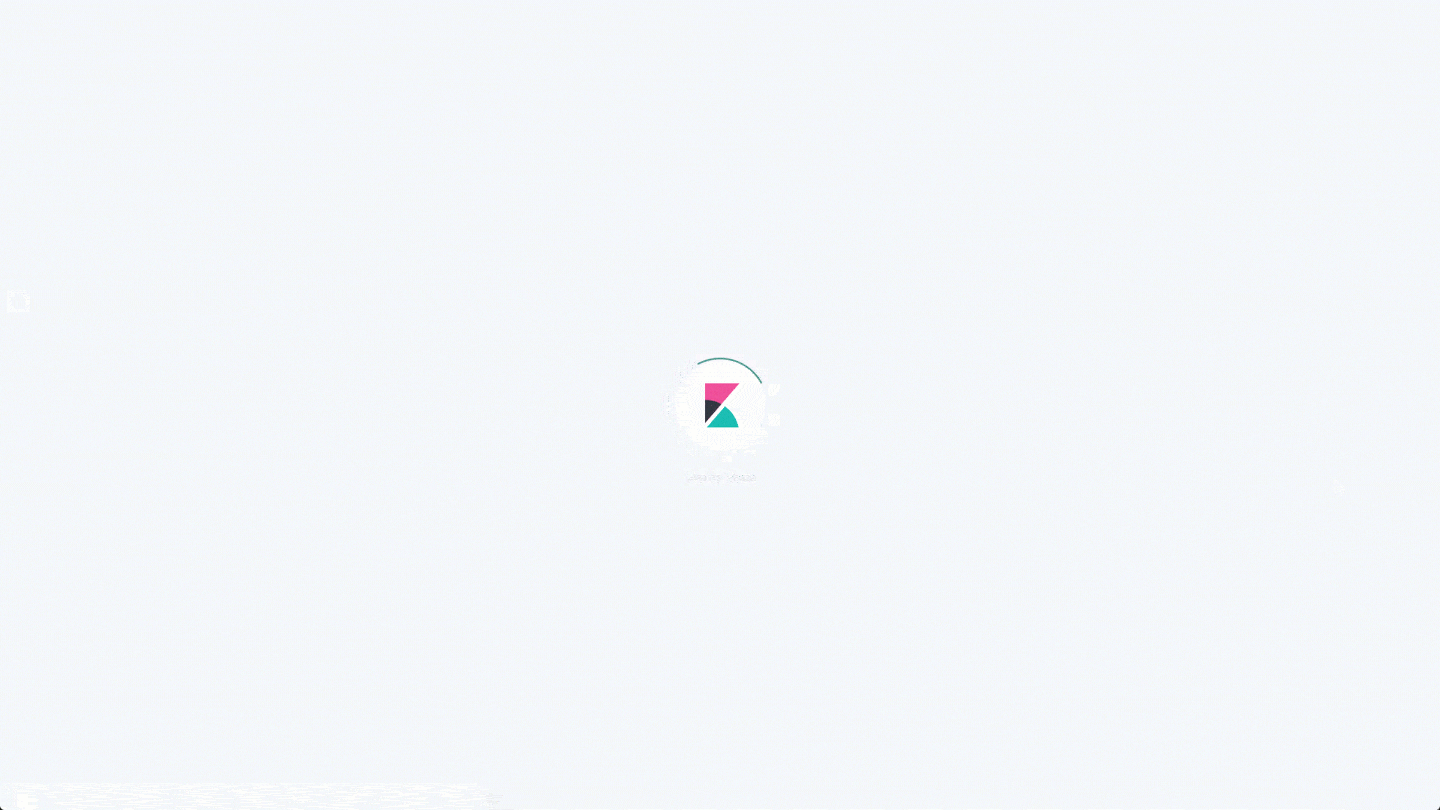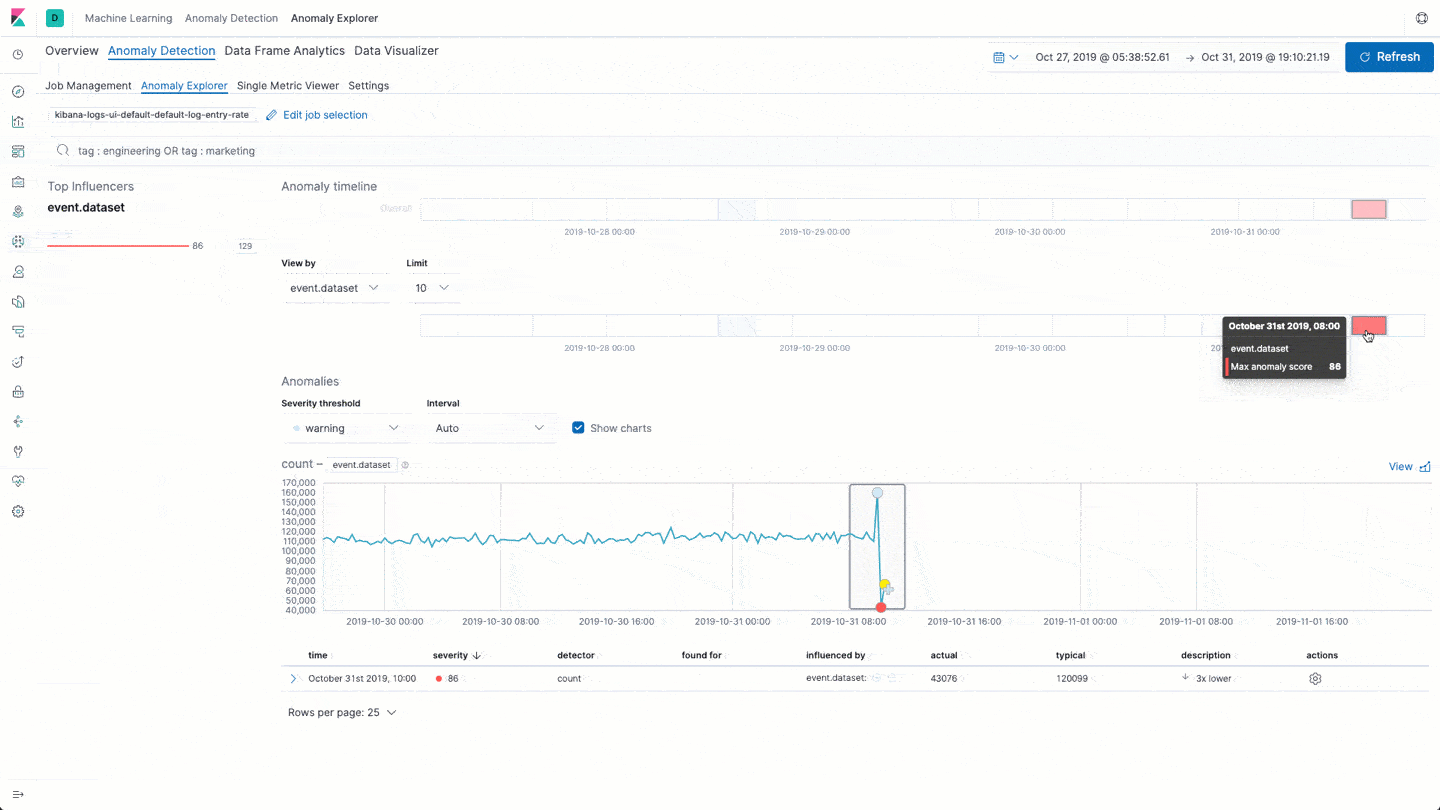
Elastic Logs 7.5.0 released | Elastic Blog
elasticsearch - Elastic Cloud APM not showing logs in Transactions Page ...
Log deduplication with Elasticsearch | Elastic Blog
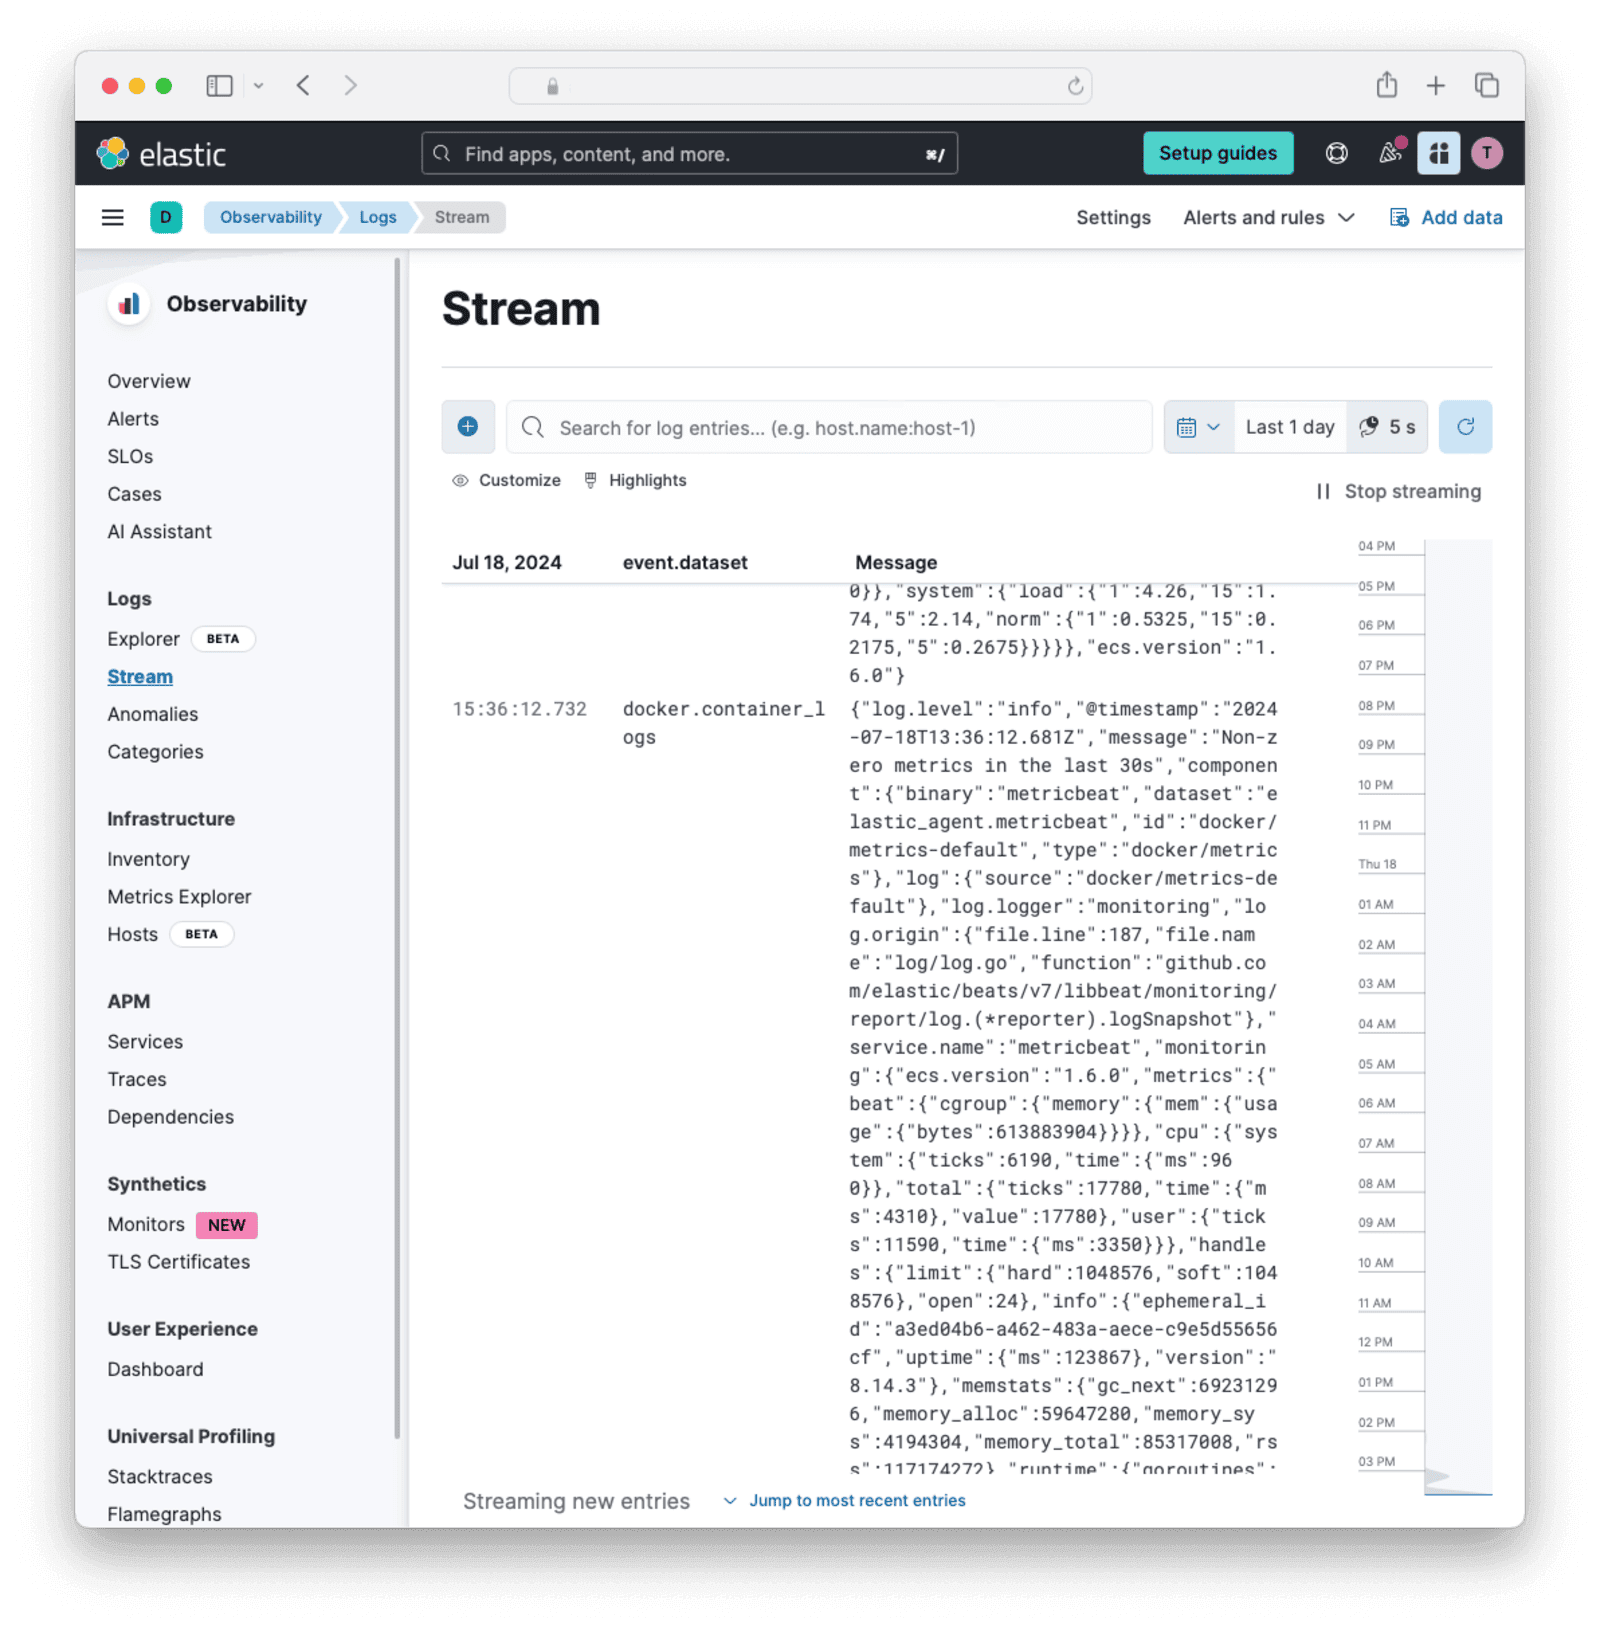
Logs Explorer | Elastic Observability [8.19] | Elastic
Connect to your own local LLM | Elastic Security [8.19] | Elastic
Elastic vs. Graylog: Log-Management-Lösungen im Vergleich – Was passt ...
Getting duplicate log entry in dashboard - Beats - Discuss the Elastic ...
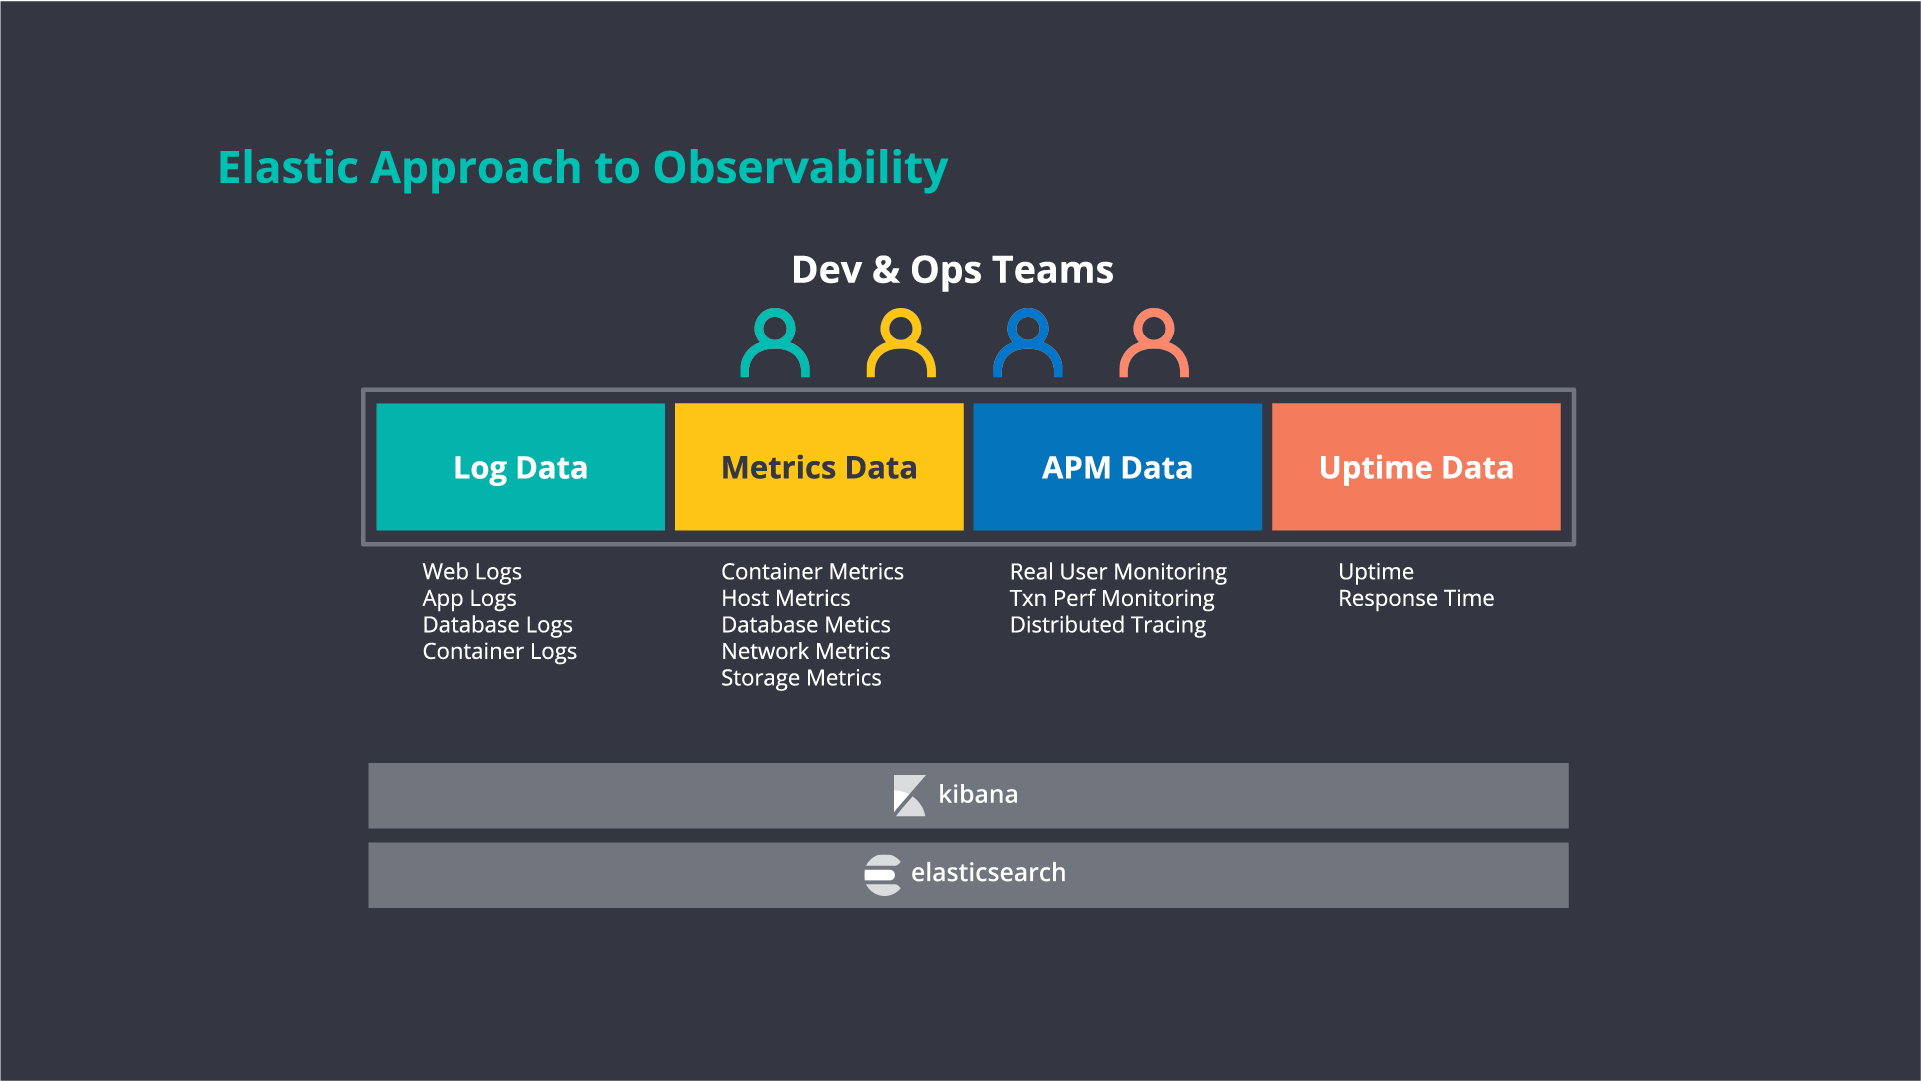
Log monitoring with Elastic Observability | Elastic
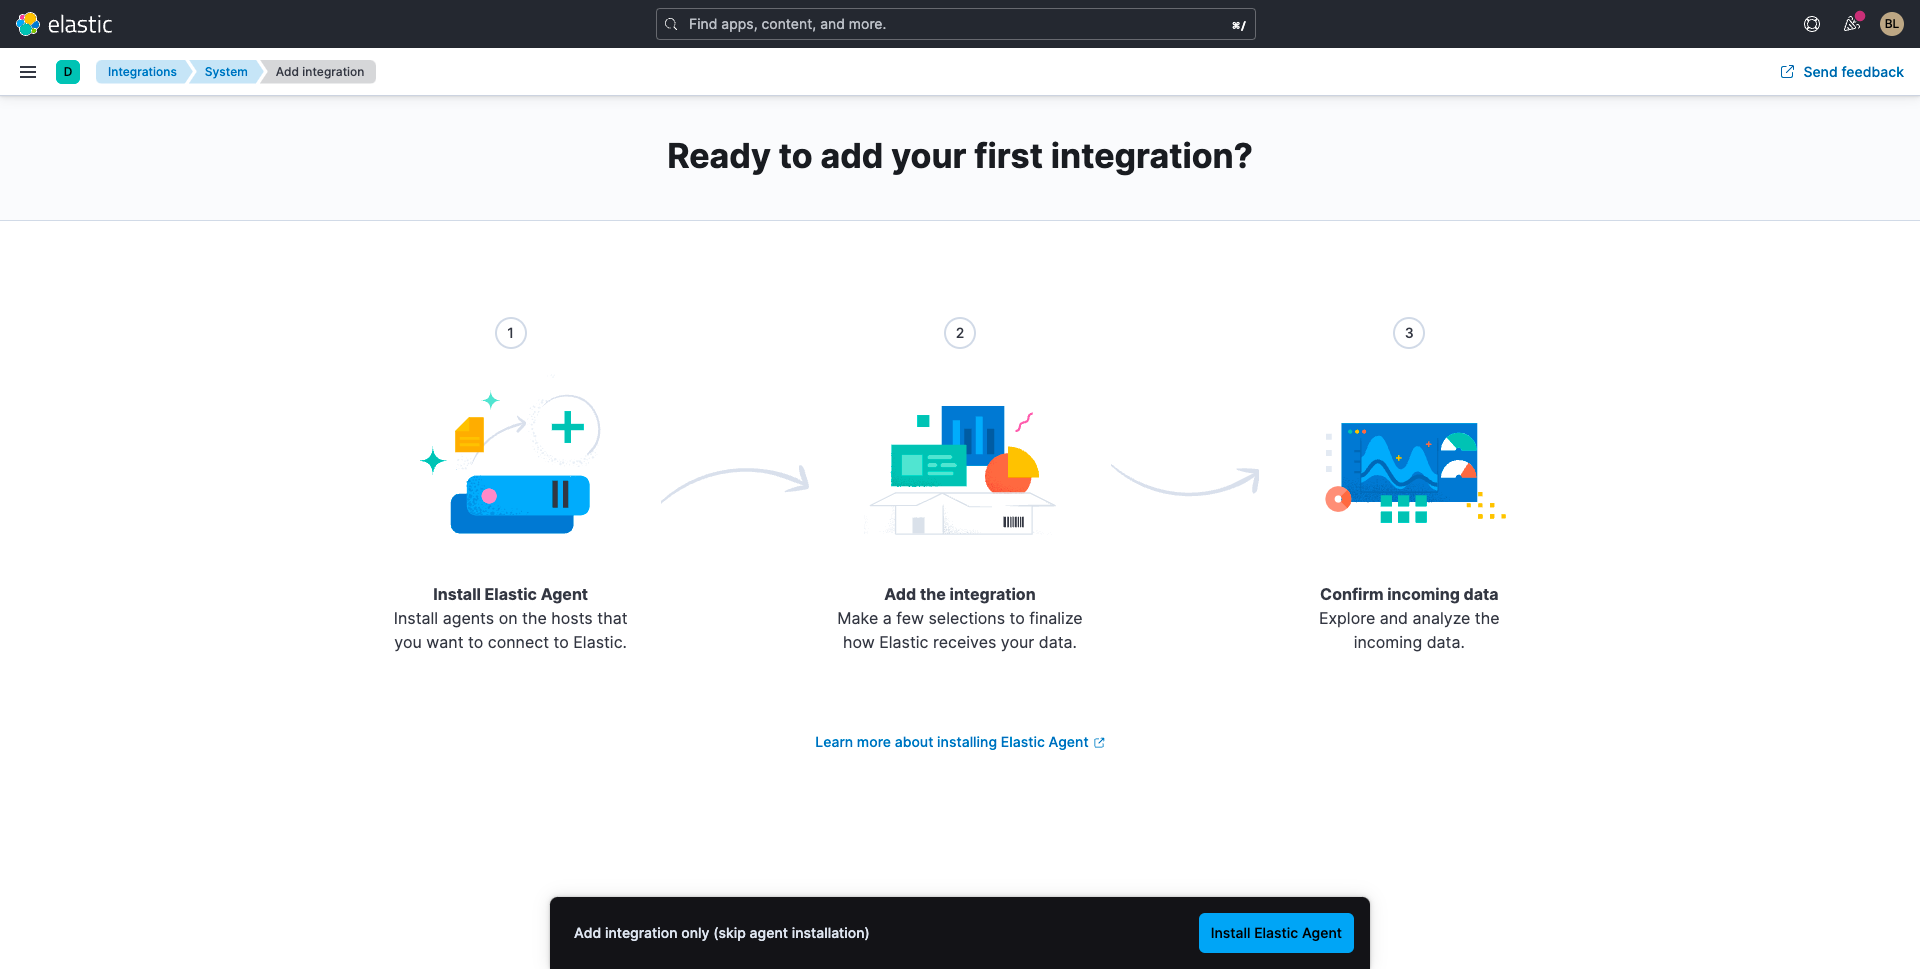
GitHub - elastic/logstash-filter-elastic_integration: The Elastic ...
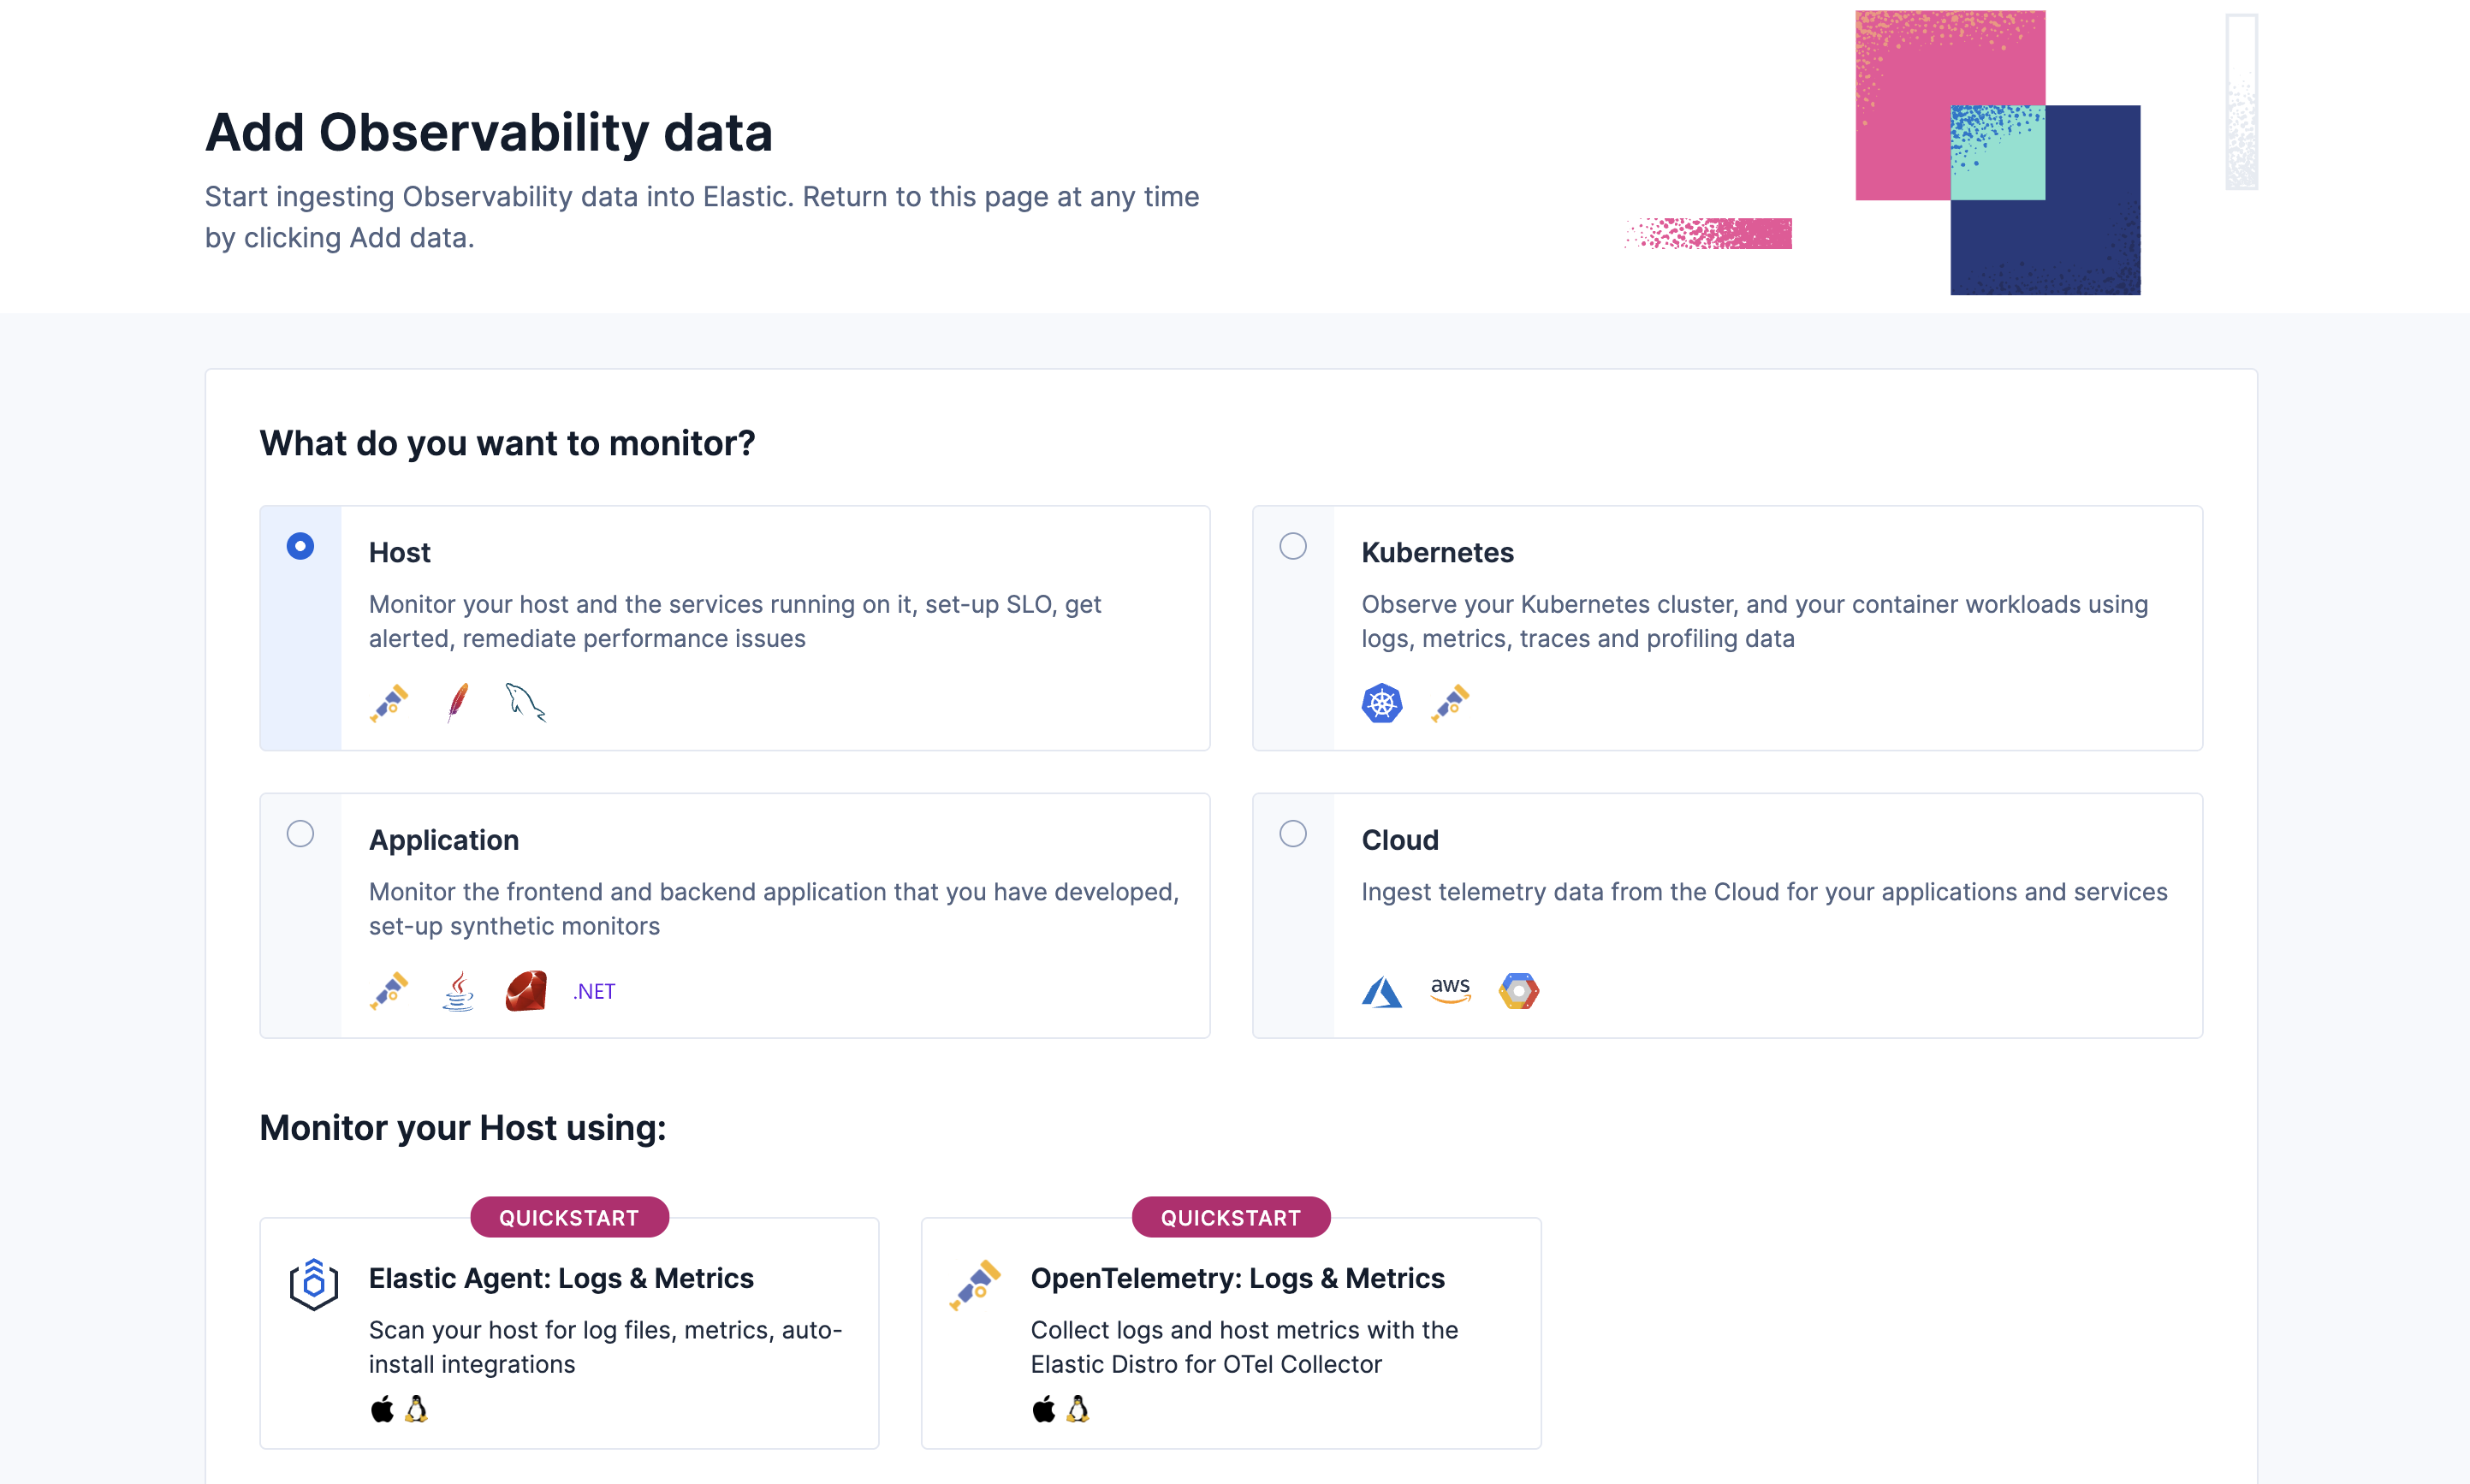
Quickstart: Monitor hosts with OpenTelemetry | Elastic Docs
Migrating a legacy logging system: Etsy’s journey to Elastic Cloud ...
Elastic | FusionAuth Docs
How to Combine Split JSON Logs from AWS Elastic Beanstalk into a Single ...
Logging | Elastic Docs
Elastic Agent Fortinet Module 7 Hours Delay Log - Elastic Agent ...
Elastic Logs 7.6 released with log categorization and more | Elastic Blog
Separating HTTPJSON array to separate log entries - Elasticsearch ...
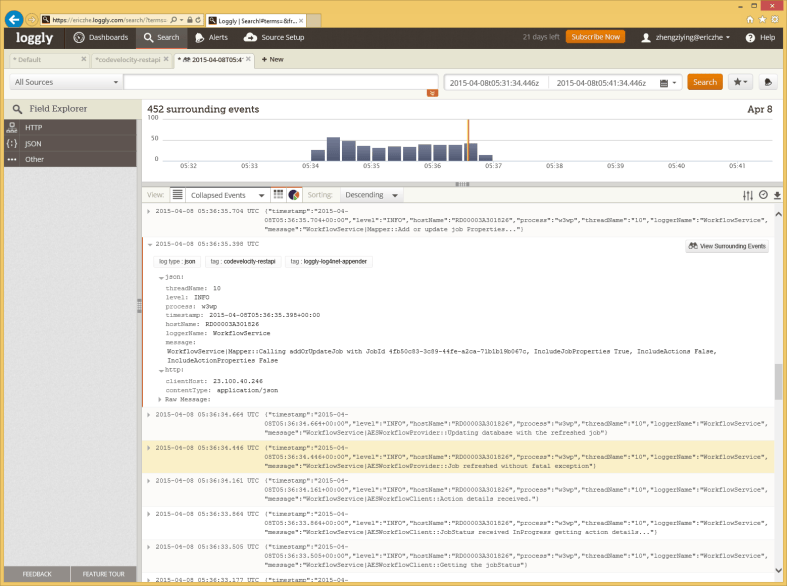
Choosing Between Loggly, Logentries and Elasticsearch | zhengziying.com
Logentries ElastiCache Redis
Making the most of your unstructured log data through enterprise log ...
Como Instalar Elasticsearch, Logstash e Kibana (Elastic Stack) no ...
Deploy Elasticsearch, Kibana & Logstash (ELK Stack) with Docker Compose ...
Using Logstash To Analyse Iis Log Files With Kibana – KUYE
Application Log Pattern at Karrie Keane blog
Zero Latency: Building a better VR gaming experience with Elasticsearch ...
elastic.io Documentation | Platform UI tour
What Is ELK Stack? | Elasticsearch, Logstash, & Kibana | NinjaOne
Understanding Elasticity and Log Relationship - YouTube
PPT - chapter nine PowerPoint Presentation, free download - ID:4499800
Elasticity and logarithms - Economics Stack Exchange
Medium
Elastic-agent 8.17.7: logs are not being harvested from .log files on ...
Solved 8.11 Derive the expressions for the elasticities | Chegg.com
Log all the searches going through Elasticsearch | Mike Polinowski
PPT - ECONOMETRICS I PowerPoint Presentation, free download - ID:2352566
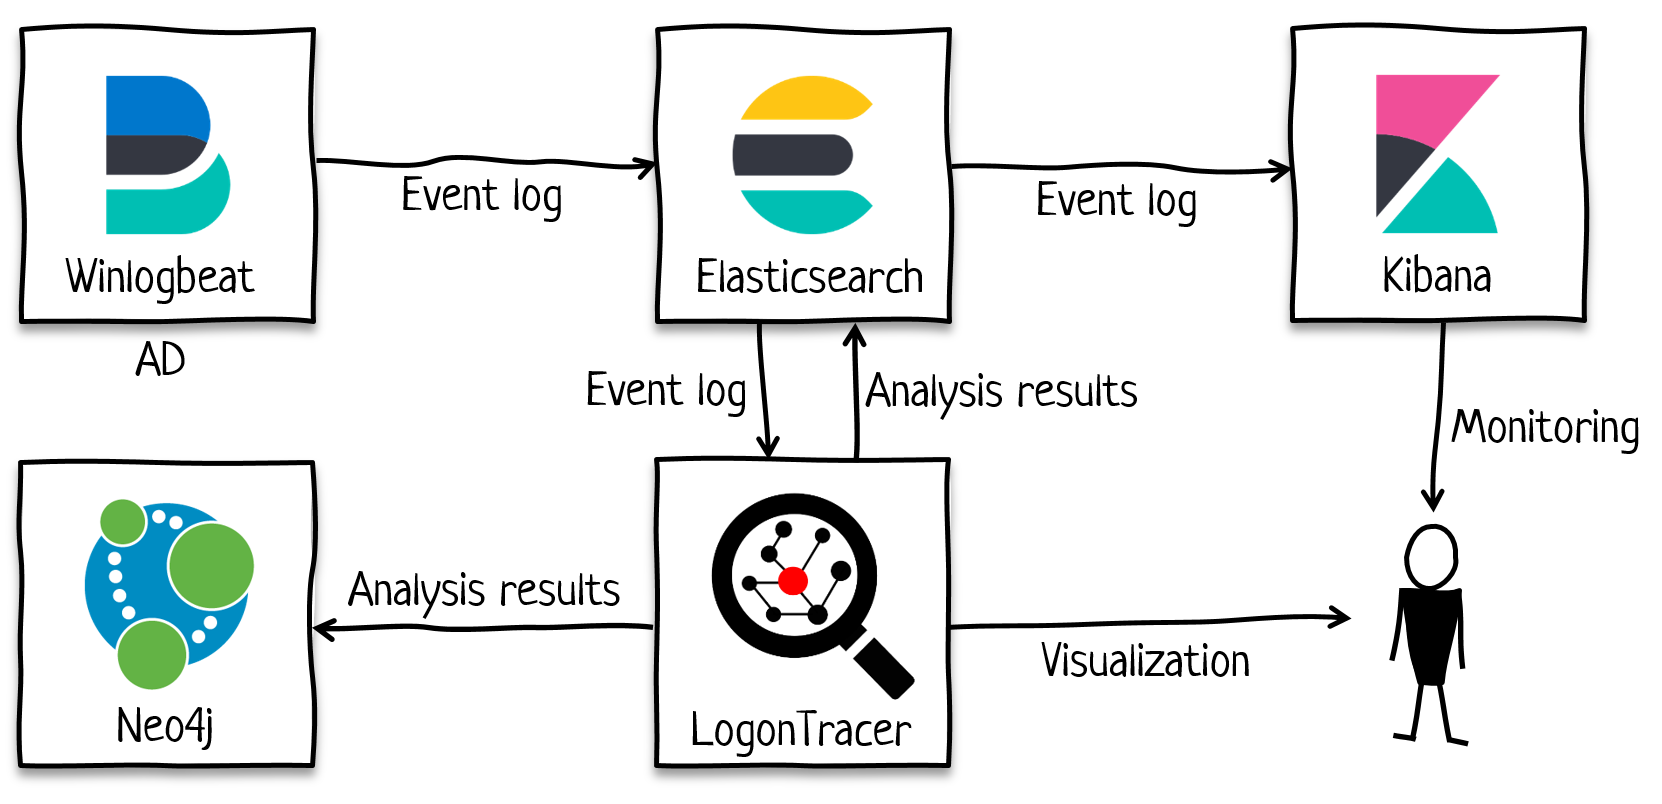
Combining LogonTracer with Elasticsearch · JPCERTCC/LogonTracer Wiki ...
Best practices for log management and improving problem resolution ...
Centralized log-management-with-elastic-stack | PPTX
analysis – Track Analysis Application — Navtools 2021.08.29 documentation
填坑填坑,万字+28张图会一会传说中的Raft协议-腾讯云开发者社区-腾讯云
Set Up a Centralized Logging System with ELK | HostMyCode
[Logs App] "Log Entry Details" is not friendly to copy/paste · Issue ...
SIF Implementation Specification 2.2 - Infrastructure Working Group
28图图解Raft协议,so easy~~-CSDN博客
ElasticSearchを使ったlog収集1 -Elastic Agentとは?- · hirohirolab
Logistic regression with elasticnet for model 1 | Download Scientific ...
How to get Log Patterns similar to what Logz.io does? - Logs - Discuss ...
How to Fill Missing Interface Entry Values Using Corresponding System ...
I am encountering an issue while attempting to verify a snapshot ...
Trace.id and transaction.id not being added to log entry - Logs ...
Elasticsearch Data Governance With DataSunrise
GitHub - aws-samples/elastic-beanstalk-image-pipeline-trigger ...
elasticsearch syslog 収集 _ elasticsearch logstash 使い方 – MSUOIB
[Research] StorageGRID Syslogging: The ELK Stack
Logging on Jelastic just got better with Logentries | Virtuozzo Blog
Mastering Kubernetes Deployments with YAML: A Practical Guide | by ...
Effortless Data Compliance for Elasticsearch With DataSunrise
Model of Data in Clearing House · Issue #532 · International-Data ...