Showing 120 of 120on this page. Filters & sort apply to loaded results; URL updates for sharing.120 of 120 on this page
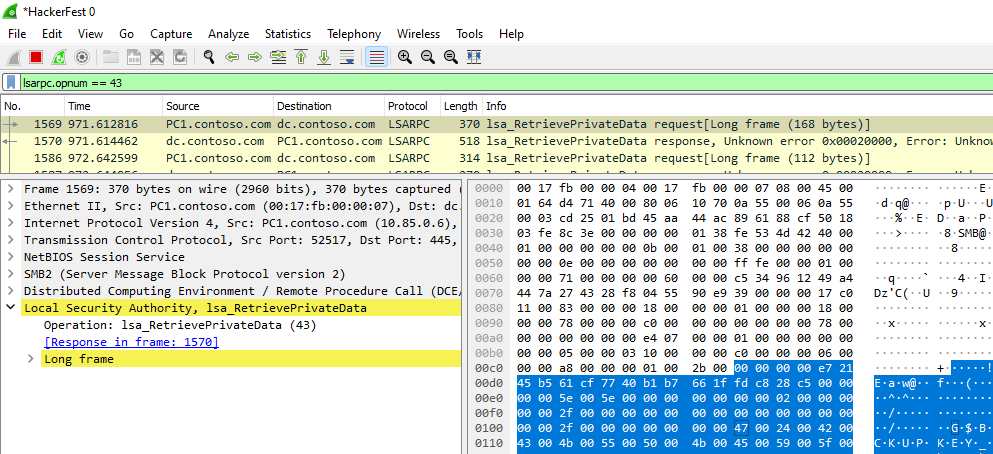
Detecting DPAPI Backup Key Theft | DSInternals
Detecting Active Directory Attacks: DCSync, DCShadow, DPAPI
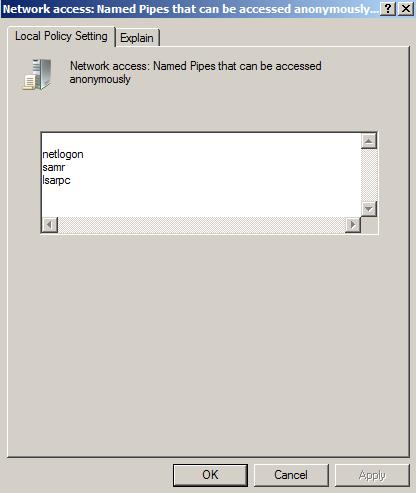
2.3.10.6 Ensure 'Network access: Named Pipes that can be accessed ...
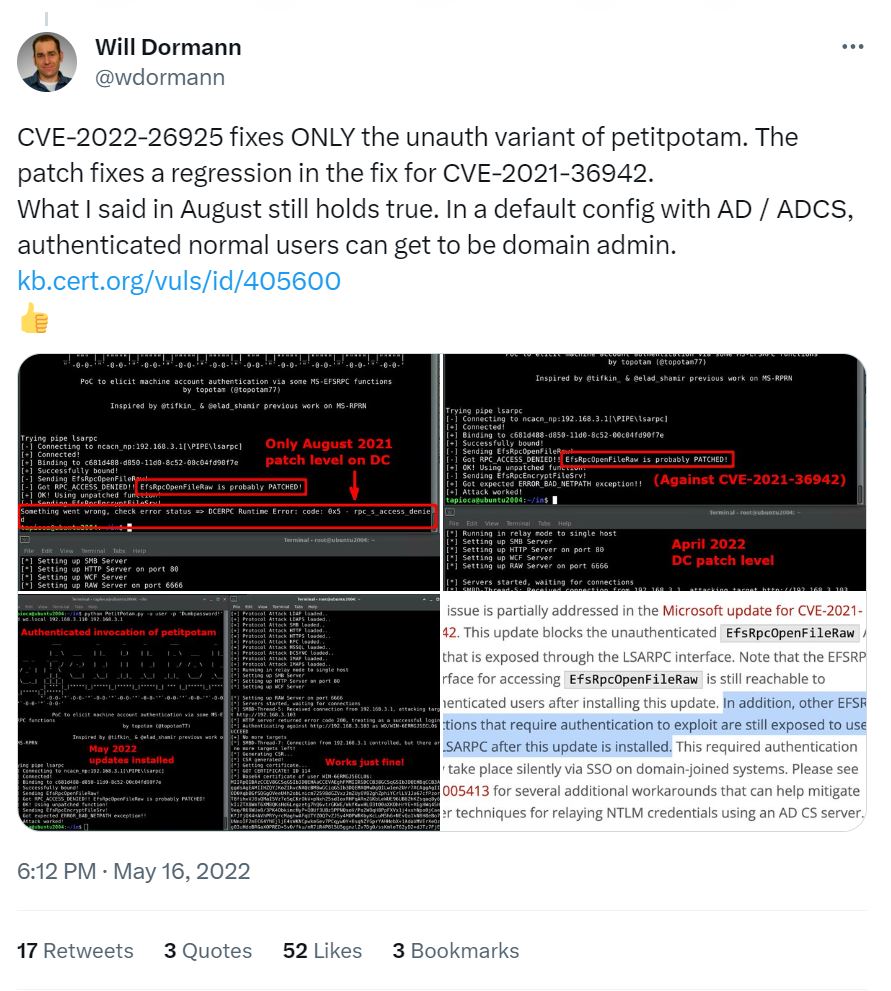
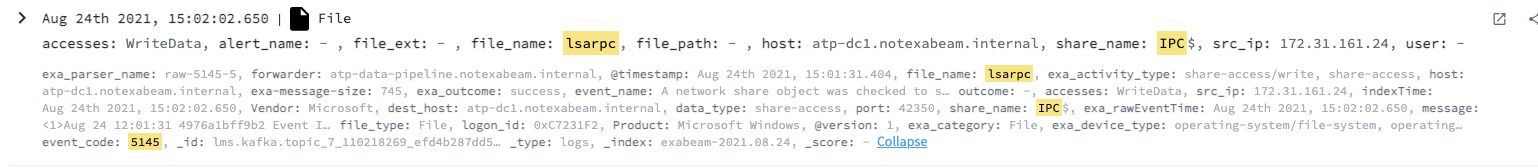
Detecting the New PetitPotam Attack With Exabeam | Exabeam
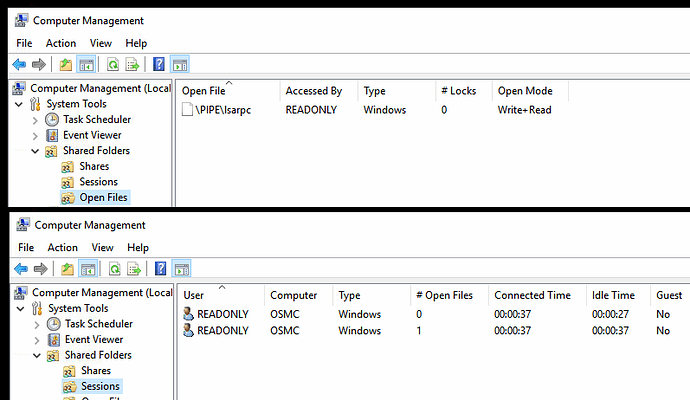
OSMC is randomly turning my windows file server on with WOL - Raspberry ...
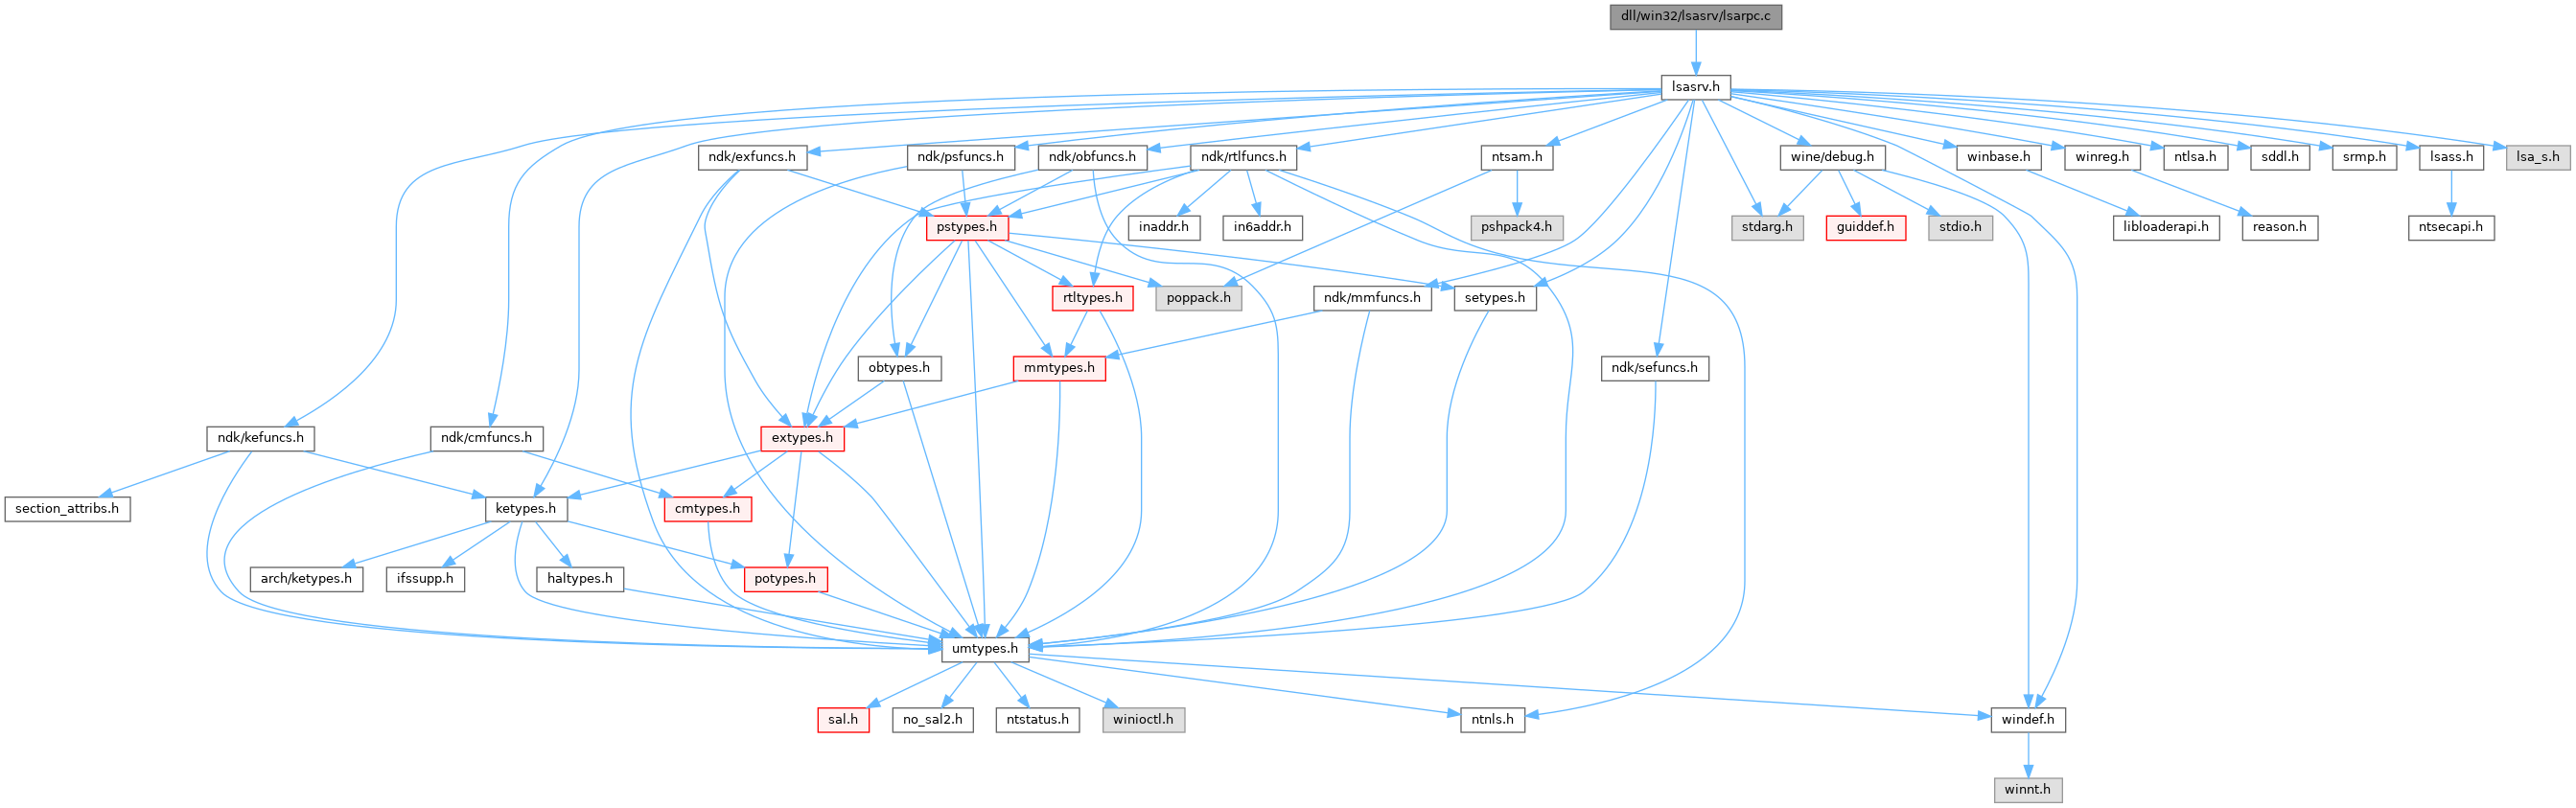
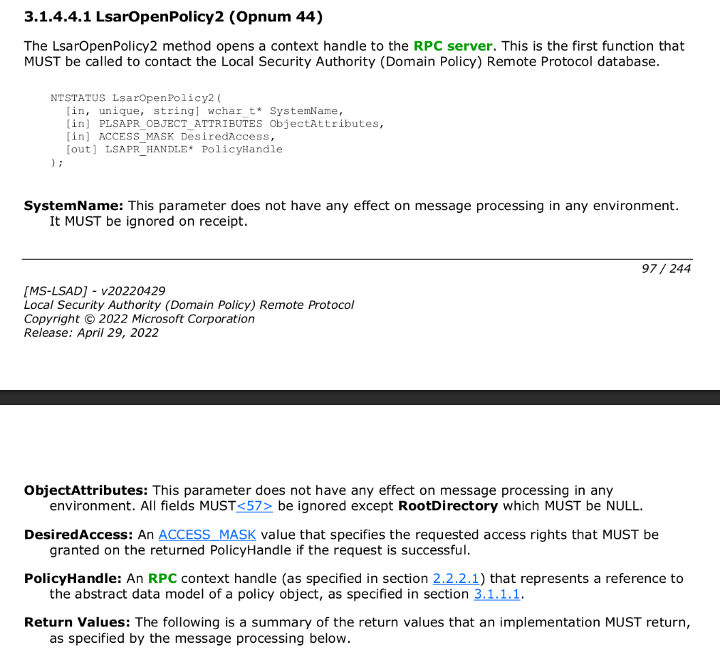
ReactOS: dll/win32/lsasrv/lsarpc.c File Reference
Blue Teamer: March 2015
Understand Kerberos in Azure NetApp Files | Microsoft Learn
Fix lsarpc.dll and Login Errors! - YouTube
CREST CCT Exam Prep Notes | PDF
Malware analysis lsarpc.exe No threats detected | ANY.RUN - Malware ...
第10章 windows网络服务评估(网络安全评估) - 知乎
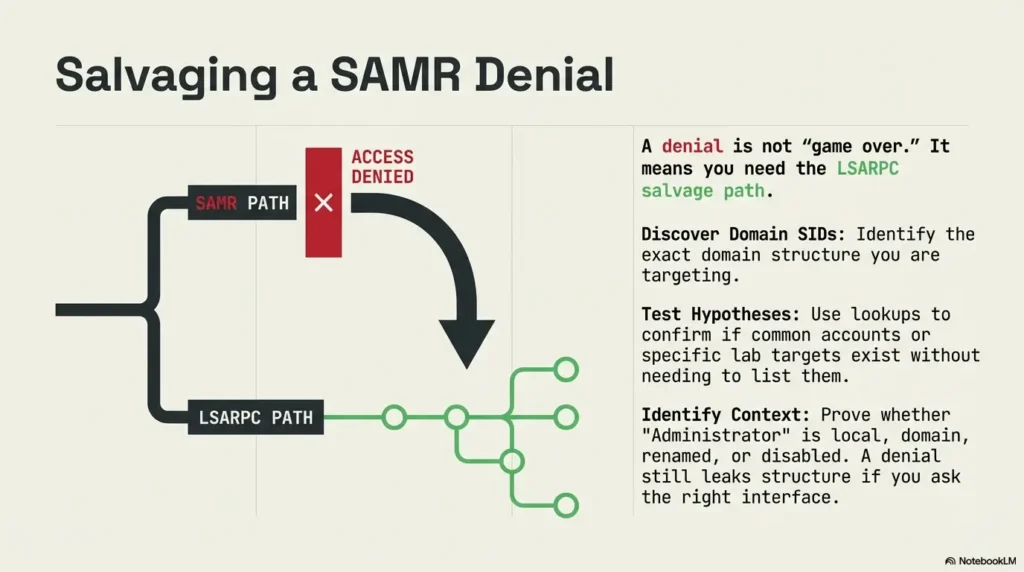
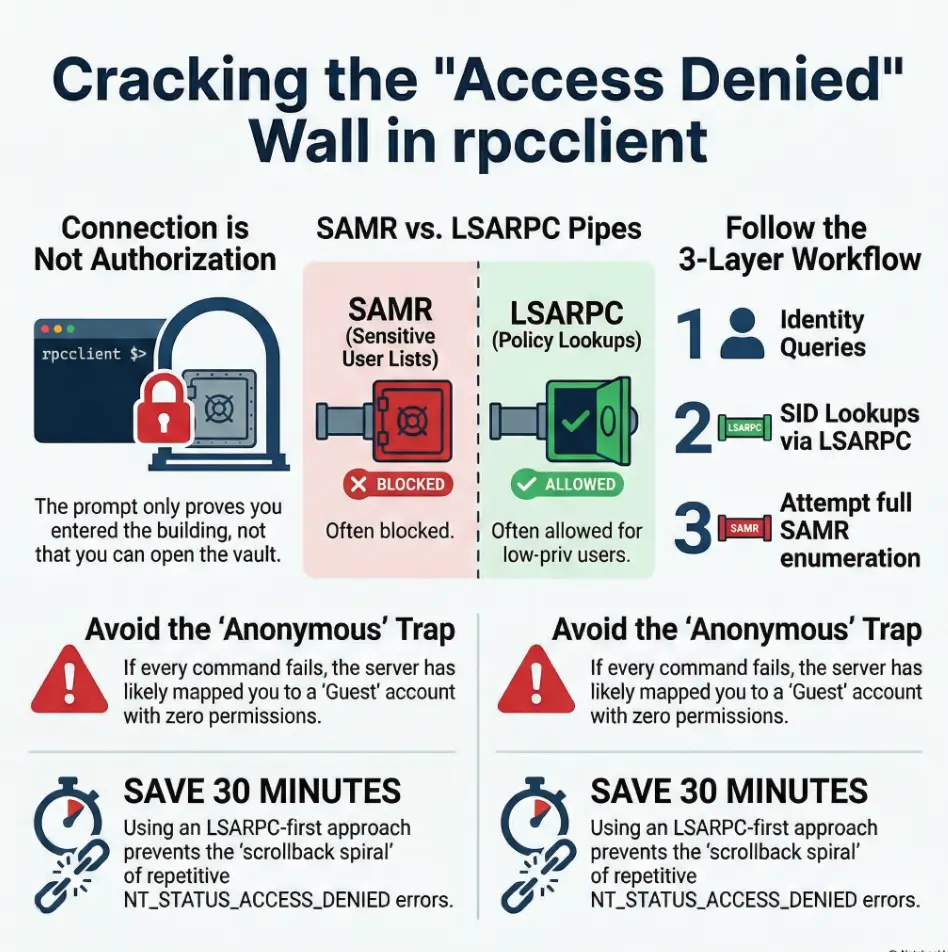
rpcclient NT_STATUS_ACCESS_DENIED: 7 Brutal Proven Fixes
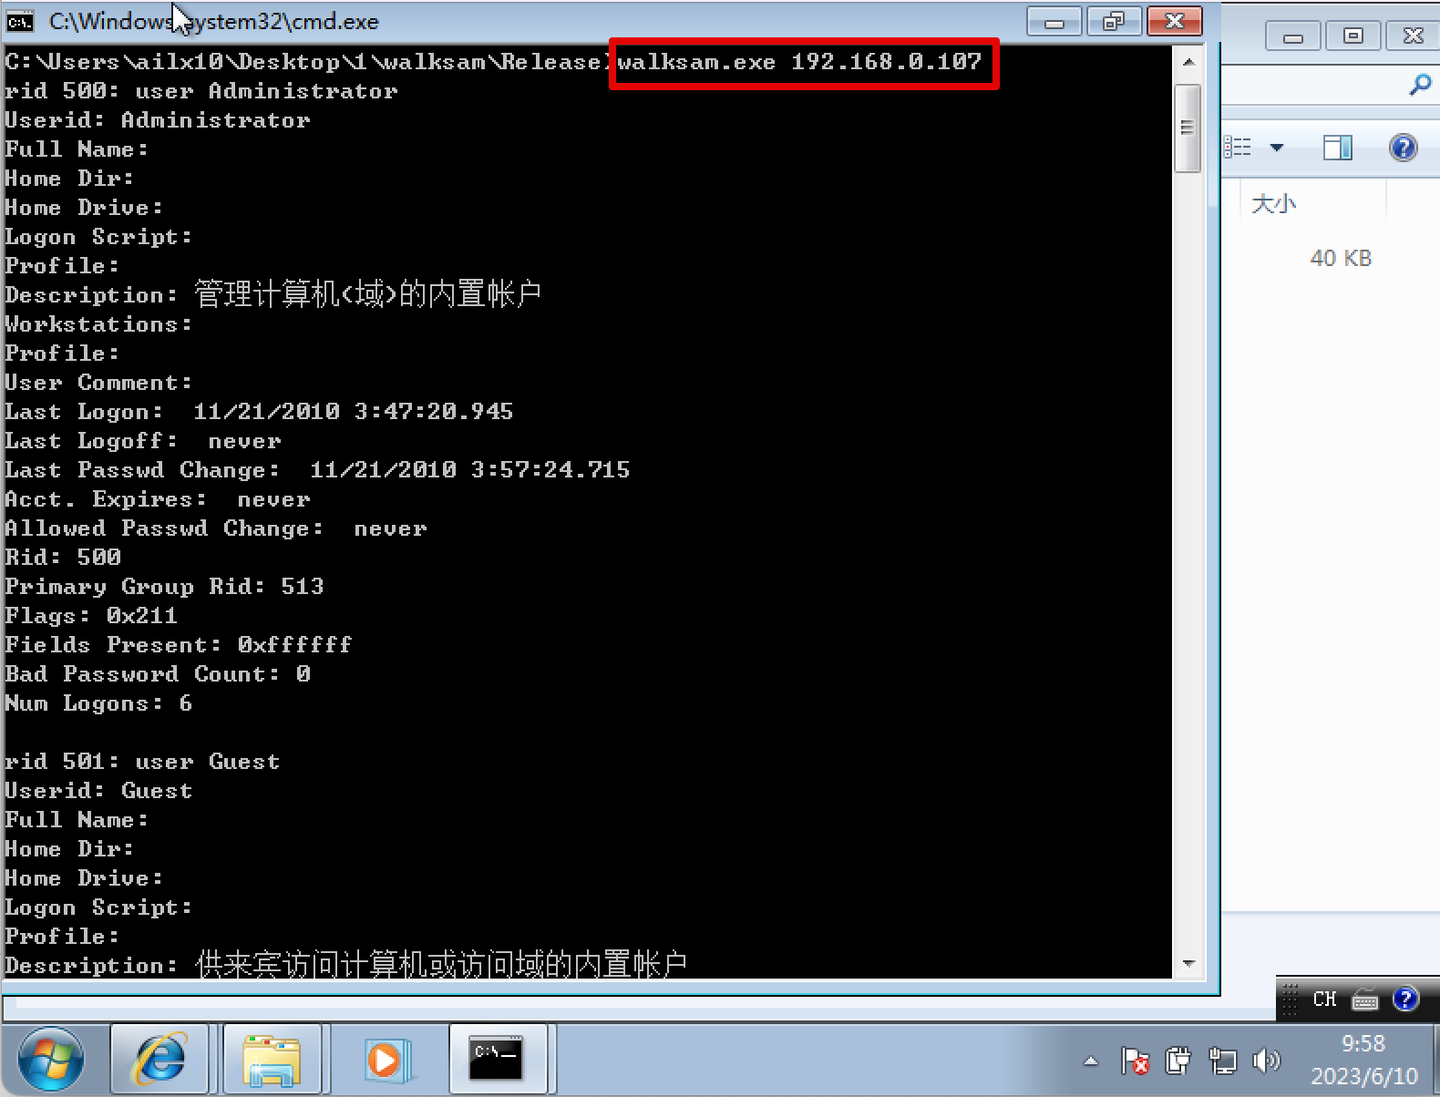
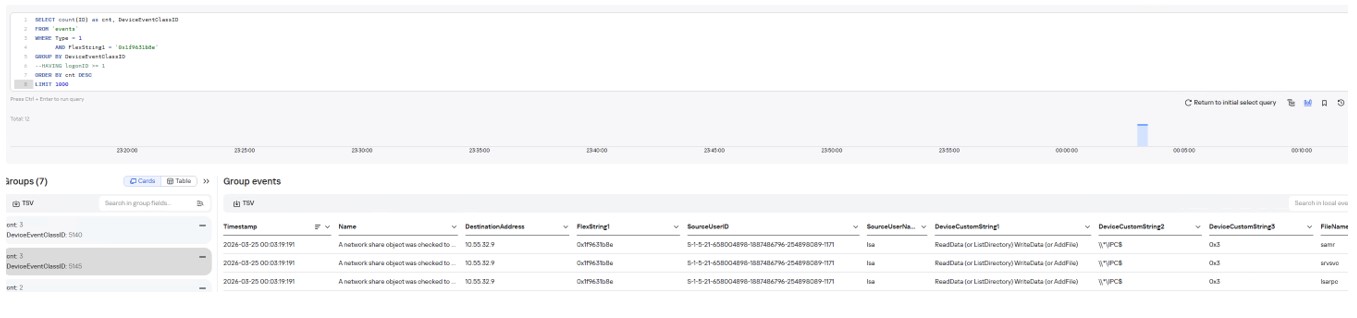
基于AD Event日志监测域内信息探测行为-腾讯云开发者社区-腾讯云
基于AD Event日志监测域内信息探测行为 - Bypass - 博客园
由BreakOut引发对SMB的进一步思考 - ShoreKiten - 博客园
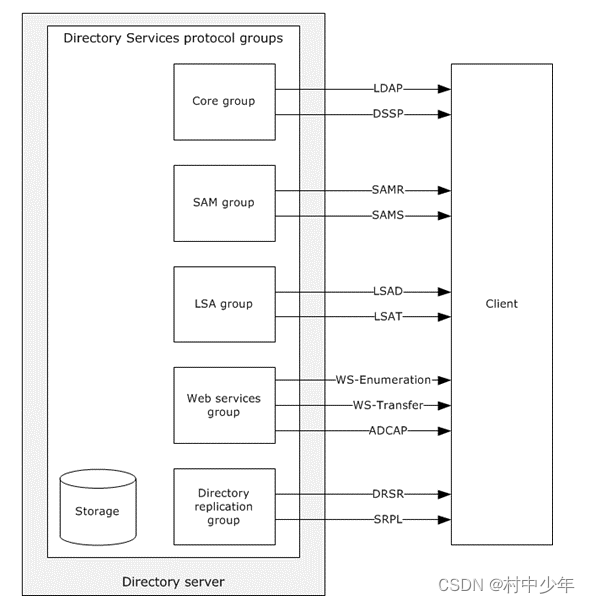
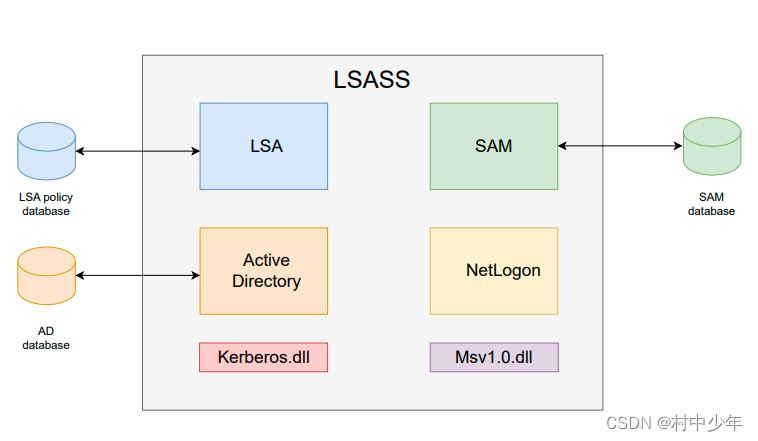
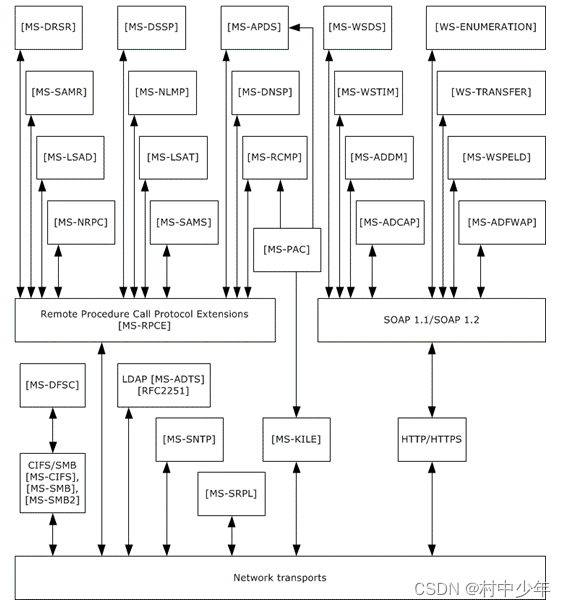
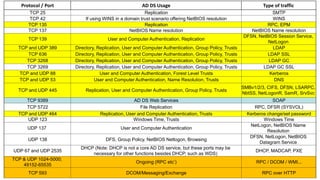
windows协议详解之-RPC/SMB/LDAP/LSA/SAM域控协议关系-CSDN博客
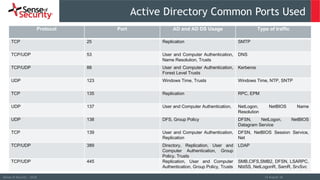
Active Directory Protocols – Samarth's Handbook
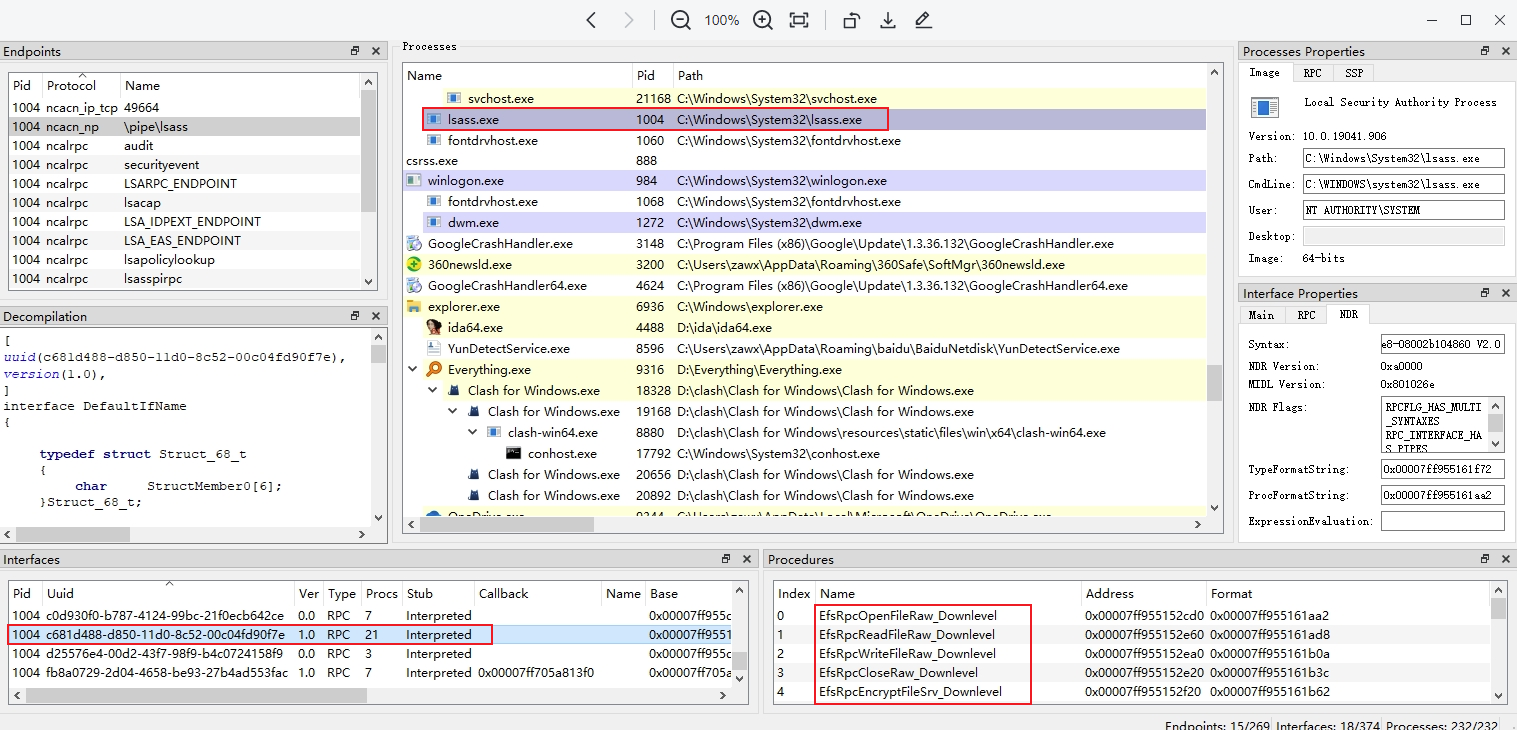
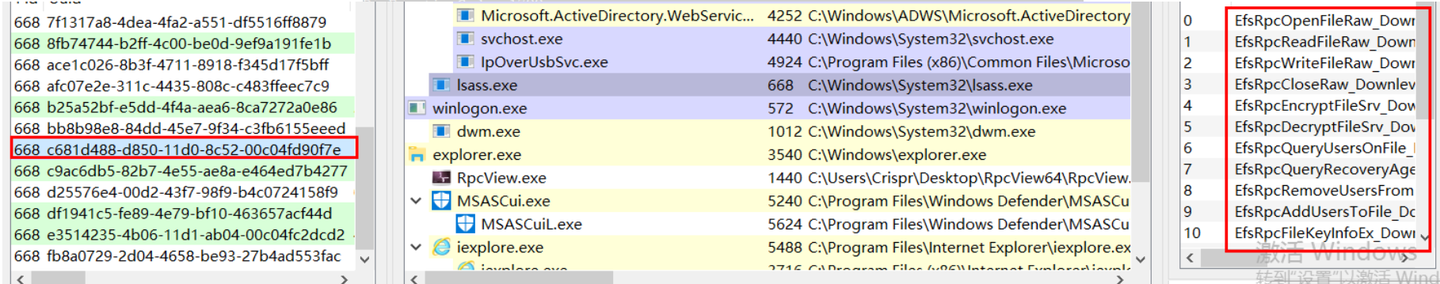
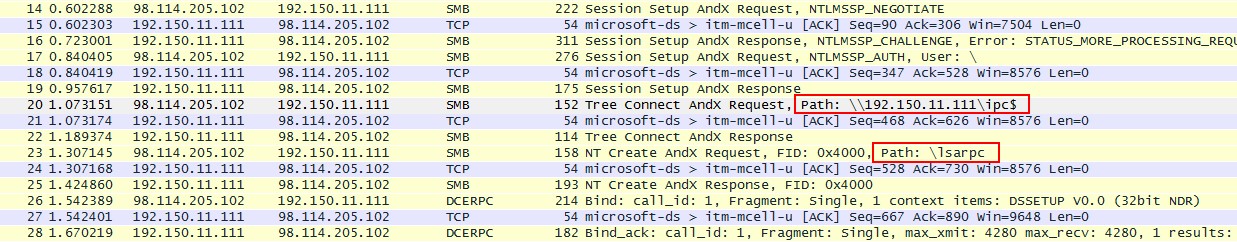
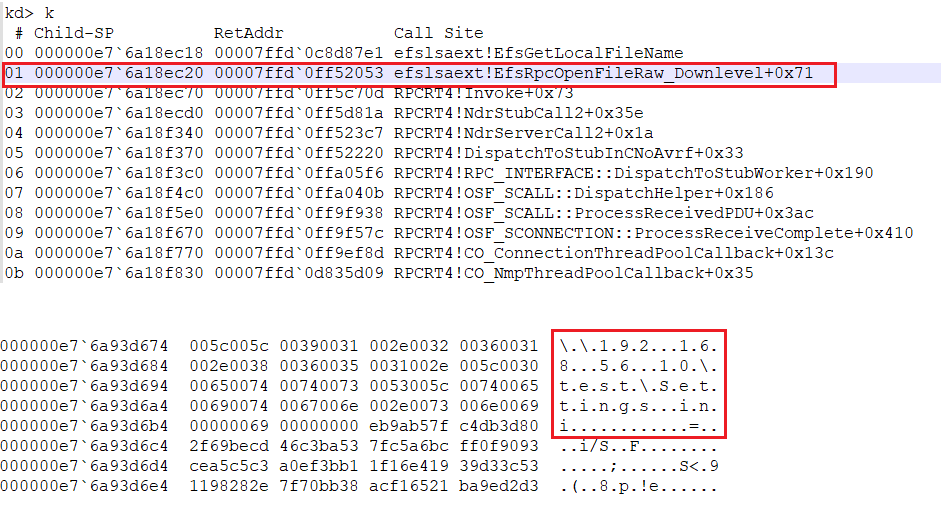
PetitPotam漏洞以及本地提权利用分析 - zpchcbd - 博客园
Use PetitPotam instead of Printerbug - Moment For Technology
A Bit About the Local Security Authority
Rpc introduction
协议%26端口 - SMB %26 DCERPC - 《GitBook》 - 极客文档
SharpHound Detection – Purple Team
Resolución de máquina Blue · alimh blog
【网络安全】安全漏洞之使用PetitPotam代替Printerbug_lsarpc 协议-CSDN博客
深入理解MSF之Getsystem | EndlessParadox
Network Flow Matrix
GitHub - xunyang1/ssp_dump_lsass: RPC 调用添加ssp扩展dump lsass · GitHub
“PetitPotam” Windows LSA Spoofing Vulnerability (CVE-2021-36942) | Secured
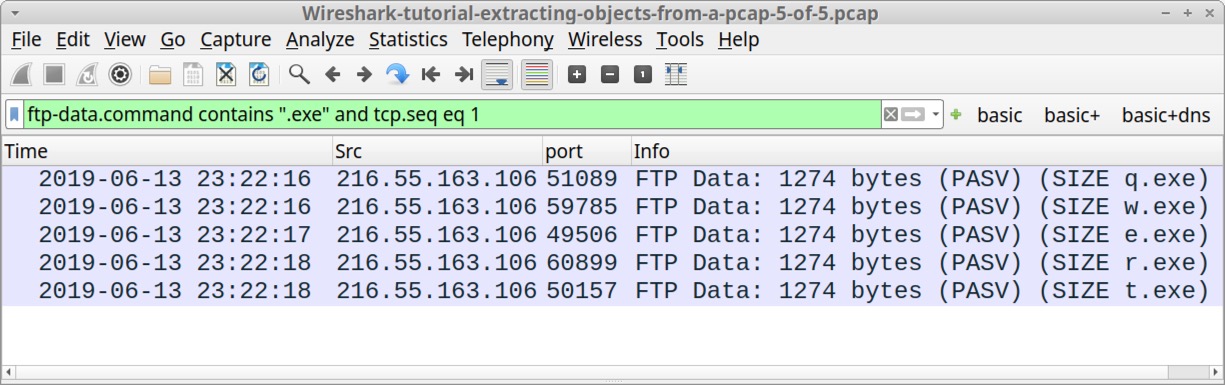
[2024-03-04 JST 改訂] Wireshark によるパケット解析講座 4: Pcapからのオブジェクトのエクスポート
主机安全技术剖析-关于Windows RPC挖掘的那些事 - 知乎
PPT - Pass-The-Hash: Gaining Root Access to Your Network PowerPoint ...
关于Windows RPC挖掘的那些事-先知社区
Live exploits intercepted for CVE-2017-0143
TrustedSec | RPC Programming for the Aspiring Windows Developer
浅谈 windows 命名管道-腾讯云开发者社区-腾讯云
Security Issue due to lsass handle · Issue #29 · zeronetworks ...
AD攻防-域用户HashDump追踪之道-腾讯云开发者社区-腾讯云
Windows 内でRPC を守る機能| Akamai
Windows 10 KB5039211 adds a new feature (direct download links)
网络流矩阵
Beyond Memory Corruption Vulnerabilities – A Security Extinction and ...
windbg - at the rpcrt4!NdrClientCall2 function - how does it know which ...
HTB: Cicada Walkthrugh
Обновление KB5039236 (Build 25398.950) для Windows Server, версия 23H2
Detection details of QID 90081 (Default Windows Administrator Account ...
NTLM coercion атаки 2026: .lnk, WebDAV и обход signing
Golden dMSA: What Is dMSA Authentication Bypass? | Semperis Research
Pháp y kỹ thuật số: Phần 3 - Network Forensics (tiếp) - QuanTriMang.com
The PetitPotam Story - K7 Labs
Rapid7 Analysis: CVE-2023-38548
TryHackMe-VulnNet: Roasted-腾讯云开发者社区-腾讯云
Windows RPC应用详解 - zha0gongz1 - 博客园
Pwning Reflection Using NTLM Reflection | serioton
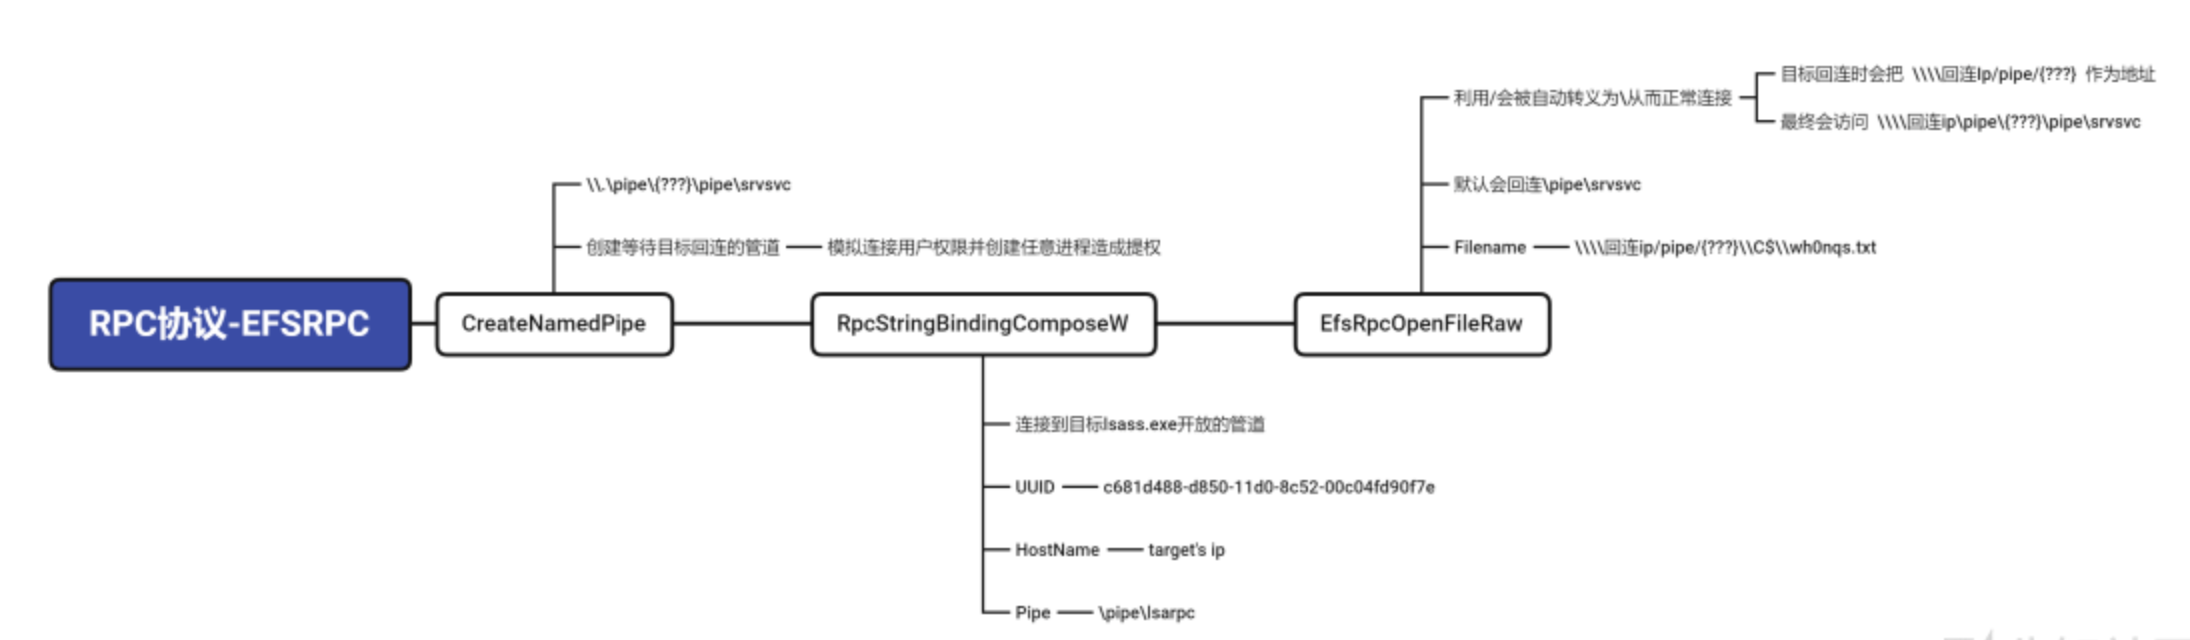
CS中继-EFSRPC调用-网盾安全培训
Кто выпустил гончую. Ищем следы коллекторов BloodHound в логах Windows ...
[bug] SMB SessionError: STATUS_PIPE_DISCONNECTED · Issue #12 ...
How PetitPotam hijacks the Windows API, and what you can do about it ...
windows RPC学习
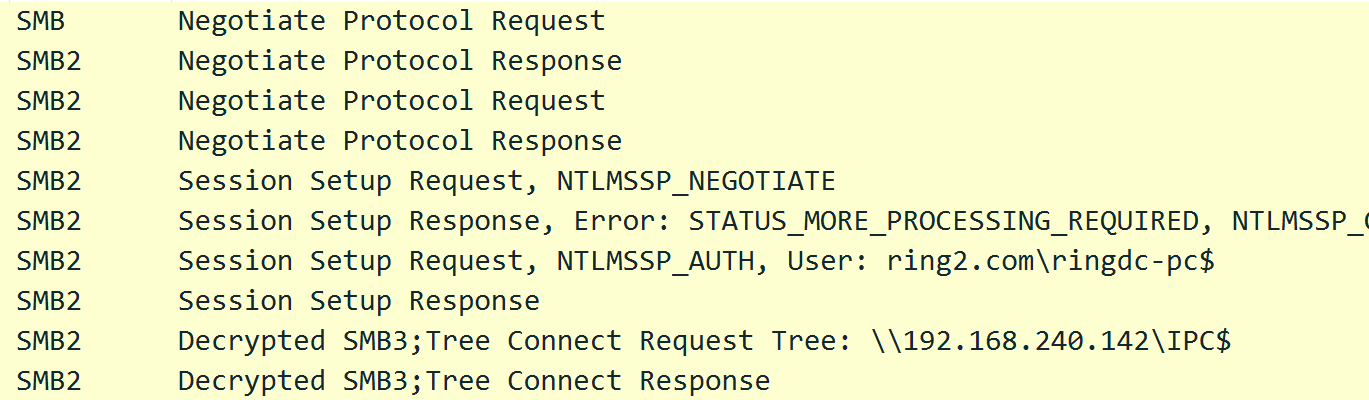
SMB | The Pentester's Best Friend
What makes anonymous pipes?
MS-RPC와 그 보안 메커니즘에 관한 개요 | Akamai
Error code: 0xC000003A STATUS_OBJECT_PATH_NOT_FOUND when ...
What Is An SMB Port + Ports 445 And 139 Explained
2024年6月のWindows Update - treedown’s Report
ISE(Identity Service Engine) 및 AD(Active Directory) 이해 - Cisco
Active Directory Recon 101 | PDF
Overview of BloodHound and Associated Collectors | Cato Networks
InSecure Remote Operations - NullCon 2023 by Yossi Sassi | PDF
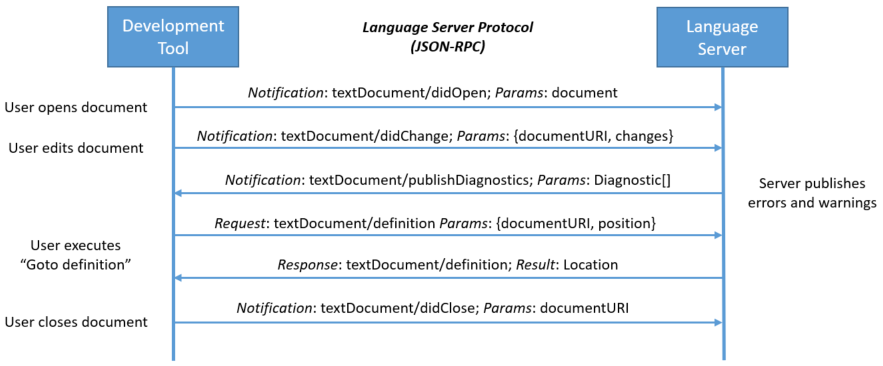
LSP for Swift | Yusuke Ohashi
Fix: LSA is Unable to Obtain an RPC Connection