Showing 120 of 120on this page. Filters & sort apply to loaded results; URL updates for sharing.120 of 120 on this page
Detecting reflective DLL loading with Windows Defender ATP | Microsoft ...
GitHub - DymOK93/ReflectiveLoader: An example of reflective DLL loading ...
How reflective DLL loading helps with Red Teaming | AHMED . posted on ...
Hardening an Adaptix C2 agent DLL with reflective loading evasion Part ...
Explaining Reflective DLL Injection in 2 min - by Miss Smurfette - YouTube
악성코드로 알아보는 Reflective DLL Injection - Security & Intelligence 이글루코퍼레이션
Rewriting the Reflective DLL Loader: A Walkthrough | IliasCyber
GitHub - S12cybersecurity/Reflective-DLL: Reflective DLL Injection ...
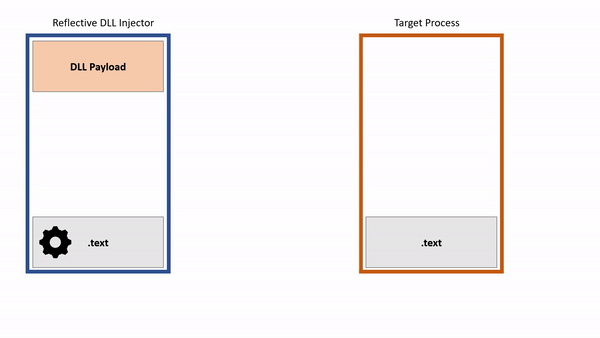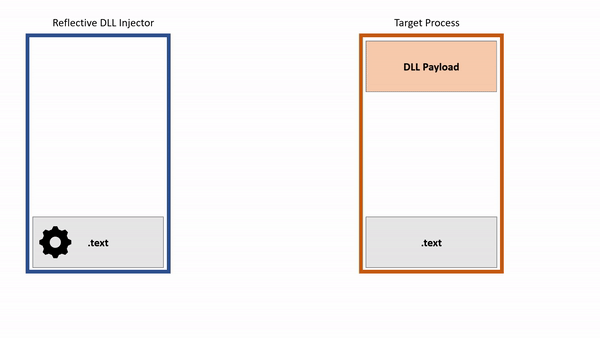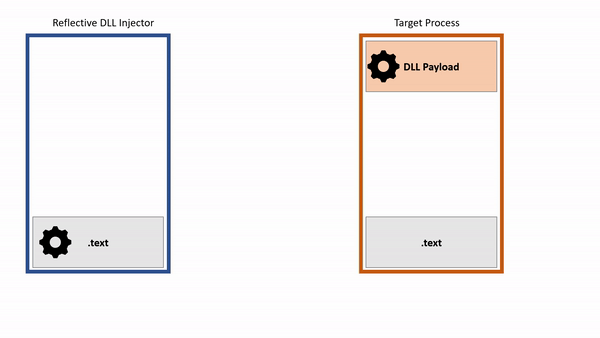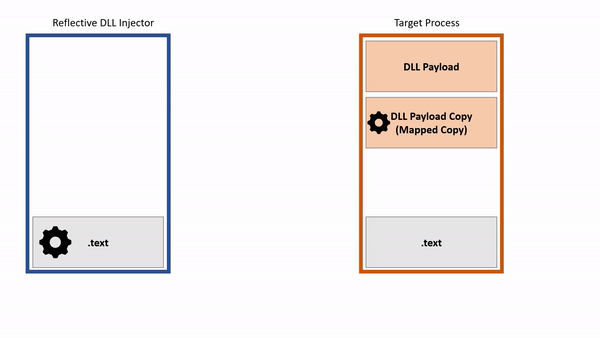
Introduction to Reflective DLL Injection
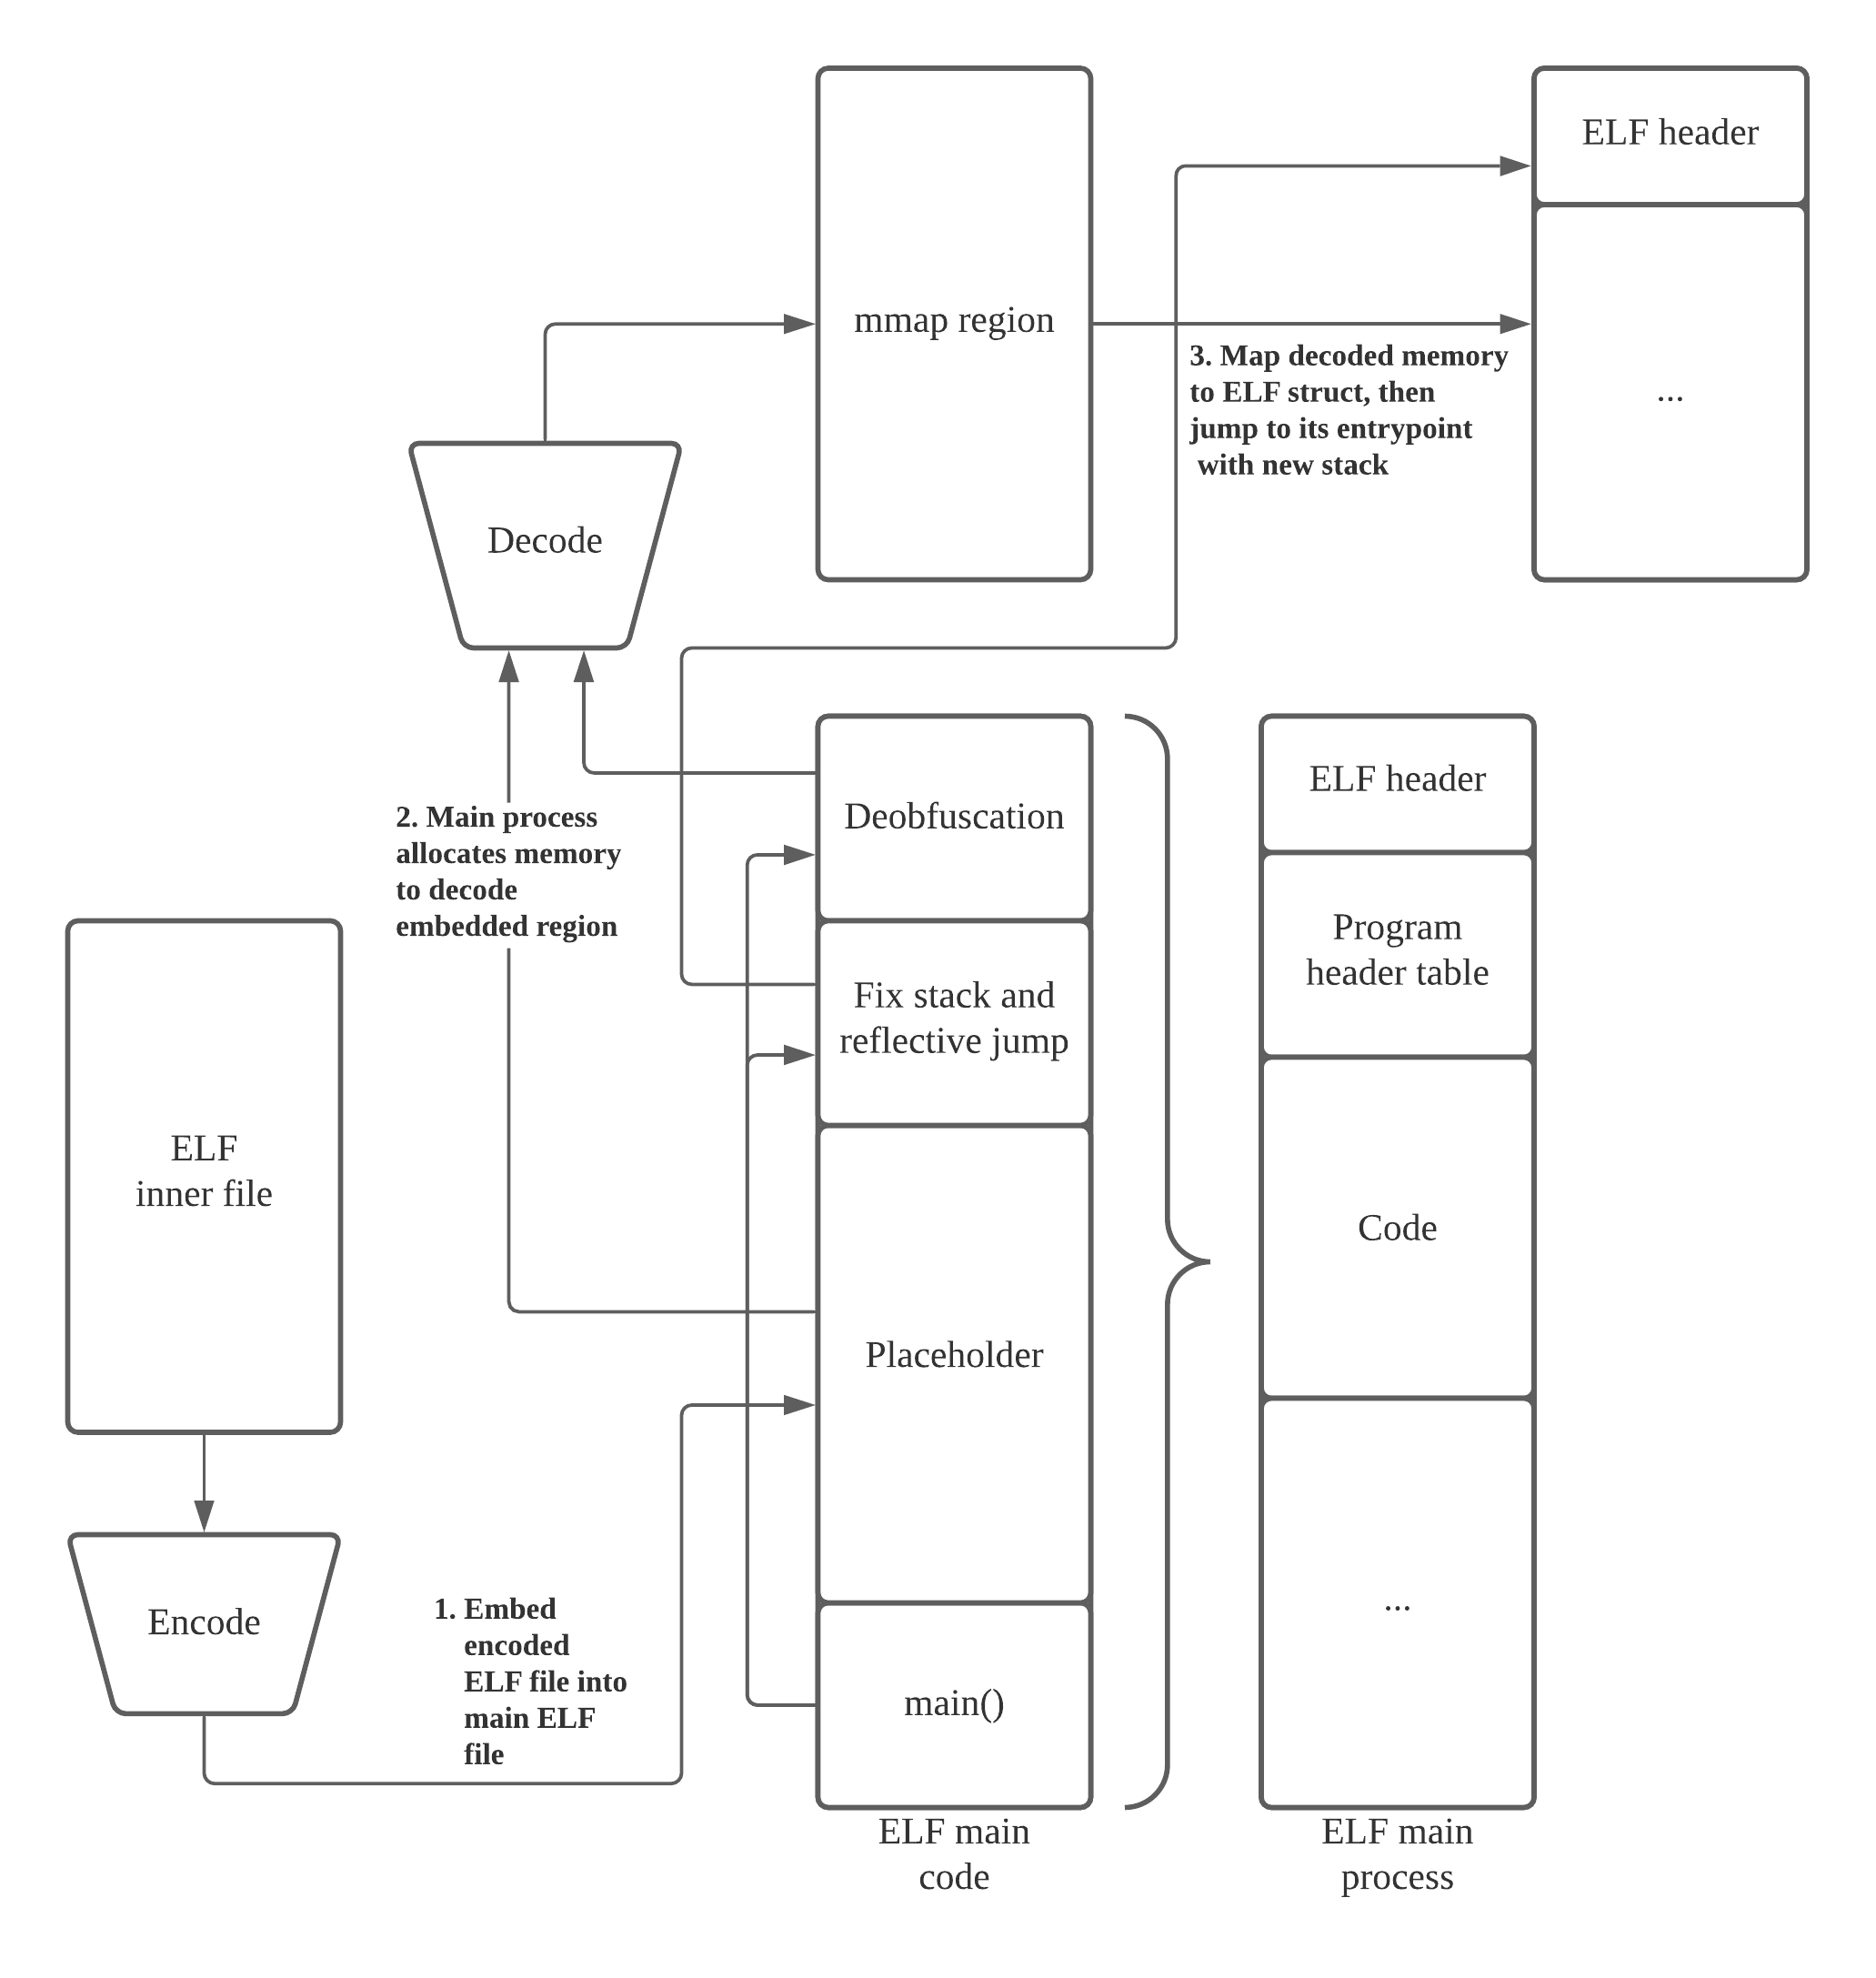
Linux Reflective Loading
Reflective DLL Injection
Reflective DLL Injection In C++ | Depth Security
All I Want for Christmas is Reflective DLL Injection :: Vincenzo — Blog
Reflective Loading Process | stephenfewer/ReflectiveDLLInjection | DeepWiki
Upgrade your DLL to Reflective DLL – Security Café
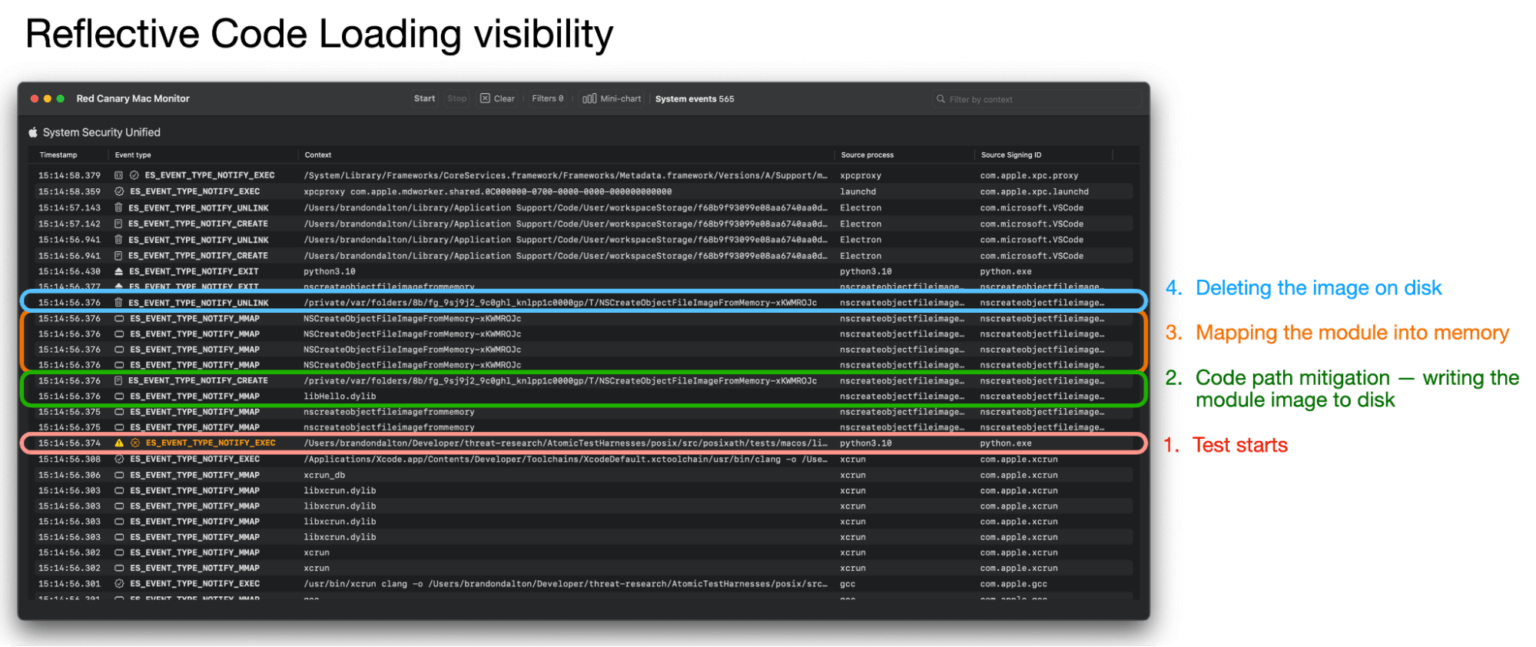
Reflective Code Loading - Red Canary Threat Detection Report
GitHub - stephenfewer/ReflectiveDLLInjection: Reflective DLL injection ...
5.2 Shellcode Reflective DLL Injection | PDF
Reflective DLL injection and bootstrapping in C - 0xflux Red Team ...
What is Reflective DLL injection?
Reflective DLL Injection - Jake McLellan - YouTube
Reflective DLL Injection In The Wild - ThreatSpike
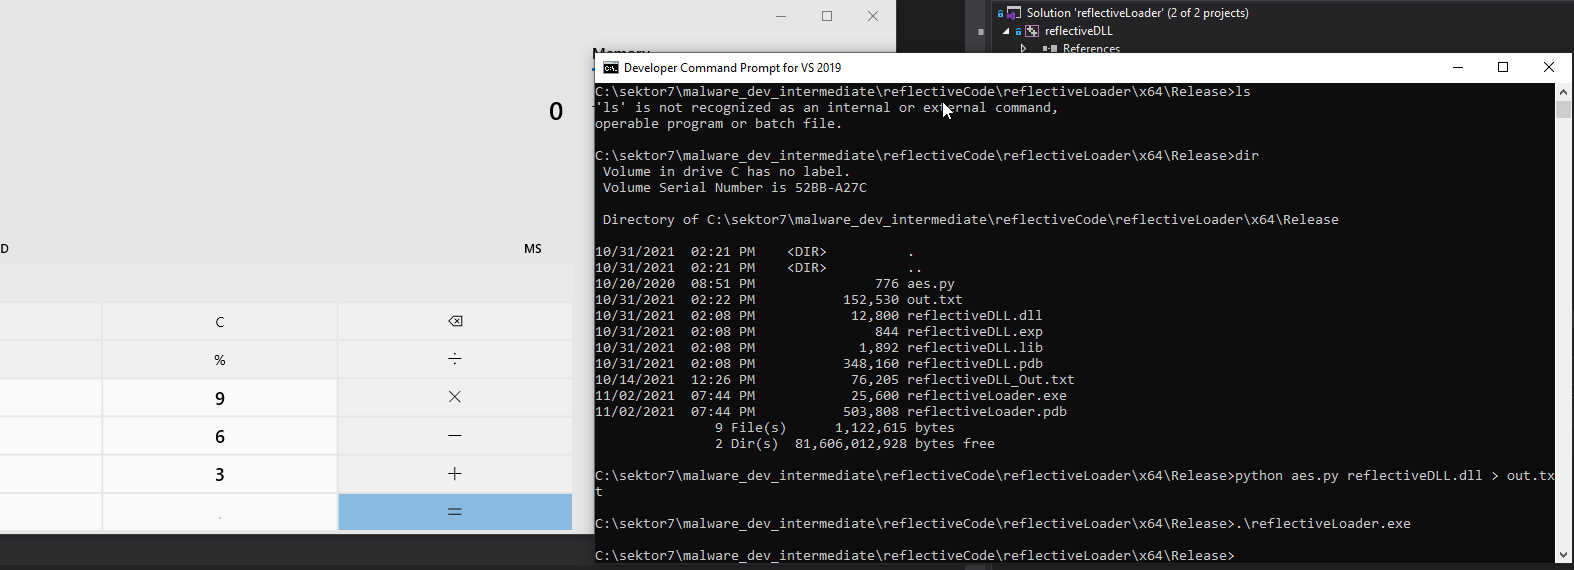
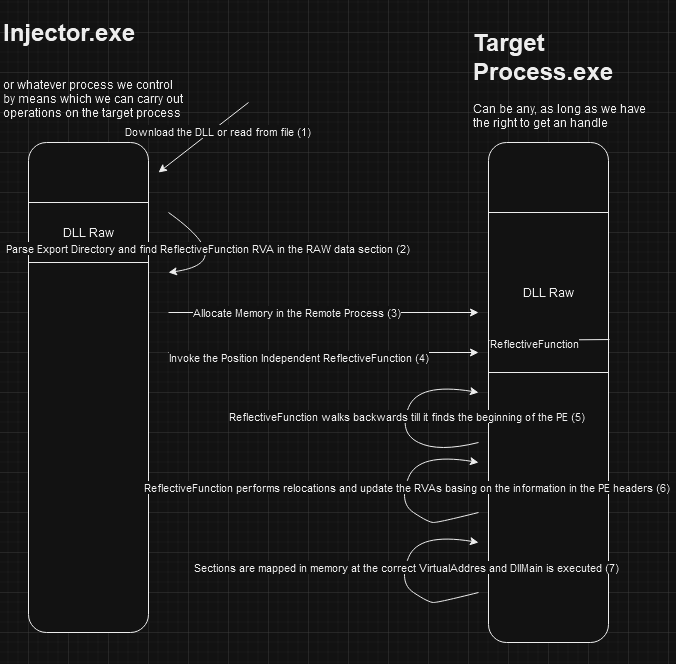
GitHub - oldboy21/RflDllOb: Reflective DLL Injection Made Bella · GitHub
Reflective DLL Injection | Red Team Notes
Reflective DLL Injection: Theory & Practice · ROBINX0
[Day4] DLL Loading - iT 邦幫忙::一起幫忙解決難題,拯救 IT 人的一天
“Enhancing Your Red Teaming Capabilities with BOF and Reflective DLL ...
Reflective DLL Injection. Welcome to this new Medium post, today… | by ...
GitHub - 0xTriboulet/rdll-rs: A reflective DLL development template for ...
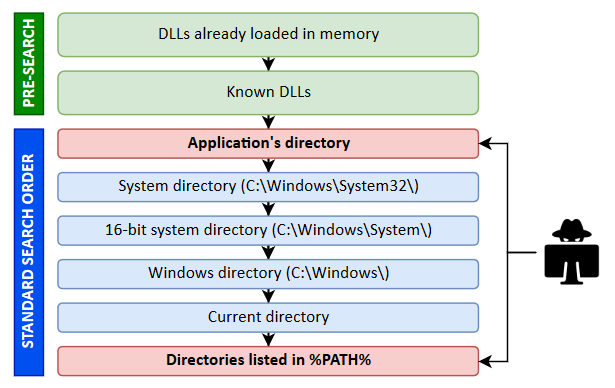
DLL Side Loading - Twelvesec
Reflective DLL Injection | Red Teaming Experiments
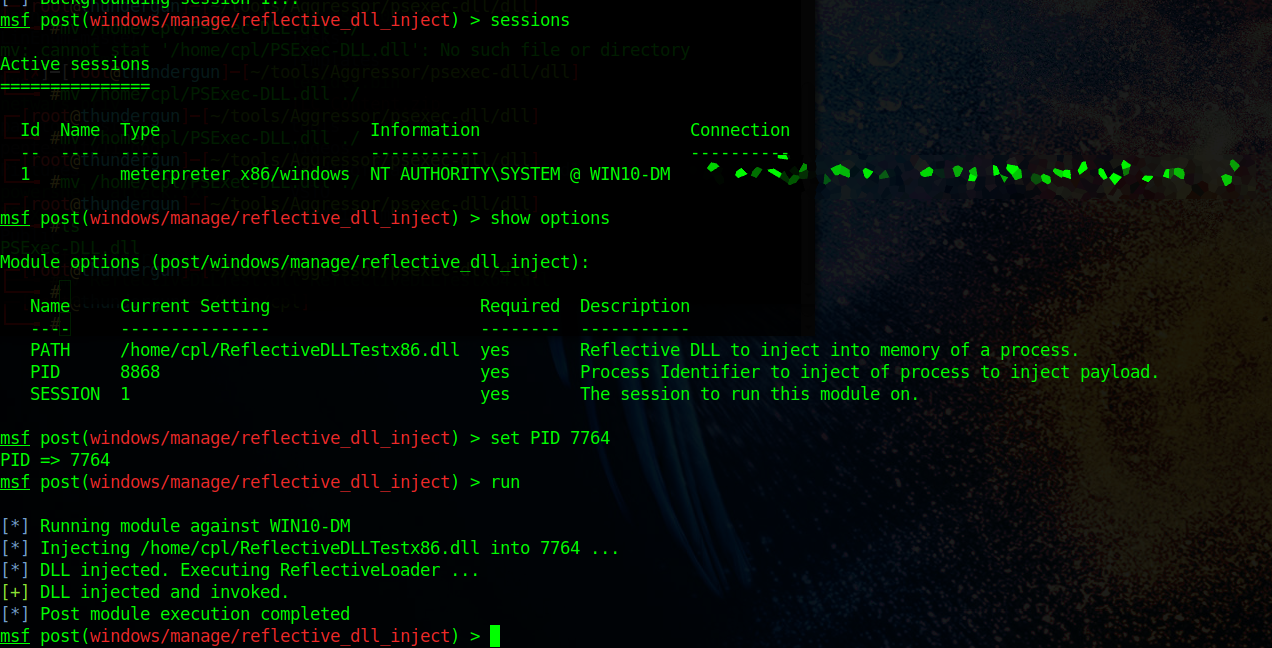
Reflective DLL Injection Metasploit Module - YouTube
Reflective DLL Injection · GitBook
Reflective Dll Injection Explained in 10 Minutes |Video Tutorial ...
NoEscape Ransomware Uses Reflective DLL Injection Tactics
USO DE INYECCIÓN DE REFLECTIVE DLL PARA ESTAR INDETECTABLE A ANTI VIRUS ...
GitHub - r3nhat/XORedReflectiveDLL: Reflective DLL Injection with ...
Reflective Dll Injection - Dll Injection - 600x339 PNG Download - PNGkit
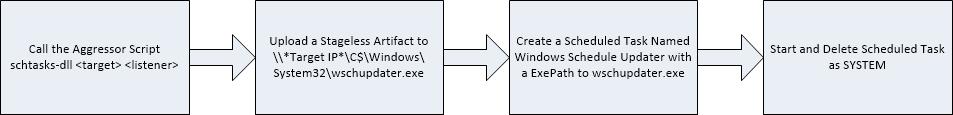
Schtasks without Schtasks.exe via Reflective DLL – ijustwannaredteam
Defining the Cobalt Strike Reflective Loader
המדריך למזריק המתחיל - Refelctive DLL Injection - מאמר חמישי ואחרון ...
Can x64 ReflectionLoader load x32 dll into x32 process? · Issue #20 ...
GitHub - patsanchique/Reflective-DLL-Injection-Loader: Inject DLL Data ...
Dll Injector Safe at Nancy Coyne blog
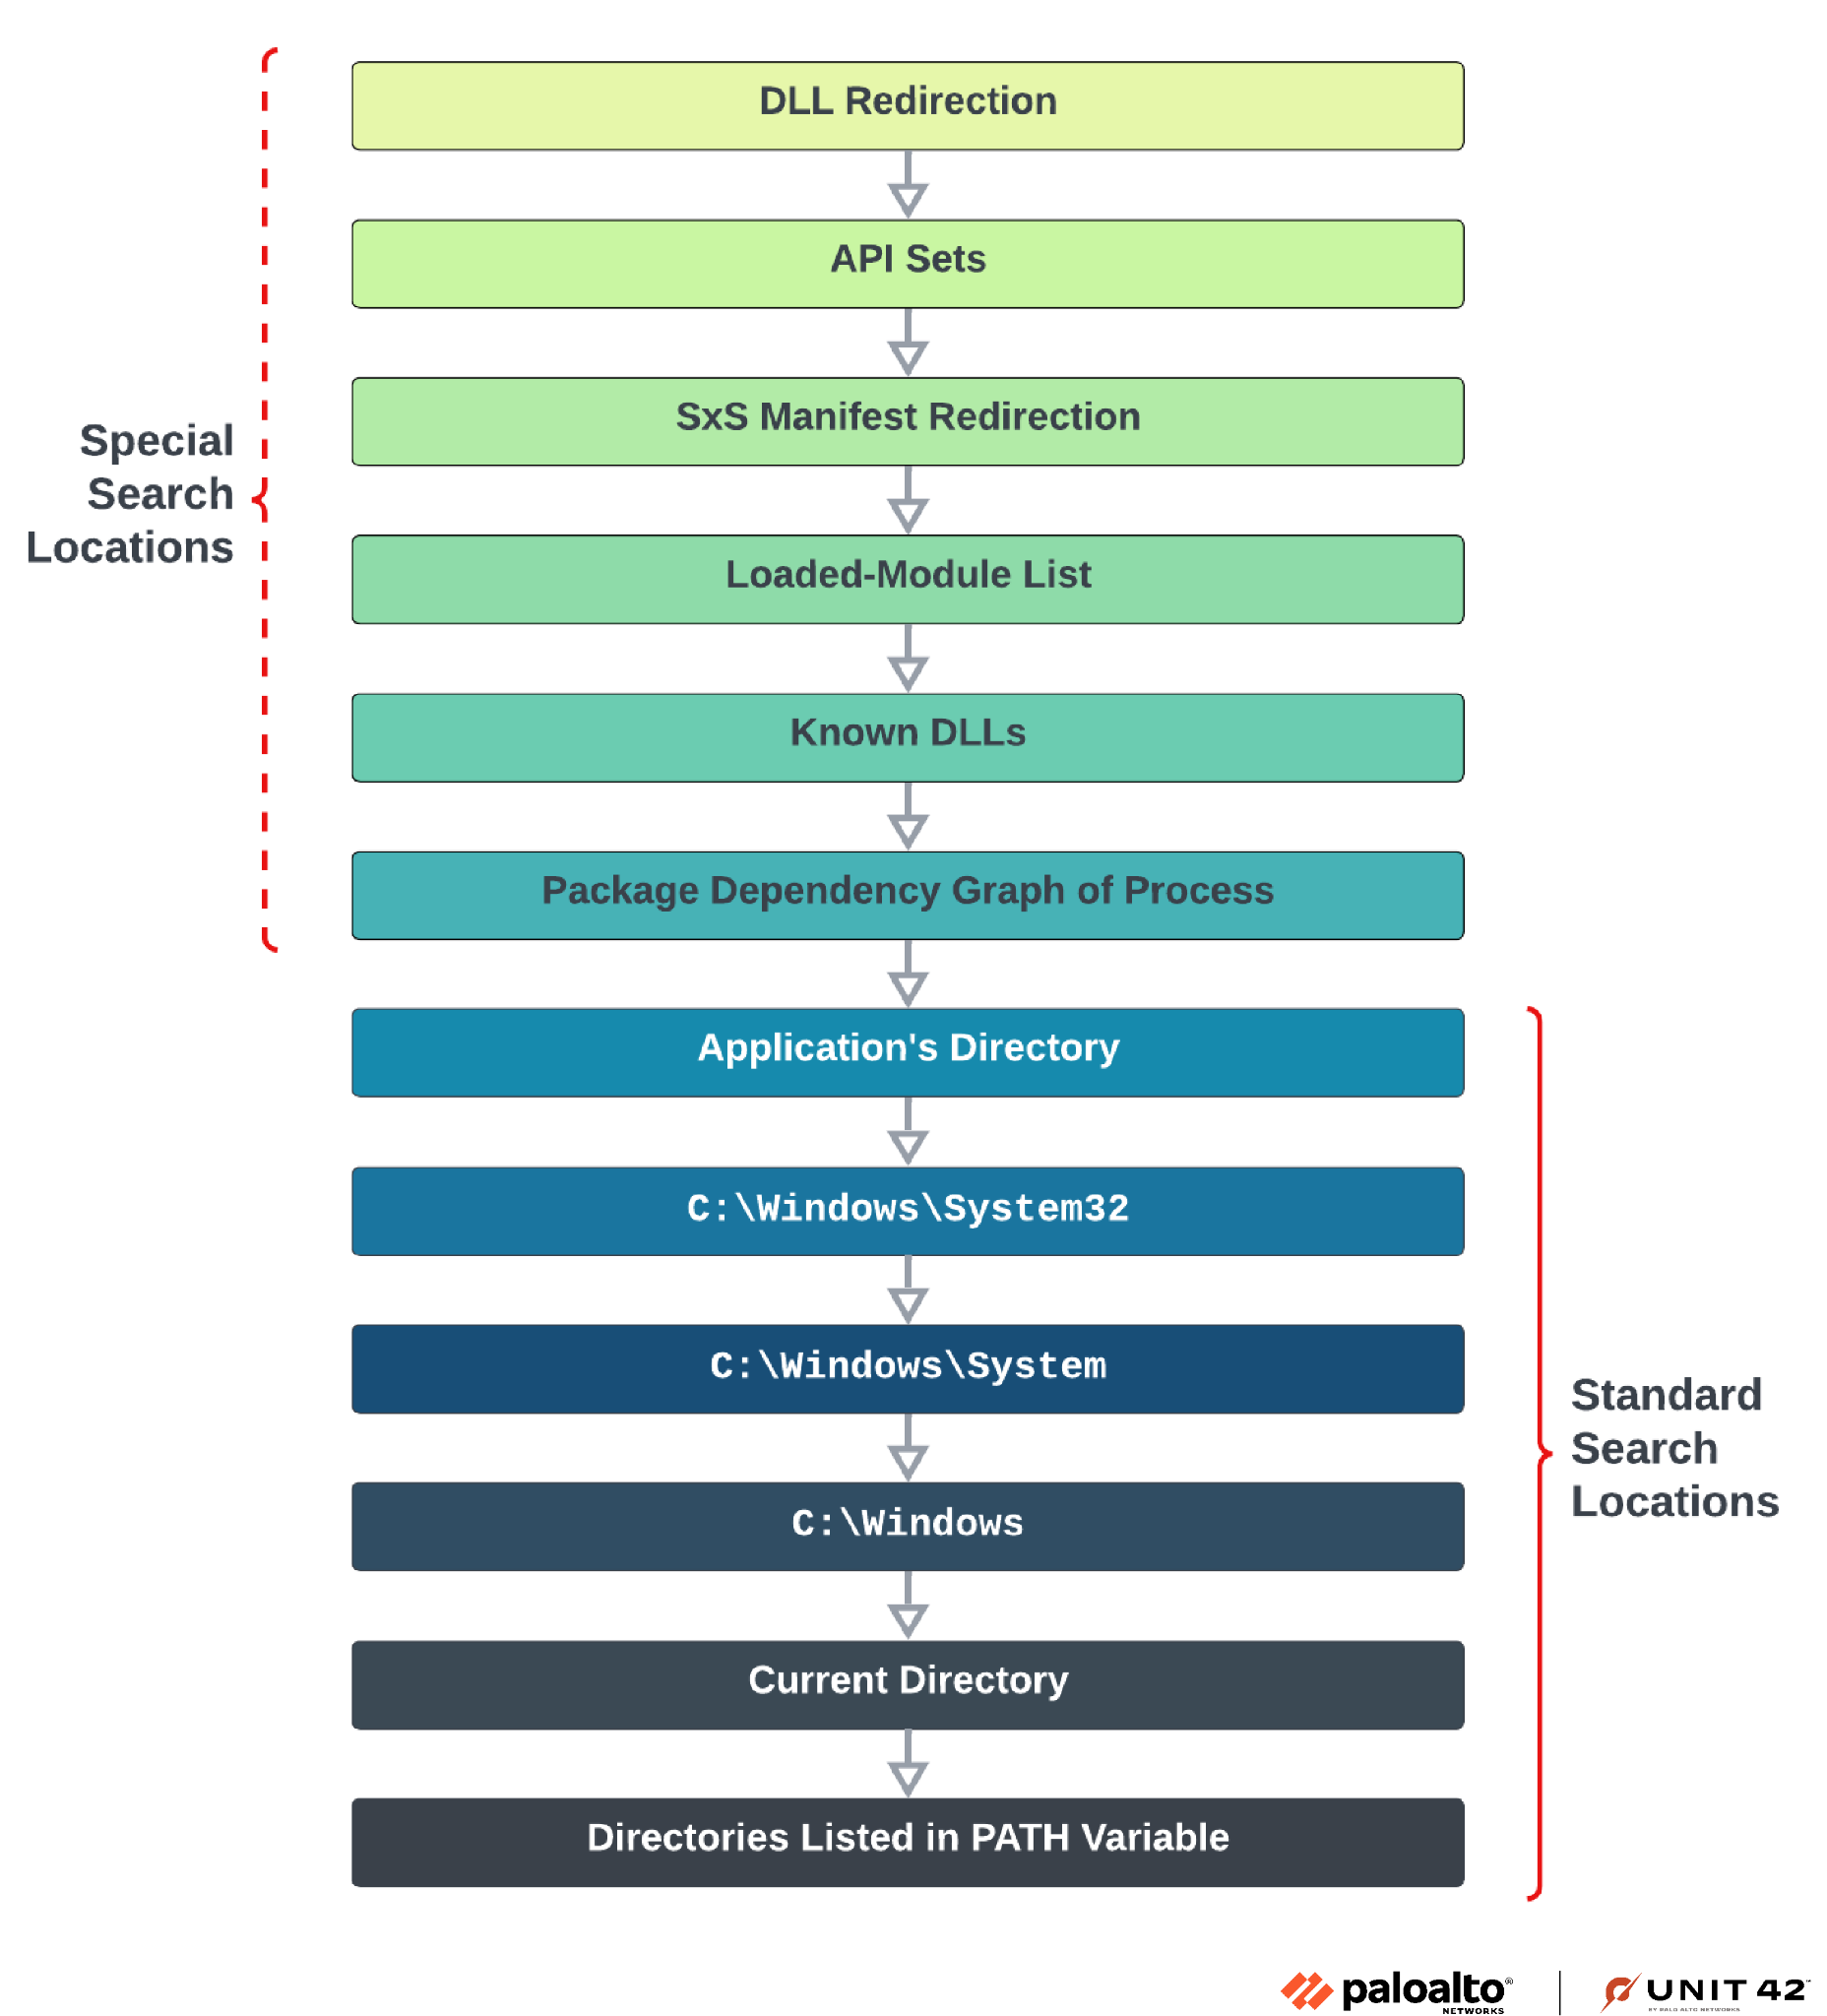
Intruders in the Library: Exploring DLL Hijacking
Reflective DLLs and You – ijustwannaredteam
User Defined Reflective Loader Part 1: Simplifying Development
DLL Hijacking PART 1: Search Order Hijacking - Security & Intelligence ...
DLL Proxying for Persistence - A Stealthy Technique – Der Benji ...
GitHub - OlivierLaflamme/cgo_ReflectedDLL
Learning Sliver C2 (11) - SpawnDLL | text/plain
Long Live The Shellcode | gatari's blog
[Day13] Dark LoadLibrary - iT 邦幫忙::一起幫忙解決難題,拯救 IT 人的一天
3つのEDRバイパス・テクニックとその回避策|Deep Instinct
Blog | Depth Security
Inyección reflejada de DLLs en Windows
PIC your malware | PDF
Cyberbit:某国际机场一半以上工作站都已被挖矿软件占领|NOSEC安全讯息平台 - 白帽汇安全研究院
ReflectiveLoading And ... | Winslow Blog
Objective-See's Blog
ProcessInjectionTechniques — Offensive-Panda
GitHub - reveng007/ReflectiveNtdll: A Dropper POC with a focus on ...
Aeternum Loader: Inside the binary - Ctrl-Alt-Intel
GitHub - Allevon412/ReflectiveDLLInjector: This program is used to ...
PDFSIDER Malware Actively Used by Threat Actors to Bypass Antivirus and ...
Shell is coming ...: reflectPatcher.py: python script to patch your ...
detecting-reflective-dll-loading-with-windows-defender-atp
Golang y CGO: Artemis 0x1 | synawk
ReflectiveDLLInjection变形应用 | idiotc4t's blog
Bypassing EDR in a Crystal Clear Way | Lorenzo Meacci
ProxyShellMiner Campaign Creating Dangerous Backdoors
Penetration Testing Lab – Offensive Techniques & Methodologies
ProcessHollowing与ReflectiveDLL | Z3ratu1's blog
How are DLLs Loaded in Windows? Fortect
ReflectiveNtdll/1.Encrypt_shellcode at main · reveng007/ReflectiveNtdll ...
When Access Brokers Go Interactive: ClickFixin’ to… | Binary Defense
一种Reflective DLL注入后的DLL卸载处理_reflectivedllinjection-CSDN博客
BlueHat v18 || Memory resident implants - code injection is alive and ...