Showing 120 of 120on this page. Filters & sort apply to loaded results; URL updates for sharing.120 of 120 on this page
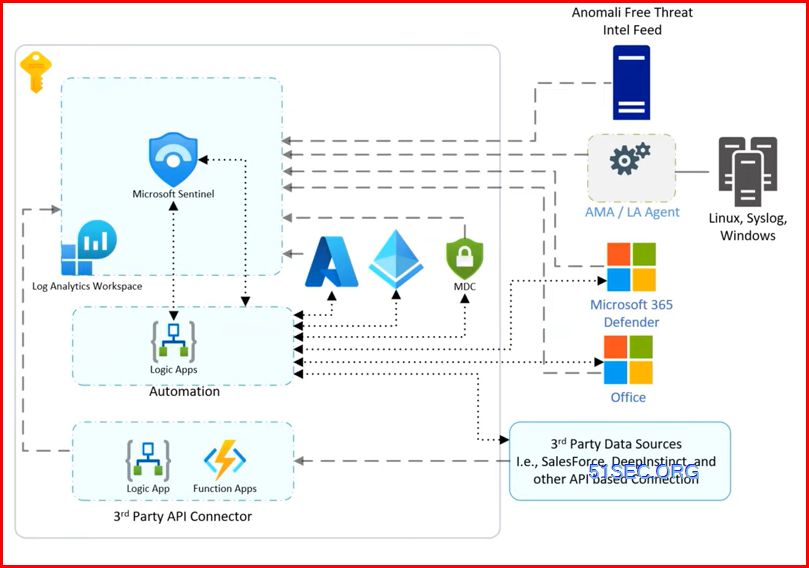
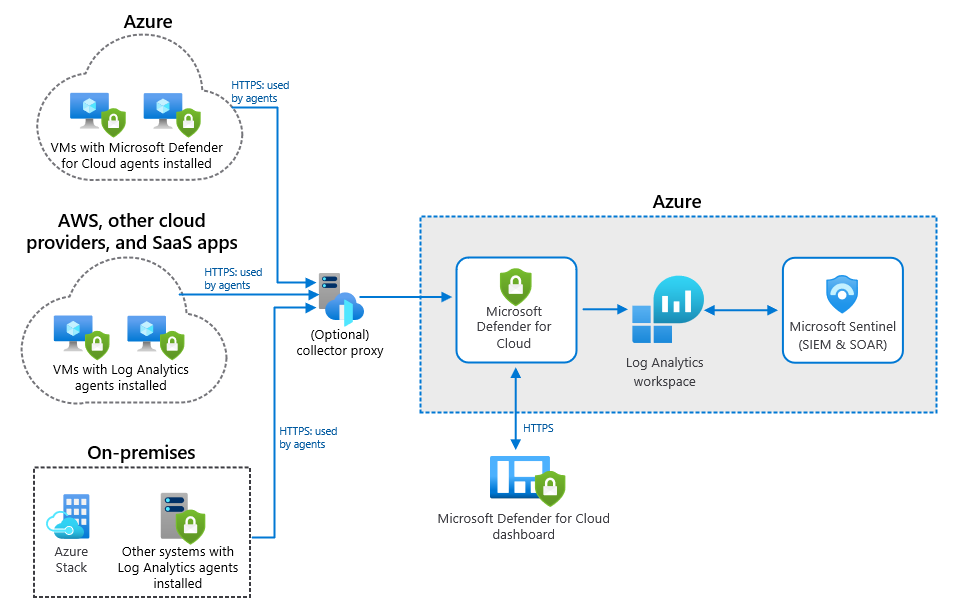
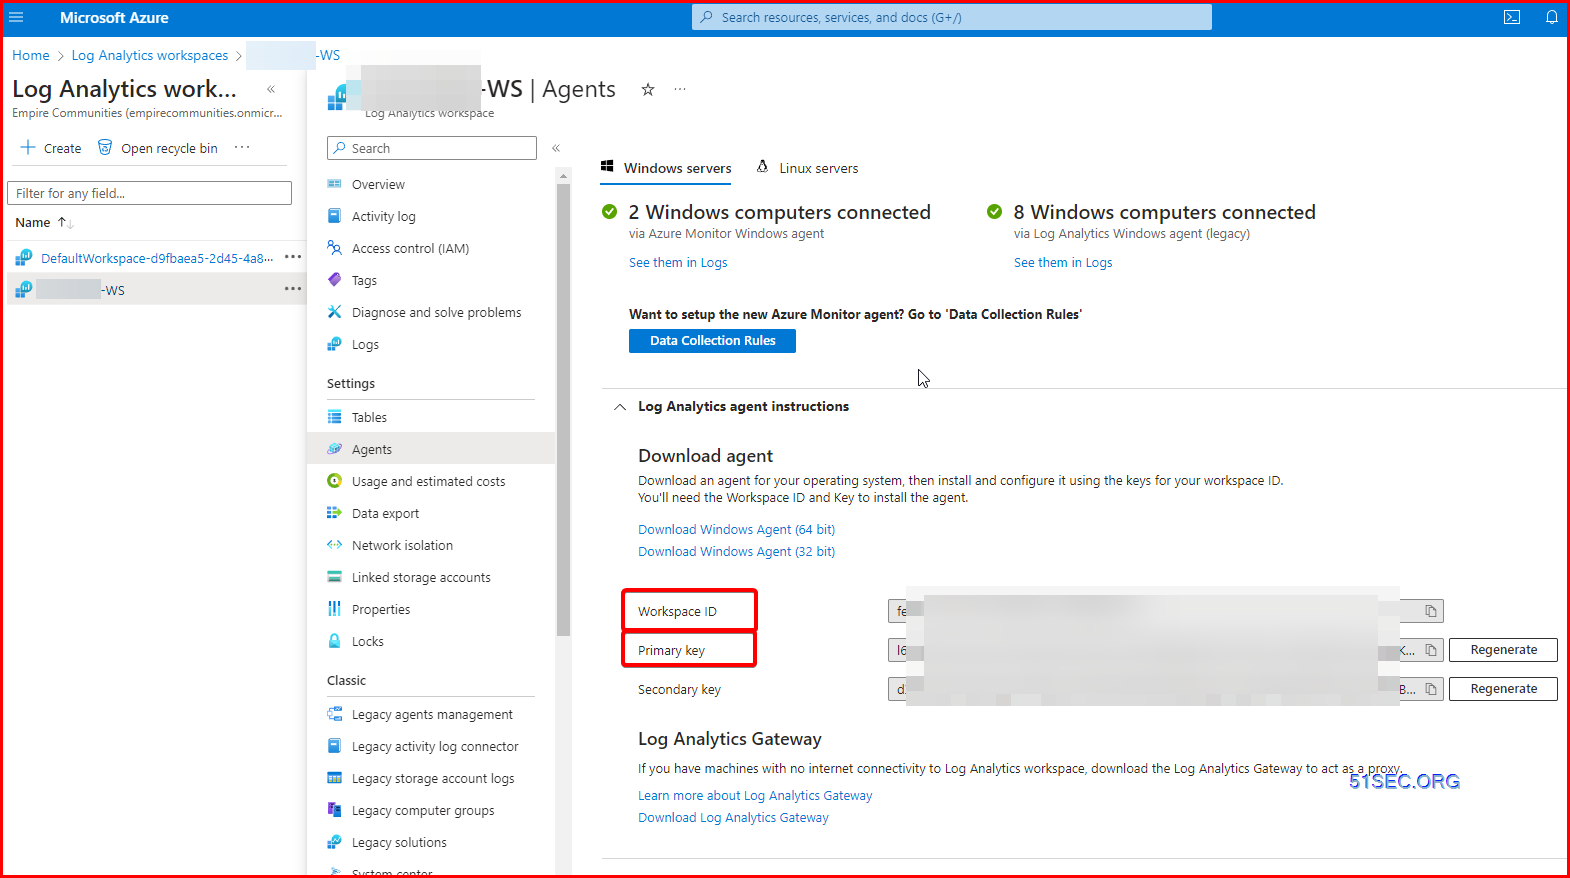
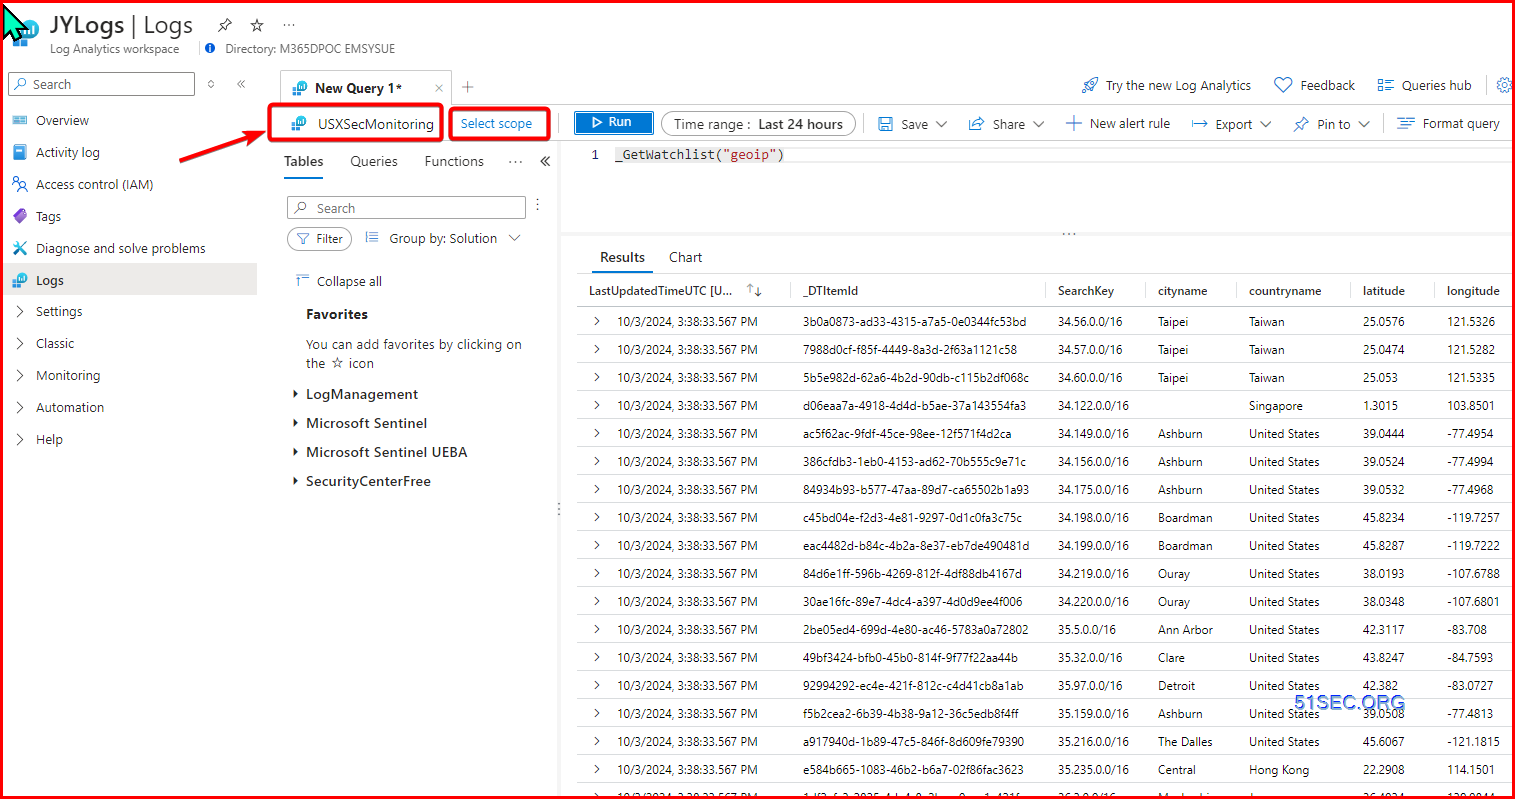
Azure Sentinel Onboarding All Kinds Of Log Sources – 51 Sec
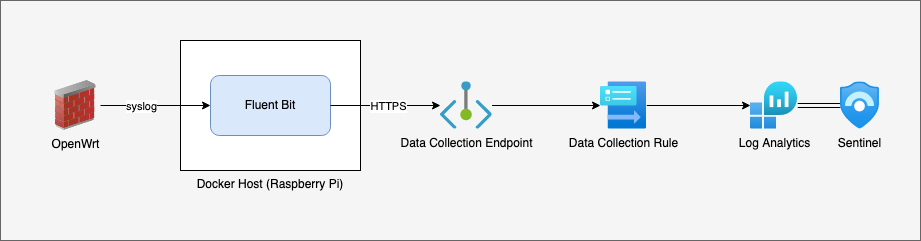
Set Up HTTPS Log Forwarding to Microsoft Sentinel
Azure Sentinel Onboarding Different Log Sources - NetSec
Optimize Log Ingestion And Access In Microsoft Sentinel - CHARBEL ...
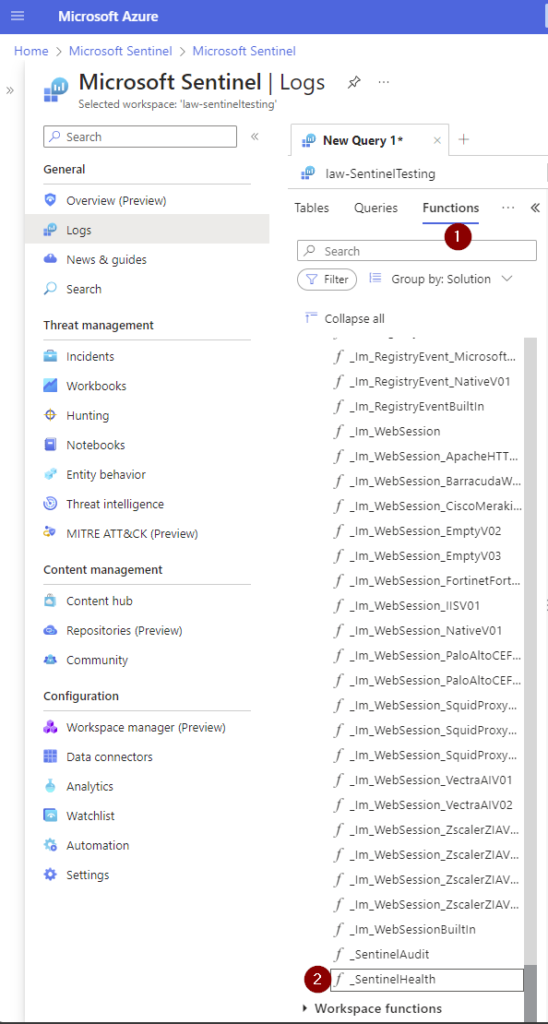
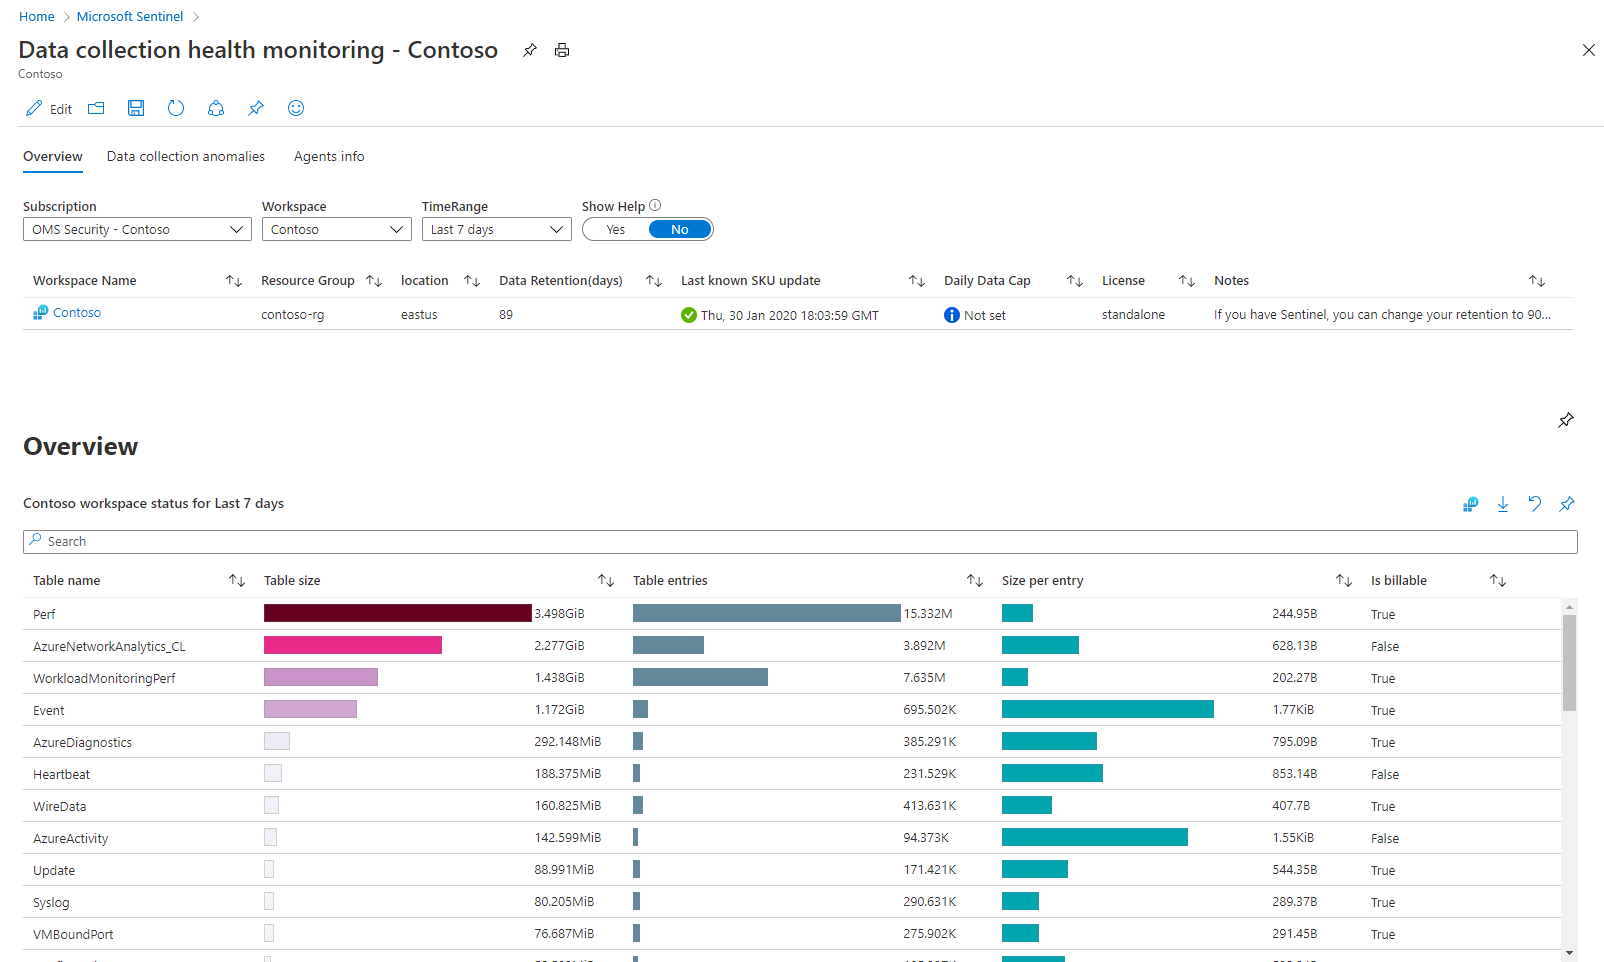
Monitor Microsoft Sentinel Data Connectors using Health Monitoring and ...
Sentinel Data Connector Health Monitoring – AzureTracks
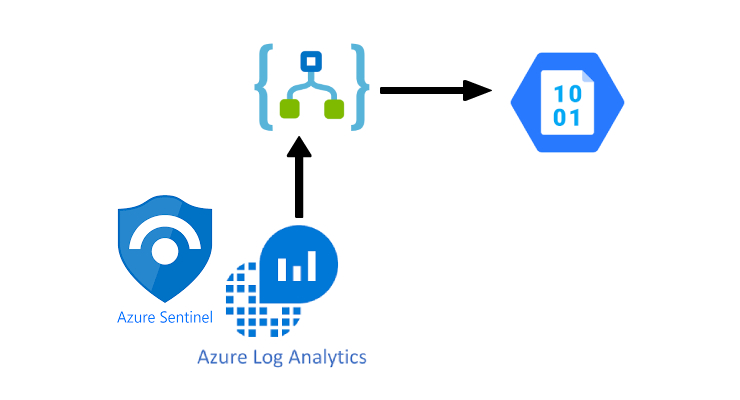
Optimize Microsoft Sentinel Log Retention With Azure Data Explorer ...
sk154872 - Microsoft Sentinel / Azure Log Analytics: Example ...
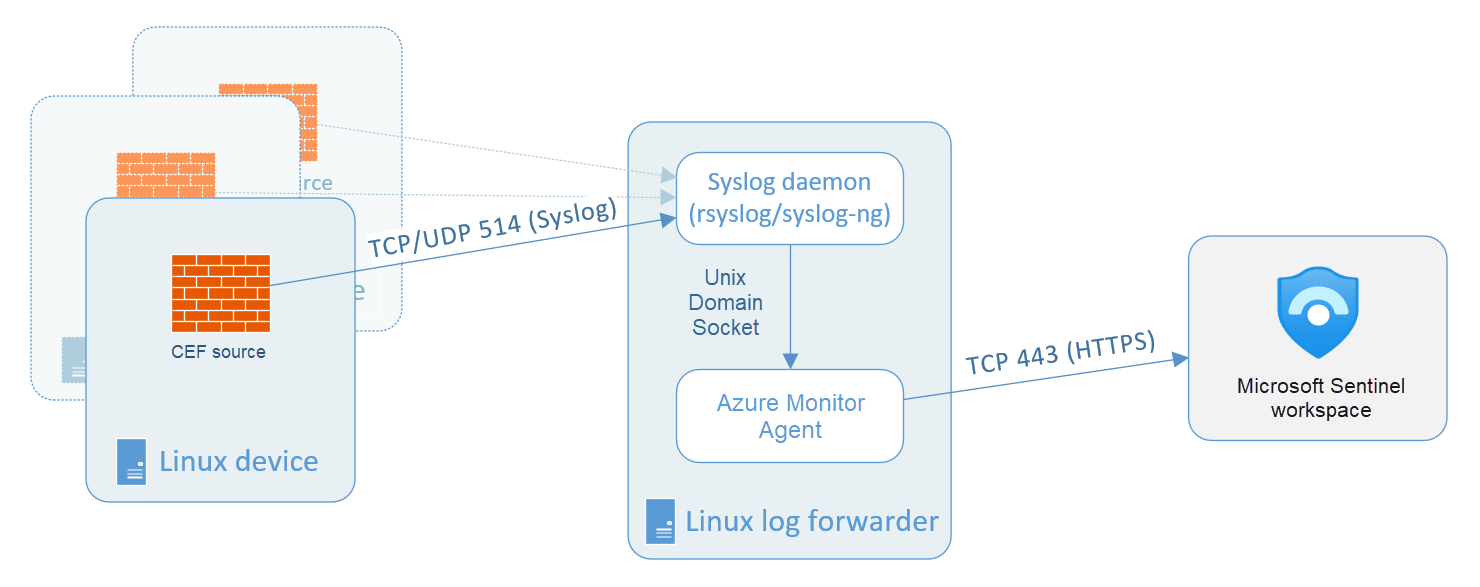
Sentinel Log Forwarder
Monitor Log Flow For Devices in Microsoft Sentinel 4
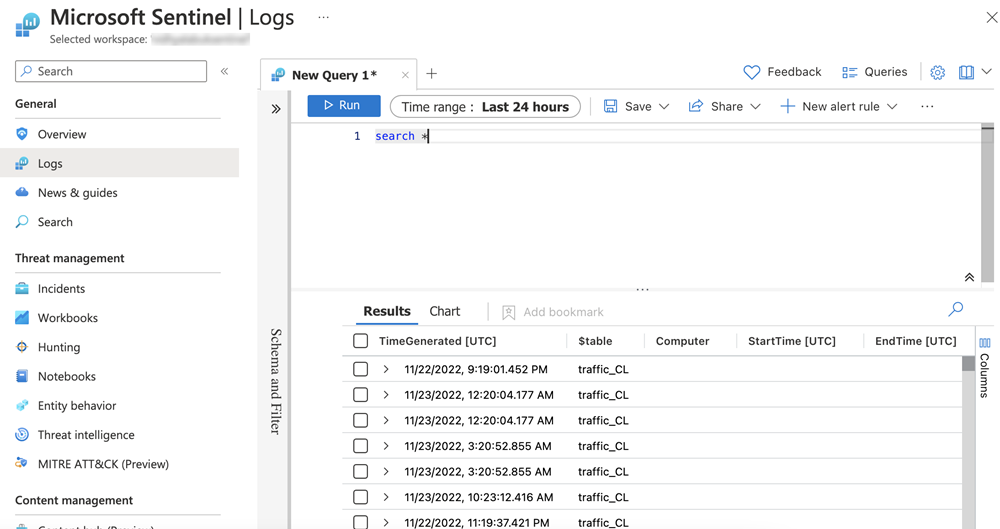
Azure Sentinel Log Analytics step-by-step
Monitor Log Flow For Devices in Microsoft Sentinel 8
Microsoft Sentinel monitoring & observability | Dynatrace Hub
Azure Sentinel Log Sources – Best practices for Microsoft Sentinel – EHNCA
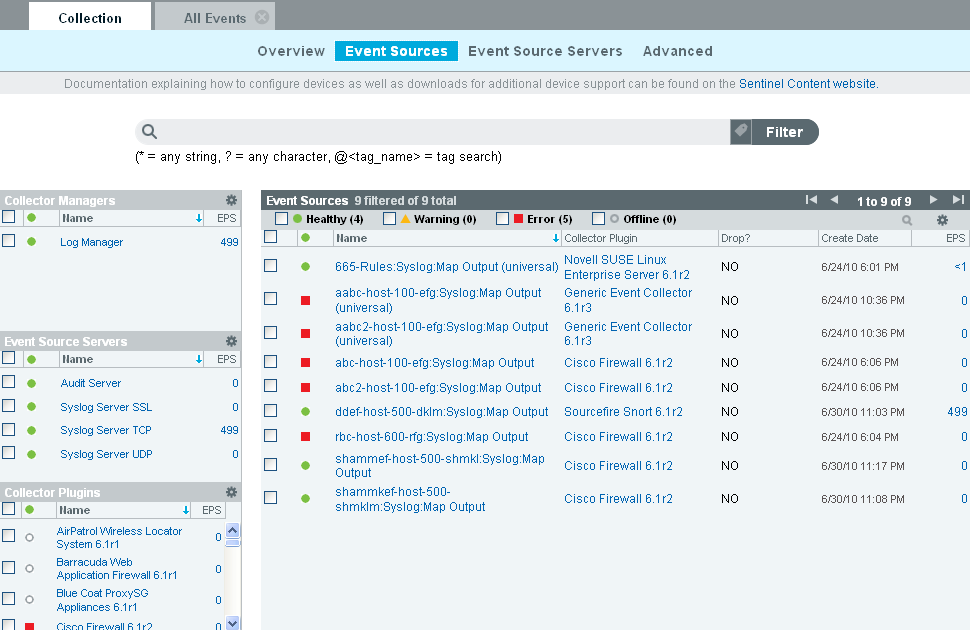
NetIQ Documentation: Sentinel Log Manager 1.0 Guide - Configuring Data ...
GitHub - BitNomad17/Azure-Sentinel-Monitoring: Microsoft Sentinel + Log ...
Log retention plans in Microsoft Sentinel | Microsoft Learn
Monitor Log Flow For Devices in Microsoft Sentinel 1
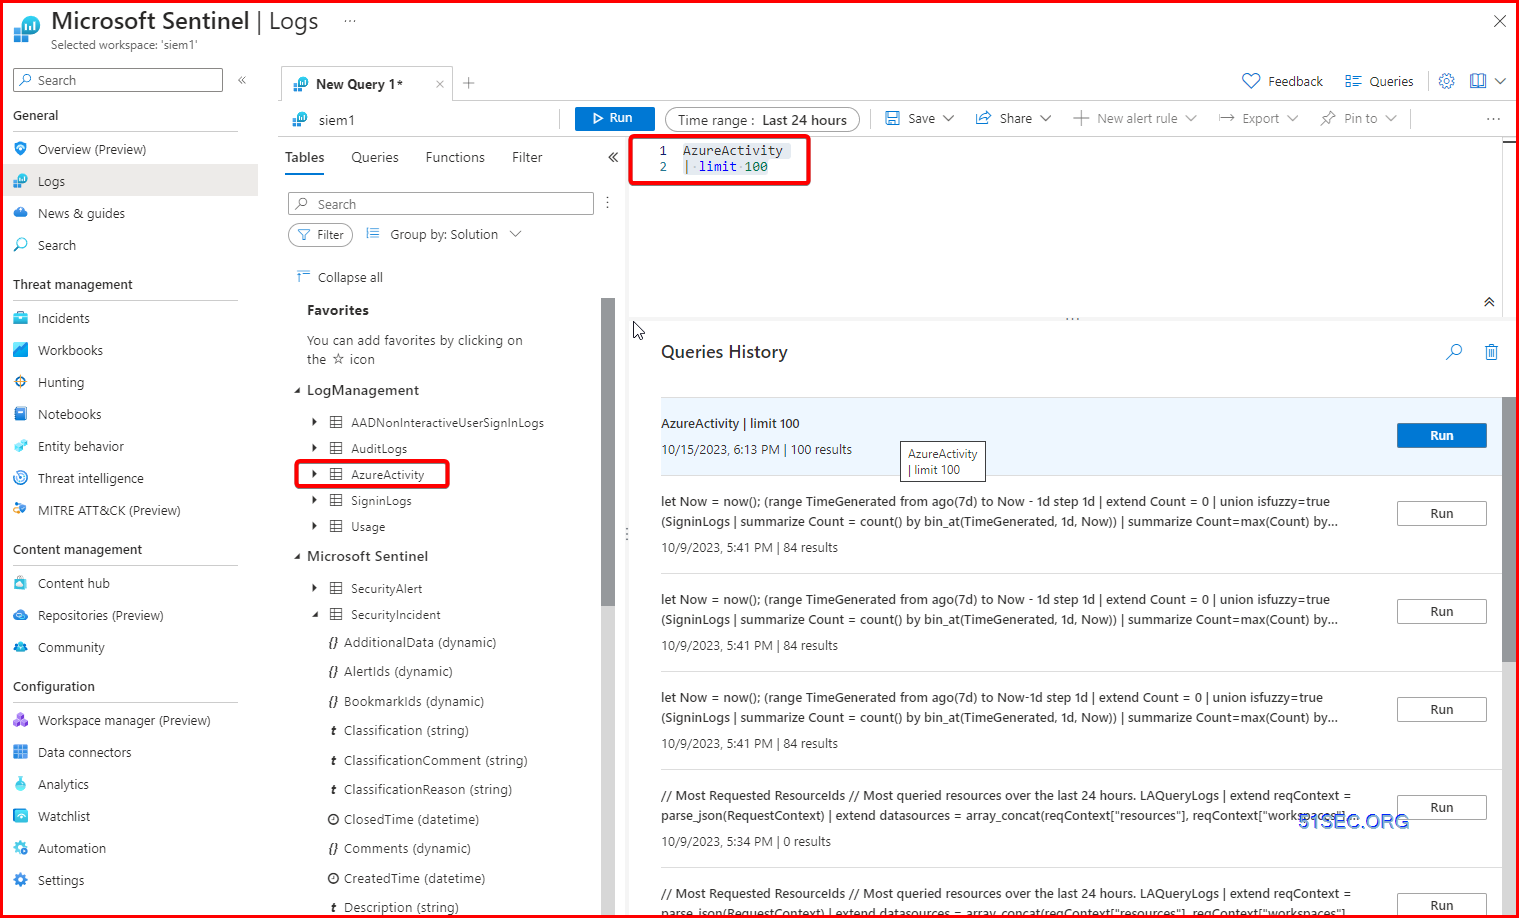
Microsoft Sentinel Activity Log – FXOECZ
NetIQ Documentation: Sentinel Log Manager 1.1 Administration Guide ...
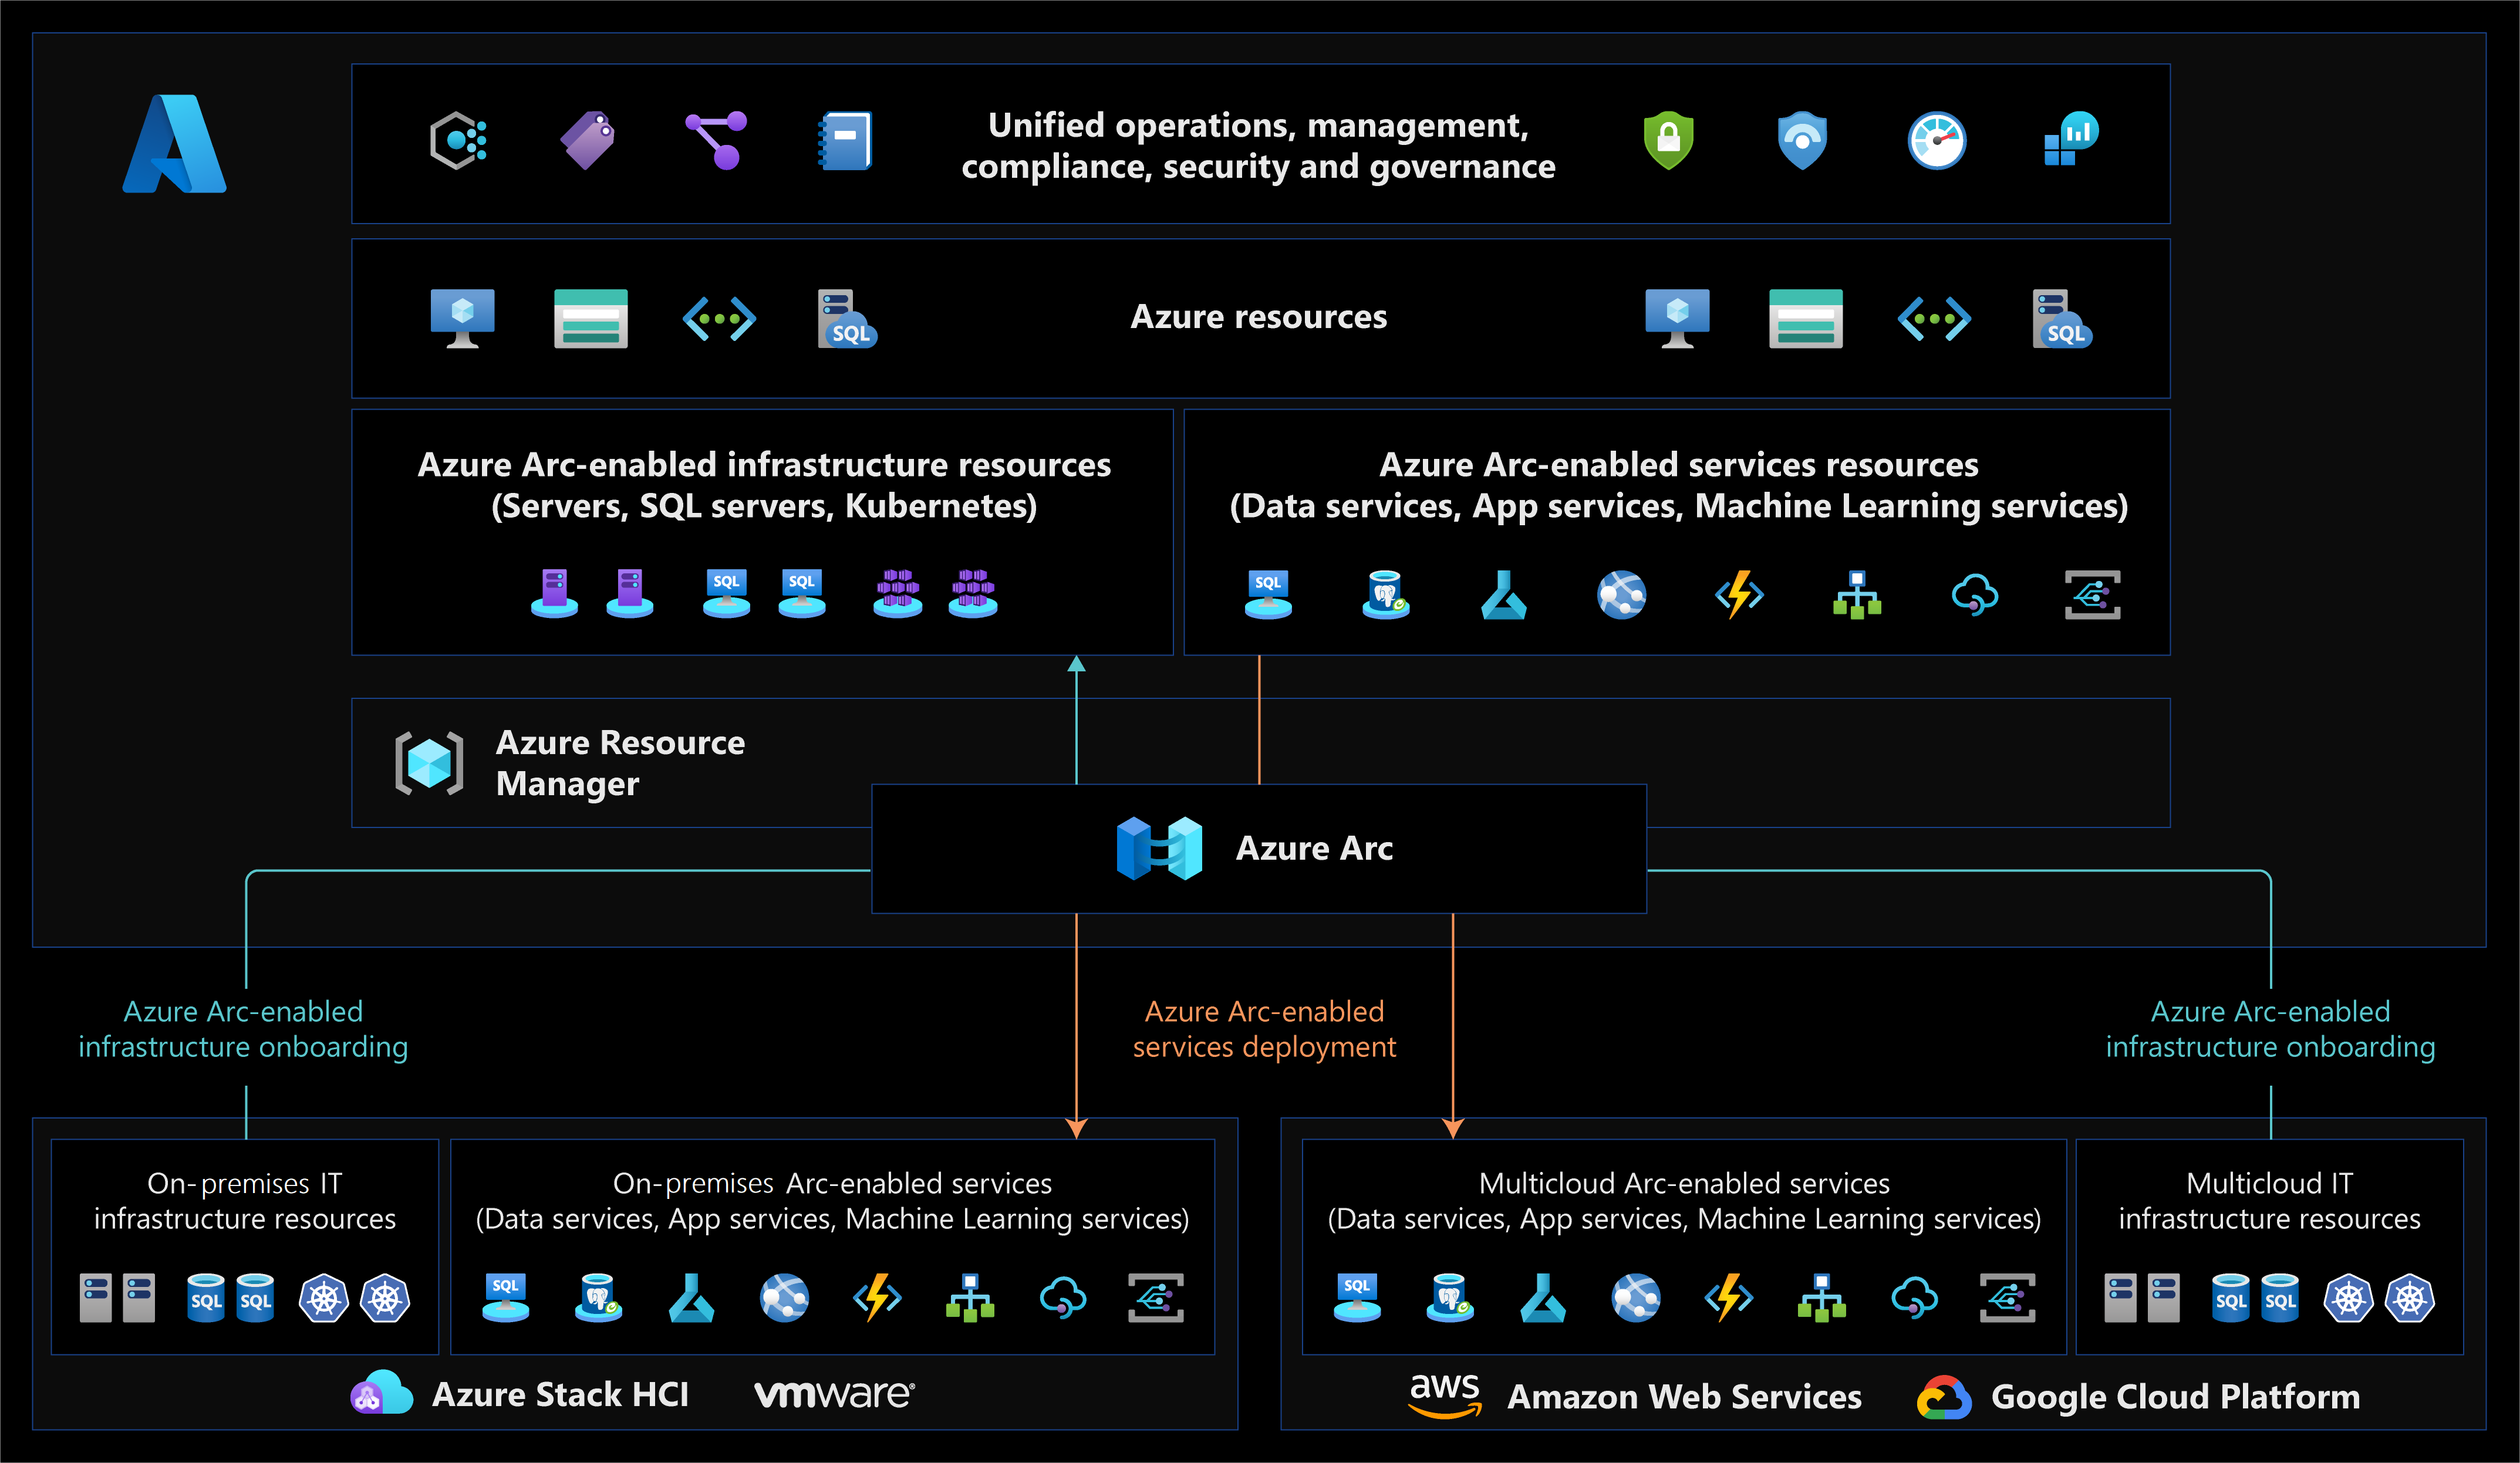
Microsoft Sentinel + Azure Arc: attivare la raccolta degli audit log ...
Azure Sentinel Log Query Scripts Collection : KQL (Kusto Query Language ...
Monitor Log Flow For Devices in Microsoft Sentinel 10
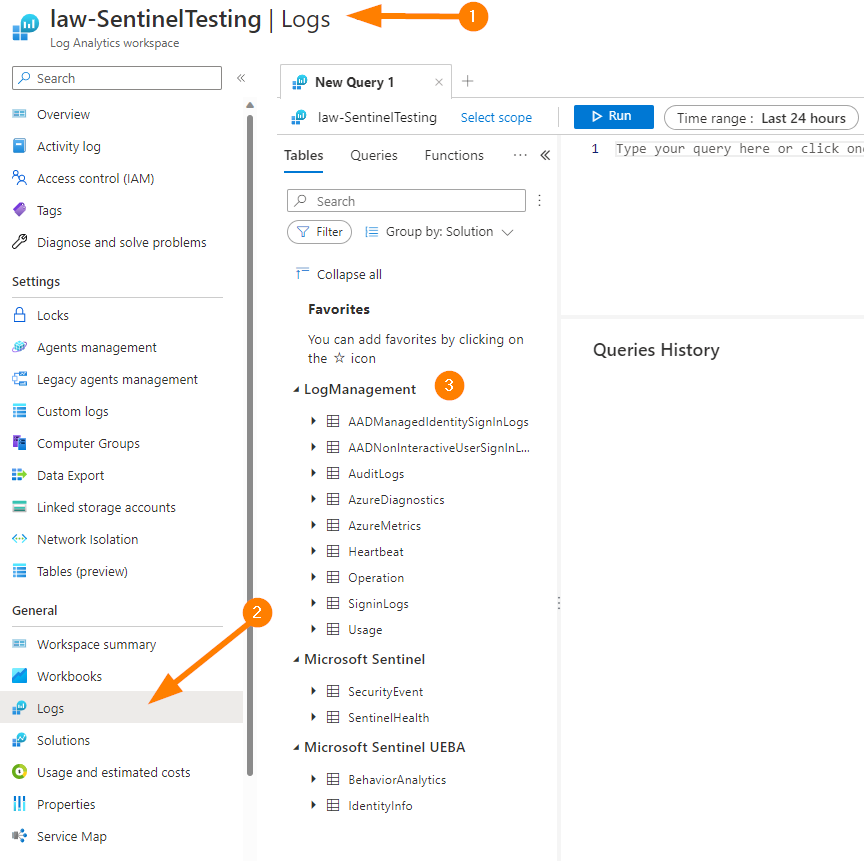
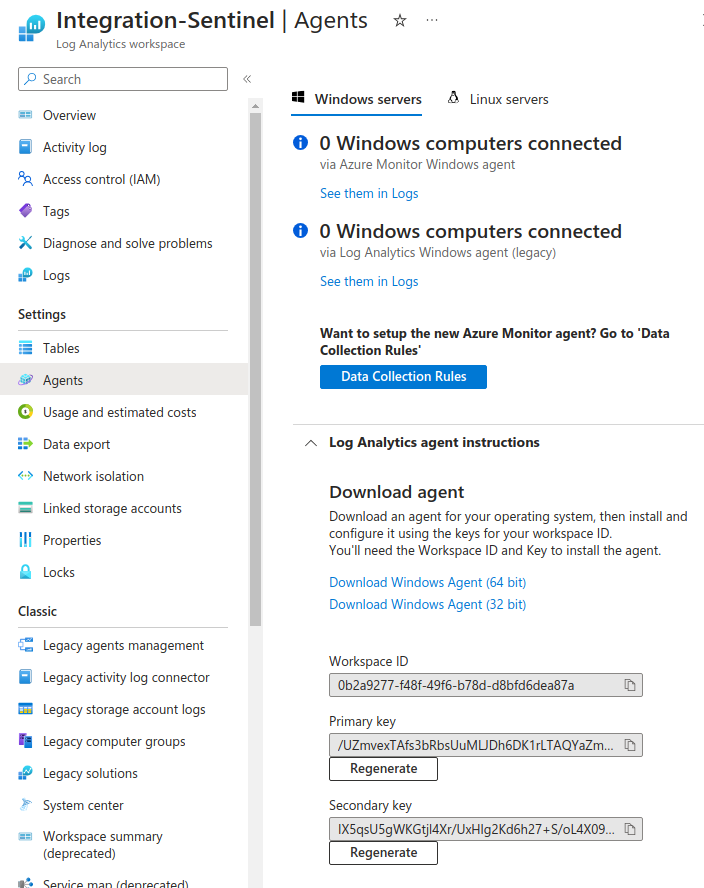
Azure sentinel log analytics - nibhtapex
Monitor Log Flow For Devices in Microsoft Sentinel 11
Sentinel & Log Analytics – Where is my Data? – AzureTracks
Monitor Log Flow For Devices in Microsoft Sentinel 12
Monitor Log Flow For Devices in Microsoft Sentinel 5
Setting Up Azure Sentinel for Advanced Security Log Capture
Sentinel Incident integration and Log Analytics Logging with Zero Trust ...
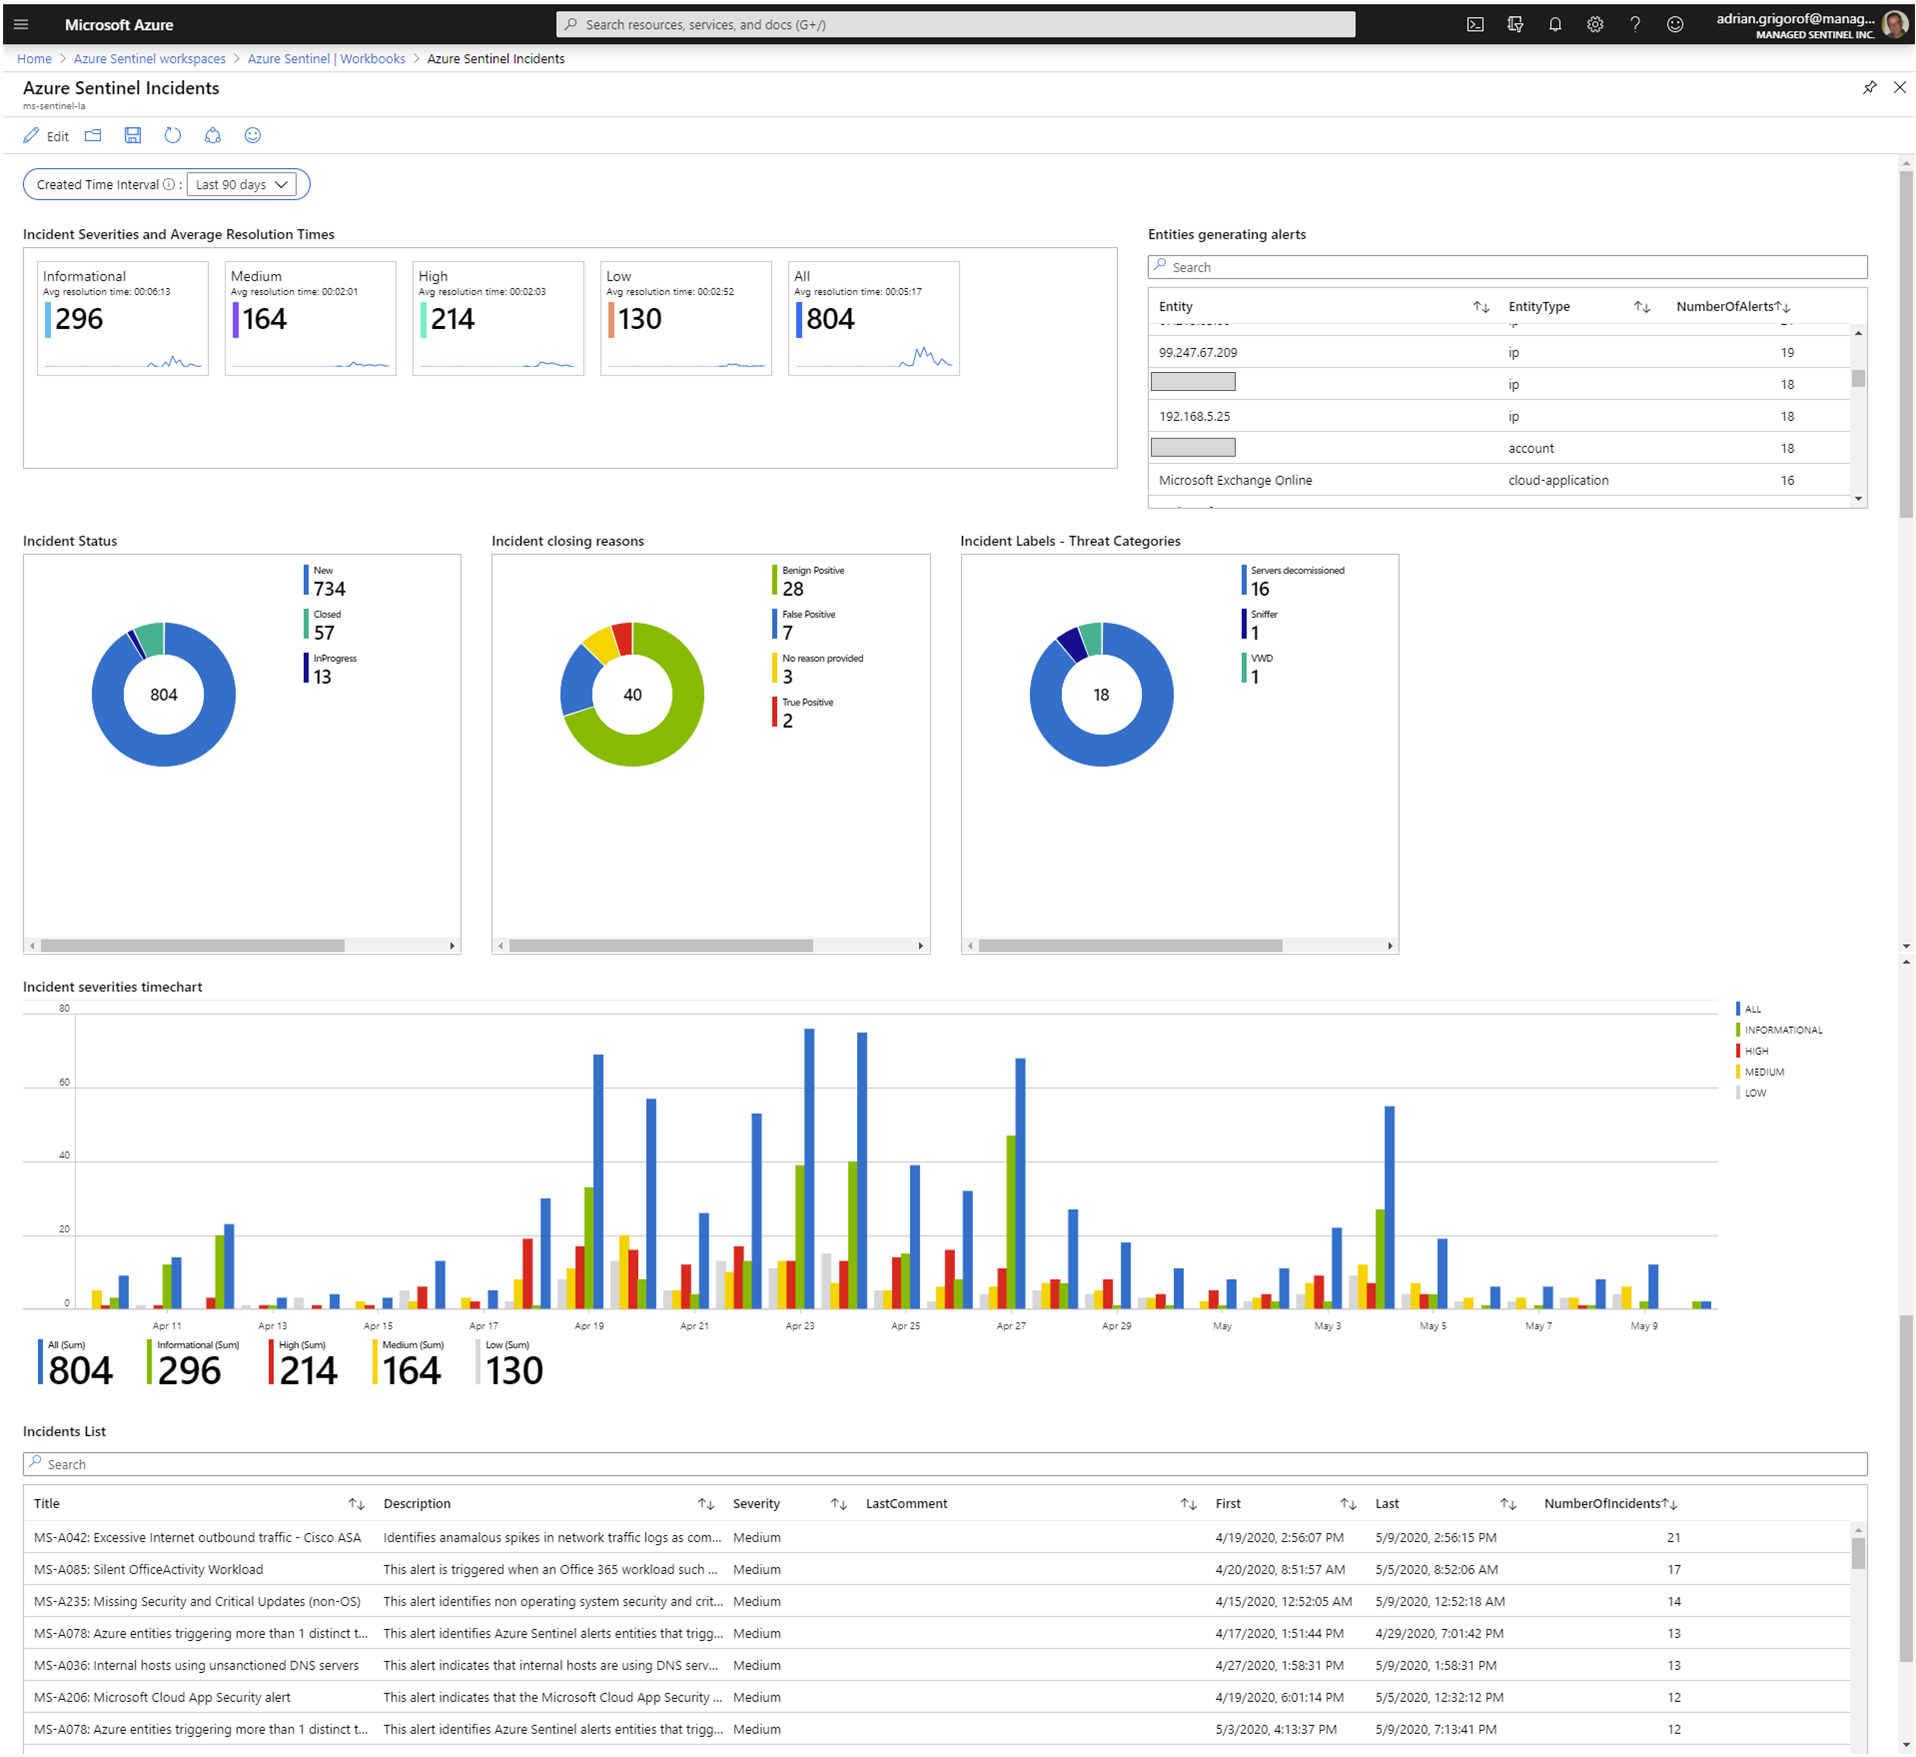
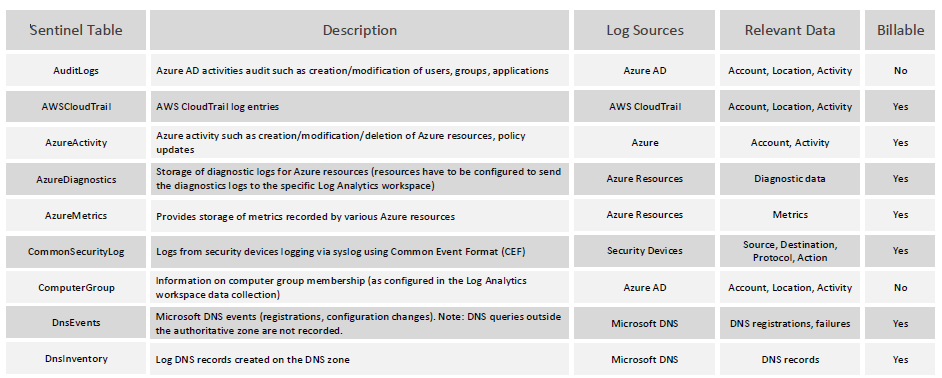
Azure Sentinel & Log Analytics Tables | Managed Sentinel
Microsoft Sentinel Log – Microsoft Sentinel Portal – NZNE
Sentinel & Log Analytics – How to Create Incidents to Test with – Part ...
Sentinel Software – for Monitoring and Data Management - Pizzi Instruments
Azure sentinel log analytics - devjoker
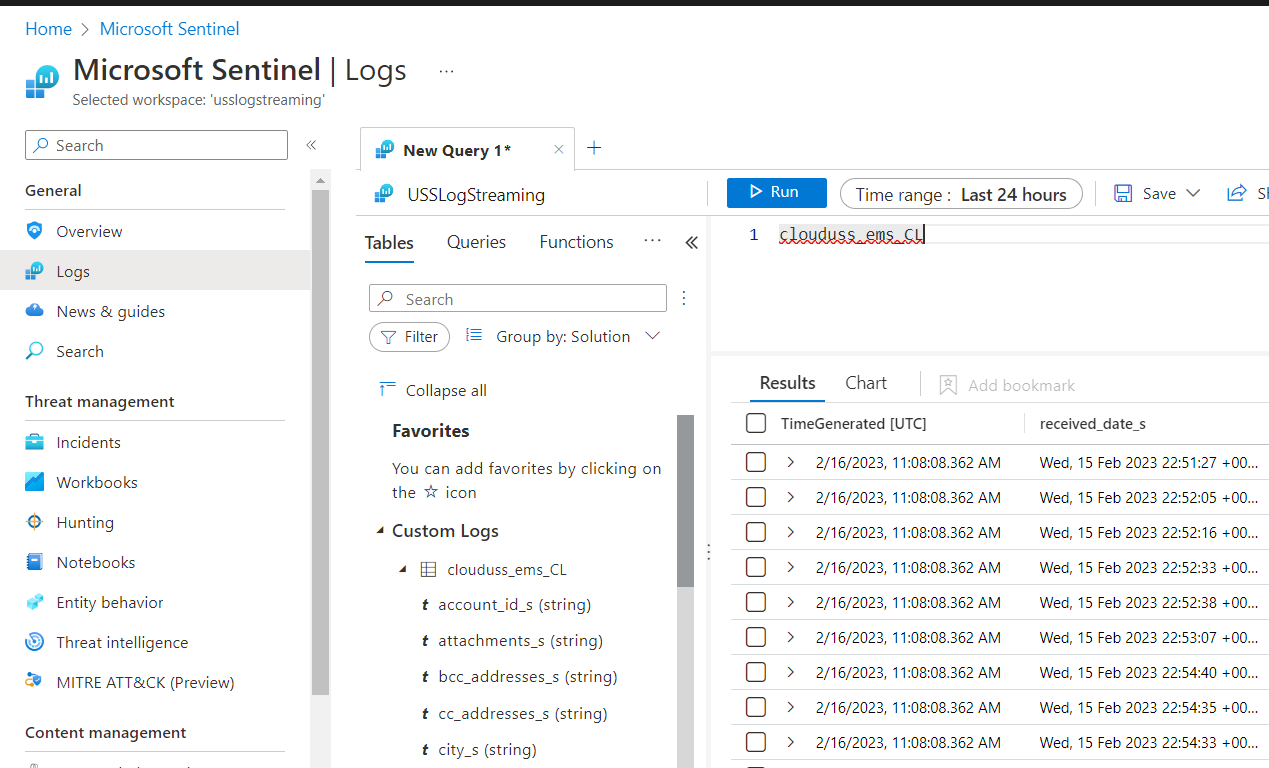
Log Streaming to Microsoft Sentinel - Help :: Unified Security Service
Microsoft Sentinel and Azure Monitor Agent - Bloggerz.cloud
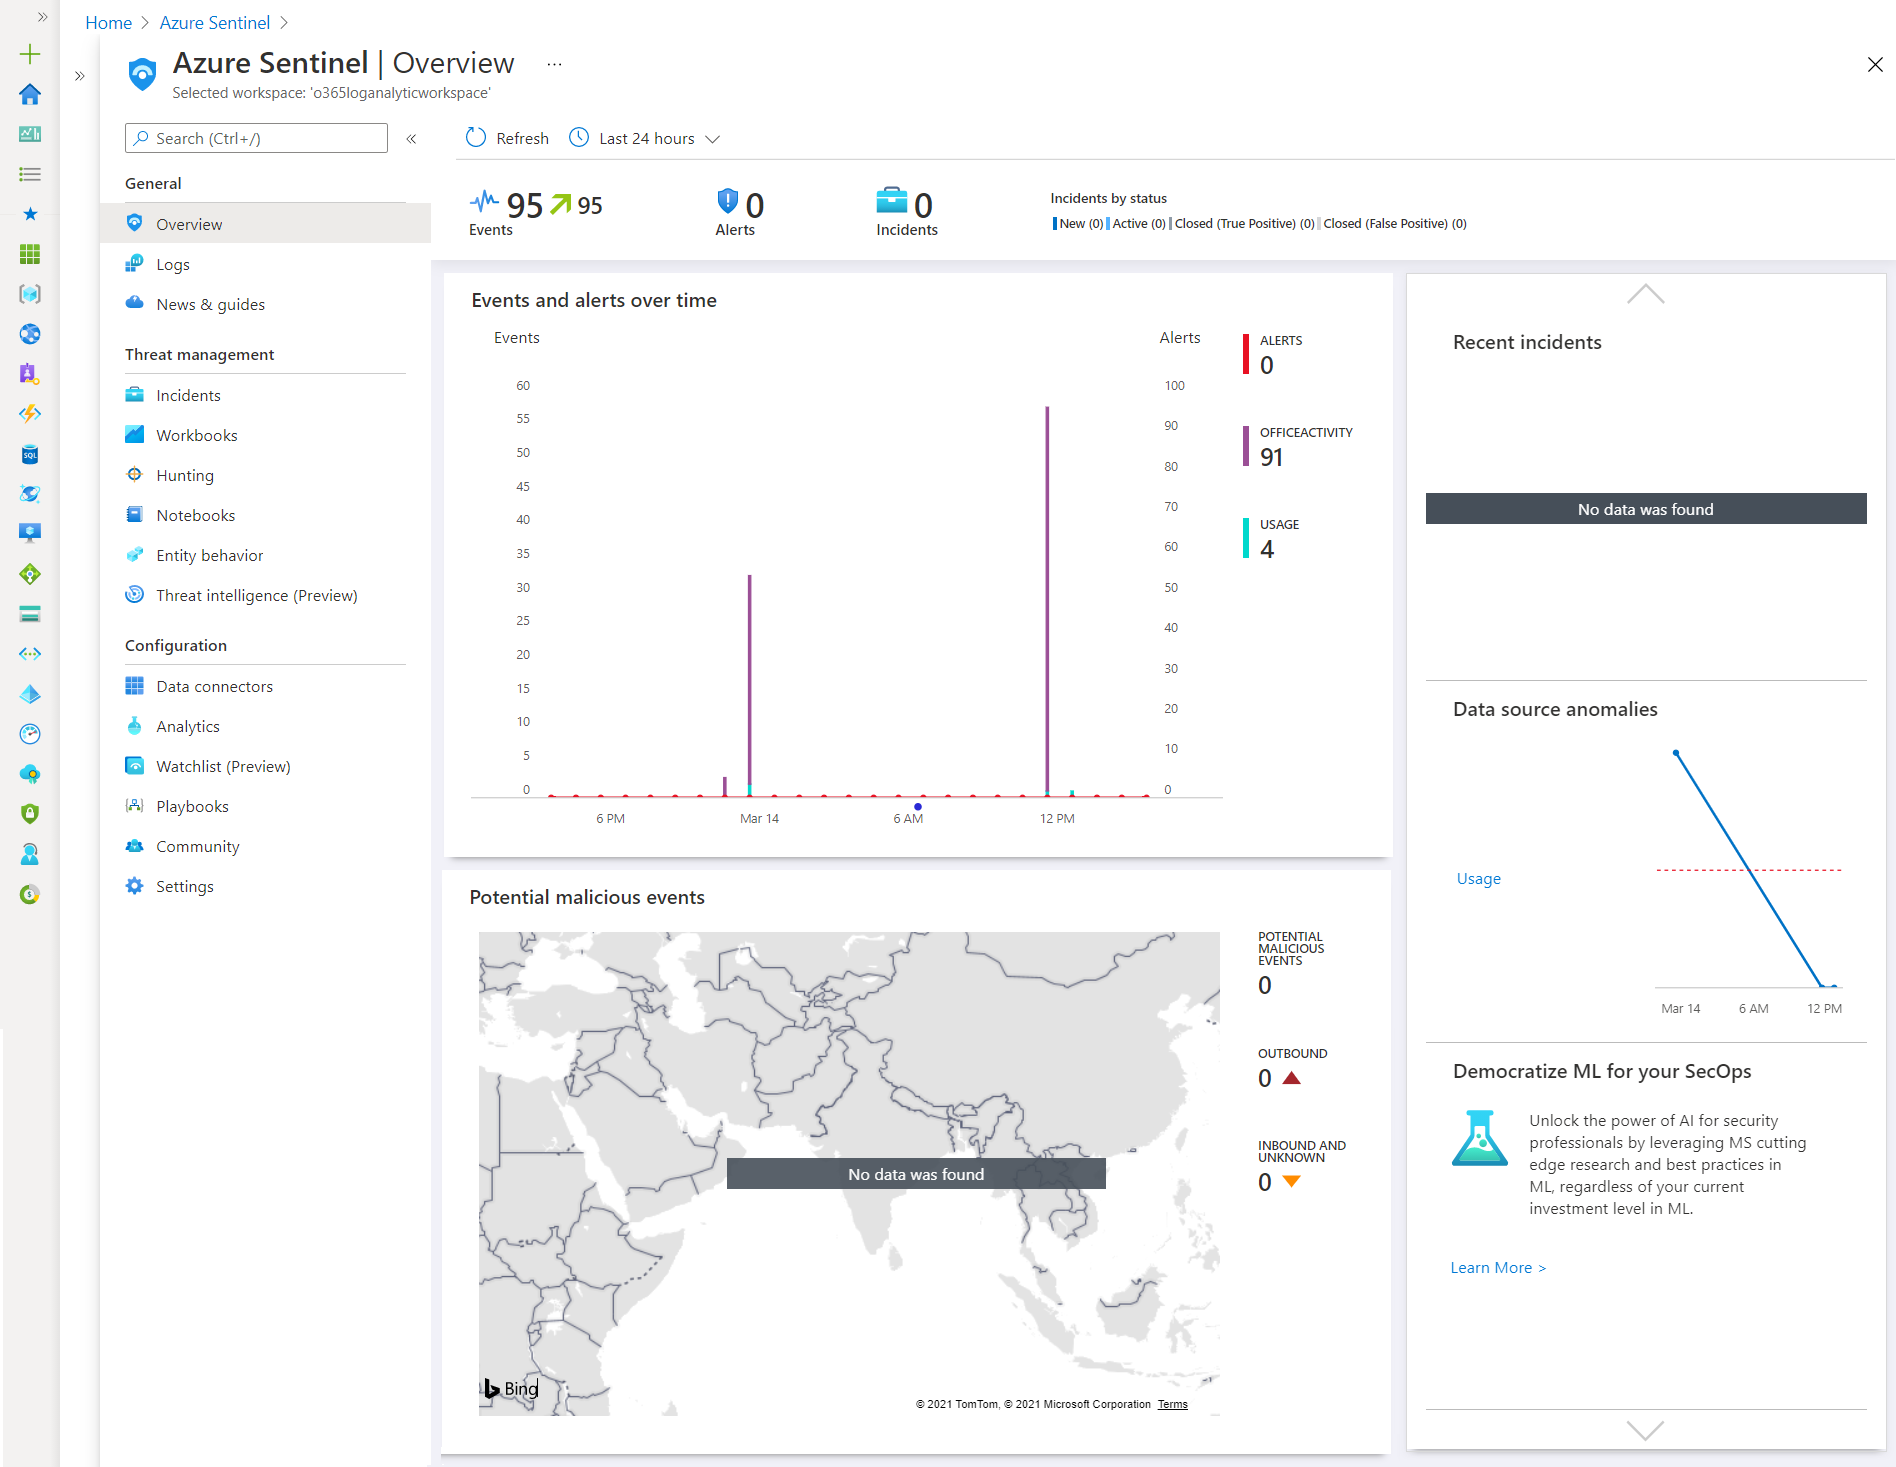
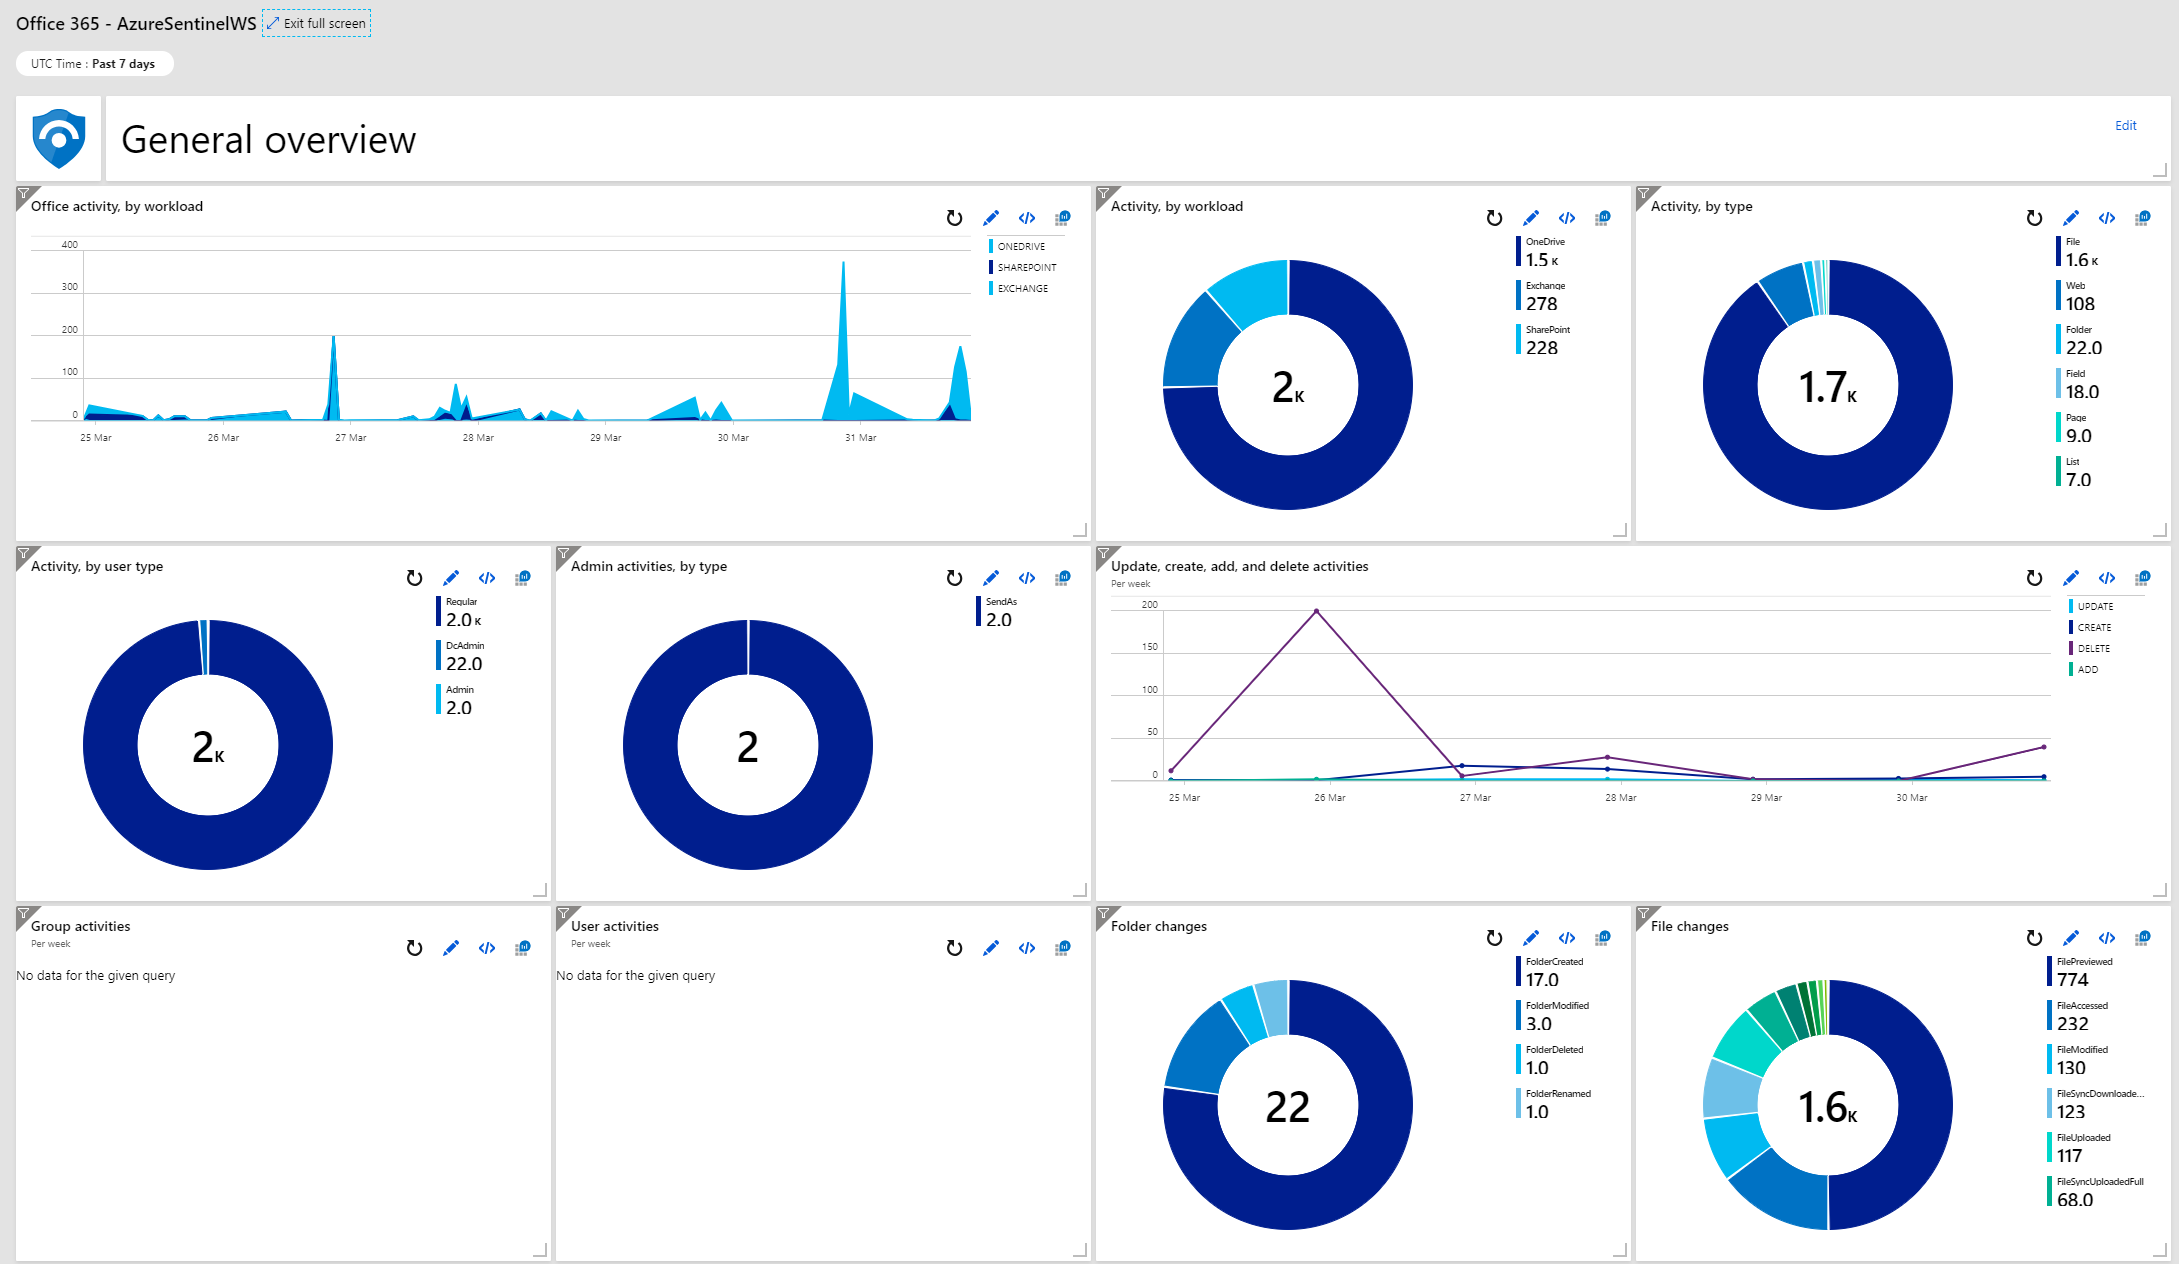
Monitor Office 365 Logs from Azure Sentinel - Nanddeep Nachan Blogs
Monitor Office 365 Logs From Azure Sentinel – JGJR
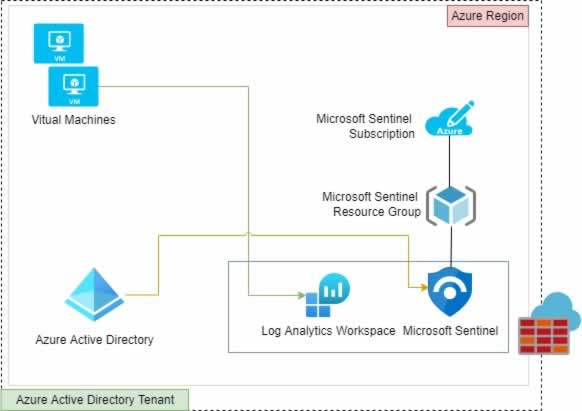
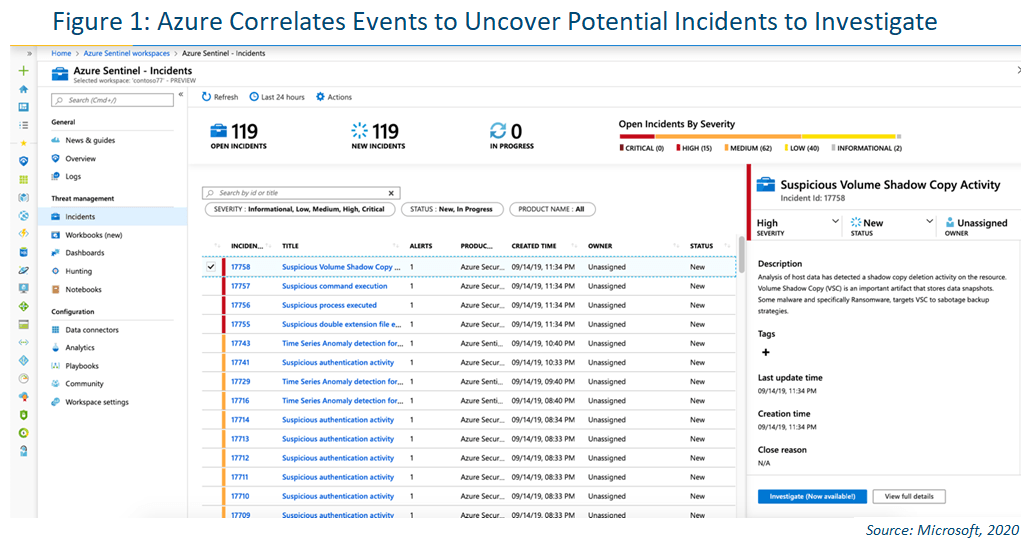
What Is Microsoft (Azure) Sentinel and Why Do We Need It?
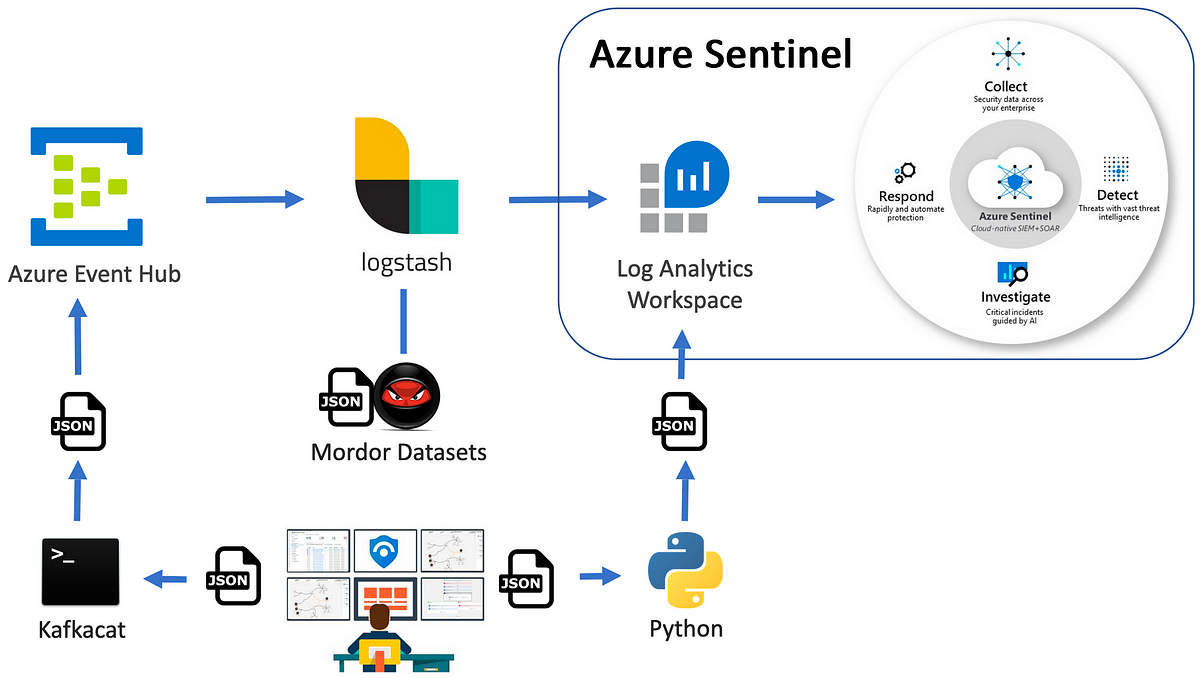
Logstash Azure Log Analytics | Logstash: Collect, Parse, Transform Logs ...
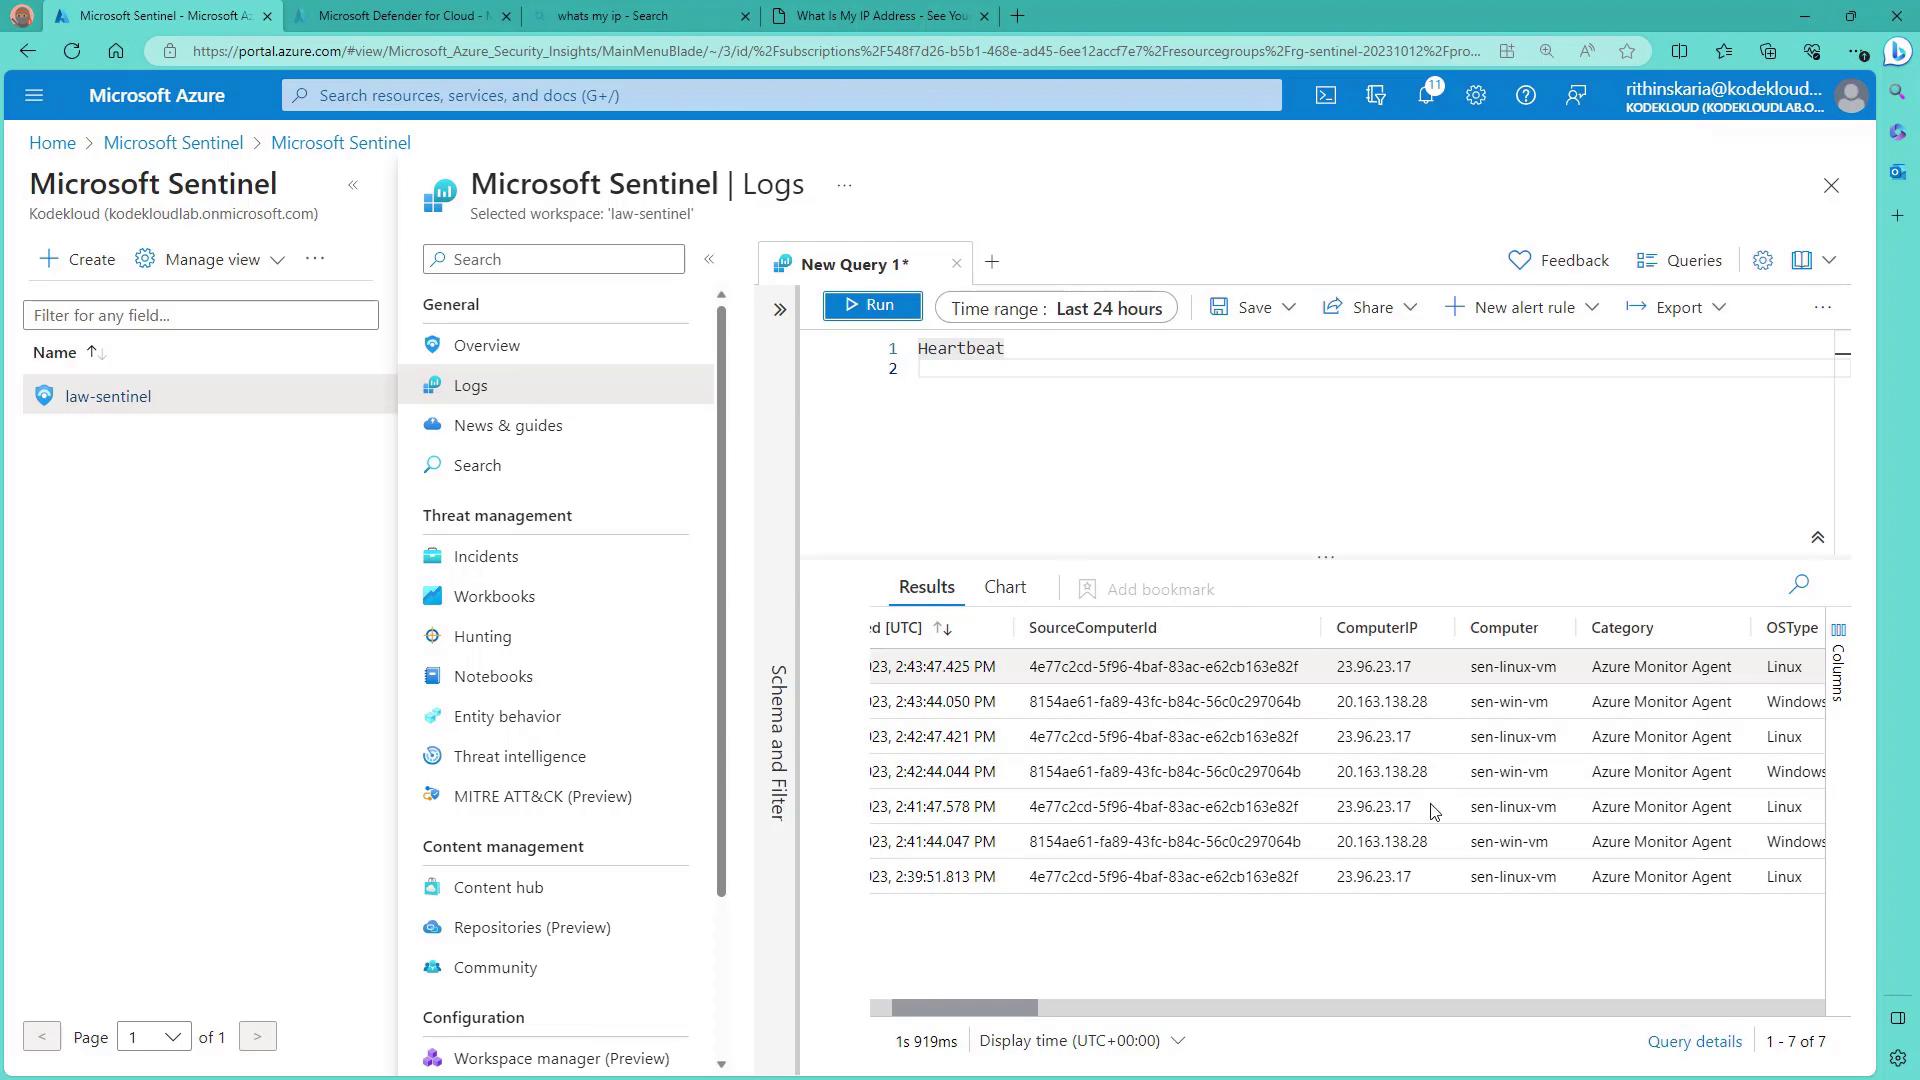
Configure data connections to Sentinel - KodeKloud
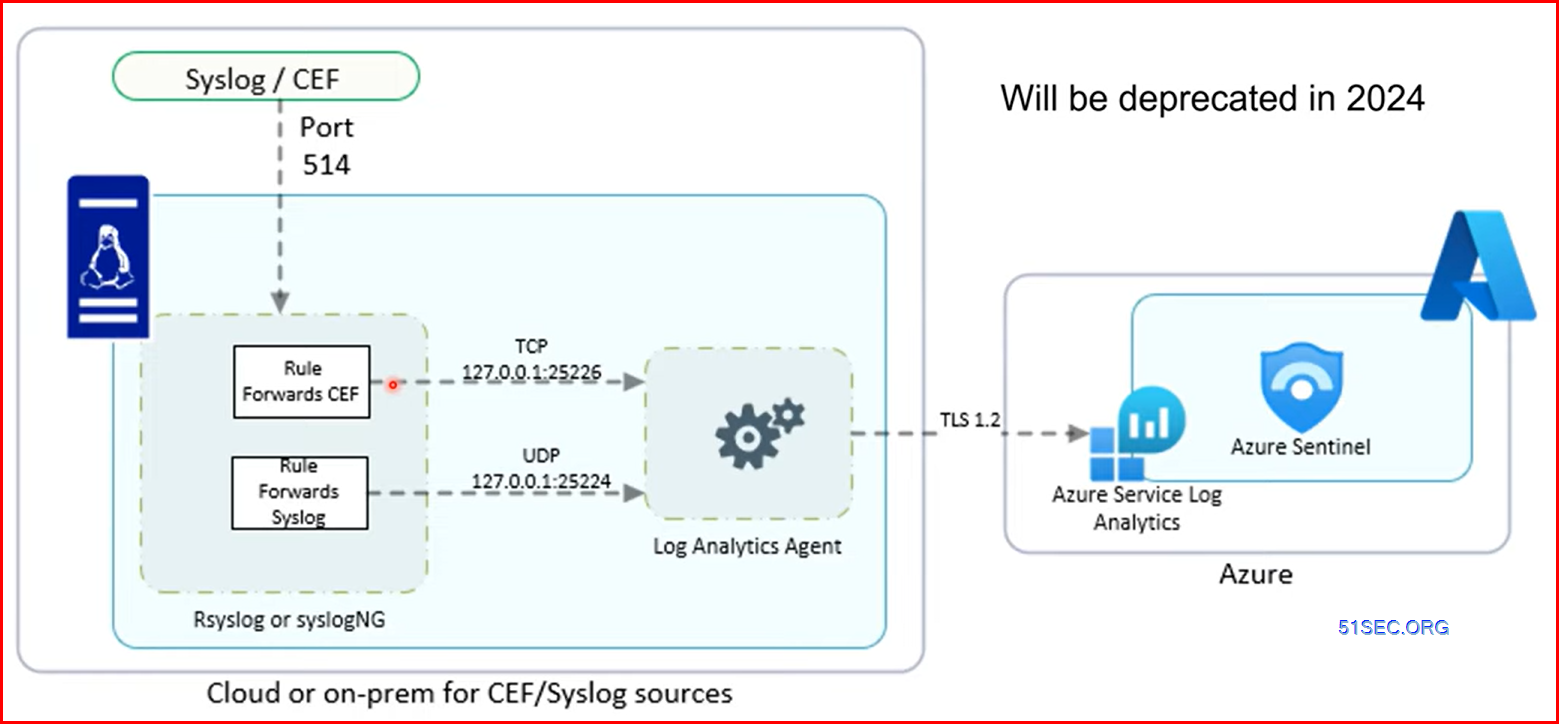
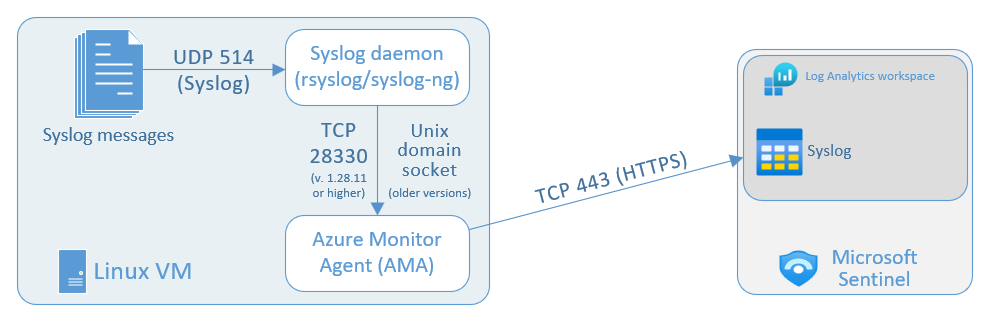
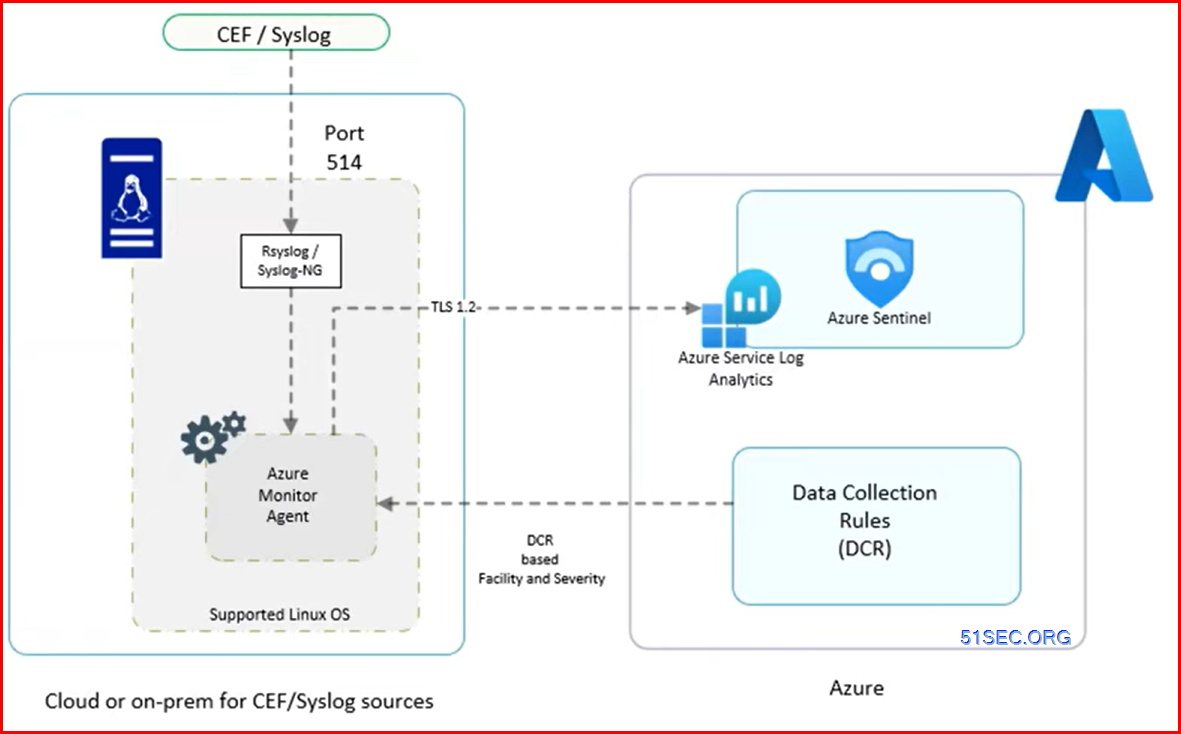
Configuring Sentinel to Collect CEF Syslog with the AMA agent – Simple ...
Sending Cribl internal logs to Microsoft Sentinel using a custom table ...
Azure Sentinel 101 - NetSec
Ingest Oracle Cloud Infrastructure logs into Microsoft Azure Sentinel ...
Use Cribl to ingest Firewall logs into Sentinel Auxiliary Logs tier
Effective Approach To Collect Linux Logs to Microsoft Sentinel 12
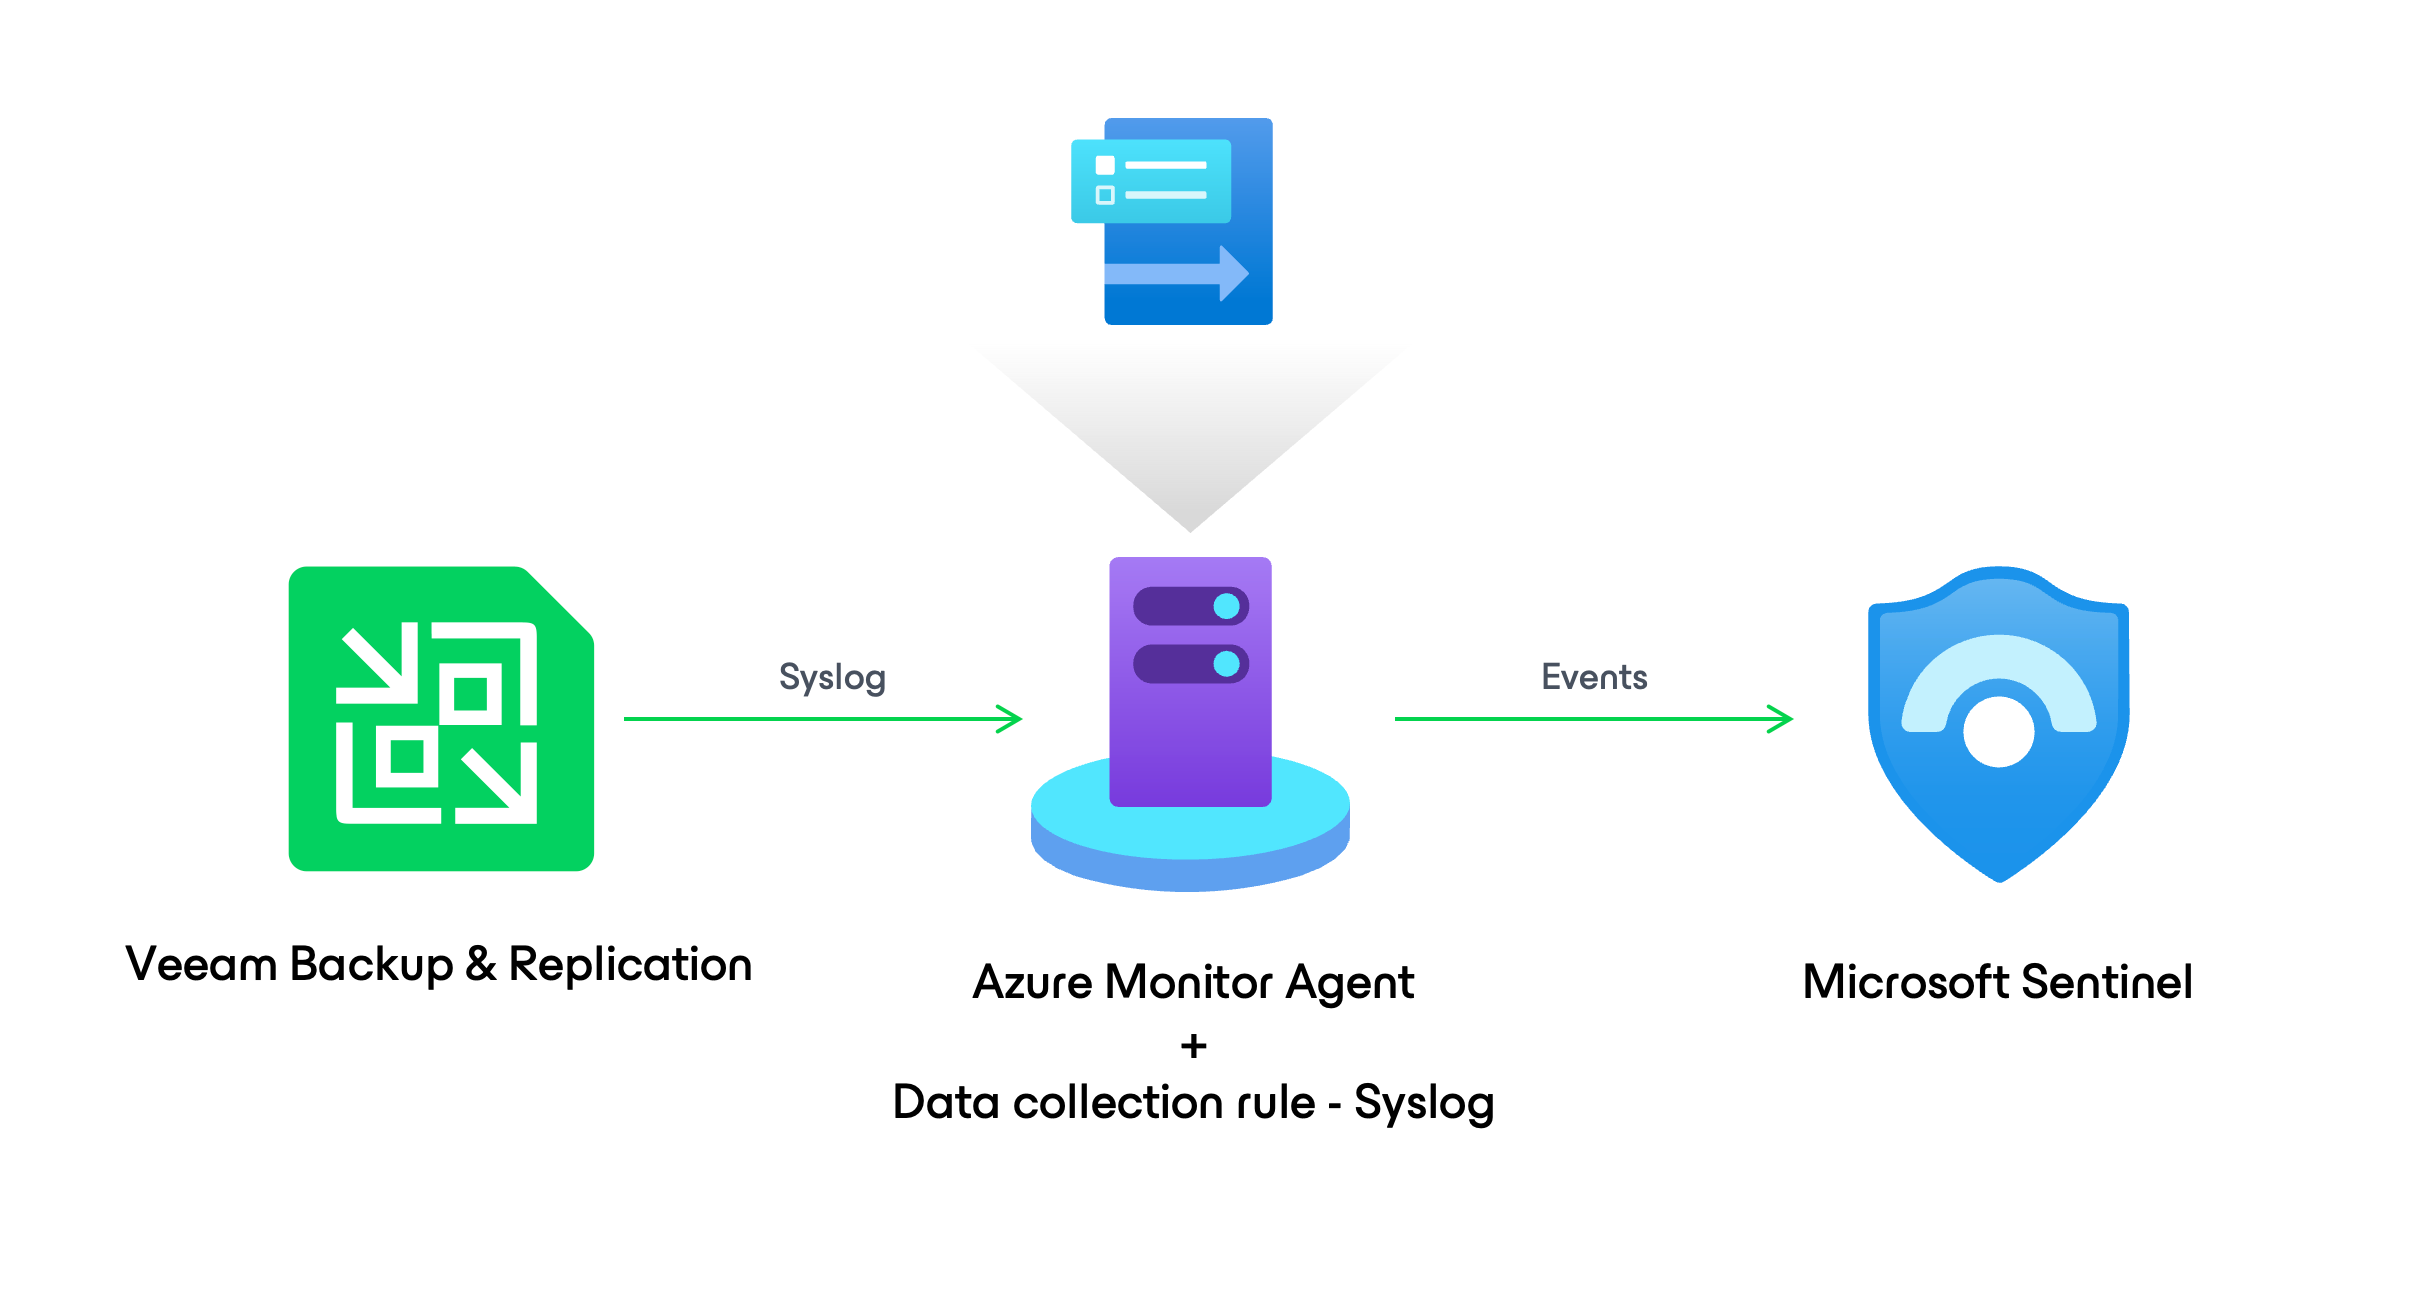
Set Up Syslog Forwarding to Microsoft Sentinel
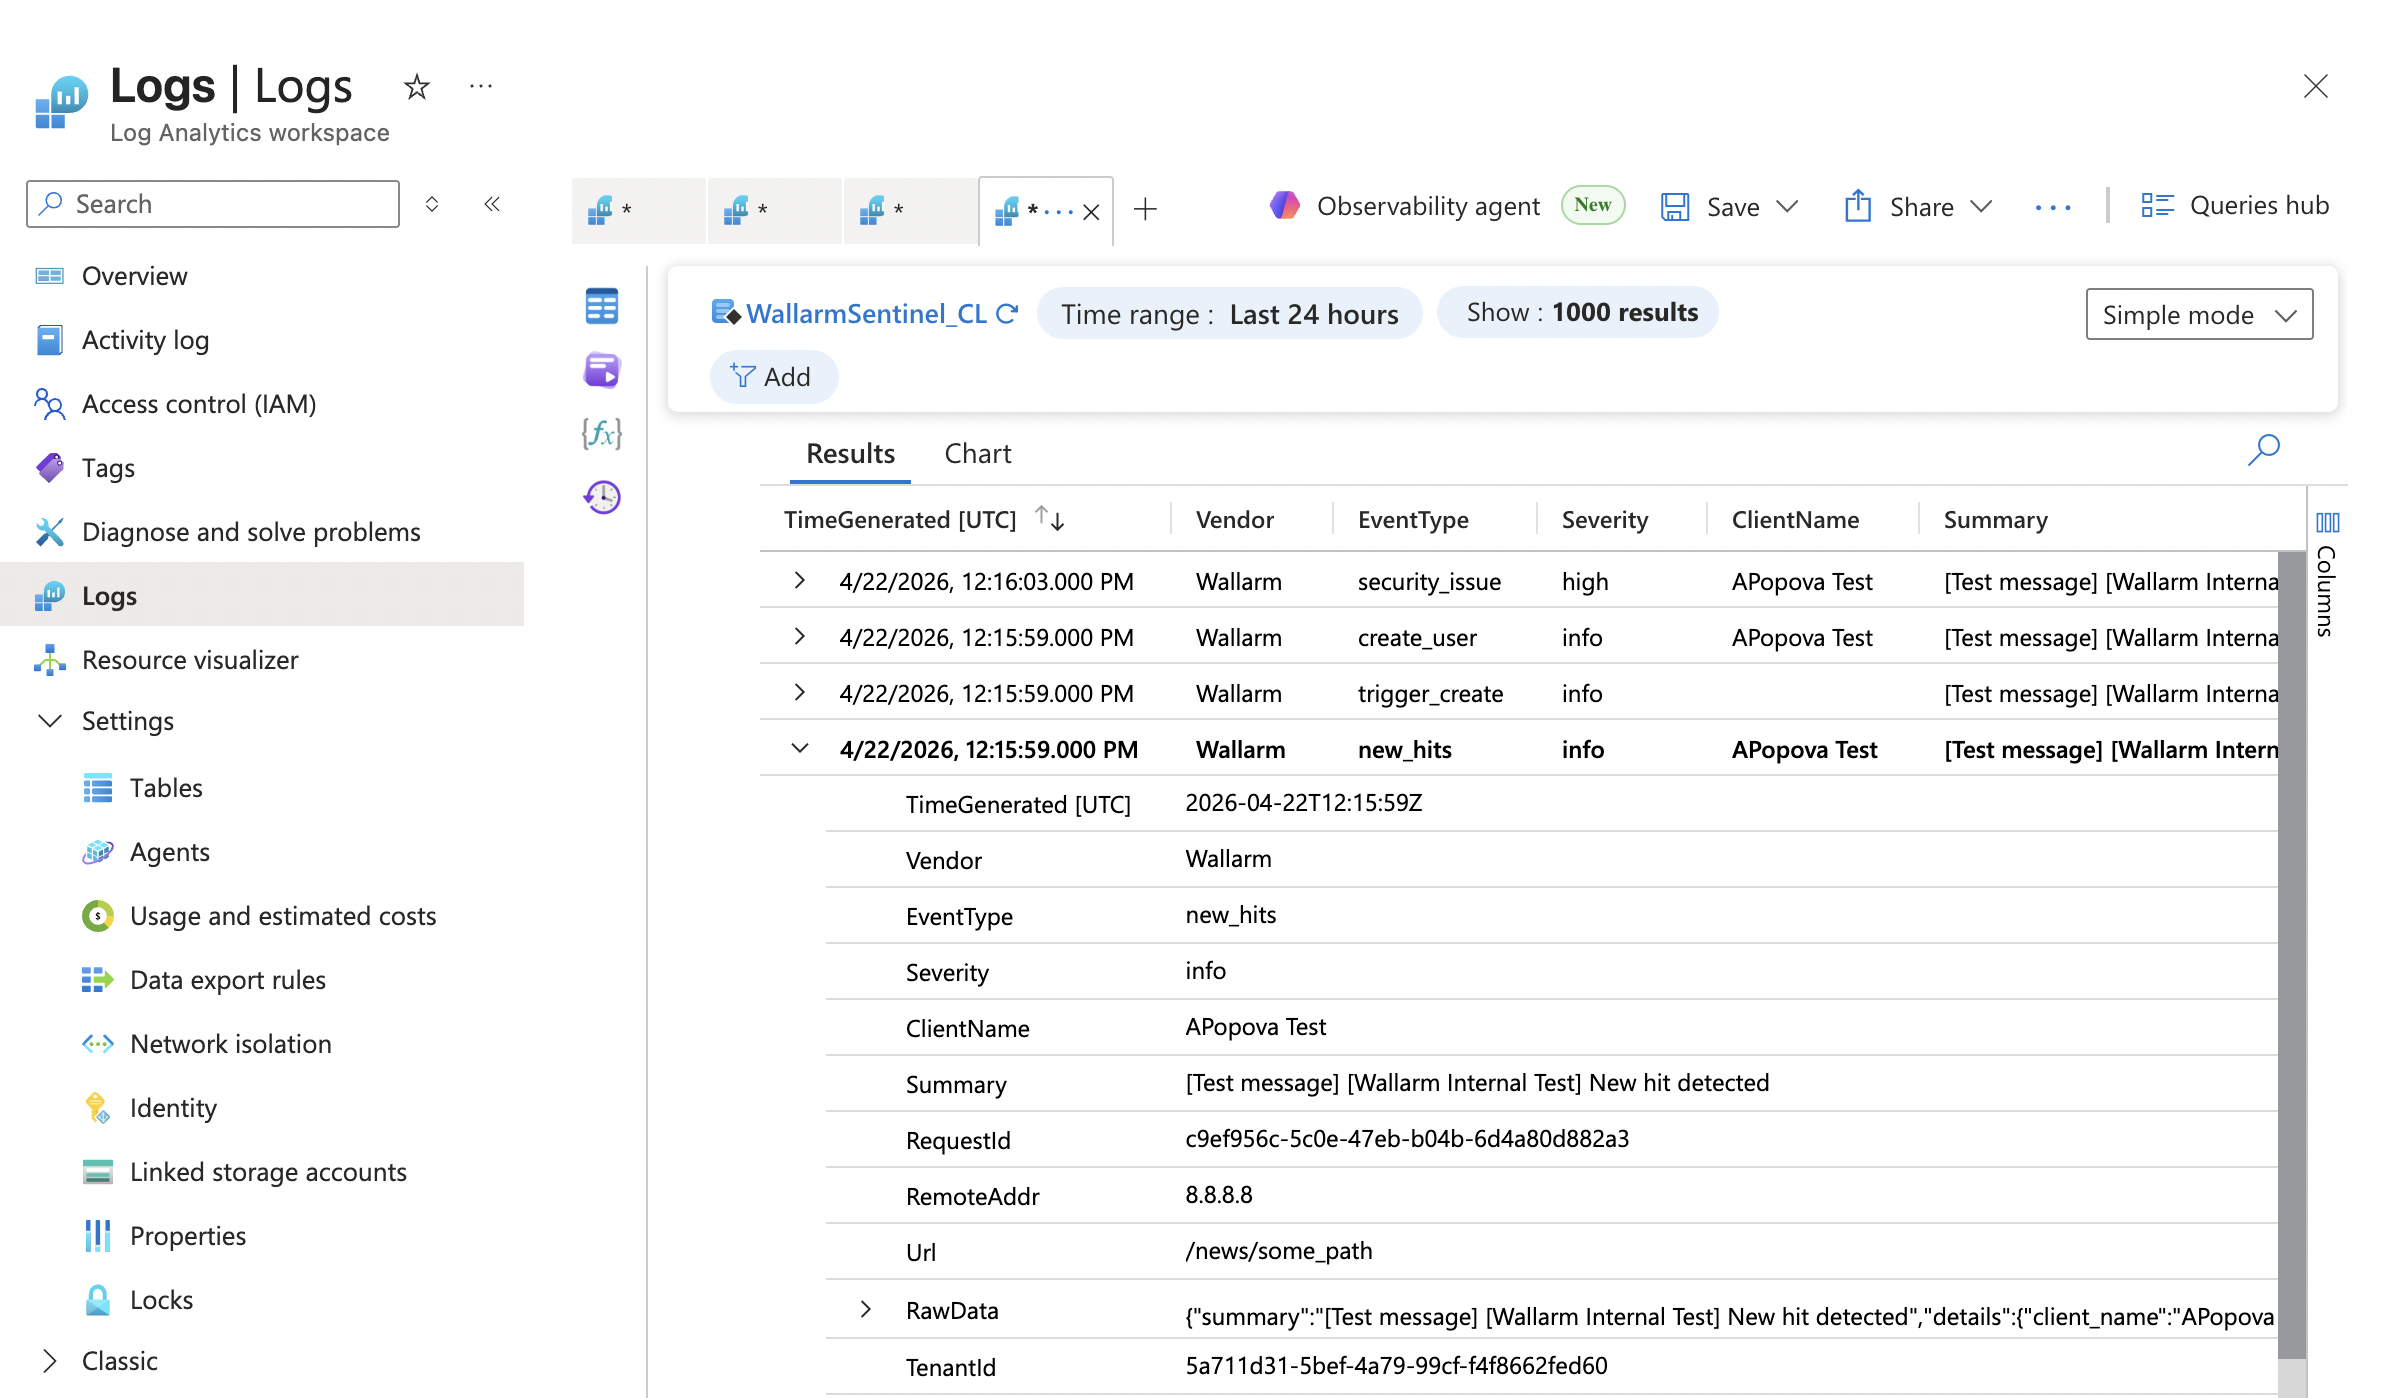
Azure Monitor Logs / Microsoft Sentinel - Wallarm Documentation
Stream CEF logs to Microsoft Sentinel with the AMA connector ...
Resource Monitoring
Azure Sentinel – logs retention | A Security Engineer
Microsoft Sentinel |Ingest logs to Sentinel using Azure Monitor Agent ...
Effective Solution To Monitor Data Connectors in Microsoft Sentinel 16
How to optimize logs in Microsoft Sentinel | ☁️ Charbel N. posted on ...
Creating and onboarding a Syslog Forwarder into Sentinel (Azure VM) (Easy)
Sending your Threat Indicators to Azure Sentinel
Monitor and optimize the execution of your Microsoft Sentinel scheduled ...
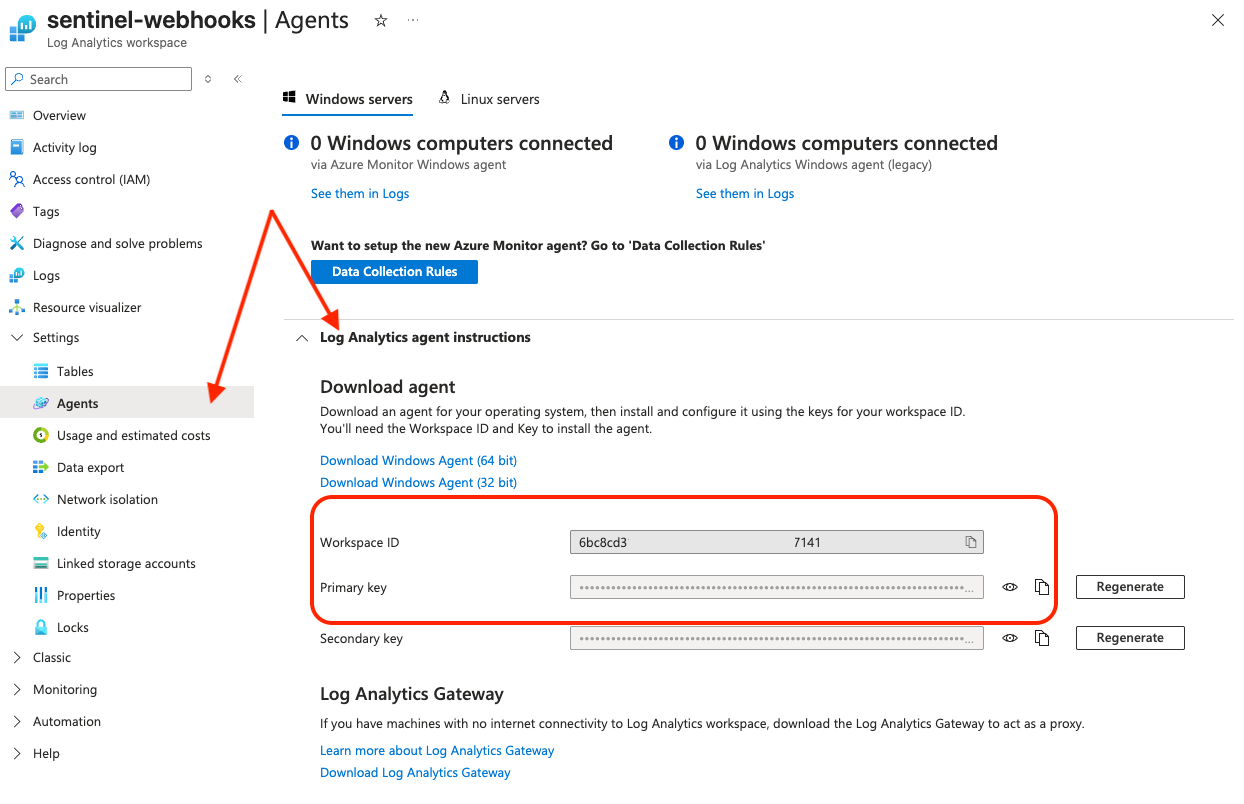
Forward Logs to Microsoft Sentinel with a Private Link 33
Monitor Sentinel Data Connector Health – AzureTracks
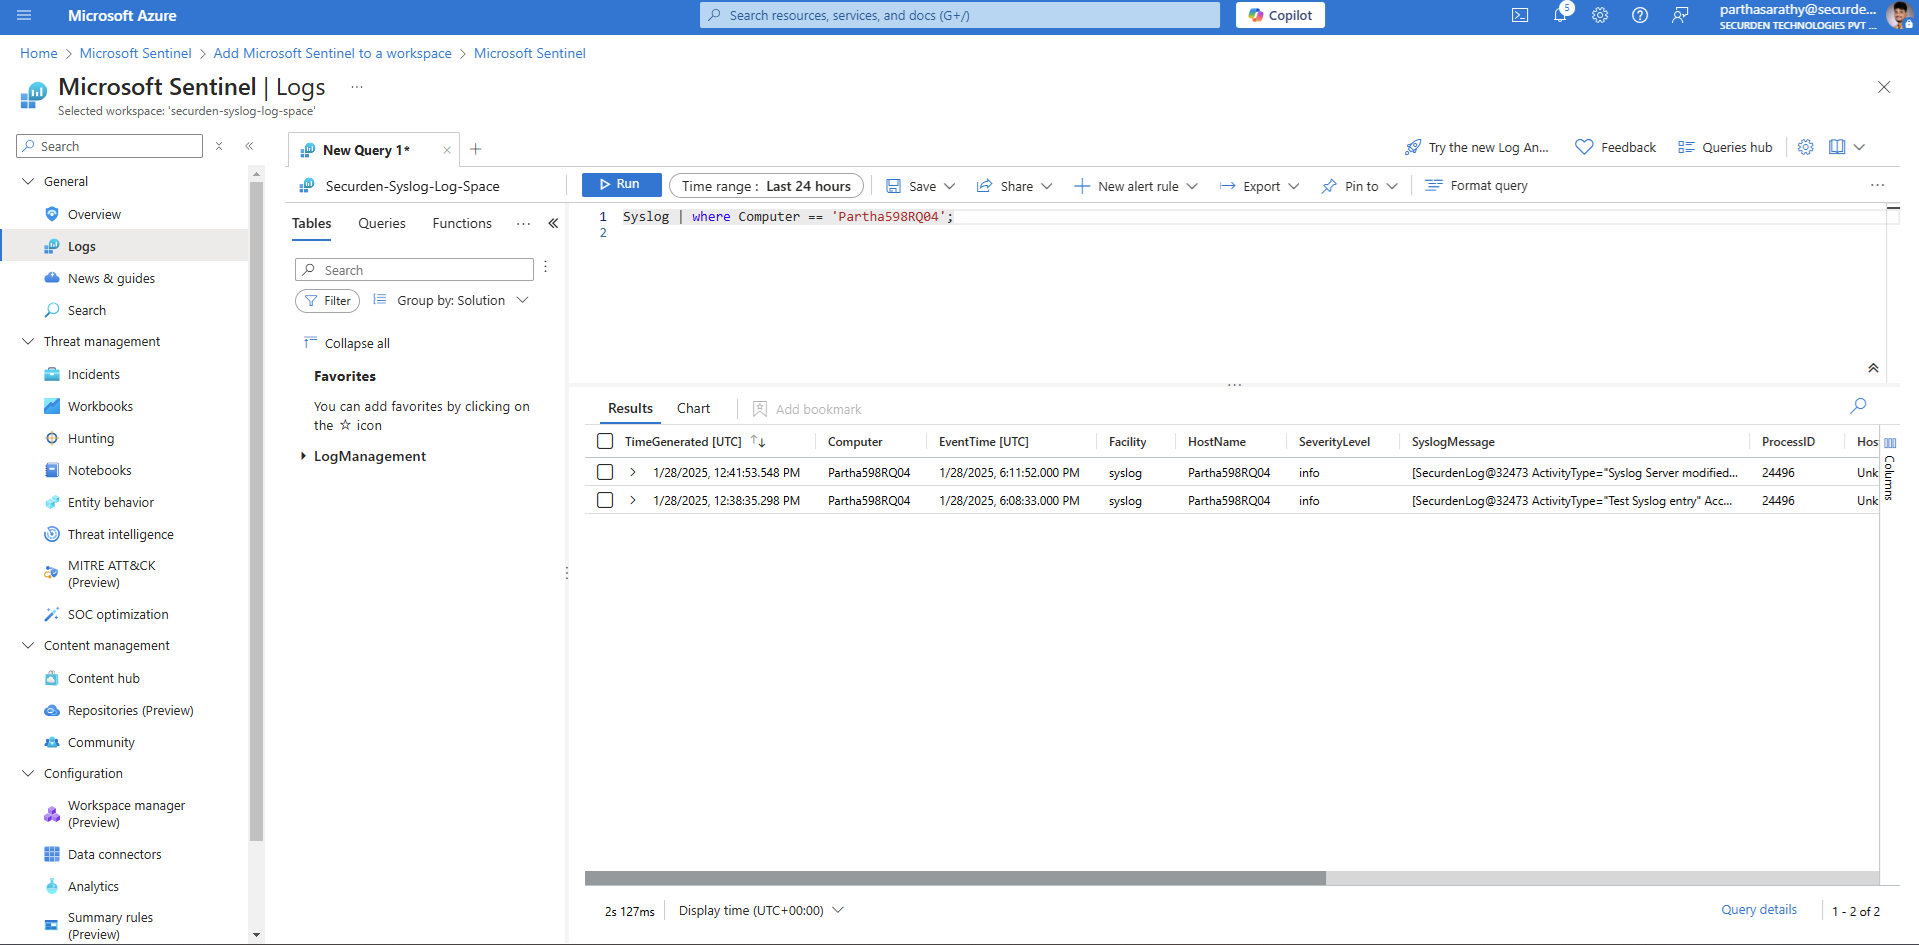
How to Integrate Azure Sentinel for Collecting Syslog | Securden EPM
Logs do AD on-premises no Microsoft Sentinel - Daniel Donda
Microsoft Sentinel Event Logs _ When to use Basic Logs – PESY
Sentinel - Automated Varian logfile analysis : r/MedicalPhysics
Simplify your SIEM migration to Microsoft Sentinel with Datadog ...
Intégration des logs Sysmon dans Microsoft Sentinel grâce au nouvel ...
Optimize Sentinel Logs for Intune via Defender XDR - Patch My PC
Ingesting events using Azure Monitor and Microsoft Sentinel for ...
Forward Logs to Microsoft Sentinel with a Private Link 43
Optimize Fortinet Traffic Logs into Microsoft Sentinel 2
Forward syslog data to Microsoft Sentinel and Azure Monitor by using ...
Monitor the health of your Microsoft Sentinel data connectors ...
Forward Logs to Microsoft Sentinel with a Private Link 42
Effective Solution To Monitor Data Connectors in Microsoft Sentinel 10
What Is Azure Sentinel (Renamed to Microsoft Sentinel)?
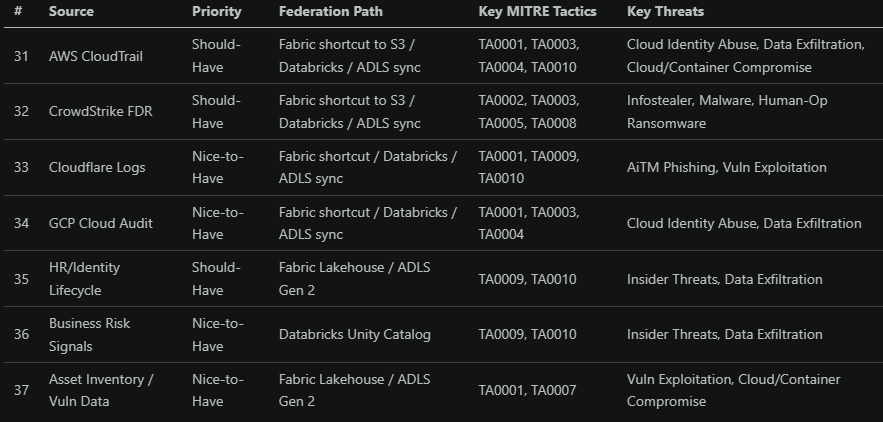
Log Sources Your SOC Needs for Detection, Forensics, and Hunting ...
🛡️ How to Ingest Syslog and CEF Logs into Microsoft Sentinel Using ...
Sentinel Lab Notes – 51 Sec
Effective Solution To Monitor Data Connectors in Microsoft Sentinel 38
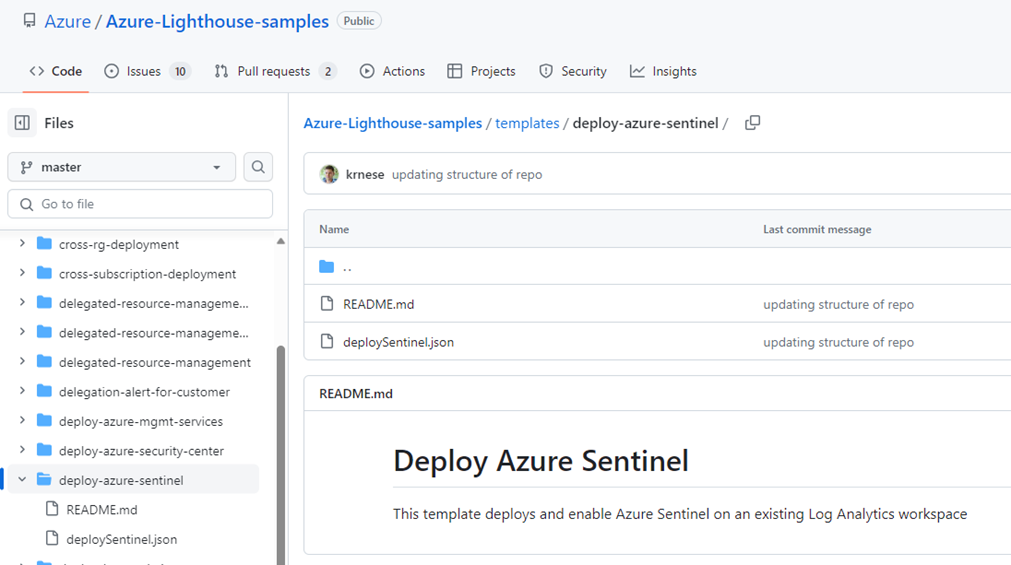
Azure Lighthouse & Sentinel at Scale – Part 3 – AzureTracks
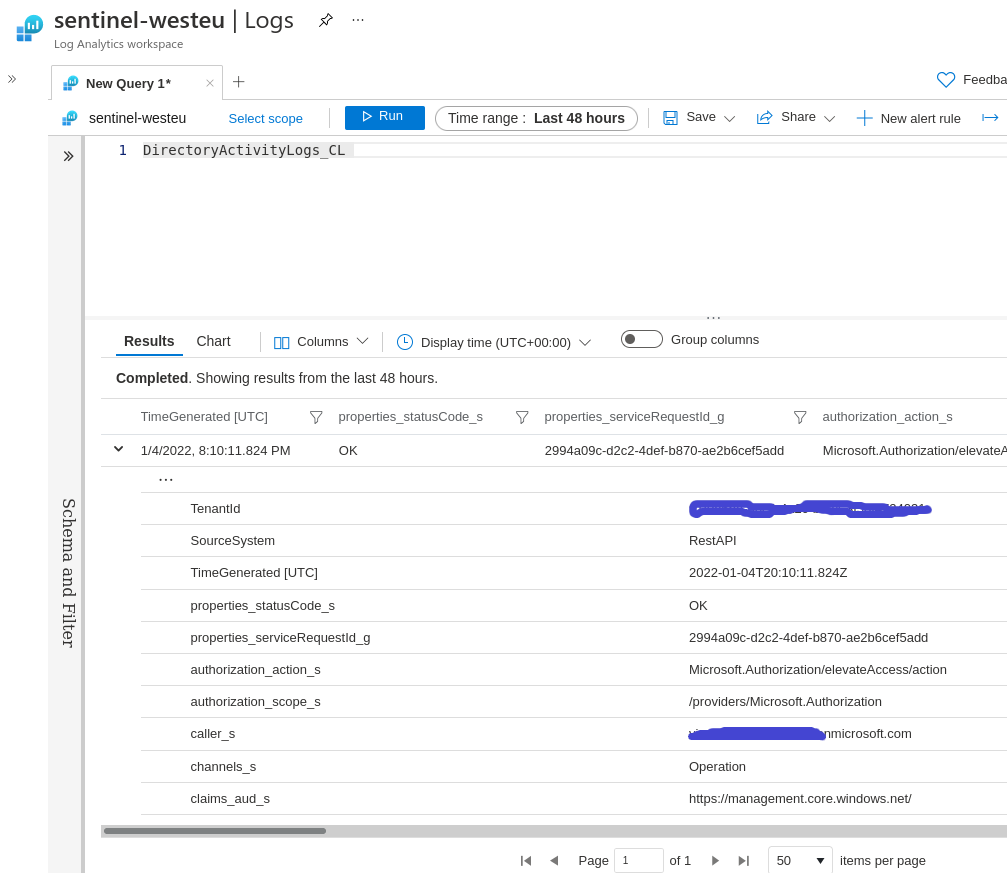
Logging User Access Admin elevations to Microsoft Sentinel | Adriaans ...
Maximizing Microsoft Sentinel ROI with VirtualMetric DataStream – Part 2 1
SENTINEL SYSTEM MONITOR
Ingest Custom Logs to Microsoft Sentinel: A Step-by-Step Guide 1
NVS_Sentinel | PPTX
Sentinel-Log-Ingestion-Resiliency | EXMDR
Top 7 Azure Reporting Tools for Efficient Data Management
Microsoft Sentinel's Audit Logs: Monitor Activity, Respond to Threats ...
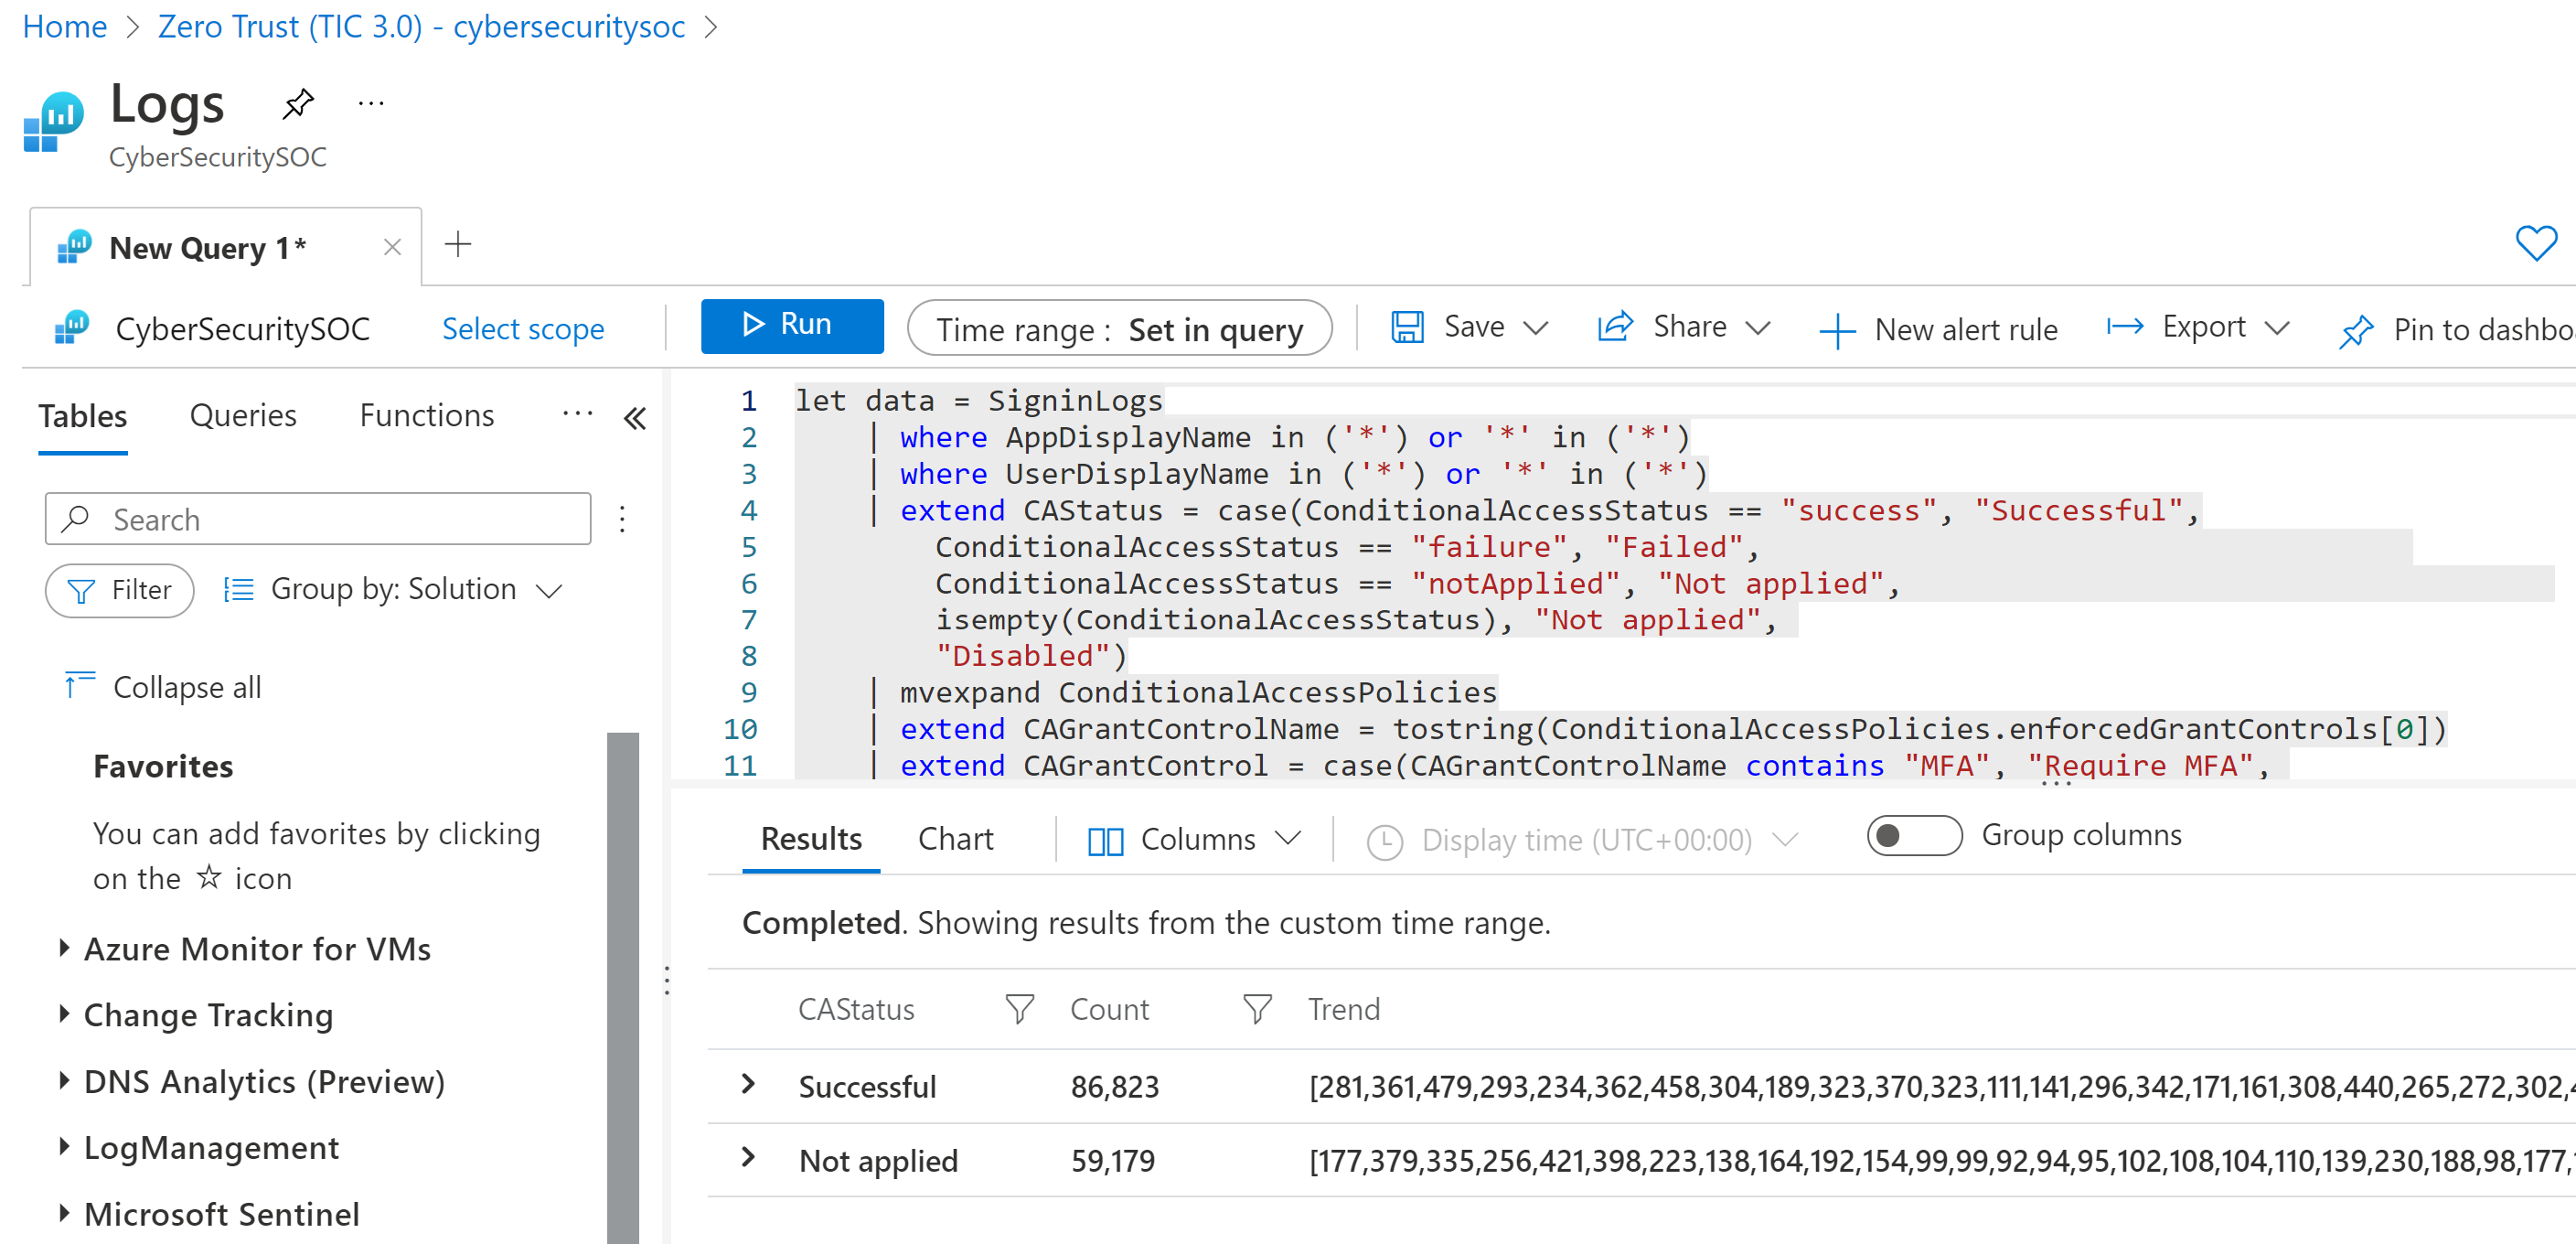
Monitor Zero Trust (TIC 3.0) security architectures with Microsoft ...
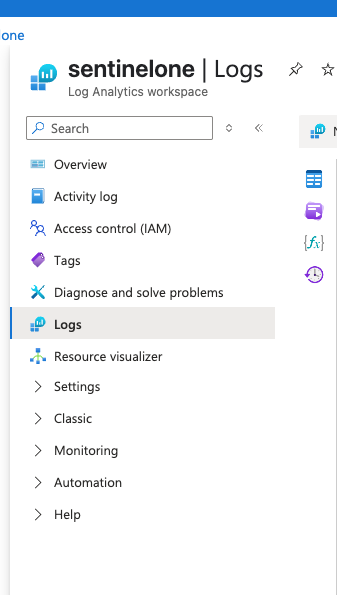
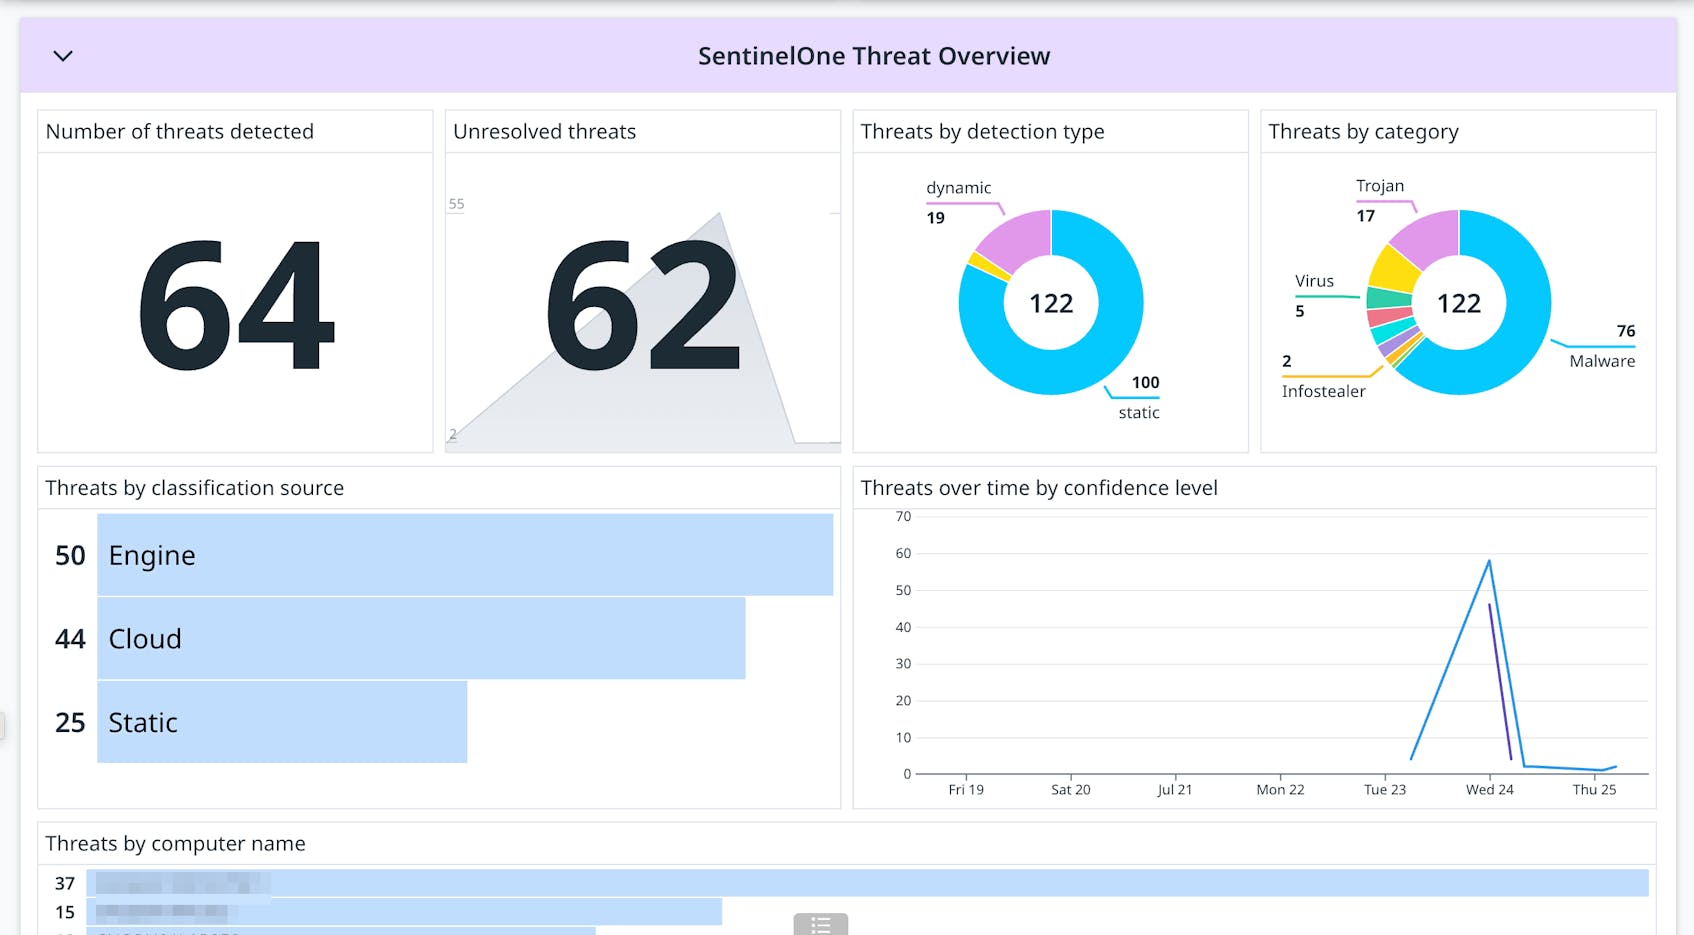
Monitor Your SentinelOne Logs and Alerts With Datadog Cloud SIEM | Datadog
Sentinelone Access Logs | How To Collect Logs – MKDOKR
GitHub - krutikmehtaa/log-Sentinel: A production-ready anomaly ...
Translate raw security logs to behavioral insights using UEBA behaviors ...
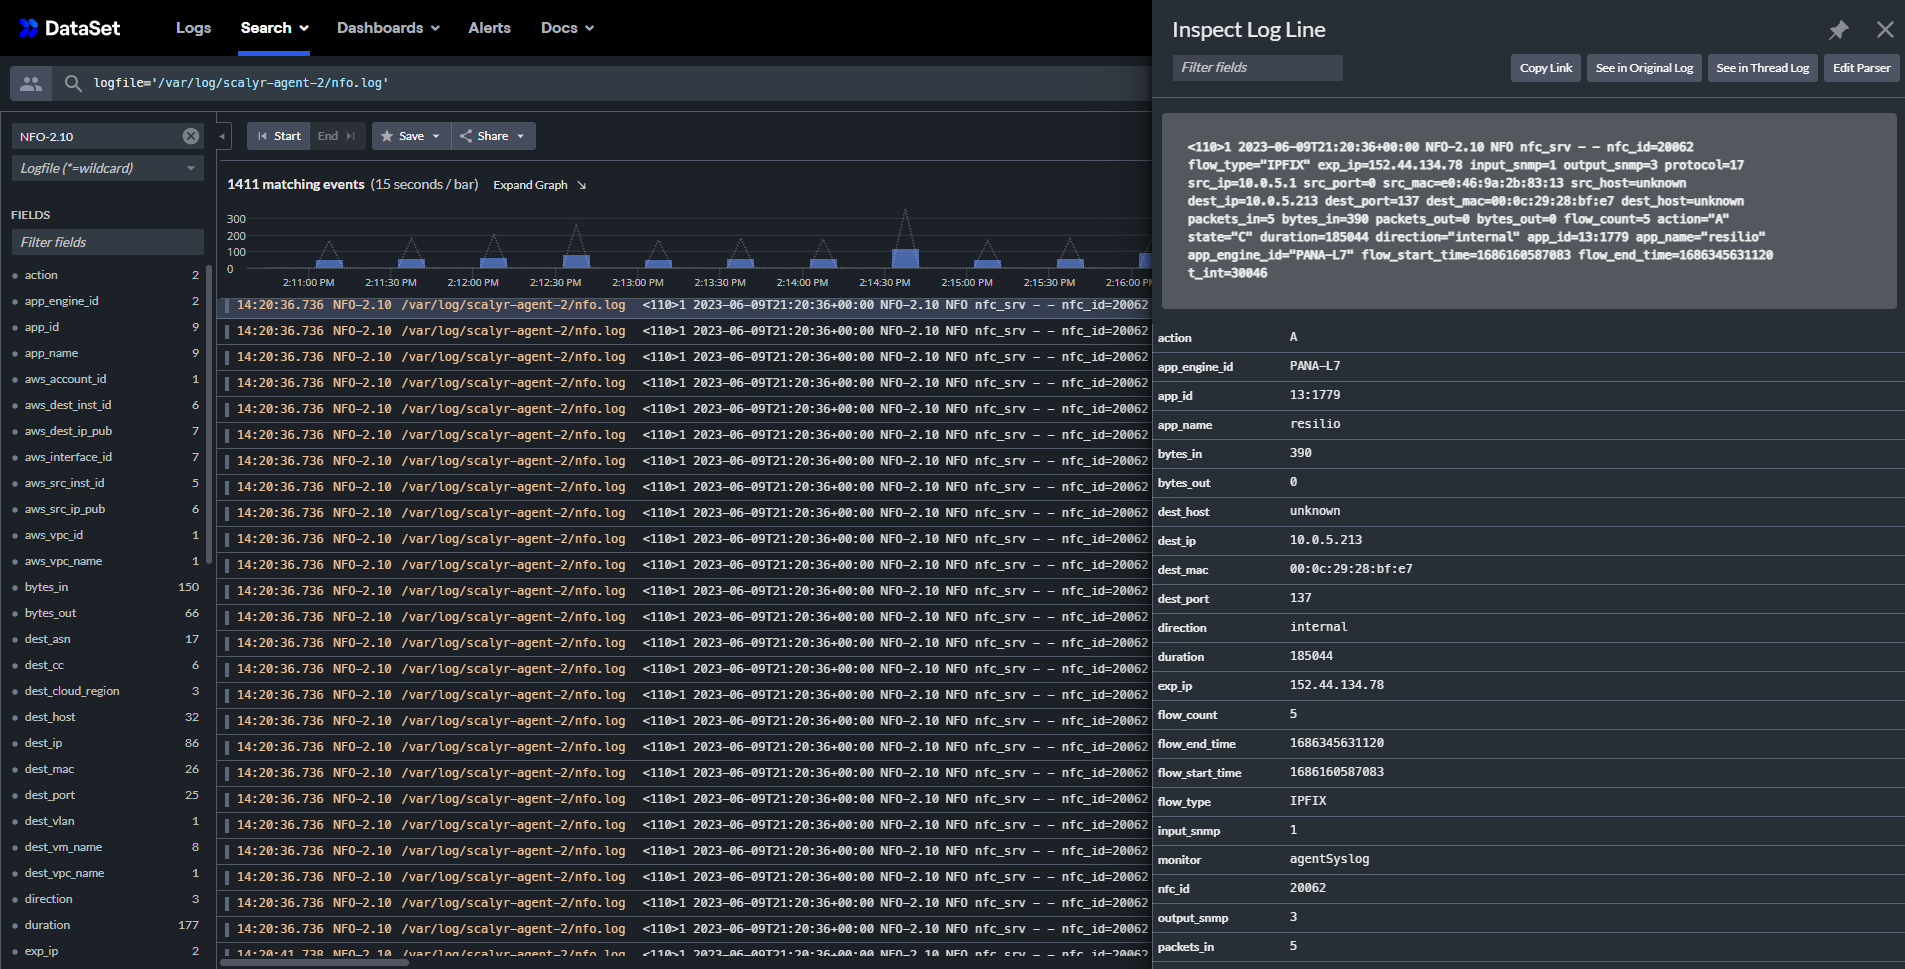
Centrally process and govern your logs in Datadog before sending them ...
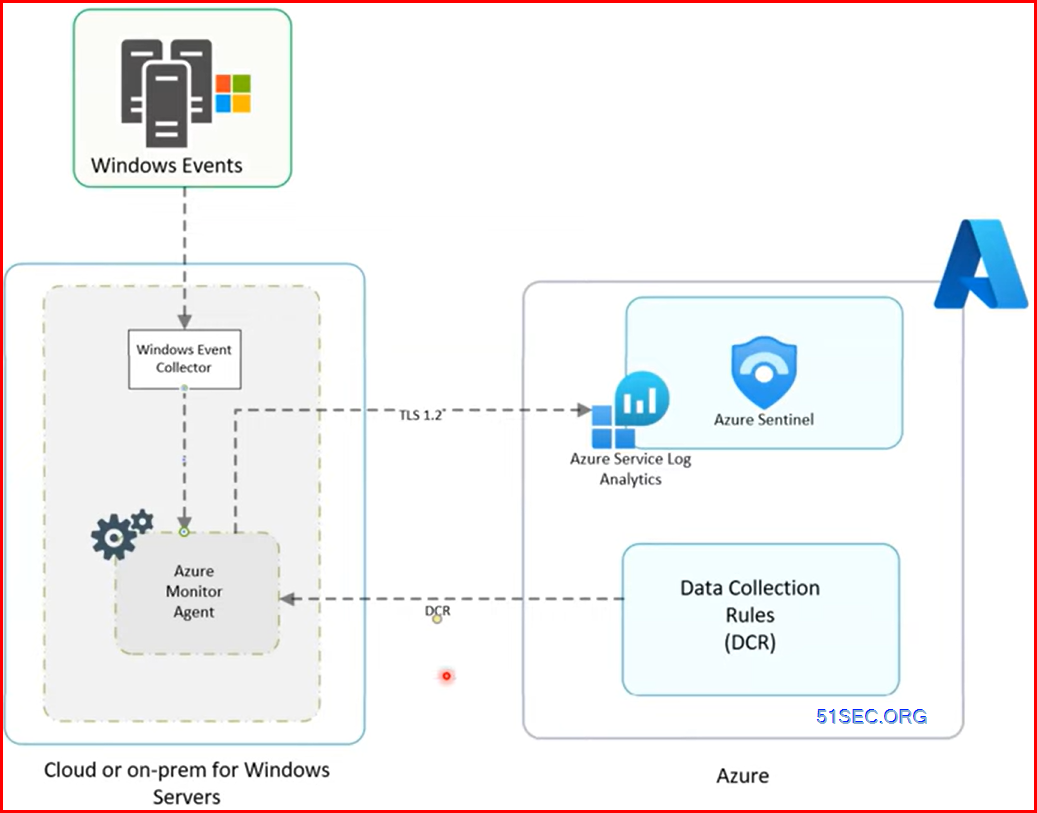
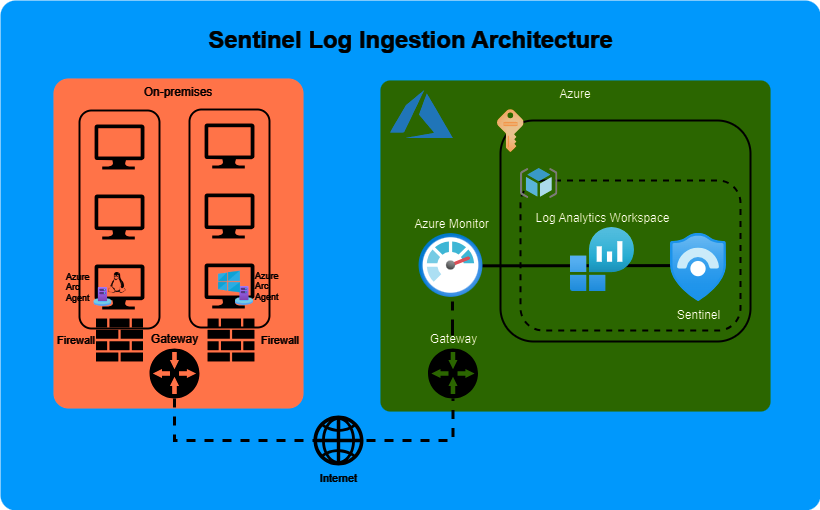
How To Ingest Logs From On-Premises Windows Server To Microsoft ...
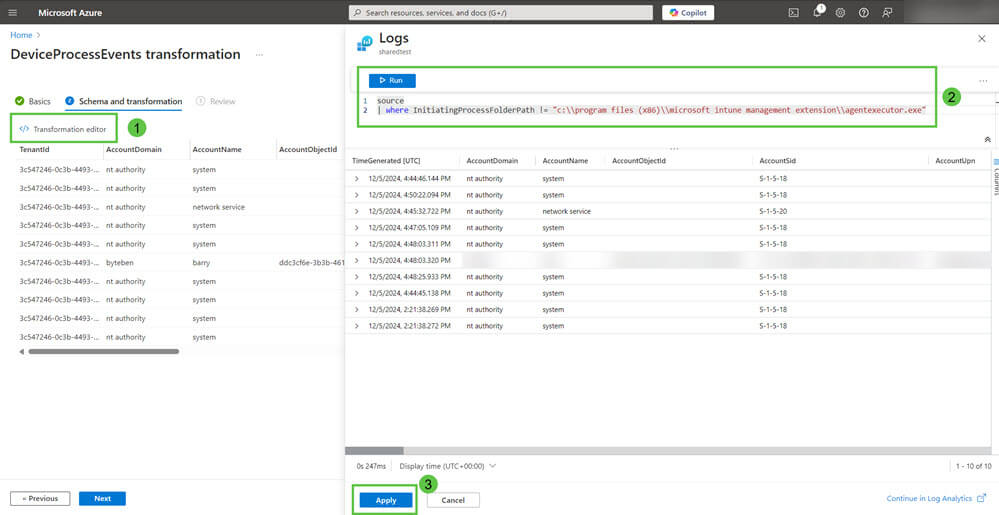
Auxiliary Logs Transformations in Microsoft Sentinel: A Step-by-Step ...