Showing 120 of 120on this page. Filters & sort apply to loaded results; URL updates for sharing.120 of 120 on this page
sk154872 - Microsoft Sentinel / Azure Log Analytics: Example ...
Azure Sentinel Log Query Scripts Collection : KQL (Kusto Query Language ...
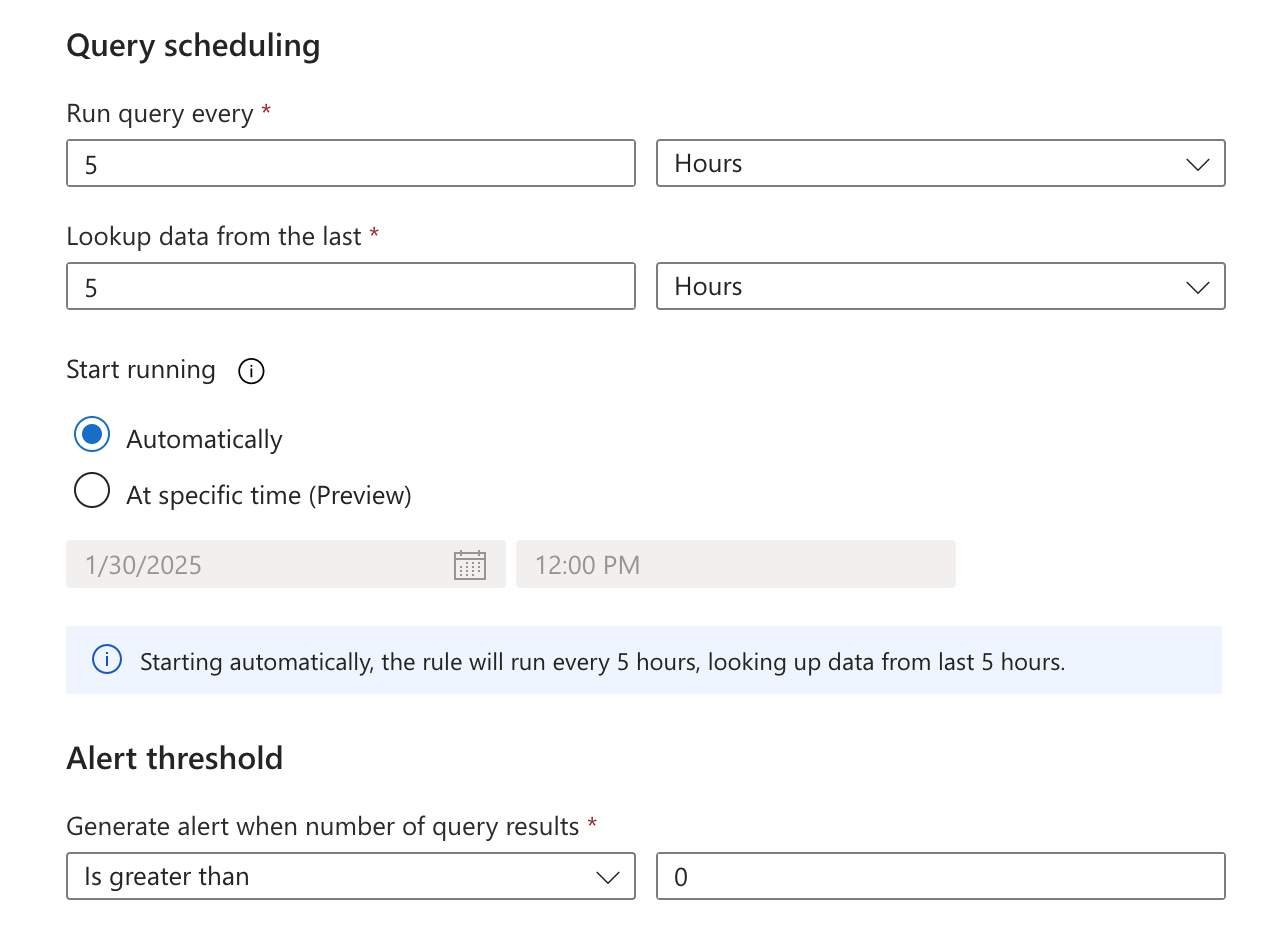
Create Analytic Rules To Query External Data In Microsoft Sentinel ...
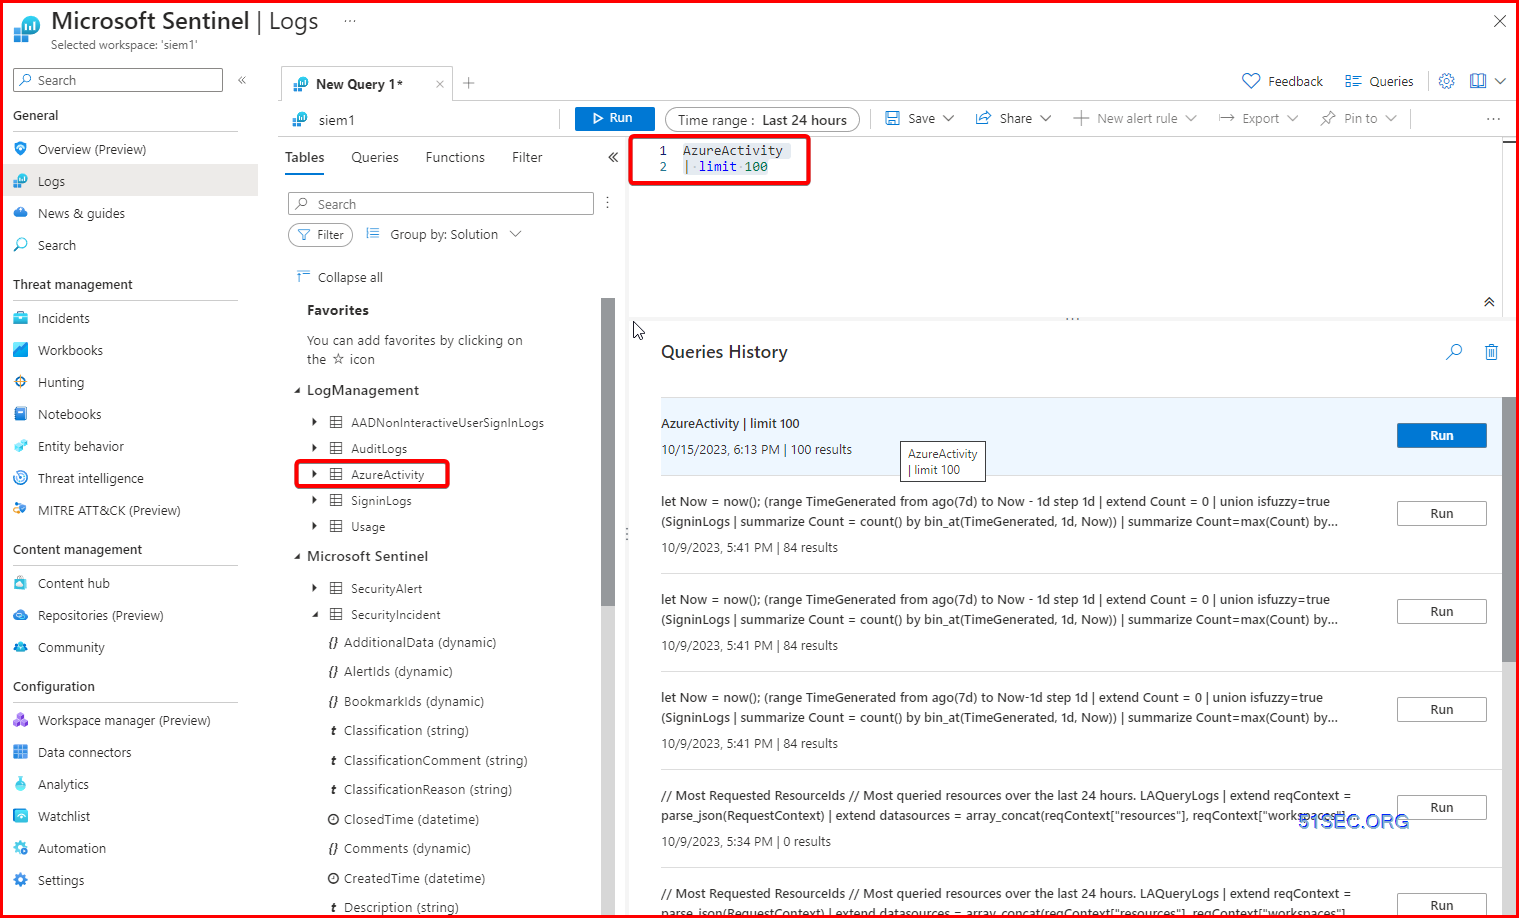
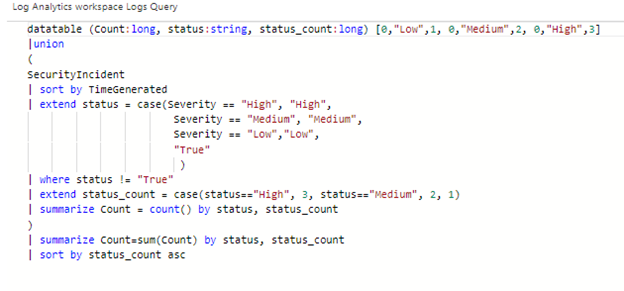
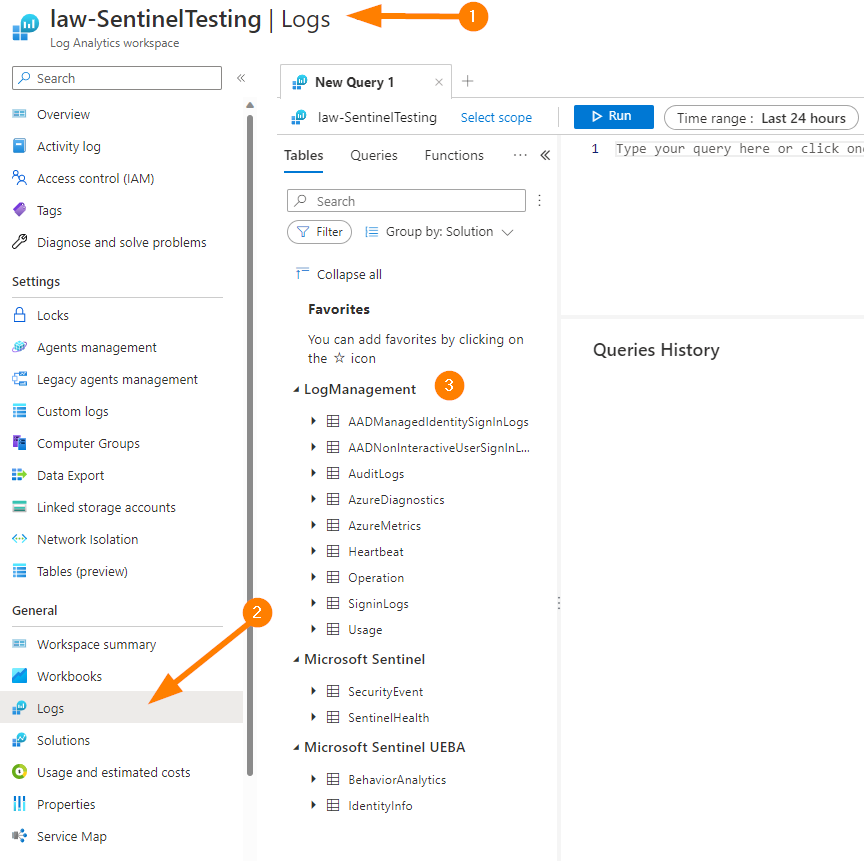
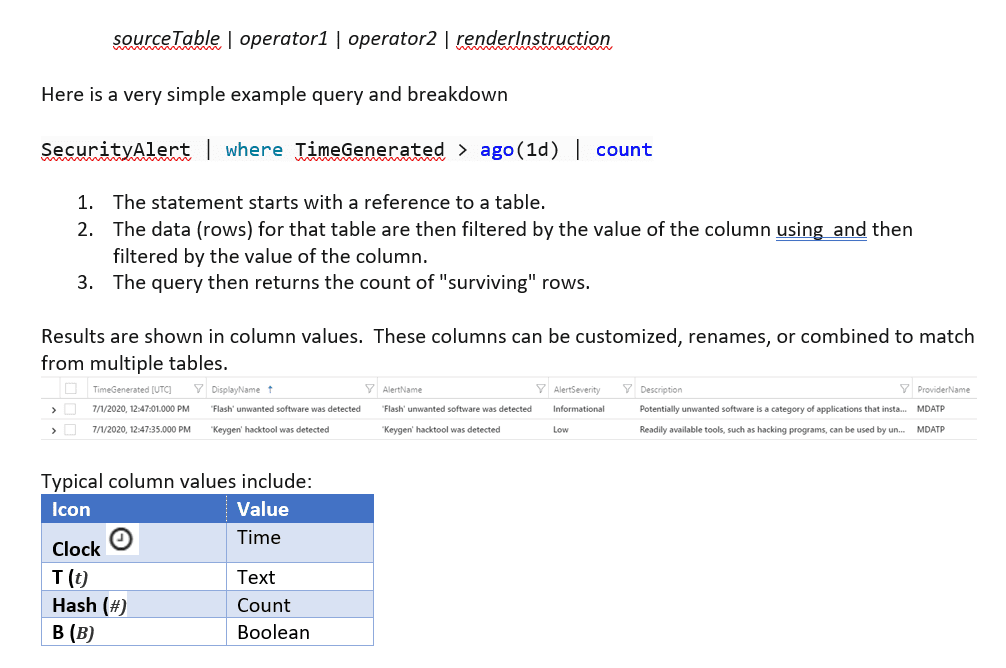
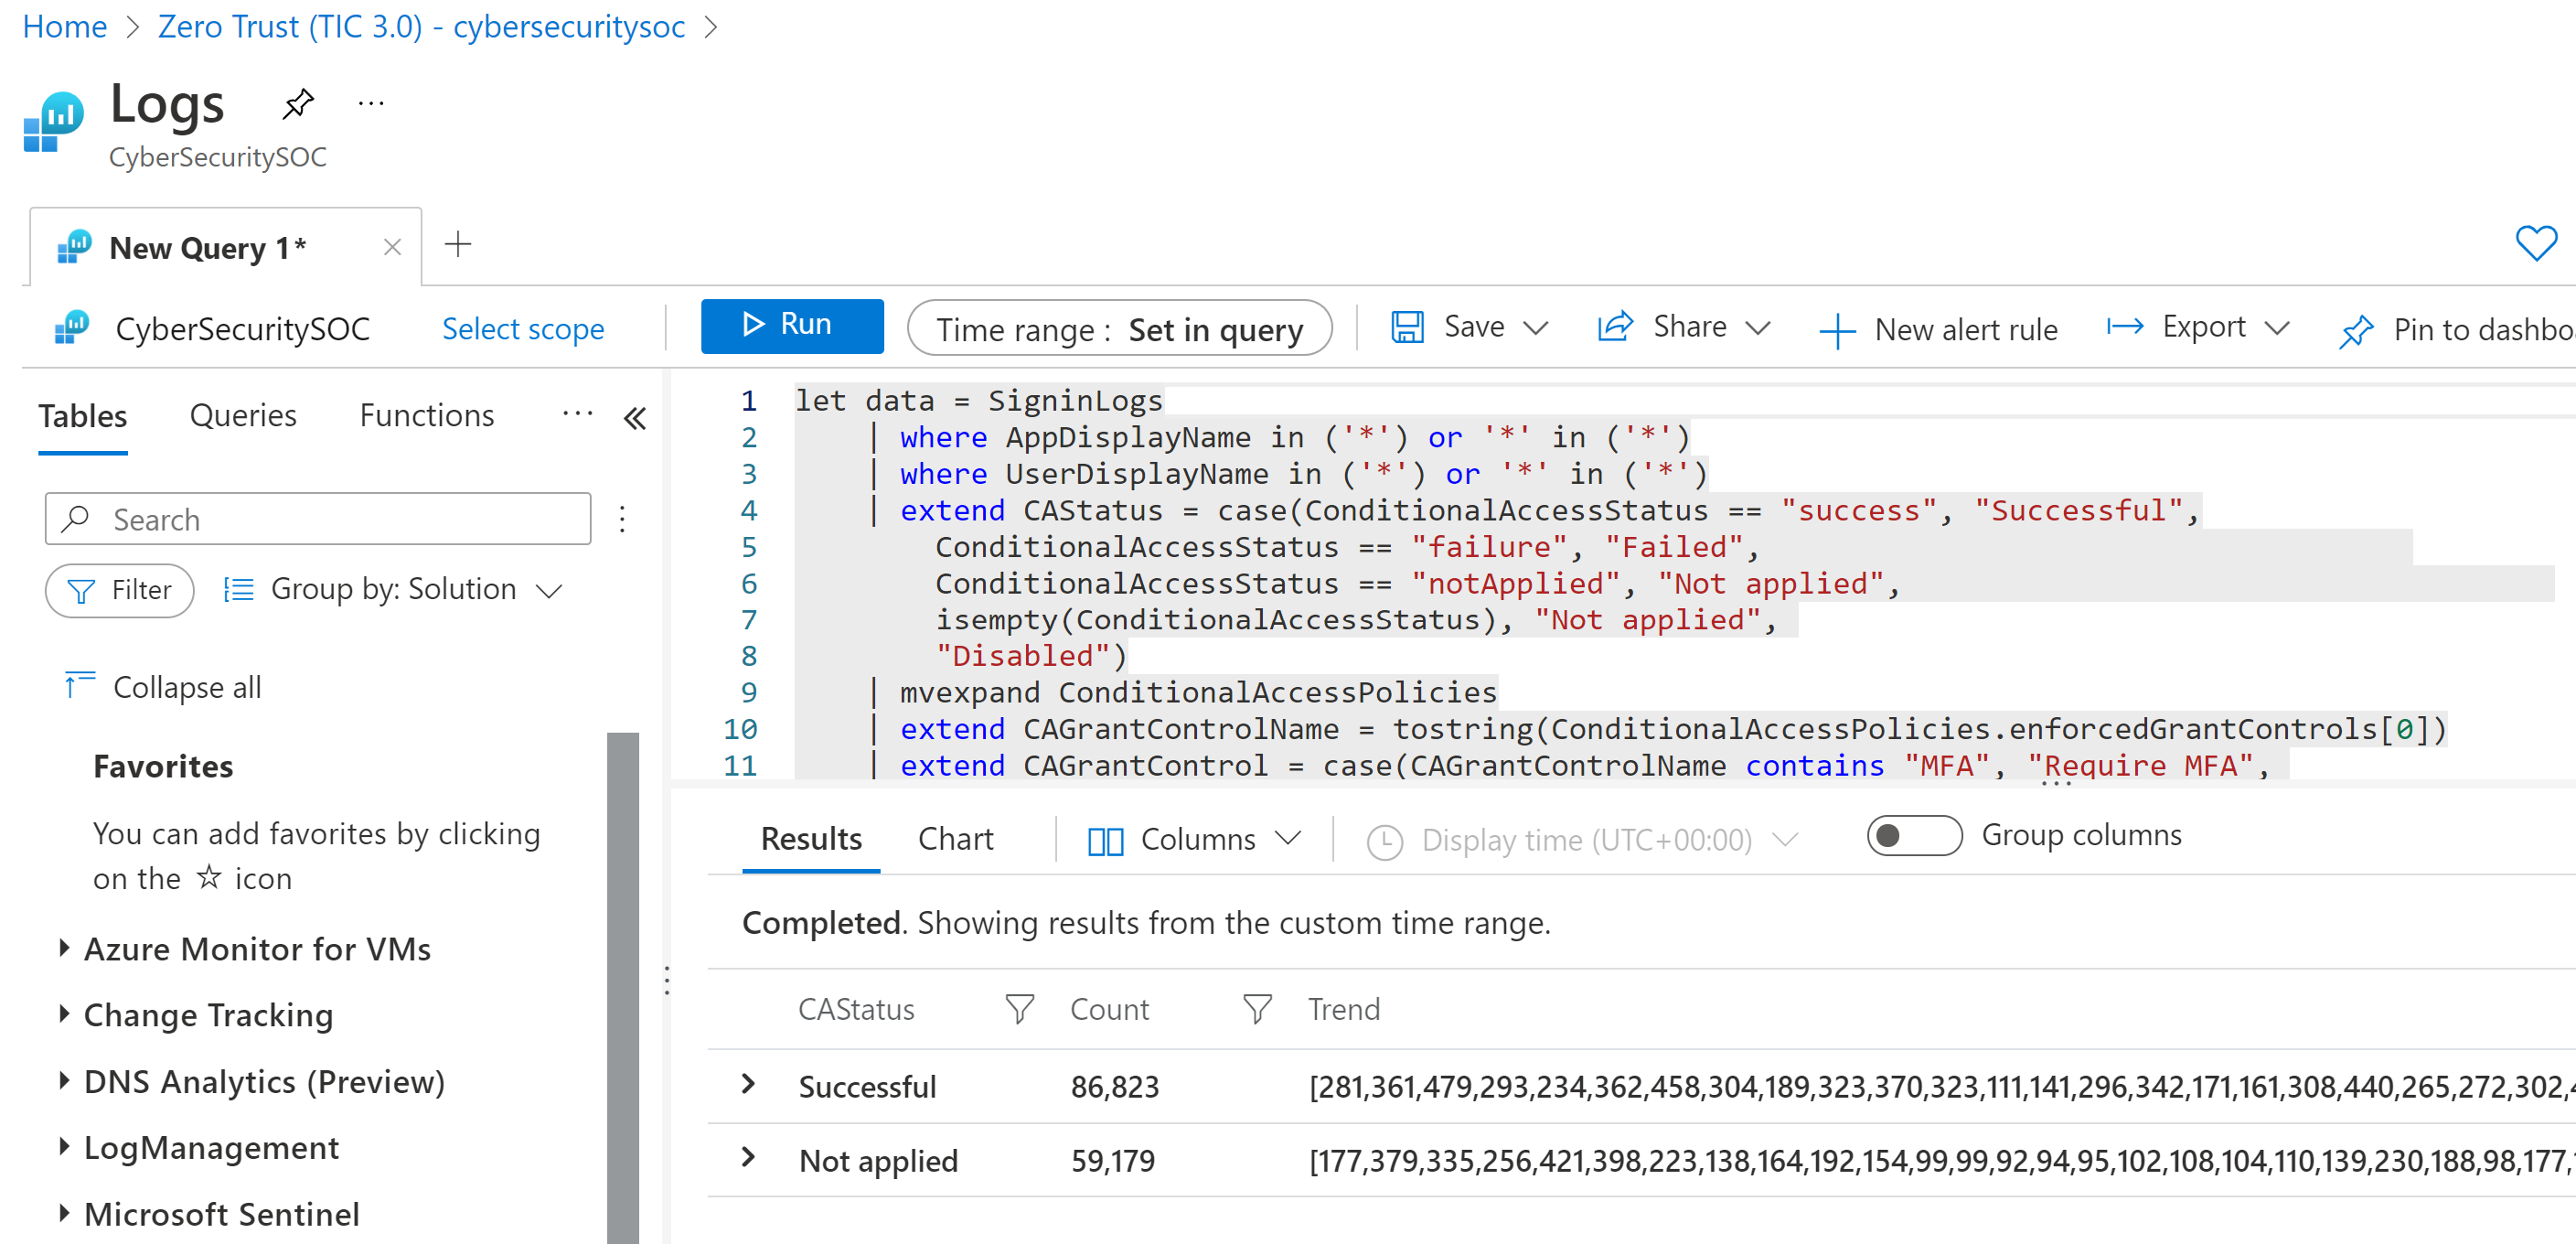
Microsoft Sentinel : KQL search query with examples
Sentinel / Azure Monitor Query Packs | Laurie Rhodes' Info
Query fulfillment process in the Sentinel System. 1. Sentinel ...
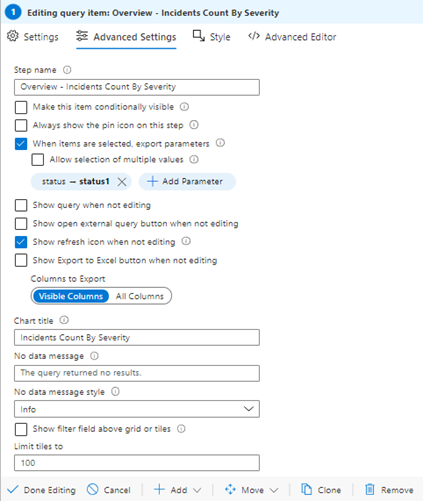
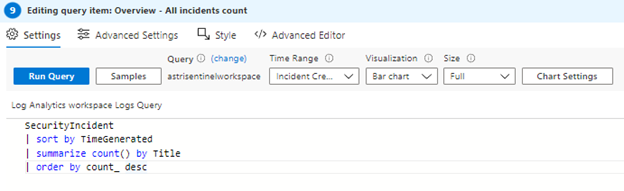
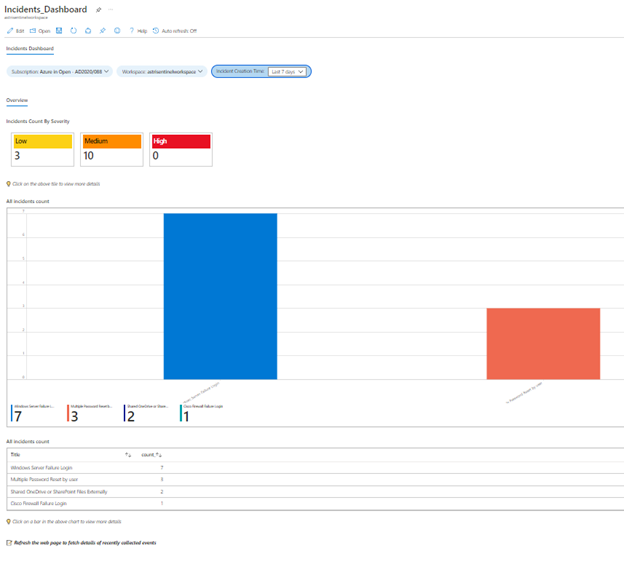
Azure Sentinel – A Guide for Customizing Sentinel Workbook (Kusto Query ...
Sentinel Query Optimization
Example Sentinel queries - Sophos Cloud Optix
IOC Query Generation for Microsoft Sentinel in Uncoder AI | SOC Prime
KQL Example Generator — Microsoft Sentinel Queries | jasperbernaers.com
Use Query Manager in SENTINEL to Modify Database (SQL) - SENTINEL ...
Find Your lost query in Microsoft Sentinel - YouTube
KQL Query to track your higher cost Azure Sentinel Tables – Concurrency
Microsoft Azure Sentinel Integration Guide
Build queries or rules with watchlists - Microsoft Sentinel | Microsoft ...
Common Tasks With KQL for Microsoft Sentinel - Kusto | Microsoft Learn
Run KQL queries against the Microsoft Sentinel data lake - Microsoft ...
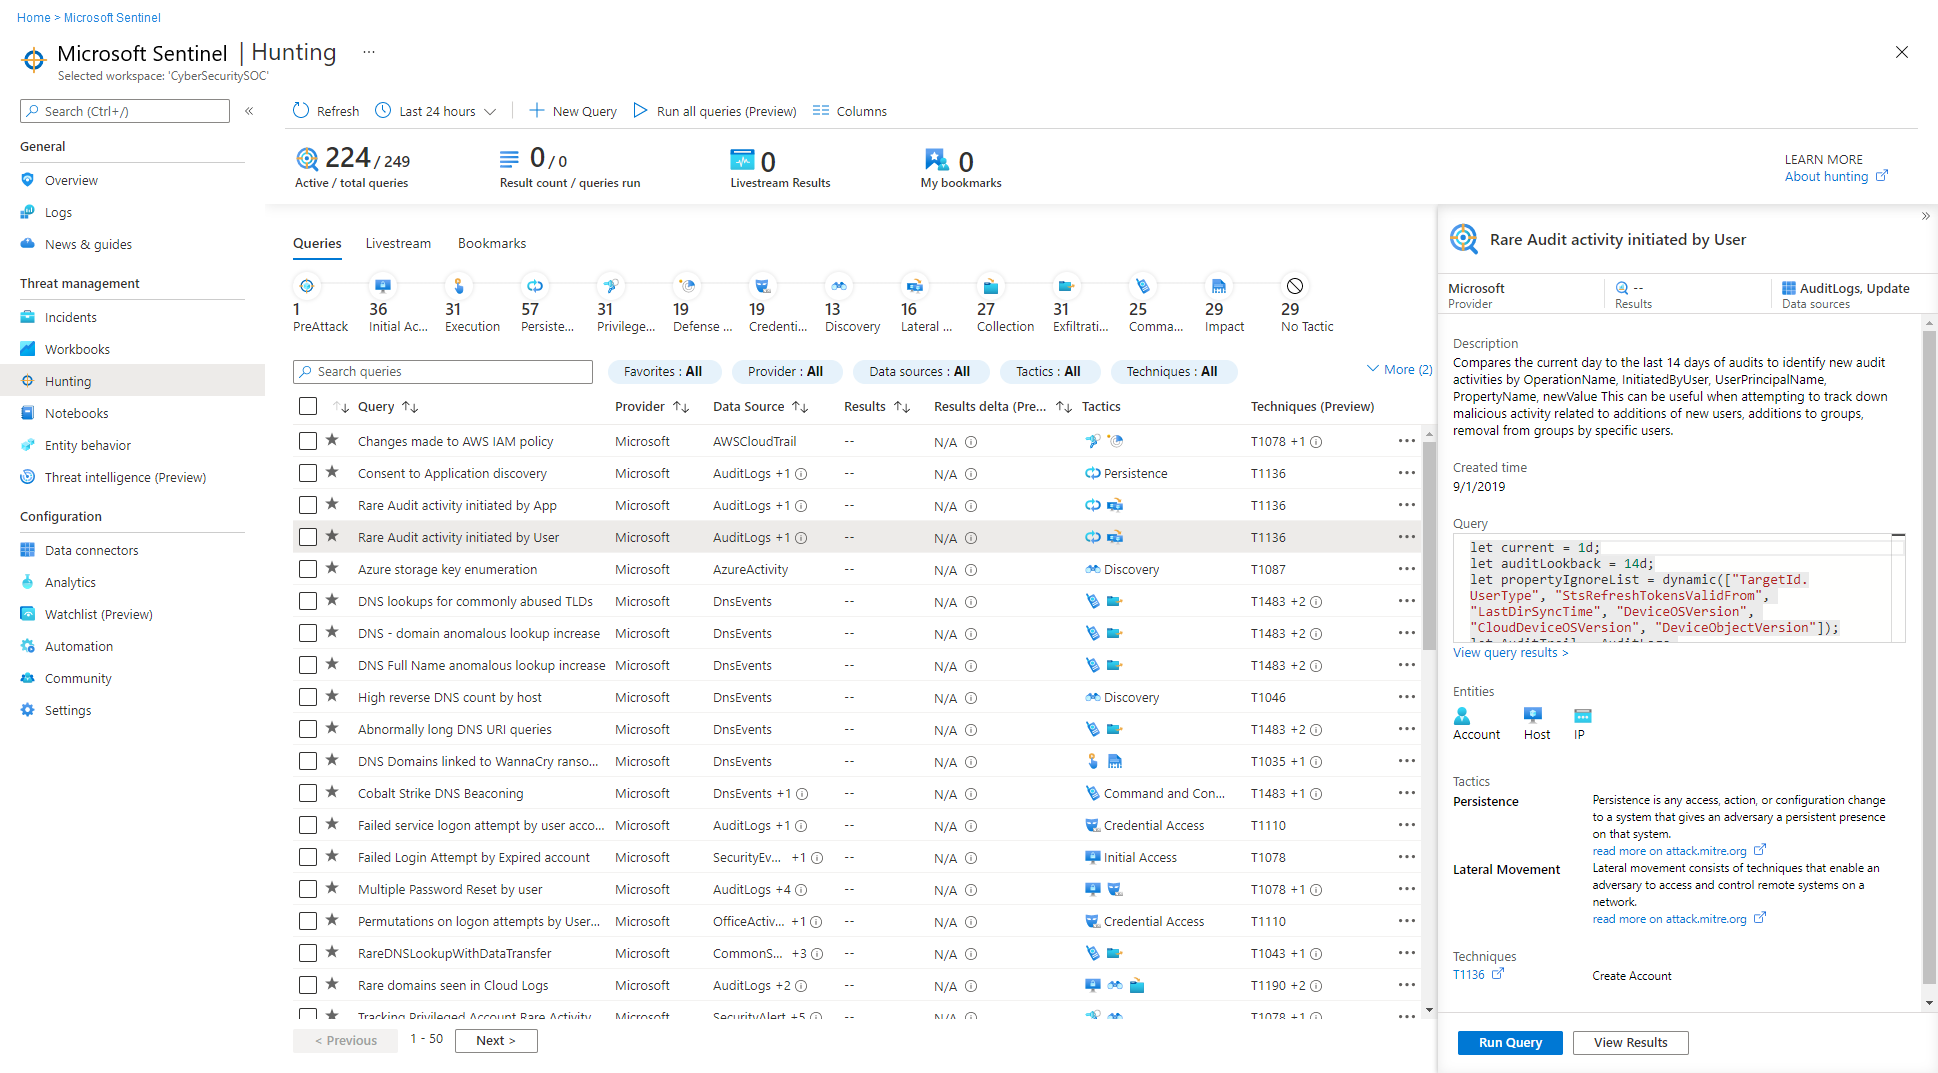
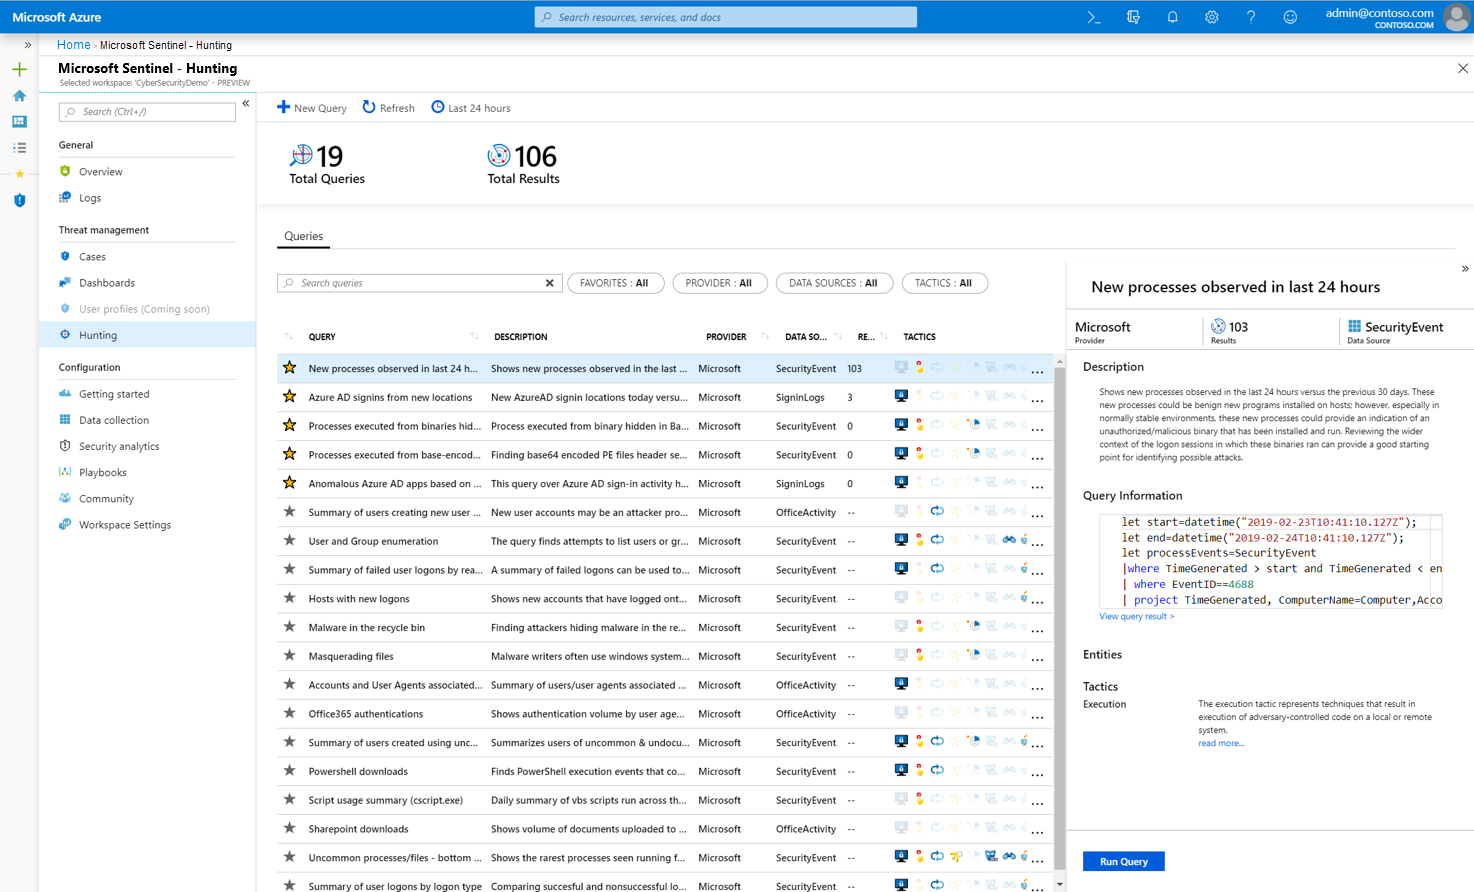
Hunting capabilities in Microsoft Sentinel | Microsoft Learn
Eseguire la ricerca con i segnalibri in Microsoft Sentinel | Microsoft ...
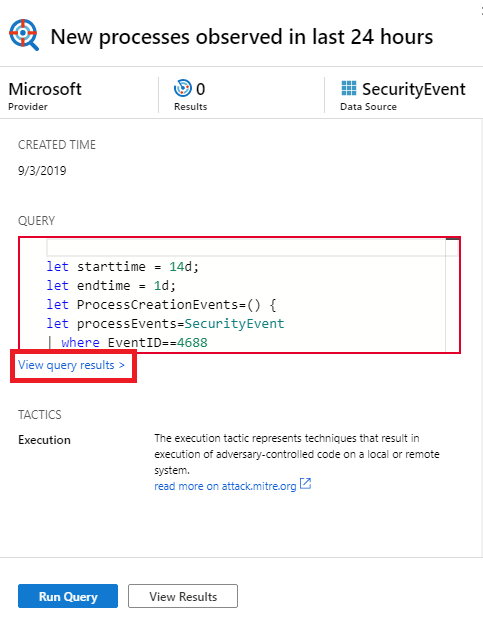
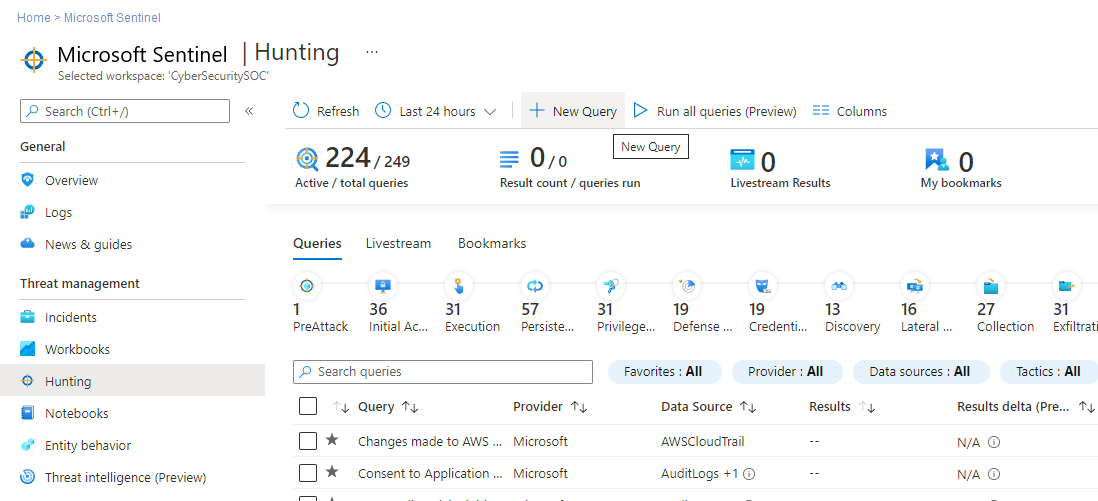
Create custom hunting queries in Microsoft Sentinel - Microsoft ...
Creating Microsoft Azure Sentinel Rules in Your SIEM Instance | SOC Prime
Uncoder AI Turns IOCs from Threat Reports into Microsoft Sentinel Queries
Optimize Microsoft Sentinel Log Retention With Azure Data Explorer ...
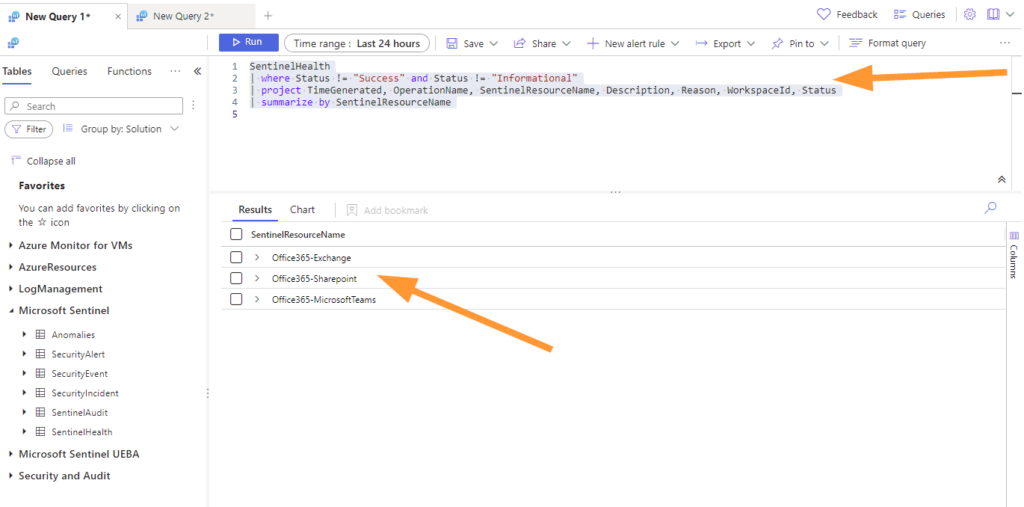
Data Connector Health Monitoring on Microsoft Sentinel – NVISO Labs
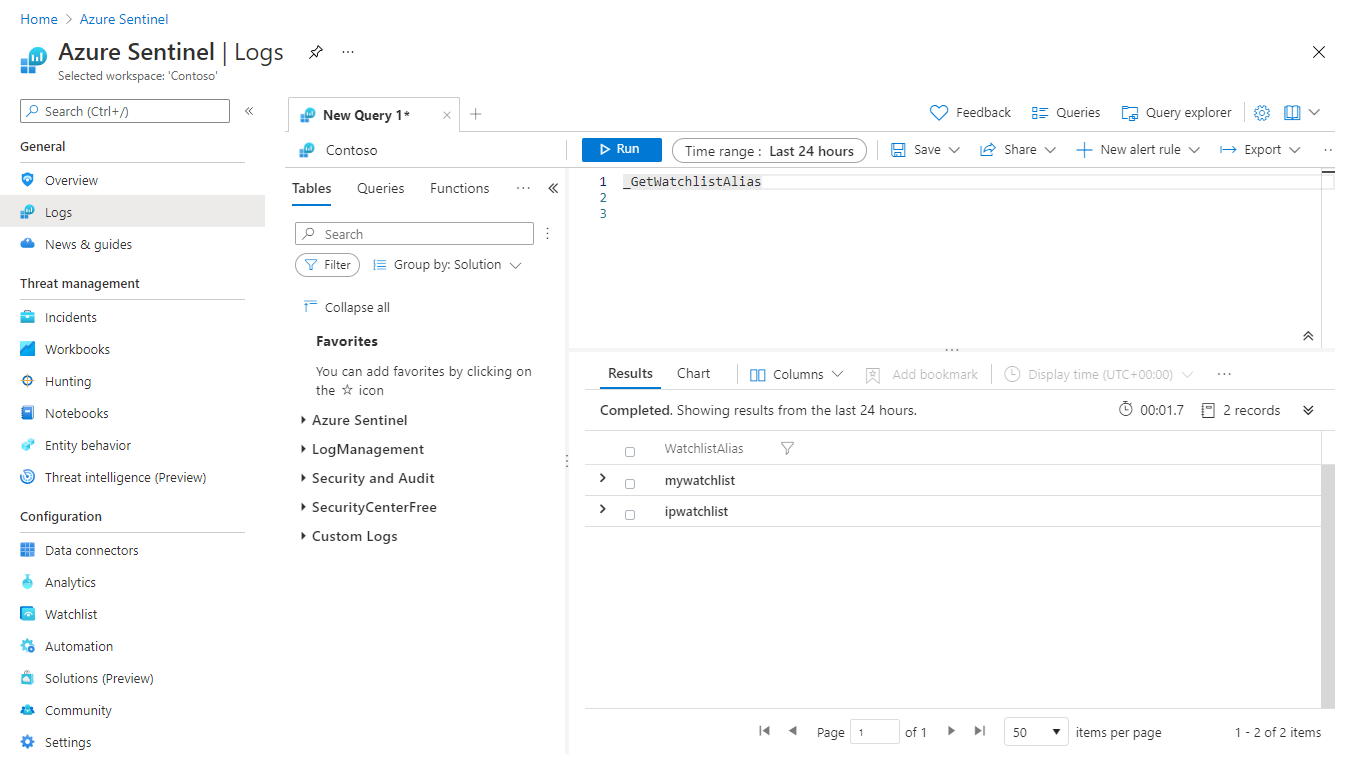
How to Use Watchlist in Azure Sentinel - CHARBEL NEMNOM - MVP | MCT ...
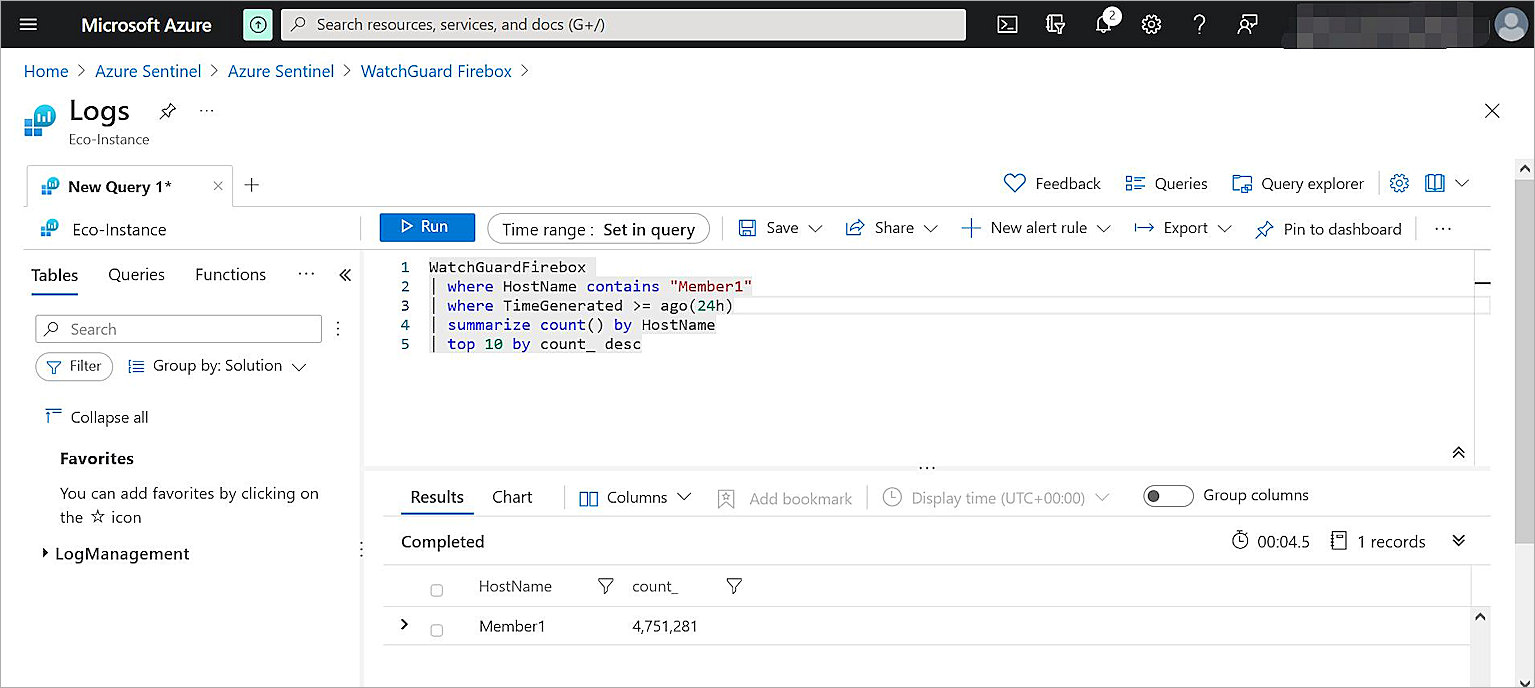
Microsoft Sentinel with WatchGuard Firebox Integration Guide
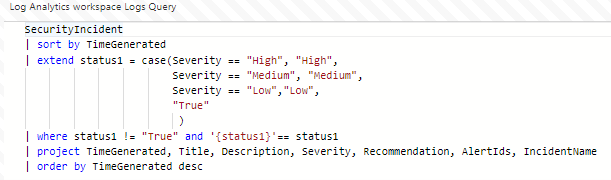
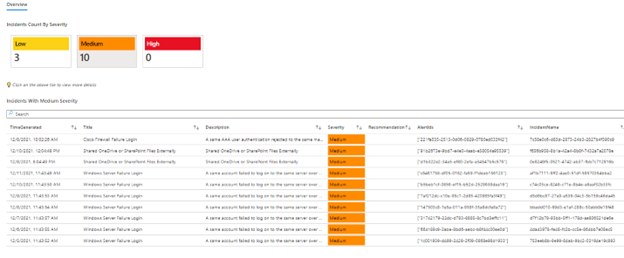
Sentinel & Log Analytics – How to Create Incidents to Test with – Part ...
Using KQL to Master Sentinel Data | Practical365
Interesting Truth about Threat Hunting using Microsoft Sentinel ...
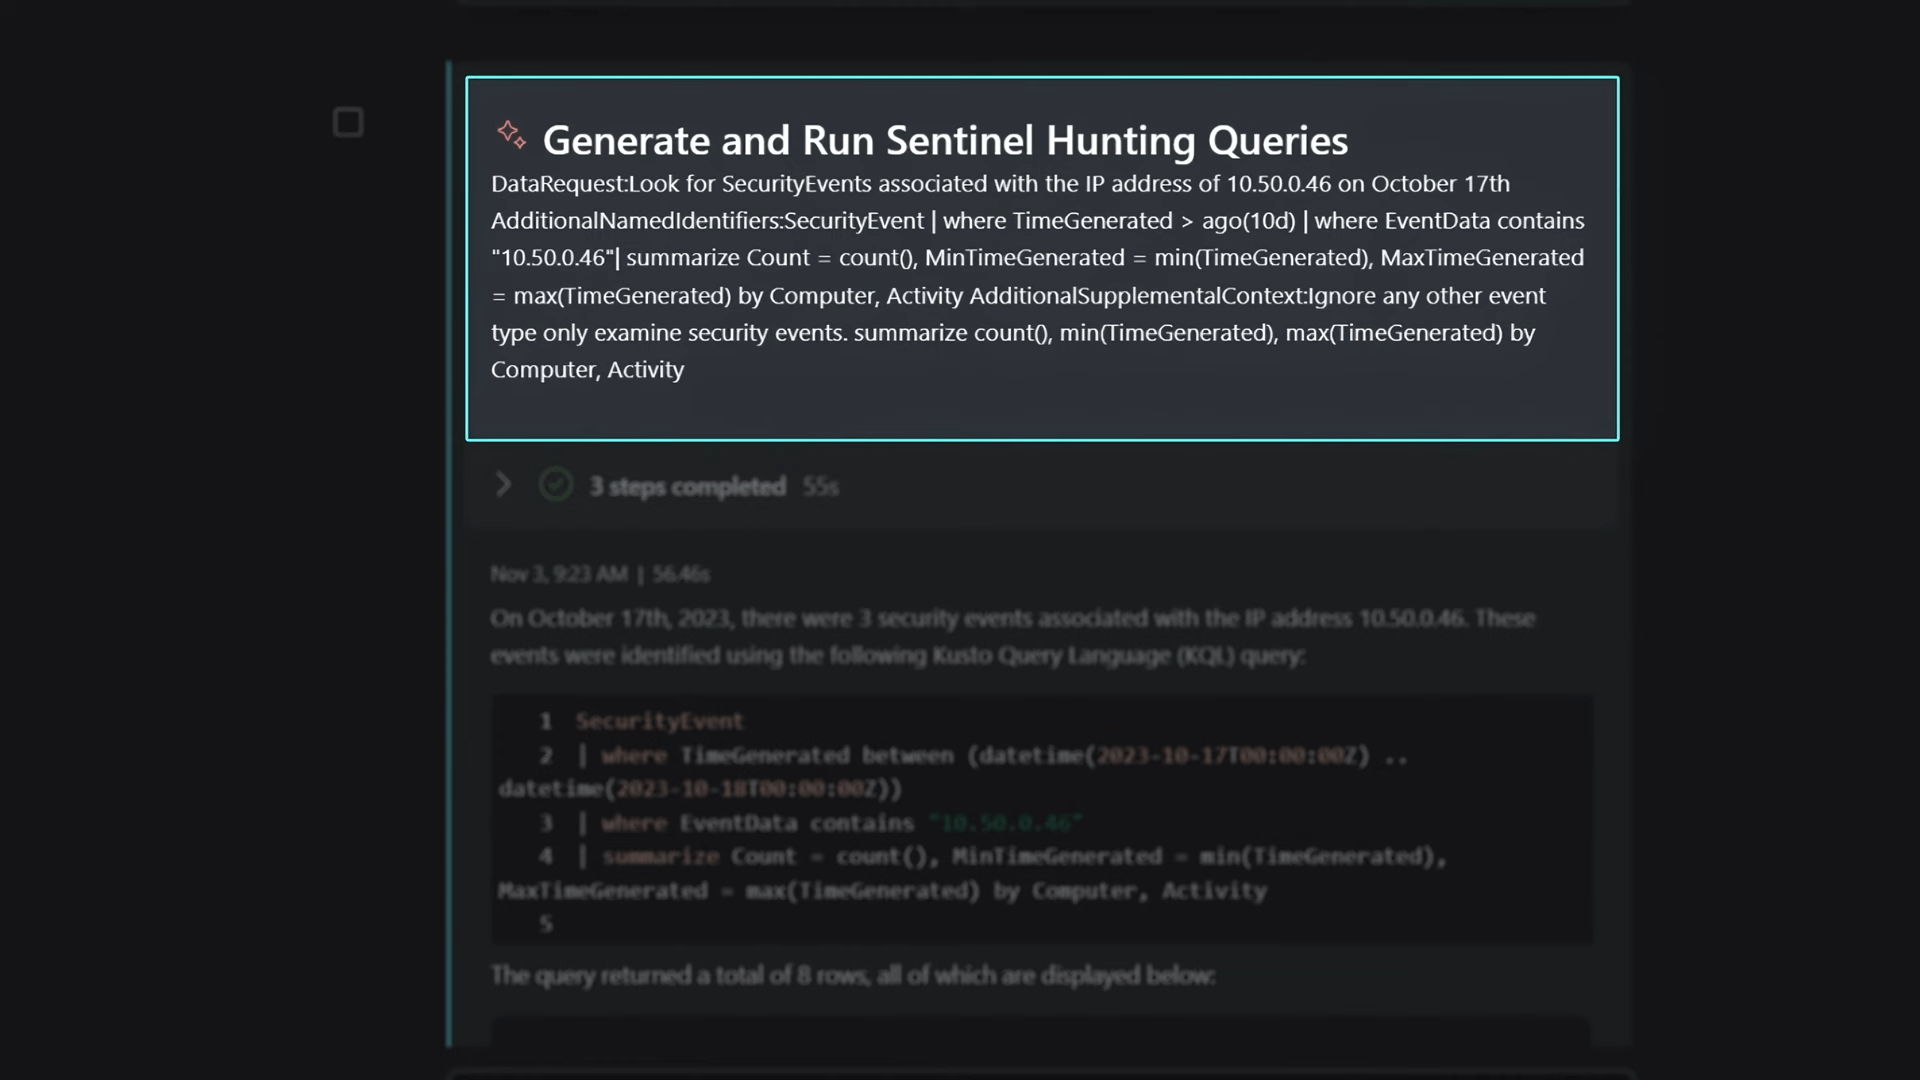
AI Validation for Sentinel Queries: Smarter KQL with Uncoder AI | SOC Prime
Using Dynamic Data Types in Sentinel | Community
Onboard to Microsoft Sentinel | Microsoft Learn
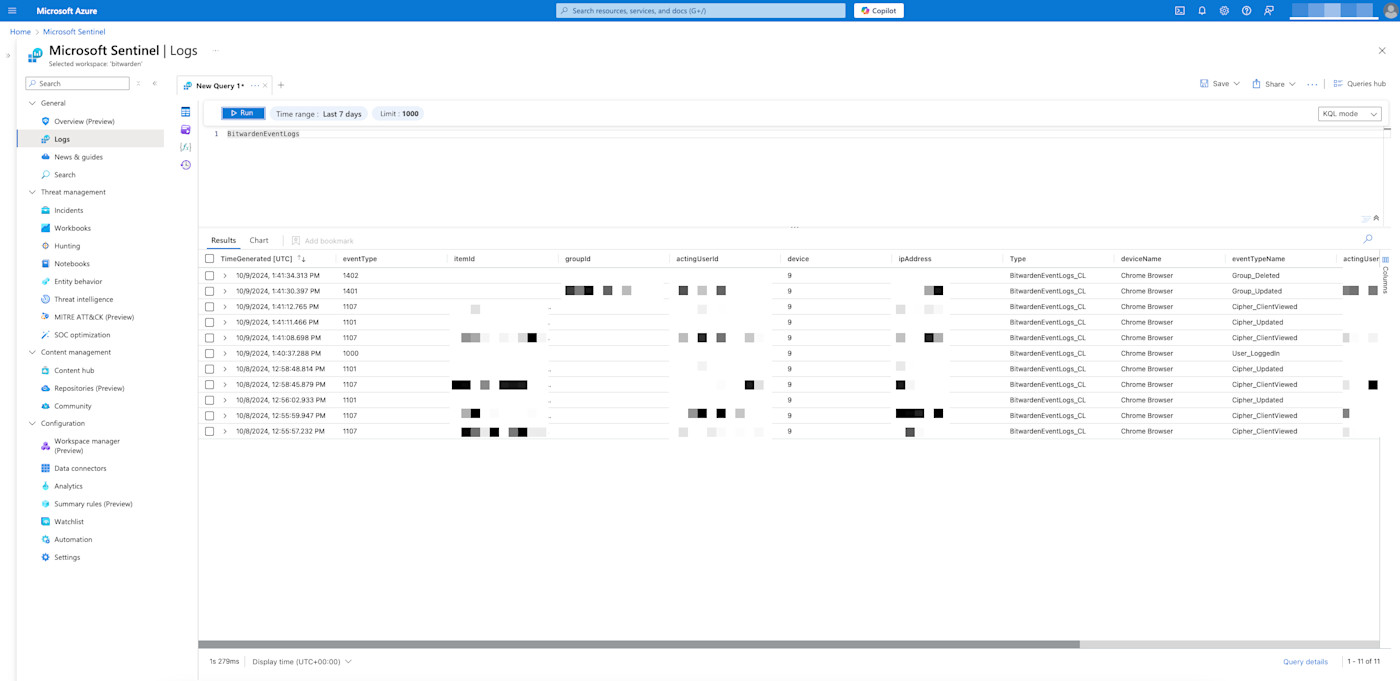
Microsoft Sentinel SIEM | Bitwarden
Use Microsoft Sentinel custom functions in advanced hunting in ...
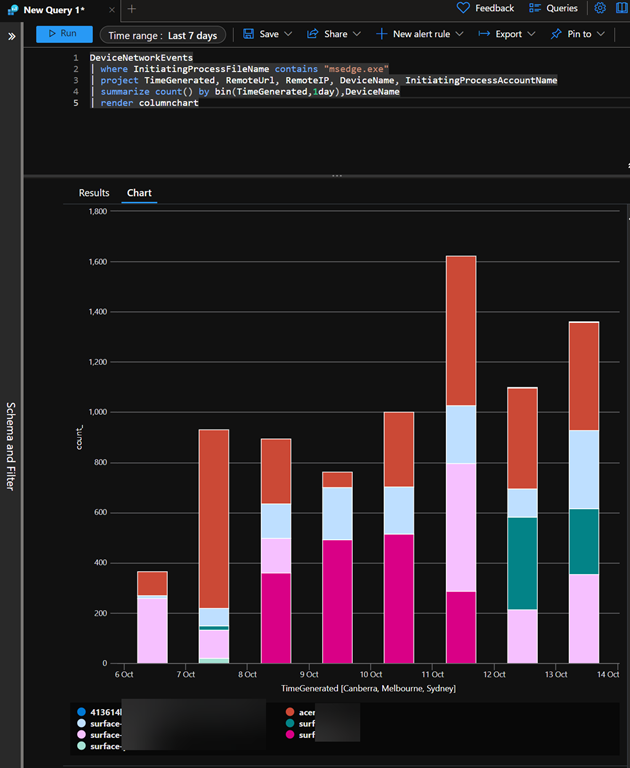
Microsoft Sentinel : KQL project operator
Visualize custom graphs in Microsoft Sentinel graph (preview ...
Microsoft Sentinel - Configuring PowerBI for Advanced Reporting ...
Sentinel Data Connector Health Monitoring – AzureTracks
GitHub - RWilliamMcCrory/AzureSentinel: Azure Sentinel Tutorial MAP ...
How to Use Threat Intelligence Indicator Feeds with Microsoft Sentinel ...
Optimize Sentinel Logs for Intune via Defender XDR - Patch My PC
Azure Sentinelはどのような基盤を組み込んでいますか?, Azure Sentinel 価格 – ZXUX
Using Sentinel to determine application usage – CIAOPS
Build queries or rules with watchlists - Microsoft Sentinel | Azure Docs
Azure sentinel | PPTX
How to use Microsoft Sentinel with Office 365 to find risks | TechTarget
Introduction to Microsoft Sentinel | Microsoft Press Store
Integrating StackRox with Microsoft Sentinel | StackRox Community
Getting started with Microsoft Sentinel
Monitor Summary Rules in Microsoft Sentinel 9
Azure Sentinel Training 2024-The ABSOLUTE Complete NINJA Guide-
Utilizing Log Analytics, Microsoft XDR & Azure Sentinel
Azure Sentinel Lists and Rules – Frank Cardinale
Google Threat Intelligence for MSFT Sentinel
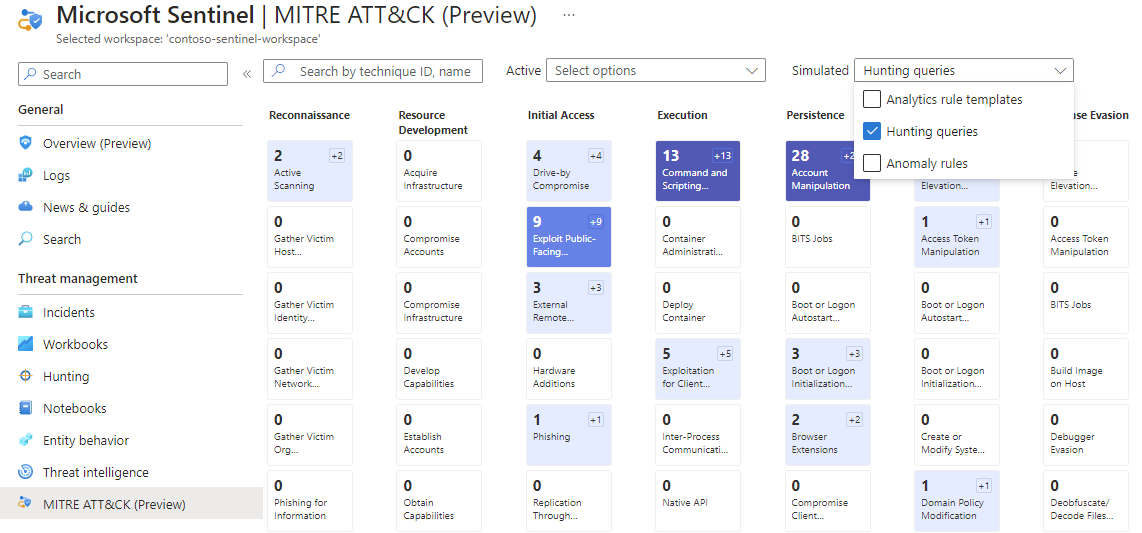
Conduct end-to-end threat hunting with Hunts - Microsoft Sentinel ...
Threat Hunting and the New Hunts in Sentinel – SEC-LABS R&D
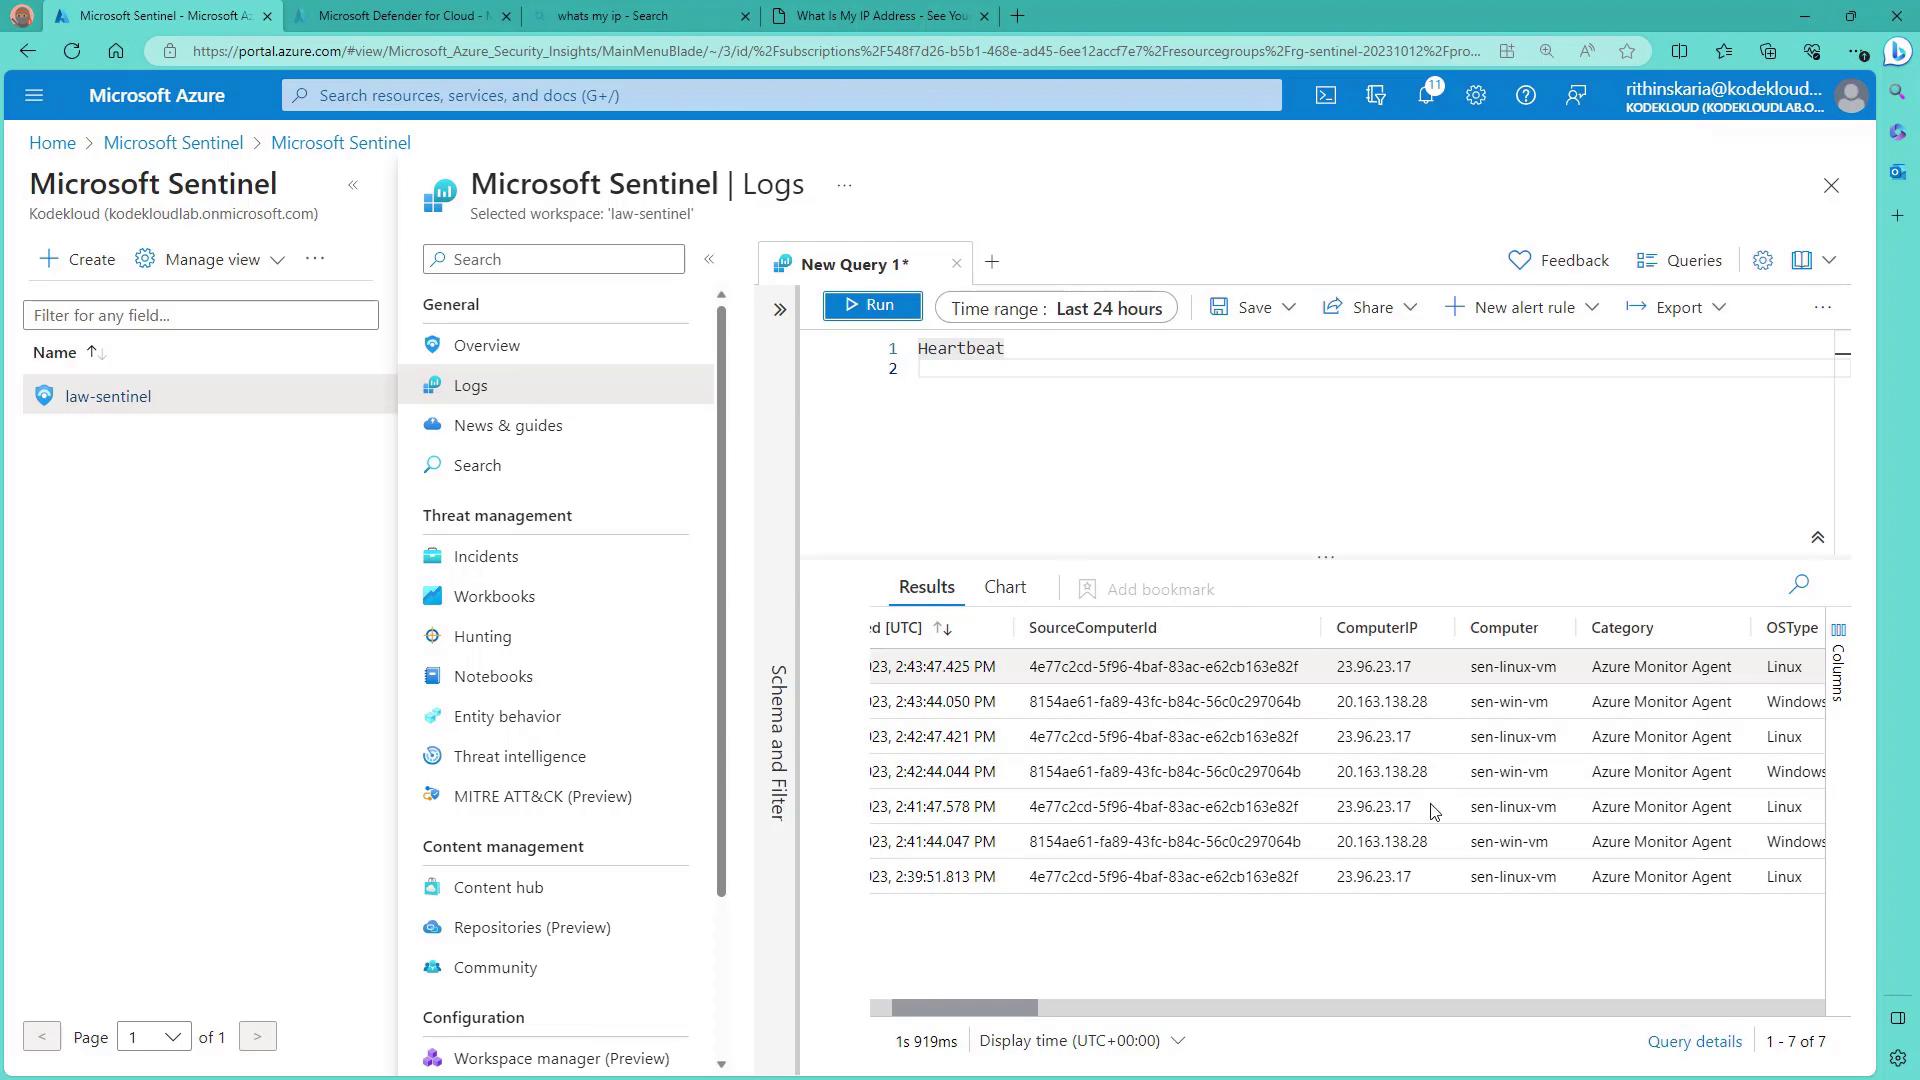
Configure data connections to Sentinel - KodeKloud
TA for Sentinel Queries | Splunkbase
How do I run a KQL query for security alerts/incidents in Microsoft ...
How to Check the Health State of Microsoft Sentinel – AzureTracks
Creating custom Azure Sentinel Hunting Queries – SEC-LABS R&D
Azure Sentinel Hunting - eGroup US
Search for specific events across large datasets in Microsoft Sentinel ...
Monitor Zero Trust (TIC 3.0) security architectures with Microsoft ...
Cortex XSOAR Tips & Tricks – Leveraging dynamic sections – number ...
What is Microsoft Sentinel? | Microsoft Learn
Translate raw security logs to behavioral insights using UEBA behaviors ...
Customize Your EDR To Adapt To Your Environment With SentinelOne ...
Investigate and Respond to Incidents with Copilot for Security - Bespin ...
PPT - The LC-3 – Chapter 5 PowerPoint Presentation, free download - ID ...
Getting Started with Microsoft Azure Sentinel: Part 2
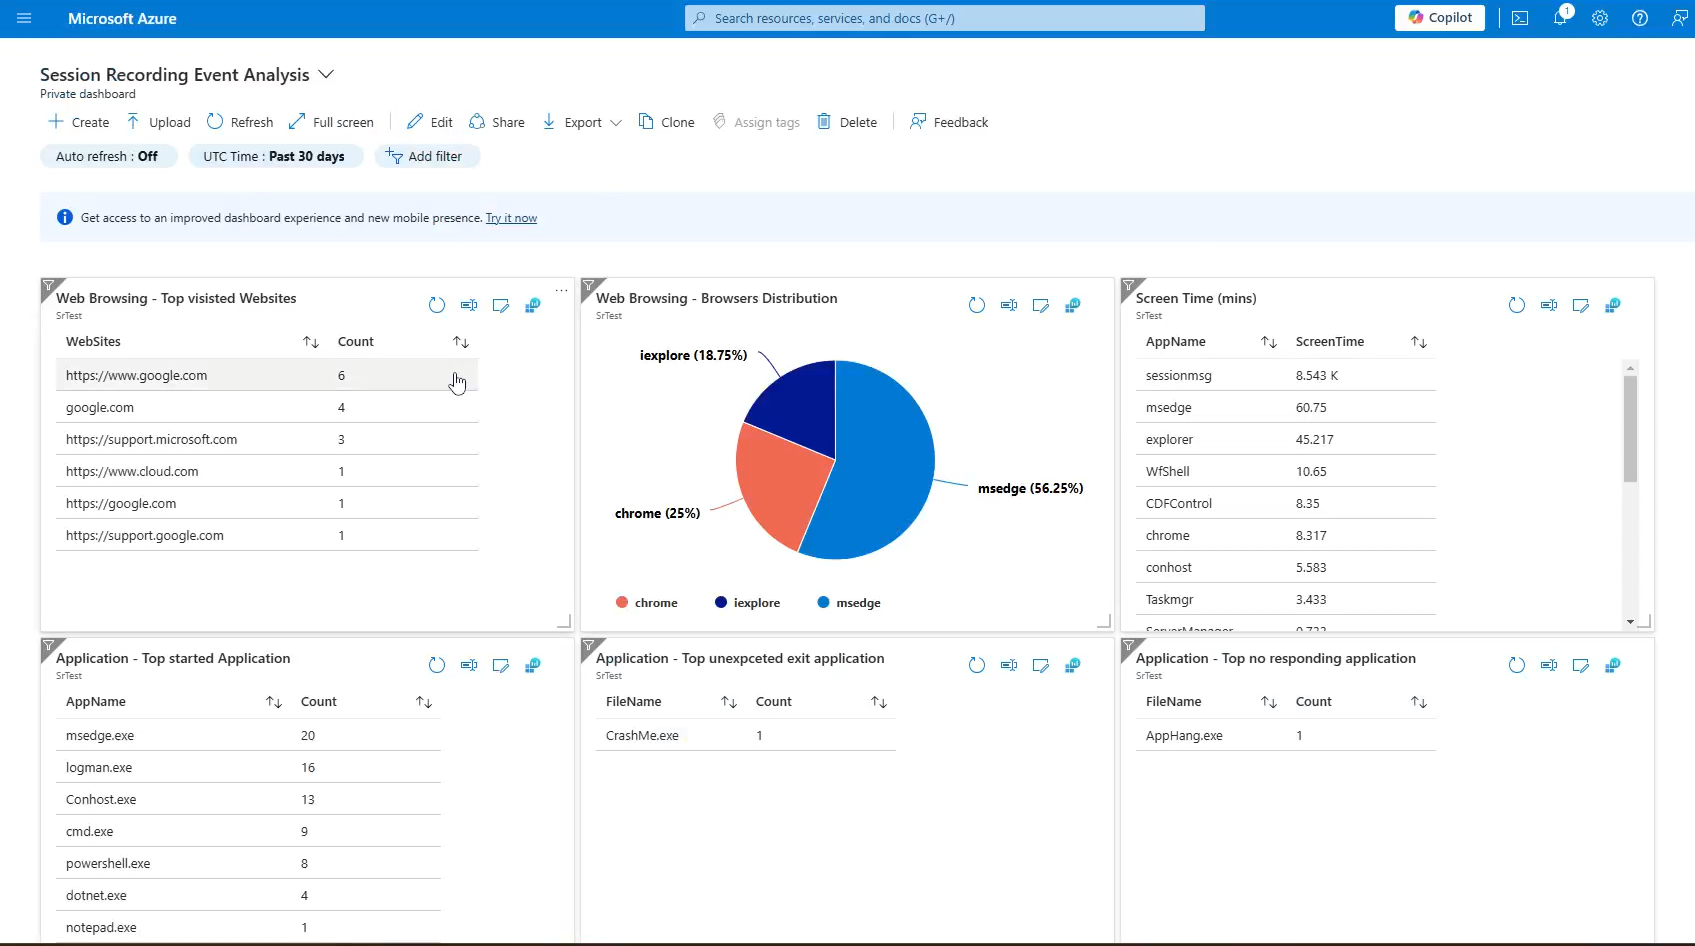
Third-party SIEM integration | Session Recording service
Microsoft shifts to a new threat actor naming taxonomy | Microsoft ...
Top 7 Azure Reporting Tools for Efficient Data Management
Triage incidents with enriched threat intelligence | Microsoft Learn
External
GitHub - 0xbythesecond/Microsoft-Sentinel
Sentinel-Queries/Functions/Function-UserInvestigation.kql at main ...
GitHub - msrarun/Sentinel-Queries1: Collection of KQL queries
GitHub - ericlindsey/sentinel_query_download: Uses ASF API to search ...