Showing 119 of 119on this page. Filters & sort apply to loaded results; URL updates for sharing.119 of 119 on this page
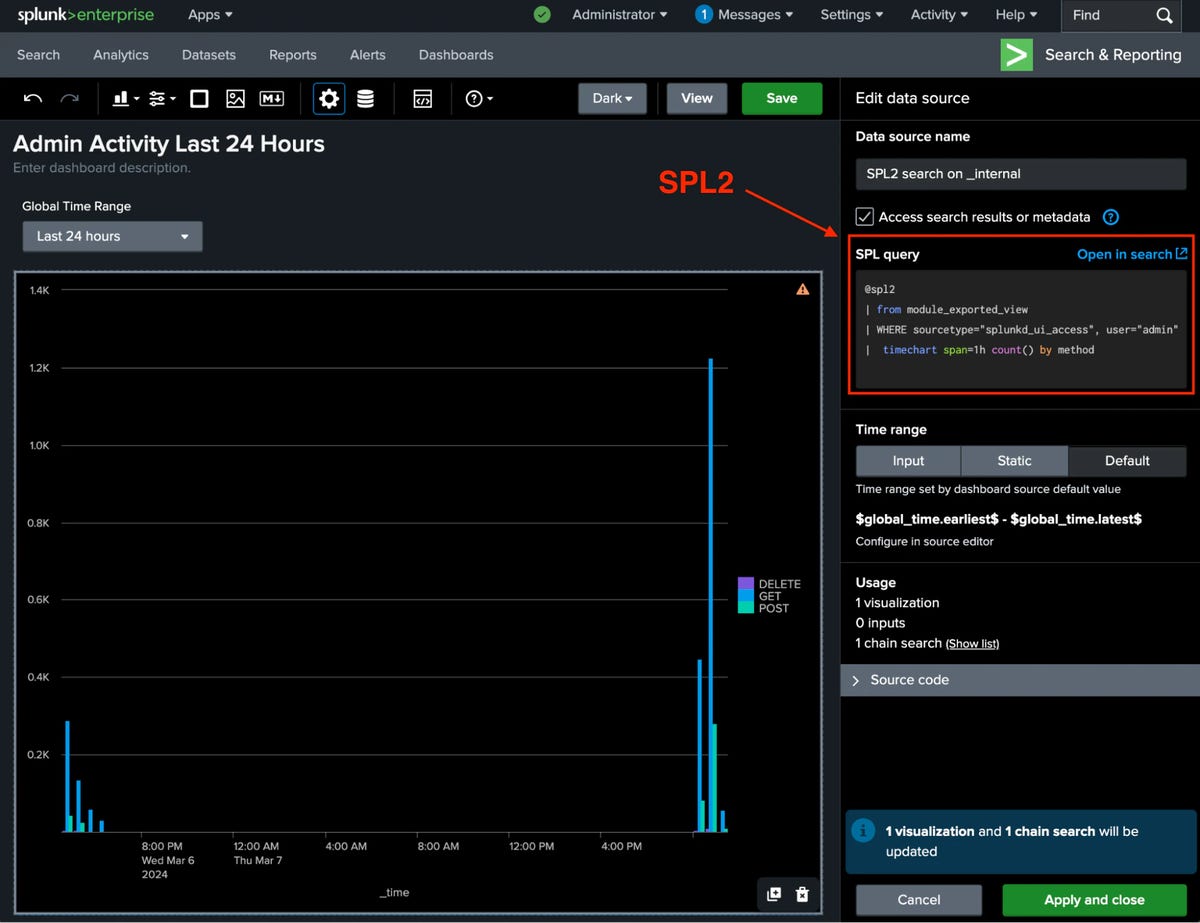
Announcing the Public Beta of SPL2 in Splunk Enterprise | Splunk
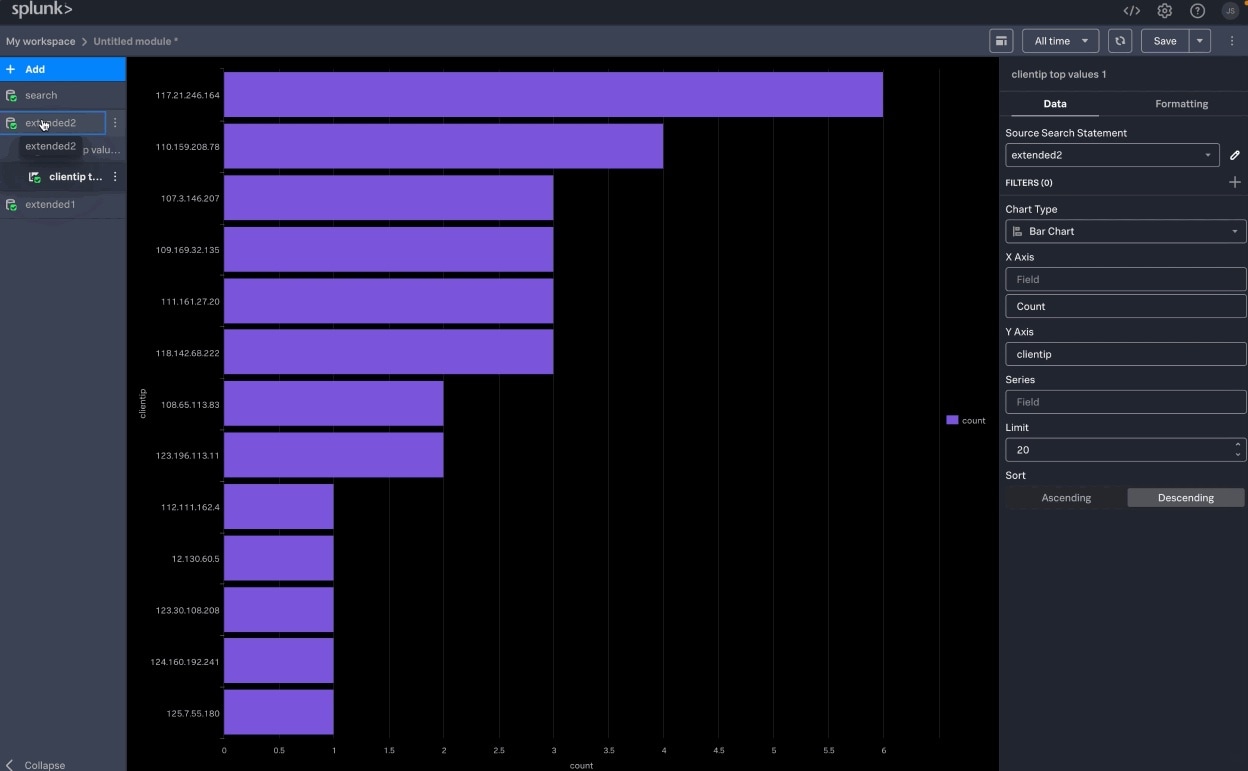
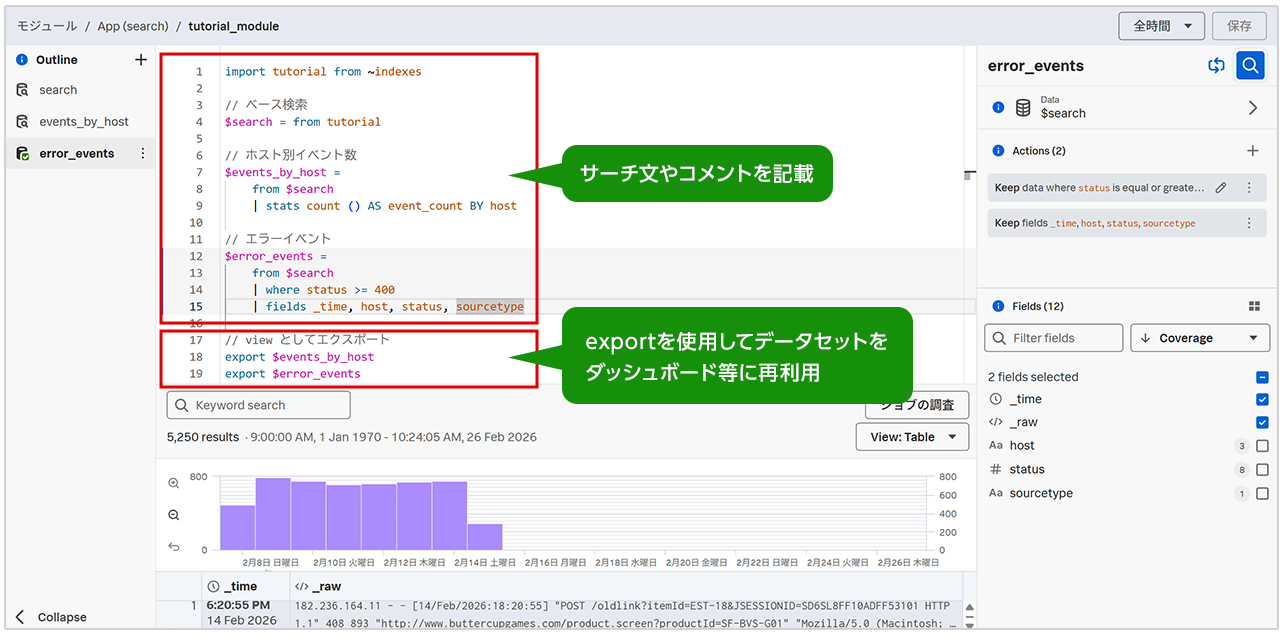
Using the SPL2 Module Editor for Incident Response... - Splunk Community
Discover how SPL2 enhances data querying in Splunk with improved syntax ...
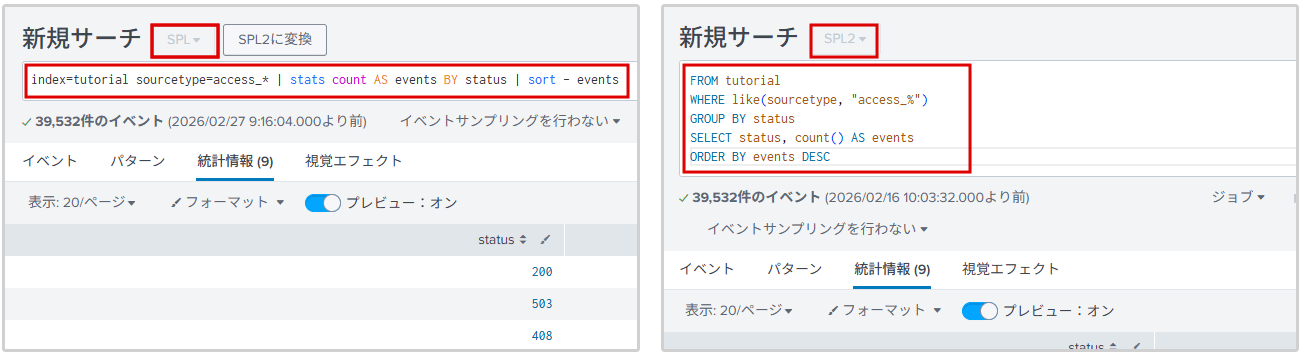
Announcing the Splunk SPL to SPL2 Converter | Splunk
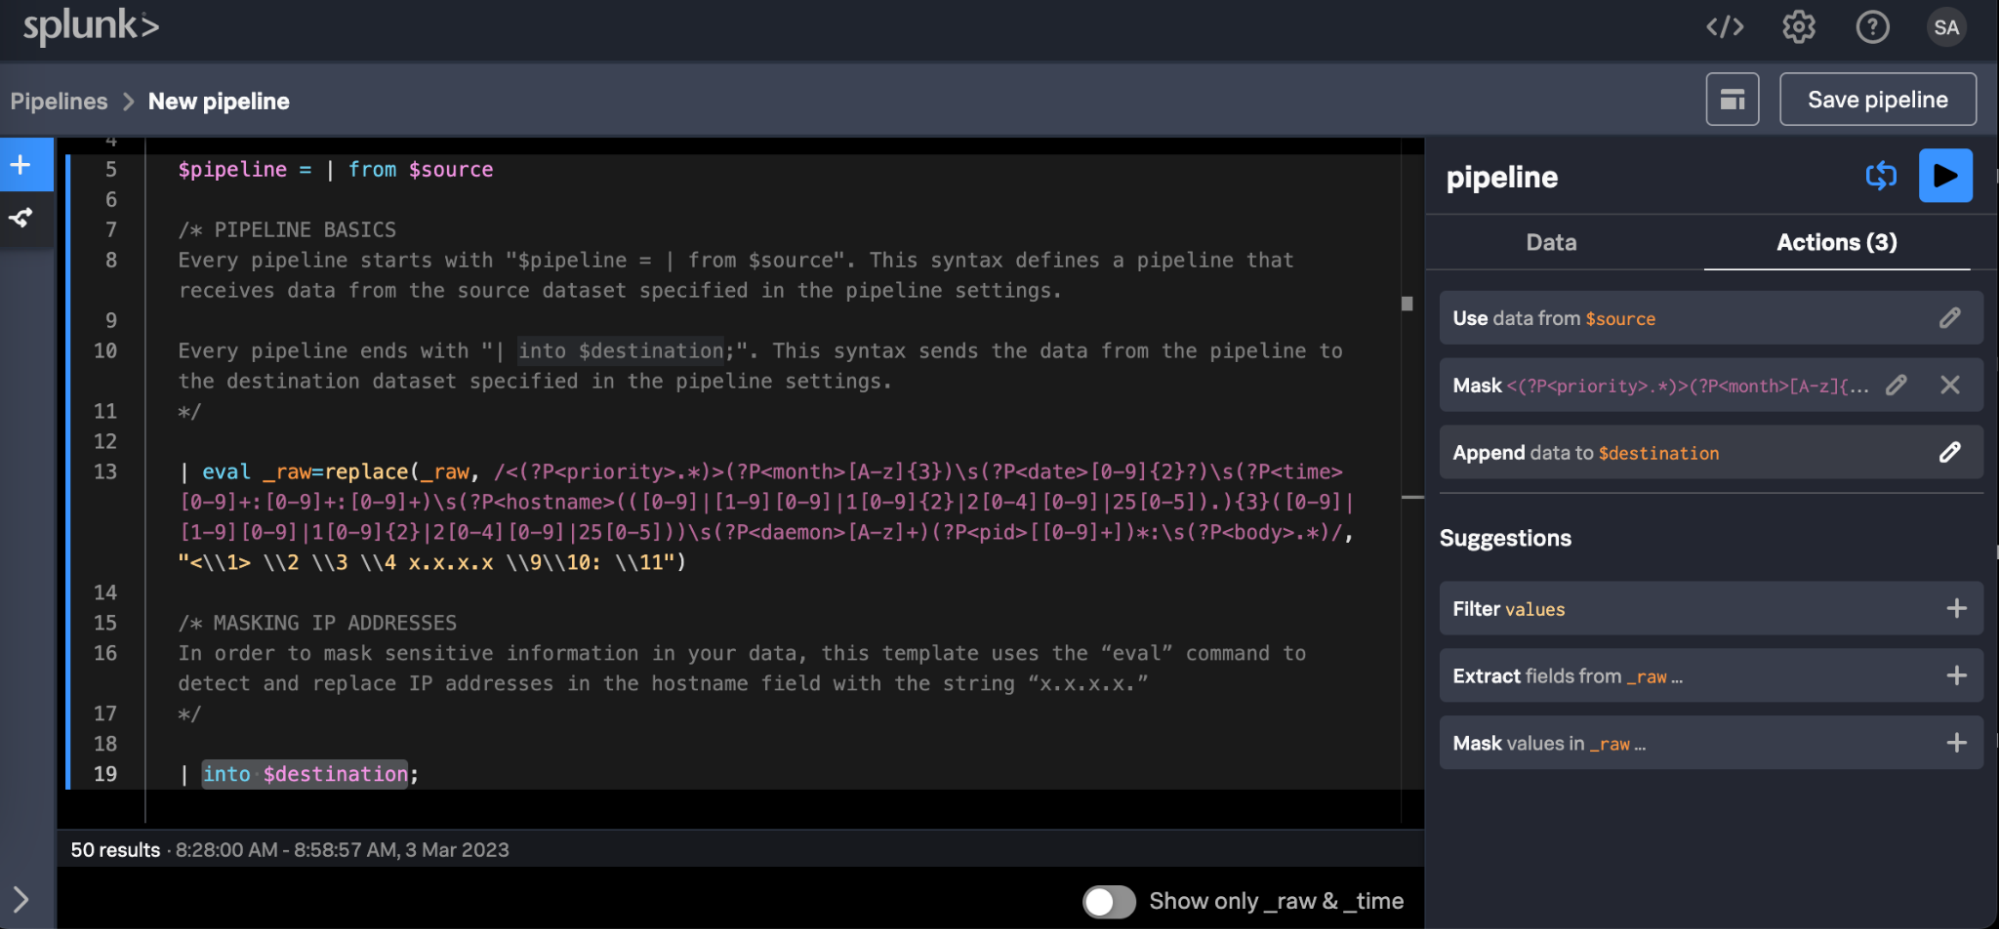
Reducing Palo Alto Networks log volume with the SPL2 template - Splunk ...
Searching data using SPL2 | Splunk Enterprise, Splunk Cloud Platform ...
Data Preparation Made Easy: SPL2 for Edge Processor | Splunk
Splunk SPL2 and BOTS - intro - YouTube
Build Your First SPL2 App! | Virtual Event | Splunk
Create a Splunk pipeline to filter, mask, and route logs - without SPL2 ...
Performance Tuning the Platform, SPL2 Templates, a... - Splunk Community
Splunk Free Tier _ Announcing the Public Beta of SPL2 in Splunk ...
SPL2 beta: CyberCX's Intel Hunt for Splunk | Splunk posted on the topic ...
Splunk Parsing Pipeline : Announcing the Public Beta of SPL2 in Splunk ...
Data Preparation Made Easy: SPL2 for Edge Processor | Splunk | Aditya ...
See Helsinki Splunk User Group meets SPL2 at Splunk Helsinki Splunk ...
Stop Editing props.conf: Splunk 10 Edge Processor & SPL2 - YouTube
Welcome to the Future of Data Search & Exploration | Splunk
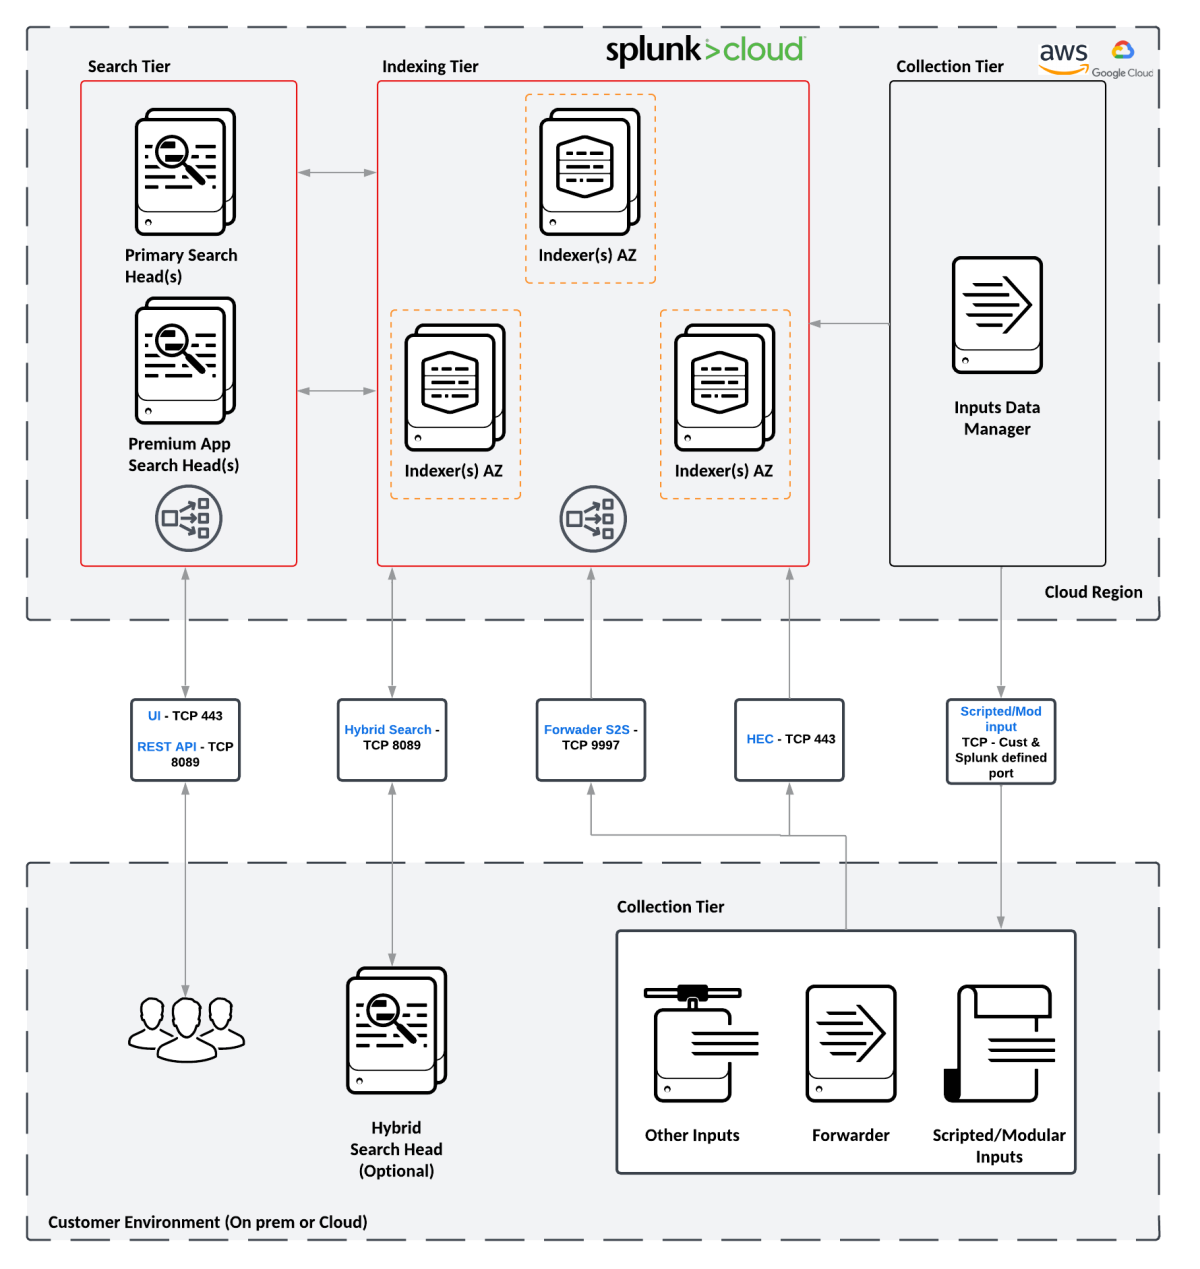
Introducing Inputs Data Manager on Splunk Cloud | Splunk
Splunk Enterprise 10.2 リリース - セキュリティ事業 - マクニカ
Boost Productivity with SPL2: The Next-Gen Language for Splunk
Splunk PNW User Group - Seattle - 2023-06-28.pdf
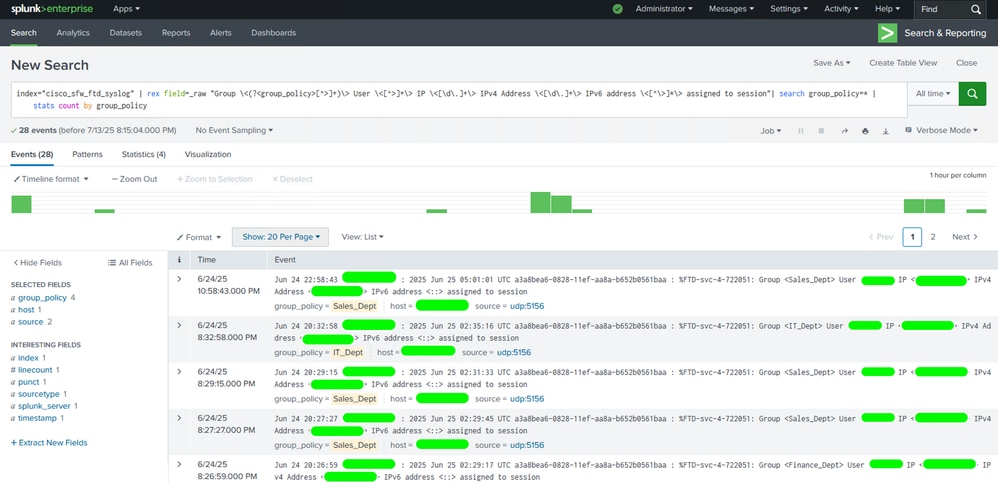
إنشاء لوحات معلومات وتنبيهات مخصصة على Splunk باستخدام Syslogs من FTD ...
Splunk Developer Program
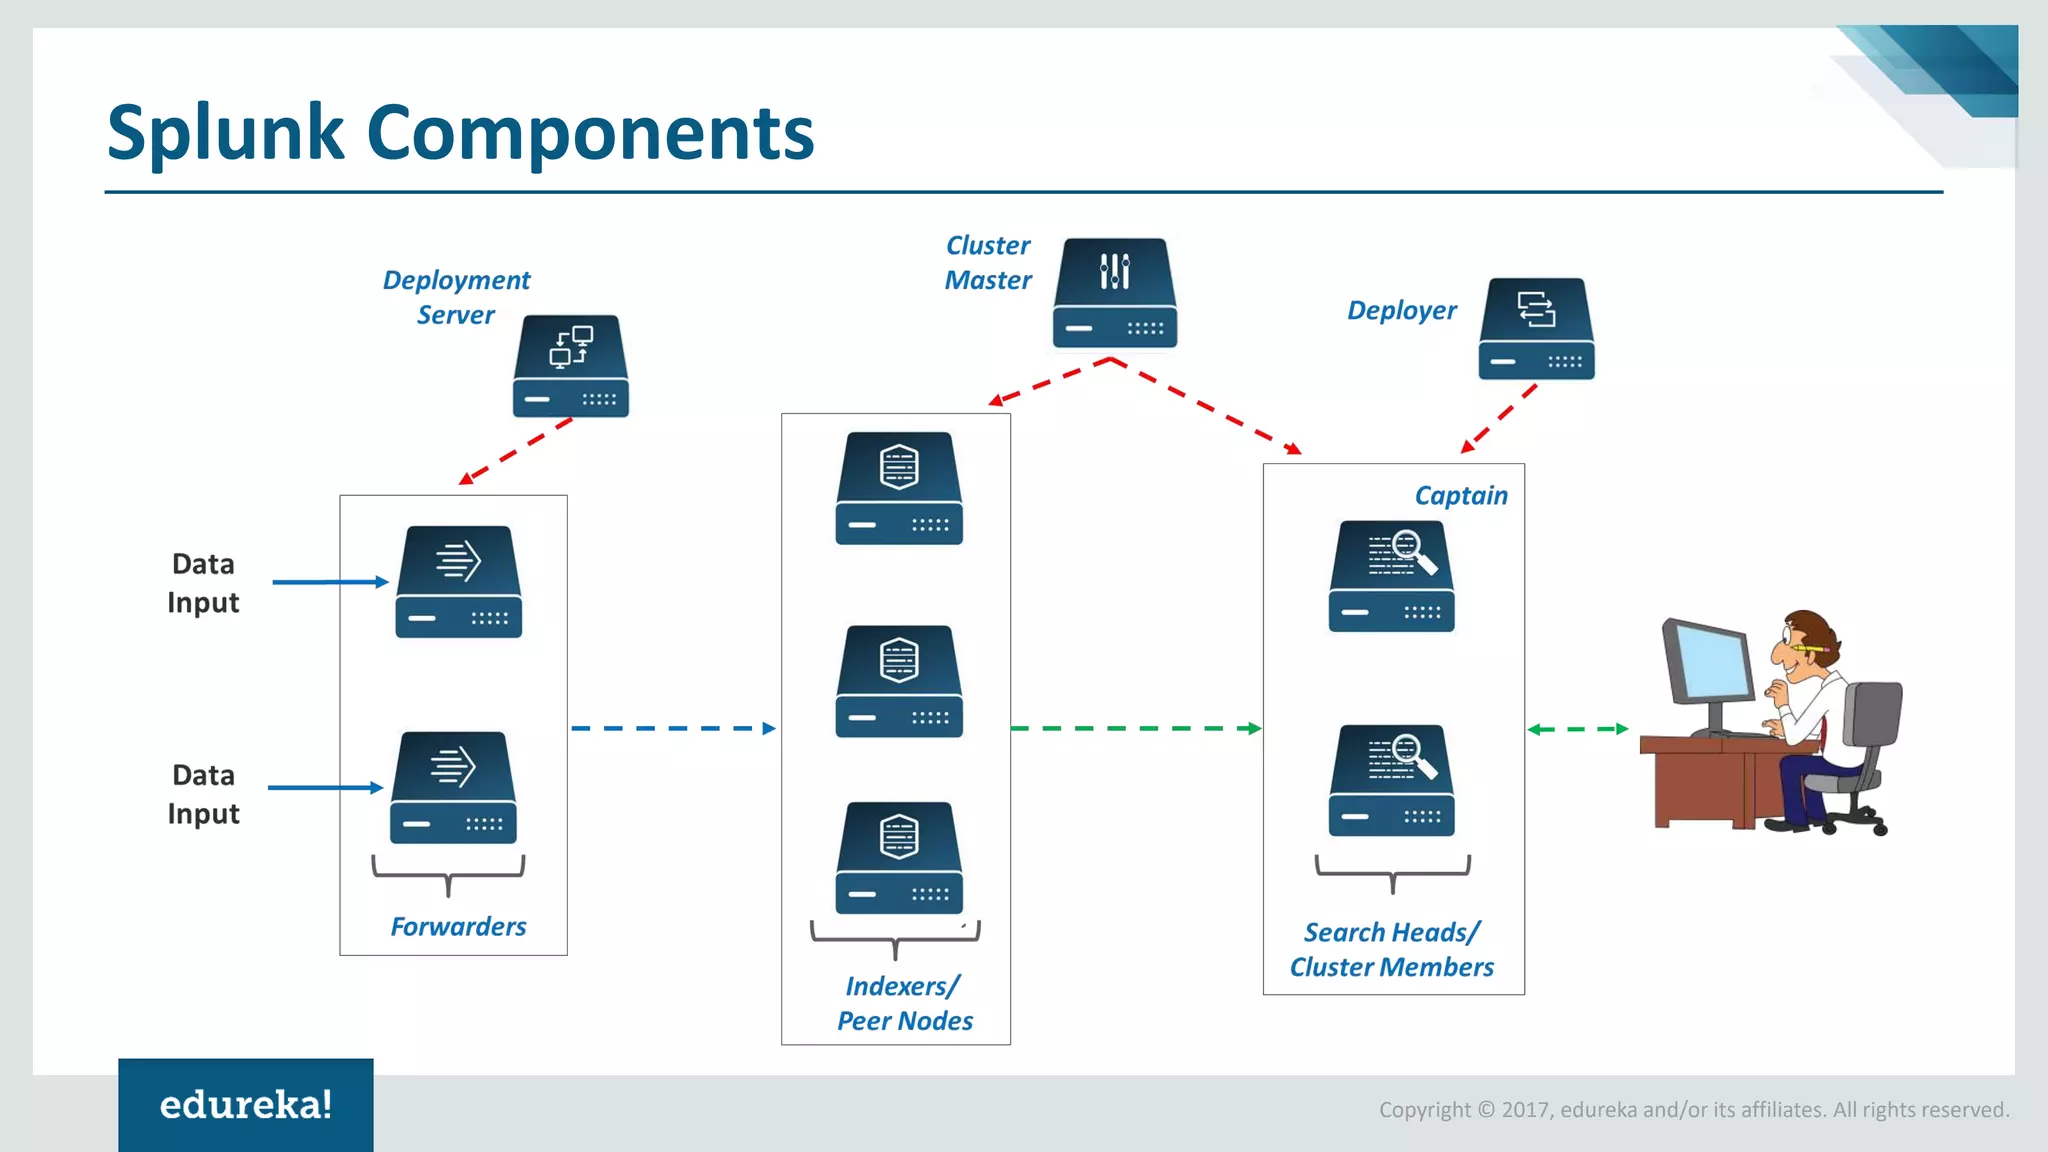
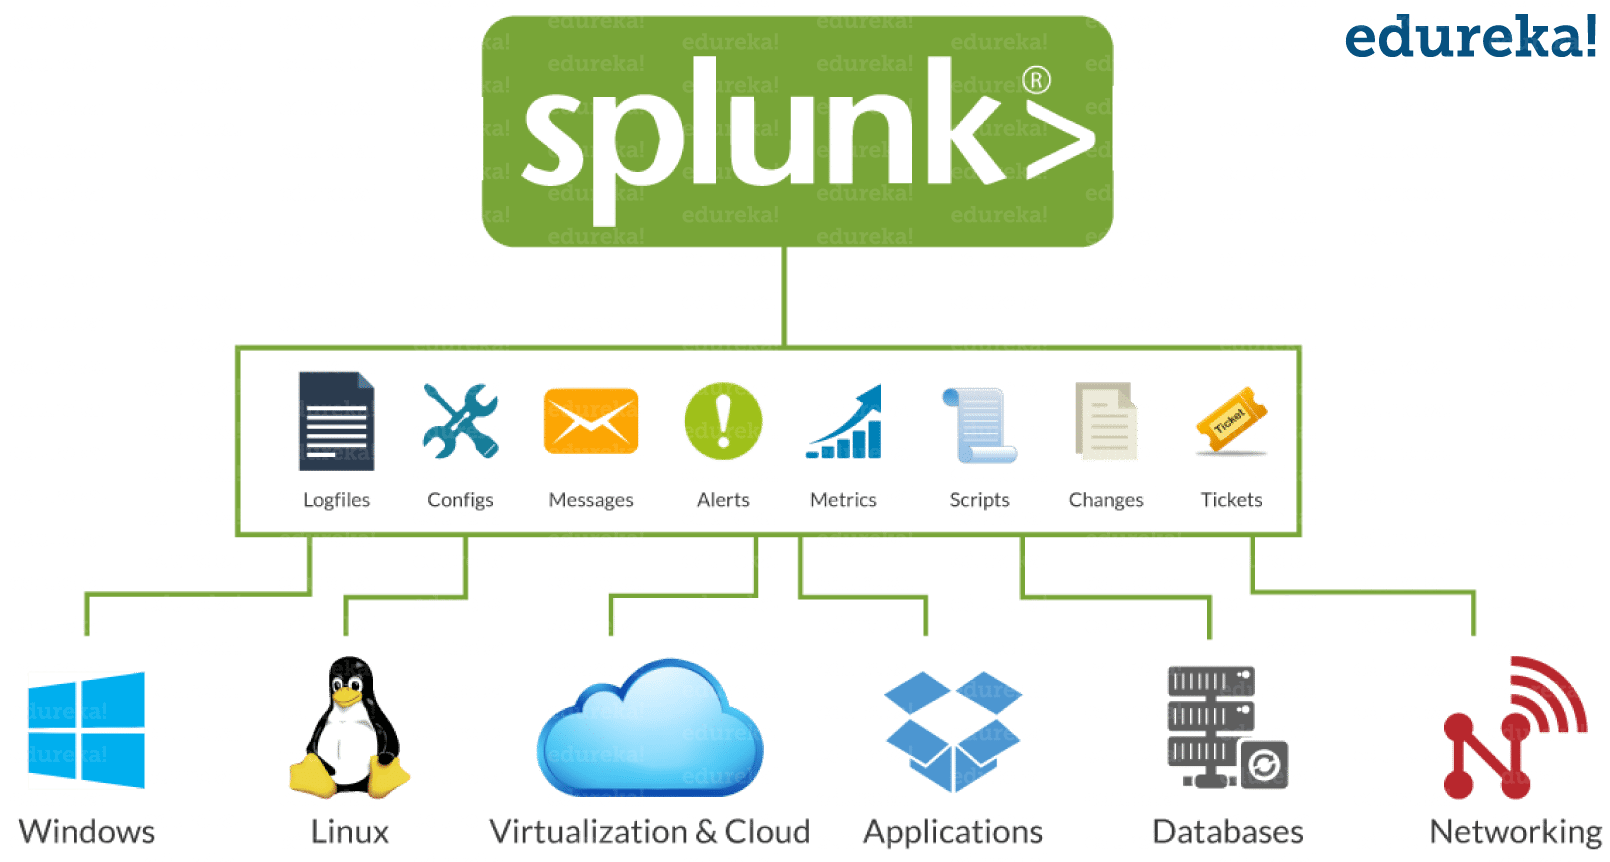
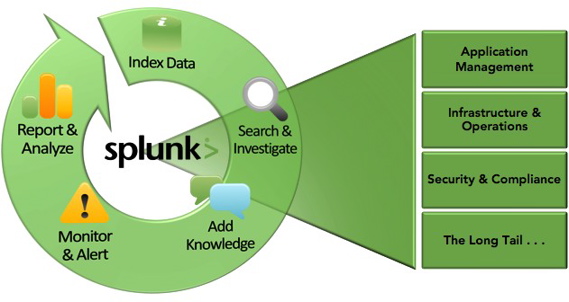
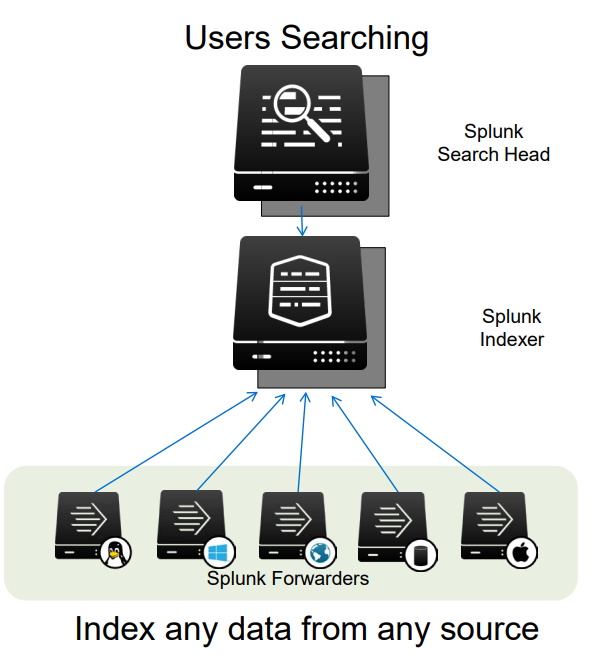
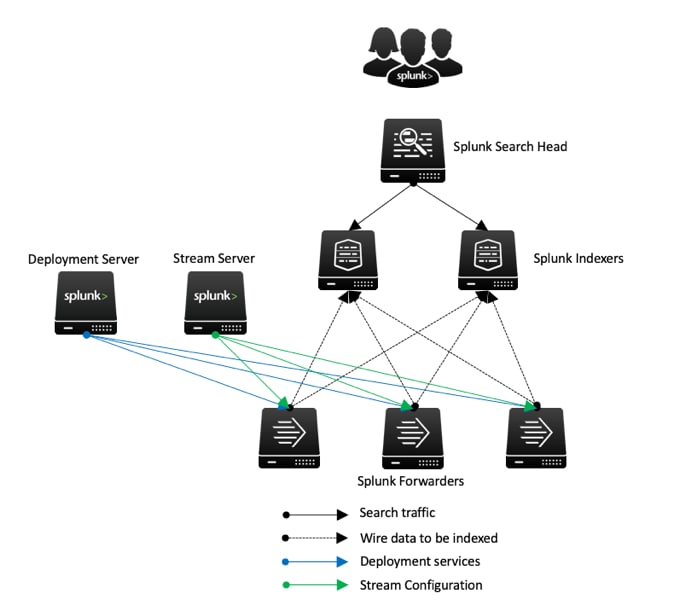
Splunk architecture
Splunk in 60 Minutes | Splunk Tutorial For Beginners | Splunk Training ...
Splunk Docs – Difference between != and NOT – PCWH
Splunk Where Example at Tawana Tibbs blog
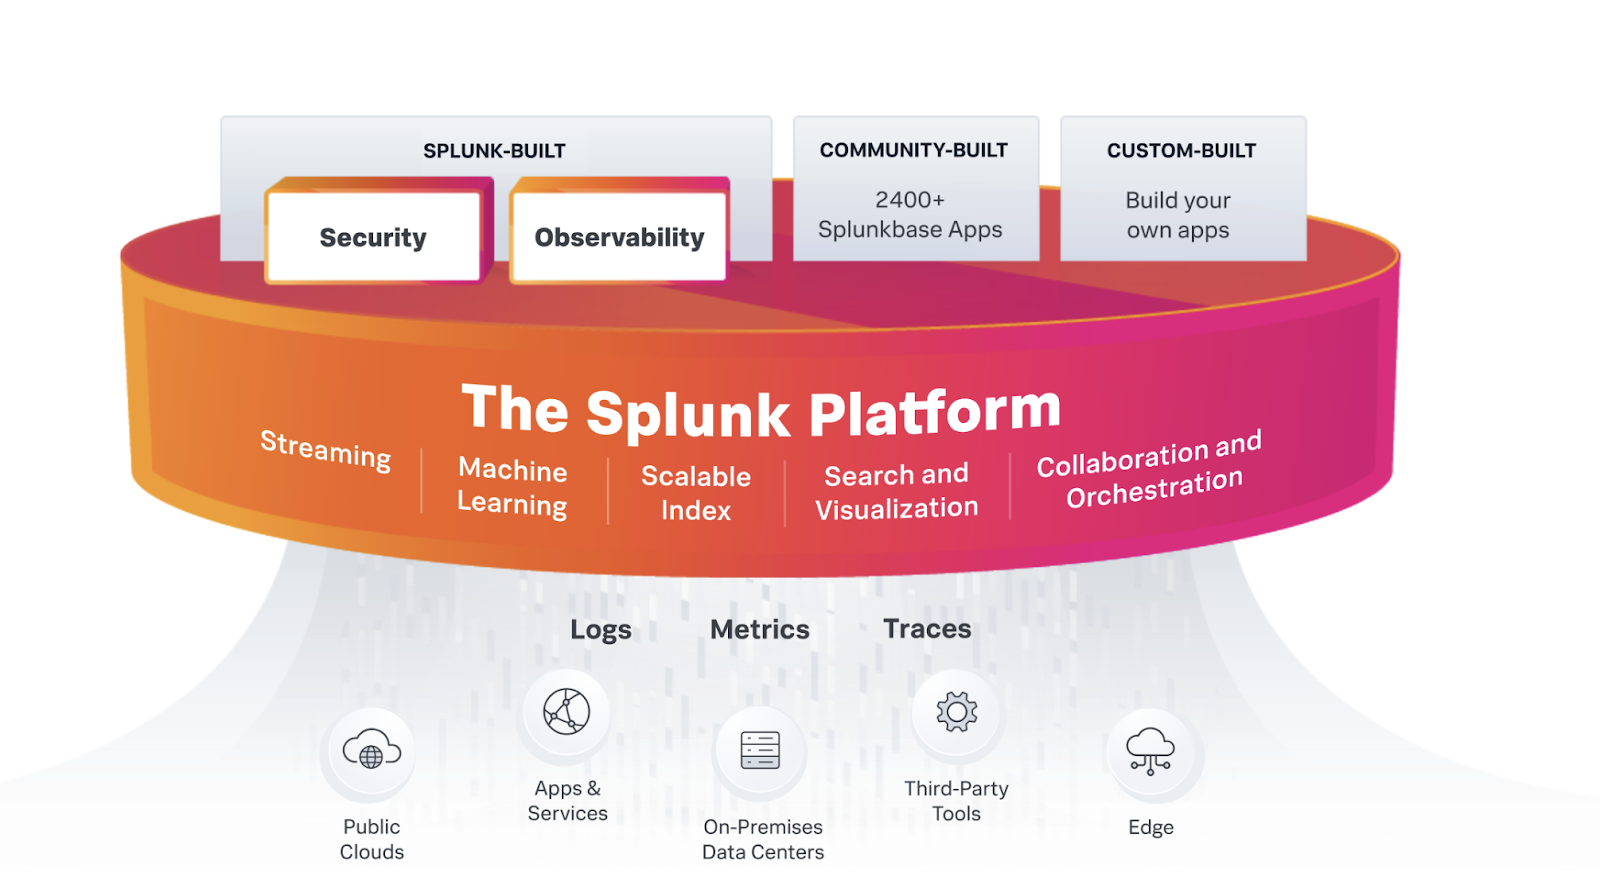
Platform | Splunk
splunk search文 | splunk 使用方法 – ZRAVBE
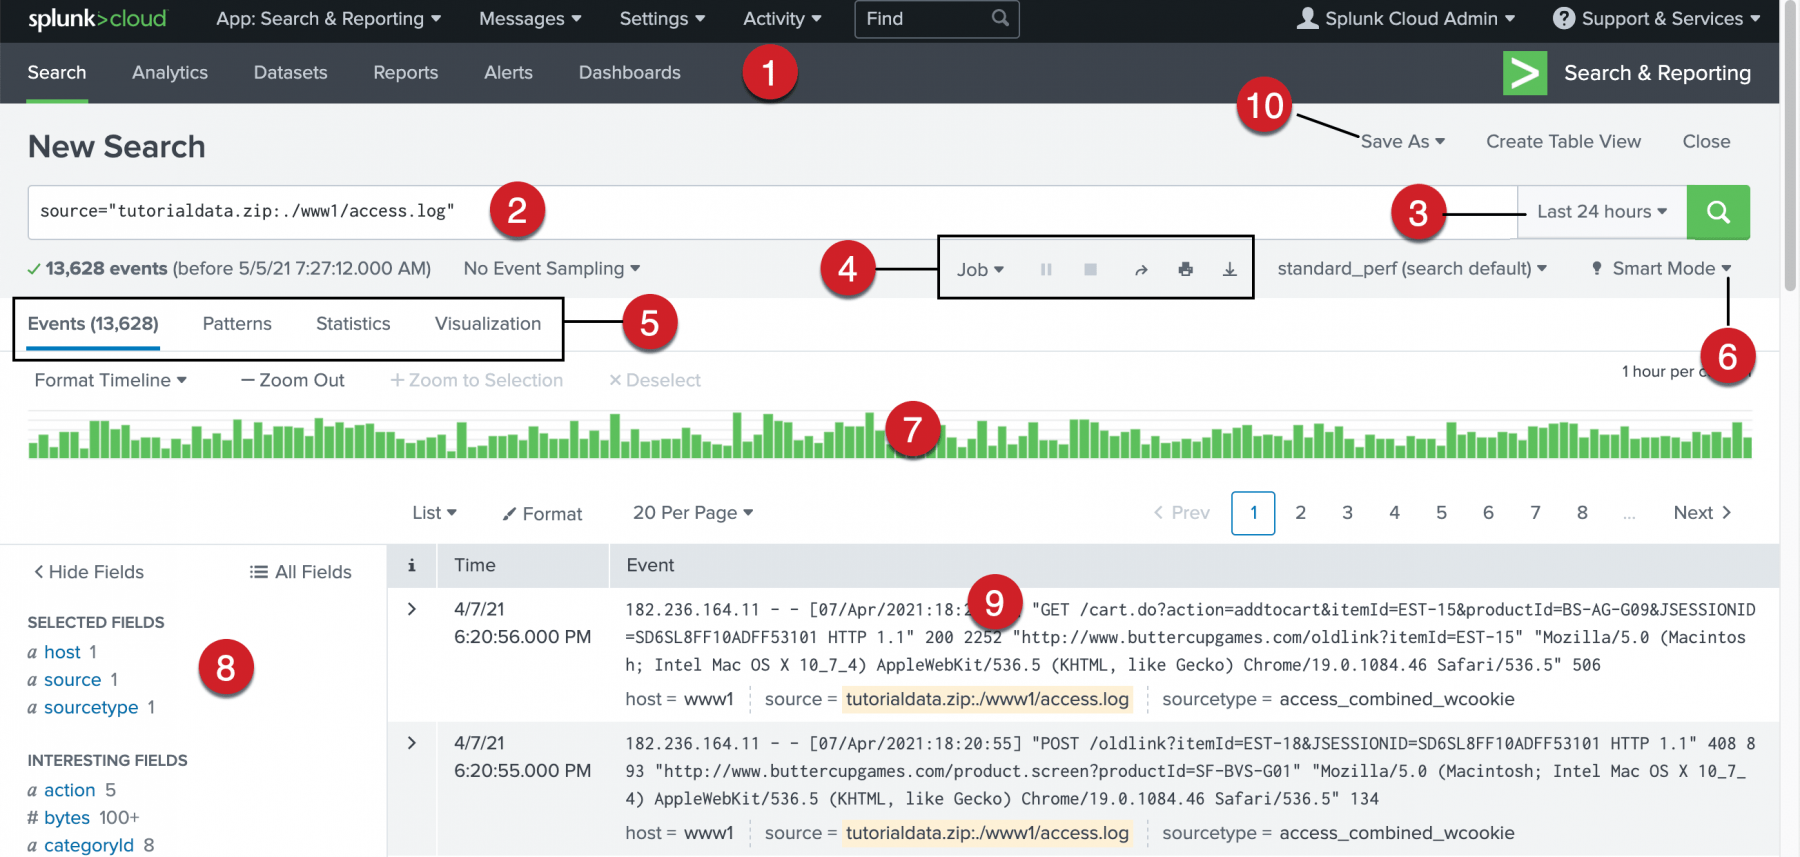
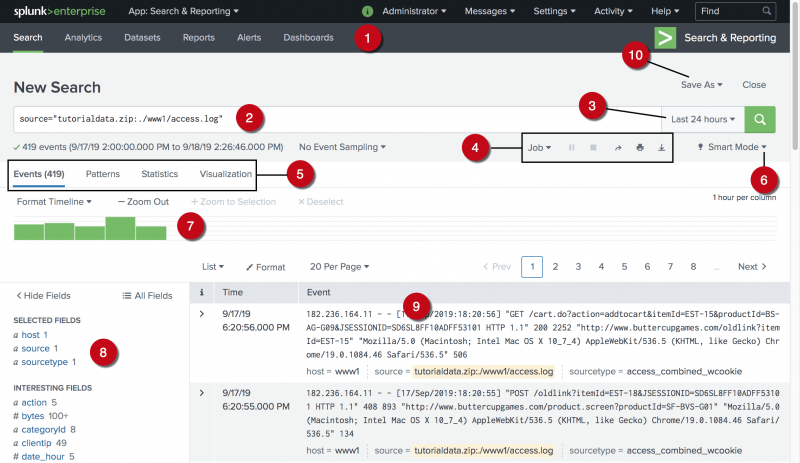
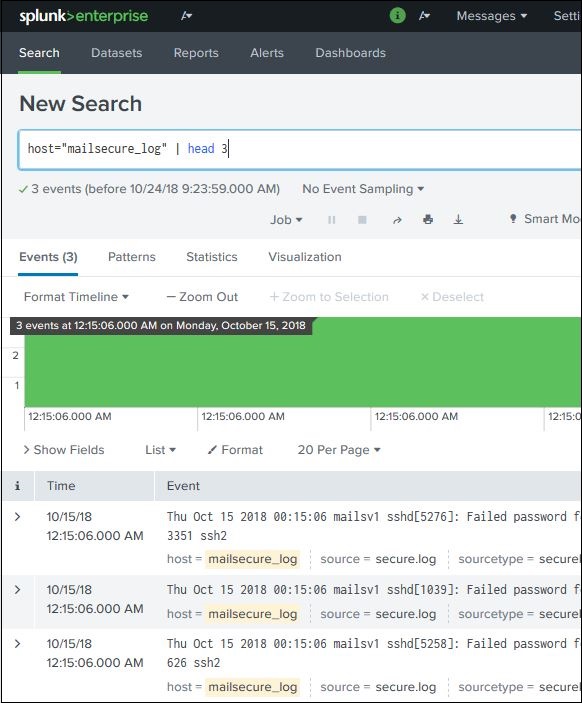
Exploring the Search views - Splunk Documentation
Splunk2 – Splunk ロゴ – What Is Splunk? The Complete Overview of What ...
Splunk Tutorial Ppt : About the Splunk Dashboard Studio tutorial – FWBD
Splunk Cloud Platform Experiences - Splunk Documentation
How To Use Splunk Tool – Splunk Infrastructure Monitoring – DDVLNE
Splunk Fields Explained at Barbara Fowler blog
Splunk Architecture Guide – Splunk Architectures – YTXPJ
Product Release: Announcing Query Splunk App 2.8 - Query
Die Splunk-Plattform | Splunk
Splunk workshop-2017-Power-of-SPL | PDF
Splunk Dmx Ingest Processor : Onboarding and managing data in Splunk ...
The All New Performance Insights for Splunk | Splunk
15. Introduction To Splunk & SPL | Exploit. Learn. Secure.
Hands-on Workshop #2: Edge Processor Setup and SPL2 Pipeline ...
Range Function Splunk at Ebony Dunlop blog
Why Is Splunk So Slow? How to Speed Up Searches, Dashboards, and Data ...
Splunk 101: A Beginner’s Guide to Harnessing Its Power
Splunk Search Field Like | Splunk Spl Cheat Sheet – NQFLWV
Splunk Tutorial For Beginners: Comment Utiliser Splunk – ALHFO
Что такое Splunk и с чем его едят — «Хакер»
什麼是 Splunk? Splunk 的主要優點和功能 | Fortinet
Splunk SPLからSPL2へのコンバーターのご紹介 | Splunk
How SPL2 Simplifies Security Investigations and Admin Workflows in ...
SPLのコマンドタイプを学ぶ~効率的なサーチの実行順序とその調査方法~ | Splunk
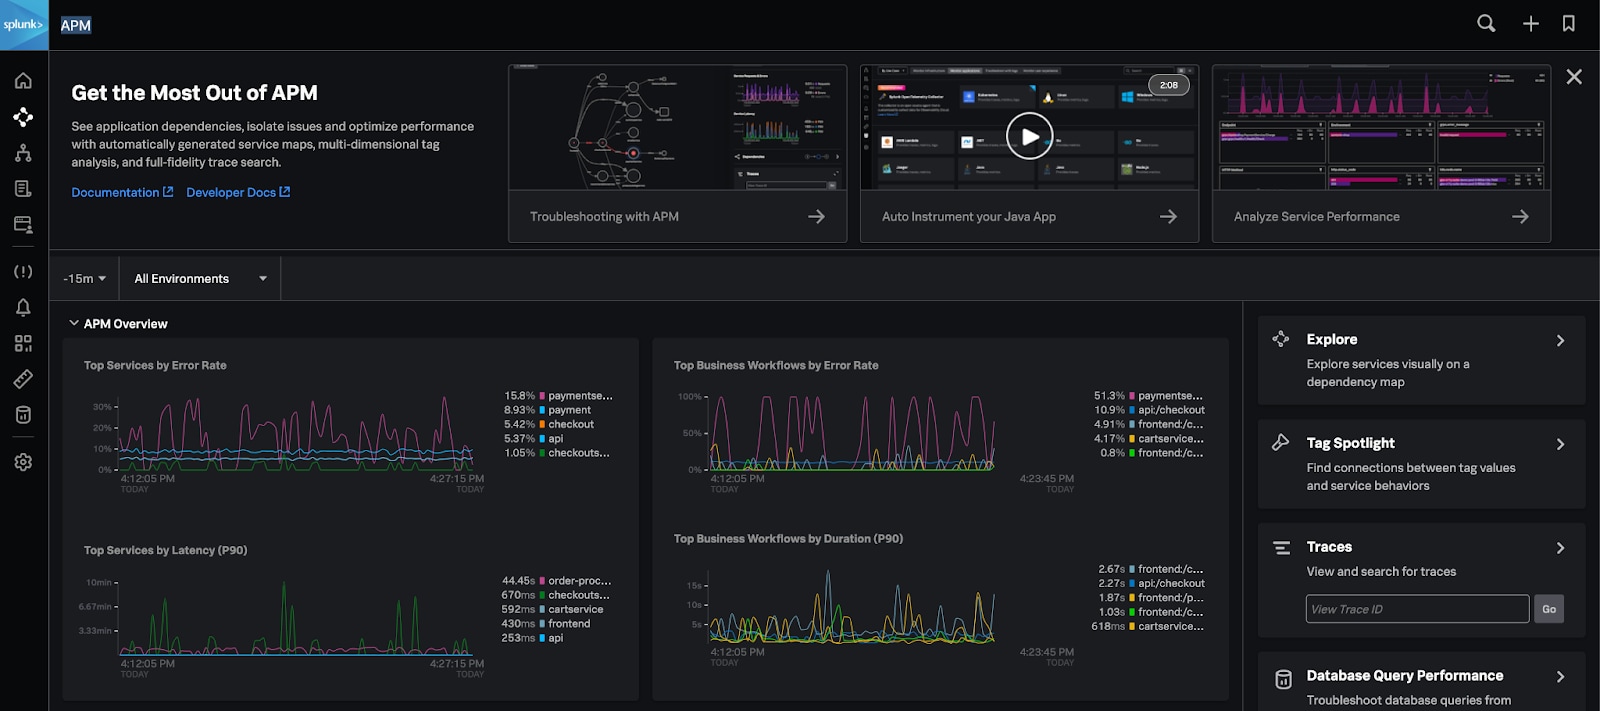
Why You Need Observability With the Splunk Platform | Splunk
Splunk Blogs | Splunk
Splunk Database Monitoring - Splunk Community
SplunkShow Enterprise Security Sandbox | Splunk
Query Federated Search for Splunk - Query
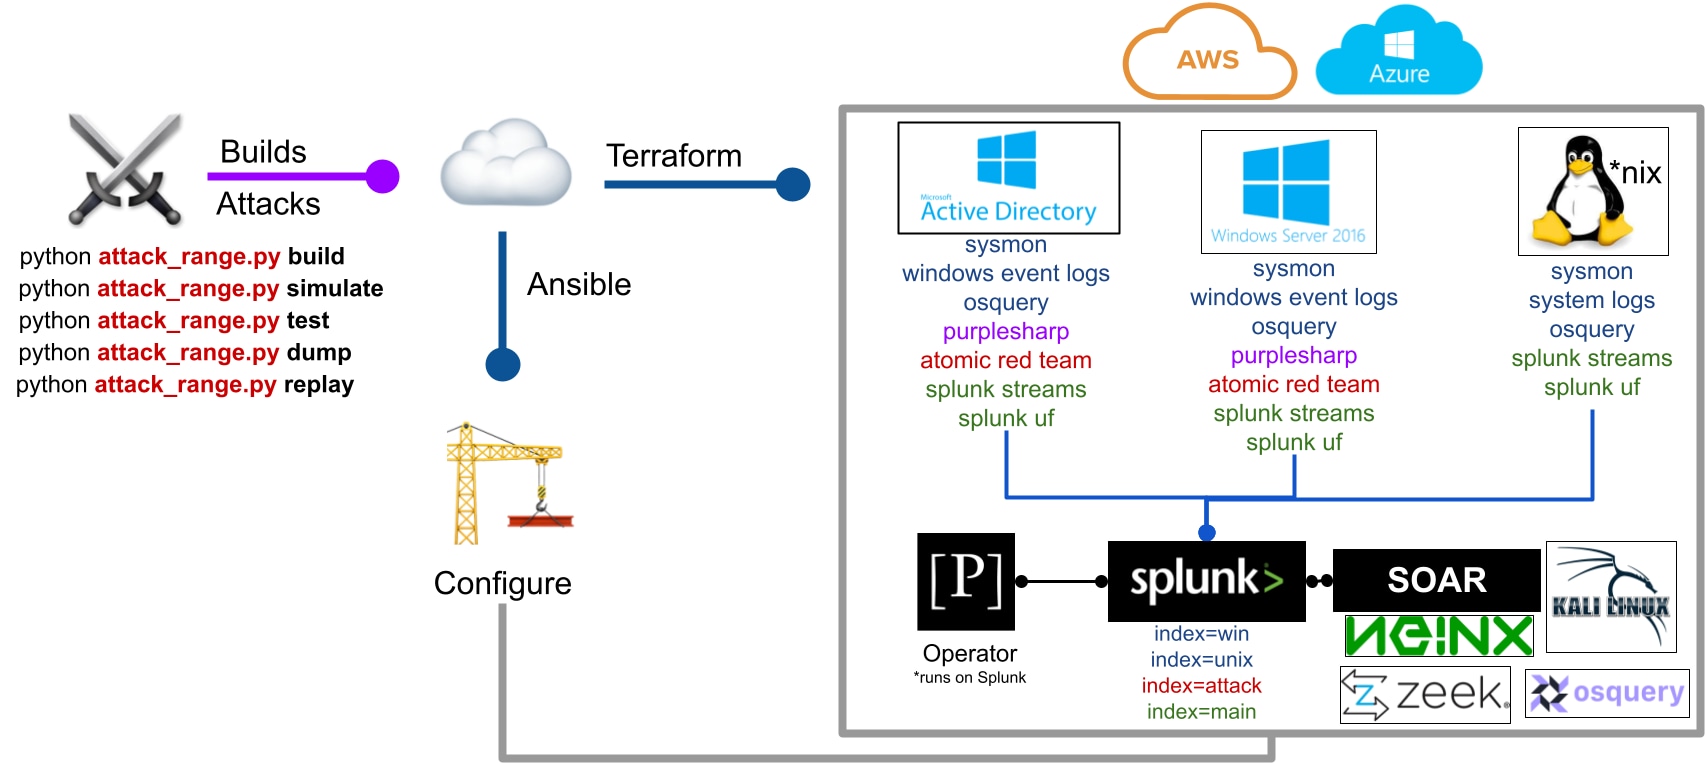
Introducing Attack Range v3.0 | Splunk
Splunk Enterprise: Reviews, Pricing, Features in 2026
Spl2 – Spl2 For Edge Processor 使い方 – GRFINZ
Splunk search basics (with real-life examples) – I-Space Research Labs
Splunk Observability | Positka
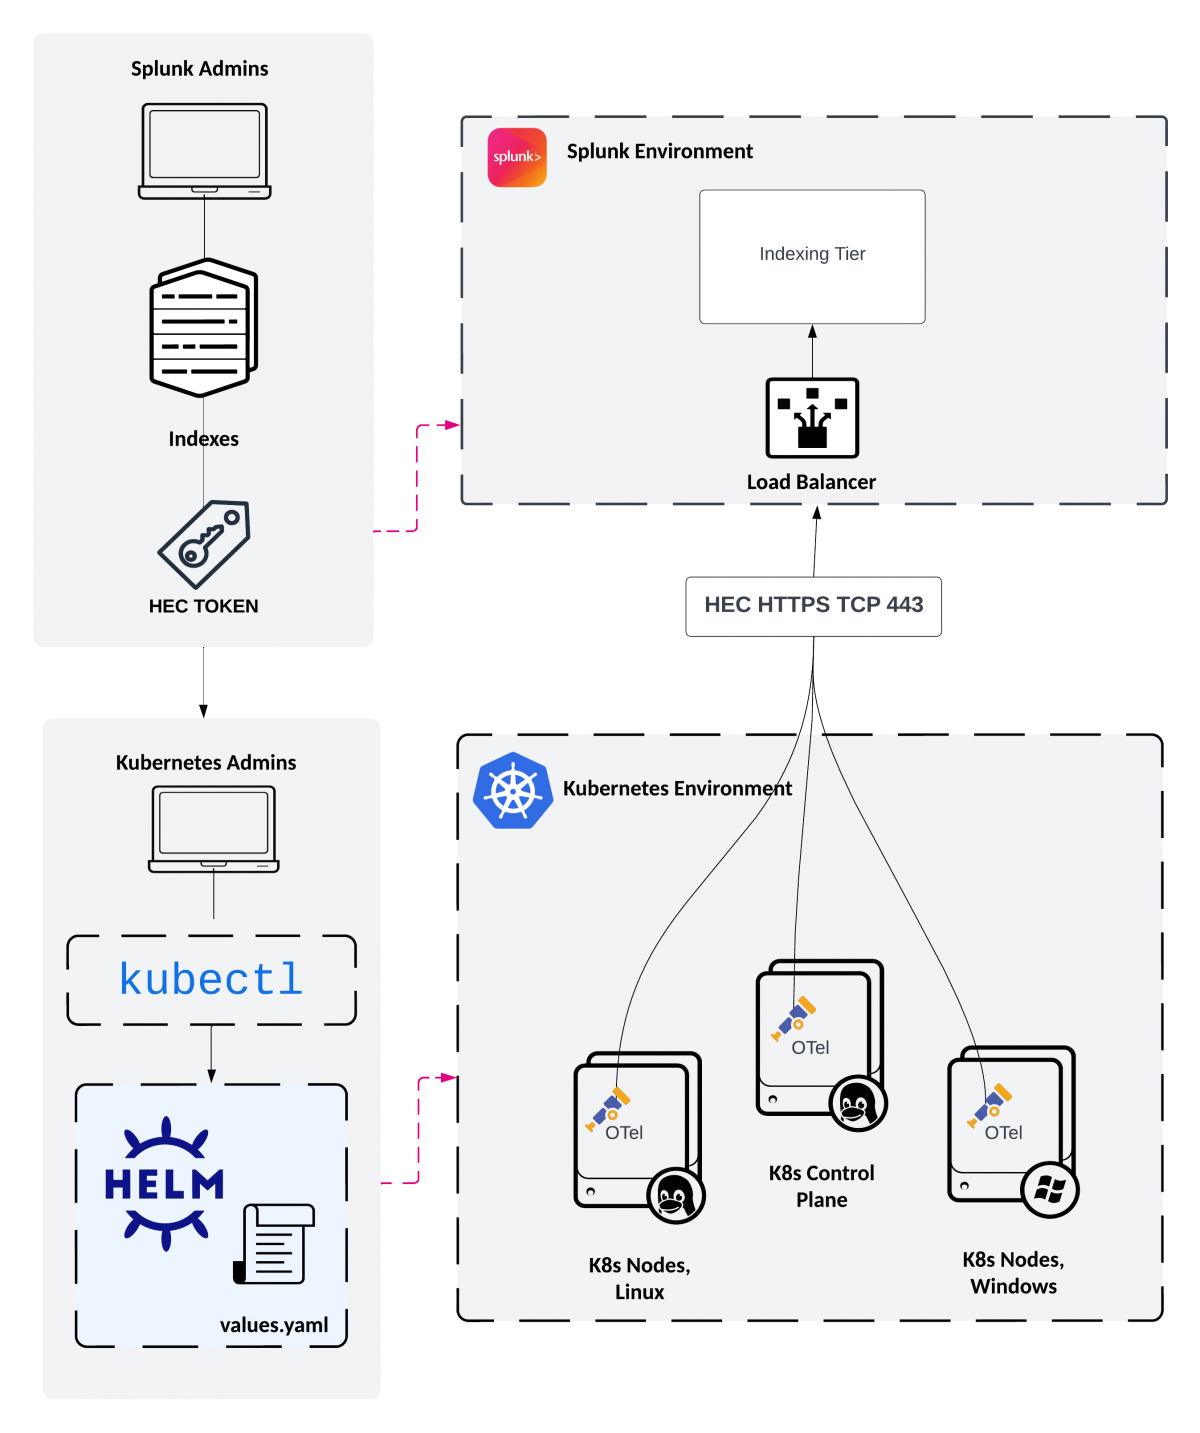
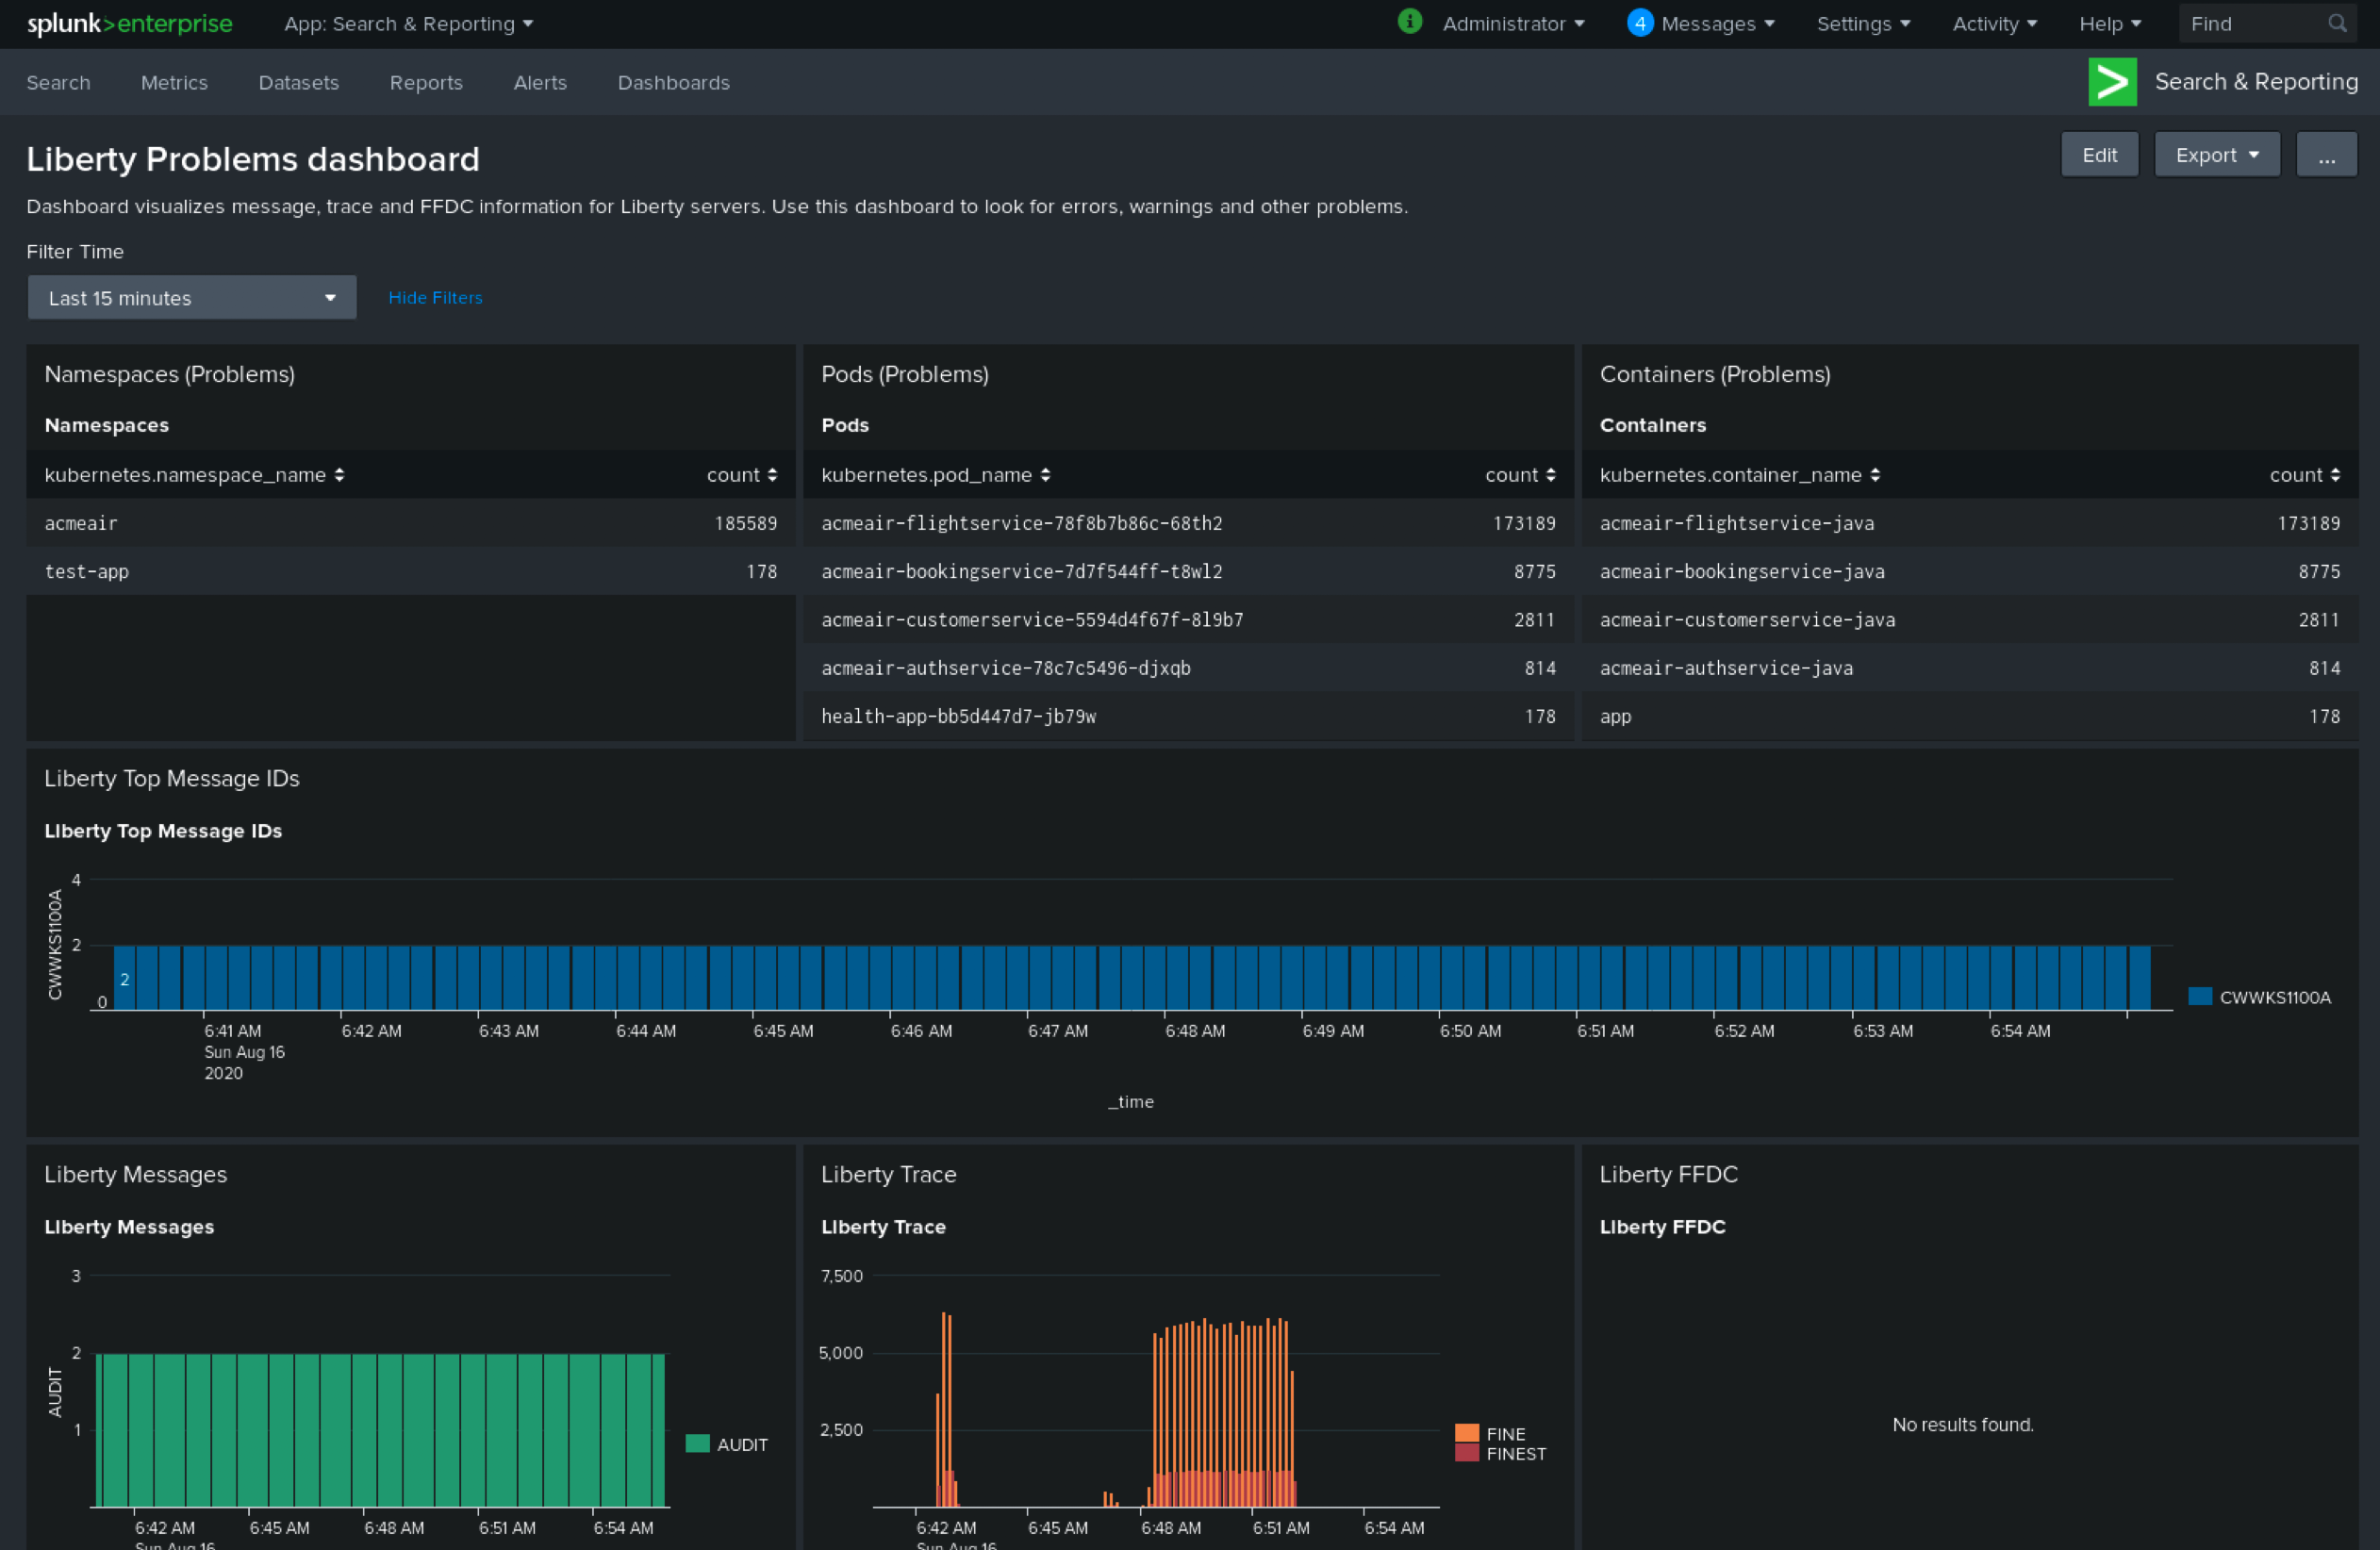
Splunk OpenTelemetry Collector for Kubernetes - Splunk Documentation
Splunk 0埋め – Splunk 値が入らない – Splunk: 表の結合方法あれこれ #SPL – YNRPO
Splunk 搜索语言详解与使用示例 | Splunk 教程
Splunk Fieldformat Example at Crystal Yazzie blog
Part 1: A Guide to Maximizing Splunk IT Service In... - Splunk Community
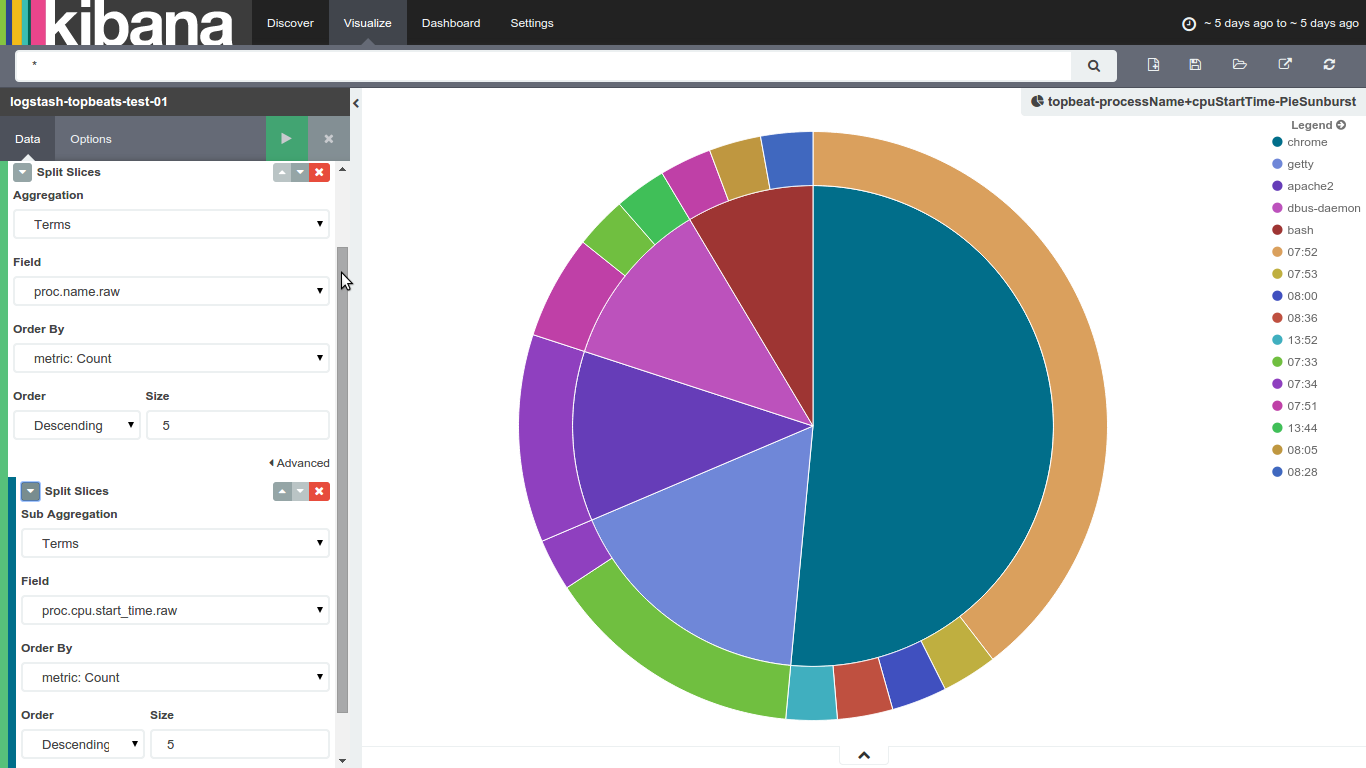
Solved: sub aggregation pie chart with splunk ? - Splunk Community
Splunk configuration
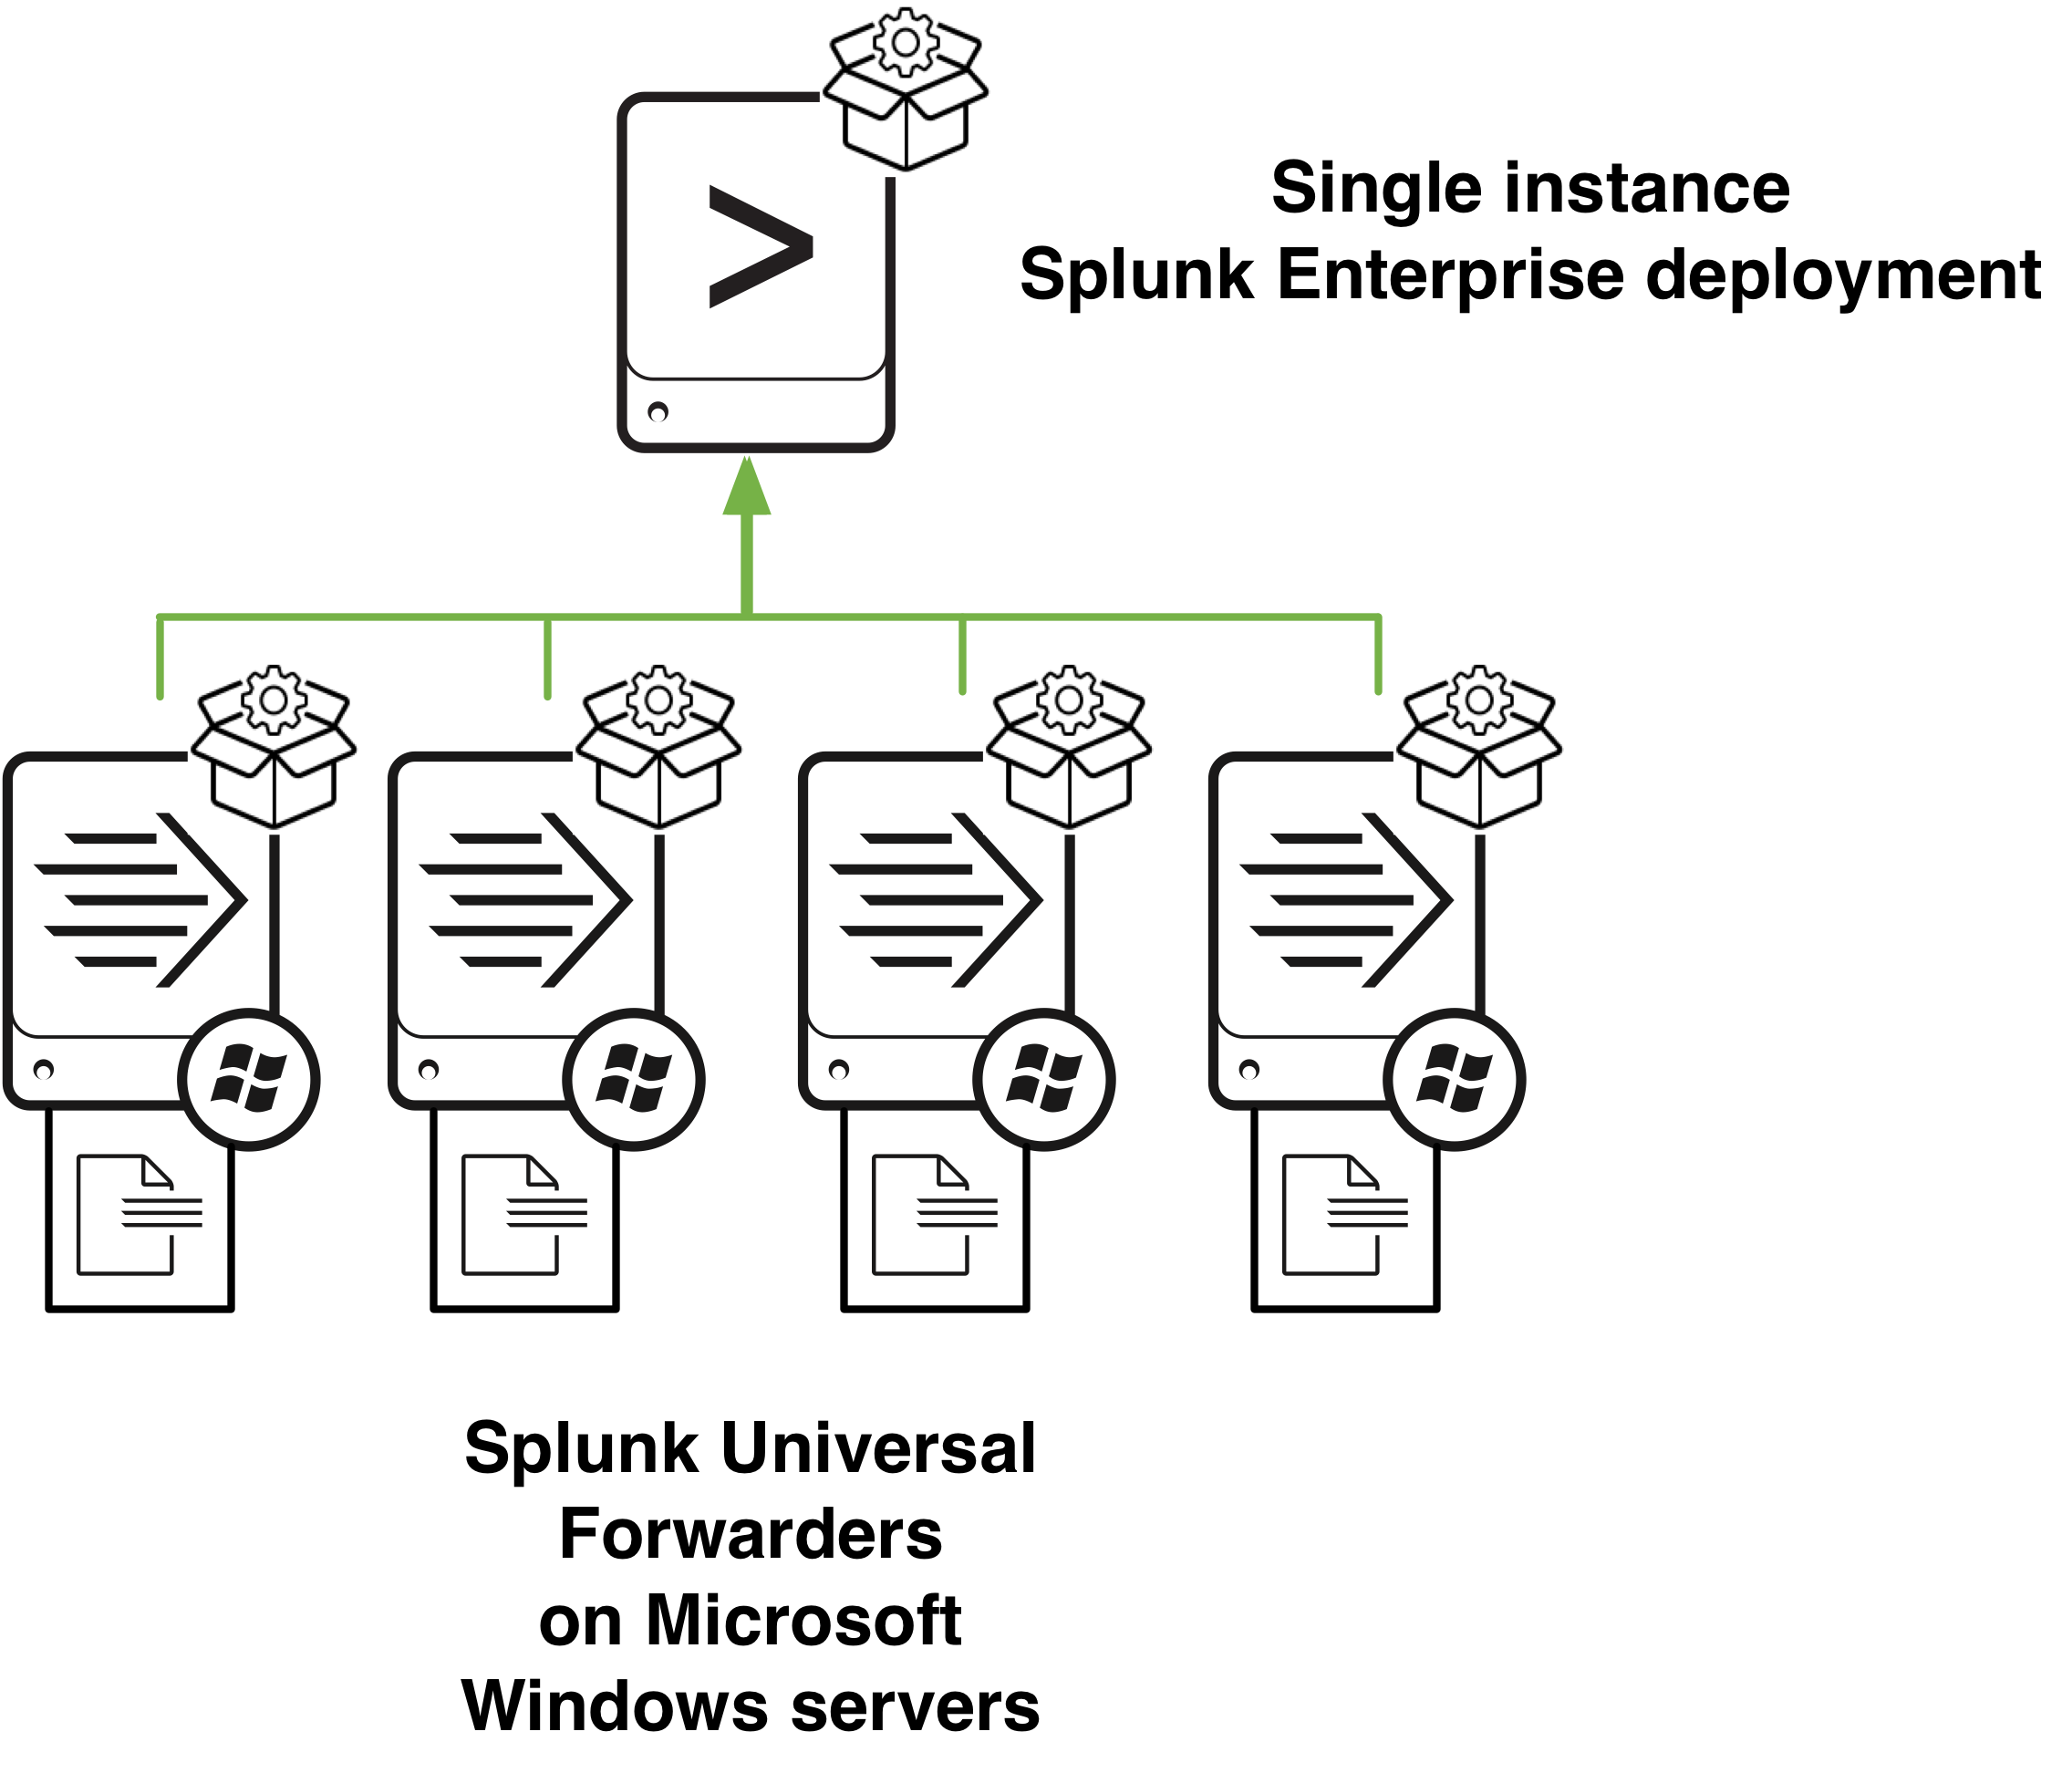
Splunk Universal Forwarder | Splunk
Splunk 平台 | Splunk
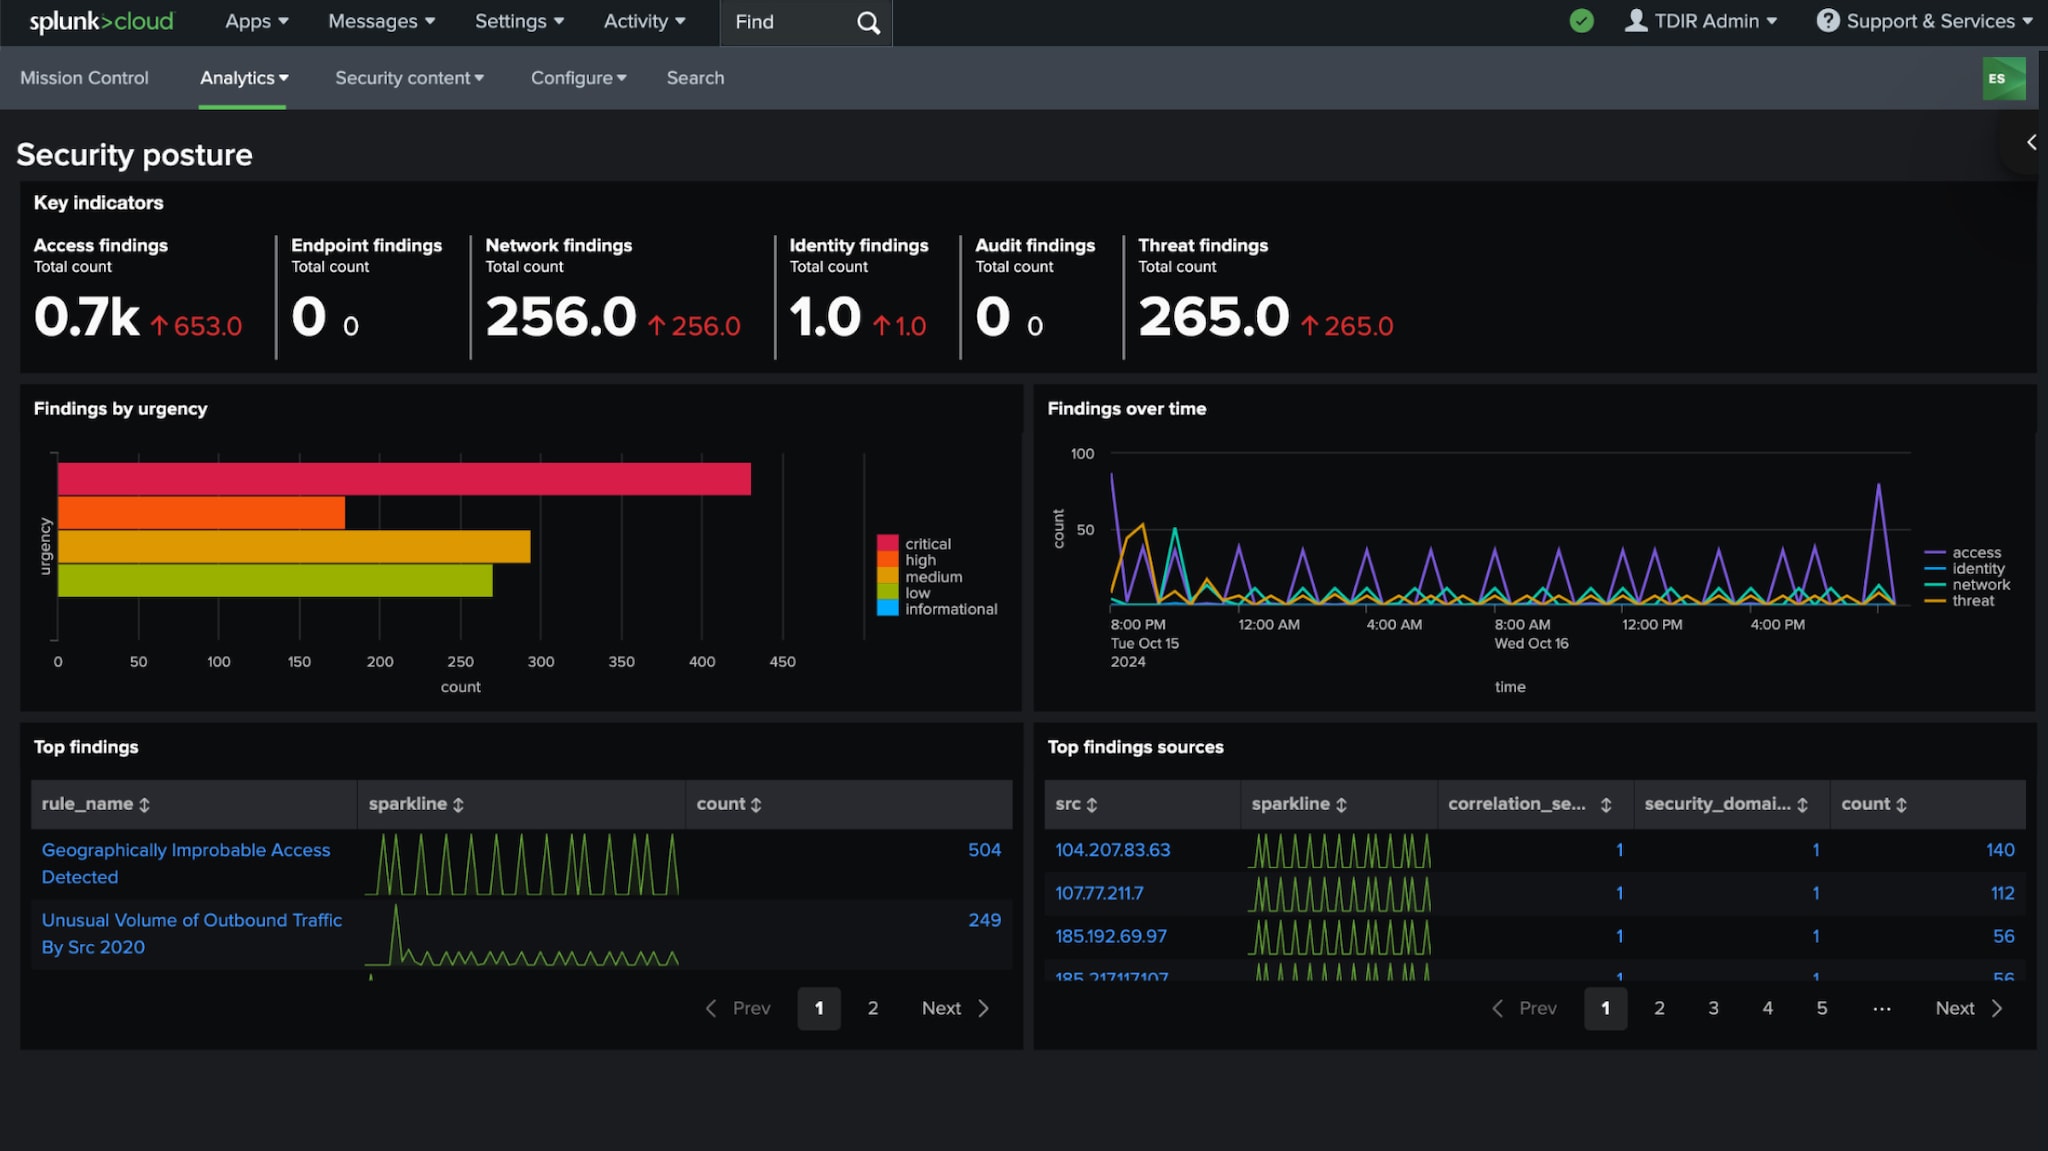
Splunk Enterprise Security Features | Splunk
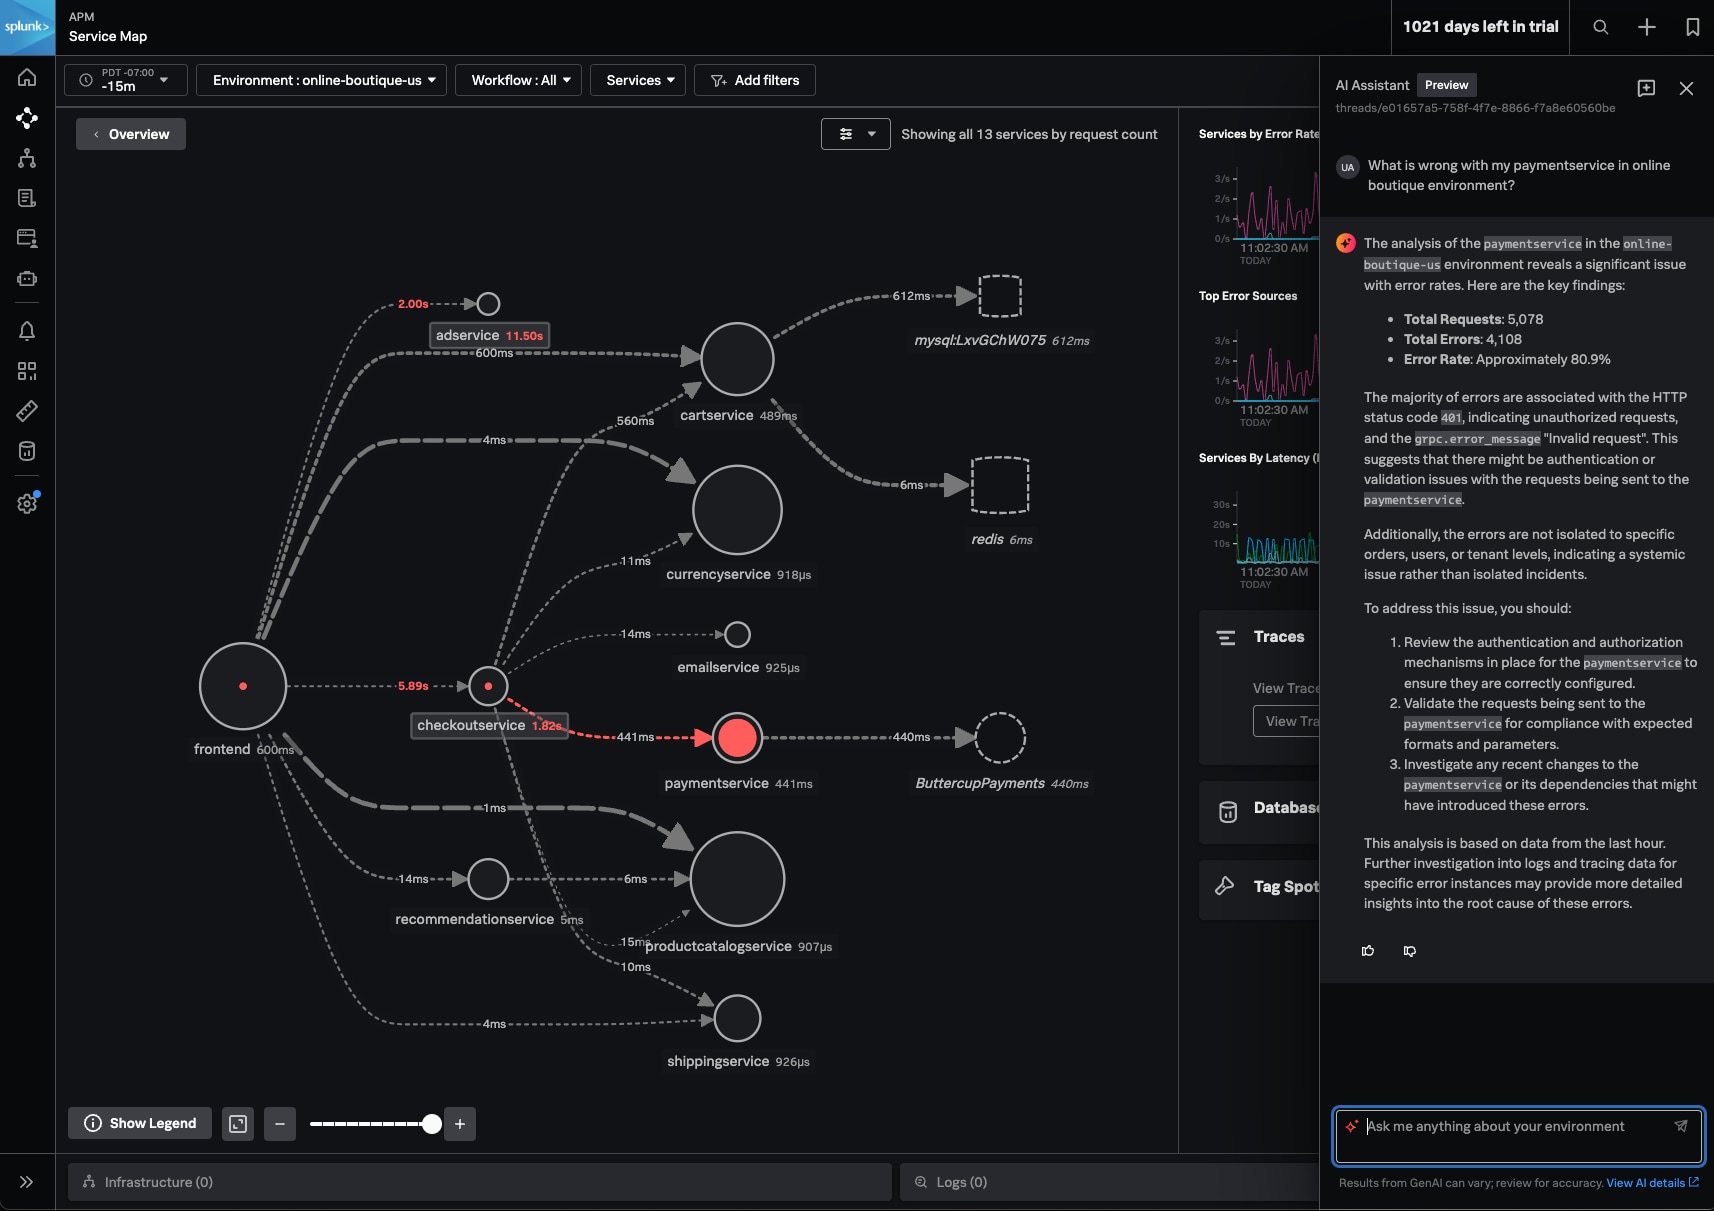
What's New in Splunk Observability Cloud and Splun... - Splunk Community
What Is Splunk Cooked Data at Cynthia Ridgeway blog
Splunk Download Log File , Log Data 101: What It Is & Why It Matters ...
How Splunk SOAR is Helping Organizations Achieve a More Resilient ...
Splunk Enterprise 9.2.0 (macOS, Linux, Windows) - 机器数据管理和分析 - sysin - 博客园
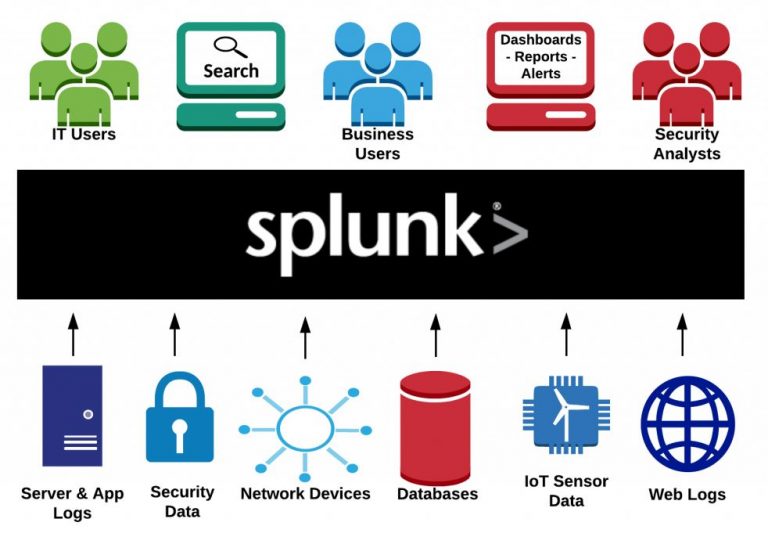
[splunk] Introducing Splunk and Splunk's Components
Say hello to SPL2, Splunk's next-generation data search and processing ...
Introducing SPL2: The Next-Generation Search & Data Preparation ...
Learn SPL Command Types: Efficient Search Execution Order and How to ...
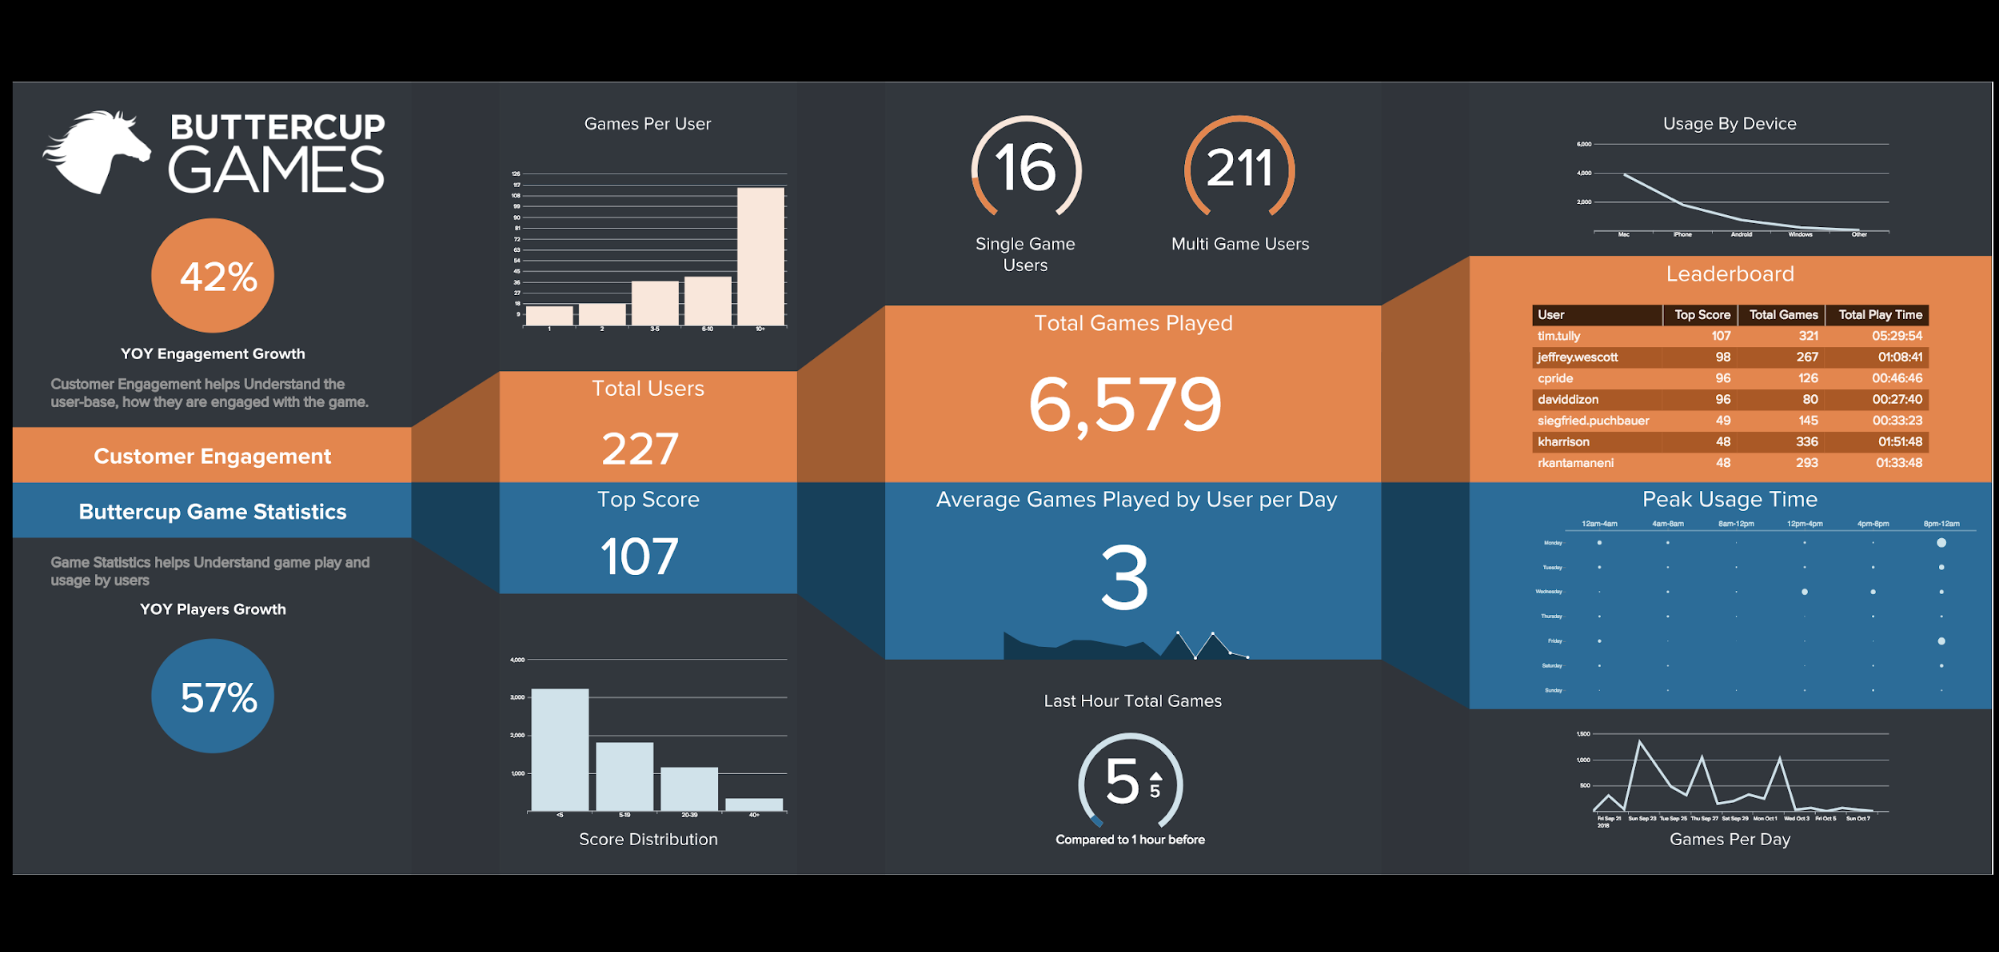
splunk-app-examples/spl2-sample-apps/sample_spl2_buttercup/default/data ...
Starting with Splunk: A Comprehensive Guide for Beginners
Platform: Our Comprehensive Guide to SPL2: Navigating New Features and ...
Datadog vs Splunk: A Feature-By-Feature 2025 Comparison
Starting with Splunk: A Comprehensive Guide for Beginners | by ...
TryHackMe | Splunk: Basics – Igor_sec's Blog