Showing 120 of 120on this page. Filters & sort apply to loaded results; URL updates for sharing.120 of 120 on this page
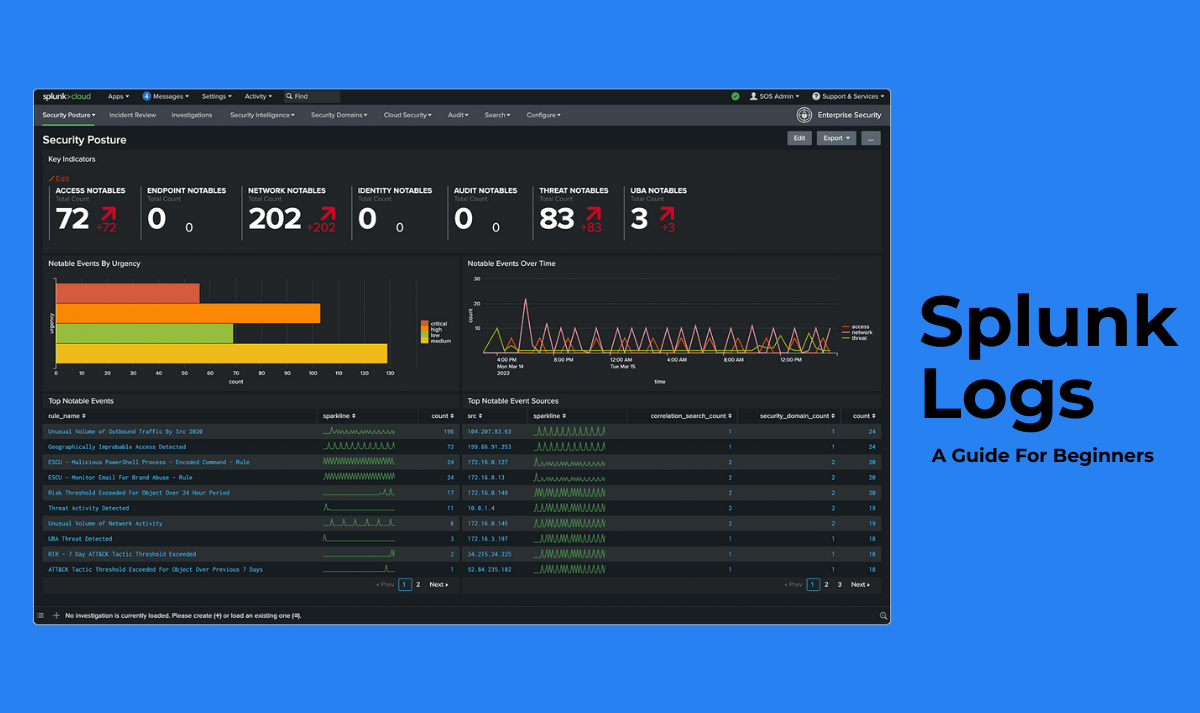
Splunk Logs- A Guide For Beginner
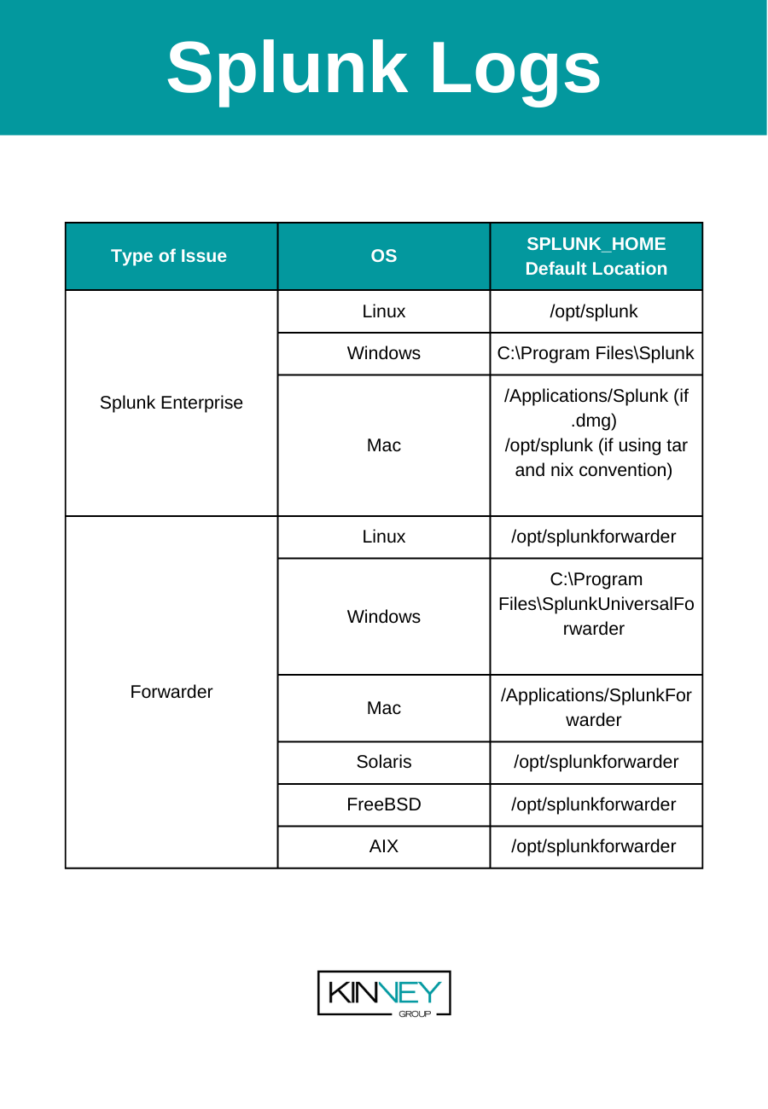
A Beginner's Guide to Splunk Logs - Kinney Group
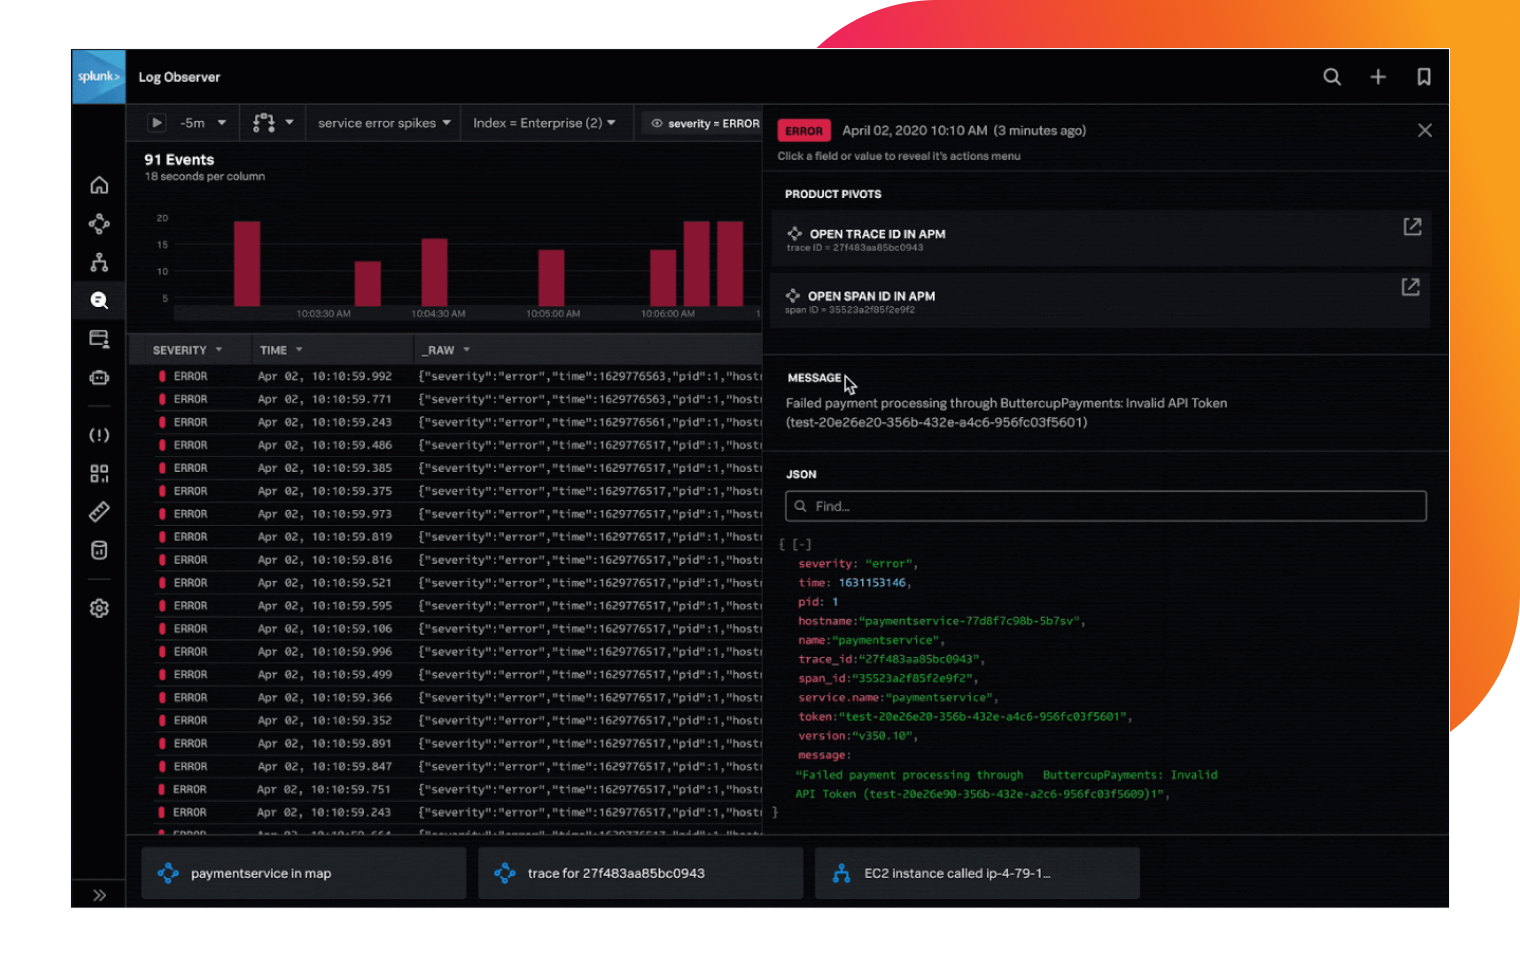
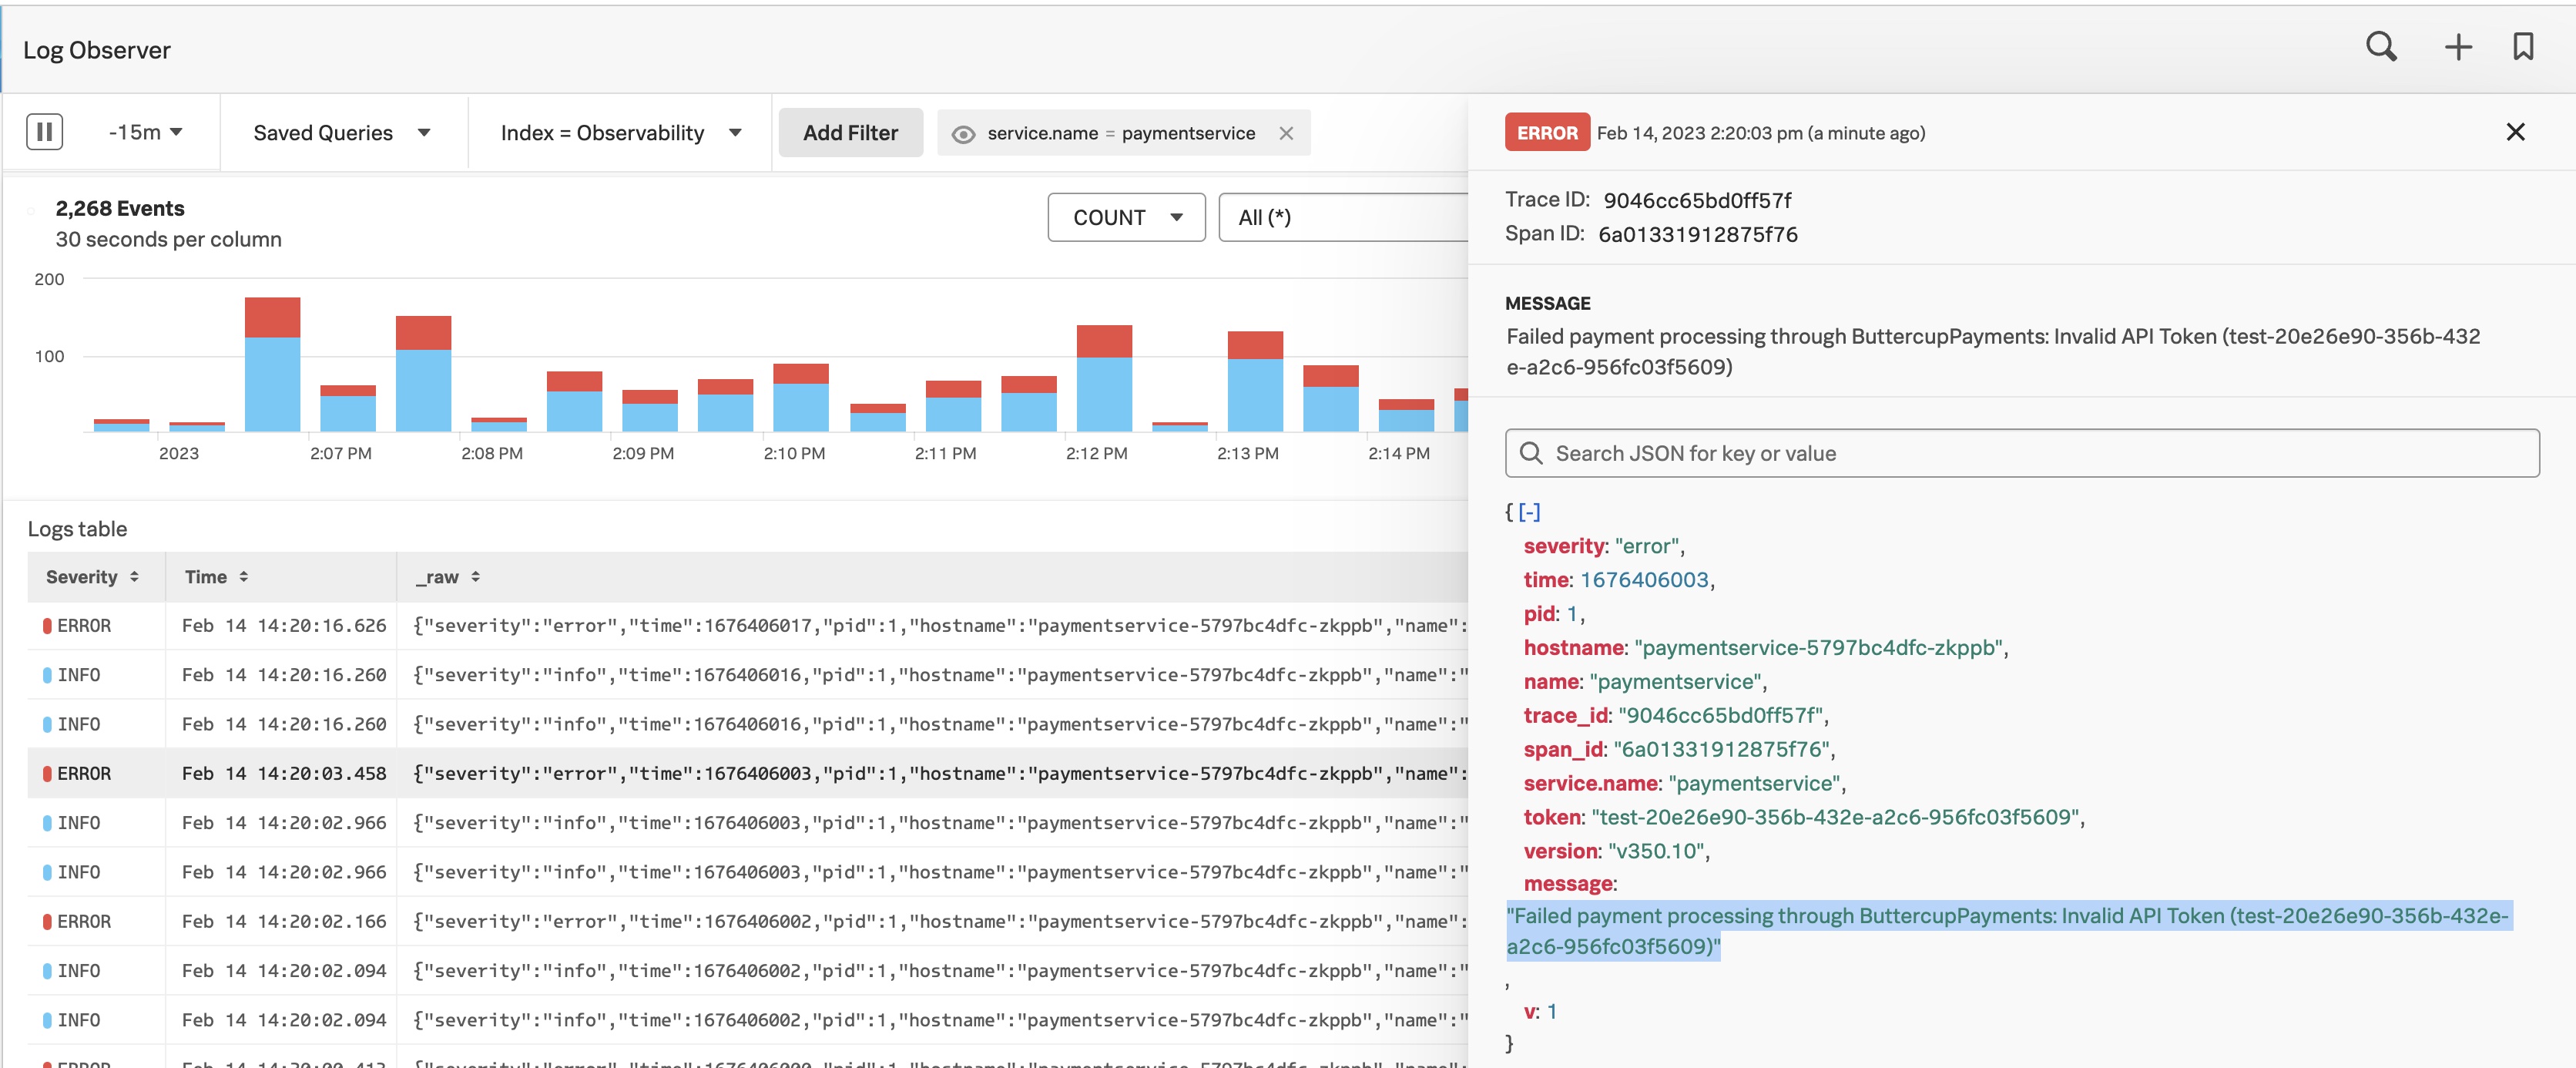
Splunk Log Observer Connect | Splunk
What Are Splunk Logs at William Gutirrez blog
Splunk Log Processing at Alana Mcgovern blog
Splunk for Beginners: Making Sense of Logs and Security Data
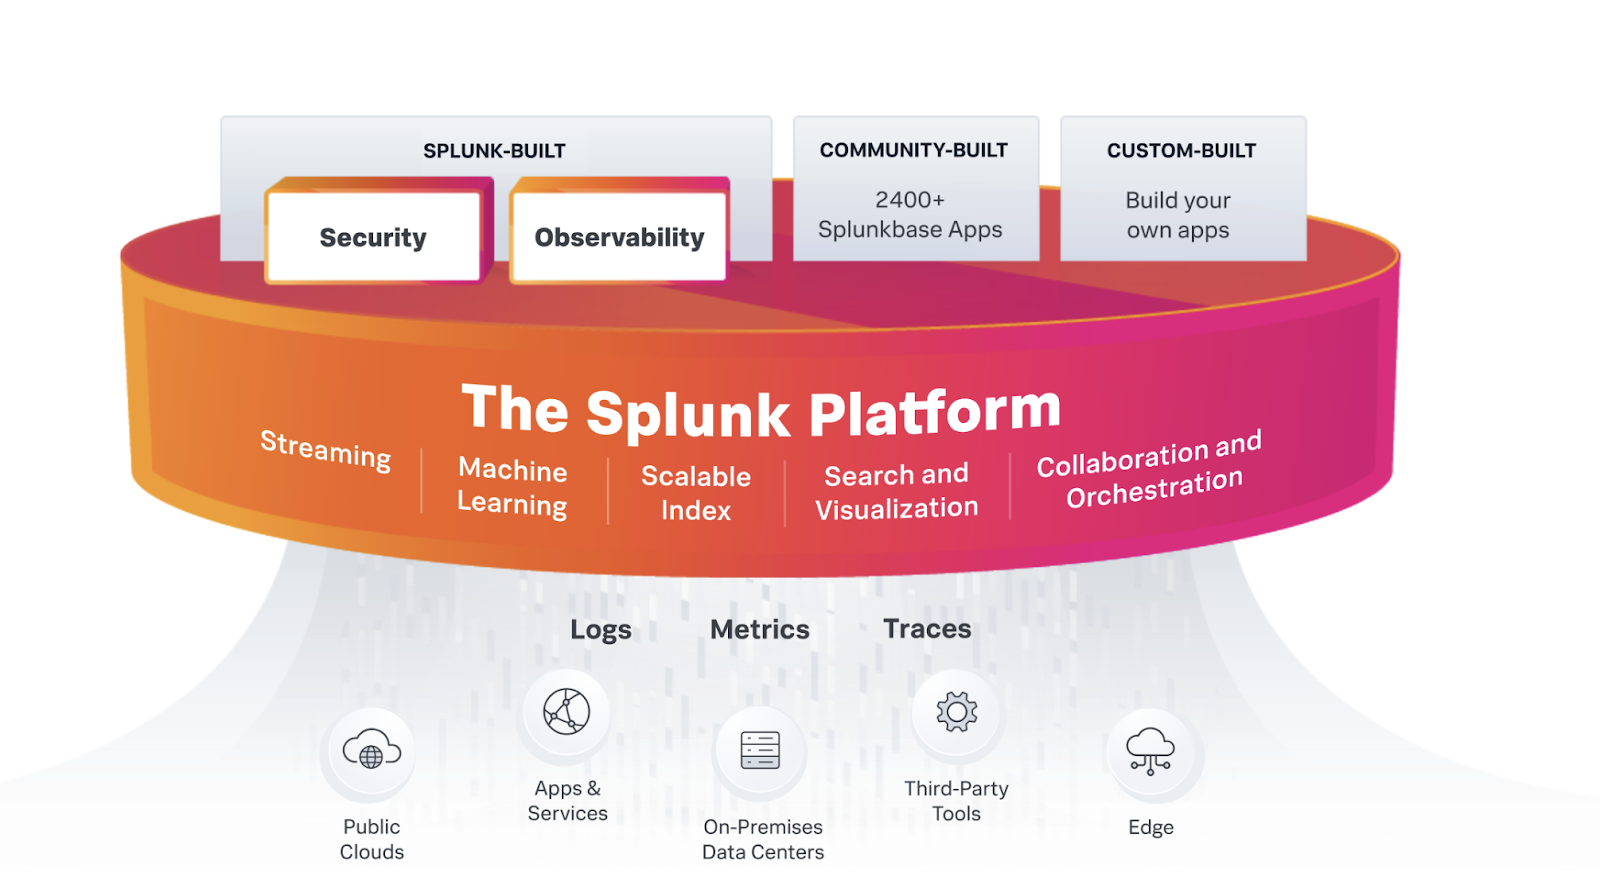
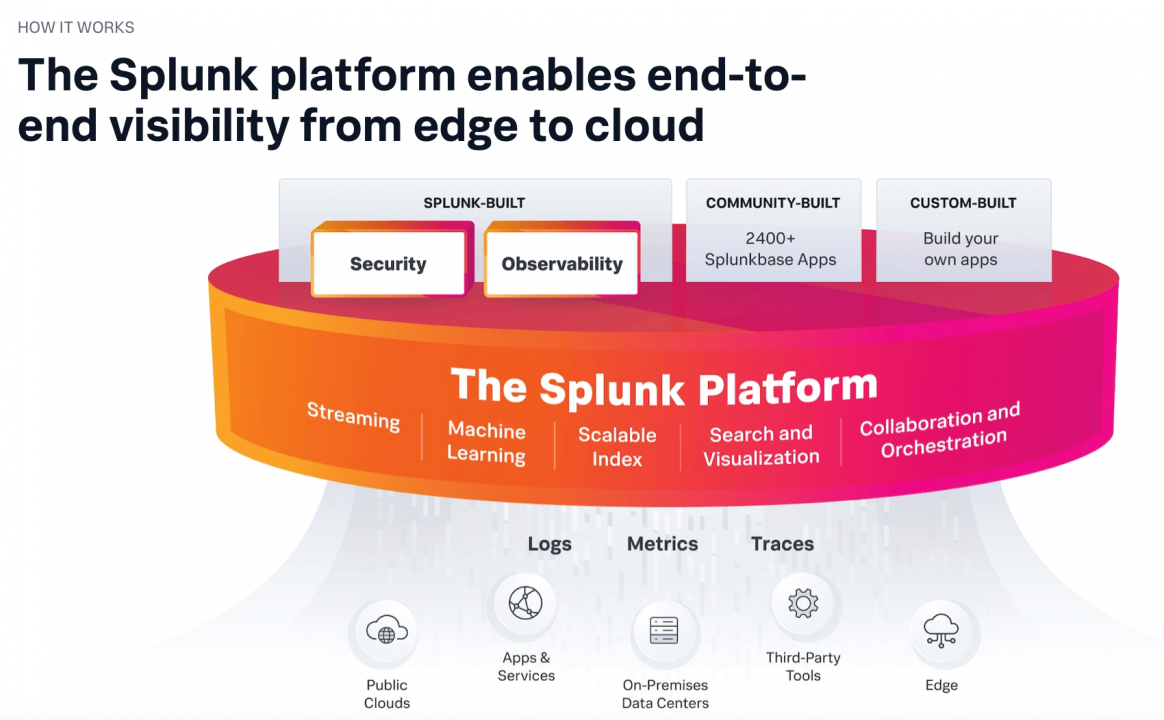
Platform | Splunk
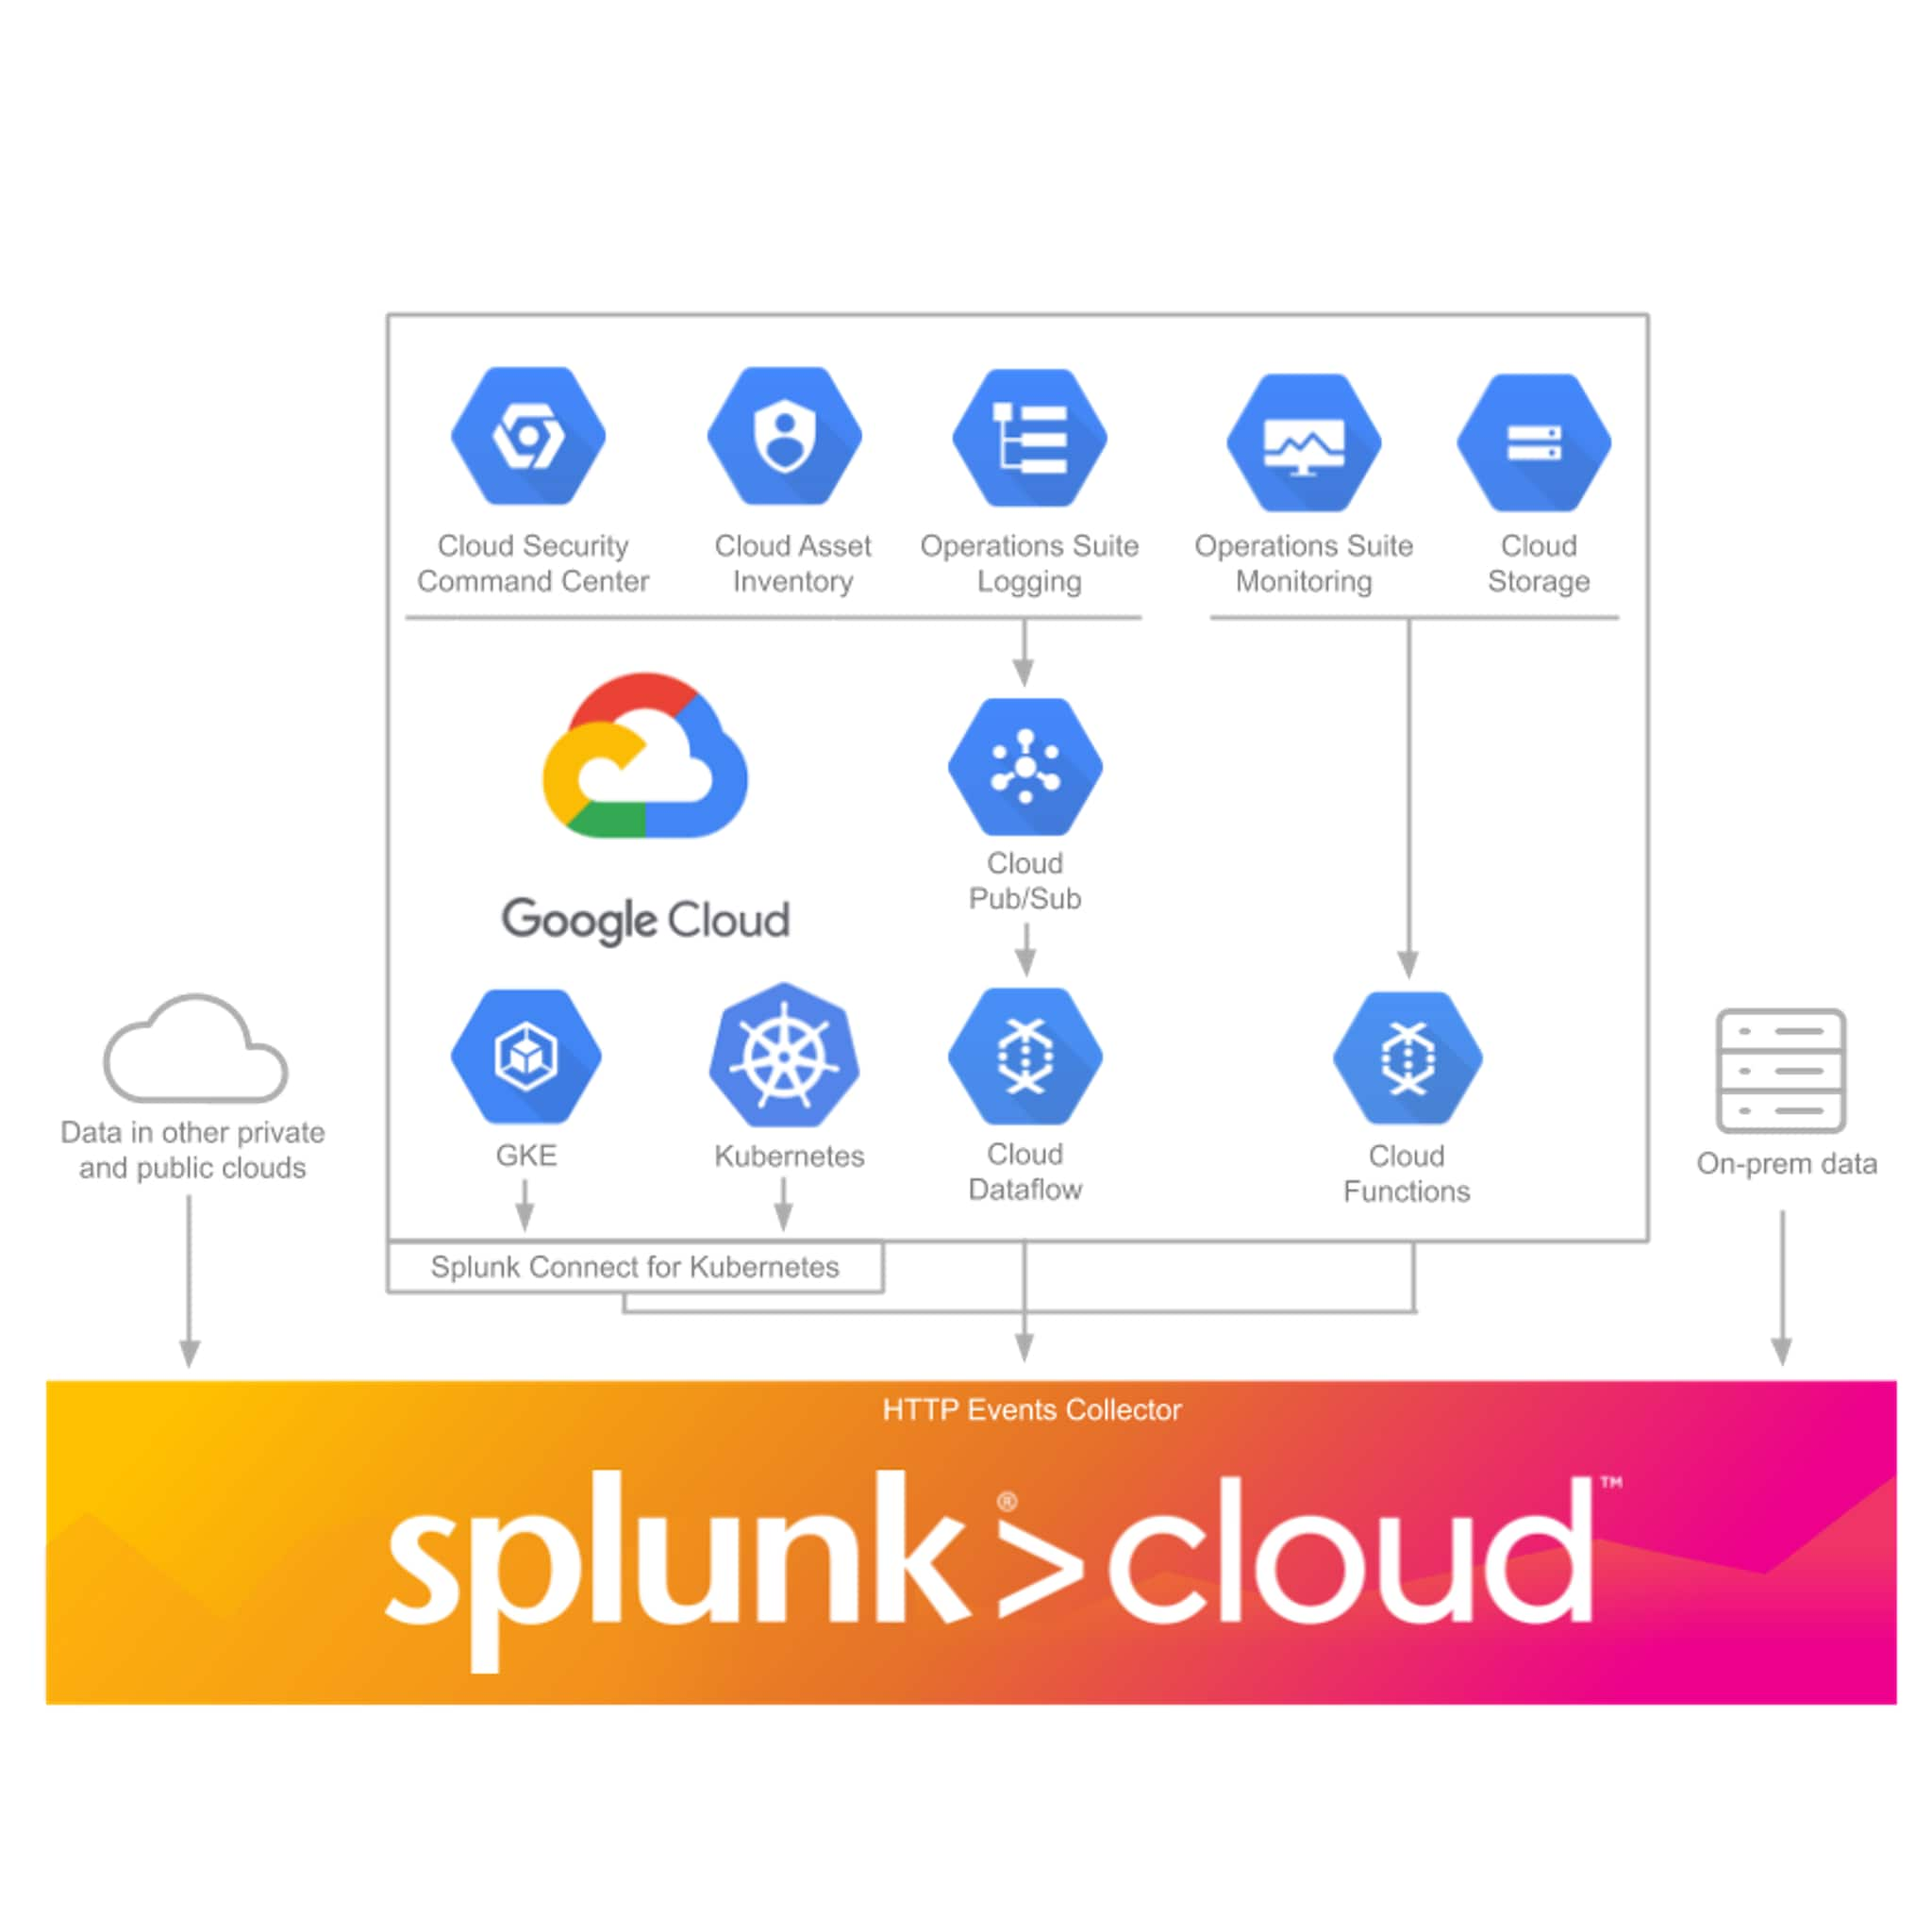
OCI Logs integration with Splunk Cloud | by Karthic | Medium
Tech Talk | How to Use Logs from Splunk Platform i... - Splunk Community
What Is Splunk Log Files at Lucas Cade blog
Splunkってなんじゃ?(IisのログをSplunkで解析) | Splunk ログ管理 – GQNK
How to Analyze Logs in Splunk - YouTube
Everything you Wanted to Know About Sending Logs t... - Splunk Community
Using Syslog-ng with Splunk | Splunk
Splunk in 60 Minutes | Splunk Tutorial For Beginners | Splunk Training ...
Splunk — performance tuning tips — indexing tier | by Gareth Anderson ...
Mint Security - Log Management & SIEM - Splunk and Sentinel
Elevate Your Security Program with Splunk and Tenable | Splunk
Delay and lagging performance issues within the Splunk Search Head ...
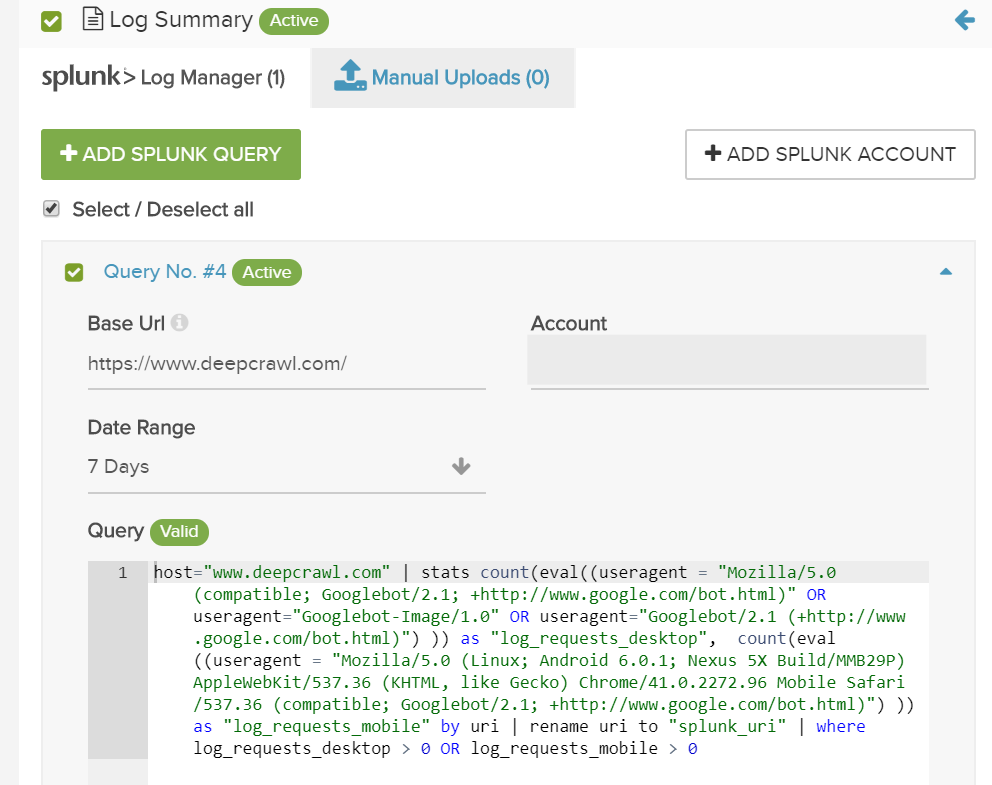
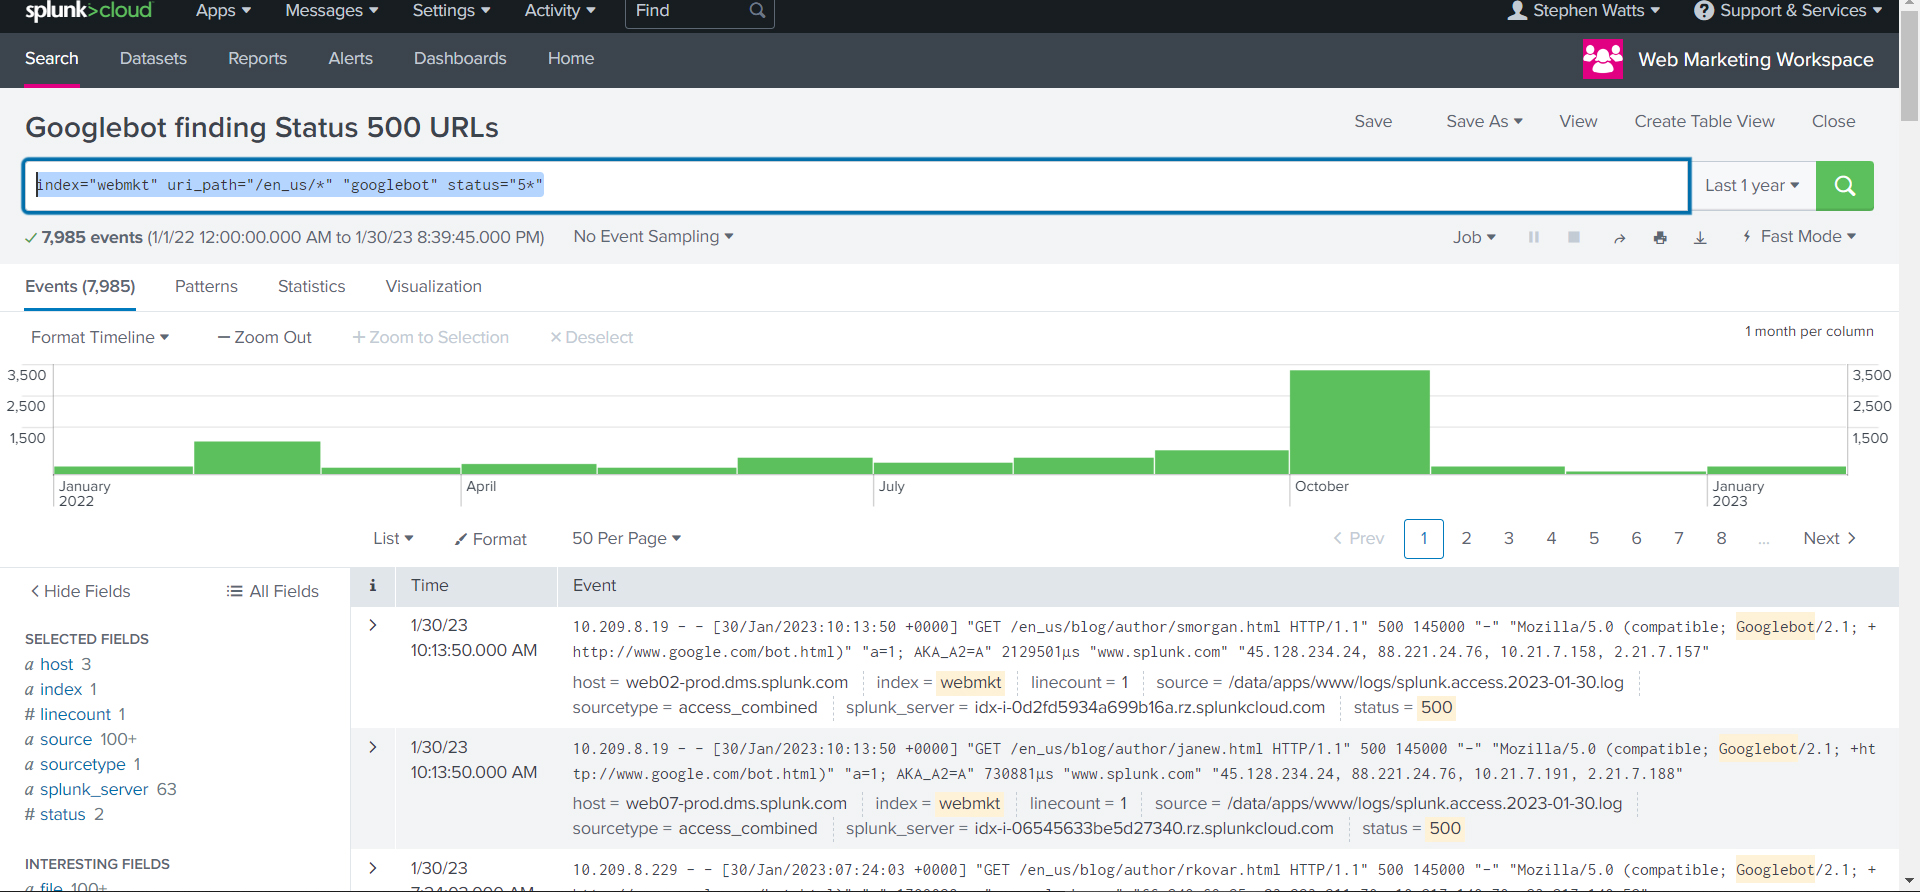
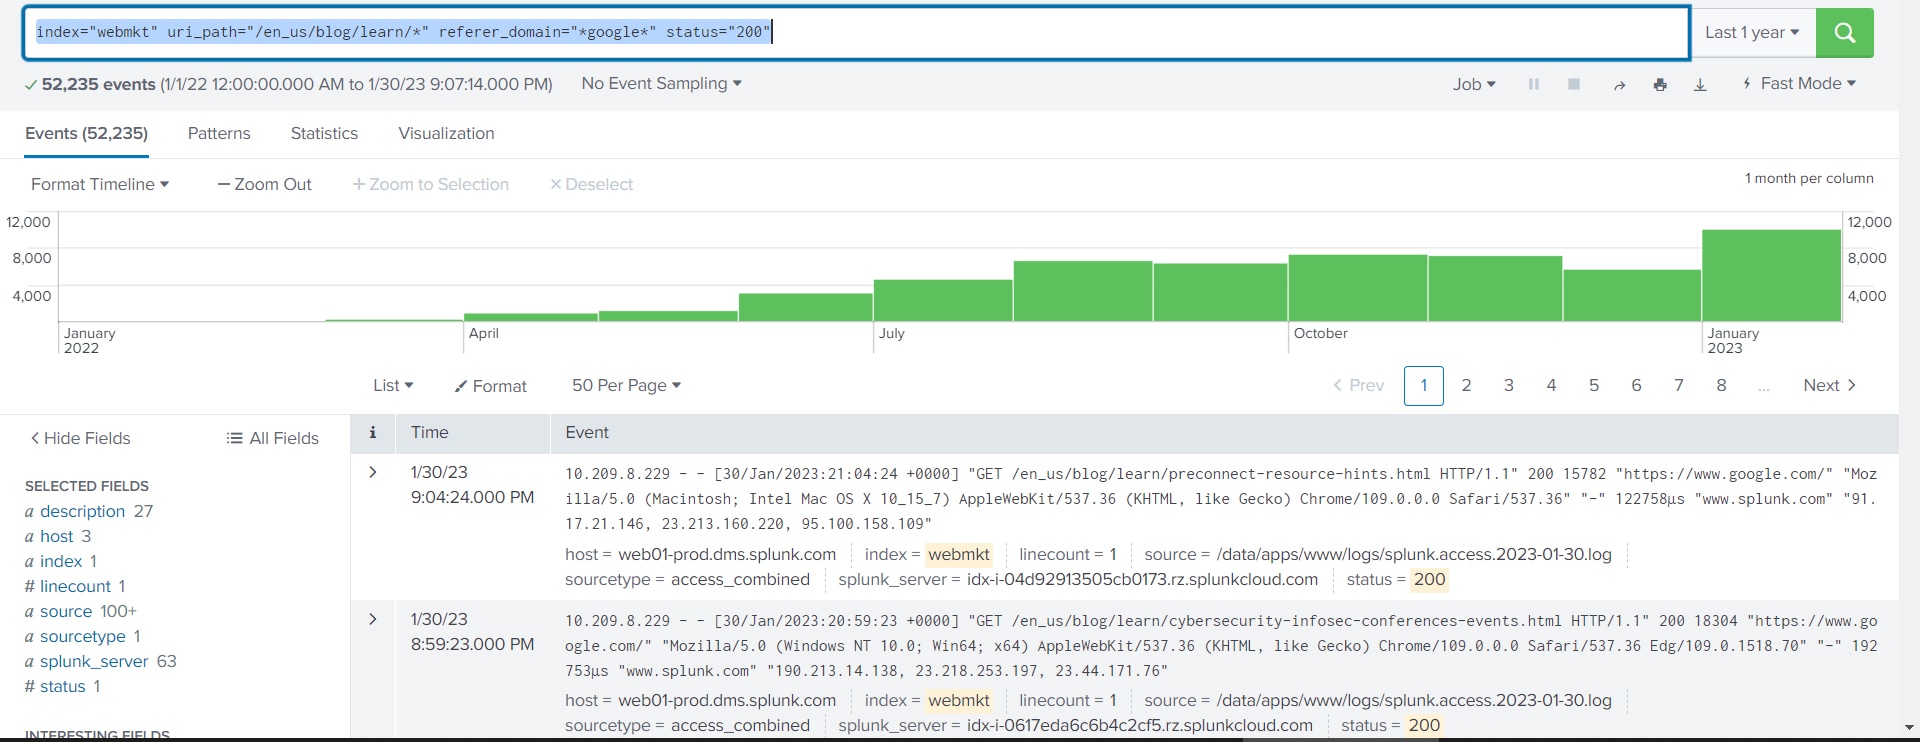
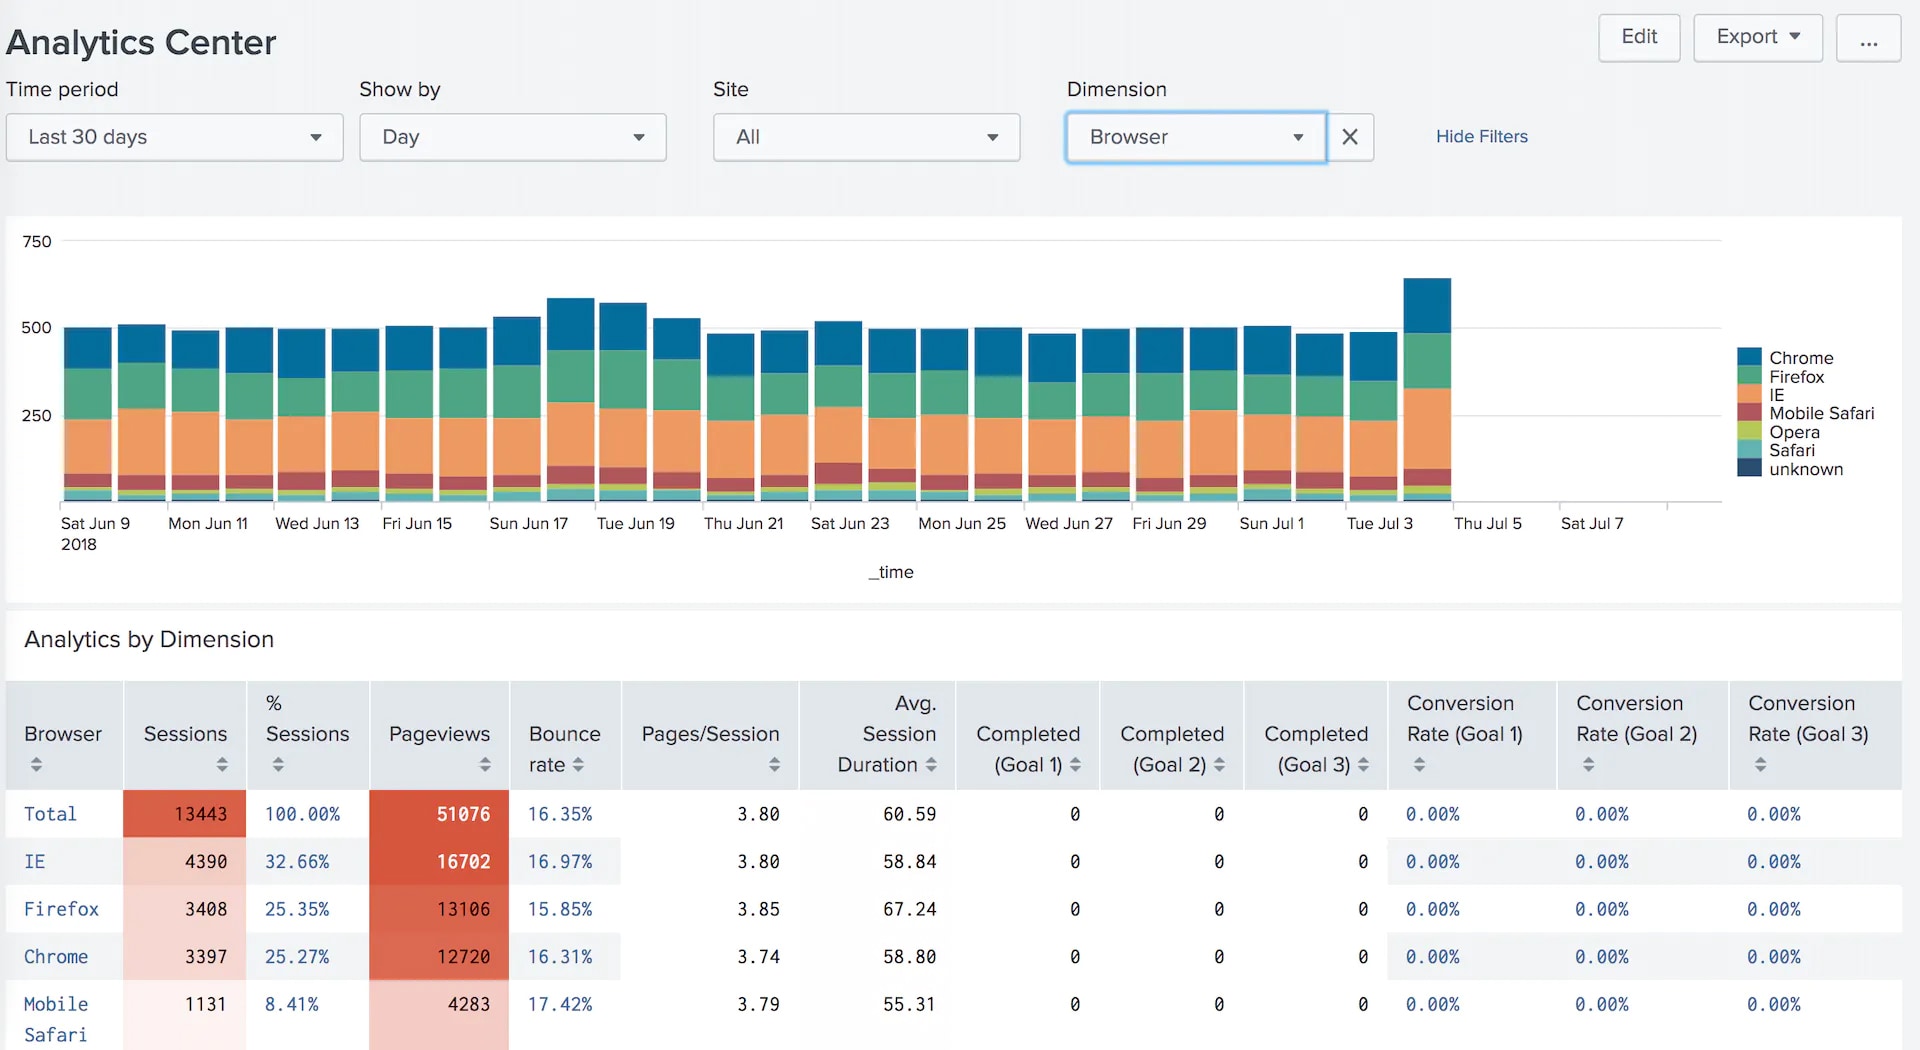
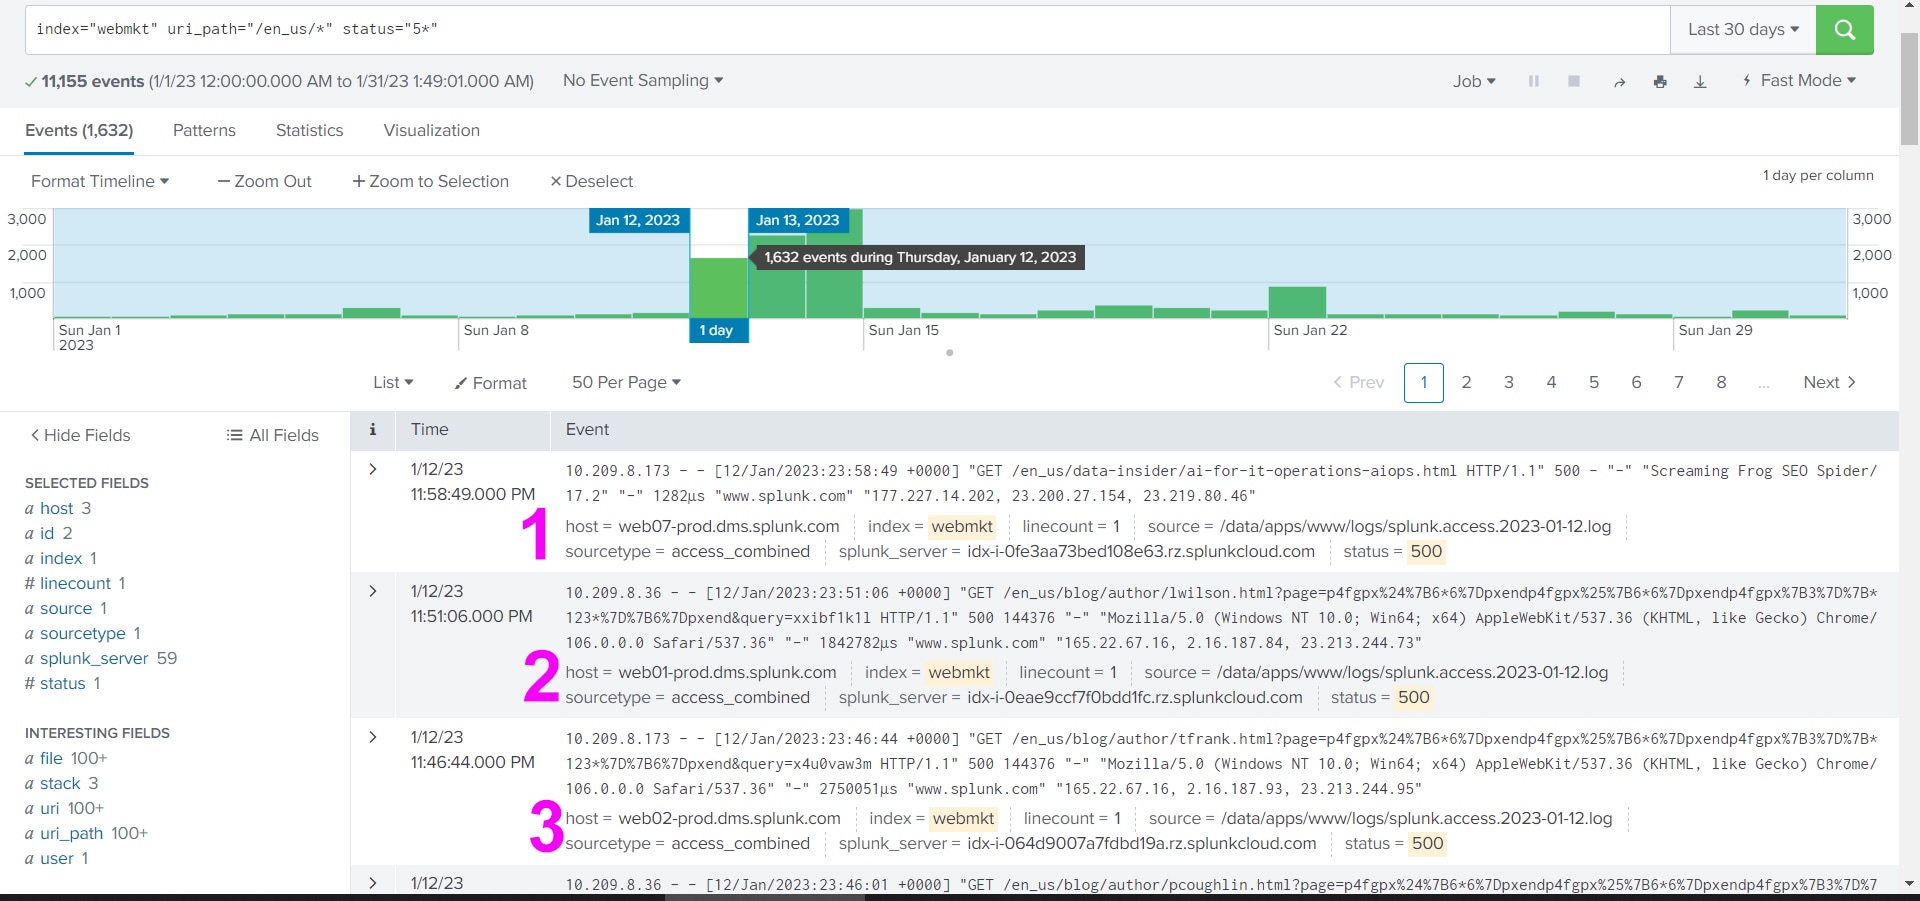
Using Splunk for SEO Log File Analysis | Splunk
Splunk Logs- Types of Splunk Logs Files Explained
Splunkサーチコマンド > stats、eventstats、streamstats | Splunk
Mastering Splunk Logs: Your Ultimate Guide to Log Analysis
Splunk Database Monitoring - Splunk Community
Walkthrough: Conducting Log Analysis with Splunk | by Daryl Brooks | Medium
Logs WIndows to Splunk Cloud - Splunk Community
Pierced Platform Clogs – FOXBLOOD
Splunk logs query - lilyneed
What's New in Splunk Observability Cloud and Splun... - Splunk Community
New Release | Splunk Cloud Platform 10.1.2507 - Splunk Community
GETTING ALL LOG DATA IN SPLUNK WITH UNIVERSAL FORWARDERS | by Yogesh ...
Splunk not formatting AMP logs - Splunk Community
Splunk For Dummies Pdf _ Splunk Tutorial Pdf – GDYDW
A Guide To Easy Log Analysis Using Splunk
Intégration de Splunk dans Sophos Firewall | SOPHOS
The Story and Evolution of Clogs - WorkWear.org | WorkWear.org
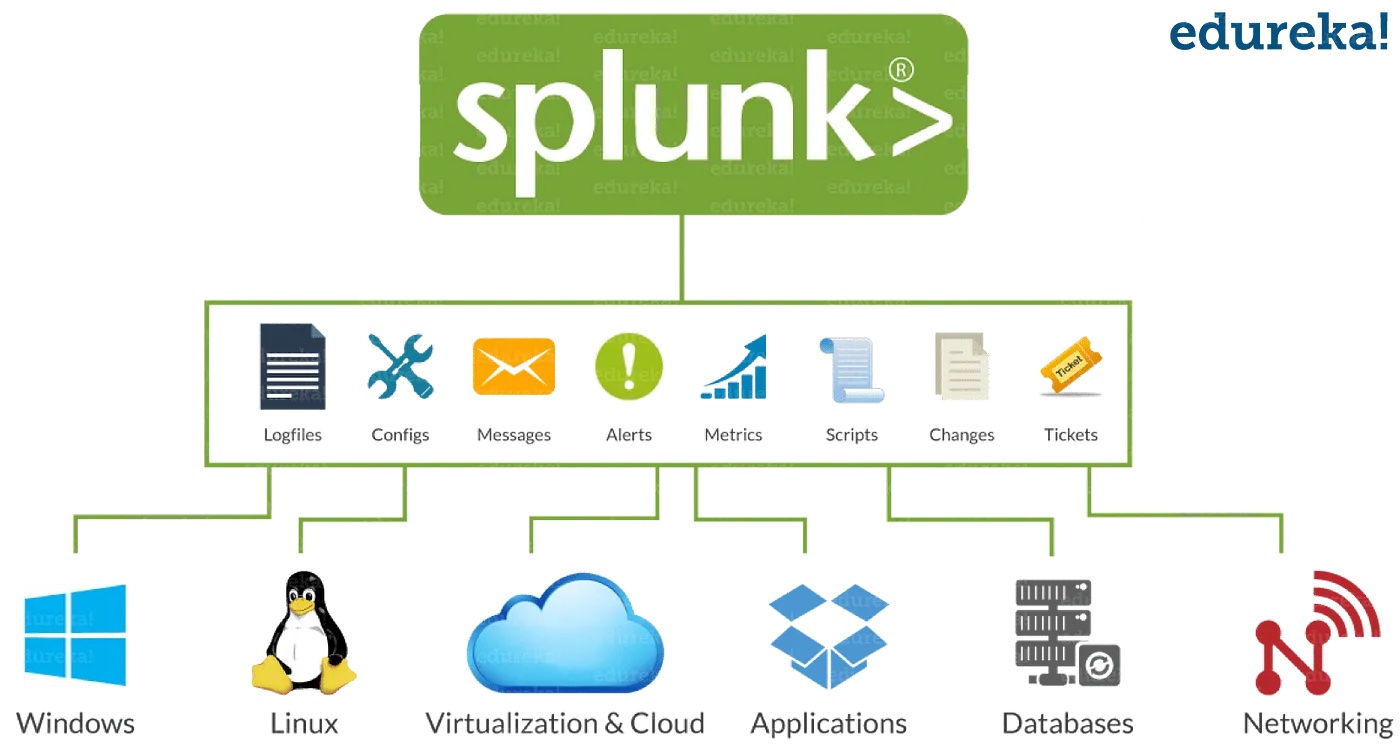
Splunk Enterprise: Architecture, Features, And Capabilities – IWZX
Что такое Splunk и с чем его едят — «Хакер»
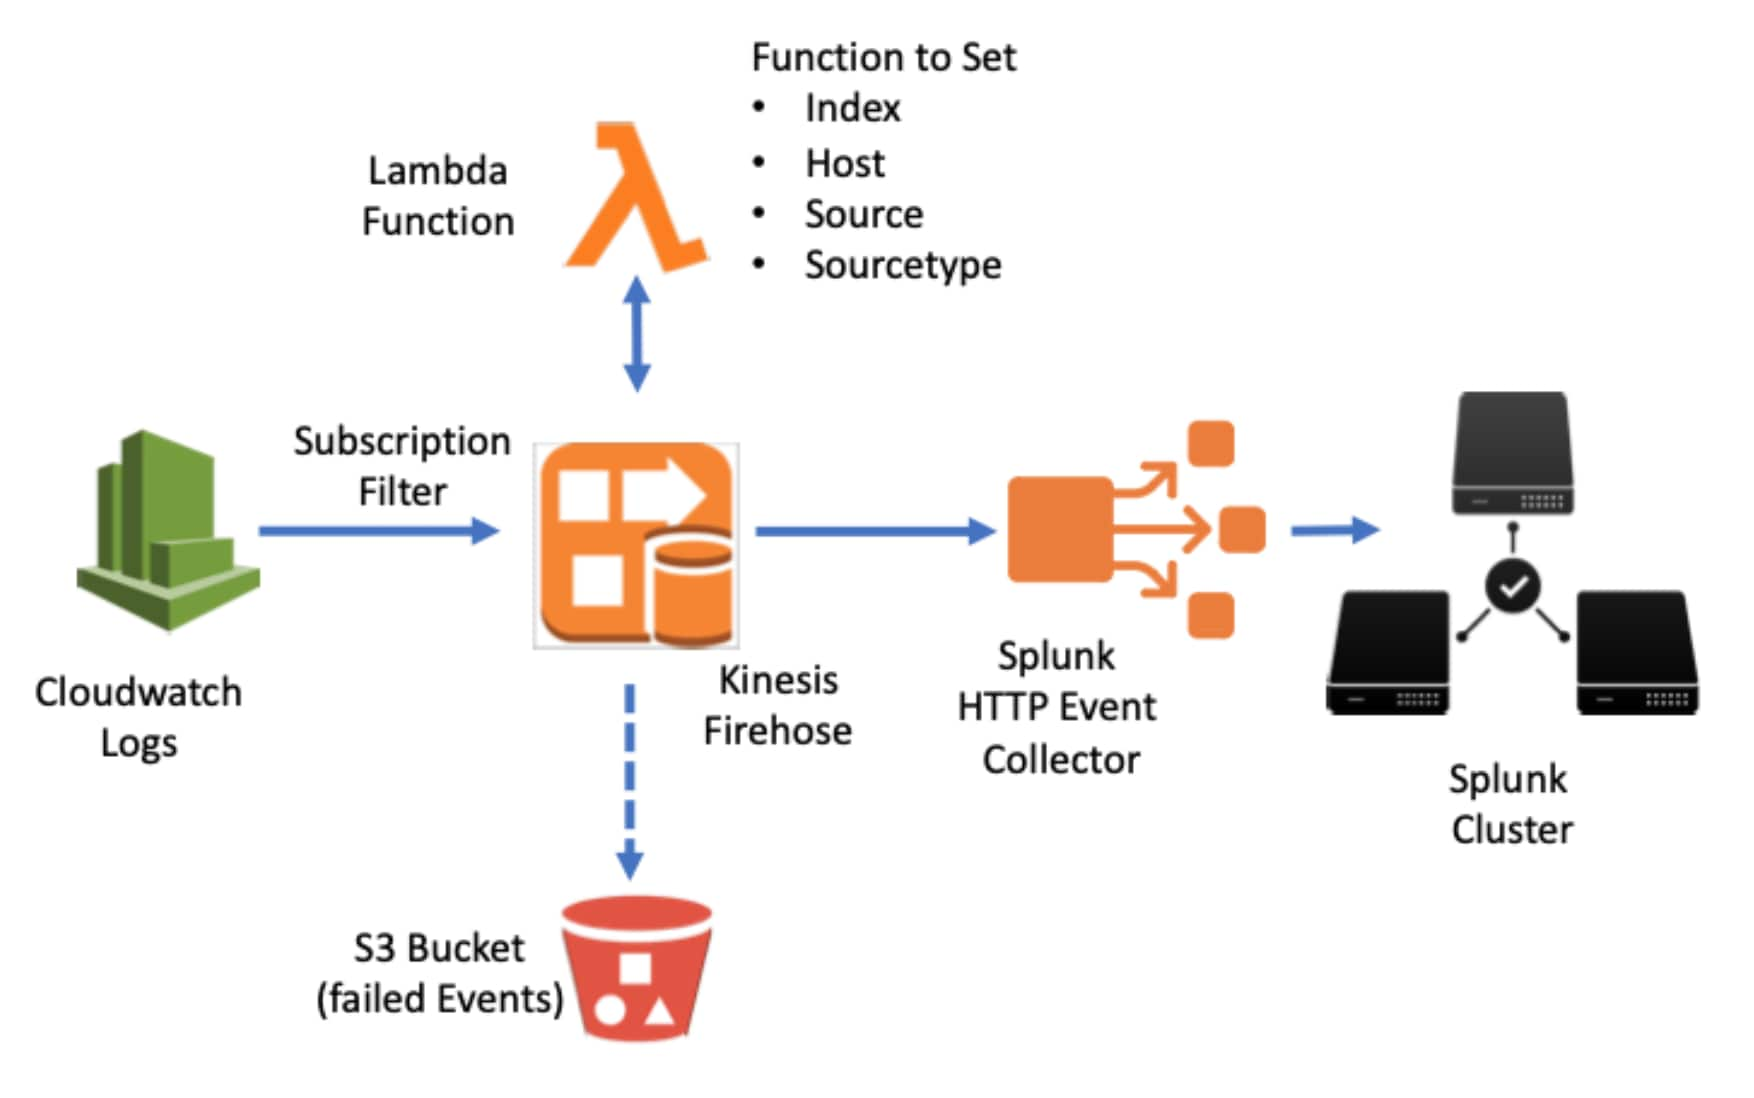
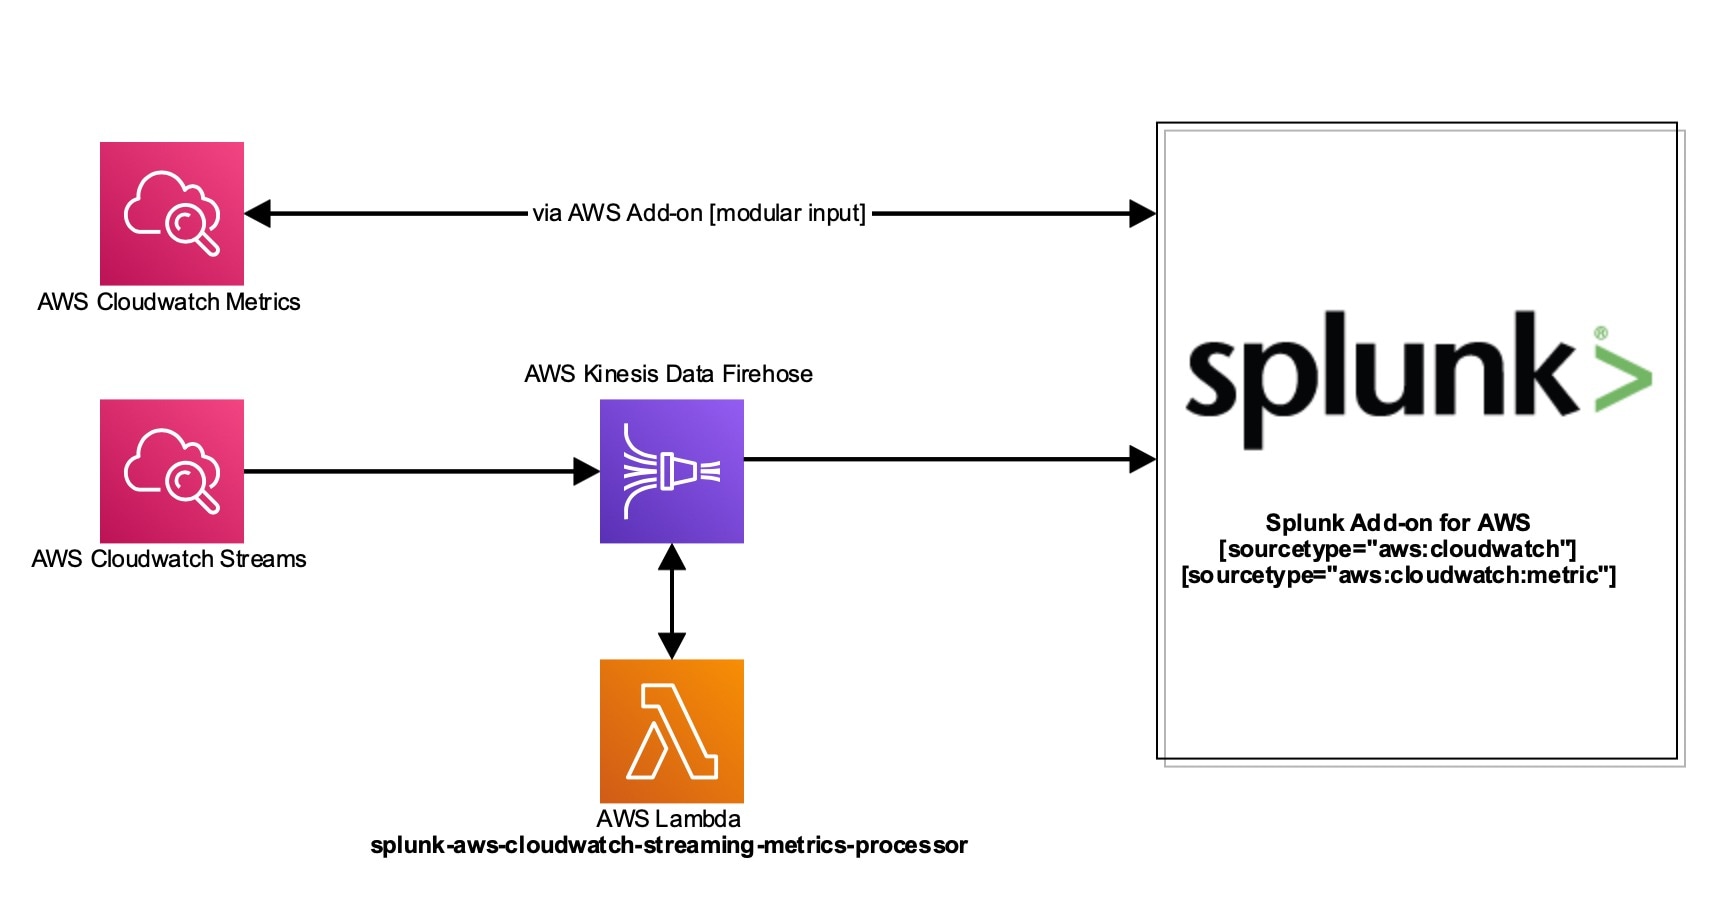
Making the Collection of Centralised S3 Logs into Splunk easy with ...
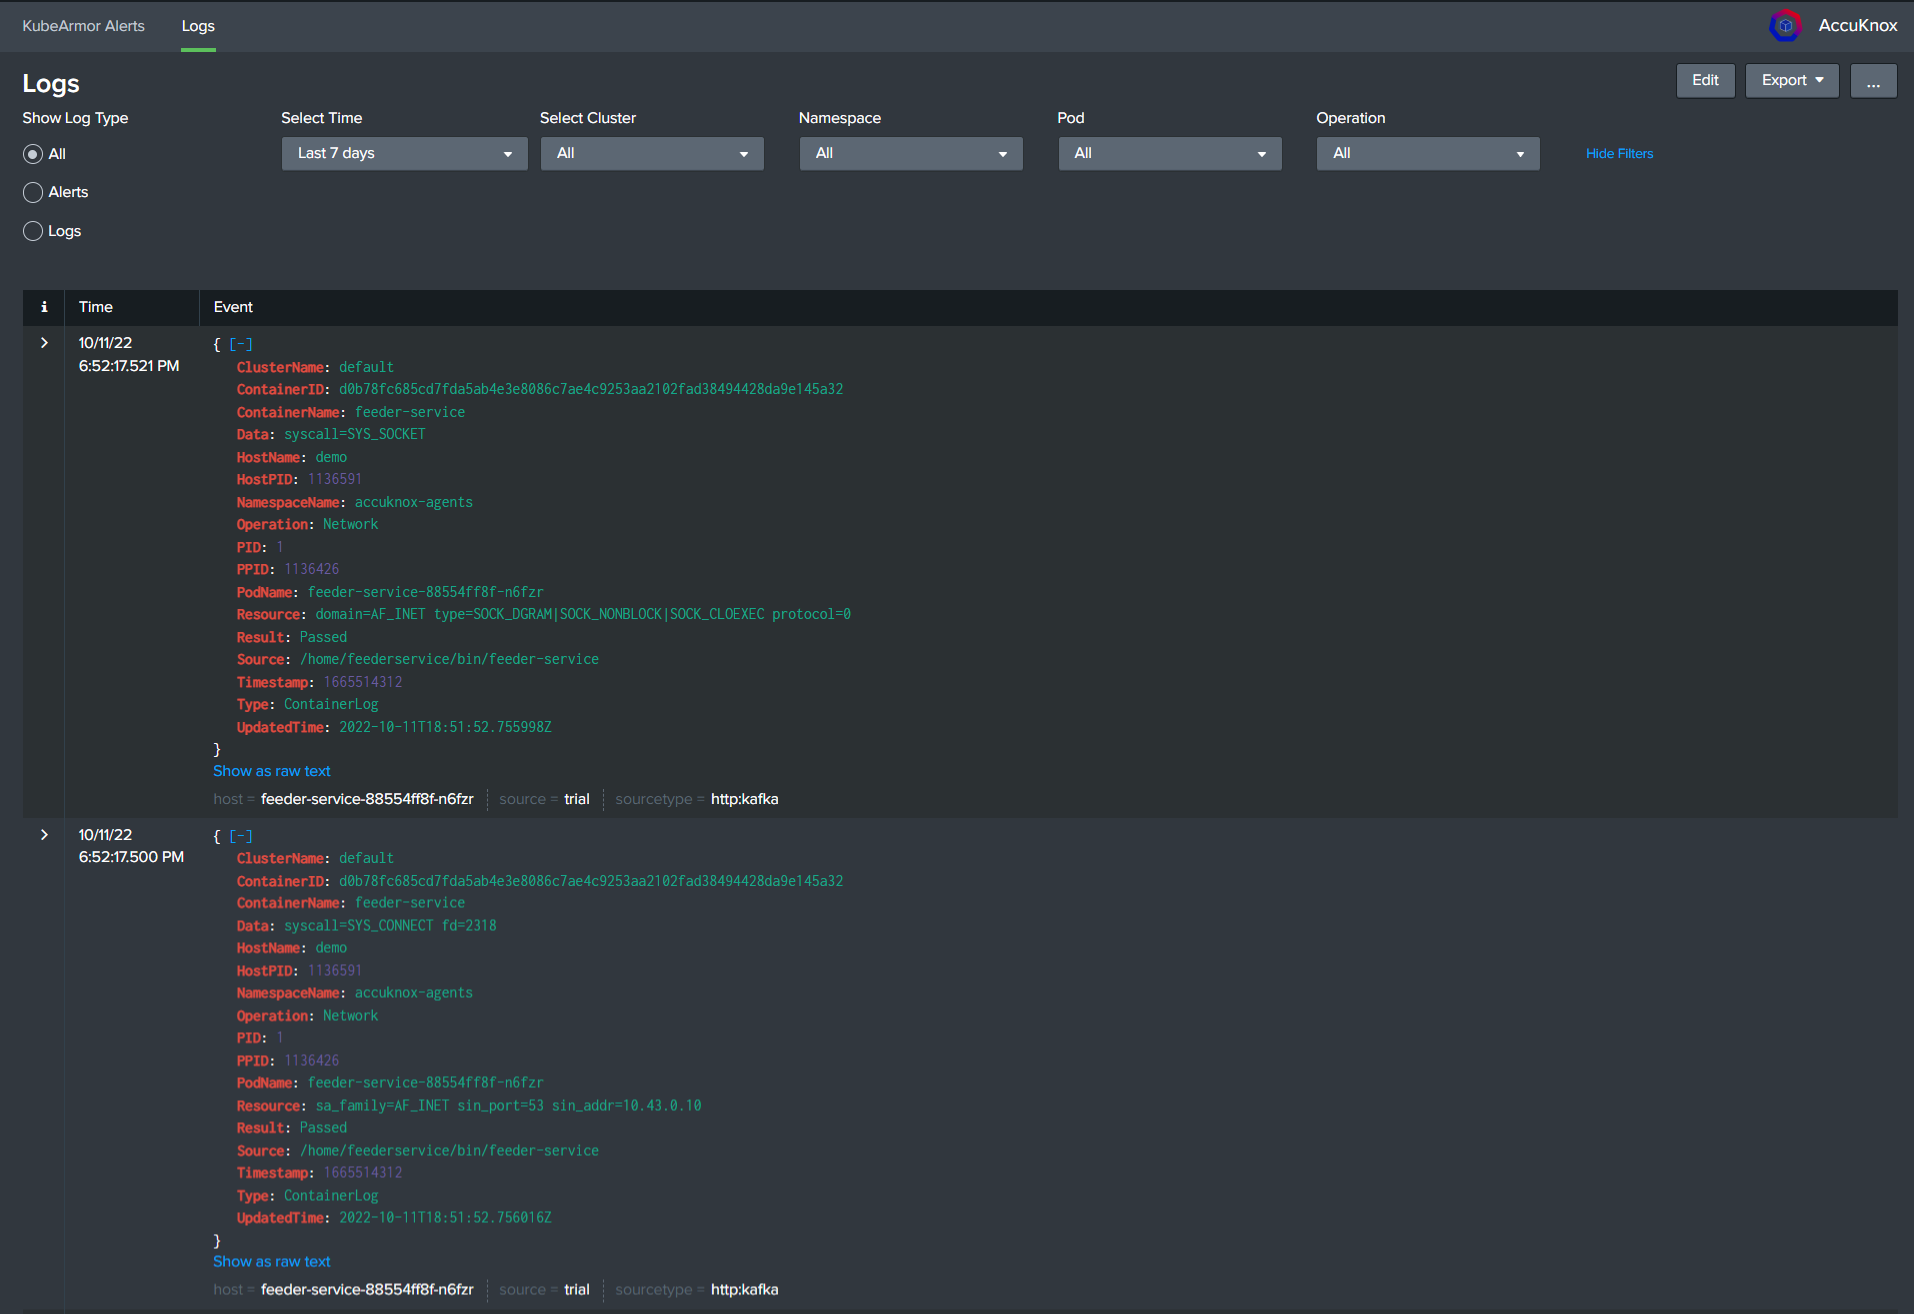
Introducing AccuKnox Insights Integration With Splunk
What Is Splunk Used For? (2026 Guide)
Splunk Cloud Platform and BYOL Integrations | Cribl Docs
How Clogs Improve Posture and Reduce Back Pain for Healthcare Workers ...
Splunk Stats Command Tutorial - YouTube
What's New in Splunk Observability - November 2025 - Splunk Community
The Beginners Guide to Splunk Logs - Kinney Group
What Is Splunk Cooked Data at Cynthia Ridgeway blog
Introducing Splunk Federated Search | Splunk
New Splunk TcpOutput persistent queue - Splunk Community
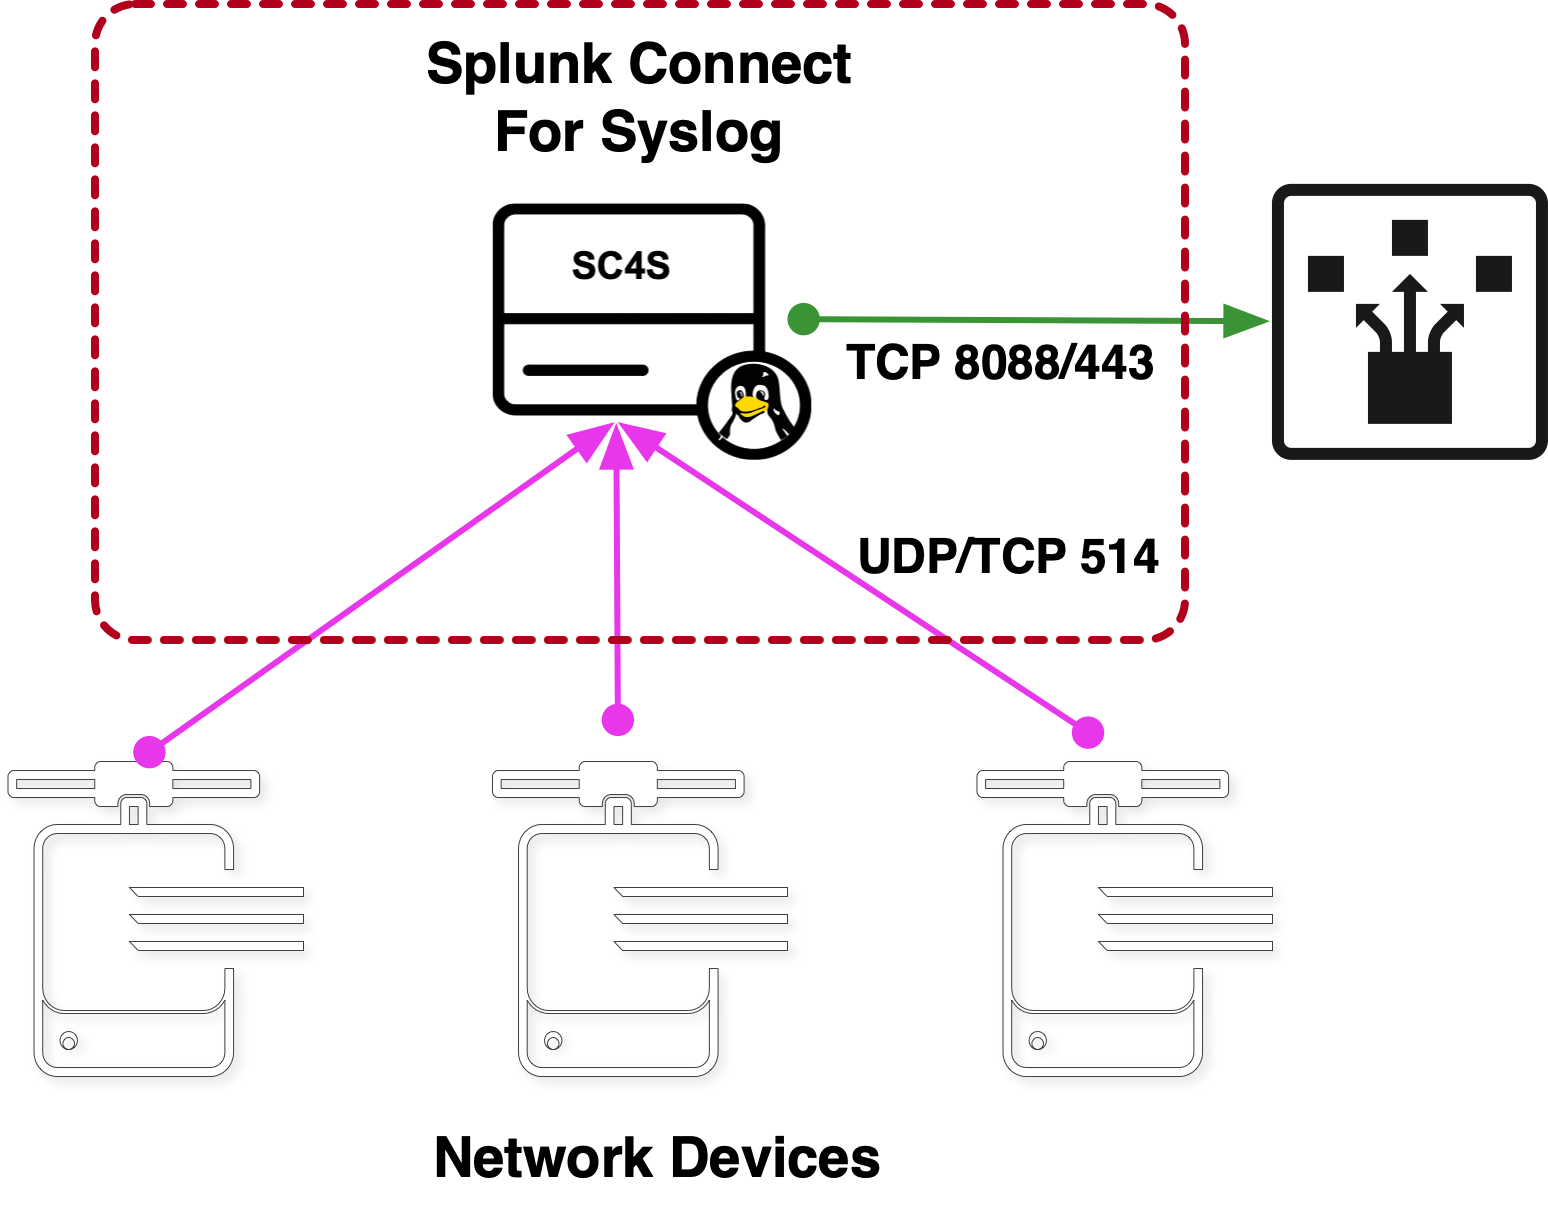
Splunk Connect For Syslog Frequently Asked Questions – MUCMV
Tech Talk | One Log to Rule Them All - Splunk Community
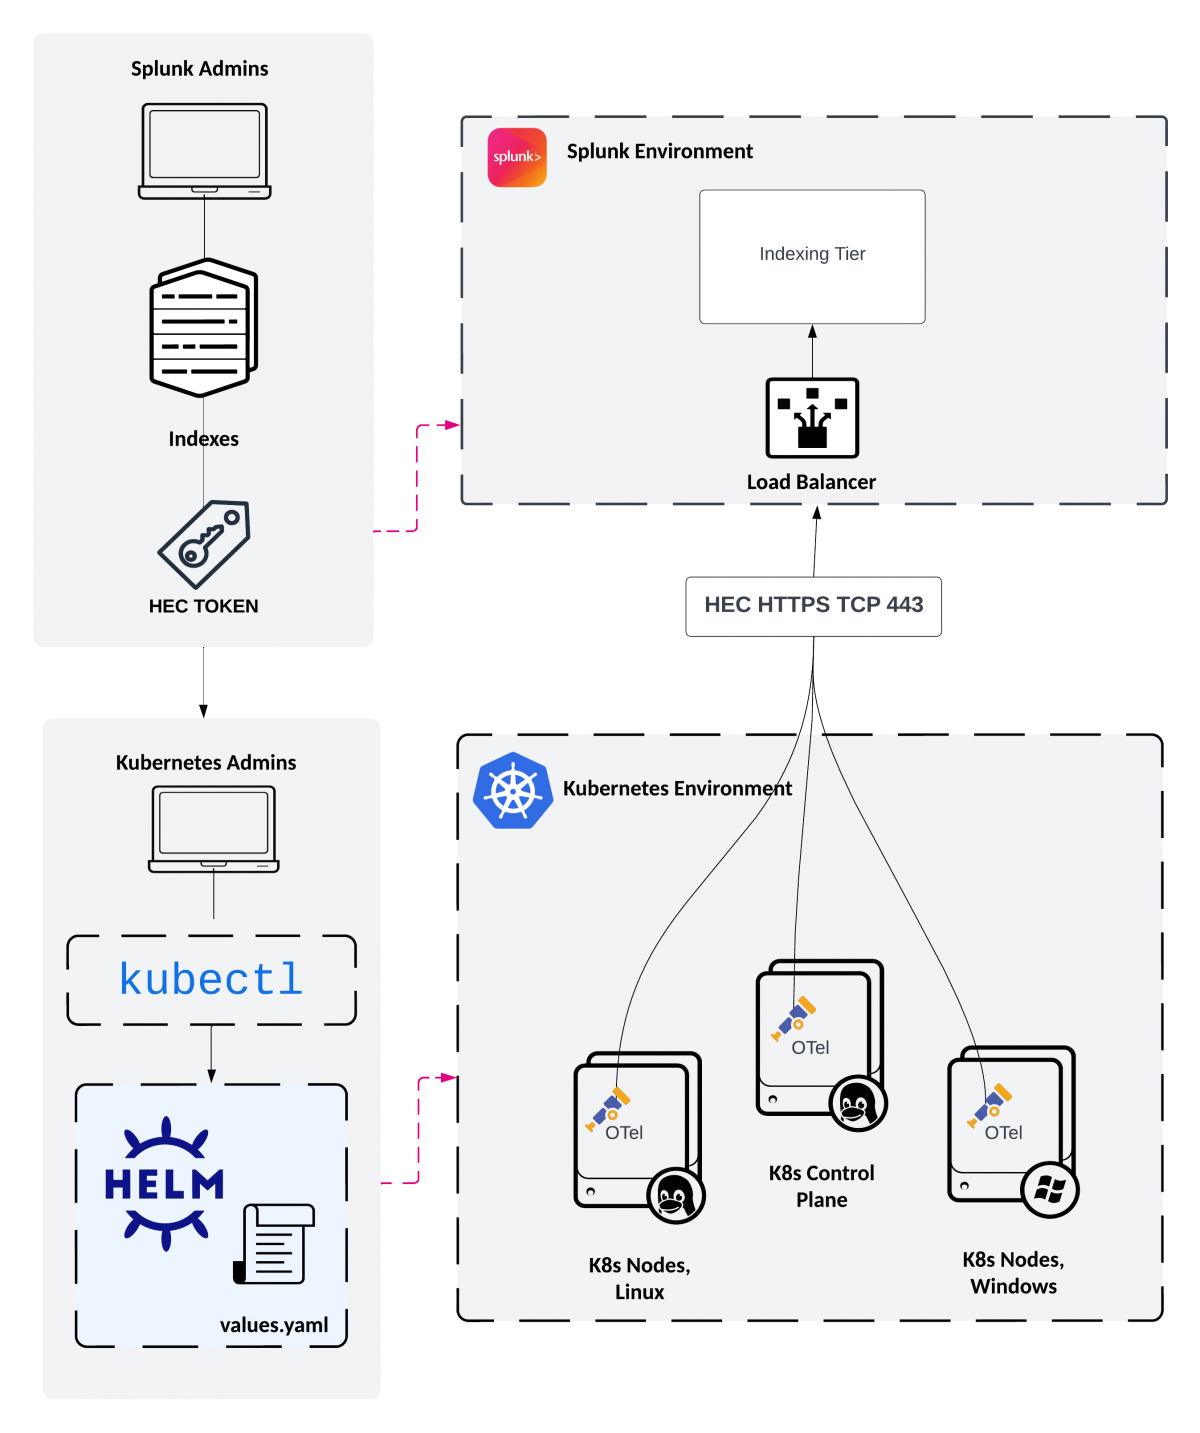
Splunk OpenTelemetry Collector for Kubernetes - Splunk Documentation
What is Splunk - Yi's Blog
Your Guide to Troubleshooting Common Errors in Splunk
高速化したデータモデルとサマリーインデックスによるサーチ時間の短縮 | Splunk
Splunk Tutorial For Beginners: Comment Utiliser Splunk – ALHFO
Clogs
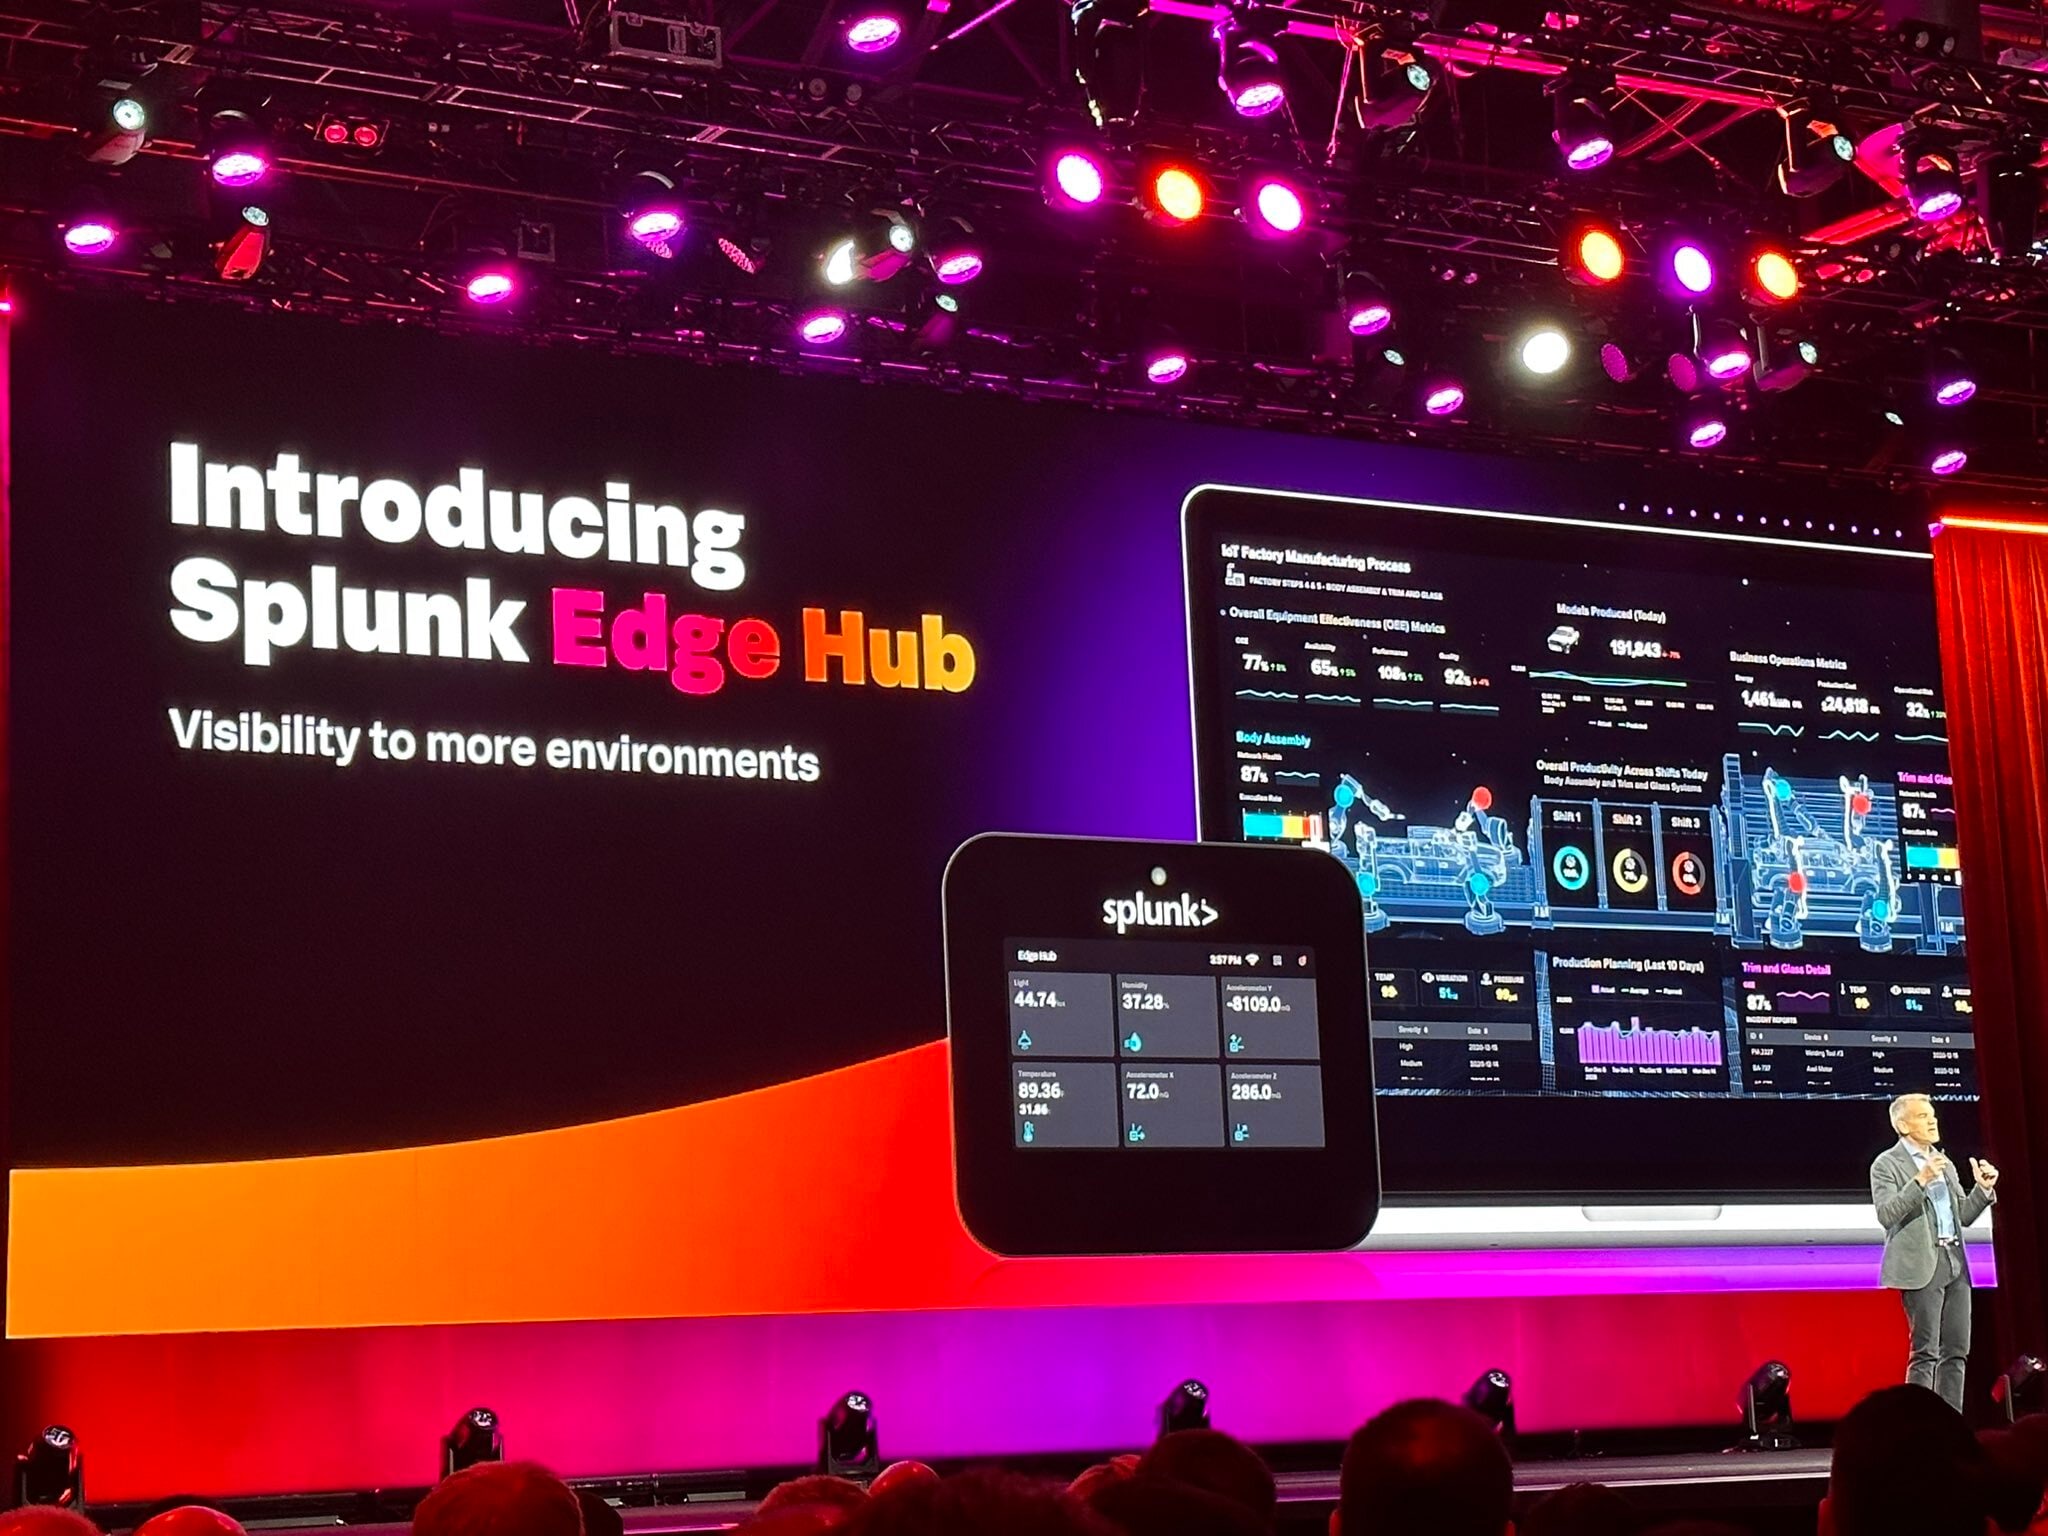
Splunk Brings Augmented Reality Into The Server Room – NEMXDG
The Top 10 Best Splunk Alternatives - Sematext
Splunk Log Observer Connect - Splunk Community
Splunk
Splunk Where List at Paul Alfaro blog
Splunk Where Exists at Sean Chaffey blog
Splunk Log Ingestion & Management | CrowdStrike Marketplace
Splunk 101: A Beginner’s Guide to Harnessing Its Power
Why cant I see my Splunk logs? - Splunk Community
Major Splunk Upgrade – Test and Validate your App ... - Splunk Community
Clogs Are Happening, Folks (No, Seriously), and Here’s How to Get in on ...
Where CISOs need to see Splunk go next | CSO Online
Transform your security operations with Splunk Enterprise Security | Splunk
Splunk UI and the Dashboard Framework: More Visual Control Than Ever ...
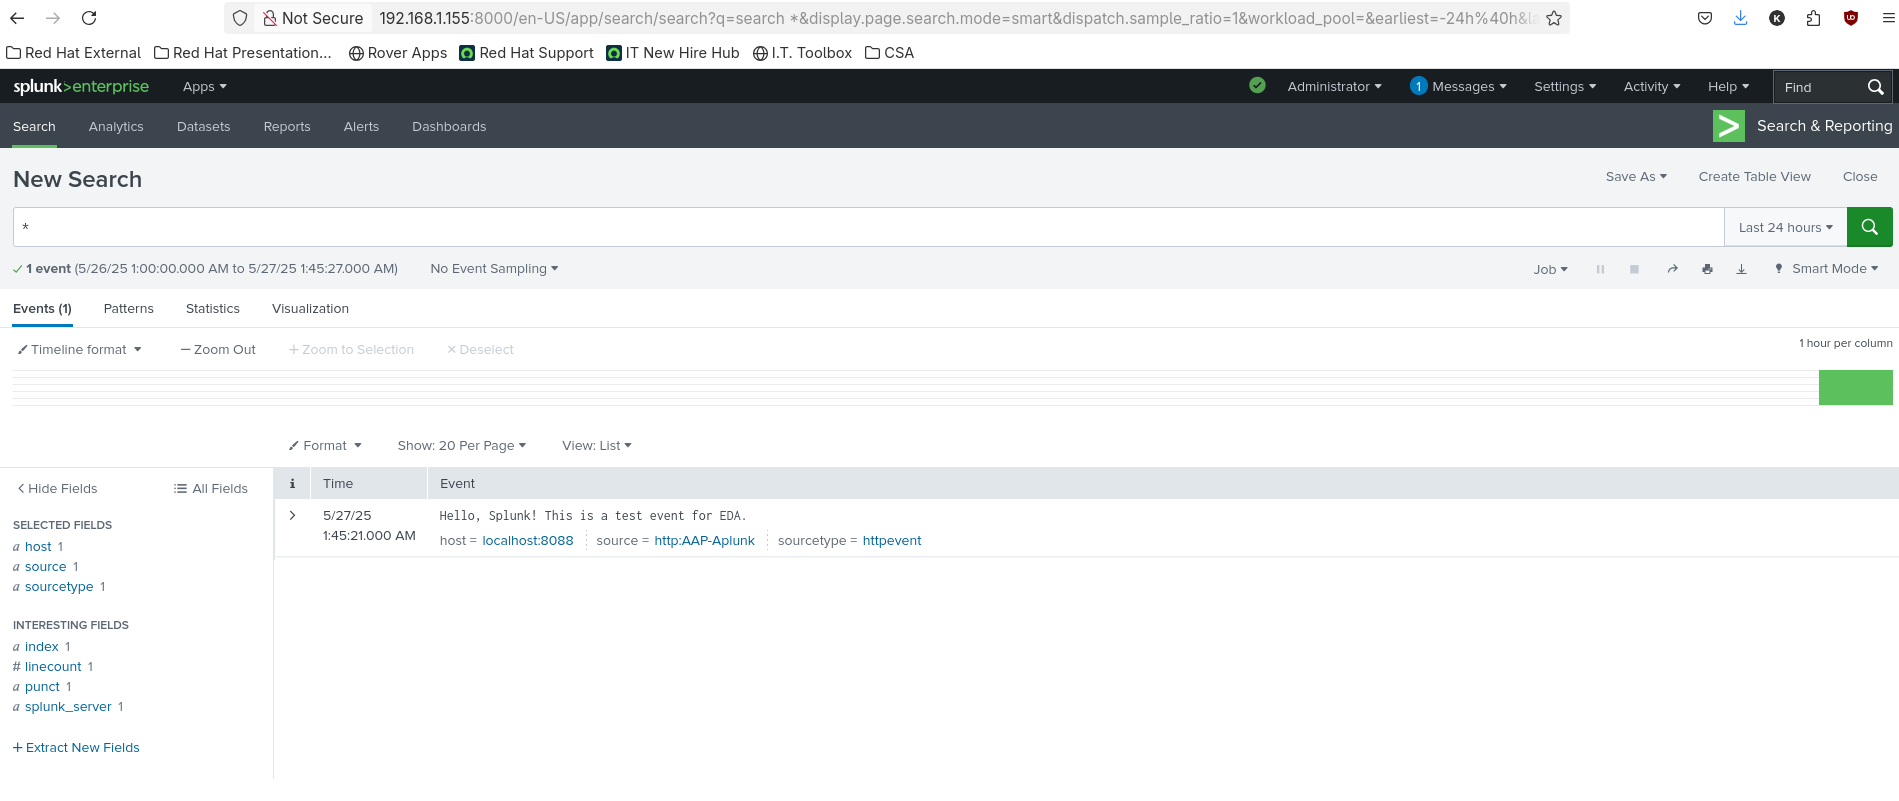
How to use Splunk as an event source for Event-Driven Ansible | Red Hat ...
Splunking Microsoft Teams Data | Splunk
How To Use Splunk Tool – Splunk Infrastructure Monitoring – DDVLNE
Everything You Need To Know About Splunk Search Modes - Kinney Group
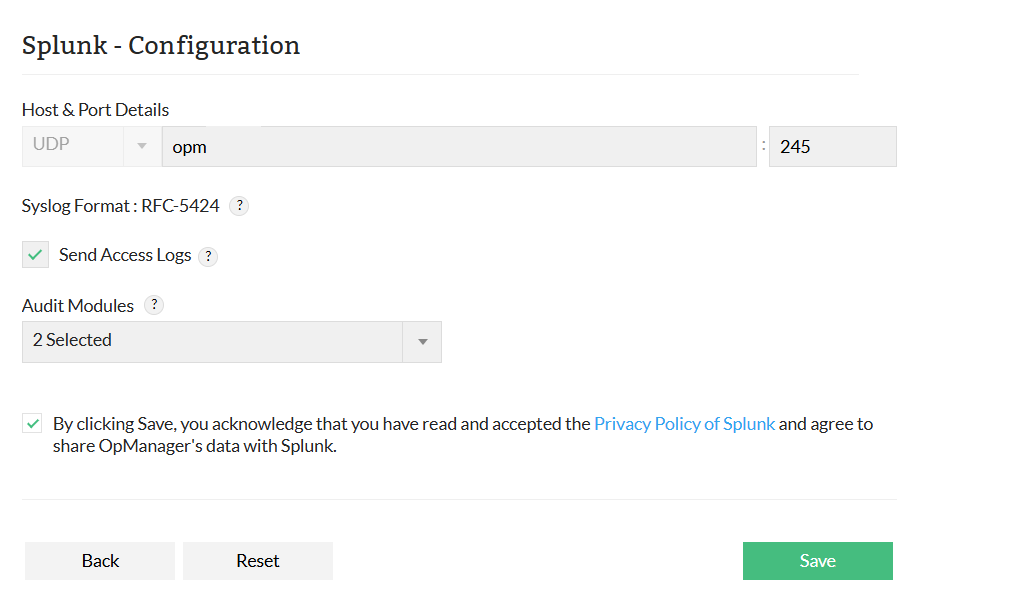
Configuring Splunk Integration | OpManager Help
Splunk 產品 | Splunk
Types Of Splunk Alerts at Robert Bence blog
Splunk Enterprise Security Features | Splunk
Women’s Clogs at M&S
What’s New in Splunk Observability – September 202... - Splunk Community
Braid Clogs - Bendables
Getting Started with Splunk - A Complete Guide for Beginners ...
Splunk Enterprise 9.0, l’importanza di visibilità e automatizzazione
What Are Splunk Dashboards at Clifford Castleberry blog
Platform Slingback Clogs
splunk 画面 – splunk ダウンロード – EXYB
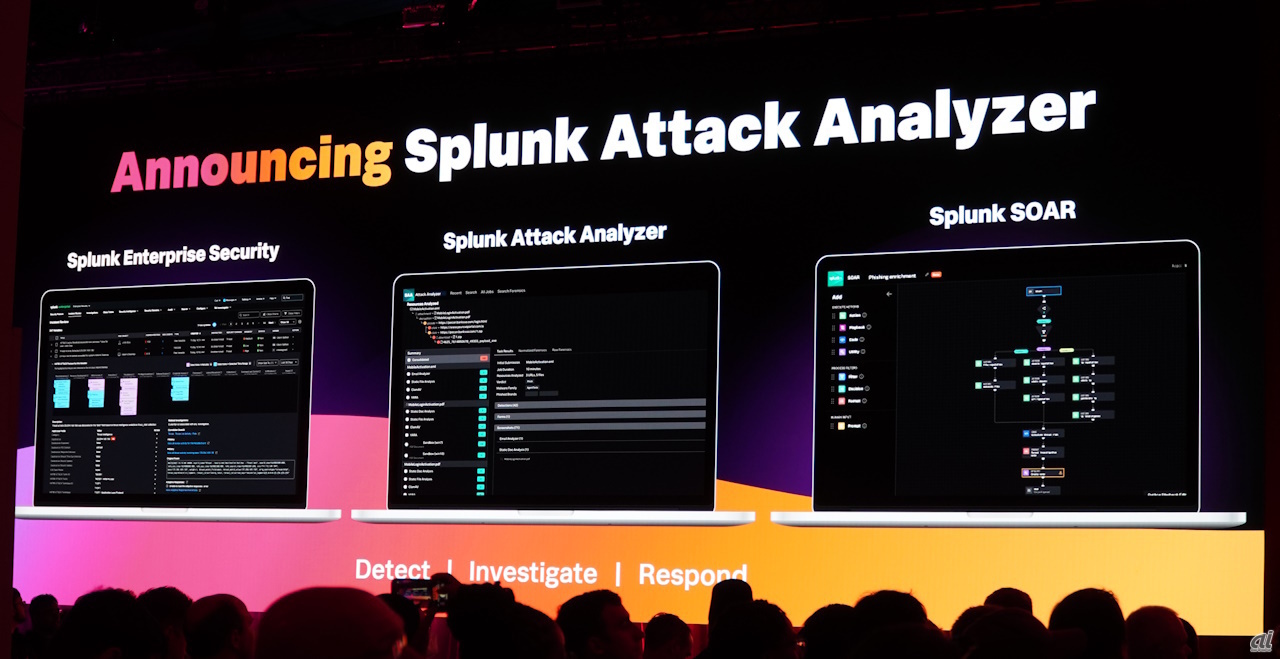
Introducing Attack Range v3.0 | Splunk
Splunk Tutorial- A Complete Guide For Beginners [Updated 2025]
Splunkの新機能でコストを抑えながらクラウド監視を拡張 | Splunk
TryHackMe | Splunk: Basics – Igor_sec's Blog
The Critical Role of Log Management in SaaS Environments
GitHub - CyberJessy/Splunk-SIEM-Lab
Types of Work Clogs: Exploring Materials, Features, and Benefits for ...
The Men's Clog in Soft Black | Rothy's
Mastering Time in Splunk: A Guide to Searching, Formatting, and Time ...
9 Running Safety Tips For Women, By Women - Believe in the Run
Crocs Echo Gum RO Clog Black Men's - 211675-001 - US
Splunk、生成AIアプリ「Splunk AI Assistant」など新機能を一挙発表 - ZDNET Japan
Clog
NBA x Crocs All-Star Weekend Collaboration | Hypebeast
The Return of Clogs: A Story of Comfort and Style - BC Living