Showing 120 of 120on this page. Filters & sort apply to loaded results; URL updates for sharing.120 of 120 on this page
Splunk Table / Field Command - YouTube
Splunk SPL Table Command Tutorial - Format Results Like a Pro ...
Splunk Table Command _ Splunk table command- Generation and data ...
Splunk Table Command | Splunk Enterprise | Splunk Cloud - YouTube
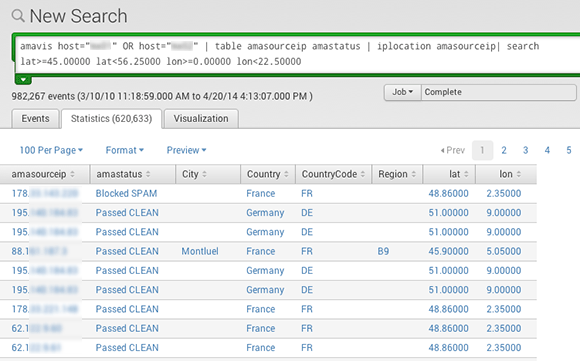
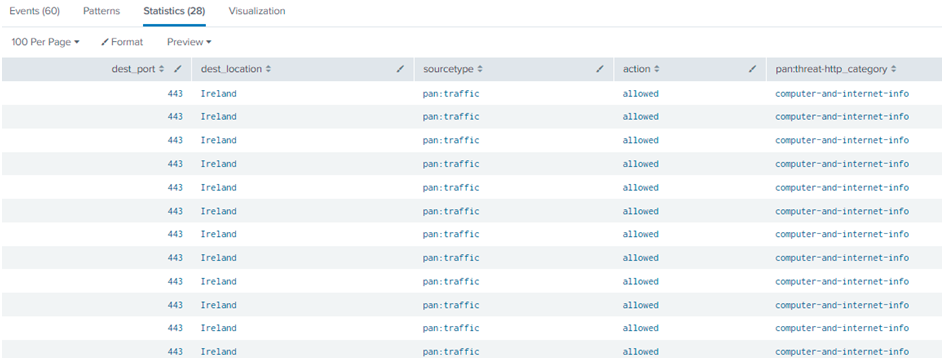
Splunk table command- Generation and data visualization
My custom command to get file size of CSV lookup table is now available ...
While using table command, Splunk converts some "IIS logs" into HTML ...
Unable to send an email alert when the table command is included in the ...
Using the table Command - Kinney Group
Using the table command in #Splunk - YouTube
Table - Splunk Documentation
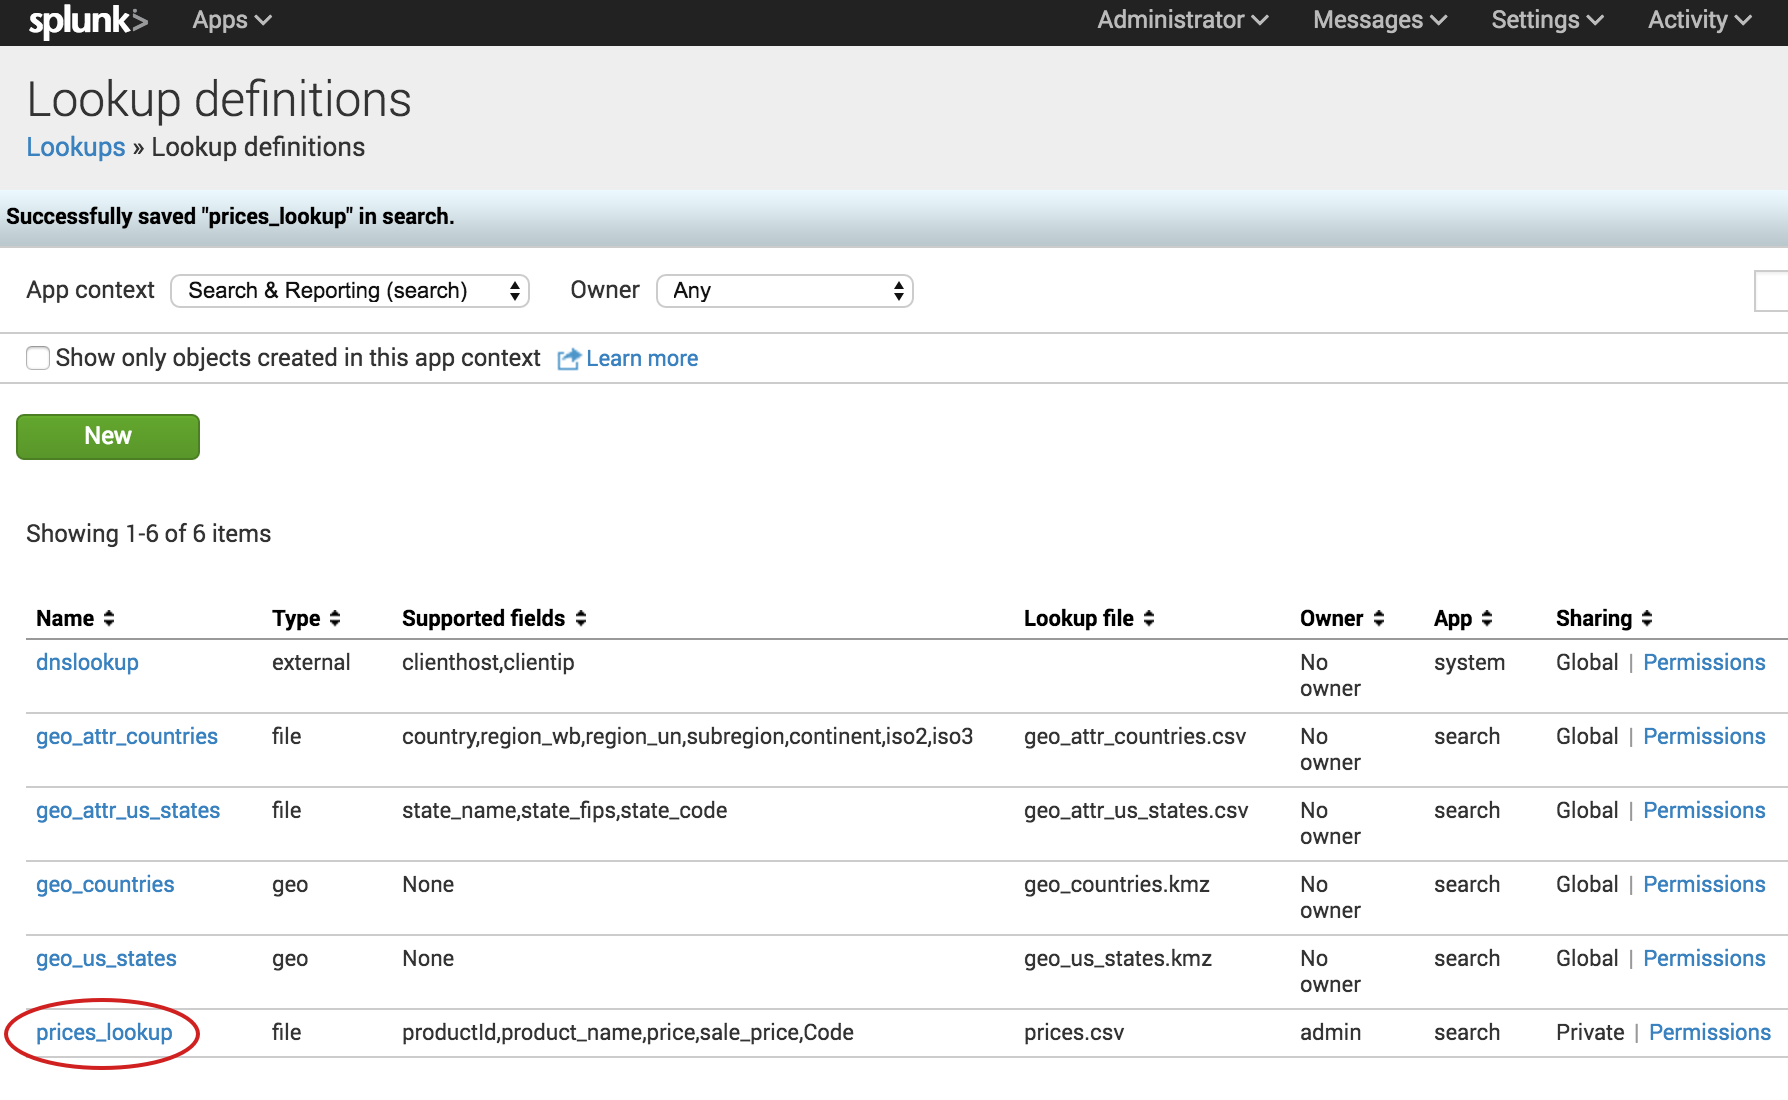
How to use a lookup table in a splunk query? – lookup table matching – PBFF
Unlock the Power of Table Command in Splunk! | SPL Tutorial for Data ...
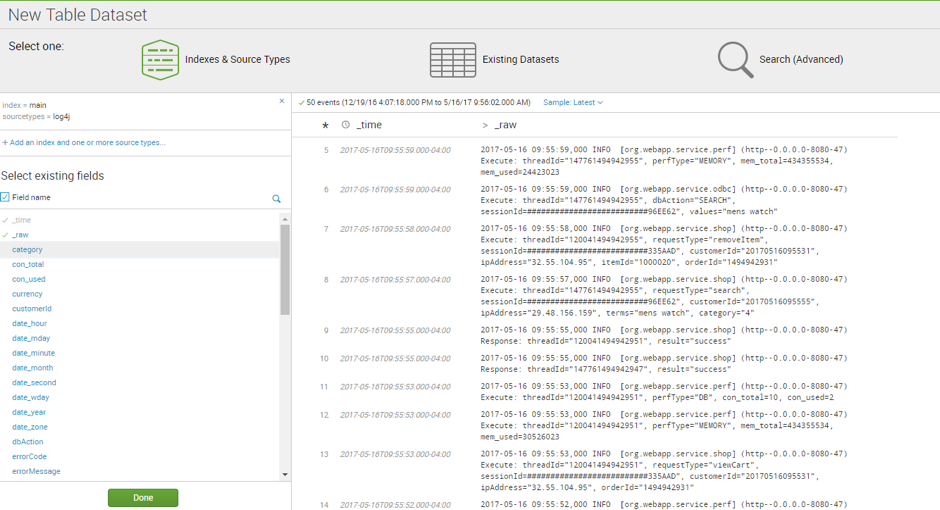
Diving into Splunk Table Datasets - Discovered Intelligence
Splunk Map Maxsearches : How to use subsearch inside a map command ...
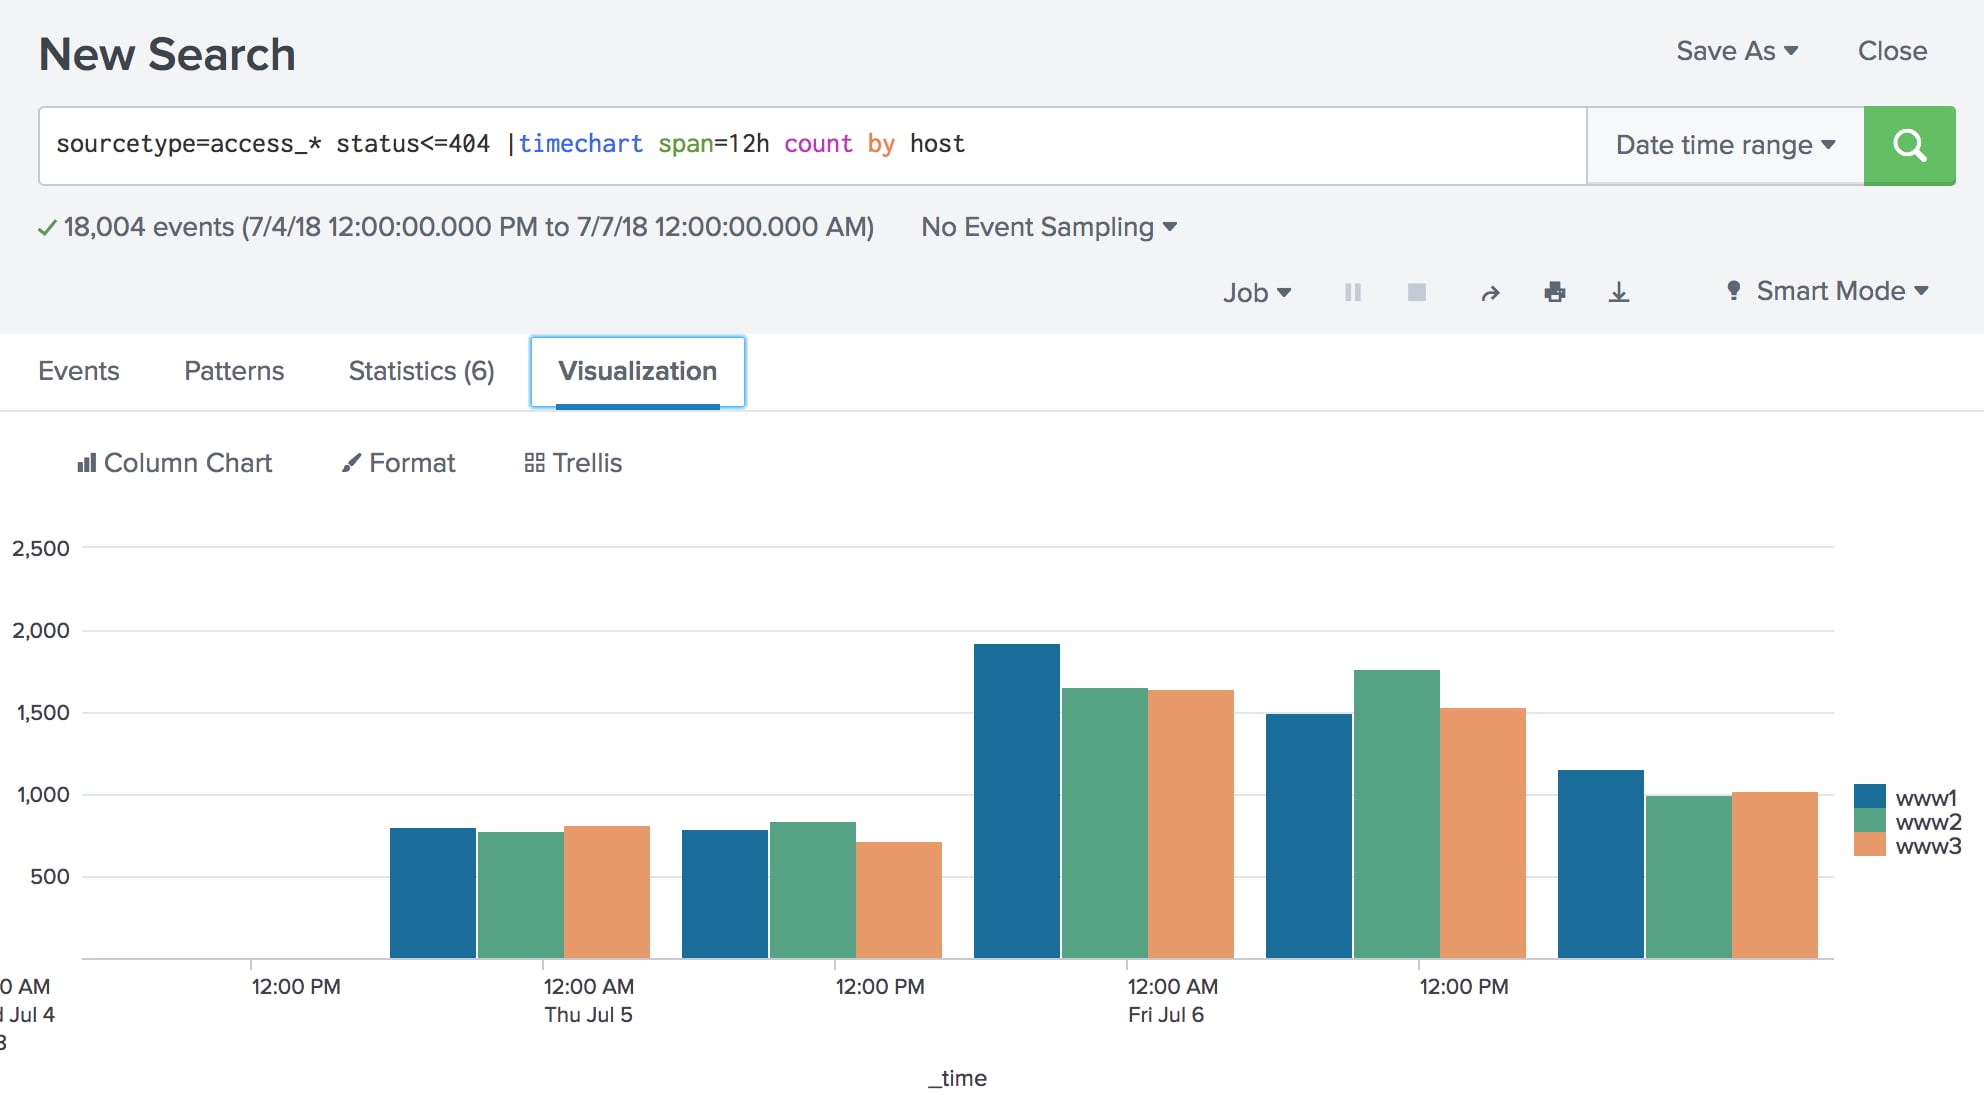
Splunk Chart Command Tutorial: Create Bar Charts, Line Graphs & Pivot ...
The Gauge Command Splunk at Charles Casale blog
Splunk Chart Command Options | Splunk Chart Examples – AWCV
The table command in #Splunk - YouTube
Splunk Add Columns To Table at Cristina Lee blog
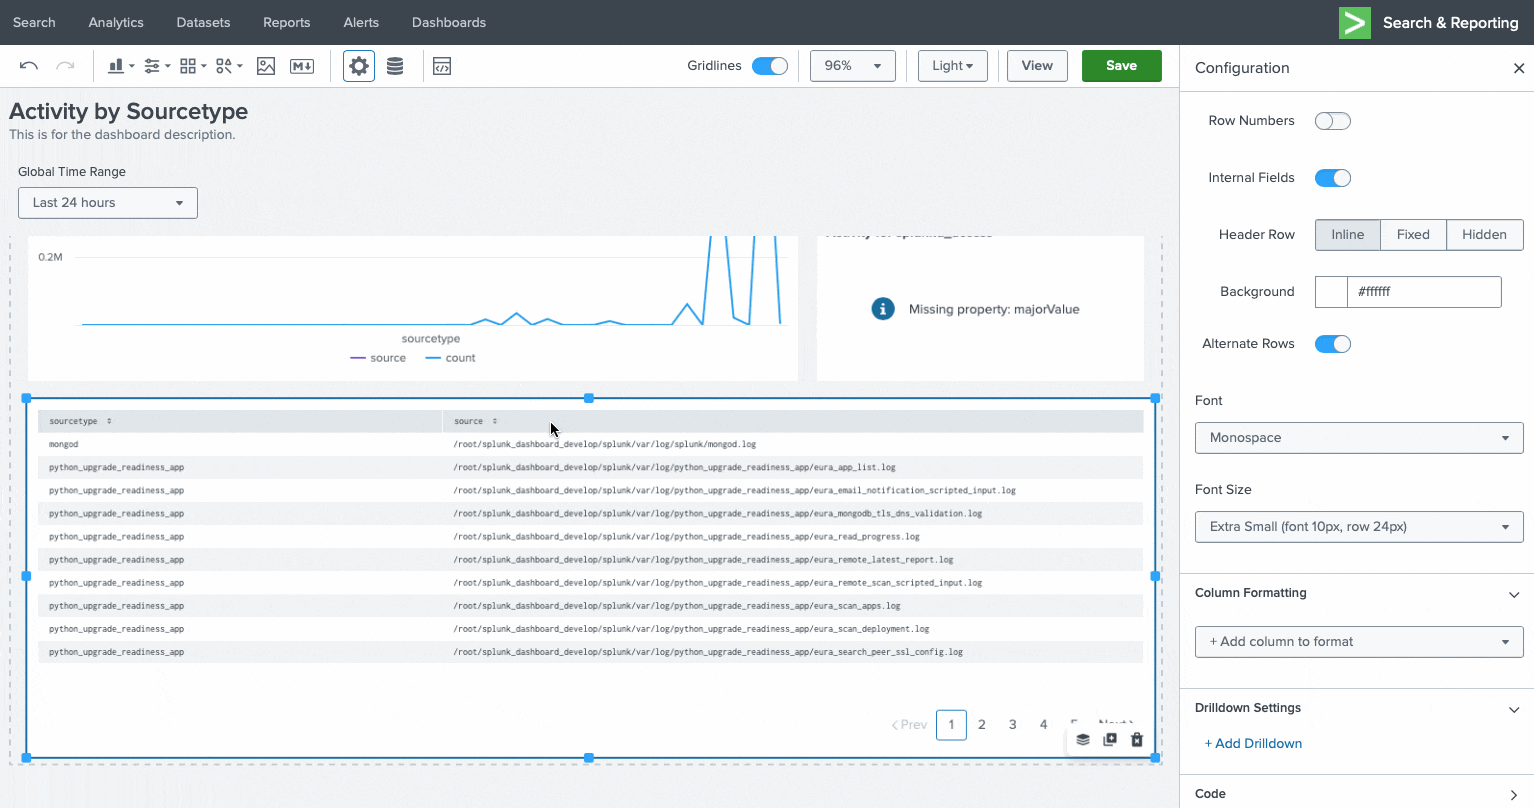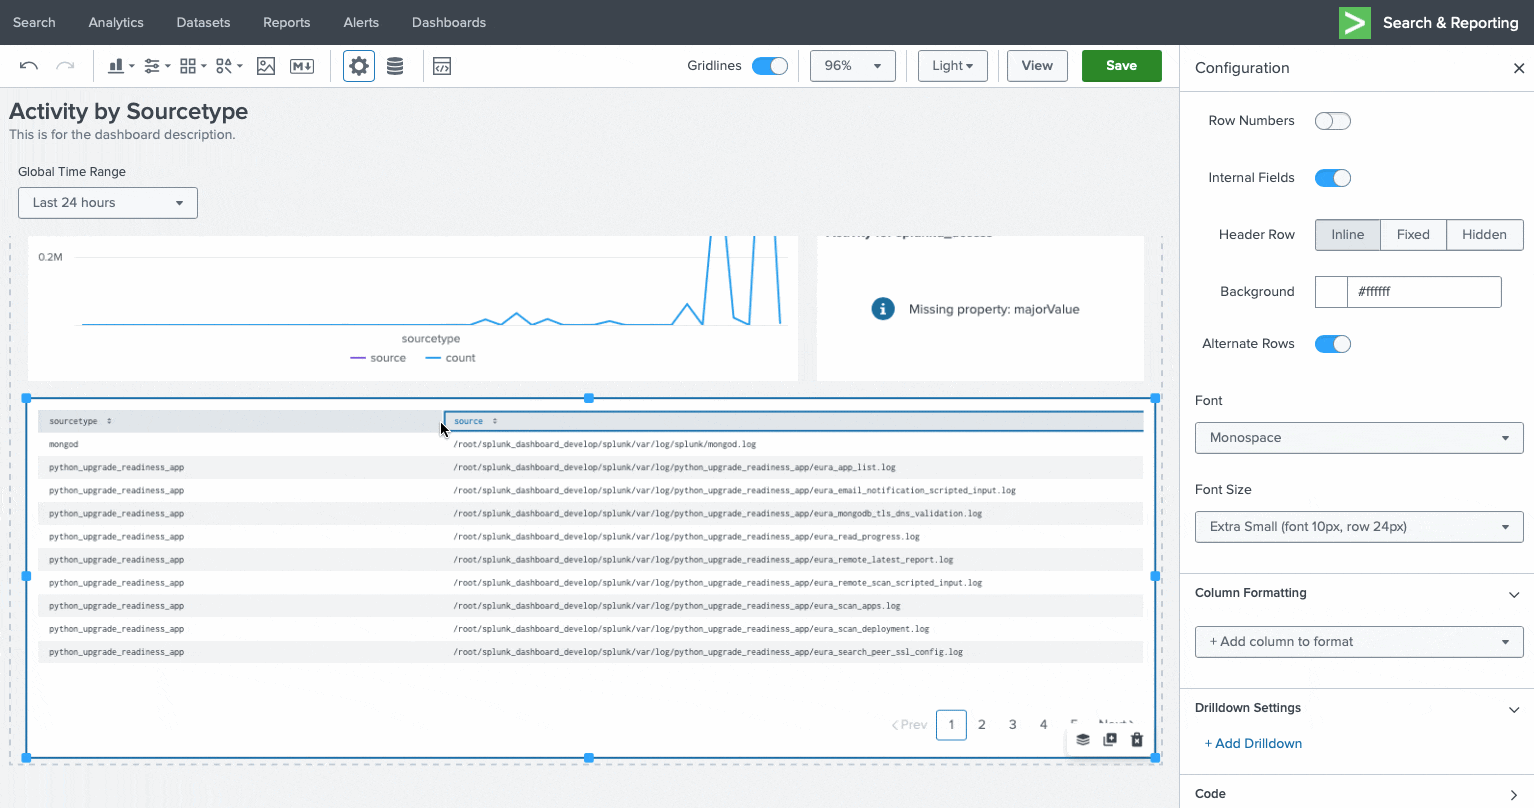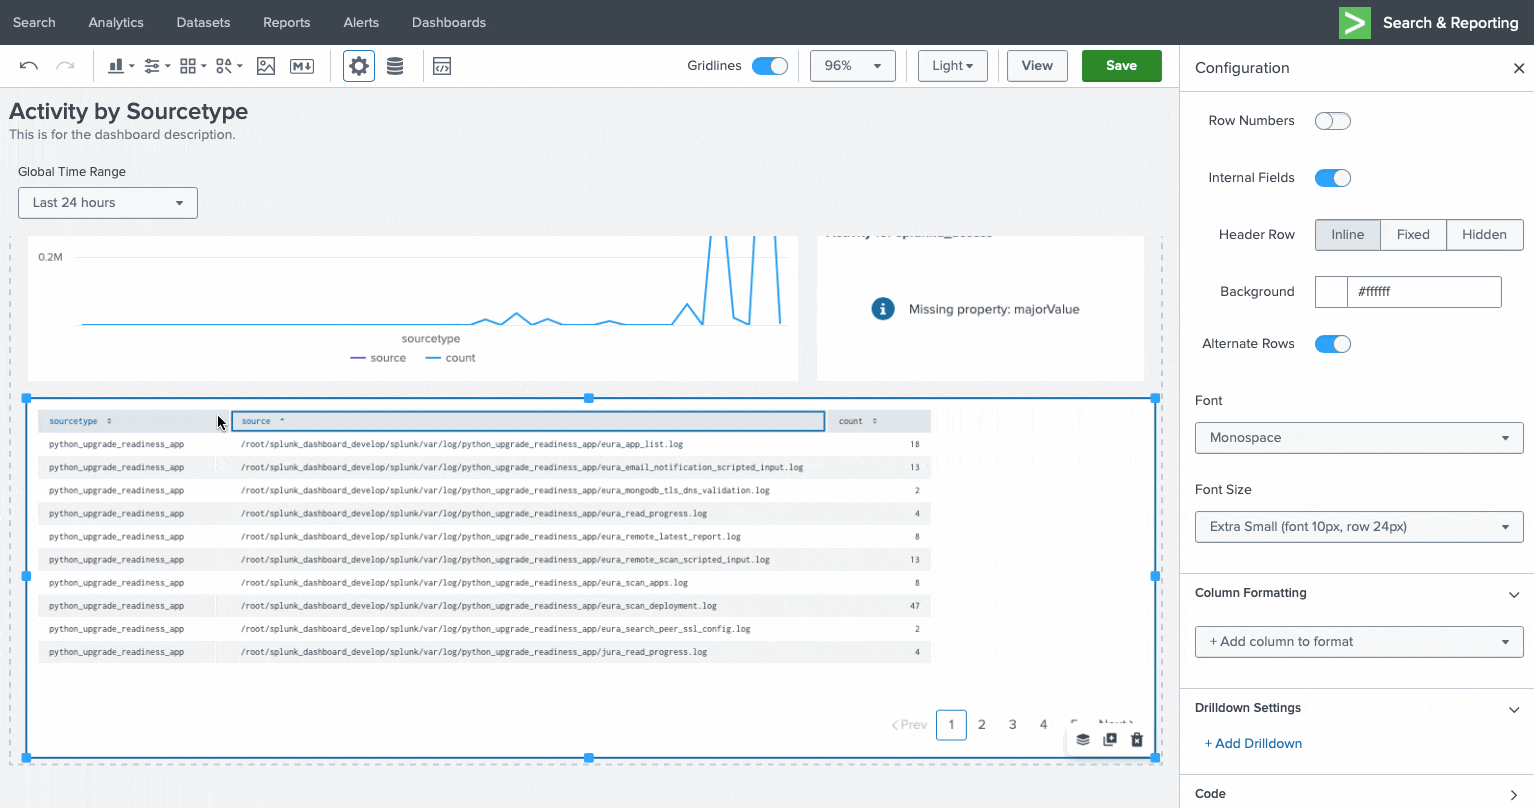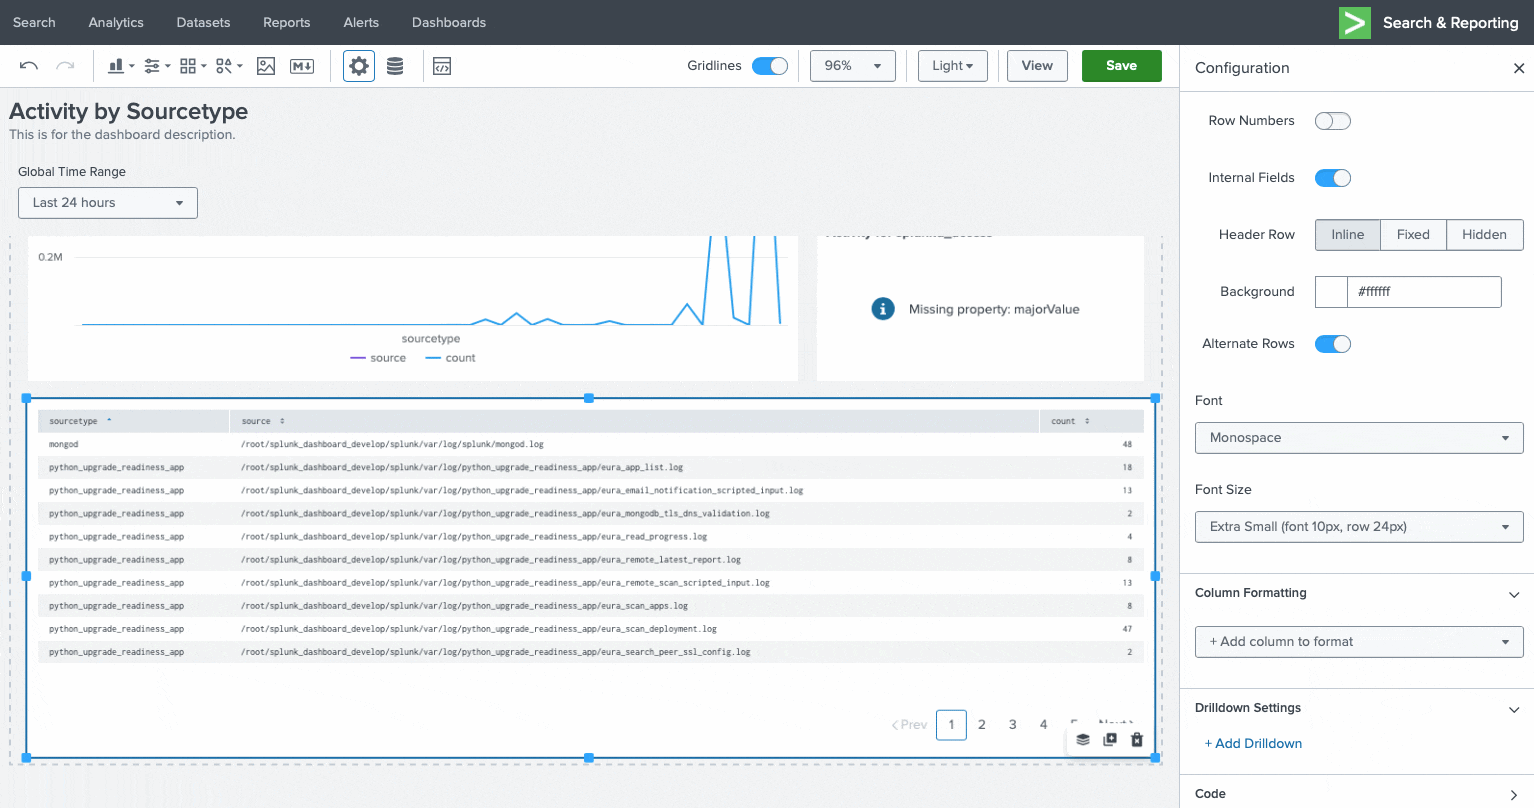
How to create a Table Dashboard on Splunk - YouTube
Splunk CLI Useful Commands Cheatsheet | PDF | Command Line Interface ...
Solved: How to make a Splunk table visualization more inte... - Splunk ...
Splunk Command Cheat Sheet: Splunk Spl Cheat Sheet – WPNQOJ
How to perform chart command with two multifield c... - Splunk Community
Splunk Check Size Of Lookup Table at Joanne Bender blog
How to make table structure in link format? - Splunk Community
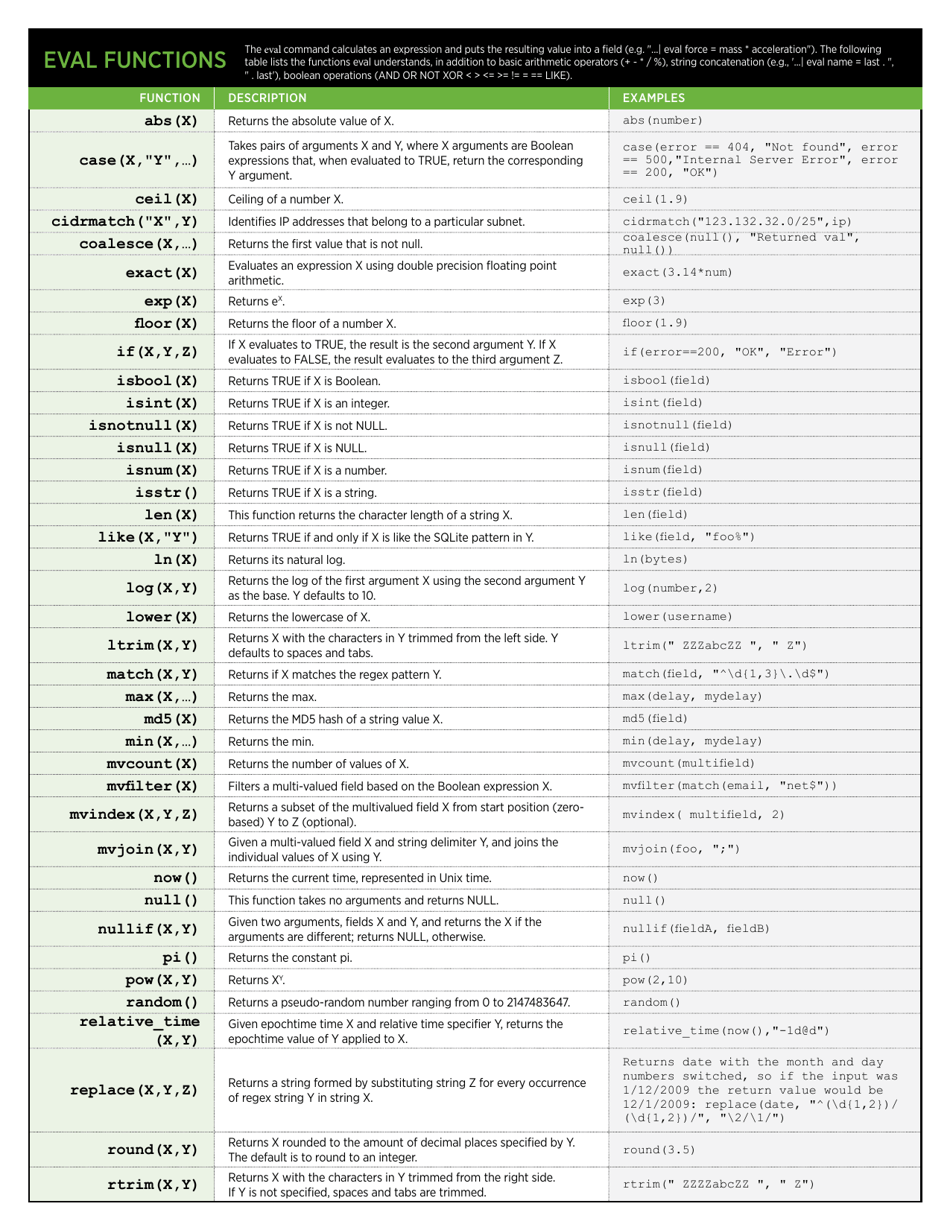
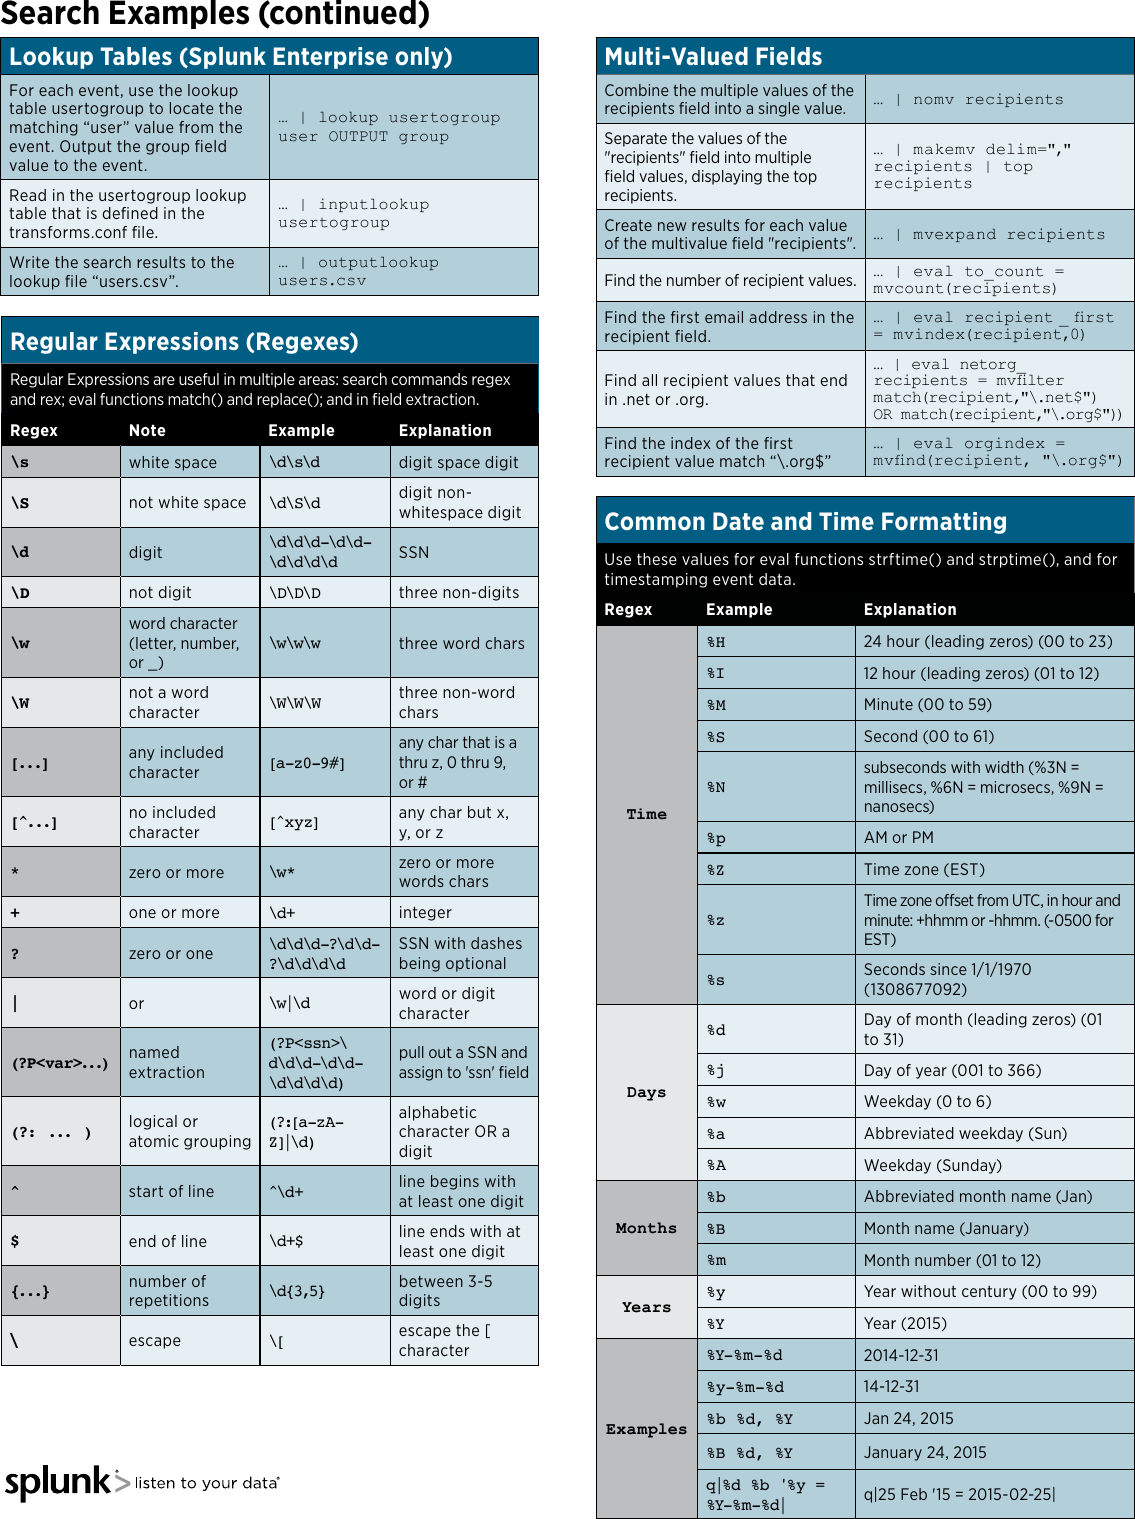
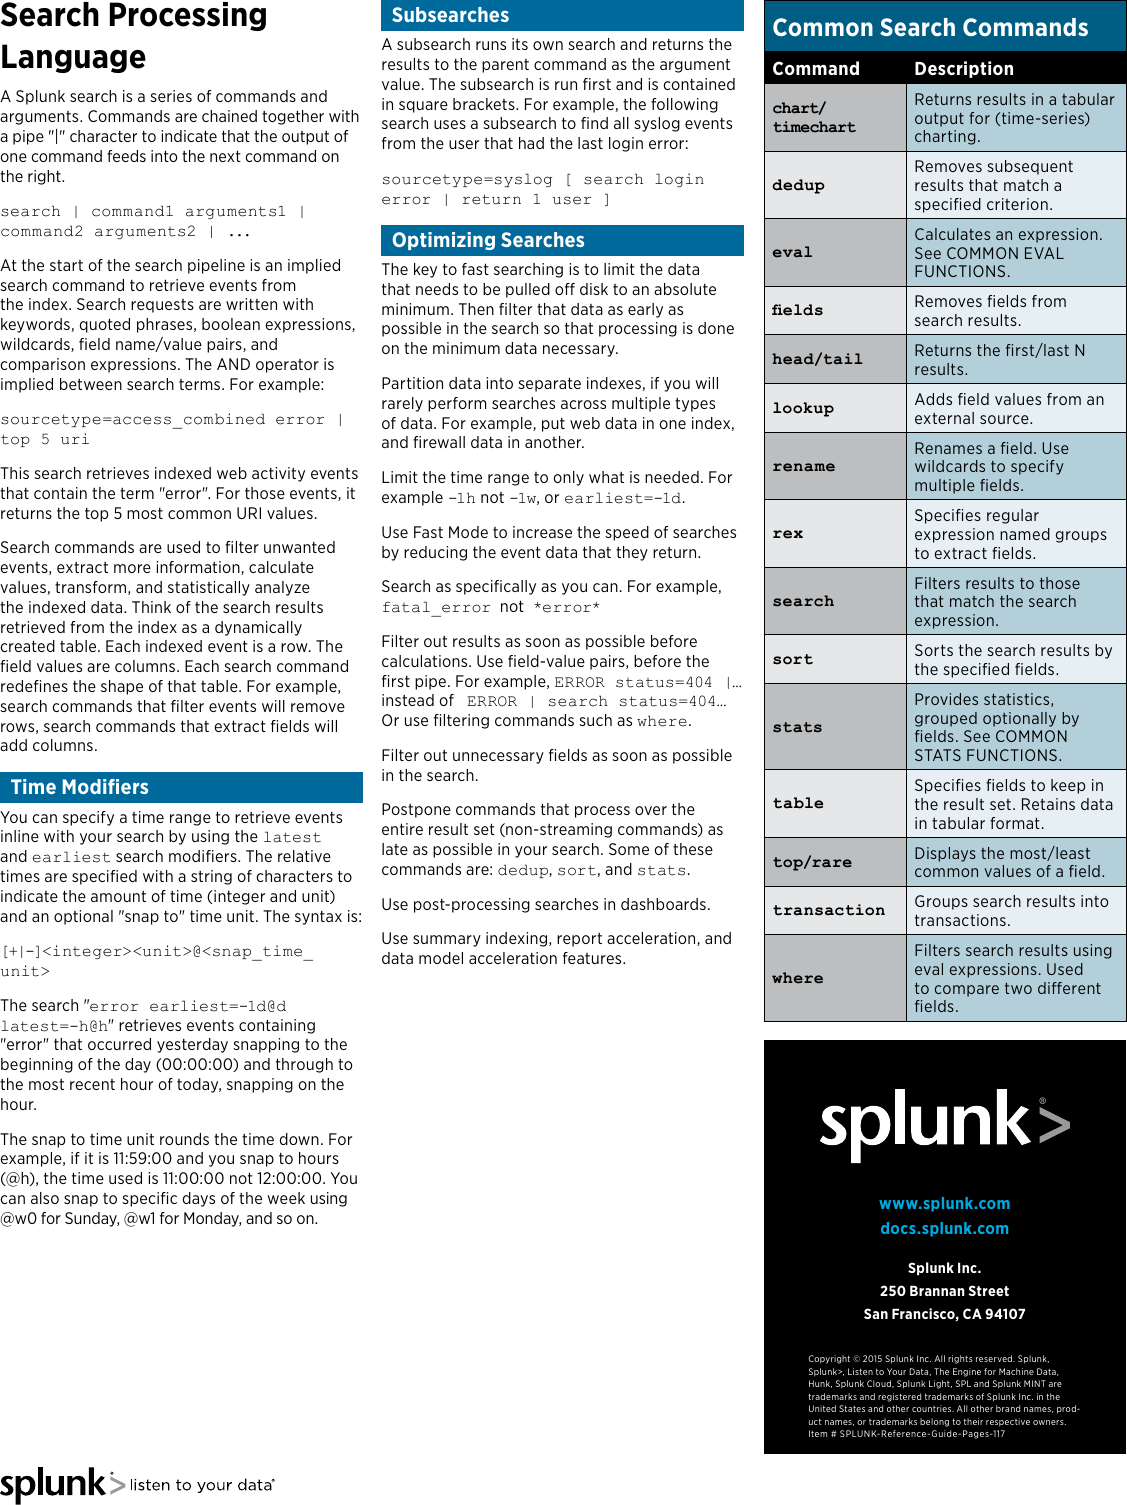
Splunk cheat sheet - Search command cheatsheet Miscellaneous The ...
Solved: Adding or removing the append command changes a pr... - Splunk ...
How to create a table row expansion? - Splunk Community
Splunk query to create a table view? - Stack Overflow
Mapping table and columns in Splunk sync
Splunk Dashboard Studio Table Input | Tech Tonic with Kiran - YouTube
Splunk | Command | Verkada Help
Solved: How to achieve this table representation in Splunk... - Splunk ...
Splunk Command Tricks for Effective Log Analysis | by Maximin | Medium
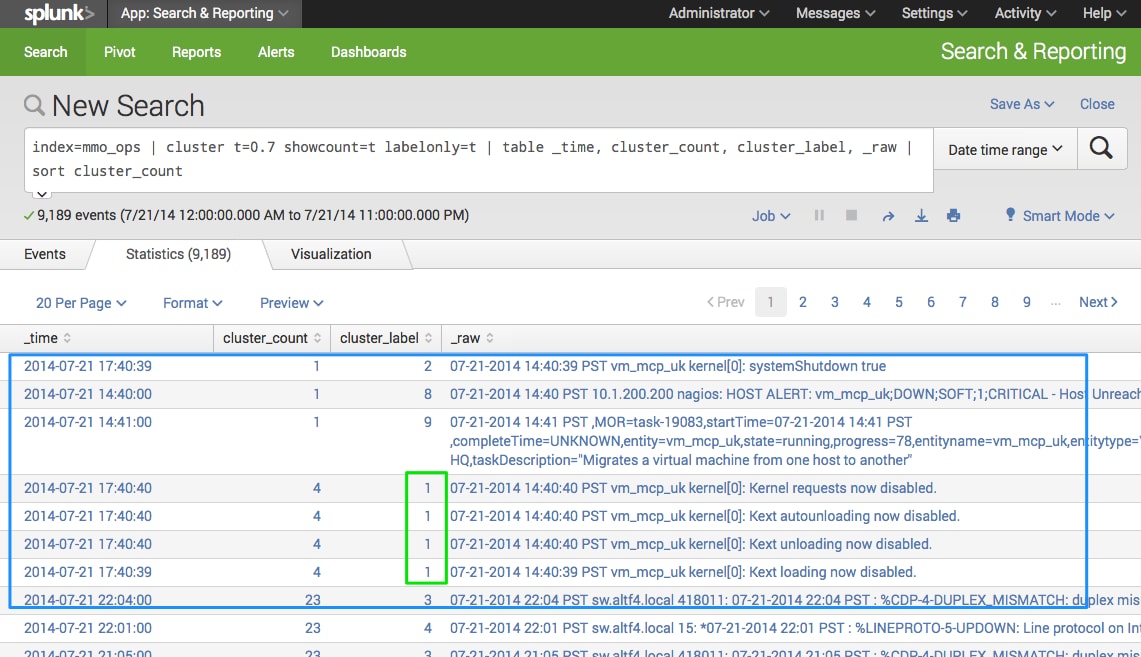
Splunk Command> Cluster | Splunk
SPL: Search Processing Language - Splunk Tutorial | Intellipaat.com
How To Combine Two Tables Splunk at Jacob Mauldin blog
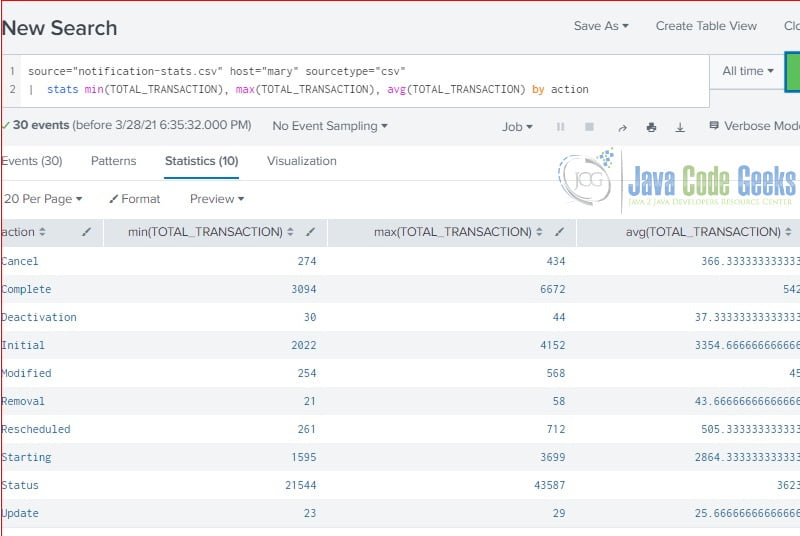
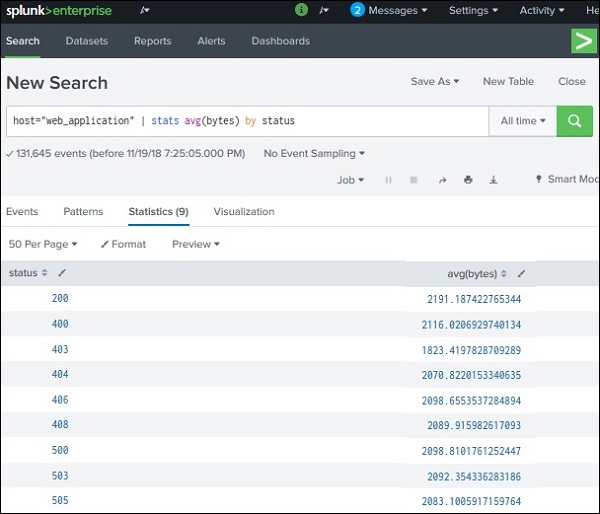
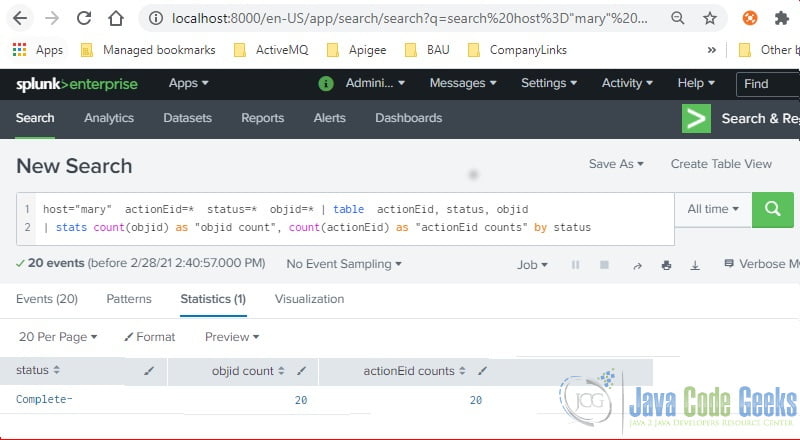
Splunk Basic Charts Example - Java Code Geeks
Log aggregation and analysis: splunk | Cognitive Overhead
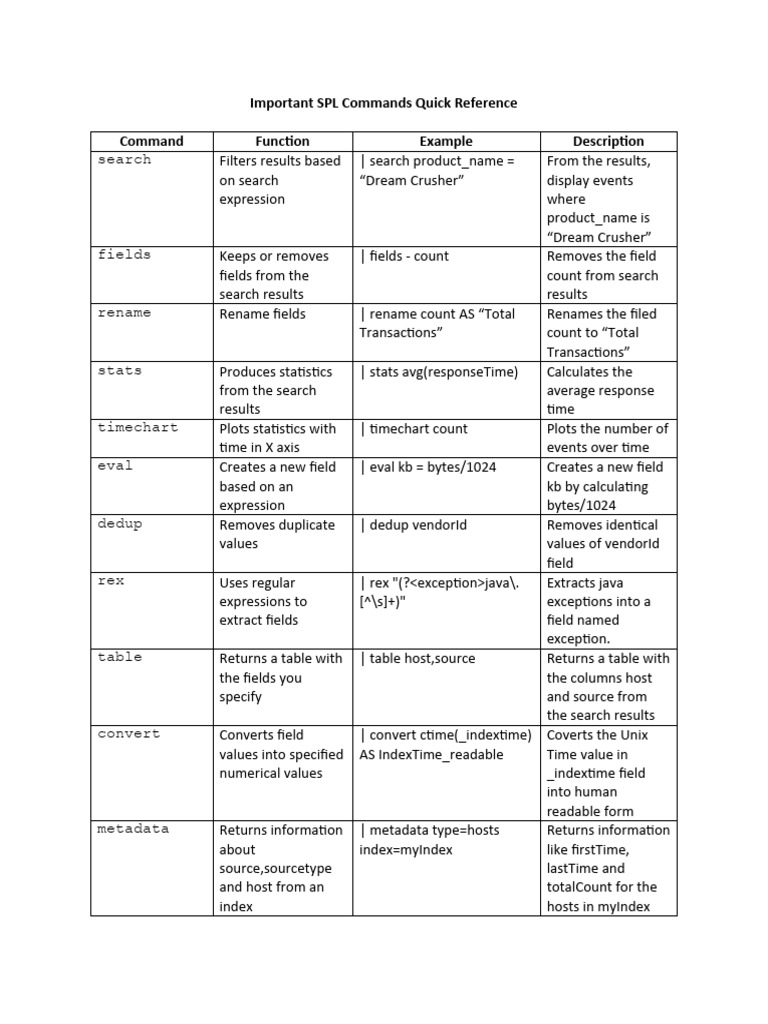
Splunk SPL Commands Quick Reference | PDF
Splunk Commands – Exploring of Join Commands and its Arguments ...
Splunk Search Escape Quotes
Splunk Quick Cheat Sheet Download Printable PDF | Templateroller
Splunk Dashboards Quick Reference Guide at Chelsea Sommerlad blog
Splunk: Using collect Command for Creating New Events in a New Index ...
How to use Splunk SPL commands to write better queries - Part I
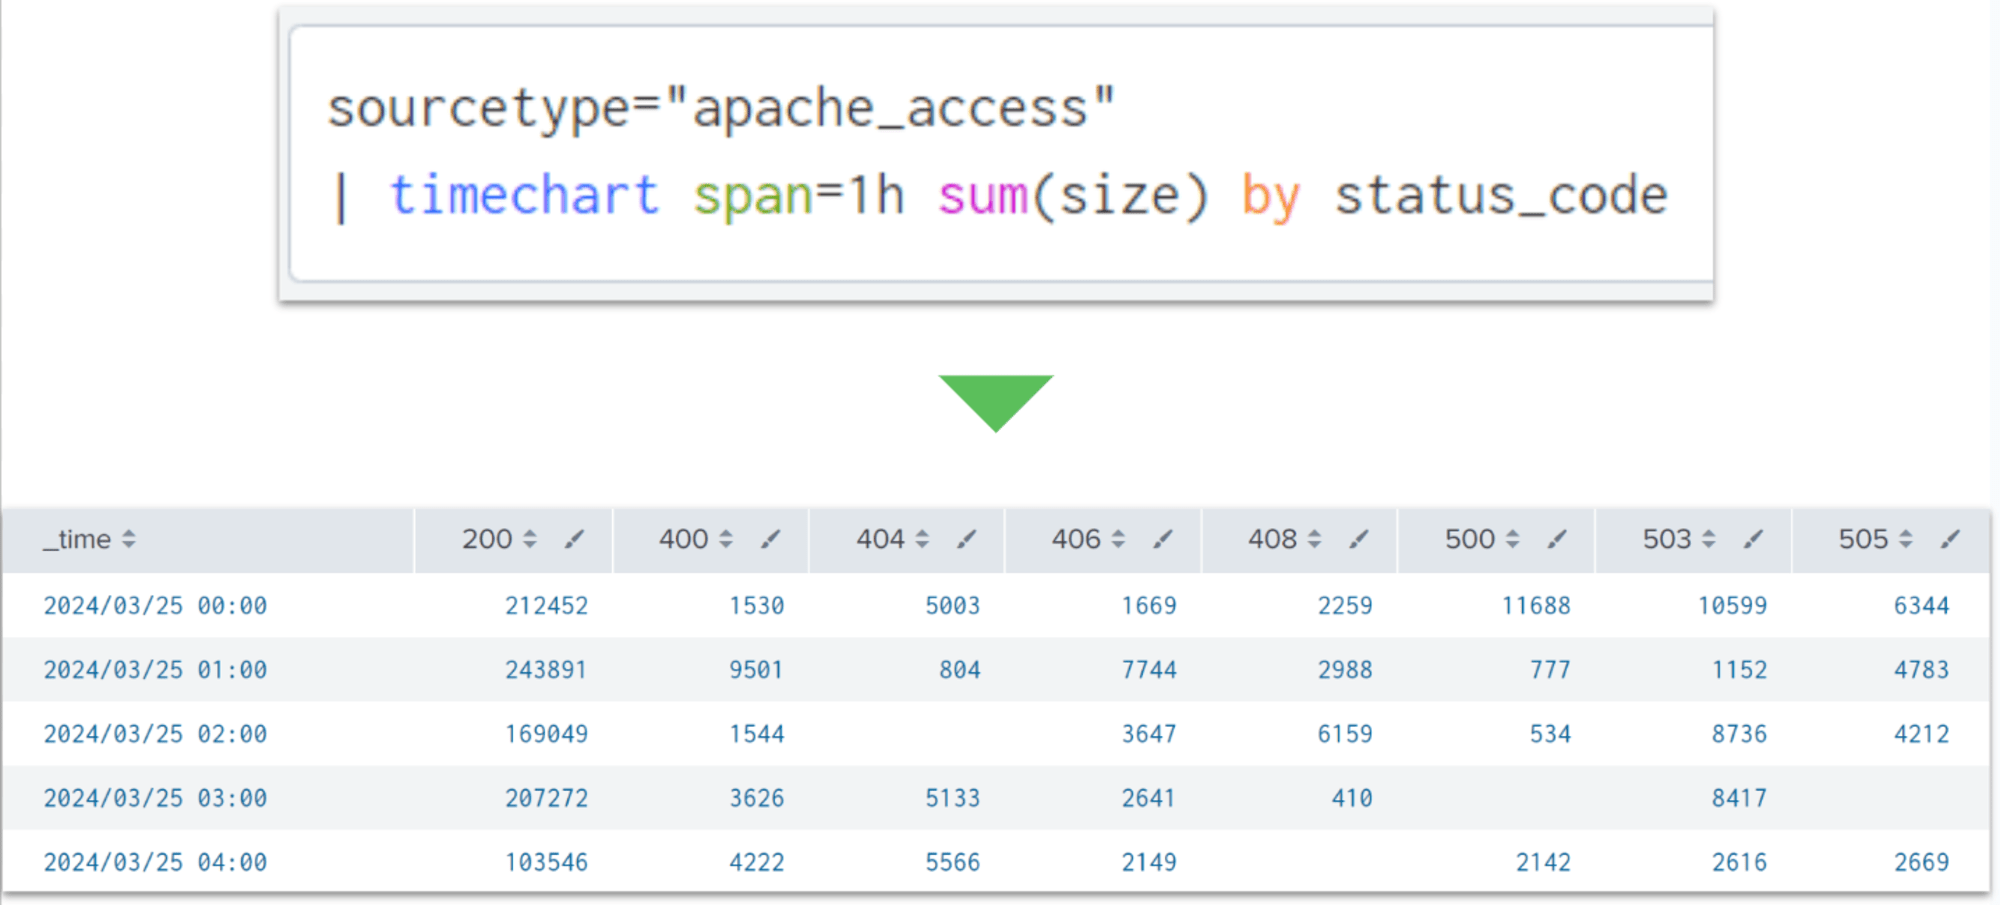
Search commands > stats, chart, and timechart | Splunk
Splunk For Dummies Pdf _ Splunk Tutorial Pdf – GDYDW
Splunkサーチコマンド > stats、chart、timechart | Splunk
Splunk Dashboards Quick Reference Guide – QTCBPC
Splunk Cheat Sheet: Search and Query Commands
Splunk Fields Explained at Barbara Fowler blog
Step-by-Step Guide:Splunk Essential Commands: Table , Rename, Fields ...
Créez des tables et graphes avec Splunk
Commandes de recherche > stats, chart et timechart | Splunk
Splunk Basic Commands With Examples at Aiden Darcy blog
15. Introduction To Splunk & SPL | Exploit. Learn. Secure.
Splunk Cluster Pushing _ Deploy a heavy forwarder – LYIFAM
How to Create Multiple Tables in One Dashboard? - Splunk Community
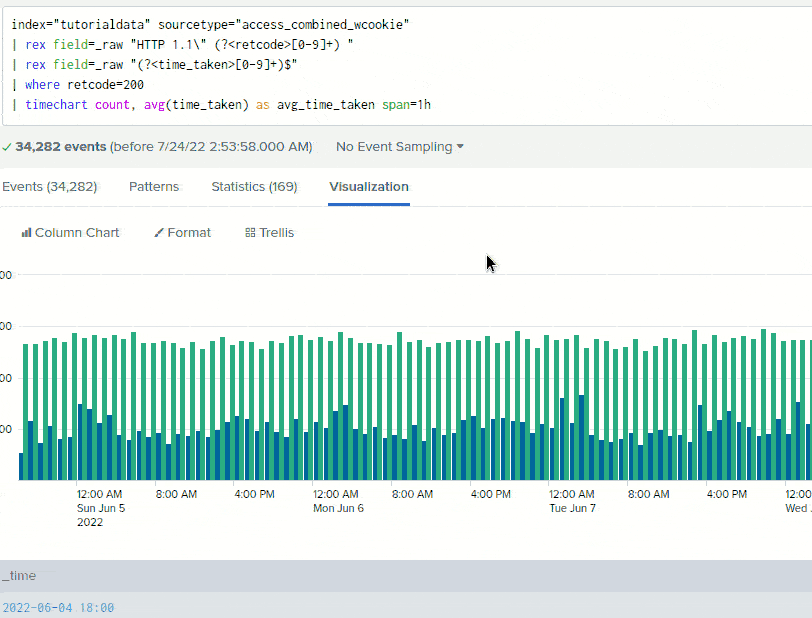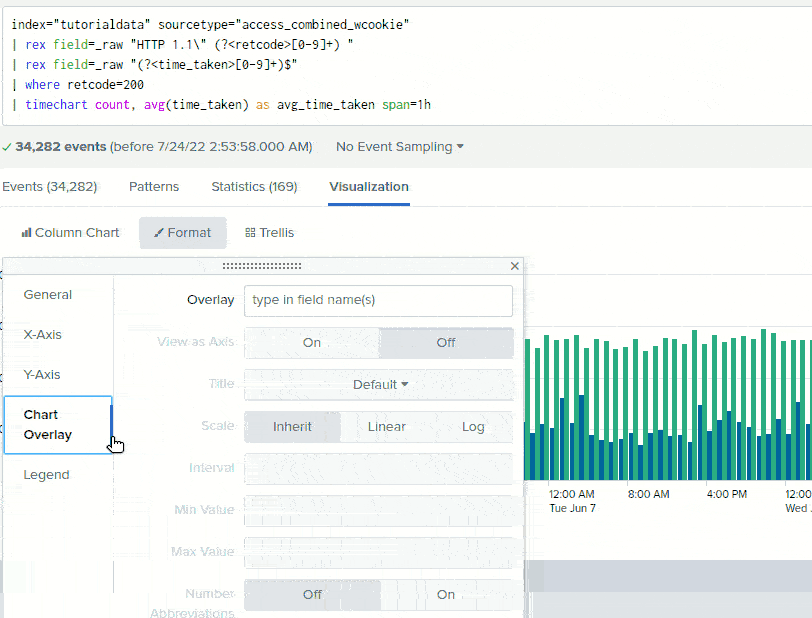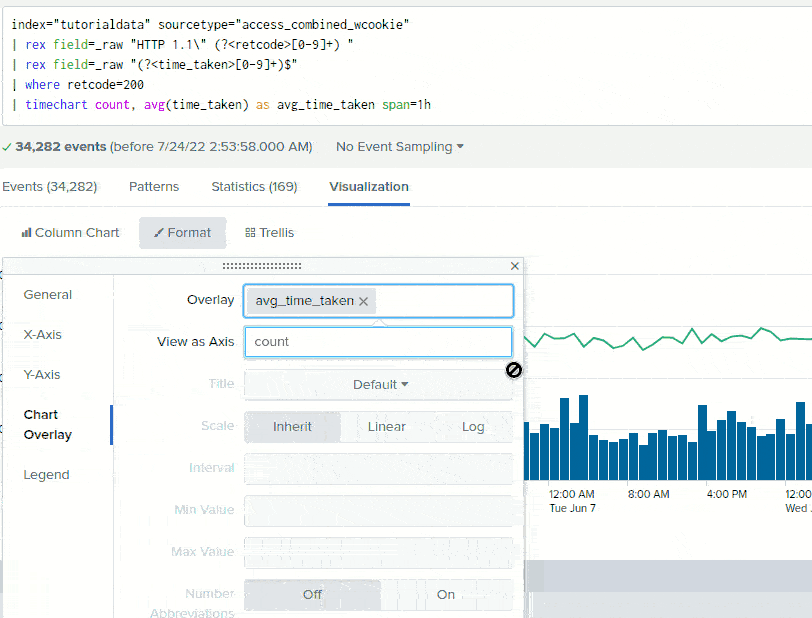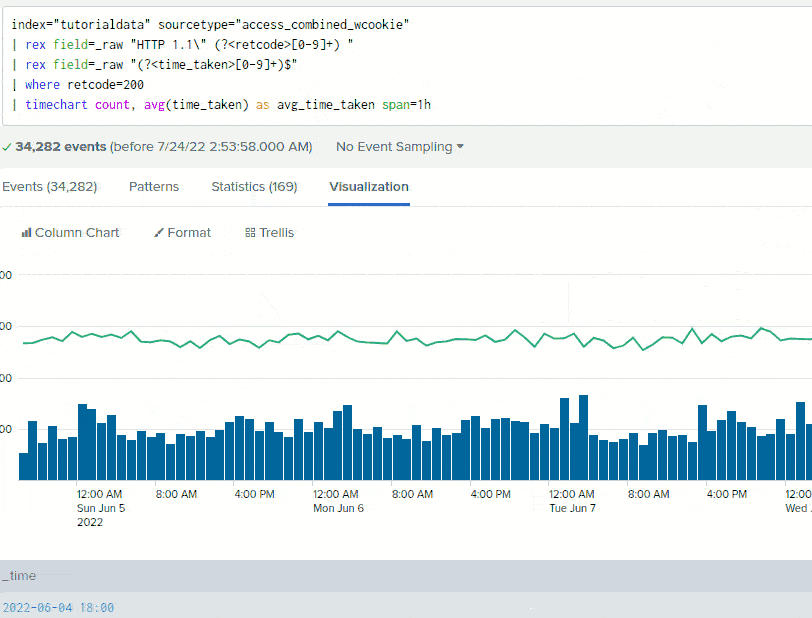
Regex v. Rex Commands in Splunk SPL | TekStream Solutions
Splunk Gauge Visualization at Lisa Black blog
How to monitor the health and status of Splunk services using REST API ...
Splunk Collect Command: Using It For Summary Indexing - Kinney Group
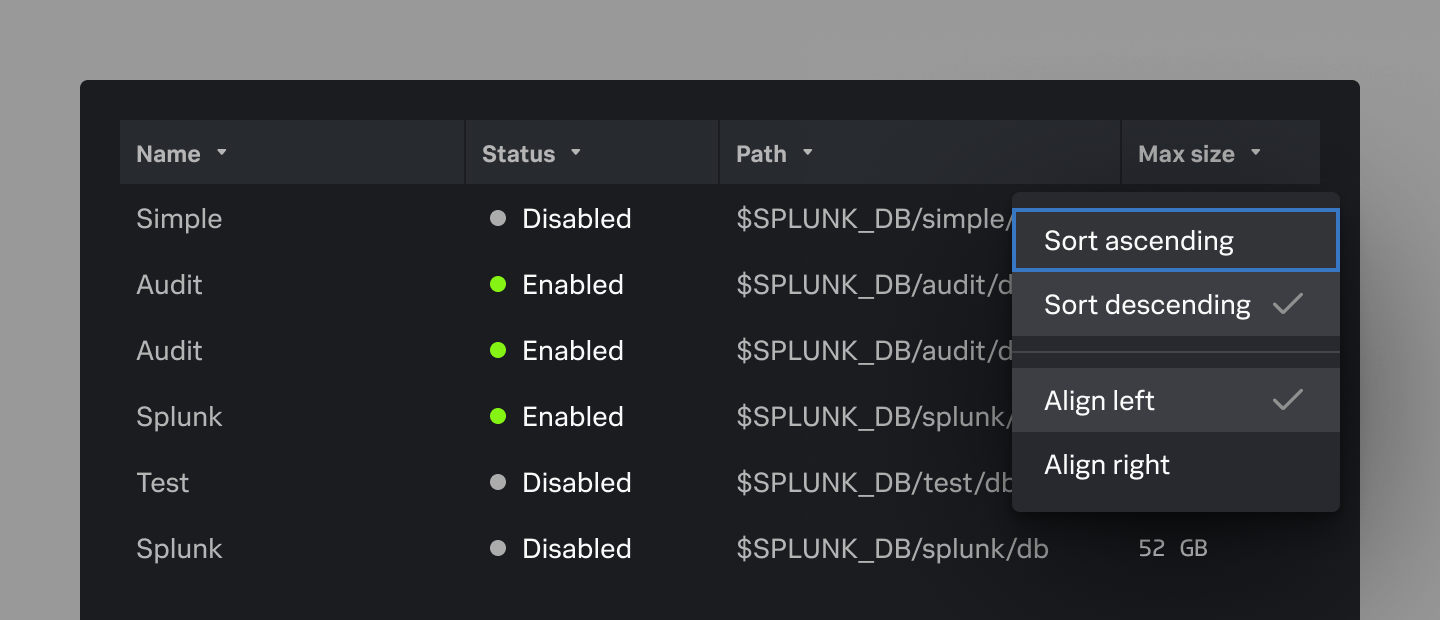
Table displays rows of data with columns labeled 'Name,' 'Status ...
Solved: How to set table/panel height via whatever means p... - Splunk ...
Glass Tables In Splunk at Daniel Gilmore blog
Use the search language - Splunk Documentation
Splunk Commands - Search Commands Tutorial
Splunk Query Cheat Sheet _ Splunk Cheat Sheet – DNMIO
How to correlate different events in Splunk and make dashboards ...
A Beginner’s Guide to Regular Expressions in Splunk – Kinney Group
Putting your machine data to use with Splunk
Dashboard Studio: It's the Little Things | Splunk
Splunk Commands for Data Analysis and Visualization
Splunk In Values at Albert Jarman blog
Splunk Session#14.1:SPLK-1001:Transforming Commands,stats Command,its ...
Splunk Commands - SPL Explanation - Part-1 | PDF
Improving the threat intelligence process in Splunk with RST Cloud
Mastering Splunk Eval Commands: A Complete Guide to Comparing ...
Splunk Certified User Session 13:Search Language,Syntax&components ...
Splunk - Displaying addcoltotals into its own column - Stack Overflow
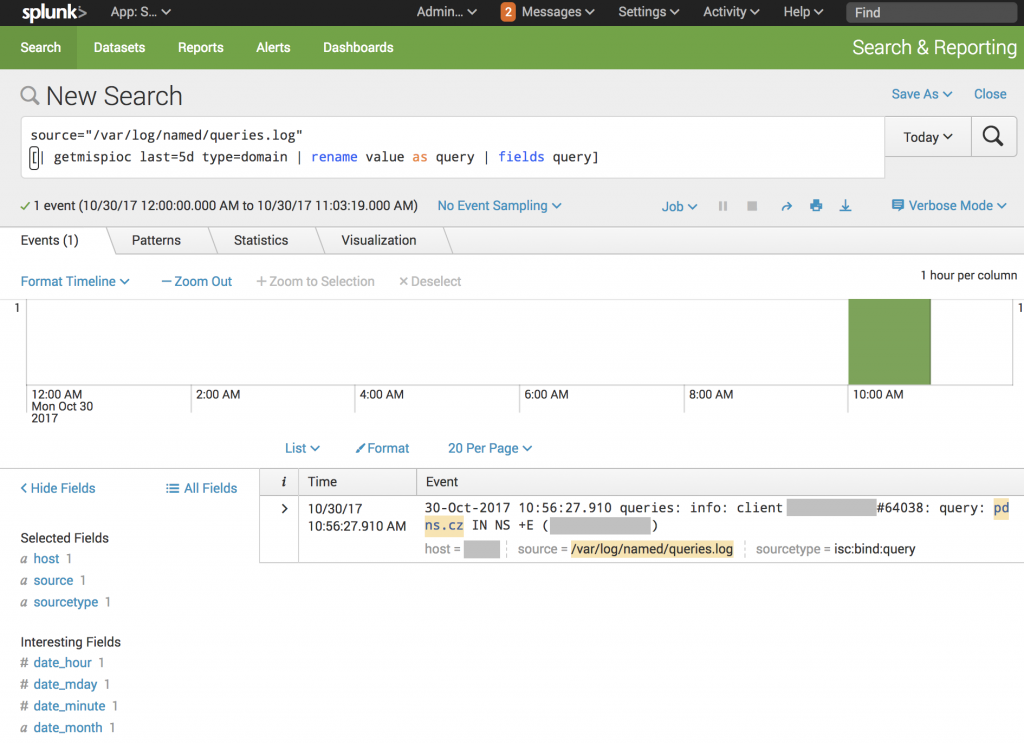
Splunk Custom Search Command: Searching for MISP IOC's - /dev/random
Splunk Basic Search Commands | for Beginners | By Mohit Damke | by ...
Business Analytics using Splunk and Database
SPL Syntax: Basic Searching Concepts
支援更多機器學習應用,Splunk提供可自定的分析環境 | iThome
Splunkのtimechartコマンドでデータのトレンドを分析・可視化するための基本的な使い方 | DevelopersIO
dashboard-simple-table-component/tutorial.md at main · splunk/dashboard ...