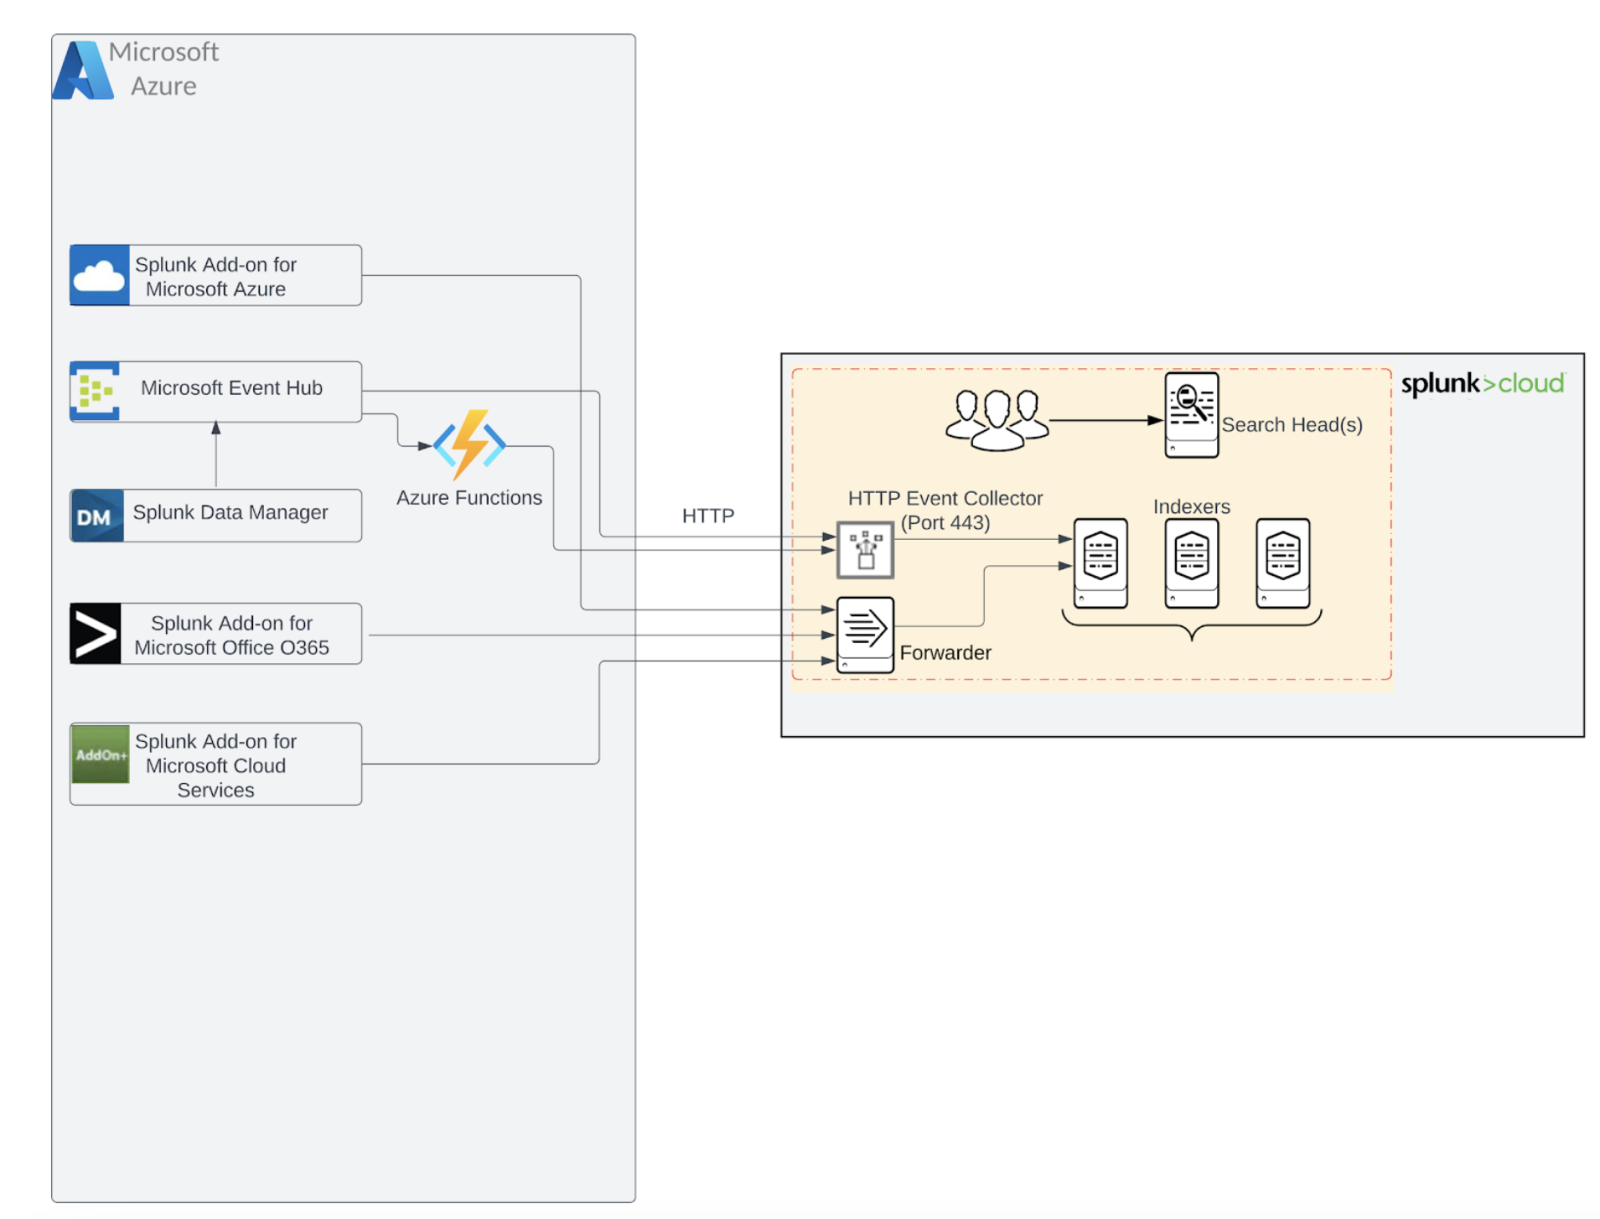
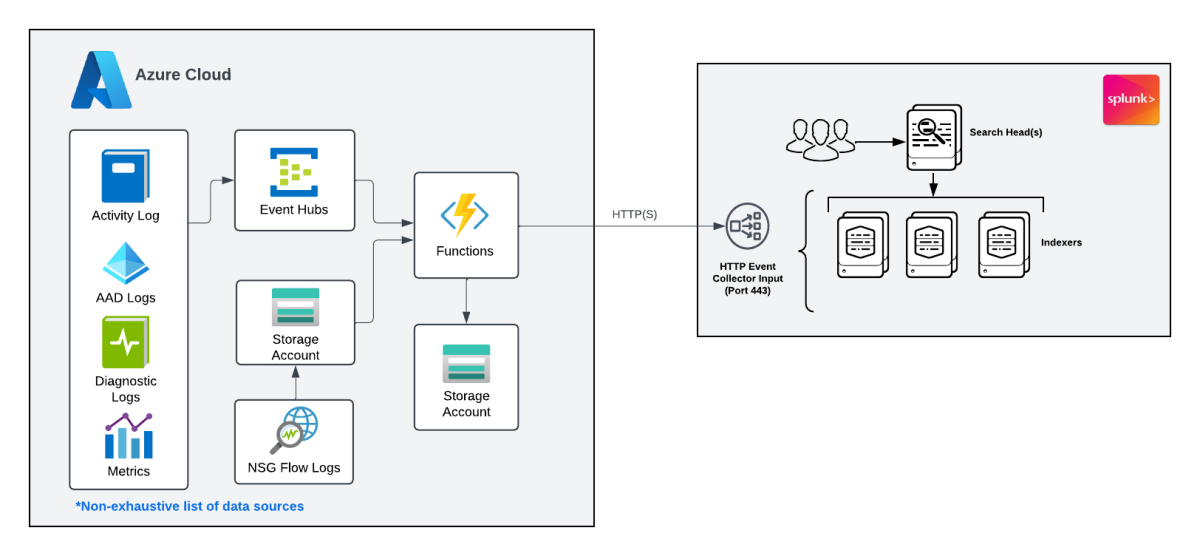
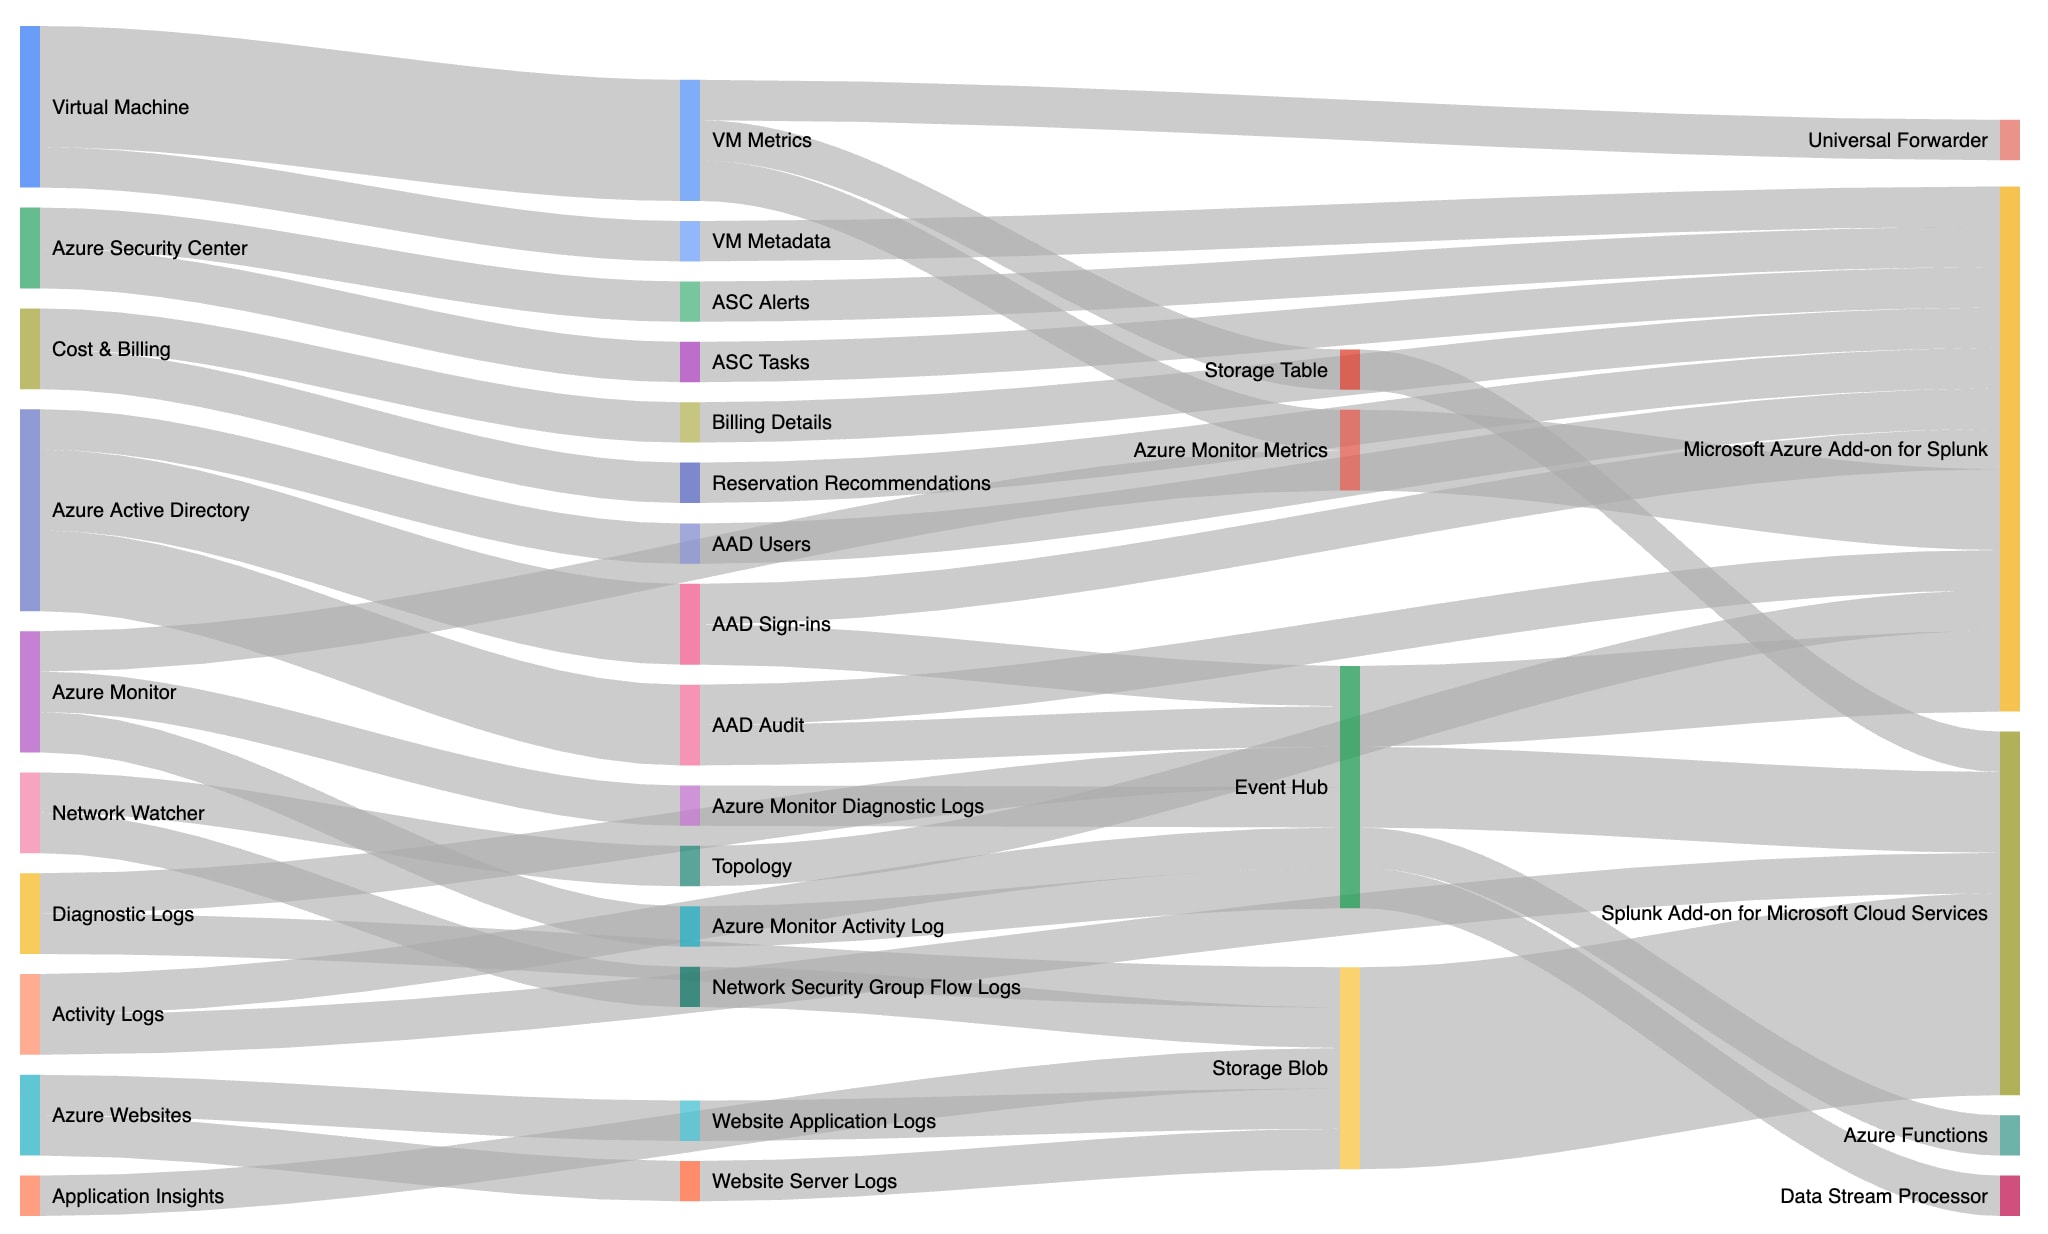
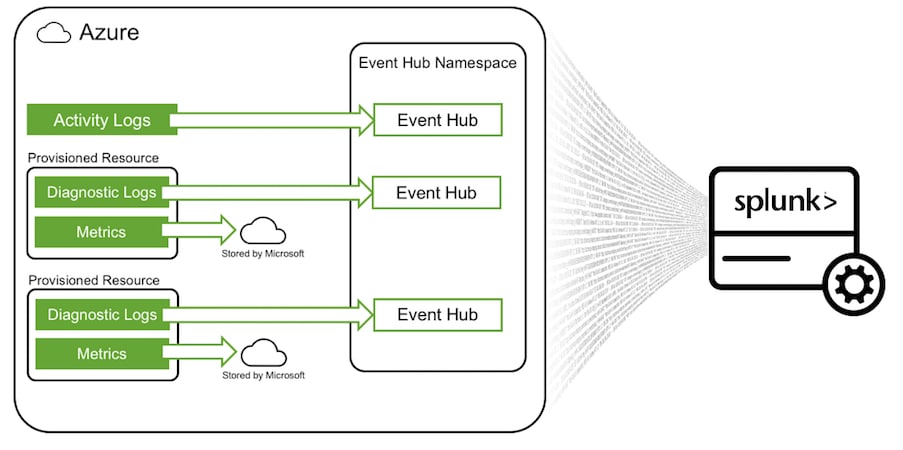
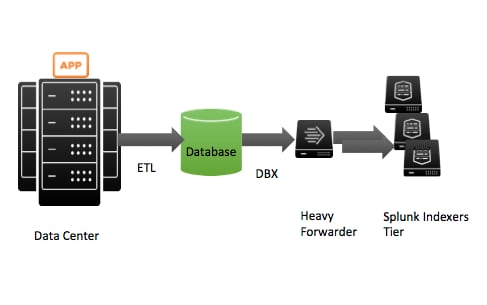
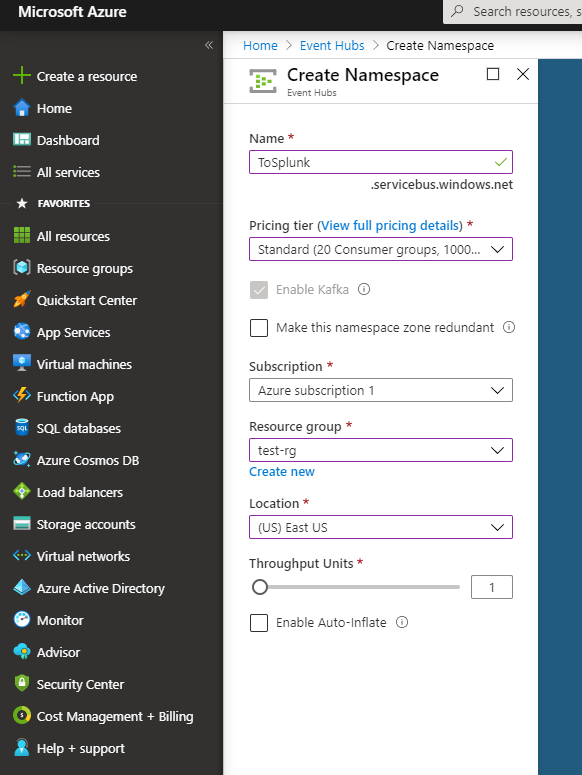
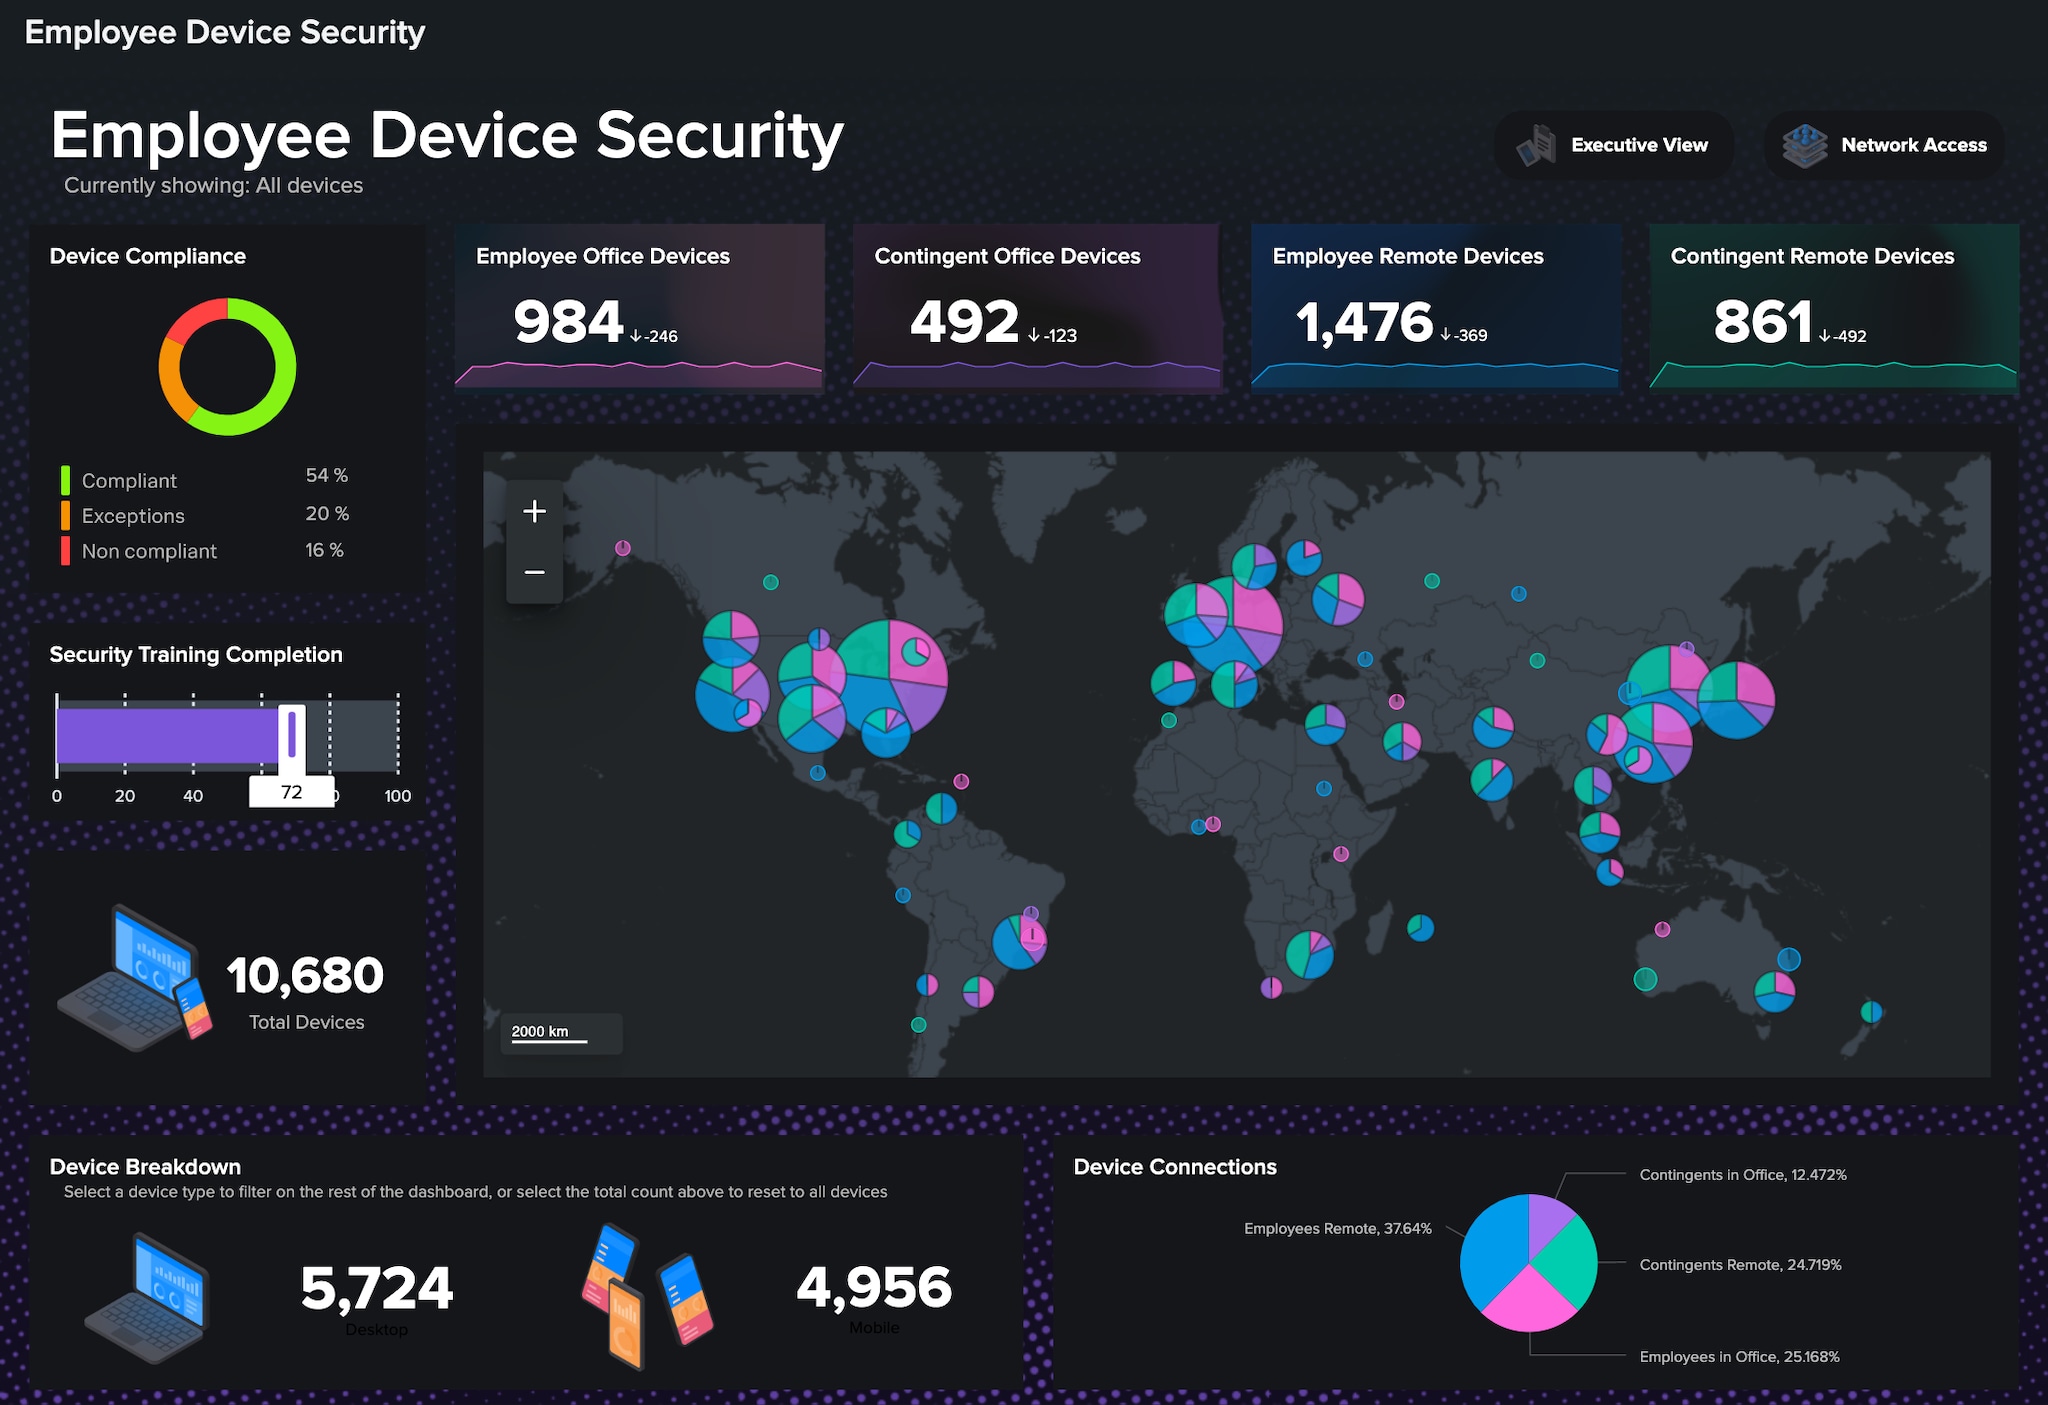
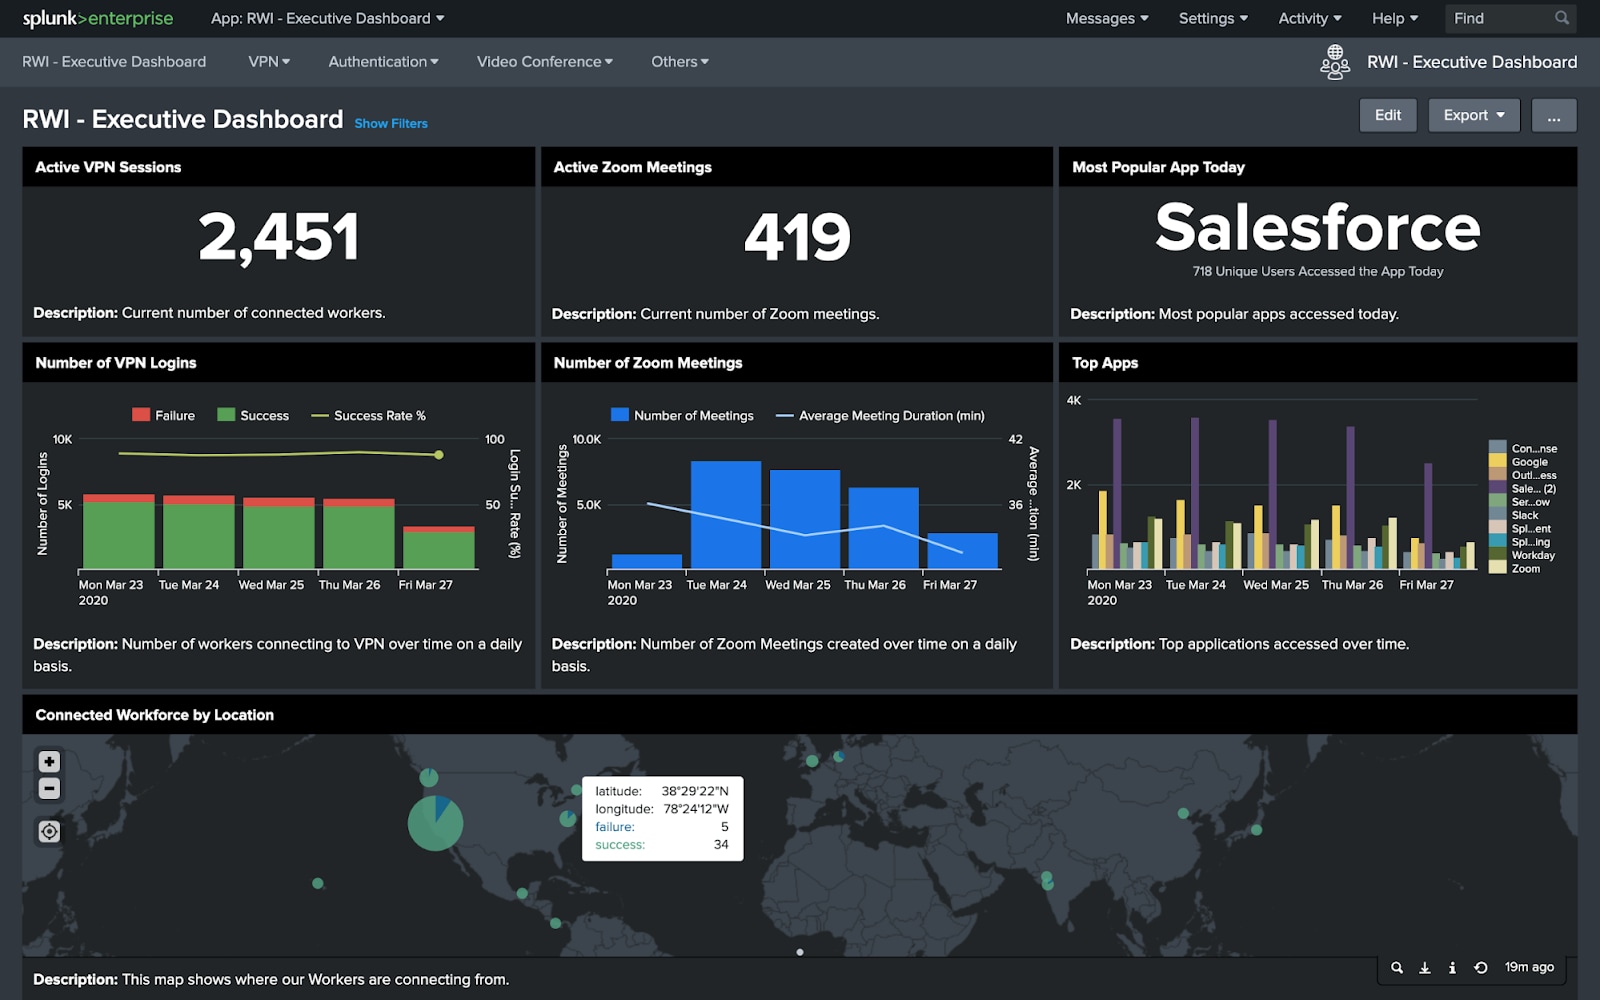
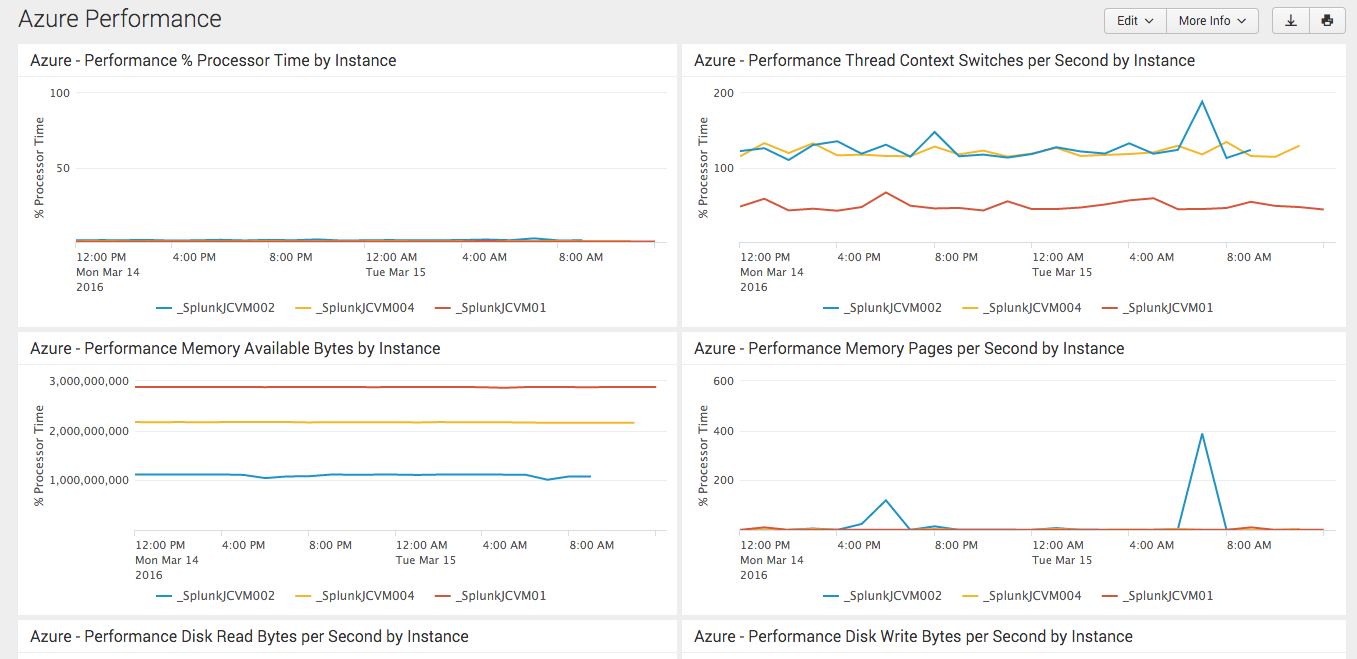
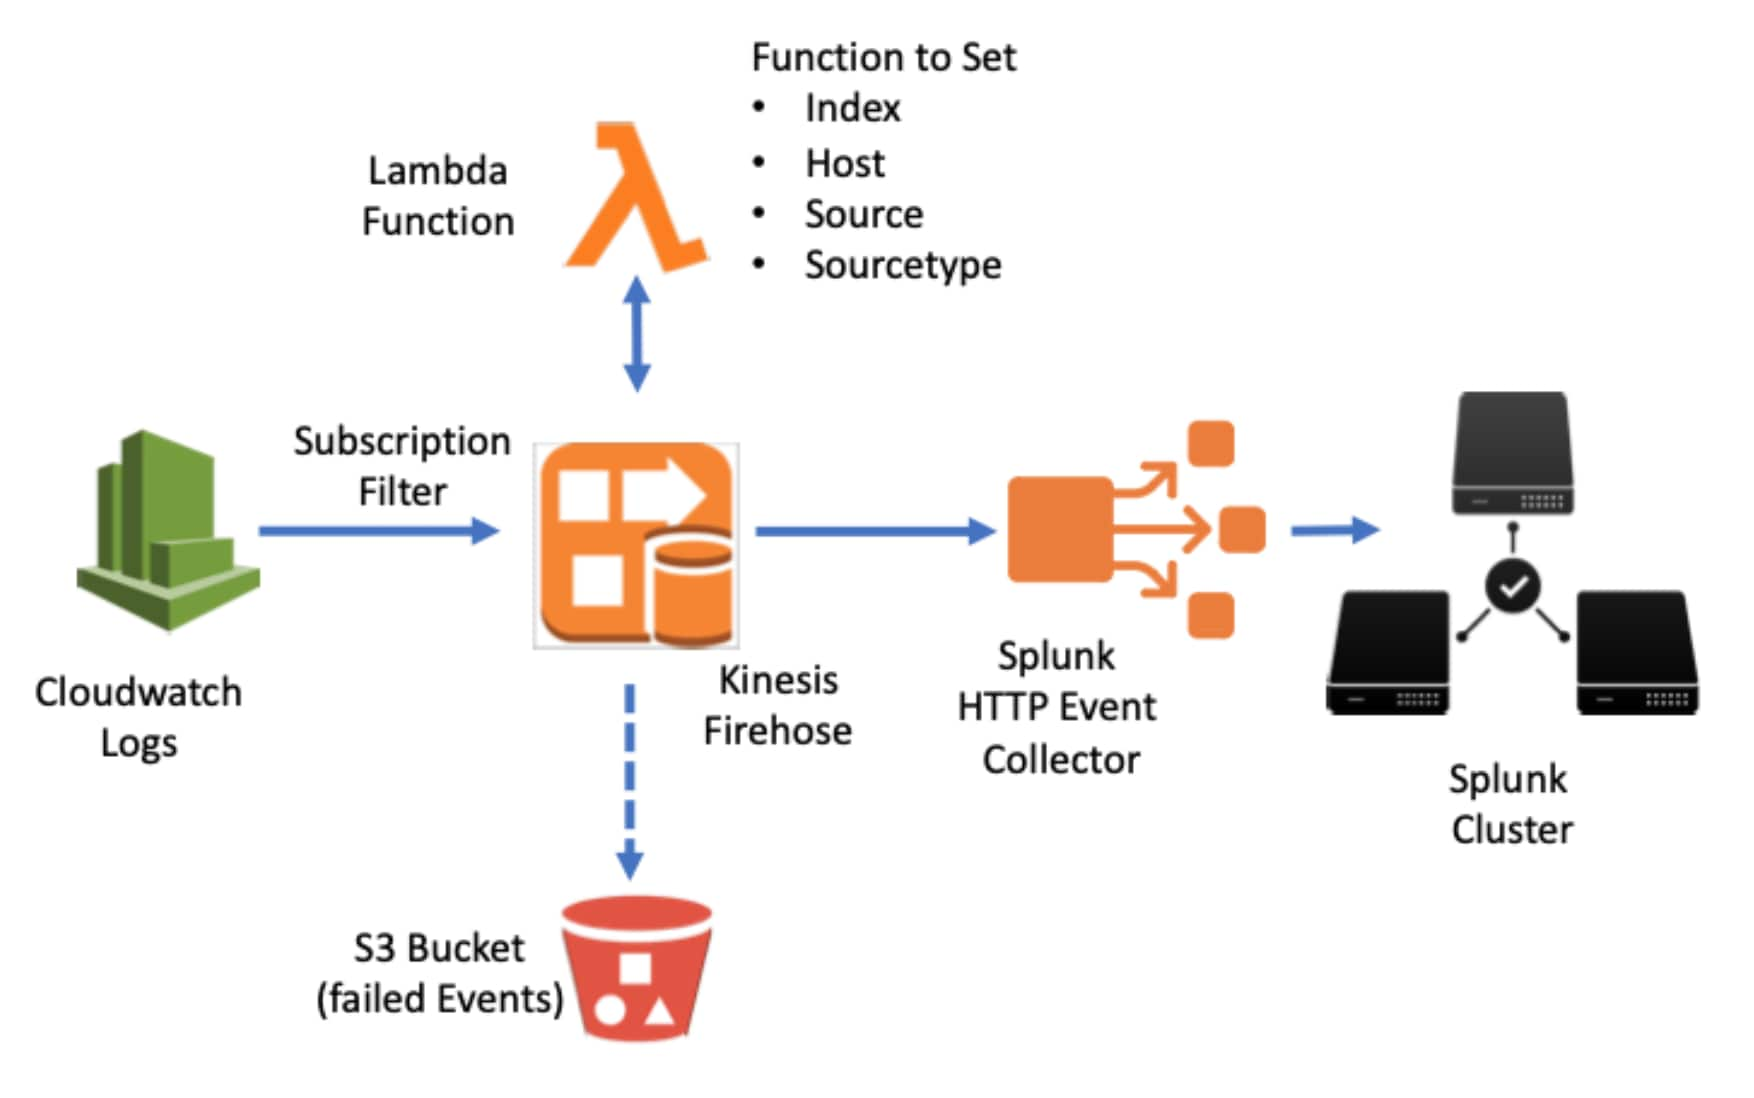
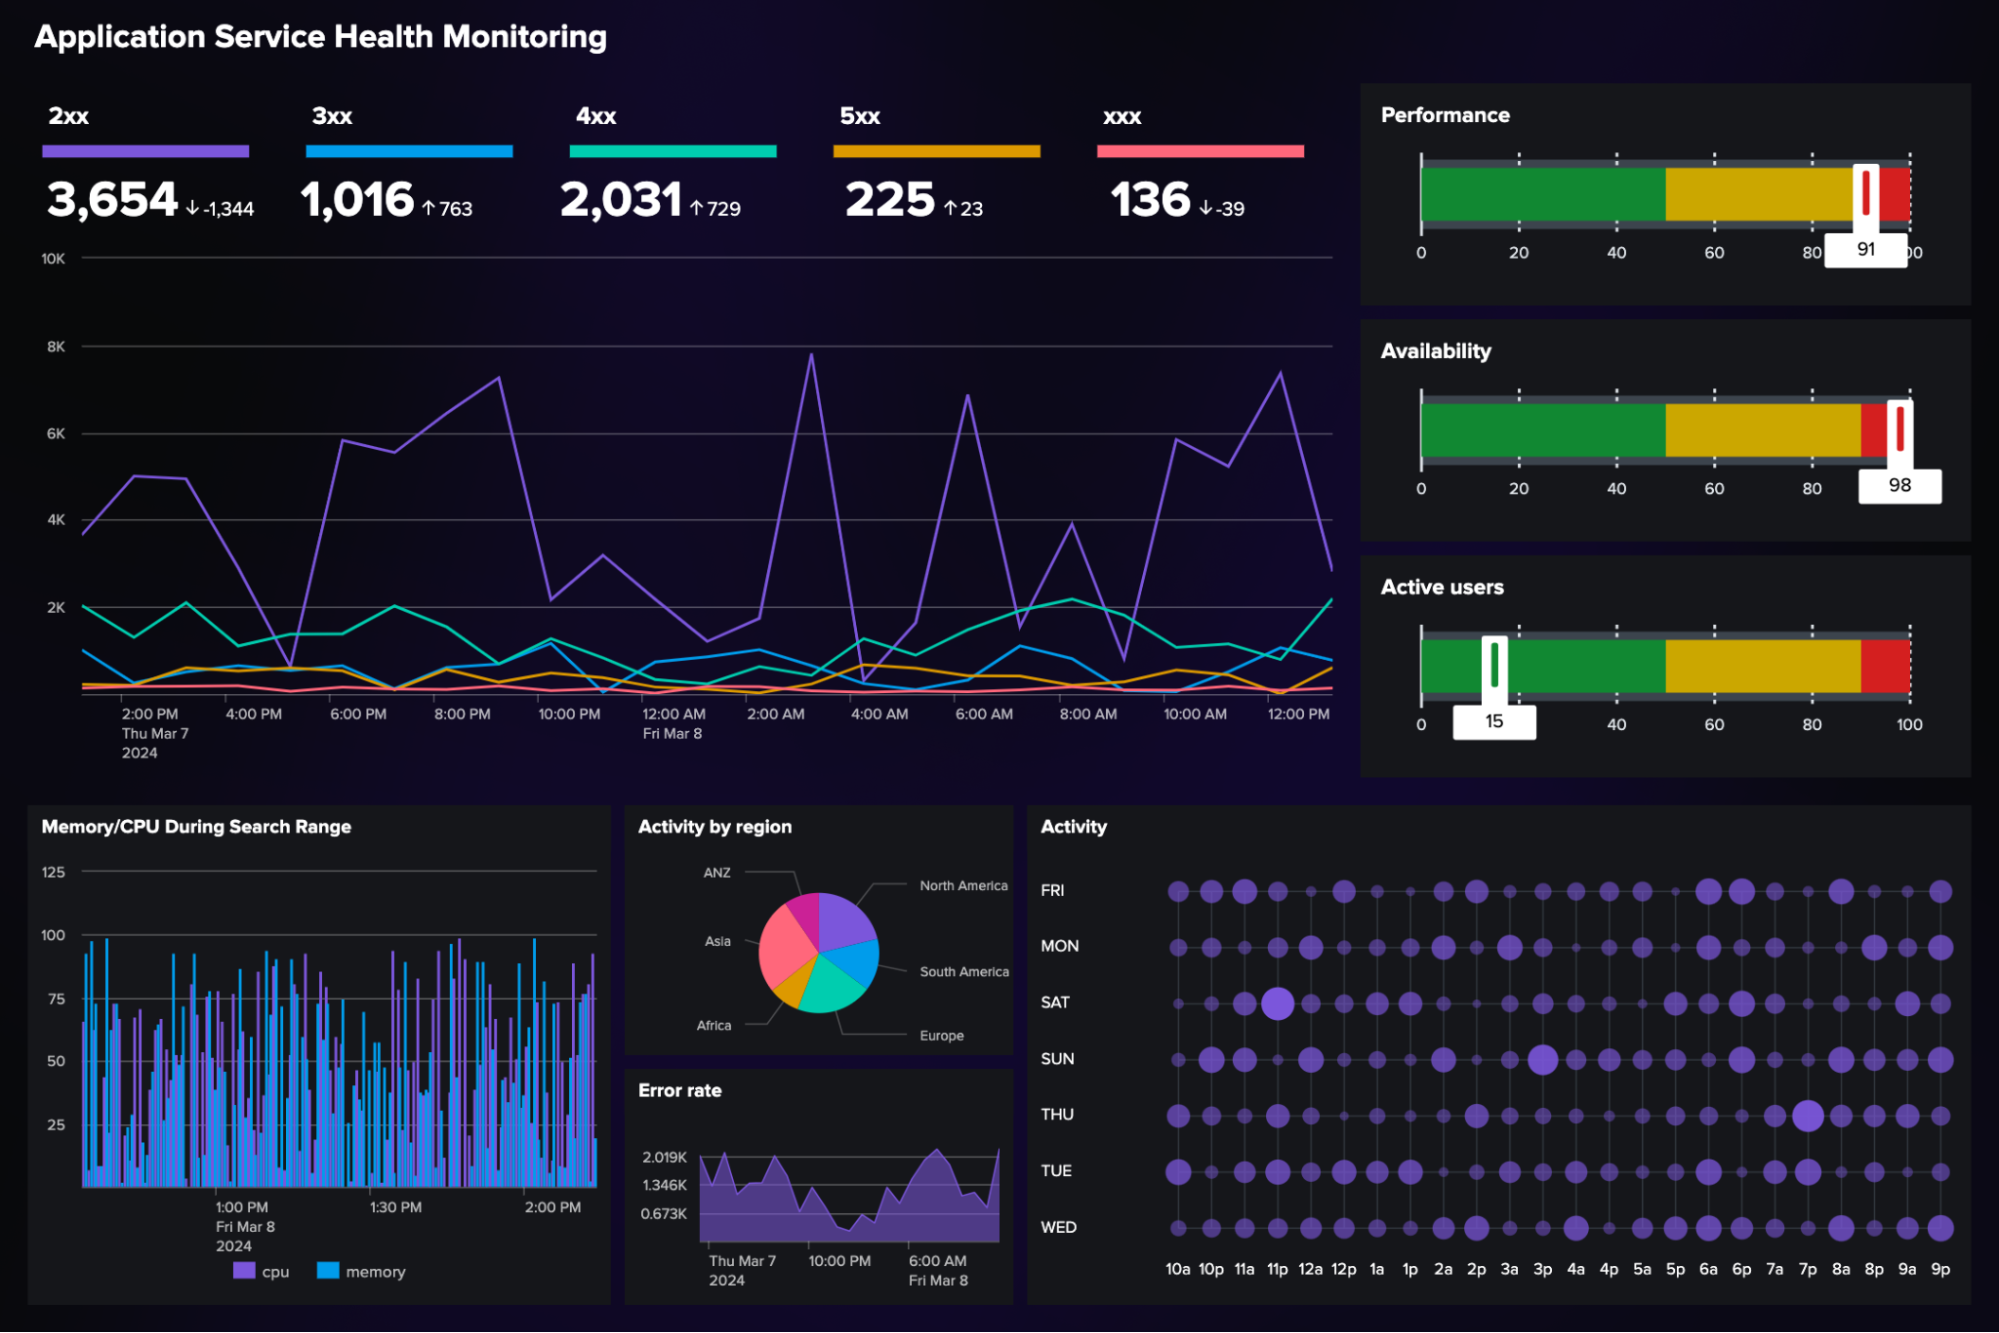
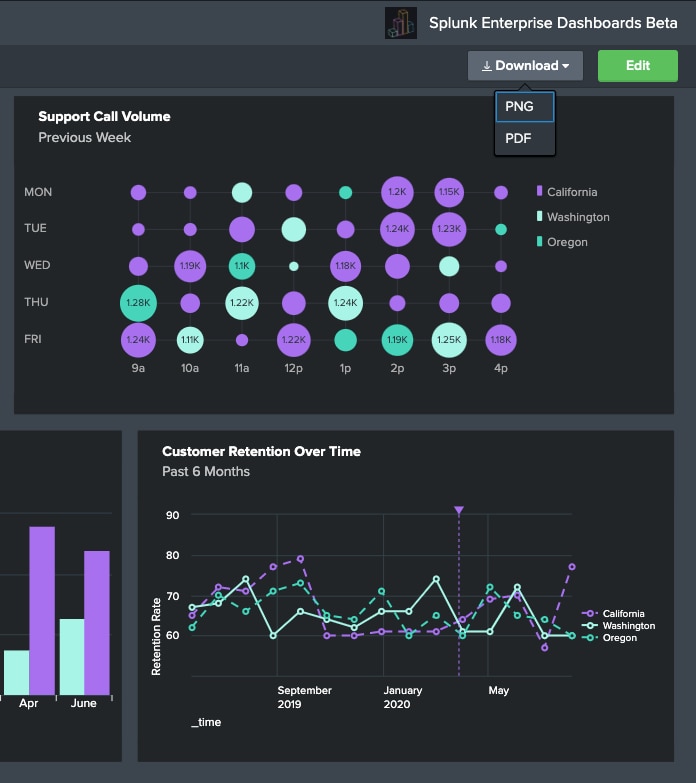
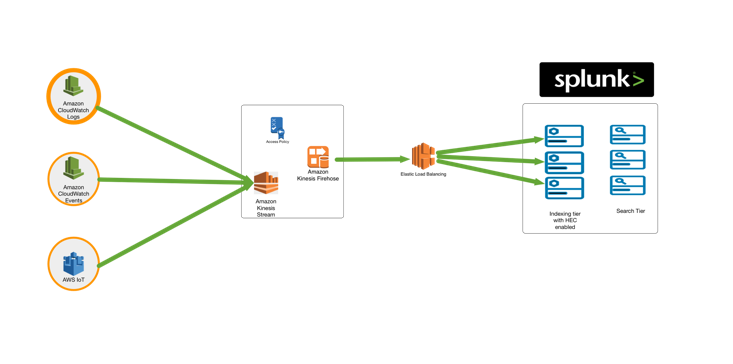
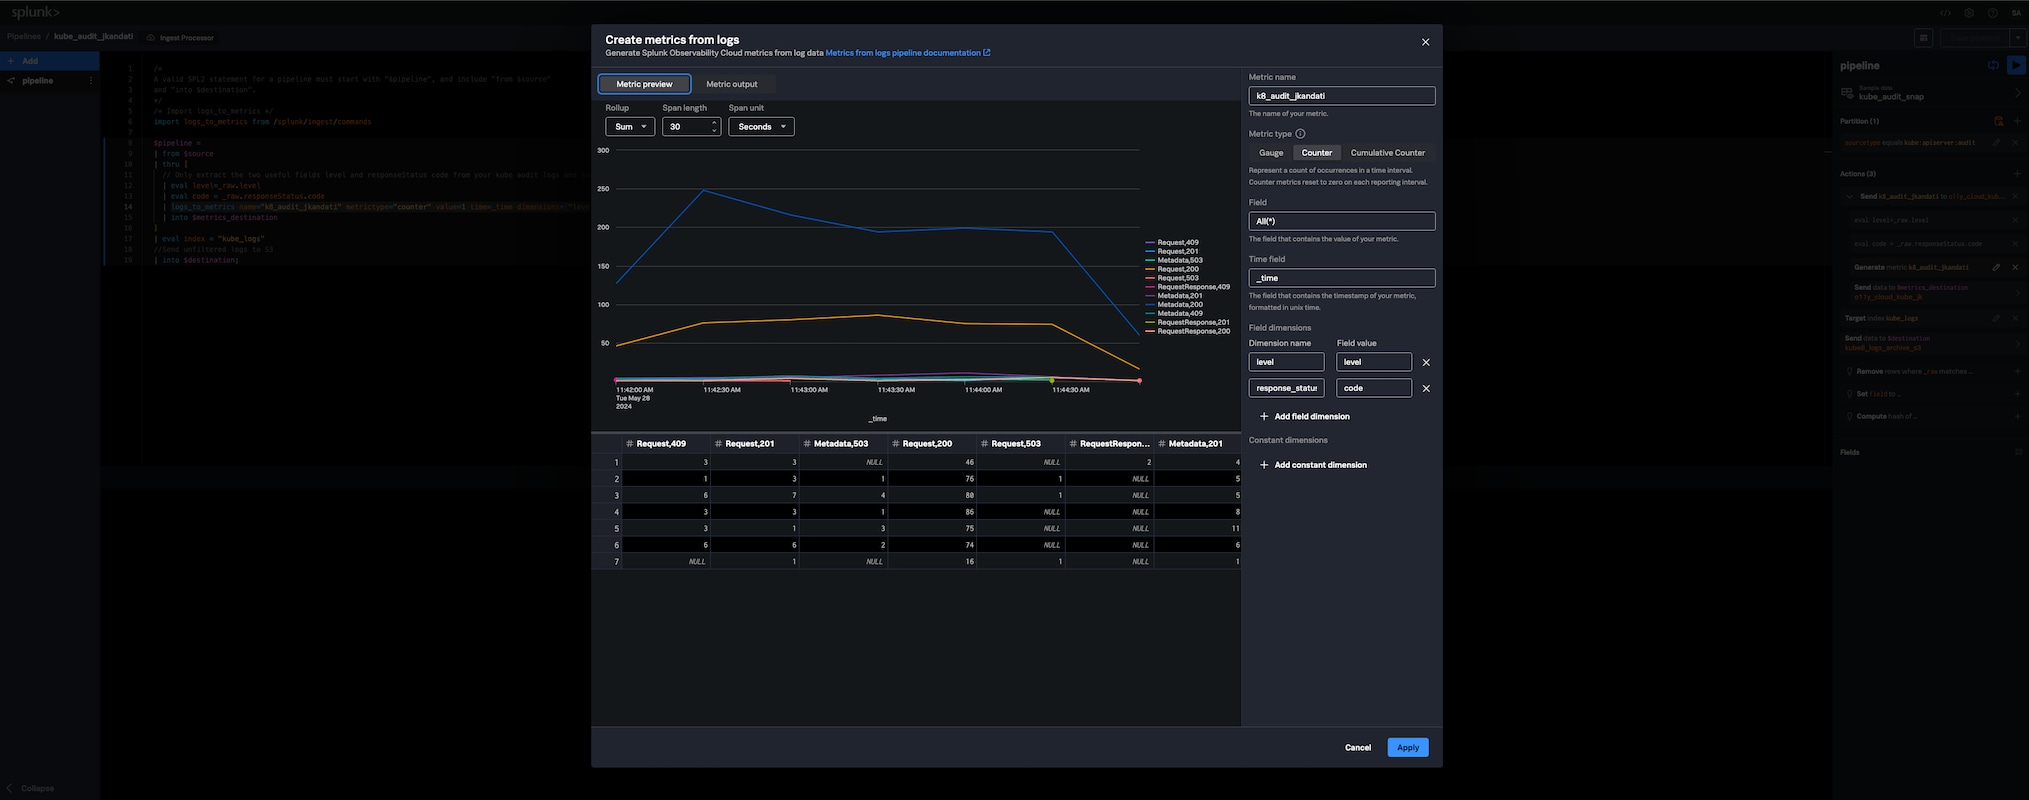
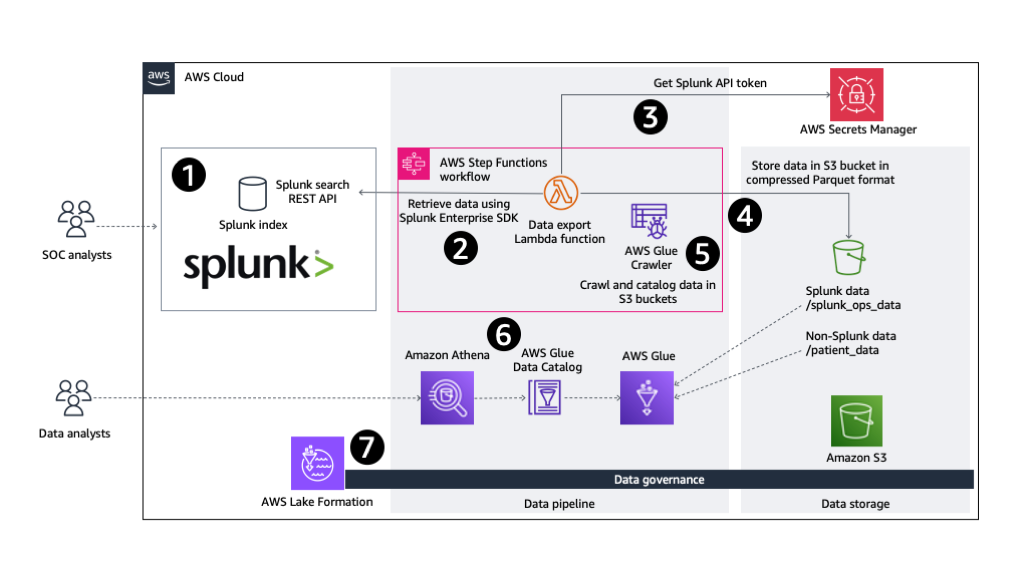
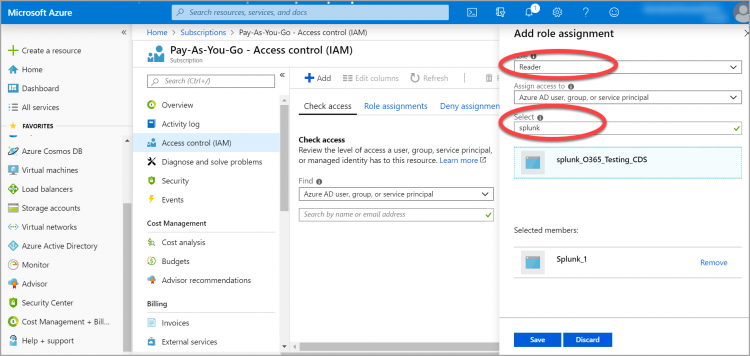
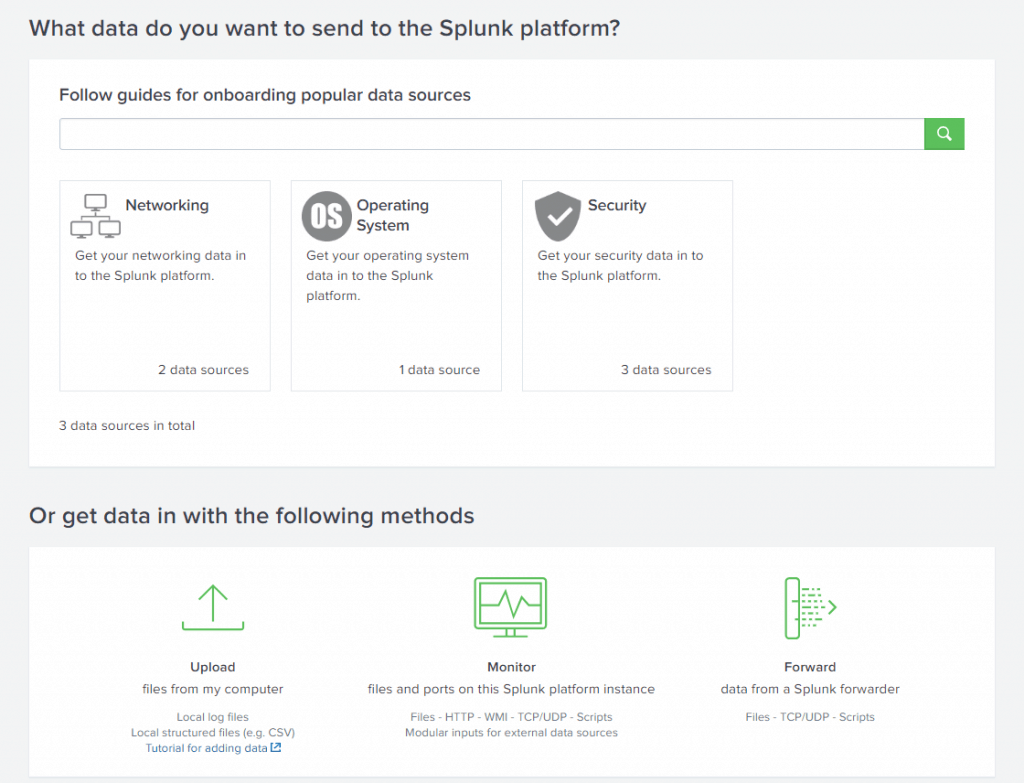
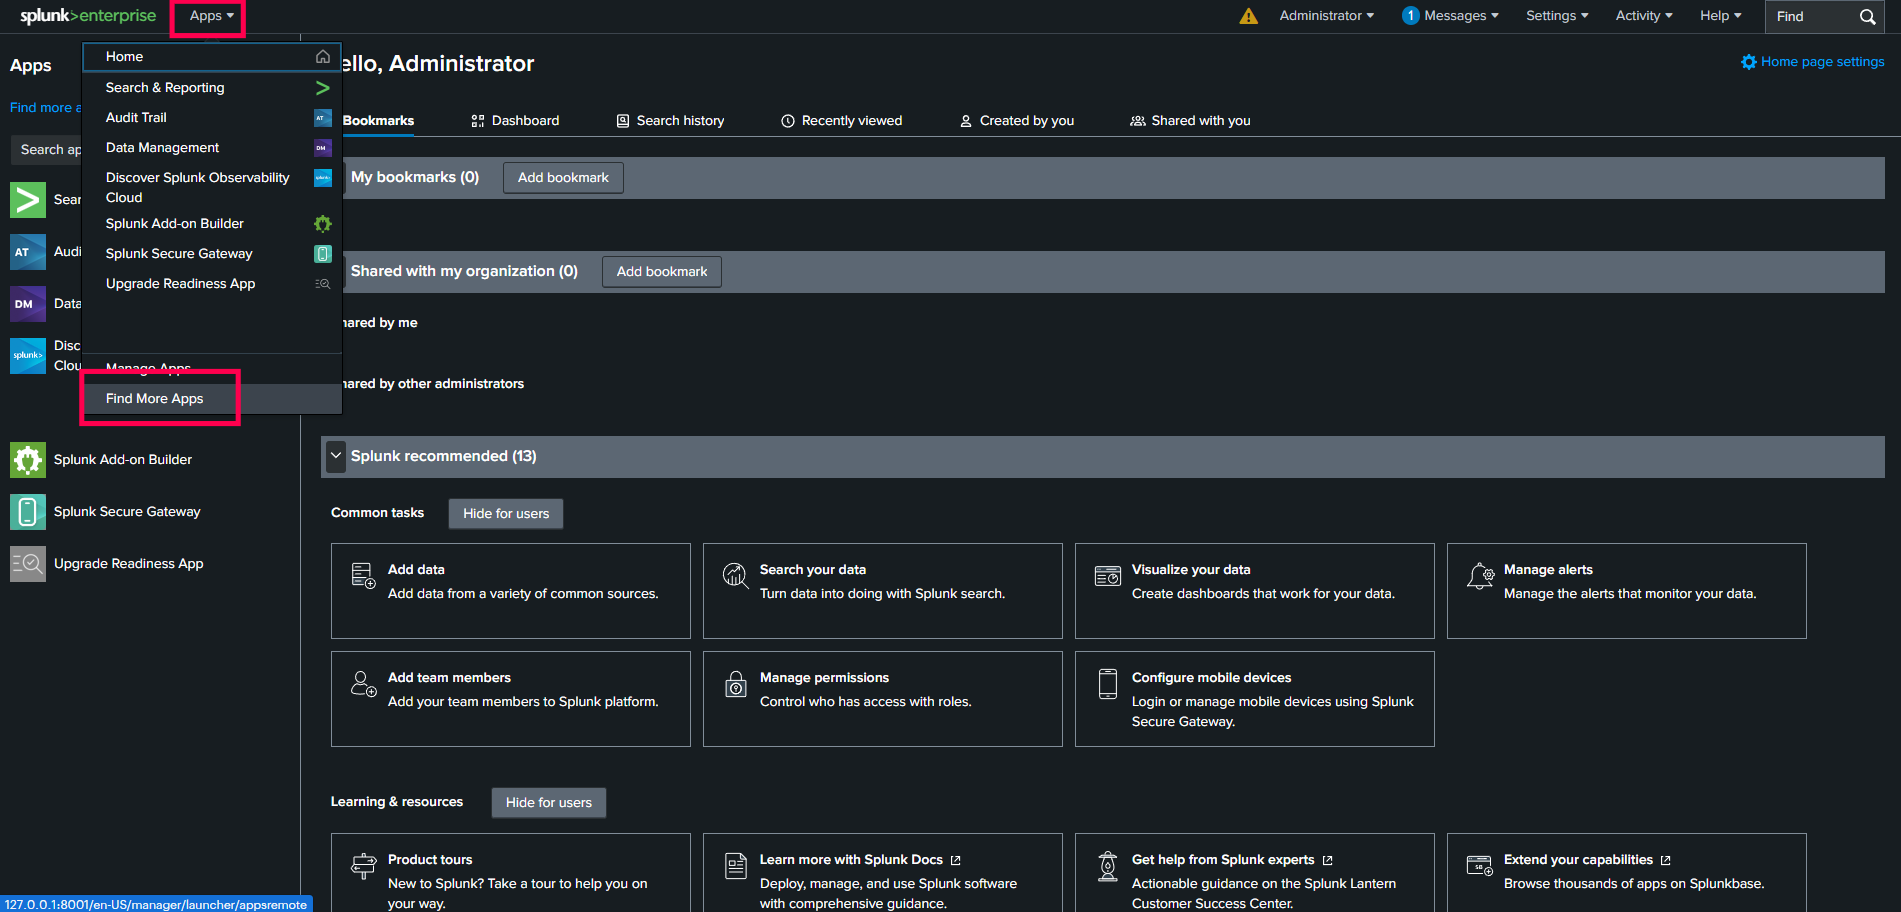
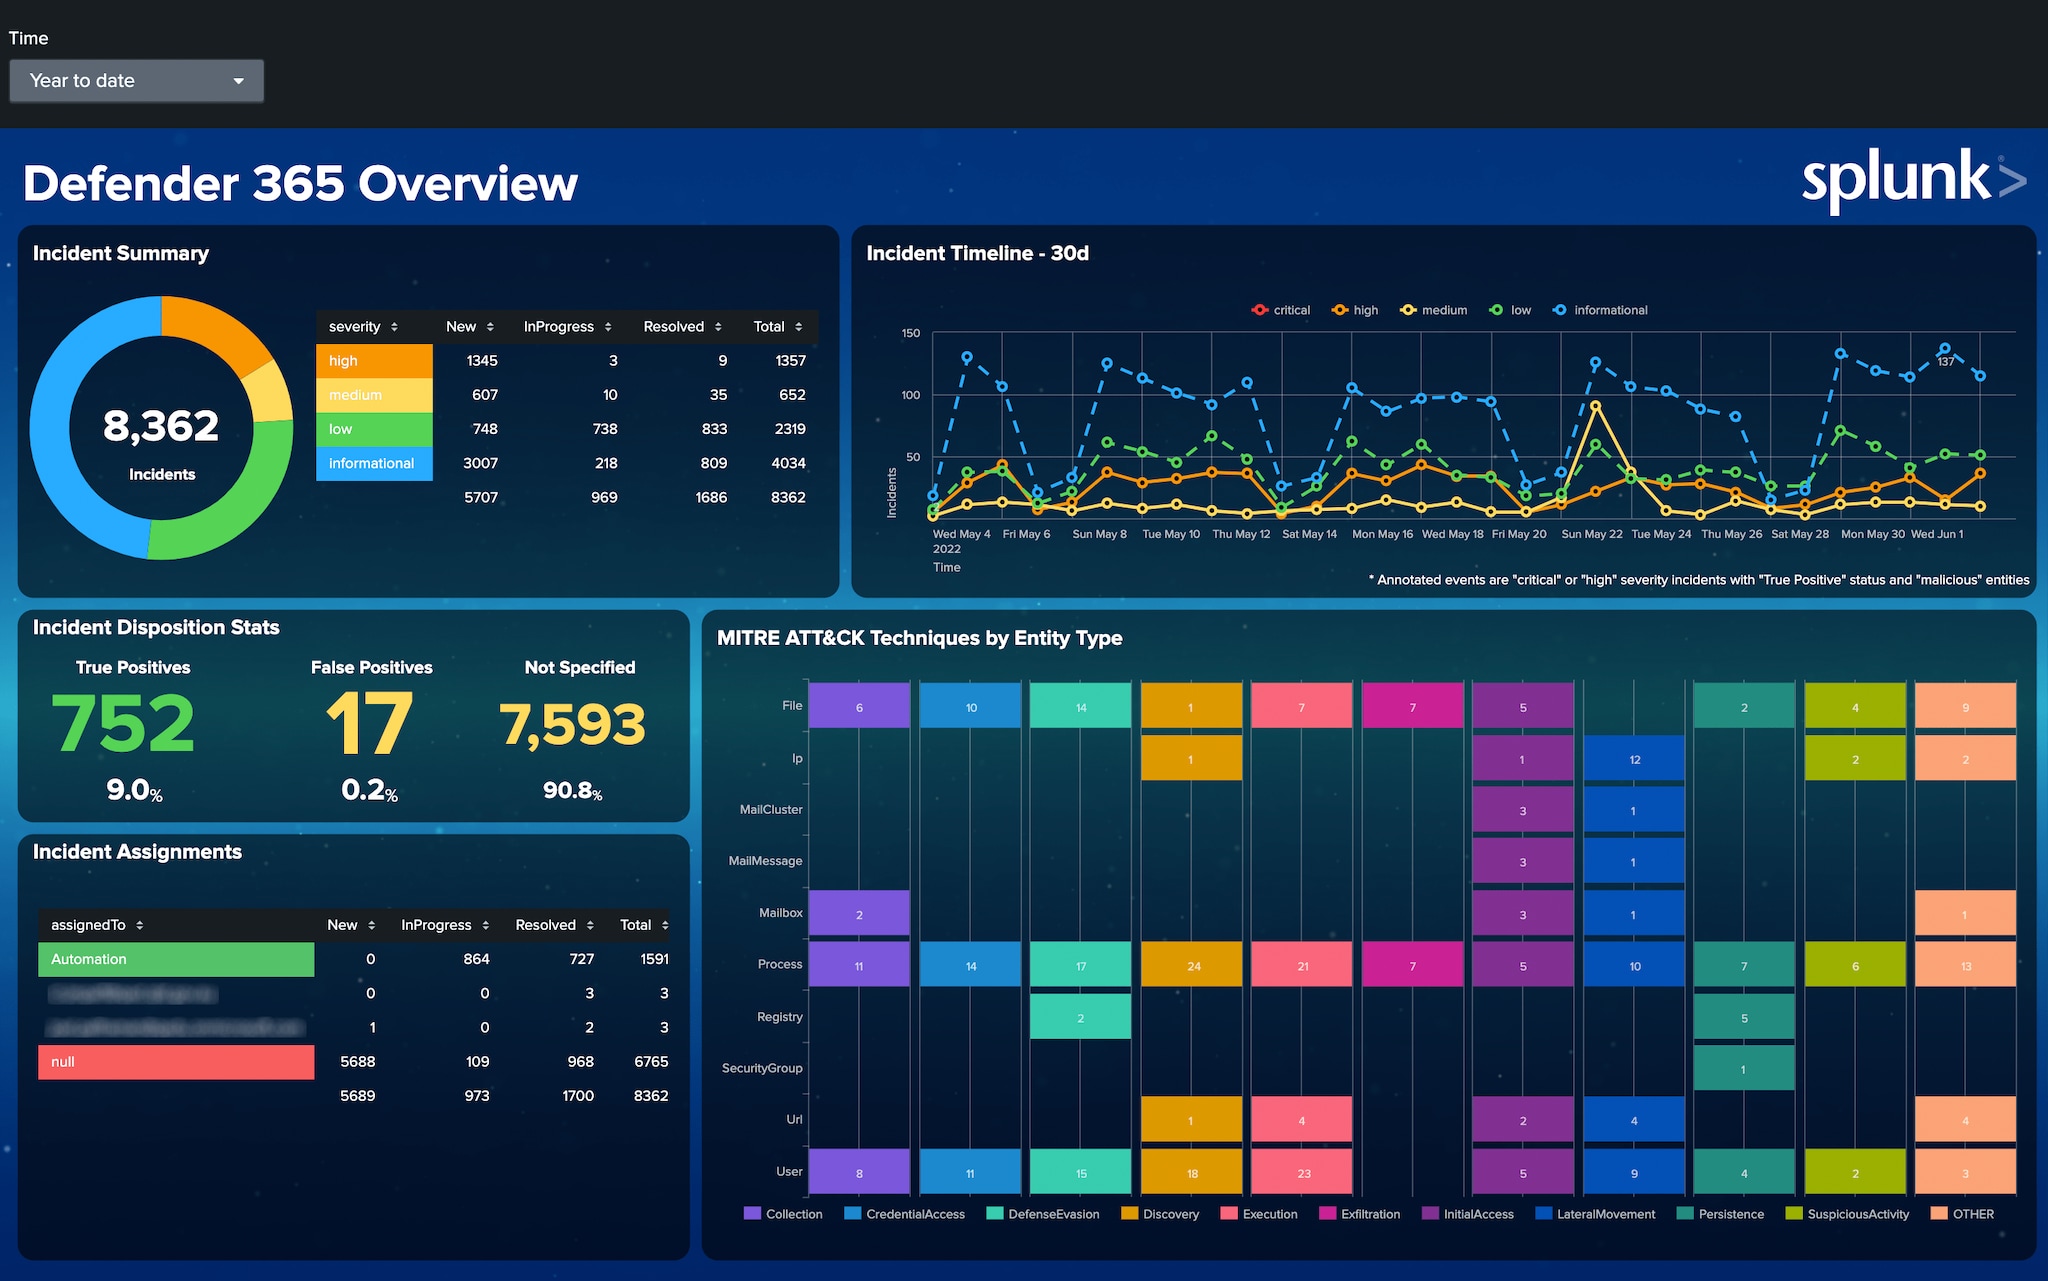
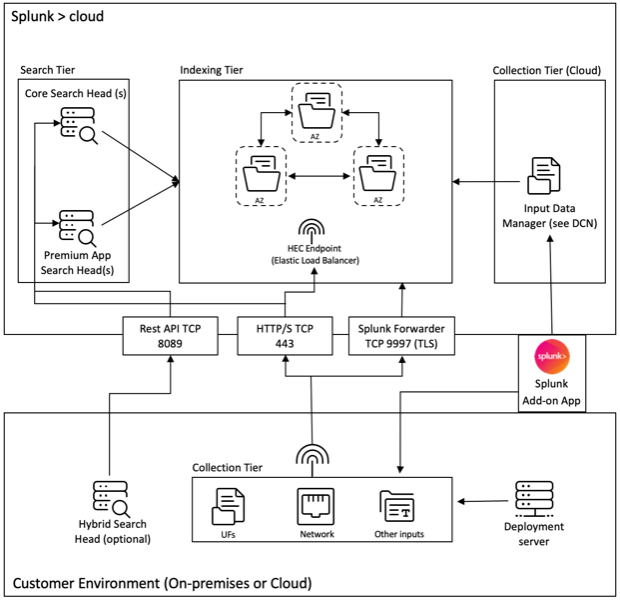
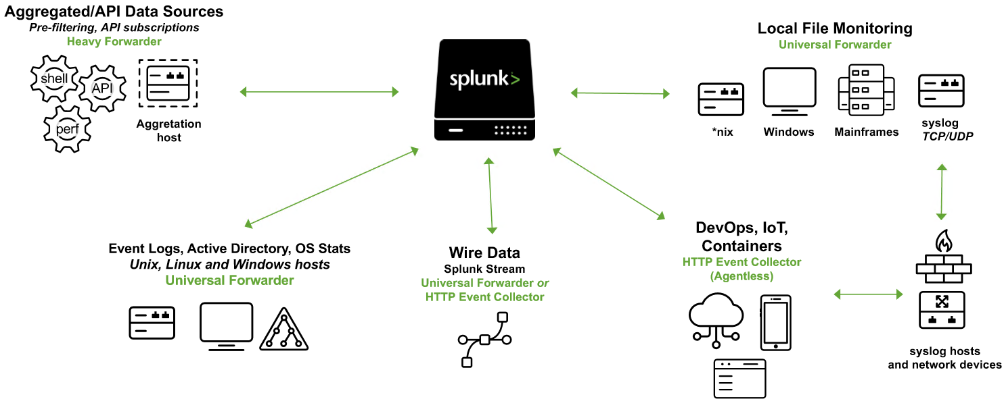
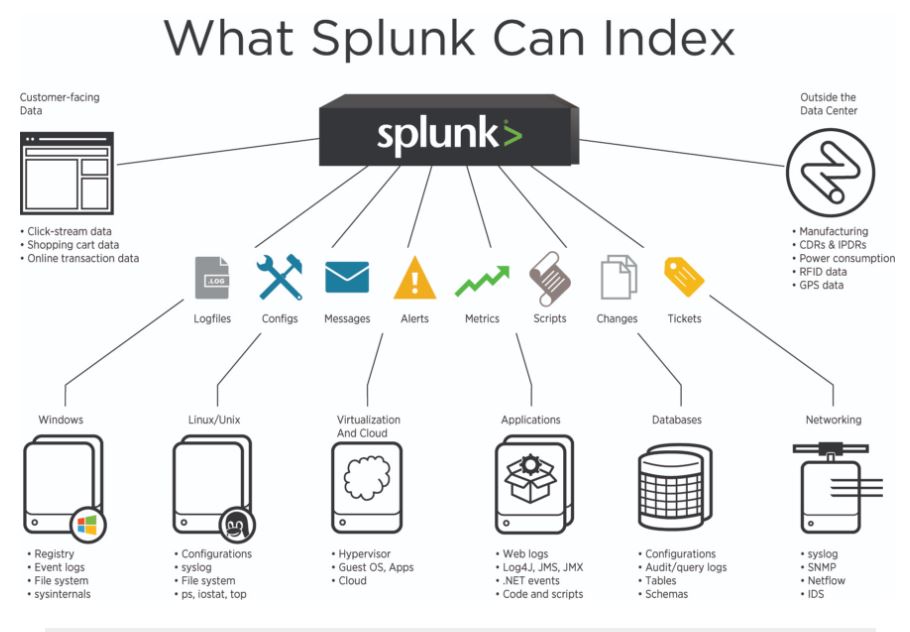
Getting Microsoft Azure data into the Splunk platform - Splunk ...
Getting Microsoft Azure data into the Splunk platform | Splunk ...
Get Microsoft Azure data into Splunk Cloud Platform | Splunk Cloud ...
Getting Microsoft Azure Data into Splunk | Splunk
Add Azure To Splunk , Get Microsoft Azure data into Splunk Cloud ...
(PDF) Gain Insights into your Microsoft Azure Data using Splunk · Azure ...
Mengekspor data Splunk ke platform target - Microsoft Sentinel ...
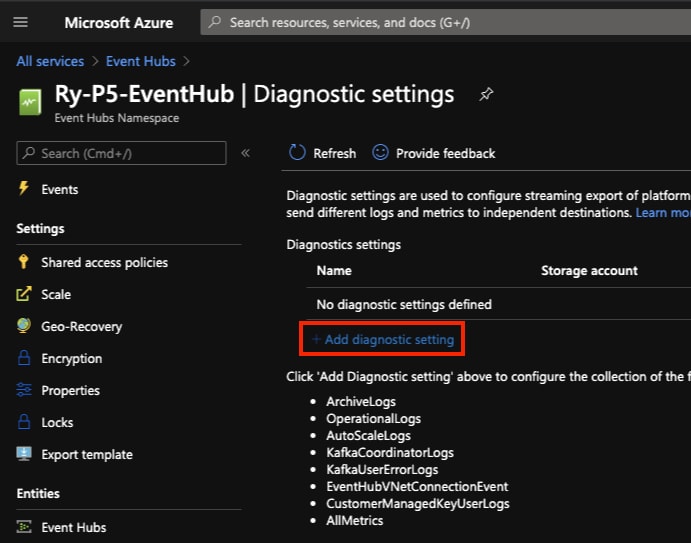
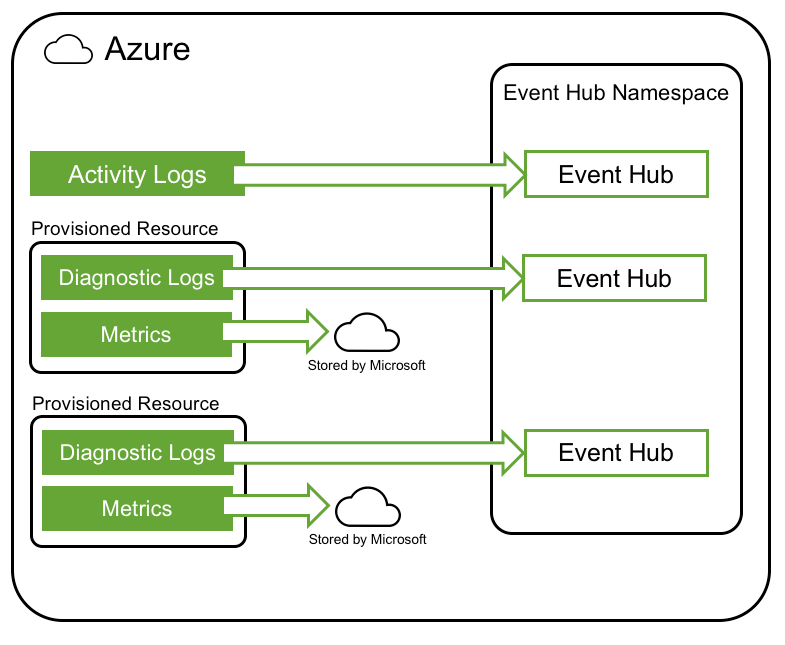
Getting started with Microsoft Azure Event Hub data - Splunk Lantern
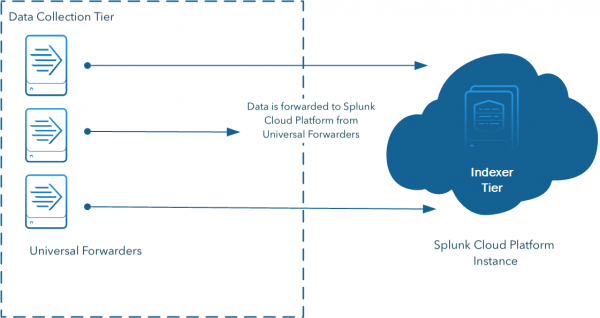
Use forwarders to get data into Splunk Cloud Platform - Splunk ...
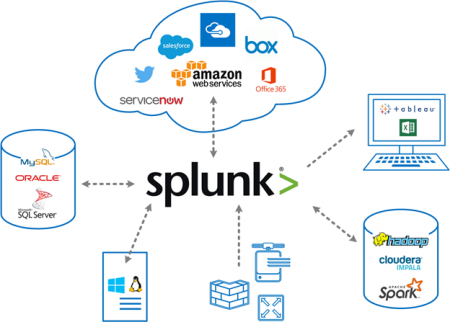
Splunk Data Integration - Getting Data Into Splunk
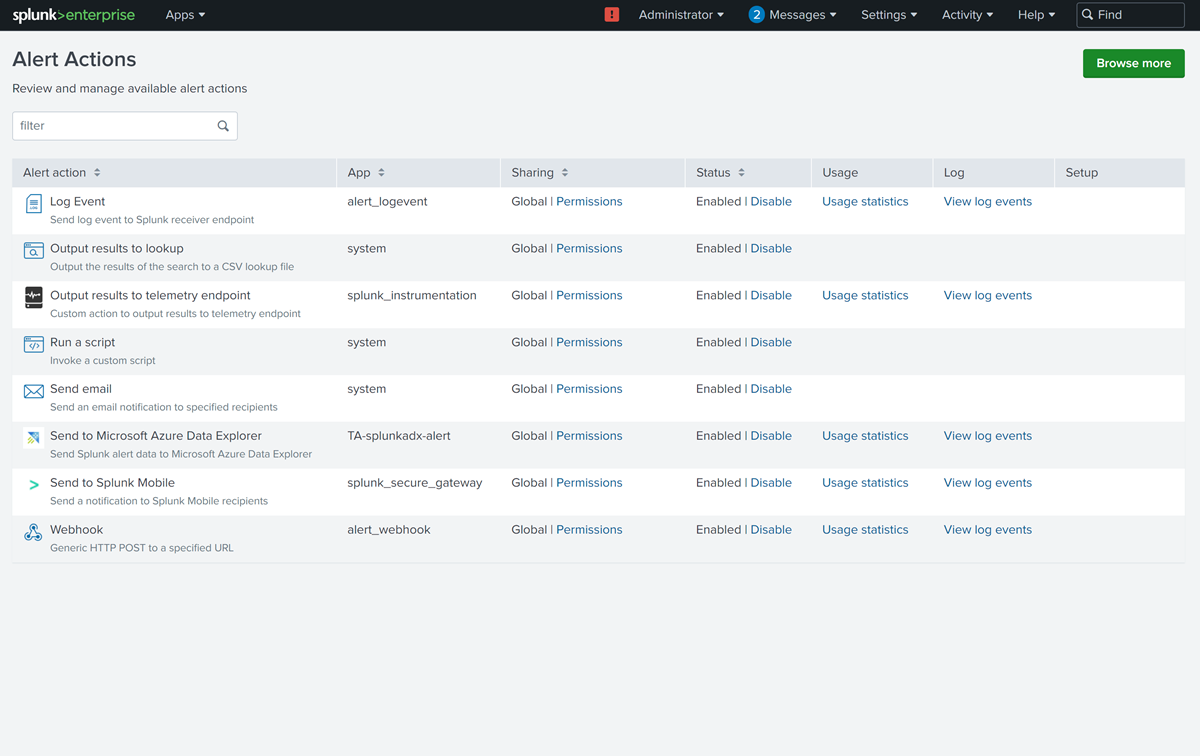
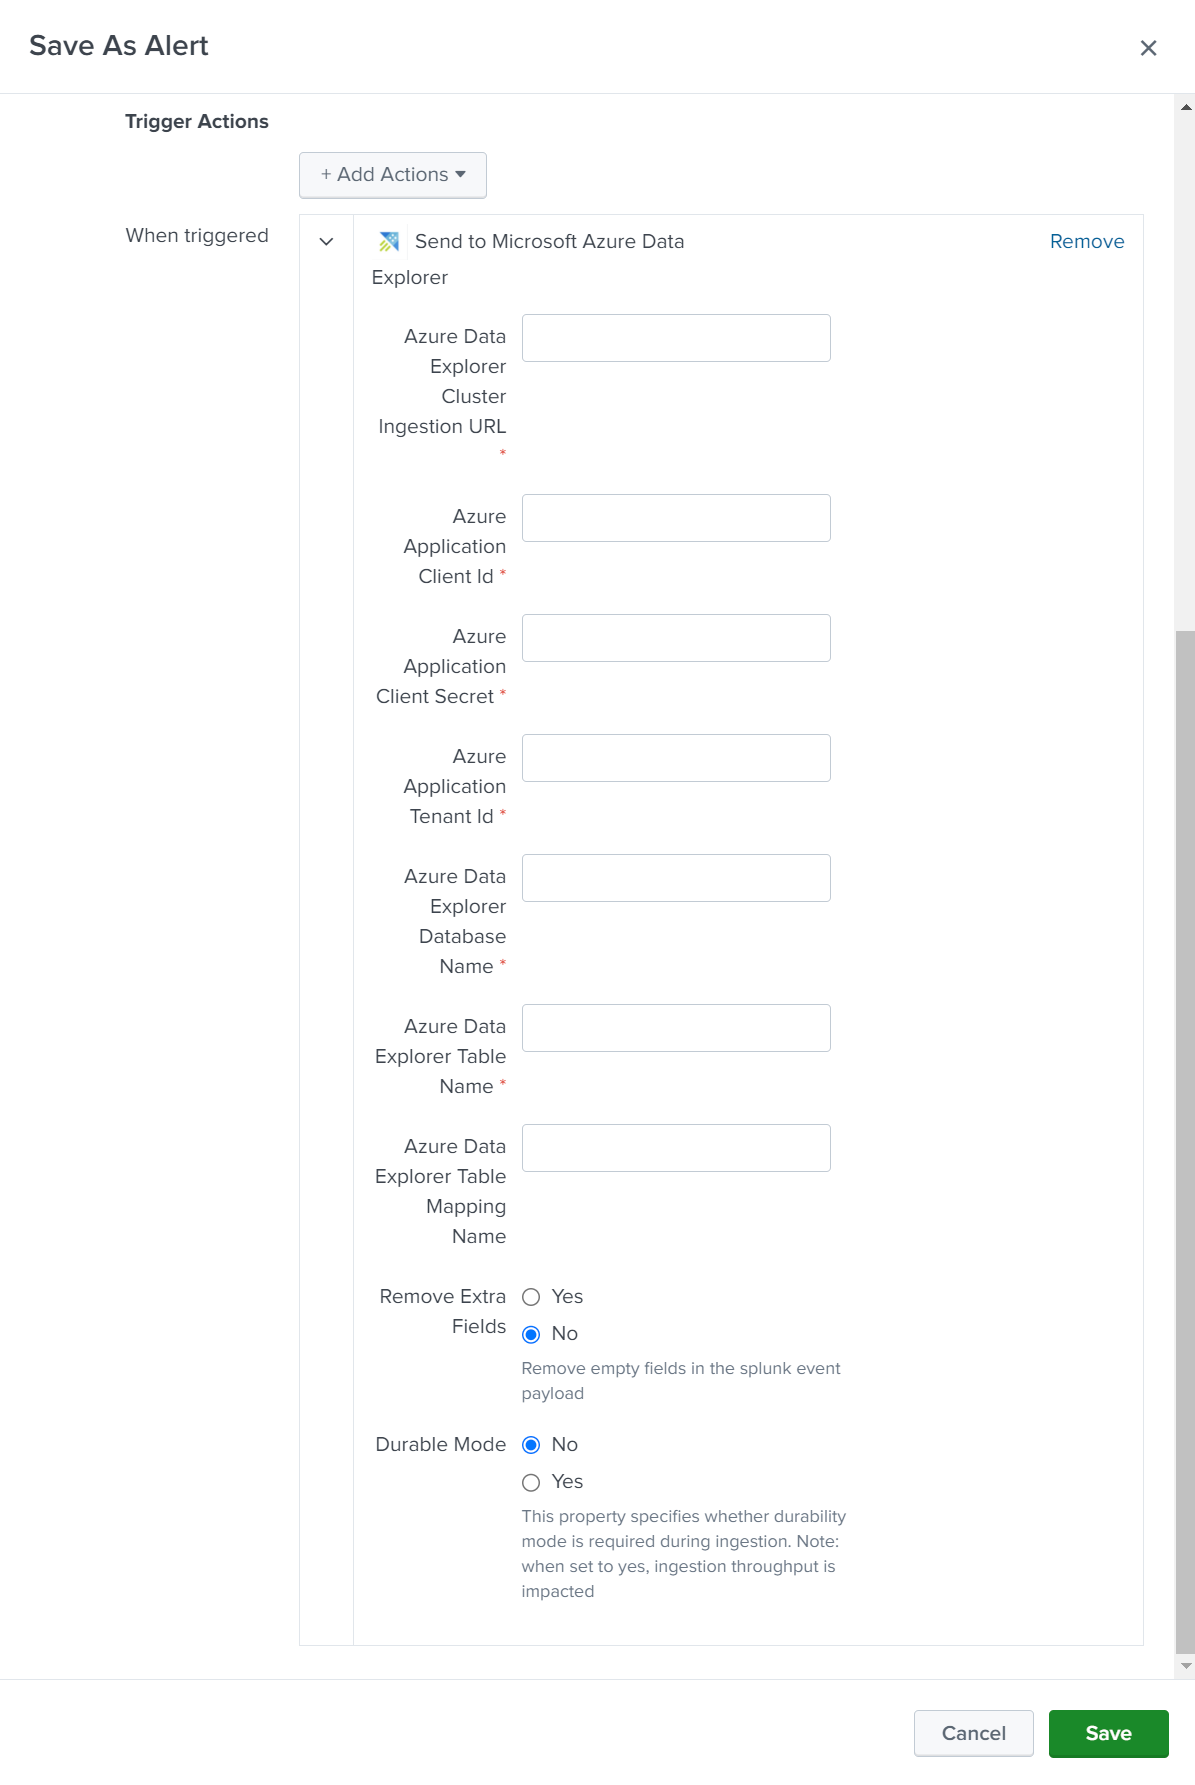
Ingest data from Splunk to Azure Data Explorer - Azure Data Explorer ...
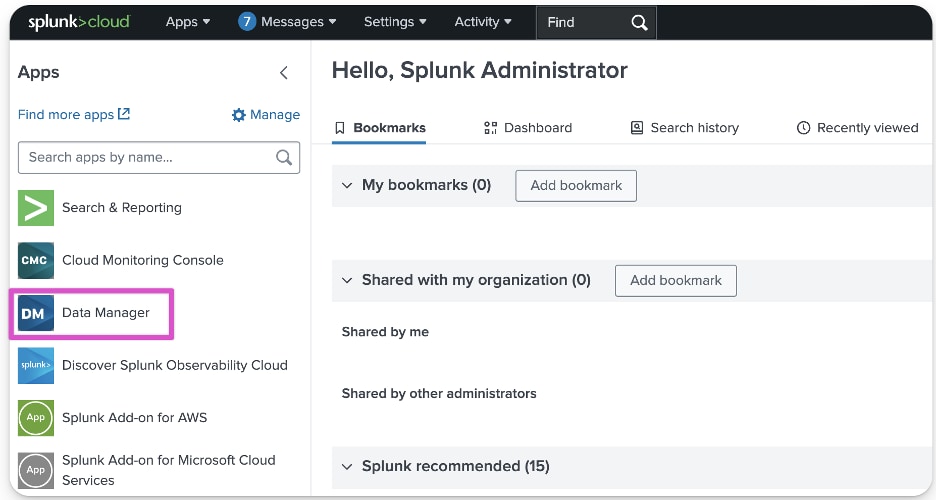
Data Manager Enables Microsoft Azure Data Onboarding! | Splunk | Daniel ...
Data Manager Enables Microsoft Azure Data Onboarding! | Splunk
Splunking Microsoft Azure Monitor Data – Part 2 – Splunk Setup | Splunk
How to use Splunk Universal Forwarder | Azure Data Explorer posted on ...
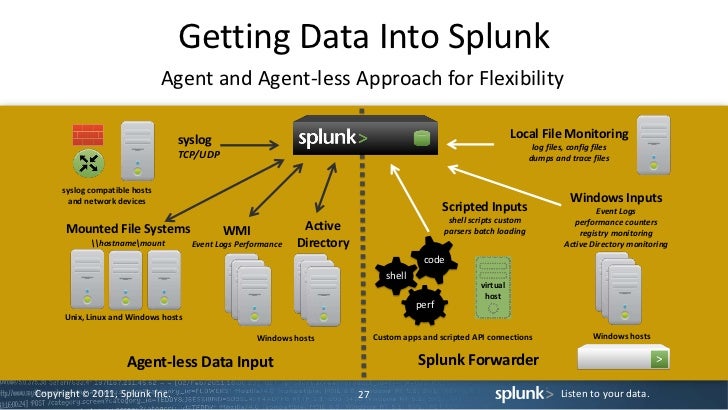
Getting Data Into Splunk Agent
Migration Mapping from Splunk Add-on for Microsoft Azure (Unsupported ...
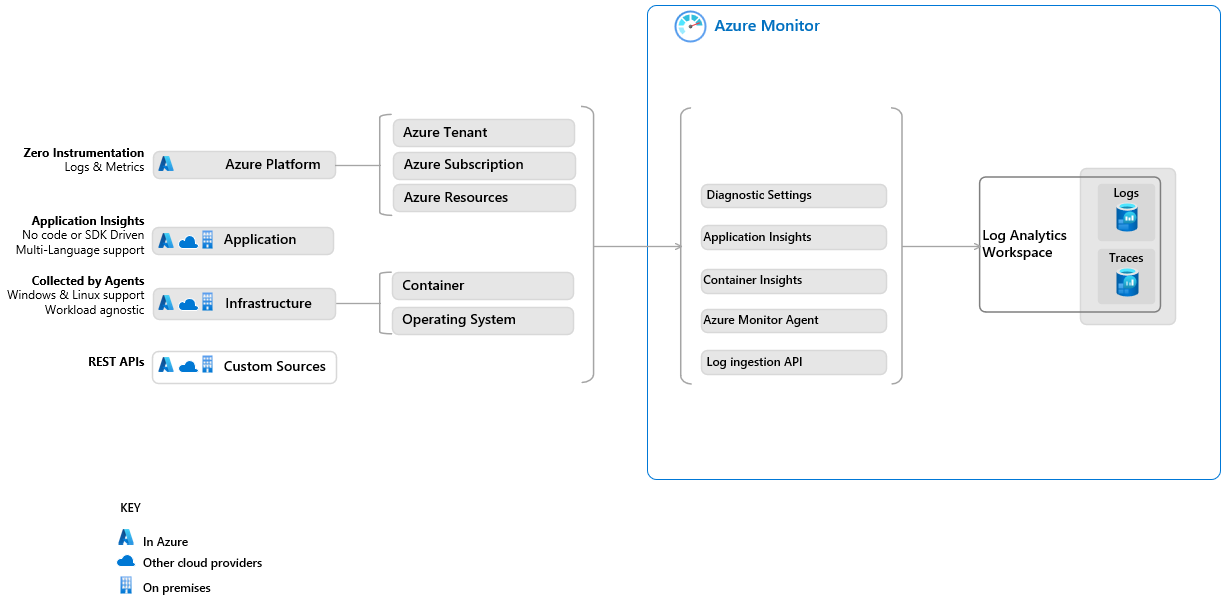
Migrate from Splunk to Azure Monitor Logs - Get started - Azure Monitor ...
Solved: How to get logs from Azure and O365 into Splunk? - Splunk Community
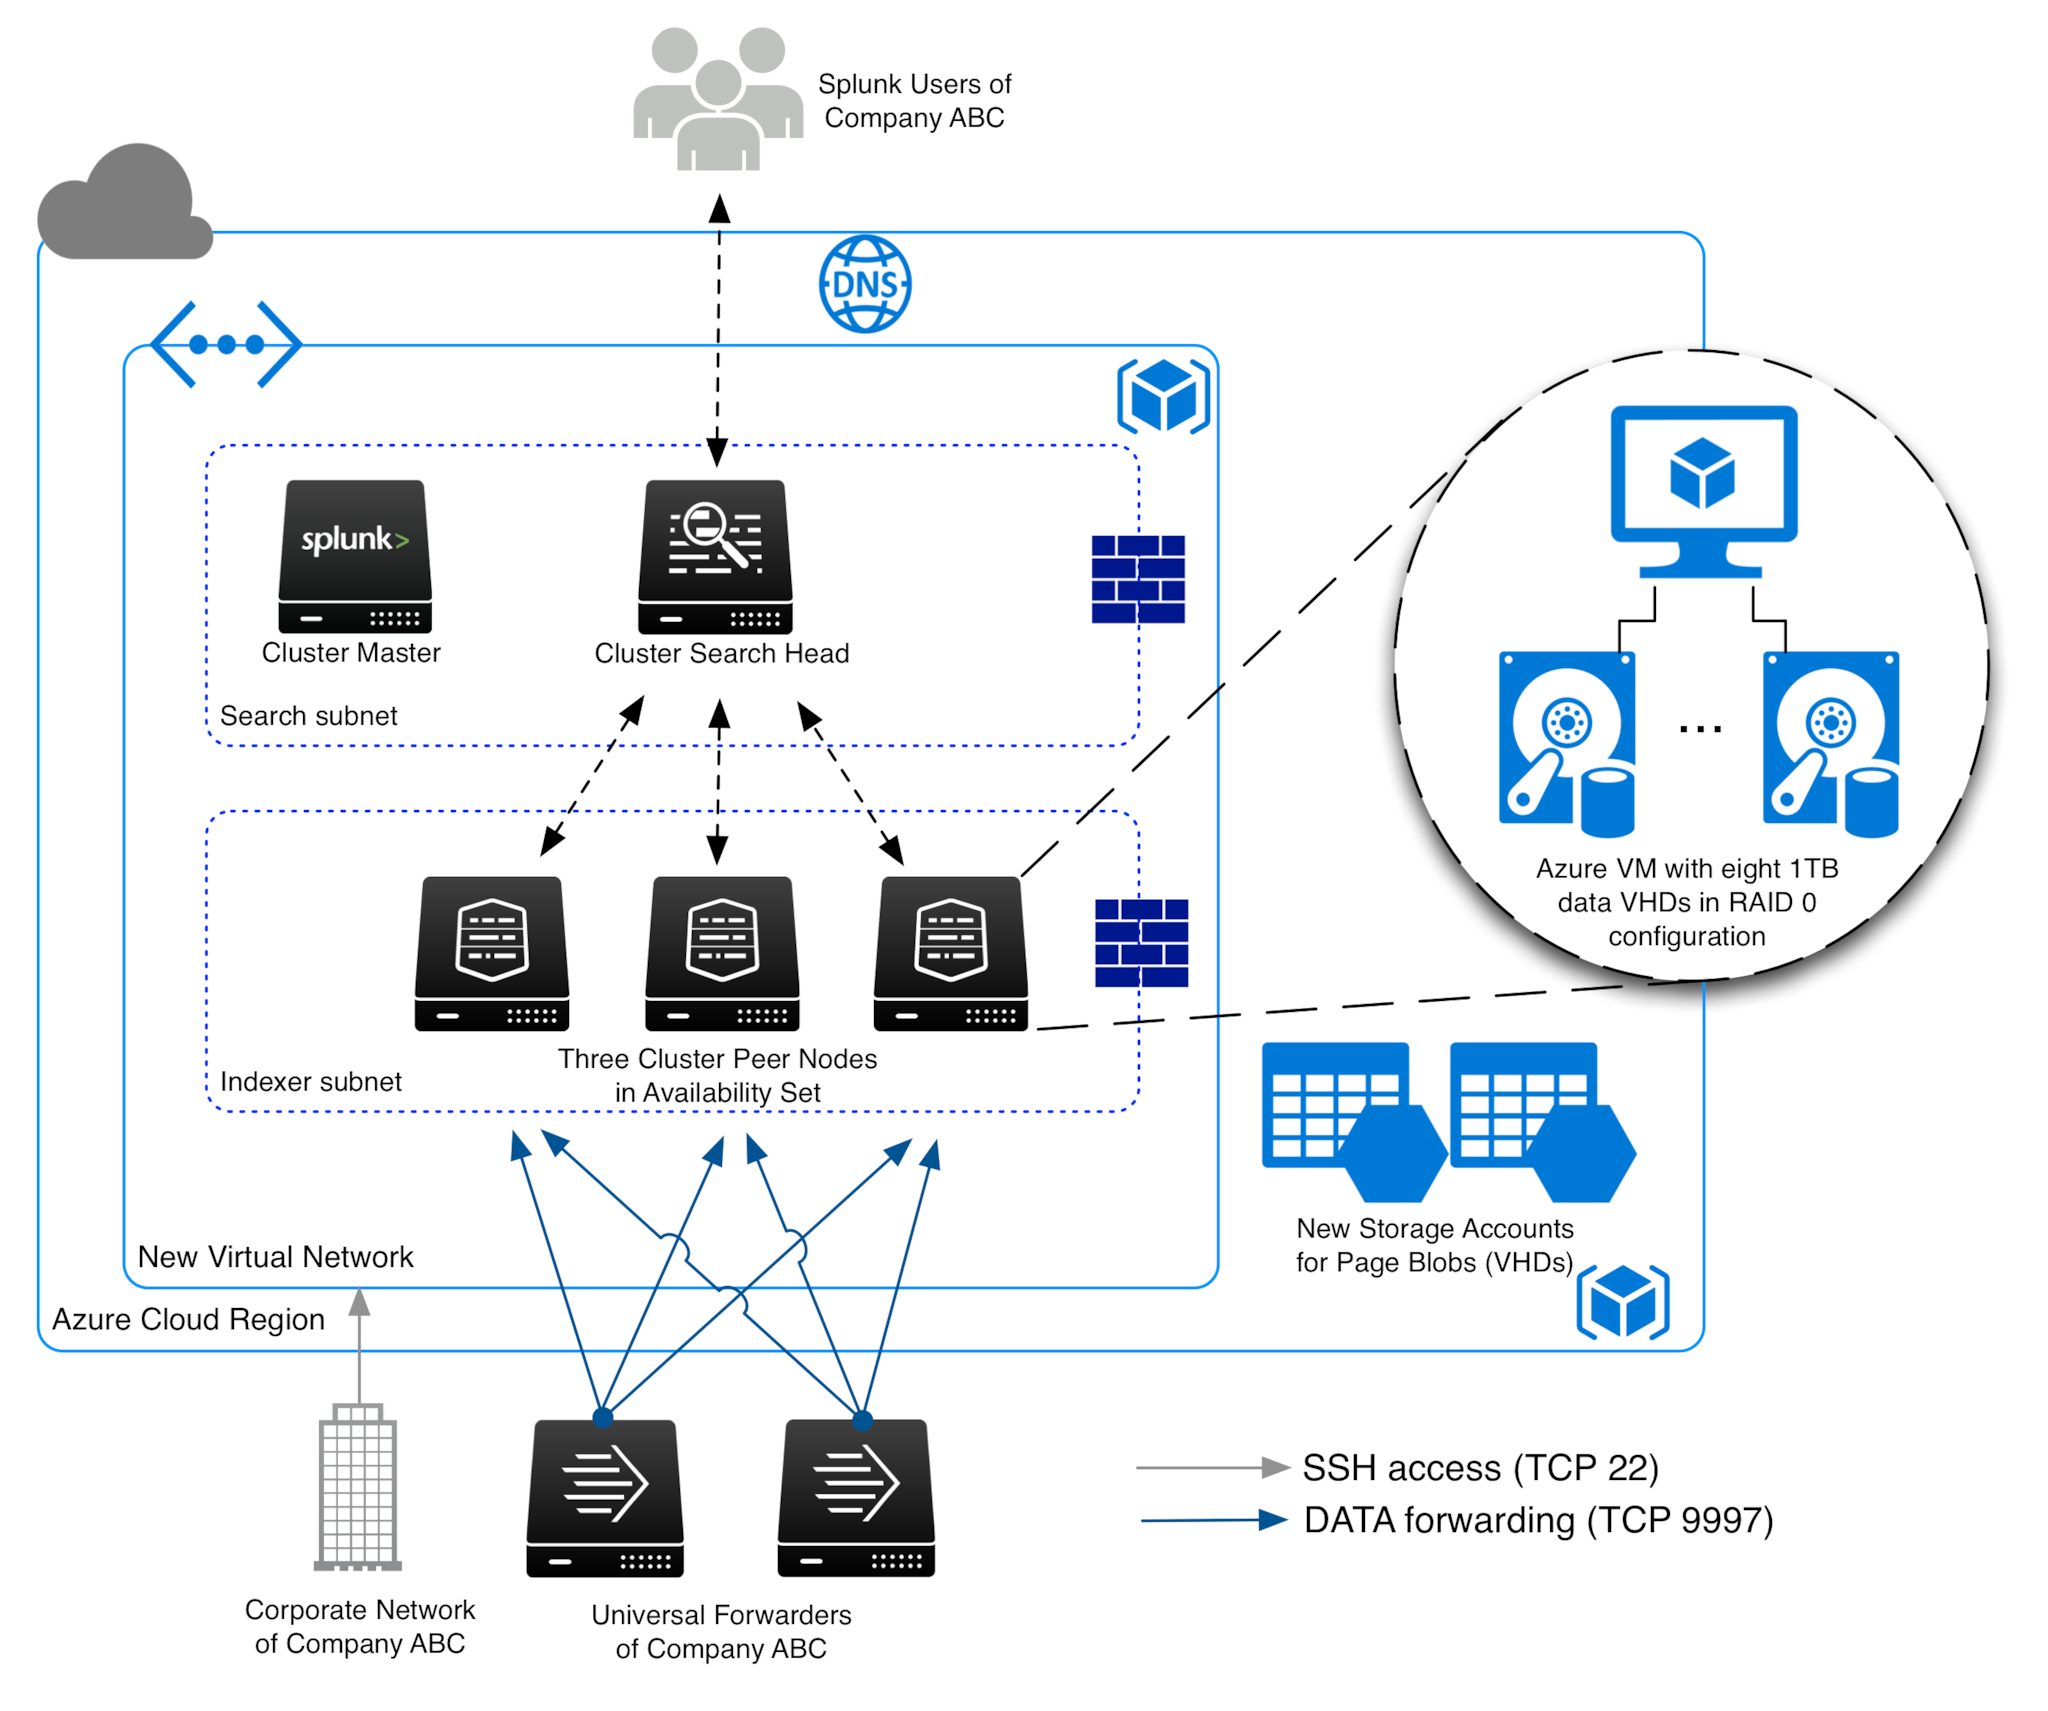
Deploying Splunk Enterprise On Microsoft Azure | PDF | Cloud Computing ...
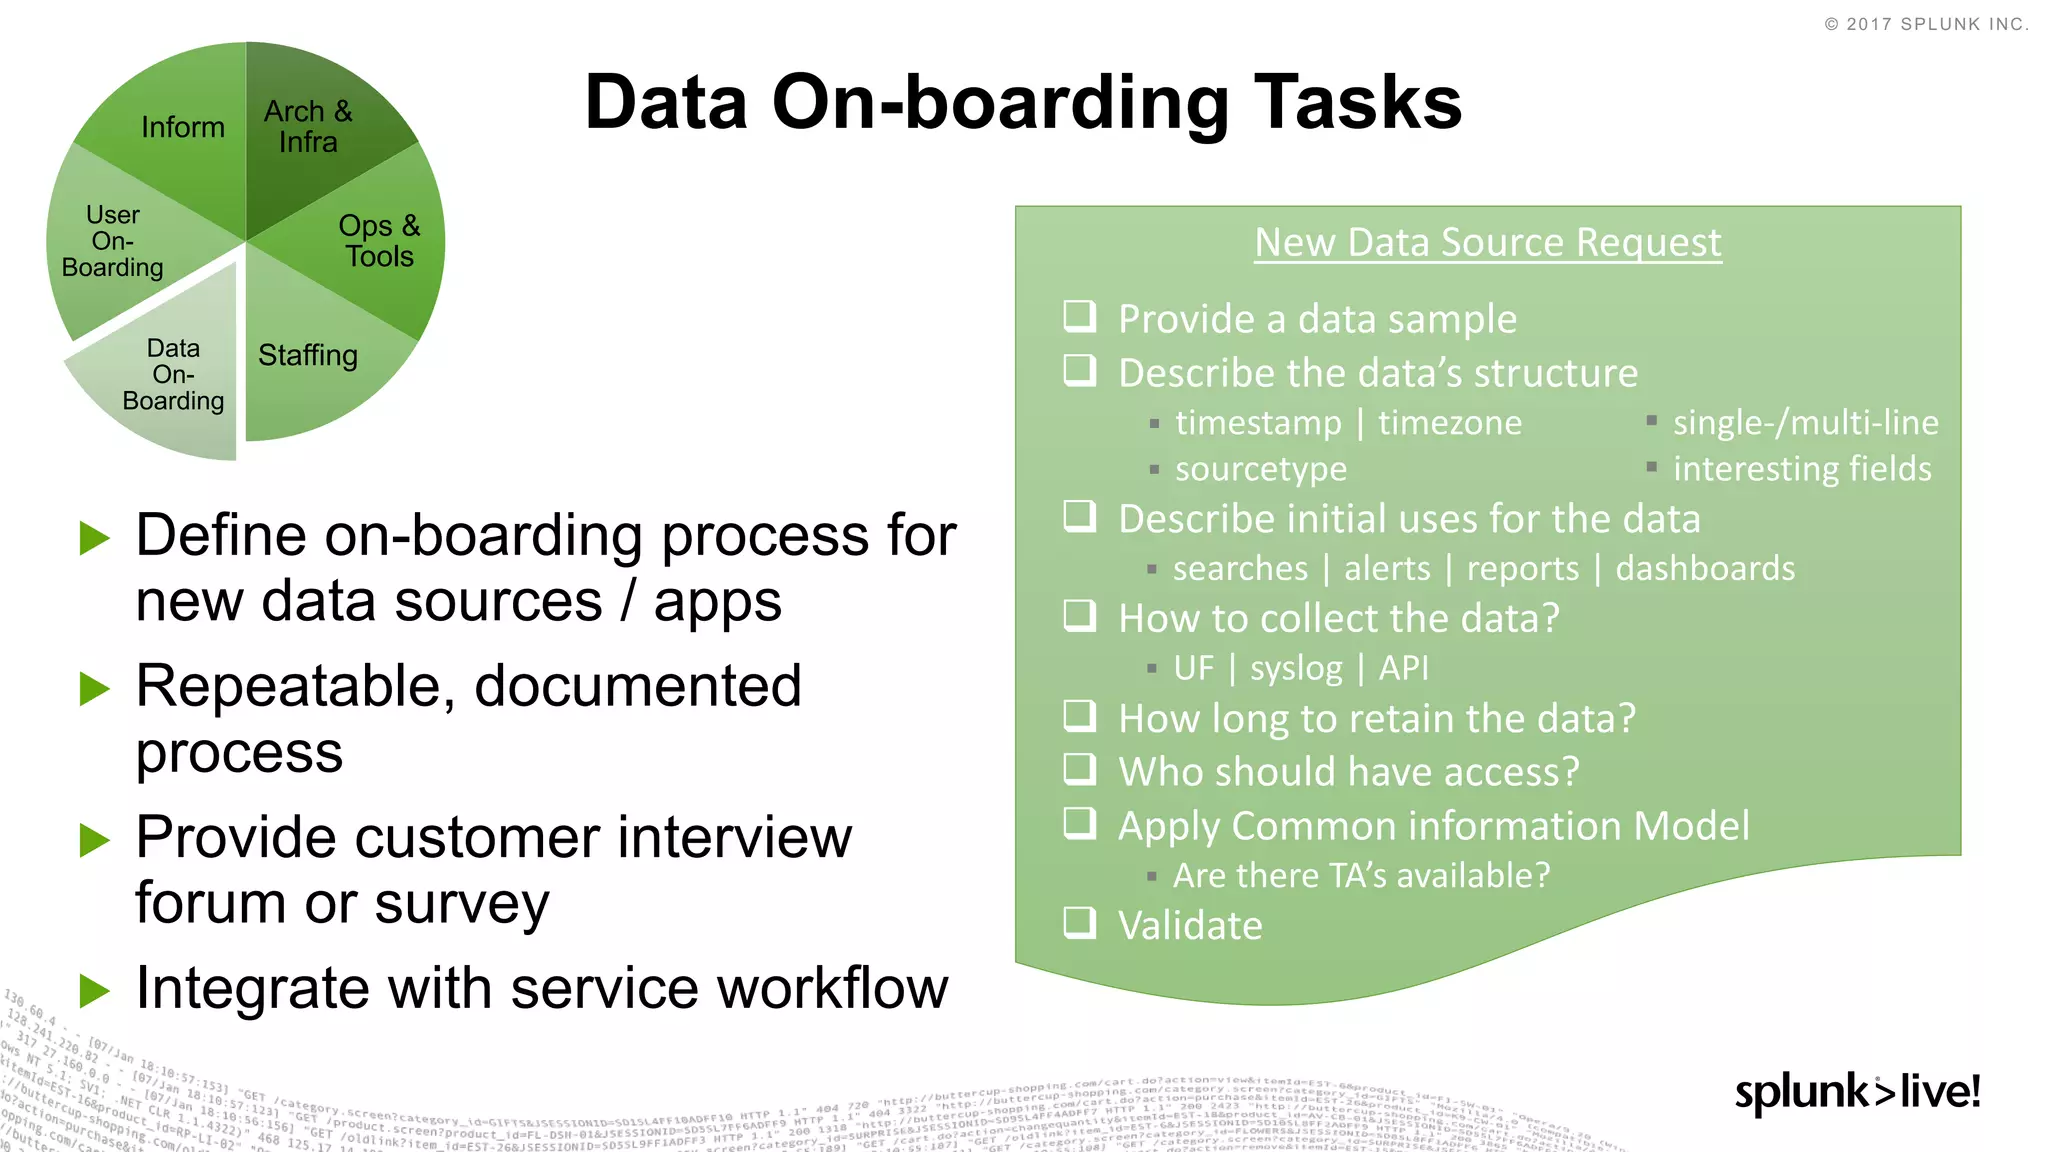
Getting Data into Splunk | PPT
Splunking Microsoft Azure Monitor Data – Part 1 – Azure Setup | Splunk
Get Azure Key Vault Data into Splunk | Pwntario Team Blog
The Splunk console's Azure integration for AKS Cluster incorrectly ...
Splunking Microsoft Azure Data | Splunk
Microsoft Azure Splunk _ Splunk Azure Add On – VMFWYG
Microsoft Azure App for Splunk | Splunkbase
From Setup to Migration: Azure Event Hubs in Data Manager | Splunk
Use Forwarders To Get Data Into Splunk Enterprise – KHMQGY
Splunk Now Generally Available on Microsoft Azure | Splunk
To collect AD azure logs to splunk - Avotrix
Driving value on Microsoft Azure | Splunk
GitHub - splunk/splunk-add-on-microsoft-azure: Splunk Add-on for ...
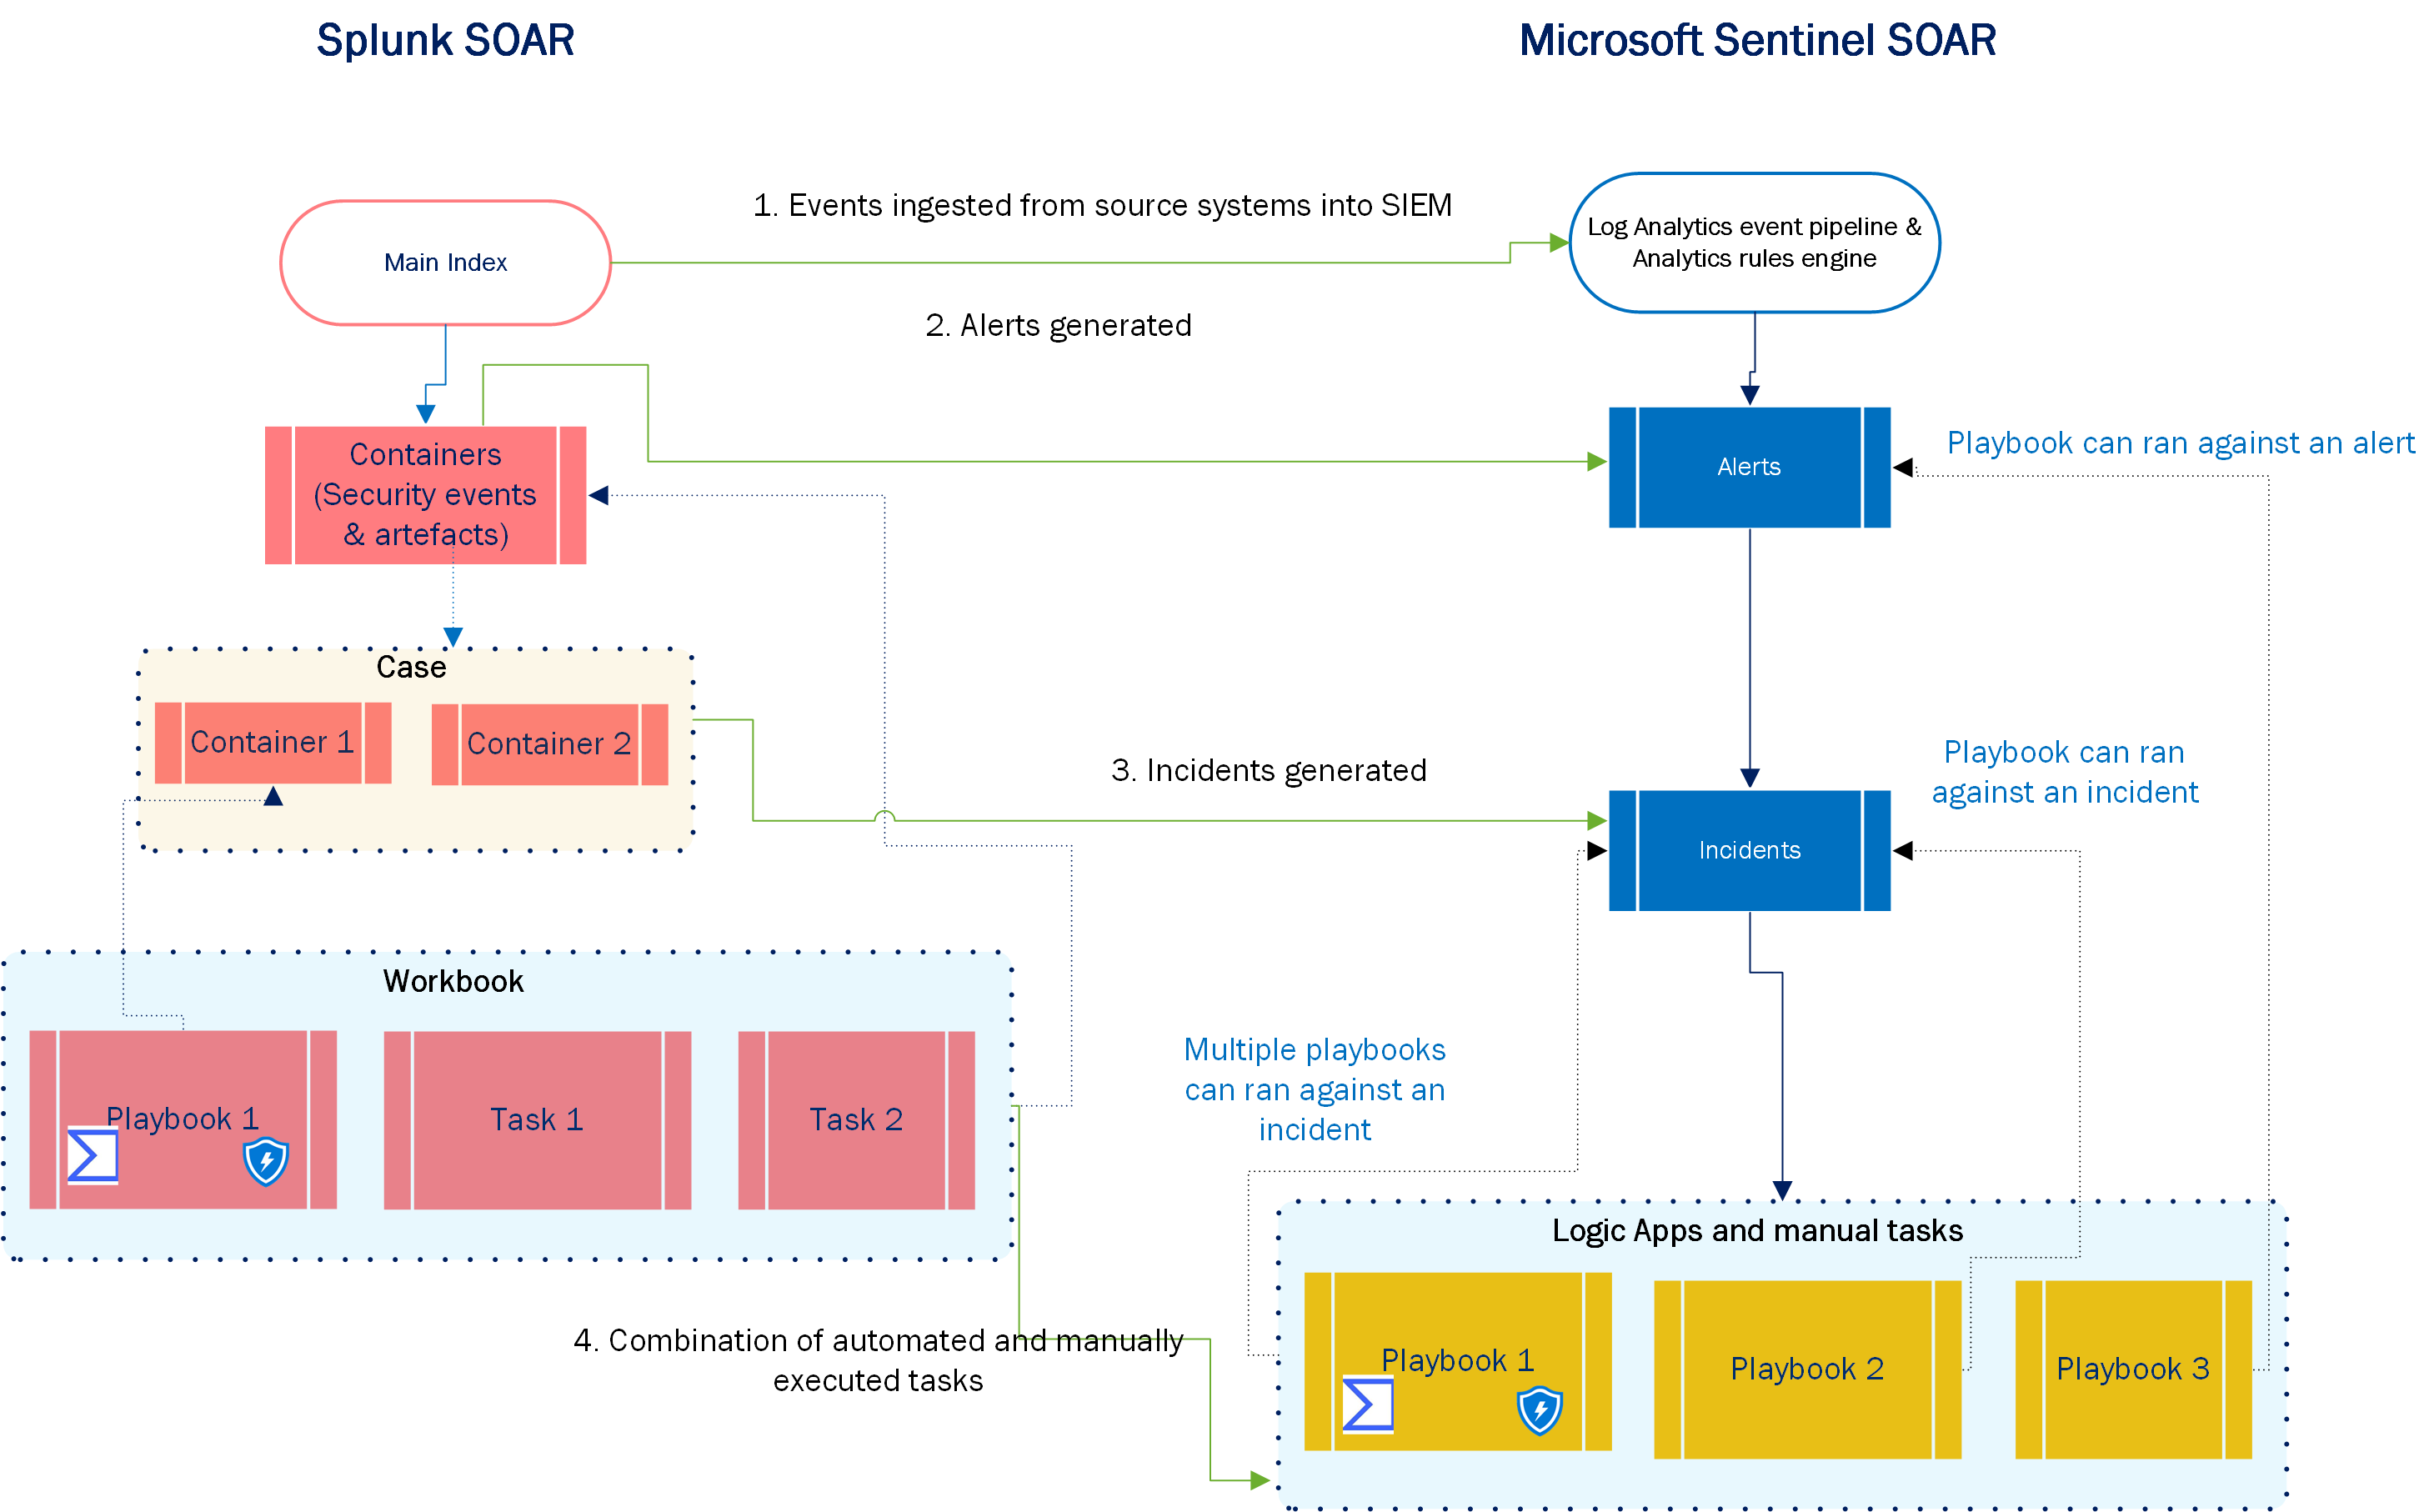
Migrate Splunk SOAR automation to Microsoft Sentinel | Azure Docs
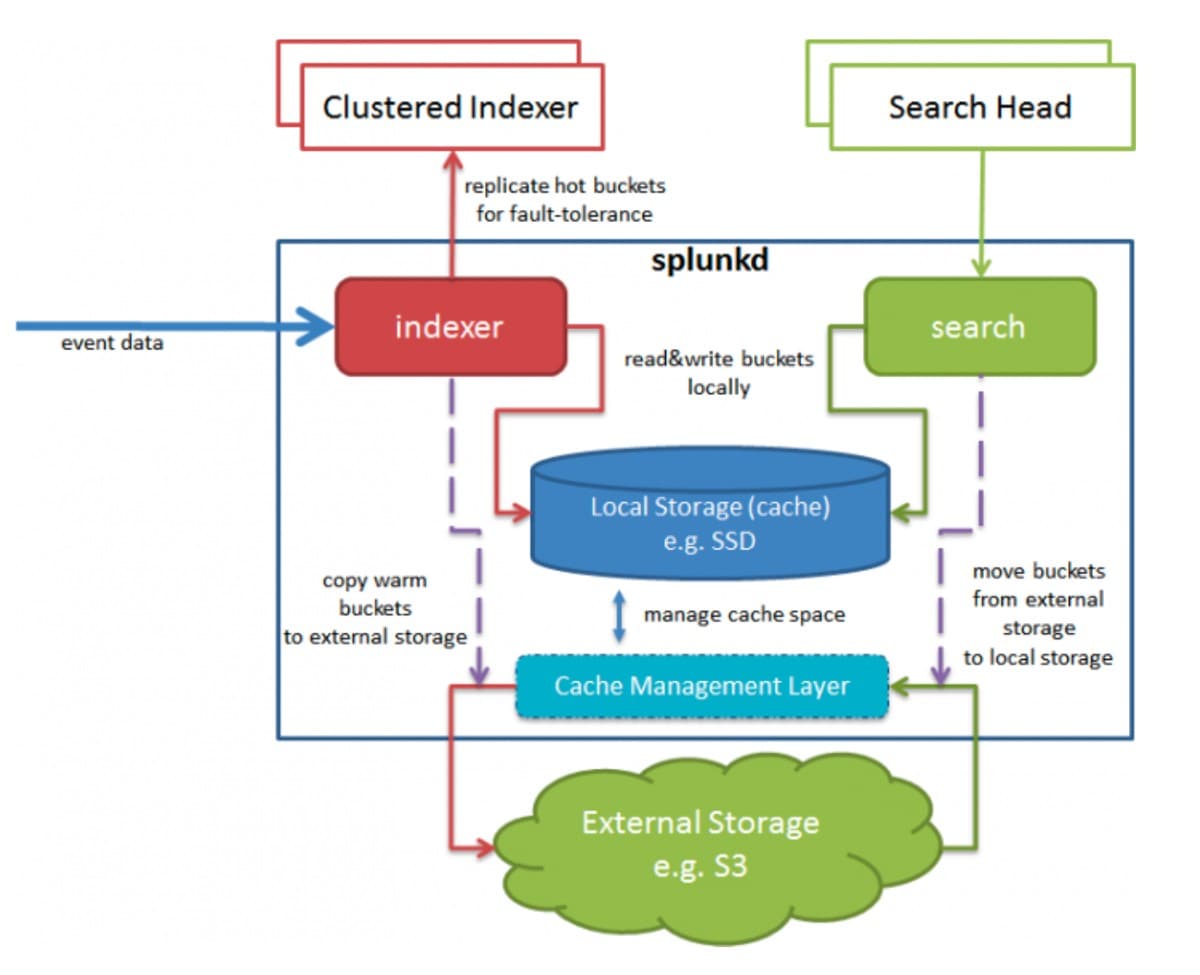
Splunk 9.0 SmartStore with Microsoft Azure Container Storage | Splunk
Microsoft Azure Monitoring Solutions | Splunk
Announcing Splunk Enterprise in Microsoft Azure Marketplace
Splunk collaborates with Microsoft to Advance Digital Resilience ...
Tuto Startup - Harness the power of AI and ML using Splunk and Amazon SageM
Ingest Data From Splunk To Azure Data Explorer – HARO
Getting Started with Splunk Cloud Platform | Splunk
GitHub - Azure/splunk-enterprise: Guidance on deploying Splunk ...
Microsoft AzureのデータをSplunkに取り込む | Splunk
azure splunk 連携 – splunk クエリ – GZIYH
Splunking Microsoft Cloud Data: Part 2 | Splunk
Splunk Cloud Platform | Splunk
Splunk Data Onboarding Template – AJRUZ
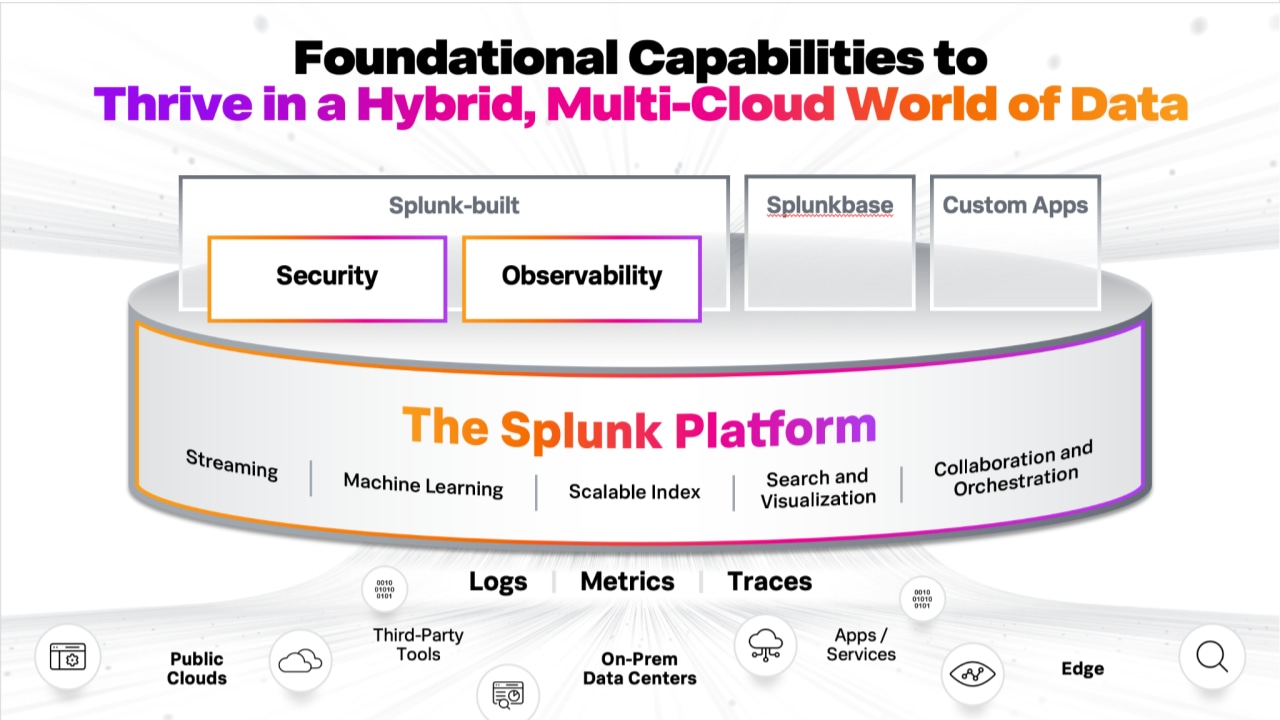
Splunk Platform: Innovation to Thrive in a Hybrid, Multi-Cloud World of ...
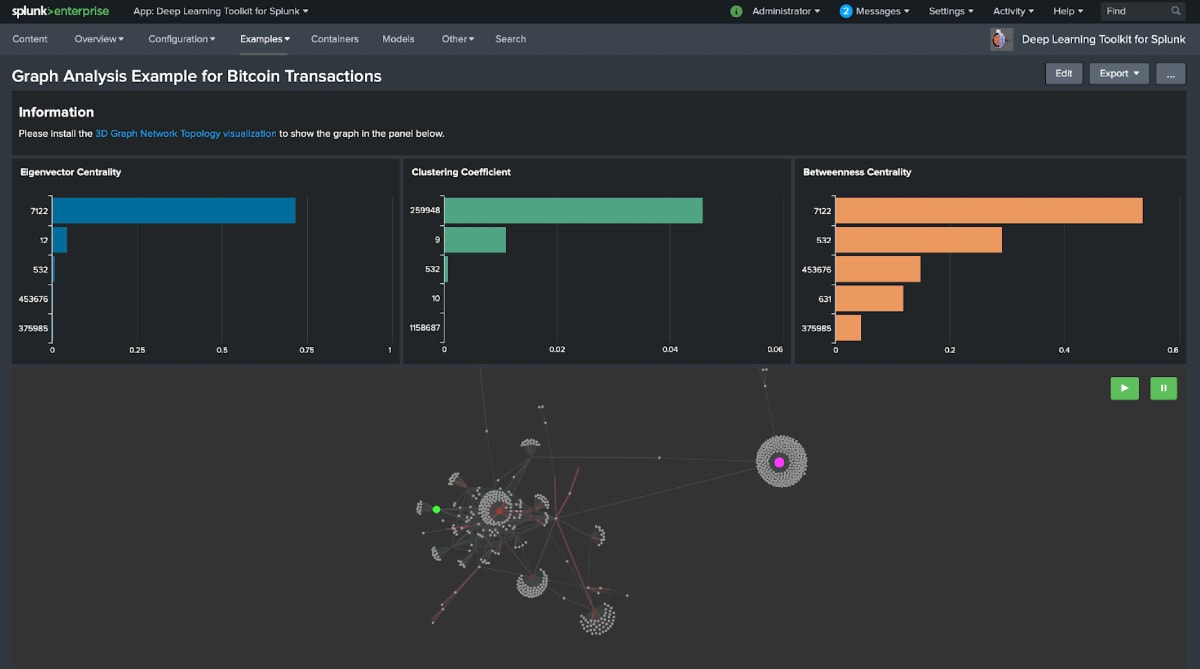
Getting Started with Machine Learning at Splunk | Splunk
Splunk - An Overview
Splunk Enterprise Security and Observability - SHI India (Formerly Locuz)
Query Splunk with Azure Automation + Logic App – SC Joe
Customer Success Story: How this enterprise used Splunk to investigate ...
Microsoft 365 App for Splunk | Splunkbase
HTTP app and Graph/Azure - Splunk Community
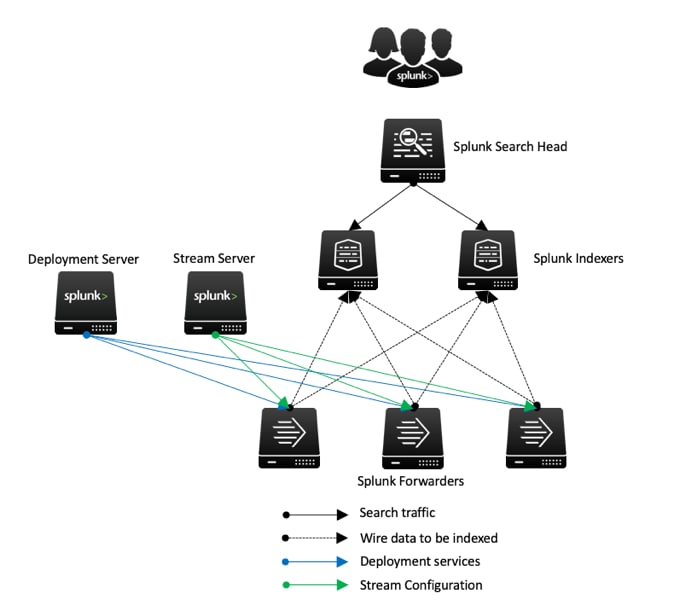
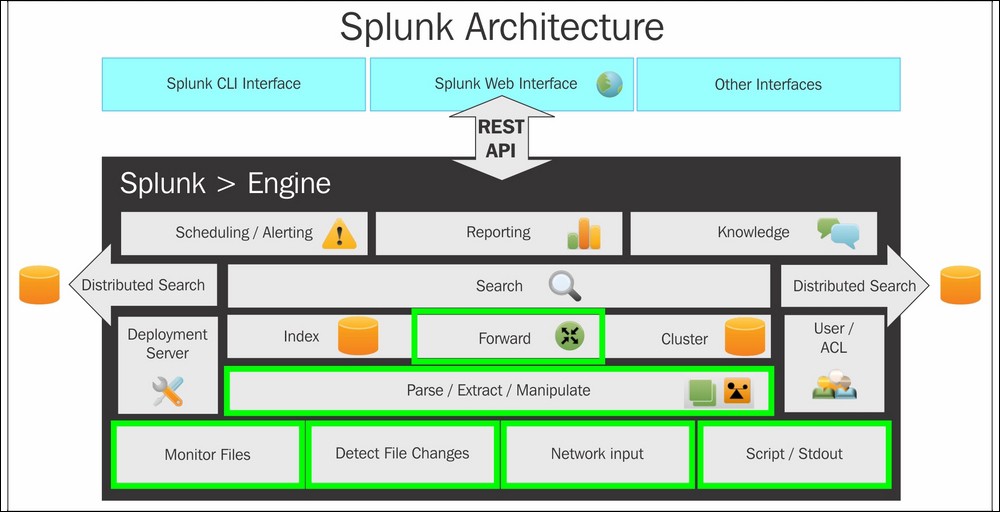
Splunk architecture
Dynamic Data:Splunk Cloud Platformのデータ保持オプション | Splunk
Splunk: Architectures Of Splunk – YKFGZG
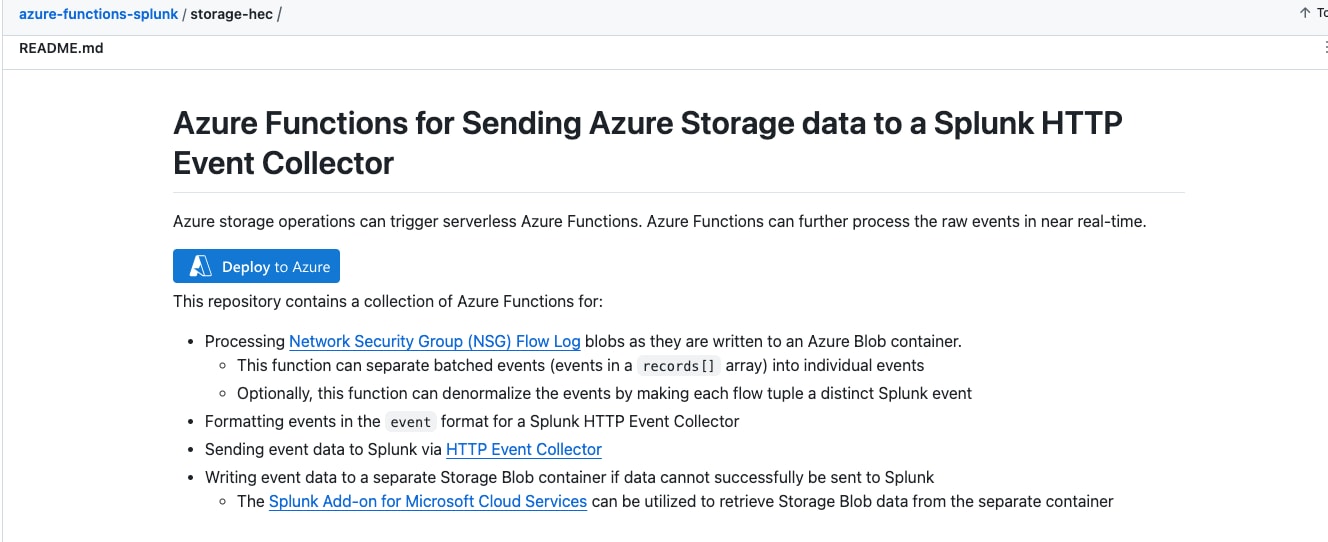
Splunking Azure: NSG Flow Logs | Splunk
Splunk® Enterprise Getting Data In
Office 365 Splunk Integration – Splunk Office 365 Download – TSXD
What is Splunk Virtual Compute (SVC)? | Splunk
Splunk Enterprise: Architecture, Features, And Capabilities – IWZX
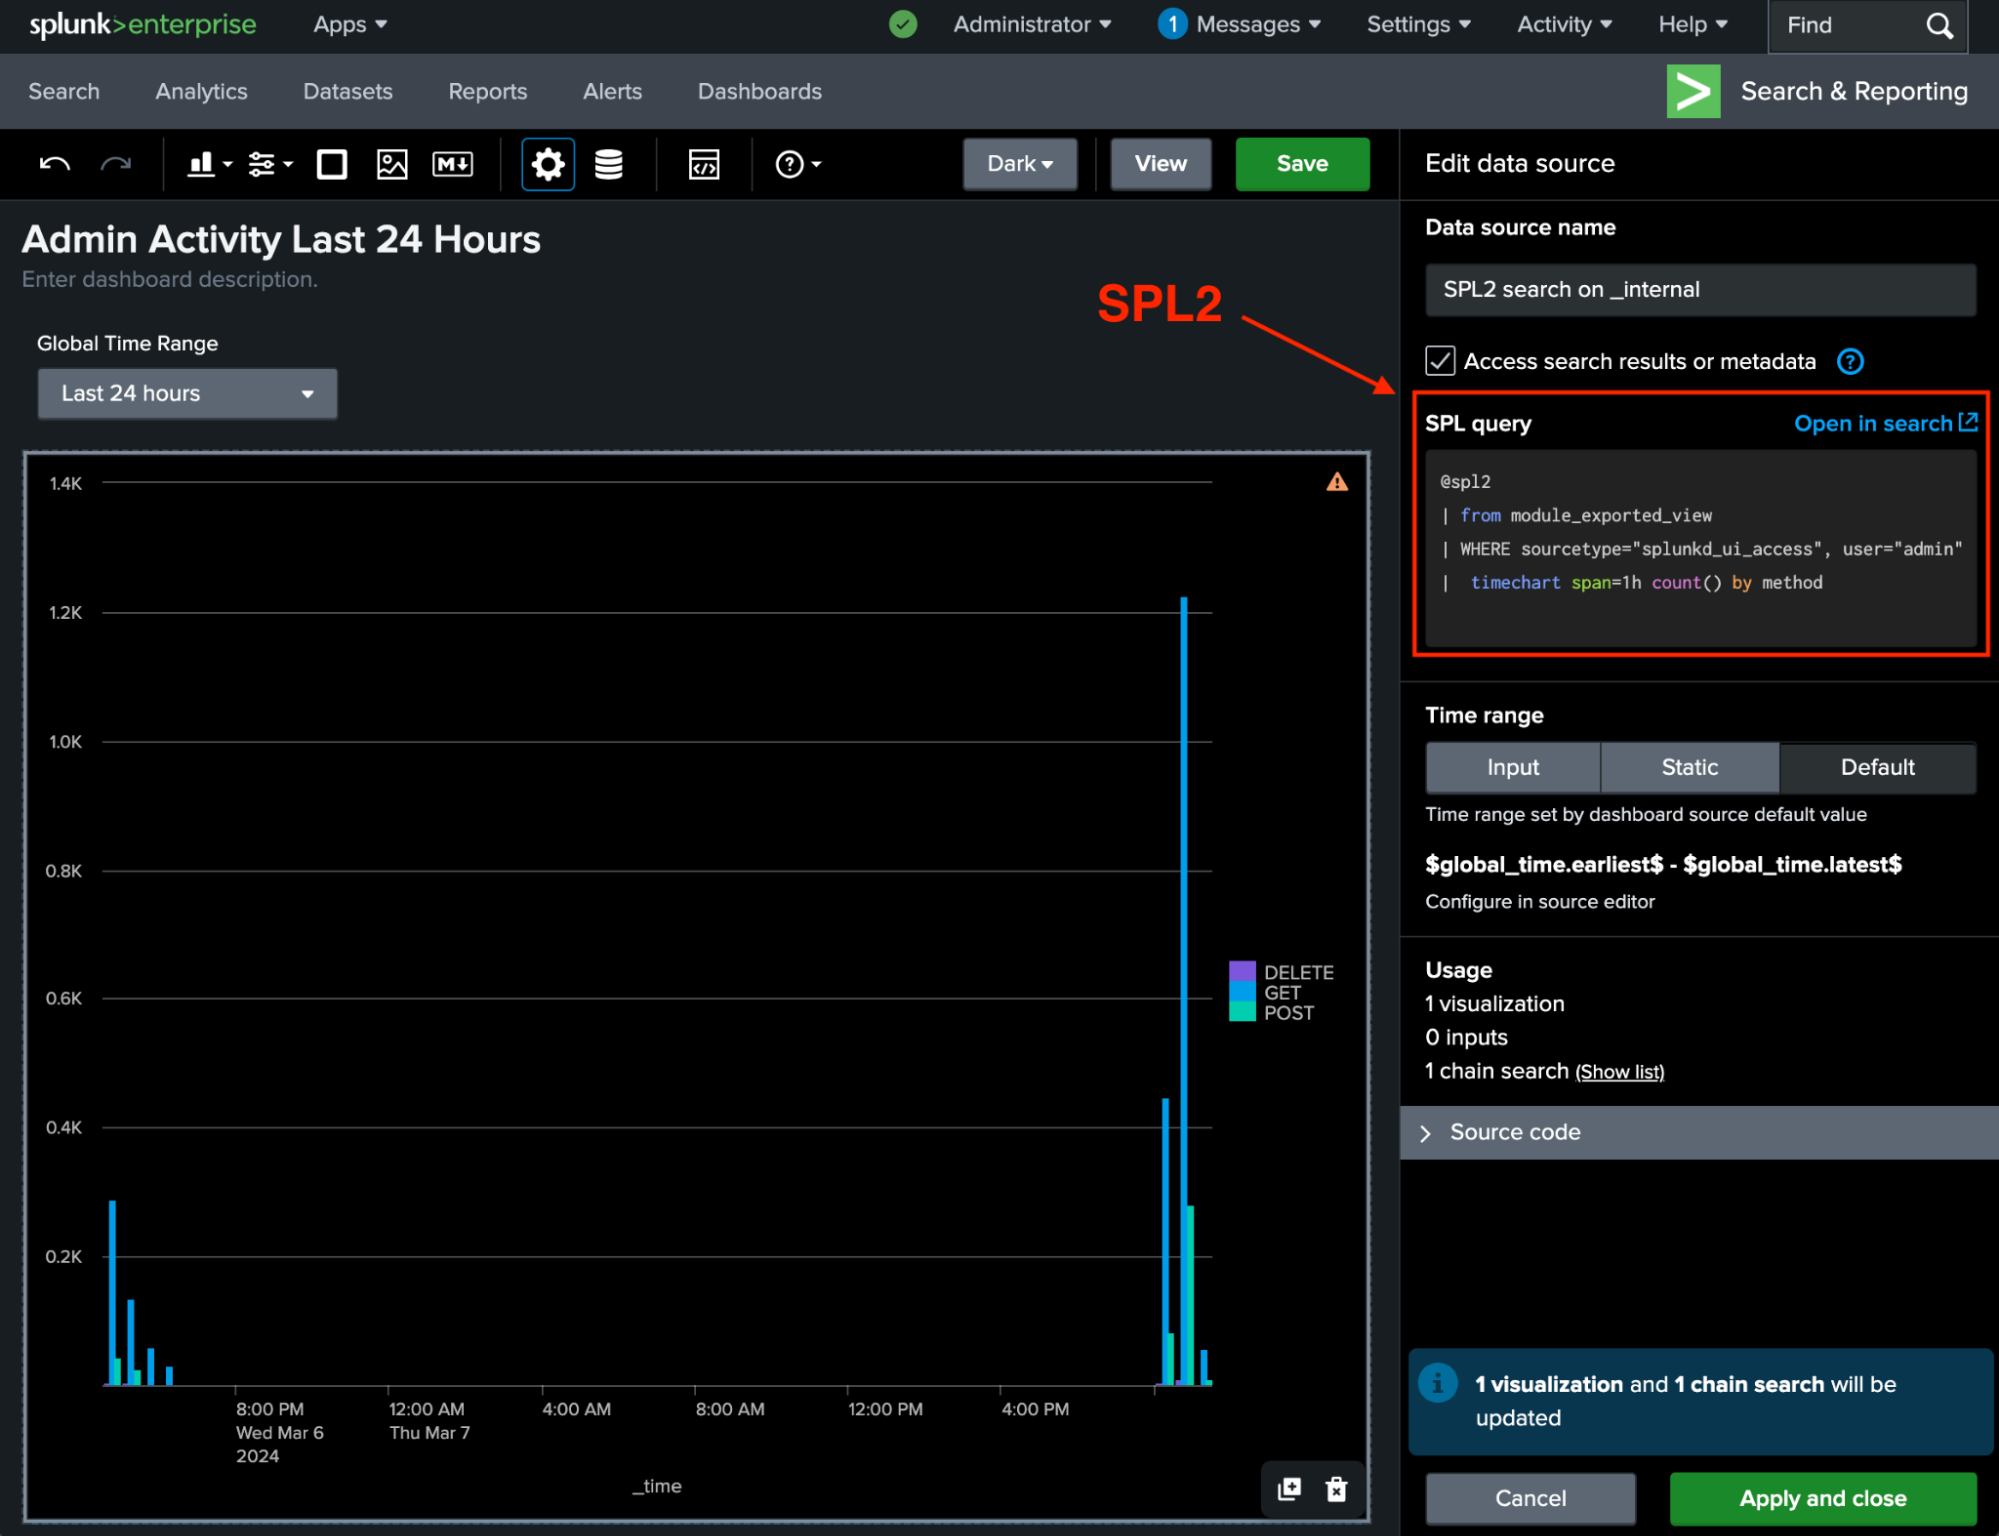
15. Introduction To Splunk & SPL | Exploit. Learn. Secure.
Splunking Azure: Event Hubs | Splunk
Entra ID: Azure→Splunk Log Pipeline using Azure Event Hub
mensfa - Blog
25 Azure Monitoring Tools To Consider For Cloud Optimization
Splunking Your *.conf Files: How to Track Configuration Changes Like a ...
Splunk, Azure, or Sentinel for FedRAMP/NIST Compliance
Starting with Splunk: A Comprehensive Guide for Beginners
Based on this image's title: “Getting Microsoft Azure data into the Splunk platform - Splunk ...”