Showing 120 of 120on this page. Filters & sort apply to loaded results; URL updates for sharing.120 of 120 on this page
From Elasticsearch (ELK) to OpenObserve Streamlining Log Management
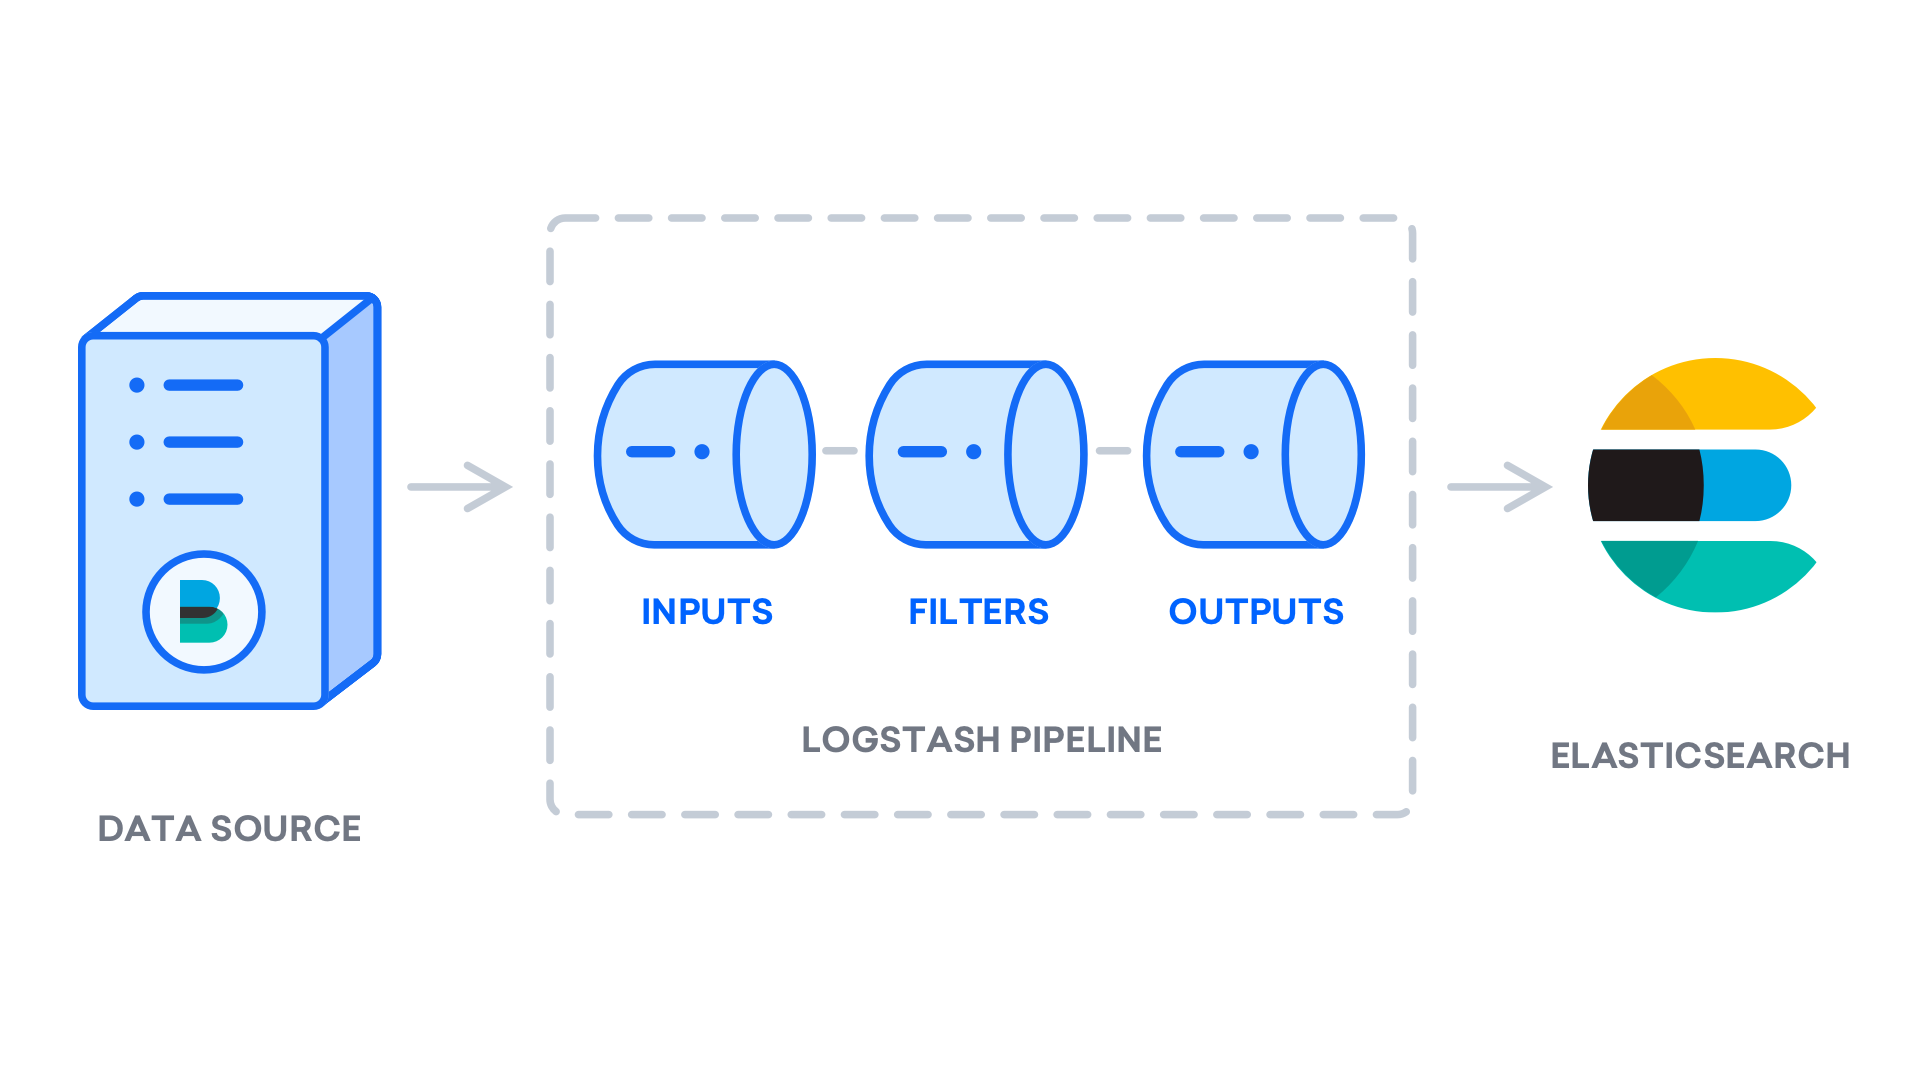
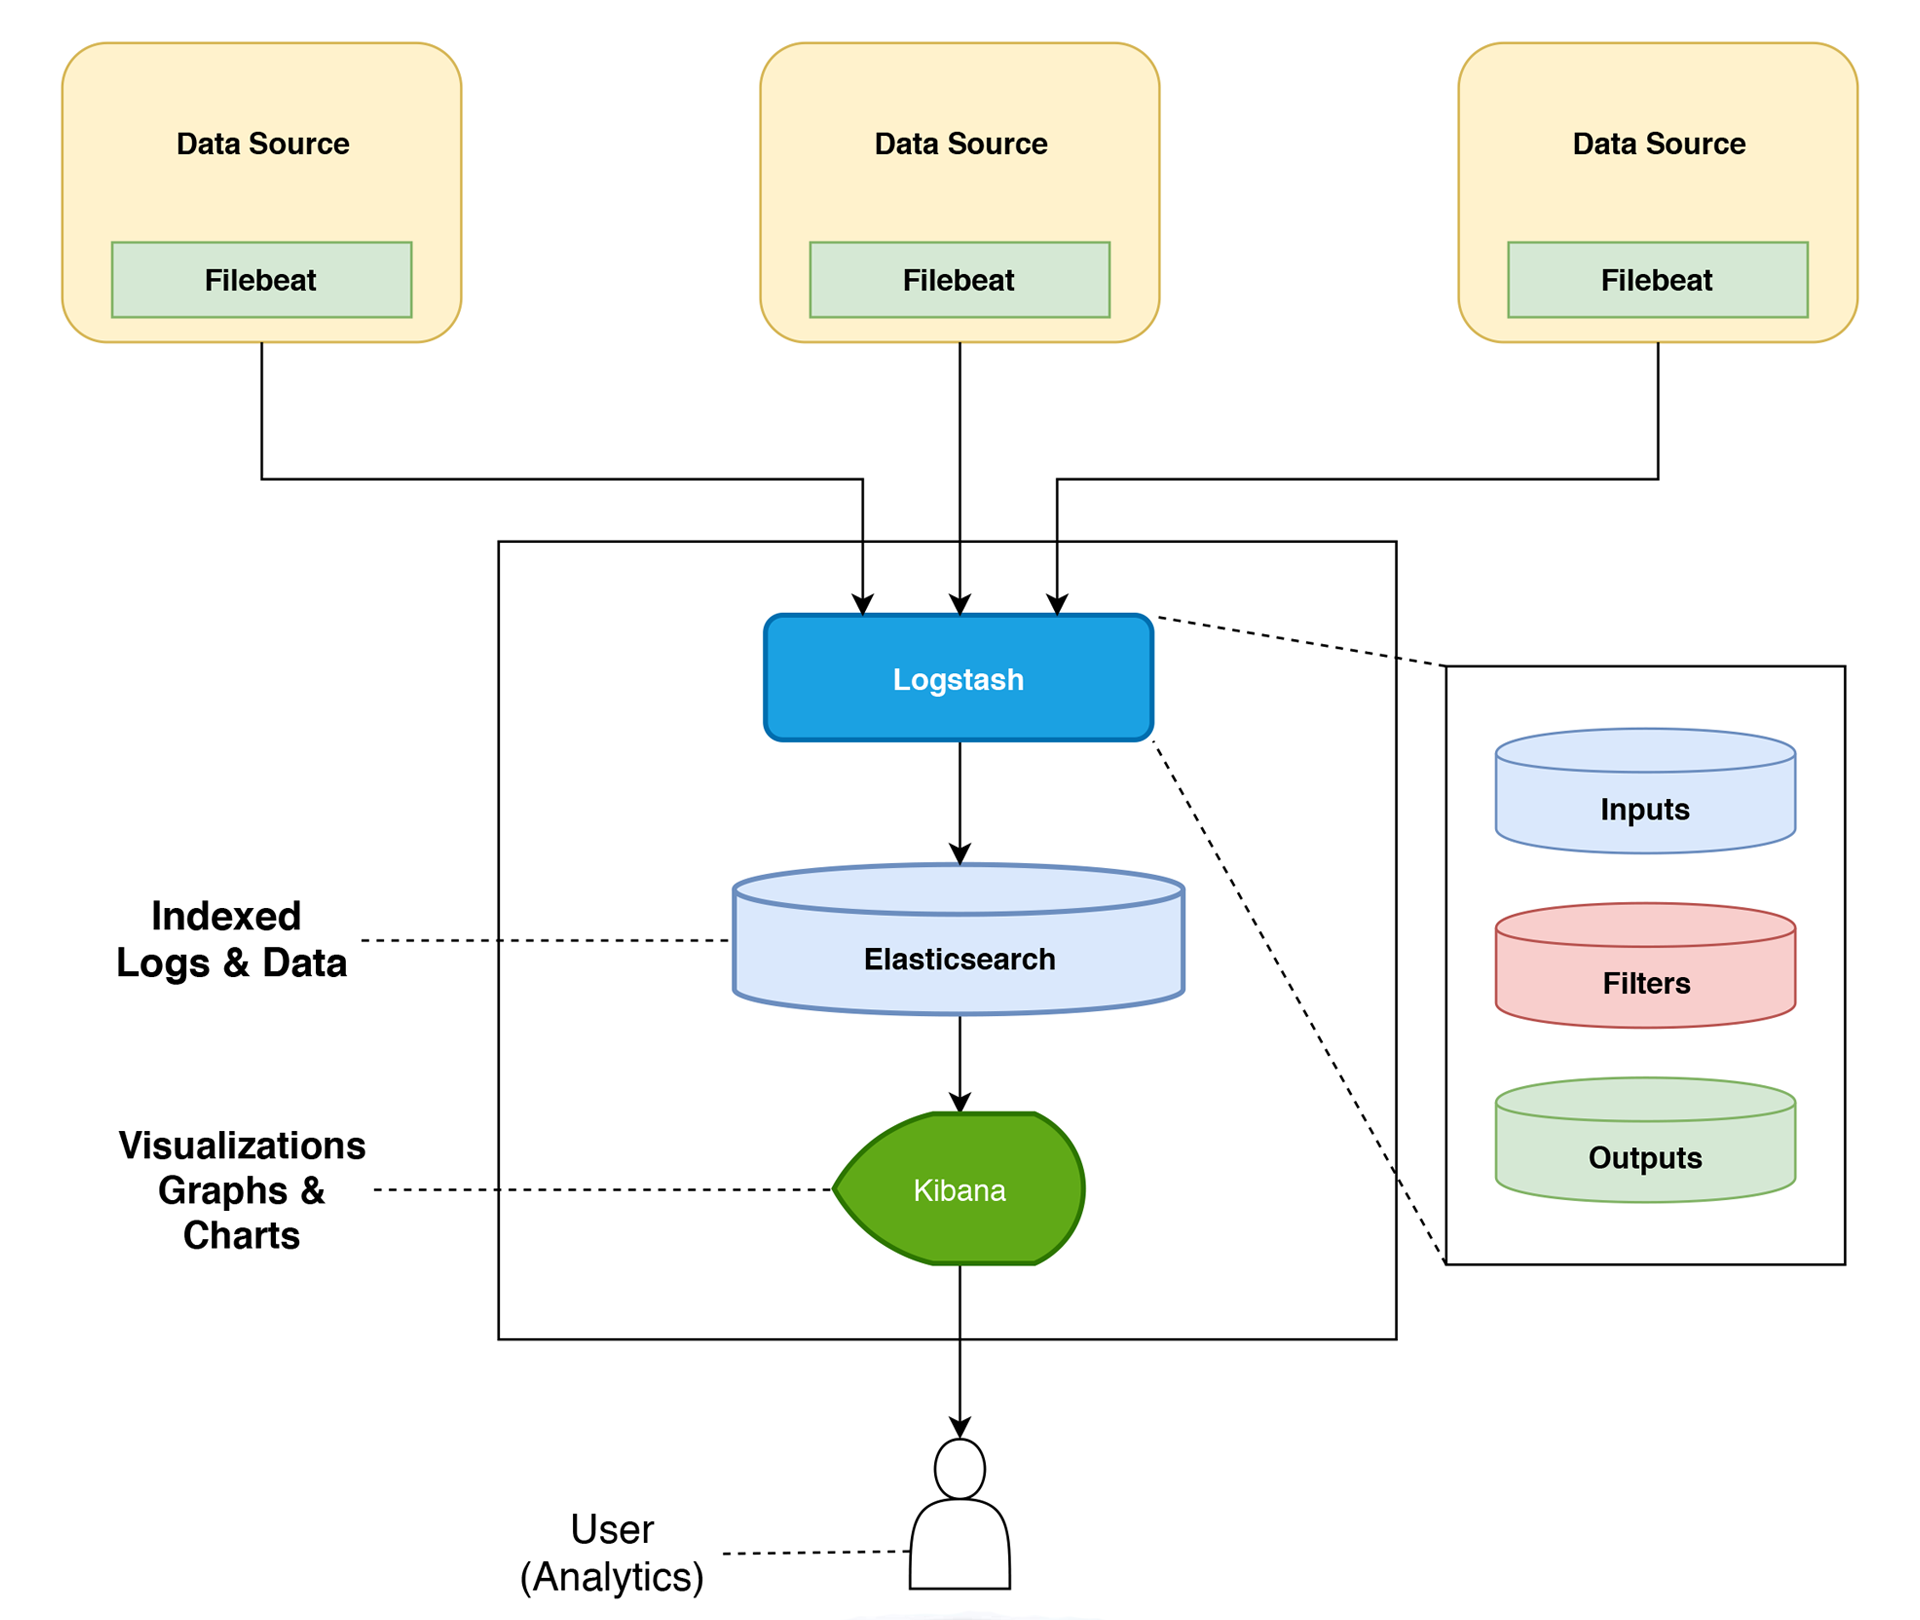
Streamlining Log Analysis with Logstash, Filebeat, and Elasticsearch
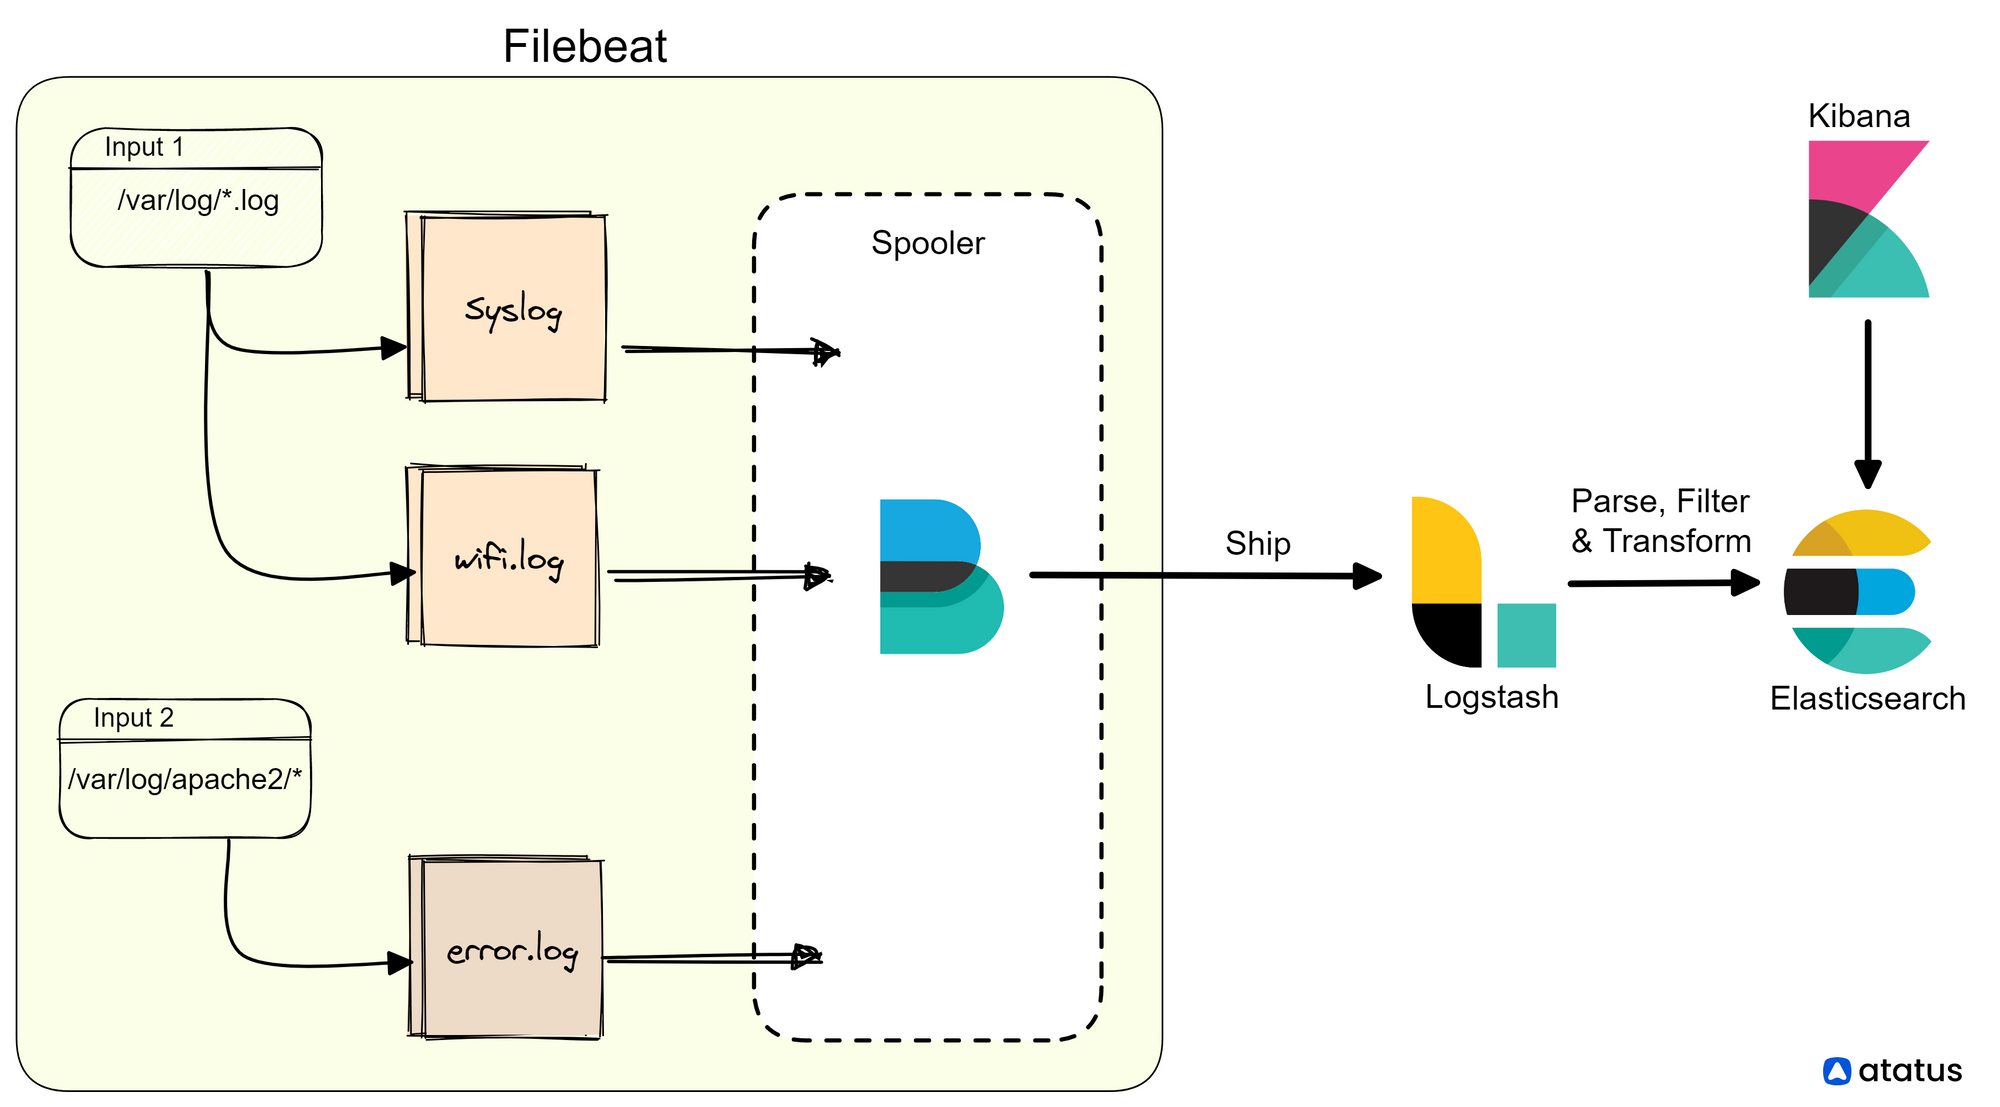
filebeat Linux: Complete Guide to Ship Log Files to Elasticsearch with ...
Elasticsearch Log Level , Logging settings in Kibana – SDQVM
Install the ELK log system for ElasticSearch - Moment For Technology
Using Elasticsearch for Log Search and Analysis | Elastic Videos
Log Shipping with Filebeat and Elasticsearch - Gigi Labs
Slow Ingestion of Final Log Chunks (Filebeat + Logstash + Elasticsearch ...
Chapter 6. Configuring action log storage for Elasticsearch and Splunk ...
Elasticsearch Log Management: Logstash, Filebeat & Kibana
ElasticSearch for Large-Scale Log Analytics - World 2 Data
Mastering Log Management: Installing and Deploying Elasticsearch ...
Elasticsearch Log Plug-In (2020.2.18 and later)
Giám sát log tối ưu với ELK - Elasticsearch Logstash Kibana - Tùng Huynh
Elasticsearch セキュリティ | Elasticsearch クエリとは – ZVSR
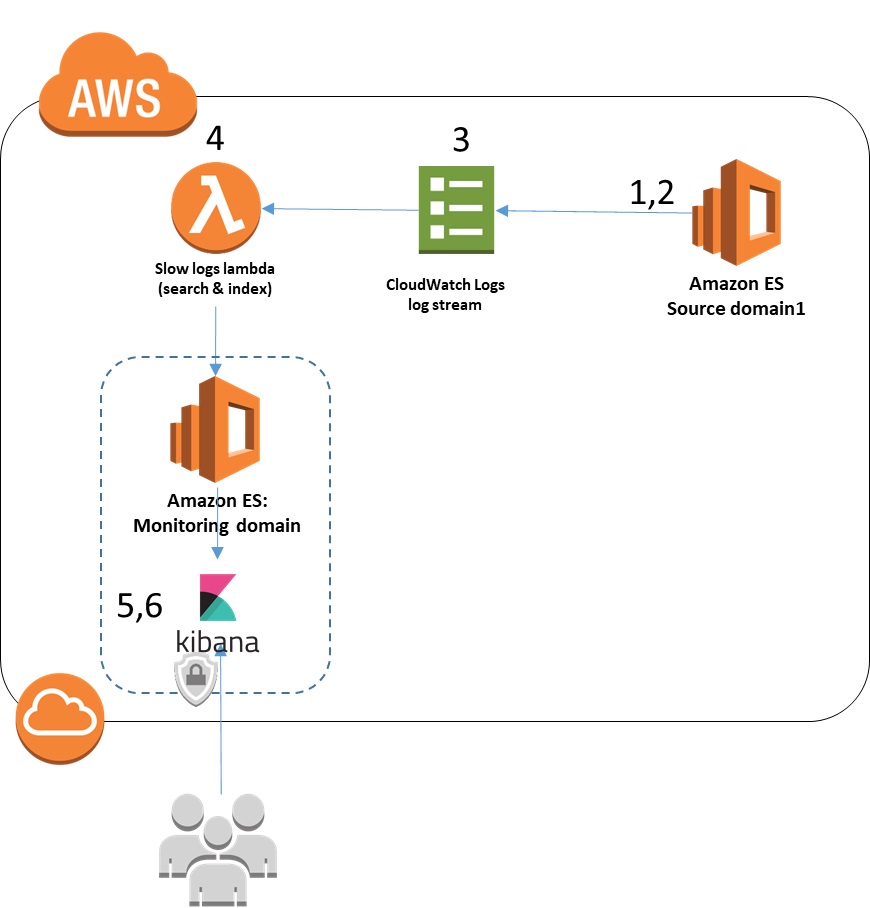
Slow Query Logging for Elasticsearch and Elastic Cloud
Ship logs to local Elasticsearch using Filebeat | by Mohamadou Abdoul ...
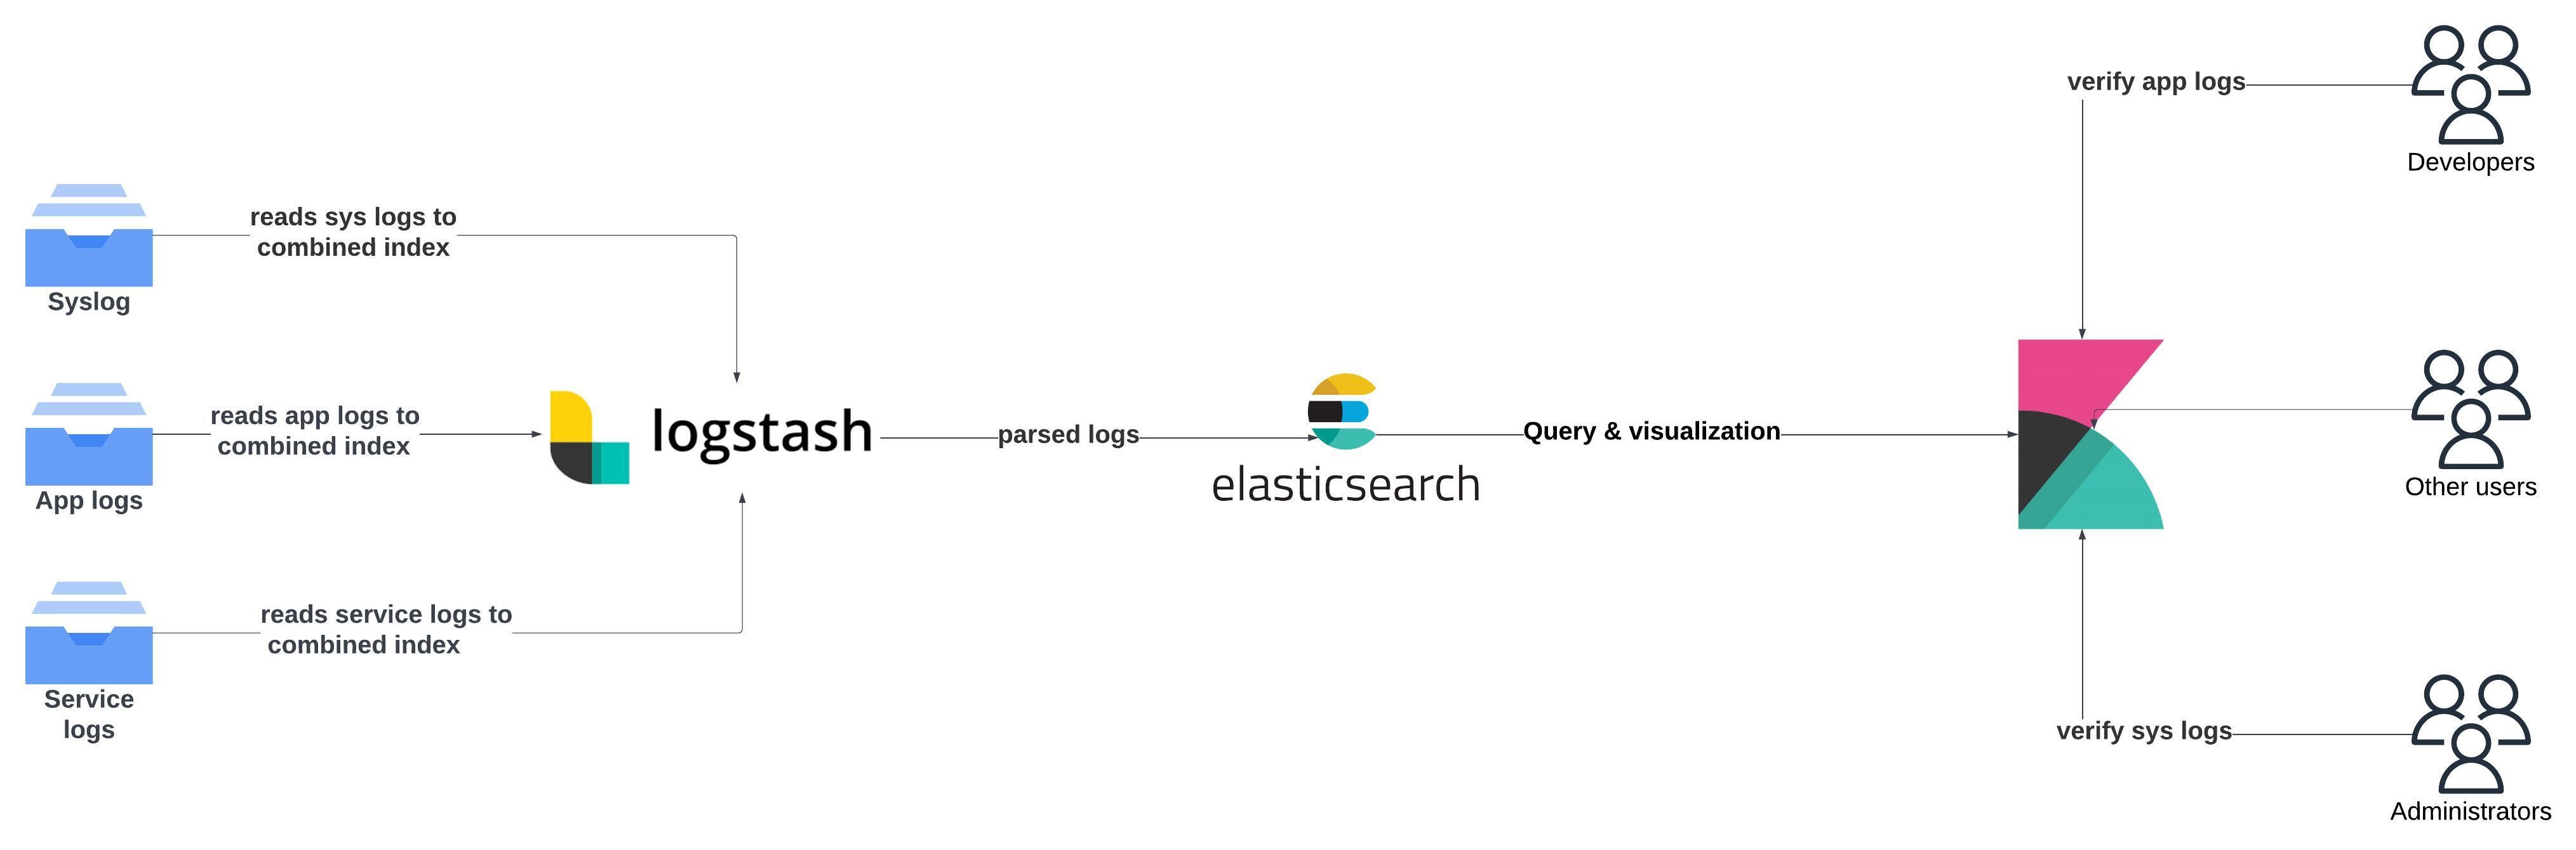
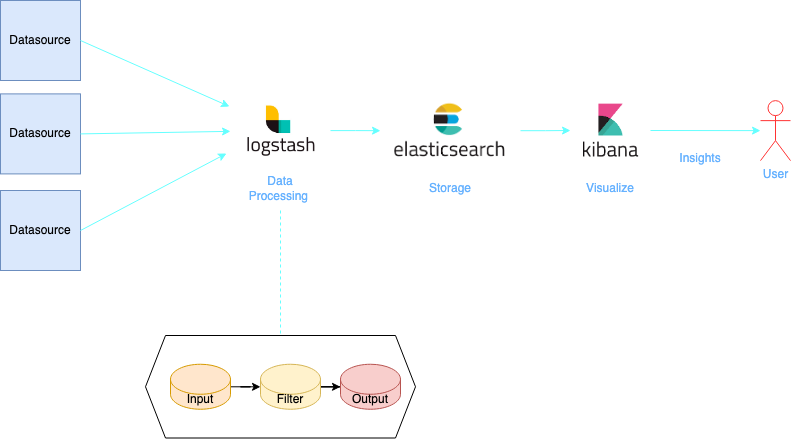
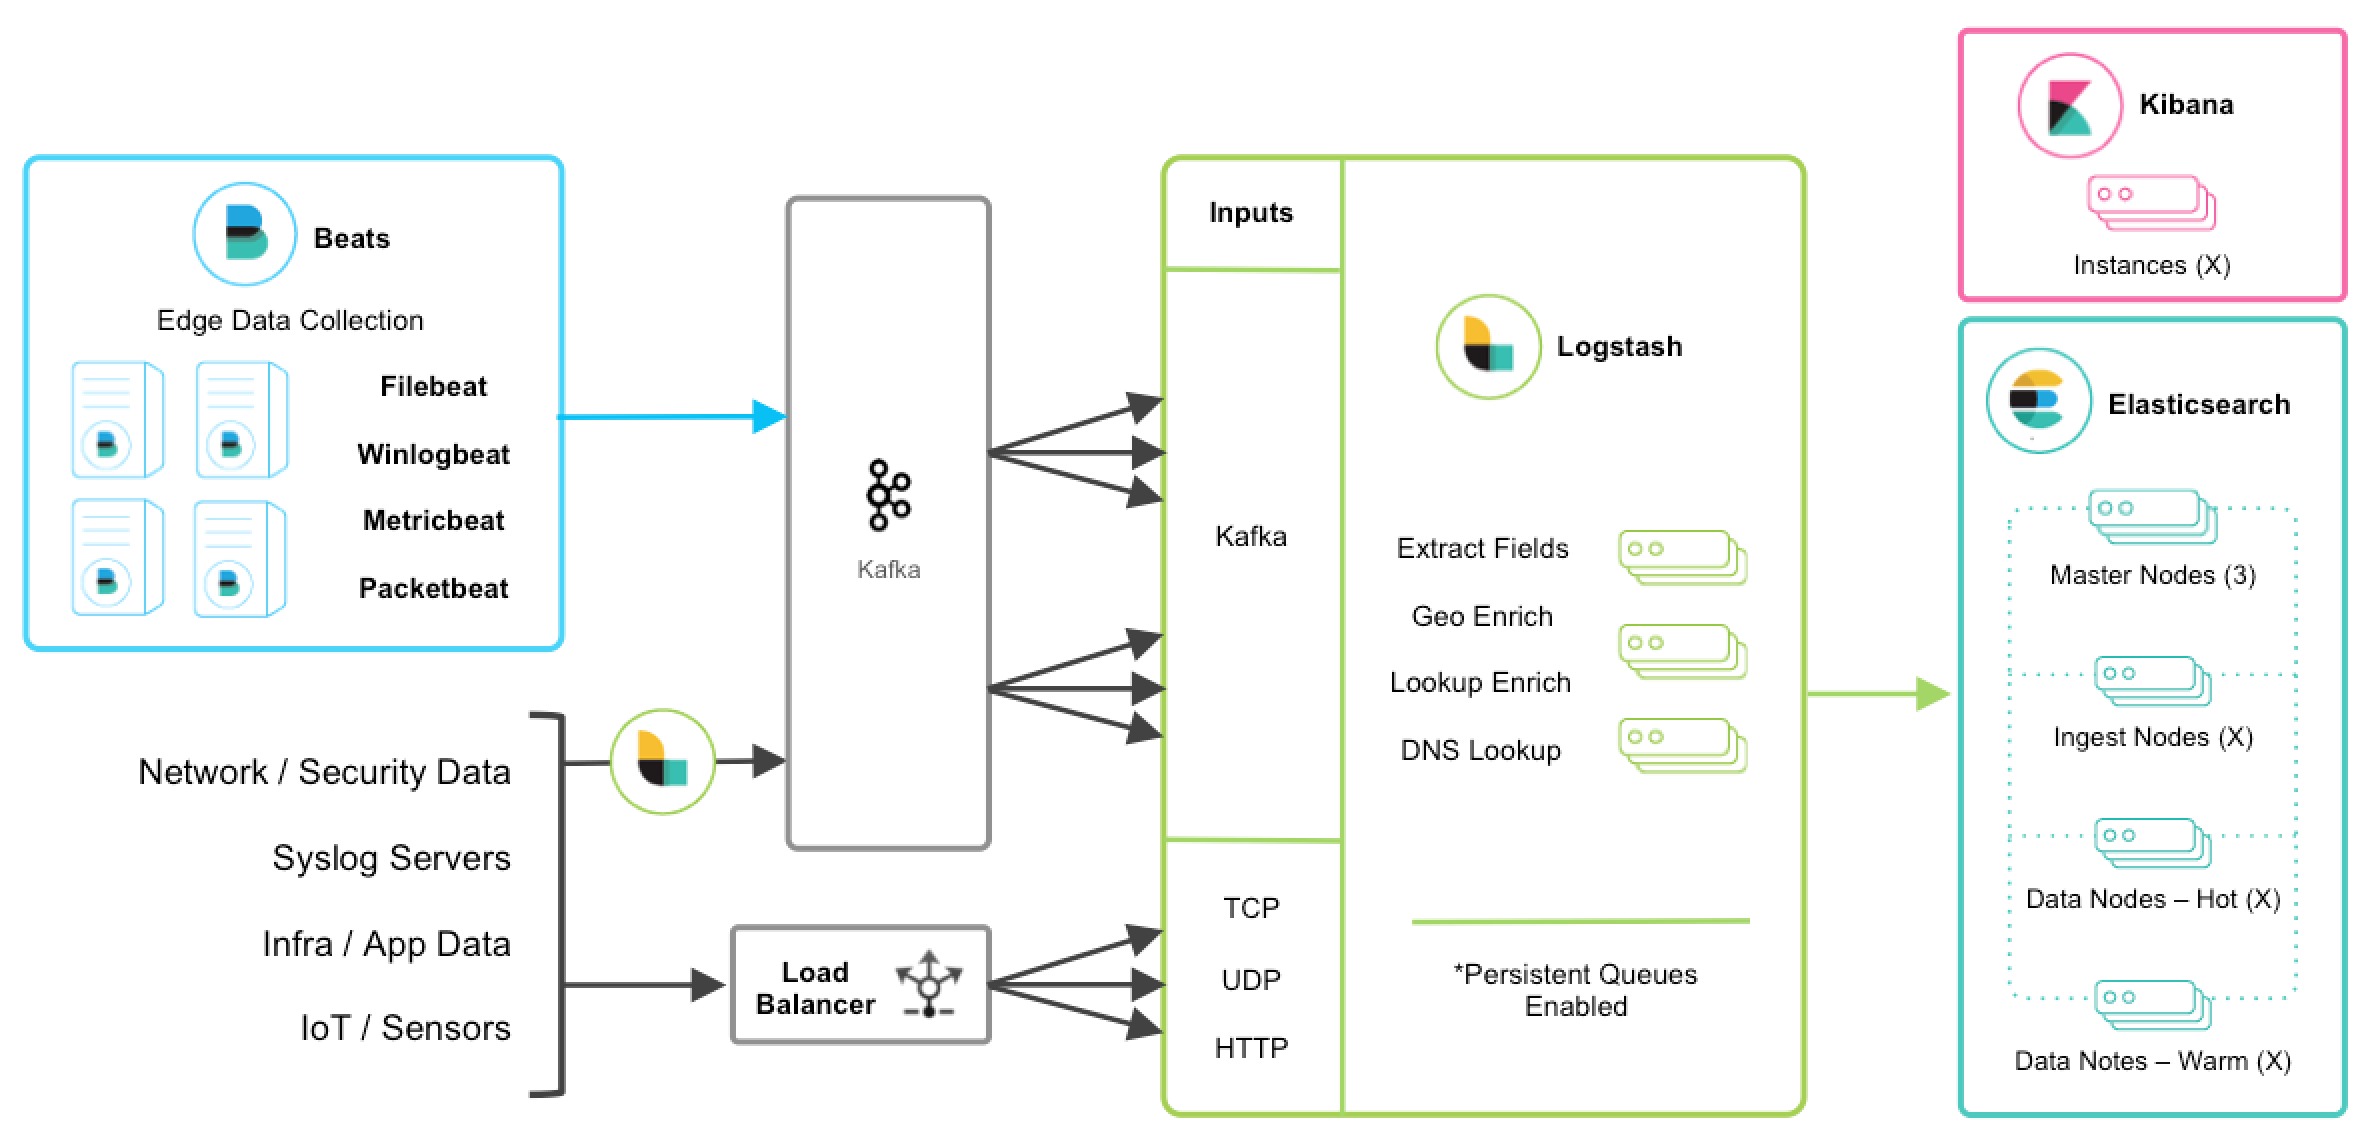
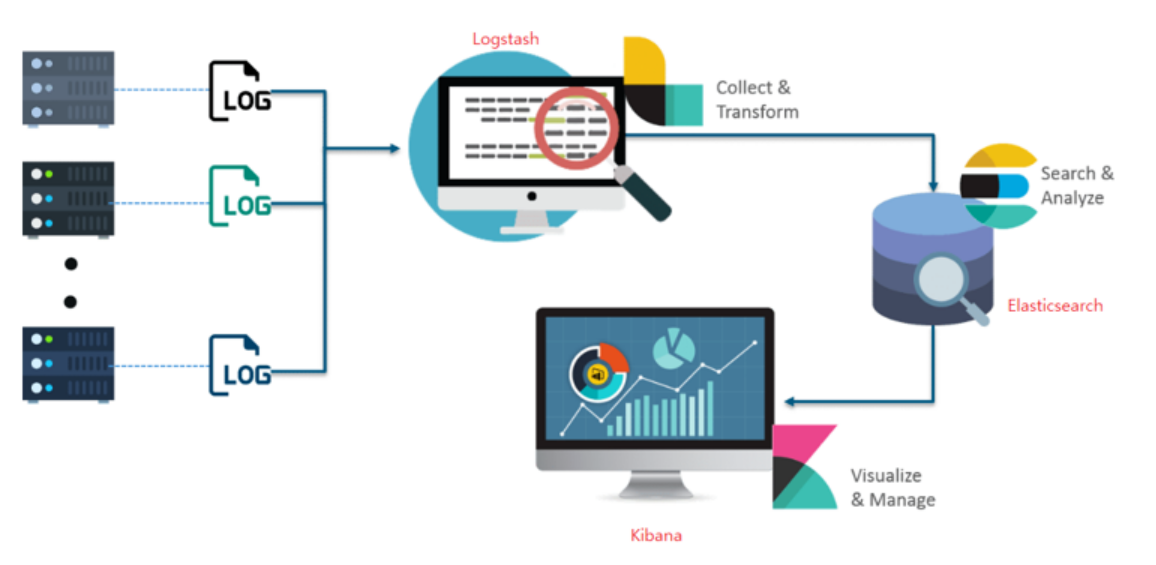
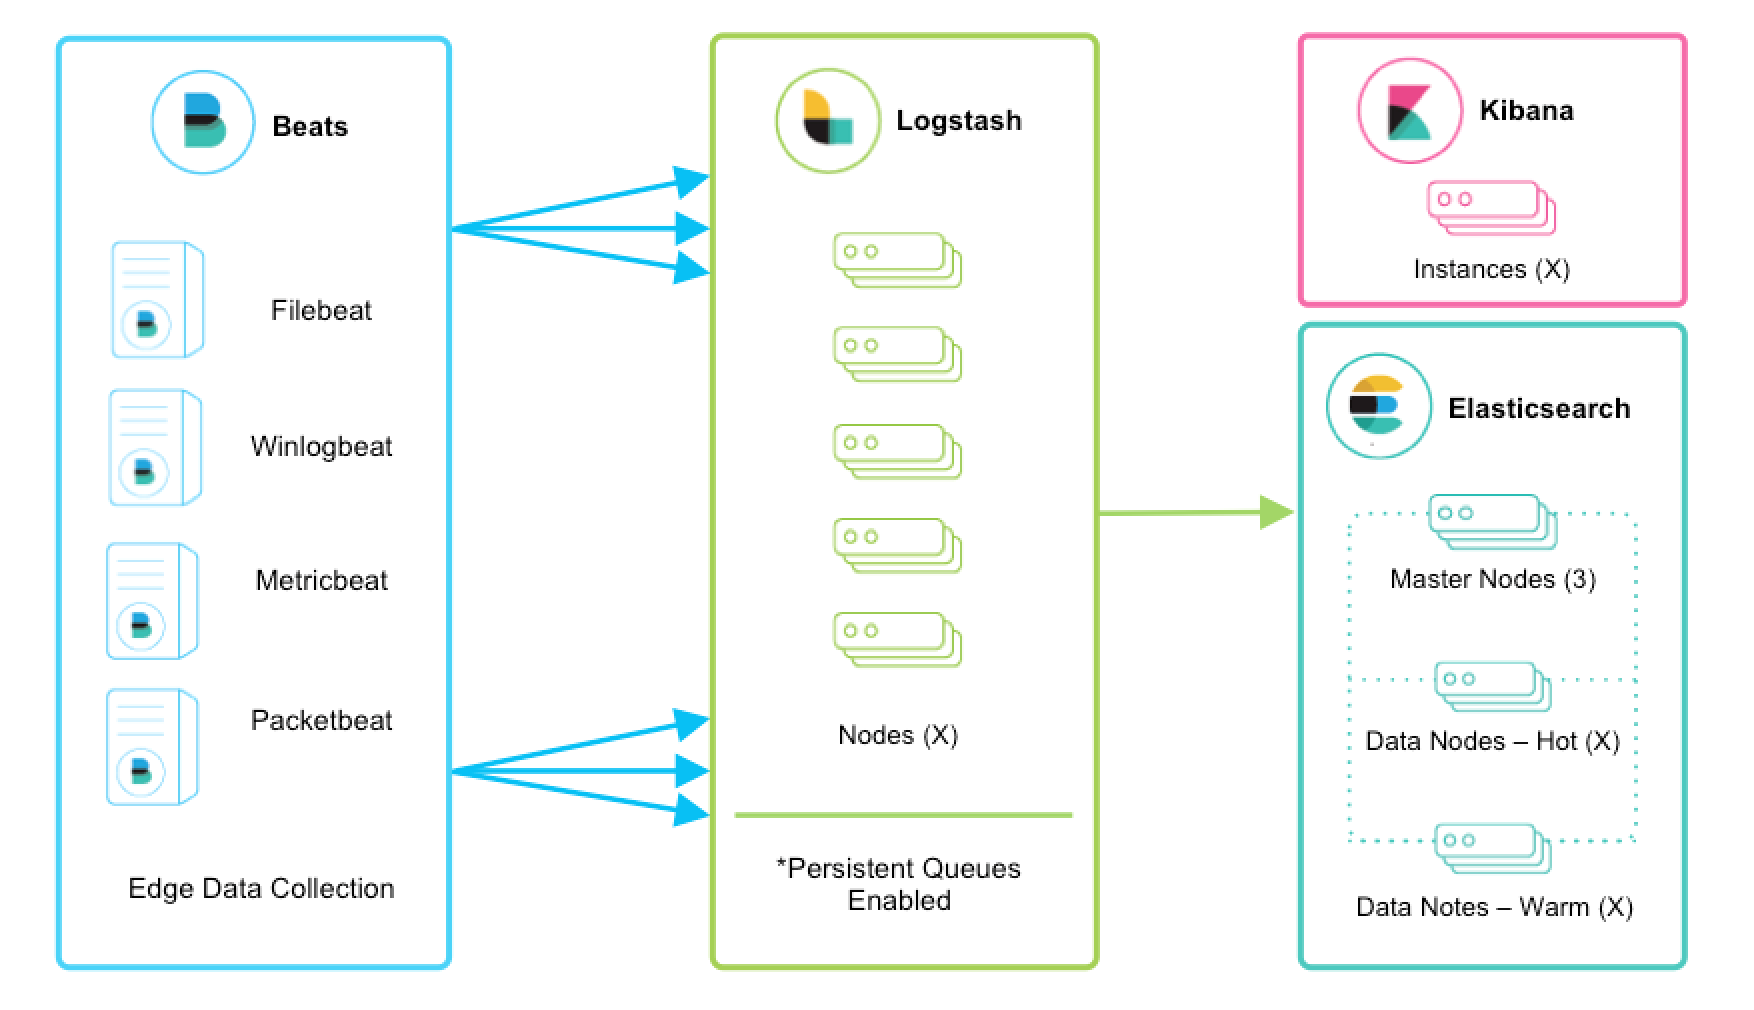
ELK Stack Architecture Elasticsearch Logstash and Kibana - SysAdminXpert
Elasticsearch Architecture
Elasticsearch Logs Integration
Tìm hiểu và cài đặt ELK Elasticsearch Logstash Kibana
Elasticsearch 8, Logstash, Kibana, Filebeat:Elastic Stack آموزش الاستی...
Logging to ElasticSearch (or any other destination) | Platformatic Open ...
Elasti Search failed to connect local host port:9200 - Elasticsearch ...
Project Management & Technology Fusion: ELK+ Stack - Elasticsearch ...
Elasticsearch 和数据架构:改进分析和存储的 4 个基本工具_elastic common schema 使用-CSDN博客
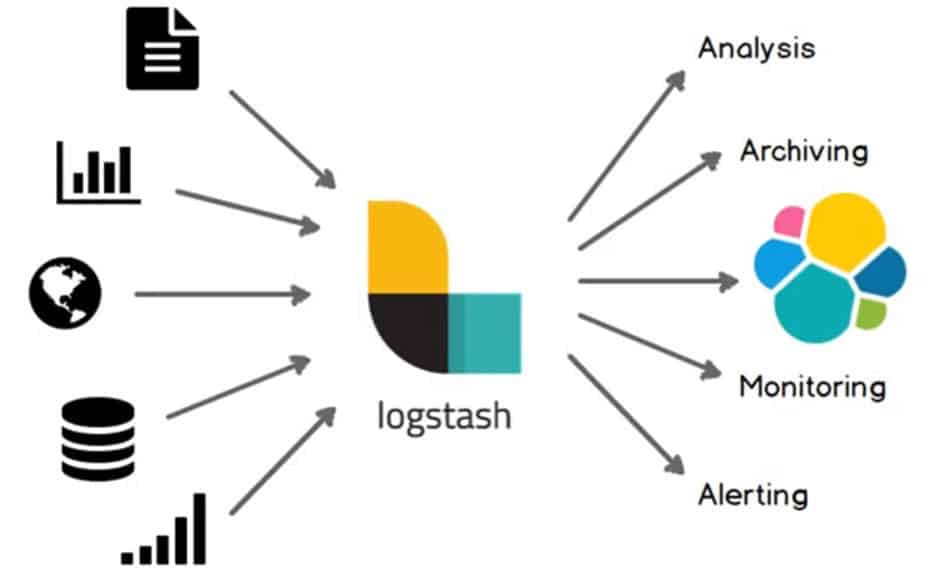
Elasticsearch Logstash
Sending Logs to Elasticsearch using Filebeat and Logstash. | by Nabin ...
🔨 Day 14: Elasticsearch Snapshot and Restore for Backups | by Vinoth ...
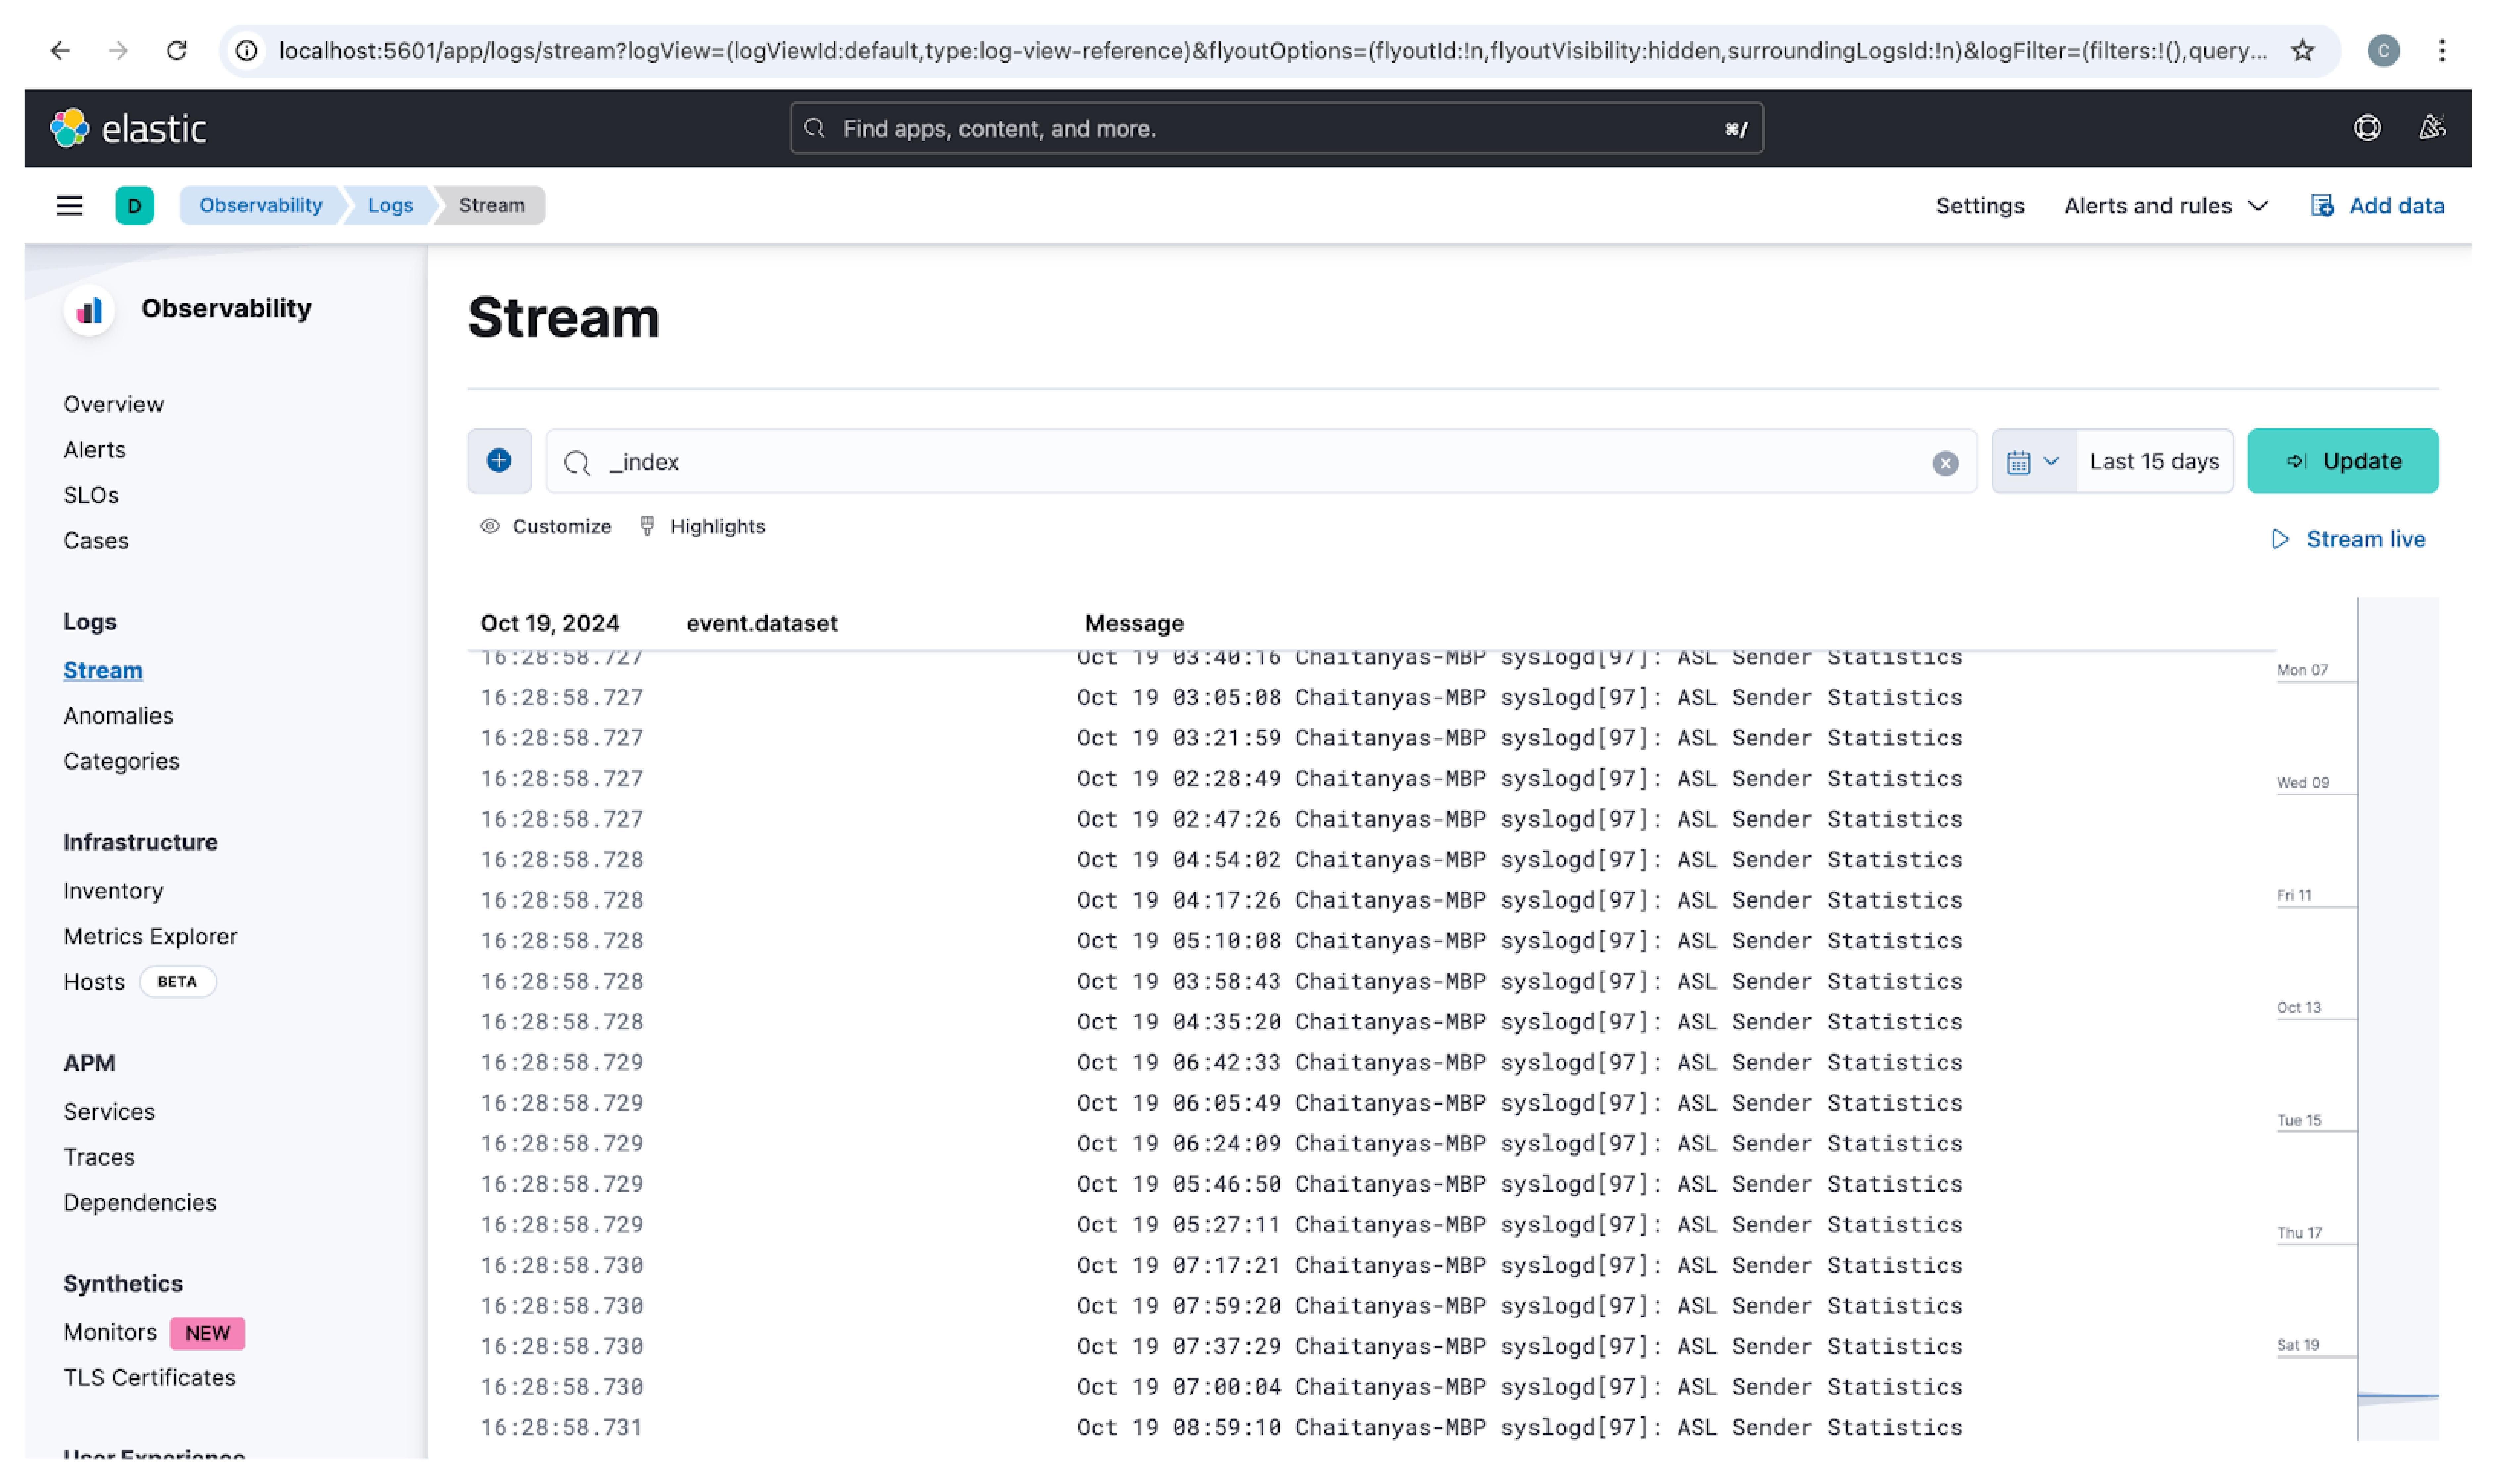
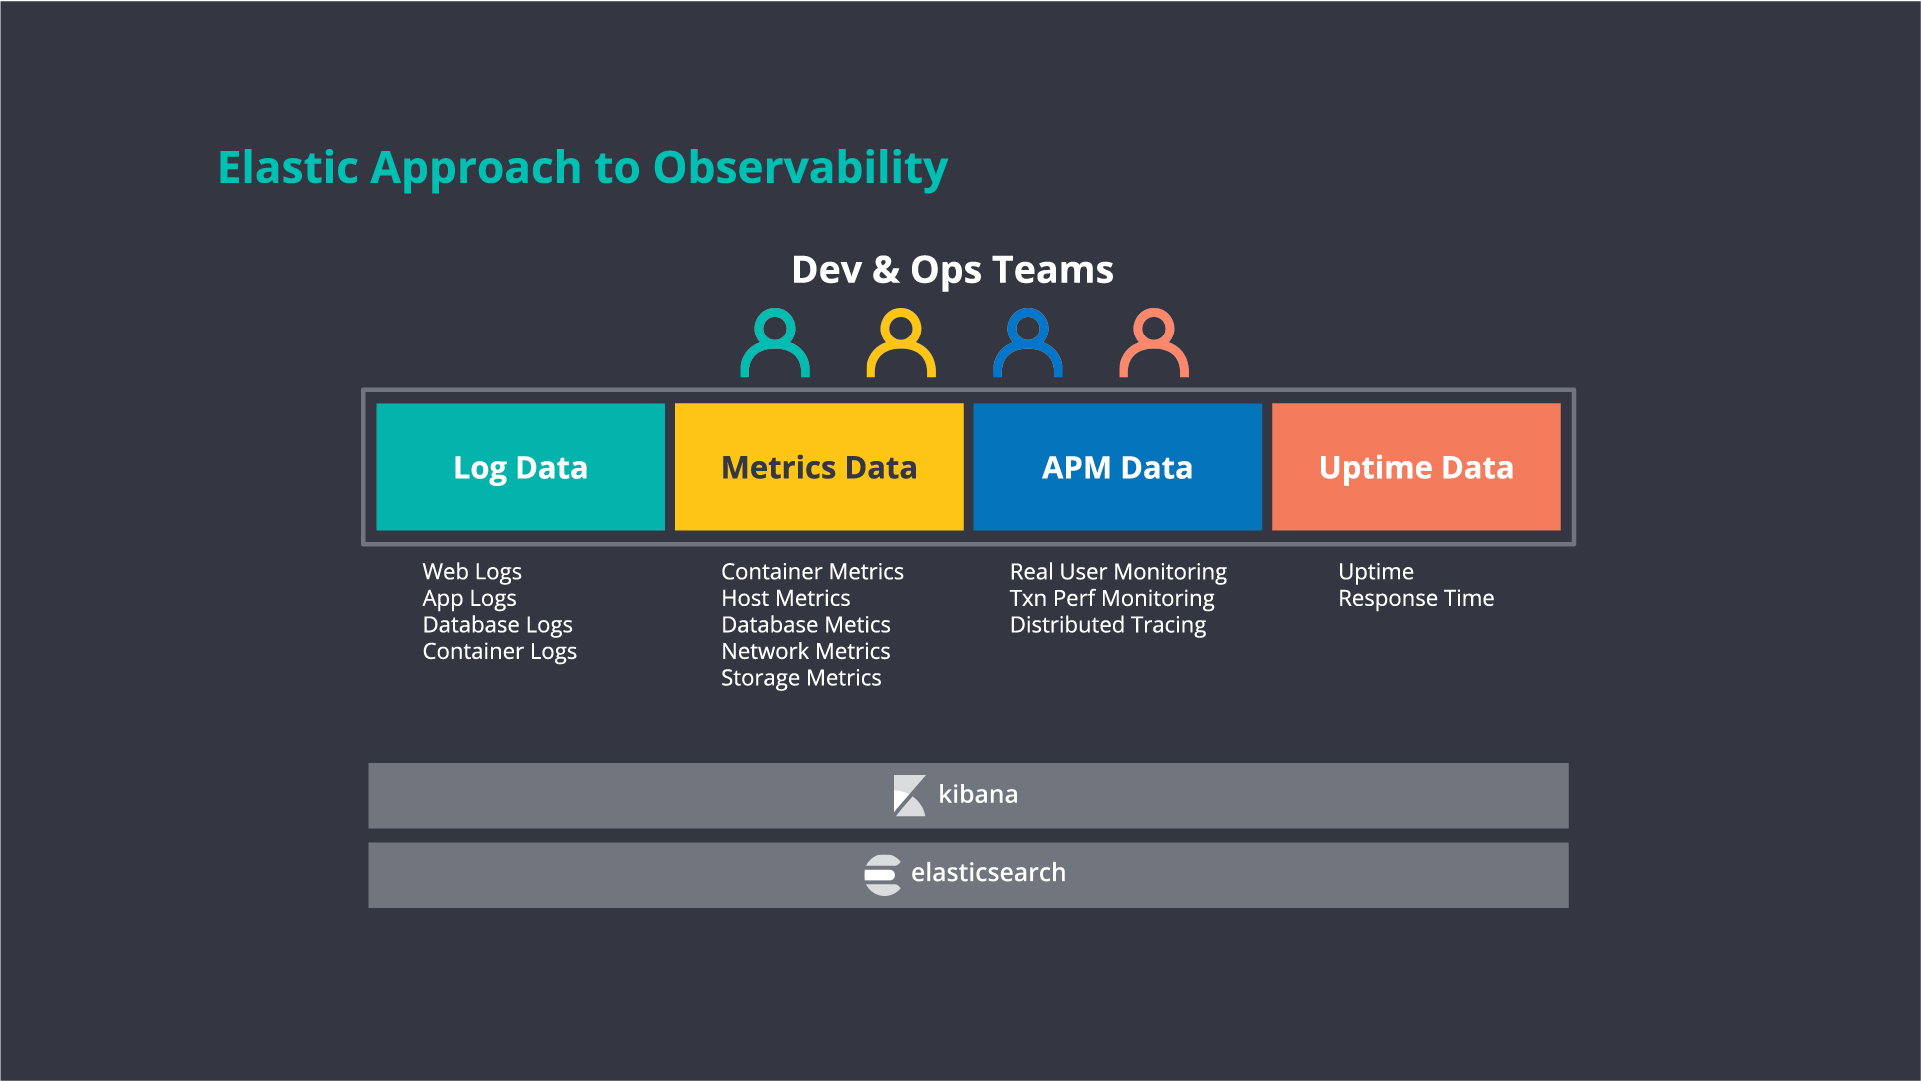
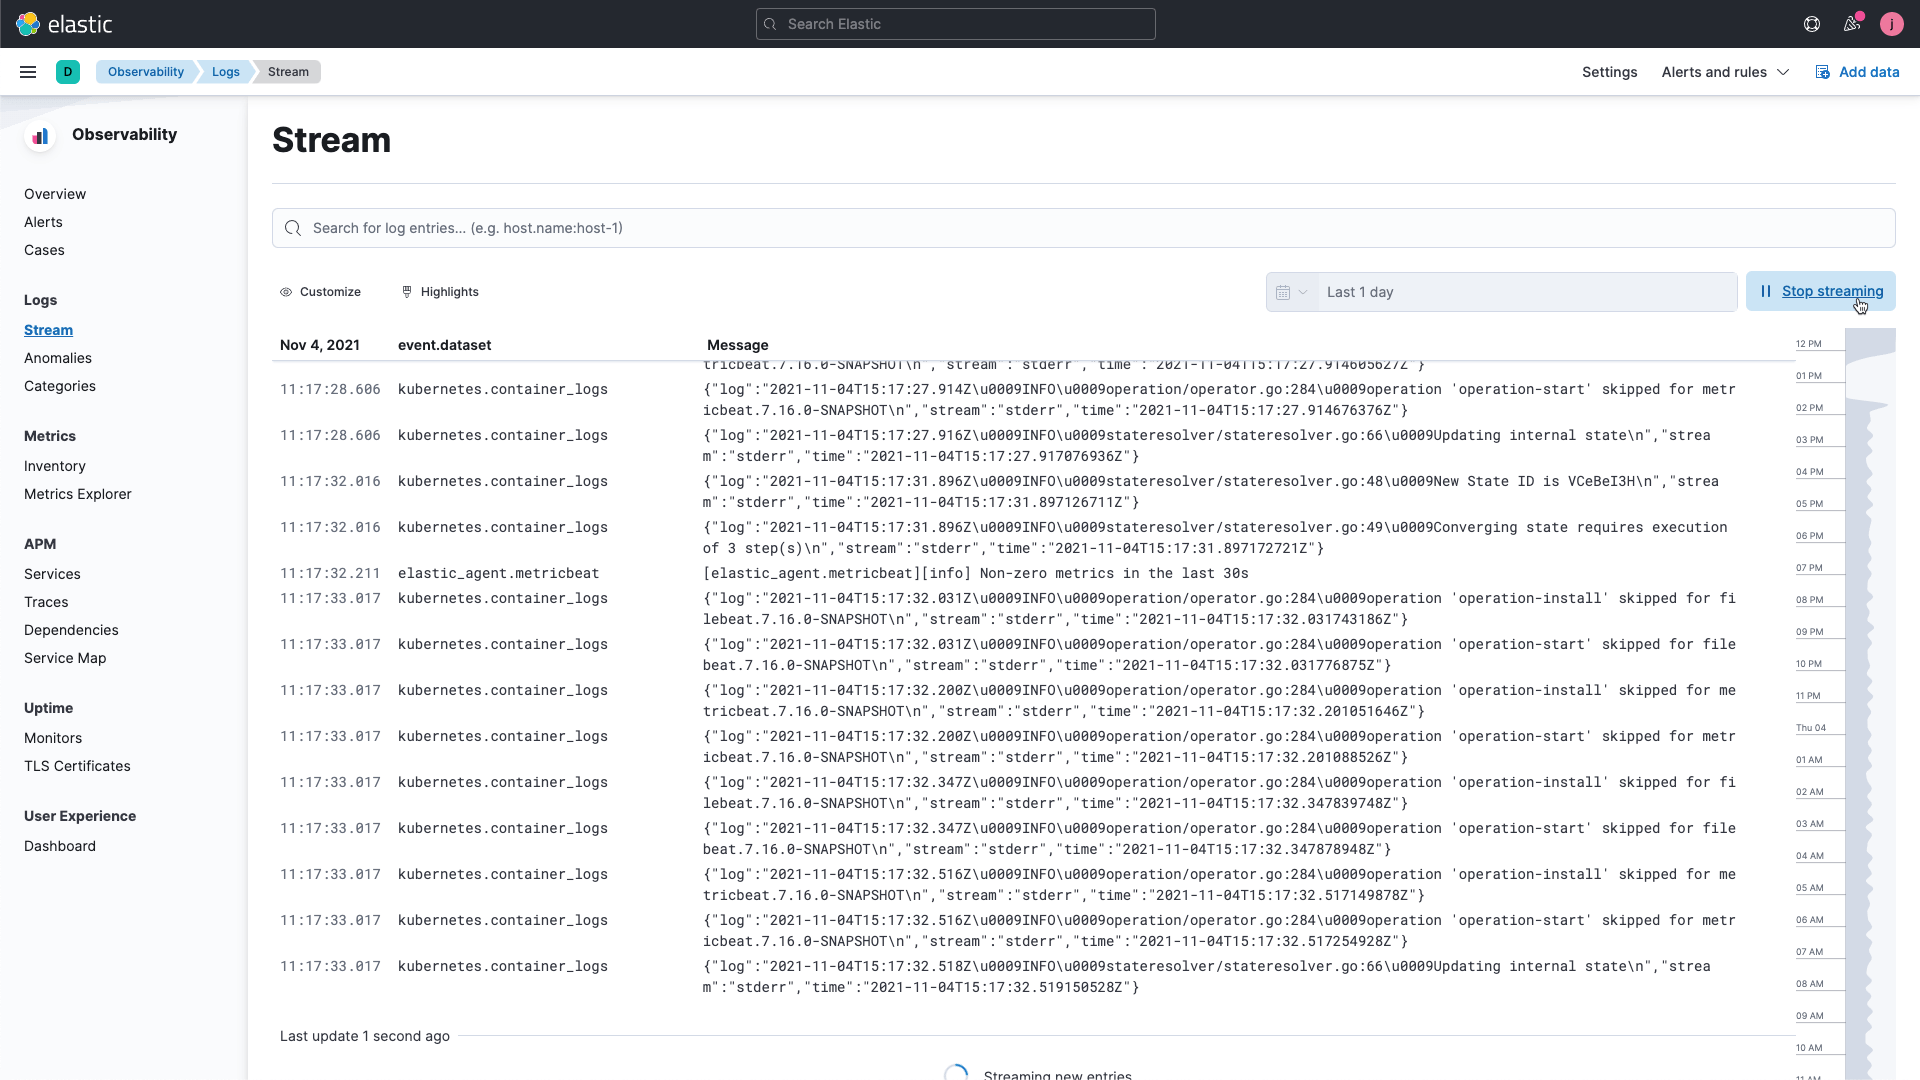
Log monitoring with Elastic Observability | Elastic
ElasticSearch,Logstash和Kiabana 部署 ELK nginx log_elasticsearch nginx log ...
Elasticsearch + Docker Compose: Part 1 - Elasticsearch, Kibana, Beats ...
Kubernetes Logging with Filebeat and Elasticsearch Part 2 | by ...
How to enable audit logging in Elasticsearch - Middleware|Technologies
Making the most of your unstructured log data through enterprise log ...
Elk Elasticsearch Elasticsearch Tutorial What Is ELK Stack (Elastic
Elasticsearch
What is the ELK Stack | ELK | Elasticsearch | Logstash | Kibana - YouTube
Elk Elasticsearch
PHP and ELK Stack: Centralized Logging with Elasticsearch Logstash and ...
Elasticsearch Dashboard
Elastic Log Format
Dockerizing Jenkins build logs with ELK stack (Filebeat, Elasticsearch ...
Getting Started with Elasticsearch and the Elastic Stack on Microsoft ...
What Is ELK Stack: Tutorial on How to Use It for Log Management
Difference Between Elastic Stack And Elasticsearch at Albert ...
How to implement logging in your REST service by using Elasticsearch ...
Elasticsearch Logstash How To Install ElasticSearch And Logstash (and
Kubernetes部署Elasticsearch – Elasticsearch Configuration – UBJM
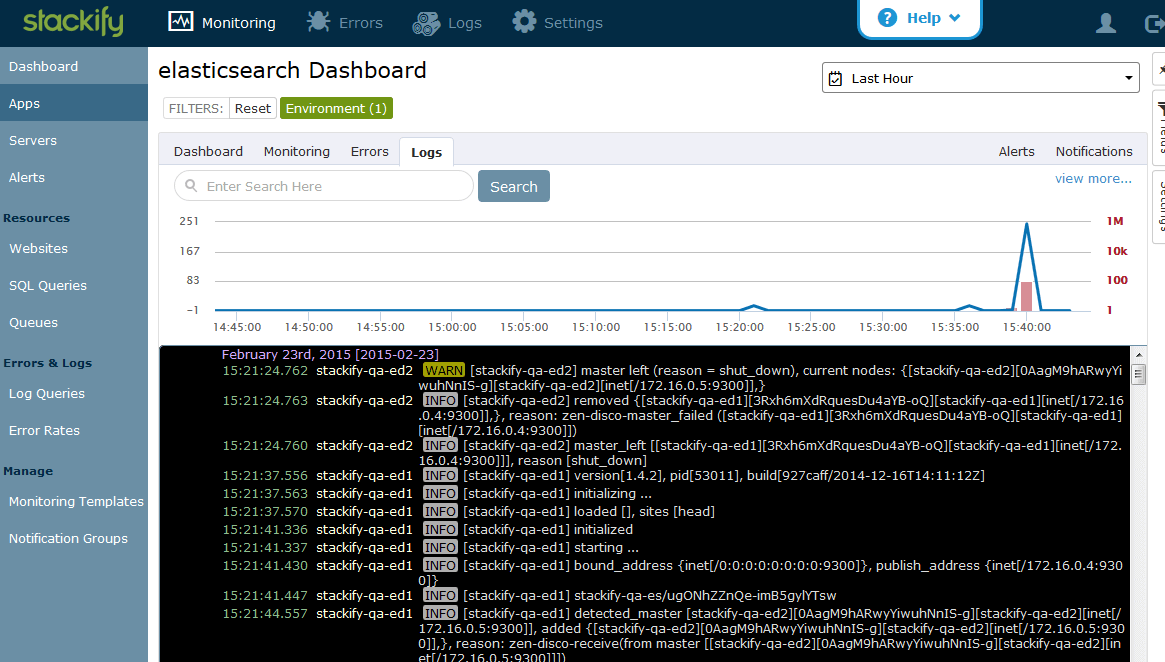
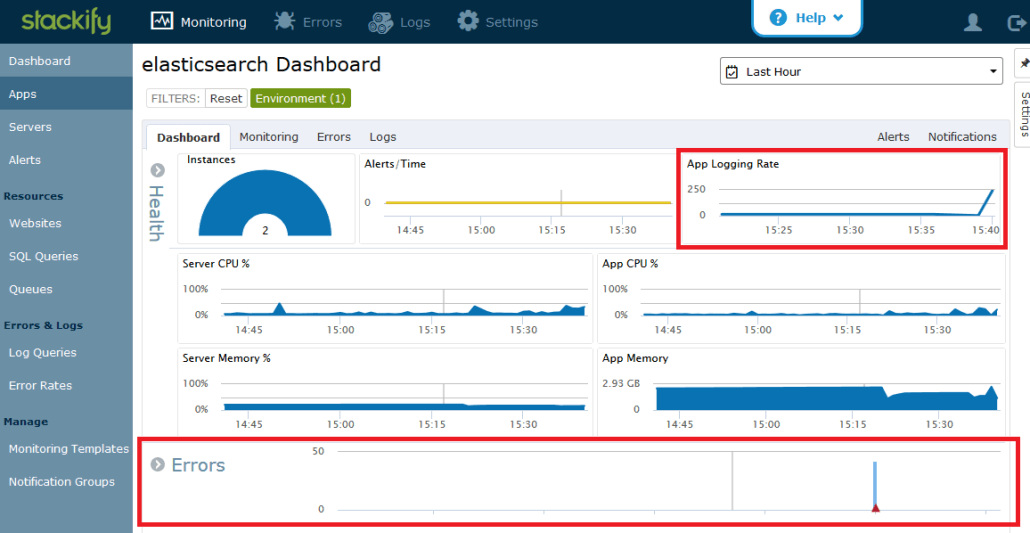
How-to: Monitor Your Elasticsearch Cluster Performance - Stackify
Introducing 7.16.2 and 6.8.22 releases of Elasticsearch and Logstash to ...
Elasticsearch:为日志分析设置安全的 Elasticsearch 管道_org.elasticsearch.launcher ...
GitHub Enterprise Insights with ElasticSearch and Kibana | Medium
The Ultimate Guide to Installing ElasticSearch with Docker | Medium
Elasticsearch - 1
Putting our Elasticsearch in order | Tech blog | Palark
ELK Stack: Logstash shows that it's receiving log entries from Filebeat ...
Better Stack Elasticsearch logging | Better Stack Documentation
Elasticsearch Logs
Elk Stack Erklärung : Introduction to Elasticsearch and the ELK Stack ...
Docs | Plural | ElasticSearch Configuration
Elasticsearch Aws
ElasticSearch 101: A Beginner’s Guide to ElasticSearch | by TechMG | Medium
How To Install Elasticsearch, Logstash, and Kibana (Elastic Stack) on ...
Elk Data Pipeline at Catherine Dorsey blog
ElasticSearchを使ったlog収集1 -Elastic Agentとは?- · hirohirolab
What is ELK Stack? Elasticsearch, Logstash and Kibana | by Lalit Soni ...
The ELK Stack ( Elasticsearch, Logstash, and Kibana ) Using Filebeat ...
How To Set Up an Elasticsearch, Fluentd and Kibana (EFK) Logging Stack ...
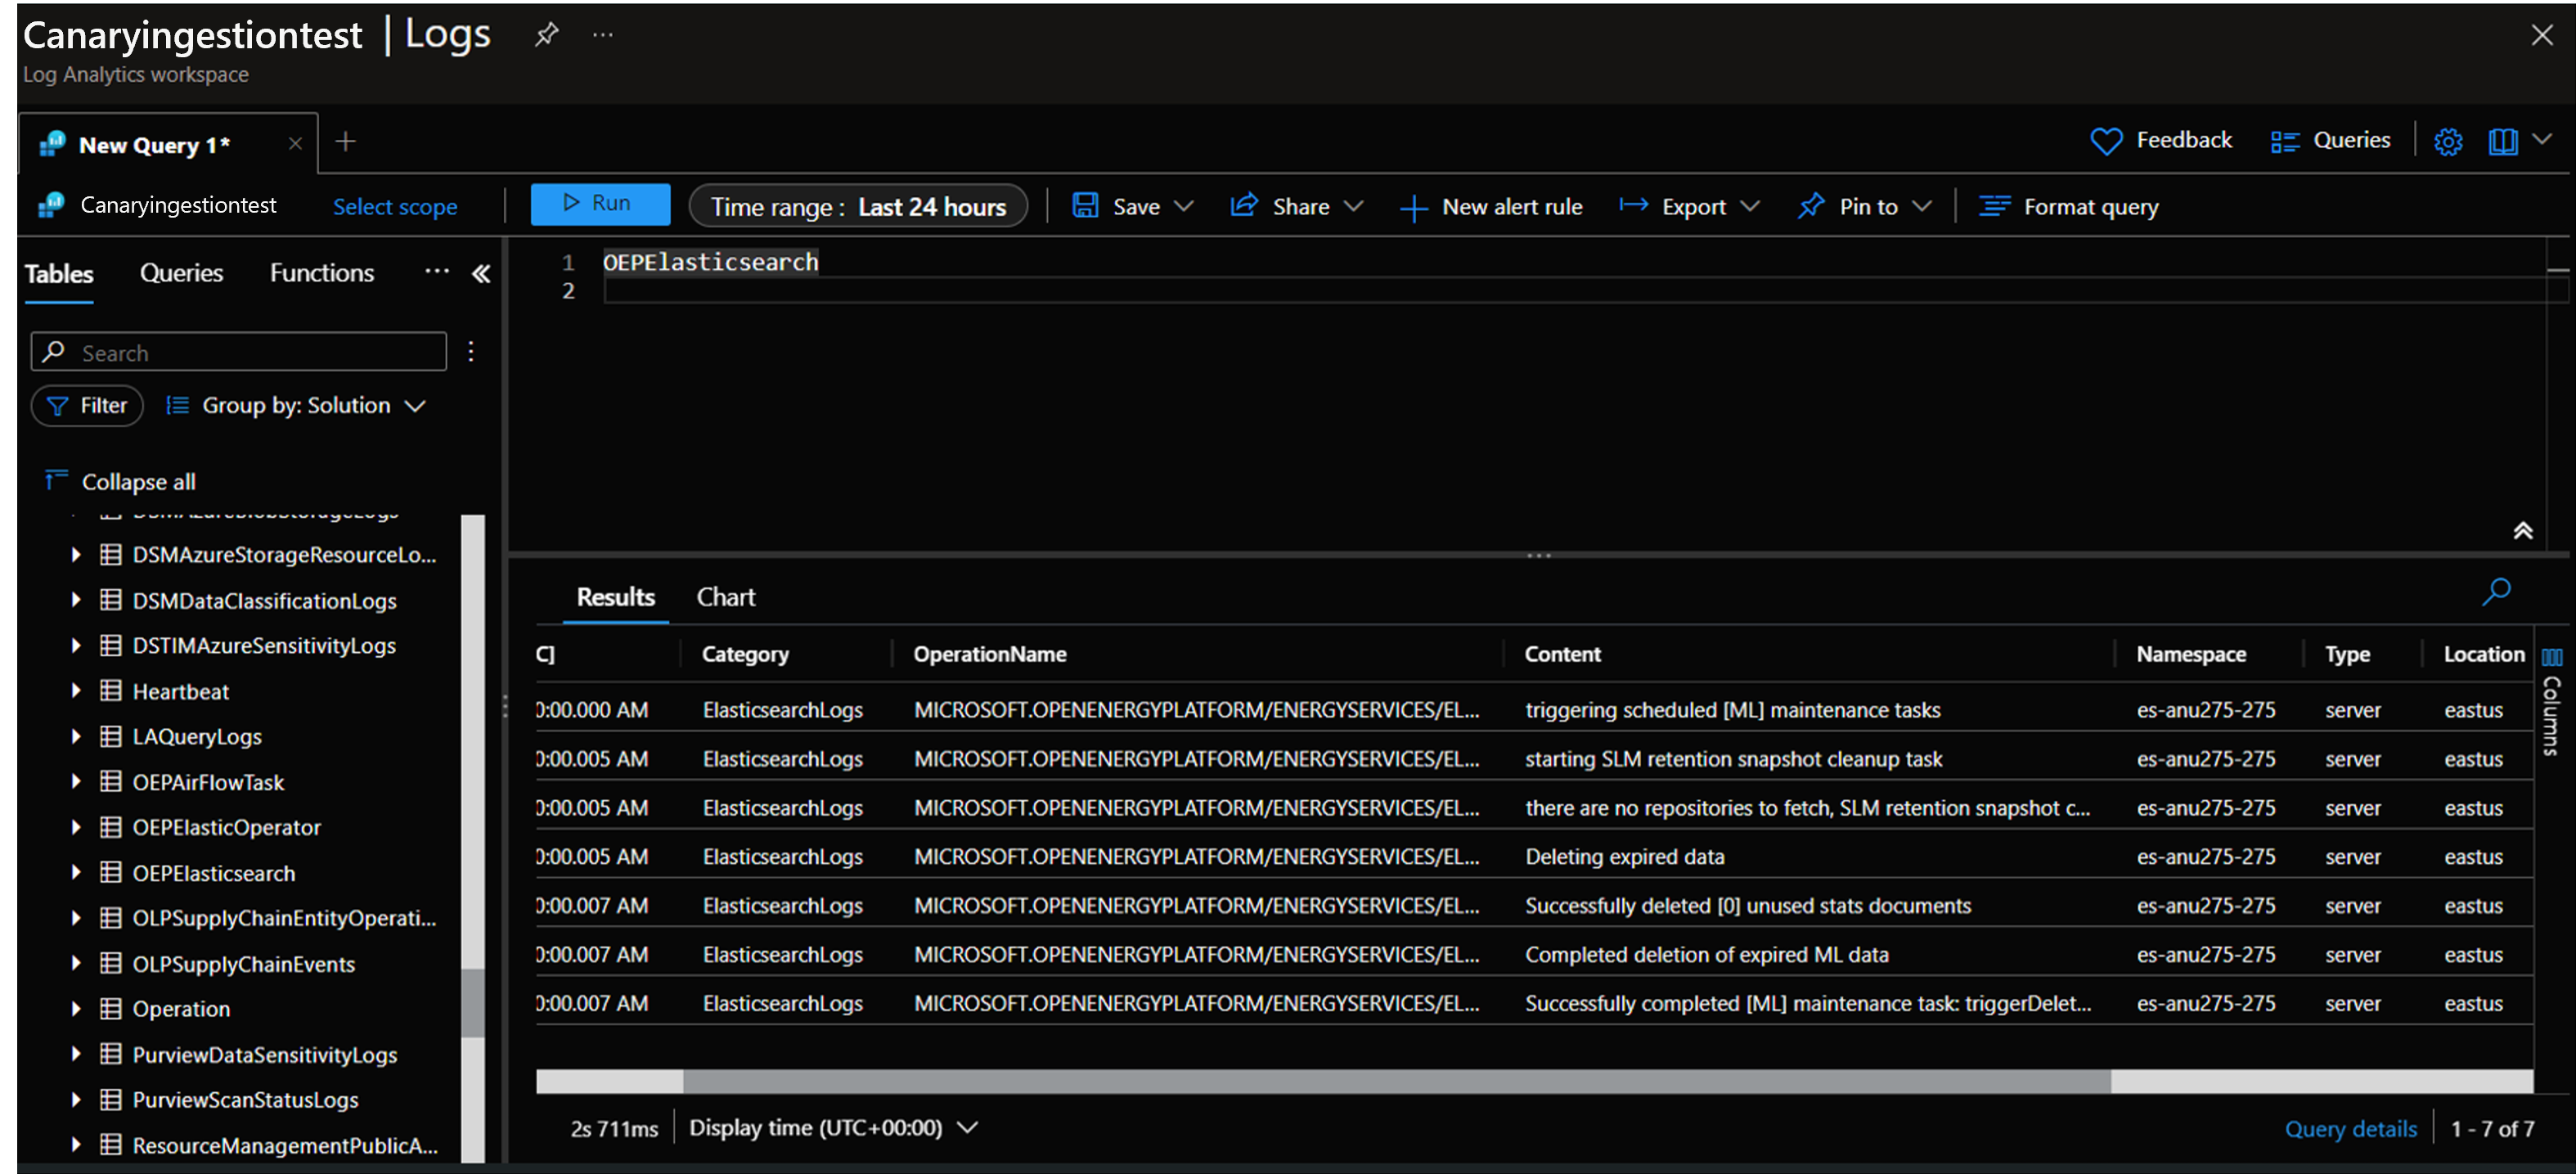
Integrate elastic logs with Azure Monitor - Microsoft Azure Data ...
dbi Blog
Centralized Logging With Elasticsearch, Kibana, Logstash and Filebeat ...
ELK (Elasticsearch, Logstash and Kibana) Review 2024: Features, Pricing ...
ELK日志分析系统(filebeat+logstash+elasticsearch+kibana)-CSDN博客
Enabling enterprise logging with Elasticsearch, Kibana, and ...
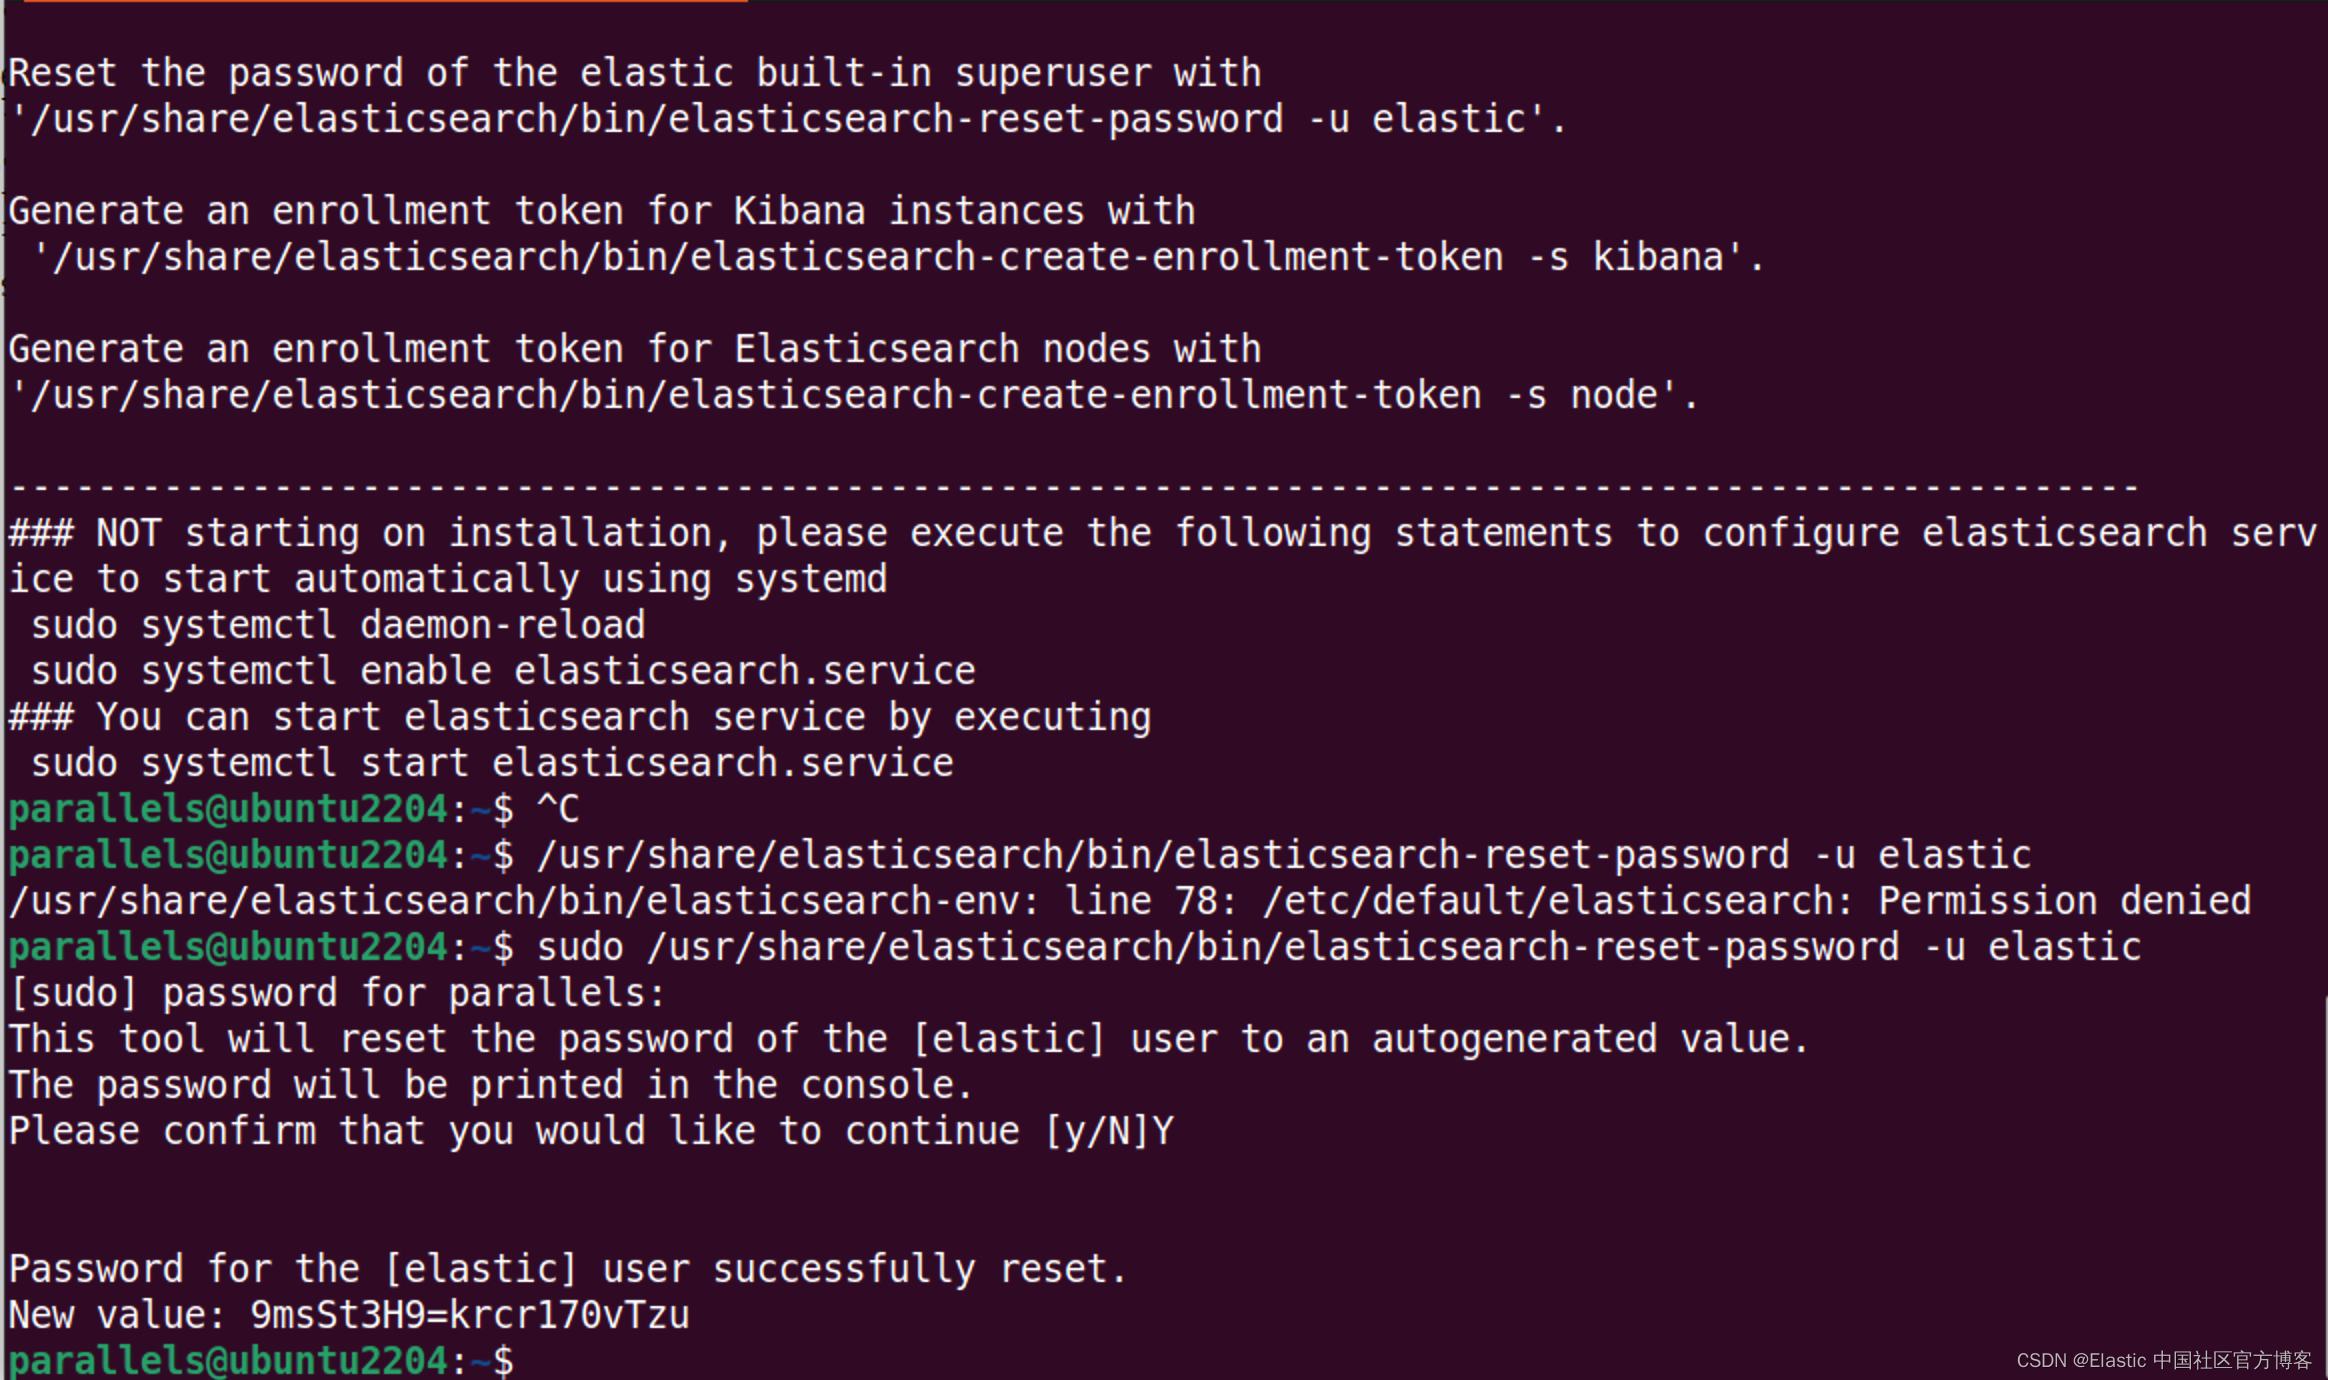
How to Install Elastic Stack on Ubuntu 22.04 LTS | by Corey Ducre (He ...
Log4j2集成ELK平台进行日志管理入门 - 丁生· - 博客园
Centralised Logging with Elasticsearch, Logstash and Kibana (ELK) | by ...
Graylog vs Elastic/ELK Stack: The Key Differences to Know | Better ...
ELK Stack: The Essentials of Elasticsearch, Logstash, and Kibana | by ...
#elkstack #logging #devops #docker #kibana #elasticsearch #logstash # ...
Kibana Logs How To Use Elasticsearch, Logstash And Kibana To Visualise
Elasticsearch学习(5) Elasticsearch+logstash +filebeat+log4j的日志系统 - 想去天空的猫 ...
【Elastic (ELK) Stack 实战教程】01、Elastic Stack 概述_elk stack-CSDN博客
Article On Matatag Lesson Logstash Logo Unpak Fhm Models
Elastic Stack Tutorial for Beginners:ELK (Elasticsearch, Logstash ...
What are Beats, how do they work. What are Beats? | by Cyber Tool ...
Historial de Actividad de Datos de Elasticsearch: Controle Sus Datos
#elkstack #elasticsearch #logstash #kibana #logging #observability # ...
GitHub - Rumbidzai19/WebApp-Log-Analysis: This project uses the ELK ...
How To Install Elasticsearch, Logstash, and Kibana (ELK Stack) on ...
ELK日志平台(elasticsearch +logstash+kibana)原理和实操(史上最全) - 技术自由圈 - 博客园
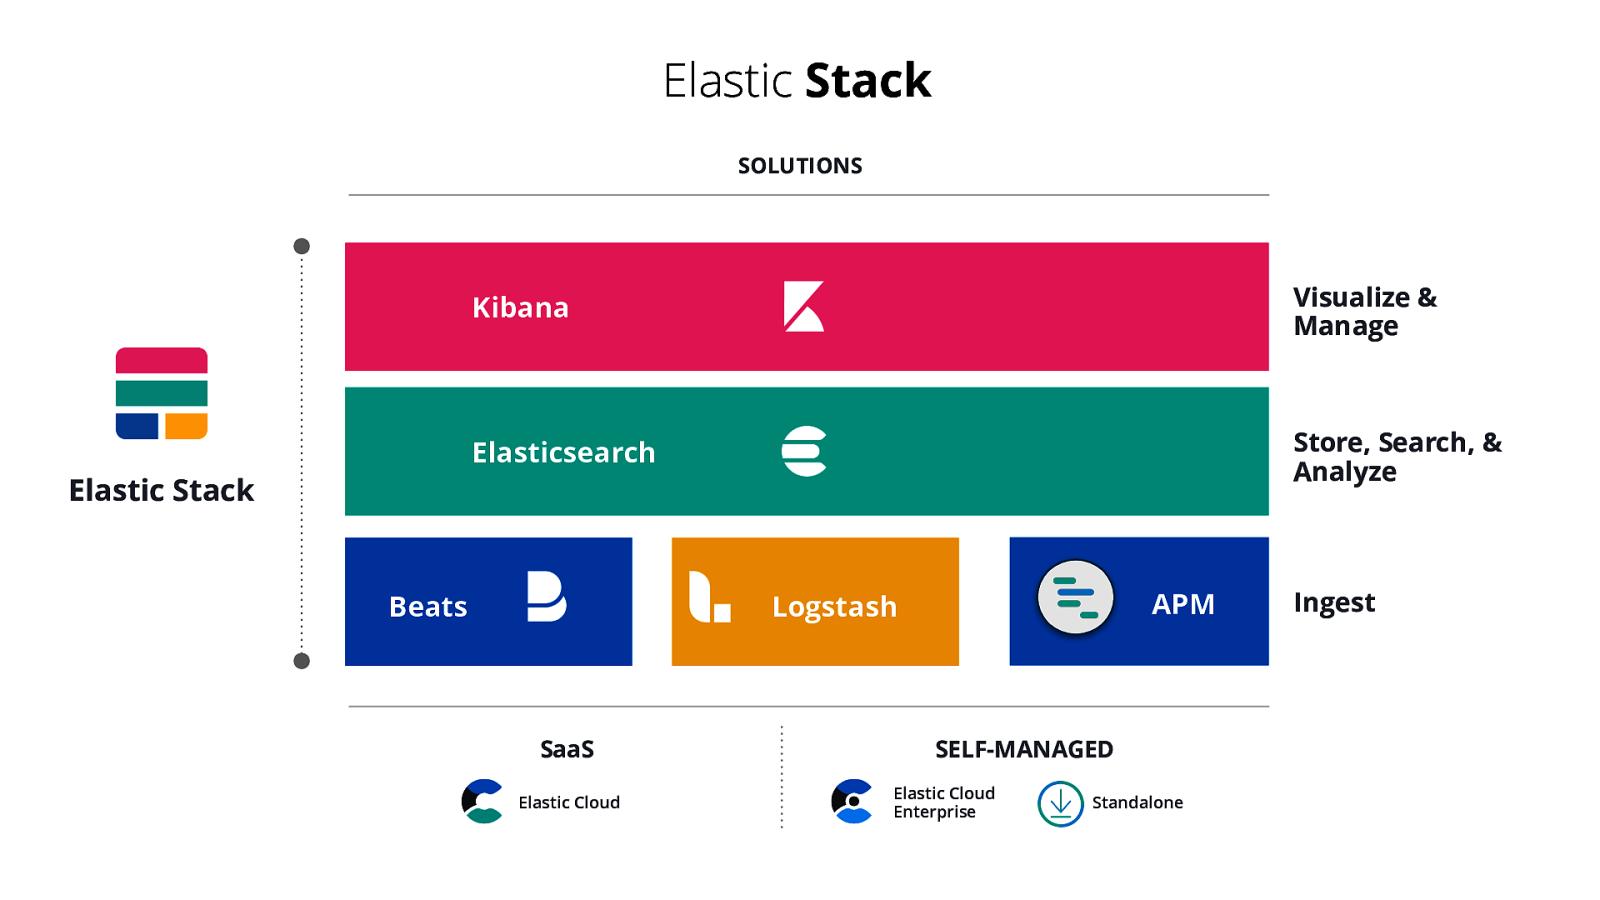
ELK Stack: Elasticsearch, Kibana, Beats e Logstash | Elastic
ELK (ElasticSearch, Logstash, Kibana) 도입
Elastic (ELK) Stack features list | Elastic
The Complete Guide to the ELK Stack - Logz.io
Elasticsearch:解析和丰富日志数据以在 Elastic 平台上进行故障排除_elastic 日志分析-CSDN博客
Logging in Kubernetes with Elasticsearch, Fluentd & Kibana (EFK) using ...
How To Use Elasticsearch, Logstash And Kibana To Visualize Logs In ...
Logging-ElasticSearch插件 | Apache ShenYu
ElasticSearchを使ったlog収集2 -Elastic Agentの追加- · hirohirolab