Showing 120 of 120on this page. Filters & sort apply to loaded results; URL updates for sharing.120 of 120 on this page
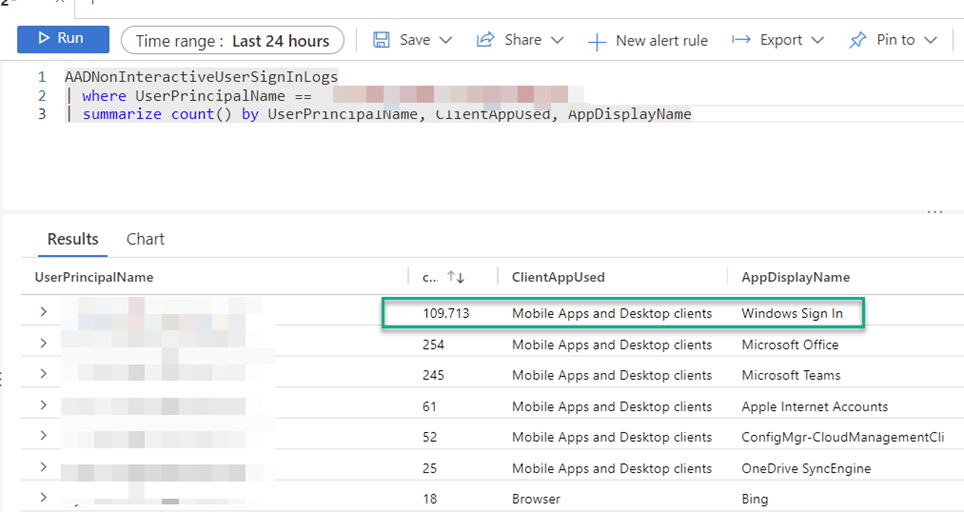
Connect Entra ID Logs to Microsoft Sentinal
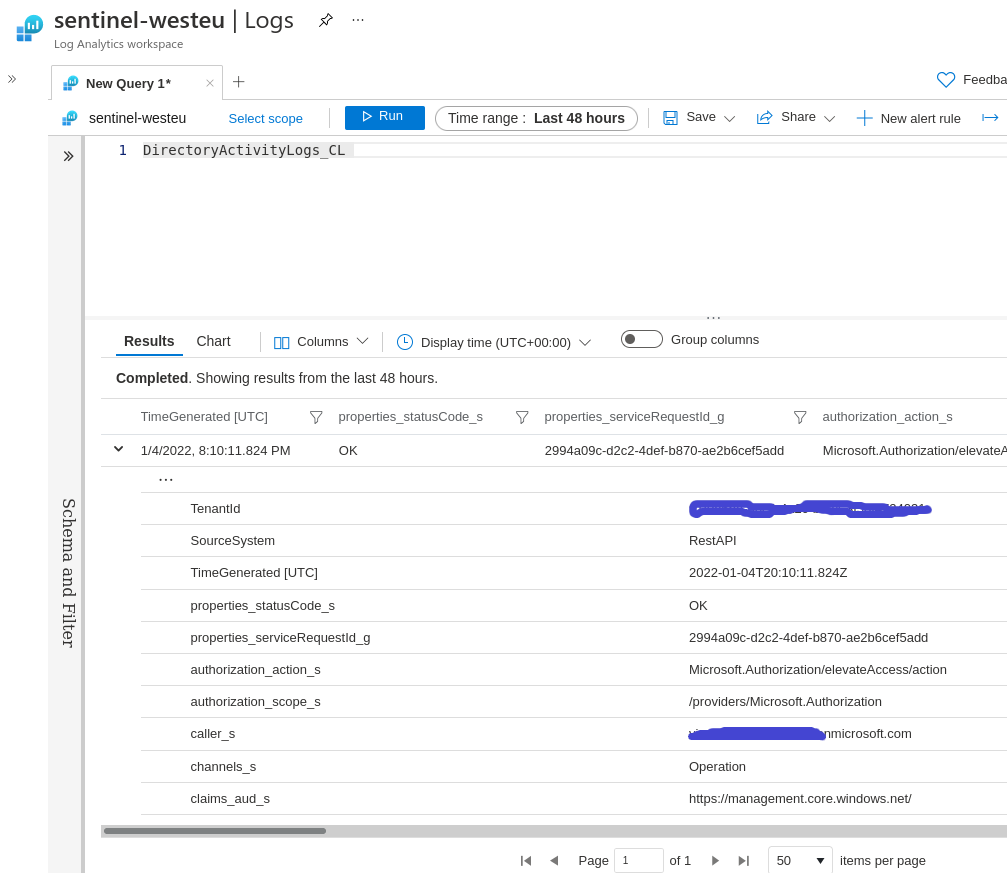
Logging User Access Admin elevations to Microsoft Sentinel | Adriaans ...
Logs do AD on-premises no Microsoft Sentinel - Daniel Donda
Microsoft Sentinel & Azure Arc - Troubleshooting Windows Event Logs ...
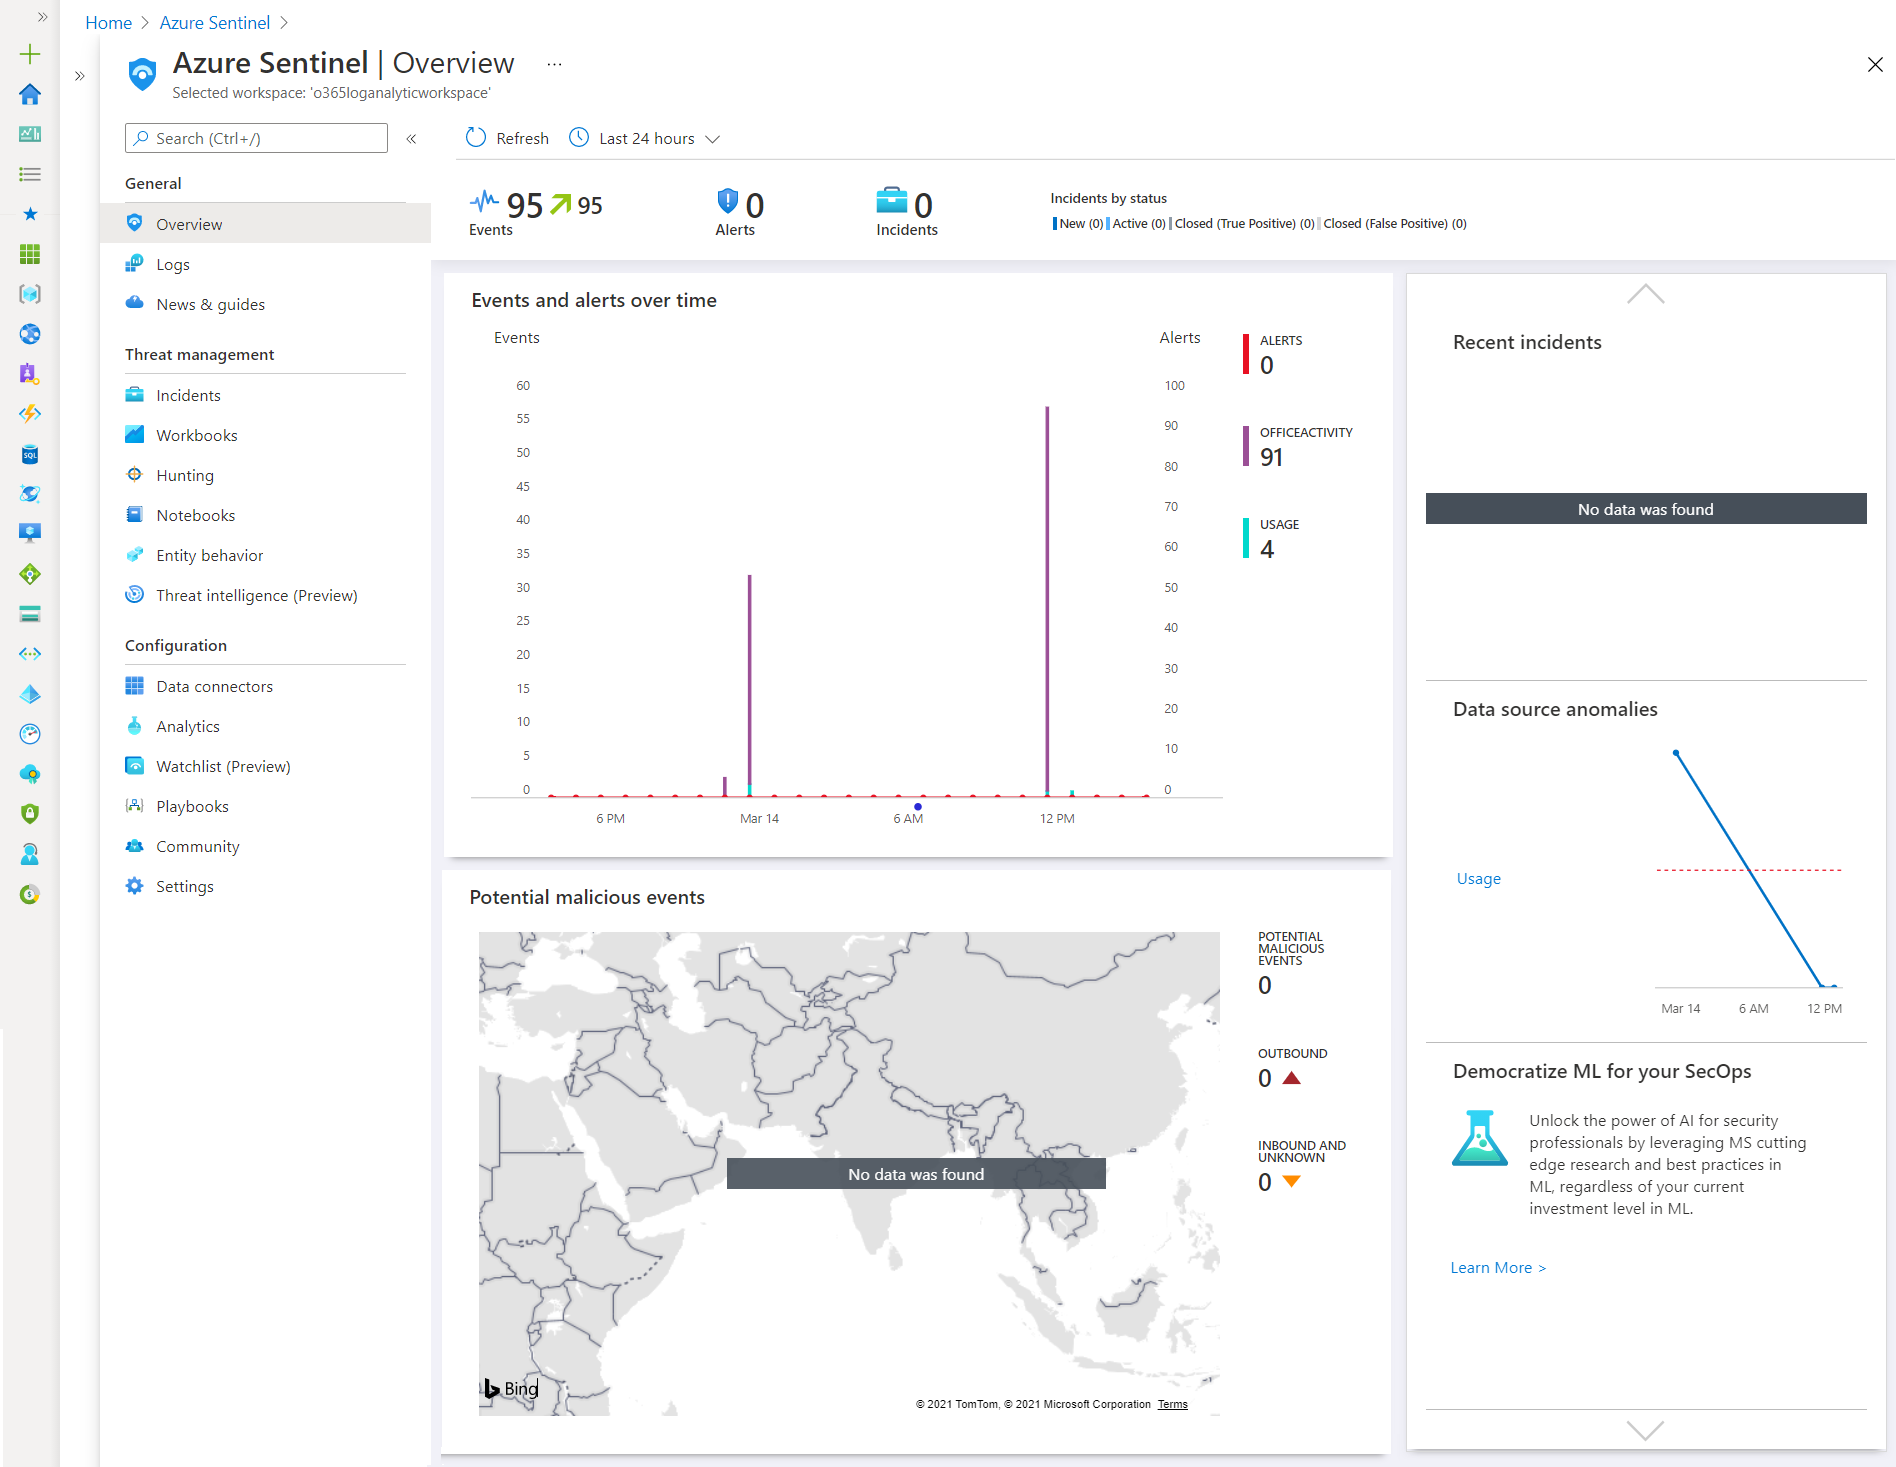
Monitor Office 365 Logs from Azure Sentinel - Nanddeep Nachan Blogs
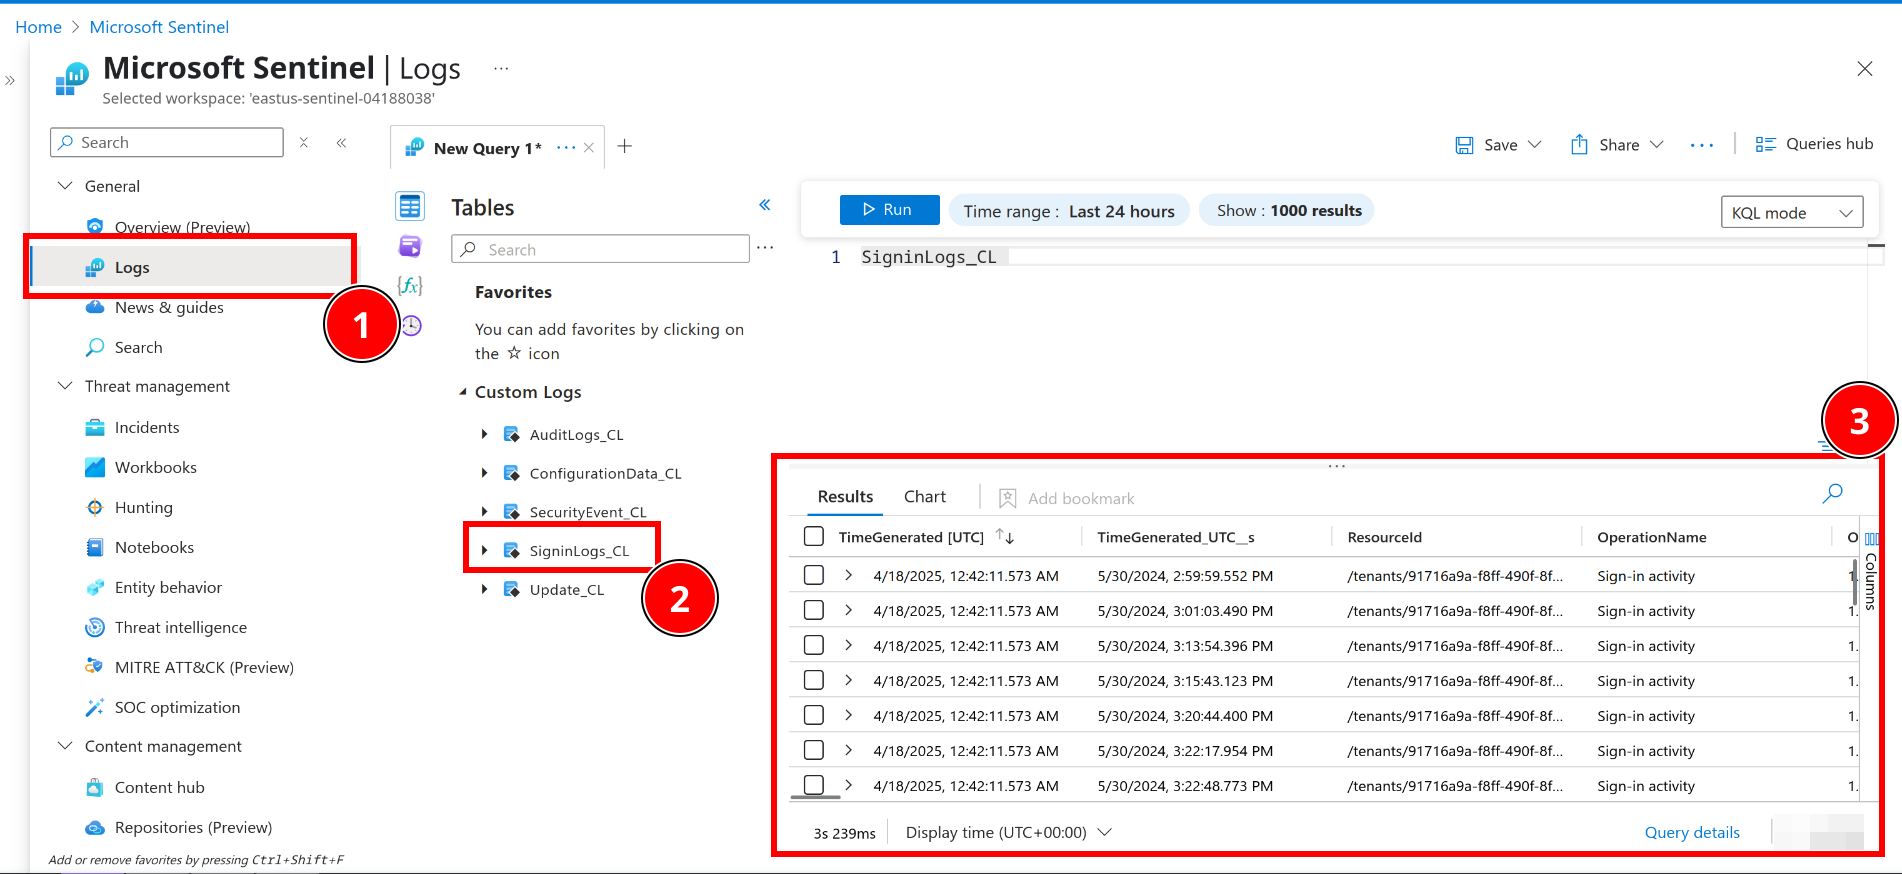
Ingest Custom Logs to Microsoft Sentinel: A Step-by-Step Guide 1
Ingestión de logs de Oracle Cloud Infrastructure en Microsoft Azure ...
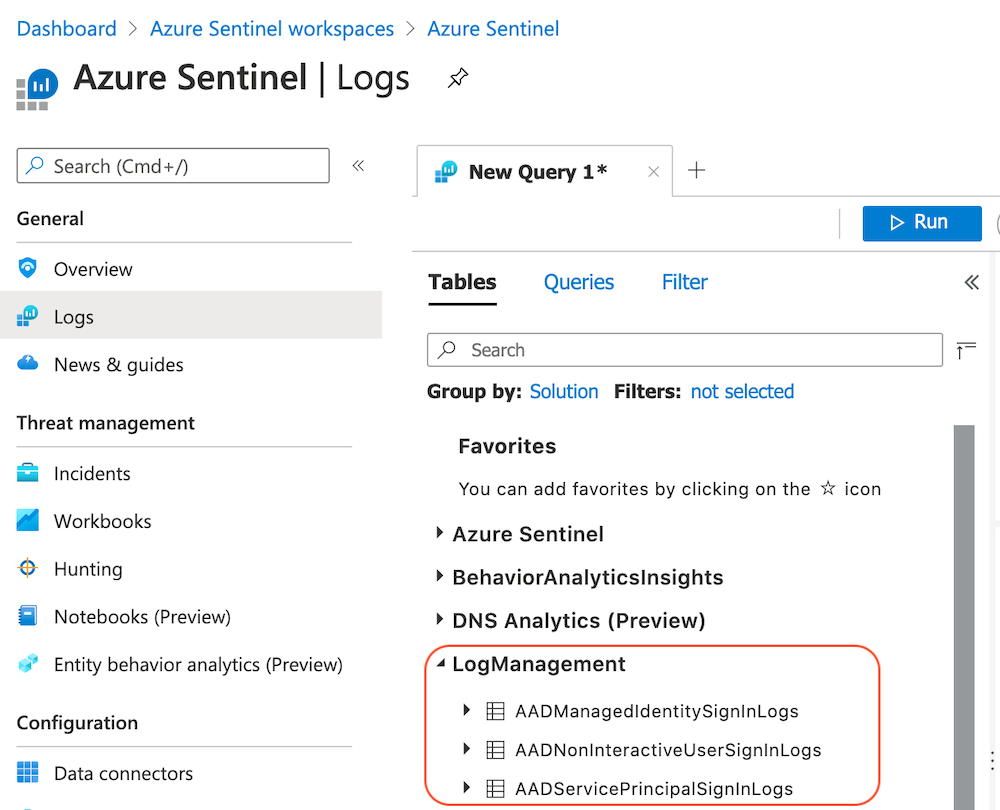
Sign-in logs and auditing of Managed Identities and Service Principals ...
Microsoft Sentinel Event Logs _ When to use Basic Logs – PESY
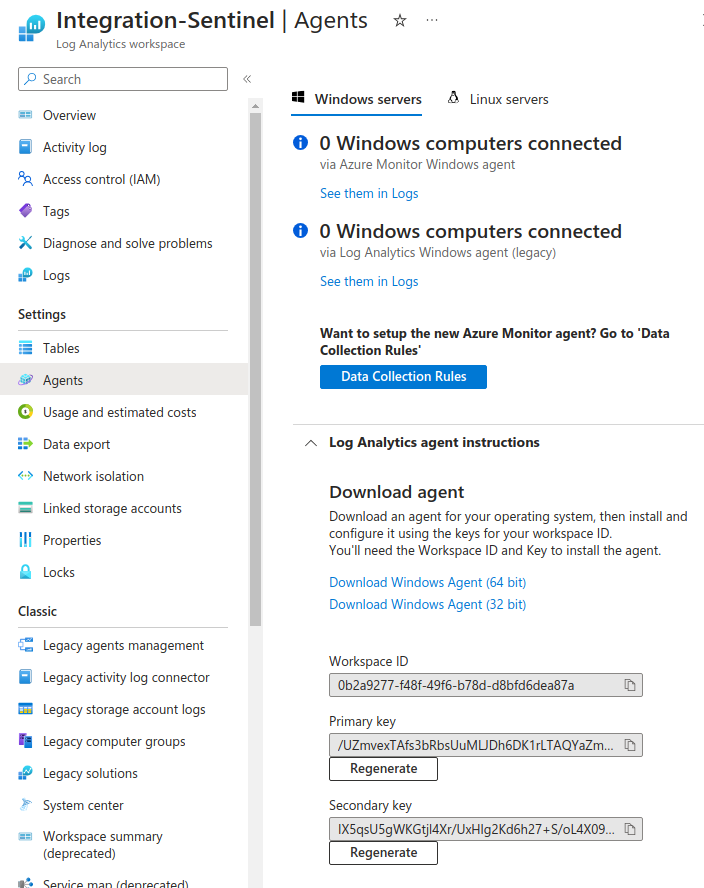
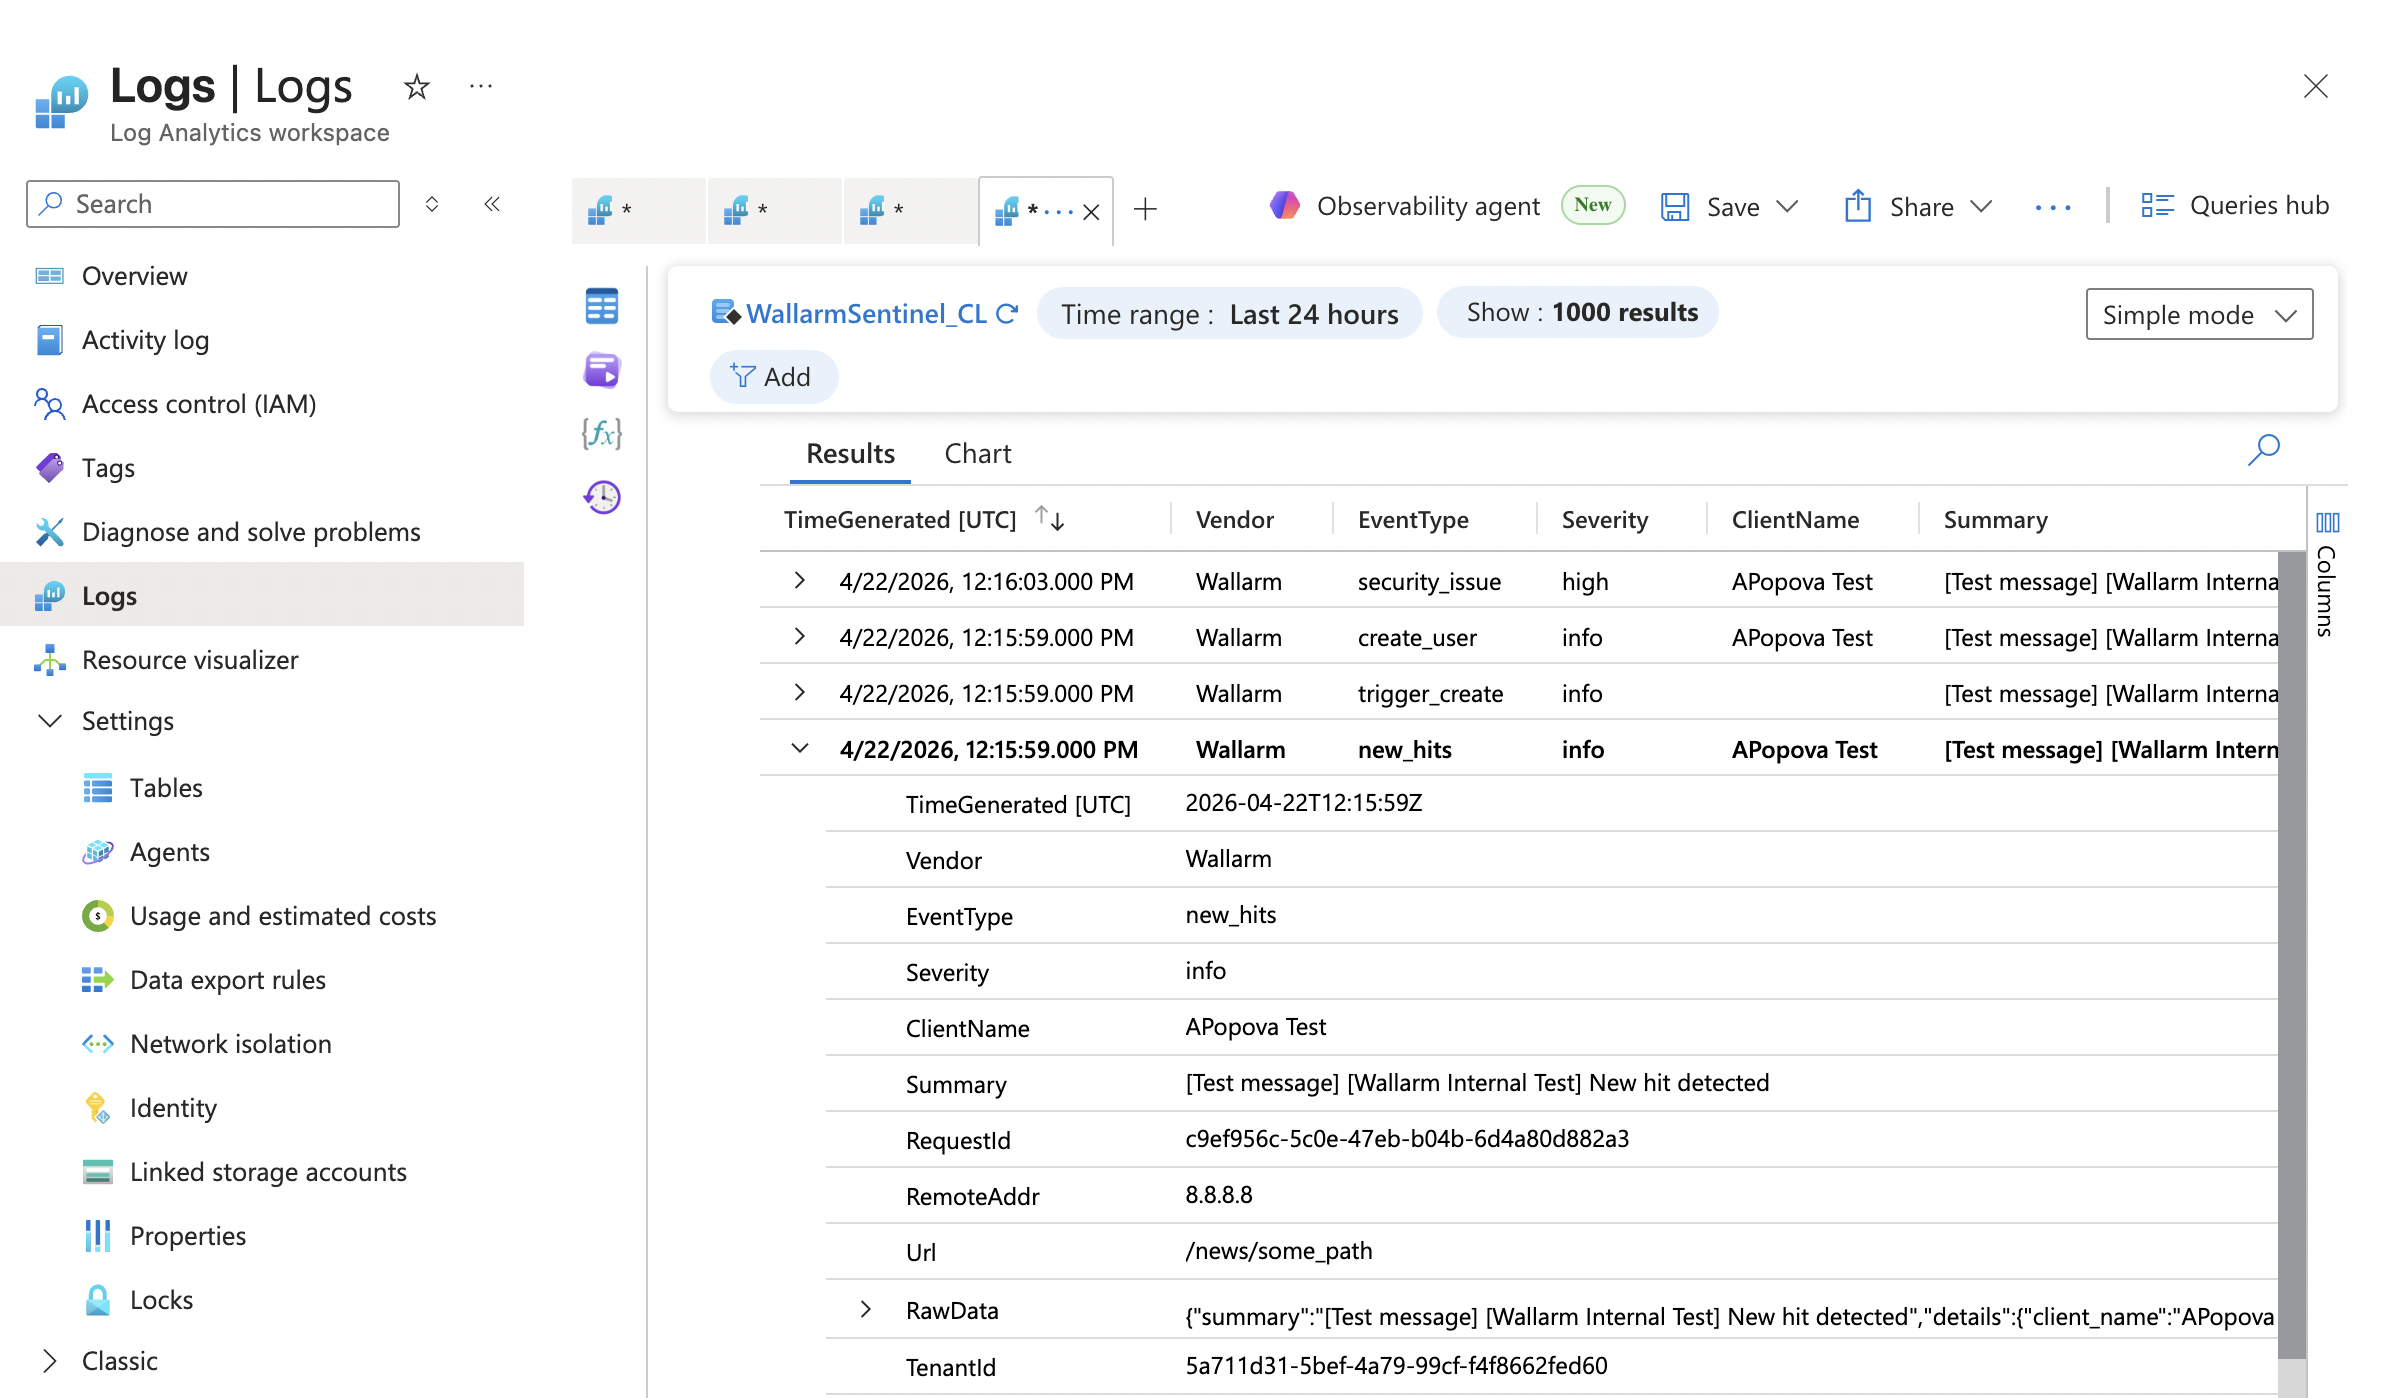
Azure Monitor Logs / Microsoft Sentinel - Wallarm Documentation
Forward Logs to Microsoft Sentinel with a Private Link 43
Oracle Exadata Database on Dedicated Infrastructure Logs on Azure for ...
Translate raw security logs to behavioral insights using UEBA behaviors ...
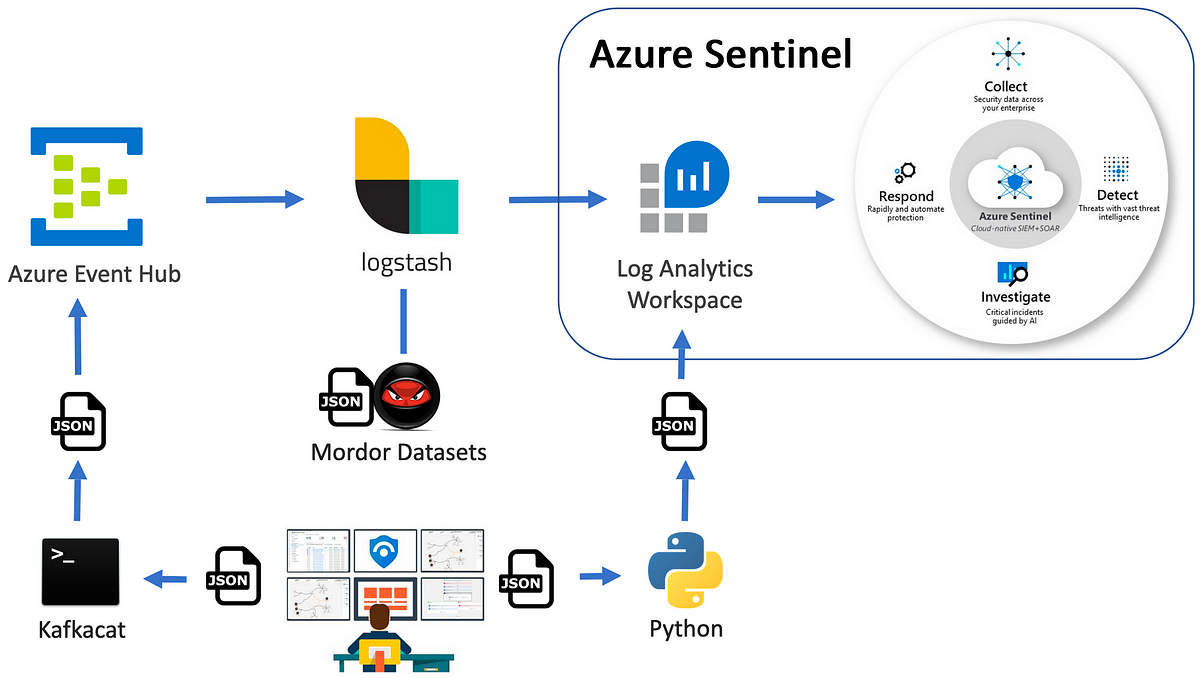
Logstash Azure Log Analytics | Logstash: Collect, Parse, Transform Logs ...
How to optimize logs in Microsoft Sentinel | ☁️ Charbel N. posted on ...
Sentinelone Access Logs | How To Collect Logs – MKDOKR
How to Collect Sentinelone Logs from the Windows , MAC and Linux
Effective Approach To Collect Linux Logs to Microsoft Sentinel 12
How to collect SentinelOne Agent logs on Linux Machine
Auxiliary Logs Transformations in Microsoft Sentinel: A Step-by-Step ...
Ingest and analyze AWS security logs in Microsoft Sentinel - AWS ...
Sentinel Log Format – Microsoft Sentinel Logs – SQMKS
Connecting Defender EASM logs to Sentinel workspace – CIAOPS
Effective Approach To Collect Linux Logs to Microsoft Sentinel 34
Store Microsoft Sentinel Logs via Azure Data Explorer
Setting up Sentinel to get logs from multiple regions - Microsoft Q&A
Ingest Firewall logs into Sentinel Auxiliary Logs tier using Logstash ...
Azure Sentinel – logs retention | A Security Engineer
Forward Logs to Microsoft Sentinel with a Private Link 44
Microsoft Sentinel - Archiving Logs Guide - Gennaro Migliaccio
Move Microsoft Sentinel Logs to Long-Term Storage
Microsoft Sentinel - Ingesting Windows Server Event Logs from Azure VMs ...
how to send MYSQL audit logs to Sentinel? - Microsoft Q&A
Microsoft Sentinel Ingest Logs from Linux Machines - YouTube
Ingest Custom Logs to Microsoft Sentinel: A Step-by-Step Guide 7
Adding Active Directory Logs to Microsoft Sentinel | Practical365
Ingest Custom Logs to Microsoft Sentinel: A Step-by-Step Guide 21
Microsoft Sentinel - Ingesting Windows Server Event Logs via Azure Arc ...
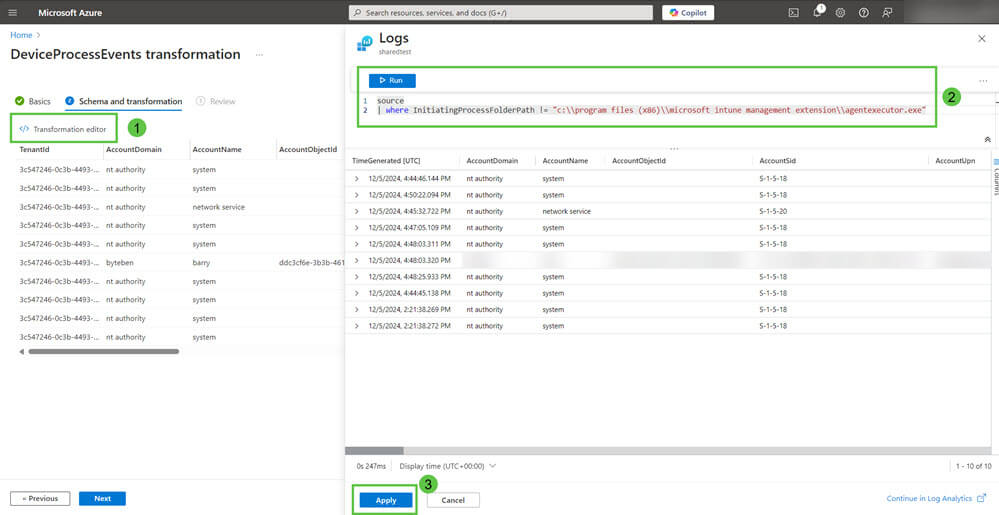
Optimize Sentinel Logs for Intune via Defender XDR - Patch My PC
Custom Logs in Sentinel not triggering incidents or showing up in ...
How To Ingest Logs From On-Premises Windows Server To Microsoft ...
Azure Sentinel logs - Check Point CheckMates
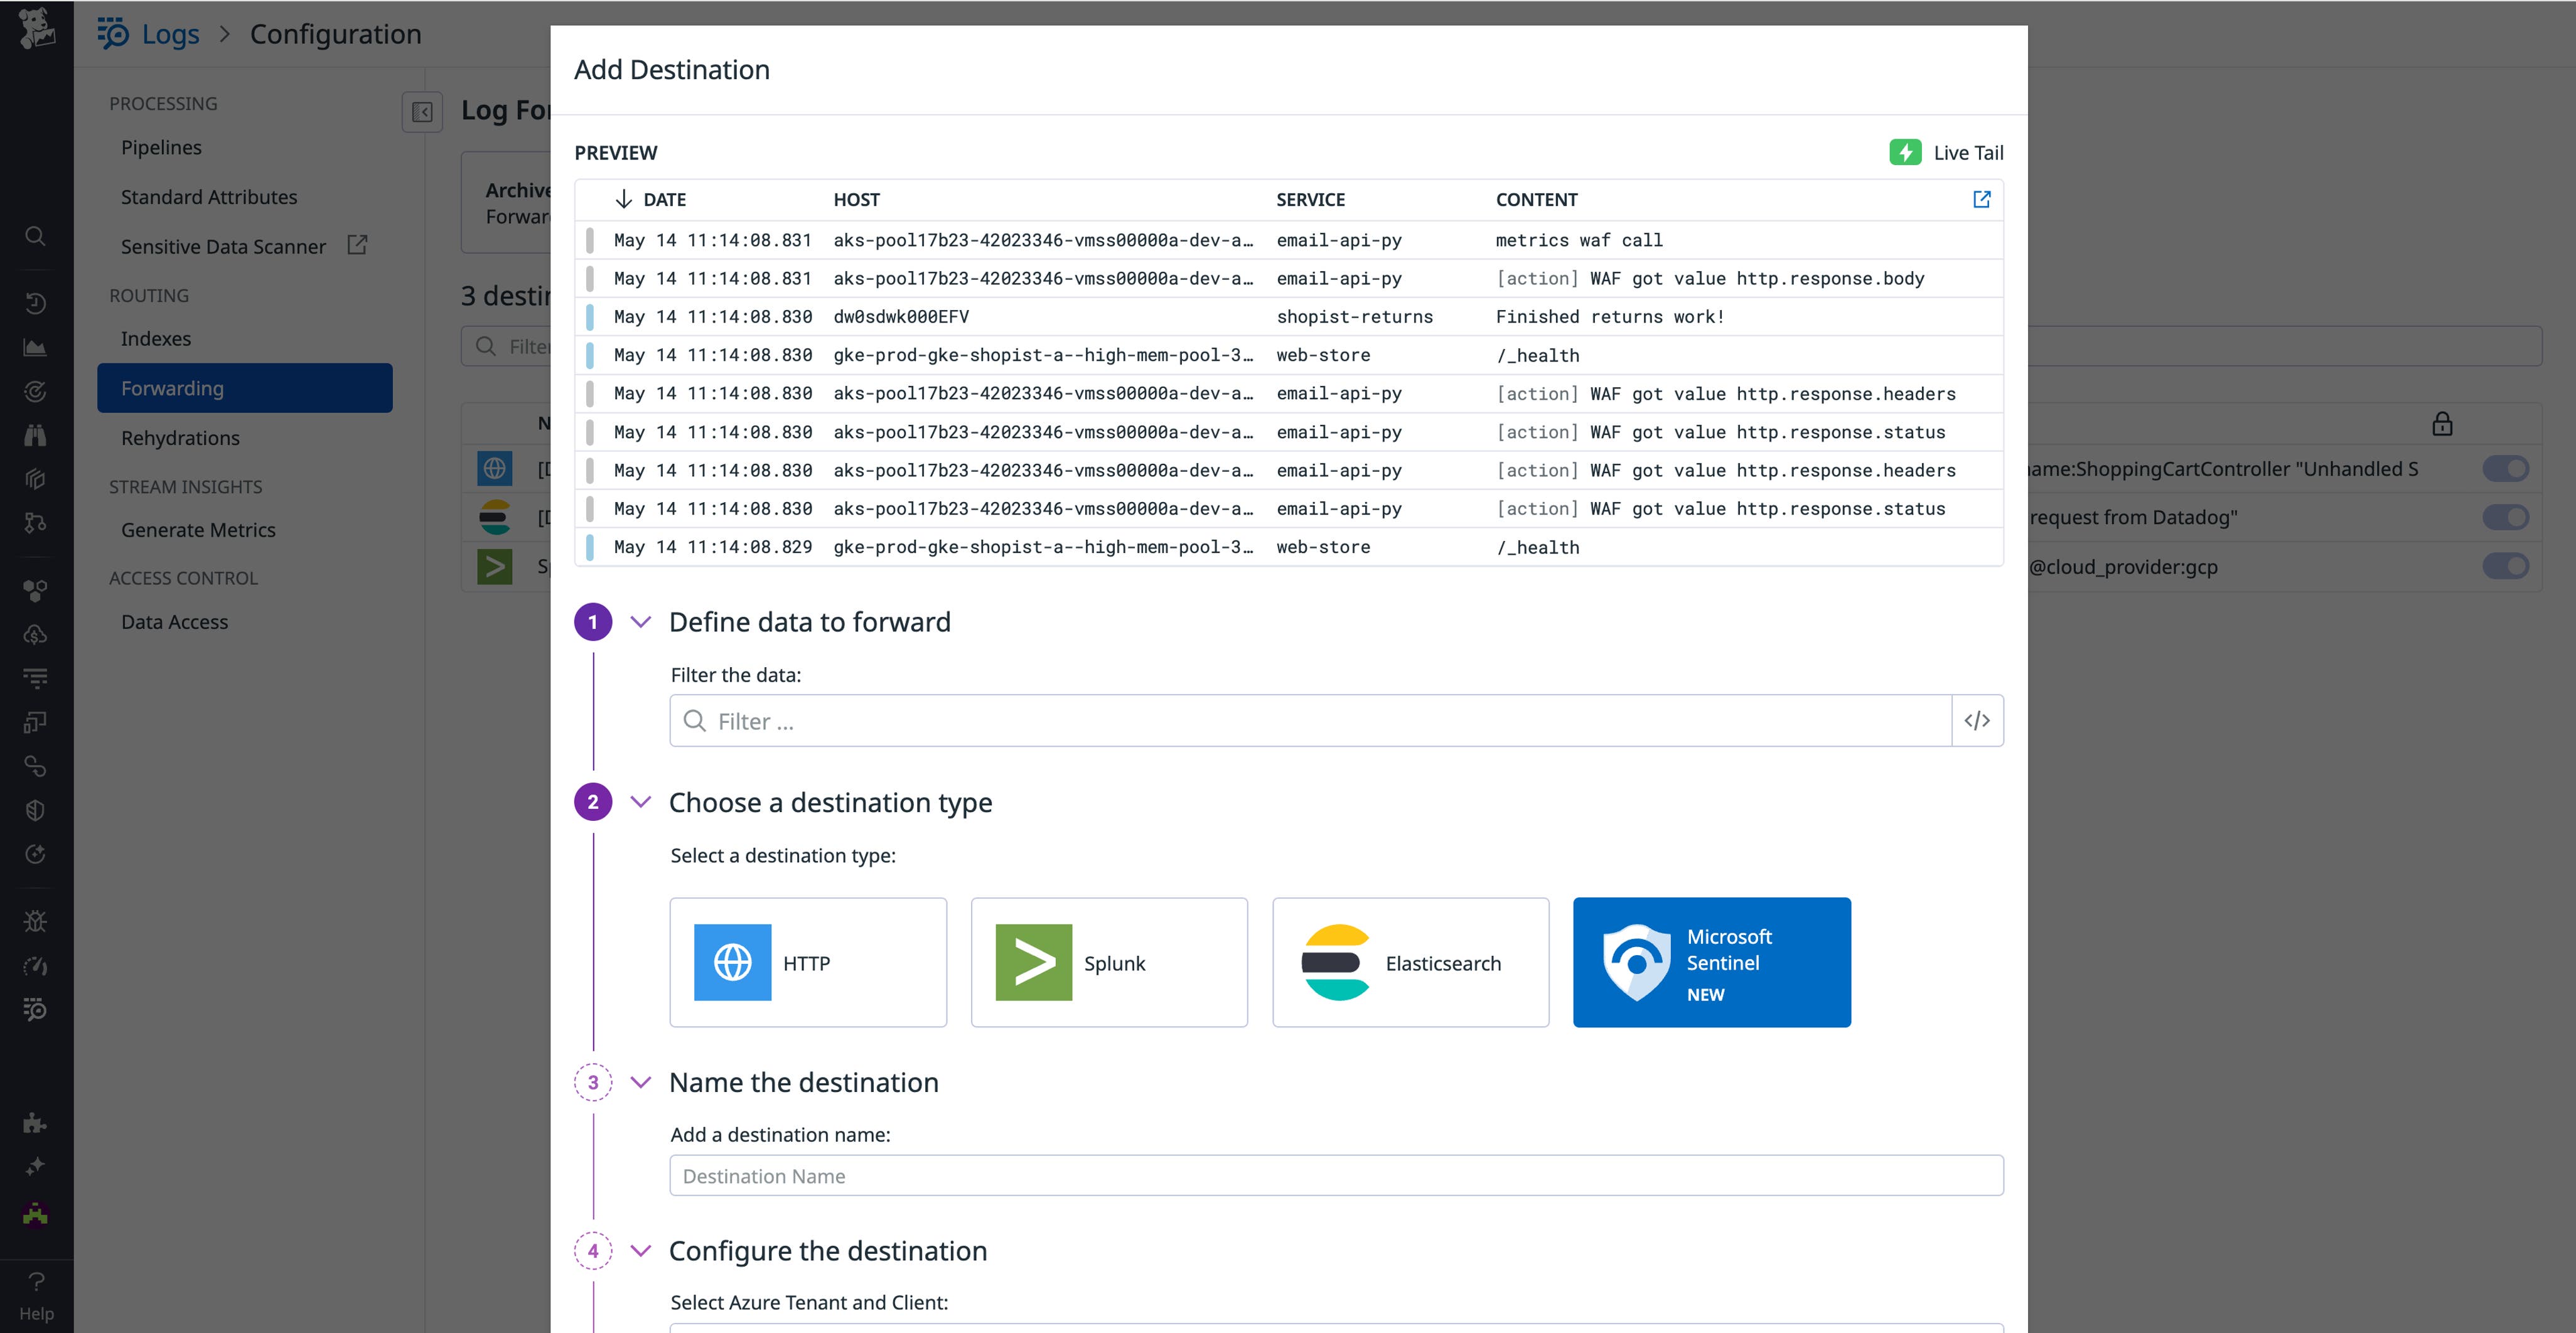
Centrally process and govern your logs in Datadog before sending them ...
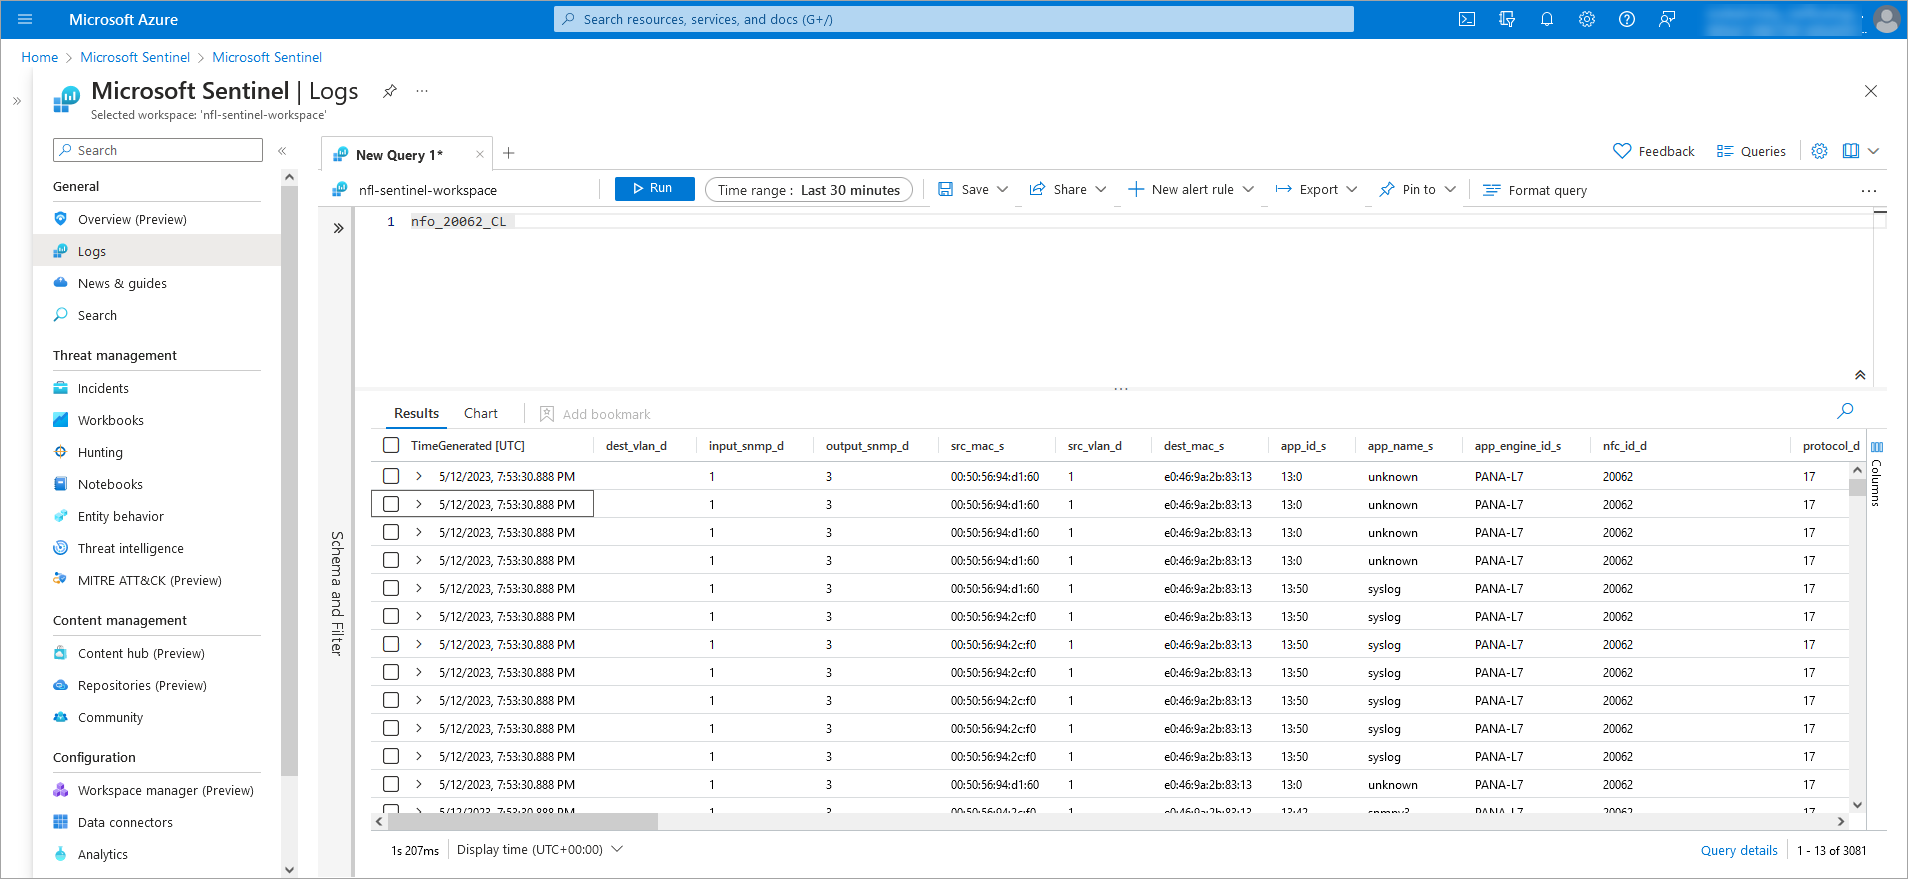
Microsoft Sentinel Integration | NetFlow Logic
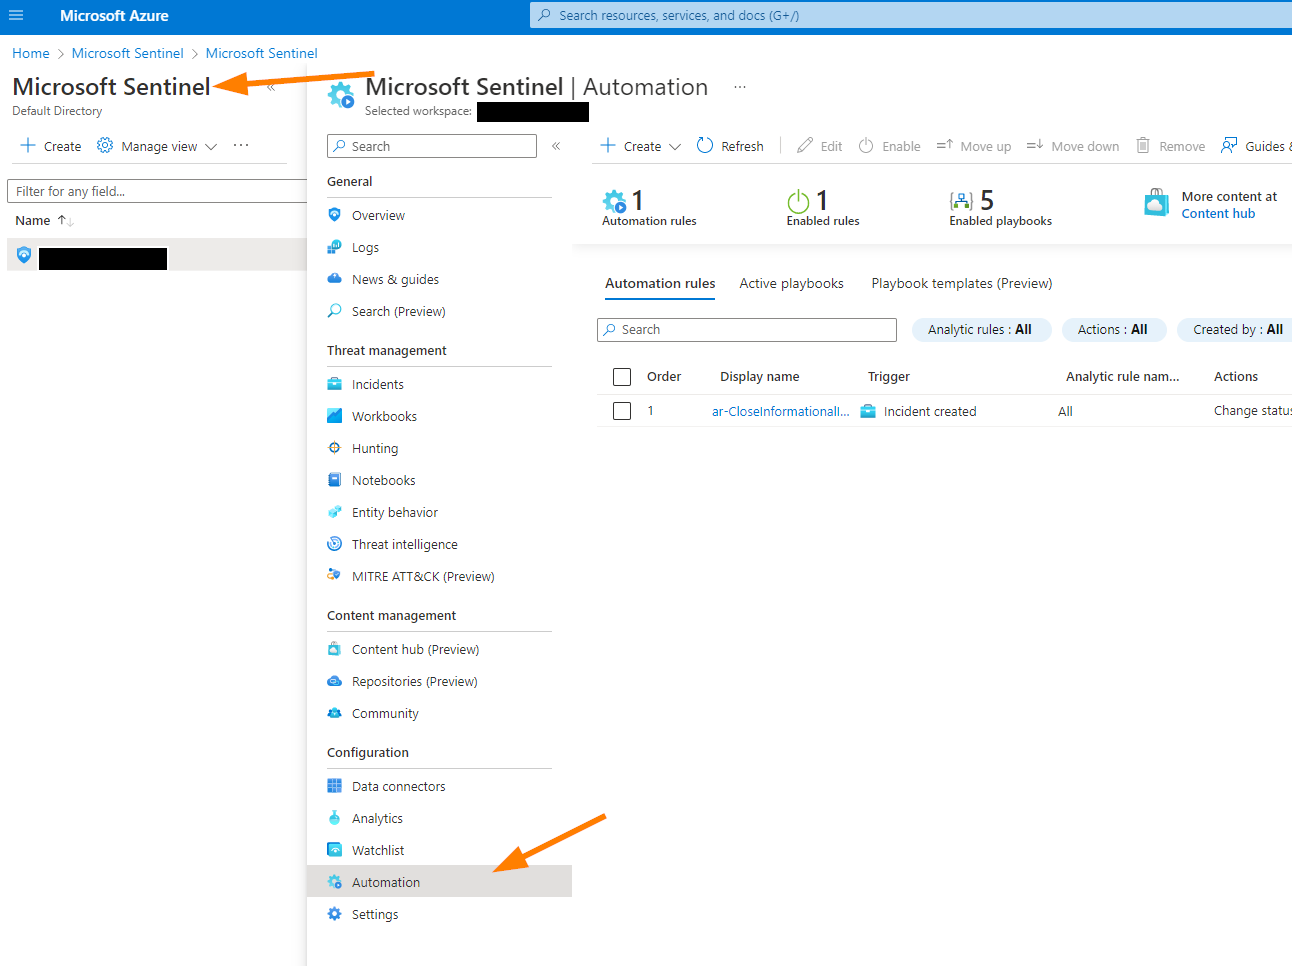
Onboard to Microsoft Sentinel | Microsoft Learn
Creating and onboarding a Syslog Forwarder into Sentinel (Azure VM) (Easy)
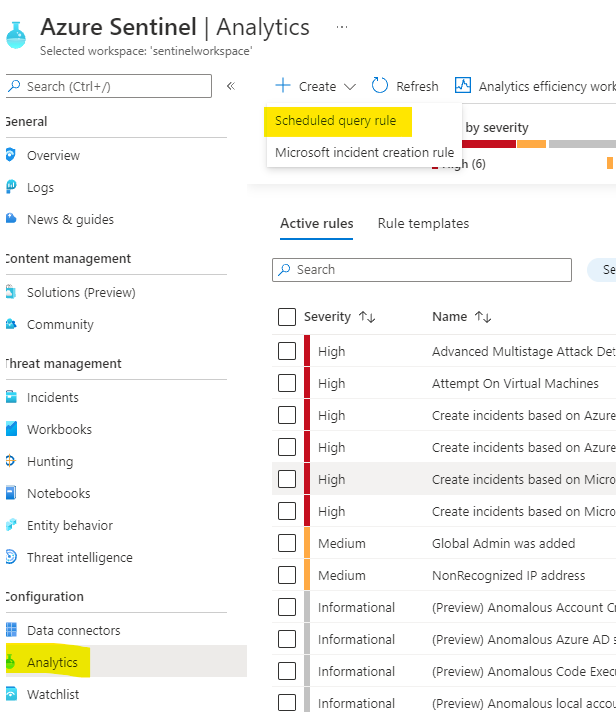
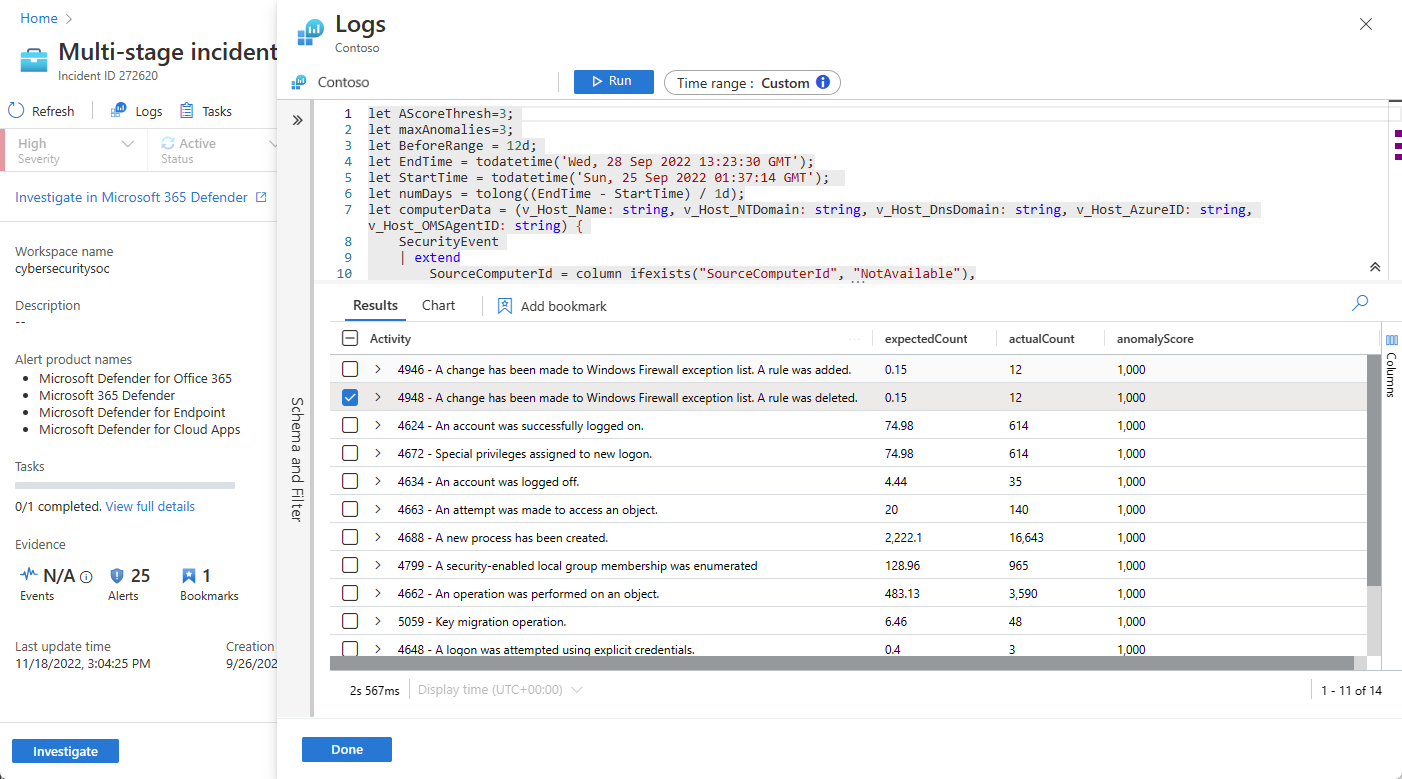
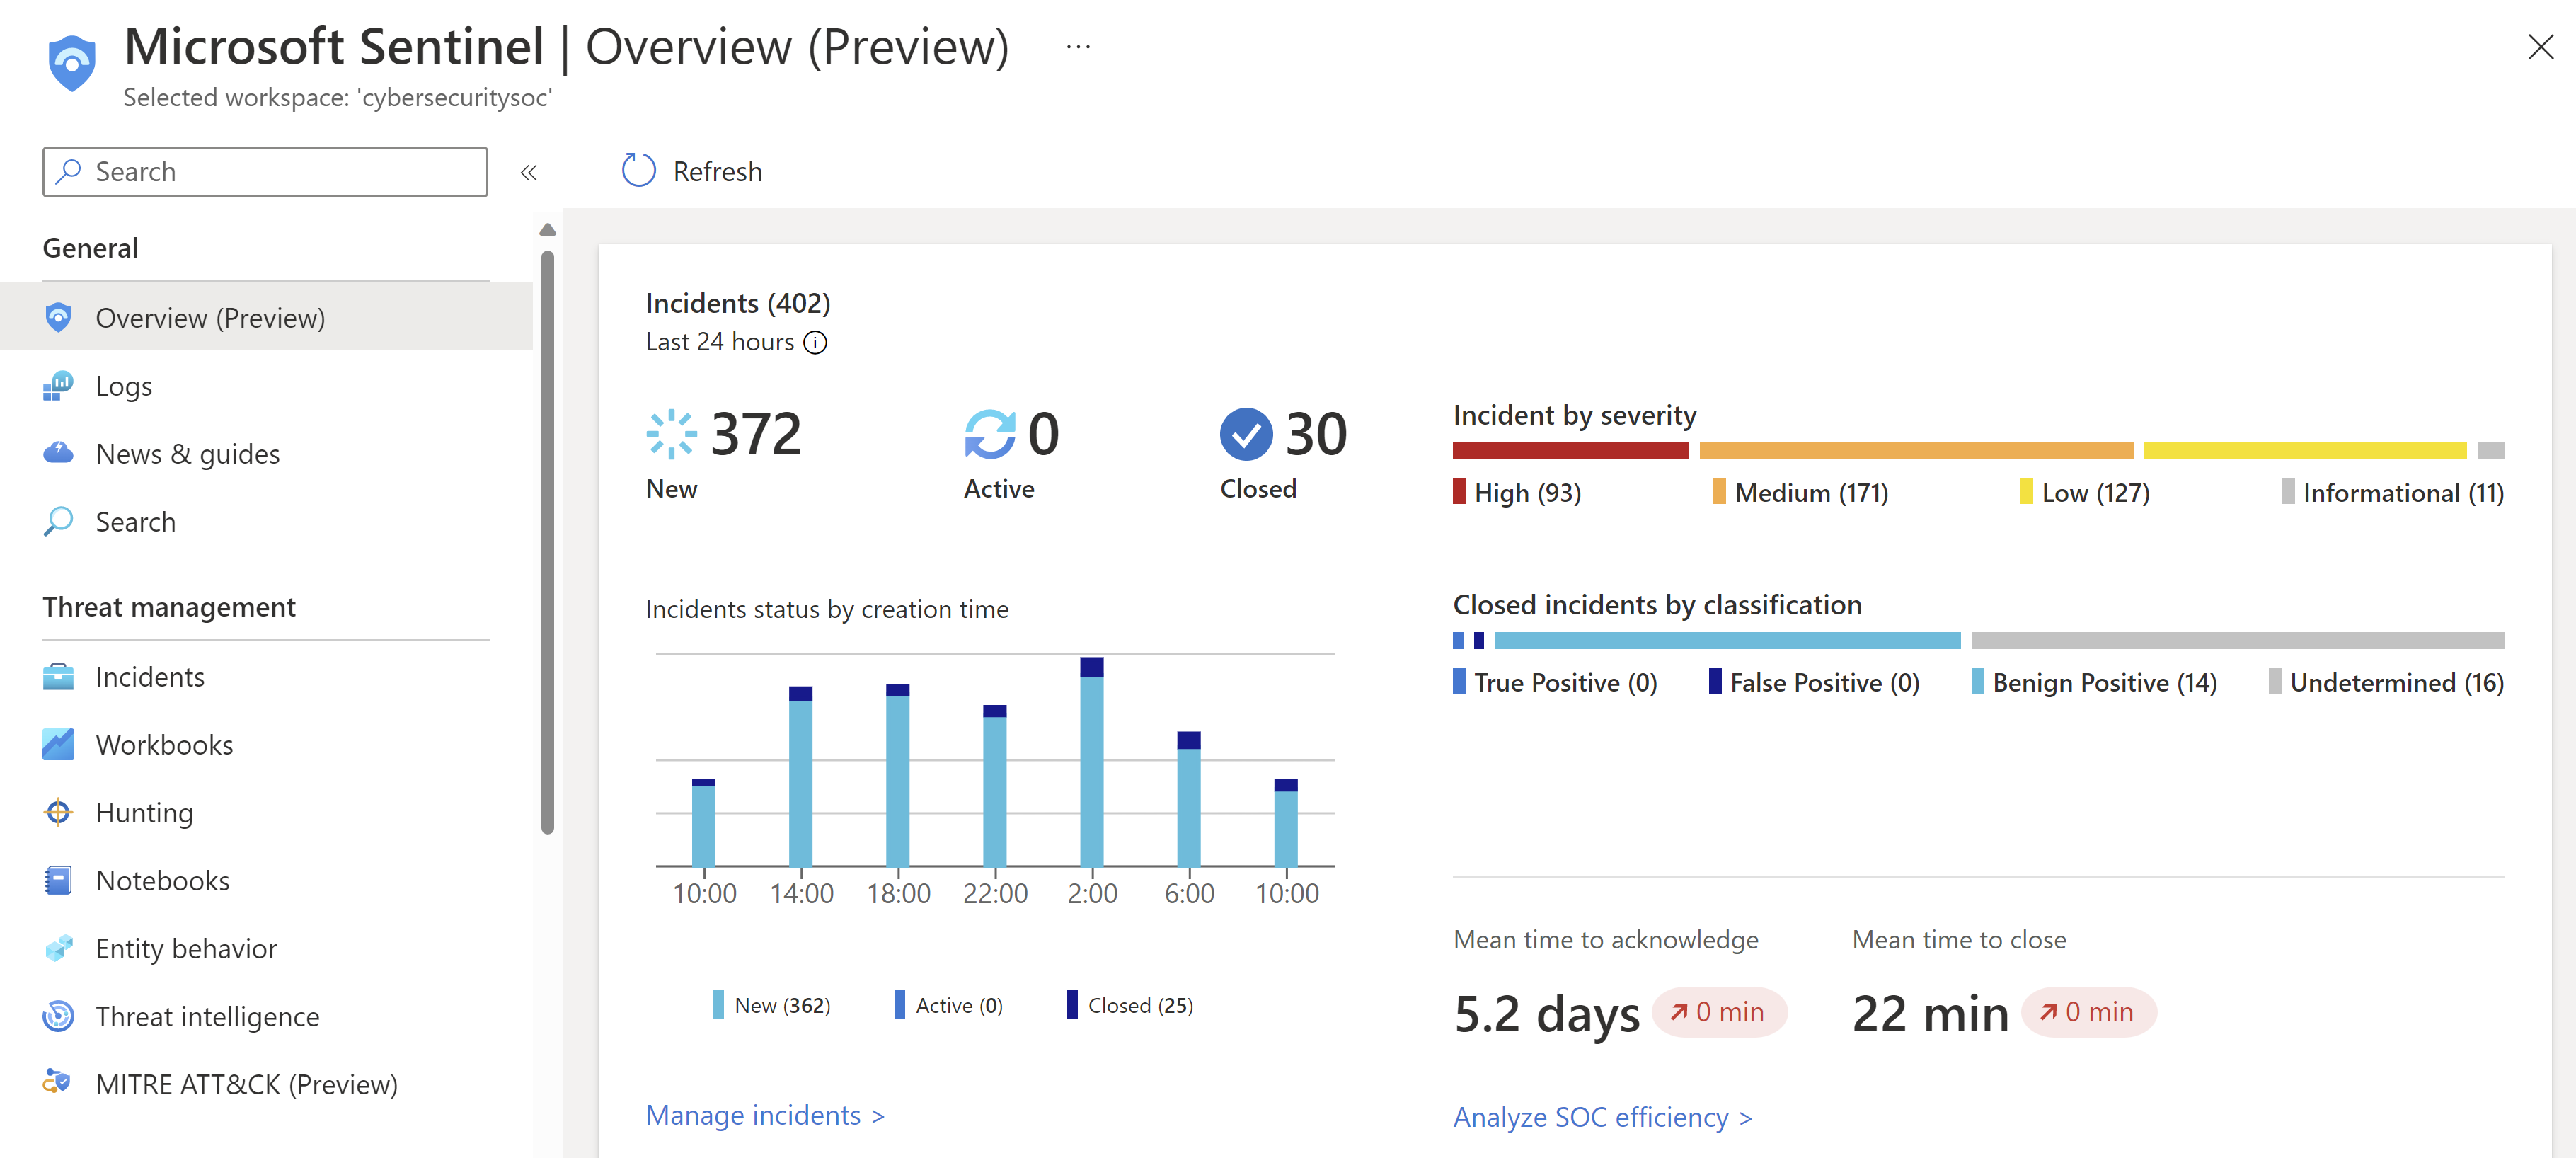
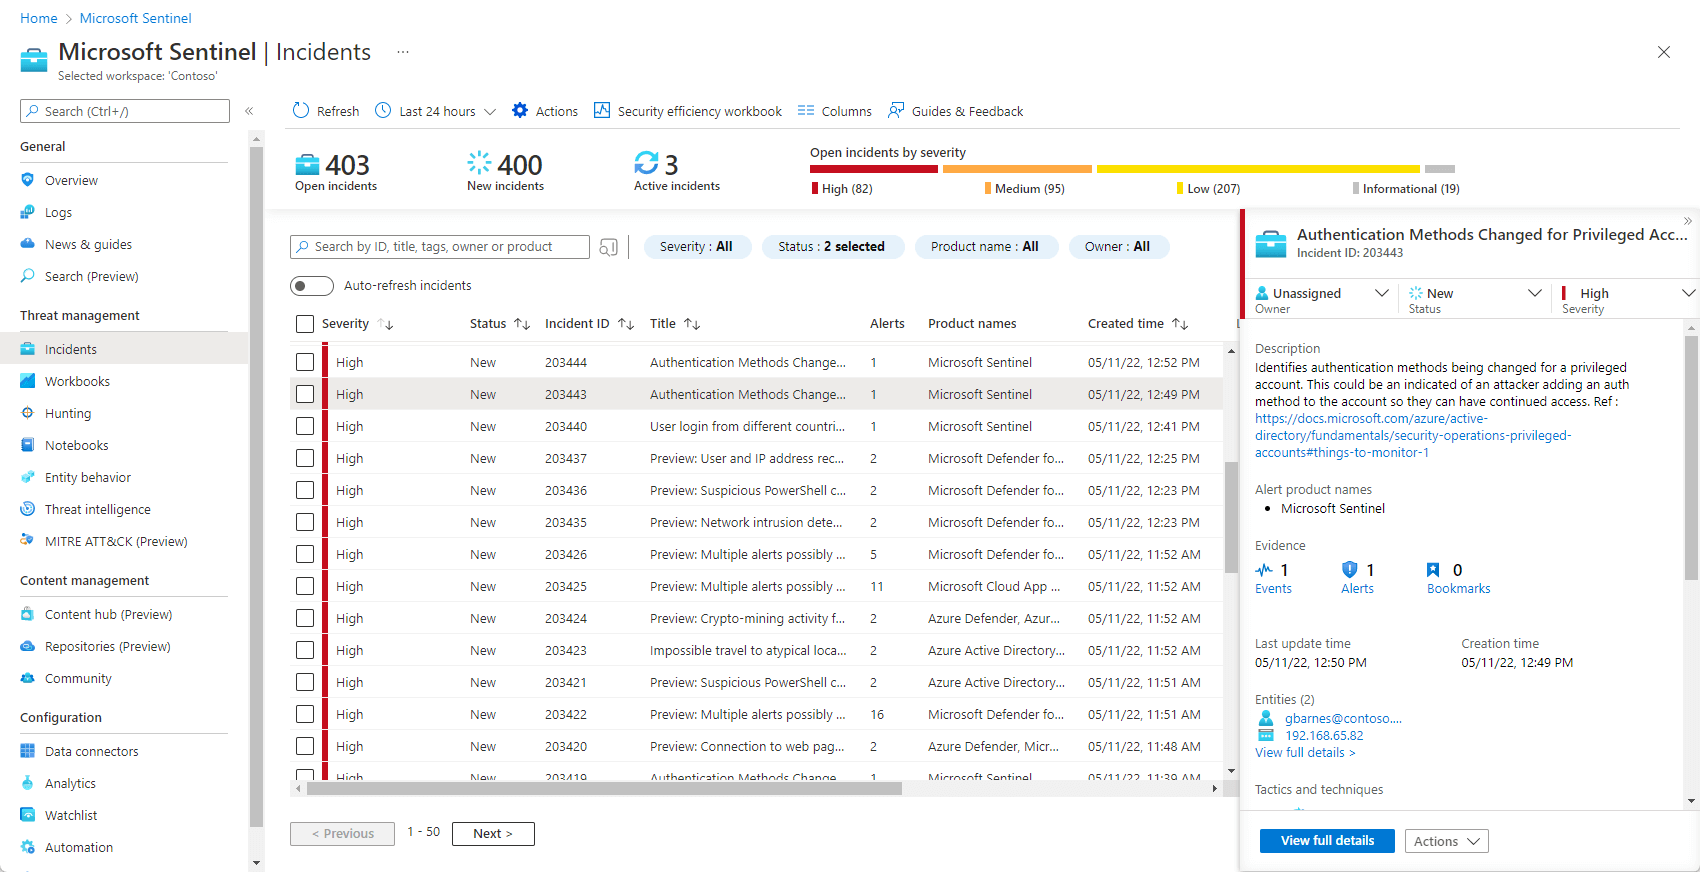
Investigate Microsoft Sentinel incidents in depth in the Azure portal ...
Configure data connections to Sentinel - KodeKloud
Collect, detect, investigate, and respond to security threats using ...
Sentinel Data Connector Health Monitoring – AzureTracks
Microsoft Sentinel integration – Help Center
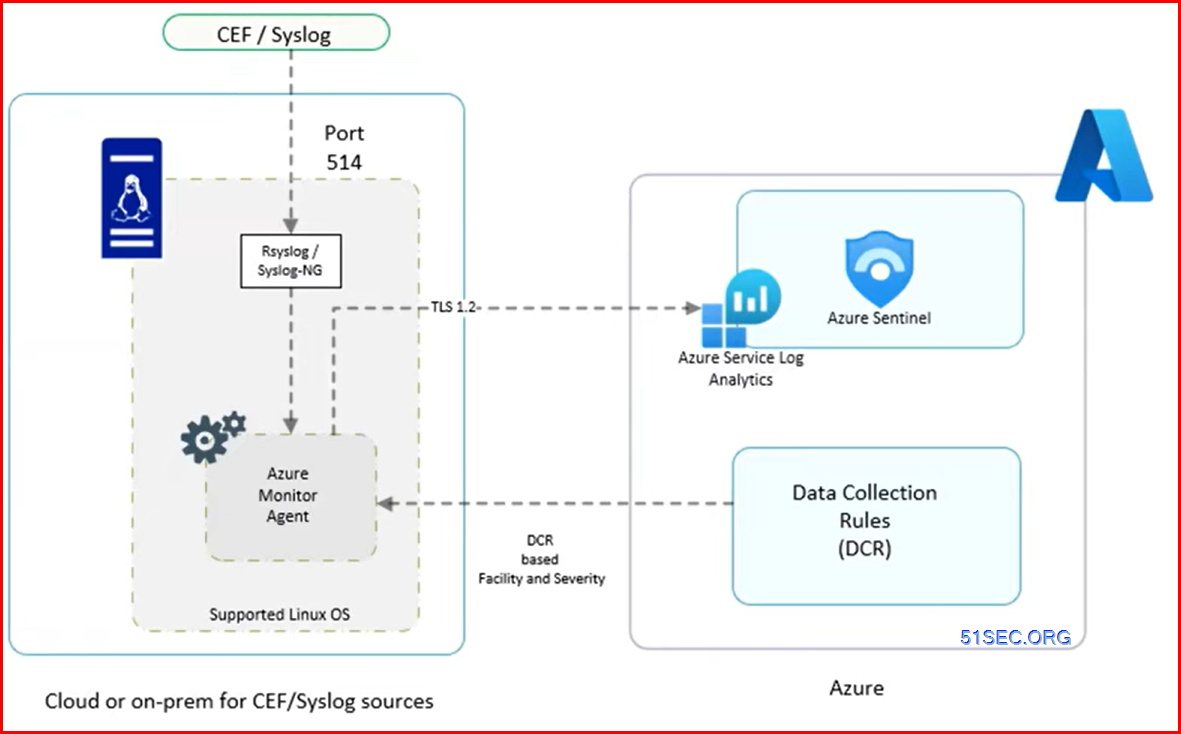
Configuring Sentinel to Collect CEF Syslog with the AMA agent – Simple ...
CTF Writeup: MS Sentinel: Just Looking | CTFs | OSINT | InfoSec
Set Up HTTPS Log Forwarding to Microsoft Sentinel
Azure HomeLabs | Isaac Park blog
Optimize Microsoft Sentinel Log Retention With Azure Data Explorer ...
Optimize Log Ingestion And Access In Microsoft Sentinel - CHARBEL ...
TryHackMe | SOC Alert Triaging - Tinsel Triage
Apa itu Microsoft Sentinel SIEM? | Microsoft Learn
Sentinel-Log-Ingestion-Resiliency | EXMDR
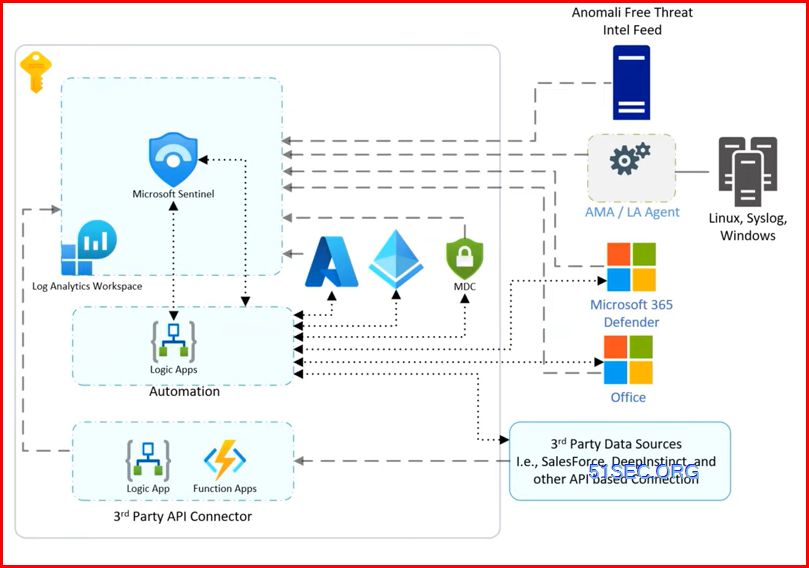
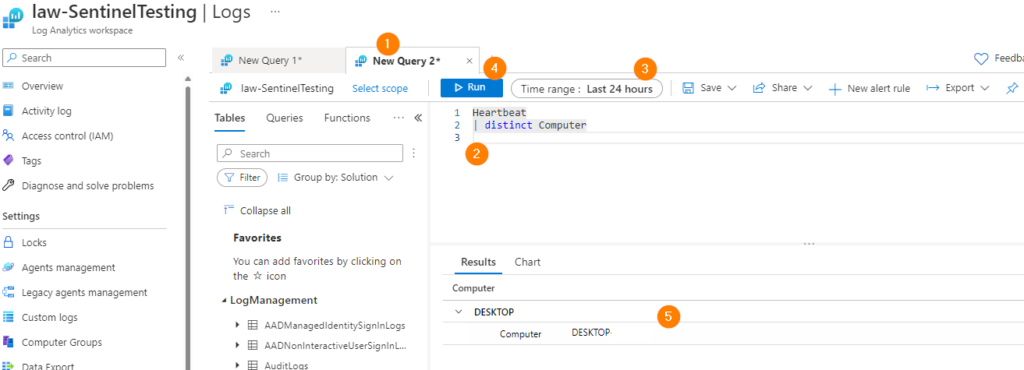
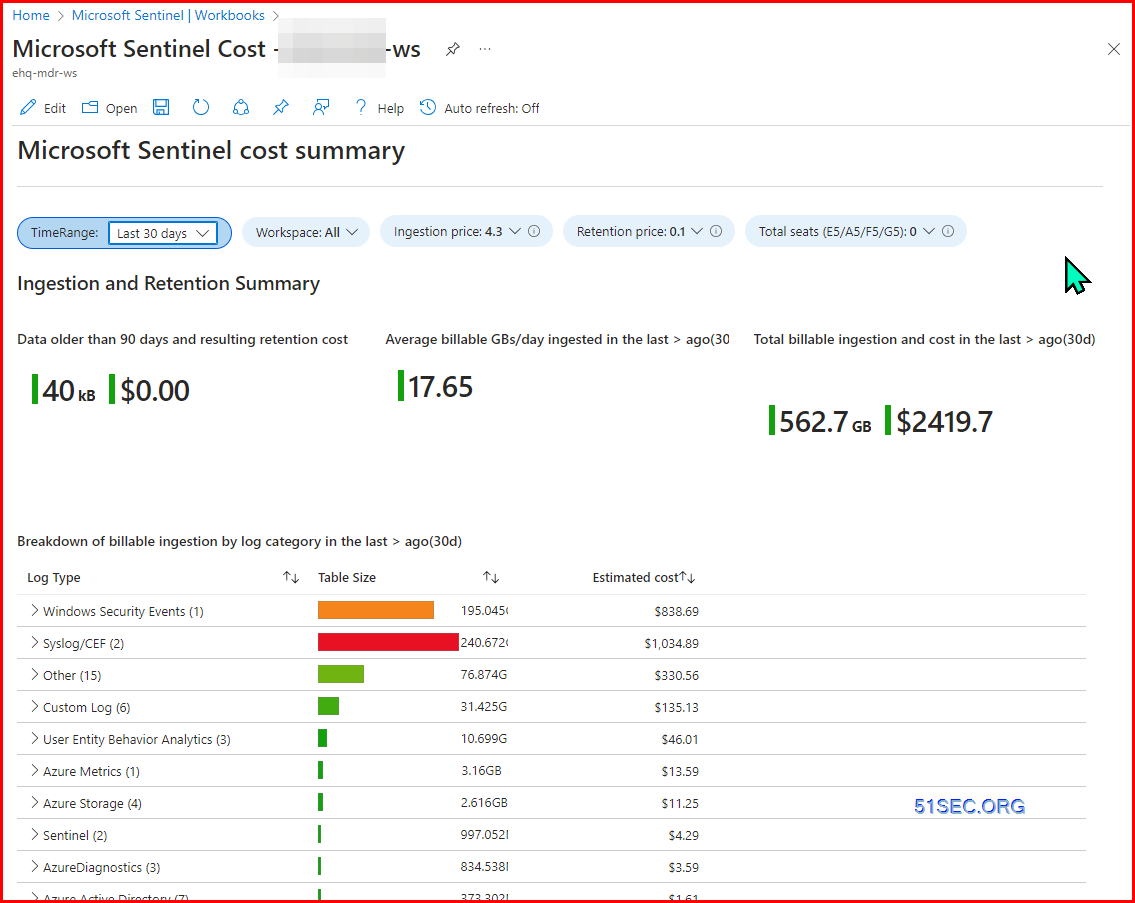
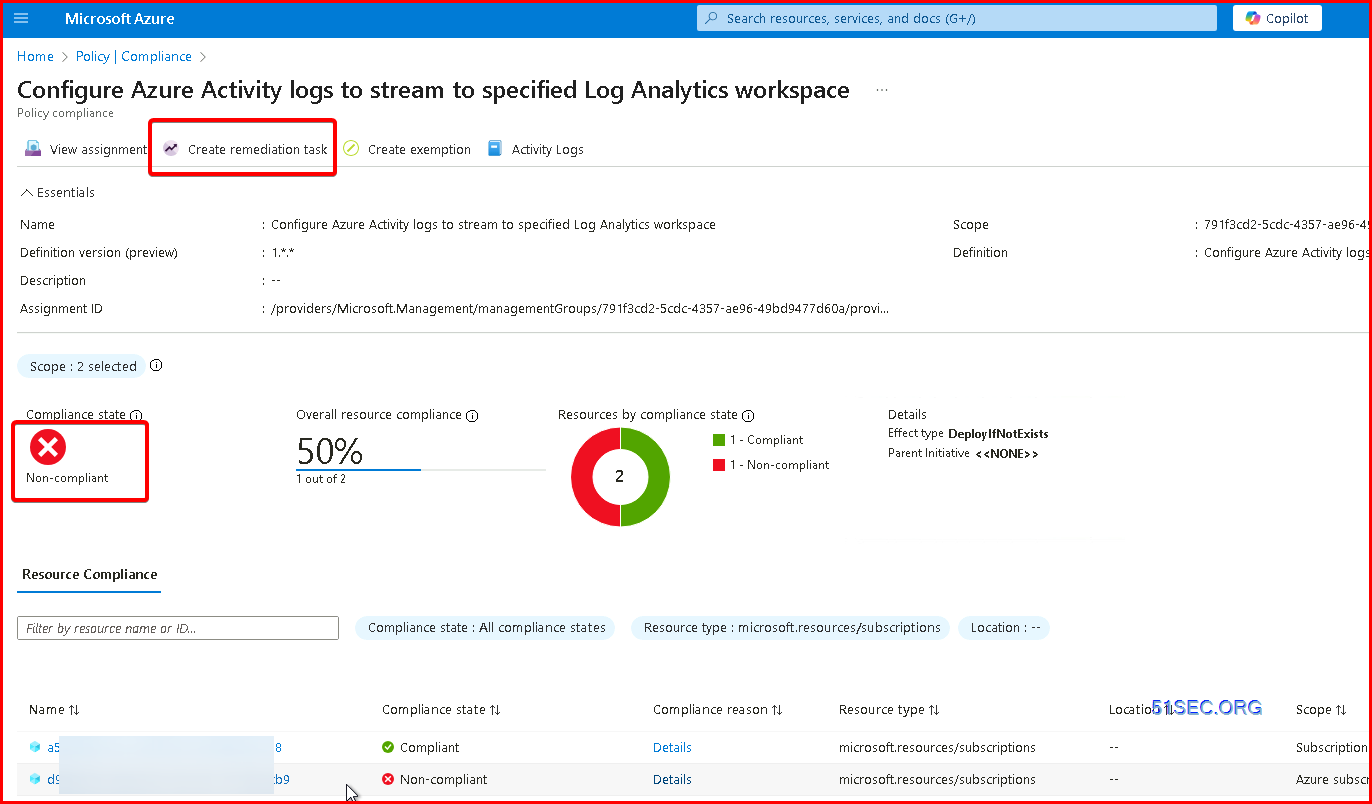
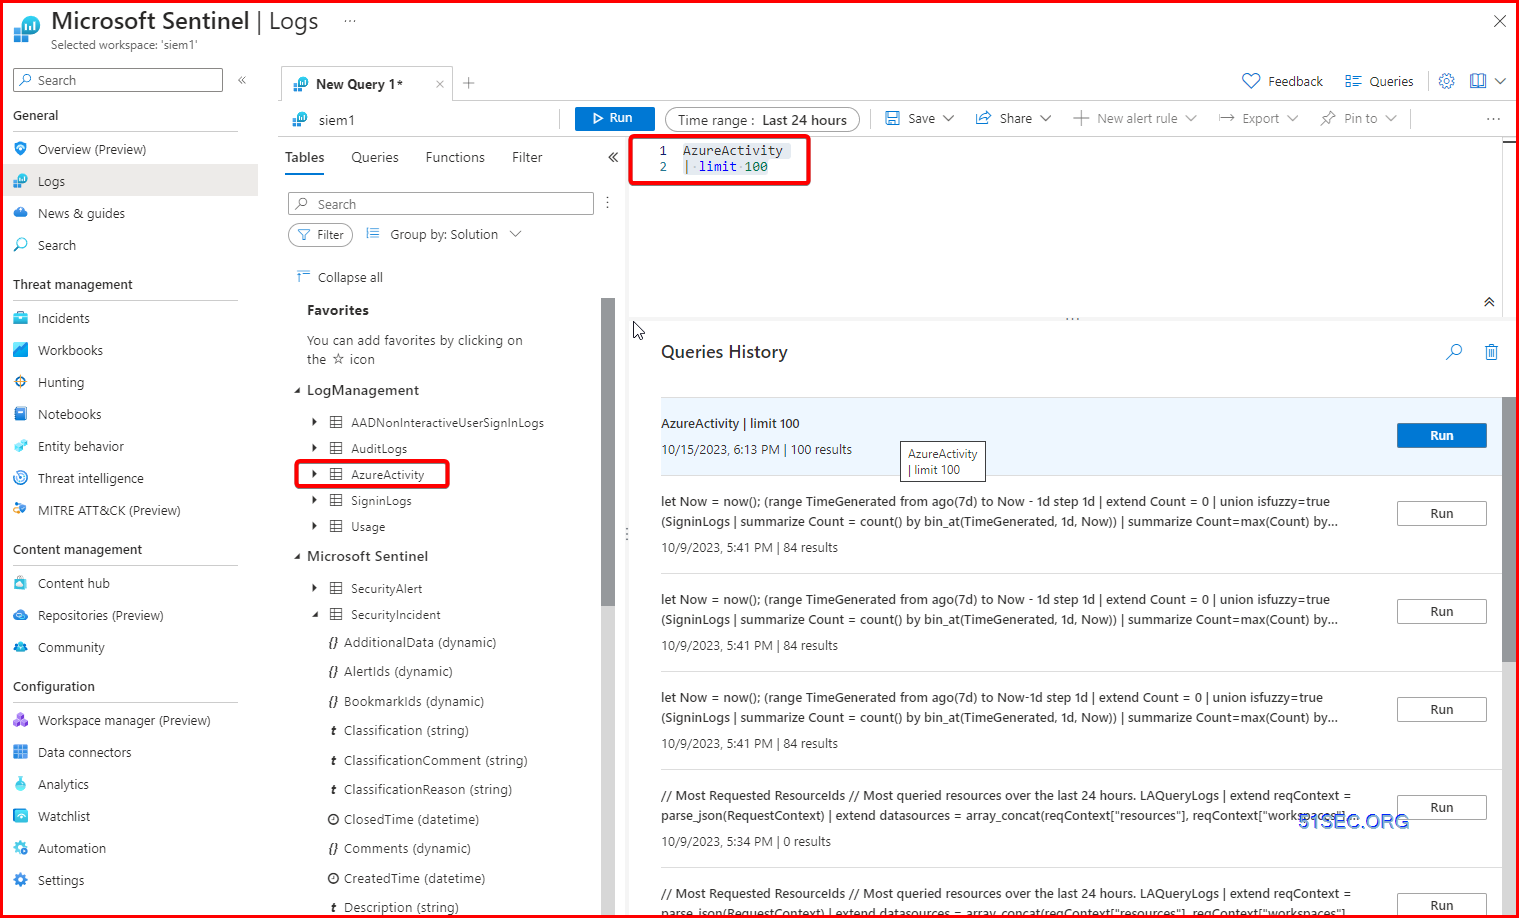
Azure Sentinel Onboarding All Kinds Of Log Sources – 51 Sec
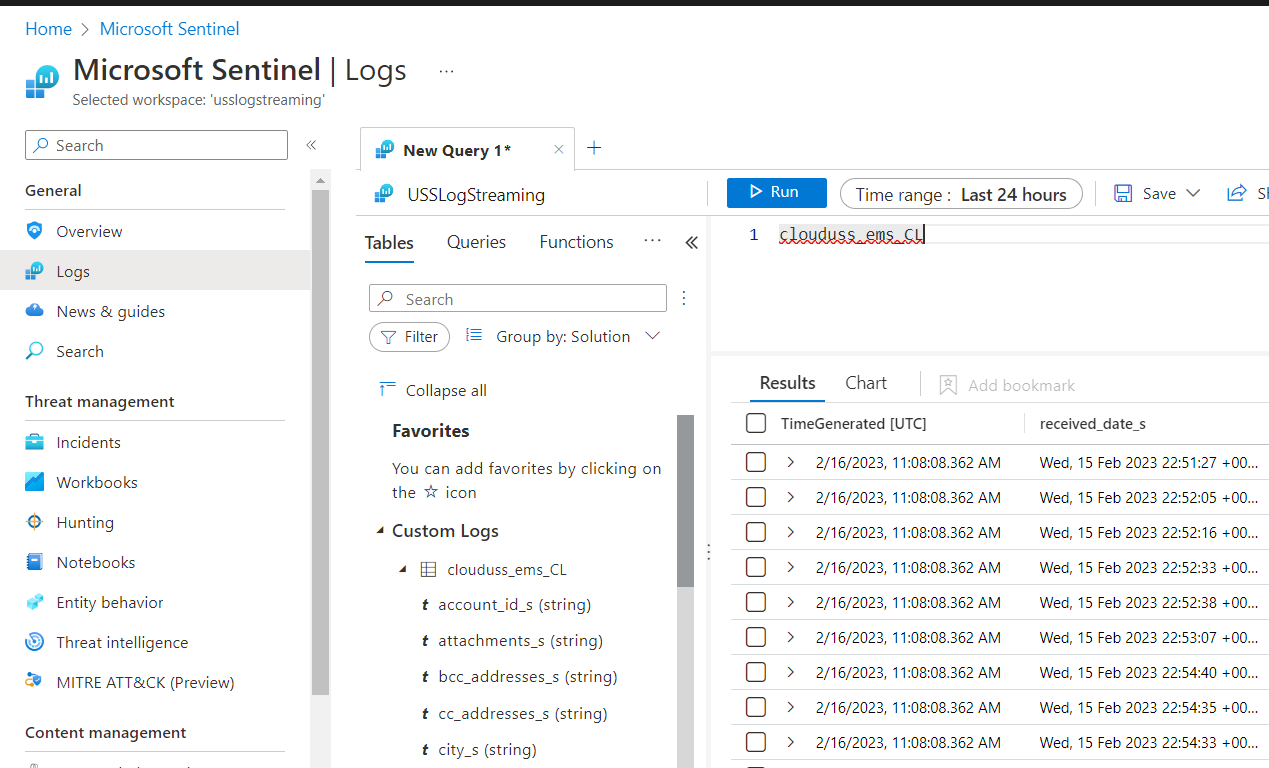
Log Streaming to Microsoft Sentinel - Help :: Unified Security Service
High Volume of Entra ID Sign-In Errors (Code 70043) Triggering MS ...
Sentinel & Log Analytics – Where is my Data? – AzureTracks
Sentinel Log Forwarder
Setting Up Azure Sentinel for Advanced Security Log Capture
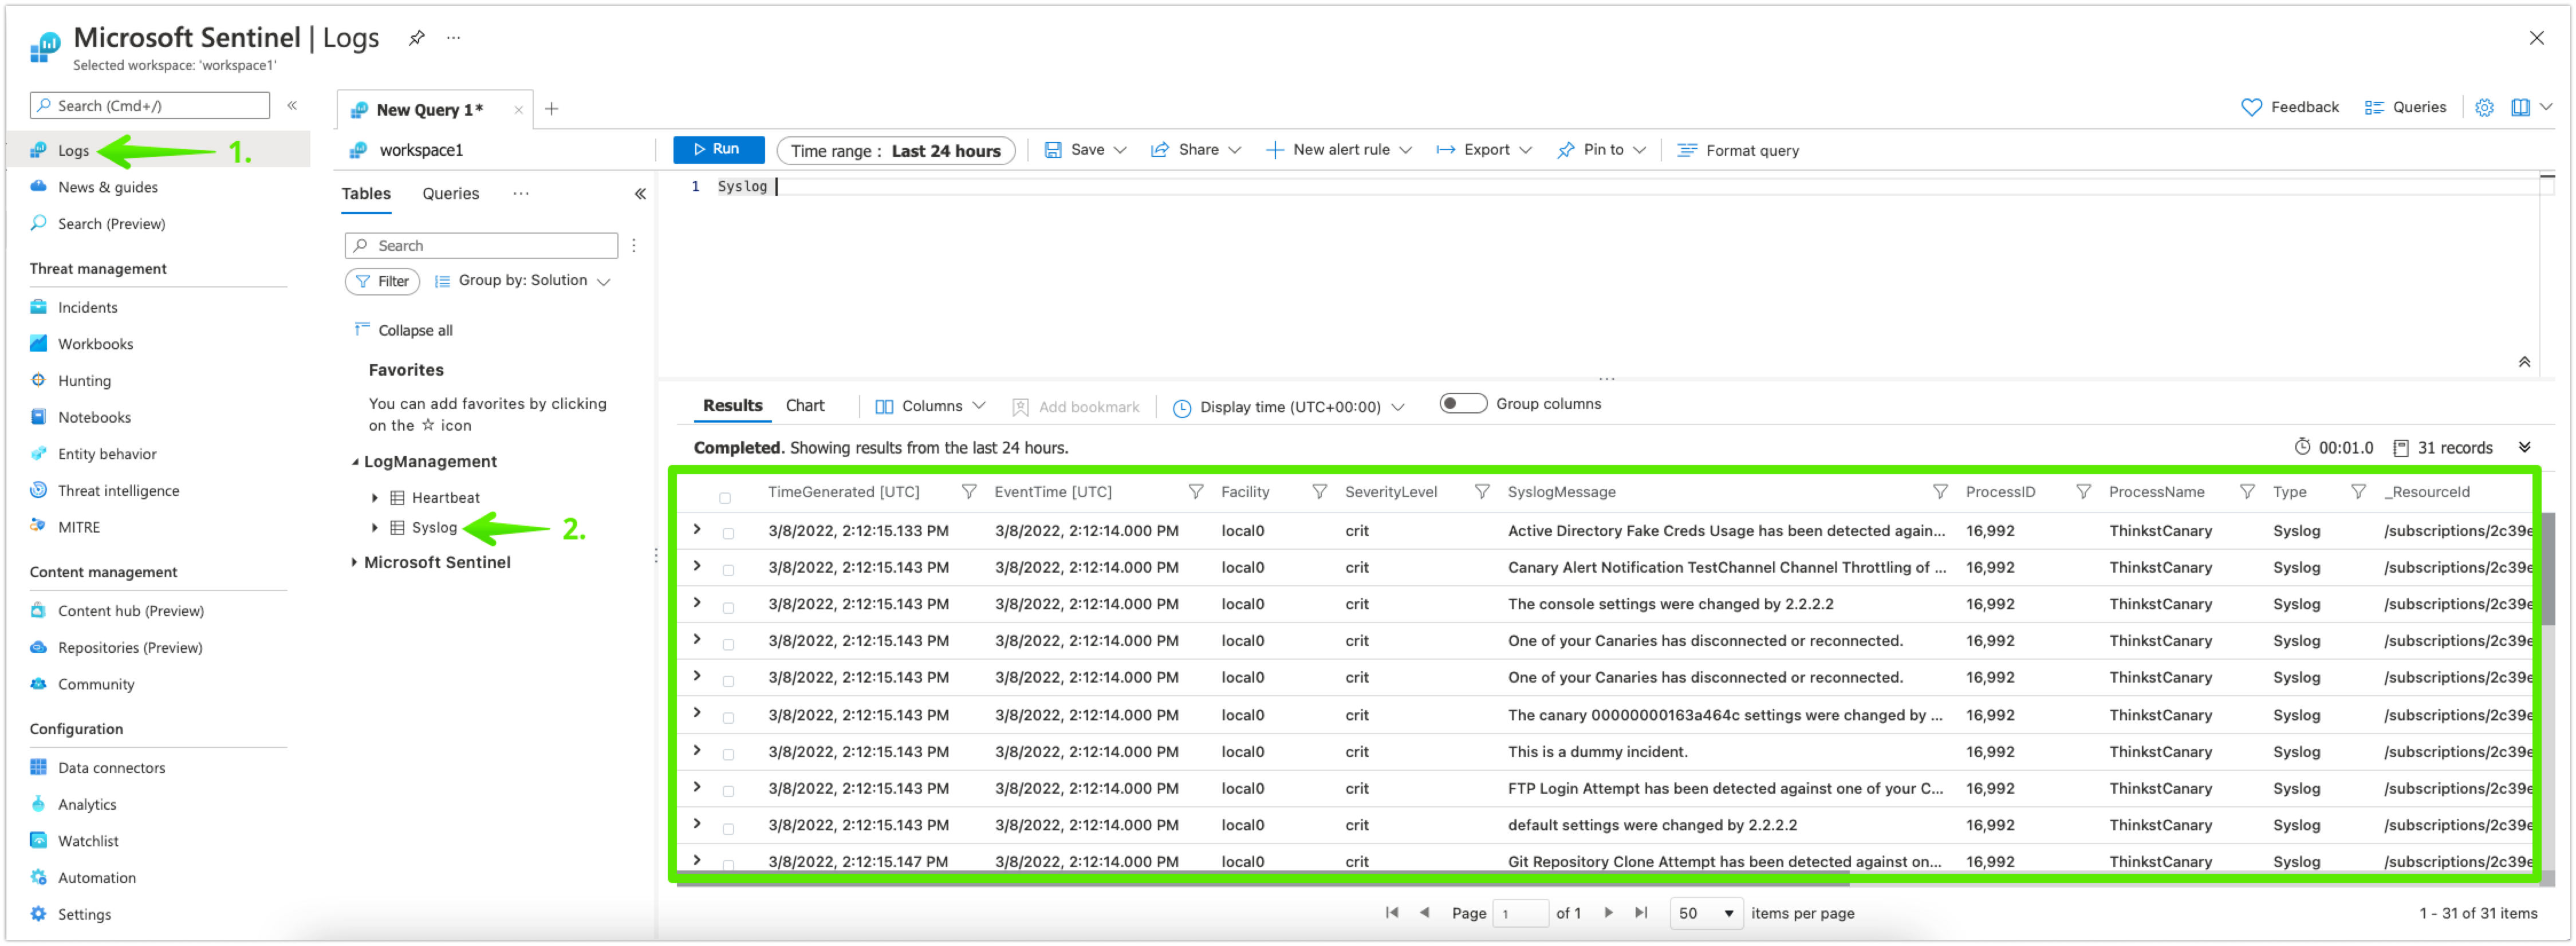
Sending alerts to Microsoft Sentinel with syslog – Thinkst Canary
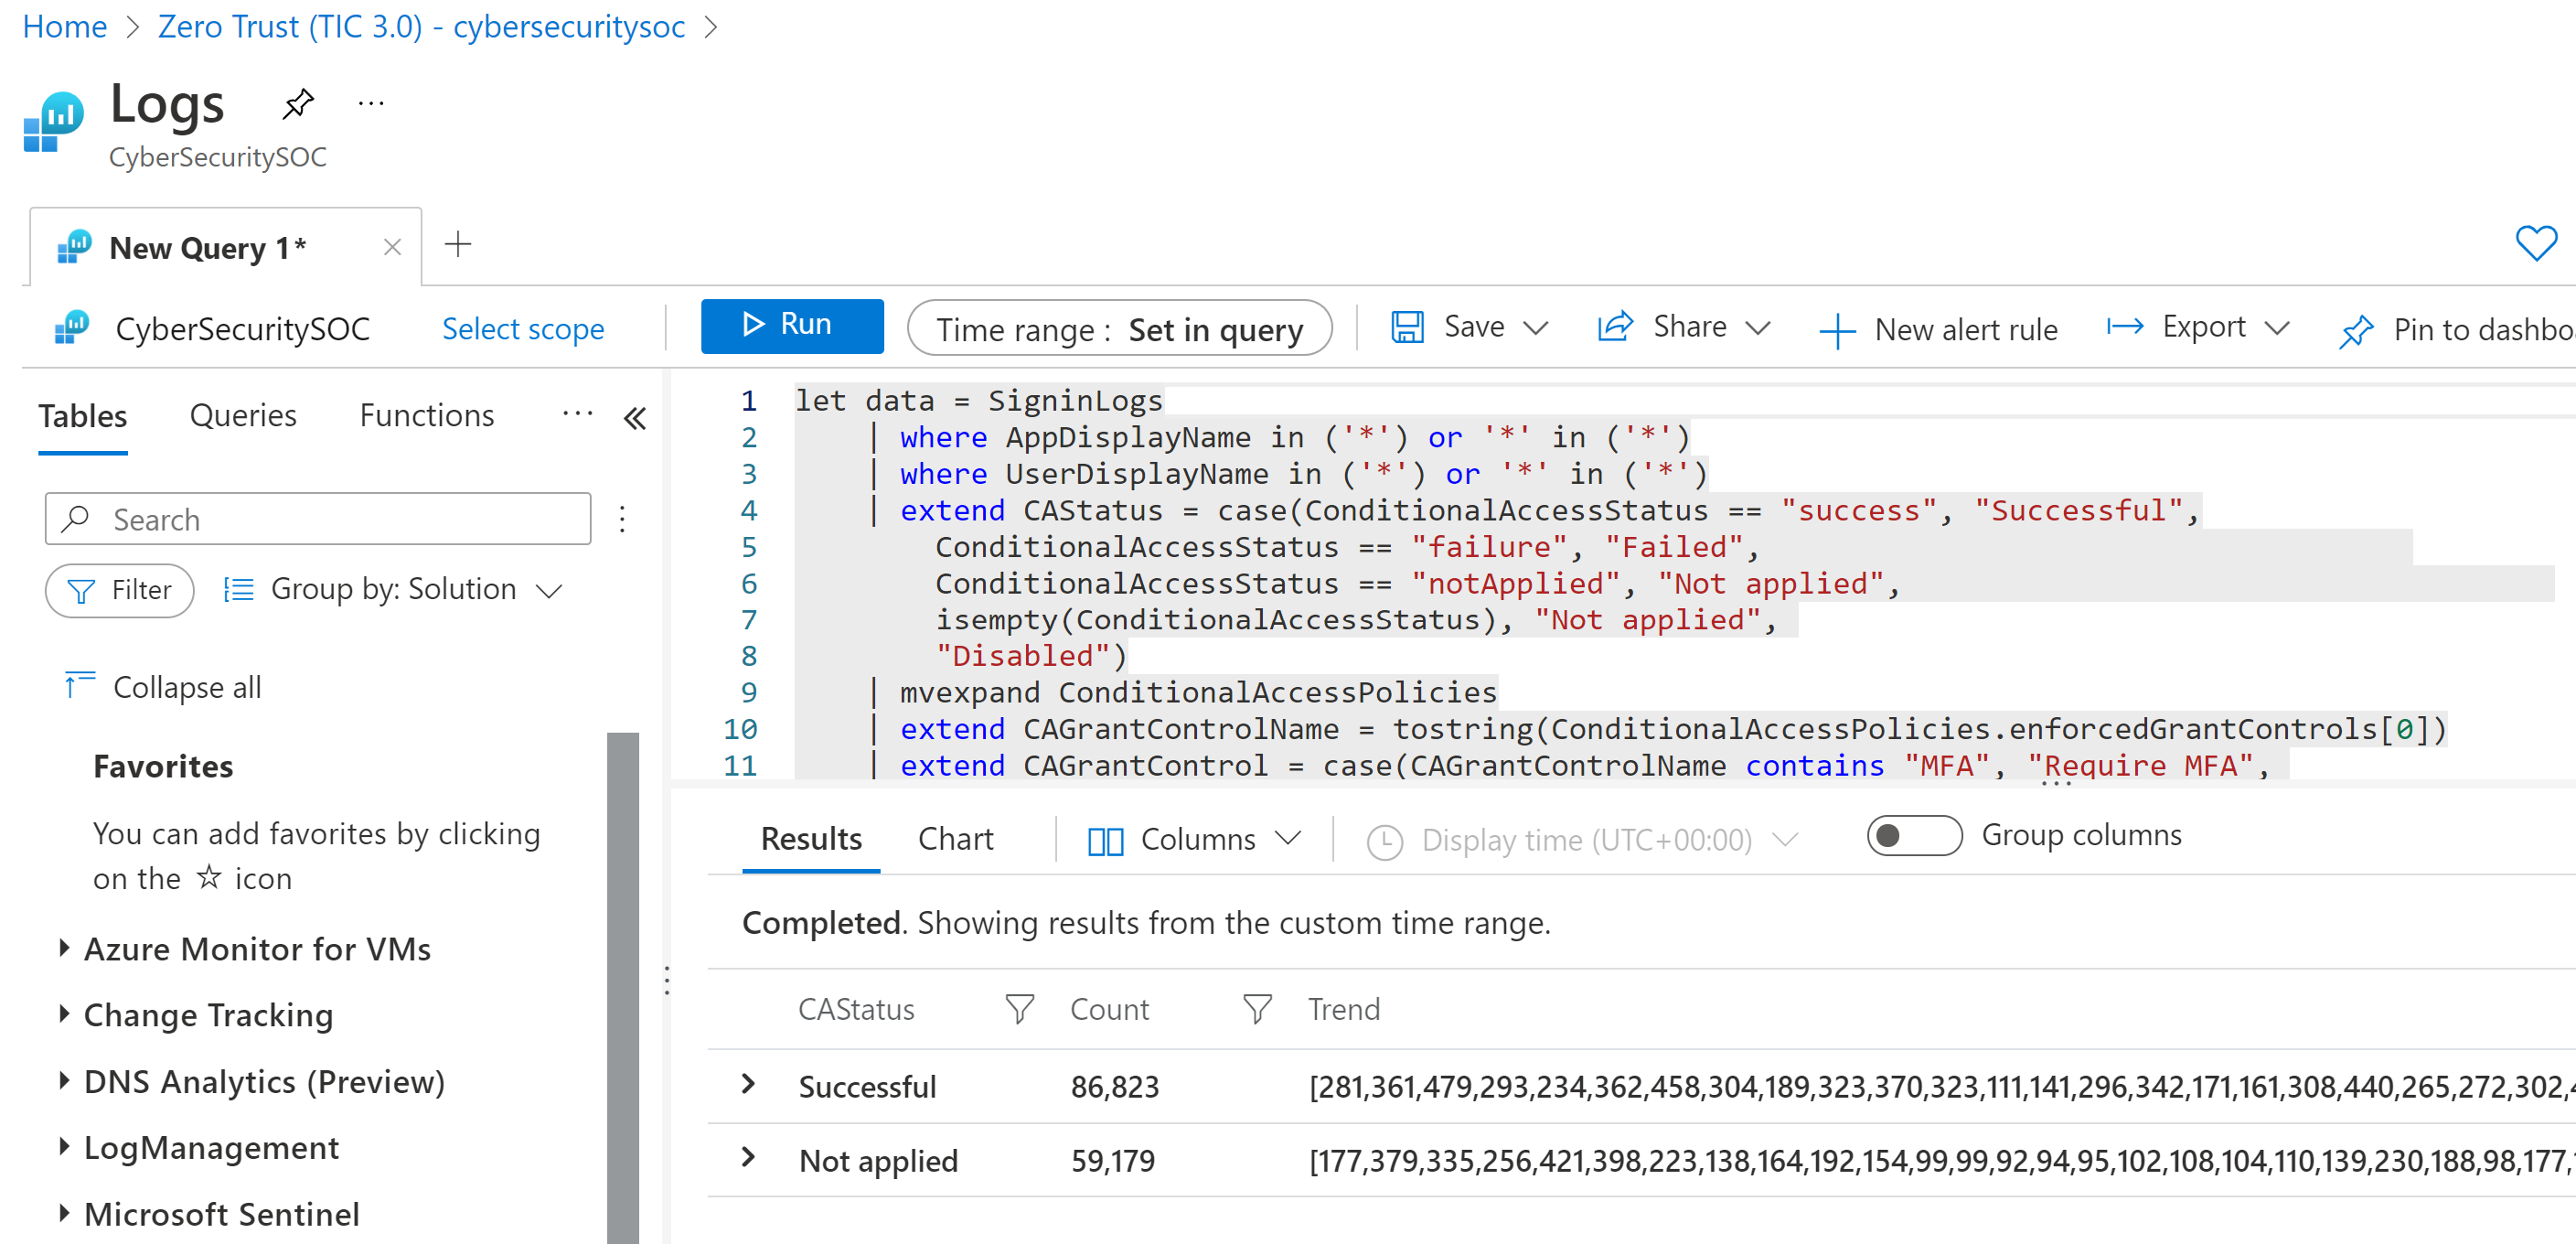
Sentinel Incident integration and Log Analytics Logging with Zero Trust ...
Getting Started with Microsoft Azure Sentinel: Part 2
SentinelOne
Master Sentinel Log Management: Calculate Ingestion Volumes
How to Create a Log Analytics workspace and deploy Microsoft Sentinel ...
Sentinel & Log Analytics – How to Create Incidents to Test with – Part ...
Configuring Microsoft Sentinel with Entra ID and UEBA | Emil Dosen
Azure Sentinel Onboarding Different Log Sources - NetSec
Log retention plans in Microsoft Sentinel | Microsoft Learn
Azure Sentinel Log Analytics step-by-step
O que é o Microsoft Sentinel? | Microsoft Learn
Sentinel Log Collector Windows 10 – IRCVP
Effective Approach To Collect Windows Firewall Events to Microsoft ...
sk154872 - Microsoft Sentinel / Azure Log Analytics: Example ...
Visualize collected data | Microsoft Learn
Microsoft Sentinel Log – Microsoft Sentinel Portal – NZNE
Tutorial: User-Based Licensing
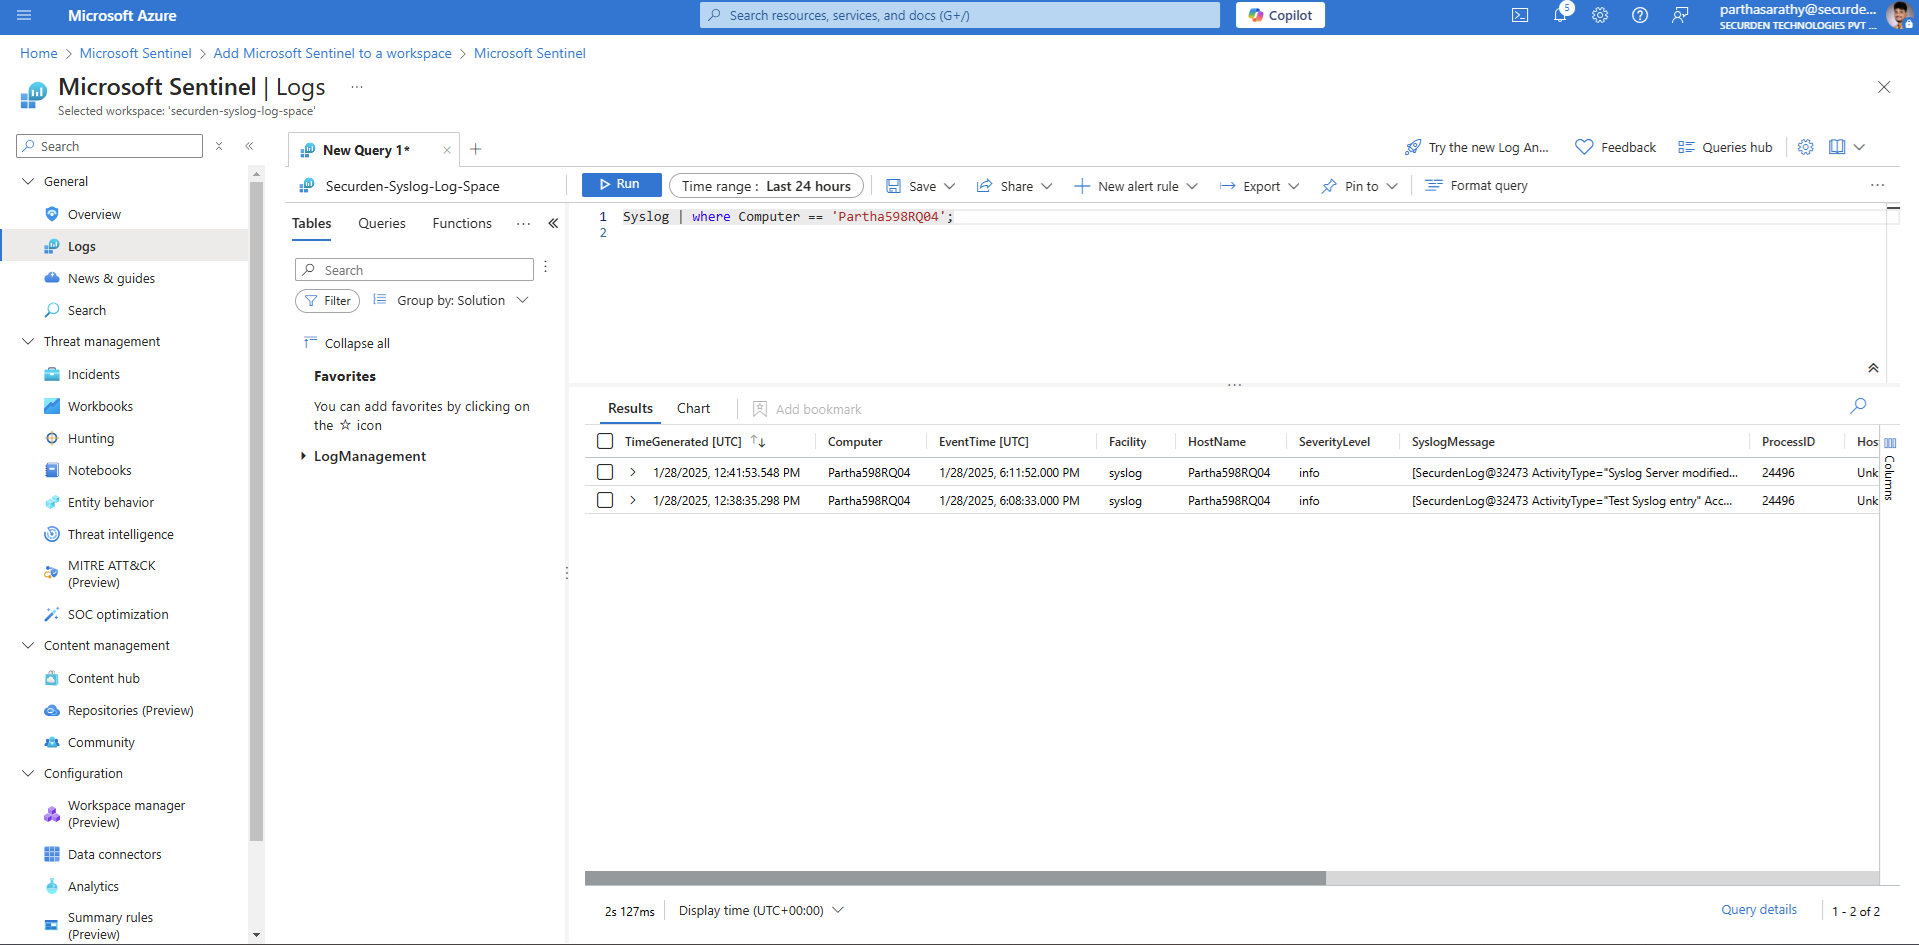
How to Integrate Azure Sentinel for Collecting Syslog | Securden EPM
What is Proton Sentinel (and should you use it?)
Azure-Sentinel/DataConnectors/microsoft-sentinel-log-analytics-logstash ...
Monitor Zero Trust (TIC 3.0) security architectures with Microsoft ...
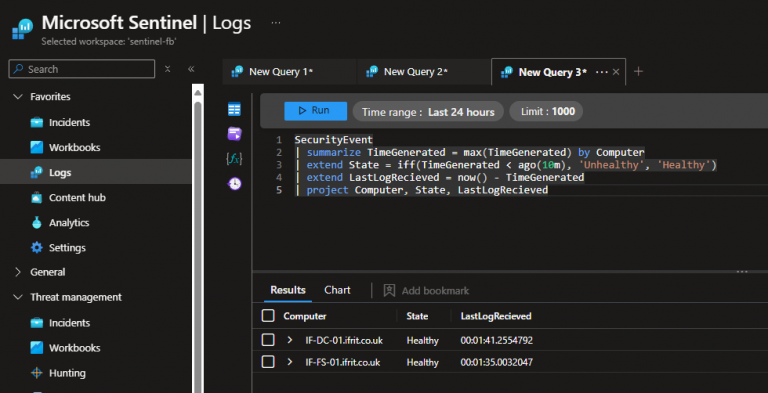
Monitor Log Flow For Devices in Microsoft Sentinel 8
Microsoft Sentinel vs Log Analytics Workspace
Azure Sentinel Log Query Scripts Collection : KQL (Kusto Query Language ...
Demystifying Microsoft Sentinel Multi-Tier Logging 8
How to analyze Microsoft Sentinel Daily Cap Alerts ...
Met Microsoft Sentinel alle incidenten en risico’s overzichtelijk bij ...
Monitor Microsoft Sentinel Data Connectors using Health Monitoring and ...
Set Up Syslog Forwarding to Microsoft Sentinel
Configuring Data Connector And Producing Activity Data in Microsoft ...
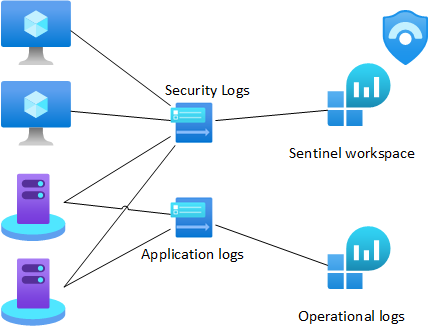
Azure Sentinel Log Collector _ Workspace architecture best practices ...
Integration with Microsoft Sentinel | NetScaler® Console service
Connect Microsoft Sentinel (Logging) – Elisity
Microsoft Sentinel Activity Log – FXOECZ
Linux安装部署Nacos和sentinel_linux安装sentinel-CSDN博客